Cisco Secure Access for Government Help

PDF

Cisco Secure Access for Government Help

Troubleshoot Virtual Appliances

Want to summarize with AI?

Log in

Describes troubleshooting virtual appliances. Log in to your Cisco Secure Access Virtual Appliance (VA) to diagnose error conditions on the Virtual Appliance.


Log in to your Cisco Secure Access Virtual Appliance (VA) to diagnose error conditions on the Virtual Appliance.

Prerequisites

A username and password to sign in to your Virtual Appliance.

Reset a Virtual Appliance's Password


Use Configuration Mode to Troubleshoot

The VA allows basic troubleshooting commands to be executed using the Configuration Mode.

Procedure

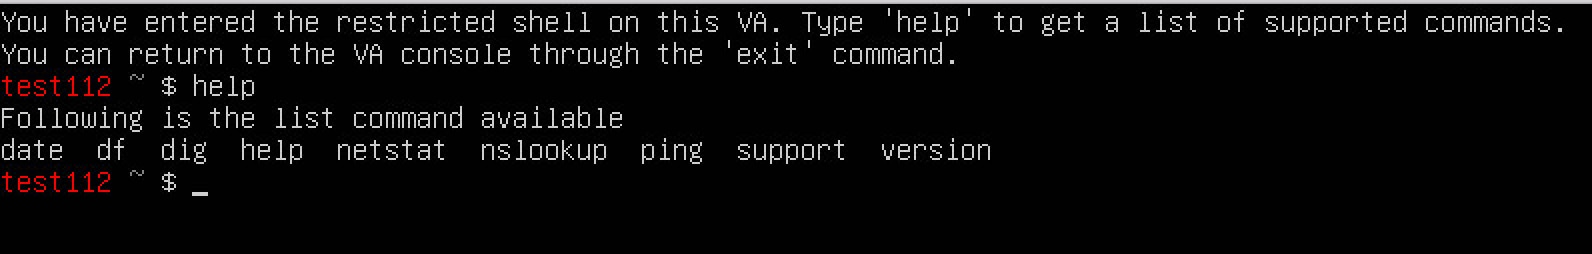
  1. To enter the Configuration Mode, on the VA console, press Ctrl+B. You can also enter the Configuration Mode by initiating an SSH connection to the VA.


    The Restricted Shell interface.
  2. To view a list of supported commands in the restricted shell, enter help.

  3. To return to the VA console, type exit.

What to do next

If the VA console crashes, the VA automatically enters the restricted shell.


Troubleshoot Intermittent DNS Resolution Failures on a VA Deployed on Azure

If you have deployed the VA on Azure as a stand-alone virtual machine (VM) without a public IP address, you might experience intermittent DNS resolution issues when heavy DNS traffic is directed at the VA. This is due to SNAT port exhaustion on virtual machines deployed to Azure (such as the VA) because Azure only pre-allocates 1024 UDP ports for standalone VMs without a public IP address. To address this issue, you may either need to assign a public IP to each VA or deploy VAs behind a public Standard Load Balancer in Azure.

Note: If you are assigning a public IP to a VA, make sure that there are no inbound port rules for this VA that allow inbound access from the internet.


Troubleshoot DNS Resolution in Configuration Mode

The nslookup command can be used to test DNS queries on the VA. This test reflects how a users' DNS lookups will be answered and is subject to internal domains routing and other processing on the VA.

You can specify a server IP address as a parameter for nslookup. This is useful for testing a Local DNS server or the Secure Access cloud directly. These tests bypass the VA software.


Troubleshoot DNS Resolution Failures Behind a Firewall

The VA offers DNSCrypt functionality that protects the content of your DNS queries. This functionality may be blocked by your firewall.

If you are using the Cisco ASA firewall, you can see an indication of this in the ASA log. For example:

Dropped UDP DNS request from inside:192.168.1.1/53904 to outside-fiber:18.254.118.193/53; label length 71 bytes exceeds protocol limit of 63 bytes

DNS resolution is not affected by this blocking, but your DNS queries are not fully protected.

To address this, ensure that your firewall allows outbound queries on port 443 and 5353 for both TCP and UDP to the Secure Access resolver IP addresses as mentioned in the Pre-requisites section.