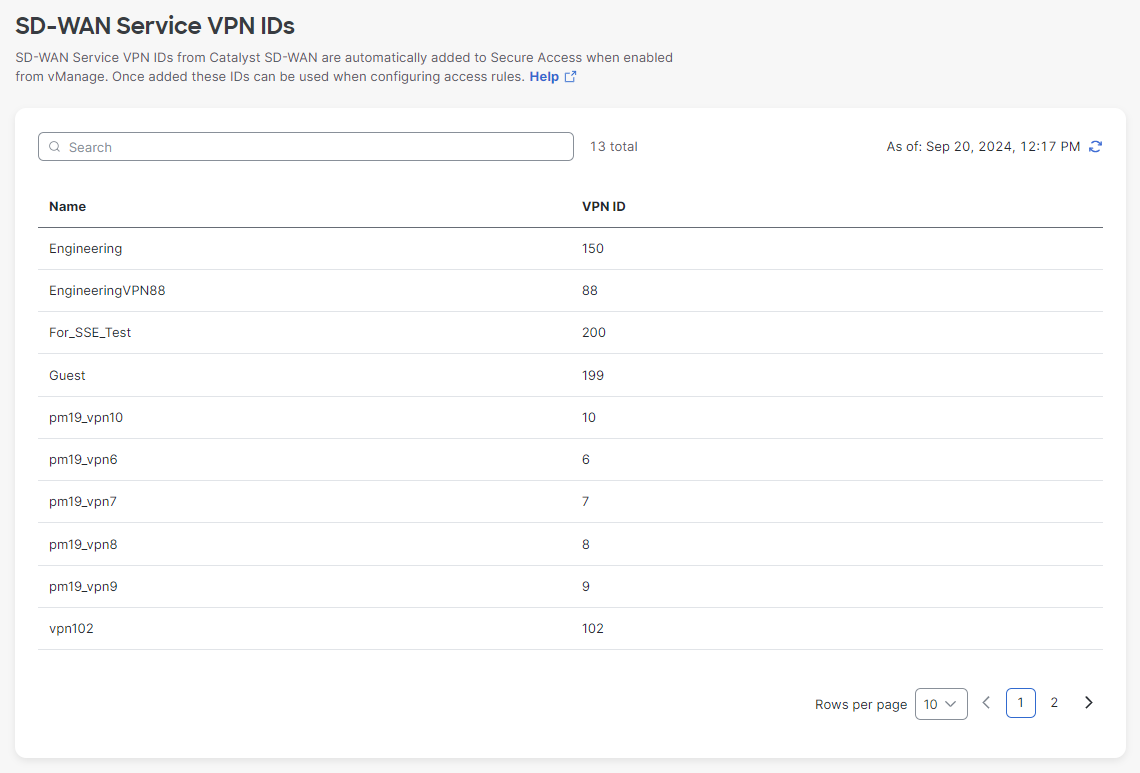
Describes integrating catalyst sd-wan with secure access. Cisco Catalyst SD-WAN integrates with Cisco Secure Access to share network context between the platforms for the purpose of applying consistent security enforcement for users, devices and workloads across the enterprise.
Cisco Catalyst SD-WAN integrates with Cisco Secure Access to share network context between the platforms for the purpose of applying consistent security enforcement for users, devices and workloads across the enterprise. Context-aware security policies become key for implementing and achieving a true zero-trust framework for the enterprise.
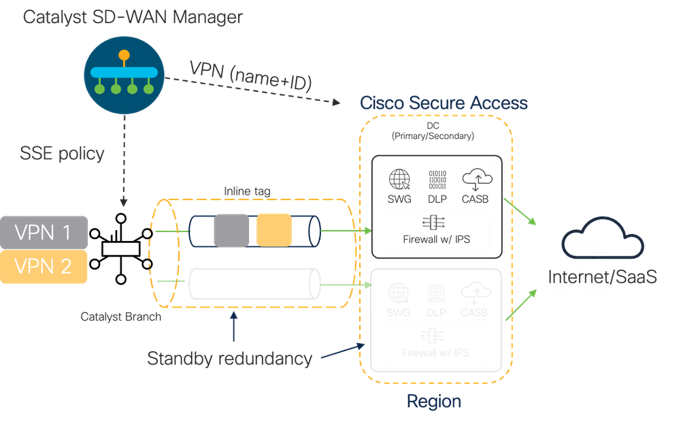
With this integration feature, administrators can automatically build tunnels with reliability to Secure Access from a Catalyst SD-WAN branch and share VPN ID/name context learned from the enterprise. Cisco Catalyst SD-WAN can be deployed and connected using either virtual or physical secure routers at branch offices, data center networks, and regional hubs. This integration allows IT teams to:
-
Connect any user to any application, with integrated capabilities for multicloud, security, predictive operations, and enhanced network visibility on a Secure Access Service Edge (SASE)-enabled architecture.
-
Ensure a predictable user experience for applications.
-
Optimize Software-as-a-Service (SaaS), Infrastructure-as-a-Service (IaaS), and Platform-as-a-Service (PaaS) connections.
-
Offer integrated security, either on-premises or in the cloud.
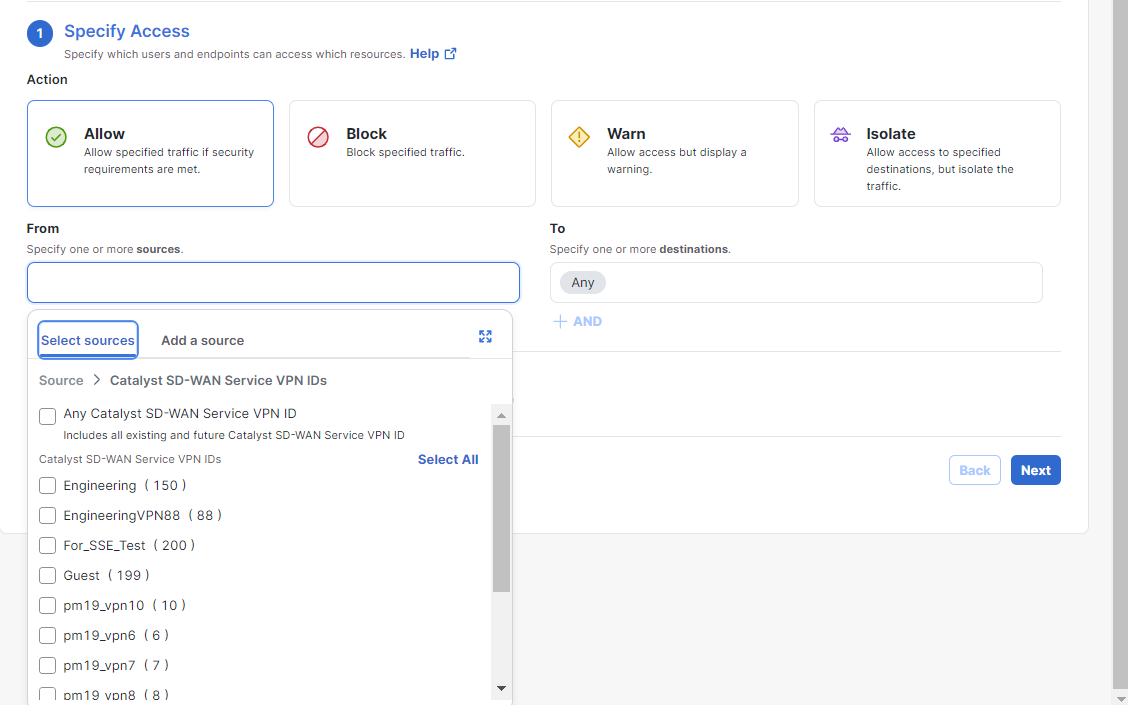
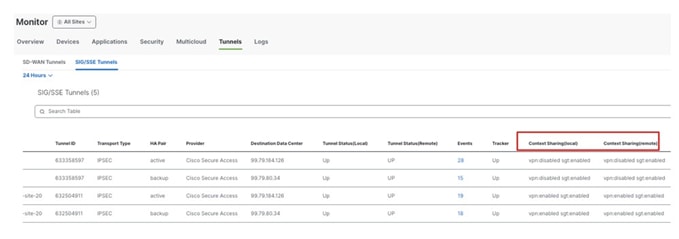
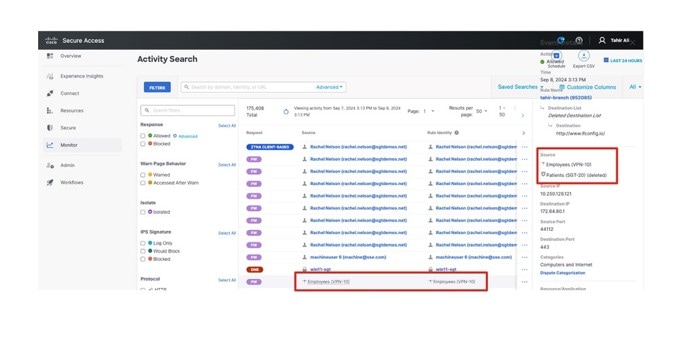
This section describes how to enable inline context propagation, represented by VPN IDs.