Traffic that is not decrypted cannot be effectively inspected for threats.
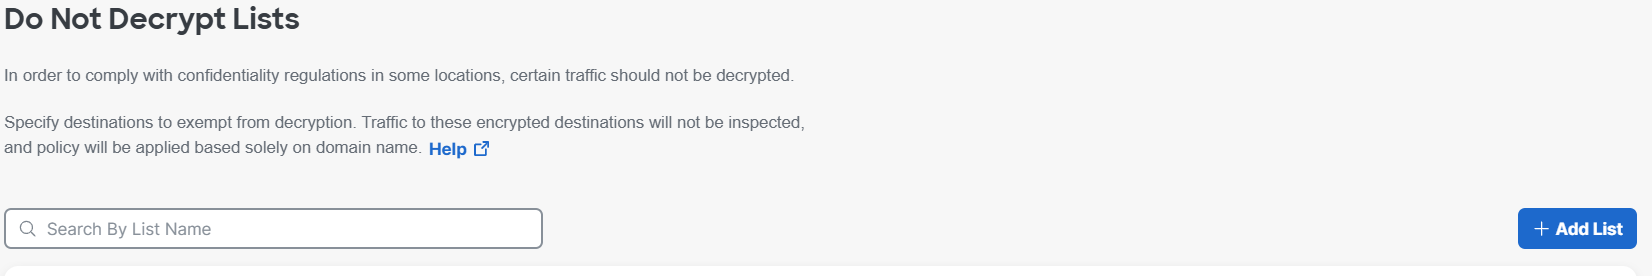
However, in order to comply with confidentiality regulations in some locations, certain traffic should not be decrypted. You can use Do Not Decrypt lists to specify these destinations.
Do Not Decrypt lists apply only to destinations in internet access rules, and they are used for both web security and intrusion prevention (IPS) features.
Currently, IPS profiles and security profiles support Do Not Decrypt lists differently:
-
All IPS profiles use a single Do Not Decrypt list.
-
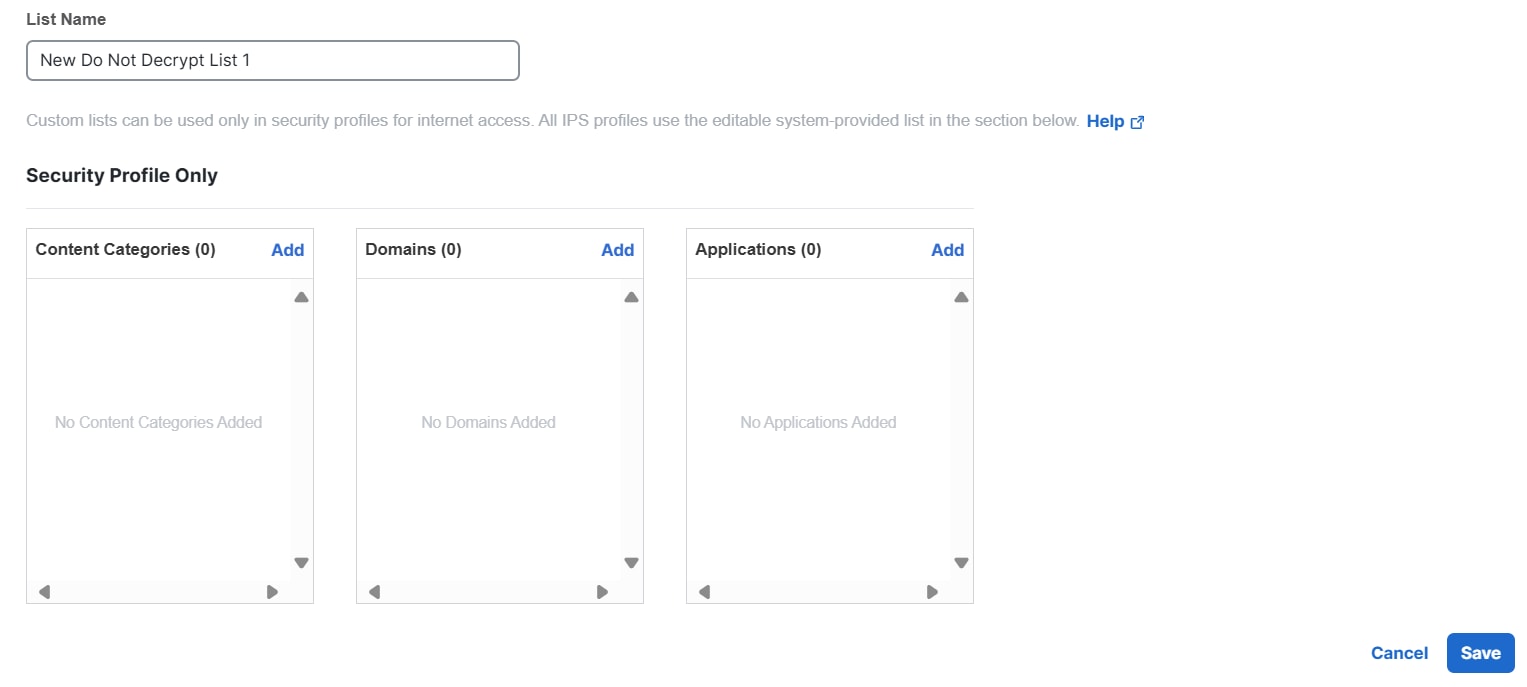
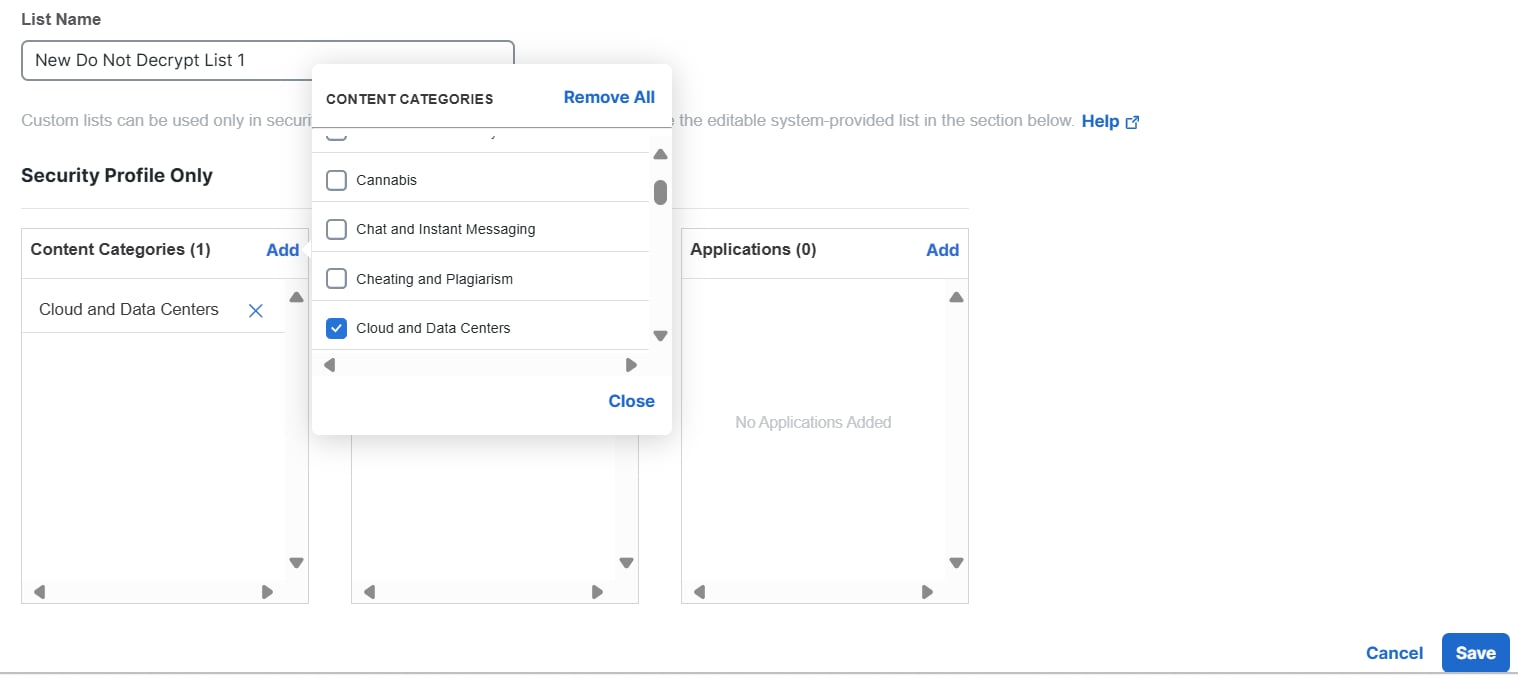
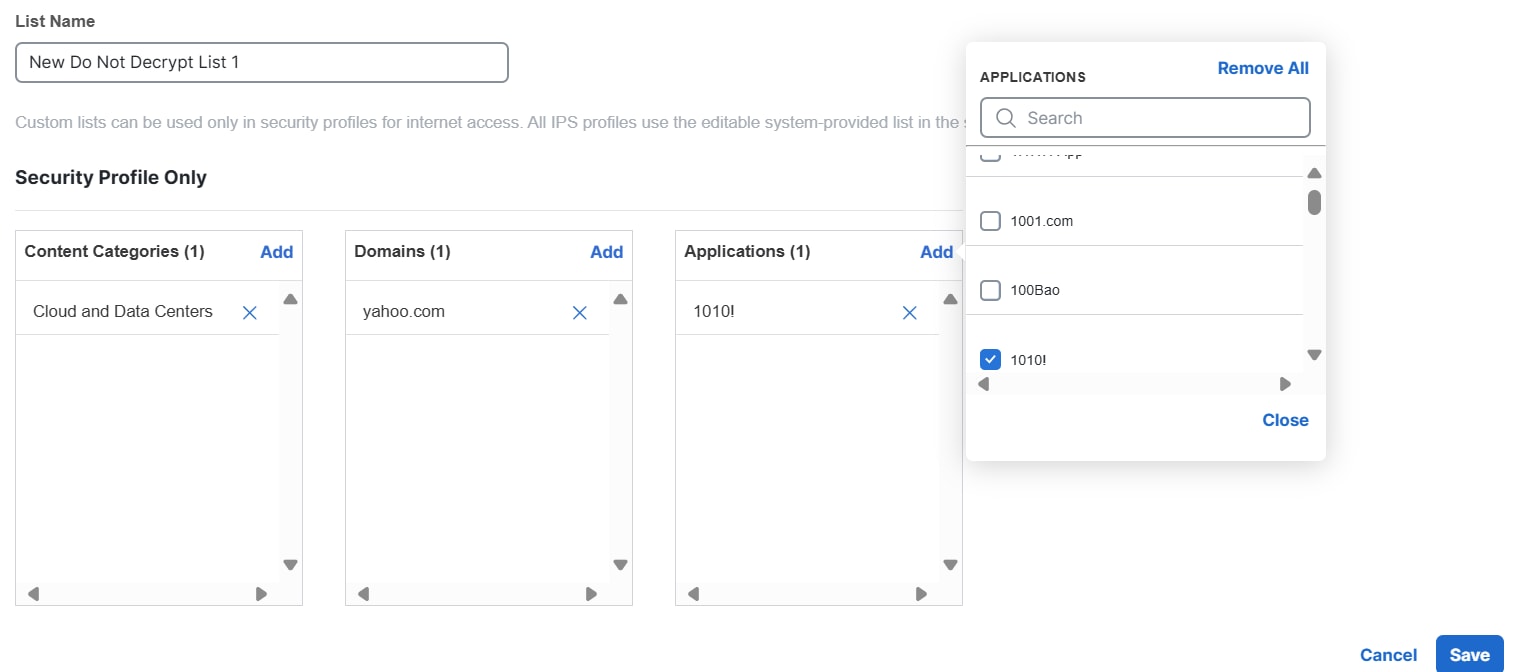
Each security profile can use any Do Not Decrypt list.
-
The types of destinations that you can specify for IPS and web features are different. See the applicable sections below.