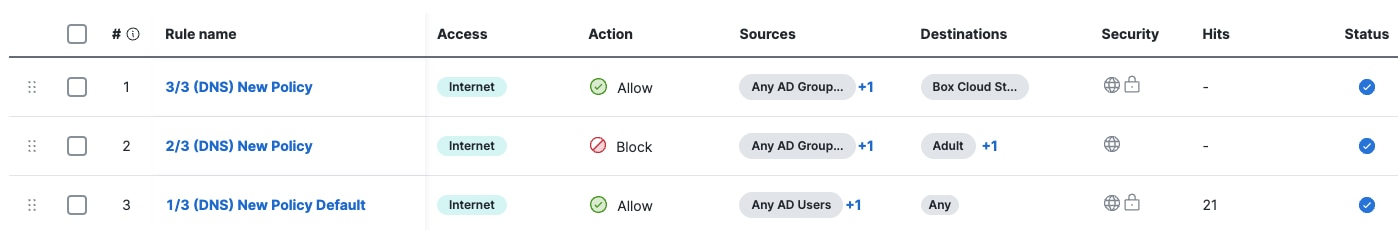
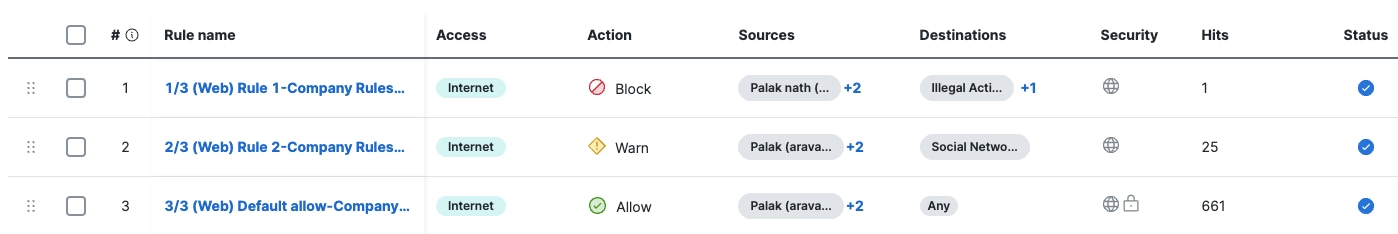
Umbrella DNS policies, Web policy, and Firewall policy are now Secure Access internet access rules. An internet access rule can now be enforced at the DNS layer, web proxy layer, and firewall layer.
The conversion to Secure Access internet access rules unifies policies from Umbrella DNS, Web, and firewall-significantly expanding their enforcement. Now, these consolidated rules can be applied across the DNS, web proxy, and firewall layers, offering more comprehensive control.
This upgrade introduces a fundamental change in policy structure, unlike Umbrella where a single policy or rule could contain multiple block and allow components, Secure Access employs a single Access policy model where each individual rule is configured exclusively to either block or allow traffic.
Secure Access uses a unified policy model where rule order determines traffic precedence. Review and test your rules thoroughly before manually reordering them, as moving a rule can change how traffic is handled and may inadvertently allow traffic that was previously blocked.
The order of rules on the Policy page is crucial for how traffic is managed. Traffic is processed by the first rule in the list that matches, and any rules below that matched rule have no effect on that traffic. It is important to arrange your rules so that more specific rules are placed above more general rules. Essential rules, such as those blocking access to sites you want to restrict for all users, should be positioned at the top. If no rule matches the traffic, Secure Access applies the default access rule for the traffic type (internet or private access), located at the bottom of the Access policy page.
Misconfigurations can lead to unintended events, such as unprotected resources or users accessing blocked destinations, so careful planning and design of your rules before implementation is essential. Test your rules by creating a new identity in Umbrella and redirecting the traffic to Secure Access. Follow these steps to Redirect Umbrella Traffic to Secure Access Sources.
Migration order
During the transition, Umbrella DNS, Web, and Firewall policies are transformed into multiple rules in Secure Access, similar to this order depending on how you selected your policies to copy into Secure Access:
-
Umbrella Web Policy sourced rules.
-
Umbrella Web Default Policy sourced rule.
-
Umbrella DNS Policy sourced rules.
-
Umbrella DNS Default Policy sourced rule.
-
Umbrella Firewall Policy sourced rules.
-
Umbrella Firewall Default Policy sourced rule.
For more information, see our Cisco Secure Access guidebook on Get Started With Internet Access Rules and Manage the Access Policy.
| Umbrella Policy Components | Secure Access Internet Access Rules |
|---|---|
| Policies | Access Policy |
| DNS policies | Internet Access Rules |
| Web policy | Internet Access Rules |
| Firewall policy | Internet Access Rules |
| Application Settings | Application List |
| Block Page Appearance | Notification Page |
| Content Categories | Content Categories |
| Destination Lists | Destination Lists |
| Identities | Sources |
| Mobile Device and Roaming Computer | Roaming Device |
| Security Settings | Threat Categories |
| Selective Decryption | Do Not Decrypt List |