Cisco Secure Access Help

PDF

Cisco Secure Access Help

Internet Access Rules

Want to summarize with AI?

Log in

Describes Internet Access Rules in Cisco Secure Access. Internet access rules specify how traffic to internet destinations should be secured and handled.


Internet access rules specify how traffic to internet destinations should be secured and handled.

Traffic to internet destinations is allowed by default. You must create rules to block access to internet destinations either for acceptable use or security reasons, to warn users before you allow access, or to isolate specified internet traffic.

  1. Plan your internet access rules

    Plan your rule set so you get the results you expect. Read the documentation and familiarize yourself with the various components that make up rules.

  2. Create rule components

    Assemble rules largely from pre-configured source and destination components, and security control components. For more information, see Components for Internet Access Rules.

  3. Specify rule defaults

    New rules will use the default security controls and other settings that you specify on the Rule Defaults page. For more information, see Default Settings for Internet Access Rules.

  4. Edit the default internet access rule

    Traffic to internet destinations that does not match any other internet access rule in the policy will be handled. For more information, see View or Edit the Default Access Rules.

  5. Add internet access rules

    For more information, see Add an Internet Access Rule.

  6. Review the global settings

    Normally you will not change these settings for internet access rules, but you should be familiar with their impact. For more information, see Global Settings for Internet Access Rules.

  7. Ensure that rules match encrypted traffic

    For more information, see Ensure Rule Matching for Encrypted Internet Traffic.

  8. Review the rule order

    Make sure the order of the rules on the Access Policy will have the results you expect. For more information, see Edit the Order of the Rules on the Policy Page.

  9. Test your internet access rules


Default Settings for Internet Access Rules

You can choose default settings that will automatically populate newly created internet access rules by default.

In Secure Access, navigate to the Secure > Access Policy, click Global Settings and Rule Defaults to configure the Default Settings.

For more information, see Rule Defaults and Edit Rule Defaults and Global Settings.

Choose rule defaults carefully. Changing the Default Settings later may impact existing rules. For more information, see Important Information About Changing Rule Defaults.

Default Settings that apply to internet access rules:

  • Intrusion Prevention (IPS) Profile—Specify the traffic-inspection behavior to use by default in new access rules. This setting applies to both private access rules and internet access rules. For more information about IPS profiles, see Manage IPS Profiles.

  • Security Profile—Specify a default set of settings that control security and other interactions for end users accessing the internet. For more information about security profiles, see Manage Security Profiles.

  • Tenant Controls—If your company uses Microsoft 365, Google G-Suite, Slack, or Dropbox, you must configure tenant controls. For more information about tenant controls, see Manage Tenant Control Profiles.


Global Settings for Internet Access Rules

Global settings generally apply to all rules. However, some settings apply only to private access rules, not to internet access rules.

Do not change global settings unless you have a specific reason to do so.

If your company uses either of the following, verify that the applicable global settings are correct for your company:

  • Microsoft 365 applications

  • Applications that use pinned certificates

Decryption-related settings:

  • Decryption—For troubleshooting purposes, you can temporarily disable decryption for the specified features, for all private and internet access rules.

  • Disable decryption for specific sources—Use this setting to disable decryption from sources on which certificates cannot be installed, such as IOT "internet of things" devices, that need to connect to the internet.

  • Decryption Logging—Choose whether to enable or disable logging of decryption events for internet access rules.

For more information about these settings, see Global Settings for Access Rules.

To change default rule settings, see Edit Rule Defaults and Global Settings.


Components for Internet Access Rules

Cisco Secure Access supports configuring security controls for sources and destinations (resources) on internet access rules in the organization's Access policy. You can create access rules by adding components that you or others have previously created or entering network information directly on a rule for sources and destinations. Pre-configured components described in this topic are reusable. You can use the same pre-configured components in multiple access rules.

Before you can add resources in Secure Access, deploy the resources in the organization's environments. Also configure resources for destinations in Secure Access: content categories, destination lists, and application lists. Once you register the resources in Secure Access, you can select these components on the internet access rules.

For example, you can define a set of users as a source, then use the same source in an internet access rule and in a private access rule for the same set of users. Some components are profiles, or groups of settings bundled together that you choose as a unit when configuring a rule.


Sources

Sources on internet rules are either pre-configured or composite components. Pre-configured source components such as Registered Networks and Network Tunnel Groups acquire and manage the web traffic in your organization. For information about pre-configured source components, see Reusable Sources in Internet Access Rules.

Composite sources may include IP addresses, CIDR blocks, and wildcard masks, and ports and port ranges. For information about composite source components, see Composite Sources in Internet Access Rules.

About Selecting Sources on an Access Rule

If you select Network Tunnel Groups, Secure Access secures and controls the traffic access from the IPsec tunnels established by your supported network devices. If you need to know what tunnels are included in a group, navigate to Connect > Network Connections > Network Tunnel Groups and look at the group configuration.

If you select a Network Tunnel Group, the destination also includes IP addresses configured in the network tunnel group for routing, in addition to all associated Internal Networks. IP addresses include routes advertised using Border Gateway Protocol, if that option is selected in the network tunnel group configuration.

If you see an option to Select All, this selects all existing items in the group at the time you select it, but the rule will not include items added to the group in future.

Number of Sources Supported in a Rule

You can add up to 250 sources in an internet access rule. The total number of sources accepted in an access rule includes both pre-configured sources (resources) and sources that you enter directly on an access rule (composite sources).

You can add at most 10 composite sources in an internet access rule.


Reusable Sources in Internet Access Rules

You can configure internet access rules for specific source-destination pairs. Sources are the users, groups of users, or other entities that comprise the From end of traffic where Secure Access applies an access rule.

In a rule, you can also specify sources by typing in IP addresses and subnets, but these are not reusable source components. For more information, see Composite Sources in Internet Access Rules


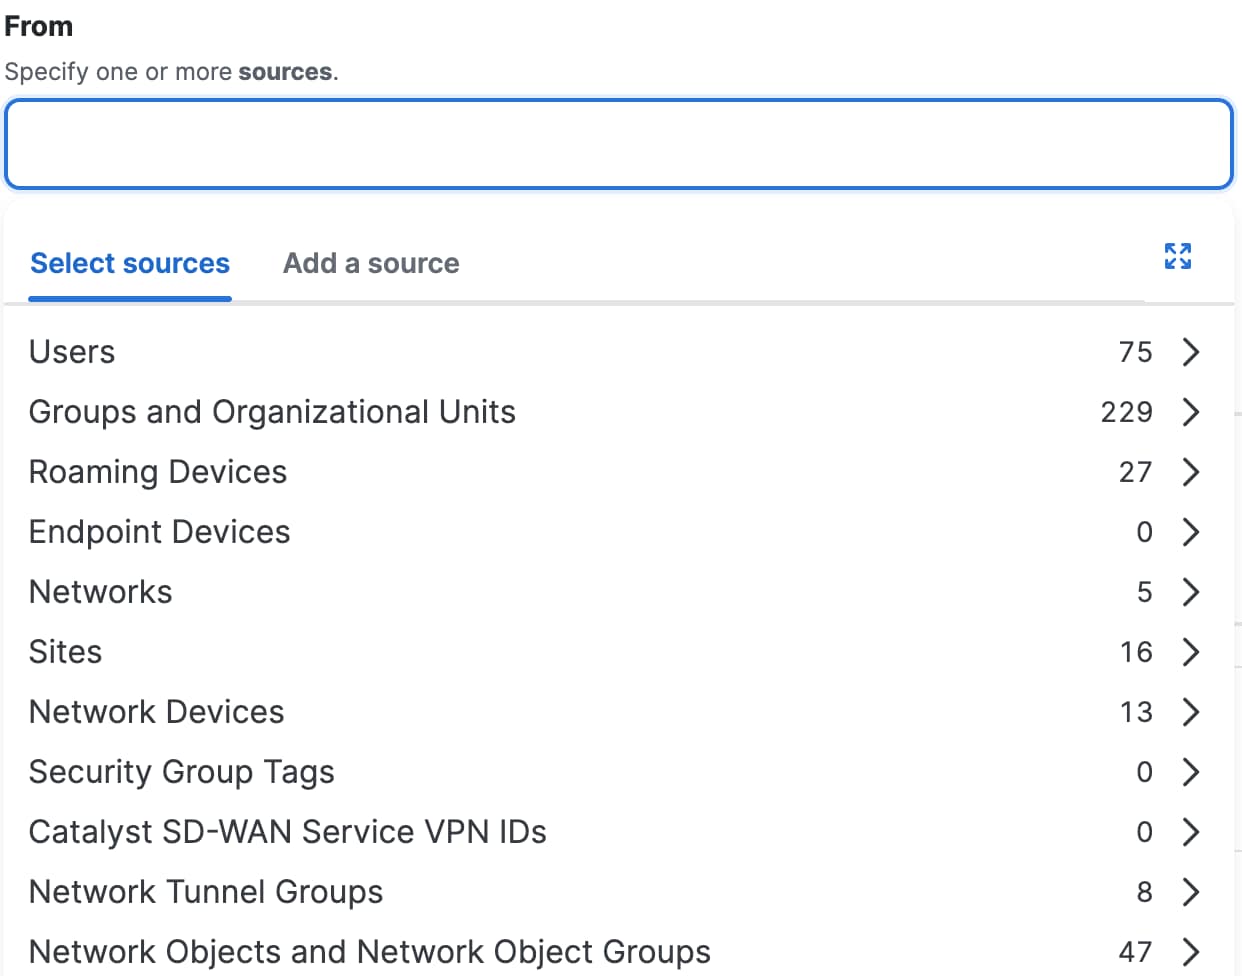
The Internet Access Rule Source Components interface.

You can use these reusable sources in your internet access rules:

  • Users

    You can apply rules to the traffic for the users in the organization.

  • Groups and Organizational Units

    You can apply rules to the traffic for users in AD Groups and Google Workspace Organizational Units.

  • Roaming Devices

    You can apply rules to traffic originating from managed devices that have the Cisco Secure Client installed, but that may not currently be on the corporate network.

  • Network Objects

    You can apply rules to the traffic originating from IP addresses in network segments defined by Network Objects.

  • Network Object Groups

    You can apply rules to the traffic originating from IP addresses in network segments defined by Network Objects in Network Object Groups.

  • Endpoint Devices

    You can apply internet access rule security controls to AD devices in Secure Access. Once provisioned, AD devices are available as sources on internet access rules. You can select all AD devices or individual AD devices identified by device name. For more information about AD device provisioning, see Manage Users, Groups, and Endpoints Devices.

  • Registered Networks

    You can apply rules to traffic originating from IP addresses in network segments defined by Registered Networks.

    • When on a Registered Network, users devices can send traffic to the Secure Access DNS resolvers and the Secure Web Gateway (SWG) directly. In this scenario, user devices are not required to deploy the Cisco Secure Client with the Internet Security and VPN modules or deploy IPsec tunnels (RAVPN).

    • If the user device has the Cisco Secure Client deployed with the Internet Security and VPN modules, then traffic is sent over IPsec tunnels to Secure Access.

  • Sites

    You can apply rules to traffic originating from IP addresses in network segments defined by Secure Access Sites.

  • Network Devices

    You can apply rules to traffic originating from network devices.

  • Security Group Tags

    You can apply rules to traffic originating from IP addresses in network segments that include Security Group Tags.

  • Catalyst SD-WAN Service VPN IDs

    You can apply rules to traffic originating from IP addresses in network segments that include VPN IDs. Be aware that if the same VPN ID (VPN 88 for example) is assigned across different branches, then traffic coming into Secure Access from these branches is subject to the same policy. A Secure Access policy rule cannot differentiate traffic between branches using the same VPN ID.

  • Network Tunnel Groups

    You can apply rules to the traffic originating from IP addresses in network segments defined by Network Tunnel Groups.


Combining Reusable Sources in a Rule with Boolean Logic

If an internet access rule includes multiple reusable sources, Secure Access applies the sources together using boolean logic.

Secure Access combines all types of reusable sources and all sources within a type using the boolean OR operator. Traffic to each source that you specify in the access rule matches the rule.

For example, if you specify a user group and a network tunnel group as sources, traffic from any member of either group matches the rule.

Using the AND Operator With Sources

Secure Access supports adding pre-configured sources on internet access rules combined with the logical AND operator. For information about adding sources with the AND operator, see Add an Internet Access Rule.

Secure Access enforces the access rule only if all sources added on the access rule match the organization's network traffic. For example, if you add a Google Workspace User source and add the AND operator with a Registered Network source, traffic for both sources must match for Secure Access to apply the access rule.

Supported Combinations of Reusable Sources with Composite Sources

You can select pre-configured sources and enter composite sources on the internet access rules in your Access policy. Secure Access uses the logical OR operator to combine the pre-configured sources with the composite sources.

You can enter these composite sources on an internet access rule:

  • IP/CIDR Blocks/Wildcard Mask

  • Ports and port ranges

For more information about composite sources, see Composite Sources in Internet Access Rules.

Supported Combinations of Reusable Sources With the AND Operator

Reusable Sources AND with Other Reusable Sources
AD Users

Registered Networks

Internal Networks

Network Tunnel Groups

AD Groups

Registered Networks

Internal Networks

Network Tunnel Groups

Google Workspace Users

Registered Networks

Network Tunnel Groups

Google Workspace Organizational Units (OUs)

Registered Networks

Network Tunnel Groups

Chromebooks

Registered Networks

Network Tunnel Groups

Mobile Devices

Registered Networks

Roaming Devices

Registered Networks

Network Tunnel Groups

Users

Groups and Organizational Units

Registered Networks

AD Users

AD Groups

Google Workspace Users

Google Workspace OUs

Chromebooks

Mobile Devices

Roaming Computers

Internal Networks

Sites

Sites

AD Users

AD Groups

Google Workspace Users

Google Workspace OUs

Chromebooks

Mobile Devices

Roaming Computers

Internal Networks

Registered Networks

Internal Networks

AD Users

AD Groups

Google Workspace Users

Google Workspace OUs

Sites


Composite Sources in Internet Access Rules

Organizations can add network address information directly in the source component of an internet access rule. The source component supports IP addresses (IPv4 and IPv6), CIDR blocks, and wildcard masks, and ports and port ranges. For more information, see Add an Internet Access Rule.

Note

Internet access rules that include composite sources support the Allow and Block actions only.

Guidelines for Adding Composite Sources in a Rule

  • Composite sources are valid public IPv4 or IPv6 addresses, private non-routable IPs (RFC-1918 compliant), CIDR blocks, wildcard masks, and ports and port ranges. For information about wildcard masks, see Using Wildcard Masks on Access Rules.

  • IP addresses do not require a deployed IPsec tunnel.

  • Secure Access does not support a comma-separated list of wildcard masks.

  • If the IP addresses added as composite sources are not associated with the organization's Registered Networks, Secure Access does not manage traffic on these IP addresses.

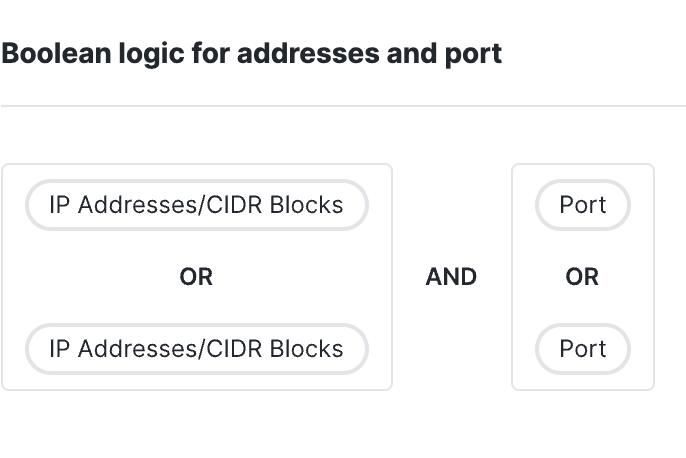
Combining Source Addresses and Ports

Combining IPs, CIDRs, or Wildcard Masks on a Source

When you add the IP addresses and CIDR blocks for a source on an internet access rule, Secure Access creates a single source entry. Secure Access uses the OR operator to combine the IP addresses, CIDR blocks, and wildcard masks that you entered on the rule.

Combining Ports and Port Ranges on a Source

When you add the ports and port ranges for a source on an internet access rule, Secure Access creates a single source entry. Secure Access uses the OR operator to combine the ports and port ranges that you entered on the rule.

Combining IP Addresses and CIDR Blocks With Ports on a Source

Secure Access uses the AND operator to combine the IP addresses and CIDR blocks with the ports and port ranges entered on the source component of the internet access rule.


The Internet Rules Sources Boolean Logic interface.

Destinations

Destinations on internet rules are either pre-configured or composite components. For information about pre-configured destination components, see Reusable Destinations in Internet Access Rules.

Composite destinations may include IP addresses, CIDR blocks, wildcard masks, fully-qualified domain names (FQDNs), ports and port ranges, and transport protocols. For information about composite destination components, see Composite Destinations in Internet Access Rules.

Number of Destinations Supported in a Rule

You can add up to 5000 destinations in an internet access rule. The total number of destinations accepted on an access rule includes both pre-configured destinations (resources) and destinations that you enter directly on an access rule (composite destinations).

You can add at most 10 composite destinations in an internet access rule.

For optimal performance, include no more than 100 destinations in a rule.

How to Add Destinations on Internet Access Rules

For more information, see Add an Internet Access Rule.

  • We recommend that you pre-configure destinations in Secure Access.

  • You can also specify web sites by their content categories, individual web application, or web application categories without creating content category lists or application lists. On an internet rule, choose Content Categories or Application Categories.

  • Depending on the destinations you select (for example certain applications, application lists, or application categories) other options may appear in the rule.

  • If you see an option to Select All, this selects all existing items in the group at the time you select it, but the rule will not include items added to the group in future.

  • When you select a list or group, entities that are added to the list or group in the future are automatically included. For example, if you select a Destination List, any destinations that you add to that destination list later are automatically included.

  • If this rule involves tenant controls, you must include the relevant application as a destination in the rule, as well as configuring the applicable tenant control profile and specifying that profile in the Security Controls section of the rule. For more information, see Manage Tenant Control Profiles.

  • When specifying applications, it is not possible to search for an application with fewer than three letters in its name—for example, QQ or YY. You must pick the applications manually from the tree under their respective categories or use a wildcard in search—for example, QQ*. This behavior is by design.


Reusable Destinations in Internet Access Rules

You can configure internet access rules in the Access policy for specific source-destination pairs. Destinations are the web applications, web sites in particular categories, or other internet destinations that comprise the "To" end of traffic where Secure Access applies an access rule.

In an access rule, you can also enter destination IP addresses and subnets, and ports and protocols directly on the rule. For more information, see Composite Destinations in Internet Access Rules.

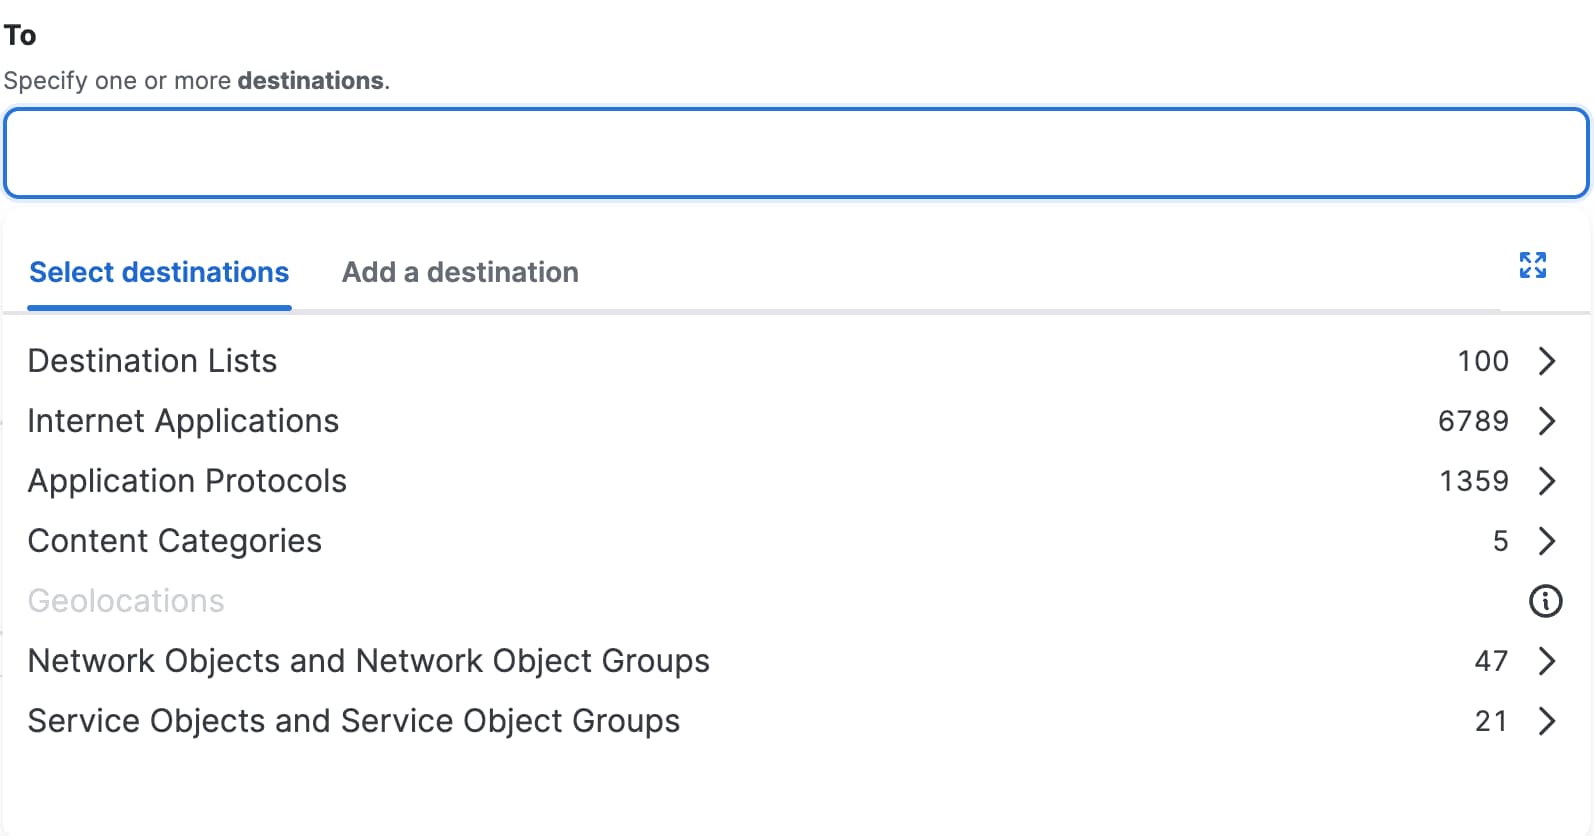
You can use these reusable destinations in your internet access rules:


The Internet Access Rules Destination Components All interface.
  • Destination Lists—Lists that group domains, URLs, IP addresses, and CIDR blocks where you want to apply the same security controls. You can create custom lists of destinations based on any criteria you choose.

  • Application Lists—Lists of web-based applications where you want to apply the same policy.

    For example, if you want to apply a single policy to all social media applications, you can create an application list that includes all applications in the Social Networking category.

    For some web-based applications, you can allow access to the application, but block uploads, downloads, and posting or sharing information. You will see these options in each rule when you configure applicable destinations in the rule. For details, see Advanced Application Controls.

  • Application Protocols—Select the application protocols for the network destinations where Secure Access applies the rule.

  • Content Category Lists—Lists of web sites based on the content or type of the site, so you can control access to a variety of sites as a group. For example, you might create a content category list that includes all sites belonging to the Adult, Child abuse, and Pornography categories.

  • Network Objects—Network Objects represent IPv4 and IPv6 addresses, CIDR blocks, ranges of IPv4 addresses, wildcard masks, or fully-qualified domain names (FQDNs). Select the Network Objects on the access rules to apply security controls to the traffic on the networks.

  • Network Object Groups—Select the Network Object Groups on the access rules to apply security controls to the traffic on the networks in groups.

  • Service Objects—Service Objects represent a port, range of ports, protocol, or traffic on any protocols. Select the Service Objects on the access rules to apply security controls to the services.

  • Service Object Groups—Select the Service Object Groups on the access rules to apply security controls to the traffic on the services in groups.

Additional Configuration Options

  • Specify web sites by content category, or specify web applications or categories of web application, without creating content category lists or application lists.

  • Apply an app risk profile to modify the list of destinations the rule targets. An app risk profile defines a list of risk characteristics. When you add an app risk profile to an access rule, the rule takes the characteristics from the profile into account when determining whether to flag an internet application.

    The app risk profile characteristics can include:

    • The label status from the App Discovery Report.

    • The application risk score calculated by Secure Access. For more information see, Procedure or Change App Details.

    • Business risk factors.

    • Various security-related attributes such as security standard compliance, or resistance to various known vulnerabilities. For more information, see Add an App Risk Profile.

Rule Enforcement with Destination Lists and Fully Qualified Domain Names

You can add destination lists that include fully qualified domain names (FQDNs) on internet access rules.

To enforce internet access rules that include destination lists with fully qualified domain names (FQDNs), Secure Access requires that DNS lookups for these FQDNs route through Secure Access. For more information, see Manage End-User Connectivity and Manage DNS Servers.

For information about decryption, see Security Profiles for Internet Access and Manage Traffic Decryption.


Composite Destinations in Internet Access Rules

You can define a destination from multiple network address components. A composite destination accepts IP addresses, CIDR blocks, wildcard masks, ports 80 and 443 for web traffic or all ports on non-web traffic, and the TCP, UDP, and ICMP transport protocols. You can choose ANY to select all available protocols on a destination. For more information, see Add an Internet Access Rule.

This option is useful if you need to quickly address a specific issue that arises, for example to immediately allow access to a necessary destination that is being blocked by another rule, or to immediately block access to a problem destination.

Limitations of Composite Destinations

  • Internet rules with composite destinations only support the Allow and Block actions.

  • Composite destinations do not accept private non-routable IP addresses.

IP Addresses, CIDR Blocks, and Wildcard Masks

  • Destinations accept valid public IP addresses, CIDR blocks, or wildcard masks.

For information about wildcard masks, see Using Wildcard Masks on Access Rules.

Ports

  • Destinations accept ports 80 and 443 only for web traffic and all ports or port ranges for non-web traffic.

Protocols

  • Destinations accept the TCP transport protocol. If you select TCP, the rule applies to web traffic and is protected by the secure web gateway.

  • Destinations accept the UDP or ICMP protocols. If you select UDP or ICMP, the rule applies to non-web traffic and is protected by the IPS.

  • For the protocol on the destination, you can choose ANY. If you select ANY, the rule applies to traffic on the TCP, UDP, and ICMP protocols. The traffic is protected by the secure web gateway.

Combining Composite Destinations on an Internet Access Rule

When you add individual network address components on a destination, Secure Access combines the field values to create a single destination entry. You can add multiple composite destinations on a rule.

  • The ports added to the destination are OR'ed together. The rule applies to traffic on ports 80 or 443.

  • The protocols added to the destination are OR'ed together. The rule applies to traffic on the selected protocols.

  • The individual network component field values that you enter for Ports, Protocols, and IPs, CIDRs, or Wildcard Masks are AND'ed together to create a single destination. The rule applies to the traffic on the composite destination.

Note
You are not required to choose an IP, protocols, or ports to add a composite destination. Instead, you can choose the ANY protocol to define a destination that matches traffic on any IP or CIDR, with any port, on the available destination protocols.

Combining Multiple Destinations in a Rule (Boolean Logic)

If an internet access rule includes multiple destinations, the following boolean logic applies:

  • All types of destinations, and all destinations within a type, are treated as using the boolean OR operator. Traffic to each destination that you specify in a rule matches the rule.

    • For example, if you specify a content category and an application list as destinations in a single rule, traffic to any destination that is a member of either group will match the rule.

  • If you specify ANY for the protocol, then all traffic on the protocols (TCP, UDP, ICMP) supported by internet rules matches the rule, regardless of any other destinations that you specify.

  • If you enter in values of different types (IP address, port, protocol), traffic matches if any of the specified values match the rule.

    • For example, if you specify an IP address and a port, traffic to any IP address on the specified port matches the rule, as does traffic to the specified address on any port.

Combine Internet Destinations with Objects and Groups

You can use the logical AND operator to combine reusable destinations with objects and groups on the internet access rules in the Access policy. Combine the Network Objects or Network Object Groups or Service Objects or Service Object Groups with these destinations.

  • Application lists, internet applications, internet application categories

  • Application protocols

  • Content categories

Network Objects Network Object Groups Service Objects Service Object Groups
Application Lists, Internet Applications Application Categories AND AND AND AND
Application Protocols AND AND AND AND
Content Categories AND AND AND AND
Destination Lists AND AND AND AND

Security Controls


Intrusion Prevention (IPS)

Intrusion Prevention protects your network and assets by inspecting traffic for specified threat characteristics.

You will specify a single intrusion prevention profile in each access rule.

Set Up Certificates for Decrypting Internet Traffic

Internet traffic must be decrypted in order to allow it to be inspected by the intrusion prevention and for web security features, for example those defined in a Security Profile. In order to decrypt this traffic, certificates are required. You may have already set up these certificates to decrypt traffic for web security features.

See Certificates for Internet Decryption.

Configure Intrusion Prevention (IPS) Profiles

Intrusion Prevention (IPS) detects a large number of known threats. Sets of settings are grouped together in profiles, which you can specify in access rules. Secure Access provides several pre-configured profiles that address common needs, such as Balanced Security and Connectivity or Maximum Security. Or you can create a custom profile using Snort signatures. You can also choose to block or just monitor traffic that matches a profile.

You can choose a different IPS profile for each access rule based on the balance of convenience vs. risk appropriate for the particular traffic.

For details, see Manage IPS Profiles.

Configure the Do Not Decrypt List for IPS

Secure Access must decrypt traffic in order to allow the Intrusion Prevention feature to inspect the traffic for threats.

However, decrypting traffic to certain sites, such as health-related or financial sites, may be restricted by privacy laws in some geographic regions.

Use the default Do Not Decrypt List to specify destinations that should not be decrypted by intrusion prevention processes (IPS.)

Web security features, for example those configured in a Security Profile, also require decryption in order to be effective; you can use this list for web security decryption, or you can create and use a different list or lists for web security.

For details, see Important Information About Do Not Decrypt Lists.

Note
IPS in Cisco Secure Access does not support traffic from the Secure Client roaming module.

Security Profile

You can specify a single Security Profile in an internet access rule. Each security profile includes multiple components that you should pre-configure.

Sets of security security settings grouped into profiles control aspects of security for internet traffic.

Enable these options in a security profile and then choose the security profile in an access rule. For more information, see Add a Security Profile for Internet Access.

  • For Decryption (including Do Not Decrypt lists), see Set Up Certificates for Decrypting Internet Traffic and Configure Do Not Decrypt Lists.

  • SSO Authentication. For more information, see Security Profiles for Internet Access.

    SSO authentication is required for some web security features.

  • Threat Categories. For more information, see Threat Categories.

    Choose the types of web-borne threats to block. Blocking some threat categories may affect legitimate traffic.

  • For File inspection, see Manage File Inspection and File Analysis.

    File inspection detects threats using Cisco Advanced Malware Protection and Cisco Secure Malware Analytics.

  • For File type blocking, see Manage File Type Control.

    Block files based on their type. For example, you can prevent users from downloading executable files from the web.

  • For SafeSearch, see SafeSearch.

    SafeSearch filters out offensive, explicit, unsafe, and harmful results from searches in Google, YouTube, Yahoo, and Bing.

  • For AI Supply Chain Blocking, see AI Supply Chain Report.

    AI Supply Chain Blocking controls end user access to files that can pose AI supply chain risk to security and compliance.

  • For End-user notifications, see Manage Notification Pages.

    If you do not want to use the default Secure Access-branded notifications, configure the notifications that are:

    • presented to end users who attempt to access internet destinations that are blocked

    • present when users attempt to access destinations that match a rule configured with the Warn action

    End-user notifications require decryption.

    Web pages shown to users who attempt to access blocked destinations or destinations allowed with a warning.


Set Up Certificates for Decrypting Internet Traffic

If you have already set up certificates for this purpose for the intrusion prevention feature, you may not need to do anything more.

Internet traffic must be decrypted in order to allow it to be inspected by the intrusion prevention and web security features, to apply acceptable use controls, for rules in which the rule action is Isolate or Warn, and to display end-user notifications when destinations are blocked.

In order to decrypt this traffic, certificates are required.

See Certificates for Internet Decryption.


Configure Do Not Decrypt Lists

Secure Access must decrypt internet traffic in order to allow Web Security features to protect your network effectively.

However, decrypting traffic to certain sites, such as health-related or financial sites, may be restricted by confidentiality law in certain geographic regions.

Use a Do Not Decrypt List to specify destinations that should not be decrypted by web security processes. You can create different Do Not Decrypt Lists for different regions or purposes.

You can use the same Do Not Decrypt List that you use for IPS, or create one or more Do Not Decrypt lists to use only for security features included in the security profile.

For details, see Important Information About Do Not Decrypt Lists.


Tenant Controls


Advanced Security Controls

This section includes options to skip enforcement of certain security features, which you may want to do permanently for trusted destinations or temporarily to troubleshoot an issue.

This section includes the ability to access files without decrypting them (sometimes known as "protected file bypass") and the ability to not enforce certain web security features for this rule.

In general, you should allow access to encrypted files only for trusted destinations, because encrypted files cannot be effectively assessed for threats. By default, access to encrypted files is not enabled.

Disable security features only when you have a specific reason to do so.

For more information, see Manage Advanced Security Controls .


Control Egress IP Address for Select SaaS Internet Destinations


Ensure Rule Matching for Encrypted Internet Traffic

In order to ensure that internet rules match encrypted traffic as expected, you must add an extra rule to decrypt the traffic. Essentially, traffic cannot be inspected until after it is decrypted, and cannot match a rule until it can be inspected, and a single rule cannot both decrypt and inspect a transaction.

This situation is best explained using the following example scenario.

Scenario

A Network ("Network1") source makes a web request to URL https://www.mydomain.com/myurl.

Rule does not match the traffic:

Top rule: Source: Any. Destination: https://www.mydomain.com/myurl. Decryption is enabled.

2nd Rule: Source Any. Destination: Any. Decryption is disabled.

Result: The 2nd rule will apply.

Explanation: The top rule specifies a destination that can only be identified if decryption has occurred for the request. However, because the only place decryption is enabled is in that same rule, that rule will never be matched and therefore decryption will not occur.

Rule matches the traffic:

Top rule: Source: Any. Destination: https://www.mydomain.com/myurl. Decryption can be enabled or disabled.

2nd Rule: Source Any. Destination: Any. Decryption is enabled.

Result: The top rule will apply.

Explanation: The 2nd rule triggers decryption, giving Secure Access visibility to the URL being requested, but does not match the rule. The rules are then re-run, top down, with the URL information. This results in matching the top rule.


Block Internet Access to Geographic Locations

To prevent users from accessing web sites hosted in certain countries, you can specify a geolocation destination on an internet access rule. This option is available only when the rule action is Block and the rule includes no destinations other than geolocations. Secure Access logs all traffic that is blocked based on configured geolocation.

The location of a site is determined by its public IP address.

Note
Blocked Internet Access

Traffic to a blocked destination may be allowed if a domain resolves to multiple IP addresses corresponding to different countries.

To block access by site location:

  1. Create an internet access rule.

  2. (Recommended) Position geolocation rules at the top of the rule list and place any exceptions above the general geolocation rules.

  3. Choose Block as the rule action.

  4. Choose Geolocations as the Destination.

  5. Select continents and countries as applicable.

  6. In the security controls section, choose a security profile in which decryption is enabled. You can also specify in this profile a notification page that will be displayed to end users who attempt to access destinations blocked by this rule.