Add a management connection so Mesh Policy Engine can reach third-party enforcers on private networks. Use the connection details to complete setup for policy deployment.
For third-party enforcers with management interfaces that do not have internet-reachable IP addresses, you need to establish a route-based site-to-site VPN connection using a Virtual Tunnel Interface (VTI) from the customer VPN peer to Cisco so that Mesh Policy Engine can access and update policies directly on your enforcers. You will have your own Cisco AWS VPC on a private network to terminate the connection on the Cisco end.
The VPN connection includes an active and a standby tunnel for redundancy; however, only one tunnel can be active. You can configure the other tunnel and manually bring it up in case of failure.
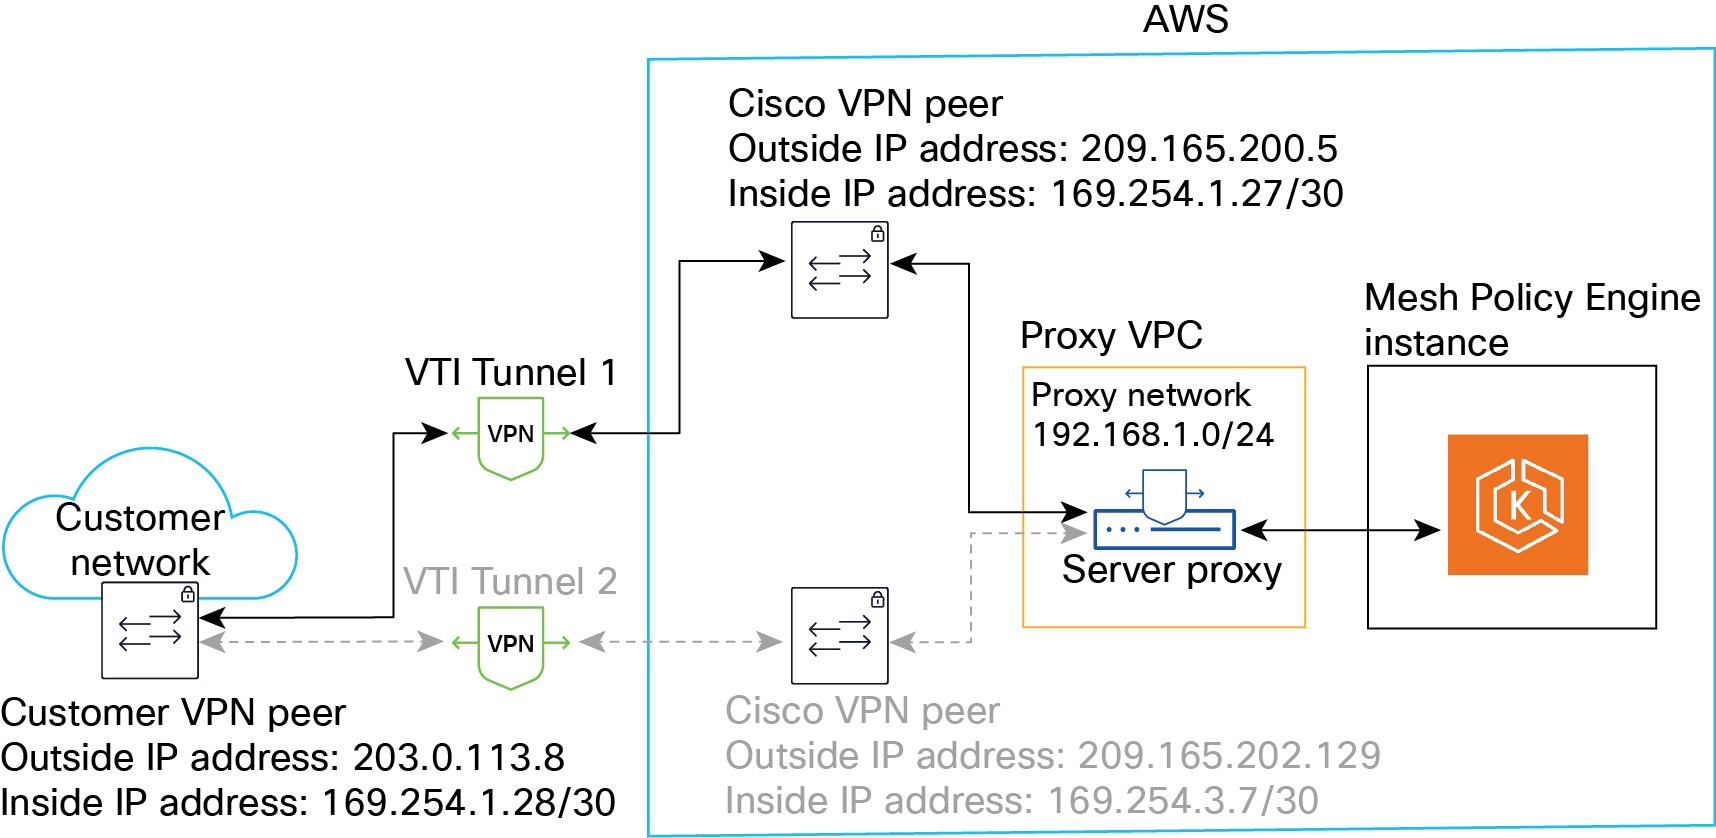
If you use active/standy failover for the customer VPN peers, you can add two VPN connections. Only one tunnel can be active, so be sure to enable only one tunnel for each connection.
For Cisco enforcers, a separate proxy connection is not required. If your third-party enforcer has a management interface with a routable IPv4 address, you don't need a VPN connection; Mesh Policy Engine can access your enforcer directly over the internet using the standard encrypted connection supported by your platform for management.
Procedure
-
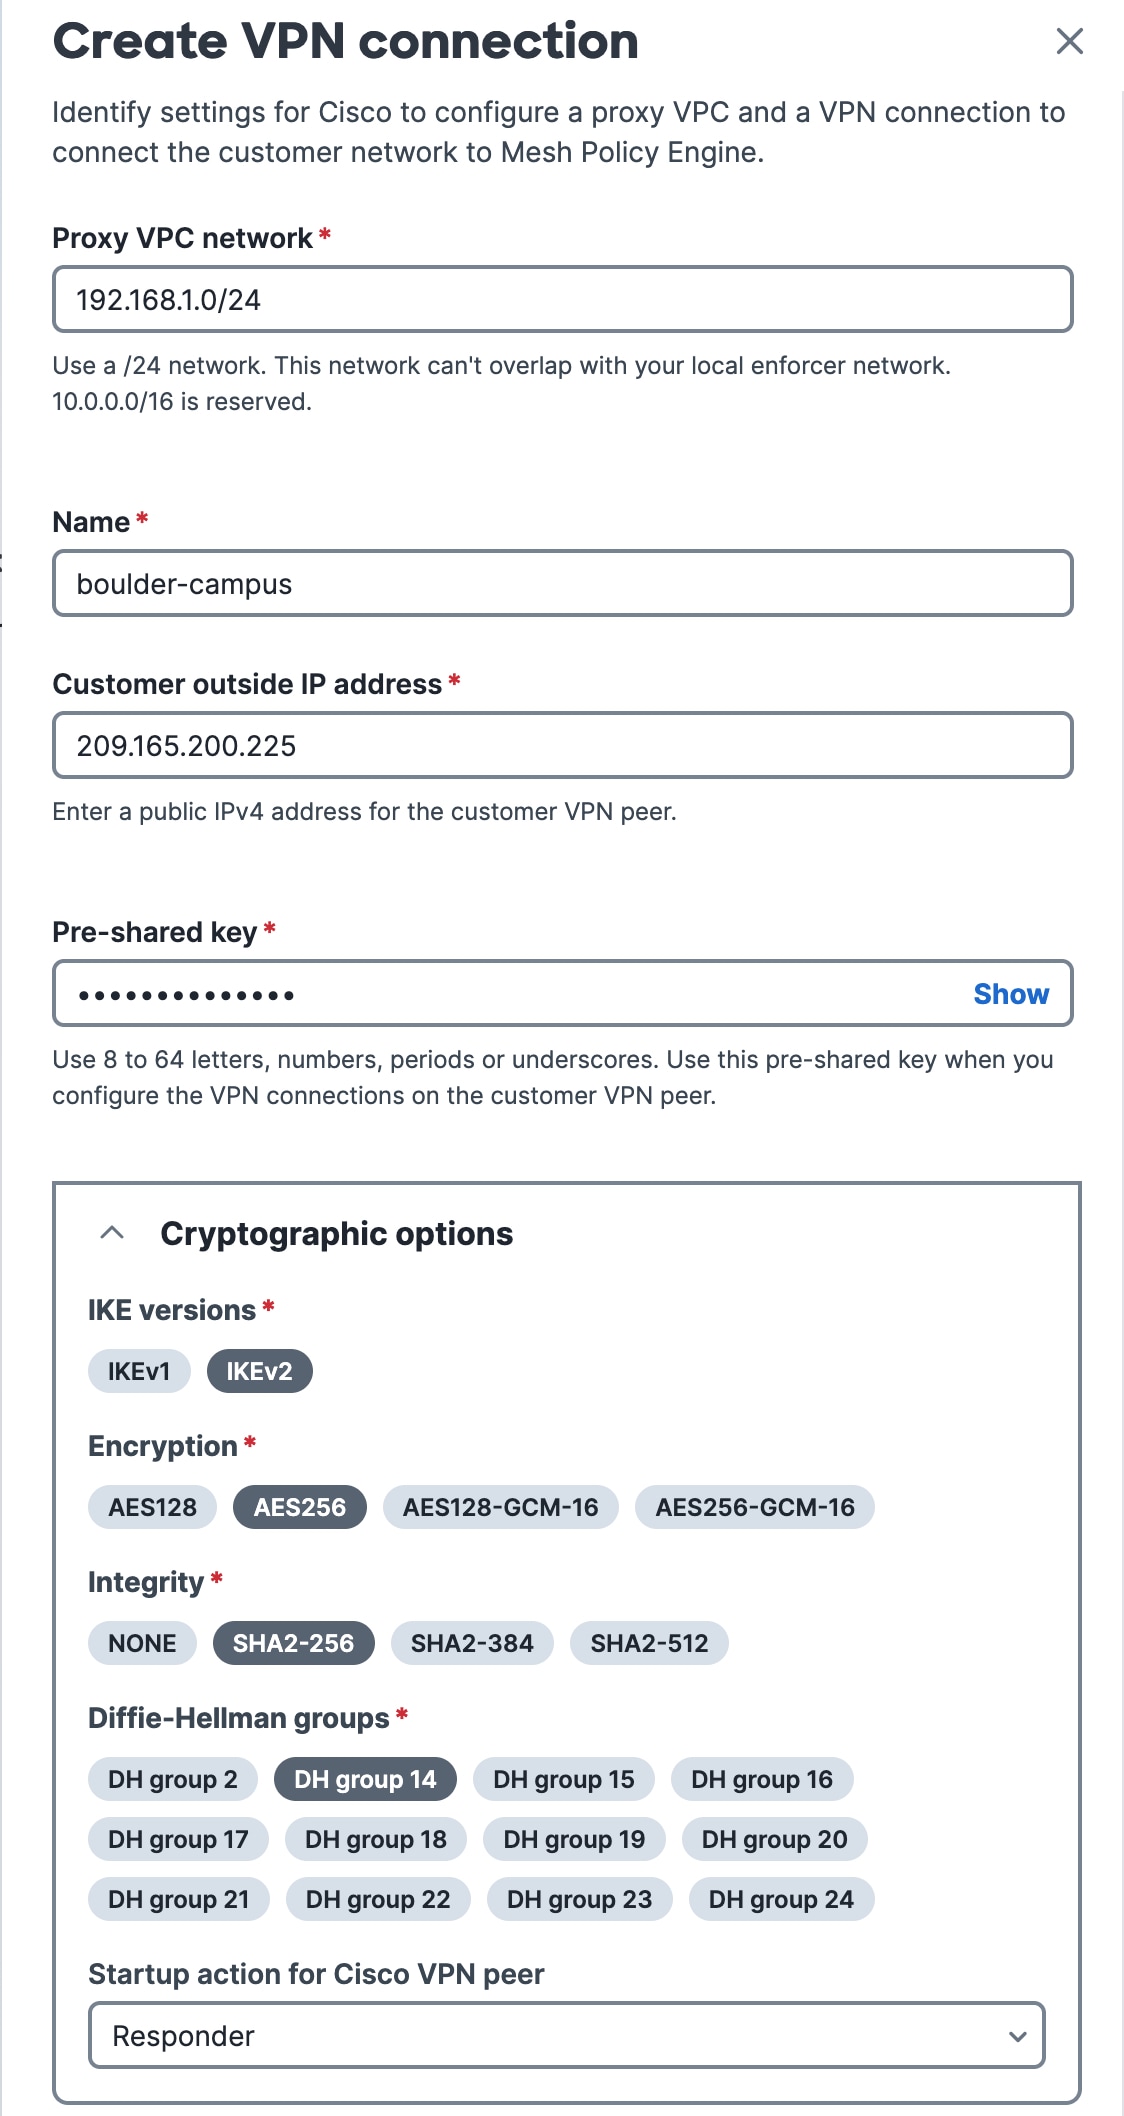
Click Create VPN connection.
Figure 2. Create VPN connection