Export Investigation as a PDF in Splunk Enterprise Security 8.x
Available Languages
Applicability
Splunk Enterprise Security 8.xDescription
In this article it is explained that the evolution of investigation management in Splunk Enterprise Security from version 7.x to 8.x.
In Splunk ES 7.x, investigations were managed using the Investigation Workbench, which supported export functionality in PDF format. These reports included activities, notes, and associated content relevant to specific security issues.
In Splunk ES version 8.x, the Investigation Workbench has been removed and replaced with the Analyst Queue. This interface features an enhanced side panel that provides detailed investigation context and it includes the ability to add text notes, attach files, insert images, include URLs etc.
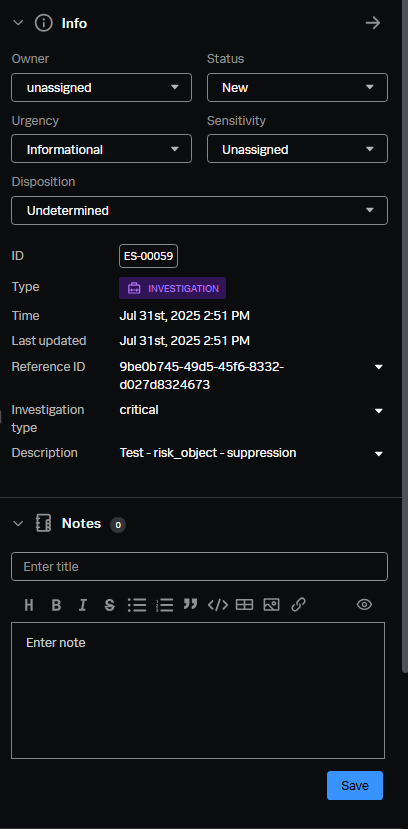
Despite these improvements, direct export of investigation data as a PDF is not in ES 8.x
Resolution
Workaround
By default, Google Chrome includes a Print feature (Ctrl+P or Command+P) that offers PDF export. However, this native print functionality does not reliably capture full investigation content, especially sections with dynamic or expandable elements.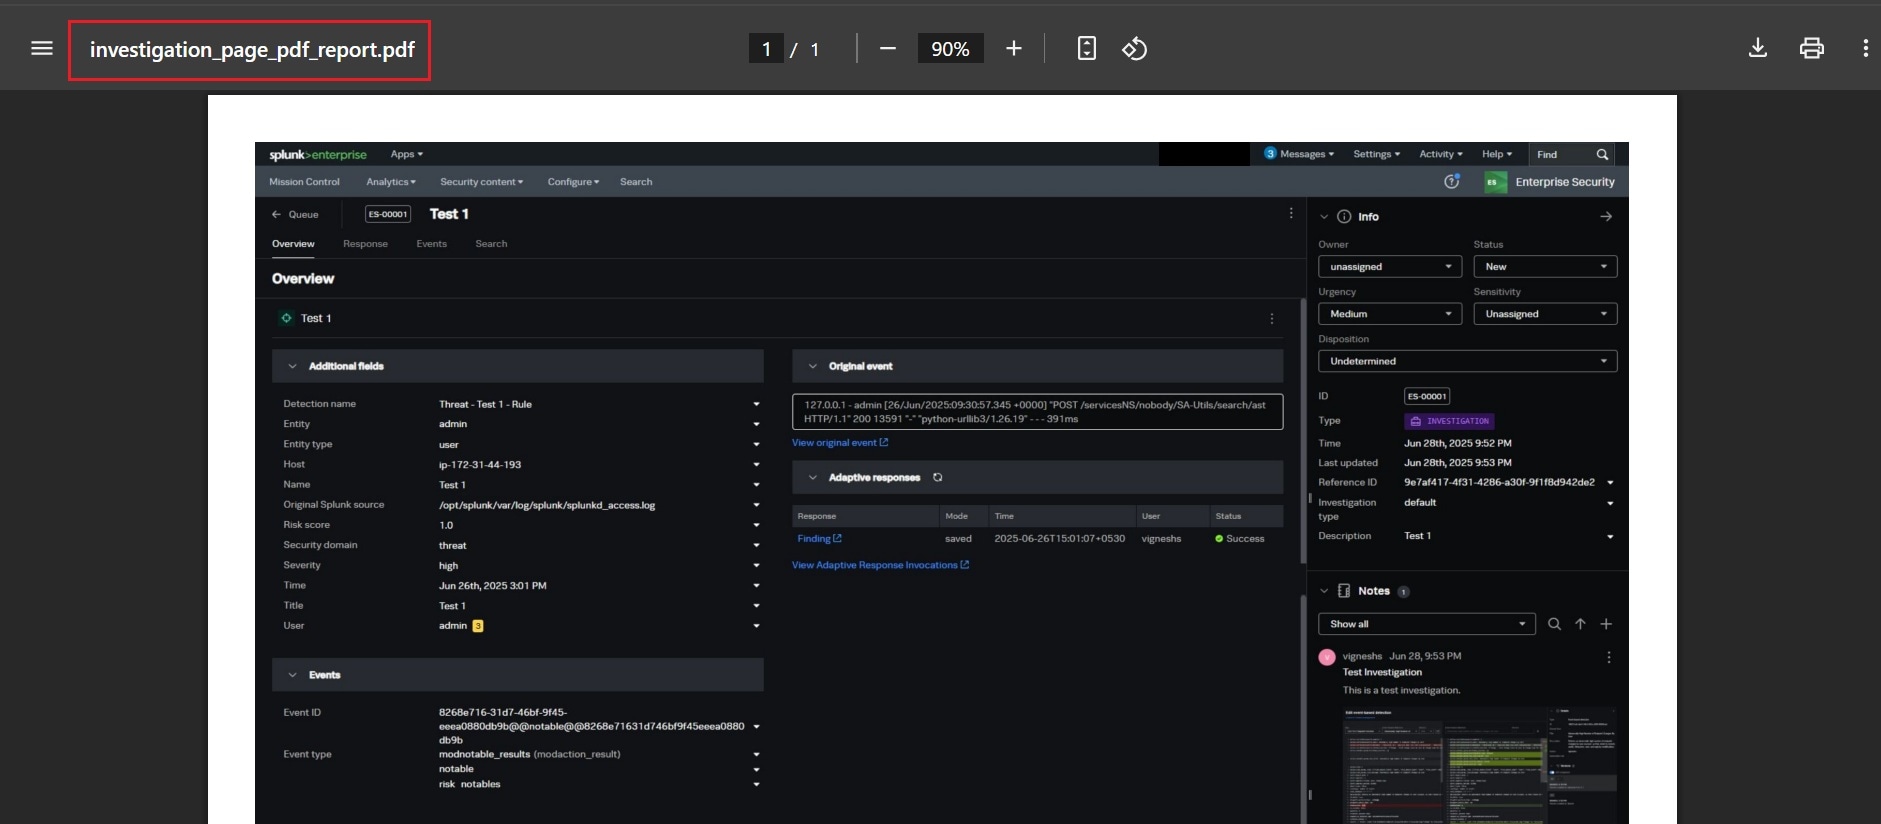
Exporting investigation data as a PDF report feature is not available in Splunk ES 8.x. However, it will be available in the upcoming version of Splunk Enterprise Security.
Related Links
Splunk Enterprise Security 8.x Analyst Queue
Splunk Enterprise Security 7.x Investigation Workbench
Splunk Ideas - ESSID-I-412 (Vote here)
Revision History
| Revision | Publish Date | Comments |
|---|---|---|
1.0 |
01-Oct-2026
|
Initial Release |
 Feedback
Contact Cisco
- Open a Support Case

- (Requires a Cisco Service Contract)
This Document Applies to These Products
Related Articles
- Restoring default navigation after upgrading to Splunk Enterprise Security 8.x
- SOAR execute playbooks for suppressed Findings in Splunk Enterprise Security 8.x
- Investigations are not visible in the Mission Control Panel in Splunk Enterprise Security 8.x
- Missing Notable Events from Incident Review Dashboard in Splunk Enterprise Security