[Splunk Security Essentials] Inaccurate data in the MITRE Attack framework dashboard
Available Languages
Applicability
Splunk Security Essentials Splunk Enterprise Splunk CloudDescription
In Splunk Security Essentials version 3.8.1, the data in the MITRE Attack Framework in the Analytics advisor shows inaccurate data in the dashboard.
As per the default behavior when clicking on the Active, Available, Needs data it should populate the data in the Selected Content dashboard, but it is not populating the exact data in the Selected Content dashboard
Investigation
The content available count is 1451 under the MITRE ATT&CK Framework.
Path: Splunk Manage Apps > Splunk Security Essentials > Analytics Advisor > MITRE ATT&CK Framework
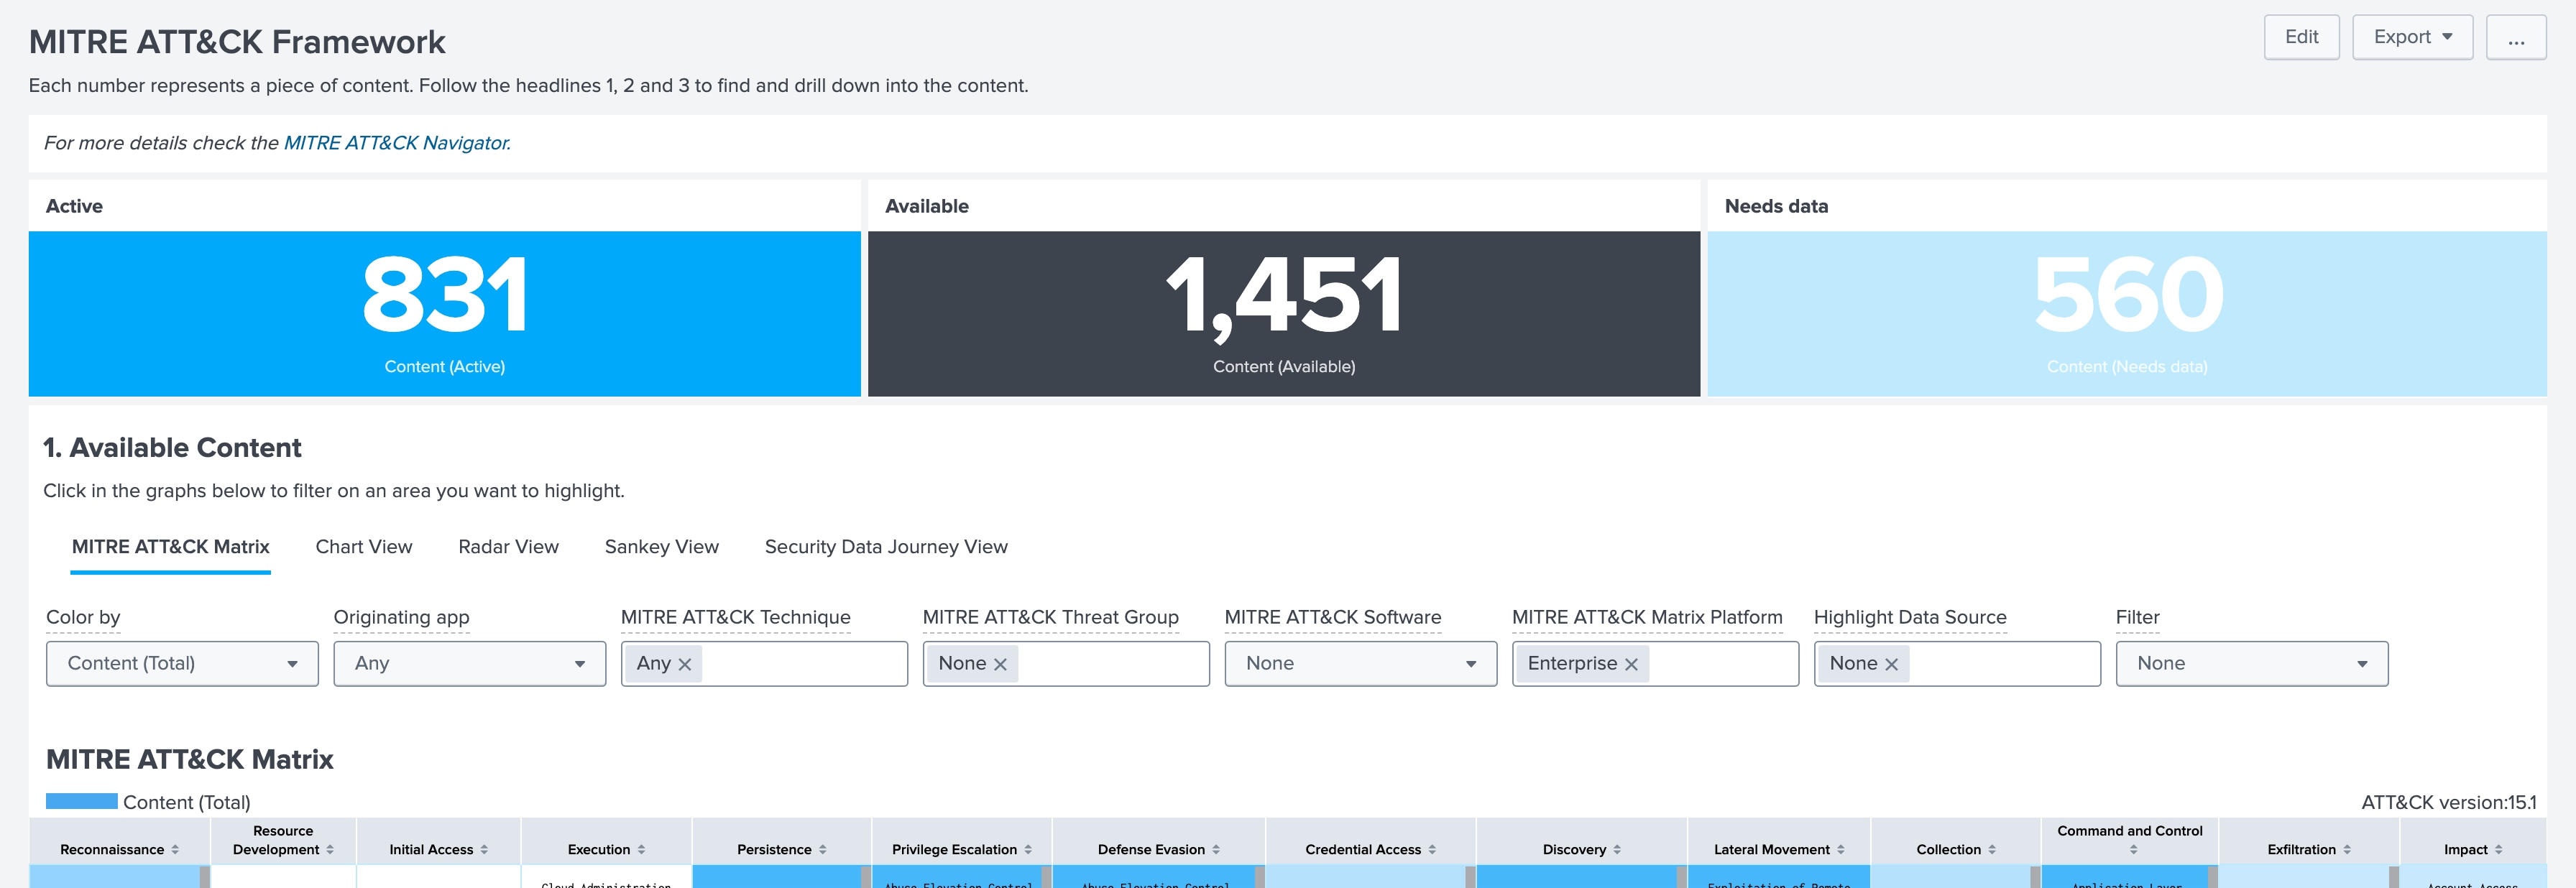
But under the Selected Content the count shows 1217.
Path: Splunk Manage Apps > Splunk Security Essentials > Analytics Advisor > 2. Selected Content
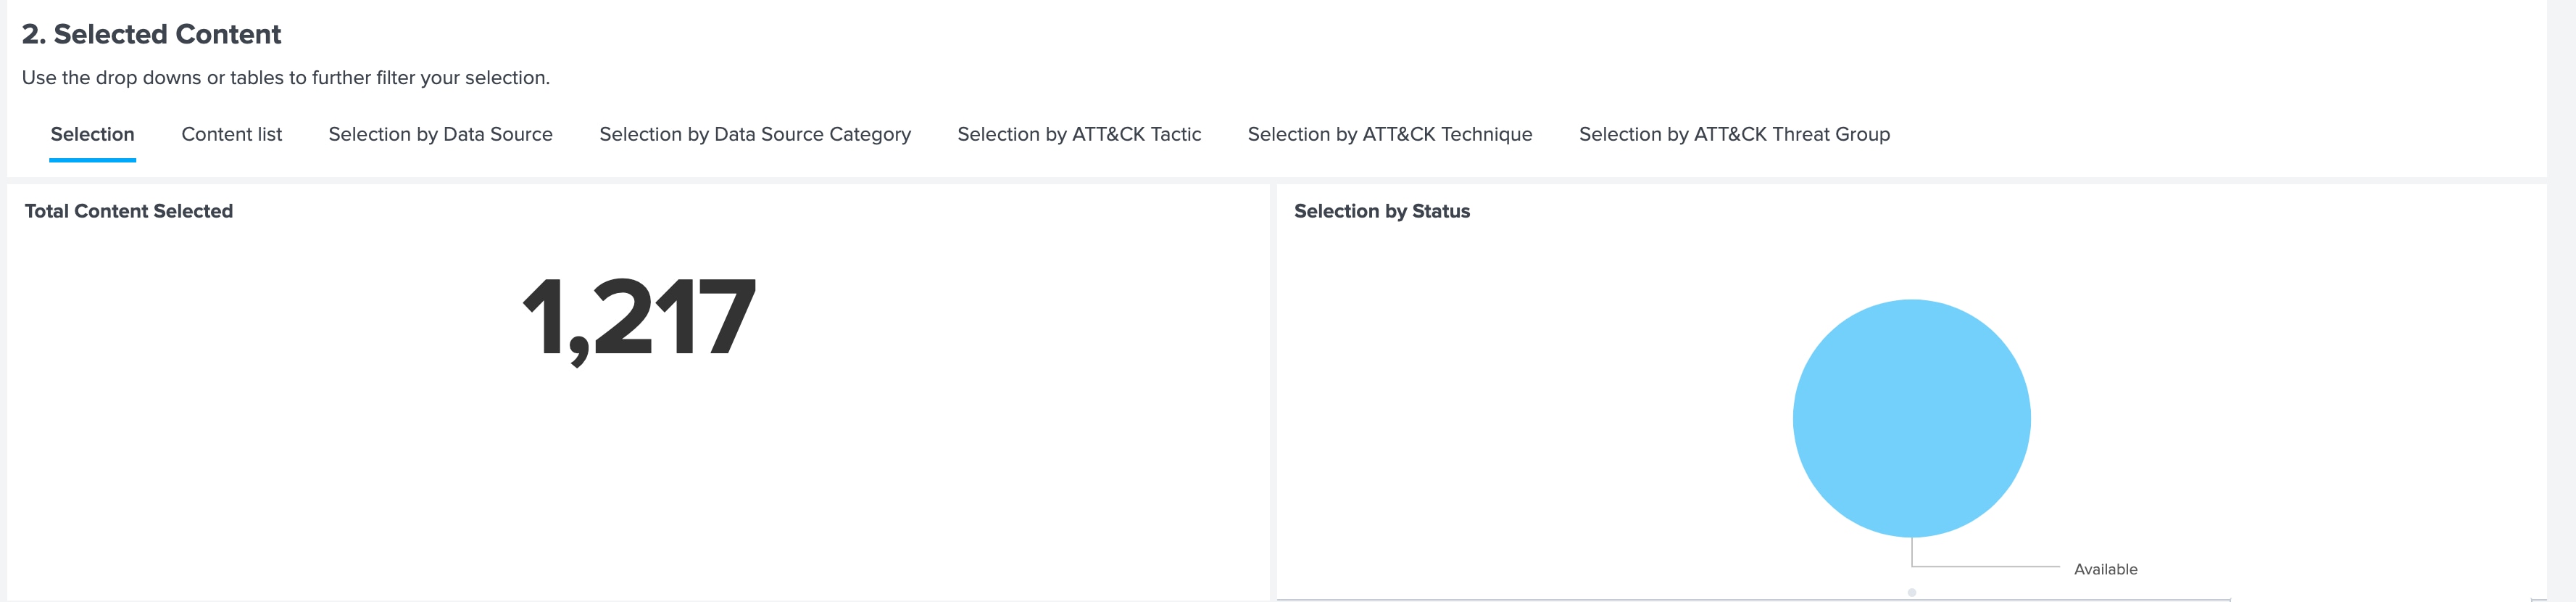
This behavior has also been observed in the local environment.
Resolution
The issue of data inaccuracy in the MITRE ATT&CK dashboard within Splunk Security Essentials is a known issue associated with the update to the ESCU content schema in version 3.8.1. The engineering team has confirmed that this will be resolved in the upcoming release of Splunk Security Essentials.
Revision History
| Revision | Publish Date | Comments |
|---|---|---|
1.0 |
29-Sep-2026
|
Initial Release |
 Feedback
Contact Cisco
- Open a Support Case

- (Requires a Cisco Service Contract)