Stack Automation by Quali Data Sheet
Available Languages
Bias-Free Language
The documentation set for this product strives to use bias-free language. For the purposes of this documentation set, bias-free is defined as language that does not imply discrimination based on age, disability, gender, racial identity, ethnic identity, sexual orientation, socioeconomic status, and intersectionality. Exceptions may be present in the documentation due to language that is hardcoded in the user interfaces of the product software, language used based on RFP documentation, or language that is used by a referenced third-party product. Learn more about how Cisco is using Inclusive Language.
Stack Automation by Quali delivers an end-to-end full-stack solution that ensures best practices and consistency while accelerating time to value from rack to application. It automates complex, multi-vendor deployments across compute, networking, storage, and software layers—transforming manual, slow processes into repeatable, rapid service delivery. This unified automation platform bridges the gap from infrastructure planning through production, enabling seamless orchestration and operational consistency across physical and virtual environments. The result is faster, reliable deployment of full-stack solutions, empowering customers to move swiftly from order to production-ready infrastructure with integrated capabilities such as augmented reality for rack-and-stack guidance and direct integration with Cisco Cloud Control.
Stack Automation by Quali, co-engineered with Cisco, is a SaaS-based deployment automation platform that shifts Cisco® infrastructure and ecosystem software from manual, component-by-component configuration to a fully automated, cloud-like day 0-1 deployment model. Delivered exclusively through Cisco and built on Quali’s Torque automation engine, the platform lets teams launch blueprints, validated by Cisco, from a self-service catalog or compose custom blueprints from existing Terraform, Ansible, and Helm assets—with agentic Copilot assistance to generate, optimize, and self-heal configurations. Stack Automation by Quali is expected to be available in Cisco Cloud Control in November 2026.
Stack Automation reaches on-premises infrastructure through a lightweight management server (virtual or physical) deployed as a virtual appliance, and orchestrates deployments spanning compute, networking, storage, security, observability, and software layers across cloud, on-premises, and hybrid environments.
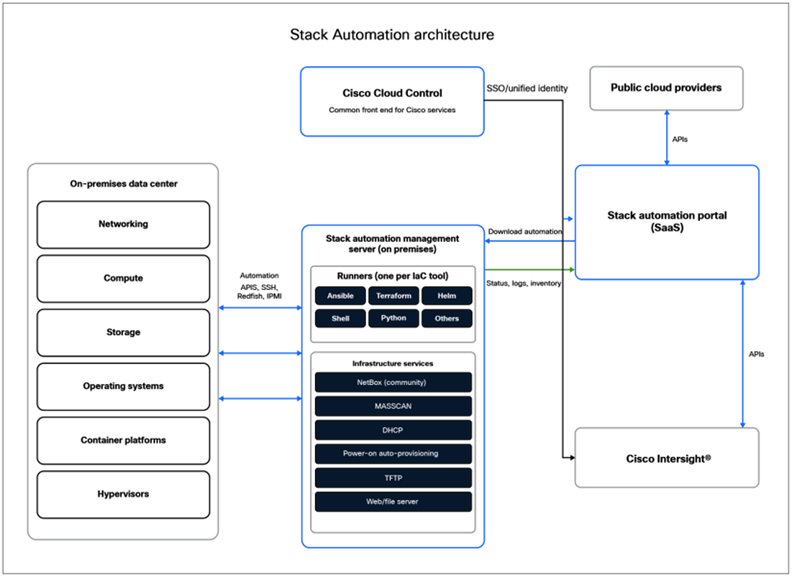
Stack Automation Architecture
Enterprise data center and infrastructure teams use full-stack solutions to deliver new infrastructure faster and with fewer specialists involved. The primary value is predictability: every deployment follows the same validated blueprint, reducing time to production from weeks to days, eliminating configuration drift between sites and freeing teams to focus on the applications the infrastructure supports.
Customization capabilities
Stack Automation by Quali adapts to each customer’s environment instead of imposing a fixed deployment model. Each solution is a blueprint made of modular building blocks: Terraform, Ansible, shell scripts, and nested blueprints. A blueprint can cover anything from a single software application to a complete infrastructure stack. Teams can customize a blueprint in several ways:
● Clone and adapt: clone an existing blueprint and adapt it visually in the Stack Automation Designer Canvas
● Agentic capabilities: use the agentic capabilities to modify blueprints or create new ones from natural-language requirements
● Edit as code: manage blueprints directly as code in Git
Launch forms can be tailored with custom inputs, default values, allowed options, and grouped sections, so operators see only the choices that matter to them. Organizations can also publish their own blueprints to the self-service catalog, apply governance policies for approvals and resource limits, and attach day-2 workflows such as upgrades, scaling, and health checks. Validated designs stay consistent, and each deployment still meets the customer’s operational requirements.
Table 1. Stack Automation by Quali’s general features and benefits
| Feature |
Benefit |
| Software-only blueprints |
A collection of 160+ Cisco® and third-party validated blueprints that can be deployed on existing on-prem and cloud infrastructure through a Stack Automation virtual or physical management server |
| Full-Stack blueprints |
A bundled, outcome-driven solution that includes a Stack Automation physical management cluster for the automation of networking, compute, security, software and observability Leveraging Cisco Validated Designs and available for a select set or Cisco AI POD, FlexPod, and Splunk® Pod offerings |
| Splunk POD Full-Stack blueprint |
Automates deployment of Splunk PODs on Cisco UCS®, simplifying complex manual configurations |
| Cisco AI POD Full-Stack blueprint |
Automates deployment of Cisco AI PODs for AI inferencing use cases, accelerating complex multi-layer configurations |
| FlexPod Full-Stack blueprint |
Automates deployment of converged infrastructure with Red Hat OpenShift on bare metal, reducing manual effort |
| Integrated with Cisco Cloud Control |
Provides a single platform for orchestration managing the entire infrastructure lifecycle from design to production health |
| Integrated with Cisco DevNet |
Allows users to move from Cisco DevNet sandbox exploration to real deployment within a connected experience |
Table 2. Day 0—planning and modeling features
| Feature |
Benefit |
| Day 0—model and prepare your full-stack environment |
Interact with AI Assistant, ask questions and make suggestions for new project ideation, and visualize power and performance estimates |
| Full-Stack Solutions integration to Cisco Commerce |
Create validated full-stack solution BoMs faster and retrieve Stack Automation Full-Stack Purchase Orders (POs) to plan their deployment before gear arrives |
| Full-Stack Purchase Order monitoring |
Learn about the status of your PO (processing, shipped, delivered) and plan ahead of time |
| Full-Stack Solutions Planning |
Once the Full-Stack PO is retrieved, provides management IP address blocks, rack height, preferred username, passwords, settings, and Cisco Intersight/Cisco Nexus® Dashboard preferences so that they can be automatically provisioned once equipment powers on |
| Automated generation of the physical management cluster switch configurations |
Simplify the onboarding process of the management cluster switches, with best practice and consistent configurations |
| Field engineer “full-stack rack and stack package” creation |
This will include the generated management switch configurations, AR assistant application link, CIMC settings, and an API key that the AR Assistant will use to retrieve the available Full-Stack Solution plans |
| Estimated performance and power consumption |
When planning and modeling full-stack solutions, an estimate of performance and power consumption is displayed based on the selected components |
Table 3. Day 1—installation and deployment
| Feature |
Benefit |
| Rack, stack, and cabling assistance for Full-Stack Solutions |
Stack Automation provides an optional Augmented Reality Assistant (powered by DC Smarter) that guides field engineers for correct racking, stacking, and cabling of each component in the solution. Validation is constantly performed at each stage to ensure automation works smoothly |
| Embedded cabling plans and best practices |
Through the Augmented-Reality Assistant (powered by DC Smarter) hardware placement and cabling follows Cisco Validated Designs and third-party best practices. This information is hosted in the embedded NetBox Community component inside the management server, which reduces deployment errors and time |
| Rack and stack validation |
Stack Automation will validate that all components and cables are correctly installed before automation starts |
| Automated IPAM, discovery, and management IP address assignment |
As devices are powered on and discovered, the management server automatically provisions the IP addresses allocated as part of the day-0 plan In addition, software-only solutions also enjoy cloud-style private networks per tenant (VPCs), managed from a single source of truth for consistent automation and self-service |
| Automated Intersight claim of devices |
Each device (with exception of the first management server) is automatically claimed to the Intersight account defined in the plan. In addition, Intersight Virtual Appliance may be locally installed in a physical Stack Automation management server if needed |
| Automated Nexus Dashboard installation or integration |
Each discovered switch is automatically added to Nexus Dashboard with full-stack solutions (with the exception of the management cluster switches). If no Nexus Dashboard exists, Stack Automation may automatically install one. Nexus Dashboard can also be automatically installed on existing infrastructure through software-only solutions |
| Automated compute, network, storage, and software for Full-Stack Solutions |
Based on the selected full-stack blueprint and after rack and stack validation succeeds, the blueprint components are automatically deployed based on the blueprint’s specifications and best practices |
| Automated deployment of Cisco and third-party software |
From OS and platforms to Cisco and third-party applications, Stack Automation deploys validated solutions on top of new full-stack elements or existing ones |
| Cisco AI POD add-on: automated deployment of Cisco Secure AI Factory with NVIDIA |
Once a Cisco AI POD full-stack solution is successfully installed, users may opt to add the Secure AI Factory with Nvidia components, such as Splunk, AI Defense, and Isovalent® Enterprise Platform |
Table 4. Day 2-operations for automated deployments
| Feature |
Benefit |
| Deployment Health Score |
A single score shows the health of every layer of a deployment, so issues are spotted and prioritized before they affect users |
| Drift detection and reconciliation |
Detects changes made outside the automation and restores the approved configuration, keeping environments consistent and compliant |
| Version updates |
Upgrades software, firmware ,and blueprints through independent automation blocks upgrade risk and downtime |
| Cost |
Shows the cost of each environment, team, and project, with automatic shutdown to cut idle spend |
| UI layout customization |
Launches forms and catalogs adapted to each team, so users see only the options they need |
| Credentials and easy access |
Stores credentials centrally and securely, and gives one-click access to deployed resources without sharing passwords |
| Actions and workflows |
Termination, extension, scaling, restarts, and custom day-2 operations, run on demand or on a schedule |
| Approvals and change control |
Built-in approval steps make sure every deployment and change is reviewed, authorized, and auditable |
| Policies |
Guardrails for security, resource limits, durations, and cost, enforced automatically at launch and runtime |
| White labeling |
Customize the portal with your own branding, logo, and colors for a seamless customer or partner experience |
| GitOps integration |
Blueprints and assets stay version-controlled in Git, so changes are reviewed, traceable, and synced automatically |
| Reports |
Usage, cost, compliance, and audit reports with dashboards that show adoption, efficiency, and return on investment |
Table 5. Other features
| Feature |
Benefit |
| Blueprint cloning |
Start from a proven blueprint and adapt it with the AI Assistant, the Designer Canvas, or as code (IaC), turning new environments around in minutes instead of building from scratch |
| AI integrations |
A built-in MCP server lets AI assistants and coding agents (Codex, Claude, GitHub Copilot) browse the catalog, author and validate blueprints, launch environments, and troubleshoot through natural language |
| Multitenancy (spaces) |
Isolated spaces per team, customer, or business unit, each with its own blueprints, users, credentials, policies, and budgets, all run from one platform |
| Notification channels |
Real-time alerts for deployments, failures, approvals and expirations, sent to Webex®, Slack, Microsoft Teams, email, or webhooks so teams can act without watching the portal |
Table 6. Validated and experimental software blueprints
| Category |
Representative solutions |
| Networking and SDN |
Nexus Dashboard, N9300v, Cisco Catalyst® Center (bare-metal and VMs), Catalyst 8000v, Cisco Crosswork Network Controller, Cisco Live Protect |
| Security |
Cisco Secure Firewall Threat Defense (FTDv), Cisco Secure Firewall Management Center (FMCv), Cisco Identity Services Engine, Cisco Cyber Vision, Isovalent Networking for Kubernetes, Isovalent Runtime Security |
| Storage and data protection |
NetApp ONTAP Select, Cohesity Virtual Edition, Veeam Backup and Replication, Qumulo Core NAS, VAST Data, Portworx by Everpure, SAN volume attach |
| Compute provisioning (OS and platform) |
Bare-metal ESXi 7.0/8.0, RHEL, Rocky Linux, Ubuntu LTS, Windows Server, Proxmox VE, VMware vCenter Server Appliance, Red Hat OpenShift on bare metal, Kubernetes, SUSE Rancher/RKE2 |
| Virtual machines as a service |
RHEL, Ubuntu, Windows Server 2025, and openSUSE VMs on VMware vCenter |
| AI, ML, and GPU-as-a-Service |
AI-ready Red Hat OpenShift cluster; NVIDIA GPU, NIM, Network, and NFD operators; NVIDIA Enterprise RAG; LLM model catalog with NVIDIA NIM; and Hugging Face (Llama, Mistral, Gemma, DeepSeek, Nemotron, Qwen, and others), vLLM, JupyterHub, and VS Code developer workspaces |
| Data and AI platforms |
MLflow, KubeRay, Milvus, Weaviate, Langfuse, Apache Airflow, Kafka, Spark, ClickHouse, Elasticsearch, PostgreSQL, Dataiku |
| Kubernetes application environments |
Ephemeral application and developer environments from Helm charts or manifests, plus per-environment data services (PostgreSQL, MySQL, Redis, RabbitMQ, Kafka, S3 object storage) |
| Observability |
Splunk Enterprise, Grafana + Prometheus, ThousandEyes® Enterprise Agent, NetBox Labs, Panduit Collector |
| Management and ecosystem integration |
Cisco Intersight Assist, Cisco Virtual APIC (vAPIC), Cisco Modeling Labs |
| Public cloud (AWS/Microsoft Azure) |
Infrastructure: VPC/VNet, EC2, VM scale sets, EKS/AKS, S3, ECR/ACR, Lambda, App Runner, App Service, RDS, Azure SQL and PostgreSQL, IAM, Secrets Manager, Key Vault Cisco on AWS: vAPIC, Nexus Dashboard, Catalyst 8000v transit VPC AI: bare-metal GPU on AWS and Azure, Amazon SageMaker, Amazon Bedrock and Bedrock Knowledge Base, Azure AI Foundry |
| Full-Stack |
Cisco AI POD (Cisco UCS X-Series), FlexPod (Cisco UCS X-Series), Splunk POD (Small, NVMe) |
Consistent results, faster time to value
Manual solution builds vary from site to site and engineer to engineer, and every variation adds troubleshooting time before the infrastructure can be used. Stack Automation by Quali removes that variability. Every deployment follows the same validated blueprint, with the same configuration standards and the same order of operations, whether it is the first site or the fiftieth.
Because the work that once took separate teams and multiple handoffs runs as one automated process, new infrastructure reaches production sooner and teams spend their time on the applications it supports rather than on building it.
Stack Automation core Benefits:
● Applies the same validated configuration at every site and every deployment
● Removes manual handoffs between network, compute, storage, and platform teams
● Shortens the path from rack installation to production-ready infrastructure
Full-Stack Solution blueprints – Cisco AI POD
Cisco AI PODs can be fully automated using Stack Automation when purchasing a validated bundled solution through Cisco partners. This Full-Stack Solution blueprint is based on the https://www.cisco.com/c/en/us/td/docs/unified_computing/ucs/UCS_CVDs/flexpod-red-hat-openshift-intel-m2-boot-manual-config.html and includes a Stack Automation Management cluster as well as the required licenses to perform and monitor the initial deployment. Any additional software blueprints outside the scope of the Full-Stack Solution blueprint will require their corresponding amount of Concurrent Compute Units (CCUs) available (from either Stack Automation by Quali Essentials or Advantage tiers) in addition to the full-stack solution license cost.
Important note: The required NetApp Storage array is not included as part of the solution bundle available through Cisco and will have to be procured through one of the Cisco and NetApp partners.
Table 7. Cisco AI POD Full-Stack components
| Component |
Detail |
| Compute |
Cisco UCS X210c M8 Compute Nodes with Intel® Xeon® 6 CPUs; CPU and memory per node |
| GPU modules |
2x Cisco UCS X580p PCIe Node, with up to 2 NVIDIA GPUs each (L40S); 2 modules per chassis |
| Storage |
NetApp AFF A50 (or similar) HA pairs running ONTAP 9.19.1 with end-to-end NVMe; drives and shelves per array |
| Fabric |
2 x Cisco UCS 6664 Fabric Interconnects and 4 x N 9332D-GX2B (spine and leaf VXLAN) at 100GbE; one Cisco UCS domain Red Hat OpenShift 4.20 bare metal, M.2 boot, NetApp Trident |
| Management Cluster |
1 to 3 x management servers (Cisco UCS C225 M8 Rack Server) and 2 x Cisco N93108YTC-FX3P |
Table 8. Cisco AI POD automation grains and tasks performed
| # |
Grain |
Kind |
Task |
| 1 |
solution-modeling |
Shell |
Checks the Cisco Commerce Order ID, builds the bill of materials and creates the solution model |
| 2 |
environment-setup |
Shell |
Defines the management IP plan and out-of-band connectivity, sets up DNS/NTP, and checks the connectivity model (management VLAN, data VLAN, uplink speed) |
| 3 |
cabling-validation |
Shell |
Checks the rack layout, runs the AR-assisted cabling guide and checks switch-to-server connections |
| 4 |
ucs-compute |
Ansible |
Provisions the Cisco UCS servers: model, count, CPUs, and memory per server |
| 5 |
redhat-openshift |
Terraform |
Deploys the OpenShift cluster (version, name, worker count). Outputs the API URL and console URL. |
| 6 |
nvidia-gpu-licensing |
Ansible |
Enables and licenses the NVIDIA GPUs by GPU type, GPUs per server, and server count |
| 7 |
nexus-networking |
Terraform |
Configures the management and data VLANs and the uplinks on Nexus. Outputs the fabric ID |
| 8 |
nexus-dashboard |
Terraform |
Connects the fabric and the OpenShift cluster to Nexus Dashboard. Outputs the dashboard URL |
| 9 |
NetApp-storage |
Terraform |
Provisions NetApp storage by type and capacity. Outputs the storage endpoint |
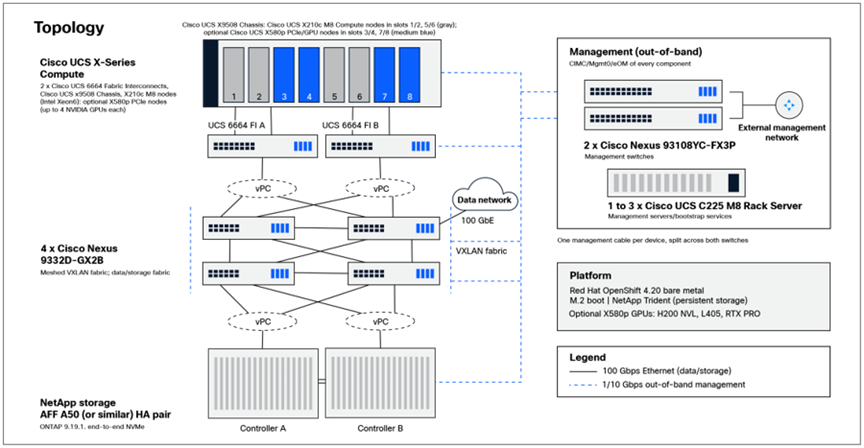
FlexPOD AI POD architecture
Full-Stack Solution blueprints – FlexPod
NetApp FlexPod can be fully automated using Stack Automation when purchasing a validated bundled solution through Cisco partners. This Full-Stack Solution blueprint is based on the FlexPod for Data Center and M2. boot CVD and includes a Stack Automation Management cluster as well as the required licenses to perform and monitor the initial deployment. Any additional software blueprints outside the scope of the Full-Stack Solution blueprint will require their corresponding amount of Concurrent Compute Units (CCUs) available (from either Stack Automation by Quali Essentials or Advantage tiers) in addition to the Full-Stack Solution license cost.
Important: The required NetApp Storage array is not included as part of the solution bundle available through Cisco and will have to be procured through one of the Cisco or NetApp partners.
Table 9. FlexPod Full-Stack components
| Component |
Detail |
| Compute |
Cisco UCS X210c M8 Compute Nodes with Intel Xeon 6 CPUs; CPU and memory per node |
| GPU modules (optional) |
Cisco UCS X580p PCIe Node, up to 4 NVIDIA GPUs each (H200 NVL, L40S, RTX PRO); 2 modules per chassis |
| Storage |
NetApp AFF A50 (or similar) HA pairs running ONTAP 9.19.1 with end-to-end NVMe; drives and shelves per array |
| Fabric |
2 x Cisco UCS 6664 Fabric Interconnects and 2 x Cisco N9332D-GX2B (access with LAN Classic) at 100GbE; one Cisco UCS domain |
| Platform |
Red Hat OpenShift 4.20 bare metal, M.2 boot, NetApp Trident |
| Management cluster |
1 to 3 x management servers (Cisco UCS C225 M8 Rack Server) and 2 x N93108YC-FX3P |
Table 10. FlexPOD automation grains and tasks performed
| # |
Grain |
Kind |
Task |
| 1 |
solution-modeling |
Shell |
Checks the Cisco Commerce order and builds the bill of materials |
| 2 |
environment-setup |
Shell |
Builds the IP plan and checks the prerequisites: AD/DNS/ DHCP servers, OpenShift installer VM, Cisco Intersight Assist, Active IQ Unified Manager, NTP |
| 3 |
cabling-validation |
Shell |
Checks the cabling between the fabric interconnects, the Nexus pair and the NetApp controllers |
| 4 |
nexus-networking |
Terraform |
Uses Nexus Dashboard to create the tenant VRF and the Layer-3 networks (bare-metal management, VM, NFS, iSCSI A/B, NVMe-TCP A/B) with HSRP and DHCP relay, plus the Layer-2 live-migration network. Attaches them to port-channels and deploys |
| 5 |
ontap-network |
Ansible |
Creates the IPspace, broadcast domains (management MTU 1500, storage MTU 9000) and VLAN ports on a0a |
| 6 |
ontap-svm |
Ansible |
Creates the OpenShift storage VM with active/active SAN. Enables NFS, iSCSI and NVMe-TCP. Mirrors the root volume. Sets export policies and auditing. Creates the network interfaces, route, vsadmin user, and DNS. |
| 7 |
ontap-s3 |
Ansible |
Creates the S3 storage VM with TLS, a user and access keys, a group and a bucket |
| 8 |
intersight-domain |
Terraform |
Creates the tenant resource group and organization. Adds the VLANs to the domain profile and deploys it. Creates the IP, MAC, and UUID pools |
| 9 |
intersight-server-policies |
Terraform |
Creates the BIOS, UEFI boot (M.2 first, then virtual media), memory, PCIe GPU, virtual media, in-band IMC and IPMI policies. Defines the vNICs: management with failover, iSCSI A/B with NVMe-TCP, and a bond pair for NFS, live migration, and VMs |
| 10 |
server-profiles |
Terraform |
Creates the server profile template, derives profiles, and assigns and deploys them to the nodes |
| 11 |
openshift-install |
Ansible |
Installs OpenShift 4.20 with the Assisted Installer, using Isovalent Cilium as the network plug-in. Boots the discovery ISO through virtual media and installs to M.2. Outputs the API and console URLs |
| 12 |
trident-storage |
Ansible |
Deploys NetApp Trident with NFS, iSCSI, and NVMe- TCP backends and storage classes. Installs the DataOps Toolkit |
| 13 |
openshift-day1- config |
Ansible |
Adds an admin user, deploys the internal image registry, and schedules etcd backups |
| 14 |
nvidia-gpu-enablement |
Ansible |
Deploys Node Feature Discovery and the NVIDIA GPU Operator on the GPU nodes (optional) |
| 15 |
openshift-virtualization |
Ansible |
Deploys OpenShift Virtualization and protects VMs with Trident Protect (optional) |
| 16 |
validation |
Shell |
Deploys a sample application and checks the cluster operators, storage classes, and node health |
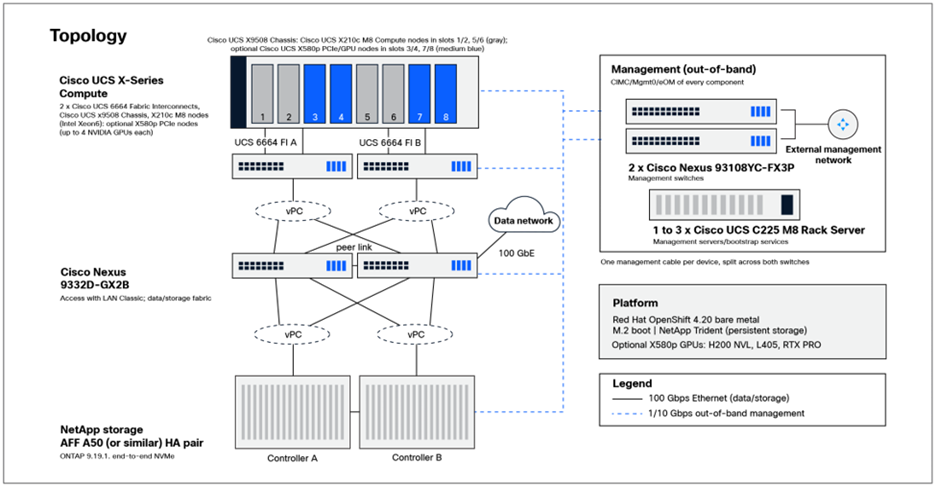
FlexPod architecture
Full-Stack Solution blueprints – Splunk POD
Splunk PODs can be fully automated using Stack Automation when purchasing a validated bundled solution through Cisco partners. This Full-Stack Solution Blueprint is based on the Splunk POD: A Turn-Key Solution for Cisco UCS Infrastructure and Splunk Deployment Guide CVD and includes a Stack Automation Management cluster as well as the required licenses to perform and monitor the initial deployment. Any additional software blueprints outside the scope of the Full-Stack Solution Blueprint will require their corresponding amount of Concurrent Compute Units (CCUs) available (from either Stack Automation by Quali Essentials or Advantage tiers), in addition to the Full-Stack Solution license cost.
Table 11. Splunk POD Full-Stack components
| Component |
Detail |
| Compute |
6 x Cisco UCS C225 M8 Rack Server, 1x AMD EPYC 9455 48 core, VIC 15237 |
| Storage |
32 NVMe drives, 4 per indexer; Ceph SmartStore, 3 replicas |
| Retention |
500 GB/day ingest; 90 days hot, 365 days cold |
| Network |
2 x N9336C-FX2; 100G to every server |
| Platform |
Splunk Enterprise on Kubernetes (Splunk Operator), RHEL 9.6 |
Table 12. Splunk POD automation grains and tasks performed
| # |
Grain |
Kind |
Task |
| 1 |
solution-modeling |
Shell |
Checks the Cisco Commerce order, picks the tier (Small/ Medium/Large/XL, NVMe or HDD) and sets node counts for Cisco UCS C225 M8 and Cisco UCS C240 M8 rack servers |
| 2 |
environment-setup |
Shell |
Builds the IP plan for CIMC and host IPs, DNS, NTP, and the HTTPS repo for the RHEL ISO. Prepares the admin/ Ansible node |
| 3 |
cabling-validation |
Shell |
Checks the 100G host links to the Nexus 9336C-FX2 pair and the 1G CIMC links to the out-of-band switch |
| 4 |
tor-switch-config |
Terraform |
Configures the Nexus pair: VLANs, vPC, LACP port-channels per host, and MTU 9000 |
| 5 |
cimc-initial-config |
Ansible |
Sets dedicated NIC mode, static CIMC IP, DNS, and NTP on each server. Collects the device ID and claim code |
| 6 |
intersight-claim |
Terraform |
Claims the servers as standalone targets. Creates the resource group and organization. Enables tech-support bundle collection |
| 7 |
intersight-policies |
Terraform |
Creates the UUID and MAC pools and the policies: Splunk BIOS tuning, UEFI boot (KVM DVD, then M.2), VIC adapter (FEC cl91), JBOD storage with M.2 RAID1 boot, Ethernet QoS MTU 9000, and LAN connectivity (eno5/eno6) |
| 8 |
server-profiles |
Terraform |
Creates the server template, derives one profile per server, then assigns and deploys them |
| 9 |
os-install |
Terraform |
Installs RHEL 9.6 to M.2 using Cisco Intersight OS install and the Server Configuration Utility, with per-host IP, hostname, and DNS |
| 10 |
os-baseline |
Ansible |
Creates the Splunk service account and SSH key. Registers RHEL and enables the CodeReady Builder repo. Disables firewalls. Upgrades the enic VIC driver. Configures chrony. Disables Transparent Huge Pages |
| 11 |
node-storage-tuning |
Ansible |
Indexers: creates an NVMe RAID5 array, formats it ext4, and mounts it at /mst/splunk. C240 nodes: sets C-state kernel arguments |
| 12 |
bond-network |
Ansible |
Creates bond0 with LACP from eno5 and eno6, static IP, and MTU 9000 |
| 13 |
splunk-pod-installer |
Ansible |
Runs the Splunk POD Kubernetes Installer, which deploys Kubernetes, Rook-Ceph, and the Splunk Operator. Places indexers, search heads, Cluster Manager, and License Manager. Sets cold-storage replication or erasure coding by tier |
| 14 |
splunk-validation |
Shell |
Checks the enic driver, mounts, bond, time sync, Kubernetes, Ceph, and Splunk cluster health. Outputs the Splunk Web URL |
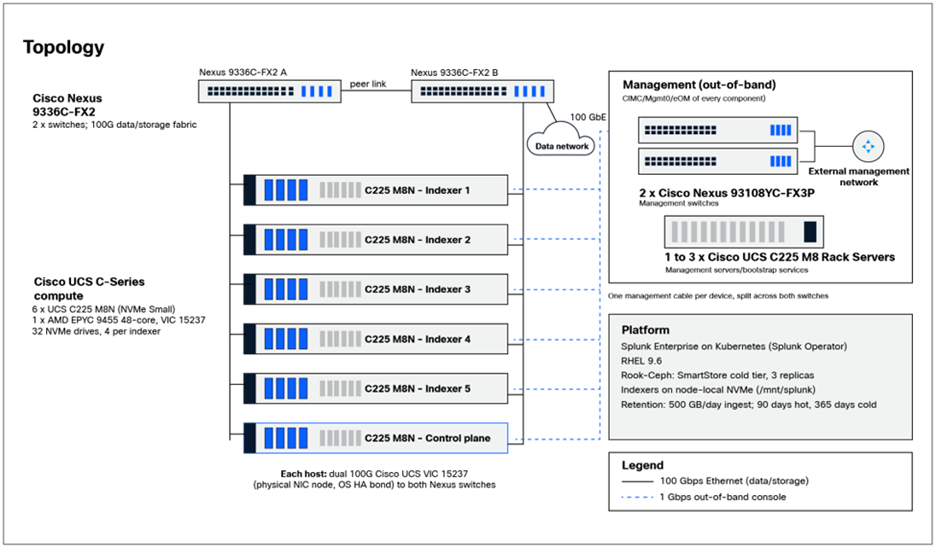
Splunk POD architecture
Table 13. Software solution blueprints per provider/target type
| Target |
Supported versions |
How Stack Automation deploys |
Example solutions |
| VMware vCenter/ vSphere |
vCenter 6.7 and later, validated through 8.0. Some appliances need 7.0 or later (see Notes) |
Terraform, Ansible, and shell, deploying OVA/ ISO images to a vCenter cluster. A preflight check confirms the vCenter version before deployment |
Cisco ISE, Cisco FMCv, Cisco FTDv, Cisco Catalyst 8000v, Cisco Crosswork, Cisco Virtual APIC, Cisco Intersight Assist, Cisco Cyber Vision, Cisco ThousandEyes, Splunk Enterprise, NetApp ONTAP Select, Veeam, Qumulo, Cohesity NetBox, Grafana, VMs (RHEL, Ubuntu, Windows, openSUSE), SUSE Rancher/RKE2 |
| Kubernetes |
Upstream Kubernetes (kubeadm), K3s, SUSE RKE2 (v1.36), Amazon EKS (1.34), and Azure AKS. Kubernetes 1.31– 1.35 for Portworx |
Helm charts, Kubernetes manifests, and shell run inside the cluster through a registered cluster target. |
LLM catalog (NVIDIA NIM, Hugging Face, vLLM), MLflow, KubeRay, Milvus, Weaviate, Langfuse, Airflow, Kafka, Spark, ClickHouse, Elasticsearch, PostgreSQL, JupyterHub, Isovalent Cilium/ Tetragon, Portworx, and application and developer environments |
| Red Hat OpenShift |
OpenShift 4.17–4.21. The NVIDIA GPU stack and bare-metal OpenShift install are validated on 4.20.8. |
Helm and OLM operators run inside the cluster through a registered OpenShift target. Kubernetes blueprints also run on OpenShift, using routes instead of ingress |
NVIDIA GPU, NIM, Network, and NFD operators, NVIDIA AI stack, GPU readiness check, Portworx, and all Kubernetes application blueprints |
| Amazon Web Services |
Any AWS commercial region, chosen at launch. Amazon EKS 1.34 by default |
Terraform, plus CloudFormation for Nexus Dashboard, using a registered AWS account target |
VPC, EC2, EKS, S3, RDS, Lambda, ECR, IAM, AWS Secrets Manager, Cisco vAPIC, Nexus Dashboard, Catalyst 8000v transit VPC, bare-metal GPU, SageMaker, Bedrock |
| Microsoft Azure |
Any Azure region, chosen at launch |
Terraform, using a registered Azure subscription target |
VNet, VM scale sets, AKS, App Service, Azure SQL, PostgreSQL Flexible Server, Key Vault, Storage, Container Registry, bare-metal GPU, Azure AI Foundry |
Stack Automation by Quali is licensed by Concurrent Compute Unit (CCU). There are three tiers: Essentials is free for up to 25 CCUs; Essentials with Support covers up to 40 CCUs; and Advantage is purchased per CCU. Each validated Full-Stack Solution (Cisco AI POD, FlexPod, or Splunk POD) is licensed per physical device through the Full-Stack Deployment License, which includes approximately 4 CCUs per device for the initial provisioning of the whole stack. Customers who do not want to use the regular instance available to all customers can purchase a Dedicated Instance license. Note that the Dedicated Instance license will be used for the future on-premises, air-gapped version.
Table 14. Stack Automation by Quali licensing levels
| License level |
Coverage |
Availability |
| Essentials |
Up to 25 CCUs |
Free |
| Essentials with Support |
Up to 40 CCUs |
Purchased (optional support) |
| Advantage |
Per CCU, for deployments beyond Essentials |
Purchased per CCU, 12- to 60-month term |
| Full-Stack Deployment |
Per physical device in a validated Cisco AI POD, FlexPod, or Splunk POD; includes approximately 4 CCUs per device |
Included in the full-stack MLB |
| Dedicated Instance |
Dedicated Stack Automation instance for customers who do not want the regular instance |
Purchased per year; also used for the future on-premises air-gapped version*** |
Table 15. CCU consumption by provisioned resource
| Provisioned resource |
CCUs consumed |
| OS provisioning on servers |
4 |
| Other device provisioning (for example, switches and storage) |
2 |
| Virtual machines |
1 |
| Containers |
0.025 |
| Lambda functions |
0.0125 |
Information about Cisco’s Environmental, Social and Governance (ESG) initiatives and performance is provided in Cisco’s CSR and sustainability reporting.
Table 16. Cisco environmental sustainability information
| Sustainability Topic |
Reference |
|
|
| General |
Information on product-material-content laws and regulations |
|
|
| Information on electronic waste laws and regulations, including our products, batteries and packaging |
|||
| Information on product takeback and reuse program |
|||
| Sustainability inquiries |
Contact: csr_inquiries@cisco.com |
||
| Material |
Product packaging weight and materials |
Contact: environment@cisco.com |
|
Table 17. Stack Automation by Quali product specifications
| Feature |
Description |
| Validated full-stack solutions |
Automated deployment of Cisco AI POD, FlexPod with Red Hat OpenShift, and Splunk POD, following Cisco Validated Designs |
| End-to-end orchestration |
One workflow from solution modeling through compute, network, storage, platform, and application deployment |
| Solution modeling |
Validates the Cisco Commerce order, builds the bill of materials, and picks the sizing tier (Small, Medium, Large, Extra-Large) |
| Self-service launch form |
Guided input form that captures each deployment's settings: sizing, VLANs, IP plan, and software versions |
| Environment preparation |
Defines the IP plan and checks DNS, NTP, and DHCP before deployment starts |
| Cabling validation |
Checks the physical rack layout and cabling against the solution's low-level design |
| Compute automation |
Claims servers in Cisco Intersight and creates pools, policies, and server profiles. Supports Intersight Managed Mode and Standalone Mode |
| Network automation |
Configures Cisco Nexus switches: VRFs, VLANs, vPCs, and port-channels, directly or through Nexus Dashboard |
| Storage automation |
Configures NetApp ONTAP (storage VMs, NFS, iSCSI, NVMe/TCP, S3) or local NVMe and Ceph storage, depending on the solution |
| Bare-metal OS and platform install |
Installs Red Hat OpenShift or RHEL with Kubernetes on M.2-booted servers through virtual media |
| GPU enablement |
Deploys the NVIDIA GPU Operator and licensing for AI workloads |
| Application deployment |
Installs Splunk Enterprise through the Splunk POD Kubernetes Installer and the Splunk Operator for Kubernetes |
| Post-deployment validation |
Runs health checks across the stack and returns access URLs for the cluster, dashboards, and applications |
| Modular building blocks |
Each stage is a reusable automation block that can run on its own or be shared across solutions |
| Repeatable, consistent deployments |
Every deployment follows the same validated sequence, cutting manual effort and configuration drift |
Table 18. Stack Automation system requirements
| Feature |
Description |
| Stack Automation portal |
The SaaS control plane where users launch and manage deployments from a self-service catalog. Its Solutions Hub provides the full-stack blueprints (Cisco AI POD, FlexPod, and Splunk POD) that run through the on-premises management server |
| Physical management server |
A dedicated Cisco UCS server that runs the Stack Automation Agent and executes blueprints on premises, linking local infrastructure to the Stack Automation portal. It provides bootstrap services (DHCP, local mirror) and can optionally host Nexus Dashboard and Intersight Assist as VMs |
| External connectivity from the management server |
stackautomation.cisco.com:443 jarvis.qtorque.io:443 registry-1.docker.io auth.docker.io production.cloudflare.docker.com:443 github.com:443 http-bulk-listener.logz.io:443 listener.logz.io:8071 repo.almalinux.org mirrors.almalinux.org vault.almalinux.org mirrors.fedoraproject.org dl.fedoraproject.org |
| Open ports (from management server to devices/targets) |
80, 443 and 22 |
Table 19. Management server (VM)
| Requirement |
Specification |
| Hypervisor platform |
VMware vCenter 6.7 or later |
| vCPU |
2 |
| RAM memory |
16GB |
| Disk |
200GB, thick-provisioned (thin provisioning not supported) |
Table 20. Blueprint connectivity
| Requirement |
Specification |
| Solutions Hub Blueprints connectivity requirement from management server |
Per blueprint (TCP 443 unless noted):
● Software repository: qualisystems.hosted-by-files.com, qualisystems.files.com
● Intersight: intersight.com or
● Red Hat/OpenShift: registry.redhat.io, registry.connect. redhat.com, registry.access.redhat.com, quay.io, mirror. openshift.com
● NVIDIA/AI: nvcr.io, api.ngc.nvidia.com, integrate.api.nvidia. com, huggingface.co, tfhub.dev
● OS media: releases.ubuntu.com, cloud-images.ubuntu.com, dl.rockylinux.org, enterprise.proxmox.com
● Packages: archive.ubuntu.com, security.ubuntu.com, pypi. org, files.pythonhosted.org, download.docker.com, pkgs. k8s.io, apt.grafana.com, nvidia.github.io, galaxy.ansible.com, formulae.brew.sh, pkg-containers.githubusercontent.com
● Tools: registry.terraform.io, releases.hashicorp.com, objects. githubusercontent.com, release-assets.githubusercontent. com, raw.githubusercontent.com, dl.k8s.io, get.helm.sh, get. k3s.io, helm.cilium.io, install.portworx.com
● Container registries: docker.io, ghcr.io, registry.k8s.io, cr.weaviate.io, docker.elastic.co
● Vendor downloads: app.thousandeyes.com, download. splunk.com, cdn.downloads.dataiku.com
● Overridable defaults on deployed systems: NTP (UDP 123) pool.ntp.org, time.google.com, time.nist.gov, clock.cisco. com; DNS (UDP/TCP 53) 8.8.8.8, 8.8.4.4, 1.1.1.1
|
Stack Automation by Quali is ordered using the part numbers below. Each validated Full-Stack Solution (Cisco AI POD, FlexPod, or Splunk POD) is ordered as its own Multi-Line Bundle (MLB), which includes all of the required hardware and software, including the Stack Automation licenses. To place an order, visit the Cisco Ordering Home Page. To download software, visit Cisco Software Central.
Table 21. Stack Automation by Quali ordering information
| Part # |
Product Description |
| STKAUTO-SAAS-ESS |
Stack Automation SaaS Essentials Support (optional). Per CCU; 12 to 60 month term |
| STKAUTO-SAAS-AD |
Stack Automation SaaS Subscription Advantage. Per CCU; 12 to 60 month term |
| STKAUTO-SAAS-DD |
Stack Automation SaaS Subscription Dedicated. Per dedicated cloud instance per year; 12 to 60 month term |
| STKAUTO-FULLSTACK |
Stack Automation Full-Stack Deployment License. Per physical device; included in full-stack MLBs; 12 to 60 month term |
| STKAUTO-MGMT-SVR |
Stack Automation Physical Management Server (UCS C225 M8). Per physical server |
| STKAUTO-AIPOD-X |
Full-Stack AI POD (UCS-X) automated by Stack Automation. MLB/solution |
| STKAUTO-FLEXPOD-I |
Full-Stack FlexPod DC solution automated by Stack Automation. MLB/solution |
| STKAUTO-SPLUNKP-SN |
Full-Stack SplunkPod (S-NVME) automated by Stack Automation. MLB/solution |
Services from Cisco and our certified partners can help you accelerate the deployment and adoption of Stack Automation by Quali. Planning and design services align full-stack automation with your business goals. Technical services help your team deploy, operate, and optimize automated infrastructure from rack to production. Optimization services are designed to continuously improve performance. For more information, please visit http://www.cisco.com/go/services.
Flexible payment solutions to help you achieve your objectives
Cisco Capital® makes it easier to get the right technology to achieve your objectives, enable business transformation, and help you stay competitive. We can help you reduce the total cost of ownership, conserve capital, and accelerate growth. In more than 100 countries, our flexible payment solutions can help you acquire hardware, software, services, and complementary third-party equipment in easy, predictable payments. Learn more.
● https://stackautomation.cisco.com/help
● https://www.cisco.com/site/us/en/solutions/data-center/stack-automation-quali/index.html