SOAR - SAML login failed with the error "Signature missing for response".
Available Languages
Applicability
Splunk SOARDescription
When logging into SOAR using SAML, the SOAR page shows the error "Signature missing for response".
Investigation
The error in wsgi.log:
[pid: 28592] [13/Dec/2024 16:13:35]    entity.py:1454 ERROR: Signature Error: Signature missing for response
[pid: 28592] [13/Dec/2024 16:13:35] client_base.py:800  ERROR: XML parse error: Signature missing for response
[pid: 28592] [13/Dec/2024 16:13:35] auth_views.py:681  ERROR: saml2_login_cb failed
Traceback (most recent call last):
  File "www/phantom_ui/ui/auth_views.py/auth_views.py", line 679, in saml2_login_cb
  File "/opt/phantom/usr/python39/lib/python3.9/site-packages/saml2/client_base.py", line 793, in parse_authn_request_response
    resp = self._parse_response(xmlstr, AuthnResponse, "assertion_consumer_service", binding, **kwargs)
  File "/opt/phantom/usr/python39/lib/python3.9/site-packages/saml2/entity.py", line 1451, in _parse_response
    response = response.loads(xmlstr, False, origxml=xmlstr)
  File "/opt/phantom/usr/python39/lib/python3.9/site-packages/saml2/response.py", line 530, in loads
    self._loads(xmldata, decode, origxml)
  File "/opt/phantom/usr/python39/lib/python3.9/site-packages/saml2/response.py", line 360, in _loads
    self.response = self.signature_check(
  File "/opt/phantom/usr/python39/lib/python3.9/site-packages/saml2/sigver.py", line 1669, in correctly_signed_response
    raise SignatureError("Signature missing for response")
saml2.sigver.SignatureError: Signature missing for response
The decoded SAML response includes <SignatureValue> however the <KeyInfo> indicates the issue.
<SignatureValue>
...
</SignatureValue>
<KeyInfo>
  <X509Data>
    <X509Certificate>
     ...
    </X509Certificate>
  </X509Data>
</KeyInfo>
Resolution
The expected is <ds:KeyInfo>. When writing XML code for a digital signature, the <KeyInfo> element should always be prefixed with "ds:" because it belongs to the XML Digital Signature (DS) namespace, meaning the correct syntax is <ds:KeyInfo>. The "ds:" indicates that the element belongs to the "http://www.w3.org/2000/09/xmldsig#" namespace, which is the standard namespace for XML Digital Signatures. Without the "ds:" prefix, the XML parser might not correctly interpret the <KeyInfo> element, potentially causing issues with signature verification.
This is good example of SAML response:
<SignatureValue>
...
</SignatureValue>
<ds:KeyInfo
xmlns:ds="http://www.w3.org/2000/09/xmldsig#">
  <ds:X509Data>
    <ds:X509Certificate>
     ...
    </ds:X509Certificate>
  </ds:X509Data>
</ds:KeyInfo>
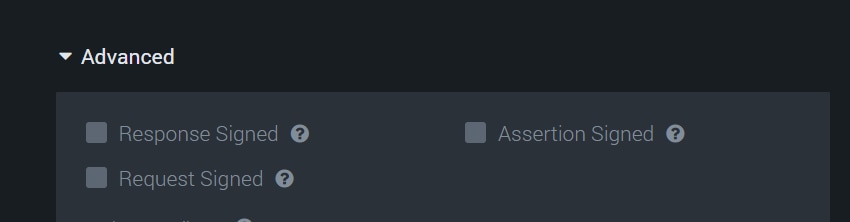
A workaround is to temporarily disable the Signature validation. In SOAR SAML2 configuration under Administration->User Management->Authentication, expand Advanced and unchecked the following fields:
Revision History
| Revision | Publish Date | Comments |
|---|---|---|
1.0 |
29-Sep-2026
|
Initial Release |
 Feedback
