Splunk DB connect app - Connection Error when integrating with SnowFlake DB
Available Languages
Applicability
Splunk Enterprise Splunk CloudDescription
The DB Connect app throws following error when trying to save a connection with Snowflake DB with correct drivers in place: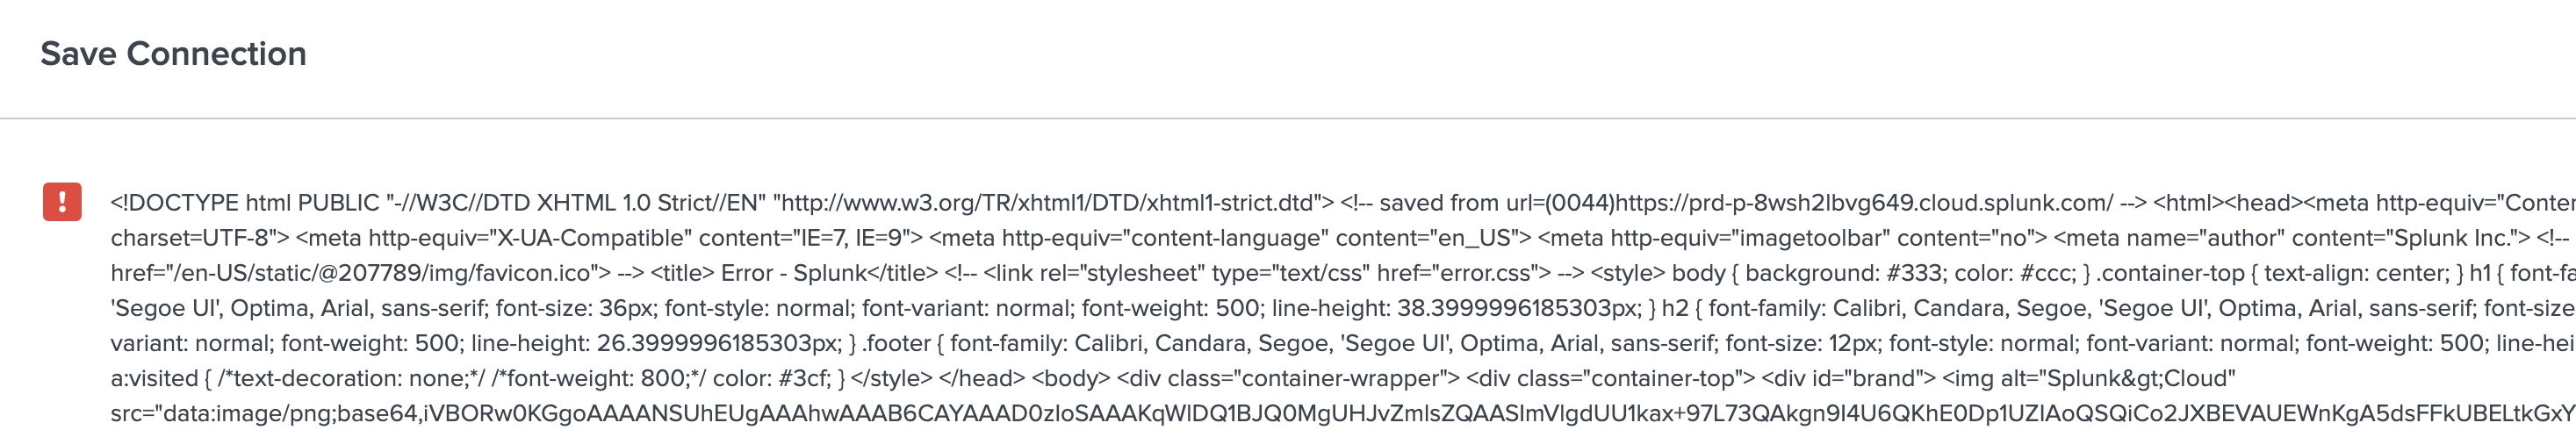
Investigation
Checked the DB Connect error logs with the following SPL:index=_internal sourcetype=*dbx* *<Connection_name>*For instance:
index=_internal sourcetype=*dbx* *CDP_Snowflake_dev*
Following exception are found in the DB Connect app logs:
2023-07-21 18:47:11.601 +0000 Trace-Id=41a8267c-2be0-41be-8cb1-112716aef0a7 [dw-59 - POST /api/connections/status] ERROR net.snowflake.client.core.SFTrustManager - WARNING!!! Using fail-open to connect. Driver is connecting to an HTTPS endpoint without OCSP based Certificate Revocation checking as it could not obtain a valid OCSP Response to use from the CA OCSP responder. Details: {"cacheEnabled":true,"ocspReqBase64":"MEgwRjBEMEIwQDAHBgUrDgMCGgQUi8GehFuYHWHPVGkhGmi44xEzbZAEFL9ft9HO3R+G9FtVrNzXEMIOqYjnAgkApw5KTDSCt38=","ocspMode":"FAIL_OPEN","sfcPeerHost":"czk12250.us-east-1.snowflakecomputing.com","ocspResponderURL":"http:\/\/o.ss2.us\/","cacheHit":false,"eventType":"OCSPValidationError","certId":"MEAwBwYFKw4DAhoEFIvBnoRbmB1hz1RpIRpouOMRM22QBBS\/X7fRzt0fhvRbVazc1xDCDqmI5wIJAKcOSkw0grd\/"}
1
The warning message indicates that the system was unable to obtain a valid Online Certificate Status Protocol (OCSP) Response from the Certificate Authority's OCSP responder. Consequently, it has opted to proceed with the connection without performing OCSP-based Certificate Revocation checking (because of fail-open connection strategy).
Resolution
There are two ways to resolve this. Either user can provide a valid OCSP responder URL or turn off the OCSP verification. Following is how both can be done:- In order to turn off just the OCSP capability, I appended the following parameter in the JDBC string:
&insecureMode=trueThis turns off the OCSP verification altogether and saves the connection successfully.
- In order to keep the OCSP verification enabled and address the invalid response concern, User should obtain the ocsp_responder_url and add the same within the JDBC connection string appending the following parameter:
&ocsp_responder_url= <ocsp_responder_url>
NOTE: Please make sure that the &insecureMode=true parameter is removed and just the above parameters added
User can get the OCSP responder URL with help of Snowflake DB admin team. Basically the OpenSSL command-line tool can be used to view the details of the server certificate and extract the OCSP responder URL from that.
Recommendation: It is highly recommended to resolve this issue promptly. Enabling OCSP-based Certificate Revocation checking helps ensure the security and validity of SSL/TLS certificates during the connection establishment process. Consider reviewing the network configurations, firewall settings, or potential issues with the Certificate Authority's OCSP responder that might be causing the inability to obtain a valid OCSP Response.
Related Links
How to Turn Off the OCSP verification in SnowFlake DBOCSP Guide for SnowFlake DB
Revision History
| Revision | Publish Date | Comments |
|---|---|---|
1.0 |
30-Sep-2026
|
Initial Release |
 Feedback
Contact Cisco
- Open a Support Case

- (Requires a Cisco Service Contract)
This Document Applies to These Products
Related Articles
- Integrating Snowflake Data Warehouse with Splunk DB Connect
- Splunk DB Connect: Unable to Save Snowflake DB Connection When Using RSA Key Pair
- Snowflake database connection with Splunk DB Connect using PAT authentication
- Splunk DB Connect: Snowflake Connection Error - "Unable to Save Due to JWT Token Invalid Issue"