FlexConnect Authentication
A FlexConnect authentication mode is a WLAN operating state that
-
defines how a FlexConnect AP handles client authentication and data switching
-
changes its behavior based on connection status to the controller, and
-
enables resilient client connectivity during both connected and standalone operation.
Connected mode: When a FlexConnect AP can reach the controller, the controller assists in client authentication.
Locally switched: The AP forwards client data directly to the local LAN or VLAN at the site instead of tunneling it through the controller.
Centrally switched: The AP forwards the client’s data traffic to the controller, depending on the WLAN configuration.
FlexConnect is a wireless solution for branch office and remote office deployments. It enables customers to configure and control access points (AP) in a branch or remote office from the corporate office through a wide area network (WAN) link without deploying a controller in each office. The FlexConnect access points can also switch client data traffic locally and perform client authentication locally when their connection to the controller is lost. When they are connected to the controller, they can also send traffic back to the controller. FlexConnect access points support multiple SSIDs. In the connected mode, the FlexConnect access point can also perform local authentication.
An access point does not have to reboot when moving from local mode to FlexConnect mode and vice-versa.
FlexConnect Deployment
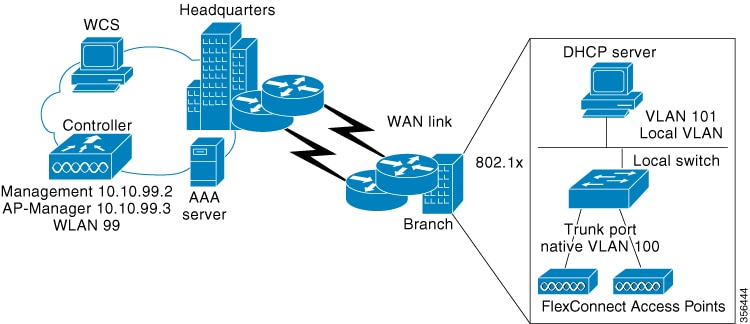
The embedded wireless controller software uses a more robust fault-tolerance methodology with FlexConnect APs. Whenever a FlexConnect AP disassociates from controller, it moves to the standalone mode. Centrally switched clients are disassociated. However, the FlexConnect access point continues to serve locally switched clients. When a FlexConnect AP loses and rejoins its primary or identically configured secondary controller, locally switched client sessions are maintained, providing seamless connectivity.
After the client connection is established, the controller does not restore the original attributes of the client. The client username, current rate and supported rates, and listen interval values are reset to the default or new configured values only after the session timer expires.
The controller can send multicast packets in the form of unicast or multicast packets to an access point. In FlexConnect mode, an access point can receive only multicast packets.
In Cisco Catalyst 9800 Series Wireless Controller, you can define a flex connect site. A FlexConnect site can have a flex connect profile associate with it. You can have a maximum of 100 access points for each flex connect site.
FlexConnect access points support a one-to-one network address translation (NAT) configuration. They also support PAT for all features except true multicast. Multicast is supported across NAT boundaries when configured using the Unicast option. FlexConnect access points also support a many-to-one NAT or PAT boundary, except when you want true multicast to operate for all centrally switched WLANs.
Workgroup Bridge and Universal Workgroup Bridge modes are supported on FlexConnect APs for locally switched clients.
FlexConnect supports IPv6 clients by bridging traffic to the local VLAN, similar to IPv4 operation.
-
An office with intermittent WAN connectivity keeps wireless clients connected using local authentication, with data switched locally until the central controller is available again.
-
A FlexConnect AP at a remote branch uses backup RADIUS for 802.1X authentication during WAN outages.
Analogy: retail chain
Imagine a retail chain with a central headquarters (controller) and a branch store (the FlexConnect AP).
Normal day: Every time a customer wants to make a purchase, the cashier phones headquarters for approval and processing. This is like central authentication and switching.
Local authentication (policy choice): Even on a normal day, the branch can be configured to keep a small credit-card terminal in the store. If management decides to use it, the cashier can approve transactions locally without phoning headquarters. The headquarters link is still up, but the store chooses to handle the verification itself. That terminal is “local authentication".
Stand-alone mode (connectivity condition): One day the phone lines to headquarters go down. The branch is forced to rely on its credit-card terminal, whether it originally planned to or not, if it wants to keep making sales. The store switches on its emergency lights, keeps serving customers, and records the day’s sales to upload later. That forced independence is “standalone mode”.
Key Takeaway
Standalone mode is the situation (phone lines down).
Local authentication is the tool (the in-store terminal) that lets the store keep serving customers—even when the phone lines are fine and especially when they are not.
How FlexConnect authentication works
Summary
FlexConnect authentication enables wireless APs to maintain client connectivity and authentication in various network scenarios, either by connecting to a central controller or operating autonomously. This process is essential for branch offices or remote sites with unreliable WAN links.
The key components involved in the process are:-
FlexConnect AP: Discovers controllers, downloads configuration, and performs client authentication and data switching either locally or through the controller.
-
The controller: Centralizes configuration management and client authentication when available.
-
Client devices: Attempt to authenticate and connect to the network through FlexConnect APs.
-
RADIUS server: Provides authentication services, either centrally through the controller or locally through a backup server in standalone modes.
Workflow
The process involves the following stages:
-
Controller Discovery and Join
- When a FlexConnect AP boots up, it searches for and joins a wireless LAN controller, downloading the latest configuration and software image.
When... Then... And... The controller is reachable, the AP enters connected mode.
The controller performs central authentication.
Based on WLAN configuration - client data is switched either through the controller (central switching), or
- locally at the AP (local switching).
The controller is not reachable, the AP enters standalone mode.
The AP performs local authentication using stored configuration and, if needed, a backup RADIUS server.
- Client data is switched locally.
- Special states (such as “authentication down, local switching”) manage client behavior when authentication cannot occur.
-
Failover and Recovery
- If controller connectivity is lost, the AP attempts to reach the gateway via ARP and retries controller discovery.
- If discovery fails, it attempts DHCP renewal and, if still unsuccessful after multiple attempts, falls back to static IP and reboots to recover.
- Return to Connected Mode Upon reconnecting to the controller, the AP disassociates clients, applies new configuration, and resumes normal connectivity, with central authentication and state management.
Result
FlexConnect authentication ensures clients can maintain connectivity and authentication even during network disruptions, supports flexible deployment models, and reduces branch office WAN dependency.
Controller discovery methods
When a FlexConnect AP boots up, it searches for a controller. If it finds one, it joins the controller, downloads the latest software and configuration, and initializes the radio. The configuration is saved in nonvolatile memory to support standalone mode if the controller becomes unreachable.
A FlexConnect AP can discover the controller’s IP address through multiple methods:
-
DHCP-based discovery: If the access point gets its IP from a DHCP server, it uses CAPWAP or LWAPP discovery. OTAP is not supported.
-
Static IP discovery: If configured with a static IP, the access point can use all discovery methods except DHCP option 43. DNS resolution is recommended if Layer 3 broadcast fails. With DNS, any AP with a static IP address that knows of a DNS server can find at least one controller.
-
Priming: For remote networks without CAPWAP or LWAPP, priming allows manual configuration through the CLI to specify the controller.
FlexConnect authentication and switching modes
 Note |
The LEDs on the AP change as the device enters different FlexConnect modes. See the hardware installation guide for your AP for information on LED patterns. |
When a client associates with a FlexConnect AP, the AP sends all authentication messages to the controller and, based on the WLAN configuration, either switches the client’s data packets locally (locally switched) or sends them to the controller (centrally switched).
For client authentication (open, shared, EAP, web authentication, and NAC) and data packets, the WLAN operates in one of the following states, determined by its configuration and the controller connectivity status:
-
Central authentication, central switching: The controller handles both client authentication and data switching. All client data is tunneled to the controller. This state is valid only in the connected mode.
-
Central authentication, local switching—In this state, the controller handles client authentication, and the FlexConnect AP switches data packets locally. After the client authenticates successfully, the controller sends a configuration command with a new payload to instruct the FlexConnect AP to start switching data packets locally. This message is sent per client. This state is applicable only in connected mode.
-
Local authentication, local switching: The AP both authenticates clients and switches data locally. This state works in both connected and standalone mode.
-
Authentication down, switch down: The WLAN disassociates clients and stops sending beacons and probes. Valid for both connected and standalone modes.
-
Authentication down, local switching: New client authentication is rejected, but existing client sessions are kept alive. Valid in standalone mode.
In the connected mode, the controller receives only minimal information about locally authenticated clients. Some information not available to the controller are:
-
Policy type
-
Access VLAN
-
VLAN name
-
Supported rates
-
Encryption cipher
When a FlexConnect AP is unable to reach the controller, WLANs configured with open, shared, WPA-PSK, or WPA2-PSK authentication continue to authenticate clients locally if an external RADIUS server is available. If the controller becomes reachable again, all clients are disassociated and a new configuration is applied before connectivity resumes.
In web-authentication mode, client DNS replies must pass through the controller during authentication. After successful web authentication, all traffic switches locally.
Standalone Mode
When a FlexConnect AP cannot reach the controller, it automatically enters standalone mode and begins authenticating clients on its own
Behavior in standalone mode
-
WLANs configured for open, shared, WPA-PSK, or WPA2-PSK authentication enter the local authentication, local switching state and continue new client authentications.
-
WLANs configured for 802.1X, WPA-802.1X, WPA2-802.1X, or Cisco Centralized Key Management require an external or local RADIUS server to remain operational.
-
WLANs configured for central switching move to authentication down, switching down; WLANs configured for local switching move to authentication down, local switching
-
The AP forwards data frames locally while it authenticates clients.
When a FlexConnect AP enters a standalone mode, the AP checks whether it is able to reach the default gateway through ARP. If so, it will continue to try and reach the controller .
If the AP fails to establish the ARP:
-
The AP attempts to discover for five times and if it still cannot find the controller , it tries to renew the DHCP on the ethernet interface to get a new DHCP IP.
-
The AP will retry for five times, and if that fails, the AP will renew the IP address of the interface again, this will happen for three attempts.
-
If the three attempts fail, the AP will fall back to the static IP and will reboot (only if the AP is configured with a static IP).
-
Reboot is done to remove the possibility of any unknown error the AP configuration.
Local authentication in a FlexConnect AP
Local authentication in a FlexConnect AP is an authentication method in which
-
the FlexConnect AP independently authenticates clients without forwarding authentication requests to a central controller
-
client data packets are switched locally by the AP, reducing round-trip latency and dependence on WAN bandwidth
-
authentication capabilities are built into the AP for handling protocols like 802.1X, WPA-PSK, WPA2-PSK, and others reduces the latency requirements of the branch office, and
-
is useful where you cannot maintain a remote office setup of a minimum bandwidth of 128 kbps with the round-trip latency no greater than 100 ms and the maximum transmission unit (MTU) no smaller than 576 bytes.
Additional information
-
Do not enable guest authentication on WLANs with FlexConnect local authentication; guest authentication is unsupported in this configuration.
-
Do not use local RADIUS authentication on the controller for FlexConnect local authentication-enabled WLANs; it is not supported.
-
Once the client has been authenticated, roaming is only supported after the controller and the other FlexConnect access points in the group are updated with the client information.
Local and backup RADIUS server configuration
-
You can also configure a local RADIUS server on a FlexConnect AP to support 802.1X in a standalone mode or with local authentication.
-
When connected to a central controller, FlexConnect APs use the controller’s primary RADIUS servers in the specified order unless overridden for a particular WLAN. The order is specified on the RADIUS Authentication Servers window or using the the config radius auth add command
-
In standalone mode, each FlexConnect AP must have its own backup RADIUS server to perform 802.1X EAP authentication for clients. The controller itself does not use a backup RADIUS server in this mode.
-
You can configure a backup RADIUS server for individual FlexConnect APs in standalone mode by using the controller CLI or for groups of FlexConnect APs in standalone mode by using either the GUI or CLI. An AP-specific backup RADIUS configuration overrides any group configuration.
Note |
A controller does not use a backup RADIUS server. The controller uses the backup RADIUS server in local authentication mode. |
WLAN authentication and switching states
When a primary RADIUS server becomes unavailable, WLANs will enter either:
-
Authentication down, switching down
state if the WLAN was configured for central switching -
Authentication down, local switching state if the WLAN was configured for local switching
Web authentication and DNS handling
When web-authentication is used on FlexConnect APs at a remote site, the clients get the IP address from the remote local subnet.
To resolve the initial URL request, the DNS is accessible through the subnet's default gateway. In order for the controller to intercept and redirect the DNS query return packets, these packets must reach the controller at the data center through a CAPWAP connection. During the web-authentication process, the FlexConnect APs allows only DNS and DHCP messages; the APs forward the DNS reply messages to the controller before web-authentication for the client is complete. After web-authentication for the client is complete, all the traffic is switched locally.
Restrictions
-
OTAP is not supported.
-
After the AP reboots with the new controller software, convert it to FlexConnect mode.
-
802.1X authentication on the AUX port is unsupported for Cisco Aironet 2700 series FlexConnect APs.
-
FlexConnect passive client mode disables IP Learn timeout by default in local switching, central authentication deployments.
-
When a FlexConnect AP enters standalone mode, only WLANs configured for open, shared, WPA-PSK, or WPA2-PSK authentication support local authentication for new clients; 802.1X types require an external or local RADIUS server.
-
When FlexConnect APs are connected to the controller (rather than in standalone mode), the controller uses its primary RADIUS servers and accesses them in the order specified on the RADIUS Authentication Servers page or in the config radius auth add CLI command (unless the server order is overridden for a particular WLAN). However, to support 802.1X EAP authentication, FlexConnect APs in standalone mode need to have their own backup RADIUS server to authenticate clients.
Note
A controller does not use a backup RADIUS server. The controller uses the backup RADIUS server in local authentication mode.
When the FlexConnect AP cannot reach its default gateway through ARP and cannot discover the controller, it attempts multiple DHCP renewals and reboots if configured with a static IP to recover connectivity; controller discovery failures trigger fallback behavior.
If the AP fails to establish the ARP, this happens:-
The AP attempts to discover for five times and if it still cannot find the controller, it tries to renew the DHCP on the ethernet interface to get a new DHCP IP.
-
The AP will retry for five times, and if that fails, the AP will renew the IP address of the interface again, this will happen for three attempts.
-
If the three attempts fail, the AP will fall back to the static IP and will reboot (only if the AP is configured with a static IP).
-
The AP reboots to eliminate potential configuration errors.
Guidelines and restrictions for FlexConnect
Configuration Changes
-
When you apply a configuration change to a locally switched WLAN, the access point resets the radio, causing associated client devices to disassociate, including those not associated with the modified WLAN. Modify the configuration only during a maintenance window. This is applicable when a centrally switched WLAN is changed to a locally switched WLAN.
-
This guideline is specific to Wave 1 APs, and not for Wave 2 APs or 11AX APs.
VLAN and Switched WLANs
-
FlexConnect mode can support only 16 VLANs per AP.
-
NAC out-of-band integration is supported only on WLANs configured for FlexConnect central switching, not for local switching.
-
FlexConnect access points with locally switched WLANs cannot perform IP source guard and prevent ARP spoofing.
Network and Client Requirements
-
You can deploy a FlexConnect access point with either a static IP address or a DHCP address. Ensure a DHCP server is available locally and able to provide the IP address for the access point at bootup.
-
FlexConnect supports up to 4 fragmented packets or a 576-byte MTU WAN link.
-
Round-trip latency must not exceed 300 milliseconds (ms) between the access point and the controller, and CAPWAP control packets must be prioritized over all other traffic.
Roaming and Associations
When a client roams from one AP to another and the roaming is successful, this happens:
-
The client does not send any traffic to the new AP.
-
The client’s state is IP LEARN pending.
-
The client is deauthenticated after 180 seconds, if there is no traffic for the entire duration. In case the DHCP Required flag is set, the deauthentication occurs after 60 seconds.
Authentication and Support
-
FlexConnect APs do not forward the DHCP packets after Change of Authorization (CoA) and change of VLANs using 802.1X encryption. You must disconnect the client from the WLAN and reconnect the client to enable the client to get an IP address in the second VLAN.
-
The configuration on the controller must be the same between the time the access point went into standalone mode and the time the access point came back to connected mode.
-
Local authentication fallback is not supported when a user is not available in the external RADIUS server.
Configuration Practices
-
In the FlexConnect mode, use a named site tag instead of default-site-tag. If you use default-site-tag, the client Pairwise Master Key (PMK) is not sent to APs. This results in client roam and reassociation issues.
Rate limiting per SSID is not supported in FlexConnect local switching mode
-
Rate limiting per SSID is not supported in FlexConnect local switching mode.
-
Rate limiting is enforced per flow (5-tuple) and not per SSID or per client.
-
For rate limiting to work as expected, FlexConnect central switching mode should be used.
-
In FlexConnect local switching mode, QoS policies are applied at the AP level.
Configure a site tag (CLI)
Configure a site tag using CLI to centrally manage configurations for APs within a network. By completing this task, you streamline the management of configuration profiles and associated devices on the network.
Use these steps to configure a site tag using CLI:
Procedure
|
Step 1 |
Enter global configuration mode. Example: |
||
|
Step 2 |
Configure site tag and enter site tag configuration mode. Example: |
||
|
Step 3 |
Move the AP to FlexConnect mode. Example:
|
||
|
Step 4 |
Map a flex profile to a site tag. Example: |
||
|
Step 5 |
Assign an AP profile to the wireless site. Example: |
||
|
Step 6 |
Add a description for the site tag. Example: |
||
|
Step 7 |
Save the configuration, exit the configuration mode, and return to privileged EXEC mode. Example: |
||
|
Step 8 |
Display the summary of site tags. Example: |
You configured the new site tag for the network. Now visible in the system, the site tag allows you to efficiently manage AP profiles and flex profiles associated with specific network sites.
Configure a policy tag (CLI)
Create and apply a policy tag to group wireless local area network (WLAN) and policy profiles for your network configuration.
Use this task when you need to define or update policy tags for your wireless network devices using the CLI.
Before you begin
-
Prepare unique names for policy tags using ASCII characters (32 to 126, no leading or trailing spaces).
-
Identify the WLAN and policy profiles you plan to map.
Procedure
|
Step 1 |
Enter global configuration mode. Example: |
||
|
Step 2 |
Configure policy tag and enter policy tag configuration mode. Example:
|
||
|
Step 3 |
Add a description to a policy tag. Example: |
||
|
Step 4 |
Map a remote-LAN profile to a policy profile. Example: |
||
|
Step 5 |
Map a policy profile to a WLAN profile. Example: |
||
|
Step 6 |
Exit policy tag configuration mode, and return to privileged EXEC mode. Example: |
||
|
Step 7 |
(Optional) Display the configured policy tags. Example:
|
Your device has the new policy tag applied. The mapped WLAN and policy profiles are now active based on your configuration.
What to do next
Verify that connected devices use the updated policy tag and the expected network policies are applied.
Attach policy and site tags to an access point (GUI)
This task allows you to efficiently organize and manage access points by assigning specific policy and site tags through GUI.
Use these steps to assign policy and site tags to an AP using GUI:
Procedure
|
Step 1 |
Choose . |
|
Step 2 |
Click the Access Point name. |
|
Step 3 |
Go to the Tags section. |
|
Step 4 |
Choose the Policy Tag from the Policy drop-down list. |
|
Step 5 |
Choose the Site Tag from the Site drop-down list. |
|
Step 6 |
Click Update and Apply to Device. |
The AP has the designated policy and site tags, ensuring it operates under defined network conditions and policy settings.
Attach policy tag and site tag to an AP (CLI)
Assign a policy tag and site tag to an AP using the CLI.
Use this procedure to associate specific network policies and locations with an AP in your Cisco wireless deployment.
Before you begin
Make sure you have the wired MAC address of the AP.
Procedure
|
Step 1 |
Enter global configuration mode. Example: |
||
|
Step 2 |
Configure a Cisco AP and enters AP profile configuration mode. Example:
|
||
|
Step 3 |
Map a policy tag to the AP. Example: |
||
|
Step 4 |
Map a site tag to the AP. Example: |
||
|
Step 5 |
Associate the RF tag. Example: |
||
|
Step 6 |
Save the configuration, exit configuration mode, and return to privileged EXEC mode. Example: |
||
|
Step 7 |
(Optional) Display AP details and the tags associated to it. Example: |
||
|
Step 8 |
Display the AP name with tag information. Example: |
||
|
Step 9 |
(Optional) Display the AP name with tag details. Example: |
The AP is now associated with the specified policy, site, and optionally, RF tags you selected
Link an ACL policy to the defined ACL (GUI)
The task of linking an ACL policy to a defined ACL using the GUI enables you to assign security rules to specific network traffic based on ACL configurations.
Use these steps to link an ACL policy to a defined ACL using the GUI
Procedure
|
Step 1 |
Choose . |
|
Step 2 |
Click Add. |
|
Step 3 |
In the General tab, enter the Name of the Flex Profile. The name can be ASCII characters from 32 to 126, without leading and trailing spaces. |
|
Step 4 |
In the Policy ACL tab, click Add. |
|
Step 5 |
Select the ACL from the ACL Name drop-down list and click Save. |
|
Step 6 |
Click Apply to Device. |
The ACL policy is linked to the defined ACL and applied to the specified device.
Apply access control lists on FlexConnect
Apply Access Control Lists (ACLs) on a FlexConnect wireless profile to filter packet movement through a network.
Use these steps to apply ACLs on FlexConnect.
Procedure
|
Step 1 |
Enter global configuration mode. Example: |
|
Step 2 |
Configure a wireless flex profile and enter wireless flex profile configuration mode. Example: |
|
Step 3 |
Configure an ACL policy. Example:Access control lists (ACLs) perform packet filtering to control the movement of packets through a network. |
|
Step 4 |
Return to wireless flex profile configuration mode. Example: |
|
Step 5 |
Configure native vlan-id information. Example: |
|
Step 6 |
Configure a VLAN. Example: |
|
Step 7 |
Configure an ACL for the interface. Example: |
|
Step 8 |
Configure VLAN information. Example: |
The ACLs are applied to the FlexConnect wireless profile, ensuring controlled packet filtering through configured VLAN settings.
 Feedback
