Release Notes for StarOS™ Software Version, Release 2026.04.l1
Available Languages
Bias-Free Language
The documentation set for this product strives to use bias-free language. For the purposes of this documentation set, bias-free is defined as language that does not imply discrimination based on age, disability, gender, racial identity, ethnic identity, sexual orientation, socioeconomic status, and intersectionality. Exceptions may be present in the documentation due to language that is hardcoded in the user interfaces of the product software, language used based on RFP documentation, or language that is used by a referenced third-party product. Learn more about how Cisco is using Inclusive Language.
- US/Canada 800-553-2447
- Worldwide Support Phone Numbers
- All Tools
 Feedback
 Feedback
StarOS™ Software, Release 2026.04.l1
StarOS™ Software, Release 2026.04.l1
This Release Notes identifies changes and issues that are related to the Legacy Platform (for ASR 5500 DPC2) software releases.
For more information about the StarOS product documentation, see the Related resources section.
Qualified products and platforms
Table 1. Products and platforms qualified in this release
| Component |
Qualified? |
| Products |
|
| CUPS |
No |
| MME |
Yes |
| ePDG |
Yes |
| P-GW |
Yes |
| SAEGW |
Yes |
| SGSN |
Yes |
| Platforms |
|
| ASR 5500 |
Yes |
| VPC-DI |
No |
| VPC-SI |
No |
The following table provides EoL milestones for Cisco StarOS software:
Table 2. EoL milestone information for StarOS™ Software
| Milestone |
Date |
| First Customer Ship (FCS) |
5-Nov-2026 |
| End of Life (EoL) |
5-Nov-2026 |
| End of Software Maintenance (EoSM) |
5-May-2028 |
| End of Vulnerability and Security Support (EoVSS) |
5-May-2028 |
| Last Date of Support (LDoS) |
31-May-2029 |
These milestones and the intervals between them are defined in the Cisco ASR 5500 and Ultra Packet Core software release lifecycle product bulletin available on cisco.com.
This section provides a brief description of the new software features introduced in this release.
Table 3. New software features for StarOS™ Software, Release 2026.04.l1
| Product impact |
Feature |
Description |
| Software reliability |
AES-256 encryption in SNMPv3 |
This feature supports AES-256 as an additional SNMPv3 privacy protocol in the existing snmp target and snmp user configuration paths. This enhancement provides higher-bit privacy encryption for SNMPv3 traffic while preserving backward compatibility with existing des and aes-192 privacy options. For more information, contact the Cisco account representative. |
This section provides a brief description of the behavior changes introduced in this release.
Table 4. Behavior changes for StarOS™ Software, Release 2026.04.l1
| Description |
Behavior changes |
| E-RAB modification collision during VoWiFi-to-VoLTE handover results in Bearer setup failure [CSCwv51804] |
Previous behavior: During a collision caused by an E-RAB Modification Indication (DCNR/NSA) where a NotToBeModified (NTM) bearer is not fully active—for example, if the default bearer is waiting for "Activate-Default-EPS-Bearer-Accept" from UE during a VoWiFi to VoLTE handover —the MME rejects the ERMI and releases the S1 connection. As a result, the UE enters an idle state, which leads to a failed bearer setup. New behavior: A new CLI-controlled configuration knob allows flexible handling of these collisions. The default behavior remains unchanged to maintain backward compatibility. Users can opt in for the new functionality. Command introduced under the mme-service configuration mode: policy erab-mod-ind collision ntm-activation-pending {allow | reject | reject-and-s1-release} · allow: Allows the E-RAB Modification indication procedure and maintains the UE in a connected state. · reject: Rejects the E-RAB Modification procedure but maintains the UE in a connected state. · reject-and-s1-release: Rejects the E-RAB Modification Indication procedure and initiates an S1 release to move the UE to an idle state. This is the default behavior. Note: This change does not alter the behavior for To Be Modified (TM) non-active bearers in ERMI and activation pending collisions. |
This table lists the resolved issues in this specific software release.
Note: This software release may contain bug fixes first introduced in other releases. To see additional information, click the bug ID to access the Cisco Bug Search Tool. To search for a documented Cisco product issue, type in the browser: <bug number> site:cisco.com.
Table 5. Resolved issues for StarOS™ Software, Release 2026.04.l1
| Bug ID |
Description |
Product Found |
| sgmentation fault observed on mme_send_delete_ded_brr_resp_with_cause |
mme |
|
| Flooding of mme-app error level log on Attach reject based on attach restrict policy |
mme |
|
| sessmgr crashes due to assertion failure at sess/egtp/egtpc/egtpc_evt_handler_func.c:1073 |
mme |
|
| E-RAB Modification Collision During VoWiFi-to-VoLTE Handover Results in Bearer Setup Failure |
mme |
|
| Incorrect Service request response or no response |
mme |
|
| MON sub doesn't display context setup response |
mme |
|
| mmemgr sending Aborts with cause "Out of resource" towards enodebs |
mme |
|
| Raid not available after standby CF reboot on cnMME |
pdn-gw |
|
| Support for jumbo X3 packet truncation. |
pdn-gw |
|
| StarOS LI AVP Decode Enhancement decoded fields remain blank or display zero values |
pdn-gw |
|
| Session Manager Crashes on the SAEGW running 21.28.m36 release |
pdn-gw |
|
| Active Charging uplink CSS accounting missing for specific L2TP IPv4 sessions |
pdn-gw |
|
| ASR5500 sessmgr crash with SIGSEGV in ipms_msg_getstats() during IPMS config/unconfig handling |
sae-gw |
|
| Wrong time zone in CDRs |
sgsn |
|
| Legacy-GW: rct process in warn state due to high memory usage after mio card switch |
staros |
This table lists the open issues in this specific software release.
Note: This software release may contain open bugs first introduced in other releases. To see additional information, click the bug ID to access the Cisco Bug Search Tool. To search for a documented Cisco product issue, type in the browser: <bug number> site:cisco.com.
Table 6. Open issues for StarOS™ Software, Release 2026.04.l1
| Bug ID |
Description |
Product Found |
| Sessmgr restart at function sessmgr_epdg_dequeue_transcb_msg() |
epdg |
|
| Sessmgr Process Assertion failure at sess/egtp/egtpc/egtpc_interface.c:298 | Function egtpc_handle_user_sap_event() |
pdn-gw |
|
| Destination-Host AVP incorrectly set to DRA hostname when OCS Origin-Host exceeds 63 characters |
pdn-gw |
|
| Show version <build> not displaying for secure boot enabled build |
staros |
This section describes the known issue that may occur during the upgrade of the StarOS image.
Install and Upgrade Notes
This Release Note does not contain general installation and upgrade instructions. Refer to the existing installation documentation for specific installation and upgrade considerations.
When upgrading the StarOS image from a previous version to the latest version, issues may arise if there is a problem with the Cisco SSH/SSL upgrade. To avoid such issues, ensure that the boot file for Service Function (SF) cards is properly synchronized.
To synchronize the boot file for all the Service Function (SF) VPC-DI non-management cards, use the following CLI command:
[local] host_name# system synchronize boot
This ensures that the changes in boot file are identically maintained across the SF cards.
Note: Ensure that you execute the system synchronize boot command before reloading for a version upgrade from any version less than 21.28.m23 to 21.28.m23, or versions higher than 21.28.m23.
Upgrade the confD version
This section explains upgrading third-party software. Upgrade the confD software to ensure system compatibility and performance.
Note: During StarOS 2026.02 release, confD is upgraded to 8.6 version.
Prerequisites:
· Ensure you have appropriate permissions to perform this upgrade.
· Back up all necessary data and configurations to avoid permanent loss during file deletion.
· ConfD must be unconfigured (stopped) before running the clear confdmgr confd all CLI command.
Perform these steps to upgrade the confD version on the system.
1. Enter the debug shell using debug shell command.
2. Navigate to the confD directory.
3. Run the command: cd /mnt/hd-raid/meta/confd/ to access the directory.
4. Remove existing files with the command; rm -rf *
-or-
Run the StarOS CLI command clear confdmgr confd all to clear the same confD contents.
Note: The /mnt/hd-raid/meta/confd directory will be empty. After clearing, confD can be started again as required. This clear cli should be used only during ConfD upgrade scenarios and not on each reload or reboot.
All files and subdirectories are deleted, preparing the system for a fresh installation. To preserve data across the Method of Procedure, users with ConfD configured must contact their Cisco account representative.
HD-RAID may fail to initialize during upgrades or downgrades between non-Hermes builds
Issue: When upgrading or downgrading between non-Hermes builds (202x.0x.lx) on ASR5k platforms, the HD-RAID may fail to initialize as expected.
Workaround: This Method of Procedure (MOP) should be used during upgrades or downgrades between non-Hermes builds.
To avoid HD-RAID failure, perform these steps during upgrade or downgrade (for example, from 2026.02.lx to 2026.03.lx:
1. Pre-requisite: Back up all files stored in /hd-raid before upgrading from .mx to .mx builds.
Note: All data in /hd-raid will be lost during recovery.
2. Before the upgrade: On the current (source) build, run the **hd raid clear** command.
3. Upgrade and reboot: Reboot the node to upgrade to the newer (target) build.
4. Wait for the hd-raid to recover and restore the files from backup.
Note: It is recommended to use this Method of Procedure (MOP) for upgrading and downgrading between .mx builds.
This section provides compatibility information of the StarOS™ Software products that are verified to work with this version of the ASR 5500.
Compatible StarOS package version
Table 7. Release package version information
| StarOS packages |
Version |
Build number |
| StarOS package |
2026.04.l1 |
21.28.m48.101855 |
Compatible software and hardware components
This table lists only the verified basic software and hardware versions. For more information on the verified software versions for the products qualified in this release contact the Cisco account representative.
Table 8. Compatibility software and hardware information, Release 2026.04.l1
| Product |
Version |
| ADC P2P Plugin |
2.74.19.2835 |
This section provides information about the release packages associated with Legacy Platform (for ASR 5500 DPC2) software.
Table 9. Software packages for Release 2026.04.l1
| Software package |
Description |
| ASR 5500 companion package |
|
| companion-asr5500-2026.04.l1.zip |
Contains the signed ASR 5500 software image, the signature file, a verification script, the x509 certificate, and a README file containing information on how to use the script to validate the certificate. |
StarOS product version numbering system
The output of the show version command displays detailed information about the version of StarOS currently running on the ASR 5500 or Cisco Virtualized Packet Core platform.
Starting 2024.01.0 release (January 2024), Cisco is transitioning to a new release versioning scheme. The release version is based on the current year and product. Refer to the figure for more details.
Note: During the transition phase, some file names will reflect the new versioning whereas others will refer to the 21.28.x- based naming convention. With the next release, StarOS-related packages will be completely migrated to the new versioning scheme.
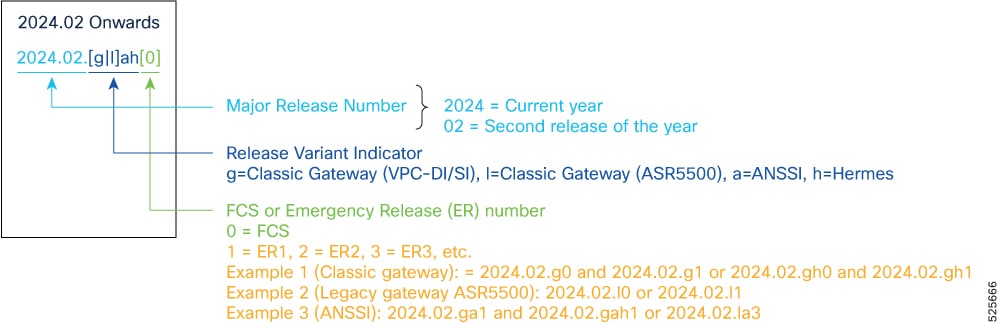
Note: For any clarification, contact your Cisco account representative.
Software integrity verification
To verify the integrity of the software image you have from Cisco, you can validate the SHA512 checksum information against the checksum identified by Cisco for the software. Image checksum information is available through Cisco.com Software Download details. Click Linux and then choose the Software Image Release Version.
To find the checksum, hover the mouse pointer over the software image you have downloaded. At the bottom you find the SHA512 checksum, if you do not see the whole checksum, you can expand it by pressing the "..." at the end.
To validate the information, calculate a SHA512 checksum using the information in the table and verify that it matches the one provided on the software download page. To calculate a SHA512 checksum on your local desktop see the table.
Table 10. Checksum calculations per operating system
| Operating system |
SHA512 checksum calculation command examples |
| Microsoft Windows |
Open a command line window and type the following command: > certutil.exe -hashfile <filename>.<extension> SHA512 |
| Apple MAC |
Open a terminal window and type the following command: $ shasum -a 512 filename.extension |
| Linux |
Open a terminal window and type the following command: $ sha512sum filename.extension OR $ shasum -a 512 filename.extension |
| Note: filename is the name of the file. extension is the file extension (for example, .zip or .tgz). |
|
If the SHA512 checksum matches, you can be sure that no one has tampered with the software image or the image has not been corrupted during download.
If the SHA512 checksum does not match, we advise you to not attempt upgrading any systems with the corrupted software image. Download the software again and verify the SHA512 checksum again. If there is a constant mismatch, please open a case with the Cisco Technical Assistance Center.
Certificate validation
In 2024.01 and later releases, software images for StarOS, VPC-DI, and VPC-SI, and the companion software packages for StarOS and VPC are signed via x509 certificates. USP ISO images are signed with a GPG key. For more information and instructions on how to validate the certificates, refer to the README file available with the respective software packages.
This table provides key resources and links to the support information and essential documentation for StarOS and CUPS products.
Table 11. Related resources and additional information
| Resource |
Link |
| Cisco ASR 5500 documentation |
|
| Cisco Ultra Packet Core documentation |
|
| Service request and additional information |
Cisco and the Cisco logo are trademarks or registered trademarks of Cisco and/or its affiliates in the U.S. and other countries. To view a list of Cisco trademarks, go to this URL: www.cisco.com/go/trademarks. Third-party trademarks mentioned are the property of their respective owners. The use of the word partner does not imply a partnership relationship between Cisco and any other company. (1110R)
Any Internet Protocol (IP) addresses and phone numbers used in this document are not intended to be actual addresses and phone numbers. Any examples, command display output, network topology diagrams, and other figures included in the document are shown for illustrative purposes only. Any use of actual IP addresses or phone numbers in illustrative content is unintentional and coincidental.
© 2026 Cisco Systems, Inc. All rights reserved.