Issue with UBA Model "Suspicious Device Access Model" displaying in Data Availability page
Available Languages
Applicability
UBA 5.4.1Description
In Splunk UBA 5.4.1, the "Suspicious Device Access Model" associated with the Unusual Machine Access anomaly type is displayed in the Data Availability page, indicating it is in use. However, this model is not actually functional or generating anomalies. The Data Availability page shows three models related to this anomaly type.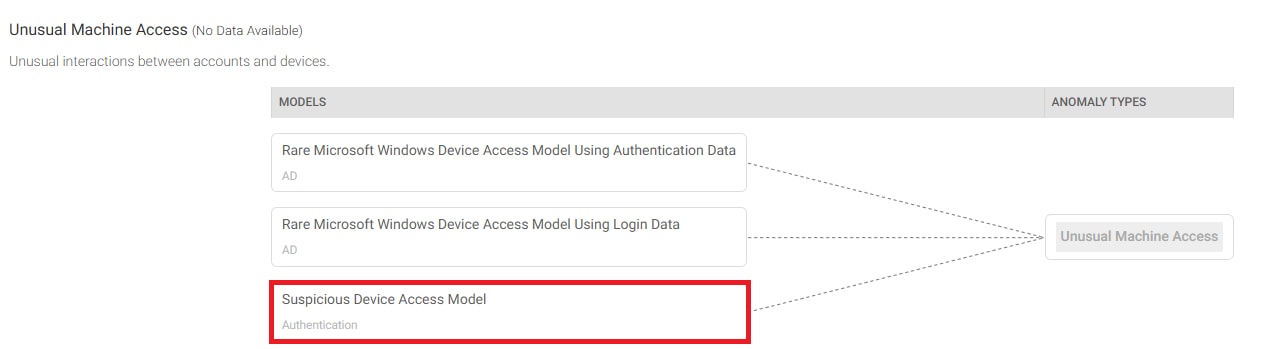
Investigation
During investigation, it was found that the "Suspicious Device Access Model" is no longer used in UBA version 5.4.1. This was verified by checking the model registry configuration file located at:
cat /opt/caspida/content/Splunk-Standard-Security/modelregistry/streaming/ModelRegistry.json | grep -A 20 "SuspiciousDeviceAccessDetection"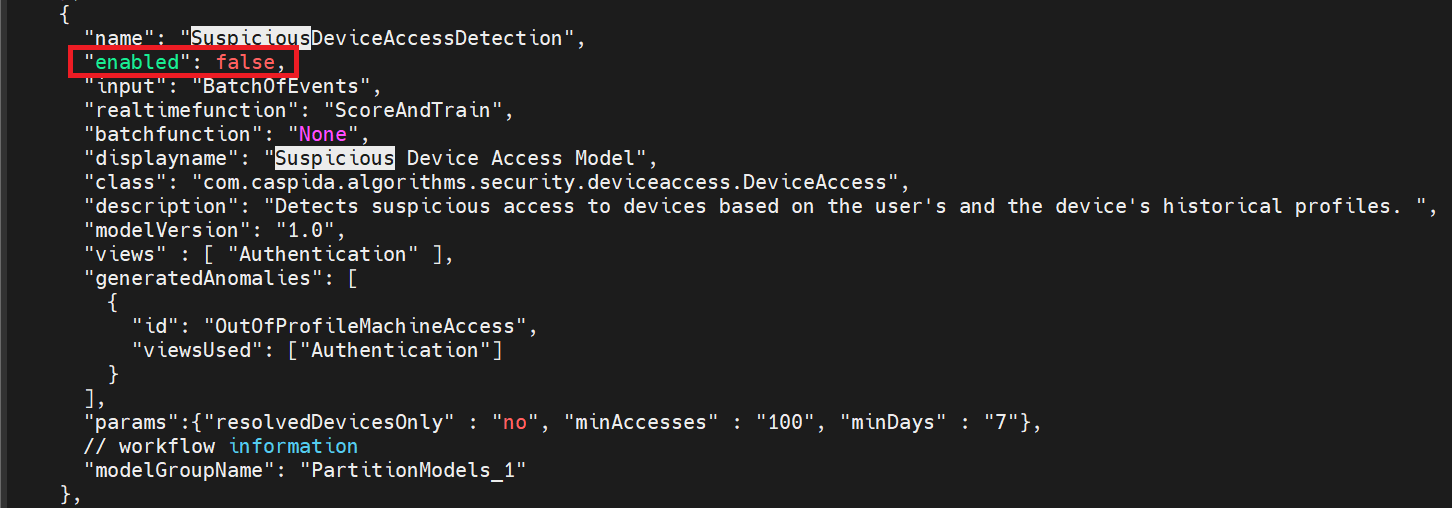
The model registry confirms that "Suspicious Device Access Model" is not registered as an active model in the current version. However, the UBA Data Availability page incorrectly displays this model as being in use, creating a discrepancy between the actual model configuration and the UI display.
Resolution
The "Suspicious Device Access Model" is deprecated and not in use in current UBA versions. The model was officially deprecated in UBA version 4.1.0.
Related Links
Revision History
| Revision | Publish Date | Comments |
|---|---|---|
1.0 |
01-Oct-2026
|
Initial Release |
 Feedback
