Annotations fields missing in Splunk ES correlation search
Available Languages
Applicability
Splunk Enterprise SecurityDescription
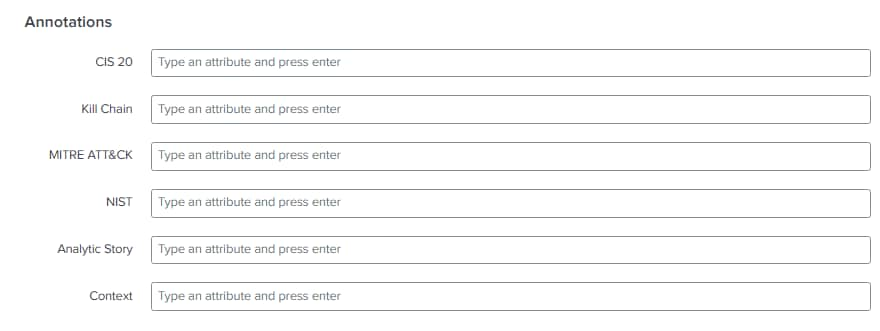
When creating a new correlation search in Splunk ES, it is noticed that some annotations such as "Impact" and "Confidence" fields are missing.
Investigation
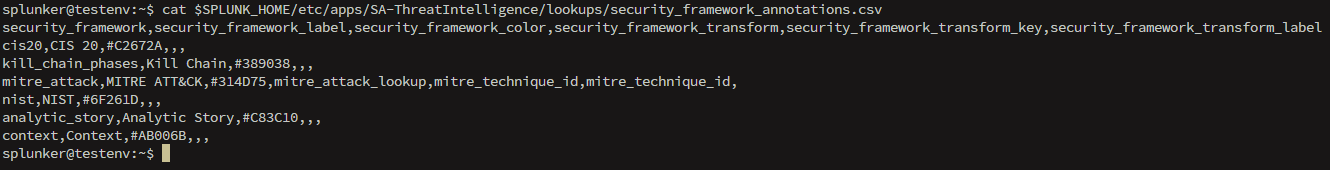
Identified that some lines are missing in the following file $SPLUNK_HOME/etc/apps/SA-ThreatIntelligence/lookups/security_framework_annotations.csv by running the following command:
cat $SPLUNK_HOME/etc/apps/SA-ThreatIntelligence/lookups/security_framework_annotations.csv
Resolution
- To resolve the issue, replace the contents of
$SPLUNK_HOME/etc/apps/SA-ThreatIntelligence/lookups/security_framework_annotations.csvwith the following default content and save it:
security_framework,security_framework_label,security_framework_color,security_framework_transform,security_framework_transform_key,security_framework_transform_label
cis20,CIS 20,#C2672A,,,
kill_chain_phases,Kill Chain,#389038,,,
mitre_attack,MITRE ATT&CK,#314D75,mitre_attack_lookup,mitre_technique_id,mitre_technique_id,
nist,NIST,#6F261D,,,
confidence,Confidence,#980AEC,,,
impact,Impact,#662D91,,,
analytic_story,Analytic Story,#C83C10,,,
context,Context,#AB006B,,,
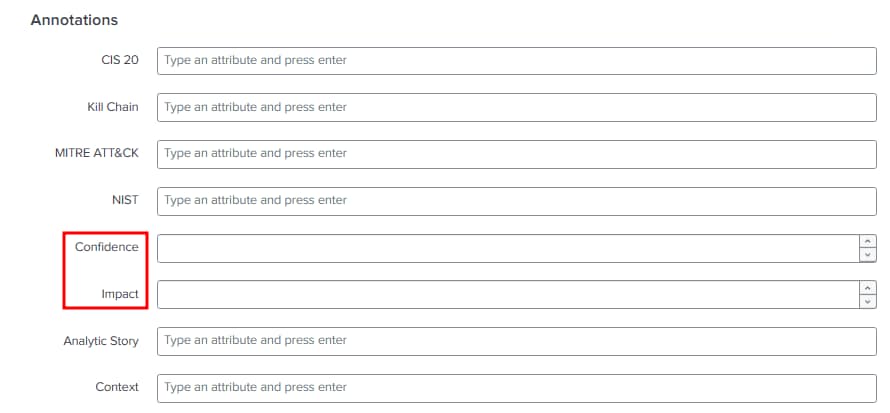
- After making the changes, navigate to Configure > Content > Content Management in Splunk ES and click on Create New Content > Correlation Search. All the annotations are now visible as expected.
Related Links
Splunk document: Splunk ES Annotations
Revision History
| Revision | Publish Date | Comments |
|---|---|---|
1.0 |
29-Sep-2026
|
Initial Release |
 Feedback
