The Correlation search in the ITSI app doesn't produce expected results.
Available Languages
Applicability
Splunk IT Service Intelligence (ITSI)Description
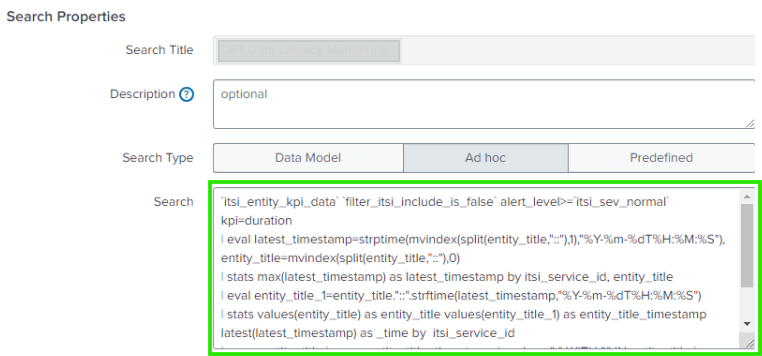
The correlation search has been configured below to generate notables with the severity "Critical".
'itsi_entity_kpi_data'filter_itsi_include_is_false' alert_level>='itsi_sev_normal' kpi=duration
| eval latest_timestamp=strptime(mvindex(split(entity_title," .: "),1),"%Y-%m-%dT%H:%M:%S"), entity_title=mvindex(split(entity_title," :: "),0)
| stats max(latest_timestamp) as latest_timestamp by itsi_service_id, entity_title
| eval entity_title_1=entity_title." :: ".strftime(latest_timestamp,"%Y-%m-%dT%H:%M:%S")
| stats values(entity_title) as entity_title values(entity_title_1) as entity_title_timestamp latest(latest_timestamp) as_time by itsi_service_id
Investigation
During the investigation, it was found that the alert_level value was defined in a macro (itsi_sev_normal).
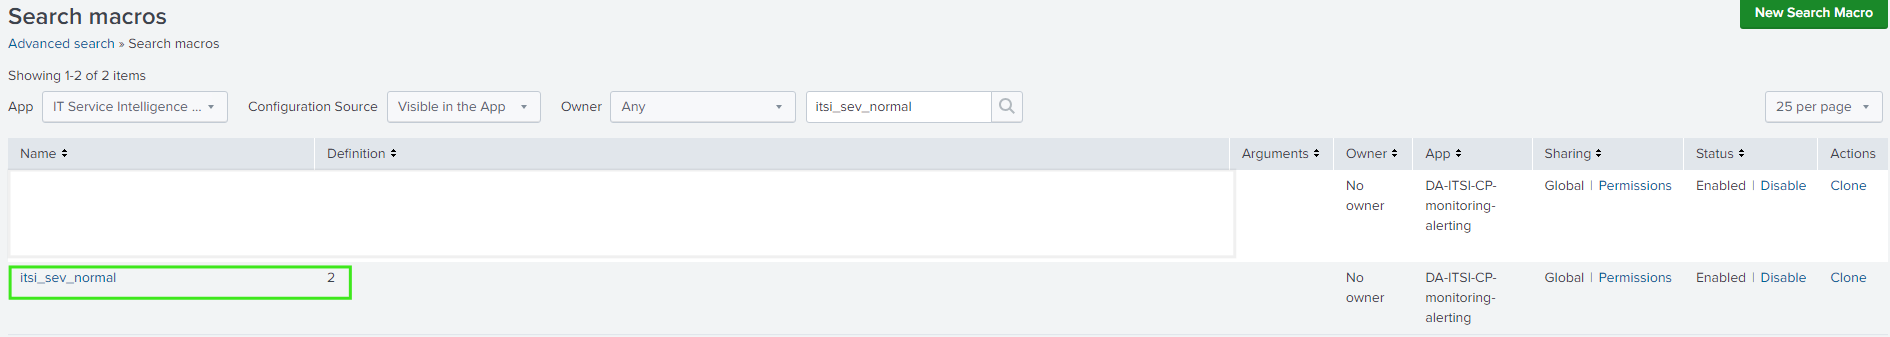
The value "2" was passed to the search and in the SPL the alert_level >= 2 has been configured.
Due to this configuration, the search is picking all the levels, including the severity normal. By default, the alert level is set to 2, which determines the severity as normal.
Resolution
To resolve this issue in the Correlation search, the equal (=) symbol needs to be removed and alert_level should be only greater than 2.
- Navigate to the Configuration dropdown.
- Select the Event Management option.
- Choose Correlation Search and from the list, select the respective correlation search.
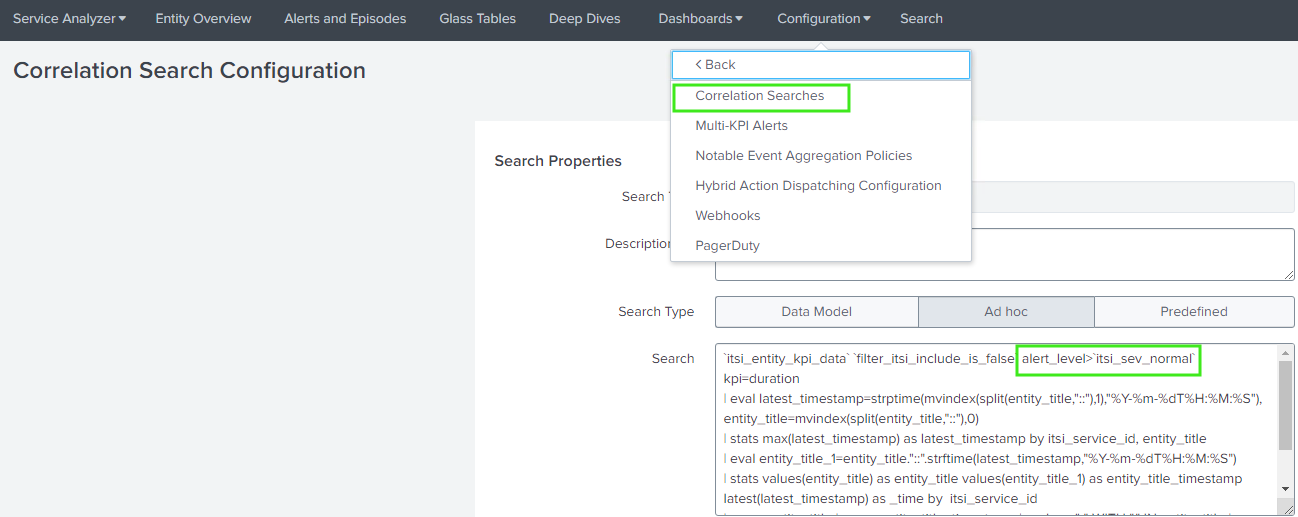
'itsi_entity_kpi_data'filter_itsi_include_is_false' alert_level>'itsi_sev_normal' kpi=duration
| eval latest_timestamp=strptime(mvindex(split(entity_title," .: "),1),"%Y-%m-%dT%H:%M:%S"), entity_title=mvindex(split(entity_title," :: "),0)
| stats max(latest_timestamp) as latest_timestamp by itsi_service_id, entity_title
| eval entity_title_1=entity_title." :: ".strftime(latest_timestamp,"%Y-%m-%dT%H:%M:%S")
| stats values(entity_title) as entity_title values(entity_title_1) as entity_title_timestamp latest(latest_timestamp) as_time by itsi_service_id
After this change, this Correlation search will generate the notables with severity (Medium, High, and Critical). Thus the expected results will be achieved.
Related Links
Revision History
| Revision | Publish Date | Comments |
|---|---|---|
1.0 |
29-Sep-2026
|
Initial Release |
 Feedback
