Ingest Actions not forwarding data to S3 AWS bucket
Available Languages
Applicability
Splunk Enterprise 9.2.4Description
Investigation
The configuration was well done configured without having issues when testing the connection using access key and secret key.
- Made that admin capabilities have the proper capabilities enabled:
$SPLUNK_HOME/etc/system/local/authorize.conf[role_admin]
list_ingest_rulesets = enabled
edit_ingest_rulesets = enabledContinued to verify that path, keys, and are properly configured.
$SPLUNK_HOME/etc/system/local/outputs.conf[rfs:RFS_DEST_XXXXX]
batchSizeThresholdKB = 131072
batchTimeout = 30
compression = gzip
description = RFS_DEST_XXXXX
dropEventsOnUploadError = false
format = ndjson
format.ndjson.index_time_fields = true
partitionBy = day
path = s3://S3_BUCKET_XXXXX/PATH_XXXXX
remote.s3.access_key = ACCESS_KEY_XXXXX
remote.s3.encryption = none
remote.s3.endpoint = S3_ENDPOINT_XXXXX
remote.s3.secret_key = SECRET_KEY_XXXXX
remote.s3.signature_version = v4
remote.s3.supports_versioning = true
remote.s3.url_version = v1Then once configured and tested successfully continued to check if data was being forwarded by running an internal query for IngestActionsRfsDestinationHandler & RfsOutputProcessor components to validate the group is connected in the specified group:
index=_internal sourcetype=splunkd component IN (IngestActionsRfsDestinationHandler,RfsOutputProcessor)
Expected events:
03-10-2025 19:20:58.587 +0000 INFO IngestActionsRfsDestinationHandler [45809 TcpChannelThread] - Reloaded S3 credentials Successfully!03-10-2025 19:21:00.993 +0000 INFO RfsOutputProcessor [45809 TcpChannelThread] - Successfully added scheme=s3 rfs_destinations={[0]='RFS_DEST_XXXXX'}Previously, in metrics if data has been tested the field name=ingest should return that data was processed:
index=_internal sourcetype=splunkd component=Metrics group=dutycycle name=ingest
03-10-2025 19:14:39.126 +0000 INFO Metrics - group=dutycycle, ingest_pipe=1, name=ingest, thread=merging, ratio=0.003But still data was not present in the AWS S3 bucket.
Resolution
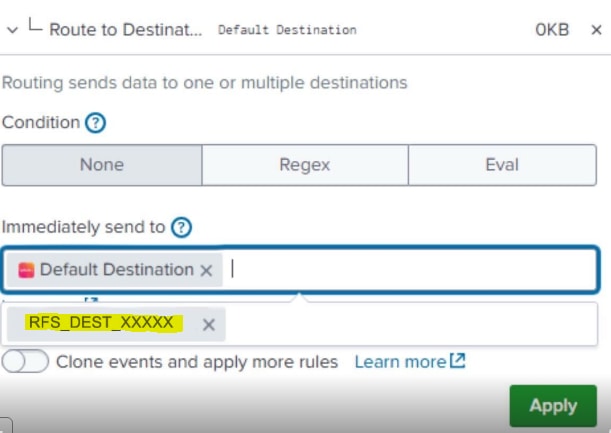
The destination is configured as the default group to send data S2S between Splunk intercommunication. The group was changed with the one configured in outputs.conf in the rfs stanza.
- Add RFS_DEST_XXXXX.
- Remove Default destination.
- Apply and save.
Related Links
Introducing Ingest Actions - Splunk community
Ingest Actions for Splunk platform - Splunk Documentation
Revision History
| Revision | Publish Date | Comments |
|---|---|---|
1.0 |
29-Sep-2026
|
Initial Release |
 Feedback
Contact Cisco
- Open a Support Case

- (Requires a Cisco Service Contract)