Azure/Entra ID - Failing group mapping
Available Languages
Applicability
Splunk Cloud, Splunk Enterprise, SAMLDescription
Azure/Entra ID is unable to parse the group attribute from assertion. Returns 'No value found in SamlResponse for match key'. This will likely trigger a 'Failed to decode relayState.' when login attempts fail.
Investigation
Most important clue can be encountered on 'splunkd.log'. This issue triggers the following message:
10-11-2025 00:00:00.000 +0000 ERROR Saml [46532 webui] - No value found in SamlResponse for match key=saml:AttributeStatement/saml:Attribute attrName=role err=No nodes found for xpath=saml:AttributeStatement/saml:AttributeThis message is related on how Azure/Entra/ADFS send SAML attributes on the XML responses. In other words, Splunk is unable to identify how the group/role attribute is named and will require an alias to fix.
Resolution
In most scenarios, adding the following aliases fix the issue:
Role alias: http://schemas.microsoft.com/ws/2008/06/identity/claims/groups
RealName alias: http://schemas.microsoft.com/identity/claims/displayname
Mail alias: http://schemas.xmlsoap.org/ws/2005/05/identity/claims/emailaddress 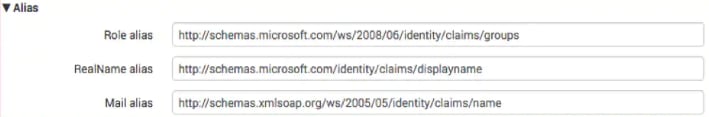
If failed, make sure to reference the most up to date documentation. For example: Configure Microsoft Entra SSO for Splunk Enterprise and Splunk Cloud for Single sign-on with Microsoft Entra ID - Microsoft Entra ID | Microsoft Learn
Related Links
Revision History
| Revision | Publish Date | Comments |
|---|---|---|
1.0 |
01-Oct-2026
|
Initial Release |
 Feedback
Contact Cisco
- Open a Support Case

- (Requires a Cisco Service Contract)