Ingest Actions Ruleset not getting applied for the sourcetype 'WinEventLog'.
Available Languages
Applicability
Splunk Enterprise Splunk CloudDescription
The events from sourcetype 'WinEventLog' is being sent to main index instead of index 'abc' even though Ingest Actions(IA) is configured to send the data to index 'abc'.
Data Flow : Universal Forwarder > Splunk Cloud.
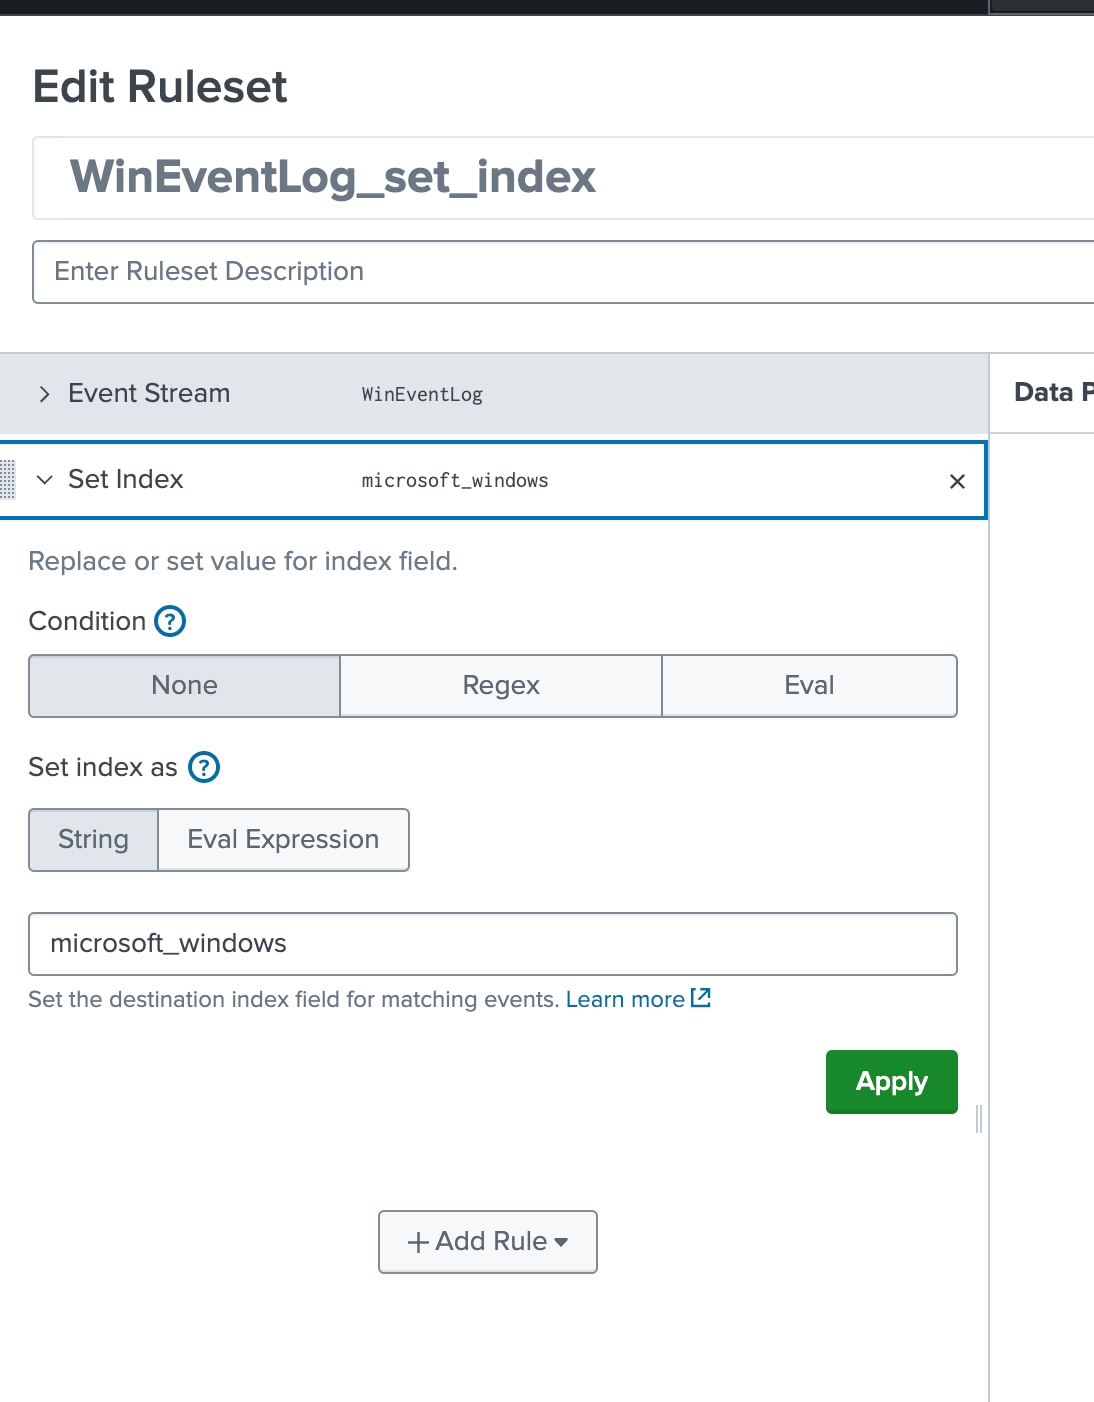
Below was the ruleset configured:
Investigation
Checked using btool for one of the indexers if the props.conf and transforms.conf configs were being pushed to the indexers or not, Below was the config present:
$SPLUNK_HOME/etc/apps/000-self-service/local/props.conf
[WinEventLog]
RULESET-WinEventLog_routing_to_correct_index = _rule:WinEventLog_routing_to_correct_index:set_index:eval:ifcsei5y
$SPLUNK_HOME/etc/apps/000-self-service/local/transforms.conf
[_rule:WinEventLog_routing_to_correct_index:set_index:eval:ifcsei5y]
INGEST_EVAL=index=if((true()), "microsoft_windows", index)
Looks like that the stanzas listed under props.conf and transforms.conf while configuring Ingest Actions under preview option from the UI got pushed to the indexers, However the IA is still not working.
While ingesting the Windows data, found that the actual sourcetype is different and it is renaming the sourcetype during the parsing process(Attaching screenshot below):
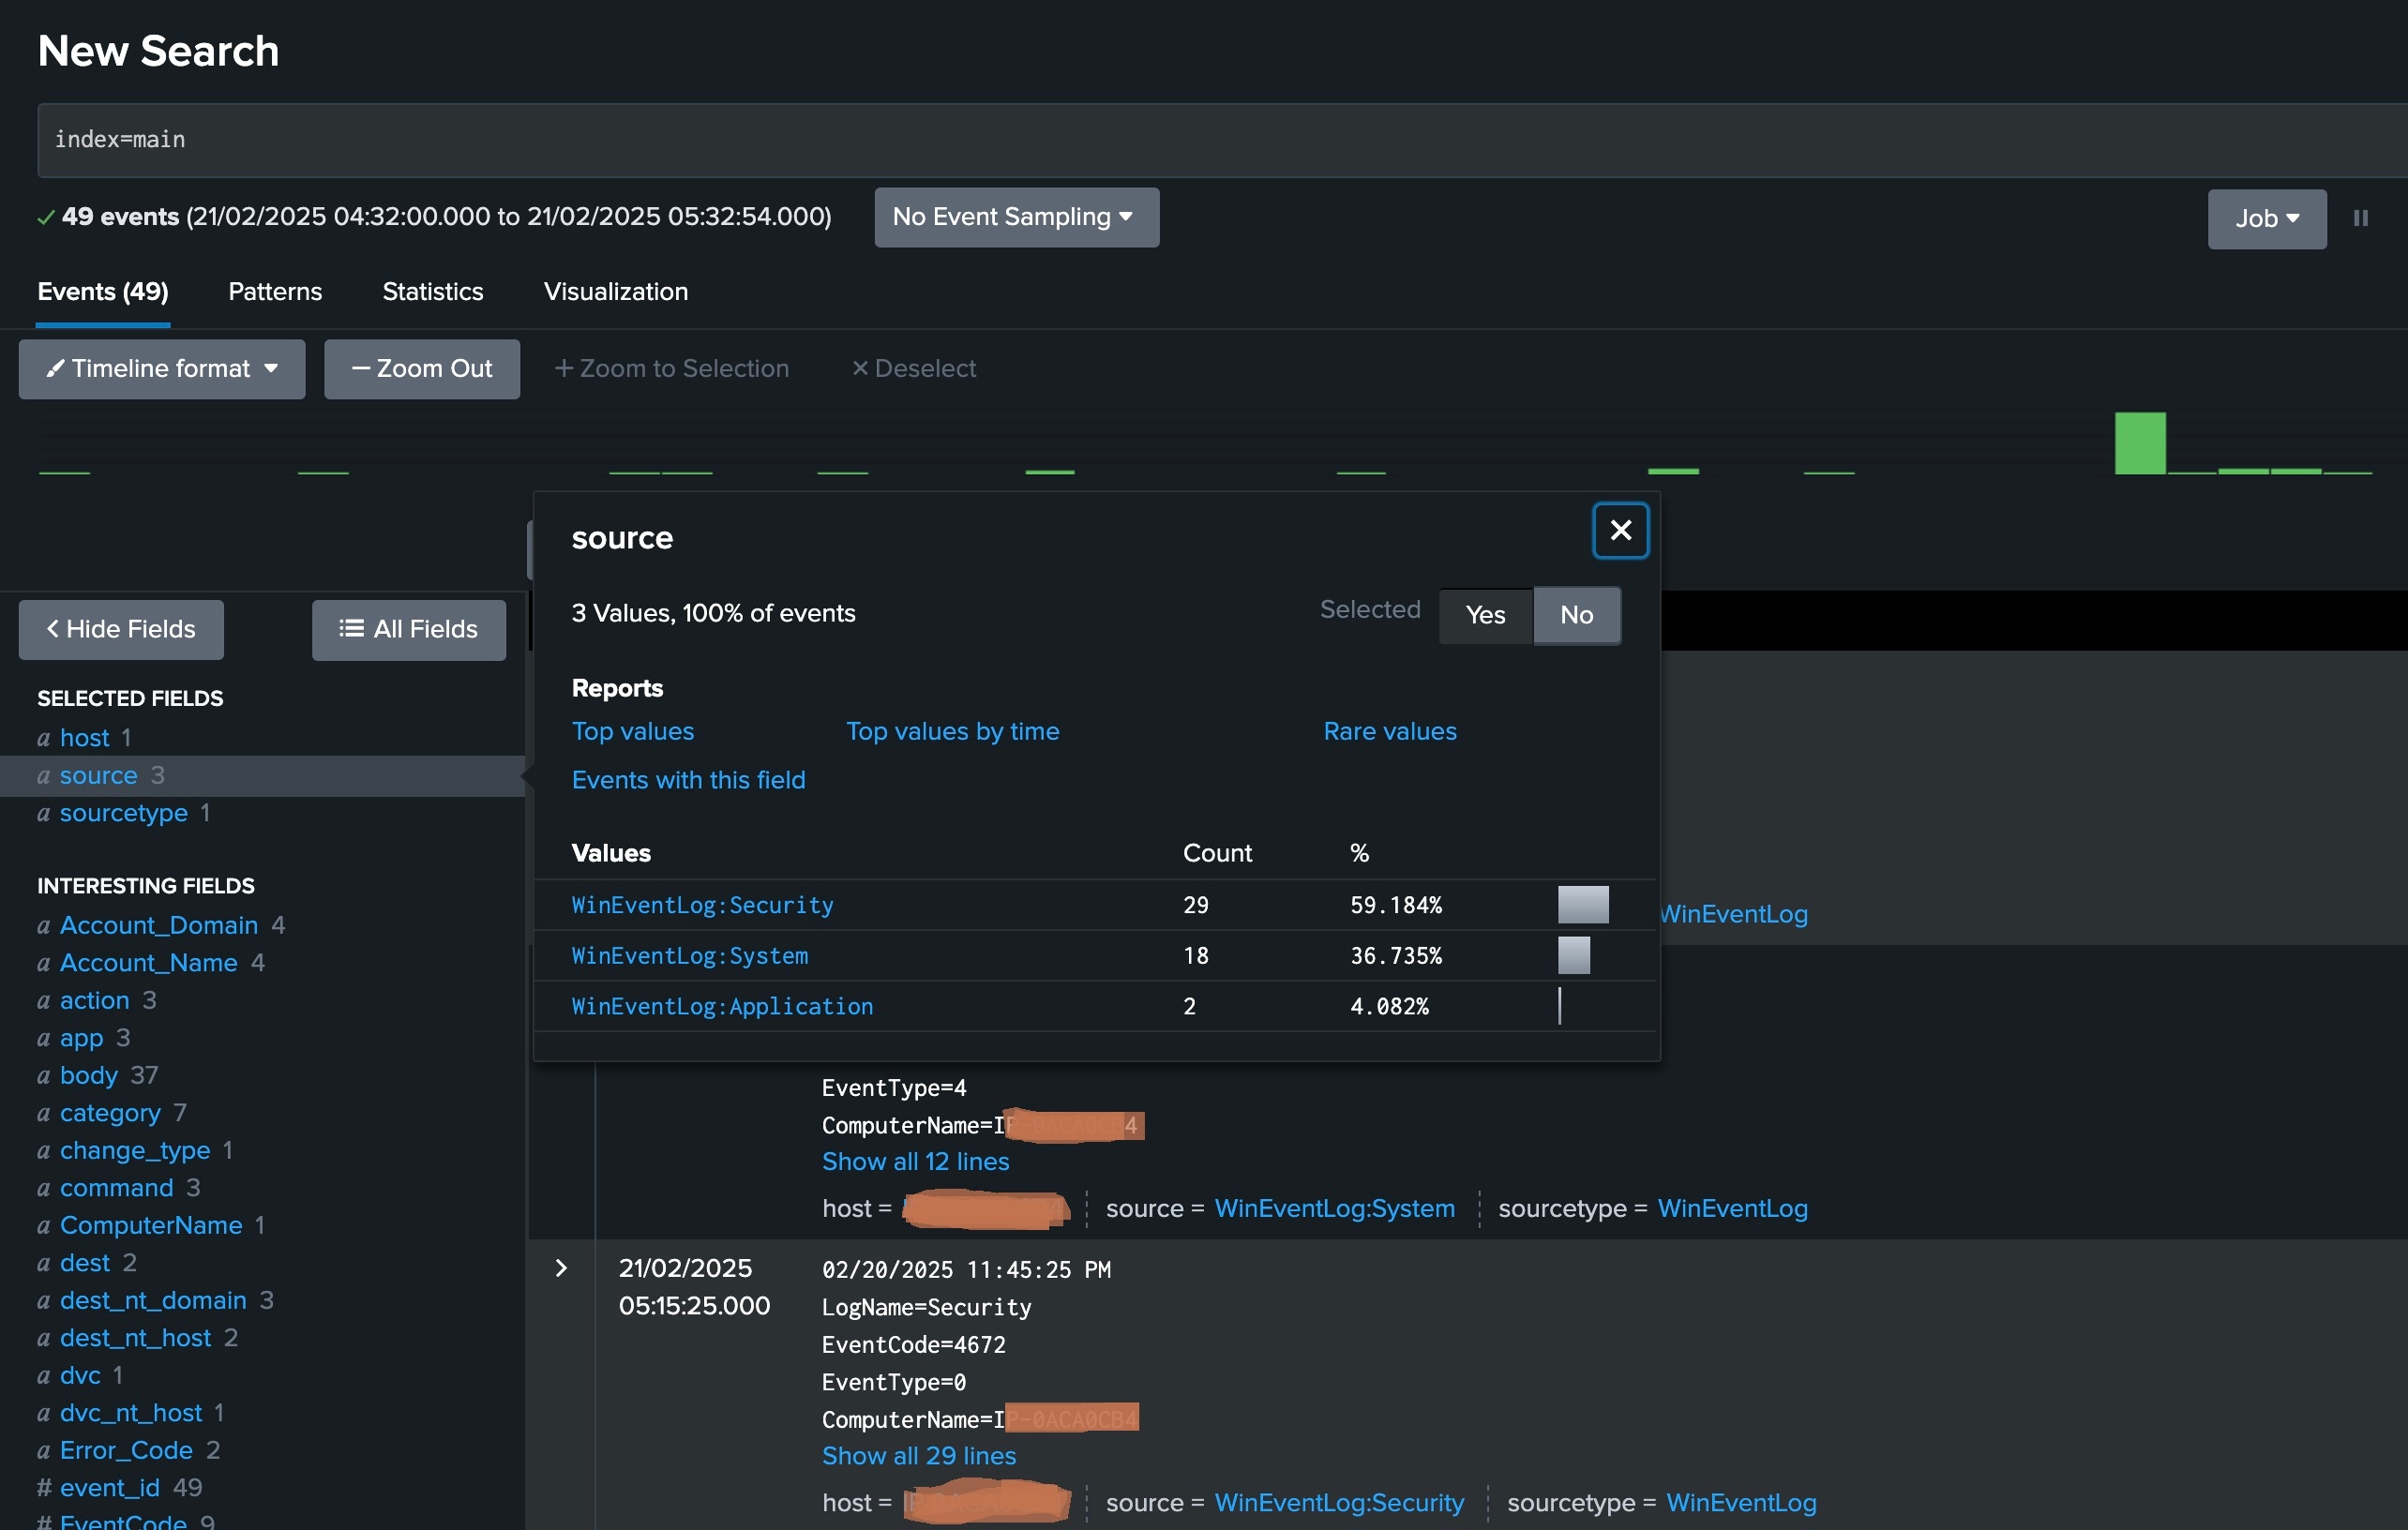
As per the above image, can see the source type is showing WinEventLog, but the actual sourcetype is different(Security,Application & System)
Resolution
To fix this, have to apply an Ingest Action with Source along with wildcard. In the above scenario, setting the sourcetype as source::WinEventLog* resolved the issue.
Related Links
Use ingest actions to improve the data input process
Using ingest actions with source types that are renamed with props and transforms
Revision History
| Revision | Publish Date | Comments |
|---|---|---|
1.0 |
29-Sep-2026
|
Initial Release |
 Feedback
Contact Cisco
- Open a Support Case

- (Requires a Cisco Service Contract)