While launching the SSE app the error "A custom JavaScript error caused an issue loading your dash-board. See the developer console for more details." was observed
Available Languages
Applicability
Splunk Security Essentials (any version) Splunk Cloud Splunk EnterpriseDescription
While searching for the data using the Splunk Security Essentials lookups, getting a Splunk Security Essentials lookup error in the SPL query output:
Could not load lookup=LOOKUP-splunk_security_essentialsAlso, while launching the Splunk Security Essentials app, getting multiple errors on the screen:
A custom JavaScript error caused an issue loading your dash-board. See the developer console for more details.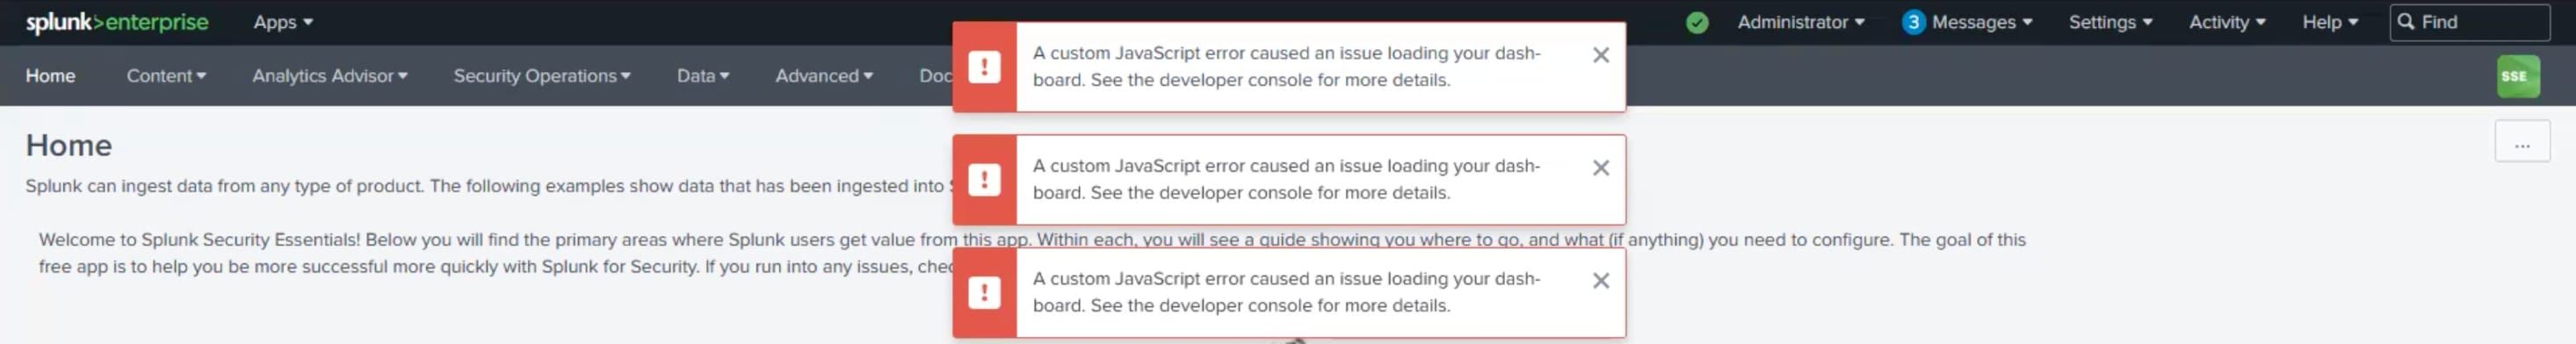
Investigation
Upon checking the browser's console logs it was observed the "KV Store is disabled" error:
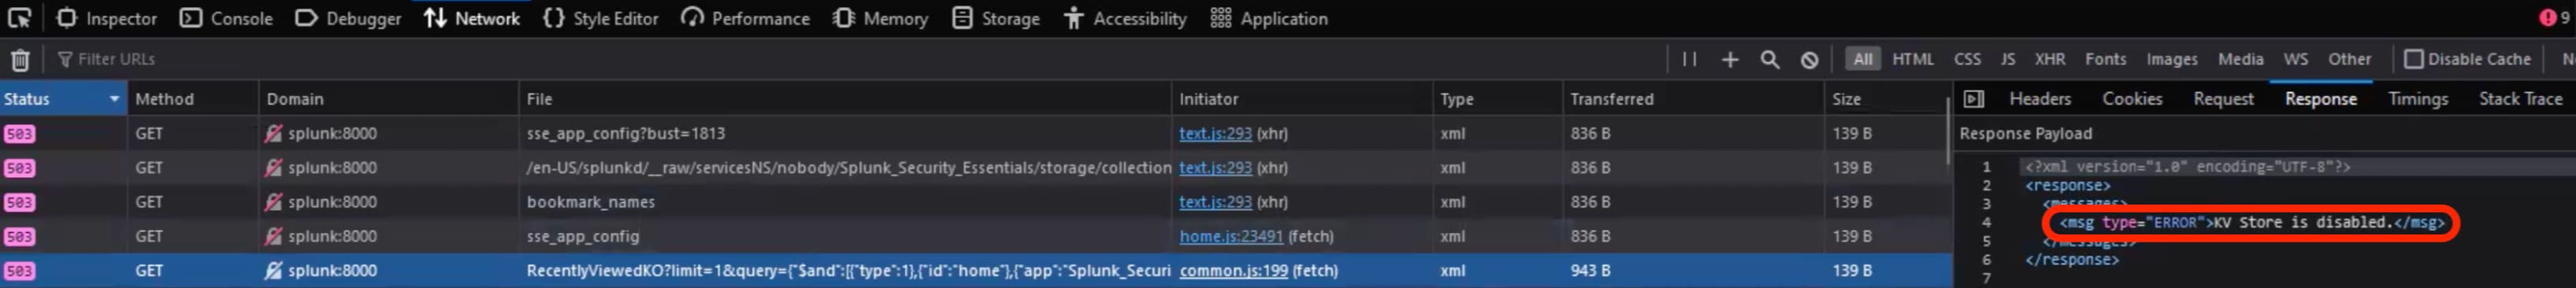
Now while checking the KV Store status in the CLI it was indeed in the disabled mode:
Resolution
The KV Store was in status : disabled due to the disabled = true configuration of server.conf present in the $SPLUNK_HOME\etc\system\local directory under [kvstore] stanza:
After changing the configuration from disabled = true to disabled = false in the server.conf, the kvstore will be in status : ready, and the Splunk Security Essentials app will be accessible without any KV Store error:

Revision History
| Revision | Publish Date | Comments |
|---|---|---|
1.0 |
29-Sep-2026
|
Initial Release |
 Feedback
Contact Cisco
- Open a Support Case

- (Requires a Cisco Service Contract)
This Document Applies to These Products
Related Articles
- ERROR: "A custom Javascript error caused an issue loading your dashboard, like due to the dashboard version update. See the developer console for more details"
- Splunk Security Essentials (SSE) Home page is failing to load with Error message - "A custom JavaScript error caused an issue loading your dashboard. See the developer console for more details."
- Lookup Editor App Javascript Error Caused an Issue Loading Your Dashboard
- Configuration page for the Splunk Supporting Add-on for Active Directory is failing with Error message ie. "A custom JavaScript error caused an issue loading your dashboard."