UBA - How to delete anomalies by creating Anomaly Action Rules.
Available Languages
Applicability
UBA 5.4.1Description
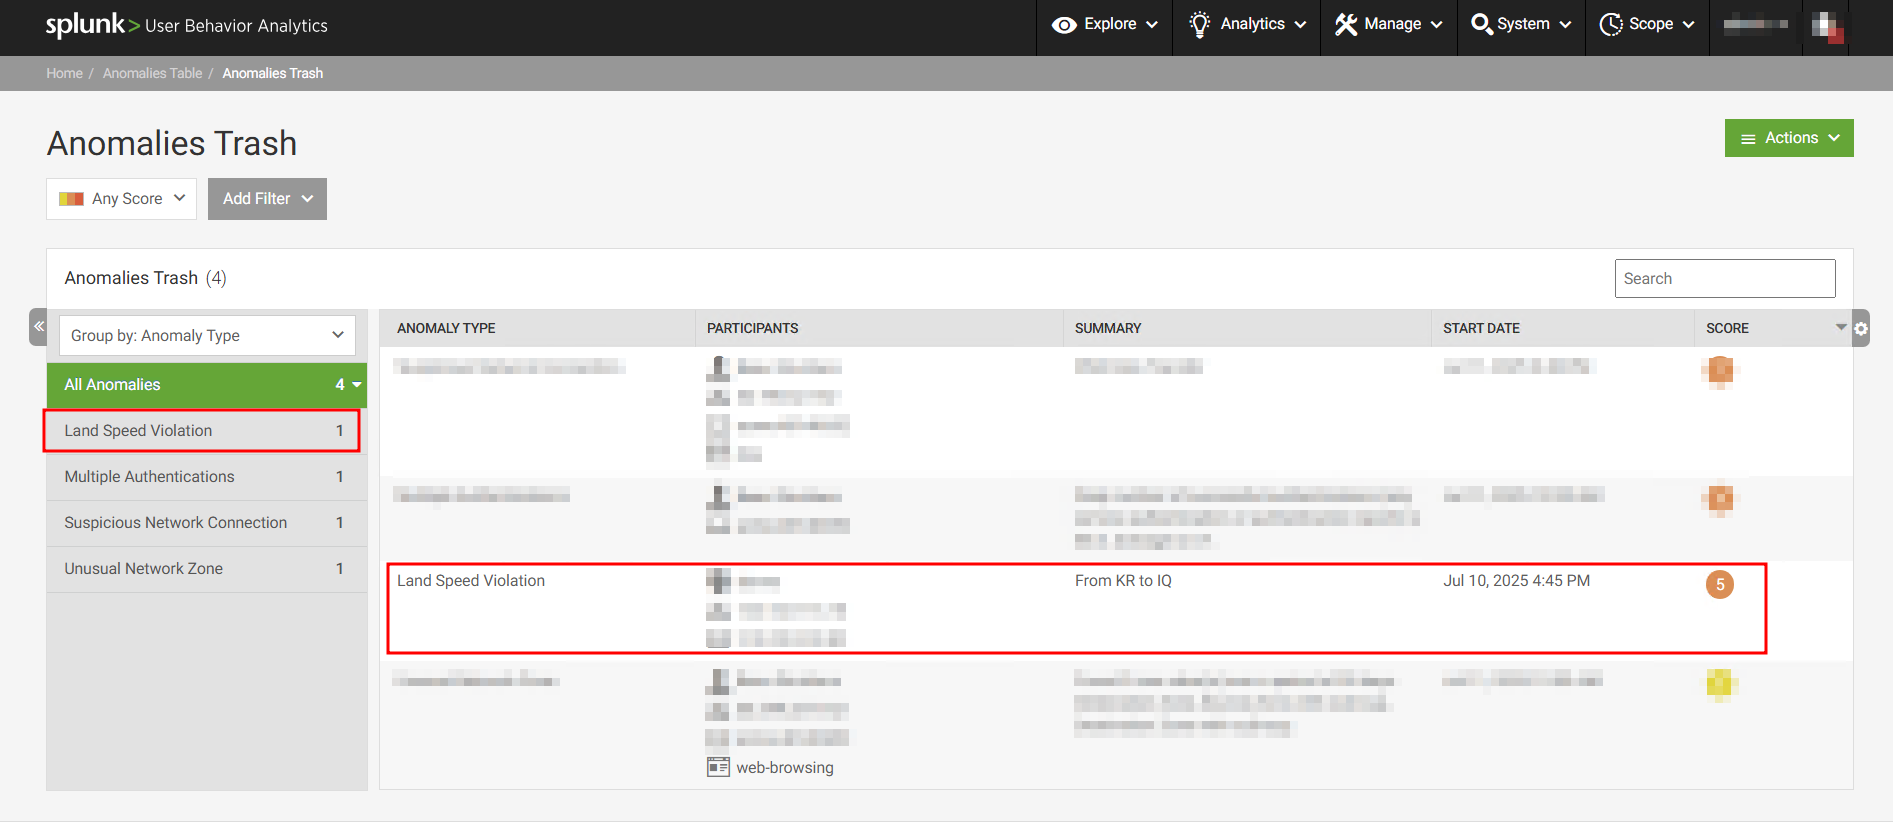
There are anomalies generated under "Land Speed Violation" anomaly type as shown below.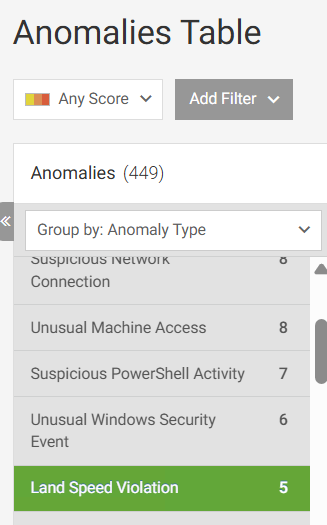
Investigation
"Land Speed Violation" anomalies triggered by expected or trusted IP ranges, such as VPN concentrators or private subnets. This will be identified when reviewing anomaly data where known IPs are repeatedly flagged.
These anomalies with the expected or trusted IPs can be considered as a false positive.
Splunk UBA provides mechanisms to suppress anomalies generated from known or trusted IP addresses and CIDR (Classless Inter-Domain Routing) ranges.
AllowListed IPs:
- Allowlisted option can be configured directly in the Anomaly Action Rule interface by selecting the anomaly type, choosing the scope (Internal or External), and entering IPs or CIDR blocks to exclude from detection.
- Anomalies matching the defined rule are automatically moved to the "Trash".
- This method will be suitable for centralized management of "allow list" logic across different rules.
Resolution
To exclude IPs or CIDR blocks from Land Speed Violation anomalies:
-
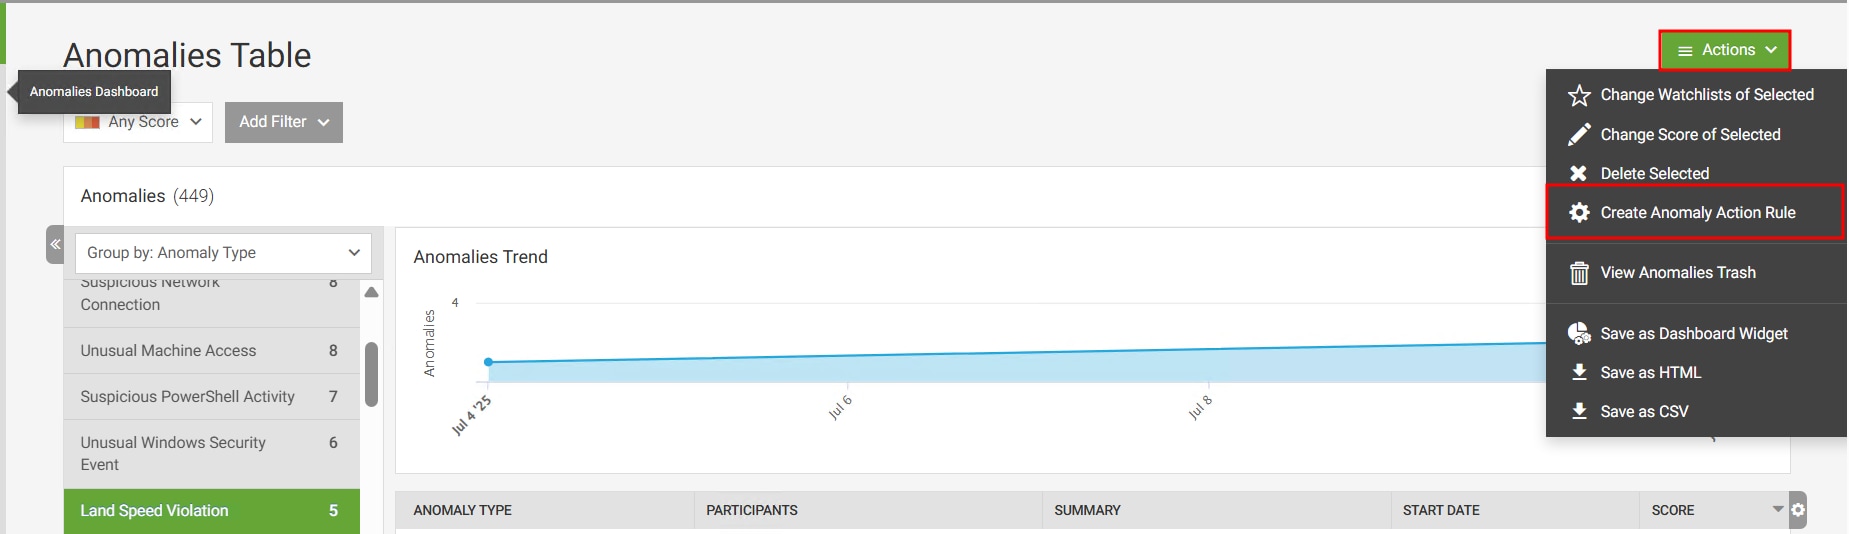
Navigate to Explore > Anomaly, select any anomaly and click on Actions > Create Anomaly Action Rule.
-
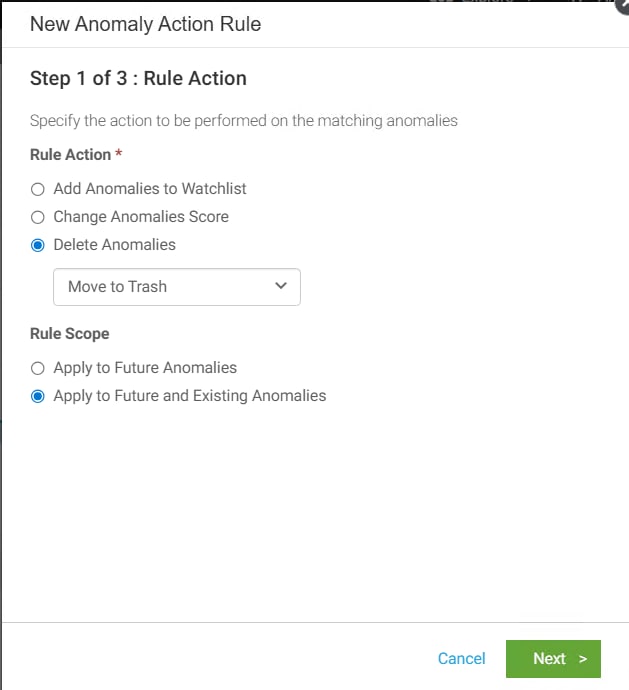
Select the desired Rule Action and Rule Scope.
-
Navigate to Anomaly Configuration and select Land Speed Violation.
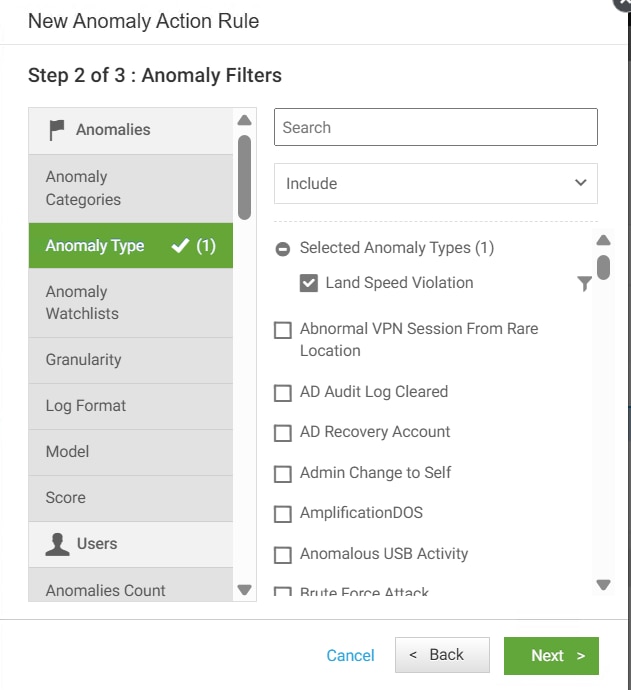
-
Choose the appropriate device scope: Internal or External
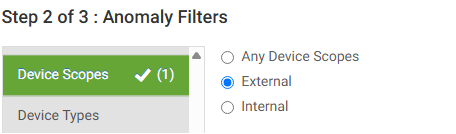
-
Add IP addresses or CIDRs to the allowlist
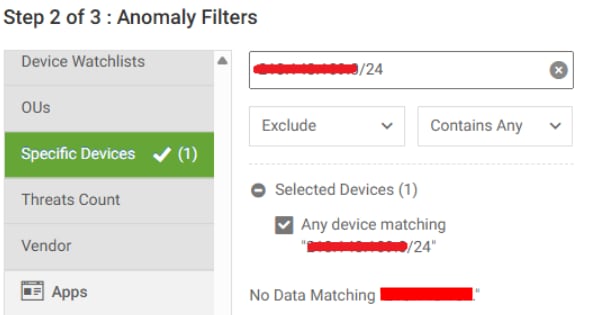
-
Click Next, assign a rule name, and OK.
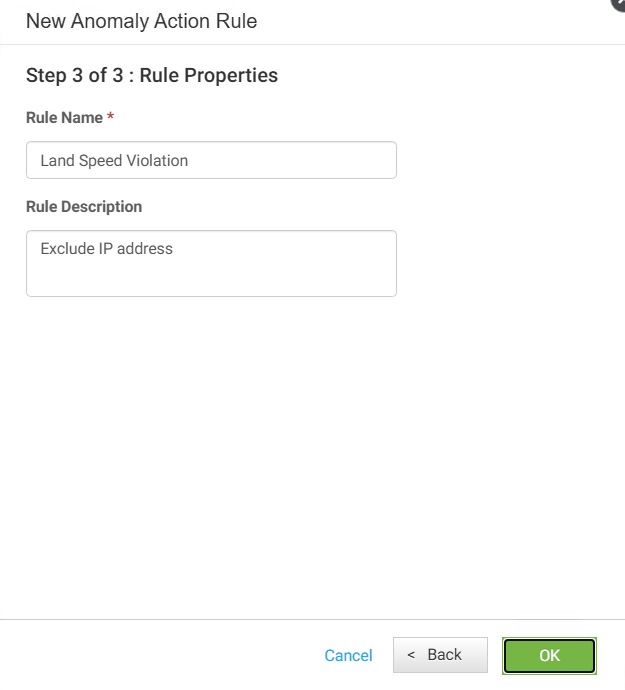
-
Confirm that matching anomalies are moved to Trash
Note: To exclude data before ingestion, modify the SPL in the data source.
Related Links
- Splunk document - Anomaly Action Rules Documentation
- Splunk document - Event Filters Documentation
- Splunk document - Use the Watchlist in an Anomaly Action Rule
Revision History
| Revision | Publish Date | Comments |
|---|---|---|
1.0 |
01-Oct-2026
|
Initial Release |
 Feedback
