UBA: Where are Threats Stored in UBA
Available Languages
Applicability
UBA (5.x) RHEL Ubuntu AWSDescription
Splunk UBA threats can be manually closed or automatically closed by Splunk UBA.- Threats automatically closed by Splunk UBA are marked as Closed By System.
- Threats manually closed by a user are marked as Closed By User.
Investigation
Sometimes, anomalies are created that generate a threat but upon further investigation, the threat does not represent a real threat in your environment. For example:
- A department-wide password expiration, rather than brute force attack attempts, led to abnormal numbers of login failures and threat creation.
- Atypical location behavior was observed for a user, such as a user who was working remotely for a week.
In such cases, you can manually close the threat as Not a Threat.
Here's how you can manually close a threat in UBA:
- Login to the UBA GUI and click on the following options:
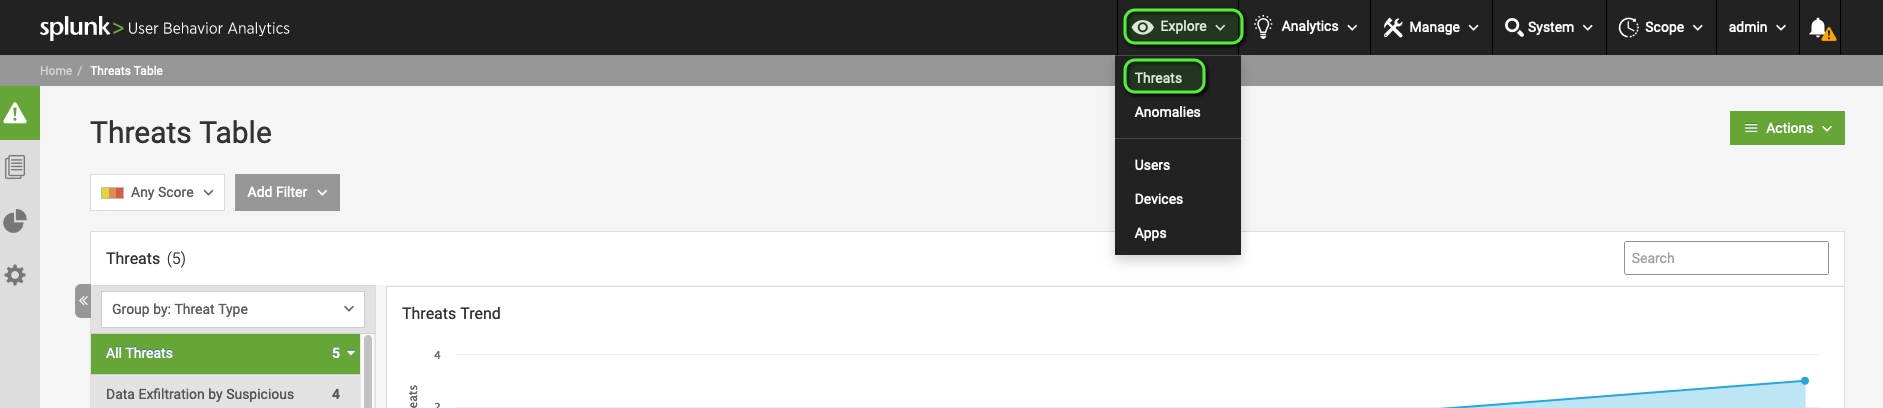
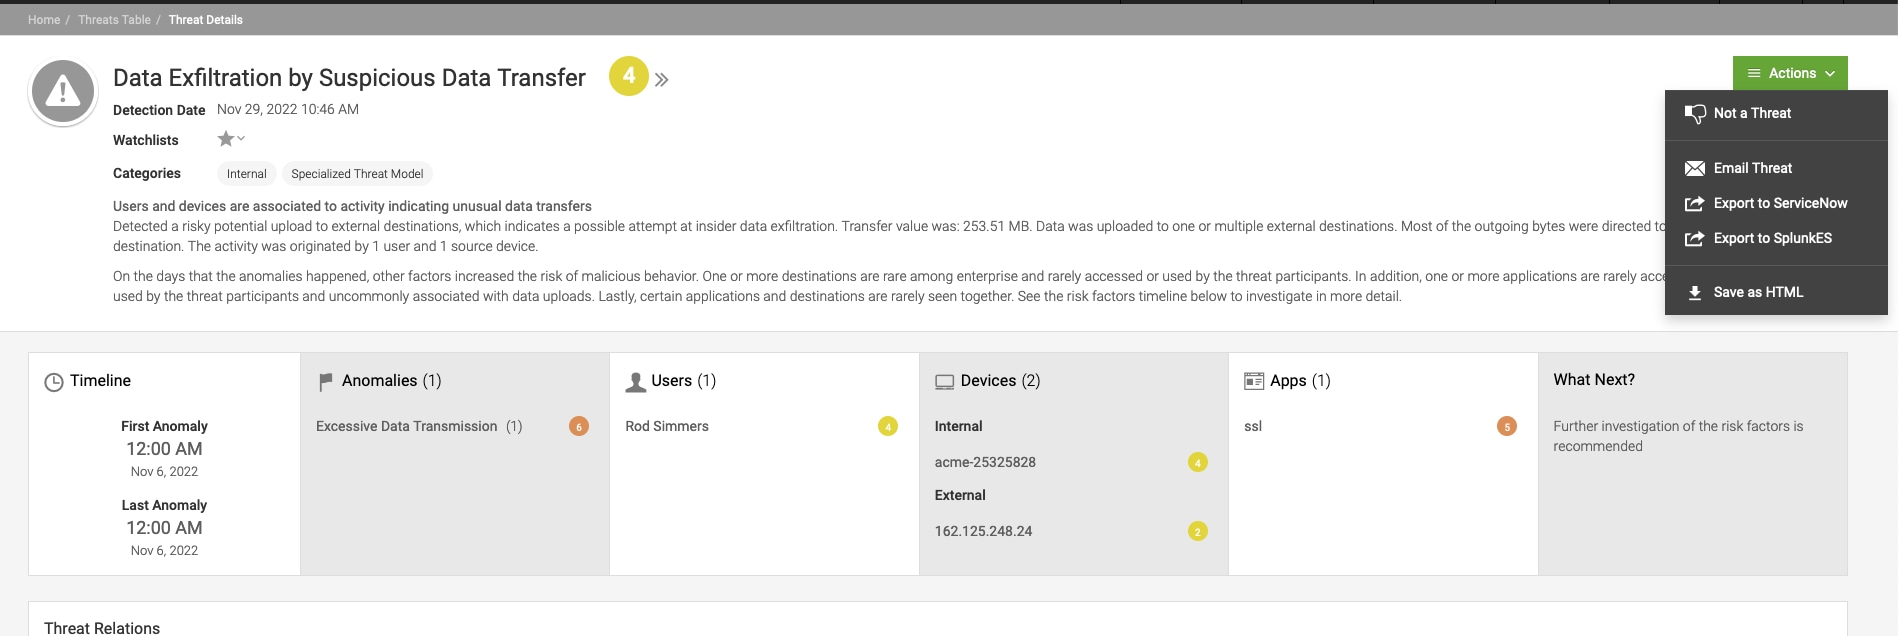
- Select a specific threat that you want to close manually as "Not a Threat" by simply clicking on the threat in question followed by clicking "Actions" on top right hand side of the page and selecting the option "Not a Threat" as show in the image below:
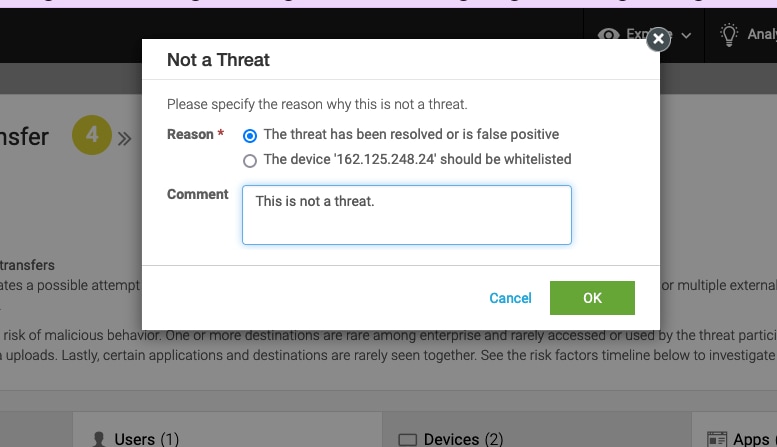
- Select the appropriate reason such as "Resolved" or "False Positive" or a device that is needed to be "Blacklisted" or "Whitelisted" followed by entering your comments in the comment section as shown in the image below:
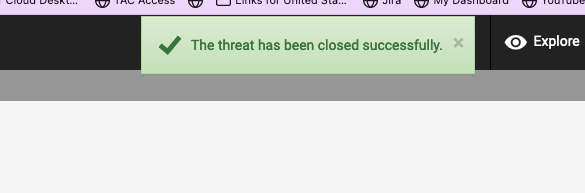
- Click "OK" once the necessary fields are populated above and look for a confirmation screen of threat being closed successfully as shown below:
Resolution
In order to check where the closed threats are saved after closed via GUI. Please follow the below mentioned steps:- Login to master node as user "caspida"
- Run the following command:
sudo su caspida; psql -d caspidadb;select * from threats where status='ClosedByUser';
- The threat that is closed would be stored under "threats" table. A sample threat closure in our lab is shown below for reference:
caspidadb=# select * from threats where status='ClosedByUser'; id | starttime | updatetime | threattype | ruleid | threattypeext | summary | description | recommendation | score | threatdata | computedby | rootsessionid | patternid | tagids | internaltags | isactive | threatcategory | firstcomputedtime | lastupdatedtime | status | testmodeon | esnotableid 1 | 2022-11-04 18:05:00 | 2022-11-05 19:29:00 | internalExfiltration | 0 | Data Exfiltration by Suspicious User or Device | Unusual activity followed by data exfiltration | Entity involved in a sequence of events constituting a threat: it first performed an unusual internal activity, followed by an unusually large data transfer to an external entity. This threat is a possible data exfiltration by the entity to malicious domain. | Investigate the users involved. Check for recent changes in their role | 4 | {"supportingEvidence" : [{"description":"","title":"Kill Chain","type":"KillChain","phases":[{"description":"Perimeter breach through compromised remote account","title":"Intrusion"},{"description":"Unusual user activity or lateral movement","groups":[{"description":"Anomalies","title":"Suspicious Pattern","anomalies":[{"score":5,"entityType":"Anomaly","id":"7514222663756969248","label":"Malicious pattern ``allow_url_include=on+-d+safe_mode=off``","time":1667585100000}]}],"title":"Expansion"},{"description":"Data exfiltration","groups":[{"description":"Anomalies","title":"Suspicious Pattern","anomalies":[{"score":5,"entityType":"Anomaly","id":"-6846510085621108678","label":"NTP Data Transfer","time":1667676540000}]}],"title":"Exfiltration"}]}], "scoreDetails" : [{"value" : 5}, {"value" : -1, "description" : "One of the stages of the threat has a single anomaly to support it"}]} | LegacyThreatComputation | | 0 | | | f | {Internal,KillChain} | 2022-11-29 02:00:05 | 2023-02-02 08:51:12 | ClosedByUser | f | 3D750413-E102-4C62-8031-C8AE450B81A5@@notable@@ffcbf2e69c043f05bf08f631051f54f5(1 row)
- The threat that is closed with comments would be stored under "blackwhitelistorigins". In order to check the comment associated with that threat, run the following command :
caspidadb=# select * from blackwhitelistorigins where type='NotAThreat';
- A sample threat closure in our lab is shown below for reference:
id | email | source | uploadtime | comment | error | type | listtype | isactive ----+-------+--------+-------------------------+----------------------------------+-------+------------+----------+---------- 42 | admin | | 2023-02-02 08:51:51.122 | This device must be whitelisted. | | NotAThreat | WhiteIP | t(1 row)
Related Links
Details about how to close threats in UBARevision History
| Revision | Publish Date | Comments |
|---|---|---|
1.0 |
29-Sep-2026
|
Initial Release |
 Feedback
