Multiple findings for the same risk entity in Splunk ES 8.1
Available Languages
Applicability
Splunk Enterprise Security > v8.1Description
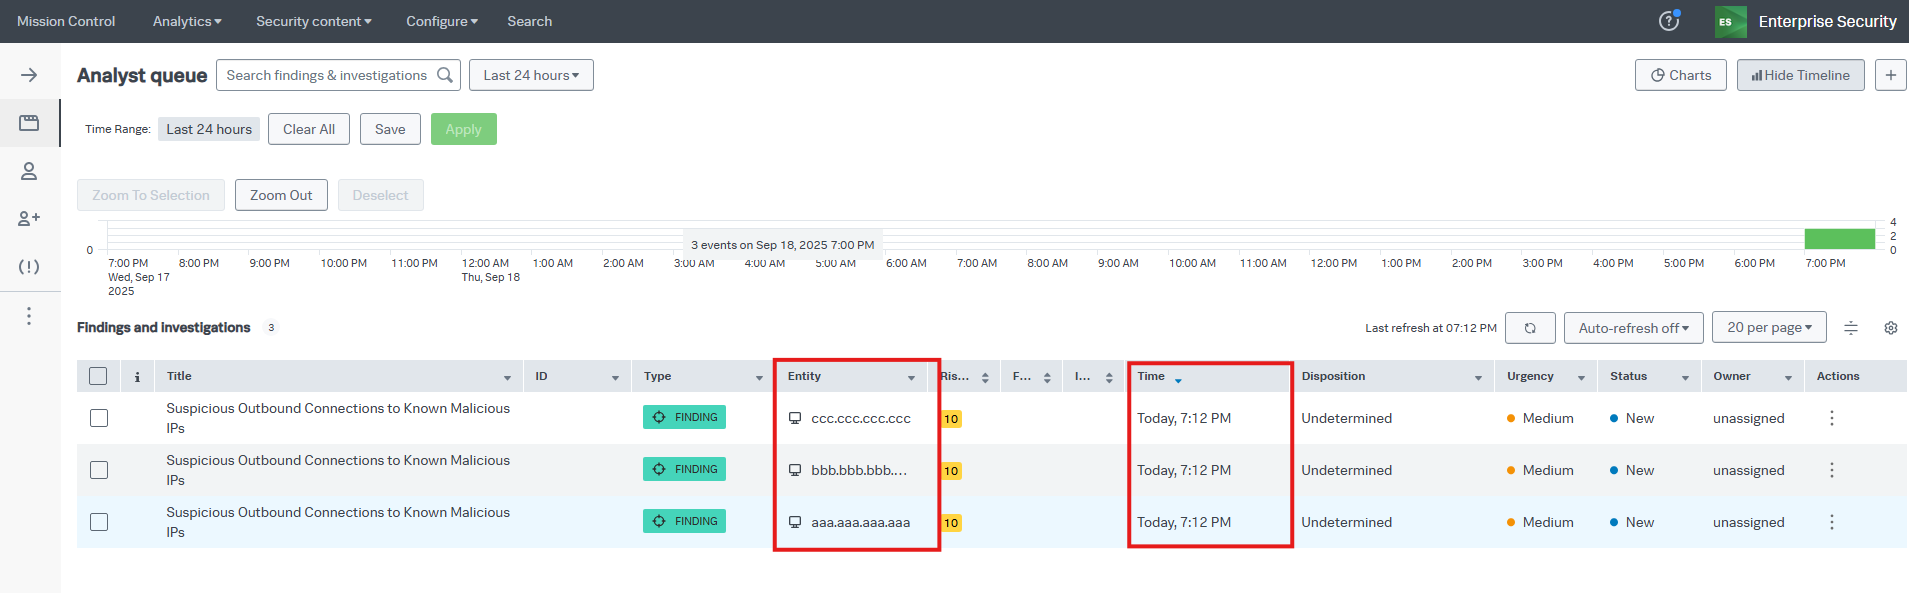
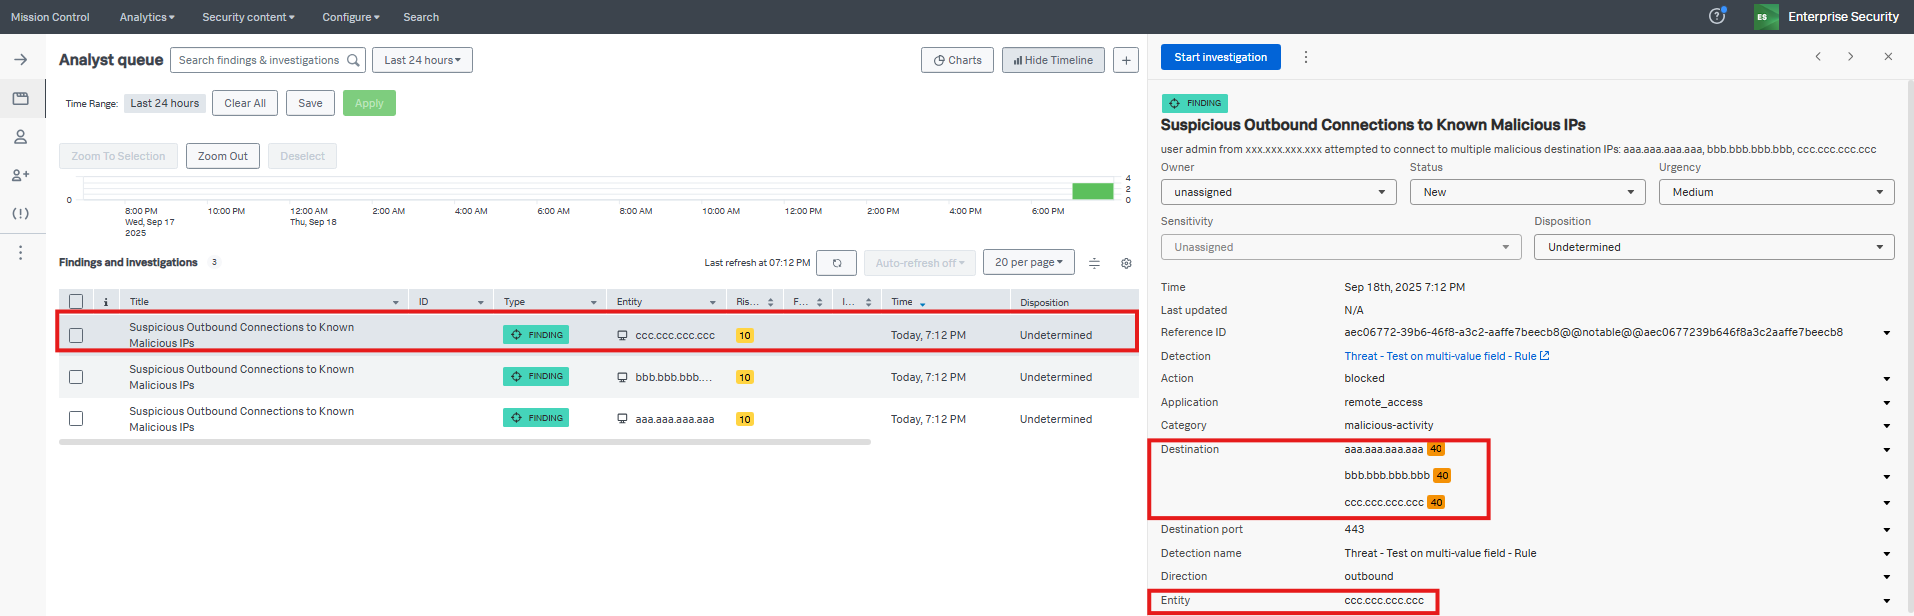
When a multi-value field were used as the Risk Entity in a detection, multiple findings were generated, each corresponding to a unique value in the field. These findings appeared as individual findings in the Mission Control Analyst Queue and shows failure in throttling.
Investigation
When a detection was configured to create findings using a multi-value field as the Risk Entity, multiple findings were generated, one for each value in that field. This behavior also affected the expected outcome of throttling configurations.
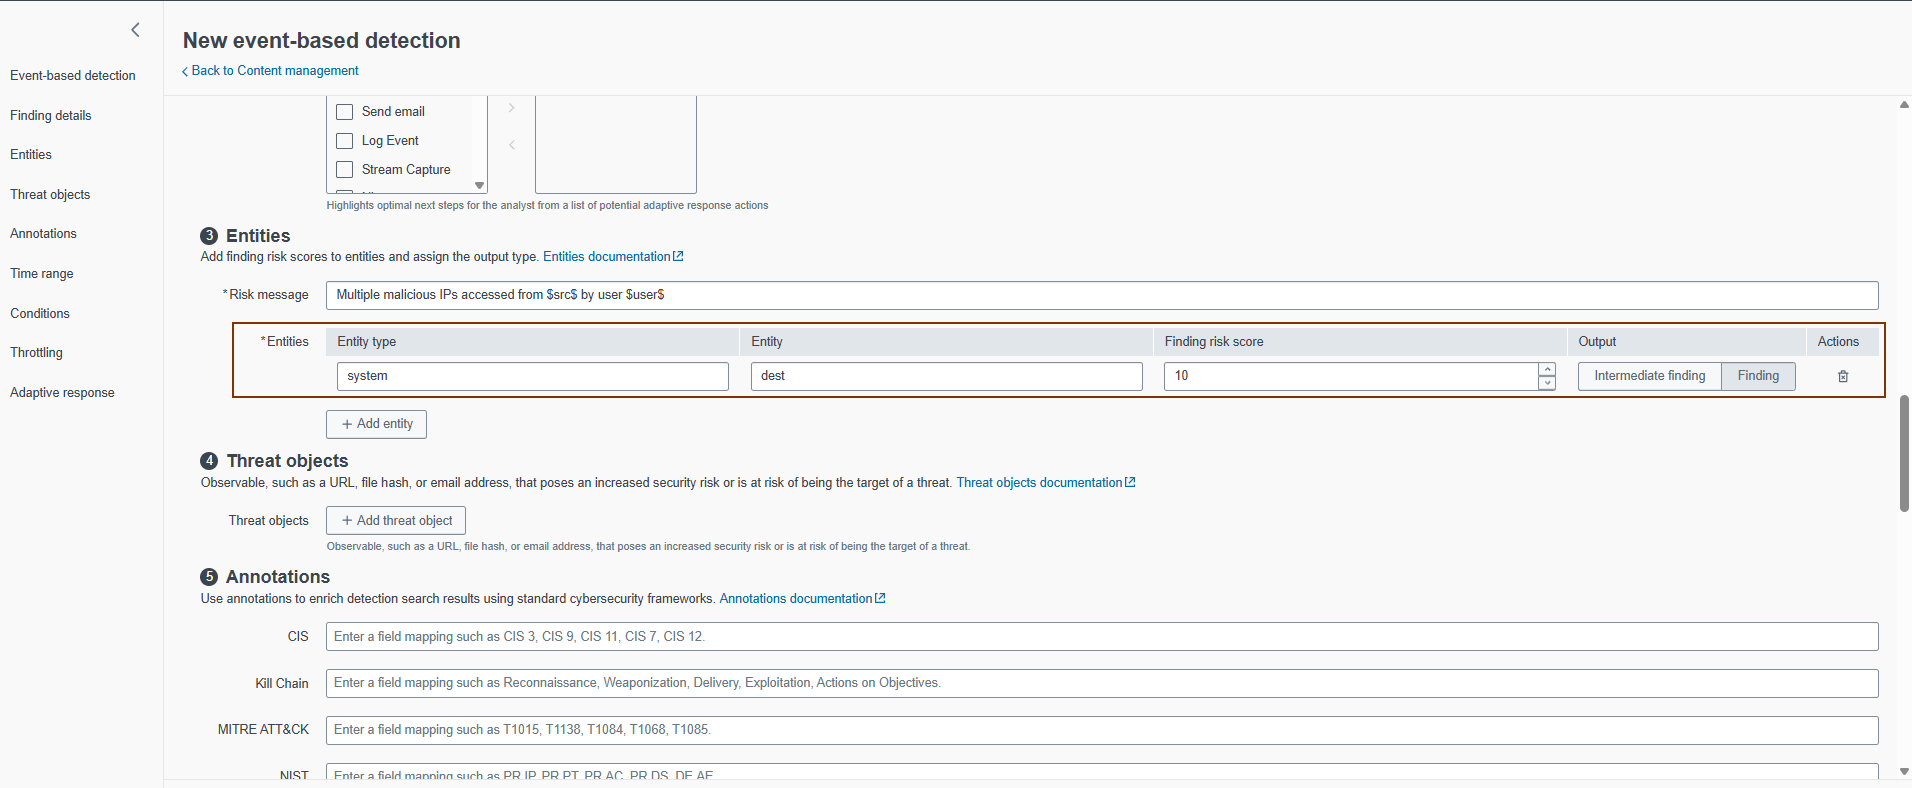
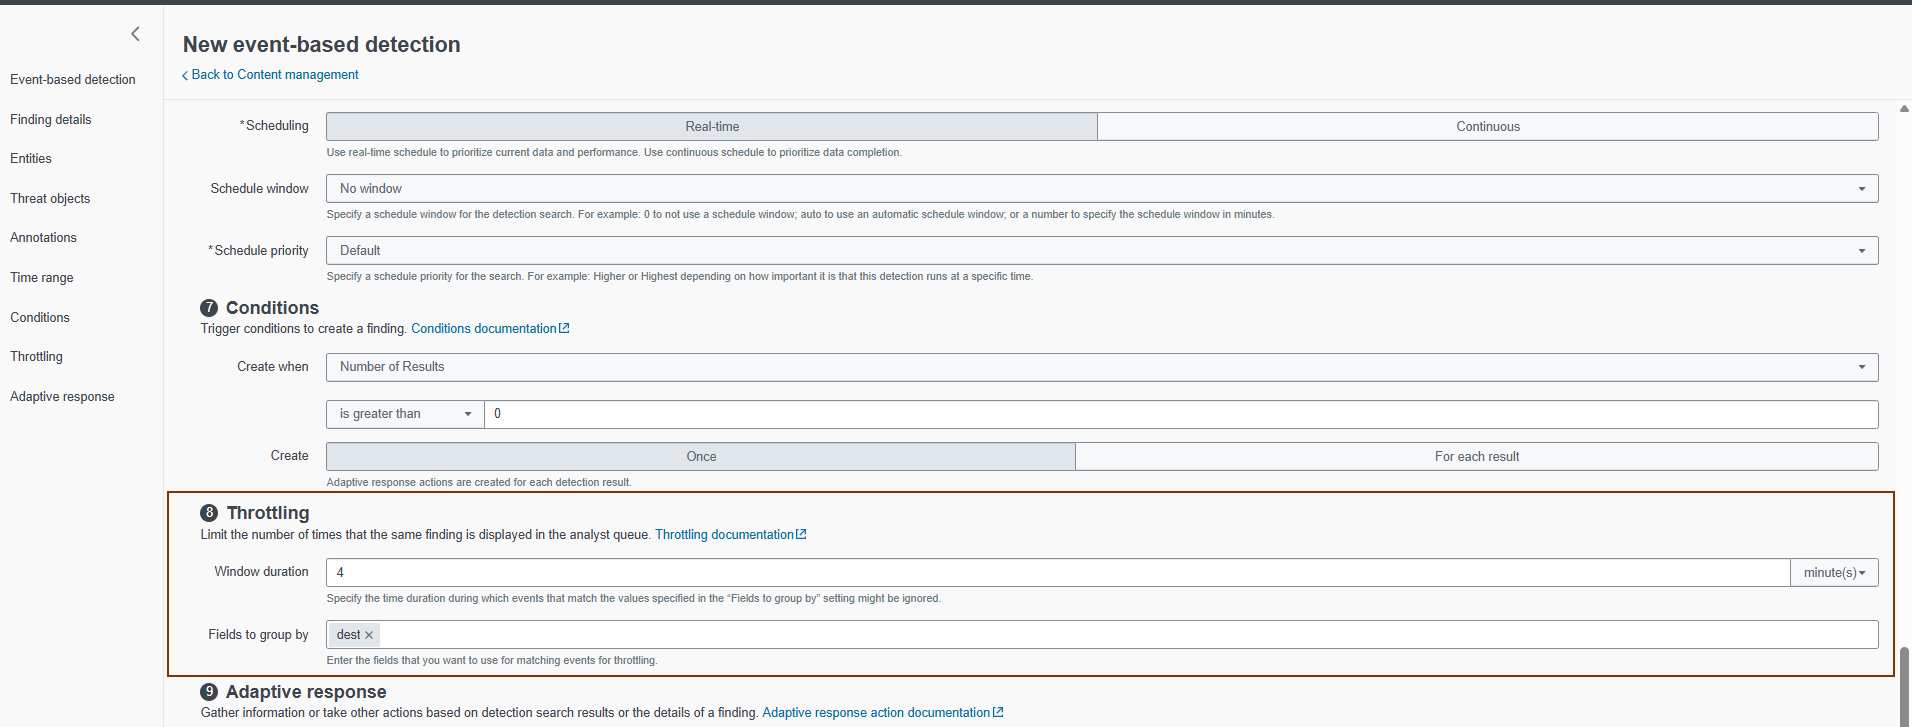
In the Event-Based Detection Editor, a multi-value field was configured to create findings, and throttling was set on the same multi-value field to reduce the noise of findings generated in the Mission Control Analyst Queue.
These findings appeared as separate entries in the Mission Control Analyst Queue; each associated with a different entity value in the entity field.
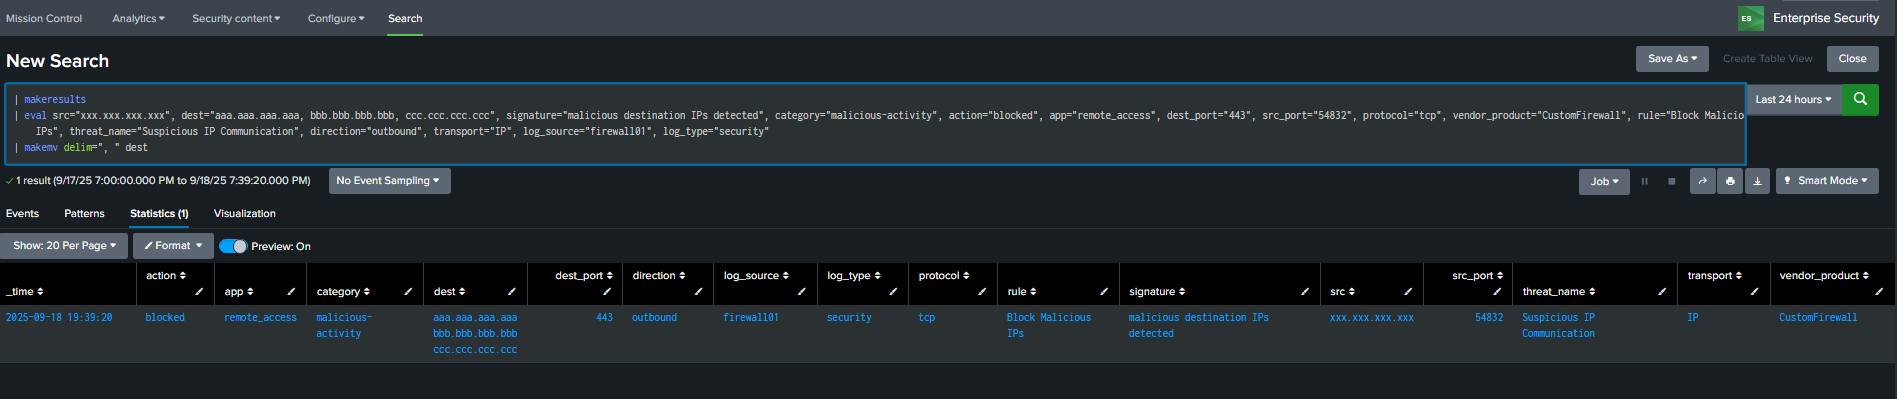
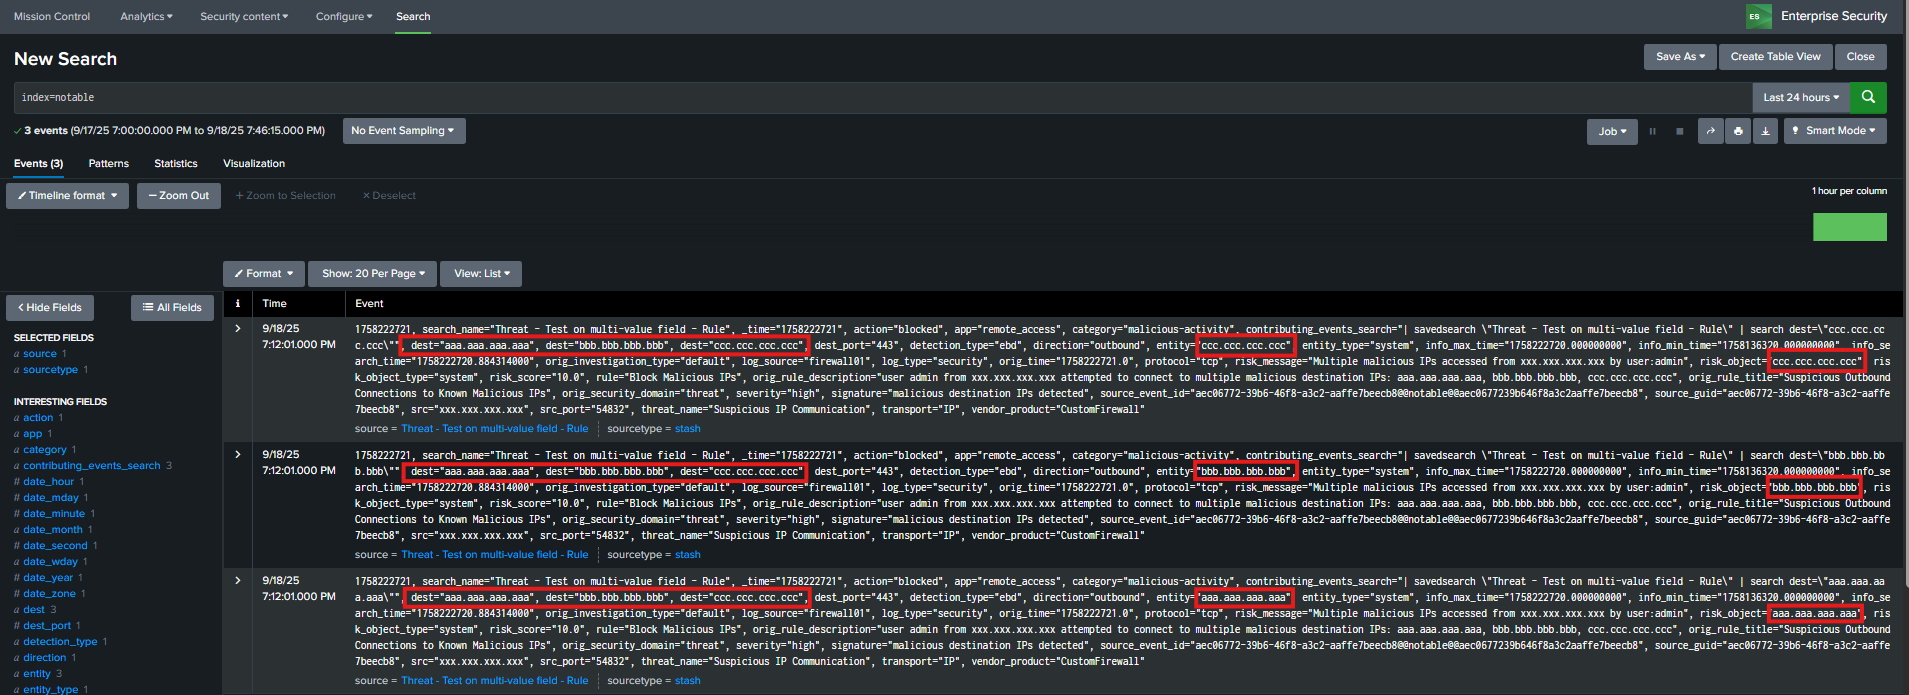
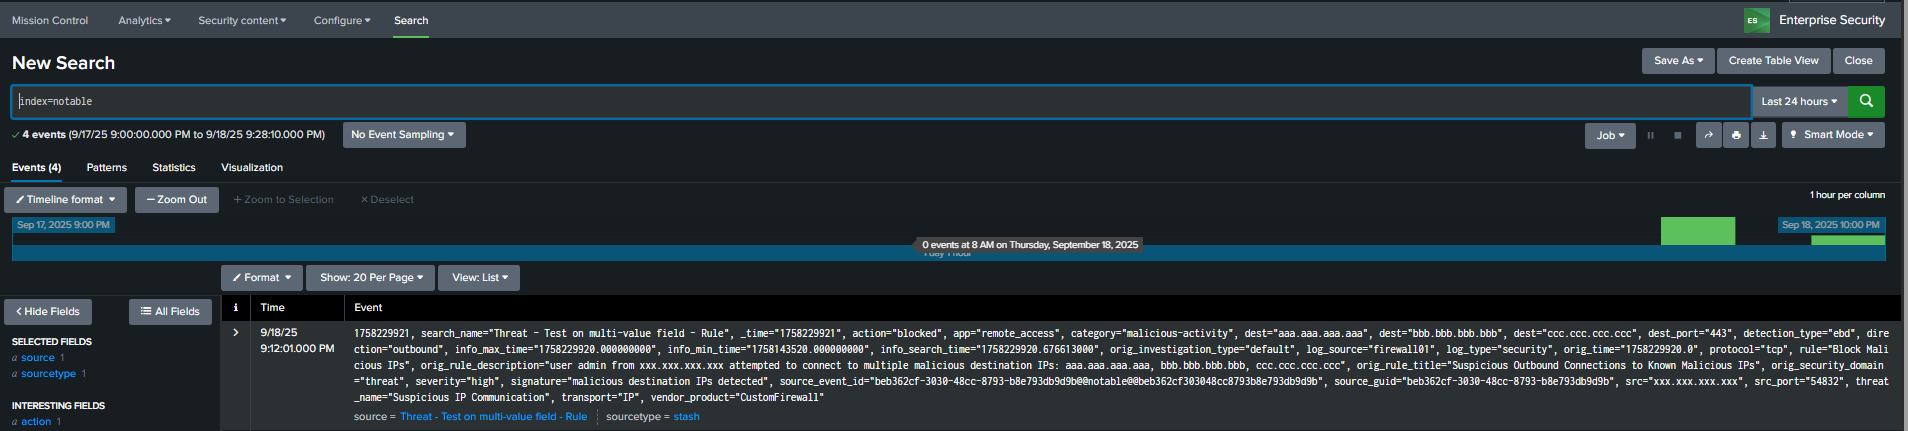
Further analysis of the notable index revealed that each value from the multi-value field was individually assigned to the entity field. As a result, multiple notables were created in Mission Control for a single detection at the same time.
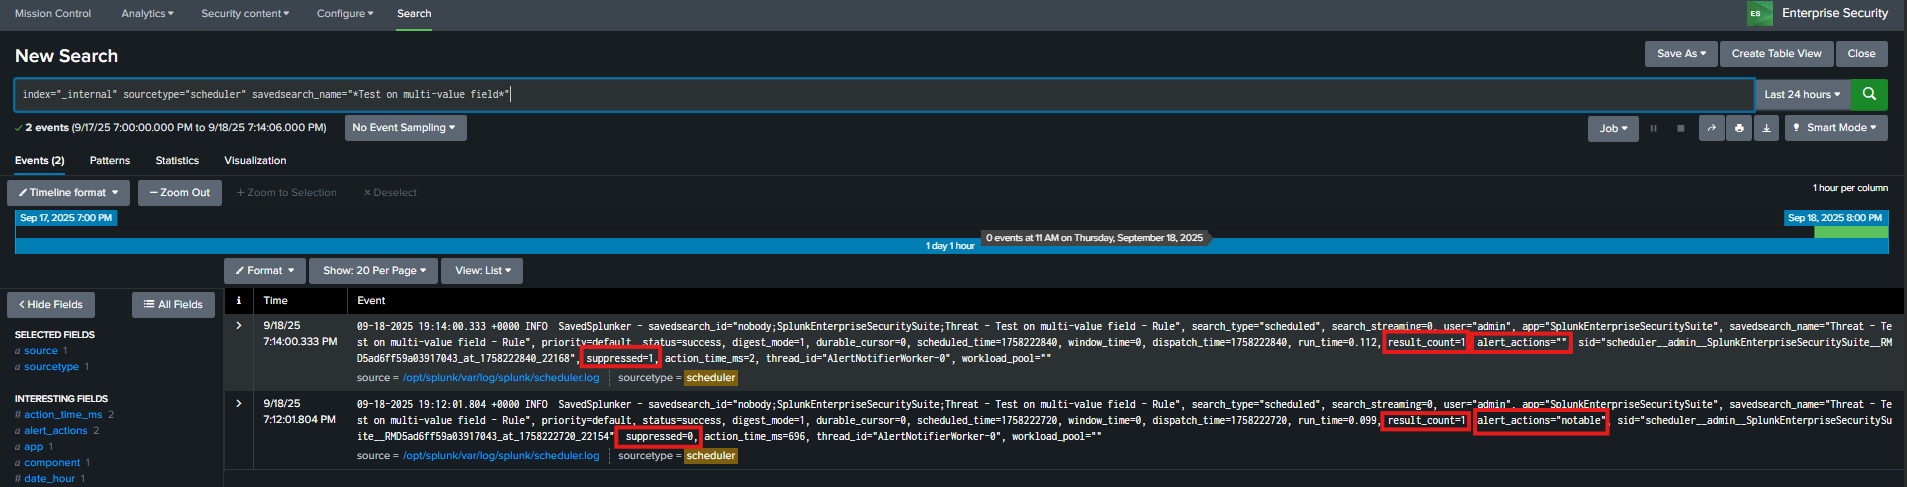
The _internal index was reviewed to confirm whether the findings were suppressed. The review confirmed that the event was suppressed as expected. However, because the entity changed with each value, separate findings were created in the notable index. This behavior explained why the Mission Control Analyst Queue displayed separate findings for a single event.
Resolution
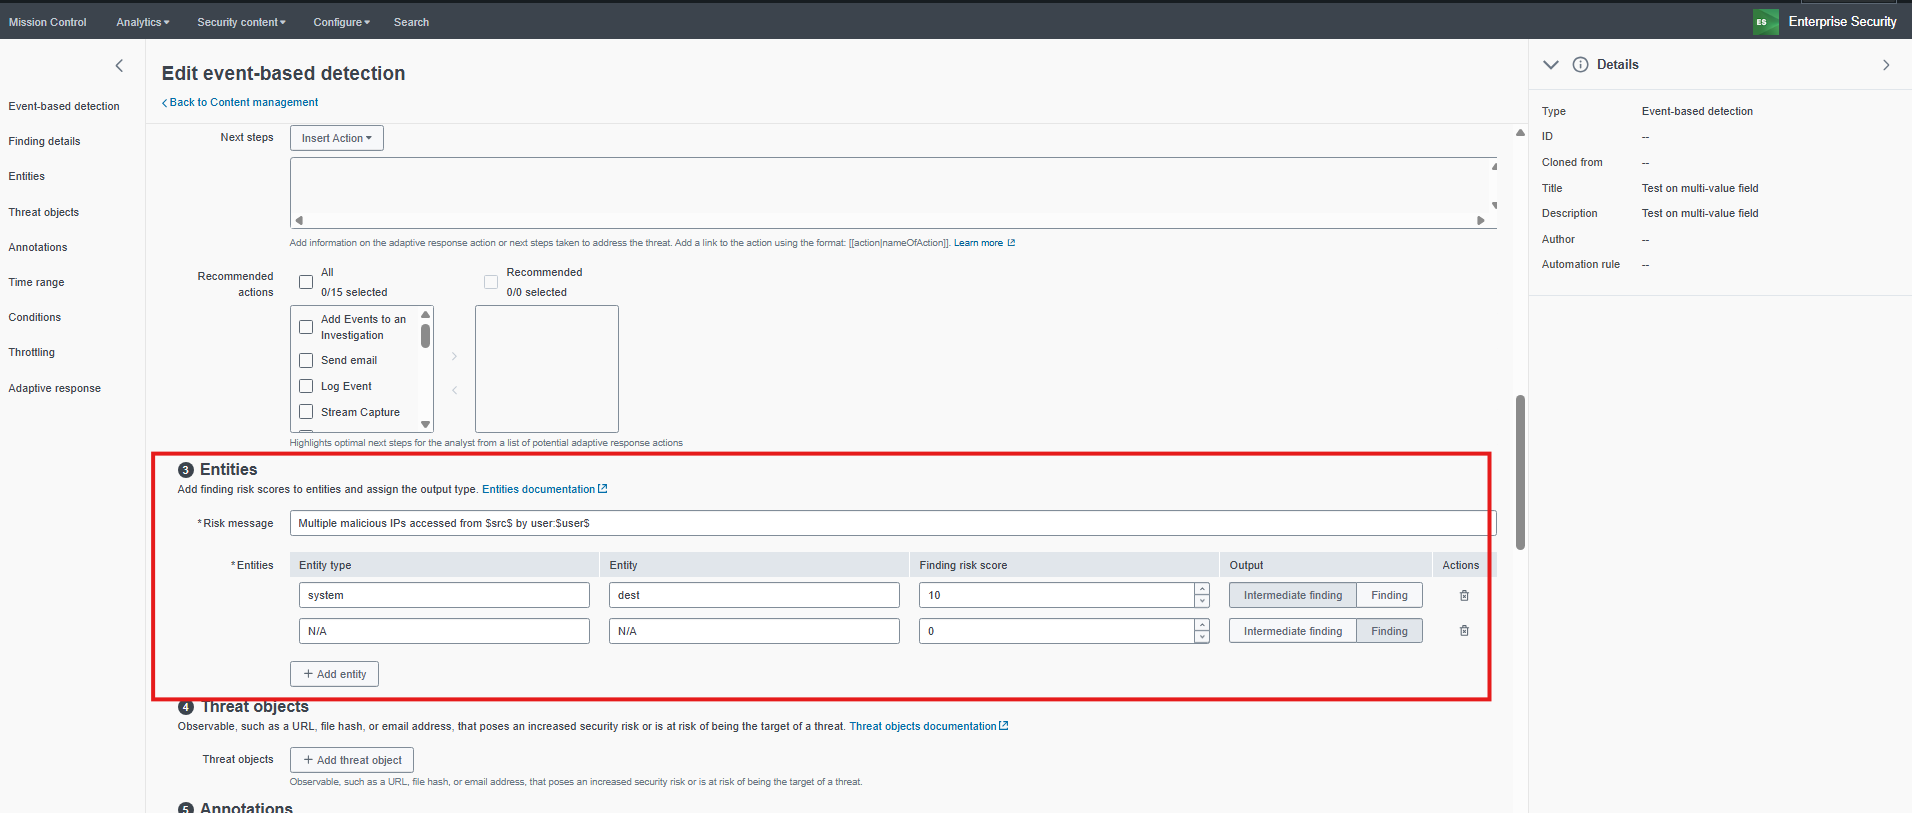
To overcome this, the multi-value field in the event was set as an intermediate finding, and the Entity Type and Entity fields were set to N/A to lower the number of findings created.
A review of the Scheduler logs showed that alerts were suppressed as expected. In the alert_actions field, two alert types were identified
- Notable (Finding)
- Risk (Intermediate Finding).
One entry showed suppressed=0, and the other entry showed suppressed=1.
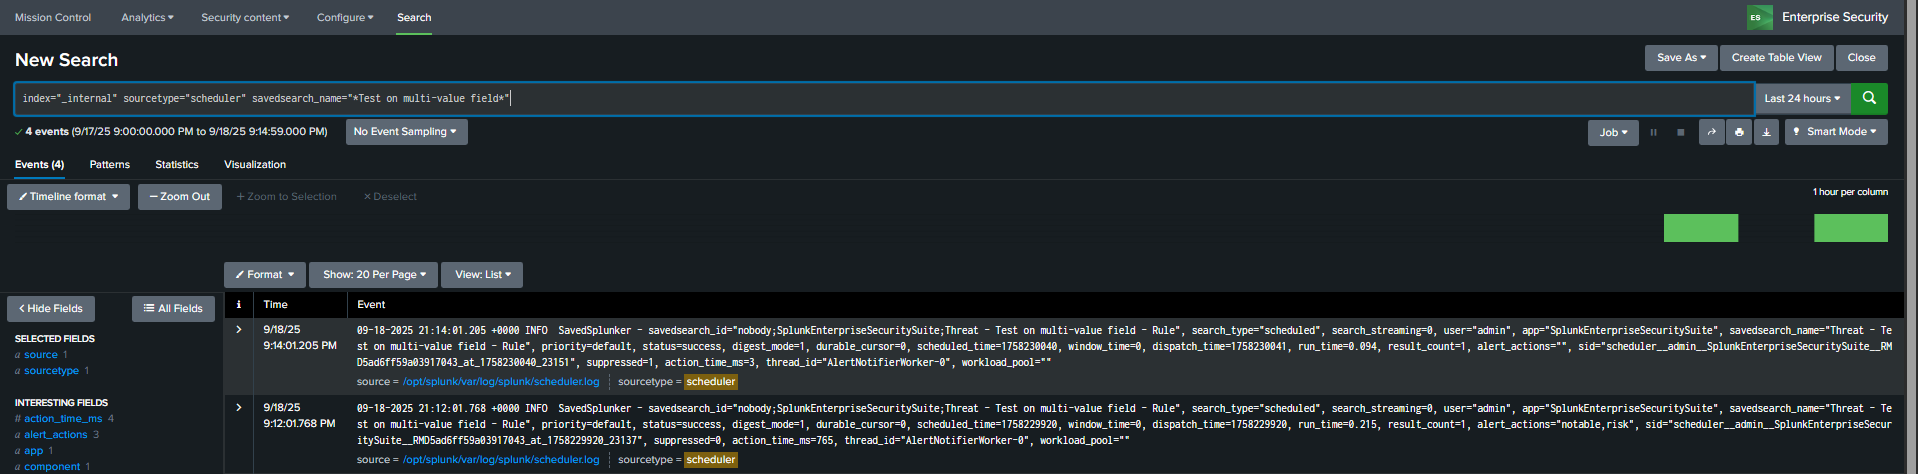
As the detection was configured to create one finding and use intermediate findings for each value in the multi-value field. This configuration reduced the number of notables created in the Mission Control Analyst Queue.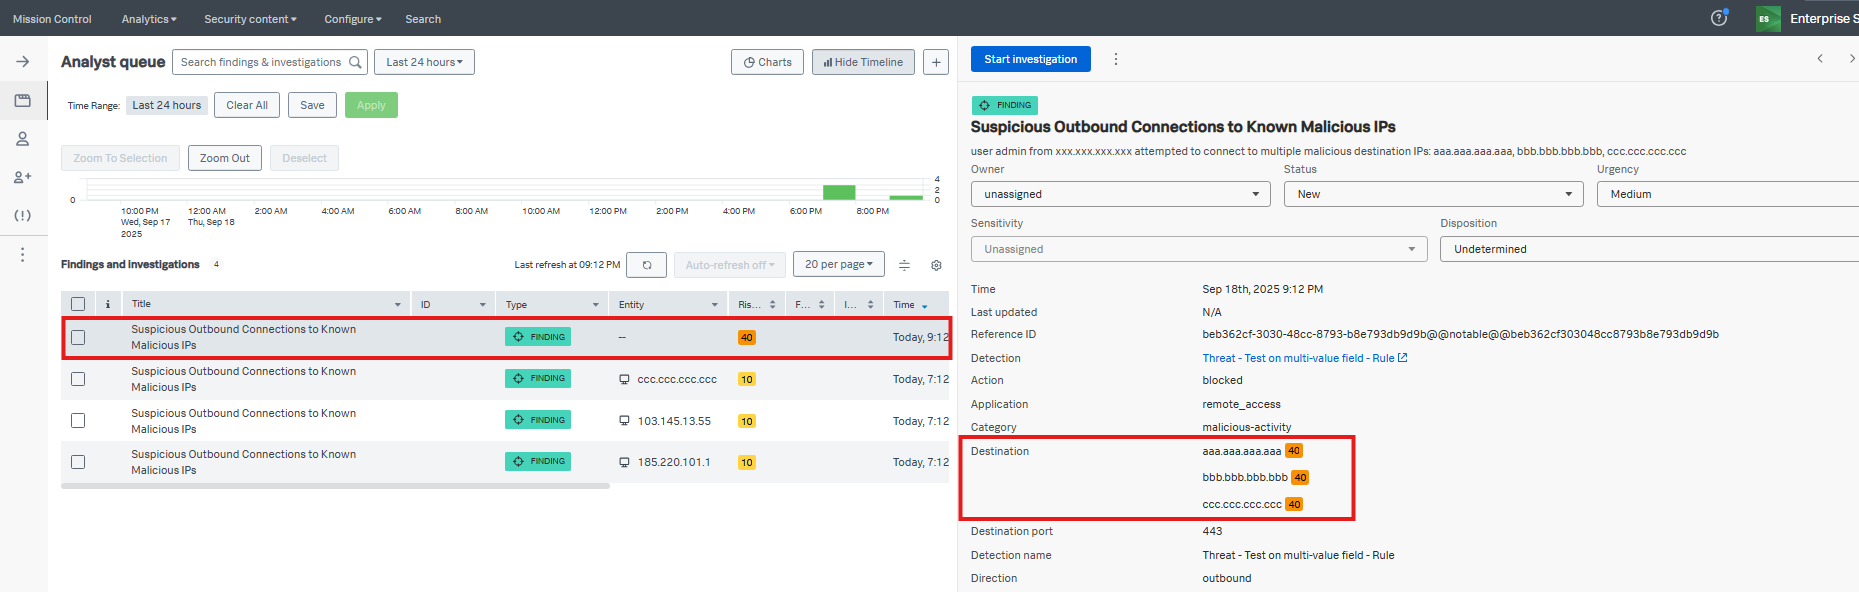
Related Links
Splunk Docs: Use detections to search for threats in Splunk Enterprise Security
Revision History
| Revision | Publish Date | Comments |
|---|---|---|
1.0 |
01-Oct-2026
|
Initial Release |
 Feedback
