Comment field is not available in Notable macro post upgrade to Enterprise Security 8.x.
Available Languages
Applicability
Splunk Enterprise Security 8.0.x.Description
In Enterprise Security (ES) version 8.x, the comments feature was deprecated.
Any comments added to an investigation are now displayed in the "Notes" section in the Analyst queue, as shown in the screenshot below.
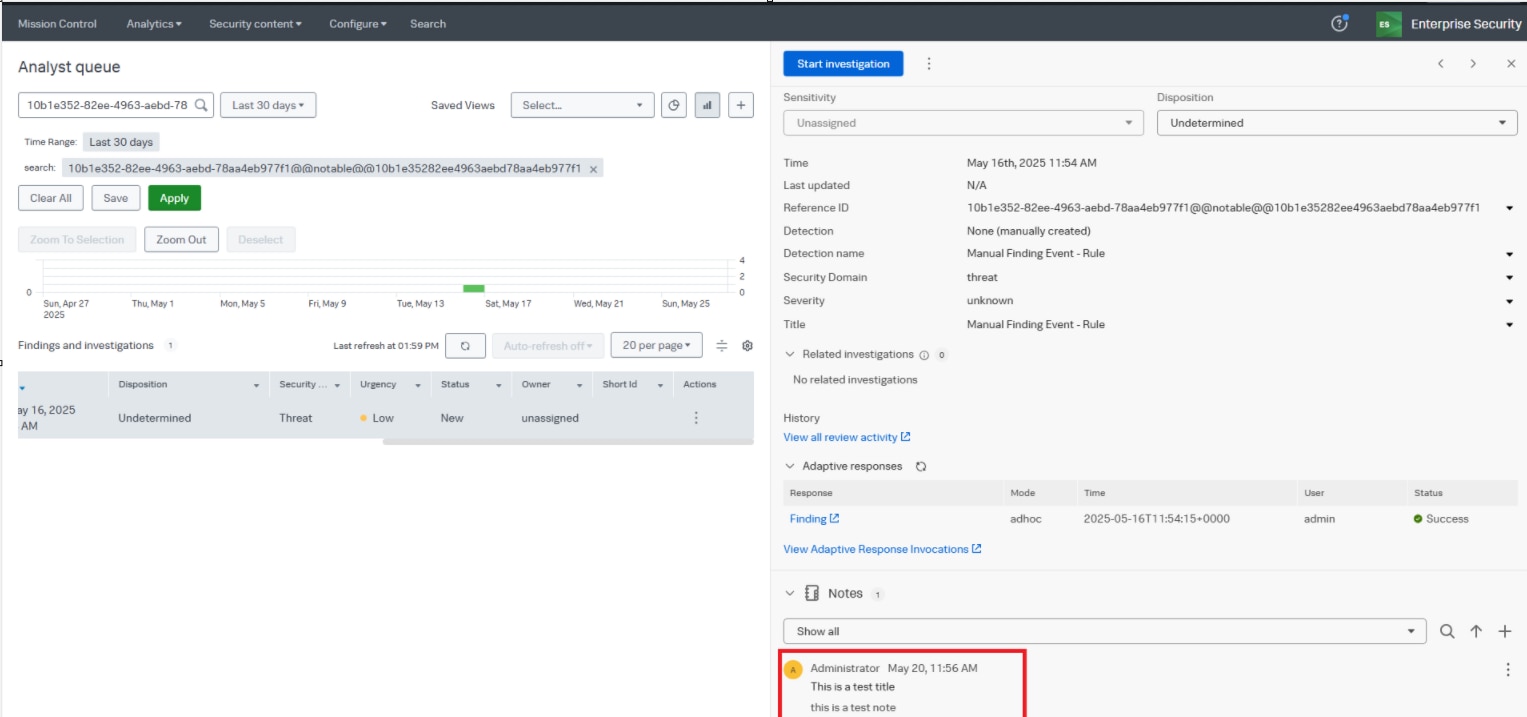
However, when executing the notable macro in the SPL for the same investigation using the "event_id," the comment field will appear empty.
The notes added to the investigation are not reflected in the comment field and cannot be retrieved or updated through it as shown below.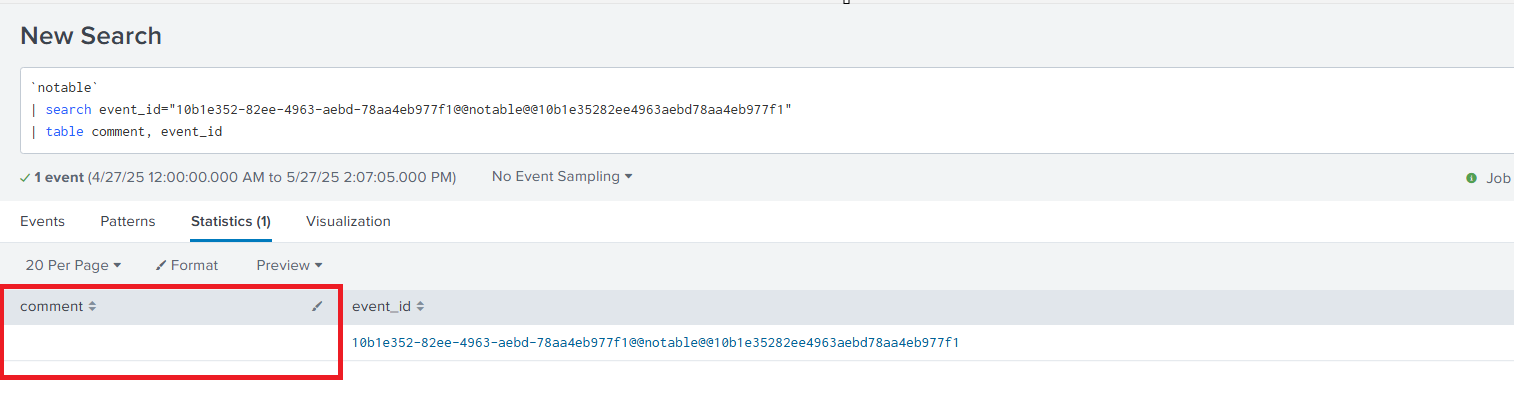
Investigation
Upon investigation it has been identified that the comment is no longer stored or can be retrieved from the notable macro.
-
It was observed that notes are being retrieved through the API in the Mission Control (Analyst Queue) dashboard, aligning with the current system design.
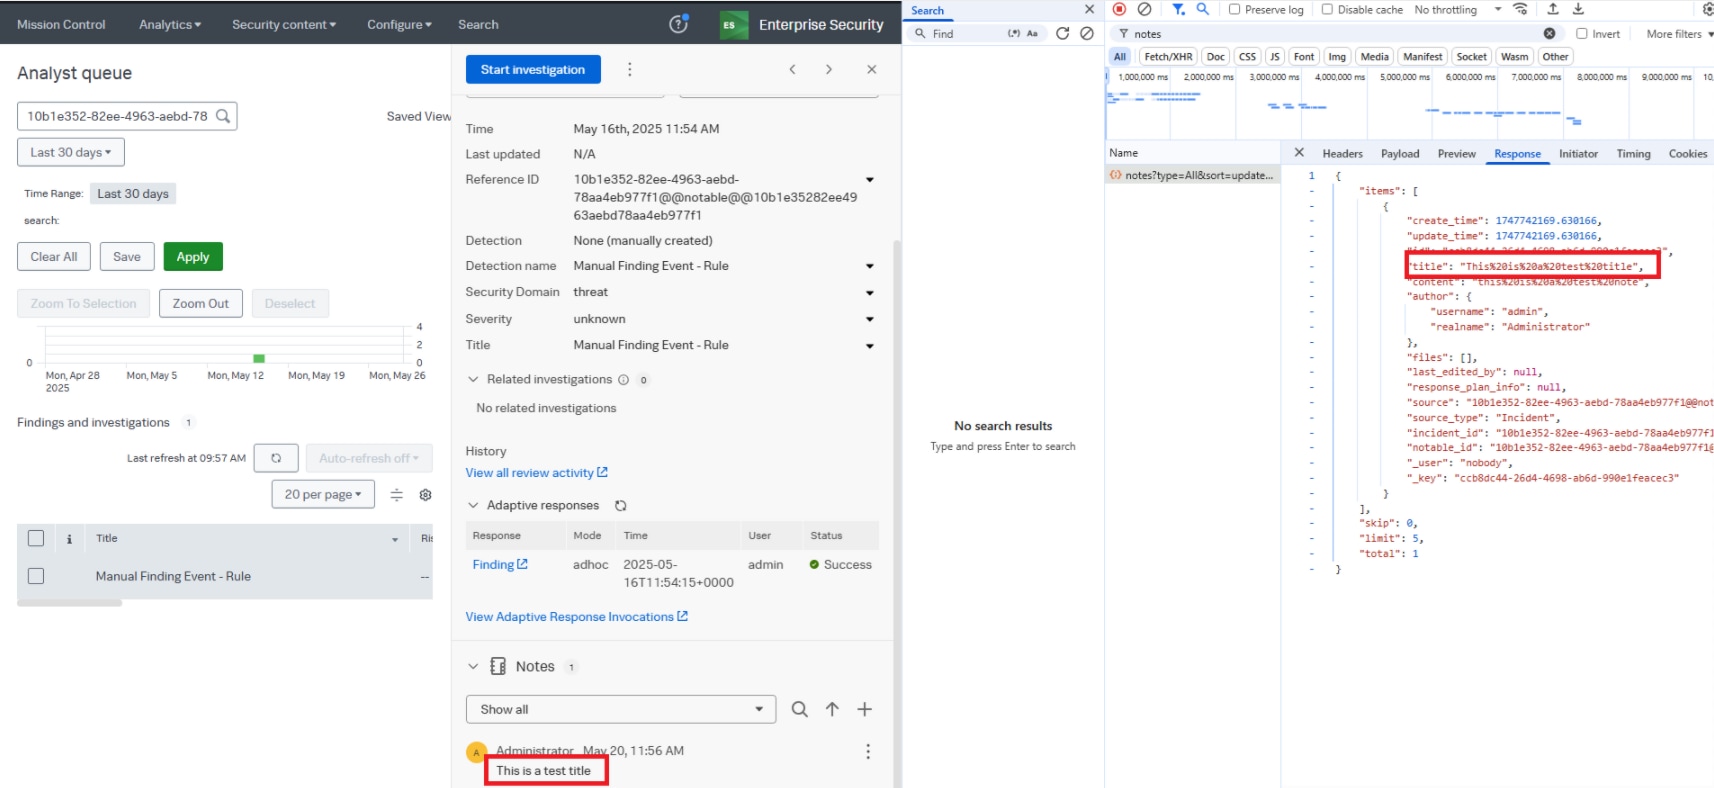
-
In the present version of the Enterprise security 8.0, comment values are not stored in any lookups or in the index.
Resolution
Workaround:
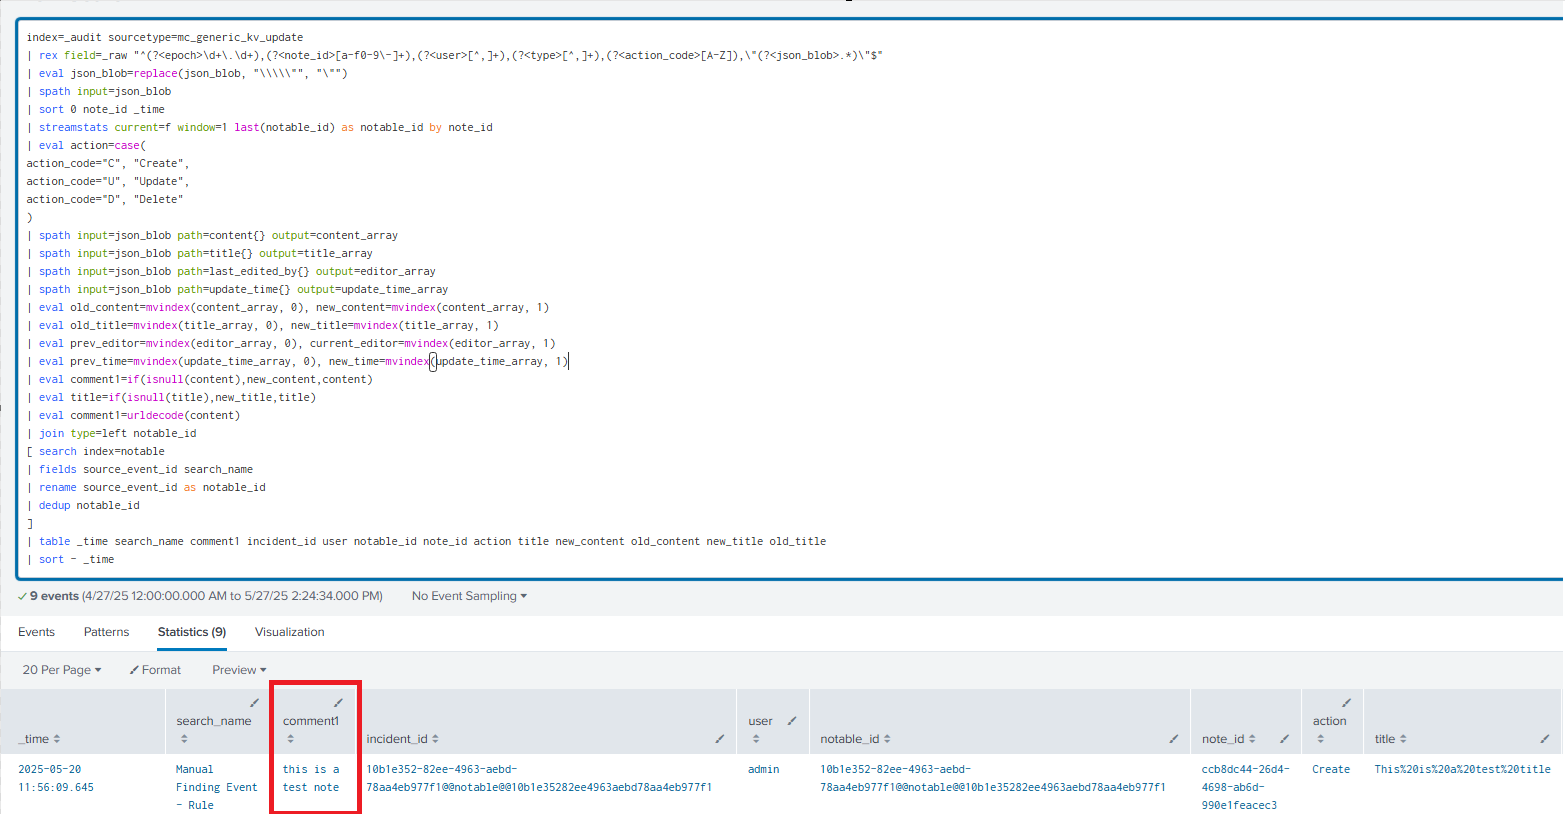
Below SPL can be used, which exposes the notes values along with the corresponding "search_name" and "event_id".
index=_audit sourcetype=mc_generic_kv_update
| rex field=_raw "^(?<epoch>\d+\.\d+),(?<note_id>[a-f0-9\-]+),(?<user>[^,]+),(?<type>[^,]+),(?<action_code>[A-Z]),\"(?<json_blob>.*)\"$"
| eval json_blob=replace(json_blob, "\\\\\"", "\"")
| spath input=json_blob
| sort 0 note_id _time
| streamstats current=f window=1 last(notable_id) as notable_id by note_id
| eval action=case(
action_code="C", "Create",
action_code="U", "Update",
action_code="D", "Delete"
)
| spath input=json_blob path=content{} output=content_array
| spath input=json_blob path=title{} output=title_array
| spath input=json_blob path=last_edited_by{} output=editor_array
| spath input=json_blob path=update_time{} output=update_time_array
| eval old_content=mvindex(content_array, 0), new_content=mvindex(content_array, 1)
| eval old_title=mvindex(title_array, 0), new_title=mvindex(title_array, 1)
| eval prev_editor=mvindex(editor_array, 0), current_editor=mvindex(editor_array, 1)
| eval prev_time=mvindex(update_time_array, 0), new_time=mvindex(update_time_array, 1)
| eval content=if(isnull(content),new_content,content)
| eval title=if(isnull(title),new_title,title)
| eval content=urldecode(content)
| join type=left notable_id
[ search index=notable
| fields source_event_id search_name
| rename source_event_id as notable_id
| dedup notable_id
]
| table _time search_name incident_id user notable_id note_id action title content new_content old_content new_title old_title
| sort - _time
Related Links
Release Notes: Enhanced capability to add notes.
Splunk Docs: Collaborate on investigations in Splunk Enterprise Security
Revision History
| Revision | Publish Date | Comments |
|---|---|---|
1.0 |
01-Oct-2026
|
Initial Release |
 Feedback
