Locate and view threat intelligence feed data in Splunk Enterprise Security
Available Languages
Applicability
Splunk Enterprise Security 7.x Splunk Enterprise Security 8.xDescription
Splunk Enterprise Security uses threat intelligence feeds to correlate Indicators of Compromise (IOCs) with ingested data to identify potential threats. These feeds are automatically downloaded, processed, and stored in KV Store lookups by threat list modular inputs. This article explains how to enable threat intelligence feeds and locate the corresponding lookups to review the stored indicator values.
Resolution
Enable Threat Intelligence Feeds
- Navigate to the appropriate menu based on the Enterprise Security version:
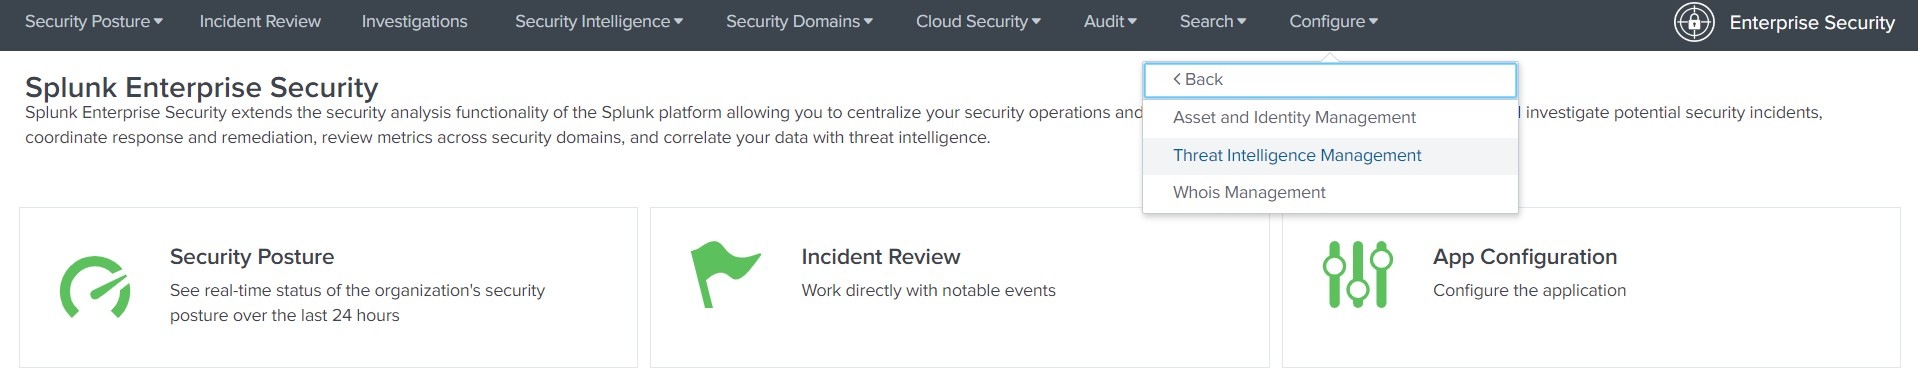
Enterprise Security 7.x > Configure > Data Enrichment > Threat Intelligence Management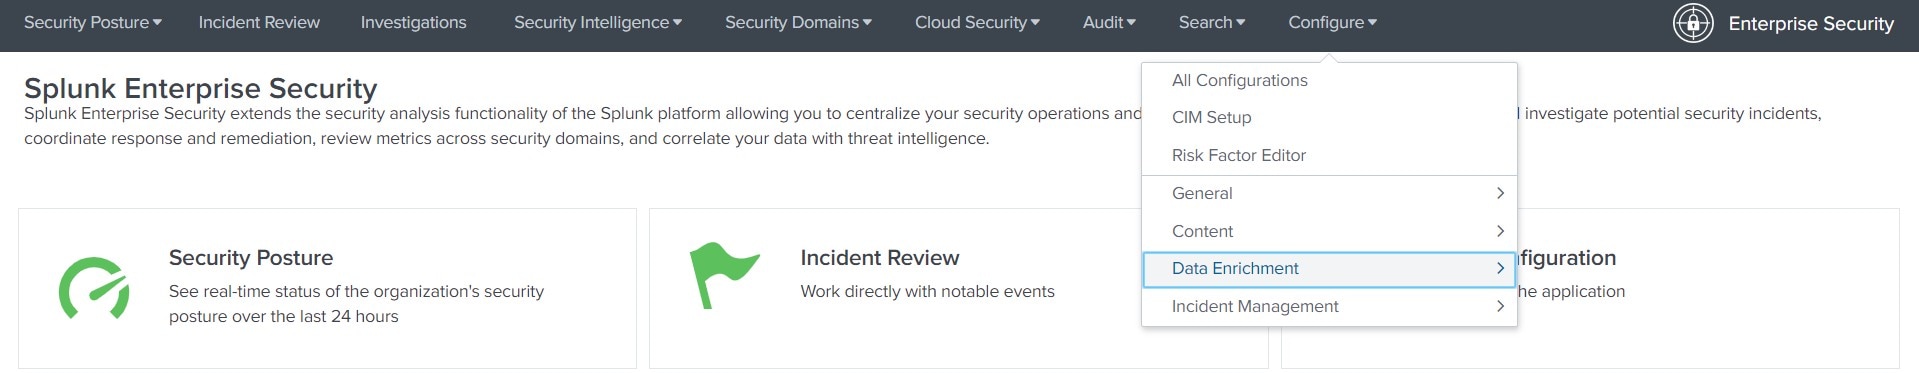
Enterprise Security 8.x > Configure > Threat Intelligence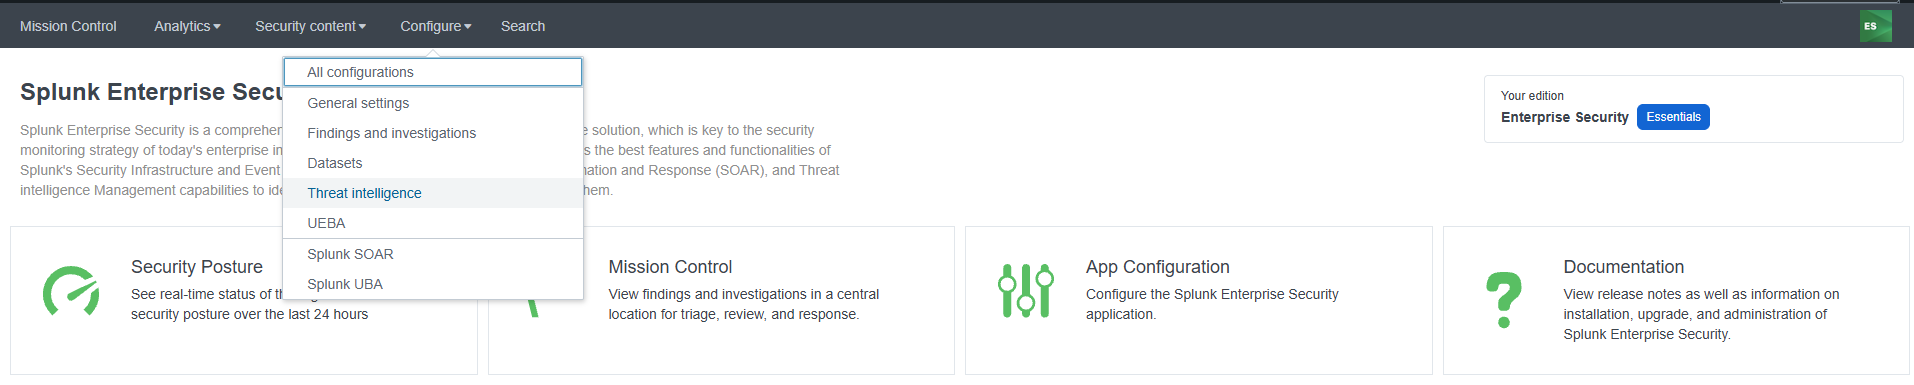
- Enable the required threat intelligence feeds.
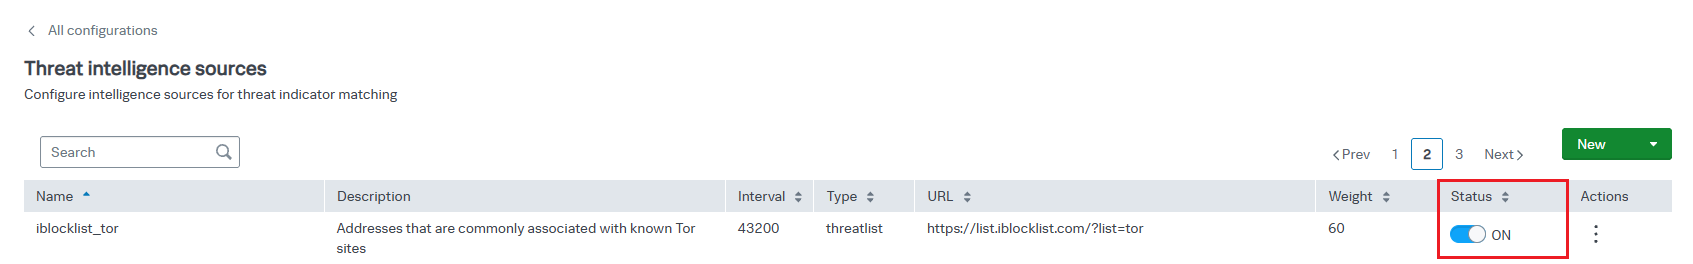
- Allow sufficient time for the feeds to download and process.
Locate Threat Intelligence Data
- Search the lookup that corresponds to the enabled threat intelligence feed:
IP address indicators are stored in the ip_intel lookup.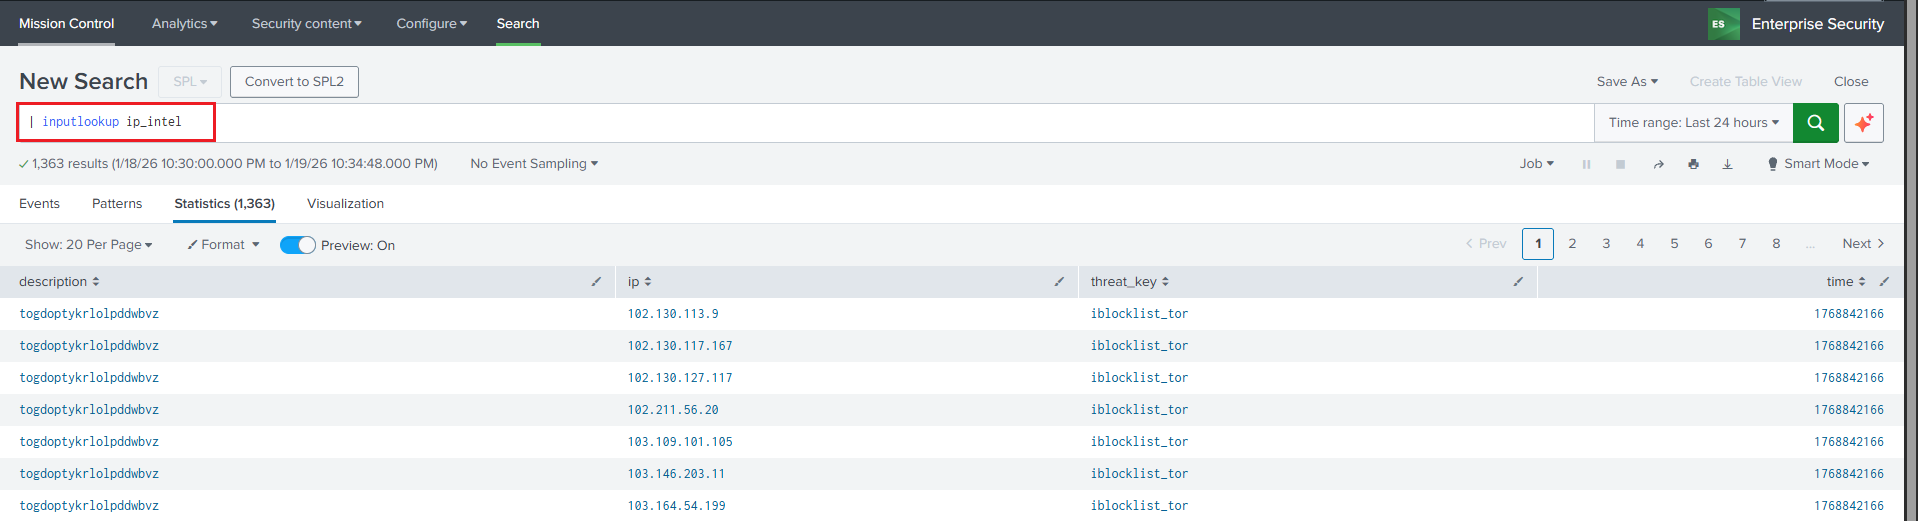
- Other indicator types, such as domains, URLs, file hases are stored in different lookup such as http_intel, file_intel lookups.
Related Links
Overview Of Threat Intelligence in Splunk Enterprise Security
Revision History
| Revision | Publish Date | Comments |
|---|---|---|
1.0 |
29-Sep-2026
|
Initial Release |
 Feedback
