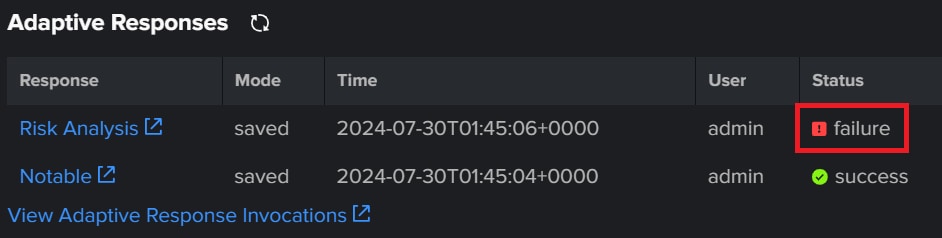
In Risk Analysis, the status shows failure in the Adaptive Responses on the Incident Review (IR) page.
Available Languages
Applicability
Splunk Enterprise SecurityDescription
The Risk Analysis in Splunk Enterprise Security uses Adaptive Response Actions to automate response based on notable events and the Risk Analysis process may fail, causing the status to be reported as failure on the Incident Review (IR) page.
Investigation
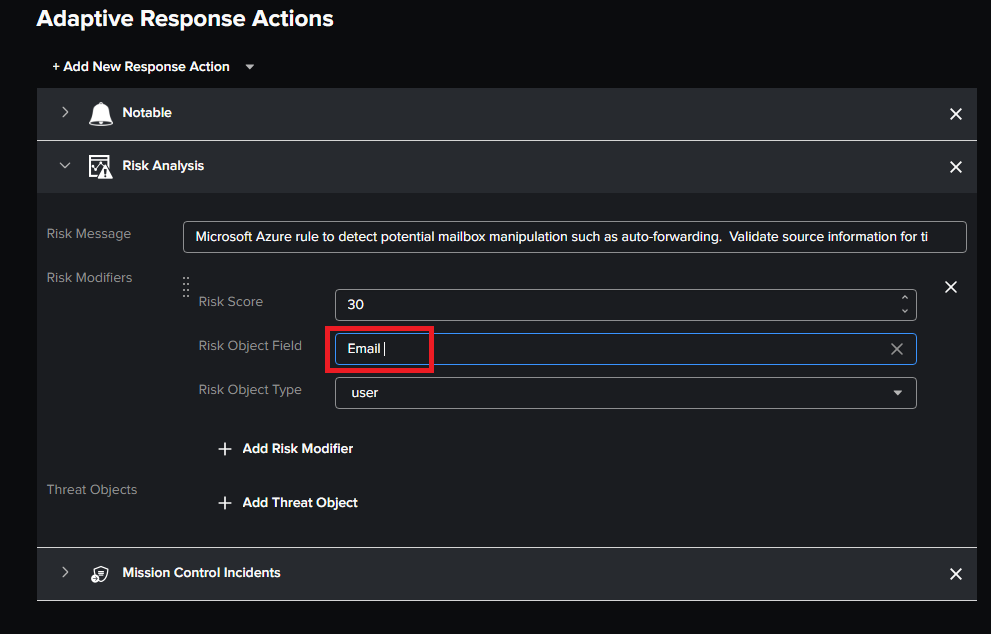
Investigated the Risk Analysis Adaptive Response Action configuration of the "email" field to see if there are extra spaces or formatting issues.
Resolution
- To resolve this issue of the Risk Analysis status always showing failure.
- Ensure that all filed names are correct.
Edit the Risk Analysis Adaptive Response action:
- Navigate to Splunk Enterprise Security > Configure > Content > Content Management > Find the correlation search > Adaptive Response
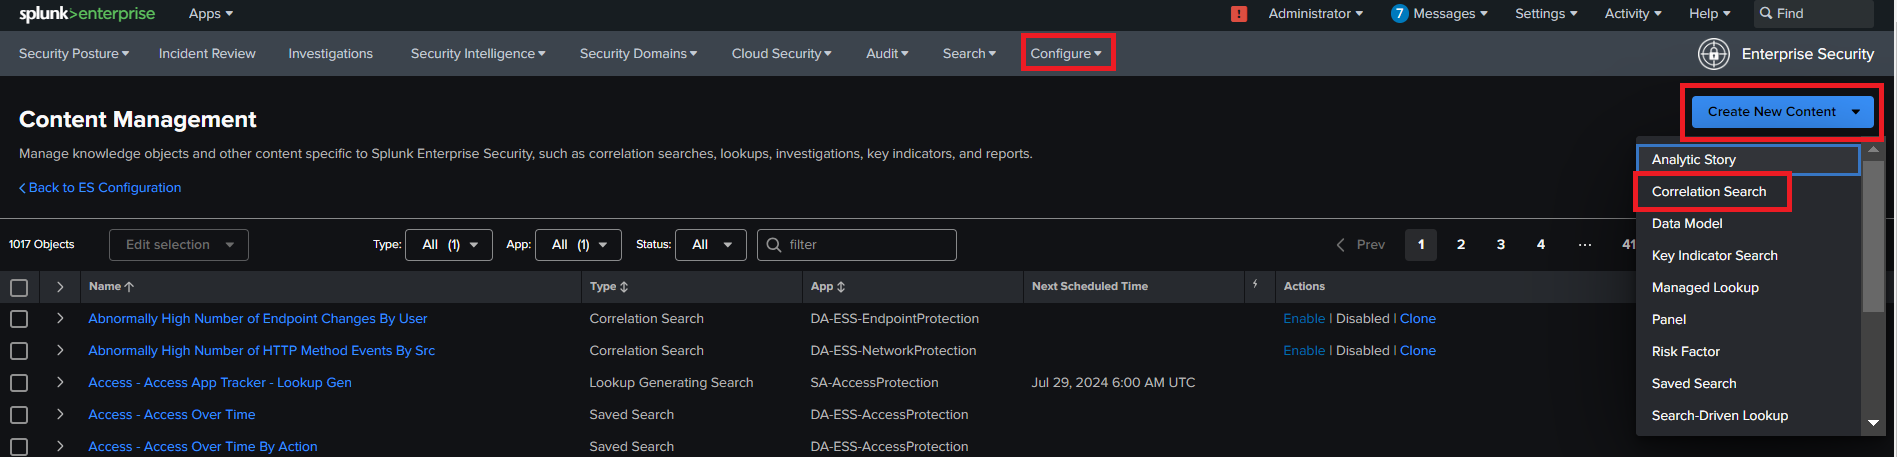
- Find the Specific Adaptive Response Action used for Risk Analysis.
- Locate the "email" field in the Adaptive Response Action Configuration.
- Ensure that there are no extra spaces before or after the email addresses.
- Ensure the email addresses are correctly formatted and separated by commas if multiple addresses are specified.
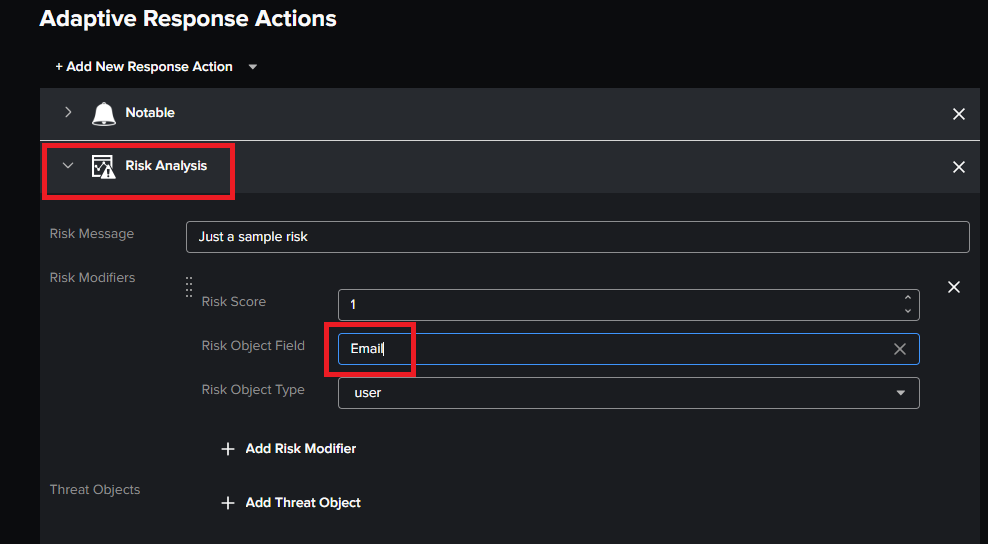
- Click Save to save the correlation search
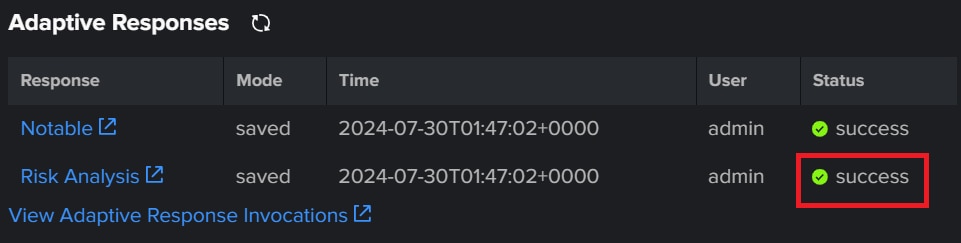
- Success response after removing the extra spaces from the Risk Field.
Related Links
Revision History
| Revision | Publish Date | Comments |
|---|---|---|
1.0 |
29-Sep-2026
|
Initial Release |
 Feedback
