Correlation Search creation in Enterprise Security through REST API
Available Languages
Applicability
Splunk Enterprise SecurityDescription
Correlation Searches in Enterprise Security can be created in the following ways,
- Splunk Web UI
- REST API.
The Correlation Search creation and configuration via Splunk Web UI was simple.
But in the case of Correlation Search configuration using the REST API has a set of criteria and limitations.
Resolution
Steps to be followed to configure a Correlation search using the REST API.
Curl Command was used to create a correlation search in the Enterprise Security app,
curl -k -u username:password -X POST https://localhost:8089/servicesNS/admin/SplunkEnterpriseSecuritySuite/saved/searches -d name="Sample_CS_API_Created_By_API" -d action.correlationsearch.enabled=1 -d action.correlationsearch.label="Label for your correlation search" -d action.correlationsearch.related_search=" search index="_internal"
| head 1 " -d search="index=_"internal"
| head 1" -d action.correlationsearch.schedule_priority=10 -d action.correlationsearch.schedule_window=60 -d cron_schedule="*/5 * * * *" -d actions="notable" -d action.notable.param.severity="low" -d action.notable.param.rule_description="This is a test correlation search" -d action.correlationsearch.throttle=1 -d action.correlationsearch.label="Risk_Analysis_search" -d action.customsearchbuilder.enabled=false -d action.makestreams.param.verbose=0 -d action.nbtstat.param.verbose=0 -d action.notable.param.verbose=0 -d action.nslookup.param.verbose=0 -d action.ping.param.verbose=0 -d action.risk=1 -d action.risk.forceCsvResults=1 -d action.risk.param._risk=
    [ {"risk_object_field":"user","risk_object_type":"user","risk_score":30}] -d action.risk.param._risk_message=$message$ -d action.risk.param._risk_score=0 -d alert.suppress=0 -d alert.track=1
By using the above curl command the Correlation Search can be created, however, while creating the correlation search by REST API.
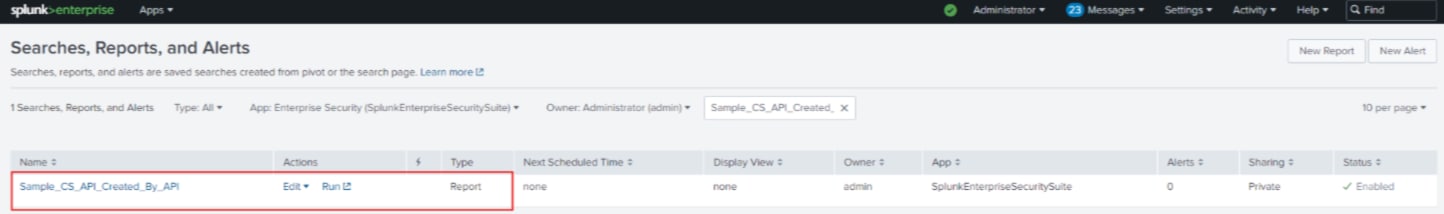
Limitation: The Correlation Search will be created as a "Report" not as an Alert.
Related Links
Revision History
| Revision | Publish Date | Comments |
|---|---|---|
1.0 |
29-Sep-2026
|
Initial Release |
 Feedback
