Network related KPI's based on Unix and Linux Add-On shows "N/A"
Available Languages
Applicability
Splunk IT Service Intelligence, Splunk Add-On for Unix and LinuxDescription
The KPI's "Network RCV KBps" and "Network Txmt KBps" shows the values as "N/A" when the metric fields do present in the "itsi_im_metrics" index which is receiving the data from Splunk Add-On for Unix and Linux.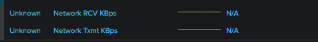
Investigation
While looking into the KPI search for both the KPIs, the search was configured to fetch the logs from the event index rather than the metric index.
Example of the SPL of the KPI's:
index="windows" OR index="perfmon"
The event indexes is configured for storing the event logs rather than the metric logs was present in these indexes.
As the network interface data relies on metric data, the metric inputs which are enabled has the data forwarded to the "itsi_im_metrics" index which is a metric index. This is the reason for the KPI values being "N/A".
Resolution
To resolve this issue, the KPI search was changed to metric search from adhoc search in the KPI base search where the required index name and the metric name was provided for the KPIs with the required threshold field.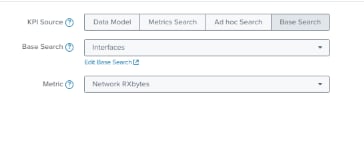
After making the required changes, the values were properly calculated for the KPI's based on the metric field.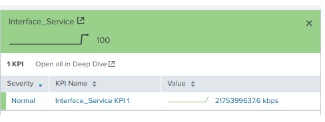
Related Links
Define a source search from a metrics search
Revision History
| Revision | Publish Date | Comments |
|---|---|---|
1.0 |
29-Sep-2026
|
Initial Release |
 Feedback
