Episodes created from the same correlation search are breaking into multiple episodes.
Available Languages
Applicability
Splunk IT Service IntelligenceDescription
Multiple episodes are created from the same correlation search and the NEAP (Notable Event Aggregation Policy) instead of grouping into single episode.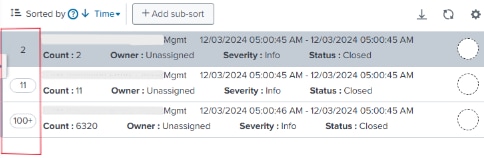
It leads to the creation of multiple external tickets which is not the intended behavior for this configuration.
Investigation
While looking into the NEAP policy of these episodes, the "event_identifier_string" was mentioned in the "Split events into multiple episodes by" field in the "Filtering Criteria and Instructions" tab of the NEAP policy.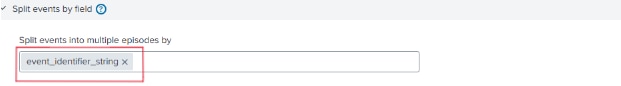
The "event_identifier_string" is different for the episodes created from this NEAP policy while checking the "itsi_grouped_alerts" index with the respective episode id.
Episode No 1: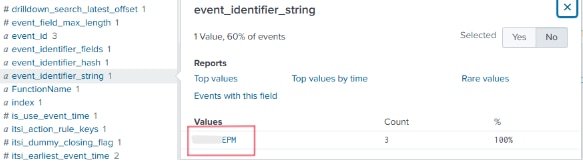
Episode No 2: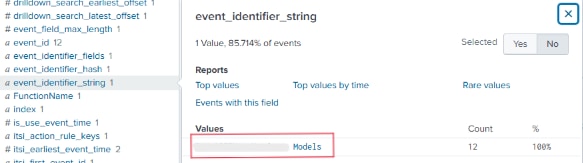
The difference in the "event_identifier_string" is the reason for the notable events to split into multiple episodes instead of grouping the events in the same episode.
Resolution
To resolve this issue, the "event_identifier_string" field was removed from the "Split events into multiple episodes by" field in the NEAP policy.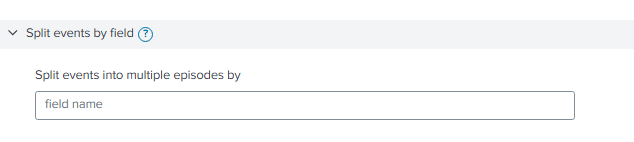
After removing the field, the notable events from the correlation search were grouped into single episode as expected.
Related Links
Notable Event Aggregation Policy - Splunk Documentation
Revision History
| Revision | Publish Date | Comments |
|---|---|---|
1.0 |
29-Sep-2026
|
Initial Release |
 Feedback
