"itsi_entities" lookup fails to match with uppercase entities
Available Languages
Applicability
Splunk IT Service IntelligenceDescription
Two entities exist in ITSI with the same configuration, but in different cases (one lowercase, one uppercase). 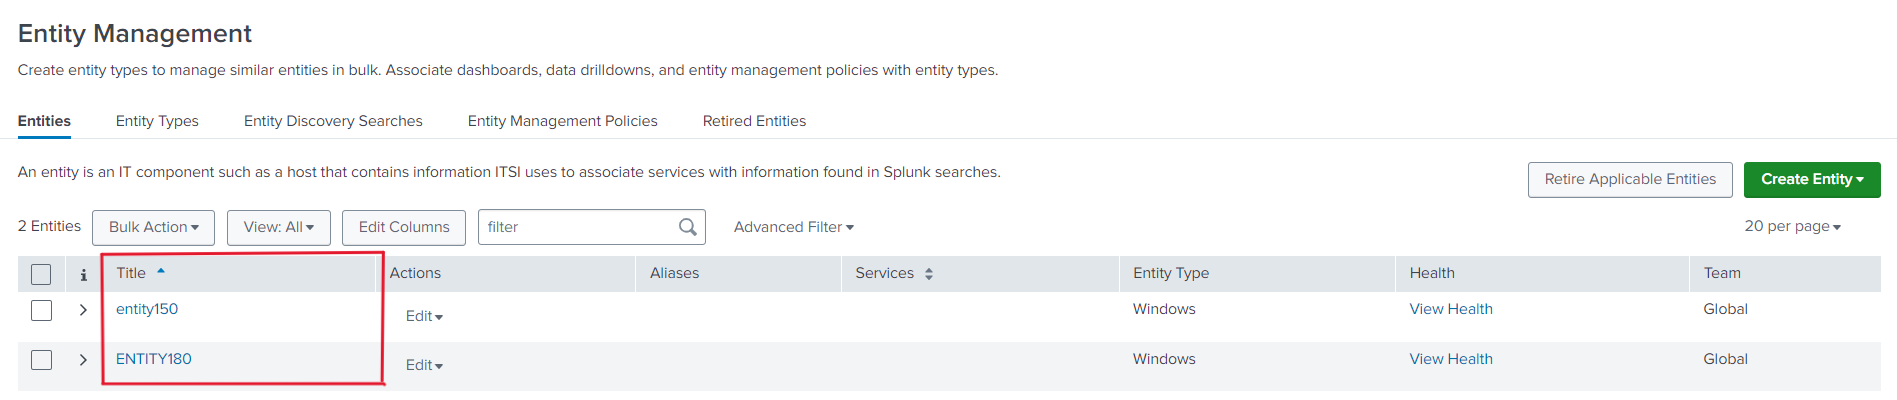
When searching for the entity title using the search irrespective of case sensitivity, different results were obtained
Lowercase entity: Lookup via "itsi_entities" returns information as expected for the entity "entity150" which is created in lowercase.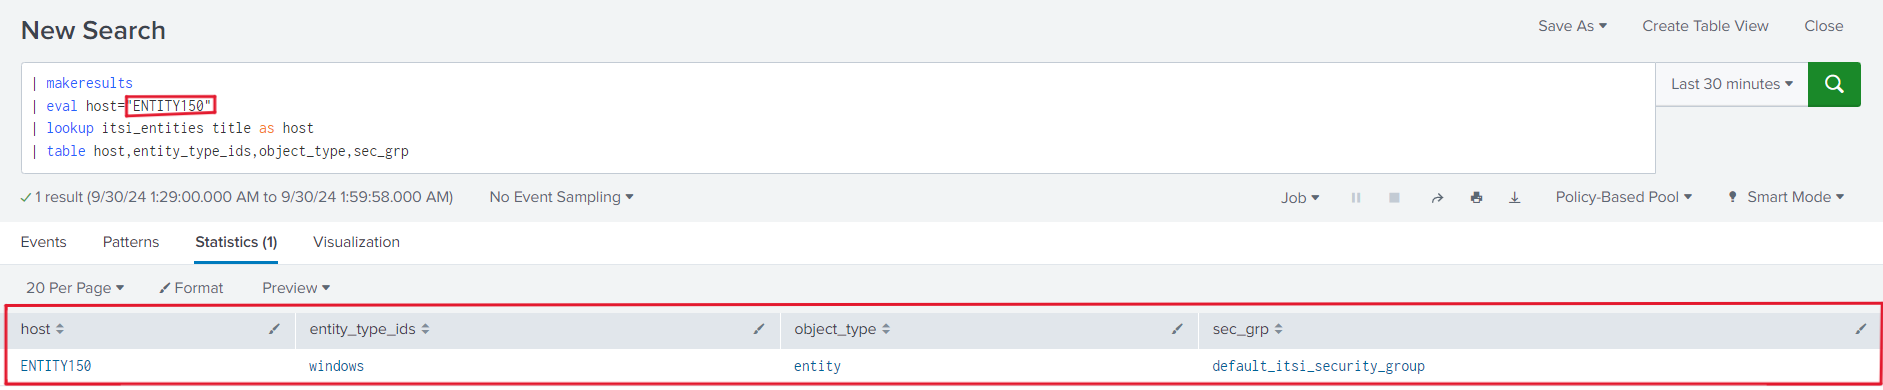
Uppercase entity: Lookup via "itsi_entities" returns no information for the entity "ENTITY180" which is created in uppercase.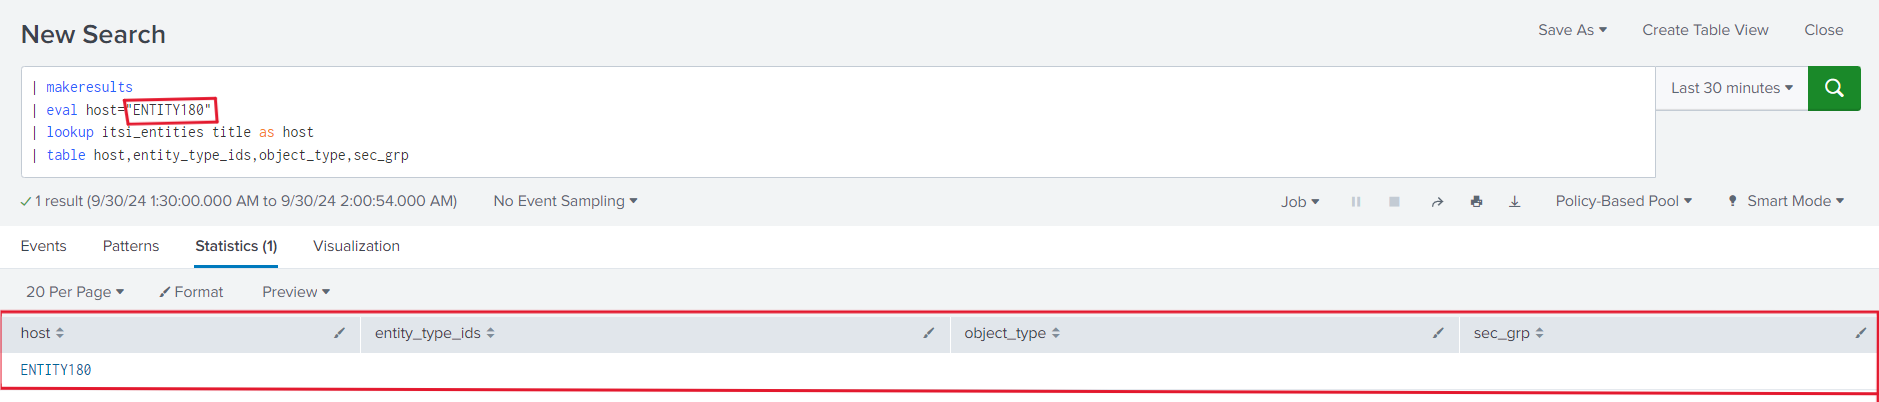
This suggests a case-sensitivity issue in the lookup process.
Investigation
When examining the configuration for lookup tables in
$SPLUNK_HOME/etc/apps/SA-ITOA/default/transforms.conf
it was found that the "case_sensitive_match" setting is set to false for the "itsi_entities" lookup.
[itsi_entities]
external_type = kvstore
collection = itsi_services
fields_list = _key, title, identifier.values, informational.values, informational.fields, services._key, in_maintenance, sec_grp, _itsi_identifier_lookups, _itsi_informational_lookups, Cloud, entity_type, entity_type_ids, sai_entity_key, _status, _itsi_entity_status_lookups, retired, retirable, last_retired, retiring_policy
filter = object_type="entity"
max_matches = 1
case_sensitive_match = false
The "case_sensitive_match" parameter has specific conditions:
If set to true: Splunk performs case-sensitive matching for all fields in a lookup table.
If set to false: Splunk performs case-insensitive matching for all fields in a lookup table.
However, for KV Store lookups, this setting ("case_sensitive_match=false") only functions as expected if all data within the KV Store lookup table is entirely in lowercase. The input data being queried can be in any case.
Given that "itsi_entities" is a KV Store lookup, setting "case_sensitive_match" to false doesn't automatically enable case-insensitive matching. If the data in the KV Store includes any uppercase characters, the lookup might not recognize entries correctly.
This issue can particularly impact fields like title, where entity names might include uppercase characters, causing searches that rely on case-insensitive matching to fail when trying to locate these entities by their title.
Resolution
To retrieve the maintenance status of all entities, we can use the lookup "operative_maintenance_log" with "itsi_entities" lookup as this lookup solely does not retrieve maintenance status of the entity:
| inputlookup operative_maintenance_log
| lookup itsi_entities _key as maintenance_object_key
| search title= "entity_title"
| table title,entity_type_ids,object_type,sec_grp,calendar_origin,maintenance_object_key,maintenance_object_type,start_time,end_time
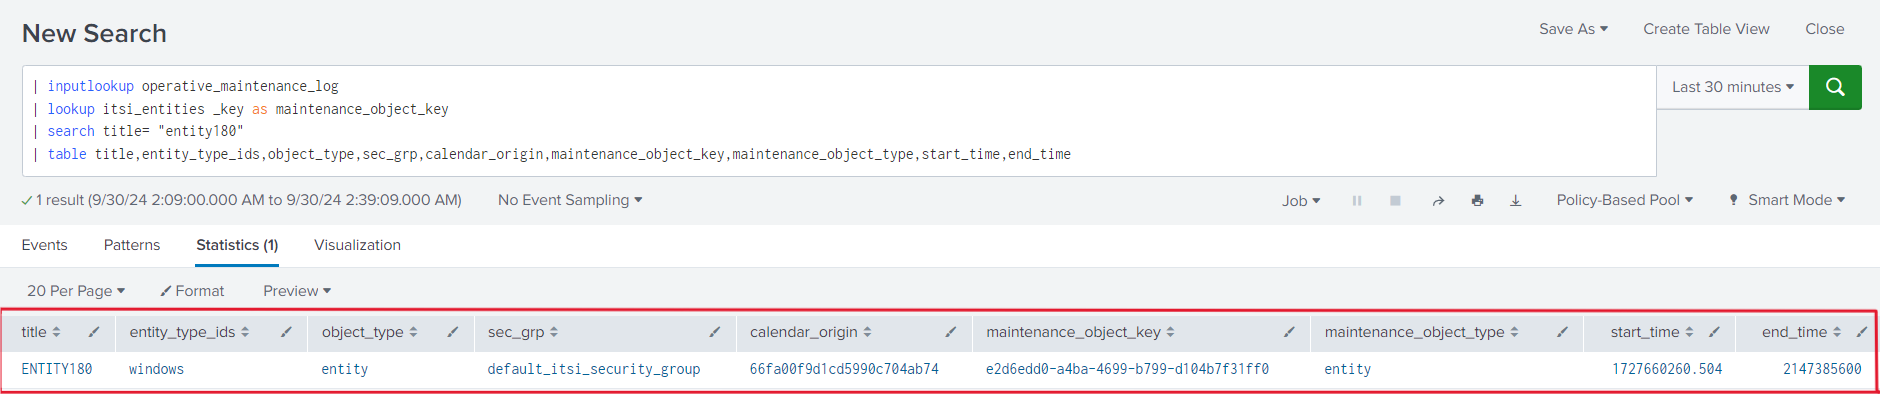
After running the search, the maintenance status of the entities was displayed irrespective of case sensitivity.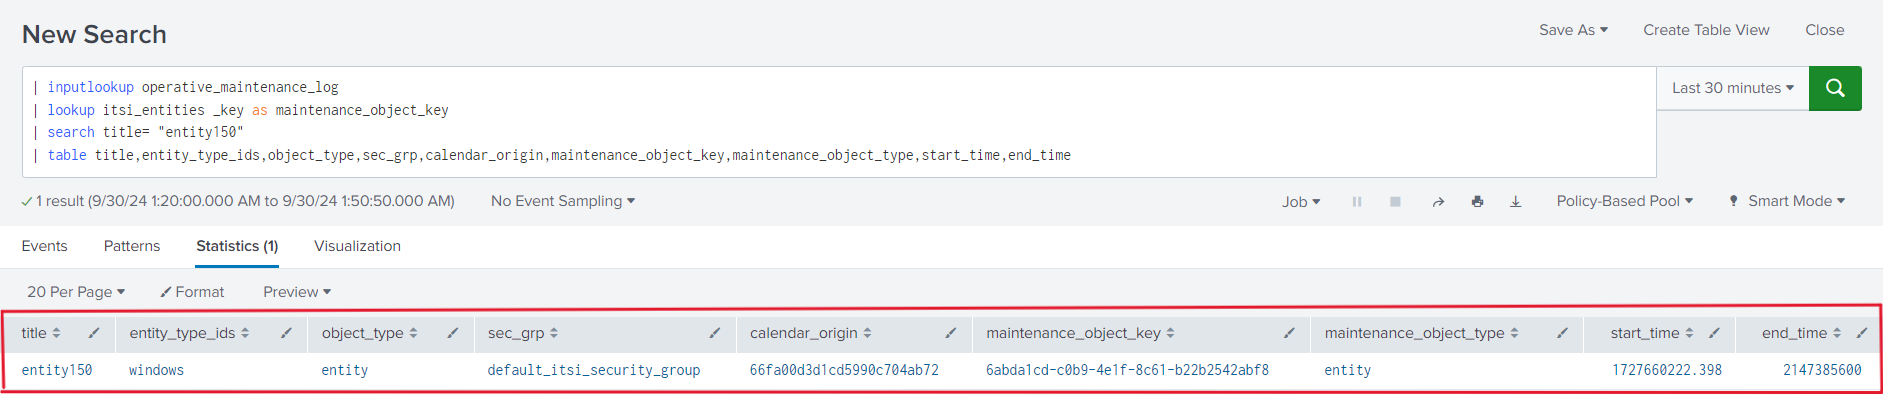
Related Links
transforms.conf - Splunk Documentation
Revision History
| Revision | Publish Date | Comments |
|---|---|---|
1.0 |
29-Sep-2026
|
Initial Release |
 Feedback
