Send to SOAR option not displaying SOAR instances when running Adaptive Response Actions in Splunk Enterprise
Available Languages
Applicability
Splunk App for SOAR Export Splunk Enterprise SecurityDescription
When a user with a custom role (inheriting ess_analyst and ess_user) attempts to use the "Send to SOAR" Adaptive Response Action in Splunk Enterprise Security, no SOAR instances appear in the SOAR instance drop-down menu.
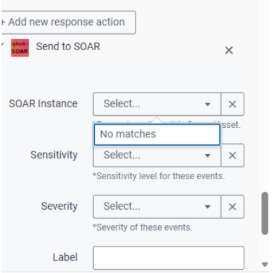
Investigation
The following steps were performed to isolate the cause:
- Capture a HAR (HTTP archive) file and confirm that the target_list_ar endpoint returns a count of 0 when the SOAR instance toggle is selected.
ERROR SearchMessages - orig_component="SearchOperator" app="search" sid="..." message_key="RESTPROC" message=The REST request on the endpoint URI /servicesNS/nobody/phantom/target_list_ar?count=0 returned HTTP 'status not OK': code=403, Forbidden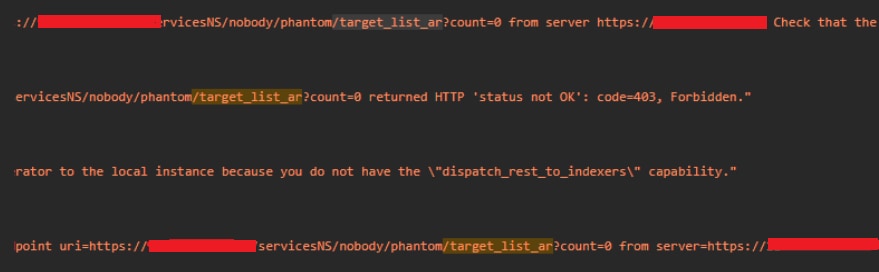
- Review the role capabilities and identify that the phantom_read and phantom_write capabilities are not assigned to the custom role.

- These capabilities grant users the ability to view and interact with SOAR instance configurations within the "Send to SOAR" Adaptive Response Action in Splunk Enterprise Security.
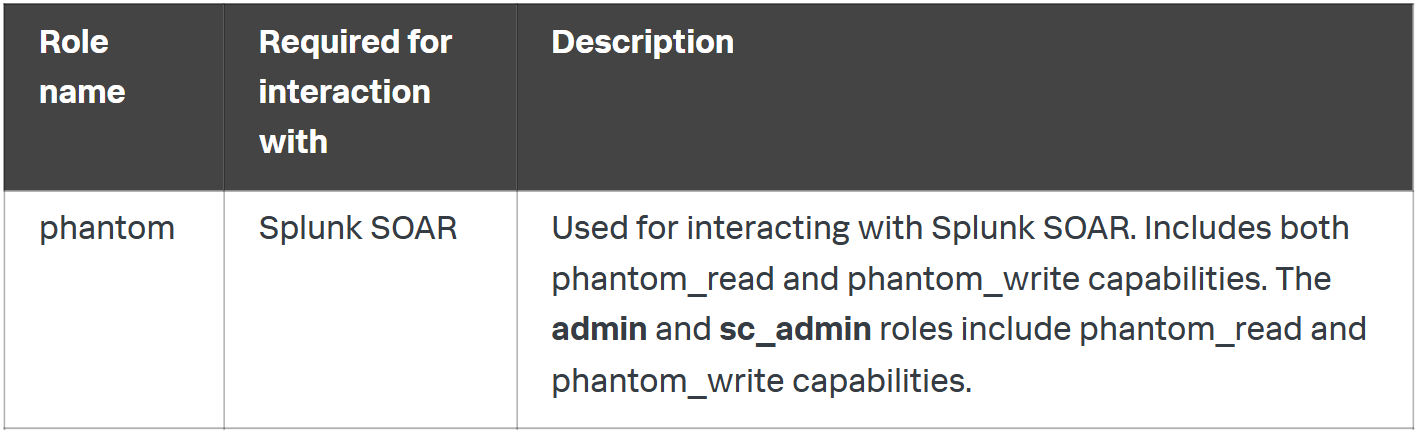
Resolution
Assign the phantom_read and phantom_write capabilities to the affected user roles by following the below steps:
- Navigate to Settings > Access Controls > Roles in the Splunk Web interface.
- Select the affected role (e.g., the custom role inheriting ess_analyst and ess_user).
- Under the Capabilities tab, locate and enable the following:
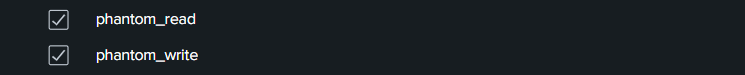
- After adding the phantom_read and phantom_write capabilities to the specified role, verify that the target_list_ar&count=0 is not visible after adding these capabilities.
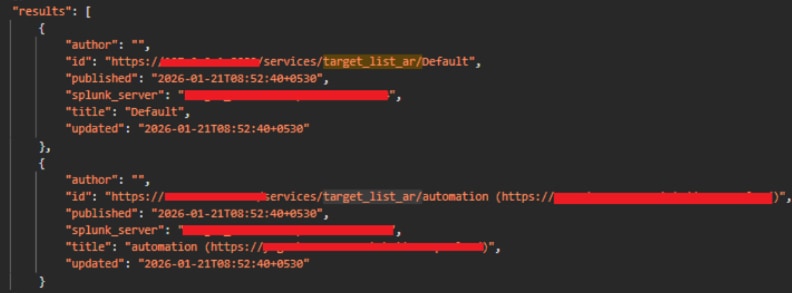
- Confirm that the SOAR instance is enabled and present in the ARA toggle for "Send to SOAR"
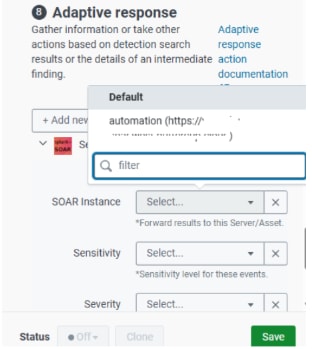
Related Links
- Splunk Docs: Allow Splunk platform users to use Splunk App for SOAR Export
- Splunk Docs: Configure role-based access control in Splunk Enterprise Security
- Splunk App for SOAR Export: Release Notes
- Splunk Article: How to capture HAR file
Revision History
| Revision | Publish Date | Comments |
|---|---|---|
1.0 |
01-Oct-2026
|
Initial Release |
 Feedback
Contact Cisco
- Open a Support Case

- (Requires a Cisco Service Contract)