Failing to send email alert due to 'SendAsDenied'
Available Languages
Applicability
Splunk EnterpriseDescription
Email Alert was configured with all the necessary information, such as below;
[email]
mailserver = smtp.myexchangeserver.com:587
auth_password = THISISPASSWORD
auth_username = noreply@abc.com
use_tls = 1
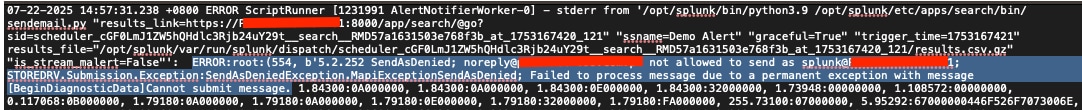
It's never succeeded to send an alert email, produces an error in the below;
ERROR:root:(554, b'5.2.252 SendAsDenied; noreply@abc.com not allowed to send as splunk@SEARCHHEAD01; STOREDRV.Submission.Exception:SendAsDeniedException.MapiExceptionSendAsDenied; Failed to process message due to a permanent exception with message [BeginDiagnosticData]Cannot submit message.The "SendAsDenied" message is specifically seen in O365 or Exchange servers, while other mail servers also display similar error messages to prevent the mailserver from being abused as a relay. "not allowed to send as " says it is not permitted to send an email under another name as it could be used as a mail relay server.
Investigation
The log message is found in splunkd.log or python.log, which has the SMTP error 554, 'SendAsDenied' which is from the SMTP server that doesn't like the authenticated account, 'noreply@abc.com' is not allowed to send an email as "splunk@HOSTNAME".
Resolution
Since the SMTP server doesn't allow the account, 'noreply@abc.com' to send as another 'splunk@HOSTNAME' , match the authenticated mail account with the sender name using 'from' in alert_actions.conf
[email]
mailserver = smtp.myexchangeserver.com:587
auth_password = THISISPASSWORD
auth_username = noreply@abc.com
from=noreply@abc.com
use_tls = 1
Or try to grant 'SendAs' permission for the auth account on Exchange/O365 or seek assistance from SMTP server admin.
Related Links
https://learn.microsoft.com/en-us/exchange/recipients/mailbox-permissions
Revision History
| Revision | Publish Date | Comments |
|---|---|---|
1.0 |
01-Oct-2026
|
Initial Release |
 Feedback
Contact Cisco
- Open a Support Case

- (Requires a Cisco Service Contract)