The Indexer is not receiving data from the Forwarder.
Available Languages
Applicability
Splunk EnterpriseDescription
There was no data that was being received by the Search Head. The internal data from Splunk as well as data coming from applications and add-ons configured on the Forwarders were not sending data to the Indexers.Investigation
1. Checked with regards to port 9997. Used the telnet command to test the connectivity and it showed connection refused. The port was down.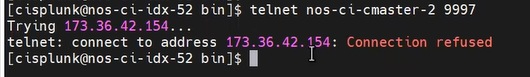
2. Validated as well with port 8089, and port 8089 was down, which indicated splunkd was not running.

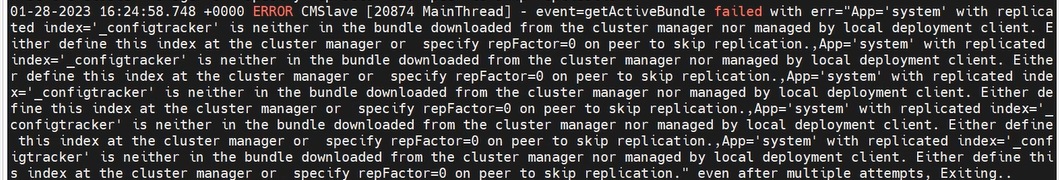
3. Traversed to splunkd.log and observed the following errors:-
Resolution
- It was indicative that there was an issue with the downloading of the bundle, as due to this, Splunk did not start (8089).With this, as no bundle was sent, no information was sent, thus 9997 was not active, and forwarders did not connect with the indexers.
repFactor = 0|auto
* Valid only for indexer cluster peer nodes.
* Determines whether an index gets replicated.
* Configuring this setting to 0 turns off replication for this index.
* Configuring to "auto" turns on replication for this index.
* You must configure this setting to the same value on all peer nodes.
* Default: 0
Workaround:-
1. Navigated to $SPLUNK_HOME/master-apps/_cluster/local/indexes.conf on the master node (cluster master):-
2. Appended the following stanza:-
[_configtracker]
repFactor = 0
3. Restarted the instance.
- The configuration change would get pushed from the cluster master to all the indexers in the environment.
[OR]
If added to a single/standalone indexer, then the process is as follows:-
1. Navigate to /opt/splunk/etc/system/local/indexes.conf on the particular indexer:-
2. Append the following stanza:-
[_configtracker]
repFactor = 0
3. Restart the instance.
- 'repFactor=0' has to be done as per 'index' basis. As here it was for the index '_configtracker' the parameter was only updated for this specified index.
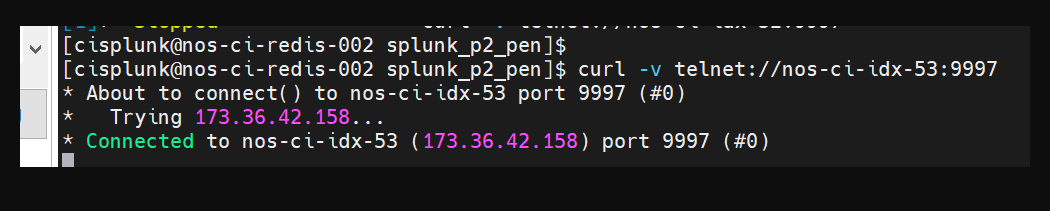
- After this change, the splunkd status was running which indicated port 8089 was up and port 9997 was up as well.
Related Links
https://community.splunk.com/t5/Getting-Data-In/What-is-the-best-practice-to-address-the-quot-is-neither-in-the/m-p/503243
https://docs.splunk.com/Documentation/Splunk/9.0.3/Admin/Indexesco
Revision History
| Revision | Publish Date | Comments |
|---|---|---|
1.0 |
29-Sep-2026
|
Initial Release |
 Feedback
Contact Cisco
- Open a Support Case

- (Requires a Cisco Service Contract)