Forwarder Is Not Sending Internal Logs to Indexer
Available Languages
Applicability
Splunk EnterpriseDescription
SplunkForwarder is the default app when install Splunk enterprise and is disabled by default. The app is used by Heavy Forwarder.If enable it, the following in $SplunkForwarder/default/outputs.conf will come into play and prevent the instance from forwarding its internal logs to the indexer as there is no _internal mentioned
forwardedindex.2.whitelist = (_audit|_introspection|_telemetry)
Investigation
When the SplunkForwarder app is enabled with following configuration in SplunkForwarder/local/app.conf[install] state = enabledand the following in SplunkForwarder/default/outputs.conf, there is no internal logs forwarding to the indexer
#   Version 7.3.9
[tcpout]
maxQueueSize = 500KB
forwardedindex.0.whitelist = .*
forwardedindex.1.blacklist = _.*
forwardedindex.2.whitelist = (_audit|_introspection|_telemetry)
forwardedindex.filter.disable = false
Resolution
Disable the SplunkForwarder app directly. This app stops the forwarder from sending the internal events to the indexer, you can use the the command below to disable it.splunk disable app SplunkForwarderYou can disable the SplunkForwarder app and continue monitoring other files in the forwarder without any issue
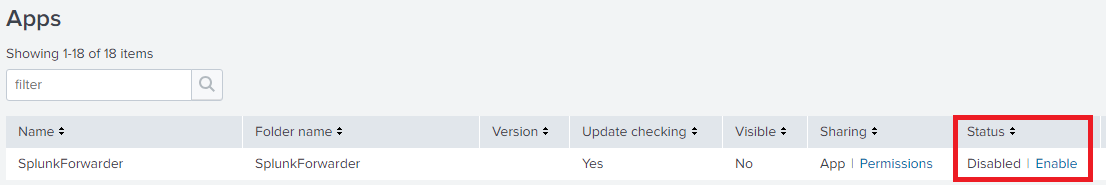
If you want to know the status of this app, you can check the app console:
Related Links
Disable_forwarding_from_the_CLI
Revision History
| Revision | Publish Date | Comments |
|---|---|---|
1.0 |
29-Sep-2026
|
Initial Release |
 Feedback
Contact Cisco
- Open a Support Case

- (Requires a Cisco Service Contract)