SAML authentication fails due to unacceptable signatureAlgorithm
Available Languages
Applicability
Splunk EnterpriseDescription
Splunk platform is configured for SSO with AD FS as the identity provider (IdP). After the full SAML configuration is completed from the web GUI, users are unable to pass through the authentication from IdP. The below error is shown on the Splunk web GUI:
IDP failed to authenticate request. Status Message="" Status Code="Responder"
Investigation
- Log into Splunk Web GUI via Splunk internal authentication by modifying URL as below:
http://<SplunkHost>:<splunkWebPort>/en-US/account/login?loginType=splunk -
Run below SPL search to check the _internal log for SAML authentication error events:
index=_internal component IN ("UserManagerPro", "AuthenticationManagerSAML", "UiSAML", "Saml*") -
Look for the following logs in splunkd.log:
WARN  SAMLConfig [7632 TcpChannelThread] - Use SHA256, SHA384, or SHA512 for 'inboundDigestMethod' rather than 'SHA1'
WARN  SAMLConfig [7632 TcpChannelThread] - Use RSA-SHA256, RSA-SHA384, or RSA-SHA512 for 'signatureAlgorithm' rather than 'RSA-SHA1'
ERROR Saml [6368 webui] - Failed to parse issuer. Could not evaluate xpath expression /samlp:Response/samlp:Status/samlp:StatusMessage or no matching nodes found. No value found in SamlResponse for key=/samlp:Response/samlp:Status/samlp:StatusMessageCould not evaluate xpath expression /samlp:Response/samlp:Status/samlp:StatusDetail/Cause or no matching nodes found. No value found in SamlResponse for key=/samlp:Response/samlp:Status/samlp:StatusDetail/CauseCould not evaluate xpath expression //saml:Assertion/saml:Issuer or no matching nodes found. No value found in SamlResponse for key=//saml:Assertion/saml:Issuer
ERROR UiSAML [6368 webui] - IDP failed to authenticate request. Status Message="" Status Code="Responder"
Note: Above log events indicate that AD FS (IdP) has rejected the authentication requests sent from Splunk platform via SP-initiated SAML request messages. The root cause of the rejection is the default RSA-SHA1 as the signatureAlgorithm attribute is not acceptable by IdP and IdP only accepts RSA-SHA256 or above for improved security.
Resolution
- Edit $SPLUNK_HOME/etc/system/local/authentication.conf and add below stanza in Splunk instance.
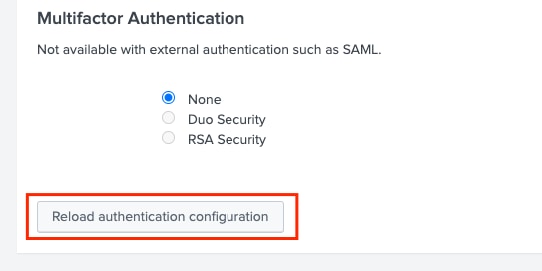
[saml] signatureAlgorithm = RSA-SHA256 - Reload SAML configuration under Settings >> Authentication Methods web page.
Related Links
Revision History
| Revision | Publish Date | Comments |
|---|---|---|
1.0 |
30-Sep-2026
|
Initial Release |
 Feedback
Contact Cisco
- Open a Support Case

- (Requires a Cisco Service Contract)