User with sc_admin role is unable to view all users.
Available Languages
Applicability
Splunk CloudDescription
Users with the sc_admin role should be able to view a list of all the users in the Cloud Instance. Settings > Users only lists a small group of all users.
Investigation
Users with admin role can retrieve the complete list of users.
At first glance, the sc_admin role has the necessary capabilities to view users. The group of users listed for the users corresponds to sc_admin users only. Users with different roles aren't listed.
Using the following command will render the same results for the user, thus confirming the issue is related to role capabilities.
rest /services/authentication/users splunk_server=local
Next, investigate roles with capabilities sc_admin role doesn't possess or can't grant. It is possible to search for the information using the following SPL. Note that to correctly executing the search requires a user who can see the complete set of users or a user with the admin role. If none is available then the best next step is to open a support case.
| rest splunk_server=local /services/authorization/roles
| fields title capabilities imported_capabilities
| search NOT title IN (admin, can_delete, cmon_role, index-manager, internal_automation_role, internal_monitoring_role, internal_ops_admin, internal_ops_admin_role, internal_observability, splunk-system-role, observability_role, ps_admin, mc_web_debug) ```ignore internal splunk roles```
| eval capability=mvappend(capabilities,imported_capabilities)
| fields capability title
| stats values(title) AS "role" by capability
| search role!="sc_admin" capability!=delete_by_keyword ```grantableRoles includes can_delete which has this```
``` CHECK grantableRoles for sc_admin to make sure that only the usual roles are listed (can_delete;power;sc_admin;user
) - the presence of others may mean this search is not valid ```
| stats values(capability) AS "Additional capability" by role
```*** Which non splunk-internal roles have a capability sc_admin doesn't - and is thus invisible to sc_admin ***```
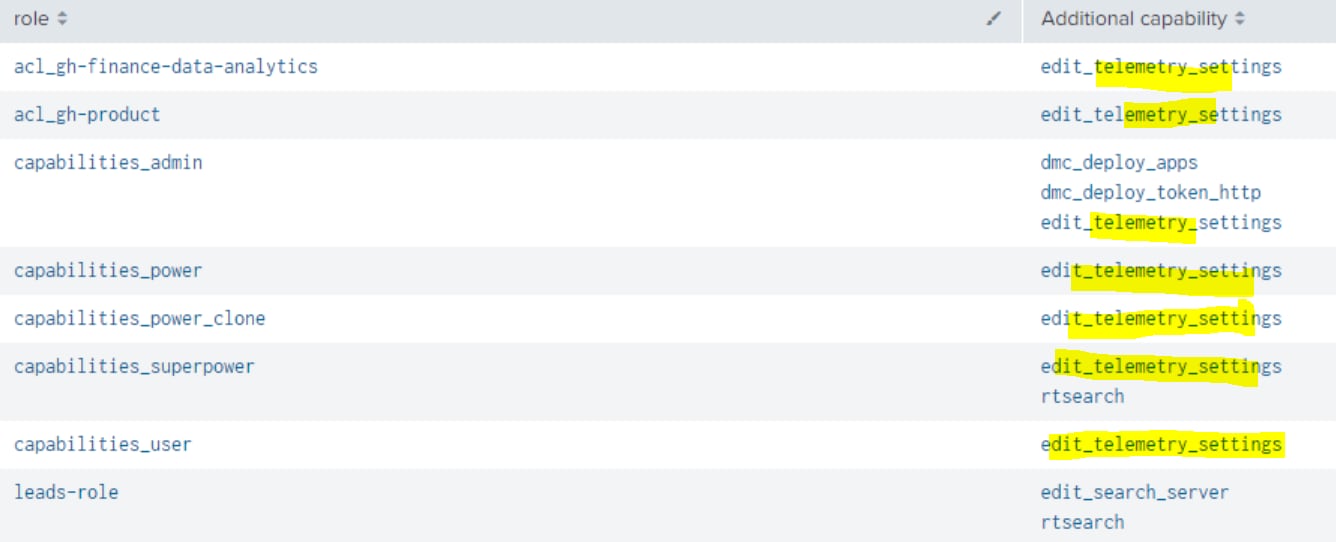
When the search was executed the following information displayed.
Resolution
Define roles on the Splunk platform with capabilities
edit_telemetry_settingsis an admin-only capability. Neither thesc_adminrole nor any other custom role should have this capability.- The
sc_adminrole has theedit_roles_grantablecapability to allow user administration. This capability is more restricted than theedit_rolesthat theadminrole has. edit_roles_grantable -
sc_adminhas a list ofgrantableRoleswhich restricts the capabilities it can grant. The basic principle is that it cannot grant capabilities that it does not itself have, or it cannot bestow. This restriction applies even to visibility. Essentially, these other roles and the users with these roles are not visible because they have "more capability" thansc_admin. Having this additional capacity is over and abovesc_admin, thus causing the issue.grantableRoles = <semicolon-separated list>
They can see only users who have been assigned roles that contain capabilities that are a union of these capabilities.
Solution:
In this case, the fix should likely be the removal of the edit_telemetry_settings capability from all roles.
Related Links
Define roles on the Splunk platform with capabilities
edit_roles_grantable
Revision History
| Revision | Publish Date | Comments |
|---|---|---|
1.0 |
29-Sep-2026
|
Initial Release |
 Feedback
Contact Cisco
- Open a Support Case

- (Requires a Cisco Service Contract)