Splunk Add-on for Unix and Linux : Having a data truncation issue with metric index due to characters limit while using scripted input
Available Languages
Applicability
Splunk Enterprise Splunk CloudDescription
In the Splunk Add-on for Unix and Linux, while ingesting the `ps_metrics.sh` scripted input, some fields containing more than 2048 characters are being truncated, resulting in incorrect field data population.
Investigation
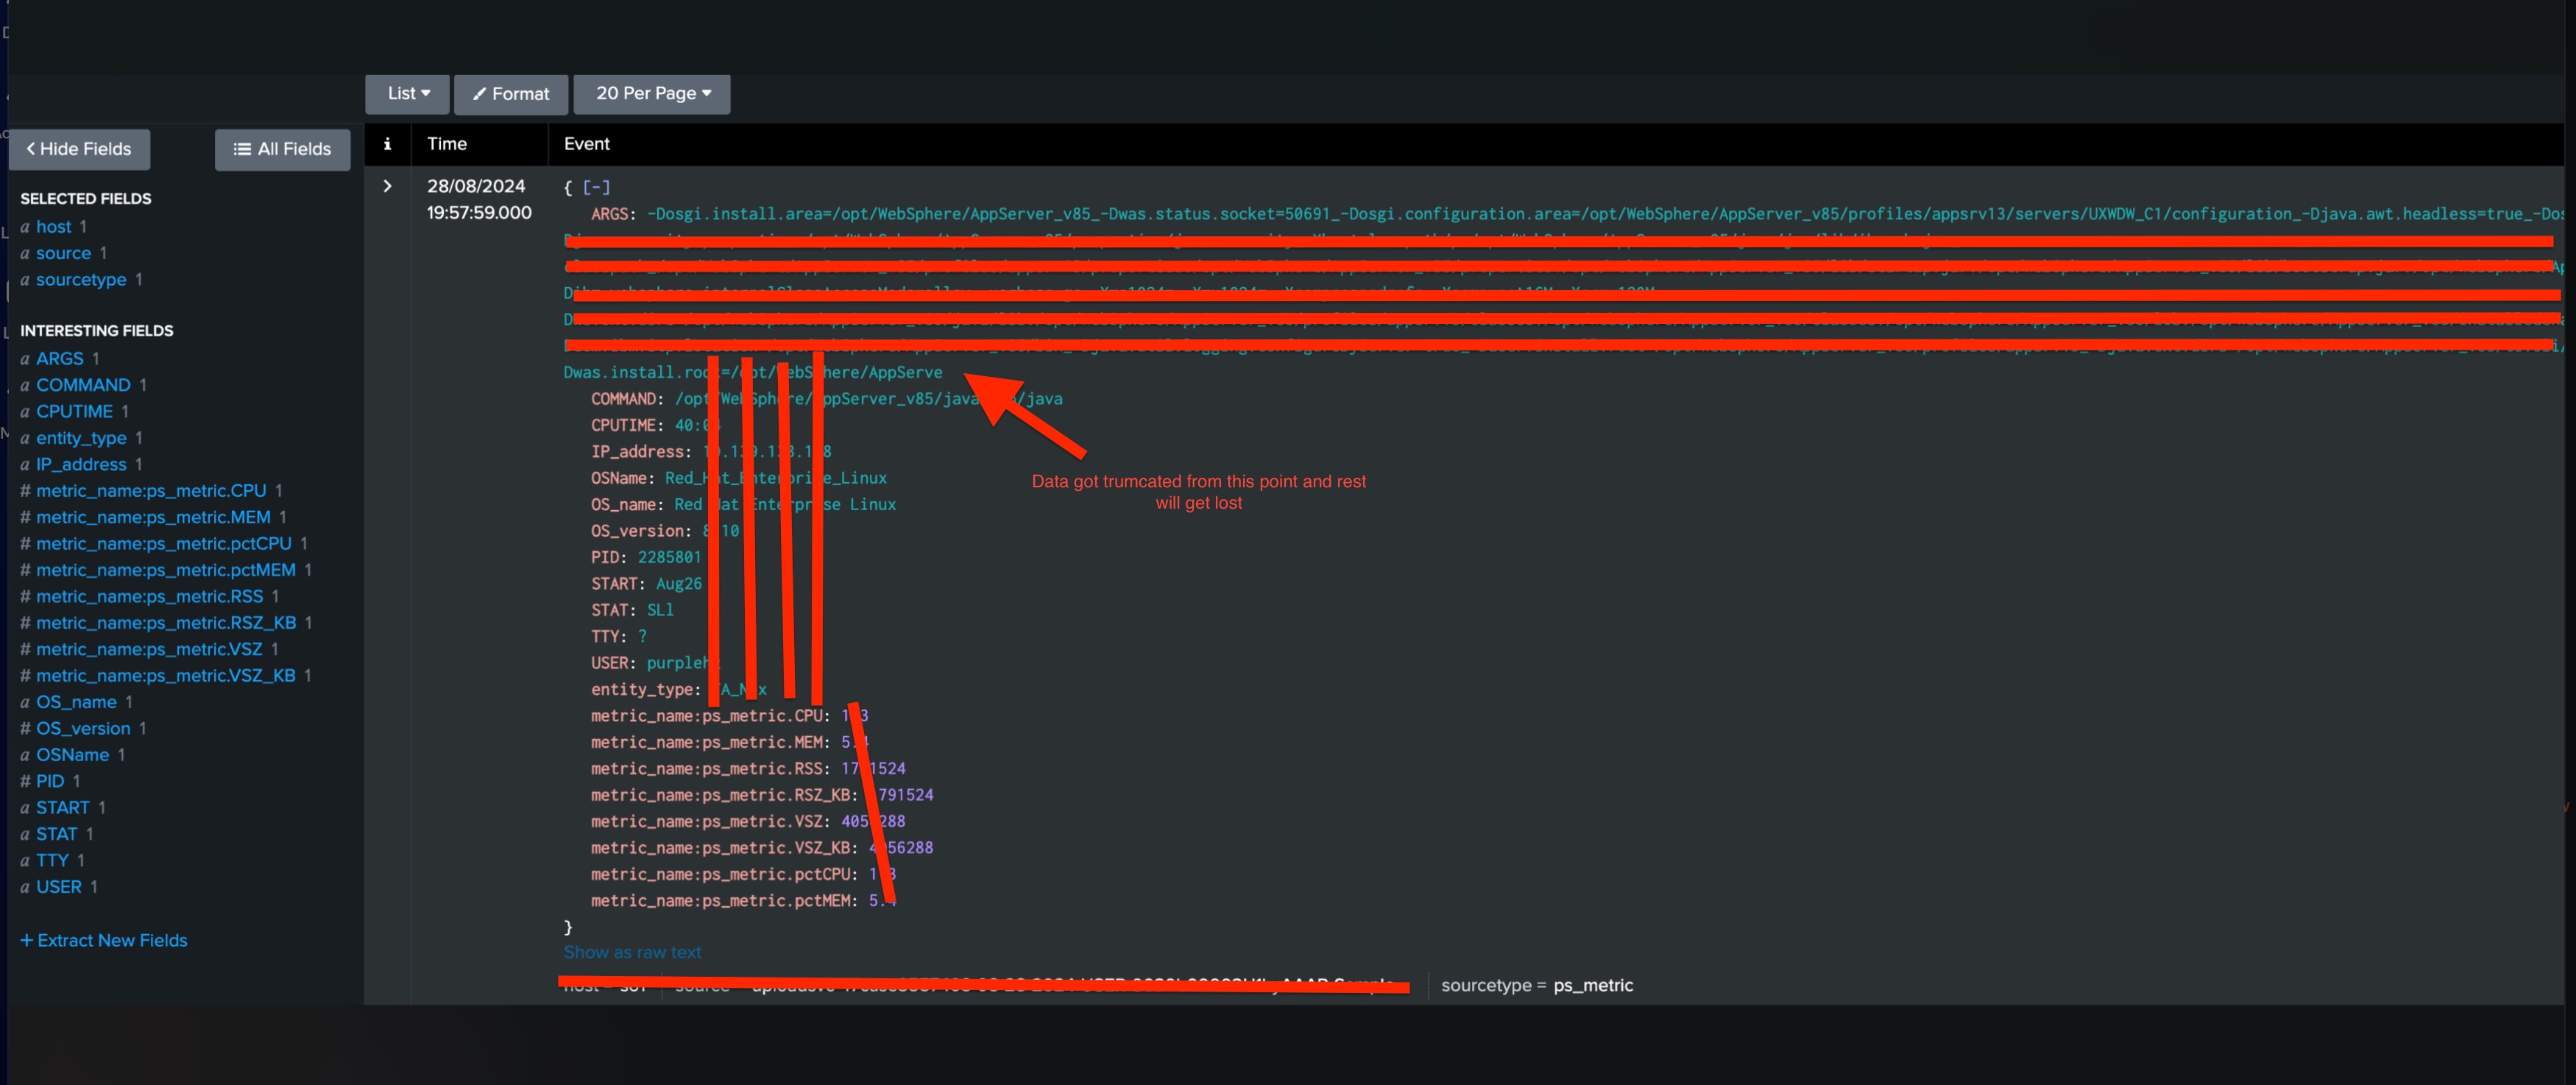
-> Here, the characters of the fields are getting exceeded from 2048 characters limit, hence its getting truncated
- > The maximum allowable length of an indexed field including the <fieldname>:: prefix is 2048 chars. Therefore, any field containing data exceeding 2048 characters will be truncated.
Resolution
There is no resolution or workaround to get past this limitation ( Chars limit is hardcoded ) other than splitting the value into multiple fields and then concat the fields together during the search.
Revision History
| Revision | Publish Date | Comments |
|---|---|---|
1.0 |
29-Sep-2026
|
Initial Release |
 Feedback
Contact Cisco
- Open a Support Case

- (Requires a Cisco Service Contract)