Scheduled Alert/Search is not starting. Next Scheduled Time value is None
Available Languages
Applicability
Splunk 9.x.xDescription
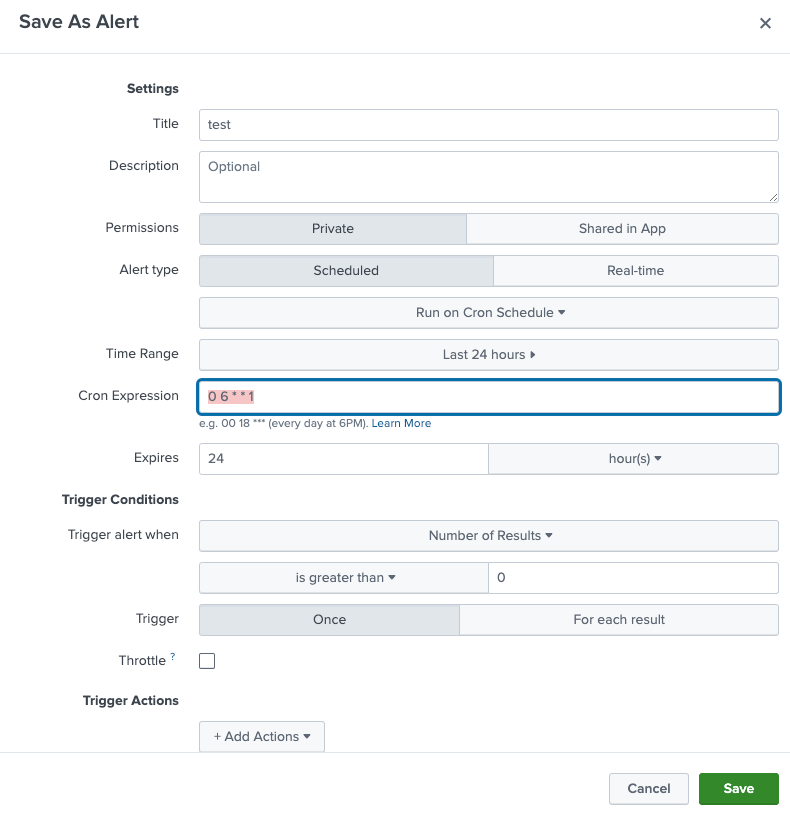
Issue reported is that each newly created Scheduled Report/Alert is not starting at desired time. Next Scheduled Time has value "None" for all of them.
Investigation
Looking into diags and details gathered during investigation, every newly created search doesn't have enableSched = 1 parameter in savedsearches.conf
[admin_test_alert]
action.email = 1
action.email.to = nathan.gilbert@williamhill.co.uk
action.email.useNSSubject = 1
action.webhook.enable_allowlist = 0
alert.suppress = 0
alert.track = 0
cron_schedule = 0 6 * * 1
disabled = 0
dispatch.earliest_time = -1w
dispatch.latest_time = now
request.ui_dispatch_app = search
search = index=wh_cisco_asa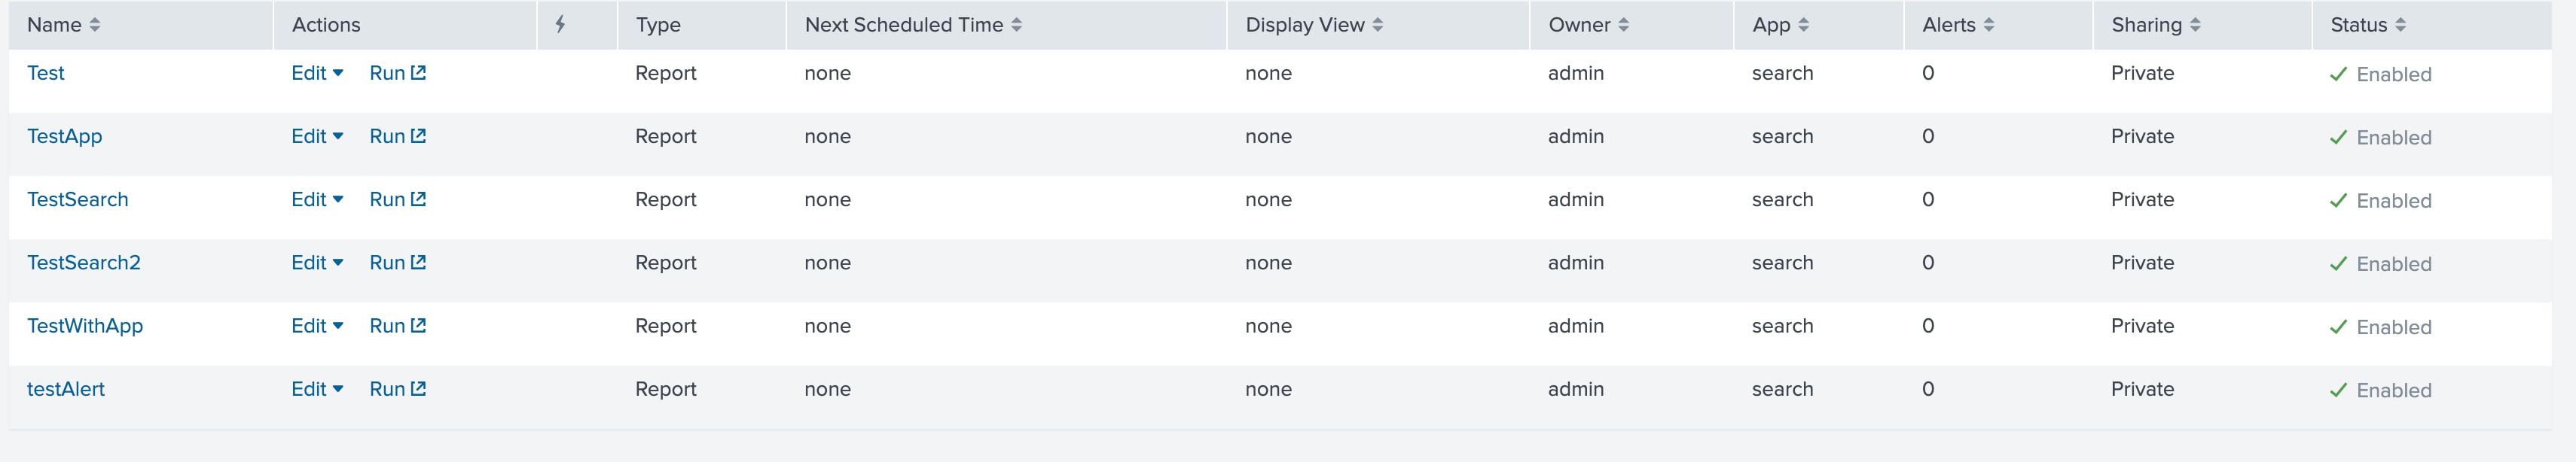
Once enableSched = 1 parameter has been added manually to each search, all of them were starting as expected.
During more deeply investigation custom application was found with [default] stanza in savedsearches.conf which contain enableSched = 1 configured.
savedsearches.conf[default]
enableSched = 1
Once that parameter has been removed from [default] stanza and after Splunk restart each newly created Scheduled Search or Alert have enableSched = 1 added by default what resolved issue.
Resolution
Workaround:
- Add enableSched = 1 to each affected search/alert and restart Splunk
Permament fix:
- Check if there is enableSched = 1 parameter configured under [default] stanza in savedsearches.conf. If yes then please remove it, restart Splunk and create new Scheduled Report/Alert
Revision History
| Revision | Publish Date | Comments |
|---|---|---|
1.0 |
29-Sep-2026
|
Initial Release |
 Feedback
Contact Cisco
- Open a Support Case

- (Requires a Cisco Service Contract)