Amazon Kinesis Data Firehose is unable to ingest data into Splunk via HEC.
Available Languages
Applicability
Splunk Add-on for Amazon Web Services Splunk Enterprise Splunk CloudDescription
The user has configured the Amazon Kinesis Data Firehose and created an HEC token on Splunk, but they are unable to ingest the data into Splunk.
Investigation
There are no error logs on the Splunk side, and the SPL query used was as follows:
index="_internal" HttpInputDataHandler sourcetype=splunkd "HEC token name"index="_introspection" sourcetype=http_event_collector_metrics| spath "data.token_name" | search "data.token_name"="HEC token name"There is CloudWatch Log Groups have been created for the Kinesis Firehose, which include the destination error logs. so, requested the user to check if there are any destination error logs generated on the AWS side. The user can refer to the screenshot below from our lab environment and compare it with their own environment.
Resolution
-
Verify that the HEC token added on the AWS side is correct.
-
Create a new HEC token and enable indexer acknowledgment.
-
Enable indexer acknowledgment on the currently used HEC token.
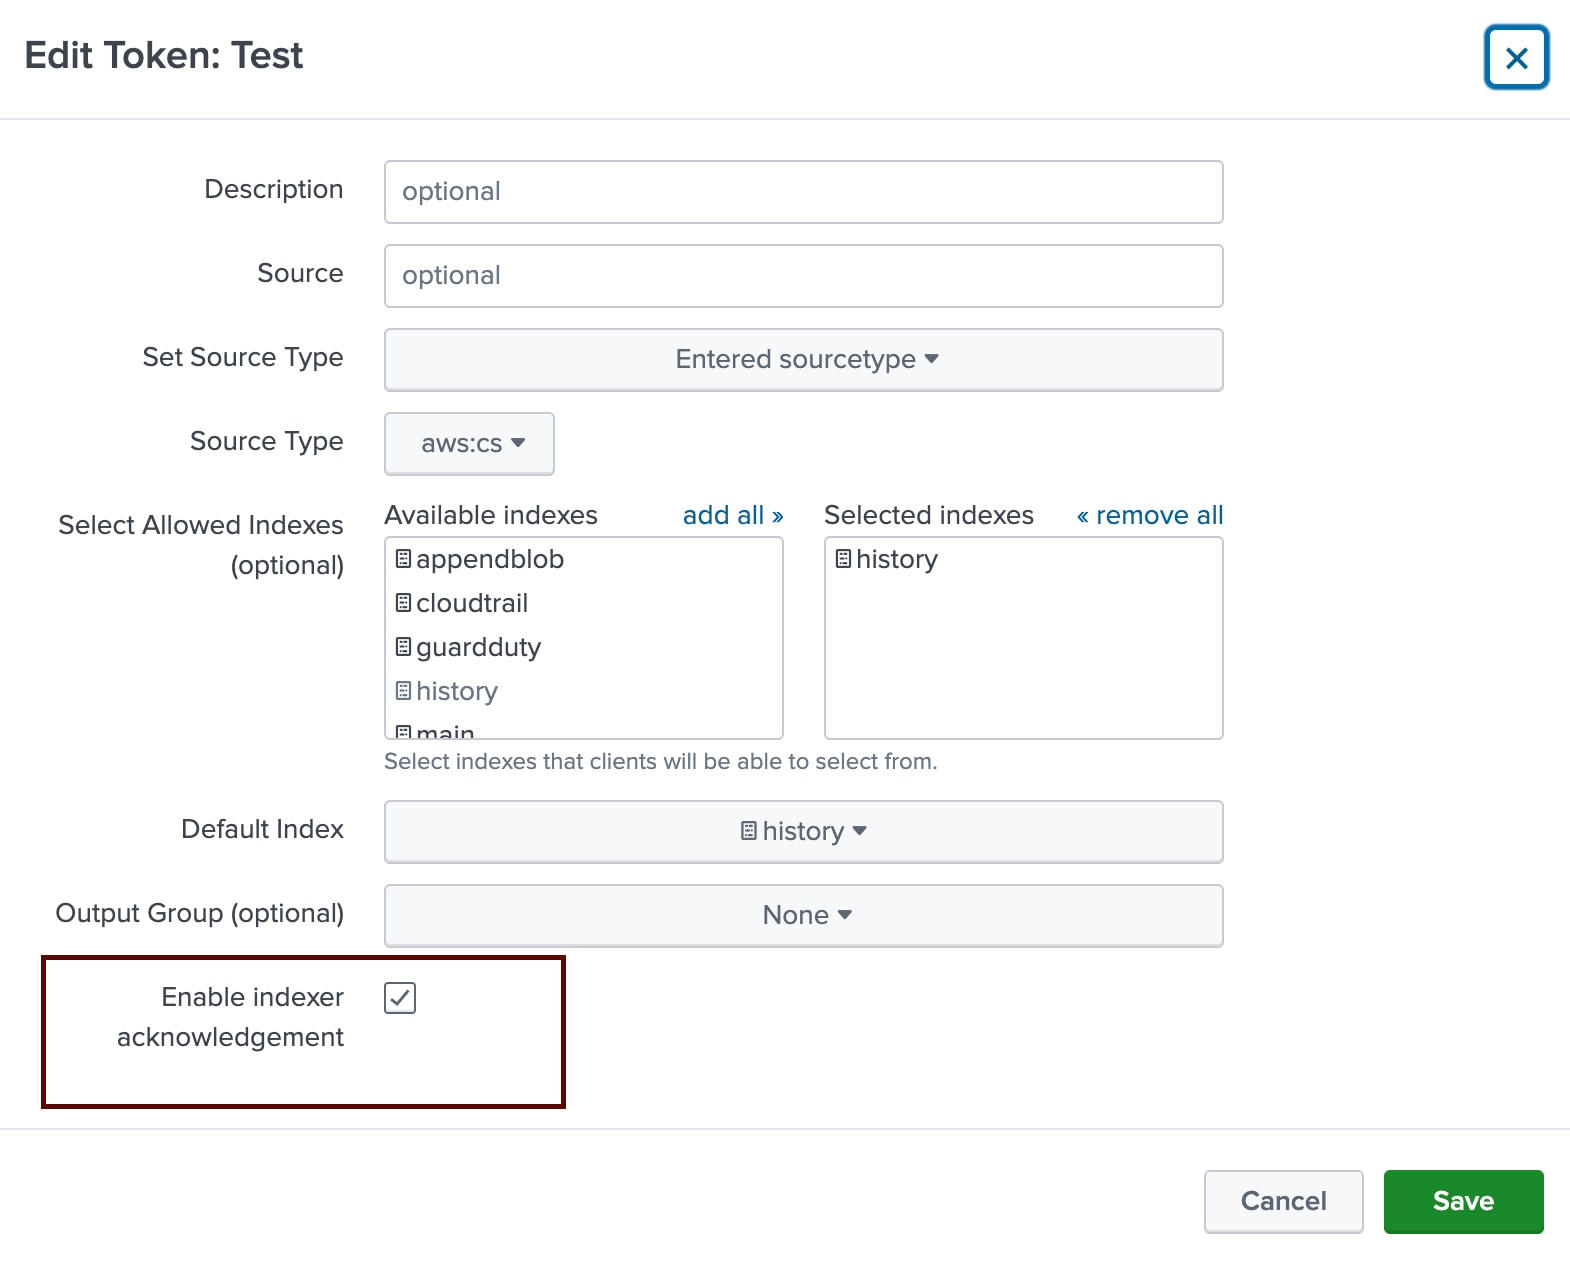
The issue was resolved after the user enabled indexer acknowledgment on the HEC token being used.
Related Links
Troubleshooting Splunk for HEC
About HTTP Event Collector Indexer Acknowledgment
Revision History
| Revision | Publish Date | Comments |
|---|---|---|
1.0 |
29-Sep-2026
|
Initial Release |
 Feedback
Contact Cisco
- Open a Support Case

- (Requires a Cisco Service Contract)