While configuring Generic S3 input in the Splunk Add-on for AWS, it is failing due to Missing Permission Issue.
Available Languages
Applicability
Splunk Apps & Add-ons Splunk Enterprise Splunk CloudDescription
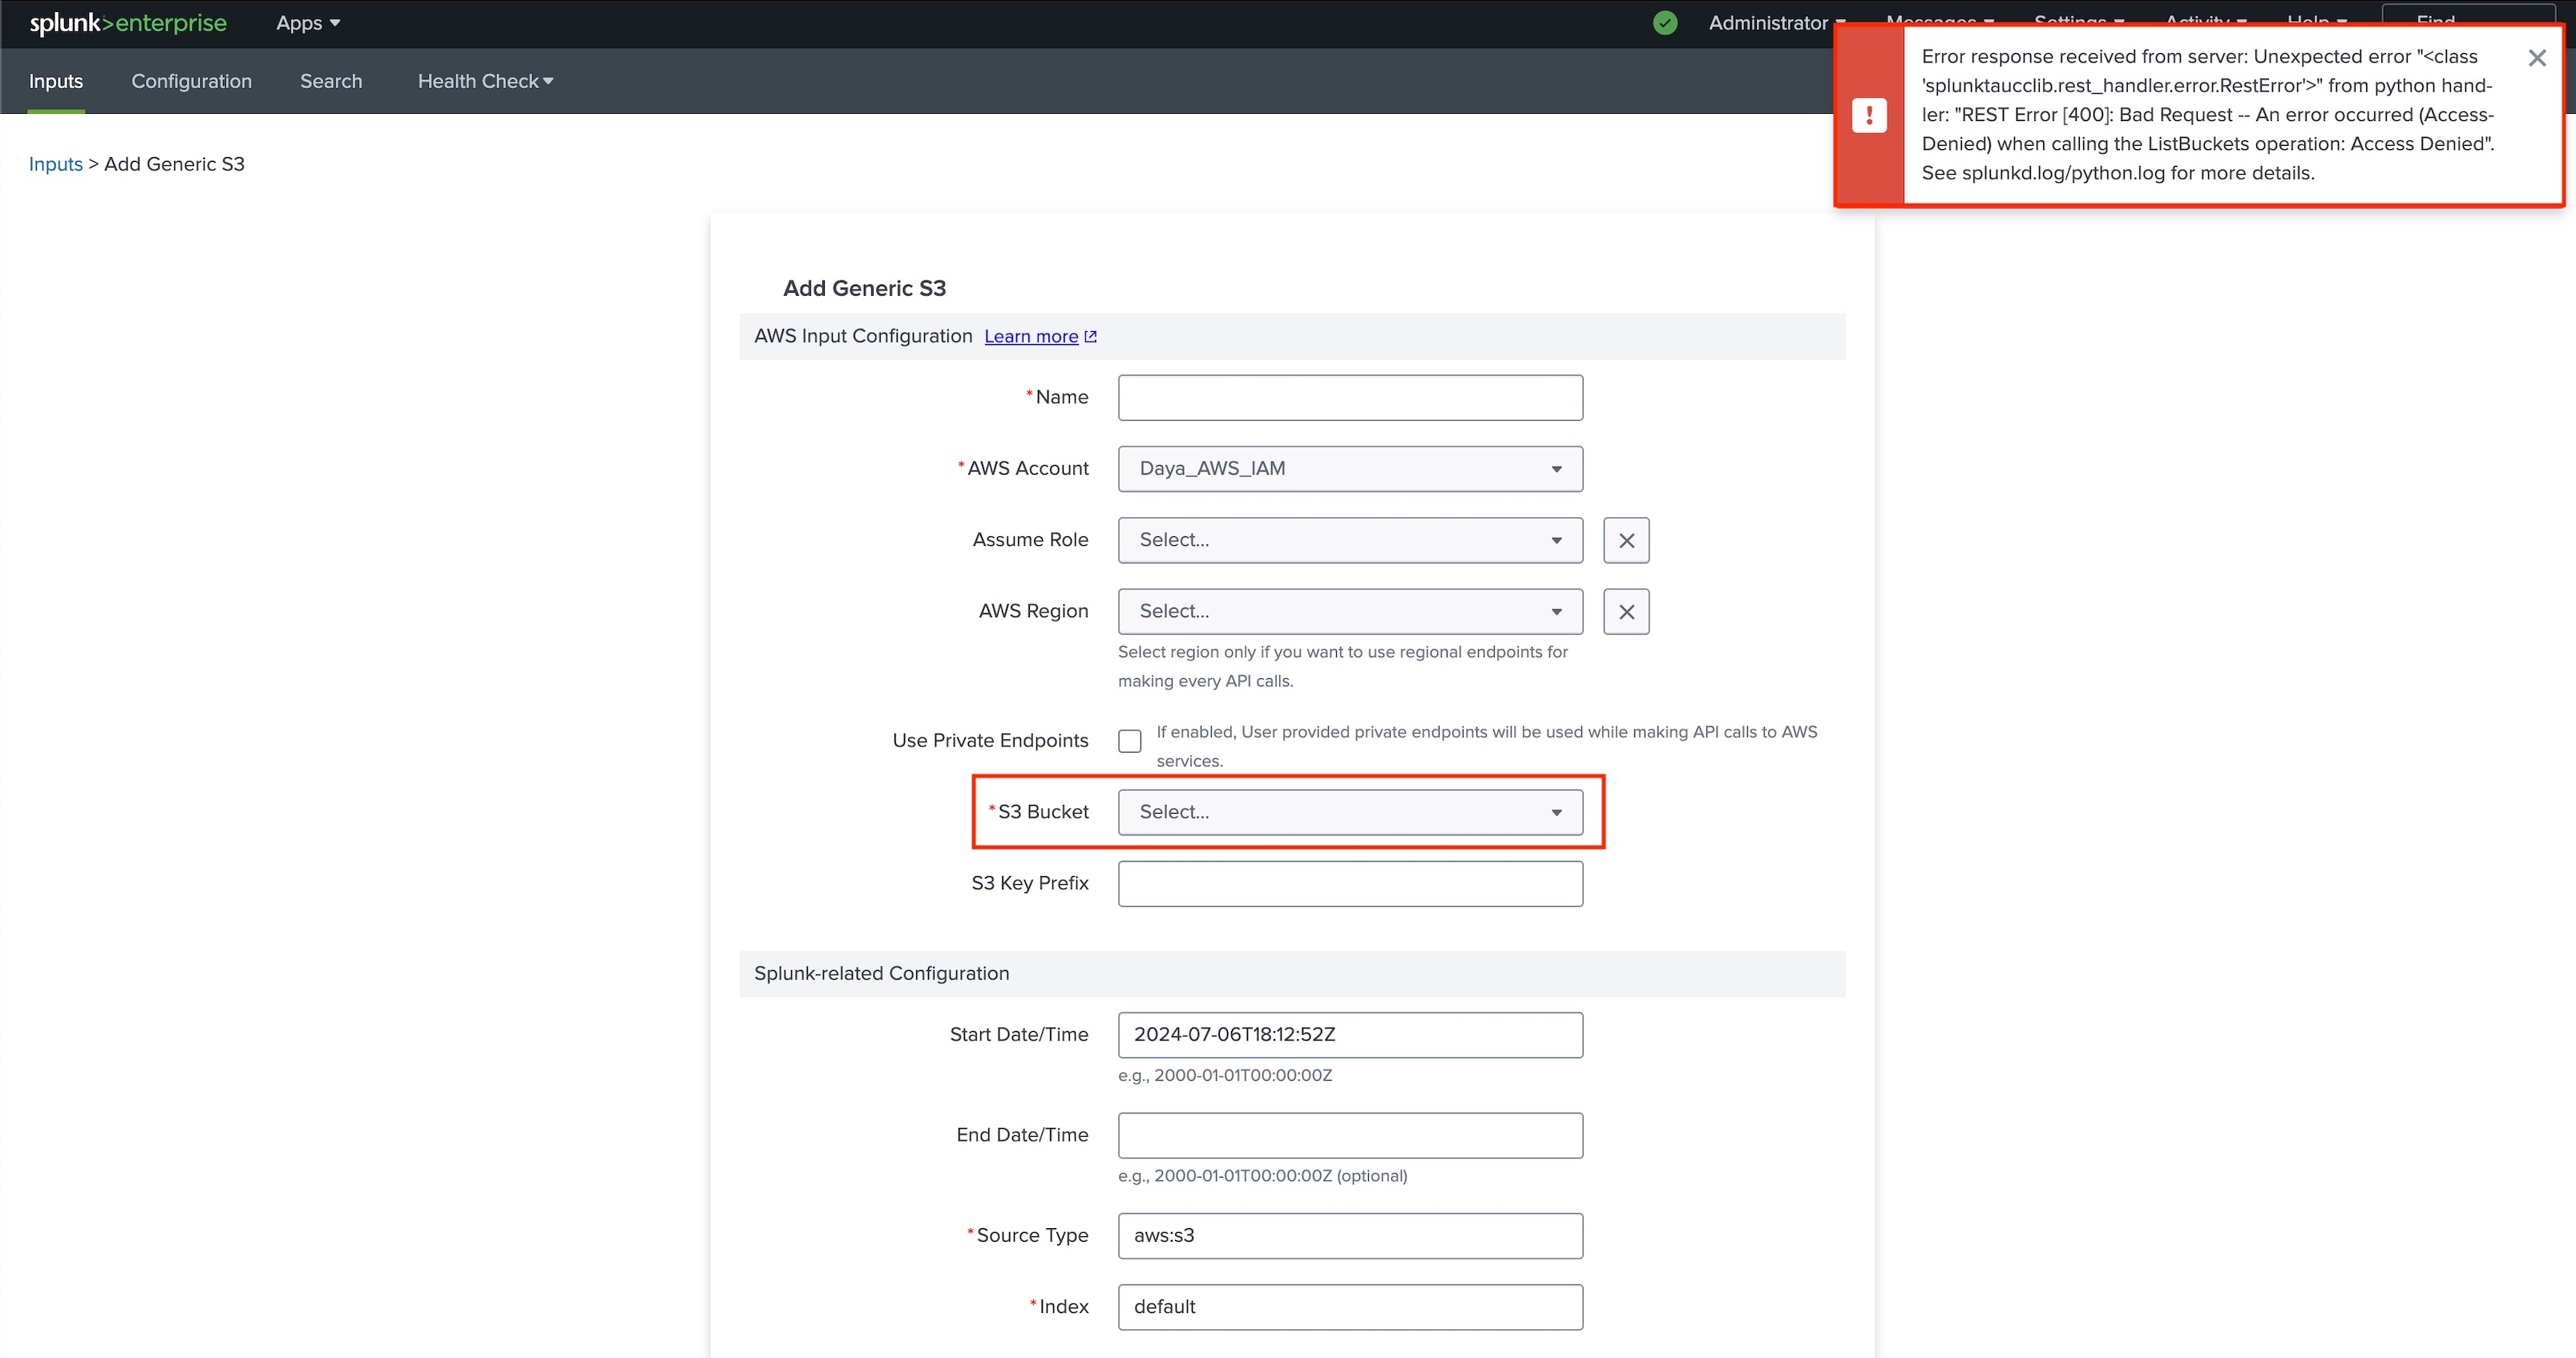
While configuring the "Generic S3" input in the Splunk Add-on for Amazon Web Services, the input can list all the regions when selecting the "AWS Region" option. However, input is not able to load the S3 Buckets and fails with an Error message - "*An error occurred (Access-Denied) when calling the ListBuckets operation; Access Denied*".
Screenshot below for reference,
Investigation
Run the below SPL Query to check if there are any error messages in the _internal logs,
SPL:
index="_internal" sourcetype=splunkd *aws* ERROR
Found the below error messages which are generated repeatedly whenever an SQS-based S3 input was added. The error message reads as below:Errors:
07-06-2024 18:13:27.853 +0000 ERROR AdminManagerExternal [108989 TcpChannelThread] - Stack trace from python handler:\nTraceback (most recent call last):\n File "<string>", line 143, in handleList\n File "/opt/splunk/etc/apps/Splunk_TA_aws/lib/botocore/client.py", line 535, in _api_call\n return self._make_api_call(operation_name, kwargs)\n File "/opt/splunk/etc/apps/Splunk_TA_aws/lib/botocore/client.py", line 983, in _make_api_call\n raise error_class(parsed_response, operation_name)\nbotocore.exceptions.ClientError: An error occurred (AccessDenied) when calling the ListBuckets operation: Access Denied\n\nDuring handling of the above exception, another exception occurred:\n\nTraceback (most recent call last):\n File "/opt/splunk/lib/python3.7/site-packages/splunk/admin.py", line 151, in init\n hand.execute(info)\n File "/opt/splunk/lib/python3.7/site-packages/splunk/admin.py", line 647, in execute\n if self.requestedAction == ACTION_LIST: self.handleList(confInfo)\n File "<string>", line 146, in handleList\nsplunktaucclib.rest_handler.error.RestError: REST Error [400]: Bad Request -- An error occurred (AccessDenied) when calling the ListBuckets operation: Access Denied\nOn debugging the above Error log, it was found that though the "ListBucket" permission was provided to the IAM User on the AWS end but it is not sufficient to retrieve all the S3 Buckets and "ListAllMyBuckets" shall also be provided to IAM users on the AWS end as well.
The "ListAllMyBuckets" permission also aligns with the required permissions that need to be added to the IAM user on the AWS end as per the Generic S3 input Docs. Required permissions are added below for reference as well,
{
    "Version": "2012-10-17",
    "Statement": [
        {
            "Effect": "Allow",
            "Action": [
                "s3:ListBucket",
                "s3:GetObject",
                "s3:ListAllMyBuckets",
                "s3:GetBucketLocation",
                "kms:Decrypt"
            ],
            "Resource": "*"
        }
    ]
}
Resolution
The issue was resolved once the "s3:ListAllMyBuckets" permission was added to the IAM user on the AWS end.
Related Links
AWS Generic S3 Input Required Permission
Revision History
| Revision | Publish Date | Comments |
|---|---|---|
1.0 |
29-Sep-2026
|
Initial Release |
 Feedback
Contact Cisco
- Open a Support Case

- (Requires a Cisco Service Contract)