Verification of SAML assertion using the IDP's certificate provided failed. Unsupported signature algorithm.
Available Languages
Applicability
Splunk CloudDescription
When configuring SAML , the following error appears: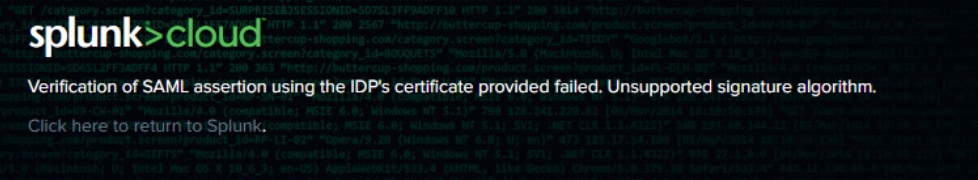
Investigation
From the splunkd.log the following will be seen:
09-09-2021 23:06:58.414 +0000 ERROR UiSAML [30617 webui] - Verification of SAML assertion using the IDP's certificate provided failed. Unsupported signature algorithm.
09-09-2021 23:06:58.414 +0000 WARN Saml [30617 webui] - Unsupported signature algorithm. Algorithm: 'RSA-SHA1' is not allowed in configuration
The following could also be seen
<ds:CanonicalizationMethod Algorithm="http://www.w3.org/2001/10/xml-exc-c14n#"/>;
<ds:SignatureMethod Algorithm="http://www.w3.org/2001/04/xmldsig-more#*rsa-sha256*"/>;
<ds:Reference URI="#s5be138b8d32b4ab6975129ce004ce6e04079545d">
<ds:Transforms>
<ds:Transform Algorithm="http://www.w3.org/2000/09/xmldsig#enveloped-signature"/>;
<ds:Transform Algorithm="http://www.w3.org/2001/10/xml-exc-c14n#"/>;
</ds:Transforms>
<ds:DigestMethod Algorithm="http://www.w3.org/2000/09/xmldsig#*sha1*"/>;And they can only support sha1 as ds:DigestMethod.But Splunk throws the following error:
ERROR Saml - For SignatureMethod 'RSA-SHA256' expected <ds
Resolution
The warning indicates that there is a mismatch coming from the IdP on the signature algorithm, as Splunk currently only supports 'RSA-SHA256'.Please ensure the IdP signature algorithm is also set to RSA-SHA256
Revision History
| Revision | Publish Date | Comments |
|---|---|---|
1.0 |
29-Sep-2026
|
Initial Release |
 Feedback
Contact Cisco
- Open a Support Case

- (Requires a Cisco Service Contract)