Splunk Instance doesn't have a "LOGOUT" button.
Available Languages
Applicability
Spunk CloudDescription
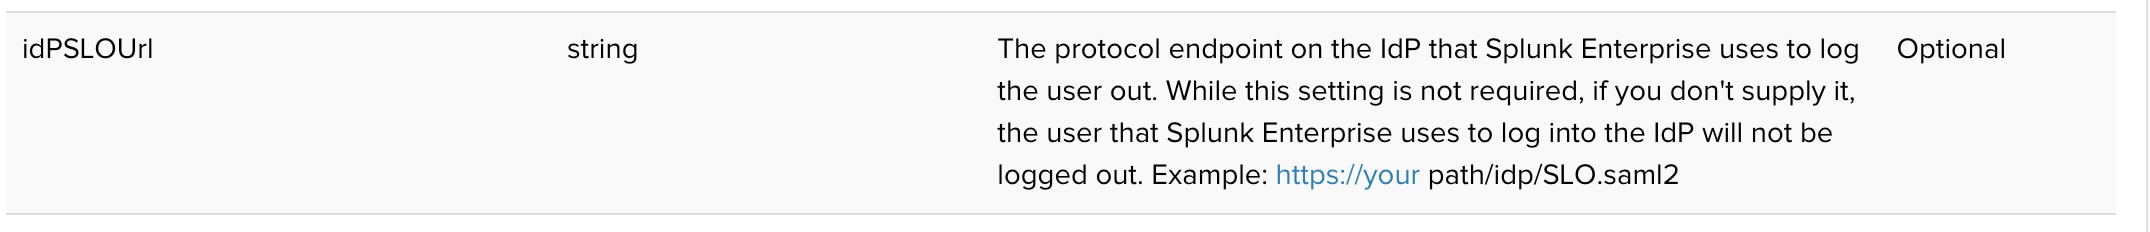
The logout link is disabled by default when using SAML. It is controlled by the idpSLOUrl setting in authentication.conf.
The definition of this setting is documented in Configure SAML SSO using configuration files on Splunk Enterprise
Note: This document is only available for Splunk Enterprise. However, the setting also applies to Splunk Cloud.
Investigation
This value can be checked using the UI by navigating the the SAML Configuration setting in Splunk Web.
- Settings> Authentication Methods
- click the SAML_settings link
- click the SAML Configuration button
- View value in "Single Log Out (SLO) URL"
The value can also be checked via command line examination of authentication.conf file and looking for the idpSLOUrl setting. ( The path from this results were set to the example used in the documentation )
splunk@sh-node:~$ splunk btool authentication list --debug | grep idpSLOUrl
/opt/splunk/etc/system/local/authentication.conf            idpSLOUrl = https://yourpath/idp/SSO.saml2
Configure basic SSO using SAML with the authentication.conf_file
Resolution
When the "Single Log Out (SLO) URL" ( idpSLOUrl in authentication.conf ) is not specified the logout button will be unavailable as seen in a typical sso configuration.
To enable the logout link an entry has to be made into the Single Log Out (SLO) URL field under SAML configuration.
- Settings> Authentication Methods
- click the SAML_settings link
- click the SAML Configuration button
- Set value in "Single Log Out (SLO) URL" to be the IdP's logout protocol/workflow. (This value is often very similar to the "Single Sign On (SSO) URL" , it is very unlikely these two values would match each other exactly.)
Important Note: To allow users to log out of the IdP and Splunk, this value must be set to the IdP's logout protocol/workflow or the user will not be logged out of either the IdP or Splunk. If the Idp's logout protocol/workflow URL is not used, the logout link will appear but when it is pressed, the user will NOT be logged out of the IdP or Splunk.
Related Links
Configure basic SSO using SAML with the authentication.conf file
Revision History
| Revision | Publish Date | Comments |
|---|---|---|
1.0 |
28-Sep-2026
|
Initial Release |
 Feedback
Contact Cisco
- Open a Support Case

- (Requires a Cisco Service Contract)