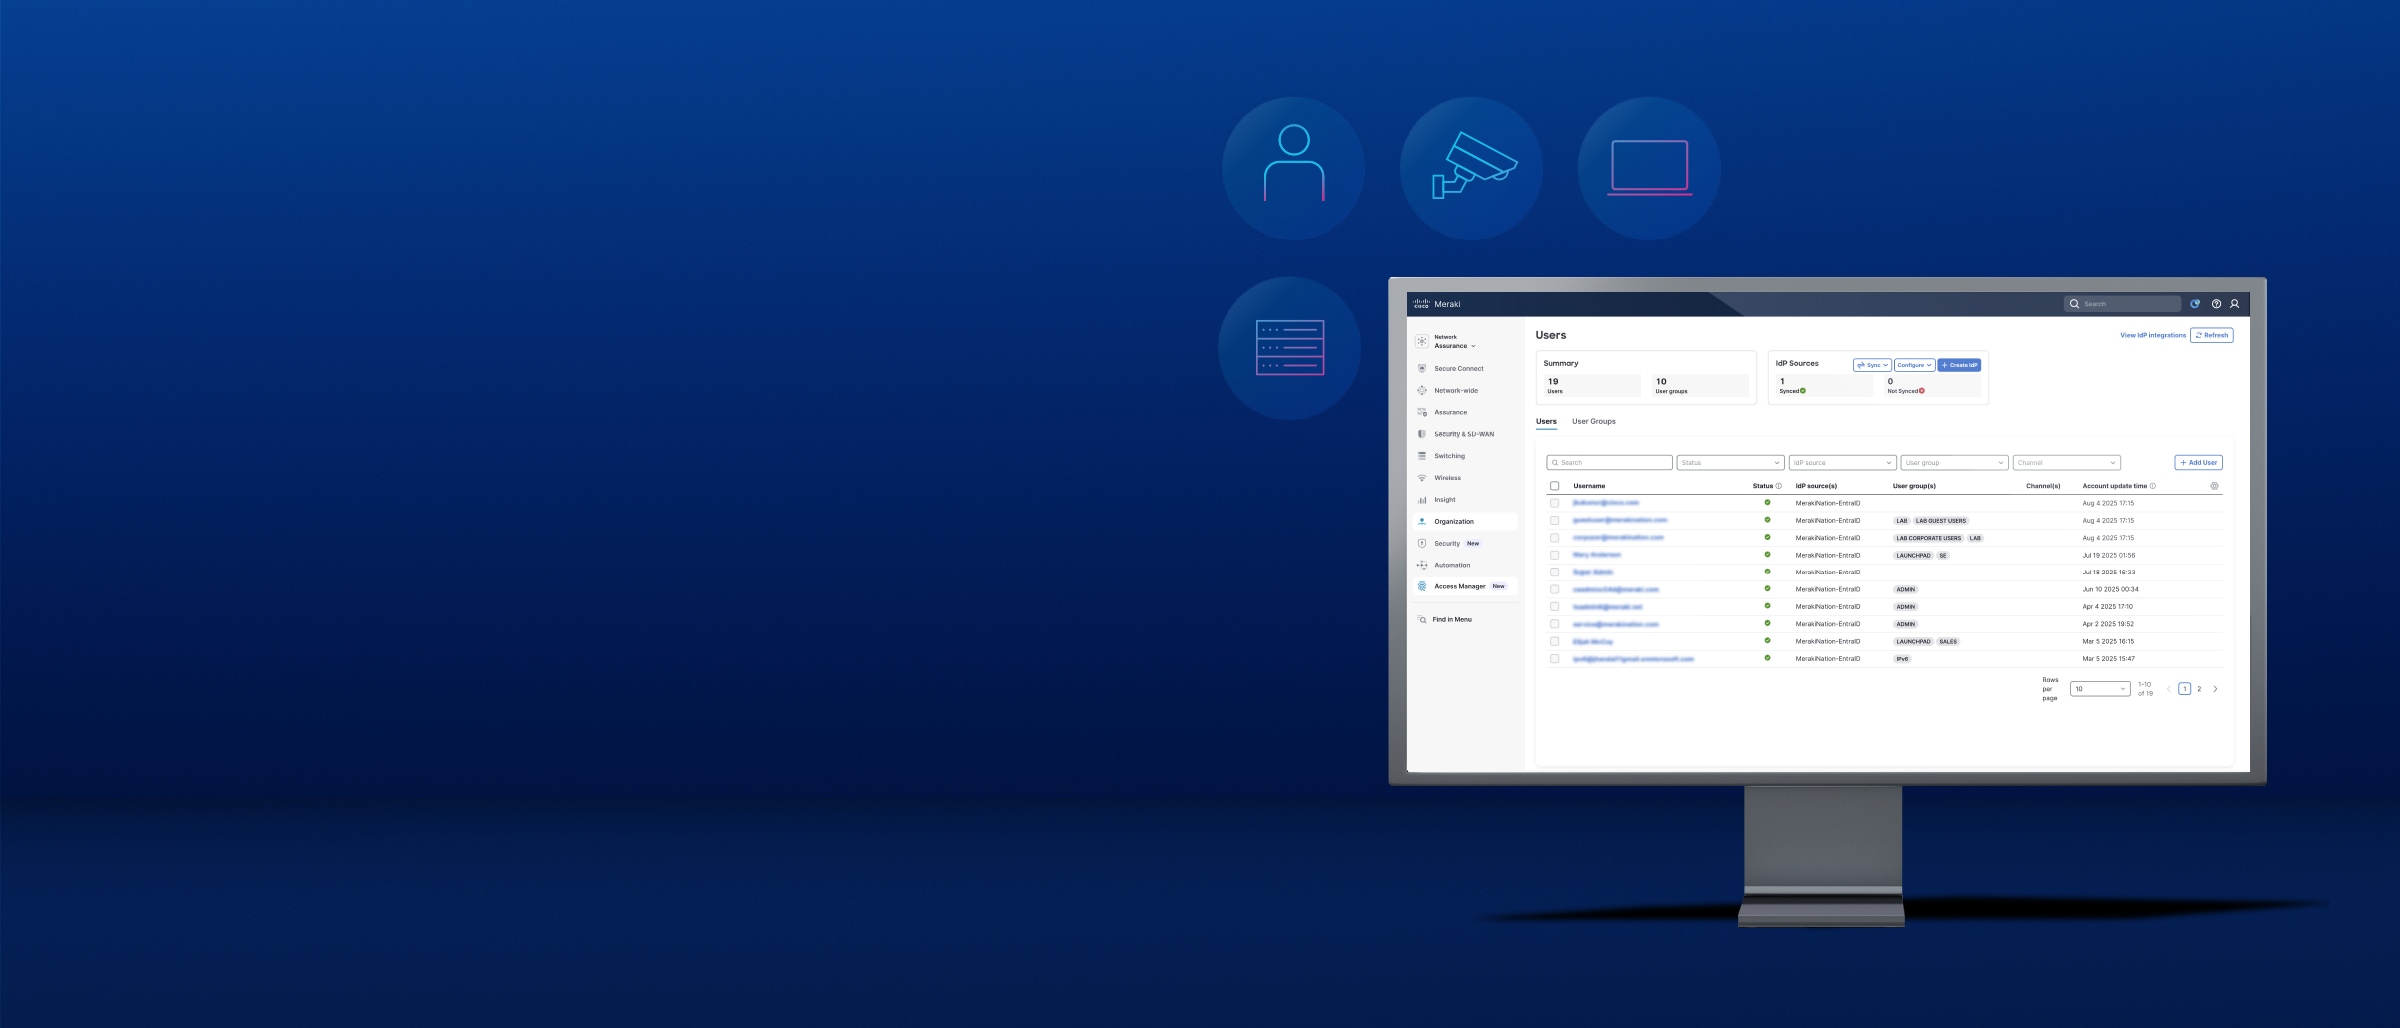
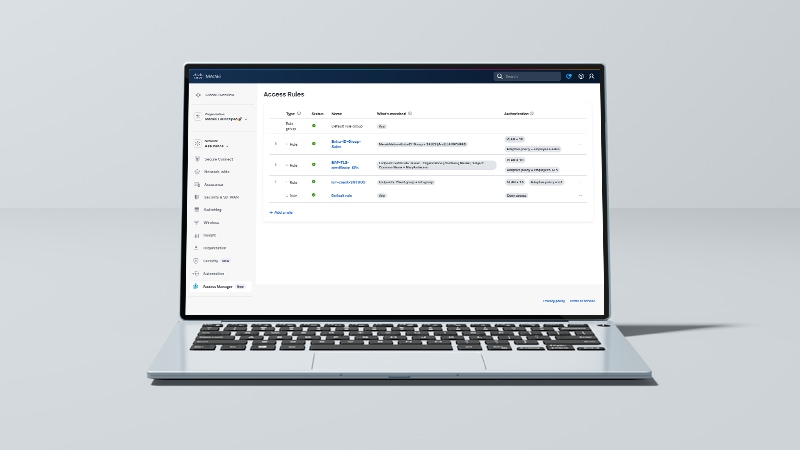
Traditional NAC often depends on appliances, external servers, and specialist skills. Access Manager delivers cloud-native identity-based access in Meraki Dashboard, helping teams deploy faster while keeping enterprise-grade policy control.
Deploy easily, segment effectively, secure comprehensively
Transform your network with identity-based security that simplifies operations, reduces hardware complexity, and delivers enterprise-grade zero-trust protection across your campus.
Embed identity into your network
Delivered as software as a service (SaaS) and integrated with the Meraki Dashboard, identity-based access is enforced seamlessly across your existing Meraki network.
Segment and protect everything
Identity-driven segmentation protects users, devices, and things across all supported infrastructure—enforced natively at every point, eliminating bottlenecks and delivering adaptive zero-trust protection.
Extend zero trust from campus to cloud
Meraki Dashboard brings together campus identity, cloud security, and context visibility with Cisco Access Manager, Cisco Secure Access, and Cisco XDR, providing continuous, adaptive zero-trust protection across your network.
At-a-Glance
Quick overview
Get a concise overview of identity-based access control with Meraki Dashboard.
Data sheet
Deeper dive
Get identity-based zero trust security without the appliances, complexity, or overhead of traditional access control solutions.
Resource landing page
One stop for all documents and resources
Access technical documentation, deployment guides, API references, video tutorials, and more—all in one place.
Solution Brief
Limit breach impact with identity-based segmentation
Learn how adaptive segmentation automatically contains compromises and prevents lateral movement—even when attackers have valid credentials.
Seamless integration ecosystem
Native Entra ID integration
Integrate seamlessly with Microsoft Entra ID for unified identity management. Leverage existing user directories without duplication or synchronization.
Unified with Meraki Dashboard
Delivered as pure SaaS within your existing Meraki Dashboard. Manage campus access, cloud security, and threat detection from one unified interface—no separate consoles or logins.
Add value to security solutions
Cisco Security Enterprise Agreement
Instant savings
Experience security software buying flexibility with one easy-to-manage agreement.
Services for security
Let the experts secure your business
Get more from your investments and enable constant vigilance to protect your organization.
Access Manager FAQs
Access Manager goes beyond authentication by combining identity, policy, segmentation, and Meraki-native enforcement. Teams can secure users, devices, and things without managing disconnected tools or separate access consoles.
Access Manager embeds identity into Meraki-managed access so policies can follow users and endpoints across supported switches and access points. It supports methods such as 802.1X, iPSK, and MAC-based access.
Yes. Access Manager can help protect managed and unmanaged endpoints by assigning the right access based on identity and context, then enforcing segmentation through the network to limit unnecessary communication.
Access Manager uses identity-based segmentation to limit each user, device, and thing to the access it needs. By enforcing policy through the network, teams can reduce unnecessary communication and contain risk faster.