Configurazione della VXLAN
Sommario
Introduzione
Questo documento descrive come configurare e verificare la VXLAN con il control plane BGP VPN sugli switch Cisco Nexus serie 9000 in un fabric spine-leaf.
Prerequisiti
Requisiti
Cisco raccomanda la conoscenza dei seguenti argomenti:
- Conoscenza del Virtual Port Channel (vPC)
- Routing IP (OSPF o IS-IS) e BGP, inclusi i riflettori di routing
- Concetti relativi al routing multicast, ad esempio la modalità sparse PIM (Protocol Independent Multicast) e il punto di rendering (RP)
Componenti usati
Le informazioni fornite in questo documento si basano sulle seguenti versioni software e hardware:
- Licenza Network Advantage
- Cisco NX-OS release 10.4(x)
- 2 Cisco Nexus N9K-C933D-GX2B come spine (riflettori di route BGP e PIM anycast RP)
- 3 x Cisco Nexus N9K-C93180YC-FX3 come foglie (VTEP); Leaf-1 e Leaf-2 sono una coppia vPC
Le informazioni discusse in questo documento fanno riferimento a dispositivi usati in uno specifico ambiente di emulazione. Su tutti i dispositivi menzionati nel documento la configurazione è stata ripristinata ai valori predefiniti. Se la rete è operativa, valutare attentamente eventuali conseguenze derivanti dall'uso dei comandi.

Nota: La configurazione illustrata in questo documento è valida per le piattaforme Nexus 9000 Cloud Scale (-EX, -FX, -FX2, -FX3, -GX, -GX2 e versioni successive) in modalità NX-OS standalone. non è applicabile agli switch Nexus 9000 in modalità ACI.
Premesse
Terminologia
| Termine |
Descrizione |
| VXLAN |
LAN estendibile virtuale: che fornisce servizi di sovrimpressione di layer 2 e layer 3 su un IP underlay indirizzato con incapsulamento MAC-in-UDP (porta UDP 4789). |
| VNI |
Identificatore di rete VXLAN: ID segmento a 24 bit. Una VNI L2 è mappata a una VLAN (dominio bridge). Un VNI L3 è associato a un VRF. |
| VTEP |
Endpoint tunnel VXLAN: Il dispositivo che incapsula e decapsula il traffico VXLAN. |
| NVE |
Network Virtualization Edge Interface (interfaccia nve1): L'interfaccia logica da cui vengono incapsulati e decapsulati. |
| BGP VPN |
Il control plane che annuncia MAC, MAC/IP (Route Type 2), prefisso IP (Route Type 5) e appartenenza VTEP (Route Type 3) tra VTEP. |
| AnyCast Gateway |
Lo stesso indirizzo IP e MAC SVI su ciascuna foglia e il gateway predefinito è sempre la foglia locale. |
| INSETTO |
Traffico broadcast, unicast sconosciuto e multicast. |
Definizione di VXLAN
- La VXLAN sovrappone i segmenti di layer 2 e layer 3 su qualsiasi sublay IP indirizzato.
- Usa l'incapsulamento MAC-in-UDP, che aggiunge 50 byte di sovraccarico al frame originale.
- Supporta fino a 16 milioni di segmenti, rispetto ai 4094 delle VLAN tradizionali.
- L'intreccio usa il protocollo Equal-Cost Multipath (ECMP) per tutti i collegamenti, senza Spanning Tree Protocol tra foglie e aculei.
Perché VXLAN BGP VPN
La versione precedente di questo documento usava flood-and-learn, in cui i VTEP imparavano gli indirizzi MAC remoti dall'flooding del piano dati. L'EVPN BGP sostituisce l'apprendimento del piano dati con un control plane ed è il modello di implementazione consigliato:
- I VTEP si scoprono a vicenda e apprendono gli indirizzi MAC e IP remoti tramite BGP, riducendo le inondazioni.
- La soppressione ARP consente di rispondere alle richieste ARP VTEP locali per gli host noti.
- Il gateway anycast distribuito e il VNI L3 per VRF ottimizzano il routing tra le subnet al primo hop.
- Sono supportate le funzionalità di multitenancy, multihoming (vPC o EVPN ESI) e l'estensione multisito.
Opzioni di replica BUM
| Modalità |
Configurazione |
Requisito per la rappresentazione |
| Multicast (in questo documento) |
mcast-group <group> nel VNI |
PIM Sparse Mode su tutti i collegamenti e i loopback di underlay e un RP (anycast RP sulle spine è comune) |
| Replica in ingresso |
protocollo bgp in entrata-replica sotto il VNI |
Solo unicast. Il VTEP in entrata invia una copia a ogni VTEP remoto che il BGP Route Type 3 ha appreso per il VNI. |
Configurazione
Esempio di rete
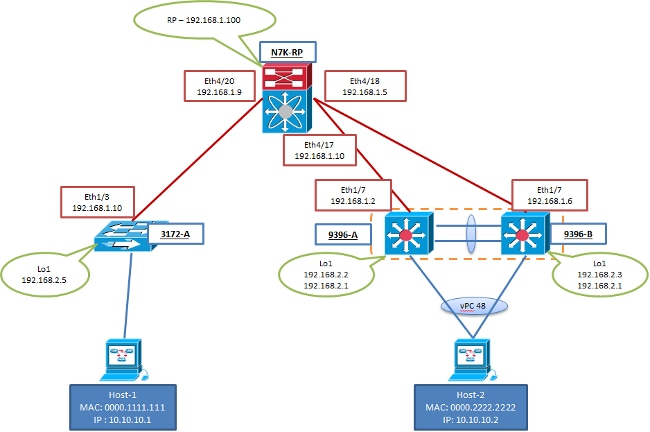
Indirizzamento
| Sul dispositivo bootflash o slot0: |
Loopback0 (routing, BGP, PIM) |
Loopback1 (origine NVE) |
Uplink (da Eth1/49 a Spine-1, da Eth1/50 a Spine-2) |
| Dorso-1 |
10.0.0.1 |
- |
Da Eth1/1-3 a Leaf-1/2/3: 10.1.1.0, 0,2, 0,4/31 |
| Dorso-2 |
10.0.0.2 |
- |
Da Eth1/1-3 a Leaf-1/2/3: 10.1.2.0, 0,2, 0,4/31 |
| Foglia-1 |
10.0.0.11 |
10.0.1.11, secondario 10.0.1.112 |
10.1.1.1/31, 10.1.2.1/31 |
| Foglia 2 |
10.0.0.12 |
10.0.1.12, secondario 10.0.1.12 |
10.1.1.3/31, 10.1.2.3/31 |
| Foglia-3 |
10.0.0.13 |
10.0.1.13 |
10.1.1.5/31, 10.1.2.5/31 |
| Oggetto Overlay |
Valore |
| Anycast RP |
10.254.254.1 (loopback254 su entrambi gli aculei), gruppi 239.1.1.0/24 |
| VLAN 10 / VNI L2 |
10010, mcast-group 239.1.1.10, gateway 192.168.10.1/24 |
| VLAN 20 / VNI L2 |
10020, mcast-group 239.1.1.20, gateway 192.168.20.1/24 |
| VRF Tenant-A / L3 VNI |
5000 (VLAN 500) |
| MAC gateway Anycast |
2020.0000.00aa |
| SVI sottostante di backup vPC |
VLAN 3900, 10.255.255.0/31 (foglia-1) e 10.255.255.1/31 (foglia-2) |
Nota: Usare loopback separati per l'origine NVE (Loopback1), il routing e il peering BGP (Loopback0). Sui VTEP vPC, il loopback dell'origine NVE ha un IP secondario che è lo stesso su entrambi i peer. I VTEP remoti utilizzano questo indirizzo condiviso (vPC anycast VTEP) per raggiungere la coppia vPC come un unico VTEP.
Configurazioni
Queste configurazioni mostrano solo le parti relative alla base e alla VXLAN. Configurare le funzionalità di gestione, AAA e altre in base ai requisiti.
Dorso-1
nv overlay evpn
feature ospf
feature bgp
feature pim
feature nv overlay

ip pim rp-address 10.254.254.1 group-list 239.1.1.0/24
ip pim anycast-rp 10.254.254.1 10.0.0.1
ip pim anycast-rp 10.254.254.1 10.0.0.2

interface loopback0
  description Routing / BGP / Anycast-RP member
  ip address 10.0.0.1/32
  ip router ospf UNDERLAY area 0.0.0.0
  ip pim sparse-mode

interface loopback254
  description Anycast-RP
  ip address 10.254.254.1/32
  ip router ospf UNDERLAY area 0.0.0.0
  ip pim sparse-mode

interface Ethernet1/1
  description to Leaf-1 Eth1/49
  no switchport
  mtu 9216
  medium p2p
  ip address 10.1.1.0/31
  ip ospf network point-to-point
  ip router ospf UNDERLAY area 0.0.0.0
  ip pim sparse-mode
  no shutdown

interface Ethernet1/2
  description to Leaf-2 Eth1/49
  no switchport
  mtu 9216
  medium p2p
  ip address 10.1.1.2/31
  ip ospf network point-to-point
  ip router ospf UNDERLAY area 0.0.0.0
  ip pim sparse-mode
  no shutdown

interface Ethernet1/3
  description to Leaf-3 Eth1/49
  no switchport
  mtu 9216
  medium p2p
  ip address 10.1.1.4/31
  ip ospf network point-to-point
  ip router ospf UNDERLAY area 0.0.0.0
  ip pim sparse-mode
  no shutdown

router ospf UNDERLAY
  router-id 10.0.0.1

router bgp 65000
  router-id 10.0.0.1
  address-family l2vpn evpn
  template peer VTEP
    remote-as 65000
    update-source loopback0
    address-family l2vpn evpn
      send-community
      send-community extended
      route-reflector-client
  neighbor 10.0.0.11
    inherit peer VTEP
  neighbor 10.0.0.12
    inherit peer VTEP
  neighbor 10.0.0.13
    inherit peer VTEP
Dorso-2
interface loopback0
  ip address 10.0.0.2/32
interface Ethernet1/1
  ip address 10.1.2.0/31
interface Ethernet1/2
  ip address 10.1.2.2/31
interface Ethernet1/3
  ip address 10.1.2.4/31
router ospf UNDERLAY
  router-id 10.0.0.2
router bgp 65000
  router-id 10.0.0.2
Foglia-1 (vPC VTEP)
nv overlay evpn
feature ospf
feature bgp
feature pim
feature fabric forwarding
feature interface-vlan
feature vn-segment-vlan-based
feature lacp
feature vpc
feature nv overlay

fabric forwarding anycast-gateway-mac 2020.0000.00aa
ip pim rp-address 10.254.254.1 group-list 239.1.1.0/24

vlan 10
  vn-segment 10010
vlan 20
  vn-segment 10020
vlan 500
  name L3VNI-Tenant-A
  vn-segment 50000
vlan 3900
  name vPC-backup-underlay

system nve infra-vlans 3900

vrf context Tenant-A
  vni 50000
  rd auto
  address-family ipv4 unicast
    route-target both auto
    route-target both auto evpn

vpc domain 10
  peer-switch
  role priority 10
  peer-keepalive destination 172.16.0.2 source 172.16.0.1 vrf management
  delay restore 150
  peer-gateway
  ip arp synchronize
  ipv6 nd synchronize

interface port-channel1
  description vPC peer-link
  switchport
  switchport mode trunk
  switchport trunk allowed vlan 10,20,500,3900
  spanning-tree port type network
  vpc peer-link

interface port-channel11
  description Server-1
  switchport
  switchport mode trunk
  switchport trunk allowed vlan 10,20
  spanning-tree port type edge trunk
  mtu 9216
  vpc 11

interface Vlan10
  no shutdown
  vrf member Tenant-A
  no ip redirects
  ip address 192.168.10.1/24
  fabric forwarding mode anycast-gateway

interface Vlan20
  no shutdown
  vrf member Tenant-A
  no ip redirects
  ip address 192.168.20.1/24
  fabric forwarding mode anycast-gateway

interface Vlan500
  description L3VNI Tenant-A
  no shutdown
  vrf member Tenant-A
  no ip redirects
  ip forward

interface Vlan3900
  description vPC backup underlay
  no shutdown
  mtu 9216
  no ip redirects
  ip address 10.255.255.0/31
  ip ospf network point-to-point
  ip router ospf UNDERLAY area 0.0.0.0
  ip pim sparse-mode

interface nve1
  no shutdown
  host-reachability protocol bgp
  advertise virtual-rmac
  source-interface loopback1
  member vni 10010
    suppress-arp
    mcast-group 239.1.1.10
  member vni 10020
    suppress-arp
    mcast-group 239.1.1.20
  member vni 50000 associate-vrf

interface Ethernet1/1
  description Server-1
  switchport
  switchport mode trunk
  switchport trunk allowed vlan 10,20
  mtu 9216
  channel-group 11 mode active
  no shutdown

interface Ethernet1/53-54
  description vPC peer-link to Leaf-2
  switchport
  switchport mode trunk
  switchport trunk allowed vlan 10,20,500,3900
  channel-group 1 mode active
  no shutdown

interface Ethernet1/49
  description to Spine-1 Eth1/1
  no switchport
  mtu 9216
  medium p2p
  ip address 10.1.1.1/31
  ip ospf network point-to-point
  ip router ospf UNDERLAY area 0.0.0.0
  ip pim sparse-mode
  no shutdown

interface Ethernet1/50
  description to Spine-2 Eth1/1
  no switchport
  mtu 9216
  medium p2p
  ip address 10.1.2.1/31
  ip ospf network point-to-point
  ip router ospf UNDERLAY area 0.0.0.0
  ip pim sparse-mode
  no shutdown

interface loopback0
  description Routing / BGP
  ip address 10.0.0.11/32
  ip router ospf UNDERLAY area 0.0.0.0
  ip pim sparse-mode

interface loopback1
  description NVE source
  ip address 10.0.1.11/32
  ip address 10.0.1.112/32 secondary
  ip router ospf UNDERLAY area 0.0.0.0
  ip pim sparse-mode

router ospf UNDERLAY
  router-id 10.0.0.11

router bgp 65000
  router-id 10.0.0.11
  address-family l2vpn evpn
    advertise-pip
  template peer SPINE-RR
    remote-as 65000
    update-source loopback0
    address-family l2vpn evpn
      send-community
      send-community extended
  neighbor 10.0.0.1
    inherit peer SPINE-RR
  neighbor 10.0.0.2
    inherit peer SPINE-RR
  vrf Tenant-A
    address-family ipv4 unicast
      advertise l2vpn evpn

evpn
  vni 10010 l2
    rd auto
    route-target import auto
    route-target export auto
  vni 10020 l2
    rd auto
    route-target import auto
    route-target export auto
Nota: Sui VTEP vPC su scala cloud, la SVI (VLAN 3900) di backup sottostante deve essere elencata nelle infra-vlan di system nve. Questa VLAN deve essere nella VRF predefinita, non deve avere un segmento VN e deve essere consentita sul collegamento peer. Trasporta il traffico VXLAN sul collegamento peer per le porte orfane e quando un peer vPC perde tutti i suoi uplink. Non configurare le VLAN infra con ID separati da 512, ad esempio 10 e 522.
annuncio-pip e annuncio di virtual-rmac dai peer vPC, che annunciano le route di tipo-5 (prefisso) e le route host-orfano con il relativo IP primario (PIP) e il proprio MAC router. Senza questi, il traffico verso un host dietro un solo peer può essere inviato al peer che non può raggiungerlo.
La soppressione ARP (suppress-arp) è supportata solo per i VNI in cui il VTEP è il gateway anycast distribuito per quel VNI.
Foglia 2 (vPC VTEP)
vpc domain 10
  role priority 20
  peer-keepalive destination 172.16.0.1 source 172.16.0.2 vrf management

interface Vlan3900
  ip address 10.255.255.1/31

interface Ethernet1/49
  ip address 10.1.1.3/31
interface Ethernet1/50
  ip address 10.1.2.3/31

interface loopback0
  ip address 10.0.0.12/32
interface loopback1
  ip address 10.0.1.12/32
  ip address 10.0.1.112/32 secondary

router ospf UNDERLAY
  router-id 10.0.0.12
router bgp 65000
  router-id 10.0.0.12
Attenzione: La configurazione NVE (VNI, gruppi mcast, interfaccia di origine, IP secondario) deve essere identica su entrambi i peer vPC. Una mancata corrispondenza è un errore di coerenza di tipo 1 del vPC e l'interfaccia NVE o i VNI sono sospesi. Eseguire il comando show vpc consistency-parameters global.
Leaf-3 (VTEP autonomo)
nv overlay evpn
feature ospf
feature bgp
feature pim
feature fabric forwarding
feature interface-vlan
feature vn-segment-vlan-based
feature nv overlay

fabric forwarding anycast-gateway-mac 2020.0000.00aa
ip pim rp-address 10.254.254.1 group-list 239.1.1.0/24

vlan 10
  vn-segment 10010
vlan 20
  vn-segment 10020
vlan 500
  name L3VNI-Tenant-A
  vn-segment 50000

vrf context Tenant-A
  vni 50000
  rd auto
  address-family ipv4 unicast
    route-target both auto
    route-target both auto evpn

interface Vlan10
  no shutdown
  vrf member Tenant-A
  no ip redirects
  ip address 192.168.10.1/24
  fabric forwarding mode anycast-gateway

interface Vlan20
  no shutdown
  vrf member Tenant-A
  no ip redirects
  ip address 192.168.20.1/24
  fabric forwarding mode anycast-gateway

interface Vlan500
  no shutdown
  vrf member Tenant-A
  no ip redirects
  ip forward

interface nve1
  no shutdown
  host-reachability protocol bgp
  source-interface loopback1
  member vni 10010
    suppress-arp
    mcast-group 239.1.1.10
  member vni 10020
    suppress-arp
    mcast-group 239.1.1.20
  member vni 50000 associate-vrf

interface Ethernet1/1
  description Server-2
  switchport
  switchport access vlan 10
  spanning-tree port type edge
  no shutdown

interface Ethernet1/2
  description Server-3
  switchport
  switchport access vlan 20
  spanning-tree port type edge
  no shutdown

interface Ethernet1/49
  description to Spine-1 Eth1/3
  no switchport
  mtu 9216
  medium p2p
  ip address 10.1.1.5/31
  ip ospf network point-to-point
  ip router ospf UNDERLAY area 0.0.0.0
  ip pim sparse-mode
  no shutdown

interface Ethernet1/50
  description to Spine-2 Eth1/3
  no switchport
  mtu 9216
  medium p2p
  ip address 10.1.2.5/31
  ip ospf network point-to-point
  ip router ospf UNDERLAY area 0.0.0.0
  ip pim sparse-mode
  no shutdown

interface loopback0
  ip address 10.0.0.13/32
  ip router ospf UNDERLAY area 0.0.0.0
  ip pim sparse-mode

interface loopback1
  description NVE source
  ip address 10.0.1.13/32
  ip router ospf UNDERLAY area 0.0.0.0
  ip pim sparse-mode

router ospf UNDERLAY
  router-id 10.0.0.13

router bgp 65000
  router-id 10.0.0.13
  template peer SPINE-RR
    remote-as 65000
    update-source loopback0
    address-family l2vpn evpn
      send-community
      send-community extended
  neighbor 10.0.0.1
    inherit peer SPINE-RR
  neighbor 10.0.0.2
    inherit peer SPINE-RR
  vrf Tenant-A
    address-family ipv4 unicast
      advertise l2vpn evpn

evpn
  vni 10010 l2
    rd auto
    route-target import auto
    route-target export auto
  vni 10020 l2
    rd auto
    route-target import auto
    route-target export auto
Facoltativo: Replica in ingresso anziché multicast
Se l'underlay non esegue il multicast, sostituire mcast-group con la replica in entrata basata su BGP su ogni VTEP. PIM e la configurazione RP non sono richiesti per i VNI L2.
interface nve1
  member vni 10010
    suppress-arp
    ingress-replication protocol bgp
  member vni 10020
    suppress-arp
    ingress-replication protocol bgp
Verifica
Per verificare che la configurazione funzioni correttamente, consultare questa sezione.
Cisco CLI Analyzer (solo utenti registrati) supporta alcuni comandi show. Usare Cisco CLI Analyzer per visualizzare un'analisi degli output del comando show.
| Area |
Comandi |
| Sottolineatura |
show ip ospf neighbors, show ip route 10.0.1.13, show ip pim neighbors, show ip pim rp |
| Piano di controllo sovrapposizione |
show bgp l2vpn evpn summary, show bgp l2vpn evpn |
| NVE |
show nve interface nve1 detail, show nve peer, show nve vni |
| Apprendimento MAC/IP |
show mac address-table vlan 10, show l2route evpn mac all, show l2route evpn mac-ip all, show ip arp suppression-cache detail |
| VNI L3 |
show ip route vrf Tenant-A, show bgp l2vpn evpn route-type 2, show bgp l2vpn evpn route-type 5 |
| Replica Multicast |
show ip route 239.1.1.10 |
| vPC |
show vpc, show vpc consistency-parameters global, show system nve infra-vlan |
Questi output provengono da uno stato stabile dopo l'invio del traffico tra Server-1, Server-2 e Server-3.
Sottolineatura
Leaf-1# show ip pim rp
PIM RP Status Information for VRF "default"
BSR disabled
Auto-RP disabled
BSR RP Candidate policy: None
BSR RP policy: None
Auto-RP Announce policy: None
Auto-RP Discovery policy: None

Anycast-RP 10.254.254.1 members:
  10.0.0.1  10.0.0.2

RP: 10.254.254.1, (0),
 uptime: 1d01h   priority: 255,
 RP-source: (local),
 group ranges:
 239.1.1.0/24
Piano di controllo sovrapposizione
Leaf-1# show bgp l2vpn evpn summary
BGP summary information for VRF default, address family L2VPN EVPN
BGP router identifier 10.0.0.11, local AS number 65000
BGP table version is 58, L2VPN EVPN config peers 2, capable peers 2

Neighbor        V    AS    MsgRcvd    MsgSent   TblVer  InQ OutQ Up/Down  State/PfxRcd
10.0.0.1        4 65000       1520       1488       58    0    0 1d01h    9
10.0.0.2        4 65000       1519       1490       58    0    0 1d01h    9
NVE e VNI
Leaf-1# show nve interface nve1 detail
Interface: nve1, State: Up, encapsulation: VXLAN
 VPC Capability: VPC-VIP-Only [notified]
 Local Router MAC: 5254.0011.1b08
 Host Learning Mode: Control-Plane
 Source-Interface: loopback1 (primary: 10.0.1.11, secondary: 10.0.1.112)
 Source Interface State: Up
 Virtual RMAC Advertisement: Yes
 NVE Flags:
 Interface Handle: 0x49000001
 Source Interface hold-down-time: 180
 Source Interface hold-up-time: 30
 Remaining hold-down time: 0 seconds
 Virtual Router MAC: 0200.0a00.0170

Leaf-1# show nve peers
Interface Peer-IP                                 State LearnType Uptime   Router-Mac
--------- --------------------------------------  ----- --------- -------- -----------------
nve1      10.0.1.13                               Up    CP        1d01h    5254.0013.1b08

Leaf-1# show nve vni
Codes: CP - Control Plane        DP - Data Plane
       UC - Unconfigured         SA - Suppress ARP
       S-ND - Suppress ND
       SU - Suppress Unknown Unicast
       Xconn - Crossconnect
       MS-IR - Multisite Ingress Replication
       HYB - Hybrid IRB mode

Interface VNI      Multicast-group   State Mode Type [BD/VRF]      Flags
--------- -------- ----------------- ----- ---- ------------------ -----
nve1      10010    239.1.1.10        Up    CP   L2 [10]            SA
nve1      10020    239.1.1.20        Up    CP   L2 [20]            SA
nve1      50000    n/a               Up    CP   L3 [Tenant-A]
Nota: Con l'EVPN BGP, i peer NVE vengono visualizzati quando un VTEP remoto annuncia le route per un VNI configurato localmente (LearnType CP). Leaf-3 vede la coppia vPC come un peer, il VTEP AnyCast 10.0.1.12. Con ADVERTIise-pip, Leaf-3 vede anche gli IP primari vPC 10.0.1.11 e 10.0.1.12 per il tipo-5 e le route orfane.
Apprendimento MAC/IP
Leaf-1# show l2route evpn mac all
Flags -(Rmac):Router MAC (Stt):Static (L):Local (R):Remote (V):vPC link
(Dup):Duplicate (Spl):Split (Rcv):Recv (AD):Auto-Delete (D):Del Pending
(S):Stale (C):Clear, (Ps):Peer Sync (O):Re-Originated (Nho):NH-Override
(Pf):Permanently-Frozen, (Orp): Orphan

Topology    Mac Address    Prod   Flags         Seq No     Next-Hops
----------- -------------- ------ ------------- ---------- ----------------
10          0050.5601.0a0a Local  L,            0          Po11
10          0050.5603.0a14 BGP    SplRcv        0          10.0.1.13 (Label: 10010)
20          0050.5603.1e1e BGP    SplRcv        0          10.0.1.13 (Label: 10020)

Leaf-1# show ip arp suppression-cache detail
Flags: + - Adjacencies synced via CFSoE
       L - Local Adjacency
       R - Remote Adjacency
       L2 - Learnt over L2 interface
       PS - Added via L2RIB, Peer Sync
       RO - Dervied from L2RIB Peer Sync Entry

Ip Address      Age      Mac Address    Vlan Physical-ifindex    Flags    Remote Vtep Addrs

192.168.10.10   00:02:11 0050.5601.0a0a   10 port-channel11       L
192.168.10.20   00:05:42 0050.5603.0a14   10 (null)               R        10.0.1.13
Routing VNI L3
Leaf-1# show ip route vrf Tenant-A 192.168.20.30
IP Route Table for VRF "Tenant-A"
'*' denotes best ucast next-hop
'**' denotes best mcast next-hop
'[x/y]' denotes [preference/metric]
'%<string>' in via output denotes VRF <string>

192.168.20.30/32, ubest/mbest: 1/0
    *via 10.0.1.13%default, [200/0], 00:10:21, bgp-65000, internal, tag 65000, segid: 50000 tunnelid: 0xa00010d encap: VXLAN
vPC
Leaf-1# show vpc consistency-parameters global | include Nve|Src|Sec|Host
Nve1 Adm St, Src Adm St,    1     Up, Up, 10.0.1.112, CP,    Up, Up, 10.0.1.112, CP,
Sec IP, Host Reach, VMAC          TRUE, Disabled,               TRUE, Disabled,
Adv, SA,mcast l2, mcast           0.0.0.0, 0.0.0.0, Disabled,   0.0.0.0, 0.0.0.0, Disabled,
Nve Vni Configuration       1     10010-10020                   10010-10020

Leaf-1# show system nve infra-vlans
Currently active infra-vlans: 3900
Formato del pacchetto
Tutti i pacchetti VXLAN provengono dal loopback dell'origine NVE del VTEP in entrata. Per gli host sulle porte vPC, si tratta dell'IP secondario condiviso (10.0.1.12). Il traffico unicast noto va all'IP NVE del VTEP remoto. Il traffico BUM va al gruppo multicast della VNI, o con la replica in entrata, e una copia unicast va a ciascun VTEP remoto.
| Intestazione |
Esempio: Da server-1 a server-2 (VLAN 10, VNI L2) |
Esempio: Da server-1 a server-3 (routing, VNI L3) |
| Ethernet esterna |
MAC uplink foglia-1 su MAC dorso |
MAC uplink foglia-1 su MAC dorso |
| IP esterno |
da 10.0.1.12 a 10.0.1.13 |
da 10.0.1.12 a 10.0.1.13 (da 10.0.1.11 a 10.0.1.13 se il traffico proviene da una porta orfana e si utilizza advertising-pip) |
| UDP esterno |
La porta di origine è un hash del flusso interno (entropia per ECMP); porta di destinazione 4789 |
Uguale |
| VXLAN |
Flag 0x08 (flag I), VNI 10010 |
Flag 0x08, VNI 50000 |
| Ethernet interna |
MAC da Server-1 a MAC Server-2 |
MAC router foglia-1 su MAC router foglia-3 |
| IP interno |
da 192.168.10.10 a 192.168.10.20 |
da 192.168.10.10 a 192.168.20.30 (TTL diminuito) |
Nota: VXLAN aggiunge 50 byte al frame originale. Impostare l'MTU sottostante (tutti gli uplink spine e foglia e la SVI di backup vPC) su almeno 50 byte in più rispetto alla MTU dell'host più grande. Si consiglia 9216.
Risoluzione dei problemi
| Sintomo |
Assegno |
Causa comune |
| Peer NVE non in visualizzazione peer NVE |
show bgp l2vpn evpn summary, show ip route <IP NVE remoto>, show nve vni |
Sessione VPN BGP inattiva; loopback NVE remoto non pubblicizzato nella base; VNI non configurato su entrambi i VTEP; elemento send-community esteso mancante |
| Interfaccia NVE inattiva o VNI sospesi su un VTEP vPC |
show nve interface nve1 detail, show vpc consistency-parameters global |
Mancata corrispondenza della configurazione NVE tra peer; il loopback della sorgente è ancora nel timer di attesa dopo un ricaricamento; IP secondario mancante o diverso |
| Gli host nella stessa VNI non possono comunicare oppure ARP non riesce |
show l2route evpn mac all, show ip arp suppression-cache detail, show ip mroute <gruppo> |
RT-2 non ricevuto (route-target o mancata corrispondenza VNI); BUM non replicato (nessun router adiacente PIM, senza RP, PIM mancante nel loopback NVE); suppress-arp su un VNI senza SVI anycast gateway |
| Routing tra VNI non riuscito |
show ip route vrf Tenant-A, show nve vni (stato VNI L3), show bgp l2vpn evpn route-type 5 |
VLAN L3 o SVI mancante o chiusa; vni mancante nel contesto VRF; pubblicizzare l2vpn evpn mancante nel BGP VRF; route-target entrambi auto evpn mancante |
| Il traffico ha esito negativo solo per le porte orfane o dopo che un peer vPC ha perso i propri uplink |
show system nve infra-vlan, show ip ospf neighbors vrf predefinito |
SVI sottostante di backup mancante, non presente nelle infra-vlan di sistema o non consentita sul collegamento peer |
| Pacchetti grandi scartati, pacchetti piccoli funzionanti |
show interface <uplink> (errori TX), ping con bit DF impostato tra i loopback NVE |
MTU underlay troppo piccola per il sovraccarico della VXLAN |
Nota: Questi elementi non sono supportati come uplink VXLAN:
- Sottointerfacce di layer 3
- SVI non configurate nelle infra-vlan di system nve
Il loopback dell'origine NVE deve trovarsi nel VRF predefinito.
Informazioni correlate
- Guida alla configurazione di Cisco Nexus serie 9000 NX-OS VXLAN, versione 10.5(x)
- Informazioni e configurazione di Nexus 9000 vPC con best practice
- Documentazione e supporto tecnico – Cisco Systems
Cronologia delle revisioni
| Revisione | Data di pubblicazione | Commenti |
|---|---|---|
3.0 |
28-Oct-2026
|
Introduzione aggiornata, ortografia, grammatica, spaziatura, righe orizzontali inserite per separare le sezioni per la leggibilità, avvisi CCW fissi, URL, testo alternativo. |
2.0 |
15-Nov-2022
|
Errori di introduzione aggiornati, disclaimer legale, gerund, traduzione automatica, SEO, requisiti di stile e formattazione. |
1.0 |
10-Jul-2015
|
Versione iniziale |

 Feedback
