FlexPod Datacenter: Citrix Virtual Apps & Desktops with vSphere 8 (2600 Sessions) Deployment Guide
Available Languages
Bias-Free Language
The documentation set for this product strives to use bias-free language. For the purposes of this documentation set, bias-free is defined as language that does not imply discrimination based on age, disability, gender, racial identity, ethnic identity, sexual orientation, socioeconomic status, and intersectionality. Exceptions may be present in the documentation due to language that is hardcoded in the user interfaces of the product software, language used based on RFP documentation, or language that is used by a referenced third-party product. Learn more about how Cisco is using Inclusive Language.
- US/Canada 800-553-2447
- Worldwide Support Phone Numbers
- All Tools
 Feedback
 Feedback
In partnership with:
About the Cisco Validated Design Program
The Cisco Validated Design (CVD) program consists of systems and solutions designed, tested, and documented to facilitate faster, more reliable, and more predictable customer deployments. For more information, go to: http://www.cisco.com/go/designzone.
Cisco Validated Designs (CVDs) consist of systems and solutions that are designed, tested, and documented to facilitate and improve customer deployments. These designs incorporate a wide range of technologies and products into a portfolio of solutions that have been developed to address the business needs of our customers.
This CVD details a high-performance, scalable Virtual Desktop Infrastructure (VDI) solution built on the FlexPod Datacenter Base Configuration—a proven, converged infrastructure combining Cisco UCS X-Series compute, Cisco Nexus 9000 Series switching, and the latest NetApp AFF A50 All-Flash system.
This solution delivers a best-practice data center architecture optimized for Citrix Virtual Apps and Desktops, utilizing VMware vSphere 8.0 U3 as the hypervisor. By integrating the Cisco UCS X215c M8 Compute Node with NetApp’s AFF A50 high-performance storage, the platform provides a compact, reliable, and efficient foundation for modern application workloads, Hosted Shared Desktops based on the Windows Server 2022 and Windows 11 virtual desktops.
This design ensures an exceptional end-user experience and validated by Login Enterprise 5.14.7 (Knowledge Worker workload). The architecture acts as a modular, large-scale building block capable of supporting up to 2,600 users, including a mix of:
● Windows Server 2022 based Hosted Shared Desktops: 2,600 sessions.
● Persistent/Non-Persistent Windows 11: 1,600 desktops.
To address the complexities of modern IT, this FlexPod solution can also be delivered as Infrastructure as Code (IaC). This approach eliminates manual configuration errors, ensuring consistency across deployments. Furthermore, the Cisco Intersight cloud platform provides comprehensive lifecycle management, orchestration, and workload optimization, allowing IT teams to manage the infrastructure with greater agility and insight.
If you’re interested in understanding the FlexPod design and deployment details, including the configuration of various elements of design and associated best practices, refer to Cisco Validated Designs for FlexPod, here: https://www.cisco.com/c/en/us/solutions/design-zone/data-center-design-guides/flexpod-design-guides.html
This chapter contains the following:
● Audience
● FlexPod Cisco Validated Design Advantages for VDI
● Cisco Desktop Virtualization Solutions
The FlexPod Datacenter Base Configuration represents a cohesive and flexible infrastructure solution that combines computing hardware, networking, and storage resources into a single, integrated architecture. Designed as a collaborative effort between Cisco and NetApp, this converged infrastructure platform is engineered to deliver high levels of efficiency, scalability, and performance, suitable for a multitude of datacenter workloads, such as complex virtual desktop infrastructure (VDI). By standardizing on a validated design, organizations can accelerate deployment, reduce operational complexities, and confidently scale their IT operations to meet evolving business demands. The FlexPod architecture leverages Cisco's Unified Computing System (Cisco UCS) servers, Cisco Nexus and MDS networking, and NetApp innovative storage systems, providing a robust foundation for virtual desktop environments.
The intended audience for this document includes, but is not limited to IT architects, sales engineers, field consultants, professional services, IT managers, IT engineers, partners, and customers who are interested in learning about and deploying the Virtual Desktop Infrastructure (VDI)
This document provides a step-by-step design, configuration, and implementation guide for the Cisco Validated Design for a large-scale Citrix Virtual Apps and Desktops Windows Sever 2022 based Hosted Shared Desktop (RDSH) sessions and Windows 11 Virtual Desktops with NetApp AFF A50, Cisco UCS X215 M8 Compute Node, and Cisco Nexus 9000 Series Ethernet Switches.
This version of the FlexPod VDI Design is based on the latest FlexPod Datacenter infrastructure.
The following design elements distinguish this version of FlexPod from previous models:
● Deploying and managing Cisco UCS X215c M8 Compute Node using Cisco Intersight
● Support for Cisco UCS X215c M8 Compute Node with AMD EPYC 9005 series processors and 6400 MHz memory
● Support for the Cisco Intersight with FW 5.3 or higher
● Validation of Cisco Nexus 9000 and Cisco MDS 9000 series switches with NetApp AFF A50 system
● Support for NetApp Storage AFF A50 with ONTAP version 9.17.1P4
● Citrix Virtual Apps and Desktops 2402 LTSR CU3 Citrix Remote Desktop Server Hosted Sessions
● Citrix Virtual Apps and Desktops 2402 LTSR CU3 Citrix Provisioning Server virtual machines
● Citrix Virtual Apps and Desktops 2402 LTSR CU3 Citrix persistent full desktops
● Support for VMware vSphere 8.0 U3
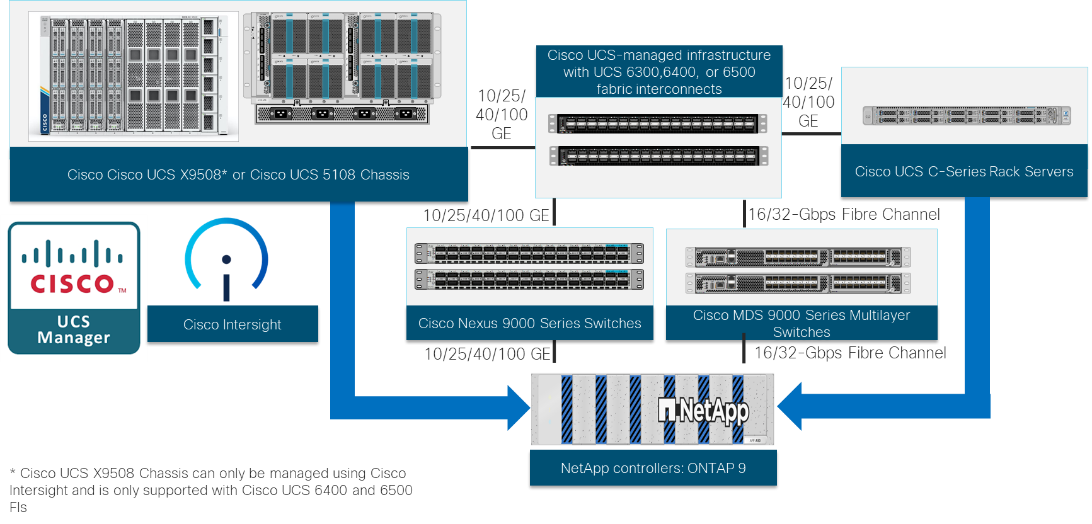
FlexPod is a defined set of hardware and software that serves as an integrated foundation for both virtualized and non-virtualized solutions. VMware vSphere built on FlexPod includes NetApp AFF, and ASA storage, Cisco Nexus networking, Cisco MDS storage networking, Cisco UCS, and VMware vSphere software in a single package. The design is flexible enough that the networking, computing, and storage can fit in one data center rack or be deployed according to your data center design. Port density enables the networking components to accommodate multiple configurations of this kind.
One benefit of the FlexPod architecture is the ability to customize or "flex" the environment to suit your requirements. A FlexPod can easily be scaled as requirements and demand change. The unit can be scaled both up (adding resources to a FlexPod unit) and out (adding more FlexPod units). The reference architecture detailed in this document highlights the resiliency, cost benefit, and ease of deployment of a Fibre Channel and IP-based storage solution. A storage system capable of serving multiple protocols across a single interface allows for personalization and investment protection because it truly is a wire-once architecture.
The following are the benefits of FlexPod:
● Consistent Performance and Scalability
◦ Consistent sub-millisecond latency with 100 percent flash storage
◦ Consolidate 100’s of enterprise-class applications in a single rack
◦ Scales easily, without disruption
◦ Continuous growth through multiple FlexPod CI deployments
● Operational Simplicity
◦ Fully tested, validated, and documented for rapid deployment
◦ Reduced management complexity
◦ No storage tuning or tiers necessary
● Lowest TCO
◦ Dramatic savings in power, cooling, and space with 100 percent flash storage
◦ Industry leading data reduction
● Enterprise-Grade Resiliency
◦ Highly available architecture with no single point of failure
◦ Nondisruptive operations with no downtime
◦ Upgrade and expand without downtime or performance loss
◦ Native data protection: snapshots and replication
◦ Suitable for even large resource-intensive workloads such as real-time analytics or heavy transactional databases
FlexPod Cisco Validated Design Advantages for VDI
The data center market segment is shifting toward heavily virtualized private, hybrid and public cloud computing models running on industry-standard systems. These environments require uniform design points that can be repeated for ease of management and scalability.
These factors have led to the need predesigned computing, networking and storage building blocks optimized to lower the initial design cost, simply management, and enable horizontal scalability and high levels of utilization. The use cases include:
● Enterprise Data Center (small failure domains)
● Service Provider Data Center (small failure domains)
● Commercial Data Center
● Remote Office/Branch Office
● SMB Standalone Deployments
Cisco Desktop Virtualization Solutions
Virtual Desktop Infrastructure (VDI) is the foundation of a modern, agile workplace. By enabling seamless access to applications and data from any device, VDI empowers your team to collaborate and innovate from anywhere.
Beyond productivity, VDI centralizes your intellectual property within the data center, allowing for granular, policy-based security and simplified data protection. It is the optimal balance of user flexibility and enterprise-grade security.
Your organization’s ability to meet user requirements for access to their desktops, applications, and data from any number of devices, from wherever they are and at any time, will improve user productivity and increase user satisfaction. While these requirements seem like a very tall order, Cisco and our partners can provide the validated solutions that will get you there economically and securely while delivering an excellent end-user experience.
Your employees and customers are embracing new ways or getting their work done. They expect you to deliver the environment they need to be successful. Deploying virtual client computing technology on Cisco UCS based on Cisco Validated Designs will provide the agile platform that allows you to adapt on demand.
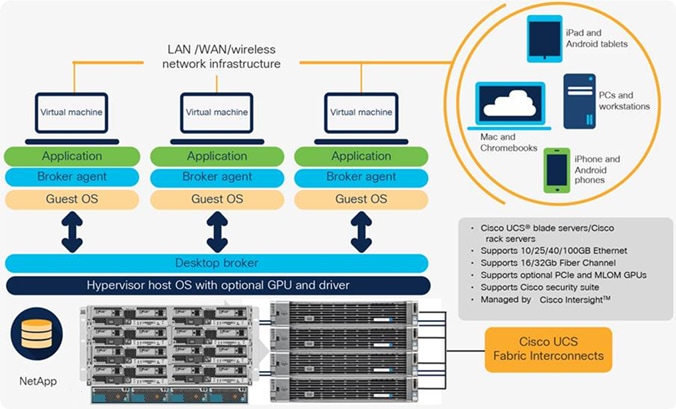
Why Cisco for virtual desktops and applications
● A better user experience on Cisco networks, delivering outstanding performance by guaranteeing Quality of Service (QoS)
● More desktop virtualization desktop sessions per server on Cisco Unified Computing System (Cisco UCS)
● Lower cost per desktop with leading virtual-machine performance, simplified deployment, and reduced cabling
● Cisco Validated Designs to help accelerate implementation and reduce risk
● Transparent integration between the computing fabric and the most widely adopted networking platform and networking architectures
● One of the most pervasive, defense-in-depth security architectures in the industry
● Transparent integration with industry-leading solutions for enterprise voice and multimedia IP communications: Cisco Unified Communications.
The following are some typical use cases:
● Healthcare: Mobility between desktops and terminals, compliance, and cost
● Federal government: Teleworking initiatives, business continuance, continuity of operations (COOP), and training centers
● Financial: Retail banks reducing IT costs, insurance agents, compliance, and privacy
● Education: K-12 student access, higher education, and remote learning
● State and local governments: IT and service consolidation across agencies and interagency security
● Retail: Branch-office IT cost reduction and remote vendors
● Manufacturing: Task and knowledge workers and offshore contractors
● Microsoft Windows 11 migration
● Graphic intense applications
● Security and compliance initiatives
● Opening of remote and branch offices or offshore facilities
● Mergers and acquisitions
Figure 3 illustrates the physical architecture.
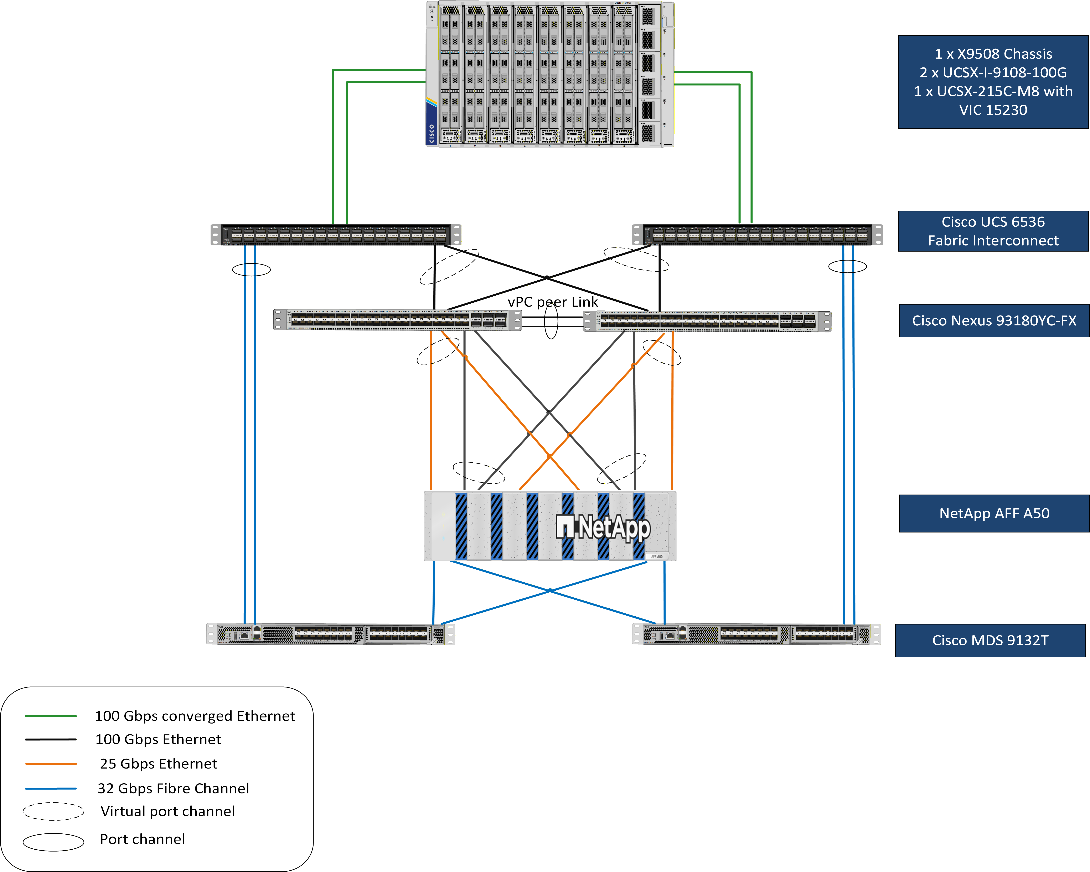
The reference hardware configuration includes:
● Two Cisco Nexus N9K C93180YC-FX switches
● Two Cisco UCS 6536 Fabric Interconnects
● Eight Cisco UCS X215c M8 Compute Node (for VDI workload)
● Infrastructure VMs for VDI were hosted on an external cluster
● One NetApp AFF A50 (high-availability pair) System
For desktop virtualization, the deployment includes Citrix Virtual Apps and Desktops Remote Desktop Session Hosts (RDSH) Sessions and Windows 11 virtual desktops running on VMware vSphere 8.0 U3.
The design is intended to provide a large-scale building block for Citrix Virtual Apps and Desktops Remote Desktop Session Hosted (RDSH) Sessions workloads consisting of Remote Desktops Server Hosted (RDSH) sessions with Windows Server 2022 hosted shared desktop sessions and Windows 11 non-persistent and persistent hosted desktops in the following:
● 2600 Hosted Shared Desktop (RDSH) Server 2022 user sessions with Microsoft Office 2021 (MCS non persistent virtual machines)
● 1600 Random Pooled Windows 11 Desktops with Microsoft Office 2021 (MCS non persistent virtual machines)
● 1600 Random Pooled Windows 11 Desktops with Microsoft Office 2021 (Citrix Provisioning Server non persistent virtual machines)
● 1600 Static Full Copy Windows 11 Desktops with Microsoft Office 2021 (MCS Full Clone virtual machines)
The data provided in this document will allow you to adjust the mix of Remote Desktop Server Hosted (RDSH) Sessions and Windows 11 Virtual Desktops to suit their environment. For example, additional Compute Node servers and chassis can be deployed to increase compute capacity, additional disk shelves can be deployed to improve I/O capability and throughput, and special hardware or software features can be added to introduce new features. This document guides you through the detailed steps for deploying the base architecture. This procedure explains everything from physical cabling to network, compute, and storage device configurations.
This Cisco Validated Design provides details for deploying a fully redundant, highly available Citrix Virtual Apps and Desktops solution with VMware vSphere on a FlexPod Datacenter architecture. Configuration guidelines are provided that refer the reader to which redundant component is being configured with each step.
For example, a single AFF A50 HA pair is referred to as storage controller 01 and storage controller 02 throughout the document. The pair of Cisco Nexus switches are labeled as Cisco Nexus A and Cisco Nexus B, while the Cisco UCS 6536 Fabric Interconnects are also configured as FI-A and FI-B.
Additionally, this document details the steps for provisioning multiple Cisco UCS hosts, using a sequential naming convention. Finally, to indicate that you should include information pertinent to your environment in a given step, <text> appears as part of the command structure.
This Cisco Validated Design prescribes a defined set of hardware and software that serves as an integrated foundation for both Microsoft Windows 11 virtual desktops and RDS server desktop sessions based on Microsoft Server 2022 The mixed workload solution includes Cisco UCS hardware and Data Platform software, Cisco Nexus switches, the Cisco UCS, Citrix Virtual Apps and Desktops and VMware vSphere software in a single package. The design is efficient such that the networking, computing, and storage components occupy 15 rack units footprint in an industry standard 42U rack. Port density on the Cisco Nexus switches and Cisco UCS Fabric Interconnects enables the networking components to accommodate multiple UCS clusters in a single Cisco UCS domain.
A key benefit of the Cisco Validated Design architecture is the ability to customize the environment to suit your requirements. A Cisco Validated Design scales easily as requirements and demand change. The unit can be scaled both up (adding resources to a Cisco Validated Design unit) and out (adding more Cisco Validated Design units).
The reference architecture detailed in this document highlights the resiliency, cost benefit, and ease of deployment of a converged desktop virtualization solution. A solution capable of consuming multiple protocols across a single interface allows for choice and investment protection because it truly is a wire-once architecture.
The combination of technologies from Cisco Systems, Inc., Citrix Systems, Inc, NetApp Inc, and Broadcom Inc. produced a highly efficient, robust, and affordable desktop virtualization solution for a virtual desktop, hosted shared desktop or mixed deployment supporting different use cases. Key components of the solution include the following:
● More power, same size. Cisco UCS X215c M8 Compute Node with up to 2x 5th or 4th Gen AMD EPYC Processors with up to 160 cores per processor and up to 384 MB of Level 3 cache per CPU and up to 6TB of main memory with 24x 256 GB DDR5 6000 MT/s or DDR5 4800 MT/s DIMMs depending on the installed CPU, with Citrix Virtual Apps and Desktops support more virtual desktop workloads. The AMD 32-core processors used in this study provided a balance between increased per-server capacity and cost.
● Fault-tolerance with high availability built into the design. The design is based on multiple Cisco UCS X-Series X215c M8 Compute Node for virtual desktop. The design provides N+1 server fault tolerance for every payload type tested.
● Stress-tested to the limits during aggressive boot scenario. The Windows Server virtual machines serving 2600 Hosted Shared Desktops user sessions and 1600 Windows 11 Virtual Desktops boot and register with the Citrix Broker in 20 minutes, providing you with an extremely fast, reliable cold-start desktop virtualization system.
● Stress-tested to the limits during simulated login storms. The 2600 user RDSH sessions and 1600 Windows 11 Virtual Desktops environment ready state in 48-minutes without overwhelming the processors, exhausting memory, or exhausting the storage subsystems, providing you with a desktop virtualization system that can easily handle the most demanding login storms.
● Ultra-condensed computing for the datacenter. The rack space required to support a system of up to 2,600 remote desktop users is 15 rack units. This includes the Cisco Nexus switches, Cisco Fabric Interconnects, X-Series chassis, and the NetApp AFF A50 system, providing high performance in a compact form factor.
● 100 percent virtualized. This CVD presents a validated design that is 100 percent virtualized on VMware ESXi 8.0 U3. All of the virtual desktops, user data, profiles, and supporting infrastructure components, including Active Directory, SQL Servers, Citrix Virtual Apps and Desktops Connection Server components, Citrix VDI virtual desktops and RDSH servers were hosted as virtual machines.
● Cisco data center management. Cisco maintains industry leadership with the new Cisco Intersight software that simplifies scaling, guarantees consistency, and eases maintenance. Cisco’s ongoing development efforts with Cisco Intersight ensure that your environments are consistent locally, across Cisco UCS Domains and across the globe. Cisco UCS software suite offers increasingly simplified operational and deployment management, and it continues to widen the span of control for your organizations’ subject matter experts in compute, storage, and network.
● Cisco 100G Fabric. Our 100G unified fabric story gets additional validation on 6500 Series Fabric Interconnects as Cisco runs more challenging workload testing, while maintaining unsurpassed user response times.
● NetApp AFF A50. Provides a high‑performance, all‑flash storage platform designed for virtual desktop infrastructure workloads. It efficiently handles demanding I/O patterns such as login storms, supports profile and user data management, and delivers simple and flexible business continuity through native snapshot and replication capabilities. With industry‑leading data efficiency and consolidation, the AFF A50 helps reduce overall storage cost per desktop while maintaining predictable performance and enterprise‑grade resilience.
● NetApp clustered Data ONTAP software. Enables seamless, nondisruptive scaling of storage by allowing capacity and performance to be added, upgraded, or removed online as requirements change. This flexibility allows the infrastructure to efficiently adapt to the evolving needs of virtual desktop environments without impacting user availability.
● Citrix Virtual Apps and Desktops advantage. Citrix Virtual Apps and Desktops follow a new unified product architecture that supports both Virtual Desktops and Remote Desktop Server Hosted server sessions. This new Citrix release simplifies tasks associated with large-scale VDI management. This modular solution supports seamless delivery of Windows apps and desktops as the number of users increase.
● Optimized performance and scale. For hosted shared desktop sessions, the best performance was achieved when the number of vCPUs assigned to the Citrix RDS virtual machines did not exceed the number of hyper-threaded (logical) cores available on the server. In other words, maximum performance is obtained when not overcommitting the CPU resources for virtual machines running virtualized RDS systems.
● Provisioning desktop machines made easy. Citrix Virtual Apps and Desktops provisions Remote Desktop Hosted Sessions (RDS) virtual desktops as well as hosted shared desktop virtual machines for this solution using a single method for both, the “Automated floating assignment desktop pool.” “Dedicated user assigned desktop pool” for persistent desktops was provisioned in the same Citrix administrative console. The new method of Instant Clone greatly reduces the amount of life-cycle spend and the maintenance windows for the guest OS.
This chapter contains the following:
● Cisco UCS Fabric Interconnect
● Cisco Unified Computing System X-Series
● Citrix Virtual App and Desktops 7 2402 LTSR
● NetApp A-Series All Flash FAS
● NetApp ONTAP Tools for VMware vSphere 10
● NetApp NFS Plug-in for VMware VAAI
The Cisco UCS Fabric Interconnect (FI) is a core part of the Cisco Unified Computing System, providing both network connectivity and management capabilities for the system. Depending on the model chosen, the Cisco UCS Fabric Interconnect offers line-rate, low-latency, lossless 10 Gigabit, 25 Gigabit, 40 Gigabit, or 100 Gigabit Ethernet, Fibre Channel over Ethernet (FCoE) and Fibre Channel connectivity. Cisco UCS Fabric Interconnects provide the management and communication backbone for the Cisco UCS C-Series, X-Series, and Cisco UCS Cisco UCS X9508 Chassis. All servers and chassis attached to the Cisco UCS Fabric Interconnects become part of a single, highly available connectivity domain.
For networking performance, the Cisco UCS 6536 Series uses a cut-through architecture, supporting deterministic, low latency, line rate 10/25/40/100 Gigabit Ethernet ports, 7.42 Tbps of switching capacity, and 1600Gbps bandwidth per Cisco UCS X9508 chassis when connected through the IFM 9108 model. The product family supports Cisco low-latency, lossless 10/25/40/100 Gigabit Ethernet unified network fabric capabilities, which increase the reliability, efficiency, and scalability of Ethernet networks. The fabric interconnect supports multiple traffic classes over the Ethernet fabric from the servers to the uplinks. Significant TCO savings come from an FCoE-optimized server design in which network interface cards (NICs), host bus adapters (HBAs), cables, and switches can be consolidated.
Cisco UCS 6536 Fabric Interconnects
The Cisco UCS Fabric Interconnects (FIs) provide a single point for connectivity and management for the entire Cisco Unified Computing System. Typically deployed as an active/active pair, the system’s FIs integrate all components into a single, highly available management domain controlled by Cisco Intersight. Cisco UCS FIs provide a single unified fabric for the system, with low-latency, lossless, cut-through switching that supports LAN, SAN, and management traffic using a single set of cables.
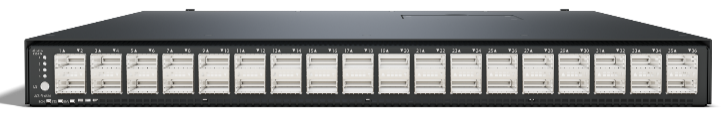
The Cisco UCS 6536 36-Port Fabric Interconnect (Figure 4) is a One-Rack-Unit (1RU) 1/10/25/40/100 Gigabit Ethernet, FCoE, and Fibre Channel switch offering up to 7.42 Tbps throughput and up to 36 ports. The switch has 32 40/100-Gbps Ethernet ports and 4 unified ports that can support 40/100-Gbps Ethernet ports or 16 Fiber Channel ports after breakout at 8/16/32-Gbps FC speeds.
Cisco Unified Computing System X-Series
The Cisco UCS X-Series Modular System is designed to take the current generation of the Cisco UCS platform to the next level with its future-ready design and cloud-based management. The system comprises modular components that can be assembled into systems through the Cisco Intersight cloud-operations platform. Intersight brings the power of SaaS to deliver proactive monitoring, automation, and optimization of workloads across hybrid-cloud environments.
The Cisco UCS X-Series provides functionalities of both blade and rack servers by offering compute density, storage capacity, and expandability in a single system, embracing a wide range of workloads in your data center. The Cisco UCS X-Series Modular System has won four CRN awards.
The Cisco UCS X-Series Modular System begins with the Cisco UCS X9508 Server Chassis engineered to be adaptable and future-ready. The chassis has a unified Ethernet fabric with Cisco UCS Intelligent Fabric Modules and Cisco UCS X-Fabric Technology for other technologies. With the chassis’ midplane-free design, either fabric can be independently upgraded.
The Cisco UCS X215c M8, Cisco UCS X210c Compute Nodes, and Cisco UCS X410c Compute Nodes provide the functionalities of both blade and rack servers by offering compute density, storage capacity, and expandability in a single form factor.
The Cisco UCS X440p PCIe Node supports adding GPUs with PCIe Gen 4.0 with the Cisco UCS X9416 X-Fabric Module. The Cisco UCS X580p PCIe Node supports adding GPUs with PCIe Gen 5.0 with the Cisco UCS X9516 X-Fabric Module. Additional nodes supporting FPGA accelerators, storage, and non-volatile memory are planned.
The Cisco UCS X-Series was designed with sustainability in mind. The Cisco UCS X-Series is equipped with modular, titanium-rated Power Supply Units (PSUs) and a 54-volt DC-power delivery system that minimizes the many internal power conversions, internal copper cabling, and amperage – saving on both overhead and power loss. With modular, counter-rotating fans and innovative zone-based cooling to optimize only those components that need more handling, the Cisco UCS X-Series can reduce overall fan power consumption. The Cisco UCS X-Series shares many components through modularity, which allows extending life and reducing waste. All these design and operation advantages add up to enable the Cisco UCS X-Series to not only meet but exceed sustainability benchmarks such as Energy Star, EPEAT, EU regulation 2019/424, and many others. Cisco UCS X-Series won the 2023 SEAL Sustainable Product Award and the Silverlinings Cloud Innovation Sustainability Solution awards.
The Cisco UCS X-Series chassis is engineered to be adaptable and flexible. As seen in Figure 5, the Cisco UCS X9508 chassis has only a power-distribution midplane. With a midplane-free design, I/O connectivity for the X9508 chassis is accomplished with frontloading, vertically oriented compute nodes intersecting with horizontally oriented I/O connectivity modules in the rear of the chassis. A unified Ethernet fabric is supplied with the Cisco UCS 9108 Intelligent Fabric Modules. In the future, Cisco UCS X-Fabric Technology interconnects will supply other industry-standard protocols as standards emerge. Interconnections can be easily updated with new modules.
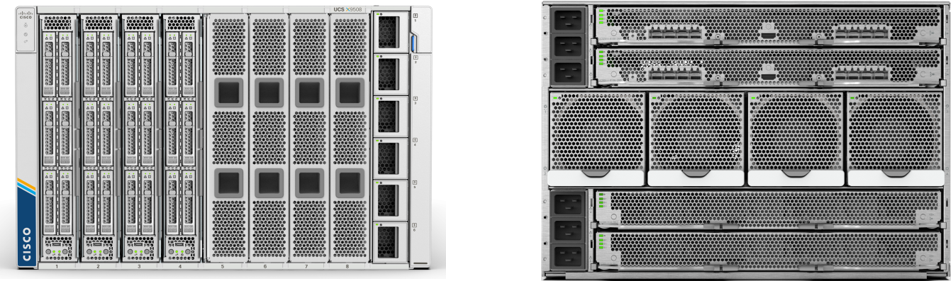
Cisco UCS X9508 features:
● 7-Rack-Unit (7RU) chassis has 8x front-facing flexible slots. These can house a combination of compute nodes and a pool of I/O resources like GPU accelerators.
● 2x Cisco UCS 9108 Intelligent Fabric Modules (IFMs) at the top of the chassis that connect the chassis to upstream Cisco UCS Fabric Interconnects. Each IFM features:
◦ Up to 100 Gbps of unified fabric connectivity per compute node
◦ 8x 25-Gbps SFP28 or 8x 100Gbps QSFP28 uplink ports. The unified fabric carries management traffic to the Cisco Intersight cloud-operations platform, Fibre Channel over Ethernet (FCoE) traffic, and production Ethernet traffic to the fabric interconnects.
● Six 2800W Power Supply Units (PSUs) provide 54V power to the chassis with N, N+1, and N+N redundancy. A higher voltage allows efficient power delivery with less copper and reduced power loss.
● Efficient, 4x100mm, dual counter-rotating fans deliver industry-leading airflow and power efficiency. Optimized thermal algorithms enable different cooling modes to best support the network environment. Cooling is modular so that future enhancements can potentially handle open- or closed-loop liquid cooling to support even higher-power processors.
Cisco UCS 9108 100G Intelligent Fabric Modules
In the end-to-end 100Gbps Ethernet design, for the Cisco UCS X9508 Chassis, the network connectivity is provided by a pair of Cisco UCS 9108 100G Intelligent Fabric Modules (IFMs). Like the fabric extenders used in the Cisco UCS 5108 Blade Server Chassis, these modules carry all network traffic to a pair of Cisco UCS 6536 Fabric Interconnects (FIs). IFMs also host the Chassis Management Controller (CMC) for chassis management. In contrast to systems with fixed networking components, Cisco UCS X9508’s midplane-free design enables easy upgrades to new networking technologies as they emerge making it straightforward to accommodate new network speeds or technologies in the future.
Each IFM supports eight 100Gb uplink ports for connecting the Cisco UCS X9508 Chassis to the FIs and 8 100Gb or 32 25Gb server ports for the eight compute nodes. IFM server ports can provide up to 200 Gbps of unified fabric connectivity per compute node across the two IFMs. The uplink ports connect the chassis to the Cisco UCS FIs, providing up to 1600Gbps connectivity across the two IFMs. The unified fabric carries management, VM, and Fibre Channel over Ethernet (FCoE) traffic to the FIs, where server management traffic is routed to the Cisco Intersight cloud operations platform, FCoE traffic is forwarded to either native Fibre Channel interfaces through unified ports on the FI (to Cisco MDS switches) or to FCoE uplinks (to Cisco Nexus switches supporting SAN switching), and data Ethernet traffic is forwarded upstream to the data center network (using Cisco Nexus switches).
Cisco UCS X215c M8 Compute Node
The Cisco UCS X9508 Chassis is designed to host up to 8 Cisco UCS X215c M8 Compute Nodes. The hardware details of the Cisco UCS X215c M8 Compute Nodes are shown in Figure 7.
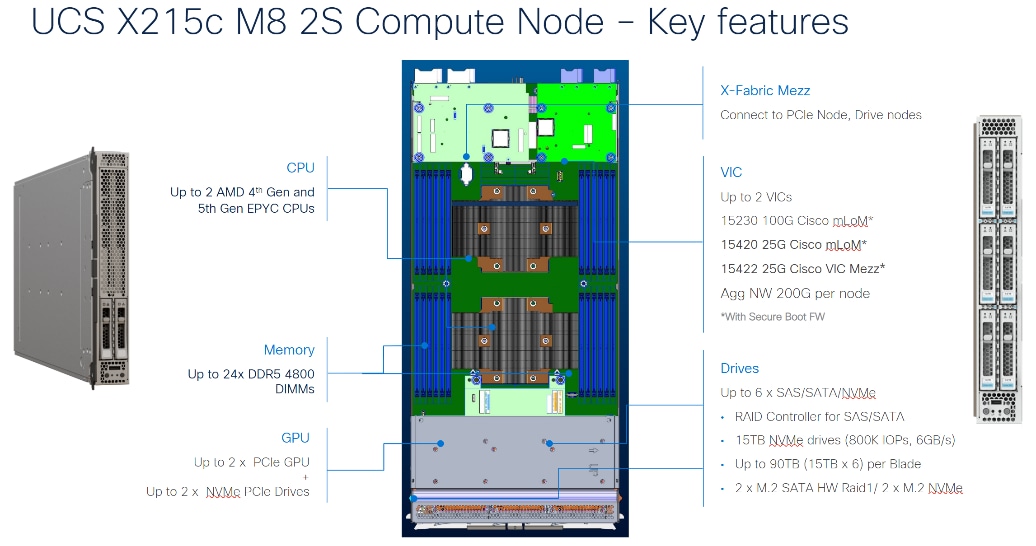
The Cisco UCS X215c M8 features:
● CPU: Up to 2x 5th and 4th Gen AMD EPYC Processors with up to 160 cores per processor (5th Gen) and up to 384 MB of Level 3 cache per CPU.
● Memory: Up to 6TB of main memory with 24x 256 GB DDR5 6000 MT/s or DDR5 4800 MT/s DIMMs depending on the CPU installed.
● Disk storage: Up to six hot-pluggable, Solid-State Drives (SSDs), or Non-volatile Memory Express (NVMe) 2.5-inch drives, or up to 8x EDSFF E3.S NVMe drives with a choice of enterprise-class Redundant Array of Independent Disks (RAIDs) or passthrough controllers, up to two M.2 SATA drives with optional hardware RAID or up to two M.2 NVMe drives in pass-through mode.
● GPUs: The Cisco UCS front mezzanine GPU module is a passive PCIe Gen 4.0 front mezzanine option with support for up to two NVMe drives and two HHHL GPUs.
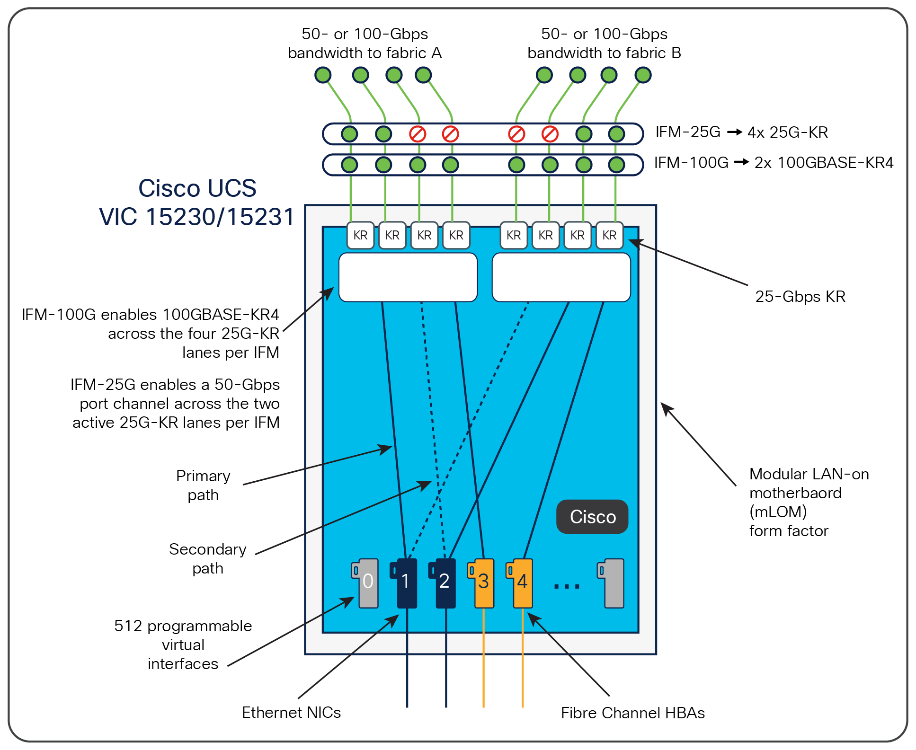
● Virtual Interface Card (VIC): Up to 2 VICs including an mLOM Cisco UCS VIC 15230 or an mLOM Cisco UCS VIC 15420 and a mezzanine Cisco UCS VIC card 15422 can be installed in a Compute Node.
● Security: The server supports an optional Trusted Platform Module (TPM). Additional security features include a secure boot FPGA and ACT2 anticounterfeit provisions.
Cisco UCS Virtual Interface Cards
This section describes the Cisco UCS X215c M8 Compute Nodes that support the following 100G Cisco UCS VIC cards.
● Cisco UCS VIC 15230
The Cisco UCS VIC 15230 is 2x100-Gbps Ethernet/FCoE-capable modular LAN on motherboard (mLOM) adapters designed exclusively for the Cisco UCS X210c and Cisco UCS X215c Compute Nodes. The Cisco UCS VIC 15230 and Cisco UCS VIC 15231 adapters enable a policy-based, stateless, agile server infrastructure that can present to the host PCIe standards-compliant interfaces that can be dynamically configured as either NICs or HBAs.
The Cisco UCS VIC 15230 is functionally equivalent to the 15231 but incorporates secure boot technology.
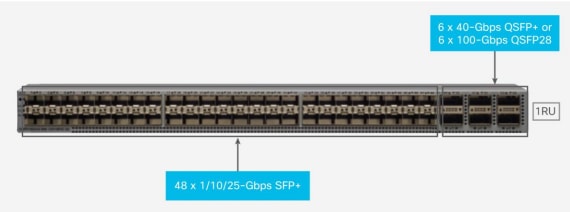
Cisco Nexus N9K-C93180YC-FX3S Switches
The Cisco Nexus N9K-C93180YC-FX3S Switch provides a flexible line-rate Layer 2 and Layer 3 feature set in a compact form factor. Designed with Cisco Cloud Scale technology, it supports highly scalable cloud architectures. With the option to operate in Cisco NX-OS or Application Centric Infrastructure (ACI) mode, it can be deployed across enterprise, service provider, and Web 2.0 data centers.
● Architectural Flexibility
◦ Includes top-of-rack or middle-of-row fiber-based server access connectivity for traditional and leaf-spine architectures
◦ Leaf node support for Cisco ACI architecture is provided in the roadmap
◦ Increase scale and simplify management through Cisco Nexus 2000 Fabric Extender support
● Feature Rich
◦ Enhanced Cisco NX-OS Software is designed for performance, resiliency, scalability, manageability, and programmability
◦ ACI-ready infrastructure helps users take advantage of automated policy-based systems management
◦ Virtual Extensible LAN (VXLAN) routing provides network services
◦ Rich traffic flow telemetry with line-rate data collection
◦ Real-time buffer utilization per port and per queue, for monitoring traffic micro-bursts and application traffic patterns
● Highly Available and Efficient Design
◦ High-density, non-blocking architecture
◦ Easily deployed into either a hot-aisle or cold-aisle configuration
◦ Redundant, hot-swappable power supplies and fan trays
● Simplified Operations
◦ Power-On Auto Provisioning (POAP) support allows for simplified software upgrades and configuration file installation
◦ An intelligent API offers switch management through remote procedure calls (RPCs, JSON, or XML) over a HTTP/HTTPS infrastructure
◦ Python Scripting for programmatic access to the switch command-line interface (CLI)
◦ Hot and cold patching, and online diagnostics
Cisco MDS 9132T 32-Gb Fiber Channel Switch
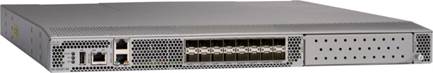
The next-generation Cisco MDS 9132T 32-Gb 32-Port Fibre Channel Switch (Figure 10) provides high-speed Fibre Channel connectivity from the server rack to the SAN core. It empowers small, midsize, and large enterprises that are rapidly deploying cloud-scale applications using extremely dense virtualized servers, providing the dual benefits of greater bandwidth and consolidation.
Small-scale SAN architectures can be built from the foundation using this low-cost, low-power, non-blocking, line-rate, and low-latency, bi-directional airflow capable, fixed standalone SAN switch connecting both storage and host ports.
Medium-size to large-scale SAN architectures built with SAN core directors can expand 32-Gb connectivity to the server rack using these switches either in switch mode or Network Port Virtualization (NPV) mode.
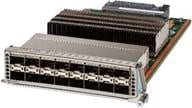
Additionally, investing in this switch for the lower-speed (4- or 8- or 16-Gb) server rack gives you the option to upgrade to 32-Gb server connectivity in the future using the 32-Gb Host Bus Adapter (HBA) that are available today. The Cisco MDS 9132T 32-Gb 32-Port Fibre Channel switch also provides unmatched flexibility through a unique port expansion module (Figure 11) that provides a robust cost-effective, field swappable, port upgrade option.
This switch also offers state-of-the-art SAN analytics and telemetry capabilities that have been built into this next-generation hardware platform. This new state-of-the-art technology couples the next-generation port ASIC with a fully dedicated Network Processing Unit designed to complete analytics calculations in real time. The telemetry data extracted from the inspection of the frame headers are calculated on board (within the switch) and, using an industry-leading open format, can be streamed to any analytics-visualization platform. This switch also includes a dedicated 10/100/1000BASE-T telemetry port to maximize data delivery to any telemetry receiver including Cisco Data Center Network Manager.
● Features
◦ High performance: Cisco MDS 9132T architecture, with chip-integrated nonblocking arbitration, provides consistent 32-Gb low-latency performance across all traffic conditions for every Fibre Channel port on the switch.
◦ Capital Expenditure (CapEx) savings: The 32-Gb ports allow you to deploy them on existing 16- or 8-Gb transceivers, reducing initial CapEx with an option to upgrade to 32-Gb transceivers and adapters in the future.
◦ High availability: Cisco MDS 9132T switches continue to provide the same outstanding availability and reliability as the previous-generation Cisco MDS 9000 Family switches by providing optional redundancy on all major components such as the power supply and fan. Dual power supplies also facilitate redundant power grids.
◦ Pay-as-you-grow: The Cisco MDS 9132T Fibre Channel switch provides an option to deploy as few as eight 32-Gb Fibre Channel ports in the entry-level variant, which can grow by 8 ports to 16 ports, and thereafter with a port expansion module with sixteen 32-Gb ports, to up to 32 ports. This approach results in lower initial investment and power consumption for entry-level configurations of up to 16 ports compared to a fully loaded switch. Upgrading through an expansion module also reduces the overhead of managing multiple instances of port activation licenses on the switch. This unique combination of port upgrade options allow four possible configurations of 8 ports, 16 ports, 24 ports and 32 ports.
◦ Next-generation Application-Specific Integrated Circuit (ASIC): The Cisco MDS 9132T Fibre Channel switch is powered by the same high-performance 32-Gb Cisco ASIC with an integrated network processor that powers the Cisco MDS 9700 48-Port 32-Gb Fibre Channel Switching Module. Among all the advanced features that this ASIC enables, one of the most notable is inspection of Fibre Channel and Small Computer System Interface (SCSI) headers at wire speed on every flow in the smallest form-factor Fibre Channel switch without the need for any external taps or appliances. The recorded flows can be analyzed on the switch and also exported using a dedicated 10/100/1000BASE-T port for telemetry and analytics purposes.
◦ Intelligent network services: Slow-drain detection and isolation, VSAN technology, Access Control Lists (ACLs) for hardware-based intelligent frame processing, smartzoning and fabric wide Quality of Service (QoS) enable migration from SAN islands to enterprise-wide storage networks. Traffic encryption is optionally available to meet stringent security requirements.
◦ Sophisticated diagnostics: The Cisco MDS 9132T provides intelligent diagnostics tools such as Inter-Switch Link (ISL) diagnostics, read diagnostic parameters, protocol decoding, network analysis tools, and integrated Cisco Call Home capability for greater reliability, faster problem resolution, and reduced service costs.
◦ Virtual machine awareness: The Cisco MDS 9132T provides visibility into all virtual machines logged into the fabric. This feature is available through HBAs capable of priority tagging the Virtual Machine Identifier (VMID) on every FC frame. Virtual machine awareness can be extended to intelligent fabric services such as analytics[1] to visualize performance of every flow originating from each virtual machine in the fabric.
◦ Programmable fabric: The Cisco MDS 9132T provides powerful Representational State Transfer (REST) and Cisco NX-API capabilities to enable flexible and rapid programming of utilities for the SAN as well as polling point-in-time telemetry data from any external tool.
◦ Single-pane management: The Cisco MDS 9132T can be provisioned, managed, monitored, and troubleshot using Cisco Data Center Network Manager (DCNM), which currently manages the entire suite of Cisco data center products.
◦ Self-contained advanced anticounterfeiting technology: The Cisco MDS 9132T uses on-board hardware that protects the entire system from malicious attacks by securing access to critical components such as the bootloader, system image loader and Joint Test Action Group (JTAG) interface.
The Cisco Intersight platform is a Software-as-a-Service (SaaS) infrastructure lifecycle management platform that delivers simplified configuration, deployment, maintenance, and support. The Cisco Intersight platform is designed to be modular, so you can adopt services based on their individual requirements. The platform significantly simplifies IT operations by bridging applications with infrastructure, providing visibility and management from bare-metal servers and hypervisors to serverless applications, thereby reducing costs and mitigating risk. This unified SaaS platform uses a unified Open API design that natively integrates with third-party platforms and tools.
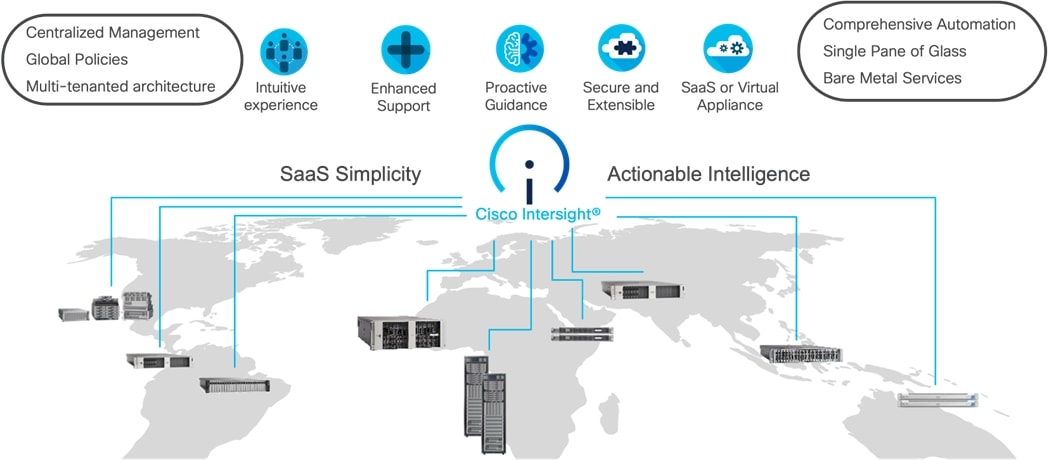
The main benefits of Cisco Intersight infrastructure services are as follows:
● Simplify daily operations by automating many daily manual tasks
● Combine the convenience of a SaaS platform with the capability to connect from anywhere and manage infrastructure through a browser or mobile app
● Stay ahead of problems and accelerate trouble resolution through advanced support capabilities
● Gain global visibility of infrastructure health and status along with advanced management and support capabilities
● Upgrade to add workload optimization and Kubernetes services when needed
Cisco Intersight Virtual Appliance and Private Virtual Appliance
In addition to the SaaS deployment model running on Intersight.com, on-premises options can be purchased separately. The Cisco Intersight Virtual Appliance and Cisco Intersight Private Virtual Appliance are available for organizations that have additional data locality or security requirements for managing systems. The Cisco Intersight Virtual Appliance delivers the management features of the Cisco Intersight platform in an easy-to-deploy VMware Open Virtualization Appliance (OVA) or Microsoft Hyper-V Server virtual machine that allows you to control the system details that leave your premises. The Cisco Intersight Private Virtual Appliance is provided in a form factor specifically designed for users who operate in disconnected (air gap) environments. The Private Virtual Appliance requires no connection to public networks or back to Cisco to operate.
Cisco Intersight Assist
Cisco Intersight Assist helps you add endpoint devices to Cisco Intersight. A data center could have multiple devices that do not connect directly with Cisco Intersight. Any device that is supported by Cisco Intersight, but does not connect directly with it, will need a connection mechanism. Cisco Intersight Assist provides that connection mechanism. FlexPod, VMware vCenter, and NetApp Active IQ Unified Manager connect to Intersight with the help of Intersight Assist VM.
Cisco Intersight Assist is available within the Cisco Intersight Virtual Appliance, which is distributed as a deployable virtual machine contained within an Open Virtual Appliance (OVA) file format. More details about the Cisco Intersight Assist VM deployment configuration is explained in later sections.
Licensing Requirements
The Cisco Intersight platform uses a subscription-based license with multiple tiers. You can purchase a subscription duration of one, three, or five years and choose the required Cisco UCS server volume tier for the selected subscription duration. Each Cisco endpoint automatically includes a Cisco Intersight base license at no additional cost when you access the Cisco Intersight portal and claim a device. You can purchase any of the following higher-tier Cisco Intersight licenses using the Cisco ordering tool:
● Cisco Intersight Infrastructure Services Essentials: The Essentials license tier offers server management with global health monitoring, inventory, proactive support through Cisco TAC integration, multi-factor authentication, along with SDK and API access.
● Cisco Intersight Infrastructure Services Advantage: The Advantage license tier offers advanced server management with extended visibility, ecosystem integration, and automation of Cisco and third-party hardware and software, along with multi-domain solutions.
For more information about the features provided in the various licensing tiers, go to Intersight documentation.
Citrix Virtual App and Desktops 7 2402 LTSR
The virtual app and desktop solution is designed for an exceptional experience.
Today's employees spend more time than ever working remotely, causing companies to rethink how IT services should be delivered. To modernize infrastructure and maximize efficiency, many are turning to desktop as a service (DaaS) to enhance their physical desktop strategy, or they are updating on-premises virtual desktop infrastructure (VDI) deployments. Managed in the cloud, these deployments are high-performance virtual instances of desktops and apps that can be delivered from any datacenter or public cloud provider.
DaaS and VDI capabilities provide corporate data protection as well as an easily accessible hybrid work solution for employees. Because all data is stored securely in the cloud or datacenter, rather than on devices, end-users can work securely from anywhere, on any device, and over any network—all with a fully IT-provided experience. IT also gains the benefit of centralized management, so they can scale their environments quickly and easily. By separating endpoints and corporate data, resources stay protected even if the devices are compromised.
As a leading VDI and DaaS provider, Citrix provides the capabilities organizations need for deploying virtual apps and desktops to reduce downtime, increase security, and alleviate the many challenges associated with traditional desktop management.
Powered by NetApp ONTAP data management software, NetApp AFF A-Series systems (NetApp AFF) deliver the industry’s highest performance, superior flexibility, and best-in-class data services and cloud integration to help you accelerate, manage, and protect business-critical data across hybrid cloud. It is a robust scale-out platform built for virtualized environments, combining low-latency performance with best-in-class data management, built-in efficiencies, integrated data protection, multiprotocol support, and nondisruptive operations. Deploy as a stand-alone system or as a high-performance tier in a NetApp ONTAP configuration.
A wide range of organizations, from enterprise to midsize businesses, rely on NetApp AFF A-Series to:
● Simplify operations with seamless data management, on the premises and in the cloud
● Accelerate traditional and new-generation applications
● Keep business-critical data available, protected, and secure
● Accelerates applications and future-proofs your infrastructure
In the modern data center, IT is charged with driving maximum performance for business-critical workloads, scaling without disruption as the business grows, and enabling the business to take on new data-driven initiatives. NetApp AFF A-Series systems handle all of it with ease.
The NetApp AFF A-Series lineup includes the AFF A1K, AFF A90, AFF A70, AFF A50, AFF A30 and AFF A20. These controllers and their technical specifications are listed in Table 1. For more information about the NetApp A-Series AFF controllers, see:
http://www.netapp.com/us/products/storage-systems/all-flash-array/aff-a-series.aspx
Table 1. NetApp AFF Technical Specifications
| Specifications |
AFF A20 |
AFF A30 |
AFF A50 |
AFF A70 |
AFF A90 |
AFF A1K |
| Maximum scale-out |
2–6 nodes (3 HA pairs) |
2-8 nodes |
2-24 nodes (12 HA pair) |
2-24 nodes (12 HA pair) |
2-24 nodes (12 HA pair) |
2-24 nodes (12 HA pair) |
| Maximum SSDs |
144 |
288 |
1440 |
2880 |
2880 |
2880 |
| Max effective capacity |
18.8PB |
36.2PB |
186PB |
330PB |
330PB |
330PB |
| Controller form factor |
2U; 24 internal SSD slots |
2U; 24 internal SSD slots |
2U; 24 internal SSD slots |
4U; 48 internal SSD slot |
4U; 48 internal SSD slot |
2X2U |
| PCIe expansion slots |
8 |
8 |
8 |
18 |
18 |
18 |
| FC target ports (64Gb autoranging) |
24 |
24 |
24 |
56 |
56 |
48 |
| FC target ports (32Gb autoranging) |
24 |
24 |
24 |
56 |
56 |
48 |
| FC target ports (16Gb autoranging) |
24 |
24 |
24 |
56 |
56 |
48 |
| 100GbE ports (40GbE autoranging) |
12 |
16 |
16 |
36 |
36 |
36 |
| 25GbE ports (10GbE autoranging) |
32 |
24 |
24 |
56 |
56 |
48 |
| 10GbE ports |
24 |
24 |
24 |
56 |
56 |
48 |
| 12Gb/6Gb SAS ports |
16 |
16 |
16 |
n/a |
n/a |
n/a |
| Storage networking supported |
NFSv4/RDMA, NVMe/TCP, NVMe/FC, FC, iSCSI, NFS, pNFS, CIFS/SMB, Amazon s3 |
NFSv4/RDMA, NVMe/TCP, NVMe/FC, FC, iSCSI, NFS, pNFS, CIFS/SMB, Amazon s3 |
NFSv4/RDMA, NVMe/TCP, NVMe/FC, FC, iSCSI, NFS, pNFS, CIFS/SMB, Amazon s3 |
NFSv4/RDMA, NVMe/TCP, NVMe/FC, FC, iSCSI, NFS, pNFS, CIFS/SMB, Amazon s3 |
NFSv4/RDMA, NVMe/TCP, NVMe/FC, FC, iSCSI, NFS, pNFS, CIFS/SMB, Amazon s3 |
NFSv4/RDMA, NVMe/TCP, NVMe/FC, FC, iSCSI, NFS, pNFS, CIFS/SMB, Amazon s3 |
NetApp AFF A‑Series delivers the performance, consistency, and scalability required to power every workload from mission‑critical enterprise applications to advanced AI innovations on a single, unified platform. Industry‑leading performance validated by independent benchmarks makes AFF A‑Series ideal for Oracle, Microsoft SQL Server, VMware, VDI, analytics, and AI workloads, while its purpose‑built, end‑to‑end NVMe architecture provides ultra‑low latency that accelerates applications and enhances user experience.
With a broad portfolio ranging from entry‑level to ultra‑high‑end systems, organizations can choose the right solution for their needs while maintaining a consistent operating model across the enterprise. Designed for modern, high‑speed networks, AFF A‑Series supports both NVMe/TCP and NVMe/FC, enabling flexible use of existing Ethernet infrastructure or maximum performance with Fibre Channel—all with seamless integration into leading operating systems and hypervisors. The platform scales non-disruptively in both performance and capacity, allowing organizations to grow without downtime, preserve existing investments, and consolidate workloads using a true scale‑out architecture.
Powered by a single ONTAP operating system, AFF A‑Series simplifies IT operations through unified SAN, NAS, and object storage, intuitive management, and automation that enables storage to be provisioned in minutes instead of days. Intelligent insights from NetApp Active IQ further optimize performance and costs with predictive analytics and proactive support. Always‑on inline data reduction, thin provisioning, and space‑efficient Snapshot technology deliver exceptional storage efficiency and lower total cost of ownership. Built as the foundation of NetApp’s data fabric, AFF A‑Series seamlessly connects on‑premises and cloud environments to support hybrid cloud, data tiering, collaboration, and disaster recovery. With integrated, application‑consistent data protection, near‑zero‑downtime business continuity, and comprehensive security—including ransomware protection, encryption, and compliance‑ready controls NetApp AFF A‑Series enables organizations to run every workload, power AI innovation, simplify at scale, and protect what matters most.
NetApp AFF A50
The NetApp AFF A50 is a midrange, high‑performance all‑flash storage system designed to deliver enterprise‑class capabilities for modern workloads while maximizing efficiency and simplicity in a compact form factor. Built on NetApp ONTAP and architected for the AI era, the NetApp AFF A50 provides end‑to‑end NVMe performance with support for both NVMe/FC and NVMe/TCP host connectivity, enabling ultra‑low latency and high throughput for business‑critical applications such as databases, virtualization, analytics, and emerging AI and GenAI workloads. NVMe/TCP allows you to leverage existing Ethernet infrastructure for faster host access, while NVMe/FC delivers maximum performance for SAN environments. The NetApp AFF A50 supports 24 internal NVMe SSDs in a 2U chassis and scales non-disruptively in a unified, scale‑out architecture, allowing organizations to grow performance and capacity without disruption. With always‑on inline data reduction, built‑in ransomware protection, integrated data protection, and seamless hybrid‑cloud connectivity, the AFF A50 combines performance, efficiency, security, and flexibility making it an ideal platform for organizations seeking to modernize infrastructure, consolidate workloads, and prepare for future AI‑driven innovation.
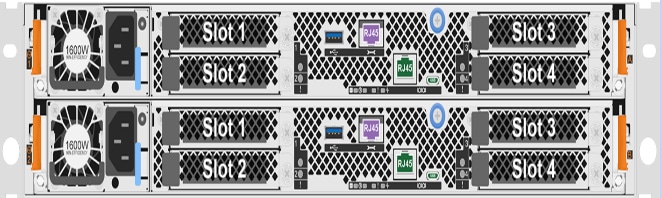

Note: Front‑end Fibre Channel connectivity is provided by a 4‑port 32 Gb Fibre Channel HBA installed in slot 1, with all ports (1a–1d) connected to dual Cisco MDS switches to deliver redundant A/B SAN fabrics. NAS and other IP‑based workloads utilize high‑bandwidth 100 Gb Ethernet connectivity through ports e2b and e4b on Ethernet adapters installed in slots 2 and 4. CIFS traffic is isolated to dedicated 25 Gb Ethernet ports e3a and e3b on the adapter in slot 3, providing resilient, active‑active connectivity to the Cisco Nexus switching infrastructure. Cluster and high‑availability interconnect traffic is segregated onto dedicated 100 Gb Ethernet ports e2a and e4a, ensuring deterministic, low‑latency node‑to‑node communication.
NetApp ONTAP 9
NetApp storage systems harness the power of ONTAP to simplify the data infrastructure from edge, core, and cloud with a common set of data services and 99.9999 percent availability. NetApp ONTAP 9 data management software from NetApp enables you to modernize your infrastructure and transition to a cloud-ready data center. NetApp ONTAP 9 has a host of features to simplify deployment and data management, accelerate and protect critical data, and make infrastructure future-ready across hybrid-cloud architectures.
NetApp ONTAP 9 is the data management software that is used with the NetApp AFF A50 all-flash storage system in this solution design. NetApp ONTAP software offers secure unified storage for applications that read and write data over block- or file-access protocol storage configurations. These storage configurations range from high-speed flash to lower-priced spinning media or cloud-based object storage. NetApp ONTAP implementations can run on NetApp engineered AFF, FAS or ASA series arrays and in private, public, or hybrid clouds (NetApp Private Storage and NetApp Cloud Volumes ONTAP). Specialized implementations offer best-in-class converged infrastructure, featured here as part of the FlexPod Datacenter solution or with access to third-party storage arrays (NetApp FlexArray virtualization). Together these implementations form the basic framework of the NetApp Data Fabric, with a common software-defined approach to data management, and fast efficient replication across systems. FlexPod and ONTAP architectures can serve as the foundation for both hybrid cloud and private cloud designs.
Read more about all the capabilities of ONTAP data management software here: https://www.netapp.com/us/products/data-management-software/ontap.aspx.
NetApp ONTAP Features for VDI
The following are the NetApp ONTAP features for VDI:
● Secure Multi-Tenancy—Tenants can be in overlapping subnet or can use identical IP subnet range.
● Multi-Protocol—Same storage system can be used for Block/File/Object storage demands.
● FlexGroup Volumes—High performance and massive capacity (~20PB and ~40 billion files) for file shares and for hosting VDI pools.
● FlexCache—Enables Single Global Namespace can be consumed around the clouds or multi-site.
● File System Analytics—Fast query to file metadata on the SMB file share.
● Ease of management with vCenter Plugins—Best practices are validated and implemented while provisioning. Supports VAAI and VASA for fast provisioning and storage capability awareness.
● SnapCenter integration with vCenter—Space efficient data protection with snapshots and FlexClones.
● Automation support—Supports RESTapi, has modules for Ansible, PowerShell, and so on.
● Storage Efficiency—Supports inline dedupe, compression, thin provisioning, and so on. Guaranteed dedupe of 8:1 for VDI.
● Adaptive QoS—Adjusts QoS setting based on space consumption.
● ActiveIQ Unified Manager—Application based storage provisioning, Performance Monitoring, End-End storage visibility diagrams.
Storage efficiency measures how effectively a storage platform maximizes usable capacity while minimizing wasted space, physical footprint, and cost. NetApp ONTAP storage efficiency technologies allow organizations to store more data in less space by eliminating duplicate blocks, zero filled blocks, and inefficiencies during data writes. By leveraging capabilities such as thin provisioning, inline and background deduplication, compression, and compaction, ONTAP reduces both on premises and cloud storage consumption while simultaneously improving performance through faster reads, accelerated copies, and rapid VM and desktop provisioning. These efficiencies are transparent to applications and operate automatically, enabling consistent cost savings and operational simplicity across enterprise and VDI environments.
ONTAP further enhances efficiency through advanced innovations such as FlexClone technology, which enables instant, space efficient copies of volumes, files, and LUNs; temperature sensitive storage efficiency (TSSE) and hardware accelerated compression, which dynamically optimize compression based on data access patterns or dedicated offload processors; and Adaptive QoS, which scales performance appropriately as volumes grow. Features such as cross volume deduplication, Snapshot based data protection, RAID DP, and SSD partitioning significantly increase usable capacity while maintaining resiliency and performance. These same storage efficiency capabilities are preserved across on premises and cloud deployments, allowing data to move seamlessly between environments using NetApp replication services while maintaining efficiency. Together, these capabilities enable ONTAP to deliver high performance, space optimized storage at scale, making it especially effective for VDI, databases, virtualized workloads, and hybrid cloud architectures.
NetApp recommends implementing SAN boot for Cisco UCS servers in the FlexPod Datacenter solution. Doing so enables the ESXI host to be safely secured by the NetApp All Flash FAS storage system, providing better performance. In this design, the FC SAN boot is validated.
In FC SAN boot, each Cisco UCS server boots by connecting the NetApp All Flash FAS storage to the Cisco MDS switch. The 32G FC storage ports, in this example 1a,1b,1c and 1d, are connected to Cisco MDS switch. The FC LIFs are created on the physical ports, and each FC LIF is uniquely identified by its target WWPN. The storage system target WWPNs can be zoned with the server initiator WWPNs in the Cisco MDS switches. The FC boot LUN is exposed to the servers through the FC LIF using the MDS switch; this enables only the authorized server to have access to the boot LUN.
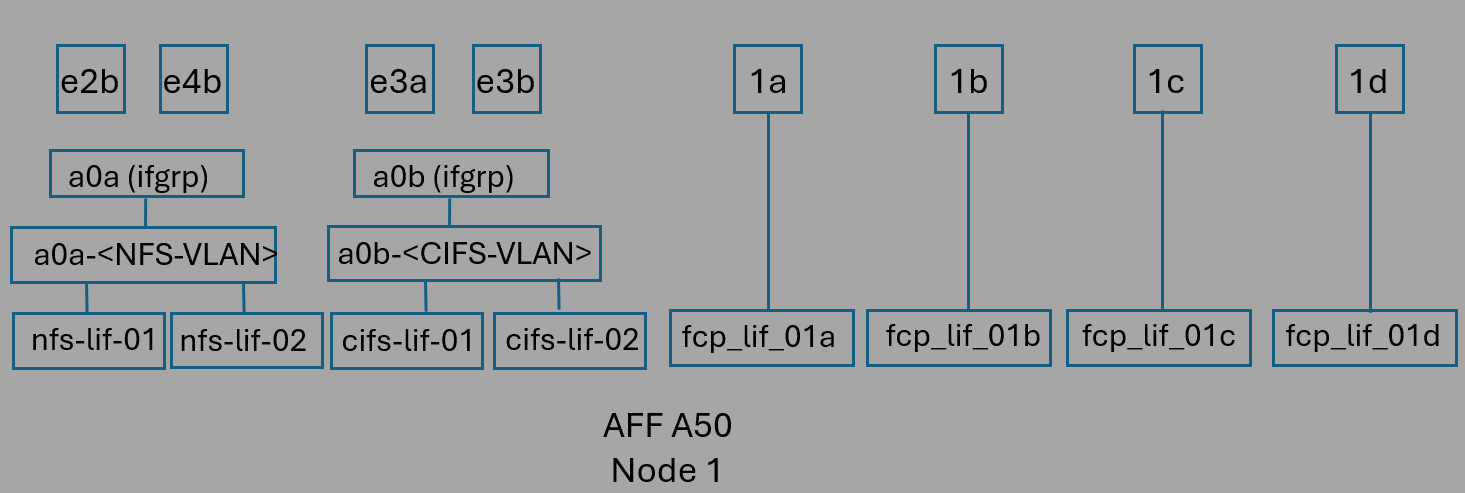
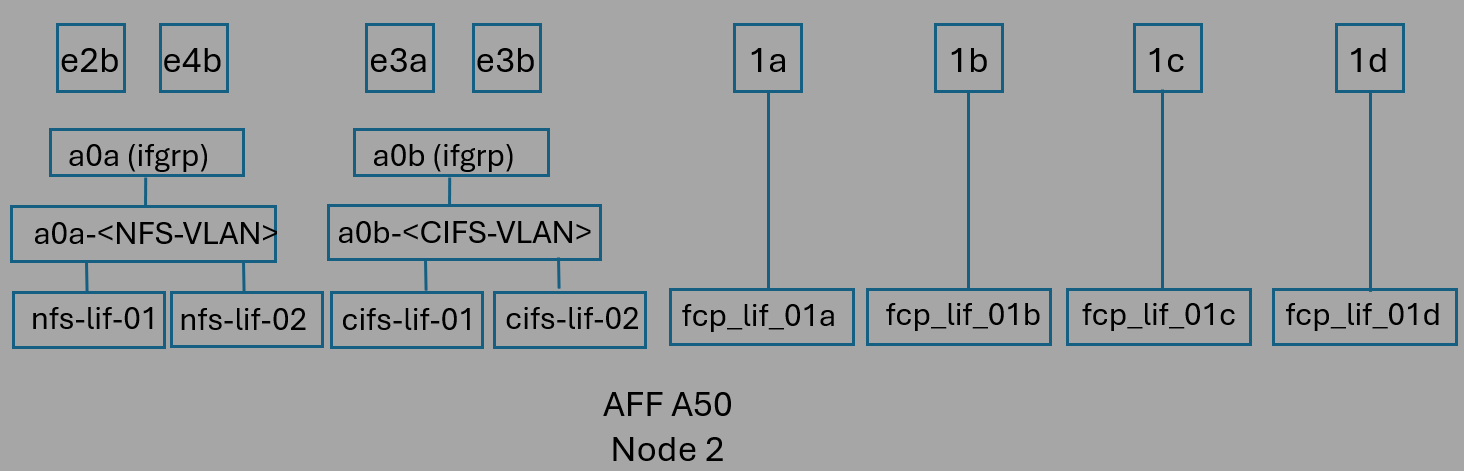
Unlike NAS network interfaces, the SAN network interfaces are not configured to fail over during a failure. Instead if a network interface becomes unavailable, the ESXI host chooses a new optimized path to an available network interface. ALUA is a standard supported by NetApp used to provide information about SCSI targets, which allows a host to identify the best path to the storage.
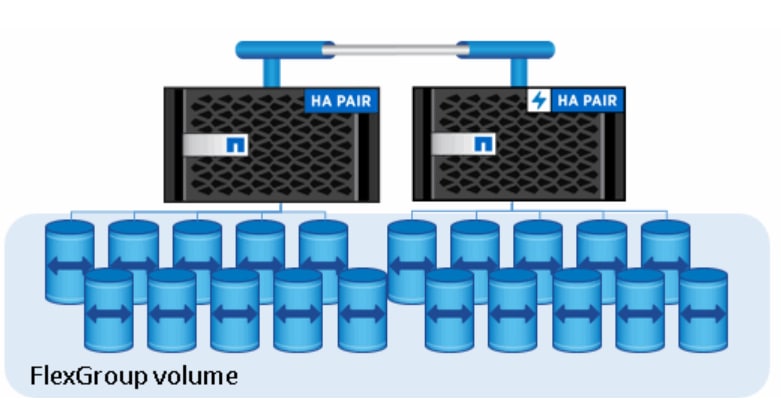
ONTAP 9.3 brought an innovation in scale-out NAS file systems: NetApp FlexGroup volumes, which plays a major role to give ONTAP the ability to be scaled non-disruptively out to 24 storage nodes while not degrading the performance of the VDI infrastructure.
With FlexGroup volumes, a storage administrator can easily provision a massive single namespace in a matter of seconds. FlexGroup volumes have virtually no capacity or file count constraints outside of the physical limits of hardware or the total volume limits of ONTAP. Limits are determined by the overall number of constituent member volumes that work in collaboration to dynamically balance load and space allocation evenly across all members. There is no required maintenance or management overhead with a FlexGroup volume. You simply create the FlexGroup volume and share it with your NAS clients. NetApp ONTAP does the rest.
FlexGroups Constituents
A FlexGroup constituent is an individual FlexVol volume that makes up a FlexGroup volume. A FlexGroup is a single, scalable namespace composed of many constituents that are automatically distributed across multiple aggregates and nodes. Each constituent handles a portion of the data and I/O, allowing FlexGroup volumes to deliver high performance, parallelism, and scalability while appearing to clients as one single volume.
Security and Data Protection
Vscan
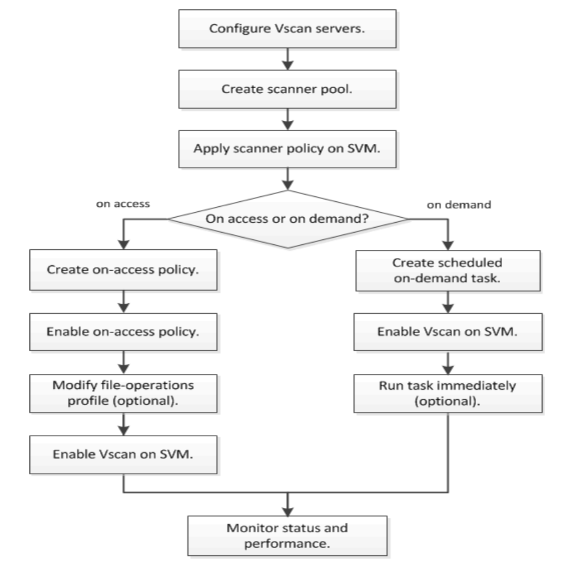
With Vscan you can use integrated antivirus functionality on NetApp storage systems to protect data from being compromised by viruses or other malicious code. NetApp virus scanning, called Vscan, combines best-in-class third-party antivirus software with ONTAP features that give you the flexibility you need to control which files get scanned and when.
Storage systems offload scanning operations to external servers hosting antivirus software from third-party vendors. The ONTAP Antivirus Connector, provided by NetApp and installed on the external server, handles communication between the storage system and the antivirus software.
You can use on-access scanning to check for viruses when clients open, read, rename, or close files over CIFS. File operation is suspended until the external server reports the scan status of the file. If the file has already been scanned, ONTAP allows the file operation. Otherwise, it requests a scan from the server.
You can use on-demand scanning to check files for viruses immediately or on a schedule. You might want to run scans only in off-peak hours, for example. The external server updates the scan status of the checked files, so that file-access latency for those files (assuming they have not been modified) is typically reduced when they are next accessed over CIFS. You can use on-demand scanning for any path in the SVM namespace, even for volumes that are exported only through NFS.
Typically, you enable both scanning modes on an SVM. In either mode, the antivirus software takes remedial action on infected files based on your settings in the software.
NetApp Volume Encryption and NetApp Aggregate Encryption
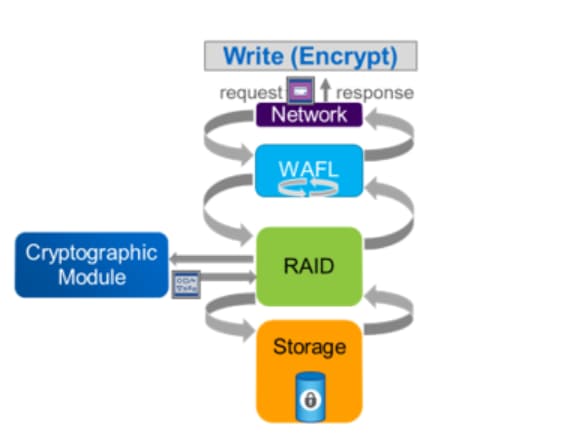
NetApp Volume Encryption (NVE) is a software-based, data-at-rest encryption solution that is FIPS 140-2 compliant. NVE allows ONTAP to encrypt data for each volume for granularity. NetApp Aggregate Encryption (NAE) is an outgrowth of NVE; it allows ONTAP to encrypt data for each volume, and the volumes can share keys across the aggregate. NVE and NAE enable you to use storage efficiency features that would be lost with encryption at the application layer. For greater storage efficiency, you can use aggregate deduplication with NAE.
Here’s how the process works: The data leaves the disk encrypted, is sent to RAID, is decrypted by the CryptoMod, and is then sent up the rest of the stack (Figure 18).
For the latest security features for ONTAP 9, go to: Security and data encryption.
For more information about Zero Trust security framework for FlexPod, go to: https://www.cisco.com/c/en/us/td/docs/unified_computing/ucs/UCS_CVDs/flexpod_zero_trust.html.
ONTAP Rest API
ONTAP Rest API enables you to automate the deployment and administration of your ONTAP storage systems using one of several available options. The ONTAP REST API provides the foundation for all the various ONTAP automation technologies.
Beginning with ONTAP 9.6, ONTAP includes an expansive workflow-driven REST API that you can use to automate deployment and management of your storage. In addition, NetApp provides a Python client library, which makes it easier to write robust code, as well as support for ONTAP automation based on Ansible.
AutoSupport and Active IQ Digital Advisor
ONTAP offers artificial intelligence-driven system monitoring and reporting through a web portal and through a mobile app. The AutoSupport component of ONTAP sends telemetry that is analyzed by Active IQ Digital Advisor. Active IQ enables you to optimize your data infrastructure across your global hybrid cloud by delivering actionable predictive analytics and proactive support through a cloud-based portal and mobile app. Data-driven insights and recommendations from Active IQ are available to all NetApp customers with an active SupportEdge contract (features vary by product and support tier).
The following are some things you can do with Active IQ:
● Plan upgrades. Active IQ identifies issues in your environment that can be resolved by upgrading to a newer version of ONTAP and the Upgrade Advisor component helps you plan for a successful upgrade.
● View system wellness. Your Active IQ dashboard reports any issues with wellness and helps you correct those issues. Monitor system capacity to make sure you never run out of storage space.
● Manage performance. Active IQ shows system performance over a longer period than you can see in ONTAP System Manager. Identify configuration and system issues that are impacting your performance.
● Maximize efficiency. View storage efficiency metrics and identify ways to store more data in less space.
● View inventory and configuration. Active IQ displays complete inventory and software and hardware configuration information. View when service contracts are expiring to ensure you remain covered.
VMware vSphere is a virtualization platform for holistically managing large collections of infrastructures (resources including CPUs, storage, and networking) as a seamless, versatile, and dynamic operating environment. Unlike traditional operating systems that manage an individual machine, VMware vSphere aggregates the infrastructure of an entire data center to create a single powerhouse with resources that can be allocated quickly and dynamically to any application in need. VMware vSphere 8.0 Update 3 can be installed using Cisco Intersight with Cisco custom ESXi images.
VMware vSphere 8.0 U3 has several improvements and simplifications including, but not limited to:
● Support for advanced virtualization and management capabilities in enterprise environments.
● Compatibility with Cisco UCS hardware and integration with Cisco Intersight for lifecycle and hardware management.
● Support for VMware vSphere Configuration Profiles introduced in earlier updates, enabling cluster-level host configuration management and compliance automation.
● Enhanced operational efficiency, performance improvements, and elevated security.
● Availability of Cisco custom ESXi 8.0 U3 installation images for streamlined deployment.
● Support for virtualized SAP HANA workloads with detailed installation and configuration guidance.
For more information about VMware vSphere and its components, see: https://www.vmware.com/products/vsphere.html.
VMware vSphere vCenter
VMware vCenter Server provides unified management of all hosts and VMs from a single console and aggregates performance monitoring of clusters, hosts, and VMs. VMware vCenter Server gives administrators a deep insight into the status and configuration of compute clusters, hosts, VMs, storage, the guest OS, and other critical components of a virtual infrastructure. VMware vCenter manages the rich set of features available in a VMware vSphere environment.
NetApp ONTAP Tools for VMware vSphere 10
NetApp ONTAP Tools for VMware vSphere 10 is a modern, integrated management solution that simplifies the lifecycle management of virtual machines running on NetApp ONTAP storage within VMware environments. Delivered as an Open Virtual Appliance (OVA), ONTAP Tools 10 is built on a horizontally scalable, event‑driven microservices architecture, enabling efficient provisioning, monitoring, protection, and recovery of VMware datastores and virtual machines directly from the vSphere client. It tightly integrates with the VMware ecosystem and includes key components such as the VASA Provider for storage policy‑based management, Storage Replication Adapter (SRA) for disaster recovery workflows, and native support for traditional datastores and VMware vVols. ONTAP Tools 10 also provides high availability at the application level, helping ensure continued operation during host, network, or application failures, while simplifying administration through role‑based access control and unified workflows all designed to reduce operational complexity and improve efficiency for VMware and storage teams.
To download ONTAP tools for VMware vSphere, go to: https://mysupport.netapp.com/site/products/all/details/otv10/downloads-tab.
NetApp NFS Plug-in for VMware VAAI
The NetApp NFS Plug-in for VMware vStorage APIs - Array Integration (VAAI) is a software library that integrates the VMware Virtual Disk Libraries that are installed on the ESXi host. The VMware VAAI package enables the offloading of certain tasks from the physical hosts to the storage array. Performing those tasks at the array level can reduce the workload on the ESXi hosts.
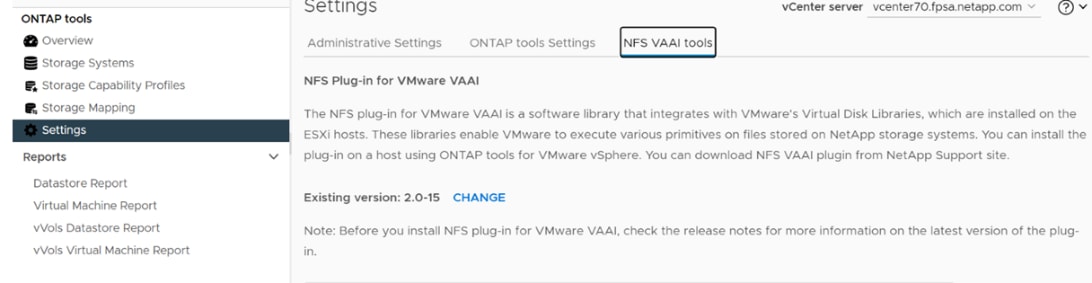
The copy offload feature and space reservation feature improve the performance of VSC operations. The NetApp NFS Plug-in for VAAI is not shipped with VSC, but you can install it by using VSC. You can download the plug-in installation package and obtain the instructions for installing the plug-in from the NetApp Support Site.
For more information about the NetApp VSC for VMware vSphere, see the NetApp Virtual Infrastructure Management Product Page.
NetApp XCP file analytics is host-based software to scan the file shares, collect and analyzes the data and provide insights into the file system. NetApp XCP file analytics works for both NetApp and non-NetApp systems and runs on Linux or Windows host. For more information, go to: http://docs.netapp.com/us-en/xcp/index.html
Architecture and Design Considerations for Desktop Virtualization
This chapter contains the following:
● Strategic and Business Alignment
● User Persona and Workload Profiling
● Infrastructure and Converged Architecture
● Operational and Security Considerations
● Citrix Virtual Apps and Desktops Design Fundamentals
In today’s hybrid workspace implementing a virtual desktop solution addresses the challenges of managing diverse device ecosystems, enforcing a Zero Trust security posture, and enabling flexible work models like BYOD—all while reducing the operational complexity associated with traditional endpoint lifecycle management.
The following is an example of the VDI Architectural Design Framework that can be followed to implement your virtual desktop solution.
Strategic and Business Alignment
Business Drivers: Evaluate drivers such as remote work, security, BYOD, and data sovereignty.
User Community Analysis: Identify the specific needs of your user base:
● Knowledge Workers: Require consistent access to apps/data across diverse locations.
● External Contractors: Require secure, segmented access with minimal device management overhead.
● Task Workers: Require high-availability access to critical, well-defined applications.
● Mobile Workers: Require offline capability and personalization features.
● Shared Workstation Users: Require rapid re-provisioning and high-frequency image updates.
Project Readiness: Ensure budget, infrastructure, and technical skill sets are secured for the pilot phase.
Success Metrics: Define KPIs (for example, login latency, application responsiveness) and determine the business impact of potential downtime (RTO/RPO).
User Persona and Workload Profiling
Desktop Environment Selection: Map users to the appropriate delivery model:
● Traditional PC: Physical device/local OS.
● Hosted Shared Desktop (RDSH): Server-based sessions (Windows Server 2022) for multi-user density.
● Published Applications: Application-level delivery via RDSH.
● Streamed Applications: Server-delivered apps running on local clients.
● Local Virtual Desktop: Client-side virtualization with data-center synchronization.
Application & Data Cataloging: Conduct a thorough audit of application dependencies and data locality. Account for cloud-native applications (for example, Salesforce) and use third-party assessment tools to identify potential bottlenecks.
Infrastructure and Converged Architecture
Compute (Cisco-Specific): Utilize Cisco UCS B-Series or C-Series servers to optimize density for virtual desktops and RDSH workloads.
Hypervisor: Standardize on a single hypervisor platform across your VDI environment. This is critical for maintaining a predictable, high-performance architecture.
Network: Implement QoS policies to prioritize real-time traffic (for example, Webex, Teams) and minimize latency across the fabric.
Storage: Deploy HCI or high-performance SANs. Ensure the storage tier is tuned for VDI-specific IOPS profiles, particularly to manage boot storms and write-intensive workloads.
Management: Utilize management platform for unified lifecycle management, policy-based automation, and predictive health monitoring.
Operational and Security Considerations
Sizing & Scalability:
● Define vCPU/vRAM allocations per sub-group.
● Specify OS versions (Windows 11, Windows Server 2022).
● Assess graphics requirements (for example, vGPU for rich media/graphics-intensive tasks).
Security & Hardening: Ensure images are hardened and integrated with VDI-aware security solutions to prevent resource contention during scans.
Profile Management: Implement robust profile management to ensure consistent user experiences across non-persistent sessions.
Fault Tolerance & DR: Establish clear failover and disaster recovery plans, including session redirection strategies for cluster-level events.
VMware vSphere has been identified as the hypervisor for Citrix Virtual Apps and Desktops environment. Standardizing on a single hypervisor platform, like VMware vSphere, is critical for maintaining a predictable, high-performance architecture.
VMware vSphere comprises the management infrastructure or virtual center server software and the hypervisor software that virtualizes the hardware resources on the servers. It offers features like Distributed Resource Scheduler, vMotion, high availability, Storage vMotion, VMFS, and a multi-pathing storage layer. More information on Vmware vSphere can be found at the VMware website: http://www.vmware.com/products/datacentervirtualization/vsphere/overview.html.
Cisco UCS and VMware vSphere are tightly integrated, providing:
● Cisco Intersight Integration: Cisco provides specific plugins and integration modules for vCenter, allowing you to manage compute resources, firmware, and BIOS settings directly from the virtualization management layer.
● Hardware Compatibility: Cisco maintains rigorous Hardware Compatibility Lists (HCLs) with VMware, ensuring that your VDI workloads run on a fully supported and validated stack.
Note: For this CVD, the hypervisor used was VMware ESXi 8.0 U3.
When utilizing Cisco UCS Server technology, it is recommended to configure Boot from SAN and store the boot partitions on remote storage, this enabled architects and administrators to take full advantage of the stateless nature of service profiles for hardware flexibility across lifecycle management of server hardware generational changes, Operating Systems/Hypervisors, and overall portability of server identity. Boot from SAN also removes the need to populate local server storage creating more administrative overhead.
NetApp AFF Storage Considerations
Note: Make sure each NetApp AFF Controller is connected to BOTH storage fabrics (A/B).
Within NetApp, the best practice is to map Hosts to iGroups and then iGroups to LUNs, this ensures same LUN ID to all hosts and allows for simplified management of ESXi Clusters across multiple nodes.
10/25/40/100 Gbe connectivity support – The AFF A50 utilizes a modular architecture with 8 PCIe expansion slots per HA pair. All Ethernet connectivity (ranging from 10GbE to 100GbE) must be provisioned via expansion NICs. Make sure required number of I/O modules to meet performance and redundancy have been included in the original AFF BOM.
16/32/64Gb Fiber Channel support - The AFF A50 series supports high-performance Fibre Channel up to 64Gb (autoranging). Always make sure the correct number of HBAs and the speed of SFPs are included in the original AFF BOM.
Oversubscription
To reduce the impact of an outage or maintenance scheduled downtime it Is good practice when designing fabrics to provide oversubscription of bandwidth, this enables a similar performance profile during component failure and protects workloads from being impacted by a reduced number of paths during a component failure or maintenance event. Oversubscription can be achieved by increasing the number of physically cabled connections between storage and compute. These connections can be utilized to deliver performance and reduced latency to the underlying workloads running on the solution.
When configuring your SAN, it’s important to remember that the more hops you have, the more latency you will see. For best performance, the ideal topology is a “Flat Fabric” where the AFF is only one hop away from any applications being hosted on it.
Citrix Virtual Apps and Desktops Design Fundamentals
An ever growing and diverse base of user devices, complexity in management of traditional desktops, security, and even Bring Your Own (BYO) device to work programs are prime reasons for moving to a virtual desktop solution.
Citrix Virtual Apps and Desktops 7 integrates Hosted Shared and VDI desktop virtualization technologies into a unified architecture that enables a scalable, simple, efficient, and manageable solution for delivering Windows applications and desktops as a service.
You can select applications from an easy-to-use “store” that is accessible from tablets, smartphones, PCs, Macs, and thin clients. Virtual Apps and Desktops delivers a native touch-optimized experience with HDX high-definition performance, even over mobile networks.
Collections of identical virtual machines or physical computers are managed as a single entity called a Machine Catalog. In this CVD, virtual machine provisioning relies on Citrix Provisioning Services and Machine Creation Services to make sure that the machines in the catalog are consistent. In this CVD, machines in the Machine Catalog are configured to run either a Multi-session OS VDA (Windows Server OS) or a Single-session OS VDA (Windows Desktop OS).
To deliver desktops and applications to users, you create a Machine Catalog and then allocate machines from the catalog to users by creating Delivery Groups. Delivery Groups provide desktops, applications, or a combination of desktops and applications to users. Creating a Delivery Group is a flexible way of allocating machines and applications to users. In a Delivery Group, you can:
● Use machines from multiple catalogs
● Allocate a user to multiple machines
● Allocate multiple users to one machine
As part of the creation process, you specify the following Delivery Group properties:
● Users, groups, and applications allocated to Delivery Groups
● Desktop settings to match users' needs
● Desktop power management options
Figure 20 illustrates how users access desktops and applications through machine catalogs and delivery groups.
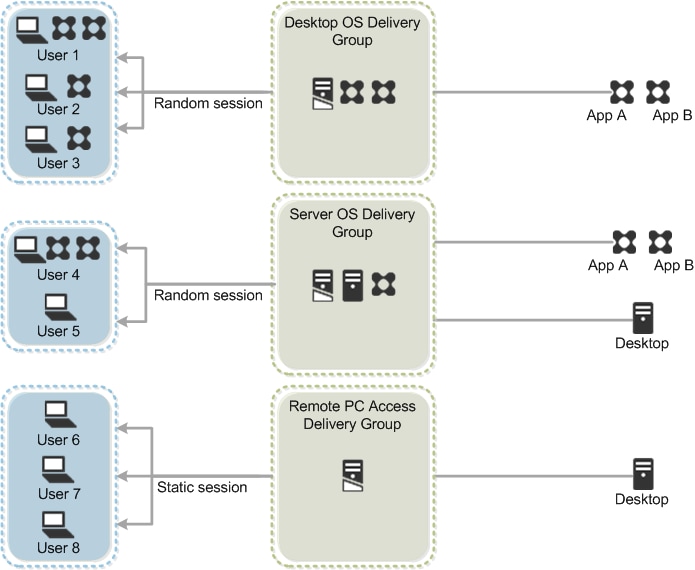
Citrix Virtual Apps and Desktops 7 can be deployed with or without Citrix Provisioning Services (PVS). The advantage of using Citrix PVS is that it allows virtual machines to be provisioned and re-provisioned in real-time from a single shared-disk image. In this way administrators can completely eliminate the need to manage and patch individual systems and reduce the number of disk images that they manage, even as the number of machines continues to grow, simultaneously providing the efficiencies of a centralized management with the benefits of distributed processing.
The Provisioning Services solution’s infrastructure is based on software-streaming technology. After installing and configuring Provisioning Services components, a single shared disk image (vDisk) is created from a device’s hard drive by taking a snapshot of the OS and application image and then storing that image as a vDisk file on the network. A device that is used during the vDisk creation process is the Master target device. Devices or virtual machines that use the created vDisks are called target devices.
When a target device is turned on, it is set to boot from the network and to communicate with a Provisioning Server. Unlike thin-client technology, processing takes place on the target device.
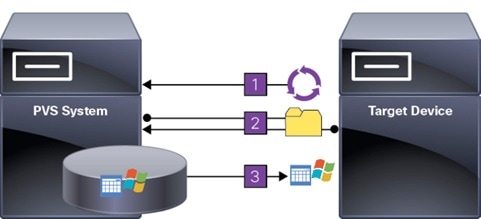
The target device downloads the boot file from a Provisioning Server (Step 2) and boots. Based on the boot configuration settings, the appropriate vDisk is mounted on the Provisioning Server (Step 3). The vDisk software is then streamed to the target device as needed, appearing as a regular hard drive to the system.
Instead of immediately pulling all the vDisk contents down to the target device (as with traditional imaging solutions), the data is brought across the network in real-time as needed. This approach allows a target device to get a completely new operating system and set of software in the time it takes to reboot. This approach dramatically decreases the amount of network bandwidth required and making it possible to support a larger number of target devices on a network without impacting performance
Citrix PVS can create desktops as Pooled or Private:
● Pooled Desktop: A pooled virtual desktop uses Citrix PVS to stream a standard desktop image to multiple desktop instances upon boot.
● Private Desktop: A private desktop is a single desktop assigned to one distinct user.
● The alternative to Citrix Provisioning Services for pooled desktop deployments is Citrix Machine Creation Services (MCS), which is integrated with the Virtual Apps and Desktops Studio console.
Locate the PVS Write Cache
When considering a PVS deployment, there are some design decisions that need to be made regarding the write cache for the target devices that leverage provisioning services. The write cache is a cache of all data that the target device has written. If data is written to the PVS vDisk in a caching mode, the data is not written back to the base vDisk. Instead, it is written to a write cache file in one of the following locations:
● Cache in device RAM. Write cache can exist as a temporary file in the target device’s RAM. This provides the fastest method of disk access since memory access is always faster than disk access.
● Cache in device RAM with overflow on hard disk. This method uses VHDX differencing format and is only available for Windows 11 and Server 2008 R2 and later. When RAM is zero, the target device write cache is only written to the local disk. When RAM is not zero, the target device write cache is written to RAM first. When RAM is full, the least recently used block of data is written to the local differencing disk to accommodate newer data on RAM. The amount of RAM specified is the non-paged kernel memory that the target device will consume.
● Cache on a server. Write cache can exist as a temporary file on a Provisioning Server. In this configuration, all writes are handled by the Provisioning Server, which can increase disk I/O and network traffic. For additional security, the Provisioning Server can be configured to encrypt write cache files. Since the write-cache file persists on the hard drive between reboots, encrypted data provides data protection in the event a hard drive is stolen.
● Cache on server persisted. This cache option allows for the saved changes between reboots. Using this option, a rebooted target device is able to retrieve changes made from previous sessions that differ from the read only vDisk image. If a vDisk is set to this method of caching, each target device that accesses the vDisk automatically has a device-specific, writable disk file created. Any changes made to the vDisk image are written to that file, which is not automatically deleted upon shutdown.
Note: In this CVD, Provisioning Server 2402 was used to manage Pooled/Non-Persistent Single-session OS Machines with “Cache in device RAM with Overflow on Hard Disk” for each virtual machine. This design enables good scalability to many thousands of desktops. Provisioning Server 2402 was used for Active Directory machine account creation and management as well as for streaming the shared disk to the hypervisor hosts.
Example Citrix Virtual Apps and Desktops Deployments
Two examples of typical Virtual Apps and Desktops deployments are as follows:
● A distributed components configuration
● A multiple site configuration
Distributed Components Configuration
You can distribute the components of your deployment among a greater number of servers or provide greater scalability and failover by increasing the number of controllers in your site. You can install management consoles on separate computers to manage the deployment remotely. A distributed deployment is necessary for an infrastructure based on remote access through NetScaler Gateway (formerly called Access Gateway).
Figure 22 shows an example of a distributed components configuration. A simplified version of this configuration is often deployed for an initial proof-of-concept (POC) deployment. This CVD deploys Citrix Virtual Apps and Desktops in a configuration that resembles this distributed component configuration shown.
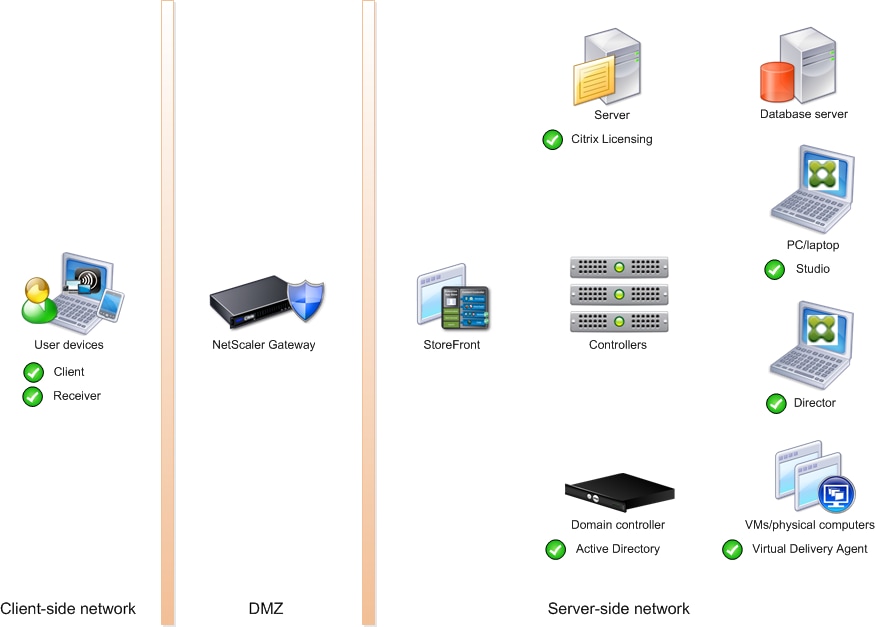
If you have multiple regional sites, you can use Citrix NetScaler to direct user connections to the most appropriate site and StoreFront to deliver desktops and applications to users.
Figure 23 depicts multiple sites; a site was created in two data centers. Having two sites globally, rather than just one, minimizes the amount of unnecessary WAN traffic.
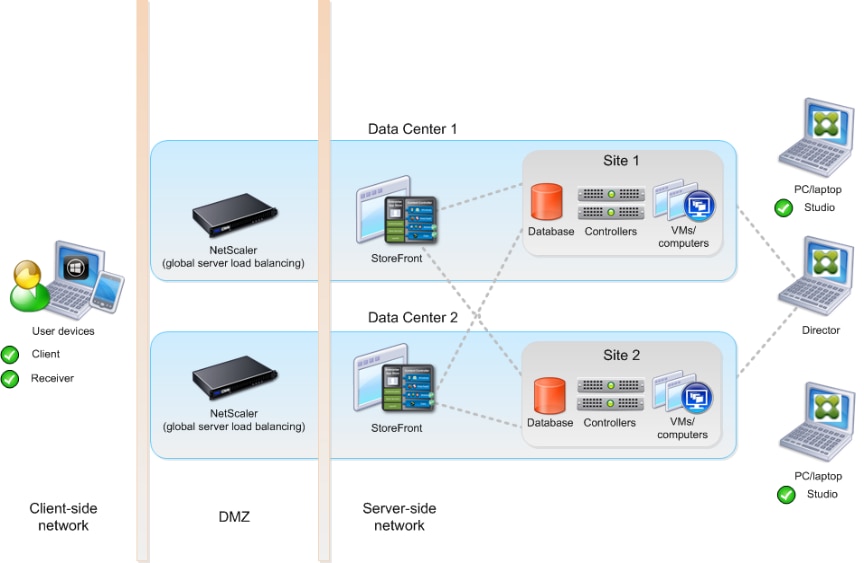
You can use StoreFront to aggregate resources from multiple sites to provide users with a single point of access with NetScaler. A separate Studio console is required to manage each site; sites cannot be managed as a single entity. You can use Director to support users across sites.
Citrix NetScaler accelerates application performance, load balances servers, increases security, and optimizes the user experience. In this example, two NetScalers are used to provide a high availability configuration. The NetScalers are configured for Global Server Load Balancing and positioned in the DMZ to provide a multi-site, fault-tolerant solution.
Note: This CVD was done based on single site and did not use NetScaler for its infrastructure and testing.
Easily deliver the Citrix portfolio of products as a service. Citrix Cloud services simplify the delivery and management of Citrix technologies extending existing on-premises software deployments and creating hybrid workspace services.
● Fast: Deploy apps and desktops, or complete secure digital workspaces in hours, not weeks.
● Adaptable: Choose to deploy on any cloud or virtual infrastructure — or a hybrid of both.
● Secure: Keep all proprietary information for your apps, desktops, and data under your control.
● Simple: Implement a fully-integrated Citrix portfolio through a single-management plane to simplify administration
Design a Virtual Apps and Desktops Environment for Different Workloads
With Citrix Virtual Apps and Desktops, the method you choose to provide applications or desktops to users depends on the types of applications and desktops you are hosting and available system resources, as well as the types of users and user experience you want to provide.
| Desktop Type |
User Experience |
| Server OS machines |
You want: Inexpensive server-based delivery to minimize the cost of delivering applications to a large number of users, while providing a secure, high-definition user experience. Your users: Perform well-defined tasks and do not require personalization or offline access to applications. Users may include task workers such as call center operators and retail workers, or users that share workstations. Application types: Any application. |
| Desktop OS machines |
You want: A client-based application delivery solution that is secure, provides centralized management, and supports a large number of users per host server (or hypervisor), while providing users with applications that display seamlessly in high-definition. Your users: Are internal, external contractors, third-party collaborators, and other provisional team members. Users do not require off-line access to hosted applications. Application types: Applications that might not work well with other applications or might interact with the operating system, such as .NET framework. These types of applications are ideal for hosting on virtual machines. Applications running on older operating systems such as Windows XP or Windows Vista, and older architectures, such as 32-bit or 16-bit. By isolating each application on its own virtual machine, if one machine fails, it does not impact other users. |
| Remote PC Access |
You want: Employees with secure remote access to a physical computer without using a VPN. For example, the user may be accessing their physical desktop PC from home or through a public WIFI hotspot. Depending upon the location, you may want to restrict the ability to print or copy and paste outside of the desktop. This method enables BYO device support without migrating desktop images into the data center. Your users: Employees or contractors that have the option to work from home but need access to specific software or data on their corporate desktops to perform their jobs remotely. Host: The same as Desktop OS machines. Application types: Applications that are delivered from an office computer and display seamlessly in high definition on the remote user's device. |
For this Cisco Validated Design, the following designs are included:
● Single-session OS Solution:
◦ MCS: 1610 Windows 11 Virtual desktops random pooled were configured and tested
◦ PVS: 1610 Windows 11 Virtual desktops random pooled were configured and tested
◦ MCS: 1610 Windows 11 Virtual desktops static persistent were configured and tested
● Multi-session OS Solution:
◦ MCS: 2600 Windows Server 2022 random pooled desktops were configured and tested
Deployment Hardware and Software
This chapter contains the following:
The architecture deployed is highly modular. While each environment might vary in its exact configuration, the reference architecture contained in this document once built, can easily be scaled as requirements, and demands change. This includes scaling both up (adding additional resources within a Cisco UCS Domain) and out (adding additional Cisco UCS Domains and NetApp storage).
The FlexPod Datacenter solution includes Cisco networking, Cisco UCS and NetApp AFF A50, which efficiently fit into a single data center rack, including the access layer network switches.
This CVD details the deployment of up to 2600 Multi-session OS, 1600 Single-session OS VDI users featuring the following software:
● VMware vSphere ESXi 8.0 U3 Hypervisor
● Microsoft SQL Server 2022
● Microsoft Windows Server 2022 and Windows 11 64-bit virtual machine Operating Systems
● Citrix Virtual Apps and Desktops 2402 LTSR CU3
● Citrix Provisioning Server 2402 LTSR CU3
● FSLogix 25.09
● Citrix StoreFront 2402 LTSR
● NetApp ONTAP Tools for VMware vSphere 10
● NetApp ONTAP 9.17.1P4
FlexPod with Cisco UCS M8 servers, Citrix Virtual Apps and Desktops Remote Desktop Server Hosted (RDSH) sessions and Windows 11 virtual desktops on vSphere 8.0 U3 delivers a Virtual Desktop Infrastructure that is redundant, using the best practices of Cisco and NetApp Storage. The solution includes VMware vSphere 8.0 U3 hypervisor installed on the Cisco UCS M8 Compute Node Server configured for stateless compute design using boot from SAN. NetApp Storage AFF A50 provides the storage infrastructure required for setting up the VDI workload. Cisco Intersight is utilized to configure and manage the Cisco UCS infrastructure with Cisco Intersight providing lifecycle management capabilities. The solution requirements and design details are covered in this section.
FlexPod VDI with Cisco UCS X215c M8 servers is a Fibre Channel and NFS-based storage access design. NetApp Storage AFF and Cisco UCS are connected through Cisco Nexus and Cisco MDS switches, and storage access utilizes the NFS and Fibre Channel protocols. For VDI IP based file share storage access NetApp Storage AFF Cisco UCS are connected through Cisco Nexus N9K-C93180YC-FX switches. The physical connectivity details are explained below.
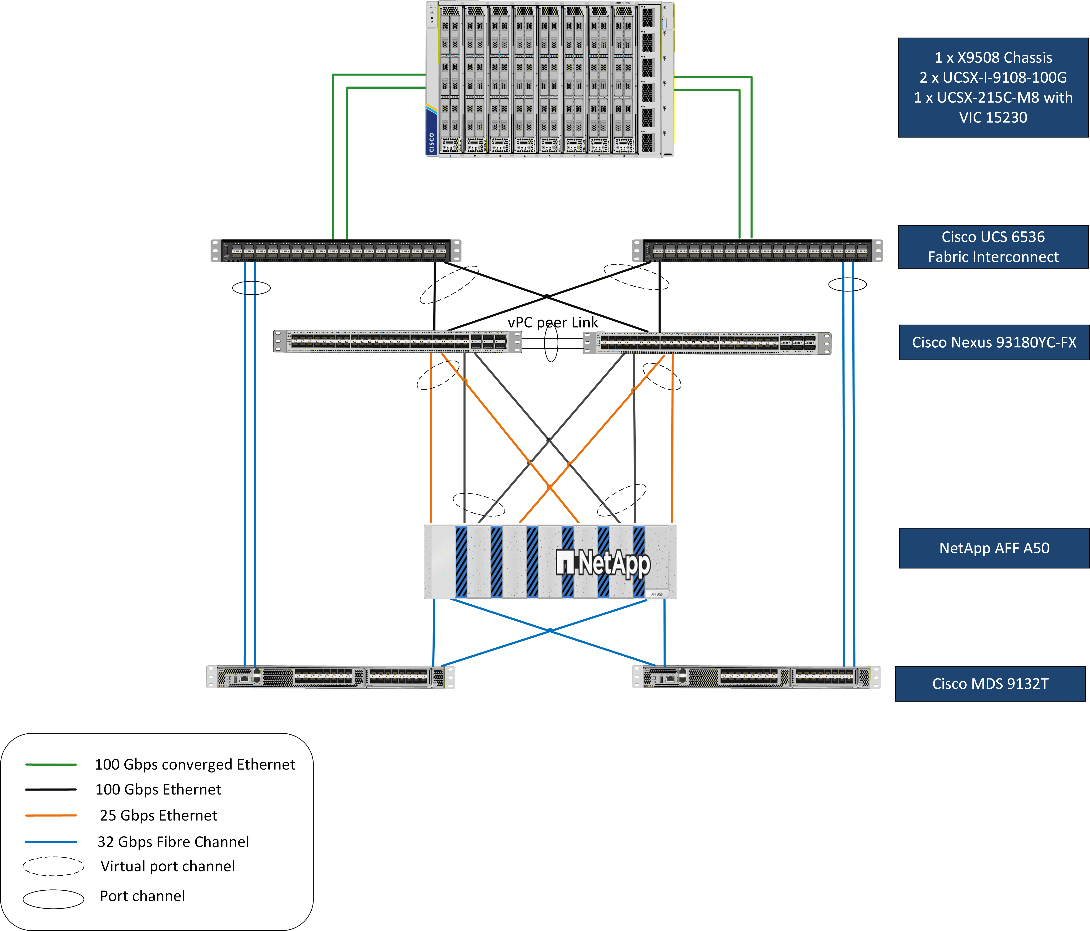
Figure 24 details the physical hardware and cabling deployed to enable this solution:
● 2 Cisco Nexus N9K-C93180YC-FX Switches in NX-OS Mode.
● 8 Cisco UCS X215c M8 Compute Nodes with AMD EPYC 9355 3.55 GHz 32-Core processors, 1TB 6400MHz RAM, and one Cisco UCS VIC 15230 card, providing N+1 server fault tolerance.
● NetApp AFF A50 System with dual redundant controllers, 1x disk shelf, and 8 x 1.9 TB solid-state NVMe drives providing storage and FC/NFS/CIFS connectivity.
Note: The common services and LoginVSI Test infrastructure are not a part of the physical topology of this solution.
Table 2 lists the software versions of the primary products installed in the environment.
Table 2. Software and Firmware Versions
| Vendor |
Product / Component |
Version / Build / Code |
| Cisco |
Cisco Infrastructure Firmware |
6.0(1.250198) bundle release |
| Cisco |
UCS X215c M8 Compute Nodes |
6.0(1.250122) bundle release |
| Cisco |
VIC 15231 |
6.0(1.250122) bundle release |
| Cisco |
Cisco Nexus N9K-C93180YC-FX |
10.4(6) |
| Cisco |
MDS 9132T |
9.4(3a) |
| NetApp |
AFF A50 |
ONTAP 9.17.1P4 |
| NetApp |
ONTAP Tools for VMWare vSphere |
10.5 |
| NetApp |
NetApp NFS Plug-in for VMWare VAAI |
2.0.1 |
| VMware |
vCenter Server Appliance |
8.0.3.24022515 |
| VMware |
vSphere 8.0 U3 |
8.0.3, 24022510 |
| VMware |
Tools |
11.2.5.17337674 |
| Citrix |
Broker |
2402 LTSR U3 |
| Citrix |
Agent |
2402 LTSR U3 |
| Citrix |
Provisioning Server |
2402 LTSR U3 |
| Citrix |
StoreFront |
2402 LTSR U3 |
The logical architecture of the validated solution which is designed to support up to 2600 users on a single chassis containing eight Cisco UCS X215c M8 Compute Node Servers, with physical redundancy for the Compute Node servers for each workload type is illustrated in Figure 25.
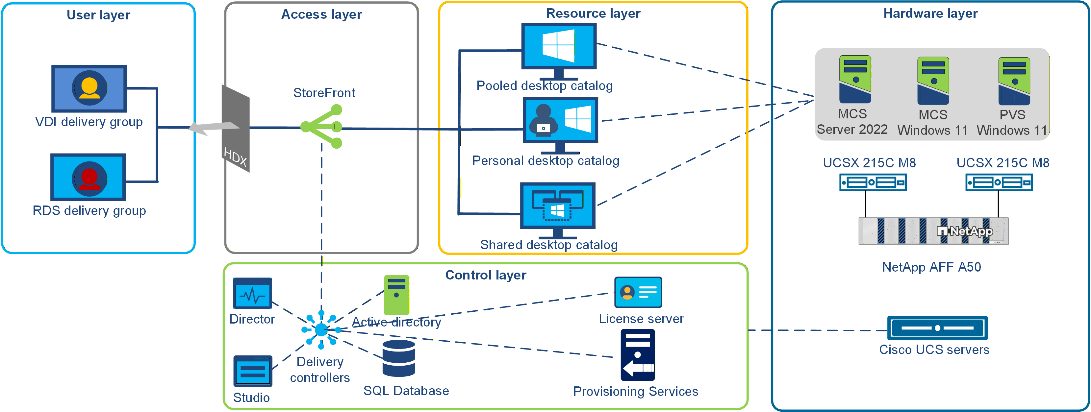
Two VMware Clusters in two vCenter data center were used to support the FlexPod for VDI solution. This design aligns with Cisco Validated Designs for FlexPod with Citrix and Broadcom, which recommend separating infrastructure and workload clusters for scalability and management, using standard switches for management traffic and distributed switches for VM and storage traffic, and supporting multiple NFS and Fibre Channel datastores for storage flexibility and performance:
● Combined Infrastructure and VSI Launcher Cluster: Hosts infrastructure VMs and Login VSI testing infrastructure, on separate storage from VDI workloads.
● VDI Workload Cluster: Dedicated to VDI user workloads with Windows Server 2022 and Windows 11 streamed desktops, leveraging Citrix Virtual Apps and Desktops.
◦ Networking Configuration
Management Network: standard vSwitch for management traffic to ensure simplicity and isolation of management functions.
VM and Storage Traffic: distributed vSwitch for all other traffic including VM network, vMotion, NFS storage data traffic to provide centralized management, scalability, and consistent network policies across hosts.
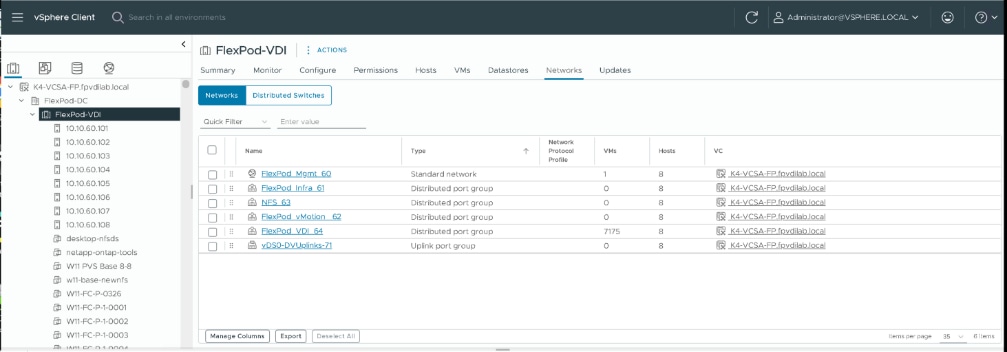
◦ Storage Configuration
Datastores:
- 4 NFS datastores for IP-based storage access.
- 4 Fibre Channel datastores for block storage access.
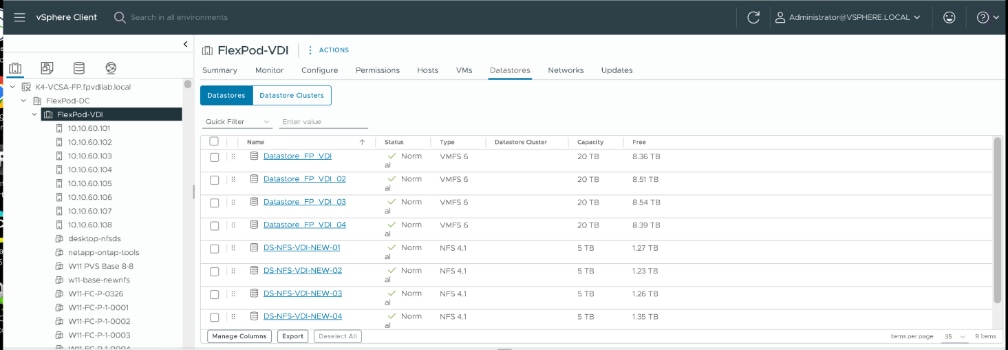
The Citrix Virtual Apps and Desktops solution described in this document provides details for configuring a fully redundant, highly-available configuration. Configuration guidelines are provided that refer to which redundant component is being configured with each step, whether that be A or B. For example, Nexus A and Nexus B identify the pair of Cisco Nexus switches that are configured. The Cisco UCS Fabric Interconnects are configured similarly.
This document is intended to allow you to configure the Citrix Virtual Apps and Desktops 2402 LTSR environment as a stand-alone solution.
The VLAN configuration recommended for the environment includes a total of six VLANs as listed in Table 3.
Table 3. VLANs Configured in this Study
| VLAN Name |
VLAN ID |
VLAN Purpose |
| Default |
1 |
Native VLAN |
| In-Band-Mgmt |
60 |
In-Band management interfaces |
| Infra-Mgmt |
61 |
Infrastructure Virtual Machines and CIFS |
| vMotion |
62 |
vMotion for DRS and migration |
| NFS- VLAN |
63 |
VLAN for NFS storage traffic |
| VCC/VM-Network |
64 |
RDSH, VDI Persistent and Non-Persistent |
| Client-Network |
65 |
Login Enterprise Infrastructure Virtual Machines |
| OOB-Mgmt |
132 |
Out-of-Band management interfaces |
This chapter contains the following:
● FlexPod Cisco Nexus Switch Configuration
The following sections detail the physical connectivity configuration of the FlexPod VMware VDI environment.
The information provided in this section is a reference for cabling the physical equipment in this Cisco Validated Design environment. To simplify cabling requirements, the tables include both local and remote device and port locations.
The tables in this section contain the details for the prescribed and supported configuration of the NetApp Storage AFF A50 storage array to the Cisco UCS 6536 Fabric Interconnects through Cisco Nexus Switches.
Note: This document assumes that out-of-band management ports are plugged into an existing management infrastructure at the deployment site. These interfaces will be used in various configuration steps.
IMPORTANT! Be sure to follow the cabling directions in this section. Failure to do so will result in unnecessary changes to the deployment since specific port locations are mentioned.
Figure 35 details the cable connections used in the validation lab for FlexPod topology based on the Cisco UCS 6536 fabric interconnect. Also, 40Gb links connect the Cisco UCS Fabric Interconnects to the Cisco Nexus Switches and the NetApp AFF A50 controllers to the Cisco Nexus Switches. Additional 1Gb management connections will be needed for an out-of-band network switch that sits apart from the FlexPod infrastructure. Each Cisco UCS fabric interconnect and Cisco Nexus switch is connected to the out-of-band network switch, and each All Flash Array controller has a connection to the out-of-band network switch. Layer 3 network connectivity is required between the Out-of-Band (OOB) and In-Band (IB) Management Subnets.
The architecture is divided into three distinct layers:
● Cisco UCS Compute Platform
● Network Access layer and LAN
● Storage Access to the NetApp AFF A50
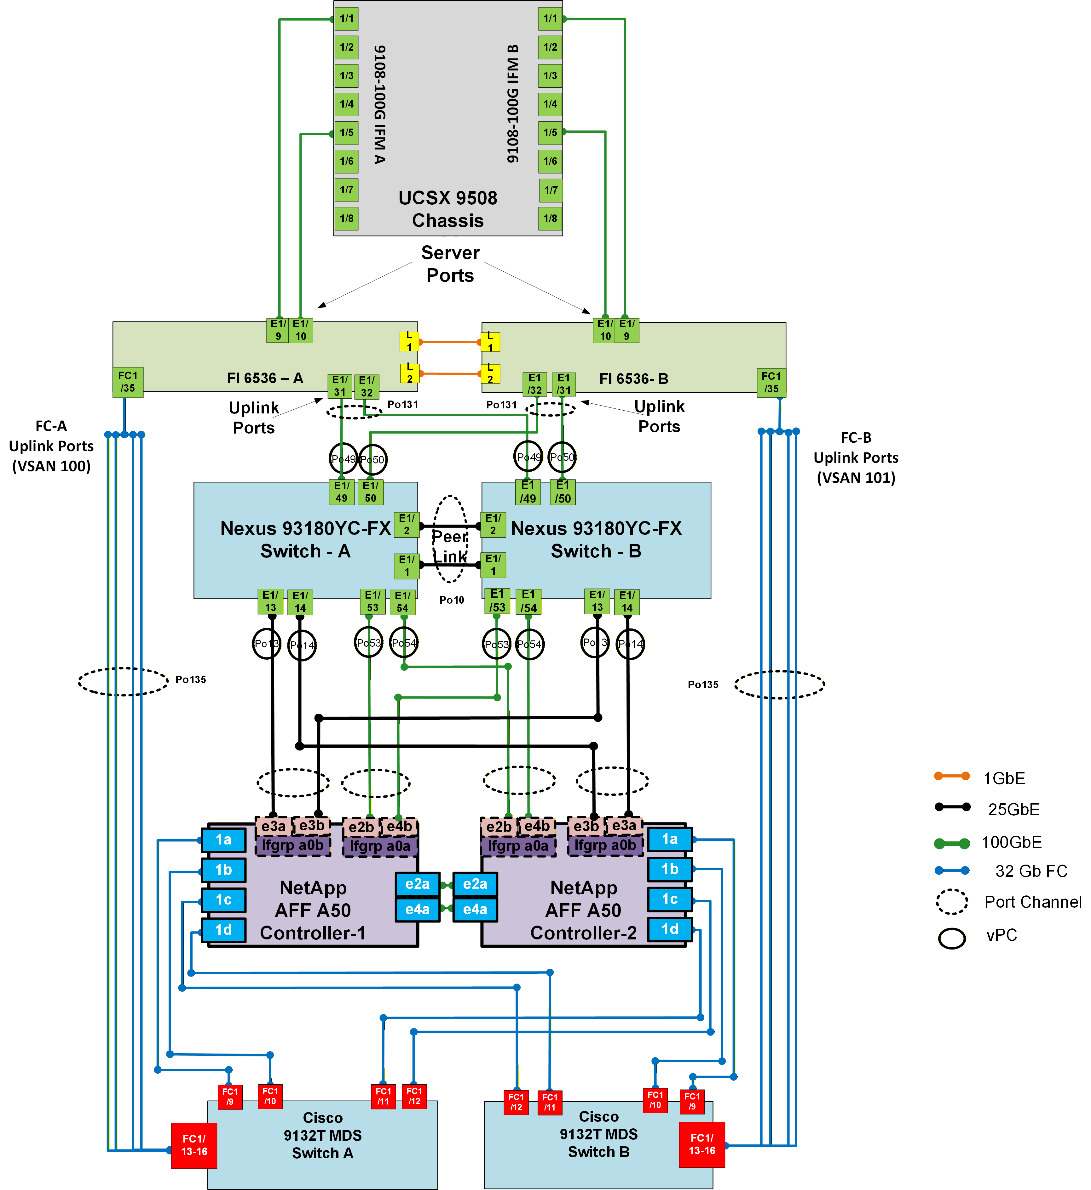
Table 4. Cisco Nexus N9K-C93180YC-FX-A Cabling Information
| Local Device |
Local Port |
Connection |
Remote Device |
Remote Port |
| Cisco Nexus N9K-C93180YC-FX A |
Eth1/13 |
25GbE |
NetApp Controller 1 |
e3a |
| Eth1/14 |
25GbE |
NetApp Controller 2 |
e3b |
|
| Eth1/53 |
100GbE |
NetApp Controller 1 |
e2b |
|
| Eth1/54 |
100GbE |
NetApp Controller 2 |
e2b |
|
| Eth1/49 |
100GbE |
Cisco UCS fabric interconnect A |
P0 1/31 |
|
| Eth1/50 |
100GbE |
Cisco UCS fabric interconnect B |
P0 1/32 |
|
| Eth1/1 |
25GbE |
Cisco Nexus N9K-C93180YC-FX B |
Eth1/1 |
|
| Eth1/2 |
25GbE |
Cisco Nexus N9K-C93180YC-FX B |
Eth1/2 |
|
| MGMT0 |
GbE |
GbE management switch |
Any |
Note: For devices requiring GbE connectivity, use the GbE Copper SFP+s (GLC-T=).
Table 5. Cisco Nexus N9K-C93180YC-FX-B Cabling Information
| Local Device |
Local Port |
Connection |
Remote Device |
Remote Port |
| Cisco Nexus N9K-C93180YC-FX B |
Eth1/13 |
25GbE |
NetApp Controller 1 |
e3b |
| Eth1/14 |
25GbE |
NetApp Controller 2 |
e3a |
|
| Eth1/53 |
100GbE |
NetApp Controller 1 |
e4b |
|
| Eth1/54 |
100GbE |
NetApp Controller 2 |
e4b |
|
| Eth1/49 |
100GbE |
Cisco UCS fabric interconnect A |
P0 1/32 |
|
| Eth1/50 |
100GbE |
Cisco UCS fabric interconnect B |
P0 1/31 |
|
| Eth1/1 |
25GbE |
Cisco Nexus N9K-C93180YC-FX A |
Eth1/1 |
|
| Eth1/2 |
25GbE |
Cisco Nexus N9K-C93180YC-FX A |
Eth1/2 |
|
| MGMT0 |
GbE |
GbE management switch |
Any |
Table 6. NetApp Controller-1 Cabling Information
| Local Device |
Local Port |
Connection |
Remote Device |
Remote Port |
| NetApp AFF A50 Node 1
|
e0M |
1GbE |
1GbE management switch |
Any |
| e2b |
100GbE |
Cisco Nexus N9K-C93180YC-FX A |
Eth1/53 |
|
| e4b |
100GbE |
Cisco Nexus N9K-C93180YC-FX B |
Eth1/53 |
|
| e3a |
25GbE |
Cisco Nexus N9K-C93180YC-FX B |
Eth1/13 |
|
| e3b |
25GbE |
Cisco Nexus N9K-C93180YC-FX A |
Eth1/13 |
|
| 1a |
32Gb FC |
Cisco MDS 9132T A |
FC1/9 |
|
| 1b |
32Gb FC |
Cisco MDS 9132T A |
FC1/10 |
|
|
|
1c |
32Gb FC |
Cisco MDS 9132T B |
FC1/12 |
|
|
1d |
32Gb FC |
Cisco MDS 9132T B |
FC1/11 |
Note: When the term e0M is used, the physical Ethernet port to which the table is referring is the port indicated by a wrench icon on the rear of the chassis.
Table 7. NetApp Controller 2 Cabling Information
| Local Device |
Local Port |
Connection |
Remote Device |
Remote Port |
| NetApp AFF A50 Node 2
|
e0M |
1GbE |
1GbE management switch |
Any |
| e2b |
100GbE |
Cisco Nexus N9K-C93180YC-FX A |
Eth1/54 |
|
| e4b |
100GbE |
Cisco Nexus N9K-C93180YC-FX B |
Eth1/54 |
|
| e3a |
25GbE |
Cisco Nexus N9K-C93180YC-FX B |
Eth1/14 |
|
| e3b |
25GbE |
Cisco Nexus N9K-C93180YC-FX A |
Eth1/14 |
|
| 1a |
32Gb FC |
Cisco MDS 9132T B |
FC1/9 |
|
| 1b |
32Gb FC |
Cisco MDS 9132T B |
FC1/10 |
|
|
|
1c |
32Gb FC |
Cisco MDS 9132T A |
FC1/12 |
|
|
1d |
32Gb FC |
Cisco MDS 9132T A |
FC1/11 |
Table 8. Cisco UCS Fabric Interconnect A Cabling Information
| Local Device |
Local Port |
Connection |
Remote Device |
Remote Port |
| Cisco UCS Fabric Interconnect A |
Eth1/31 |
100GbE |
Cisco Nexus N9K-C93180YC-FX A |
Eth1/49 |
| Eth1/32 |
100GbE |
Cisco Nexus N9K-C93180YC-FX B |
Eth1/49 |
|
| Eth1/9 |
100GbE |
UCS 9508 Chassis IFM A |
IFM 1 Port1/1 |
|
| Eth1/10 |
100GbE |
UCS 9508 Chassis IFM A |
IFM 1 Port1/5 |
|
| FC 1/35/1 |
32G FC |
Cisco MDS 9132T 32-Gb-A |
FC 1/13 |
|
| FC 1/35/2 |
32G FC |
Cisco MDS 9132T 32-Gb-A |
FC 1/14 |
|
| FC 1/35/3 |
32G FC |
Cisco MDS 9132T 32-Gb-A |
FC 1/15 |
|
| FC 1/35/4 |
32G FC |
Cisco MDS 9132T 32-Gb-A |
FC 1/16 |
|
| MGMT0 |
1GbE |
1GbE Management switch |
Any |
|
| L1 |
1GbE |
Cisco UCS fabric interconnect B |
L1 |
|
| L2 |
1GbE |
Cisco UCS fabric interconnect B |
L2 |
Table 9. Cisco UCS Fabric Interconnect B Cabling Information
| Local Device |
Local Port |
Connection |
Remote Device |
Remote Port |
| Cisco UCS Fabric Interconnect B |
Eth1/31 |
100bE |
Cisco Nexus N9K-C93180YC-FX B |
Eth1/50 |
| Eth1/32 |
100GbE |
Cisco Nexus N9K-C93180YC-FX B |
Eth1/50 |
|
| Eth1/9 |
100GbE |
UCS 9508 Chassis IFM B |
IFM 2 Port1/1 |
|
| Eth1/10 |
100GbE |
UCS 9508 Chassis IFM B |
IFM 2 Port1/5 |
|
| FC 1/35/1 |
100G FC |
Cisco MDS 9132T 32-Gb-B |
FC 1/13 |
|
| FC 1/35/2 |
32G FC |
Cisco MDS 9132T 32-Gb-B |
FC 1/14 |
|
| FC 1/35/3 |
32G FC |
Cisco MDS 9132T 32-Gb-B |
FC 1/15 |
|
| FC 1/35/4 |
32G FC |
Cisco MDS 9132T 32-Gb-B |
FC 1/16 |
|
| MGMT0 |
1GbE |
GbE management switch |
Any |
|
| L1 |
1GbE |
Cisco UCS fabric interconnect A |
L1 |
|
| L2 |
1GbE |
Cisco UCS fabric interconnect A |
L2 |
Note: We used four 32Gb FC connections from each fabric interconnect to each MDS switch and four 32Gb FC connections from each NetApp AFF A50 storage array controller to each MDS switch.
Table 10. Cisco MDS 9132T-A Cabling Information
| Local Device |
Local Port |
Connection |
Remote Device |
Remote Port |
| Cisco MDS 9132T-A
|
FC1/9 |
32Gb FC |
NetApp AFF A50 Node 1 |
1a |
| FC1/10 |
32Gb FC |
NetApp AFF A50 Node 1 |
1b |
|
| FC1/11 |
32Gb FC |
NetApp AFF A50 Node 2 |
1d |
|
| FC1/12 |
32Gb FC |
NetApp AFF A50 Node 2 |
1c |
|
|
|
FC1/13 |
32Gb FC |
Cisco 6536 Fabric Interconnect-A |
FC1/35/1 |
|
|
FC1/14 |
32Gb FC |
Cisco 6536 Fabric Interconnect-A |
FC1/35/2 |
|
|
FC1/15 |
32Gb FC |
Cisco 6536 Fabric Interconnect-A |
FC1/35/3 |
|
|
FC1/16 |
32Gb FC |
Cisco 6536 Fabric Interconnect-A |
FC1/35/4 |
Table 11. Cisco MDS 9132T-B Cabling Information
| Local Device |
Local Port |
Connection |
Remote Device |
Remote Port |
| Cisco MDS 9132T-B
|
FC1/9 |
32Gb FC |
NetApp AFF A50 Node 2 |
1a |
| FC1/10 |
32Gb FC |
NetApp AFF A50 Node 2 |
1b |
|
| FC1/11 |
32Gb FC |
NetApp AFF A50 Node 1 |
1d |
|
| FC1/12 |
32Gb FC |
NetApp AFF A50 Node 1 |
1c |
|
|
|
FC1/13 |
32Gb FC |
Cisco 6536 Fabric Interconnect-B |
FC1/35/1 |
|
|
FC1/14 |
32Gb FC |
Cisco 6536 Fabric Interconnect-B |
FC1/35/2 |
|
|
FC1/15 |
32Gb FC |
Cisco 6536 Fabric Interconnect-B |
FC1/35/3 |
|
|
FC1/16 |
32Gb FC |
Cisco 6536 Fabric Interconnect-B |
FC1/35/4 |
Network Switch Configuration
This section provides a detailed procedure for configuring the Cisco Nexus N9K-C93180YC-FX switches for use in a FlexPod environment. The Cisco Nexus N9K-C93180YC-FX will be used LAN switching in this solution.
IMPORTANT! Follow these steps precisely because failure to do so could result in an improper configuration.
Follow the physical connectivity guidelines for FlexPod as explained in section Solution Cabling.
The following procedures describe how to configure the Cisco Nexus switches for use in a base FlexPod environment. This procedure assumes the use of Cisco Nexus 9000 10.4(6) or later, the Cisco suggested Nexus switch release at the time of this validation.
The following procedure includes the setup of NTP distribution on both the mgmt0 port and the in-band management VLAN. The interface-vlan feature and ntp commands are used to set this up. This procedure also assumes that the default VRF is used to route the in-band management VLAN.
Note: In this validation, port speed and duplex are hard set at both ends of every 100GE connection.
Procedure 1. Set Up Initial Configuration on Cisco Nexus A
Set up the initial configuration for the Cisco Nexus A switch on <nexus-A-hostname>
Step 1. On initial boot and connection to the serial or console port of the switch, the NX-OS setup should automatically start and attempt to enter Power on Auto Provisioning.
Abort Power On Auto Provisioning [yes - continue with normal setup, skip - bypass password and basic configuration, no - continue with Power On Auto Provisioning] (yes/skip/no)[no]: yes
Disabling POAP.......Disabling POAP
poap: Rolling back, please wait... (This may take 5-15 minutes)
---- System Admin Account Setup ----
Do you want to enforce secure password standard (yes/no) [y]: Enter
Enter the password for "admin": <password>
Confirm the password for "admin": <password>
Would you like to enter the basic configuration dialog (yes/no): yes
Create another login account (yes/no) [n]: Enter
Configure read-only SNMP community string (yes/no) [n]: Enter
Configure read-write SNMP community string (yes/no) [n]: Enter
Enter the switch name: <nexus-A-hostname>
Continue with Out-of-band (mgmt0) management configuration? (yes/no) [y]: Enter
Mgmt0 IPv4 address: <nexus-A-mgmt0-ip>
Mgmt0 IPv4 netmask: <nexus-A-mgmt0-netmask>
Configure the default gateway? (yes/no) [y]: Enter
IPv4 address of the default gateway: <nexus-A-mgmt0-gw>
Configure advanced IP options? (yes/no) [n]: Enter
Enable the telnet service? (yes/no) [n]: Enter
Enable the ssh service? (yes/no) [y]: Enter
Type of ssh key you would like to generate (dsa/rsa) [rsa]: Enter
Number of rsa key bits <1024-2048> [1024]: Enter
Configure the ntp server? (yes/no) [n]: Enter
Configure default interface layer (L3/L2) [L2]: Enter
Configure default switchport interface state (shut/noshut) [noshut]: shut
Enter basic FC configurations (yes/no) [n]: Enter
removed (strict/moderate/lenient/dense) [strict]: Enter
Would you like to edit the configuration? (yes/no) [n]: Enter
Step 2. Review the configuration summary before enabling the configuration.
Use this configuration and save it? (yes/no) [y]: Enter
Procedure 2. Set Up Initial Configuration on Cisco Nexus B
Set up the initial configuration for the Cisco Nexus B switch on <nexus-B-hostname>.
Step 1. On initial boot and connection to the serial or console port of the switch, the NX-OS setup should automatically start and attempt to enter Power on Auto Provisioning.
Abort Power On Auto Provisioning [yes - continue with normal setup, skip - bypass password and basic configuration, no - continue with Power On Auto Provisioning] (yes/skip/no)[no]: yes
Disabling POAP.......Disabling POAP
poap: Rolling back, please wait... (This may take 5-15 minutes)
---- System Admin Account Setup ----
Do you want to enforce secure password standard (yes/no) [y]: Enter
Enter the password for "admin": <password>
Confirm the password for "admin": <password>
Would you like to enter the basic configuration dialog (yes/no): yes
Create another login account (yes/no) [n]: Enter
Configure read-only SNMP community string (yes/no) [n]: Enter
Configure read-write SNMP community string (yes/no) [n]: Enter
Enter the switch name: <nexus-B-hostname>
Continue with Out-of-band (mgmt0) management configuration? (yes/no) [y]: Enter
Mgmt0 IPv4 address: <nexus-B-mgmt0-ip>
Mgmt0 IPv4 netmask: <nexus-B-mgmt0-netmask>
Configure the default gateway? (yes/no) [y]: Enter
IPv4 address of the default gateway: <nexus-B-mgmt0-gw>
Configure advanced IP options? (yes/no) [n]: Enter
Enable the telnet service? (yes/no) [n]: Enter
Enable the ssh service? (yes/no) [y]: Enter
Type of ssh key you would like to generate (dsa/rsa) [rsa]: Enter
Number of rsa key bits <1024-2048> [1024]: Enter
Configure the ntp server? (yes/no) [n]: Enter
Configure default interface layer (L3/L2) [L2]: Enter
Configure default switchport interface state (shut/noshut) [noshut]: shut
Enter basic FC configurations (yes/no) [n]: Enter
Configure CoPP system profile (strict/moderate/lenient/dense) [strict]: Enter
Would you like to edit the configuration? (yes/no) [n]: Enter
Step 2. Review the configuration summary before enabling the configuration.
Use this configuration and save it? (yes/no) [y]: Enter
FlexPod Cisco Nexus Switch Configuration
This section contains the procedures to configure the FlexPod Cisco Nexus switch.
Procedure 3. Enable Features on Cisco Nexus A and Cisco Nexus B
Step 1. Log in as admin.
Step 2. Run the following commands to enable additional features:
config t
feature udld
feature interface-vlan
feature lacp
feature vpc
feature lldp
Procedure 4. Set Global Configurations on Cisco Nexus A and Cisco Nexus B
Step 1. Run the following commands to set global configurations:
spanning-tree port type network default
spanning-tree port type edge bpduguard default
spanning-tree port type edge bpdufilter default
port-channel load-balance src-dst l4port
ntp server <global-ntp-server-ip> use-vrf management
ntp master 3
clock timezone <timezone> <hour-offset> <minute-offset>
clock summer-time <timezone> <start-week> <start-day> <start-month> <start-time> <end-week> <end-day> <end-month> <end-time> <offset-minutes>
ip route 0.0.0.0/0 <ib-mgmt-vlan-gateway>
copy run start
Tech tip: It is important to configure the local time so that logging time alignment and any backup schedules are correct. For more information on configuring the timezone and daylight savings time or summer time, see Cisco Nexus 9000 Series NX-OS Fundamentals Configuration Guide, Release 9.3(x). Sample clock commands for the United States Eastern timezone are:
clock timezone EST -5 0
clock summer-time EDT 2 Sunday March 02:00 1 Sunday November 02:00 60.
Procedure 5. Create VLANs on Cisco Nexus A and Cisco Nexus B
Step 1. From the global configuration mode, run the following commands:
vlan <ib-mgmt-vlan-id>
name In-Band-Mgmt
vlan <infrastructure-vlan-id>
name Infra-Mgmt
vlan <vmotion-vlan-id>
name vMotion
vlan <vm-traffic-vlan-id>
name VCC/VM-Network
vlan <infra-nfs-vlan-id>
name NFS-VLAN
vlan <client-vlan-id>
name Client-Network
exit
Procedure 6. Add DHCP Distribution Interface on Cisco Nexus A
Step 1. From the global configuration mode, run the following commands:
interface vlan<infrastructure-vlan-id>
ip address <switch-a-infra-ip>/<infrastructure-vlan-netmask-length>
hsrp version 2
hsrp <infrastructure-vlan-id>
preempt
priority 110
ip <infra-gw-ip>
ip dhcp relay address <infra-dhcp-ip>
no shutdown
exit
Procedure 7. Add DHCP Distribution Interface on Cisco Nexus B
Step 1. From the global configuration mode, run the following commands:
interface vlan<infrastructure-vlan-id>
ip address <switch-b-infra-ip>/<infrastructure-vlan-netmask-length>
hsrp version 2
hsrp <infrastructure-vlan-id>
preempt
priority 110
ip <infra-gw-ip>
ip dhcp relay address <infra-dhcp-ip>
no shutdown
exit
Procedure 8. Add NTP Distribution Interface on Cisco Nexus A
Step 1. From the global configuration mode, run the following commands:
interface vlan<ib-mgmt-vlan-id>
ip address <switch-a-ntp-ip>/<ib-mgmt-vlan-netmask-length>
no shutdown
exit
ntp peer <switch-b-ntp-ip> use-vrf default
Procedure 9. Add NTP Distribution Interface on Cisco Nexus B
Step 1. From the global configuration mode, run the following commands:
interface vlan<ib-mgmt-vlan-id>
ip address <switch-b-ntp-ip>/<ib-mgmt-vlan-netmask-length>
no shutdown
exit
ntp peer <switch-a-ntp-ip> use-vrf default
Procedure 10. Add Port Profiles on Cisco Nexus A and Cisco Nexus B
This version of the FlexPod solution uses port profiles for virtual port channel (vPC) connections to NetApp Storage, Cisco UCS, and the vPC peer link.
Step 1. From the global configuration mode, run the following commands:
port-profile type port-channel FP-ONTAP-Storage
switchport mode trunk
switchport trunk native vlan <native-vlan-id>
switchport trunk allowed vlan <ib-mgmt-vlan-id>, <infra-nfs-vlan-id>, <infrastructure-vlan-id>
spanning-tree port type edge trunk
mtu 9216
state enabled
port-profile type port-channel FP-UCS
switchport mode trunk
switchport trunk native vlan <native-vlan-id>
switchport trunk allowed vlan <ib-mgmt-vlan-id>, <infra-nfs-vlan-id>, <vmotion-vlan-id>, <vm-traffic-vlan-id>, <infrastructure-vlan-id>
spanning-tree port type edge trunk
mtu 9216
state enabled
port-profile type port-channel vPC-Peer-Link
switchport mode trunk
switchport trunk native vlan <native-vlan-id>
switchport trunk allowed vlan <ib-mgmt-vlan-id>, <infra-nfs-vlan-id>, <vmotion-vlan-id>, <vm-traffic-vlan-id>, <infrastructure-vlan-id>
spanning-tree port type network
state enabled
Procedure 11. Add Individual Port Descriptions for Troubleshooting and Enable UDLD for Cisco UCS Interfaces on Cisco Nexus A
Note: In this procedure and in the following sections, configure the AFF nodename <st-node> and Cisco UCS 6536 fabric interconnect clustername <ucs-clustername> interfaces as appropriate to your deployment.
Step 1. From the global configuration mode, run the following commands:
interface Eth1/49
description <ucs-clustername>-a:1/31
udld enable
interface Eth1/50
description <ucs-clustername>-b:1/32
udld enable
Step 2. For fibre optic connections to Cisco UCS systems (AOC or SFP-based), entering udld enable will result in a message stating that this command is not applicable to fiber ports. This message is expected. If you have fibre optic connections, do not enter the udld enable command.
interface Eth1/1
description <nexus-b-hostname>:1/1
interface Eth1/2
description <nexus-b-hostname>:1/2
interface Eth1/13
description <st-clustername>-01:e3a
interface Eth1/14
description <st-clustername>-02:e3b
interface Eth1/53
description <st-clustername>-01:e2b
interface Eth1/54
description <st-clustername>-02:e2b
exit
Procedure 12. Add Individual Port Descriptions for Troubleshooting and Enable UDLD for Cisco UCS Interfaces on Cisco Nexus B
Step 1. From the global configuration mode, run the following commands:
interface Eth1/49
description <ucs-clustername>-b:1/32
udld enable
interface Eth1/50
description <ucs-clustername>-a:1/31
udld enable
Step 2. For fibre optic connections to Cisco UCS systems (AOC or SFP-based), entering udld enable will result in a message stating that this command is not applicable to fiber ports. This message is expected.
interface Eth1/1
description <nexus-a-hostname>:1/1
interface Eth1/2
description <nexus-a-hostname>:1/2
exit
interface Eth1/13
description <st-clustername>-01:e3b
interface Eth1/14
description <st-clustername>-02:e3a
interface Eth1/53
description <st-clustername>-01:e4b
interface Eth1/54
description <st-clustername>-02:e4b
exit
Procedure 13. Create Port Channels on Cisco Nexus A and Cisco Nexus B
Step 1. From the global configuration mode, run the following commands:
interface Po10
description vPC peer-link
interface Eth1/1-2
channel-group 10 mode active
no shutdown
interface Po13
description <st-clustername>-01-cifs
interface Eth1/13
channel-group 13 mode active
no shutdown
interface Po14
description <st-clustername>-02-cifs
interface Eth1/14
channel-group 14 mode active
no shutdown
interface Po49
description <ucs-clustername>-a
interface Eth1/49
channel-group 49 mode active
no shutdown
interface Po50
description <ucs-clustername>-b
interface Eth1/50
channel-group 50 mode active
no shutdown
interface Po153
description <st-clustername>-a-nfs
interface Eth1/53
channel-group 53 mode active
no shutdown
interface Po54
description <st-clustername>-b-nfs
interface Eth1/54
channel-group 54 mode active
no shutdown
exit
copy run start
Procedure 14. Configure Port Channel Parameters on Cisco Nexus A and Cisco Nexus B
Step 1. From the global configuration mode, run the following commands:
interface Po10
inherit port-profile vPC-Peer-Link
interface Po13
inherit port-profile FP-ONTAP-Storage
interface Po14
inherit port-profile FP-ONTAP-Storage
interface Po149
inherit port-profile FP-UCS
interface Po150
inherit port-profile FP-UCS
interface Po53
inherit port-profile FP-ONTAP-Storage
interface Po54
inherit port-profile FP-ONTAP-Storage
exit
copy run start
Procedure 15. Configure Virtual Port Channels on Cisco Nexus A
Step 1. From the global configuration mode, run the following commands:
vpc domain <nexus-vpc-domain-id>
role priority 10
peer-keepalive destination <nexus-B-mgmt0-ip> source <nexus-A-mgmt0-ip>
peer-switch
peer-gateway
auto-recovery
delay restore 150
ip arp synchronize
interface Po10
vpc peer-link
interface Po13
vpc 13
interface Po14
vpc 14
interface Po49
vpc 49
interface Po50
vpc 50
interface Po53
vpc 53
interface Po54
vpc 54
exit
copy run start
Procedure 16. Configure Virtual Port Channels on Cisco Nexus B
Step 1. From the global configuration mode, run the following commands:
vpc domain <nexus-vpc-domain-id>
role priority 20
peer-keepalive destination <nexus-A-mgmt0-ip> source <nexus-B-mgmt0-ip>
peer-switch
peer-gateway
auto-recovery
delay restore 150
ip arp synchronize
interface Po10
vpc peer-link
interface Po13
vpc 13
interface Po14
vpc 14
interface Po49
vpc 49
interface Po50
vpc 50
interface Po53
vpc 53
interface Po54
vpc 54
exit
copy run start
Uplink into Existing Network Infrastructure
Depending on the available network infrastructure, several methods and features can be used to uplink the FlexPod environment. If an existing Cisco Nexus environment is present, we recommend using vPCs to uplink the Cisco Nexus switches included in the FlexPod environment into the infrastructure. The previously described procedures can be used to create an uplink vPC to the existing environment. Make sure to run copy run start to save the configuration on each switch after the configuration is completed.
The following commands can be used to check for correct switch configuration:
Note: Some of these commands need to run after further configuration of the FlexPod components are complete to see complete results.
show run
show vpc
show port-channel summary
show ntp peer-status
show cdp neighbors
show lldp neighbors
show run int
show int
show udld neighbors
show int status
Fabric Switch Configuration
This section provides a detailed procedure for configuring the Cisco MDS 9132T switches for use in a FlexPod environment. The Cisco Nexus MDS 9132T used for SAN switching in this solution.
IMPORTANT! Follow these steps precisely because failure to do so could result in an improper configuration.
Physical Connectivity
Follow the physical connectivity guidelines for FlexPod as explained in section Solution Cabling.
Cisco MDS 9132T 32-Gb FC Switch Configuration
Figure 28 illustrates the cable connectivity between the Cisco MDS 9132T 32-Gb switch and the Cisco 6536 Fabric Interconnects and NetApp AFF A50 storage array.
Procedure 1. Configure features and name for MDS Switch A and MDS Switch B
Follow these steps on both MDS switches.
Step 1. Log in as admin user into MDS Switch A:
config terminal
feature npiv
feature nxapi
feature fport-channel-trunk
switchname L151K5-MDS-C9132T-A
copy running-config startup-config
Step 2. Log in as admin user into MDS Switch B. Repeat step 1 on MDS Switch B.
Procedure 2. Configure VSANs for MDS Switch A and MDS Switch B
Step 1. Log in as admin user into MDS Switch A. Create VSAN 100 for Storage Traffic:
config terminal
VSAN database
vsan 101
exit
zone smart-zoning enable vsan 101
interface port-channel135
switchport mode F
switchport trunk allowed vsan 101
switchport speed 32000
switchport rate-mode dedicated
switchport trunk mode auto
vsan database
vsan 101 interface fc 1/9-12
exit
interface fc 1/9-12
switchport trunk allowed vsan 101
switchport trunk mode off
port-license acquire
no shutdown
interface fc1/13-16
switchport trunk mode auto
port-license acquire
channel-group 135 force
no shutdown
exit
copy running-config startup-configg
Step 2. Log in as admin user into MDS Switch B. Create VSAN 101 for Storage Traffic:
config terminal
vsan database
vsan 102
exit
zone smart-zoning enable vsan 102
interface port-channel135
switchport mode F
switchport trunk allowed vsan 102
switchport speed auto max 32000
switchport rate-mode dedicated
switchport trunk mode auto
vsan database
vsan 102 interface fc 1/9-12
exit
interface fc 1/9-12
switchport trunk allowed vsan 102
switchport trunk mode off
port-license acquire
no shutdown
interface fc1/13-16
switchport trunk mode auto
port-license acquire
channel-group 135 force
no shutdown
exit
copy running-config startup-config
Procedure 3. Create and Configure Fiber Channel Zoning
This procedure sets up the Fibre Channel connections between the Cisco MDS 9132T 32-Gb switches, the Cisco UCS Fabric Interconnects, and the NetApp AFF A50 array.
Note: Before you configure the zoning details, decide how many paths are needed for each LUN and extract the WWPN numbers for each of the HBAs from each server. We used 2 HBAs for each Server. One of the HBAs (HBA-A) is connected to MDS Switch-A and other HBAs (HBA-B) is connected to MDS Switch-B.
Step 1. Log into the Cisco Intersight portal as a user with account administrator role.
Step 2. From the Service Selector drop-down list, choose Infrastructure Service.
Step 3. Navigate to Configure > Pools. Filter WWPN type pools.
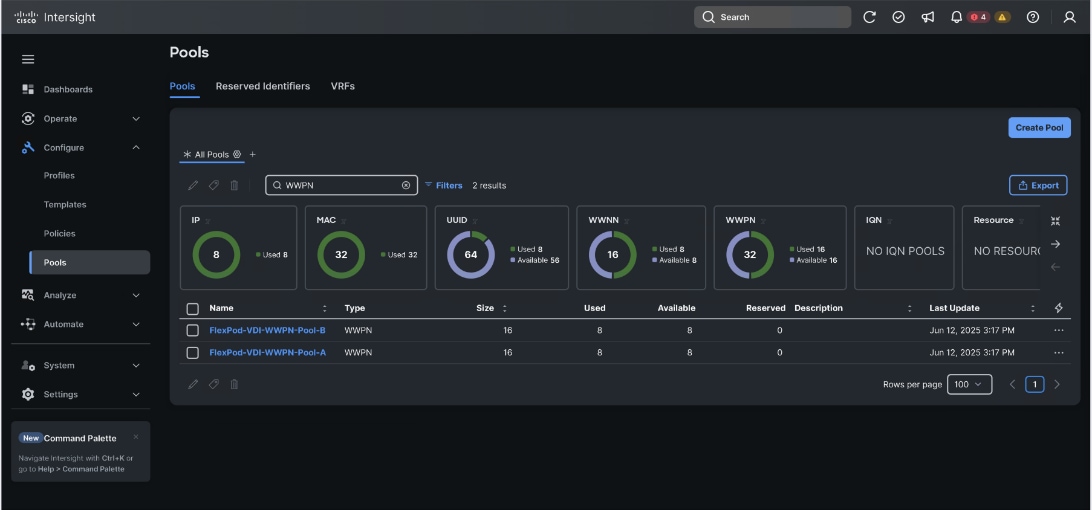
Step 4. Select Usage tab and collect the WWPNs and profiles to which they are assigned.
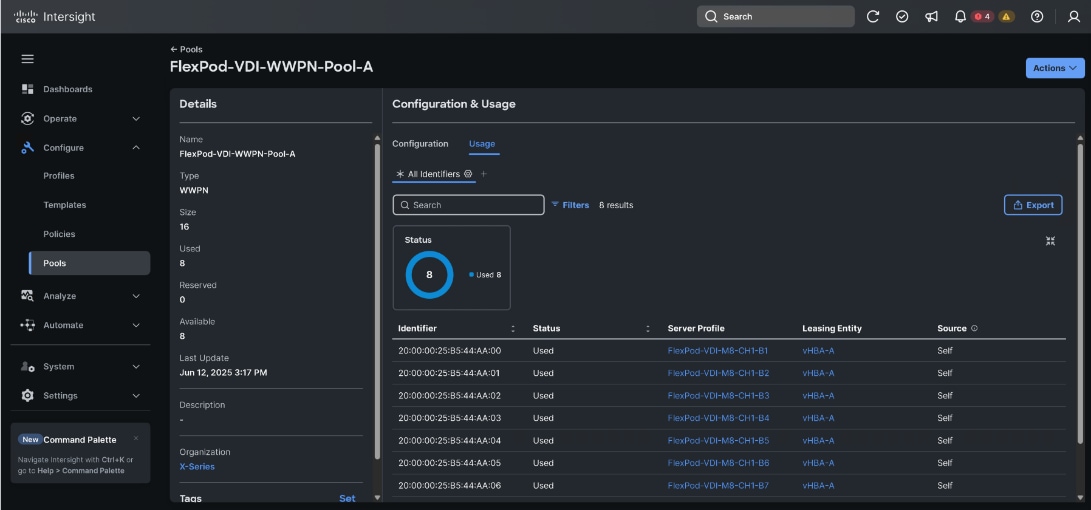
Step 5. Connect to the ONTAP System Manager and go to the Network Overview tab and extract the WWPN of FC Ports connected to the Cisco MDS Switches from Network interfaces section.
Note: We connected 8 FC ports from AFF A50 to Cisco MDS Switches. FC ports Node1 1a, Node1 1b, Node2 1c, Node2 1d are connected to MDS Switch-A and similarly FC ports Node2 1a, Node2 1b, Node1 1c, Node1 1d are connected to MDS Switch-B.
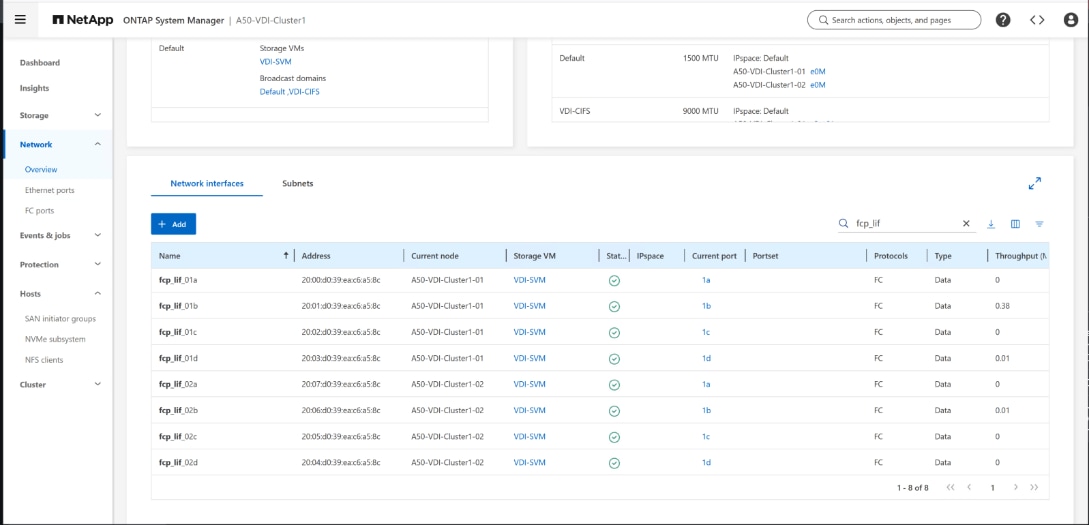
Procedure 4. Create Device Aliases for Fiber Channel Zoning for SAN Boot Paths and Datapaths on Cisco MDS Switch A
Step 1. Log in as admin user and run the following commands from the global configuration mode:
configure terminal
device-alias mode enhanced
device-alias database
device-alias name A50-VDI-Cluster1-1a pwwn 20:00:d0:39:ea:c6:a5:8c
device-alias name A50-VDI-Cluster1-1b pwwn 20:01:d0:39:ea:c6:a5:8c
device-alias name A50-VDI-Cluster2-1d pwwn 20:05:d0:39:ea:c6:a5:8c
device-alias name A50-VDI-Cluster2-1c pwwn 20:04:d0:39:ea:c6:a5:8c
device-alias name Host-CH1-B1-HBA-A pwwn 20:00:00:25:B5:44:AA:00
device-alias name Host-CH1-B2-HBA-A pwwn 20:00:00:25:B5:44:AA:01
device-alias name Host-CH1-B3-HBA-A pwwn 20:00:00:25:B5:44:AA:02
device-alias name Host-CH1-B4-HBA-A pwwn 20:00:00:25:B5:44:AA:03
device-alias name Host-CH1-B5-HBA-A pwwn 20:00:00:25:B5:44:AA:04
device-alias name Host-CH1-B6-HBA-A pwwn 20:00:00:25:B5:44:AA:05
device-alias name Host-CH1-B7-HBA-A pwwn 20:00:00:25:B5:44:AA:06
device-alias name Host-CH1-B8-HBA-A pwwn 20:00:00:25:B5:44:AA:07
exit
device-alias commit
Step 1. Log in as admin user and run the following commands from the global configuration mode:
configure terminal
device-alias mode enhanced
device-alias database
device-alias name A50-VDI-Cluster2-1a pwwn 20:07:d0:39:ea:c6:a5:8c
device-alias name A50-VDI-Cluster2-1b pwwn 20:06:d0:39:ea:c6:a5:8c
device-alias name A50-VDI-Cluster1-1c pwwn 20:02:d0:39:ea:c6:a5:8c
device-alias name A50-VDI-Cluster1-1d pwwn 20:03:d0:39:ea:c6:a5:8c
device-alias name Host-CH1-B1-HBA-B pwwn 20:00:00:25:B5:44:BB:00
device-alias name Host-CH1-B2-HBA-B pwwn 20:00:00:25:B5:44:BB:01
device-alias name Host-CH1-B3-HBA-B pwwn 20:00:00:25:B5:44:BB:02
device-alias name Host-CH1-B4-HBA-B pwwn 20:00:00:25:B5:44:BB:03
device-alias name Host-CH1-B5-HBA-B pwwn 20:00:00:25:B5:44:BB:04
device-alias name Host-CH1-B6-HBA-B pwwn 20:00:00:25:B5:44:BB:05
device-alias name Host-CH1-B7-HBA-B pwwn 20:00:00:25:B5:44:BB:06
device-alias name Host-CH1-B8-HBA-B pwwn 20:00:00:25:B5:44:BB:07
exit
device-alias commit
Procedure 6. Create Fiber Channel Zoning for Cisco MDS Switch A for each Service Profile
Step 1. Log in as admin user and create the zone:
configure terminal
zone name FlexPod-Fabric-A vsan 101
member device-alias A50-VDI-Cluster1-1a target
member device-alias A50-VDI-Cluster1-1b target
member device-alias A50-VDI-Cluster2-1d target
member device-alias A50-VDI-Cluster2-1c target
member device-alias Host-CH1-B1-HBA-A init
member device-alias Host-CH1-B2-HBA-A init
member device-alias Host-CH1-B3-HBA-A init
member device-alias Host-CH1-B4-HBA-A init
member device-alias Host-CH1-B5-HBA-A init
member device-alias Host-CH1-B6-HBA-A init
member device-alias Host-CH1-B7-HBA-A init
member device-alias Host-CH1-B8-HBA-A init
Step 2. After the zone for the Cisco UCS server profile has been created, create the zone set and add the created zones as members:
configure terminal
zoneset name FlexPod-VDI-Fabric-A vsan 101
member FlexPod-Fabric-A
Step 3. Activate the zone set by running following commands:
zoneset activate name FlexPod-VDI-Fabric-A vsan 101
exit
copy running-config startup-config
Procedure 7. Create Fiber Channel Zoning for Cisco MDS Switch B for each Service Profile
Step 1. Log in as admin user and create the zone as shown below:
configure terminal
zone name FlexPod-Fabric-B vsan 102
member device-alias A50-VDI-Cluster2-1a target
member device-alias A50-VDI-Cluster2-1b target
member device-alias A50-VDI-Cluster1-1d target
member device-alias A50-VDI-Cluster1-1c target
member device-alias Host-CH1-B1-HBA-B init
member device-alias Host-CH1-B2-HBA-B init
member device-alias Host-CH1-B3-HBA-B init
member device-alias Host-CH1-B4-HBA-B init
member device-alias Host-CH1-B5-HBA-B init
member device-alias Host-CH1-B6-HBA-B init
member device-alias Host-CH1-B7-HBA-B init
member device-alias Host-CH1-B8-HBA-B init
Step 2. After the zone for the Cisco UCS server profile has been created, create the zone set and add the necessary members:
zoneset name FlexPod-VDI-Fabric-B vsan 102
member FlexPod-Fabric-B
Step 3. Activate the zone set by running following commands:
zoneset activate name FlexPod-VDI-Fabric-B vsan 102
exit
copy running-config startup-config
This chapter contains the following:
To confirm that the hardware and software components that you would like to use are supported with the version of ONTAP that you plan to install, follow these steps at the NetApp Support site.
Access the HWU application to view the System Configuration guides. Click the Products tab to select the Platforms menu to view the compatibility between different versions of the ONTAP software and the NetApp storage appliances with your desired specifications.
Alternatively, to compare components by storage appliance, click Utilities and select Compare Storage Systems.
Follow the physical installation procedures for the controllers found here: https://docs.netapp.com/us-en/ontap-systems/index.html.
NetApp storage systems support a wide variety of disk shelves and disk drives. The complete list of disk shelves that are supported by the AFF A50 and AFF A800 is available at the NetApp Support site.
When using SAS disk shelves with NetApp storage controllers, go to: https://docs.netapp.com/us-en/ontap-systems/sas3/install-new-system.html for proper cabling guidelines.
When using NVMe drive shelves with NetApp storage controllers, go to: https://docs.netapp.com/us-en/ontap-systems/ns224/hot-add-shelf.html for installation and servicing guidelines.
NetApp ONTAP 9.17.1 P4
This section contains the information needed to configure NetApp ONTAP 9.17.1 P4.
Complete Configuration Worksheet
Before running the setup script, complete the Cluster setup worksheet in the ONTAP 9 Documentation Center. You must have access to the NetApp Support site to open the cluster setup worksheet.
Before running the setup script, review the configuration worksheets in the Software setup section of the ONTAP 9 Documentation Center to learn about configuring ONTAP. Table 12 lists the information needed to configure two ONTAP nodes. Customize the cluster-detail values with the information applicable to your deployment.
Table 12. ONTAP Software Installation Prerequisites
| Cluster Detail |
Cluster Detail Value |
| Cluster node 01 IP address |
<node01-mgmt-ip> |
| Cluster node 01 netmask |
<node01-mgmt-mask> |
| Cluster node 01 gateway |
<node01-mgmt-gateway> |
| Cluster node 02 IP address |
<node02-mgmt-ip> |
| Cluster node 02 netmask |
<node02-mgmt-mask> |
| Cluster node 02 gateway |
<node02-mgmt-gateway> |
| ONTAP 9.17.1 P4 URL (http server hosting ONTAP software) |
<url-boot-software> |
Procedure 1. Configure Node 01
Step 1. Connect to the storage system console port. You should see a Loader-A prompt. However, if the storage system is in a reboot loop, press Ctrl-C to exit the autoboot loop when the following message displays:
Starting AUTOBOOT press Ctrl-C to abort…
Step 2. Allow the system to boot up.
autoboot
Step 3. Press Ctrl-C when prompted.
Note: If NetApp ONTAP 9.17.1 P4 is not the version of software being booted, continue with the following steps to install new software. If NetApp ONTAP 9.17.1 P4 is the version being booted, select option 8 and y to reboot the node. Continue with section Set Up Node.
Step 4. To install new software, select option 7 from the menu.
Step 5. Enter y to continue the installation.
Step 6. Select e0M for the network port for the download.
Step 7. Enter n to skip the reboot.
Step 8. Select option 7 from the menu: Install new software first
Step 9. Enter y to continue the installation.
Step 10. Enter the IP address, netmask, and default gateway for e0M.
Enter the IP address for port e0M: <node01-mgmt-ip>
Enter the netmask for port e0M: <node01-mgmt-mask>
Enter the IP address of the default gateway: <node01-mgmt-gateway>
Step 11. Enter the URL where the software can be found.
Step 12. The e0M interface should be connected to the management network and the web server must be reachable (using ping) from node 01.
<url-boot-software>
Step 13. Press Enter for the user name, indicating no user name.
Step 14. Enter y to set the newly installed software as the default to be used for subsequent reboots.
Step 15. Enter yes to reboot the node.
Note: When installing new software, the system might perform firmware upgrades to the BIOS and adapter cards, causing reboots and possible stops at the Loader-A prompt. If these actions occur, the system might deviate from this procedure.
Note: During the ONTAP installation, a prompt to reboot the node requests a Y/N response. The prompt requires the entire Yes or No response to reboot the node and continue the installation.
Step 16. Press Ctrl-C when the following message displays:
Press Ctrl-C for Boot Menu
Step 17. Select option 4 for Clean Configuration and Initialize All Disks.
Step 18. Enter y to zero disks, reset config, and install a new file system.
Step 19. Enter yes to erase all the data on the disks.
Note: When the initialization and creation of the root aggregate is complete, the storage system reboots. You can continue with the configuration of node 02 while the initialization and creation of the root aggregate for node 01 is in progress. For more information about root aggregate and disk partitioning, refer to the ONTAP documentation on root-data partitioning: https://docs.netapp.com/us-en/ontap/concepts/root-data-partitioning-concept.html.
Procedure 2. Configure Node 02
Step 1. Connect to the storage system console port. You should see a Loader-B prompt. However, if the storage system is in a reboot loop, press Ctrl-C to exit the autoboot loop when the following message displays: Starting
AUTOBOOT press Ctrl-C to abort…
Step 2. Allow the system to boot up.
autoboot
Step 3. Press Ctrl-C when prompted.
Note: If NetApp ONTAP 9.17.1P4 is not the version of software being booted, continue with the following steps to install new software. If NetApp ONTAP 9.17.1P4 is the version being booted, select option 8 and y to reboot the node, then continue with section Set Up Node.
Step 4. To install new software, select option 7.
Step 5. Enter y to continue the installation.
Step 6. Select e0M for the network port you want to use for the download.
Step 7. Enter n to skip the reboot.
Step 8. Select option 7: Install new software first
Step 9. Enter y to continue the installation
Step 10. Enter the IP address, netmask, and default gateway for e0M.
Enter the IP address for port e0M: <node02-mgmt-ip>
Enter the netmask for port e0M: <node02-mgmt-mask>
Enter the IP address of the default gateway: <node02-mgmt-gateway>
Step 11. Enter the URL where the software can be found.
Step 12. The web server must be reachable (ping) from node 02.
<url-boot-software>
Step 13. Press Enter for the username, indicating no user name.
Step 14. Enter y to set the newly installed software as the default to be used for subsequent reboots.
Step 15. Enter yes to reboot the node.
Note: When installing new software, the system might perform firmware upgrades to the BIOS and adapter cards, causing reboots and possible stops at the Loader-B prompt. If these actions occur, the system might deviate from this procedure.
Note: During the ONTAP installation a prompt to reboot the node requests a Y/N response. The prompt requires the entire Yes or No response to reboot the node and continue the installation.
Step 16. Press Ctrl-C when you see this message:
Press Ctrl-C for Boot Menu
Step 17. Select option 4 for Clean Configuration and Initialize All Disks.
Step 18. Enter y to zero disks, reset config, and install a new file system.
Step 19. Enter yes to erase all the data on the disks.
Step 1. From a console port program attached to the storage controller A (node 01) console port, run the node setup script. This script appears when ONTAP 9.17.1P4 boots on the node for the first time.
Step 2. Follow the prompts to set up node 01.
Welcome to node setup.
You can enter the following commands at any time:
"help" or "?" - if you want to have a question clarified,
"back" - if you want to change previously answered questions, and
"exit" or "quit" - if you want to quit the setup wizard.
Any changes you made before quitting will be saved.
You can return to cluster setup at any time by typing “cluster setup.”
To accept a default or omit a question, do not enter a value.
This system will send event messages and weekly reports to NetApp Technical Support.
To disable this feature, enter "autosupport modify -support disable" within 24 hours.
Enabling AutoSupport can significantly speed problem determination and resolution should a problem occur on your system.
For further information on AutoSupport, see: http://support.netapp.com/autosupport/
Type yes to confirm and continue {yes}: yes
Enter the node management interface port [e0M]: Enter
Enter the node management interface IP address: <node01-mgmt-ip>
Enter the node management interface netmask: <node01-mgmt-mask>
Enter the node management interface default gateway: <node01-mgmt-gateway>
A node management interface on port e0M with IP address <node01-mgmt-ip> has been created
Use your web browser to complete cluster setup by accesing https://<node01-mgmt-ip>. Otherwise press Enter to complete cluster setup using the command line interface.
Step 3. To complete cluster setup, open a web browser and navigate to https://<node01-mgmt-ip>.
Table 13. Cluster Create in ONTAP Prerequisites
| Cluster Detail |
Cluster Detail Value |
| Cluster name |
<clustername> |
| Cluster Admin SVM |
<cluster-adm-svm> |
| Infrastructure Data SVM |
<infra-data-svm> |
| ONTAP One |
<cluster-base-license-key> |
| Cluster management IP address |
<clustermgmt-ip> |
| Cluster management netmask |
<clustermgmt-mask> |
| Cluster management gateway |
<clustermgmt-gateway> |
| Cluster node 01 IP address |
<node01-mgmt-ip> |
| Cluster node 01 netmask |
<node01-mgmt-mask> |
| Cluster node 01 gateway |
<node01-mgmt-gateway> |
| Cluster node 02 IP address |
<node02-mgmt-ip> |
| Cluster node 02 netmask |
<node02-mgmt-mask> |
| Cluster node 02 gateway |
<node02-mgmt-gateway> |
| Node 01 service processor IP address |
<node01-sp-ip> |
| Node 01 service processor network mask |
<node01-sp-mask> |
| Node 01 service processor gateway |
<node01-sp-gateway> |
| Node 02 service processor IP address |
<node02-sp-ip> |
| Node 02 service processor network mask |
<node02-sp-mask> |
| Node 02 service processor gateway |
<node02-sp-gateway> |
| Node 01 node name |
<st-node01> |
| Node 02 node name |
<st-node02> |
| DNS domain name |
<dns-domain-name> |
| DNS server IP address |
<dns-ip> |
| NTP server A IP address |
<switch-a-ntp-ip> |
| NTP server B IP address |
<switch-b-ntp-ip> |
| SNMPv3 User |
<snmp-v3-usr> |
| SNMPv3 Authentication Protocol |
<snmp-v3-auth-proto> |
| SNMPv3 Privacy Protocol |
<snmpv3-priv-proto> |
Note: Cluster setup can also be performed using the CLI. This document describes the cluster setup using the NetApp ONTAP System Manager guided setup.
Step 4. Complete the required information on the Initialize Storage System screen:
a. In the Cluster screen, enter the cluster name and administrator password.
b. Complete the Networking information for the cluster and each node.
Tech tip: The nodes should be discovered automatically; if they are not, Refresh the browser page. By default, the cluster interfaces are created on all the new factory shipping storage controllers.
If all the nodes are not discovered, then configure the cluster using the command line.
The node management interface can be on the same subnet as the cluster management interface, or it can be on a different subnet. In this document, we assume that it is on the same subnet.
c. Click Submit.
Step 5. A few minutes will pass while the cluster is configured. When prompted, login to ONTAP System Manager to continue the cluster configuration.
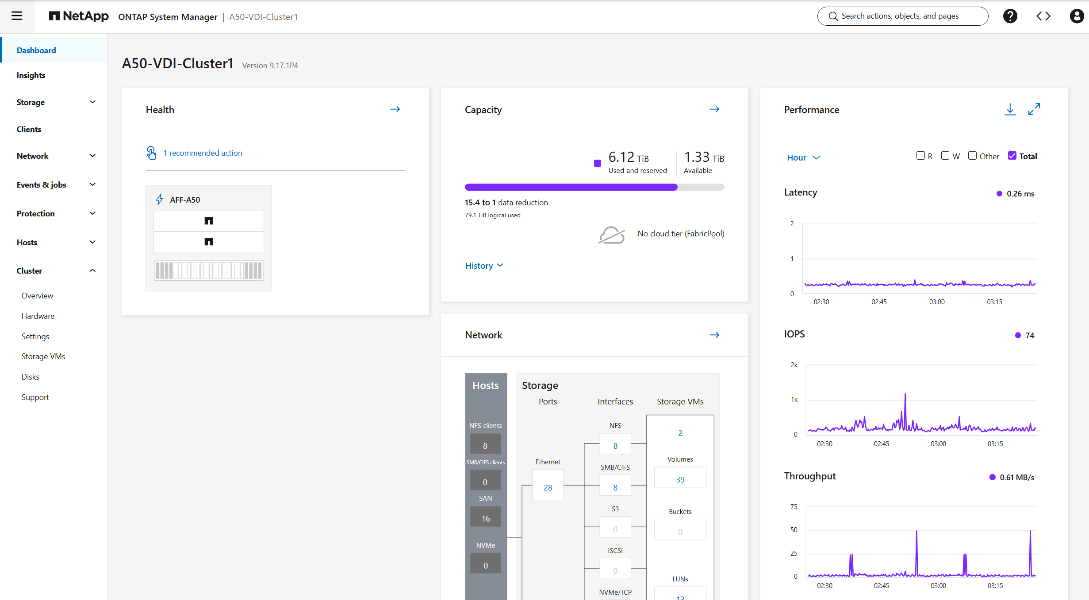
Step 6. From the Dashboard click the Cluster menu and click Overview.
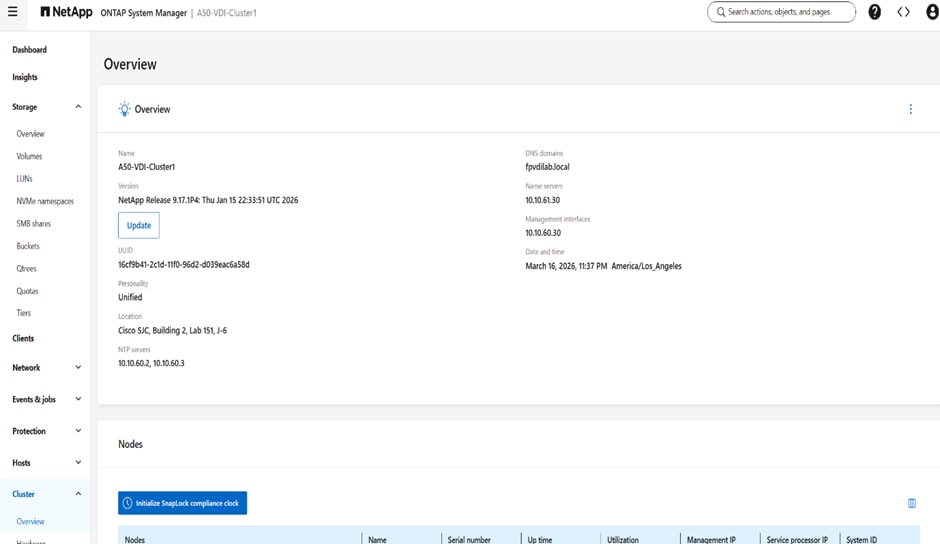
Step 7. Click the More button in the Overview pane and click Edit.
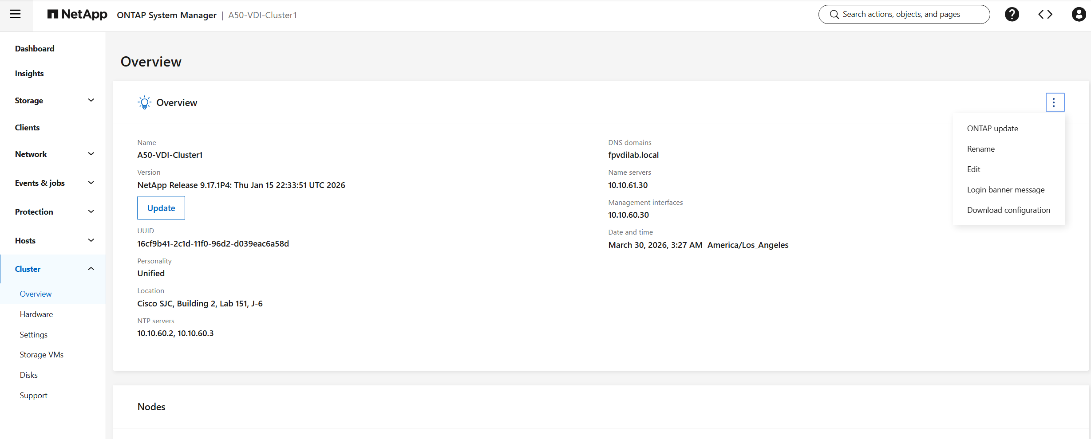
Step 8. Add additional cluster configuration details and click Save to make the changes persistent:
- Cluster location
- DNS domain name
- DNS server IP addresses
- DNS server IP addresses can be added individually or with a comma separated list on a single line.
Step 9. Click Save to make the changes persistent.
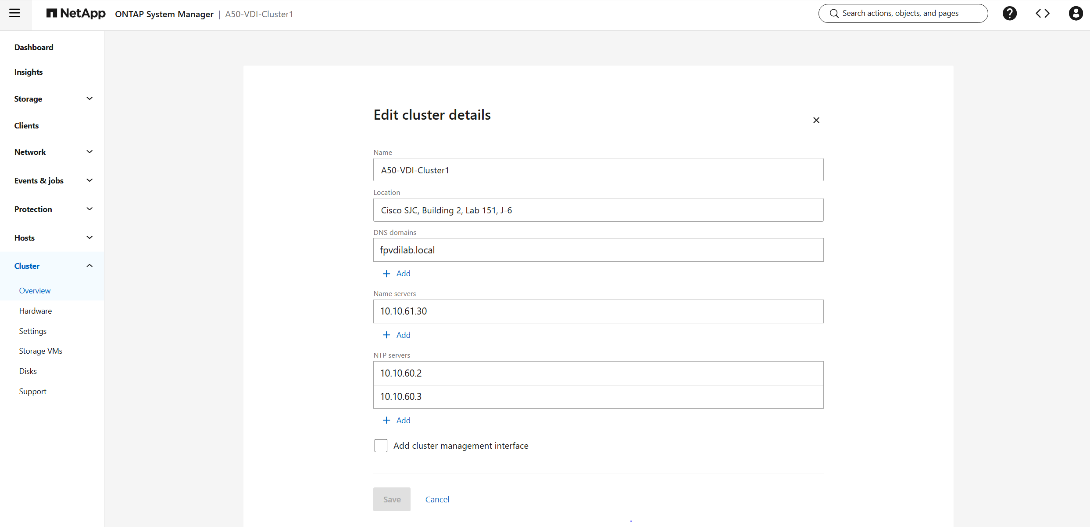
Step 10. Select the Settings menu under the Cluster menu.
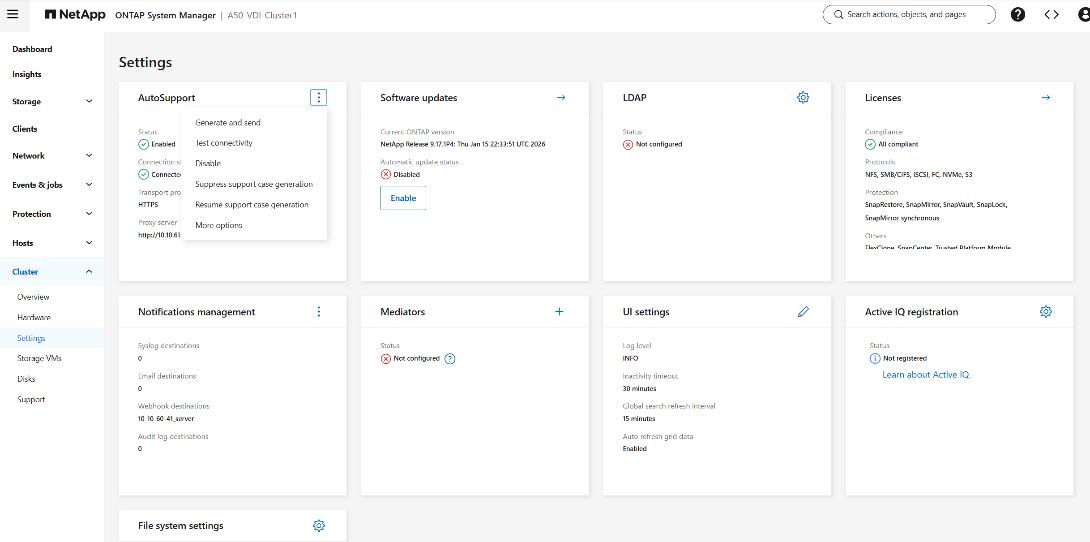
Step 11. If AutoSupport was not configured during the initial setup, click the ellipsis in the AutoSupport tile and select More options.
Step 12. To enable AutoSupport click the slider.
Step 13. Click Edit to change the transport protocol, add a proxy server address and a mail host as needed.
Step 14. Click Save to enable the changes.
Step 15. In the Email tile, click Edit and enter the desired email information:
- Email send from address
- Email recipient addresses
- Recipient Category
Step 16. Click Save when complete.
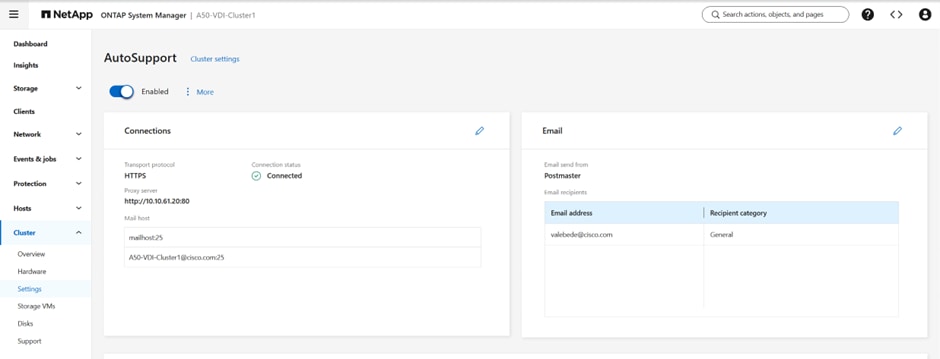
Step 17. Select CLUSTER > Settings to return to the cluster settings page.
Step 18. Locate the Licenses tile on the right and click the arrow.
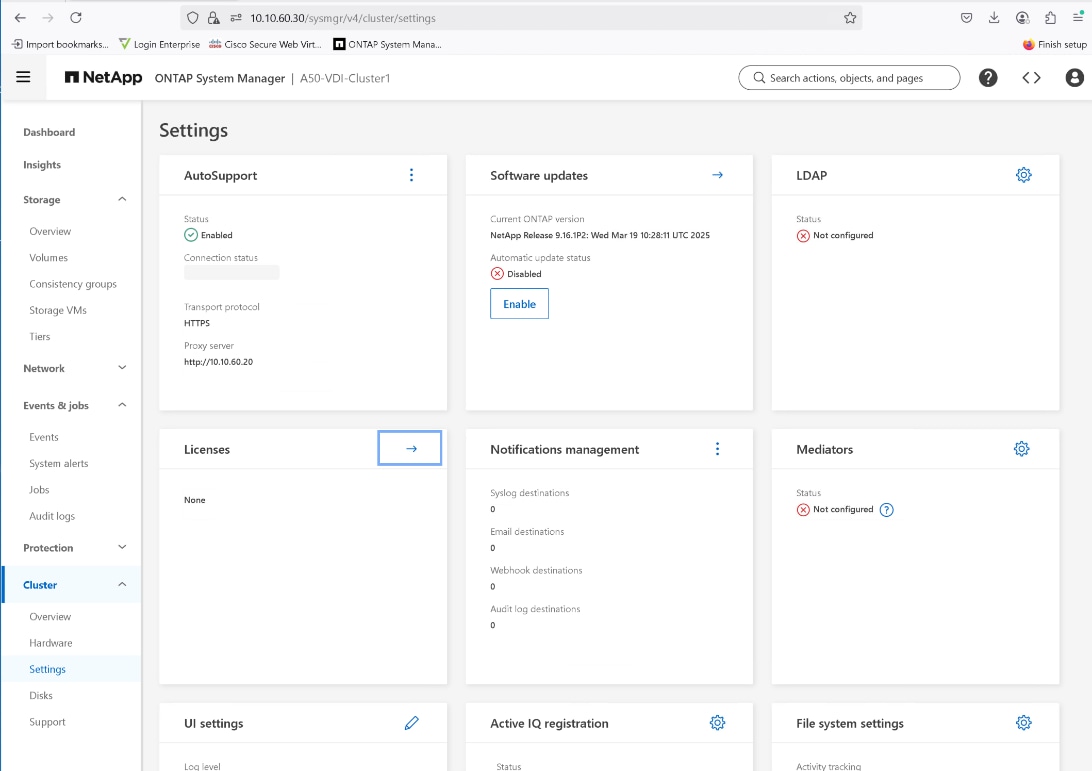
Step 19. Add the desired licenses to the cluster by clicking Add and browse to the license files.
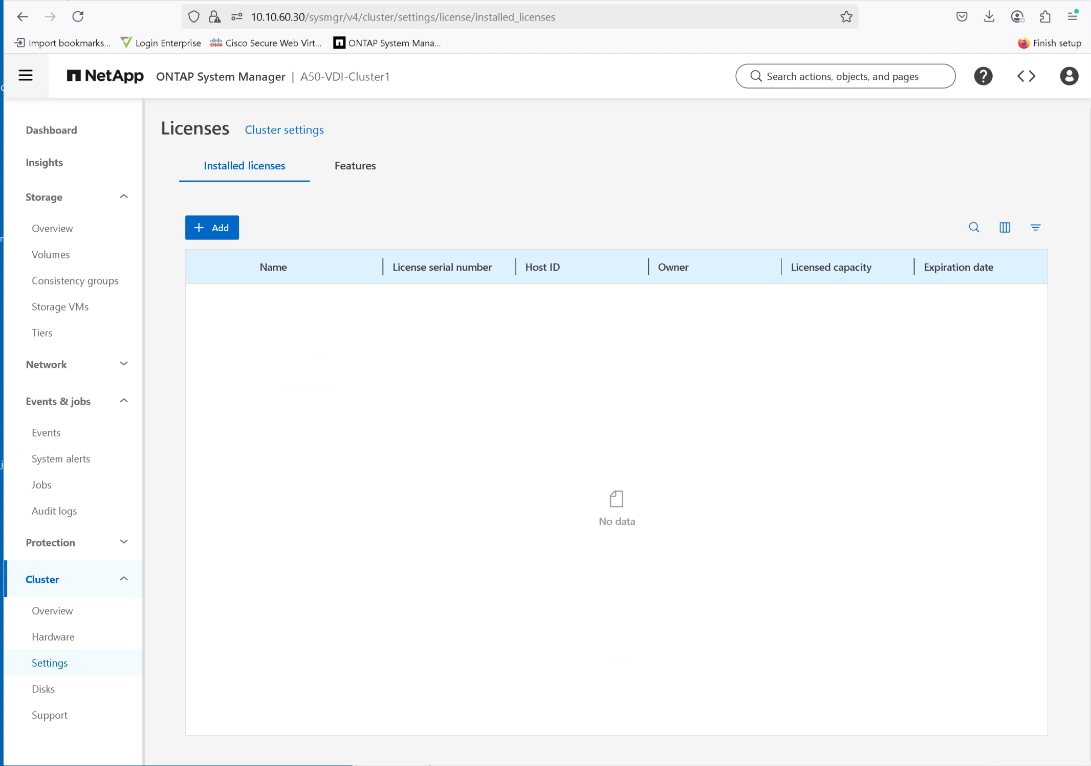
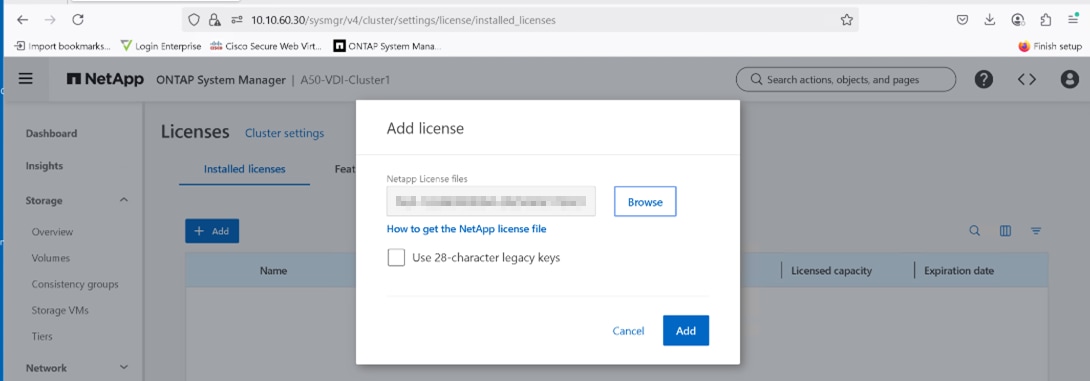
Note: NetApp ONTAP 9.10.1 and later for FAS/AFF storage systems uses a new file-based licensing solution to enable per-node NetApp ONTAP features. The new license key format is referred to as a NetApp License File, or NLF. For more information, go to: NetApp ONTAP 9.10.1 and later Licensing Overview - NetApp Knowledge Base
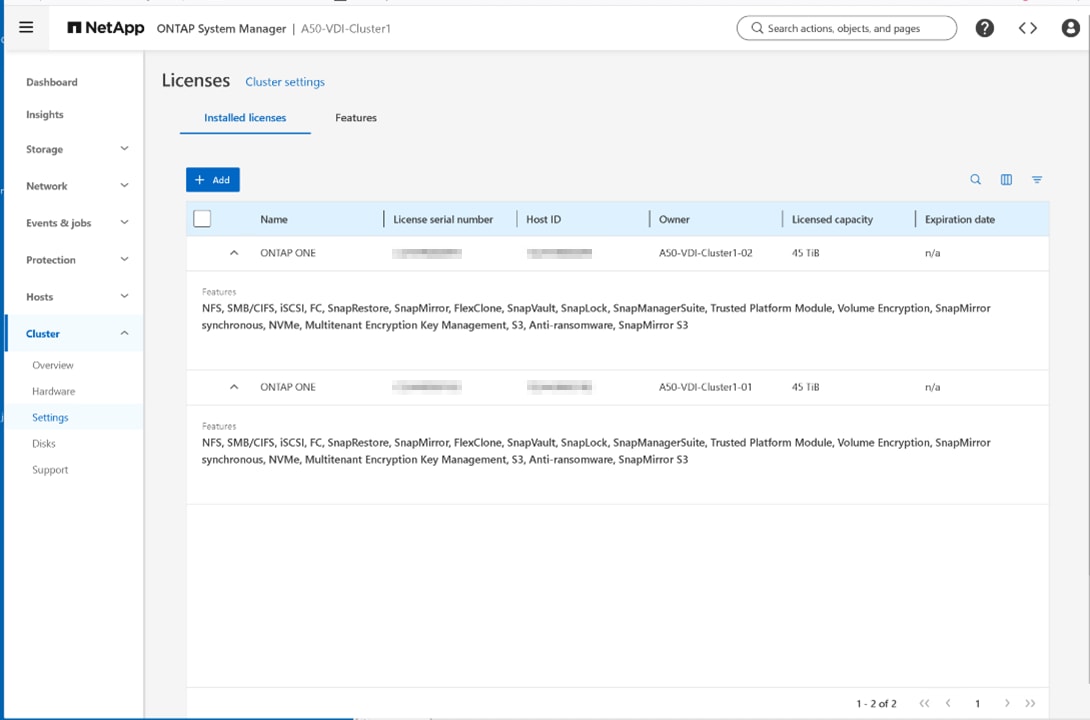
Step 20. Configure storage aggregates by selecting the Storage menu and selecting Tiers.
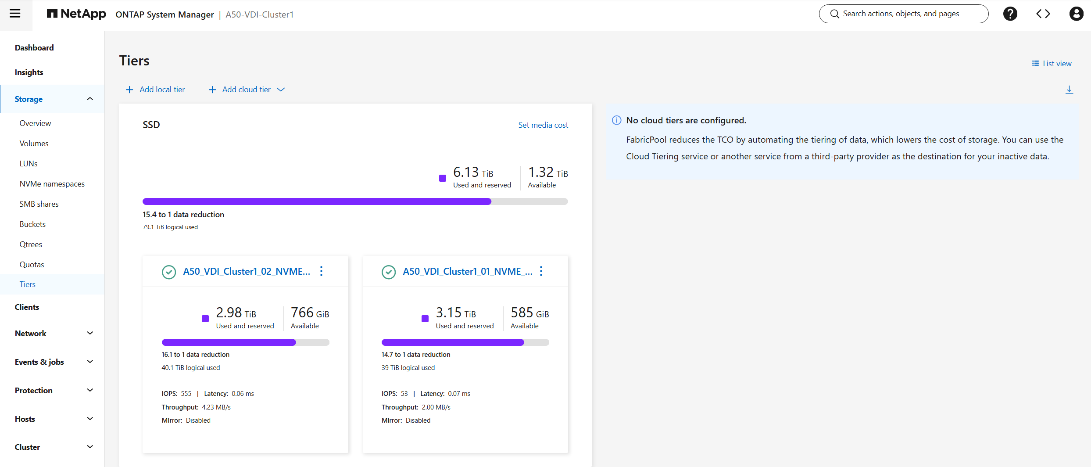
Step 21. Click Add Local Tier and allow ONTAP System Manager to recommend a storage aggregate configuration.
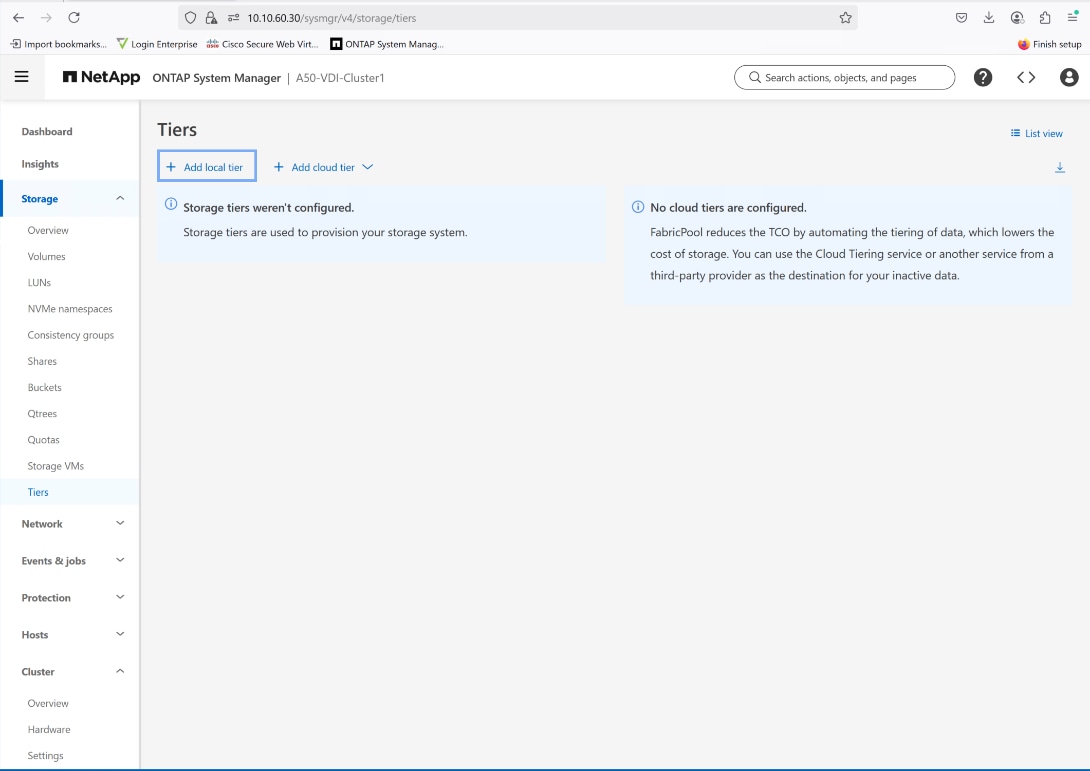
Step 22. ONTAP will use best practices to recommend an aggregate layout. Click the Recommended details link to view the aggregate information.
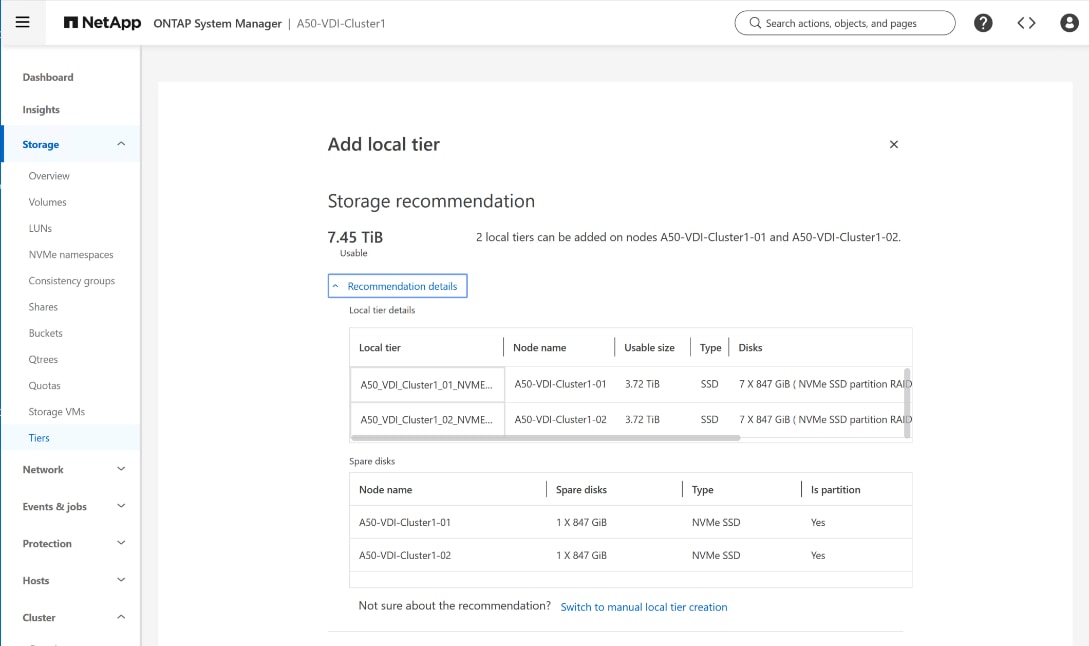
Step 23. Optionally, enable NetApp Aggregate Encryption (NAE) by checking the box for Configure Onboard Key Manager for encryption. Enter and confirm the passphrase and save it in a secure location for future use
Step 24. Click Save to make the configuration persistent.
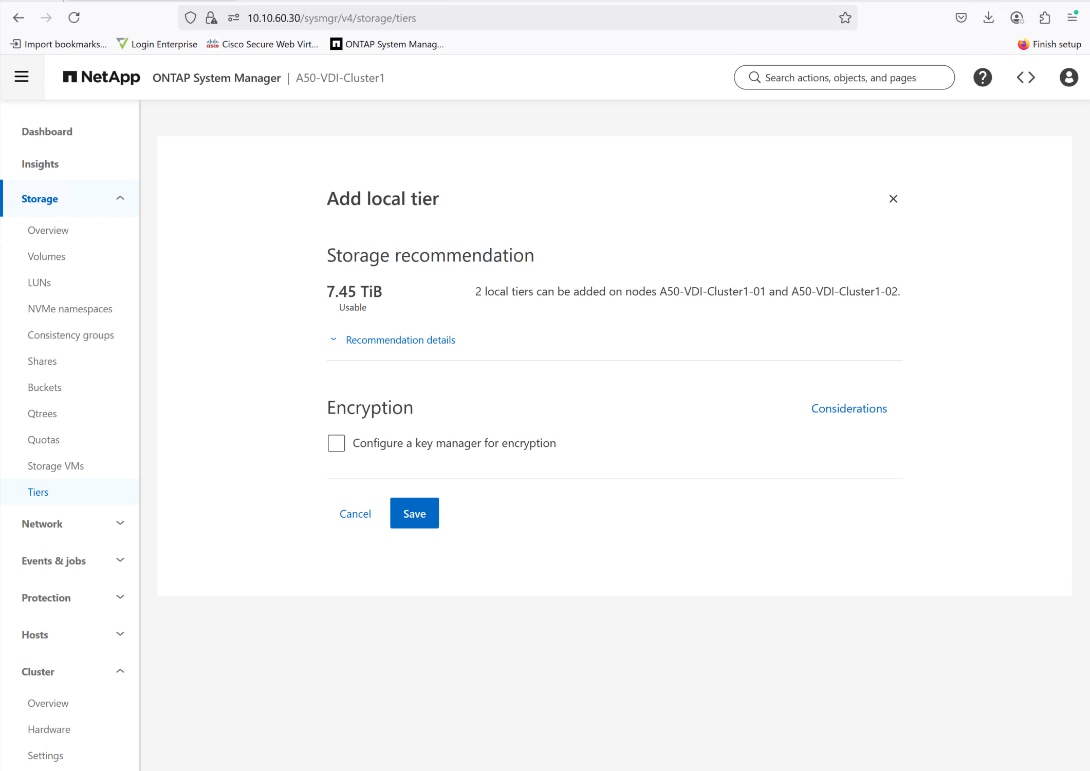
The aggregates are created successfully as shown below:
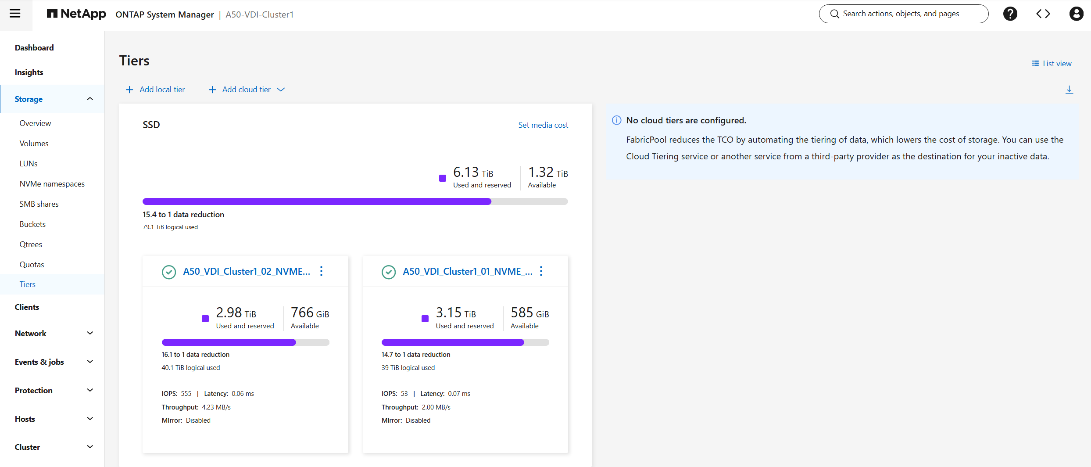
Note: Aggregate encryption may not be supported for all deployments. Review the NetApp Encryption Power Guide and the Security Hardening Guide for NetApp ONTAP 9 (TR-4569) to help determine if aggregate encryption is right for your environment.
Procedure 4. Log into the Cluster
Step 1. Open an SSH connection to either the cluster IP or the host name.
Step 2. Log into the admin user with the password you provided earlier.
Procedure 5. Verify Storage Failover
Step 1. Verify the status of the storage failover:
A50-VDI-Cluster1::> storage failover show
Takeover
Node Partner Possible State Description
-------------- -------------- -------- -------------------------------------
A50-VDI-Cluster1-01
A50-VDI- true Connected to A50-VDI-Cluster1-02
Cluster1-02
A50-VDI-Cluster1-02
A50-VDI- true Connected to A50-VDI-Cluster1-01
Cluster1-01
2 entries were displayed
Note: Both <st-node01> and <st-node02> must be capable of performing a takeover. Continue with Step 2 if the nodes can perform a takeover.
Step 2. Enable failover on one of the two nodes if it was not completed during the installation:
storage failover modify -node <st-node01> -enabled true
Note: Enabling failover on one node enables it for both nodes.
Step 3. Verify the HA status for a two-node cluster:
Note: This step is not applicable for clusters with more than two nodes.
A50-VDI-Cluster1::> cluster ha show
High-Availability Configured: true
Note: If HA is not configured use the following commands. Only enable HA mode for two-node clusters. Do not run this command for clusters with more than two nodes because it causes problems with failover.
cluster ha modify -configured true
Do you want to continue? {y|n}: y
Step 4. Verify that hardware assist is correctly configured:
A50-VDI-Cluster1::> storage failover hwassist show
Node
-----------------
A50-VDI-Cluster1-01
Partner: A50-VDI-Cluster1-02
Hwassist Enabled: true
Hwassist IP: 10.10.60.31
Hwassist Port: 4444
Monitor Status: active
Inactive Reason: -
Corrective Action: -
Keep-Alive Status: healthy
A50-VDI-Cluster1-02
Partner: A50-VDI-Cluster1-01
Hwassist Enabled: true
Hwassist IP: 10.10.60.32
Hwassist Port: 4444
Monitor Status: active
Inactive Reason: -
Corrective Action: -
Keep-Alive Status: healthy
2 entries were displayed.
Procedure 6. Set Auto-Revert on Cluster Management Interface
Step 1. Set the auto-revert parameter on the cluster management interface:
Note: A storage virtual machine (SVM) is referred to as a Vserver or vserver in the GUI and CLI.
network interface modify -vserver <clustername> -lif cluster_mgmt_lif_1 -auto-revert true
Procedure 7. Zero All Spare Disks
Step 1. Zero all spare disks in the cluster by running the following command:
disk zerospares
Tech tip: Advanced Data Partitioning creates a root partition and two data partitions on each SSD drive in an AFF configuration. Disk autoassign should have assigned one data partition to each node in an HA pair. If a different disk assignment is required, disk autoassignment must be disabled on both nodes in the HA pair by running the disk option modify command. Spare partitions can then be moved from one node to another by running the disk removeowner and disk assign commands.
Procedure 8. Set Up Service Processor Network Interface
Step 1. Assign a static IPv4 address to the Service Processor on each node by running the following commands:
system service-processor network modify –node <st-node01> -address-family IPv4 –enable true –dhcp none –ip-address <node01-sp-ip> -netmask <node01-sp-mask> -gateway <node01-sp-gateway>
system service-processor network modify –node <st-node02> -address-family IPv4 –enable true –dhcp none –ip-address <node02-sp-ip> -netmask <node02-sp-mask> -gateway <node02-sp-gateway>
Note: The Service Processor IP addresses should be in the same subnet as the node management IP addresses.
Step 2. Verify the configuration:
A50-VDI-Cluster1::> system service-processor network show
Address
Node Status Family Link State IP Address
------------- -------------- --------- ----------- ------------------------
A50-VDI-Cluster1-01
online IPv4 up 10.10.60.33
DHCP: none
MAC Address: d0:39:ea:c6:a5:8e
Network Gateway: 10.10.60.1
Network Mask (IPv4 only): 255.255.255.0
Prefix Length (IPv6 only): -
IPv6 RA Enabled: -
Subnet Name: -
SP Network Setup Status: succeeded
A50-VDI-Cluster1-02
online IPv4 up 10.10.60.34
DHCP: none
MAC Address: d0:39:ea:c6:a6:ba
Network Gateway: 10.10.60.1
Network Mask (IPv4 only): 255.255.255.0
Prefix Length (IPv6 only): -
IPv6 RA Enabled: -
Subnet Name: -
SP Network Setup Status: succeeded
Procedure 9. Create Manual Provisioned Aggregates - Optional
Note: An aggregate containing the root volume is created during the ONTAP setup process. To manually create additional aggregates, determine the aggregate name, the node on which to create it, and the number of disks it should contain.
Step 1. Create new aggregates by running the following commands:
storage aggregate create -aggregate <aggr1_node01> -node <st-node01> -diskcount <num-disks> -diskclass solid-state
storage aggregate create -aggregate <aggr1_node02> -node <st-node02> -diskcount <num-disks> -diskclass solid-state
Note: You should have the minimum number of hot spare disks for the recommended hot spare disk partitions for their aggregate.
Note: For all-flash aggregates, you should have a minimum of one hot spare disk or disk partition. For non-flash homogenous aggregates, you should have a minimum of two hot spare disks or disk partitions. For Flash Pool aggregates, you should have a minimum of two hot spare disks or disk partitions for each disk type.
Tech tip: In an AFF configuration with a small number of SSDs, you might want to create an aggregate with all, but one remaining disk (spare) assigned to the controller.
Note: The aggregate cannot be created until disk zeroing completes. Run the storage aggregate show command to display the aggregate creation status. Do not proceed until both aggr1_node01 and aggr1_node02 are online.
Procedure 10. Remove Default Broadcast Domains
Note: By default, all network ports are included in separate default broadcast domain. Network ports used for data services (for example, e0e, e0f, and so on) should be removed from their default broadcast domain and that broadcast domain should be deleted.
Step 1. Run the following commands:
network port broadcast-domain delete -broadcast-domain <Default-N> -ipspace Default
network port broadcast-domain show
Note: Delete the Default broadcast domains with Network ports (Default-1, Default-2, and so on). This does not include Cluster ports and management ports.
Procedure 11. Disable Flow Control on 25/100GbE Data Ports
Step 1. Disable the flow control on 25 and 100GbE data ports by running the following command to configure the ports on node 01:
network port modify -node <st-node01> -port e2b,e4b,e3a,e3b -flowcontrol-admin none
Warning: This command will cause a several second interruption of service on this network port.
Do you want to continue? {y|n}: y
Warning: Changes to a cluster port can affect the health of the Cluster. Are you sure you want to continue? {y|n}:
Warning: Changes to a cluster port can affect the health of the Cluster. Are you sure you want to continue? {y|n}:y
Step 2. Run the following command to configure the ports on node 02:
A50-VDI-Cluster1::> network port modify -port e2b,e4b,e3a,e3b -flowcontrol-admin none -node A50-VDI-Cluster1-02
Warning: This command will cause a several second interruption of service on this network port.
Do you want to continue? {y|n}: y
6 entries were modified.
Note: Disable flow control only on ports that are used for data traffic.
Procedure 12. Enable Cisco Discovery Protocol
Step 1. Enable the Cisco Discovery Protocol (CDP) on the NetApp storage controllers by running the following command to enable CDP in ONTAP:
node run -node * options cdpd.enable on
Procedure 13. Enable Link-layer Discovery Protocol on all Ethernet Ports
Step 1. Enable the exchange of Link-layer Discovery Protocol (LLDP) neighbor information between the storage and network switches, on all ports, of all nodes in the cluster, by running the following command:
node run * options lldp.enable on
Procedure 14. Enable FIPS Mode on the NetApp ONTAP Cluster - Optional
NetApp ONTAP is compliant in the Federal Information Processing Standards (FIPS) 140-2 for all SSL connections. When SSL FIPS mode is enabled, SSL communication from NetApp ONTAP to external client or server components outside of NetApp ONTAP will use FIPS compliant crypto for SSL.
Note: FIPS mode was not used in this configuration
Step 1. To enable FIPS on the NetApp ONTAP cluster, run the following commands:
set -privilege advanced
security config modify -interface SSL -is-fips-enabled true
Note: If you are running NetApp ONTAP 9.8 or earlier manually reboot each node in the cluster one by one. Beginning in NetApp ONTAP 9.9.1, rebooting is not required.
Procedure 15. Configure Timezone
Step 1. To configure time synchronization on the cluster, follow this step:
timezone -timezone <timezone>
Note: For example, in the eastern United States, the time zone is America/Los_Angeles.
Procedure 16. Configure Simple Network Management Protocol - SNMP
Note: If you enabled FIPS then look at the following points while configuring SNMP.
Note: The SNMP users or SNMP traphosts that are non-compliant with FIPS will be deleted automatically. “Configure SNMP traphosts” configuration will be non-compliant with FIPS.
Note: The SNMPv1 user, SNMPv2c user (After configuring SNMP community) or SNMPv3 user (with none or MD5 as authentication protocol or none or DES as encryption protocol or both) is non-compliant with FIPS.
Step 1. Configure basic SNMP information, such as the location and contact. When polled, this information is visible as the sysLocation and sysContact variables in SNMP.
snmp contact <snmp-contact>
snmp location “<snmp-location>”
snmp init 1
options snmp.enable on
Step 2. Configure SNMP traps to send to remote hosts, such as an Active IQ Unified Manager server or another fault management system.
Note: This step works when FIPS is disabled.
Note: An SNMPv1 traphost or SNMPv3 traphost (configured with an SNMPv3 user non-compliant to FIPS) is non-compliant to FIPS.
snmp traphost add <oncommand-um-server-fqdn>
Step 3. Configure SNMP community.
Note: This step works when FIPS is disabled.
Note: SNMPv1 and SNMPv2c are not supported when cluster FIPS mode is enabled.
system snmp community add -type ro -community-name -vserver
Note: In new installations of NetApp ONTAP, SNMPv1 and SNMPv2c are disabled by default. SNMPv1 and SNMPv2c are enabled after you create an SNMP community.
Note: NetApp ONTAP supports read-only communities.
Procedure 17. Configure SNMPv3 Access
Note: SNMPv3 offers advanced security by using encryption and passphrases. The SNMPv3 user can run SNMP utilities from the traphost using the authentication and privacy settings that you specify.
Note: Configure SNMP traps to send to remote hosts, such as an Active IQ Unified Manager server or another fault management system.
Note: When FIPS is enabled, below are the supported/compliant options for authentication and privacy protocol:
● Authentication Protocol: sha, sha2-256
● Privacy protocol: aes128
Step 1. Configure the SNMPv3 access by running the following command:
security login create -user-or-group-name <<snmp-v3-usr>> -application snmp -authentication-method usm
Enter the authoritative entity's EngineID [local EngineID]:
Which authentication protocol do you want to choose (none, md5, sha, sha2-256) [none]: <<snmp-v3-auth-proto>>
Enter the authentication protocol password (minimum 8 characters long):
Enter the authentication protocol password again:
Which privacy protocol do you want to choose (none, des, aes128) [none]: <<snmpv3-priv-proto>>
Enter privacy protocol password (minimum 8 characters long):
Enter privacy protocol password again:
Note: Refer to the NetApp SNMP Configuration Express Guide for additional information when configuring SNMPv3 security users.
Procedure 18. Configure login banner for the NetApp ONTAP Cluster
Step 1. To create login banner for the NetApp ONTAP cluster, run the following command:
security login banner modify -message "Access restricted to authorized users" -vserver <clustername>
Procedure 19. Remove insecure ciphers from the NetApp ONTAP Cluster
Step 1. Ciphers with the suffix CBC are considered insecure. To remove the CBC ciphers, run the following NetApp ONTAP command:
security ssh remove -vserver <clustername> -ciphers aes256-cbc,aes192-cbc,aes128-cbc,3des-cbc
Procedure 20. Create Management Broadcast Domain
Step 1. If the management interfaces are required to be on a separate VLAN, create a new broadcast domain for those interfaces by running the following command:
network port broadcast-domain create -broadcast-domain IB-MGMT -mtu 1500
Procedure 21. Create NFS Broadcast Domain
Step 1. To create an NFS, data broadcast domain with a maximum transmission unit (MTU) of 9000, run the following commands to create a broadcast domain for NFS in ONTAP:
network port broadcast-domain create -broadcast-domain Infra-NFS -mtu 9000
Procedure 22. Create CIFS Broadcast Domain
Step 1. To create a CIFS data broadcast domain with a maximum transmission unit (MTU) of 9000, run the following commands to create a broadcast domain for CIFS in ONTAP:
network port broadcast-domain create -broadcast-domain CIFS-VLAN -mtu 9000
Procedure 23. Create Interface Groups
Step 1. To create the LACP interface groups for the 25 and 100GbE data interfaces, run the following commands:
A50-VDI-Cluster1::> network port ifgrp create -node <st-node01> -ifgrp a0a -distr-func port -mode multimode_lacp
network port ifgrp add-port -node <st-node01> -ifgrp a0a -port e2b
network port ifgrp add-port -node <st-node01> -ifgrp a0a -port e4b
A50-VDI-Cluster1::> network port ifgrp create -node <st-node01> -ifgrp a0b -distr-func ip -mode multimode_lacp
network port ifgrp add-port -node <st-node01> -ifgrp a0b -port e3a
network port ifgrp add-port -node <st-node01> -ifgrp a0b -port e3b
A50-VDI-Cluster1::> network port ifgrp create -node <st-node02> -ifgrp a0a -distr-func port -mode multimode_lacp
network port ifgrp add-port -node <st-node02> -ifgrp a0a -port e2b
network port ifgrp add-port -node <st-node02> -ifgrp a0a -port e4b
A50-VDI-Cluster1::> network port ifgrp create -node <st-node02> -ifgrp a0b -distr-func ip -mode multimode_lacp
network port ifgrp add-port -node <st-node02> -ifgrp a0b -port e3a
network port ifgrp add-port -node <st-node02> -ifgrp a0b -port e3b
Step 2. To verify, run the following:
A50-VDI-Cluster1::> network port ifgrp show
Port Distribution Active
Node IfGrp Function MAC Address Ports Ports
-------- ---------- ------------ ----------------- ------- -------------------
A50-VDI-Cluster1-01
a0a port d2:39:ea:c6:a5:8d full e2b, e4b
a0b ip d2:39:ea:c6:a5:8c full e3a, e3b
A50-VDI-Cluster1-02
a0a port d2:39:ea:c6:a6:b9 full e2b, e4b
a0b ip d2:39:ea:c6:a6:b8 full e3a, e3b
4 entries were displayed.
Procedure 24. Change MTU on Interface Groups
Step 1. To change the MTU size on the base interface-group ports before creating the VLAN ports, run the following commands:
network port modify –node <st-node01> -port a0a –mtu 9000
network port modify –node <st-node02> -port a0a –mtu 9000
network port modify –node <st-node01> -port a0b –mtu 9000
network port modify –node <st-node02> -port a0b –mtu 9000
Step 1. Create the management VLAN ports and add them to the management broadcast domain:
network port vlan create –node <st-node01> -vlan-name a0a-<ib-mgmt-vlan-id>
network port vlan create –node <st-node02> -vlan-name a0a-<ib-mgmt-vlan-id>
network port broadcast-domain add-ports -broadcast-domain IB-MGMT -ports <st-node01>:a0a-<ib-mgmt-vlan-id>,<st-node02>:a0a-<ib-mgmt-vlan-id>
Step 2. Create the NFS VLAN ports and add them to the Infra-NFS broadcast domain:
network port vlan create –node <st-node01> -vlan-name a0a-<infra-nfs-vlan-id>
network port vlan create –node <st-node02> -vlan-name a0a-<infra-nfs-vlan-id>
network port broadcast-domain add-ports -broadcast-domain Infra-NFS -ports <st-node01>:a0a-<infra-nfs-vlan-id>,<st-node02>:a0a-<infra-nfs-vlan-id>
Procedure 26. Create an Infrastructure SVM
Step 1. Run the vserver create command:
vserver create –vserver VDI-SVM
Step 2. Add the required data protocols to the SVM:
vserver add-protocols -protocols nfs,cifs,fcp, nvme -vserver VDI-SVM
Note: For FC-NVMe configuration, add “fcp” and “nvme” protocols to the SVM.
Note: For NVMe/TCP configuration with iSCSI booting, add “nvme” and “iscsi” protocols to the SVM.
Step 3. Remove the unused data protocols from the SVM:
vserver remove-protocols -vserver VDI-SVM -protocols iscsi,nvme
Note: It is recommended to remove iSCSI or FCP protocols if the protocol is not in use (in this case iSCSI was removed).
Step 4. Add the two data aggregates to the VDI-SVM aggregate list for the NetApp ONTAP Tools:
vserver modify –vserver VDI-SVM –aggr-list <aggr1_node01>,<aggr1_node02>
Step 5. Enable and run the NFS protocol in the VDI-SVM:
vserver nfs create -vserver VDI-SVM -udp disabled -v3 enabled -v4.1 enabled -vstorage enabled
Note: If the NFS license was not installed during the cluster configuration, make sure to install the license before starting the NFS service.
Step 6. Verify the NFS vstorage parameter for the NetApp NFS VAAI plug-in was enabled:
A50-VDI-Cluster::> vserver nfs show -fields vstorage
vserver vstorage
--------- --------
VDI-SVM enabled
Procedure 27. Configure CIFS Servers
Note: You can enable and configure CIFS servers on storage virtual machines (SVMs) with NetApp FlexVol volumes to let SMB clients access files on your cluster. Each data SVM in the cluster can be bound to exactly one Active Directory domain. However, the data SVMs do not need to be bound to the same domain. Each data SVM can be bound to a unique Active Directory domain.
Step 1. To configure DNS for the VDI-SVM, run the following command:
dns create -vserver <vserver-name> -domains <dns-domain> -nameserve <dns-servers>
Example:
dns create -vserver VDI-SVM -domains fpvdilab.local -nameservers 10.10.61.30
Note: The node management network interfaces should be able to route to the Active Directory domain controller to which you want to join the CIFS server. Alternatively, a data network interface must exist on the SVM that can route to the Active Directory domain controller.
Step 2. Create a network interface on the IB-MGMT VLAN:
network interface create –vserver Infra-SVM –lif svm-mgmt -service-policy default-management –home-node <st-node01> -home-port a0a-<ib-mgmt-vlan-id> –address <svm-mgmt-ip> -netmask <svm-mgmt-mask> -status-admin up –failover-policy broadcast-domain-wide –auto-revert true
Step 3. Create the CIFS service:
vserver cifs create -vserver VDI-SVM -cifs-server Infra-CIFS -domain <domain.com>
In order to create an Active Directory machine account for the CIFS server, you must supply the name and password of a Windows account with sufficient privileges to add computers to the "CN=Computers" container within the"DOMAIN.COM" domain.
Enter the user name: Administrator@active_diectory.local
Enter the password:
A50-VDI-Cluster1::> vserver cifs show -vserver VDI-SVM
Vserver: VDI-SVM
CIFS Server NetBIOS Name: VDI-CIFS
NetBIOS Domain/Workgroup Name: FPVDILAB
Fully Qualified Domain Name: FPVDILAB.LOCAL
Organizational Unit: CN=Computers
Default Site Used by LIFs Without Site Membership:
Workgroup Name: -
Authentication Style: domain
CIFS Server Administrative Status: up
CIFS Server Description:
List of NetBIOS Aliases: -
Procedure 28. Modify Storage Virtual machine Option
Note: Note: NetApp ONTAP can use automatic node referrals to increase SMB client performance on SVMs with FlexVol volumes. This feature allows the SVM to automatically redirect a client request to a network interface on the node where the FlexVol volume resides.
Step 1. Run the following command to enable automatic node referrals on your SVM:
set -privilege advanced
vserver cifs options modify -vserver Infra-SVM -is-referral-enabled true
Procedure 29. Create Load-Sharing Mirrors of a SVM Root Volume
Step 1. Create a volume to be the load-sharing mirror of the infrastructure SVM root volume only on the node that does not have the Root Volume:
volume show -vserver VDI-SVM # Identify the aggregate and node where the vserver root volume is located.
A50-VDI-Cluster1::> volume show -vserver VDI-SVM
Vserver Volume Aggregate State Type Size Available Used%
--------- ------------ ------------ ---------- ---- ---------- ---------- -----
VDI-SVM VDI_SVM_root A50_VDI_Cluster1_02_NVME_SSD_1
online RW 1GB 965.6MB 0%
volume create –vserver VDI-SVM –volume VDI_SVM_root_m01 –aggregate <aggr1_node01> –size 1GB –type DP
Step 2. Create a job schedule to update the root volume mirror relationships every 15 minutes:
job schedule interval create -name 15min -minutes 15
Step 3. Create the mirroring relationships:
snapmirror create –source-path VDI-SVM: VDI_SVM_root -destination-path VDI-SVM:VDI_SVM_root_m01 –type LS -schedule 15min
Step 4. Initialize the mirroring relationships:
snapmirror initialize-ls-set –source-path VDI-SVM:VDI_SVM_root
Step 5. Verify the relationship:
A50-VDI-Cluster1::> snapmirror show -type ls -vserver VDI-SVM
Progress
Source Destination Mirror Relationship Total Last
Path Type Path State Status Progress Healthy Updated
----------- ---- ------------ ------- -------------- --------- ------- --------
A50-VDI-Cluster1://VDI-SVM/VDI_SVM_root
LS A50-VDI-Cluster1://VDI-SVM/VDI_SVM_root_m01
Snapmirrored
Idle - true -
1 entries were displayed.
Procedure 30. Configure HTTPS Access to the Storage Controller
Step 1. Increase the privilege level to access the certificate commands:
set -privilege diag
Do you want to continue? {y|n}: y
Step 2. Generally, a self-signed certificate is already in place. Verify the certificate and obtain parameters (for example, the <serial-number>) by running the following command:
security certificate show
Step 3. For each SVM shown, the certificate common name should match the DNS fully qualified domain name (FQDN) of the SVM. Delete the two default certificates and replace them with either self-signed certificates or certificates from a certificate authority (CA). To delete the default certificates, run the following commands:
security certificate delete -vserver VDI-SVM -common-name VDI-SVM -ca VDI-SVM -type server -serial <serial-number>
Note: Deleting expired certificates before creating new certificates is a best practice. Run the security certificate delete command to delete the expired certificates. In the following command, use TAB completion to select and delete each default certificate.
Step 4. To generate and install self-signed certificates, run the following commands as one-time commands. Generate a server certificate for the VDI-SVM and the cluster SVM. Use TAB completion to aid in the completion of these commands:
security certificate create -common-name <cert-common-name> -type server -size 2048 -country <cert-country> -state <cert-state> -locality <cert-locality> -organization <cert-org> -unit <cert-unit> -email-addr <cert-email> -expire-days <cert-days> -protocol SSL -hash-function SHA256 -vserver VDI-SVM
Step 5. To obtain the values for the parameters required in step 5 (<cert-ca> and <cert-serial>), run the security certificate show command.
Step 6. Enable each certificate that was just created by using the –server-enabled true and –client-enabled false parameters. Use TAB completion to aid in the completion of these commands:
security ssl modify -vserver <clustername> -server-enabled true -client-enabled false -ca <cert-ca> -serial <cert-serial> -common-name <cert-common-name>
Step 7. Disable HTTP cluster management access:
network interface service-policy remove-service -vserver <clustername> -policy default-management -service management-http
Note: It is normal for some of these commands to return an error message stating that the entry does not exist.
Step 8. Return to the normal admin privilege level and verify that the system logs are available in a web browser:
set –privilege admin
https://<node01-mgmt-ip>/spi
https://<node02-mgmt-ip>/spi
Procedure 31. Set password for SVM vsadmin user and unlock the user
Step 1. Set a password for the SVM vsadmin user and unlock the user using the following commands:
security login password –username vsadmin –vserver Infra-SVM
Enter a new password: <password>
Enter it again: <password>
security login unlock –username vsadmin –vserver Infra-SVM
Procedure 32. Configure login banner for the SVM
Step 1. To create login banner for the SVM, run the following command:
Security login banner modify -vserver Infra-SVM -message "This Infra-SVM is reserved for authorized users only!"
Procedure 33. Remove insecure ciphers from the SVM
Step 1. Ciphers with the suffix CBC are considered insecure. To remove the CBC ciphers, run the following NetApp ONTAP command:
security ssh remove -vserver Infra-SVM -ciphers aes256-cbc,aes192-cbc,aes128-cbc,3des-cbc
Procedure 34. Configure Export Policy Rule
Step 1. Create a new rule for the infrastructure NFS subnet in the default export policy:
vserver export-policy rule create –vserver Infra-SVM -policyname default –ruleindex 1 –protocol nfs -clientmatch <infra-nfs-subnet-cidr> -rorule sys –rwrule sys -superuser sys –allow-suid true
Step 2. Assign the FlexPod export policy to the infrastructure SVM root volume:
volume modify –vserver Infra-SVM –volume Infra_SVM_root –policy default
Procedure 35. Create CIFS Export Policy
Note: Optionally, you can use export policies to restrict CIFS access to files and folders on CIFS volumes. You can use export policies in combination with share level and file level permissions to determine effective access rights.
Step 1. Run the following command to create an export policy that limits access to devices in the domain:
export-policy create -vserver Infra-SVM -policyname cifs_policy
export-policy rule create -vserver Infra-SVM -policyname cifs_policy -clientmatch <domain_name> -rorule
krb5i,krb5p -rwrule krb5i,krb5p
Procedure 36. Create a NetApp FlexVol Volume
The following information is required to create a NetApp FlexVol volume:
● The volume name
● The volume size
● The aggregate on which the volume exists
Step 1. To create FlexVols for datastores, run the following commands:
volume create -vserver Infra-SVM -volume infra_datastore -aggregate <aggr1_node01> -size 1TB -state online -policy default -junction-path /infra_datastore -space-guarantee none -percent-snapshot-space 0
Note: If you are going to setup and use SnapCenter to backup the infra_datastore volume, add “- snapshot-policy none” to the end of the volume create command for the infra_datastore volume.
Step 2. Create vCLS datastores to be used by the vSphere environment to host vSphere Cluster Services (vCLS) VMs using the command below:
volume create -vserver Infra-SVM -volume vCLS -aggregate <aggr1_node02> -size 100GB -state online -policy default -junction-path /vCLS -space-guarantee none -percent-snapshot-space 0
Step 3. To create swap volumes, run the following commands:
volume create -vserver Infra-SVM -volume infra_swap -aggregate <aggr1_node01> -size 200GB -state online -policy default -junction-path /infra_swap -space-guarantee none -percent-snapshot-space 0 -snapshot-policy none.
Step 4. To create a FlexVol for the boot LUNs of servers, run the following command:
volume create -vserver Infra-SVM -volume esxi_boot -aggregate <aggr1_node01> -size 320GB -state online -policy default -space-guarantee none -percent-snapshot-space 0
Step 5. Run the following command to create a FlexVol for storing SVM audit log configuration:
volume create -vserver Infra-SVM -volume audit_log -aggregate <aggr1_node01> -size 50GB -state online -policy default -junction-path /audit_log -space-guarantee none -percent-snapshot-space 0
Procedure 37. Create a NetApp FlexGroup Volume
Step 1. To create CIFS and NFS volumes, run the following commands:
volume create -vserver VDI-SVM -volume cifs_vol_01_new -aggr-list aggr01_node01,aggr01_node02 -aggr-list-multiplier 4 -state online –policy cifs_policy -size 2TB -junction-path /cifs_vol_01_new -space-guarantee none -percent-snapshot-space 0
volume create -vserver VDI-SVM -volume cifs_vol_02_new -aggr-list aggr01_node01,aggr01_node02 -aggr-list-multiplier 4 -state online –policy cifs_policy -size 800GB -junction-path /cifs_vol_02_new -space-guarantee none -percent-snapshot-space 0
volume create -vserver VDI-SVM -volume Datastore_NFS_VDI -aggr-list aggr01_node01,aggr01_node02 -aggr-list-multiplier 4 -state online –policy nfs_policy -size 5TB -junction-path /Datastore_NFS_VDI -space-guarantee none -percent-snapshot-space 0
volume create -vserver VDI-SVM -volume Datastore_NFS_VDI_02 -aggr-list aggr01_node01,aggr01_node02 -aggr-list-multiplier 4 -state online –policy nfs_policy -size 5TB -junction-path /Datastore_NFS_VDI_02 -space-guarantee none -percent-snapshot-space 0
volume create -vserver VDI-SVM -volume Datastore_NFS_VDI_03 -aggr-list aggr01_node01,aggr01_node02 -aggr-list-multiplier 4 -state online –policy nfs_policy -size 5TB -junction-path /Datastore_NFS_VDI_03 -space-guarantee none -percent-snapshot-space 0
volume create -vserver VDI-SVM -volume Datastore_NFS_VDI_04 -aggr-list aggr01_node01,aggr01_node02 -aggr-list-multiplier 4 -state online –policy nfs_policy -size 5TB -junction-path /Datastore_NFS_VDI_04 -space-guarantee none -percent-snapshot-space 0
Procedure 38. Create FCP Datastores
Step 1. To create FCP volumes, run the following commands:
volume create -vserver VDI-SVM -volume Datastore_FP_VDI -aggr-list aggr01_node01 -state online -size 20TB -space-guarantee none -percent-snapshot-space 0
volume create -vserver VDI-SVM -volume Datastore_FP_VDI_02 -aggr-list aggr01_node02 -state online -size 20TB -space-guarantee none -percent-snapshot-space 0
volume create -vserver VDI-SVM -volume Datastore_FP_VDI_03 -aggr-list aggr01_node02 -state online -size 20TB -space-guarantee none -percent-snapshot-space 0
volume create -vserver VDI-SVM -volume Datastore_FP_VDI_04 -aggr-list aggr01_node01 -state online -size 20TB -space-guarantee none -percent-snapshot-space 0
Step 2. To create FCP LUNs, run the following commands:
lun create -vserver VDI-SVM -path /vol/Datastore_FP_VDI/Datastore_FP_VDI -size 20TB -ostype vmware -space-reserve disabled
lun create -vserver VDI-SVM -path /vol/Datastore_FP_VDI_02/Datastore_FP_VDI_02 -size 20TB -ostype vmware -space-reserve disabled
lun create -vserver VDI-SVM -path /vol/Datastore_FP_VDI_03/Datastore_FP_VDI_03 -size 20TB -ostype vmware -space-reserve disabled
lun create -vserver VDI-SVM -path /vol/Datastore_FP_VDI_04/Datastore_FP_VDI_04 -size 20TB -ostype vmware -space-reserve disabled
Step 3. To create igroup, run the following commands:
lun igroup create –vserver VDI-SVM –igroup ESXCH1B1-FC –protocol fcp –ostype vmware –initiator <vm-host-01-wwpna>, <vm-host-01-wwpnb>
lun igroup create –vserver VDI-SVM –igroup ESXCH1B2-FC-FC –protocol fcp –ostype vmware –initiator <vm-host-01-wwpna>, <vm-host-01-wwpnb>
lun igroup create –vserver VDI-SVM –igroup ESXCH1B3-FC-FC –protocol fcp –ostype vmware –initiator <vm-host-01-wwpna>, <vm-host-01-wwpnb>
lun igroup create –vserver VDI-SVM –igroup ESXCH1B4-FC-FC –protocol fcp –ostype vmware –initiator <vm-host-01-wwpna>, <vm-host-01-wwpnb>
Step 4. To map Luns to igroup, run the following commands:
lun mapping create –vserver VDI-SVM –path /vol/Datastore_FP_VDI/Datastore_FP_VDI –igroup ESXCH1B1-FC –lun-id 1
lun mapping create –vserver VDI-SVM –path /vol/Datastore_FP_VDI_02/Datastore_FP_VDI_02 –igroup ESXCH1B2-FC –lun-id 3
lun mapping create –vserver VDI-SVM –path /vol/Datastore_FP_VDI_03/Datastore_FP_VDI_03 –igroup ESXCH1B3-FC –lun-id 4
lun mapping create –vserver VDI-SVM –path /vol/Datastore_FP_VDI_04/Datastore_FP_VDI_04 –igroup ESXCH1B3-FC –lun-id 5
Step 5. Update set of load-sharing mirrors using the command below:
snapmirror update-ls-set -source-path VDI-SVM :VDI_SVM _root
Note: If you are going to setup and use SnapCenter to backup the infra_datastore volume, add “-snapshot-policy none” to the end of the volume create command for the infra_datastore volume.
Procedure 39. Disable Volume Efficiency on swap volume
Step 1. On NetApp AFF systems, deduplication is enabled by default. To disable the efficiency policy on the infra_swap volume, run the following command:
volume efficiency off –vserver Infra-SVM –volume infra_swap
Procedure 40. Create CIFS Shares
Note: A CIFS share is a named access point in a volume that enables CIFS clients to view, browse, and manipulate files on a file server.
Step 1. Run the following commands to create CIFS shares:
cifs share create -vserver Infra-SVM -share-name <CIFS_share_1> -path /cifs_vol_01 -share properties oplocks,browsable,continuously-available,showsnapshot
cifs share create -vserver Infra-SVM -share-name <CIFS_share_2> -path /cifs_vol_02 -share properties oplocks,browsable,continuously-available,showsnapshot
cifs share create -vserver Infra-SVM -share-name <CIFS_share_3> -path /cifs_vol_03 -share properties oplocks,browsable,continuously-available,showsnapshot
Step 1. Run the following commands to create NFS LIFs:
network interface create -vserver VDI-SVM -lif nfs-lif-01 -service-policy default-data-files -home-node <st-node01> -home-port a0a-<infra-nfs-vlan-id> –address <node01-nfs-lif-01-ip> -netmask <node01-nfs-lif-01-mask> -status-admin up –failover-policy broadcast-domain-wide –auto-revert true
network interface create -vserver VDI-SVM -lif nfs-lif-02 -service-policy default-data-files -home-node <st-node02> -home-port a0a-<infra-nfs-vlan-id> –address <node02-nfs-lif-02-ip> -netmask <node02-nfs-lif-02-mask>> -status-admin up –failover-policy broadcast-domain-wide –auto-revert true
Step 2. Run the following commands to verify:
A50-VDI-Cluster1::> network interface show -vserver VDI-SVM -service-policy default-data-files
Logical Status Network Current Current Is
Vserver Interface Admin/Oper Address/Mask Node Port Home
----------- ---------- ---------- ------------------ ------------- ------- ----
VDI-SVM
nfs-lif-01 up/up 10.10.63.32/24 A50-VDI-Cluster1-01
a0a-63 true
nfs-lif-02 up/up 10.10.63.33/24 A50-VDI-Cluster1-02
a0a-63 true
2 entries were displayed.
Procedure 42. Create FCP LIFs
Step 1. Run the following commands to create FCP LIFs:
A50-VDI-Cluster1::> network interface create -vserver VDI-SVM -lif <fcp-lif-name> -data-protocol fcp -home-node <st-node01> -home-port 1a –status-admin up
A50-VDI-Cluster1::> network interface create -vserver VDI-SVM -lif <fcp-lif-name> -data-protocol fcp -home-node <st-node01> -home-port 1b –status-admin up
A50-VDI-Cluster1::> network interface create -vserver VDI-SVM -lif <fcp-lif-name> -data-protocol fcp -home-node <st-node01> -home-port 1c –status-admin up
A50-VDI-Cluster1::> network interface create -vserver VDI-SVM -lif <fcp-lif-name> -data-protocol fcp -home-node <st-node01> -home-port 1d –status-admin up
Step 2. Run the following commands to verify:
A50-VDI-Cluster1::> network interface show -vserver VDI-SVM -data-protocol fcp
Logical Status Network Current Current Is
Vserver Interface Admin/Oper Address/Mask Node Port Home
----------- ---------- ---------- ------------------ ------------- ------- ----
VDI-SVM
fcp_lif_01a up/down 20:00:d0:39:ea:c6:a5:8c
A50-VDI-Cluster1-01
1a true
fcp_lif_01b up/down 20:01:d0:39:ea:c6:a5:8c
A50-VDI-Cluster1-01
1b true
fcp_lif_01c up/down 20:02:d0:39:ea:c6:a5:8c
A50-VDI-Cluster1-01
1c true
fcp_lif_01d up/down 20:03:d0:39:ea:c6:a5:8c
A50-VDI-Cluster1-01
1d true
fcp_lif_02a up/down 20:07:d0:39:ea:c6:a5:8c
A50-VDI-Cluster1-02
1a true
fcp_lif_02b up/down 20:06:d0:39:ea:c6:a5:8c
A50-VDI-Cluster1-02
1b true
fcp_lif_02c up/down 20:05:d0:39:ea:c6:a5:8c
A50-VDI-Cluster1-02
1c true
fcp_lif_02d up/down 20:04:d0:39:ea:c6:a5:8c
A50-VDI-Cluster1-02
1d true
Procedure 43. Create CIFS LIFs
Step 1. Run the following commands to create CIFS LIFs:
network interface create -vserver Infra-SVM -lif cifs_lif01 -service-policy default-data-files -home-node <st-node01> -home-port a0a-<infra-cifs-vlan-id> –address <node01-cifs_lif01-ip> -netmask <node01-cifs_lif01-mask> -status-admin up –failover-policy broadcast-domain-wide –auto-revert true
network interface create -vserver Infra-SVM -lif cifs_lif02 -service-policy default-data-files -home-node <st-node02> -home-port a0a-<infra-cifs-vlan-id> –address <node02-cifs_lif02-ip> -netmask <node02-cifs_lif02-mask>> -status-admin up –failover-policy broadcast-domain-wide –auto-revert true
Step 1. Create a default route that enables the SVM management interface to reach the outside world:
network route create –vserver Infra-SVM -destination 0.0.0.0/0 –gateway <svm-mgmt-gateway>
Step 2. To verify, run the following:
A50-VDI-Cluster::> network route show -vserver Infra-SVM
Vserver Destination Gateway Metric
------------------- --------------- --------------- ------
Infra-SVM
0.0.0.0/0 10.10.31.1 20
Note: A cluster serves data through at least one and possibly several SVMs. By completing these steps, you have created a single data SVM. You can create additional SVMs depending on their requirement.
Procedure 45. Configure Auto-Support
Step 1. NetApp AutoSupport sends support summary information to NetApp through HTTPS. To configure AutoSupport using command-line interface, run the following command:
system node autosupport modify -node * -state enable –mail-hosts -transport https -support enable -from <storage-admin-email> -to <storage-admin-email>
Cisco Intersight Managed Mode Configuration
This chapter contains the following:
● Cisco Intersight Managed Mode on Cisco UCS Fabric Interconnects
● Configure a Cisco UCS Domain Profile
● Cisco UCS Domain Configuration
● Configure Server Profile Template
The Cisco Intersight platform is a management solution delivered as a service with embedded analytics for Cisco and third-party IT infrastructures. The Cisco Intersight managed mode (also referred to as Cisco IMM or Intersight managed mode) is a new architecture that manages Cisco UCS fabric interconnect–attached systems through a Redfish-based standard model. Cisco Intersight managed mode standardizes both policy and operation management Cisco UCS X215c M8 compute nodes used in this deployment guide.
Cisco Intersight Managed Mode on Cisco UCS Fabric Interconnects
This section details the process to configure Cisco Intersight Managed Mode (Cisco IMM) on Cisco UCS Fabric Interconnects (Cisco UCS Fis).
Procedure 1. Set up Cisco Intersight Managed Mode on Cisco UCS Fabric Interconnects
Note: The Cisco UCS fabric interconnects need to be set up to support Cisco Intersight managed mode. When converting an existing pair of Cisco UCS fabric interconnects from Cisco UCS Manager mode to Intersight Mange Mode (IMM), first erase the configuration and reboot your system.
WARNING! Converting fabric interconnects to Cisco Intersight Managed Mode is a disruptive process, and configuration information will be lost. You are encouraged to make a backup of their existing configuration.
Step 1. Configure Fabric Interconnect A (FI-A). On the Basic System Configuration Dialog screen, set the management mode to Intersight. All the remaining settings are like those for the Cisco UCS Manager managed mode (UCSM-Managed).
Cisco UCS Fabric Interconnect A
To configure the Cisco UCS for use in a FlexPod environment in intersight managed mode, follow these steps:
Step 2. Connect to the console port on the first Cisco UCS fabric interconnect.
Enter the configuration method. (console/gui) ? console
Enter the management mode. (ucsm/intersight)? intersight
You have chosen to setup a new Fabric interconnect in “intersight” managed mode. Continue? (y/n): y
Enforce strong password? (y/n) [y]: Enter
Enter the password for "admin": <password>
Confirm the password for "admin": <password>
Enter the switch fabric (A/B) []: A
Enter the system name: <ucs-cluster-name>
Physical Switch Mgmt0 IP address : <ucsa-mgmt-ip>
Physical Switch Mgmt0 IPv4 netmask : <ucsa-mgmt-mask>
IPv4 address of the default gateway : <ucsa-mgmt-gateway>
Configure the DNS Server IP address? (yes/no) [n]: y
DNS IP address : <dns-server-1-ip>
Configure the default domain name? (yes/no) [n]: y
Default domain name : <ad-dns-domain-name>
<SNIP>
Verify and save the configuration.
Step 3. After applying the settings, make sure you can ping the fabric interconnect management IP address. When Fabric Interconnect A is correctly set up and is available, Fabric Interconnect B will automatically discover Fabric Interconnect A during its setup process as shown in the next step.
Step 4. Configure Fabric Interconnect B (FI-B). For the configuration method, choose console. Fabric Interconnect B will detect the presence of Fabric Interconnect A and will prompt you to enter the admin password for Fabric Interconnect A. Provide the management IP address for Fabric Interconnect B and apply the configuration.
Cisco UCS Fabric Interconnect A
Enter the configuration method. (console/gui) ? console
Installer has detected the presence of a peer Fabric interconnect. This Fabric interconnect will be added to the cluster. Continue (y/n) ? y
Enter the admin password of the peer Fabric interconnect: <password>
Connecting to peer Fabric interconnect... done
Retrieving config from peer Fabric interconnect... done
Peer Fabric interconnect Mgmt0 IPv4 Address: <ucsa-mgmt-ip>
Peer Fabric interconnect Mgmt0 IPv4 Netmask: <ucsa-mgmt-mask>
Peer FI is IPv4 Cluster enabled. Please Provide Local Fabric Interconnect Mgmt0 IPv4 Address
Physical Switch Mgmt0 IP address : <ucsb-mgmt-ip>
Local fabric interconnect model(UCS-FI-6536)
Peer fabric interconnect is compatible with the local fabric interconnect. Continuing with the installer...
Apply and save the configuration (select 'no' if you want to re-enter)? (yes/no): yes
Procedure 2. Set up a new Cisco Intersight account
Step 1. Go to https://intersight.com and click Create an account.
Step 2. Read and accept the license agreement. Click Next.
Step 3. Provide an Account Name and click Create.
On successful creation of the Intersight account, the following page will be displayed:
Note: You can also choose to add the Cisco UCS FIs to an existing Cisco Intersight account.
Procedure 3. Set up Cisco Intersight account and associate it with Cisco Smart Licensing
Note: When setting up a new Cisco Intersight account (as described in this document), the account needs to be enabled for Cisco Smart Software Licensing.
Step 1. Log into the Cisco Smart Licensing portal: https://software.cisco.com/software/csws/ws/platform/home?locale=en_US#module/SmartLicensing.
Step 2. Verify that the correct virtual account is selected.
Step 3. Under Inventory > General, generate a new token for product registration.
Step 4. Copy this newly created token.
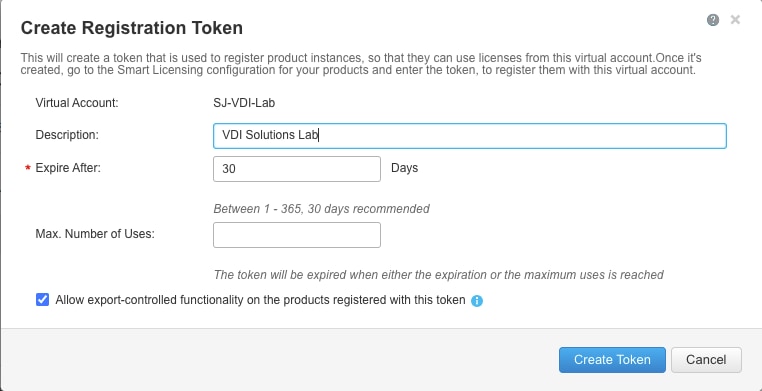
Step 5. Log into the Cisco Intersight portal and click the drop-down list. Click System.
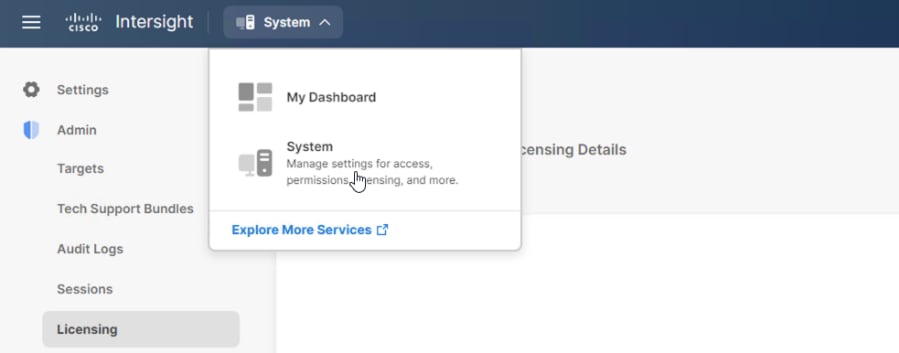
Step 6. Under Cisco Intersight > Licensing, click Register.
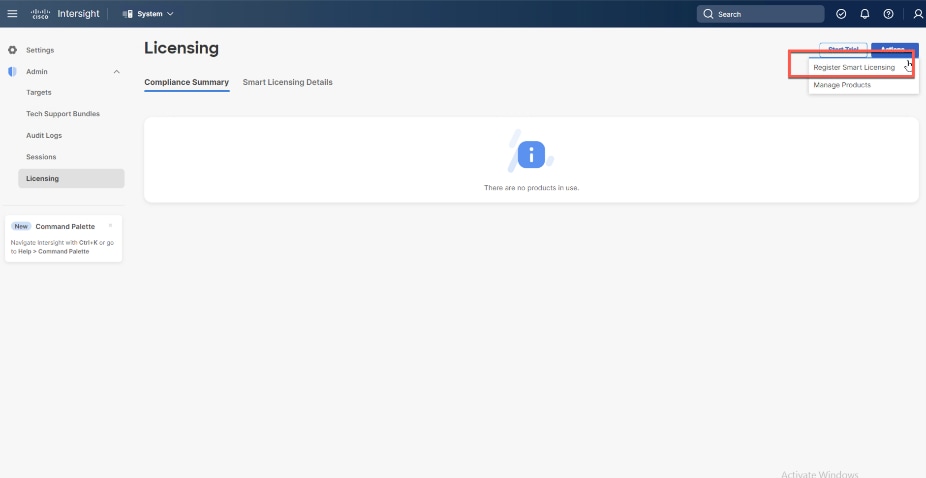
Step 7. Enter the copied token from the Cisco Smart Licensing portal. Click Next.
Step 8. From the drop-down list, select the pre-selected Default Tier * and select the license type (for example, Premier).
Step 9. Select Move All Servers to Default Tier.
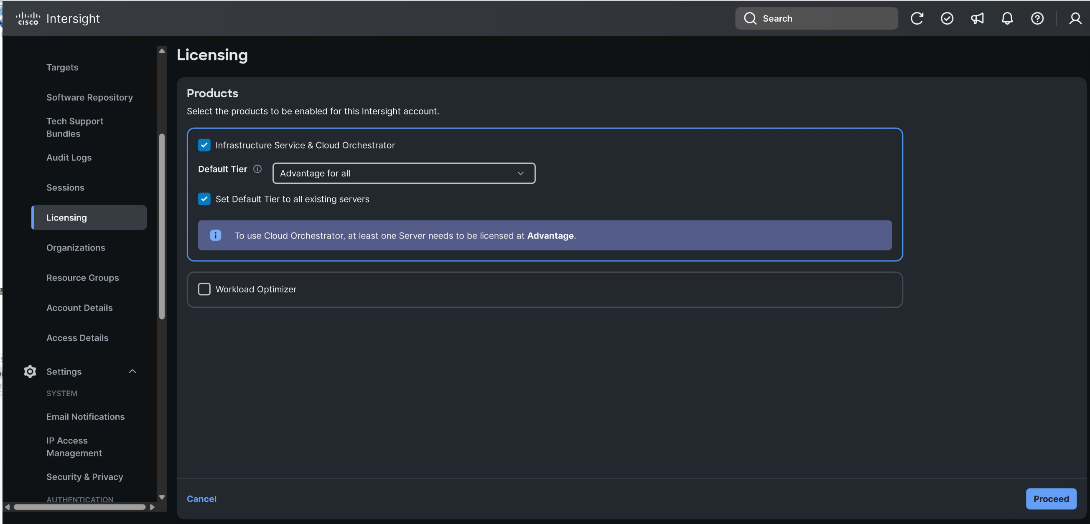
Step 10. Click Proceed.
When the registration is successful (takes a few minutes), the information about the associated Cisco Smart account and default licensing tier selected in the last step is displayed.
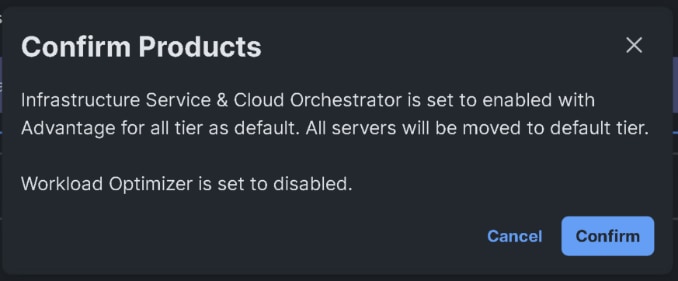
Procedure 4. Set up Cisco Intersight Resource Group
Note: In this procedure, a Cisco Intersight resource group is created where resources such as targets will be logically grouped. In this deployment, a single resource group is created to host all the resources, but you can choose to create multiple resource groups for granular control of the resources.
Step 1. Log into Cisco Intersight.
Step 2. Click Settings (the gear icon) and click Settings.
Step 3. Click Resource Groups.
Step 4. Click + Create Resource Group.
Step 5. Provide a name for the Resource Group (for example, X-Series).
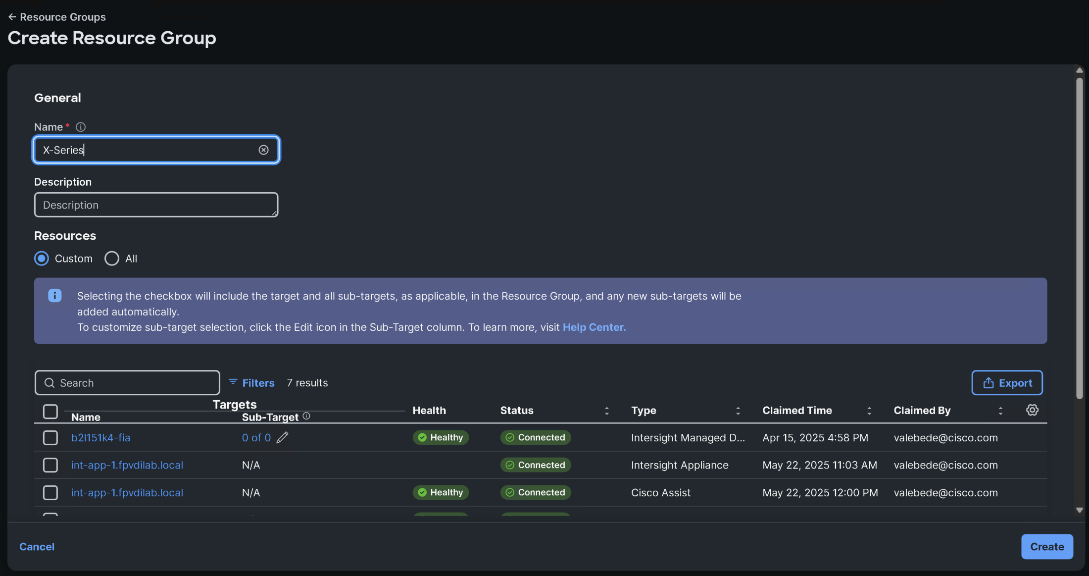
Step 6. Under Memberships, click Custom.
Step 7. Click Create.
Procedure 5. Set up Cisco Intersight Organization
Note: In this procedure, a Cisco Intersight organization is created where all Cisco Intersight managed mode configurations including policies are defined.
Step 1. Log into the Cisco Intersight portal.
Step 2. Click Settings (the gear icon) and select Settings.
Step 3. Click Organizations.
Step 4. Click + Create Organization.
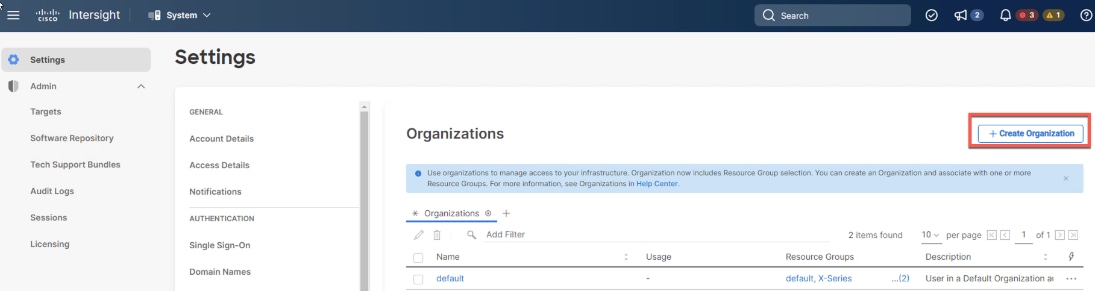
Step 5. Provide a name for the organization (for example, VDI).
Step 6. Select the Resource Group created in the last step (for example, VDI Lab).
Step 7. Click Create.
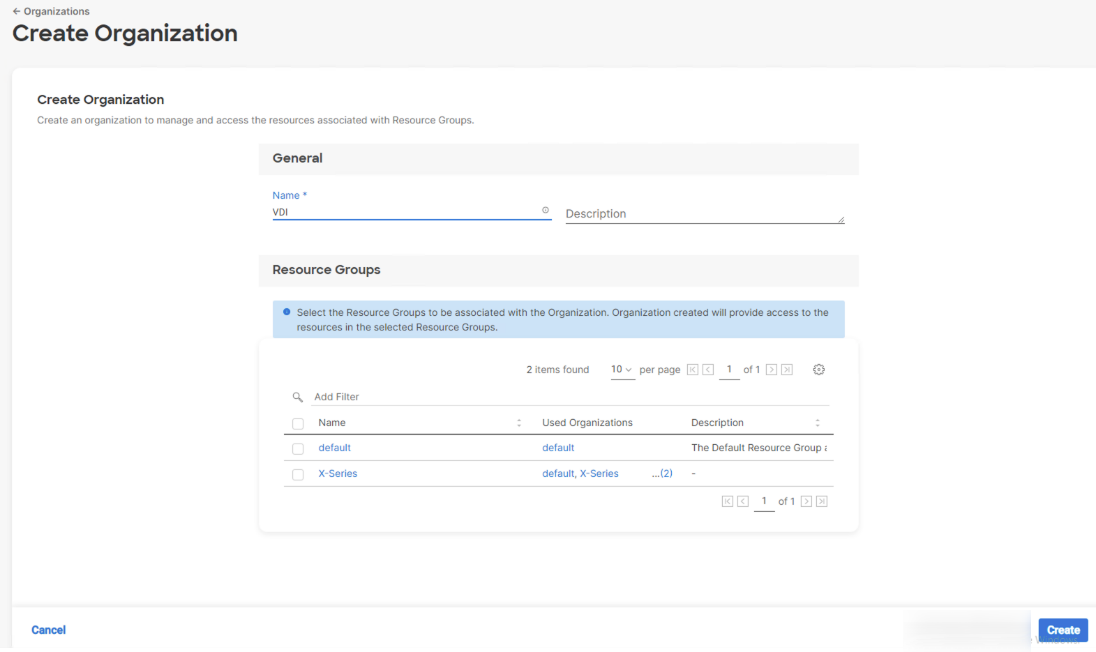
Procedure 6. Claim Cisco UCS Fabric Interconnects in Cisco Intersight
Note: Make sure the initial configuration for the fabric interconnects has been completed. Log into Fabric Interconnect A using a web browser to capture the Cisco Intersight connectivity information.
Step 1. Use the management IP address of Fabric Interconnect A to access the device from a web browser and the previously configured admin password to Log into the device.
Step 2. Under DEVICE CONNECTOR, the current device status will show “Not claimed.” Note, or copy, the Device ID, and Claim Code information for claiming the device in Cisco Intersight.
Step 3. Log into Cisco Intersight.
Step 4. Click Targets.
Step 5. Click Claim New Target.
Step 6. Select Cisco UCS Domain (Intersight Managed) and click Start.
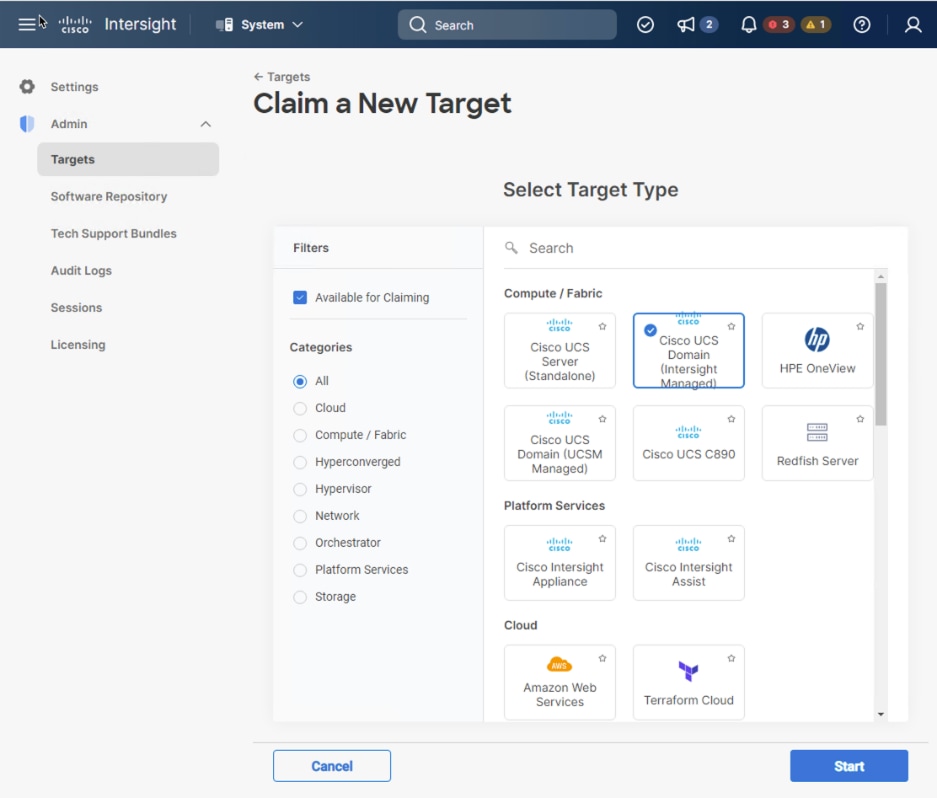
Step 7. Enter the Device ID and Claim Code captured from the Cisco UCS FI.
Step 8. Select the previously created Resource Group and click Claim.
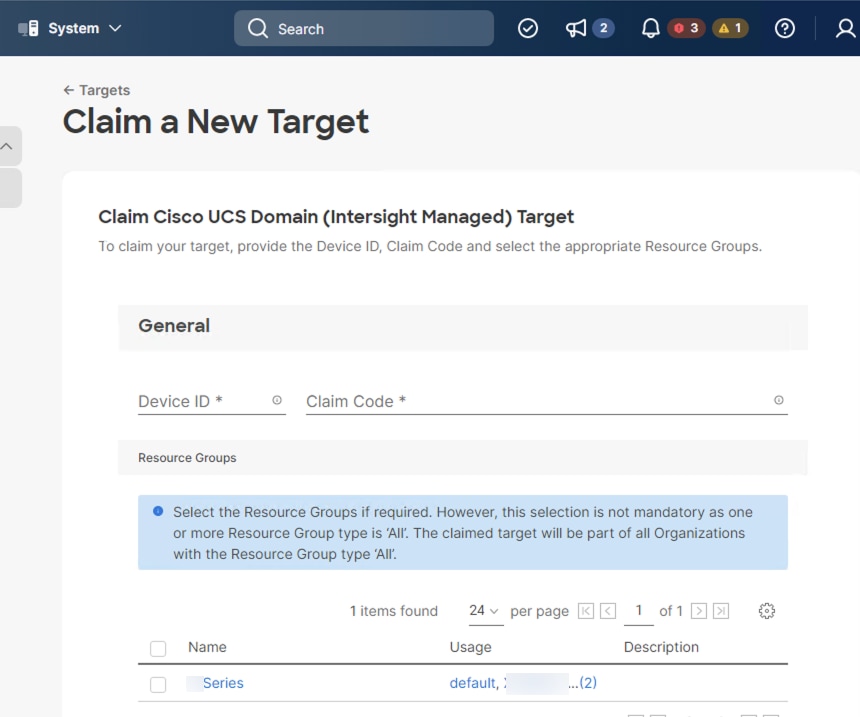
On successfully device claim, Cisco UCS FI appears as a target in Cisco Intersight.
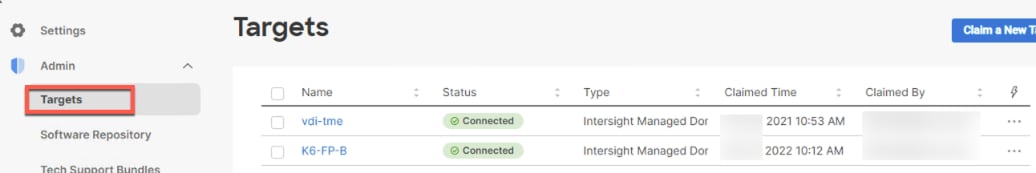
Procedure 7. Verify the addition of Cisco UCS Fabric Interconnects to Cisco Intersight
Step 1. Log back into the web GUI of the Cisco UCS fabric interconnect and click Refresh.
The fabric interconnect status should now be set to Claimed.
Configure a Cisco UCS Domain Profile
A Cisco UCS domain profile configures a fabric interconnect pair through reusable policies, allows configuration of the ports and port channels, and configures the VLANs in the network. It defines the characteristics of and configured ports on fabric interconnects. The domain-related policies can be attached to the profile either at the time of creation or later. One Cisco UCS domain profile can be assigned to one fabric interconnect domain.
Procedure 1. Create a Cisco UCS Domain Profile
Step 1. Log into the Cisco Intersight portal.
Step 2. Under CONFIGURE in the left pane and click Profiles.
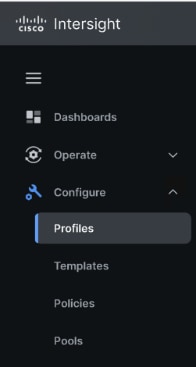
Step 3. In the main window, click UCS Domain Profiles and click Create UCS Domain Profile.
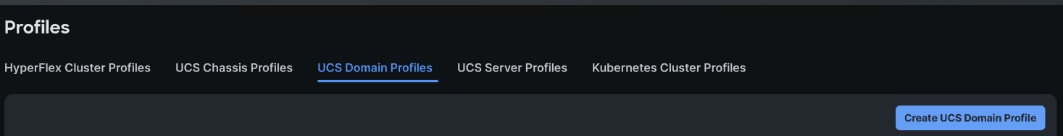
Step 4. Click Start to begin.
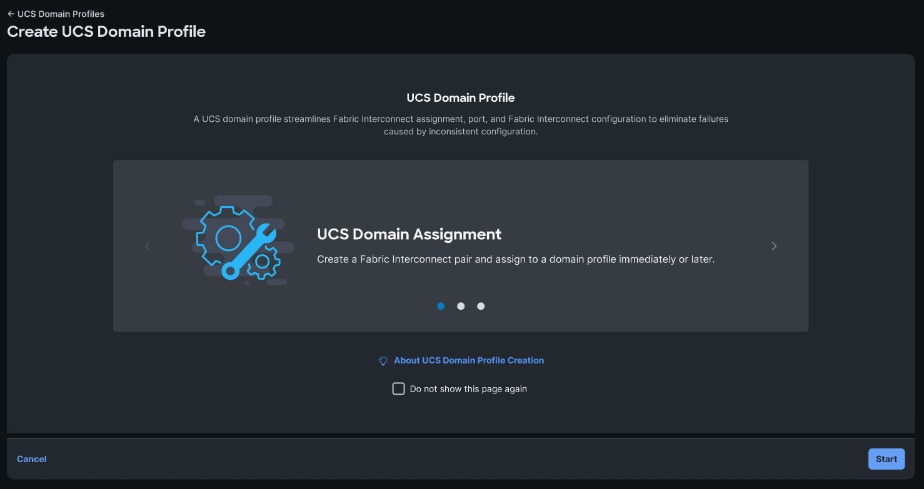
Procedure 2. General Configuration
Step 1. From the drop-down list, select the organization (for example, X-Series).
Step 2. Provide a name for the domain profile (for example, VDI-Domain-Profile).
Step 3. Provide an optional Description.
Step 4. Click Next.
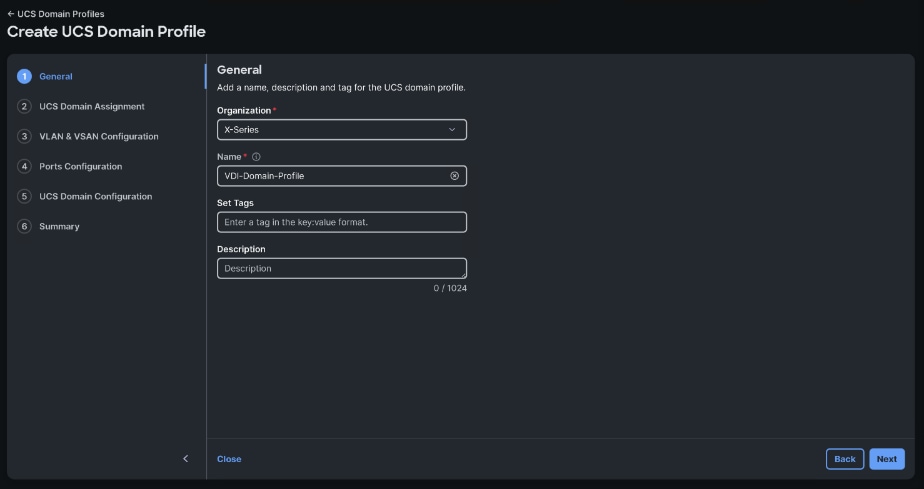
Procedure 3. Cisco UCS Domain Assignment
Step 1. To assign the Cisco UCS domain to this new domain profile, click Assign Now and select the previously added Cisco UCS domain (for example, b2l151k4-fia).
Step 2. Click Next.
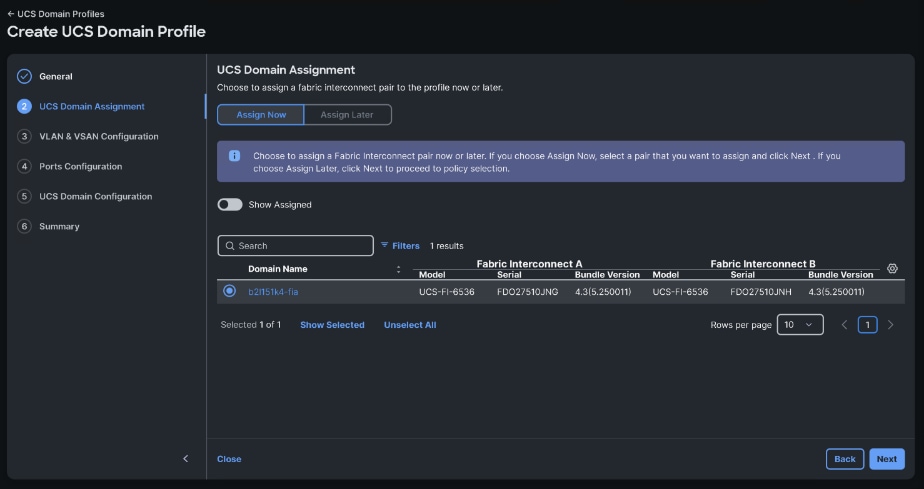
Procedure 4. Create and apply the VLAN Policy
Note: In this procedure, a single VLAN policy is created for both fabric interconnects
Step 1. Click Select Policy next to VLAN Configuration under Fabric Interconnect A.
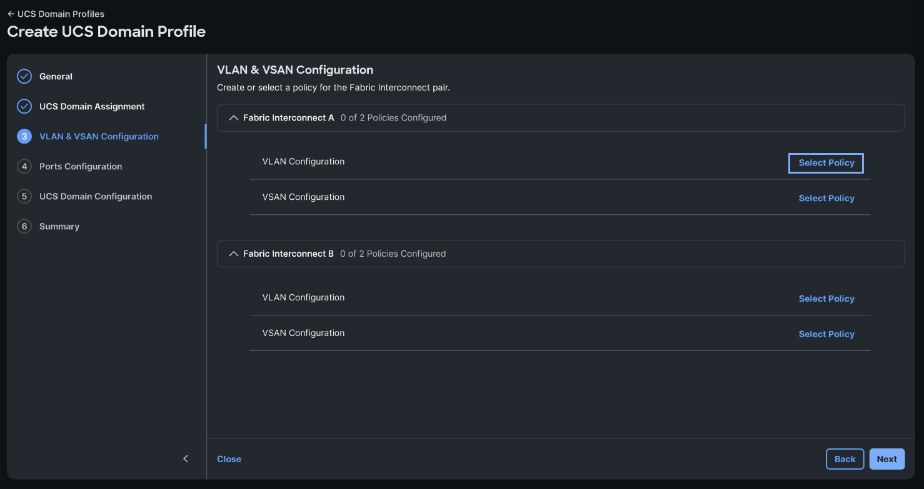
Step 2. Click Create New.
Step 3. Verify correct organization is selected from the drop-down list and provide a name for the policy (for example, VDI-VLAN-Policy).
Step 4. Click Next.
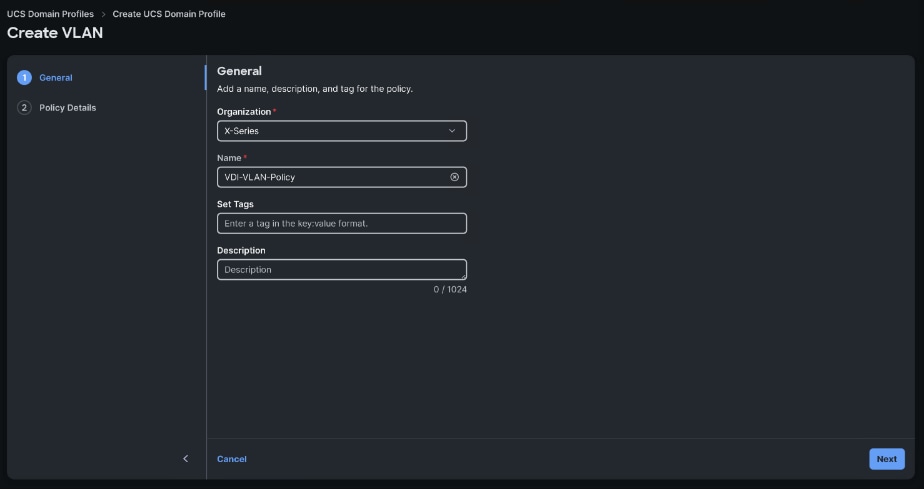
Step 5. Click Add VLANs.
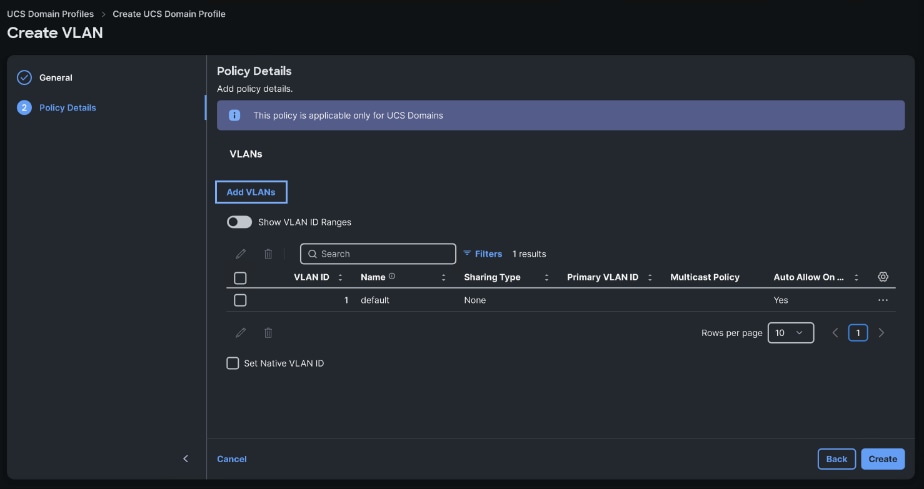
Step 6. Provide a name and VLAN ID for the native VLAN.
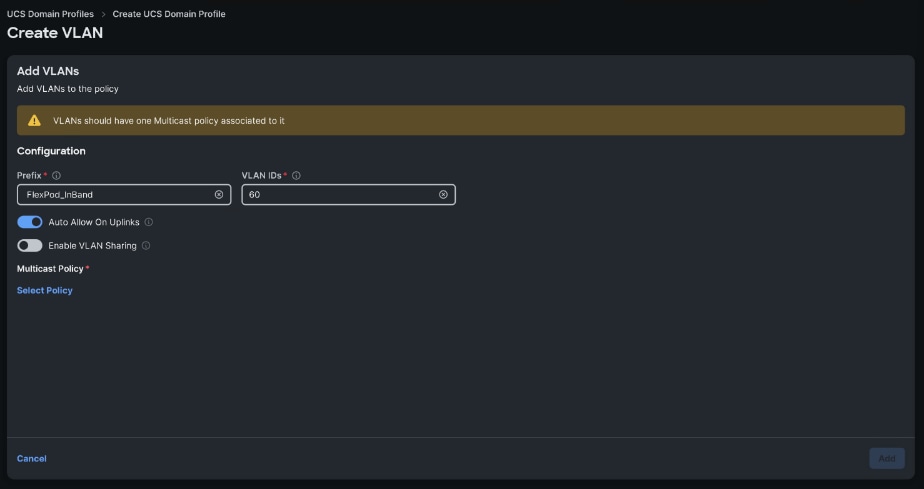
Step 7. Make sure Auto Allow On Uplinks is enabled.
Step 8. To create the required Multicast policy, click Select Policy under Multicast*.
Step 9. In the window on the right, click Create New to create a new Multicast Policy.
Step 10. Provide a Name for the Multicast Policy (for example, FlexPod-MCAST-Policy).
Step 11. Provide optional Description and click Next.
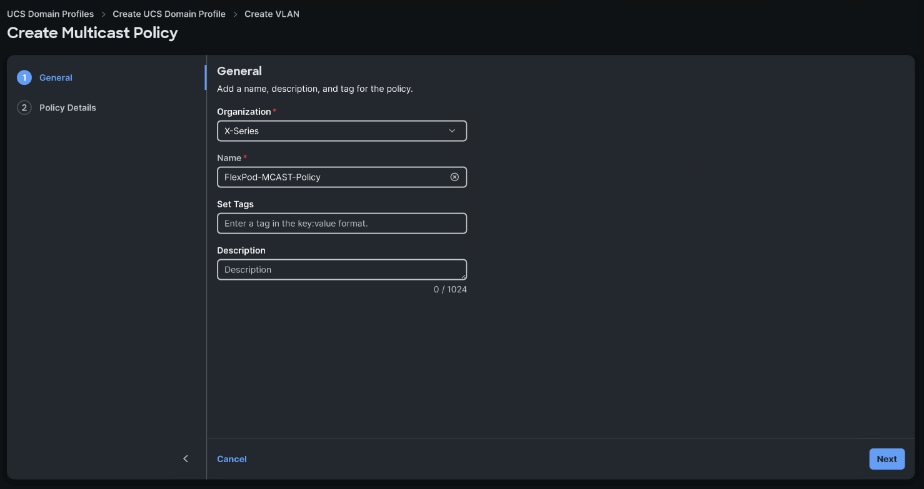
Step 12. Leave the Snooping State selected and click Create.
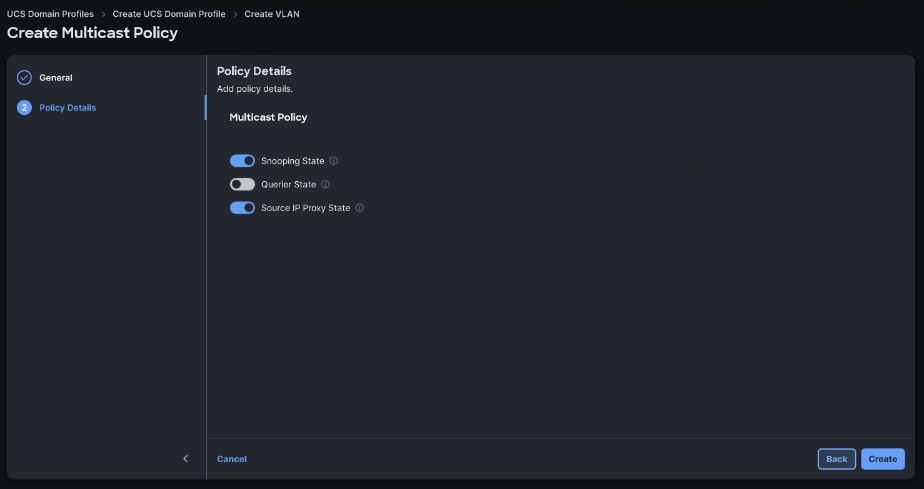
Step 13. Click Add to add the VLAN.
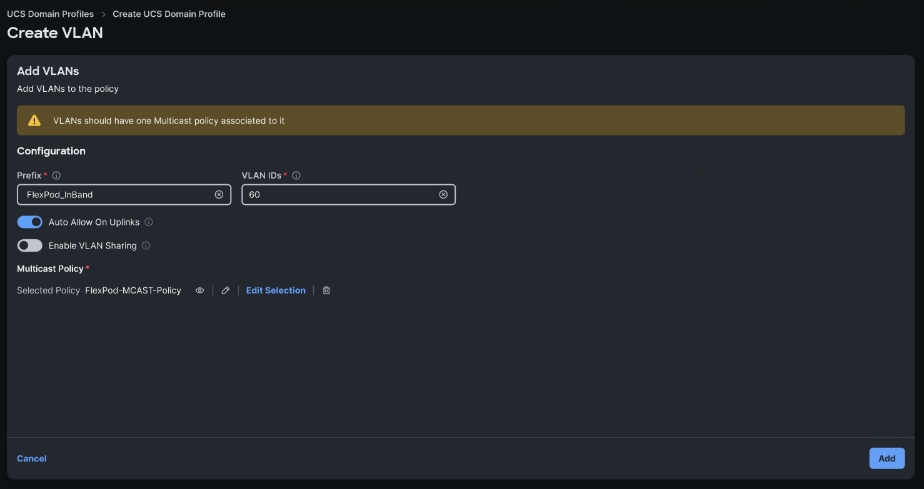
Note: Select Set Native VLAN ID and enter the VLAN number (for example, 2) under VLAN ID.
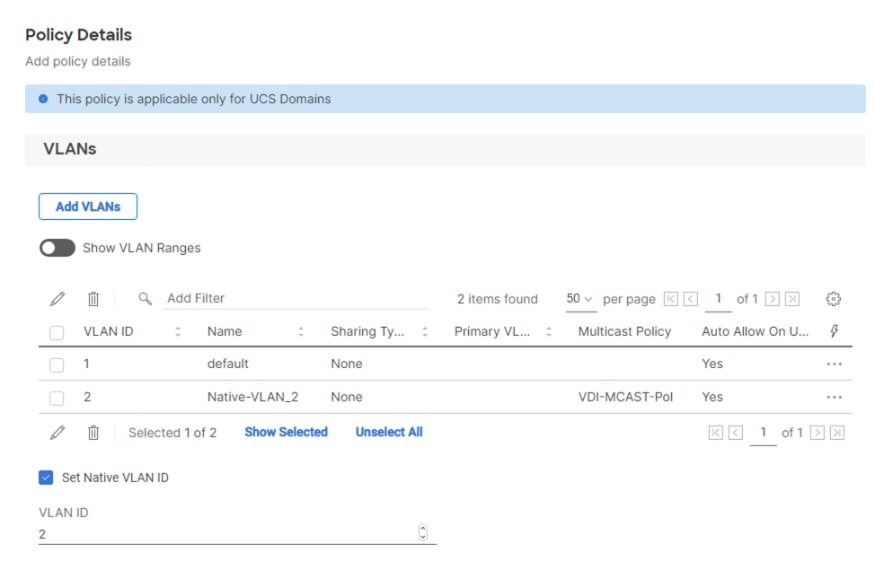
Step 14. Add the remaining VLANs for FlexPod by clicking Add VLANs and entering the VLANs one by one. Reuse the previously created multicast policy for all the VLANs.
The VLANs created during this validation are shown below:
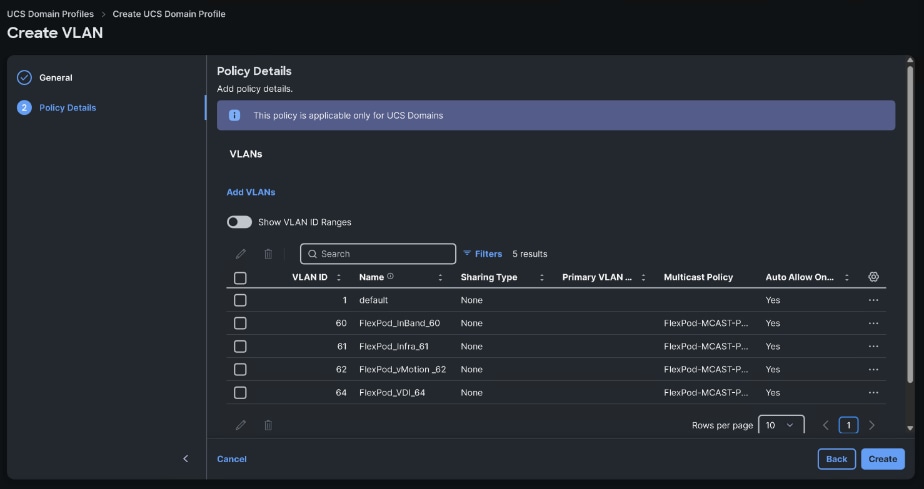
Step 15. Click Create to finish creating the VLAN policy and associated VLANs.
Step 16. Click Select Policy next to VLAN Configuration for Fabric Interconnect B and
Step 17. Select the same VLAN policy.
Procedure 5. Create and apply the VSAN Policy
Step 1. Click Select Policy next to VSAN Configuration under Fabric Interconnect A.
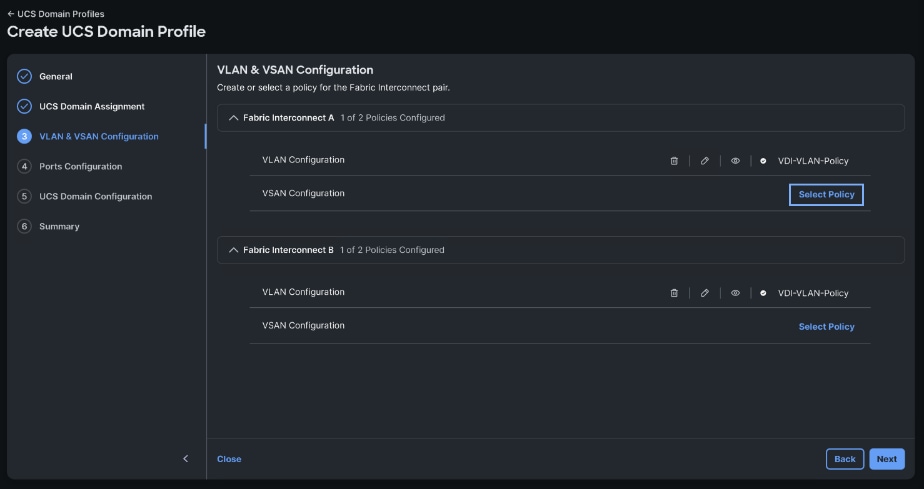
Step 3. Verify correct organization is selected from the drop-down list and provide a name for the policy (for example, VDI-VSANA-Policy).
Step 4. Click Next.
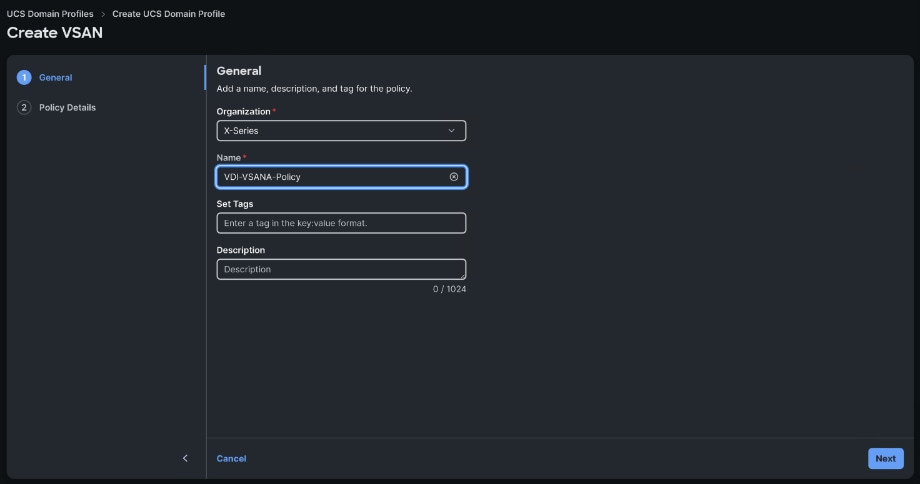
Step 5. Click Add VSAN.
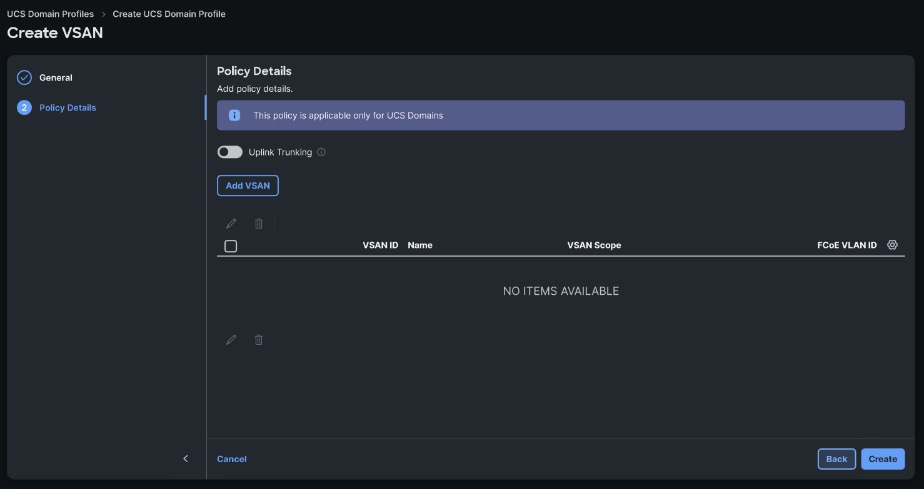
Step 6. Provide a Name, VASN Scope and VSAN ID.
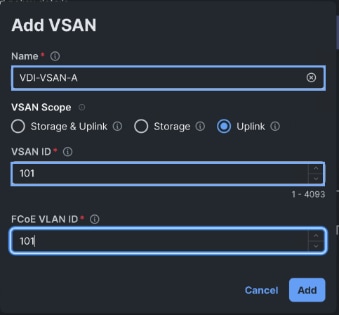
Step 7. In the window on the right, click Create to create a new Policy.
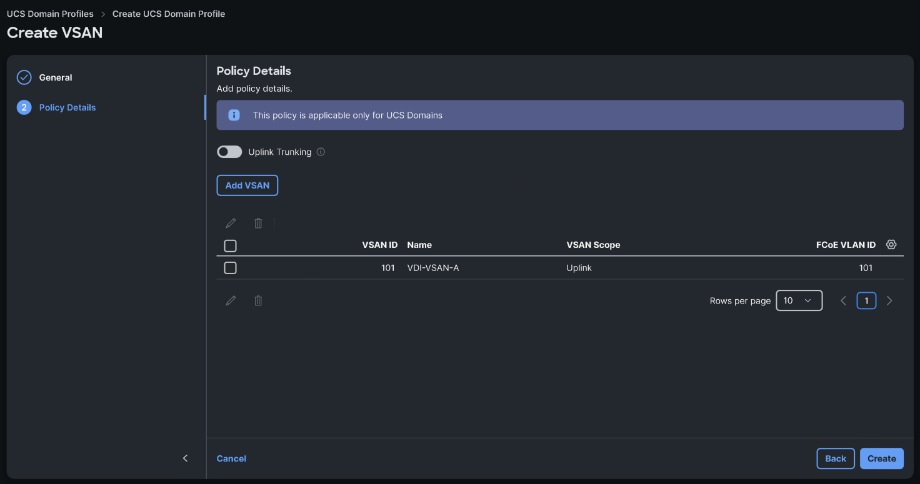
Step 8. Click Select Policy next to VSAN Configuration for Fabric Interconnect B.
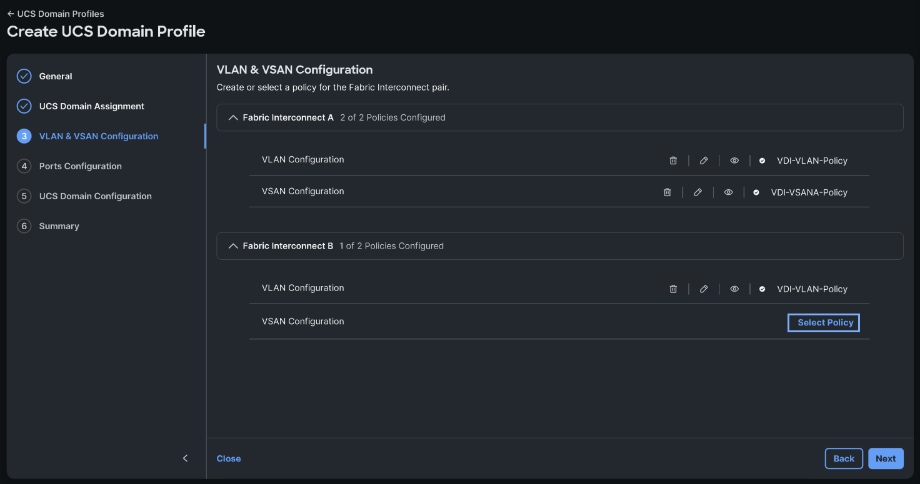
Step 9. Select the same VLAN policy.
Step 10. Click Create New.
Step 11. Verify correct organization is selected from the drop-down list and provide a name for the policy (for example, VDI-VSANB-Policy).
Step 12. Click Next.
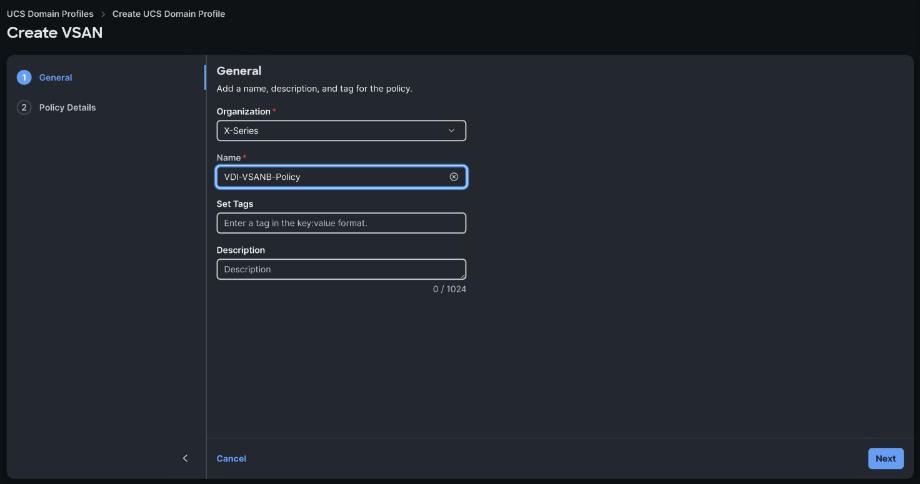
Step 13. Click Add VSAN.
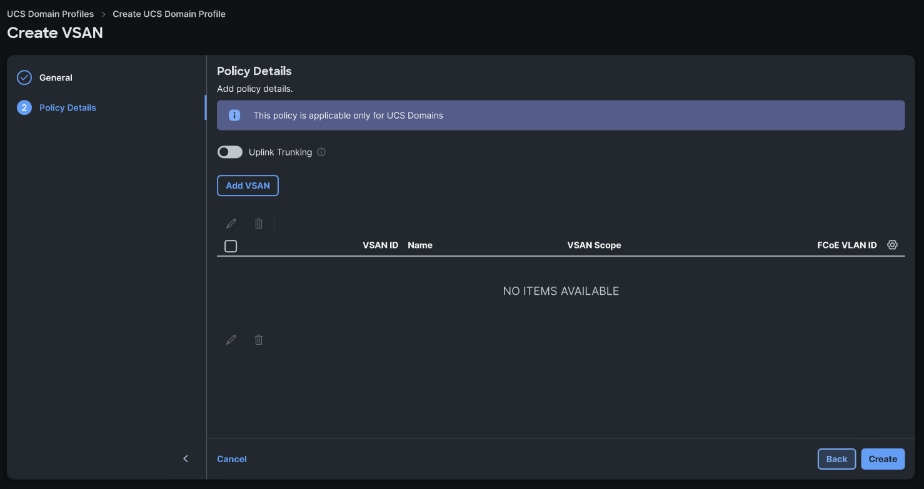
Step 14. Provide a Name and VSAN ID.
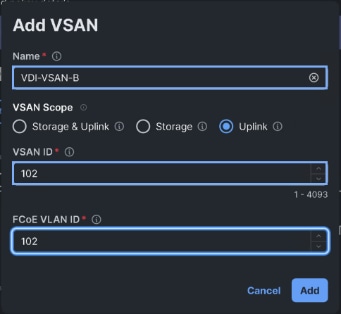
Step 15. In the window on the right, click Create to create a new Policy.
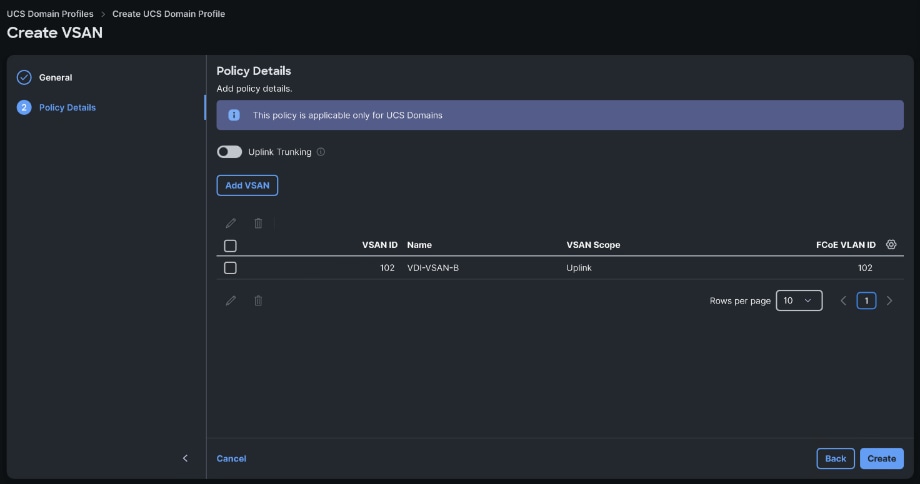
Step 16. Click Next
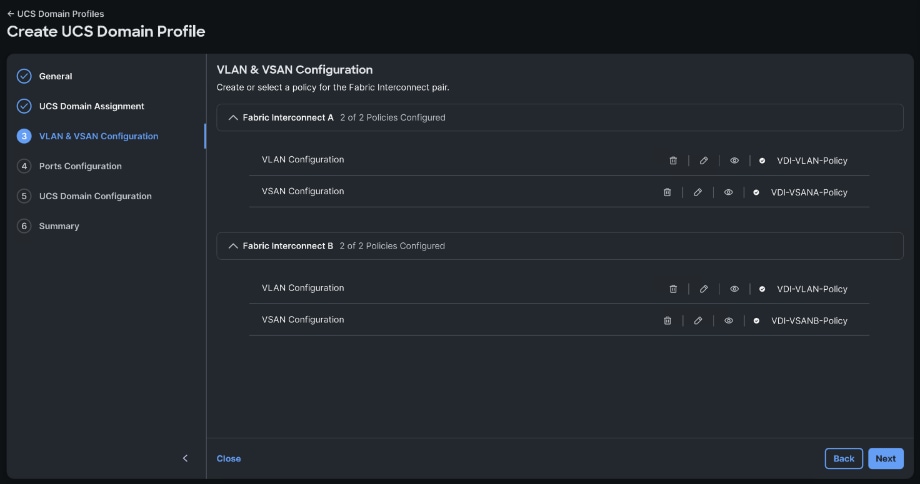
Procedure 6. Configure the Ports on the Fabric Interconnects
Step 1. Click Select Policy for Fabric Interconnect A.
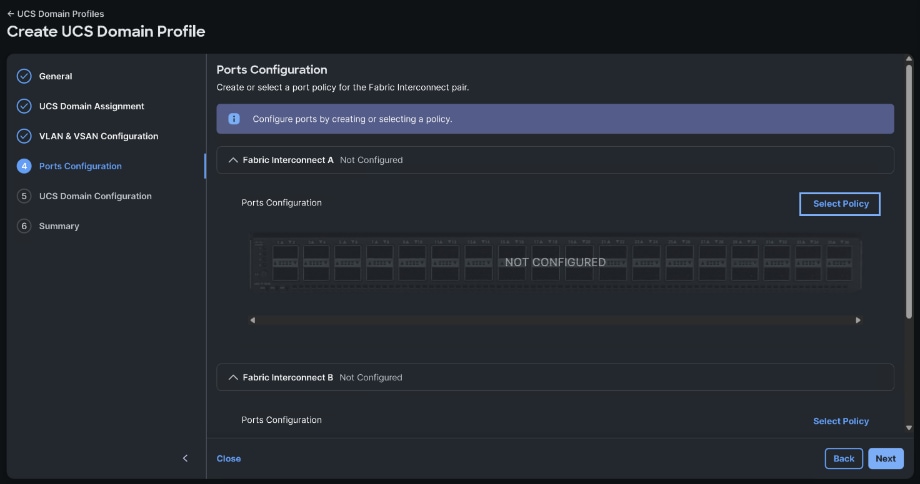
Step 2. Click Create New to define a new port configuration policy.
Note: Use two separate port policies for the fabric interconnects. Using separate policies provide flexibility when port configuration (port numbers or speed) differs between the two FIs.
Step 3. Verify correct organization is selected from the drop-down list (for example, X-Series) and provide a name for the policy (for example, VDI-FIA-Port-Policy).
Step 4. Click Next to pass the Unified Port page.
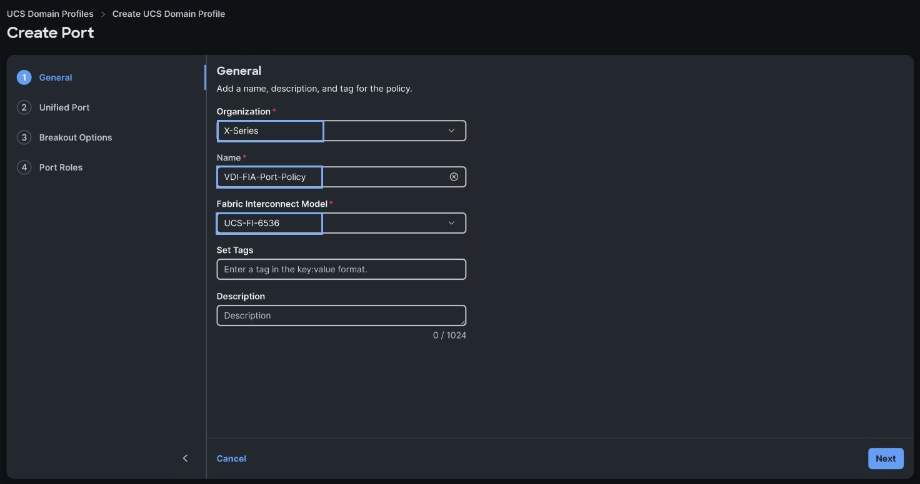
Step 5. Click Next to pass the Breakout Options page.
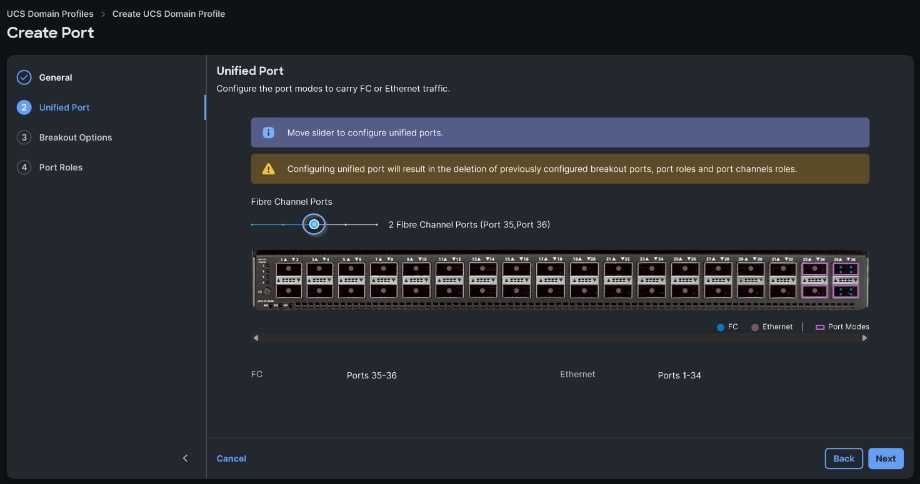
Step 6. Select ports 9-12, click Configure to configure the role.
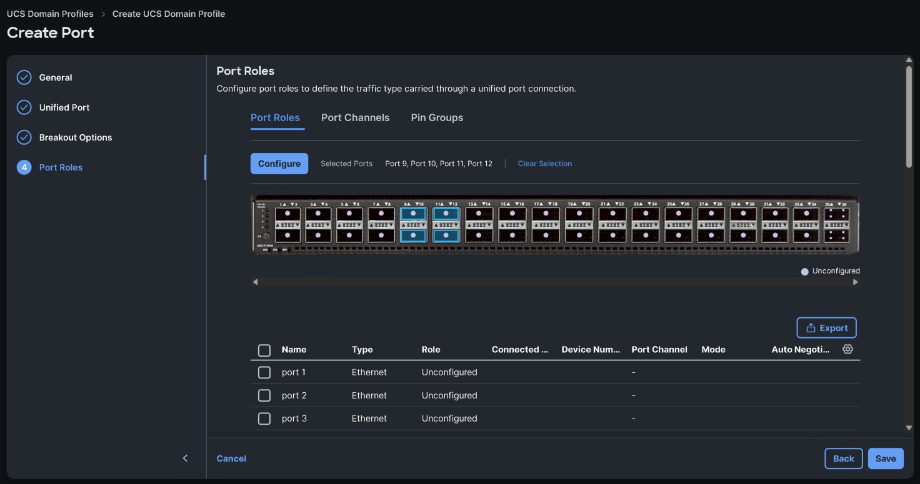
Step 7. From the drop-down list, select Server as the role.
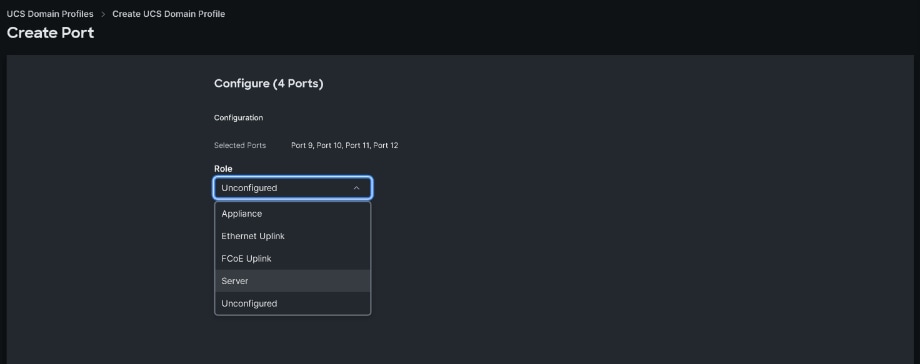
Step 8. Click Save.
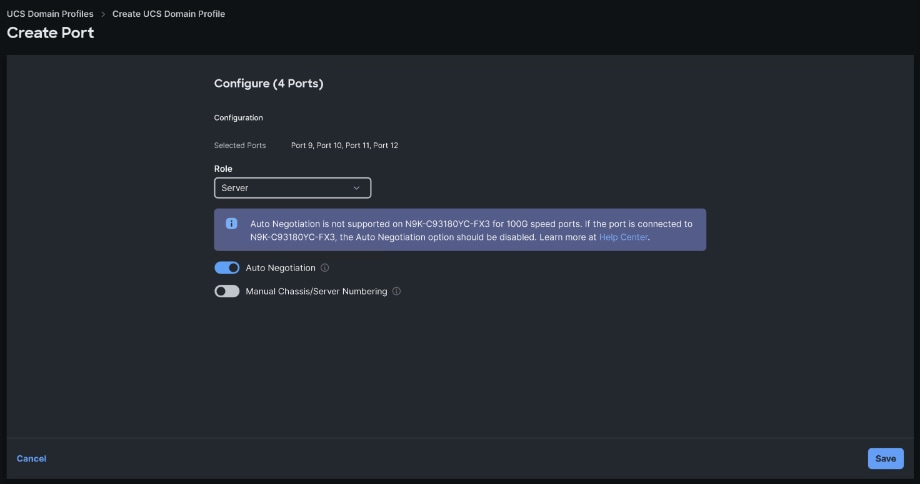
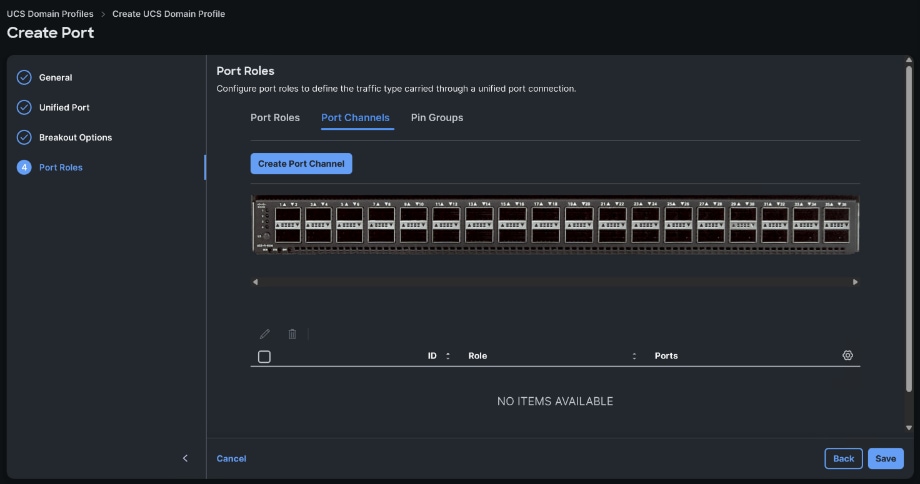
Step 10. Select Ethernet Uplink Port Channel as the role, provide a port-channel ID (for example, 11), and select a value for Admin Speed from drop down menu (for example, Auto).
Note: You can create the Ethernet Network Group, Flow Control, Ling Aggregation or Link control policy for defining disjoint Layer-2 domain or fine tune port-channel parameters. These policies were not used in this deployment and system default values were utilized.
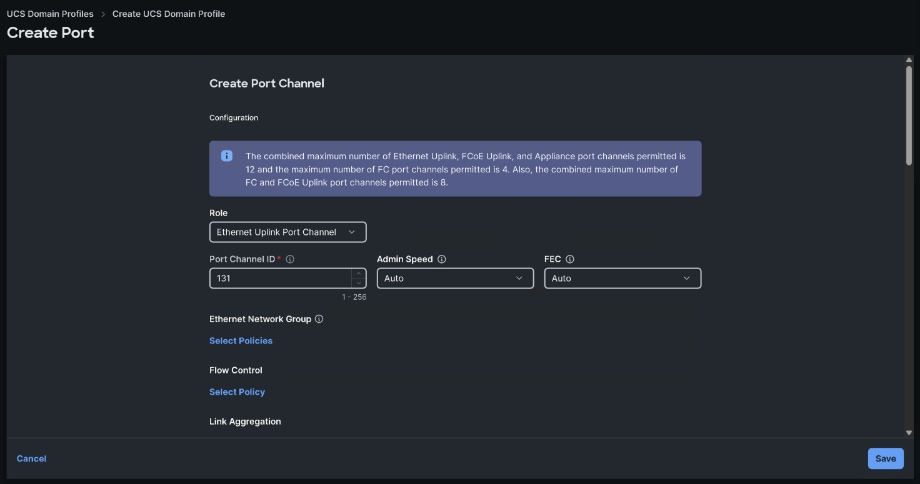
Step 11. Scroll down and select uplink ports from the list of available ports (for example, ports 31-32).
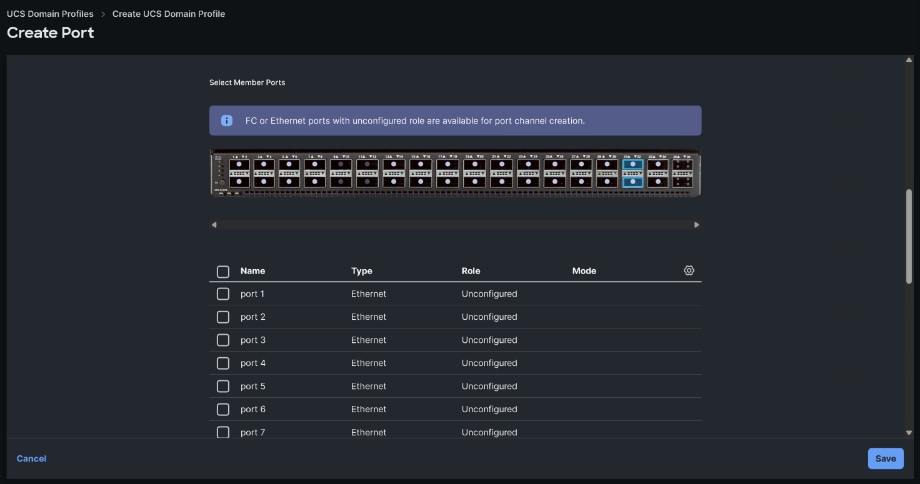
Step 12. Click Save.
Step 13. Configure the FC uplink port channel by selecting the Port Channel in the main pane and then clicking Create Port Channel.
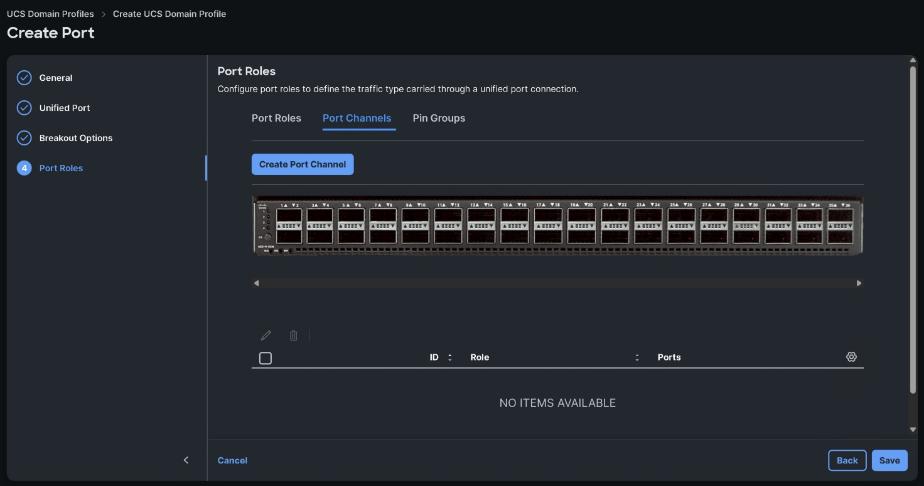
Step 14. Select FC Uplink Port Channel as the role, provide a port-channel ID (for example, 135), and select a value for Admin Speed from drop-down list (for example, 32Gbps), and select uplink ports from the list of available ports (for example, port 35(1-4) and 36(1-4)).
Step 15. Click Save.
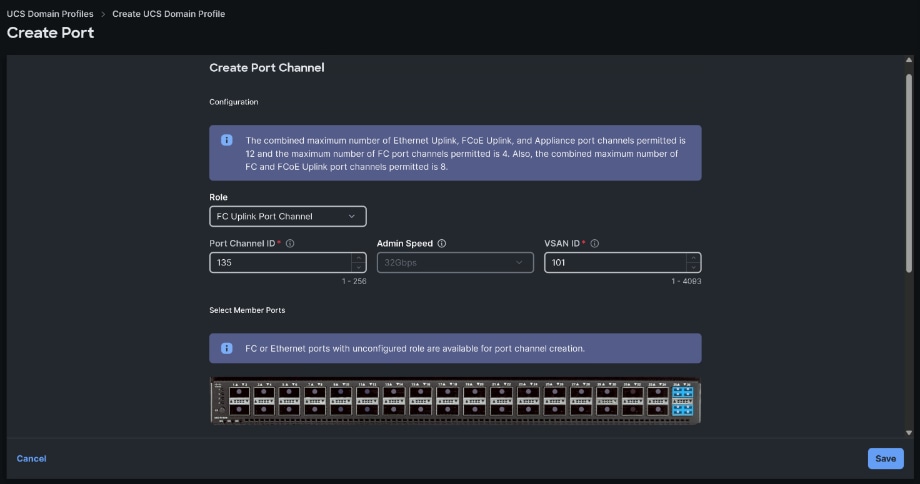
Step 16. Click Save to create the port policy for Fabric Interconnect A.
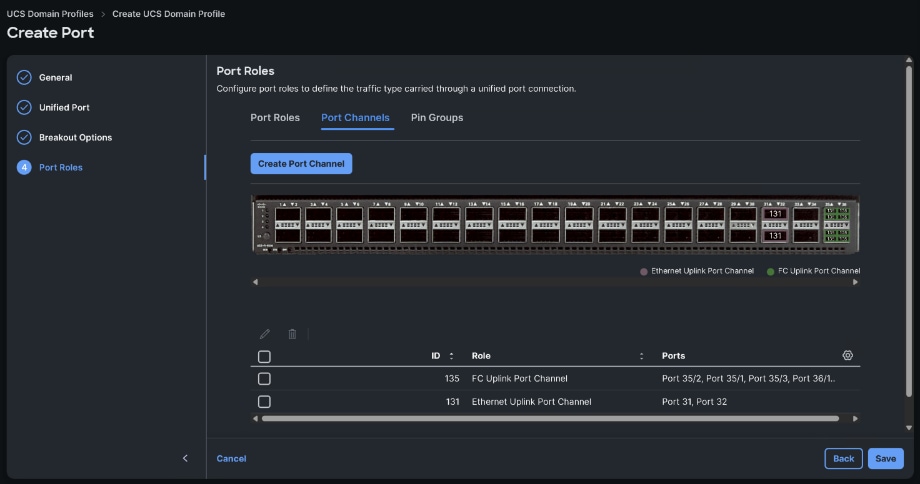
Step 17. Repeat steps 1 - 16 to create the port policy for Fabric Interconnect B.
Step 18. Click Next to continue to UCS Domain Configuration.
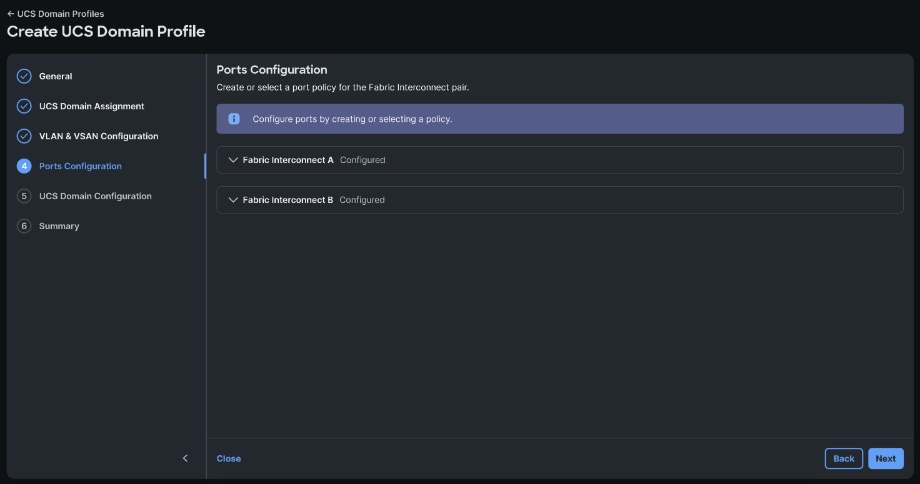
Cisco UCS Domain Configuration
Note: Under UCS domain configuration, additional policies can be configured to setup NTP, Syslog, DNS settings, SNMP, QoS and UCS operating mode (end host or switch mode). For this deployment, three policies (NTP, Network Connectivity and System QoS) will be configured.
Procedure 1. Configure NTP Policy for the Cisco UCS Domain
Step 1. Click Select Policy next to NTP and then click Create New.
Step 2. Verify correct organization is selected from the drop-down list (for example, X-Series) and provide a name for the policy (for example, VDI-NTPPol).
Step 3. Click Next.
Step 4. Enable NTP, provide the NTP server IP addresses, and select the Timezone from the drop-down list.
Step 5. If required, add a second NTP server by clicking + next to the first NTP server IP address.
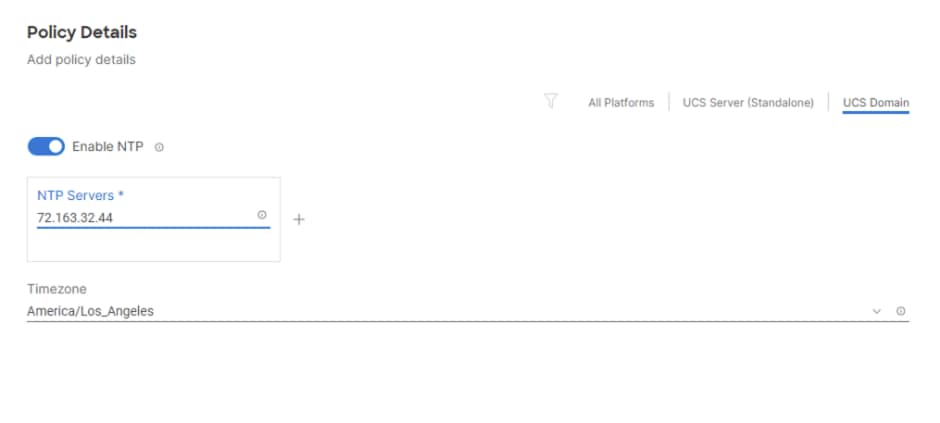
Step 6. Click Create.
Procedure 2. Configure Network Connectivity Policy
Note: To define the Doman Name Service (DNS) servers for Cisco UCS, configure network connectivity policy.
Step 1. Click Select Policy next to Network Connectivity and then click Create New.
Step 2. Verify correct organization is selected from the drop-down list (for example, X-Series) and provide a name for the policy (for example, VDI-NetConn-Pol).
Step 3. Provide DNS server IP addresses for Cisco UCS.
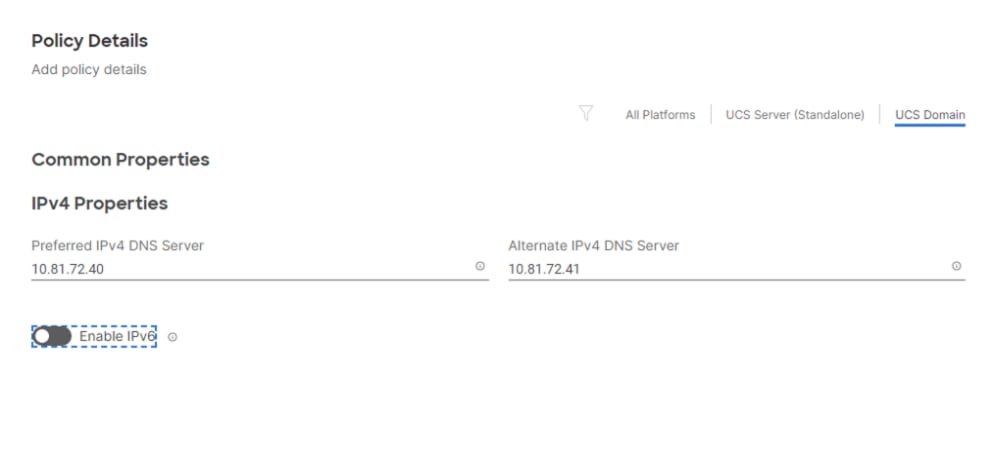
Step 4. Click Create.
Procedure 3. Configure System QoS Policy
To define the QoS settings for Cisco UCS, configure System QoS policy.
Step 1. Click Select Policy next to System QoS* and click Create New.
Step 2. Verify correct organization is selected from the drop-down list (for example, X-Series) and provide a name for the policy (for example, VDI-QoSPol).
Step 3. Click Next.
Step 4. Change the MTU for Best Effort class to 9216.
Step 5. Keep the default selections or change the parameters if necessary.
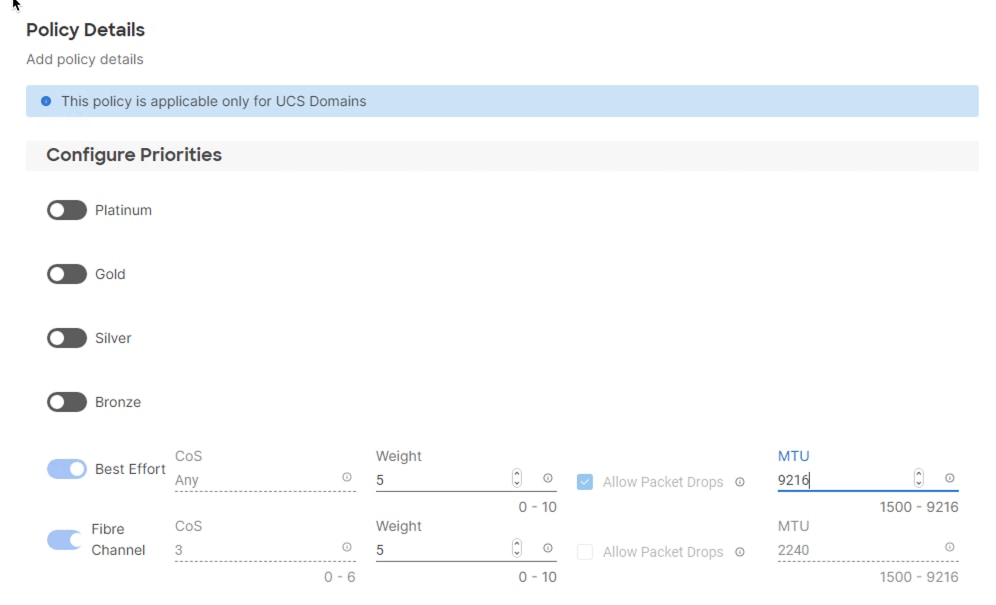
Step 6. Click Create.
Step 7. Click Next.
Step 1. Verify all the settings including the fabric interconnect settings, by expanding the settings and make sure that the configuration is correct.
Procedure 5. Deploy the Cisco UCS Domain Profile
Note: After verifying the domain profile configuration, deploy the Cisco UCS profile.
Step 1. From the UCS domain profile Summary view, click Deploy.
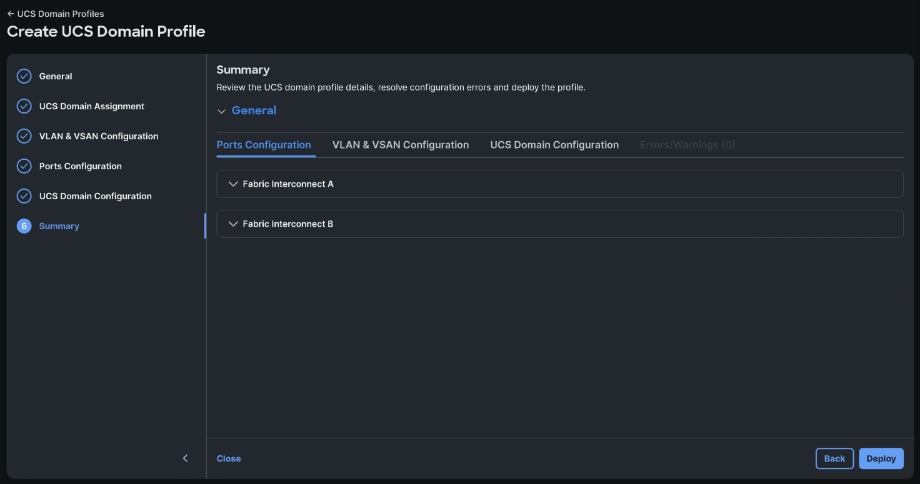
Step 2. Acknowledge any warnings and click Deploy again.
The system will take some time to validate and configure the settings on the fabric interconnects. Log into the console servers to see when the Cisco UCS fabric interconnects have finished configuration and are successfully rebooted.
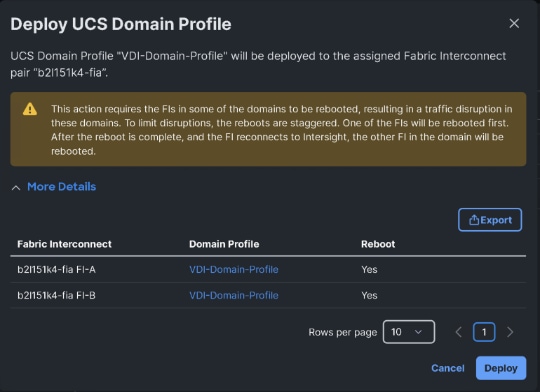
Procedure 6. Verify Cisco UCS Domain Profile Deployment
When the Cisco UCS domain profile has been successfully deployed, the Cisco UCS chassis and the Compute Nodes should be successfully discovered.
Note: It takes a while to discover the Compute Nodes for the first time. Watch the number of outstanding tasks in Cisco Intersight:

Step 1. Log into Cisco Intersight. Under CONFIGURE > Profiles > UCS Domain Profiles verify that the domain profile has been successfully deployed.
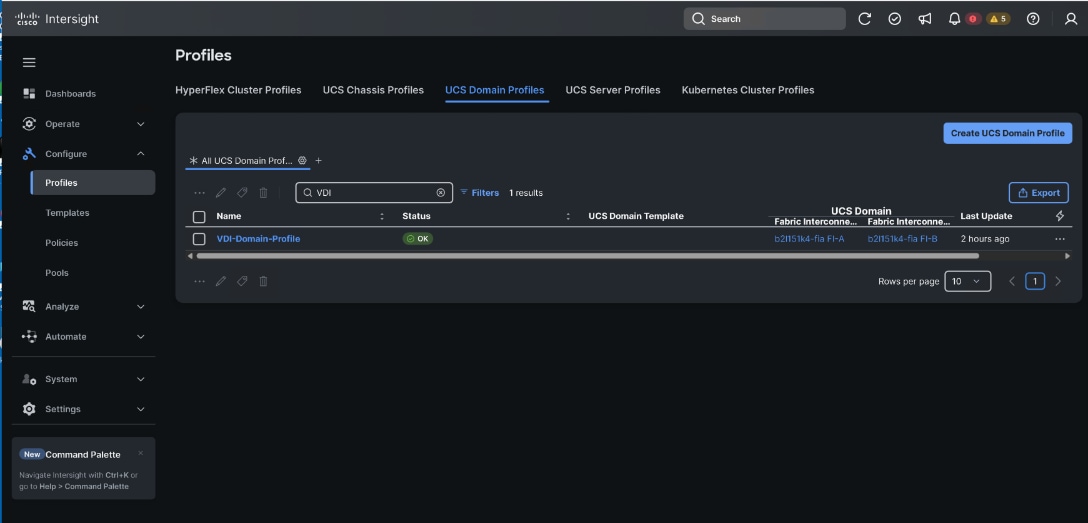
Step 2. Verify that the servers have been successfully discovered and are visible under OPERATE > Servers.
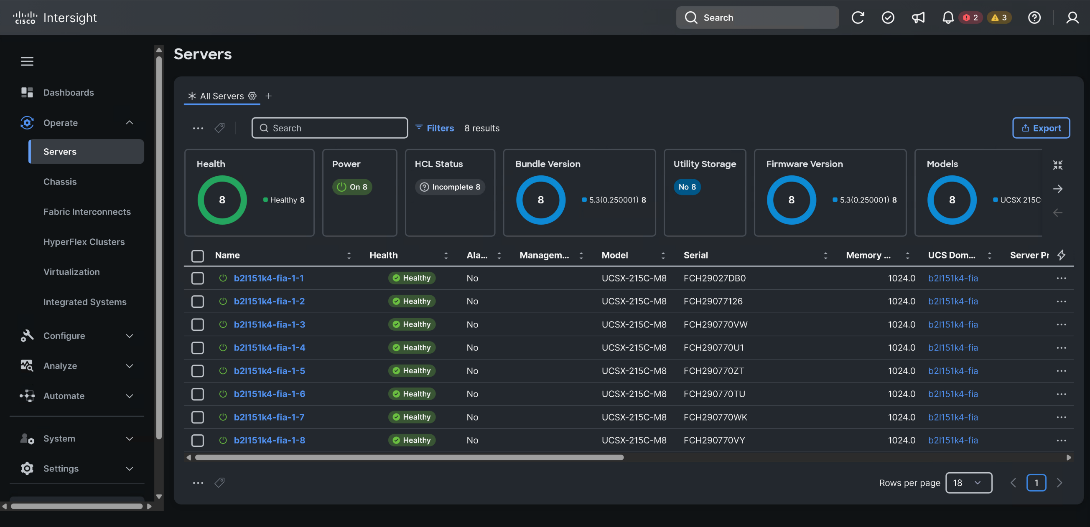
Configure Server Profile Template
In the Cisco Intersight platform, a server profile enables resource management by simplifying policy alignment and server configuration. The server profiles are derived from a server profile template. The server profile template and its associated policies can be created using the server profile template wizard. After creating server profile template, you can derive multiple consistent server profiles from the template.
In this deployment, four vNICs and two vHBAs are configured. These devices are manually placed as listed in Table 14.
Table 14. vHBA and vNIC placement for FC connected storage
| vNIC/vHBA Name |
Slot |
Switch ID |
PCI Order |
| vHBA-A |
MLOM |
A |
0 |
| vHBA-B |
MLOM |
B |
1 |
| 01-vSwitch0-A |
MLOM |
A |
2 |
| 02-vSwitch0-B |
MLOM |
B |
3 |
| 03-VDS0-A |
MLOM |
A |
4 |
| 04-VDS0-B |
MLOM |
B |
5 |
Note: Two vHBAs (vHBA-A and vHBA-B) are configured to support FC boot from SAN.
Procedure 1. Configure a Server Profile Template
Step 1. Log into Cisco Intersight.
Step 2. Go to CONFIGURE > Templates and click Create UCS Server Profile Template.
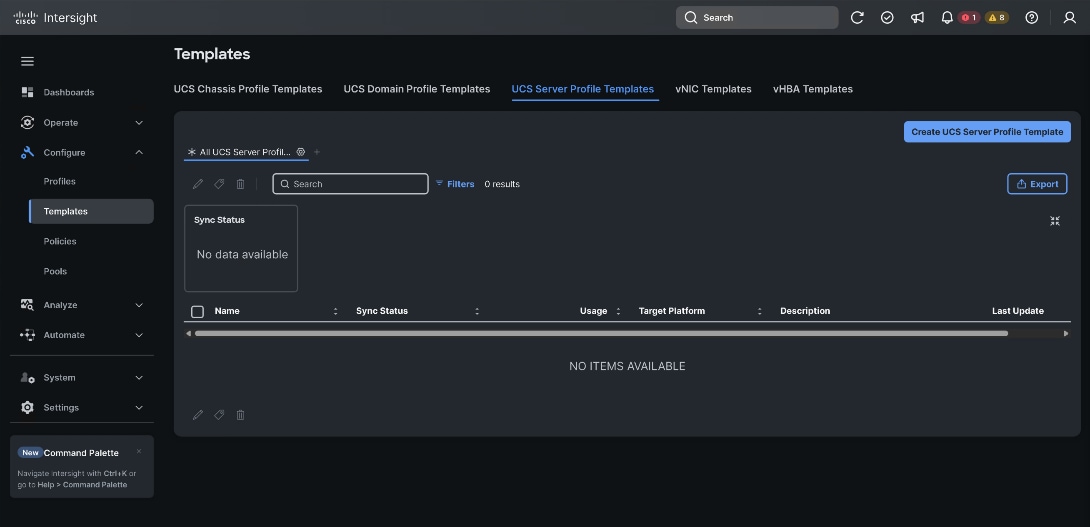
Step 3. Select the organization from the drop-down list (for example, x-series).
Step 4. Provide a name for the server profile template. The name used in this deployment is FlexPod-VDI-M8-ServerProf-Template.
Step 5. Click UCS Server (FI-Attached).
Step 6. Provide an optional description.
Step 7. Click Next.
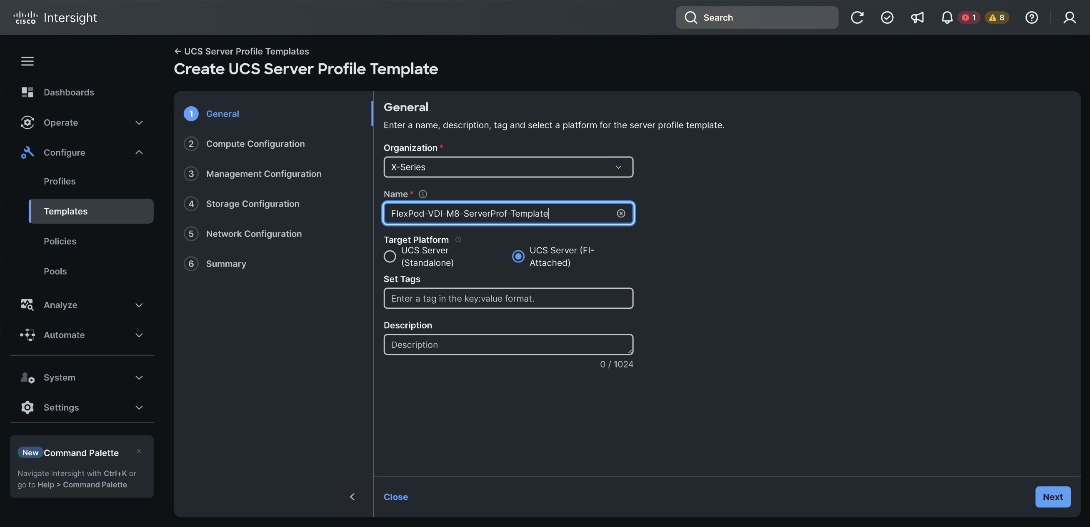
Procedure 2. Configure UUID Pool
Step 1. Click Select Pool under UUID Pool.
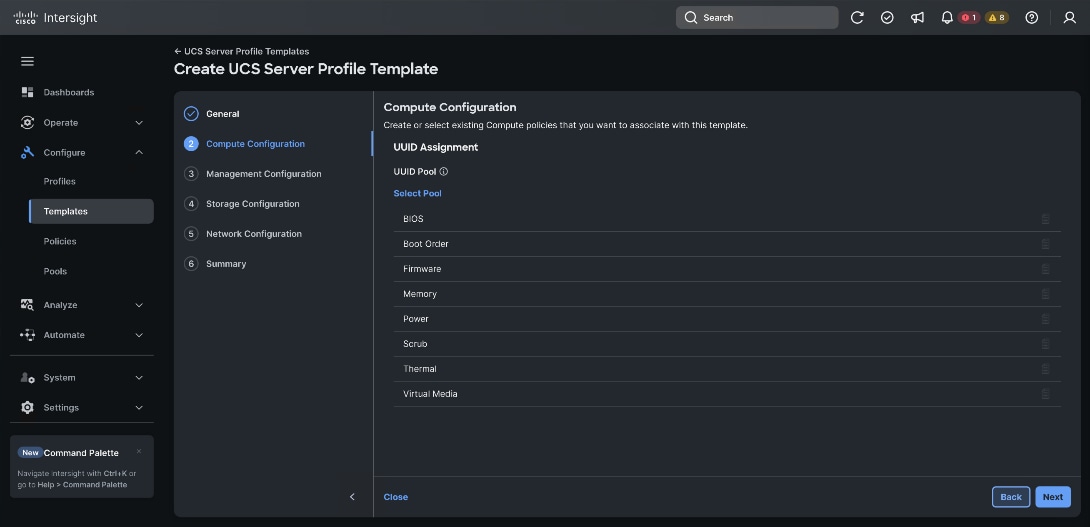
Step 2. Click Create Pool.
Step 3. Verify correct organization is selected from the drop-down list (for example, X-Series) and provide a name for the UUID Pool (for example, FlexPod-VDI-UUID-Pool).
Step 4. Provide an optional Description and click Next.
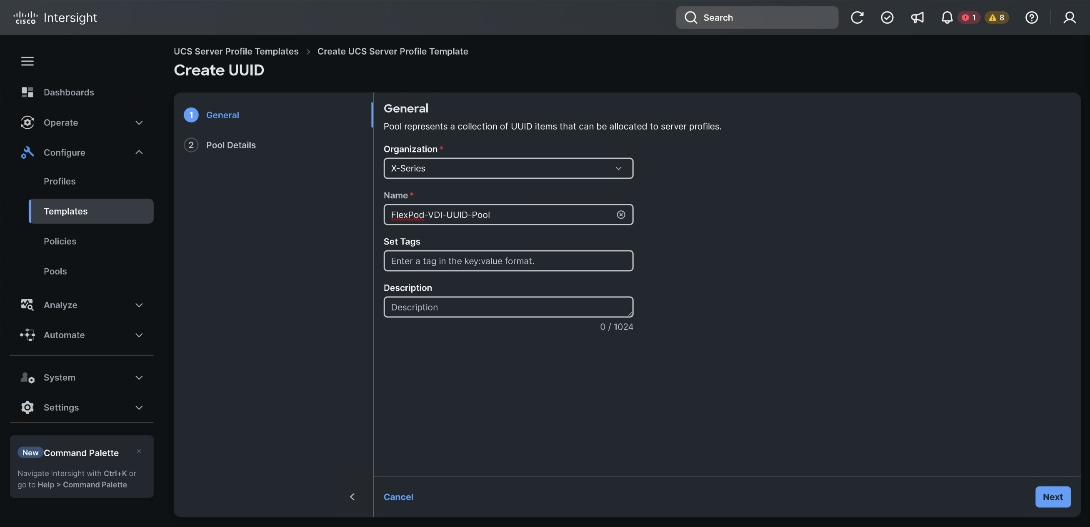
Step 5. Provide a UUID Prefix (for example, a random prefix of 33FB3F9C-BF35-4BDE was used).
Step 6. Add a UUID block.
Step 7. Click Create.
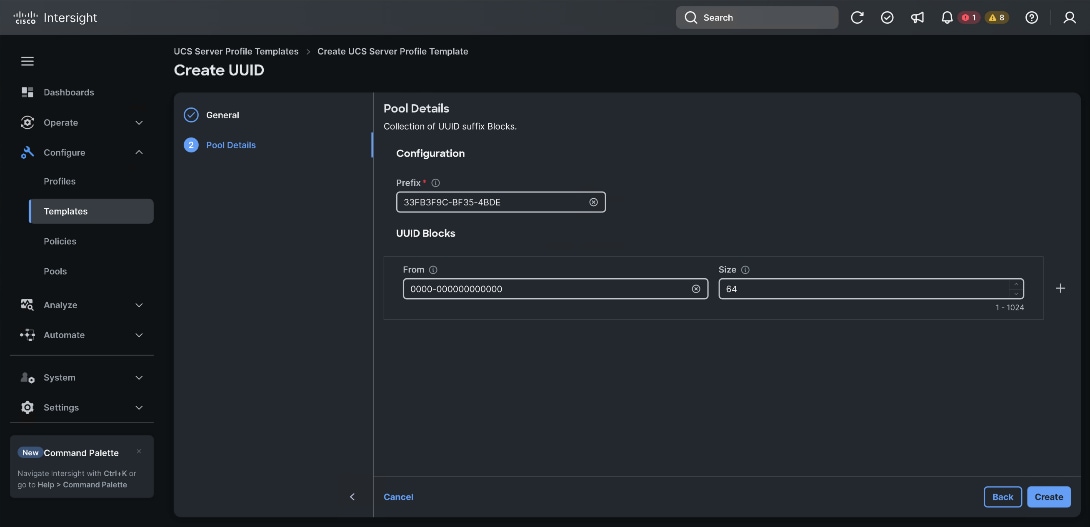
Procedure 3. Configure BIOS Policy
Step 1. Click Select Policy next to BIOS and click Create New.

Step 2. Verify correct organization is selected from the drop-down list (for example, X-Series) and provide a name for the policy (for example, FlexPod-VDI-X215CM8-BIOS-Policy).
Step 3. Click Next.
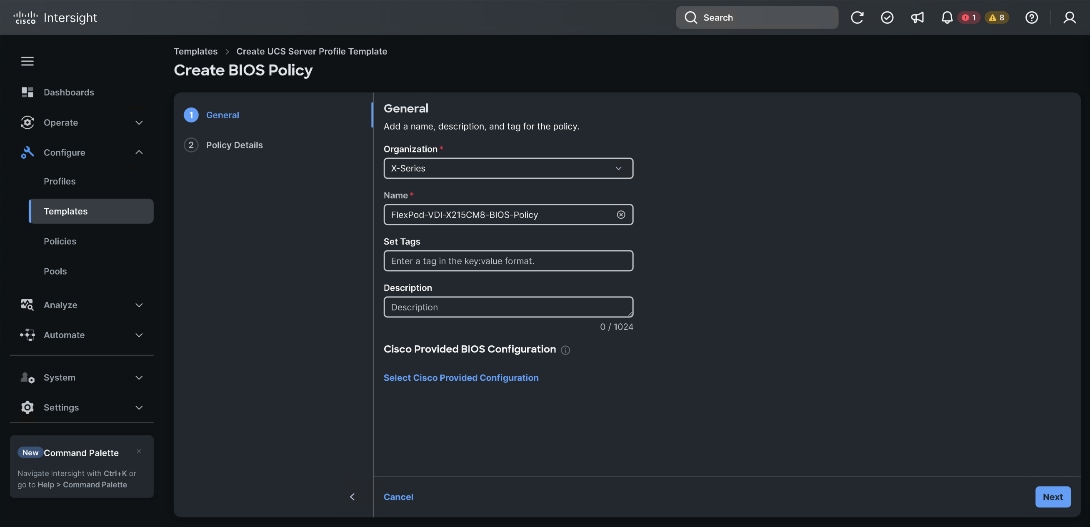
Step 4. From the Policy Details screen, select appropriate values for the BIOS settings. In this deployment, the BIOS values were selected based on recommendations in the performance tuning guide for Cisco UCS M8 BIOS: Performance Tuning for Cisco UCS M8 Platforms with AMD EPYC 4th Gen and 5th Gen Processorsl.
- Power and Performance > CPPC: enabled
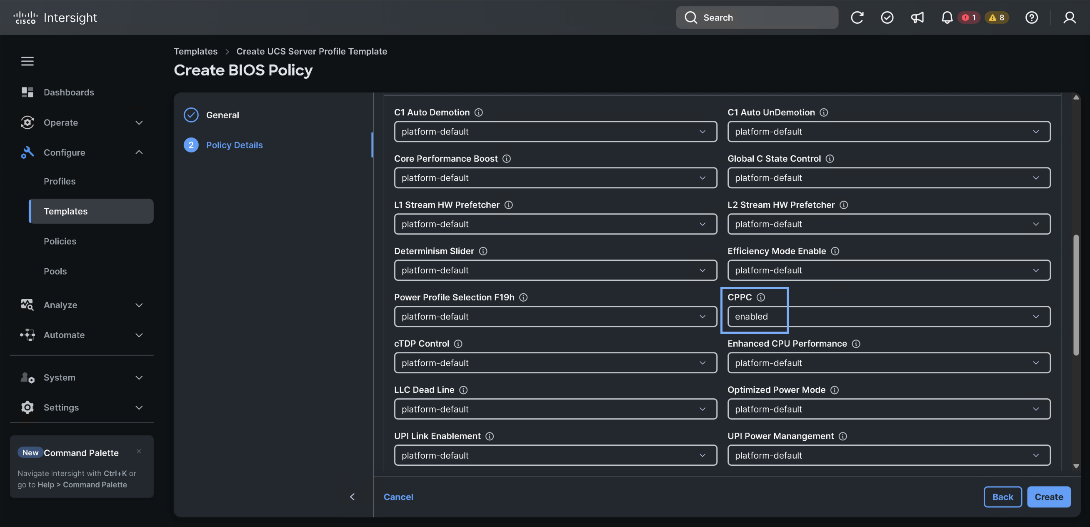
Step 5. Click Create.
Procedure 4. Configure Boot Order Policy
Step 1. Click Select Policy next to BIOS and click Create New.

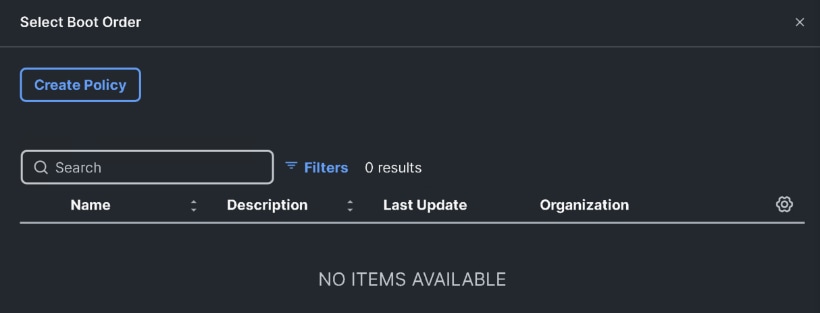
Step 2. Verify correct organization is selected from the drop-down list (for example, X-Series) and provide a name for the policy (for example, FlexPod-VDI-X215CM8-BootOrder-Policy).
Step 3. Click Next.
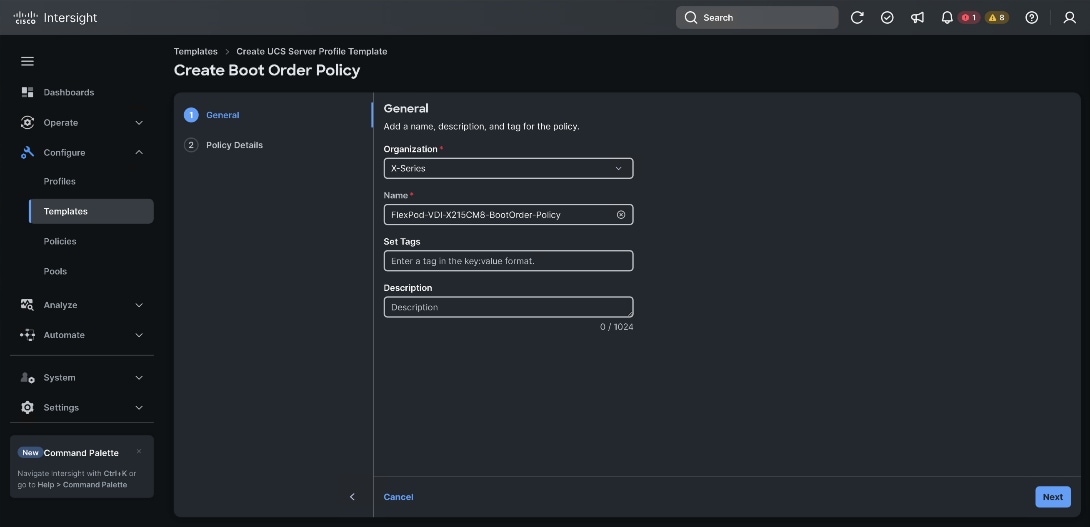
From the Policy Details screen, select appropriate values for the BIOS settings. In this deployment, the BIOS values were selected based on recommendations in the performance tuning guide for Cisco UCS M8.
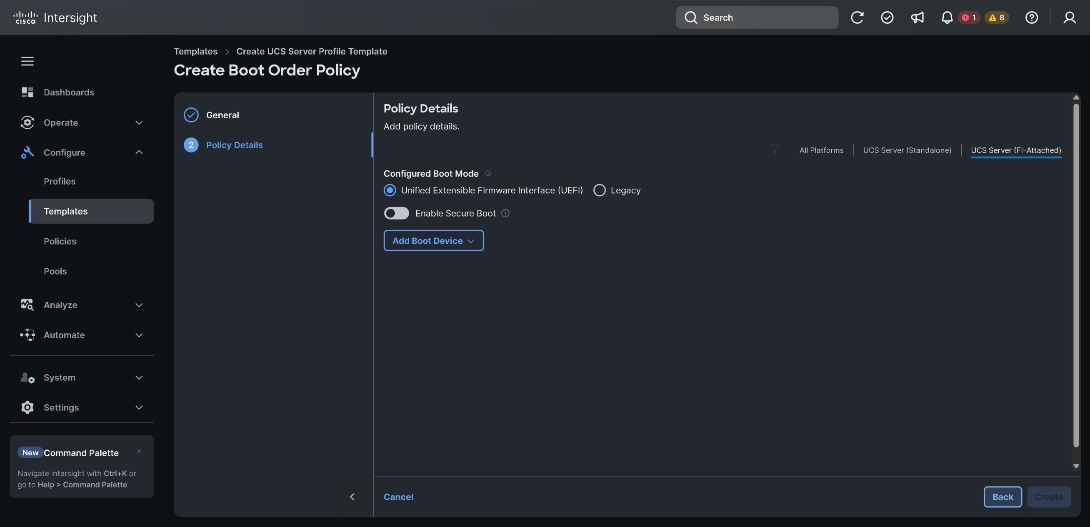
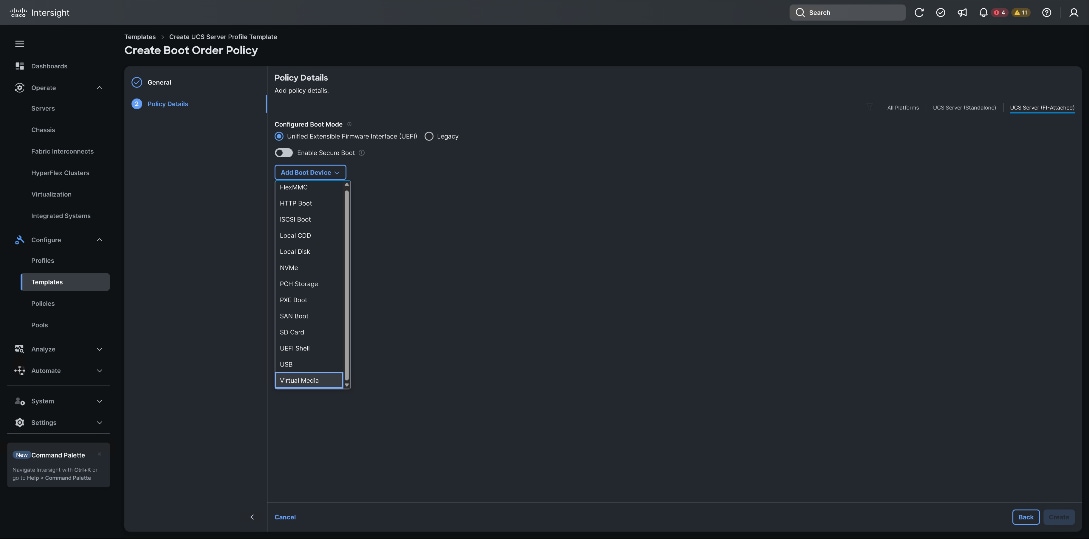
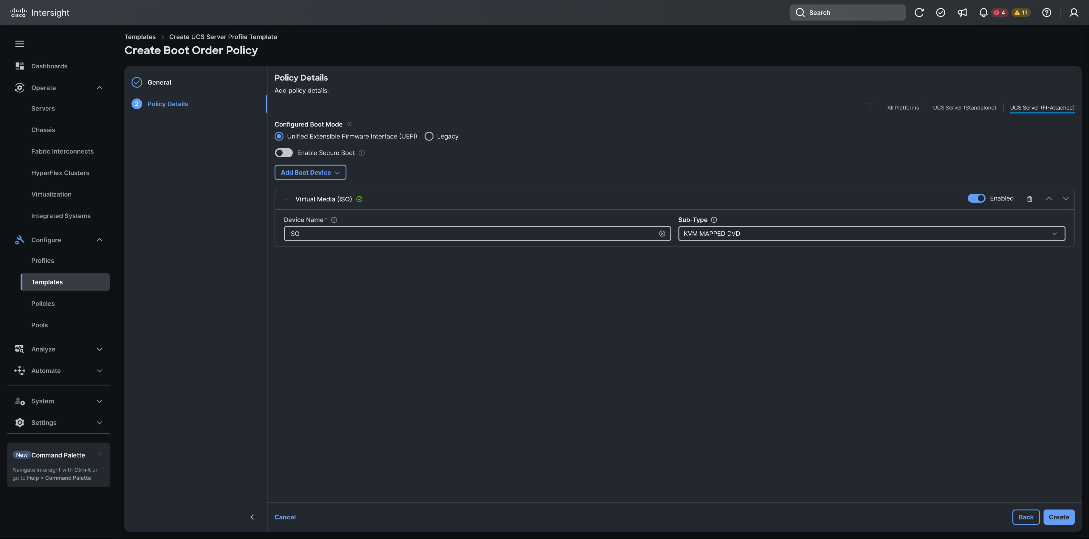
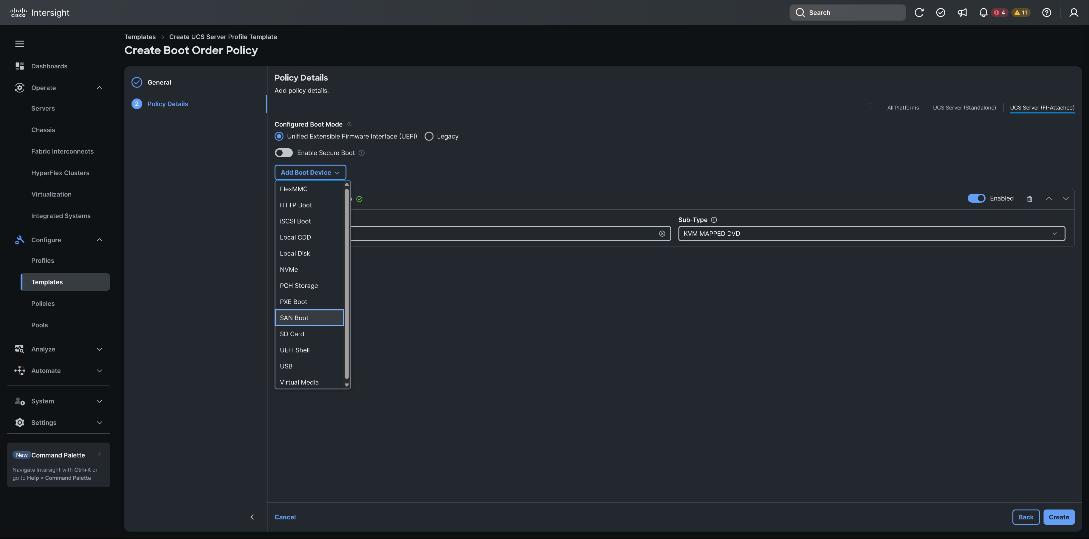
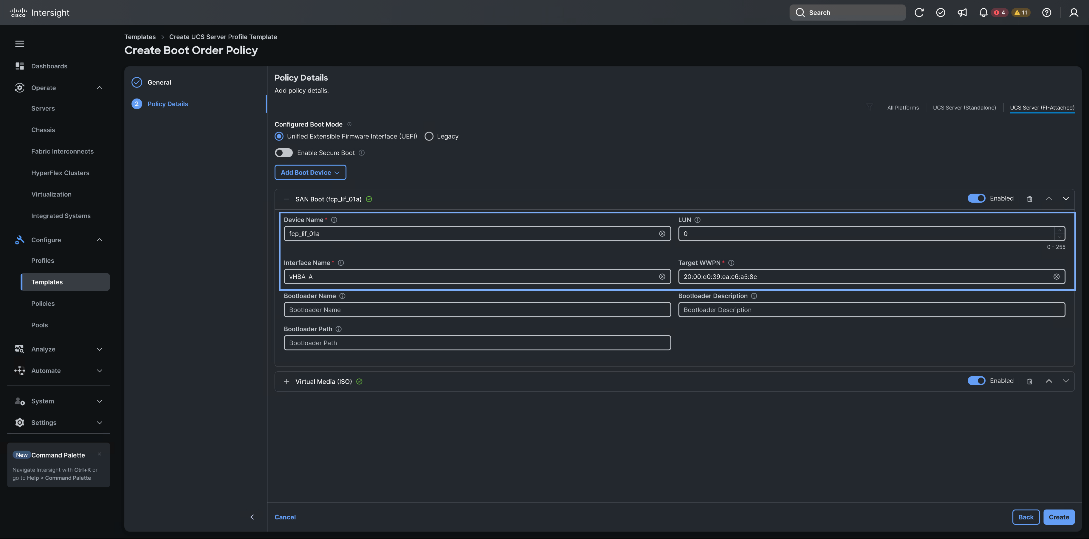
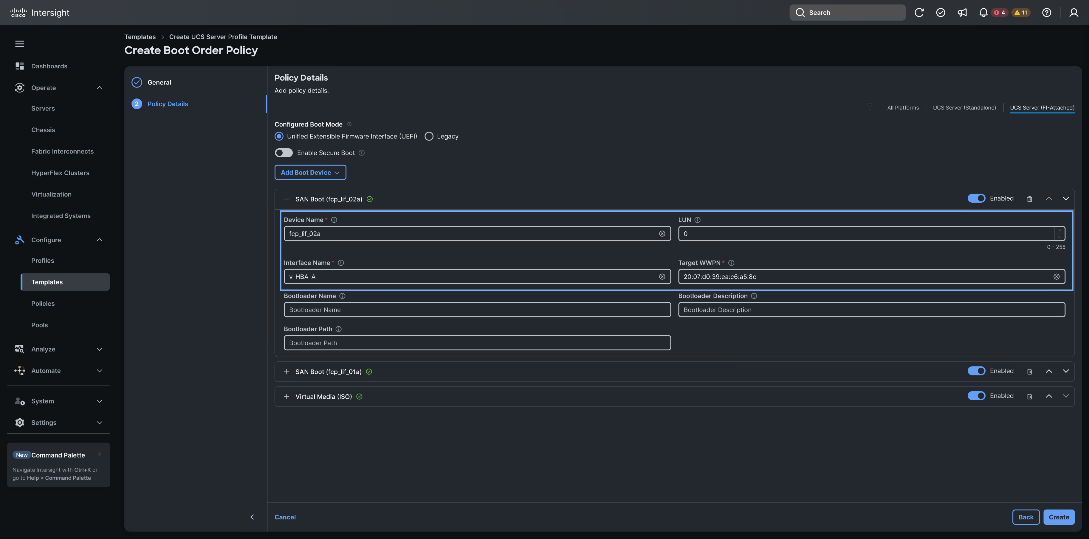
Step 4. Click Create.
Step 5. Click Next to go to Management Configuration.
Three policies will be added to the management configuration:
● IMC Access to define the pool of IP addresses for compute node KVM access
● IPMI Over LAN to allow Intersight to manage IPMI messages
● Local User to provide local administrator to access KVM
Procedure 1. Configure Cisco IMC Access Policy
Step 1. Click Select Policy.
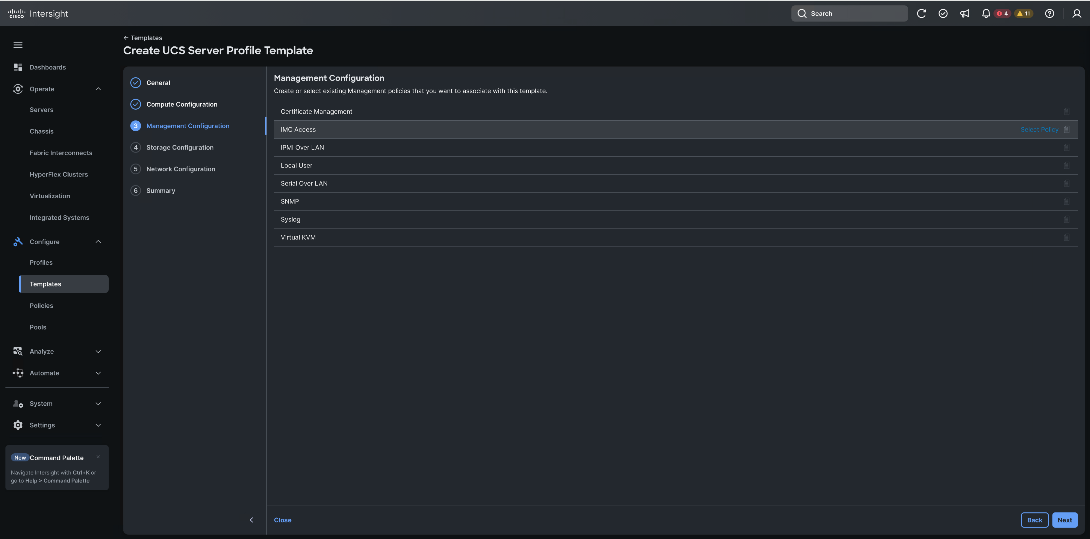
Step 2. Click Create Policy.
Step 3. Verify correct organization is selected from the drop-down list (for example, X-Series) and provide a name for the policy (for example, FlexPod-VDI-IMC-Access-Policy).
Step 4. Click Next.
Note: You can select in-band management access to the compute node using an in-band management VLAN (for example, VLAN 30) or out-of-band management access via the Mgmt0 interfaces of the FIs. KVM Policies like SNMP, vMedia and Syslog are currently not supported via Out-Of-Band and will require an In-Band IP to be configured. Since these policies were not configured in this deployment, out-of-band management access was configured so that KVM access to compute nodes is not impacted by any potential switching issues in the fabric.
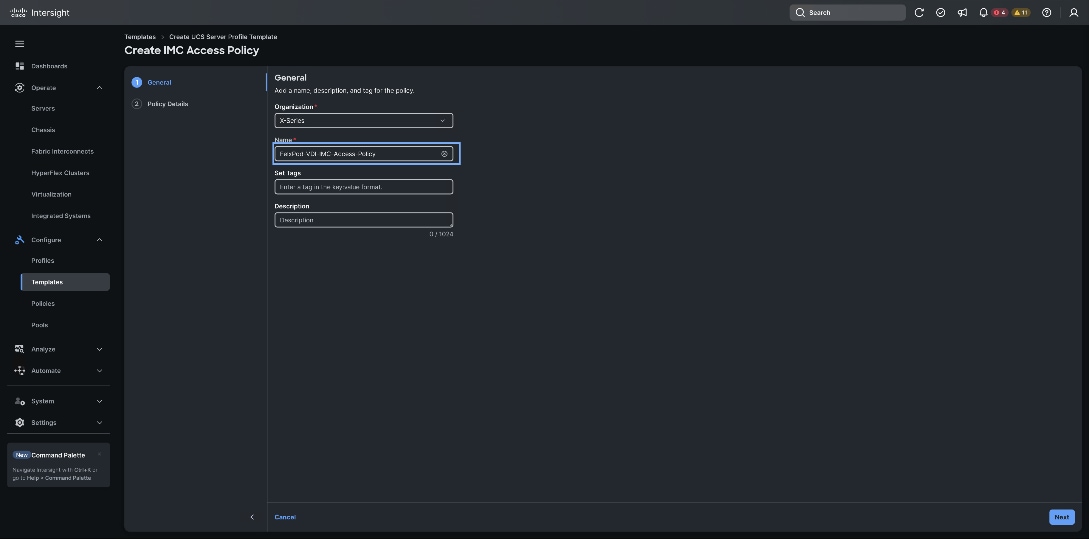
Step 5. Click UCS Server (FI-Attached).
Step 6. Enable Out-Of-Band Configuration.
Step 7. Under IP Pool, click Select IP Pool and then click Create New.
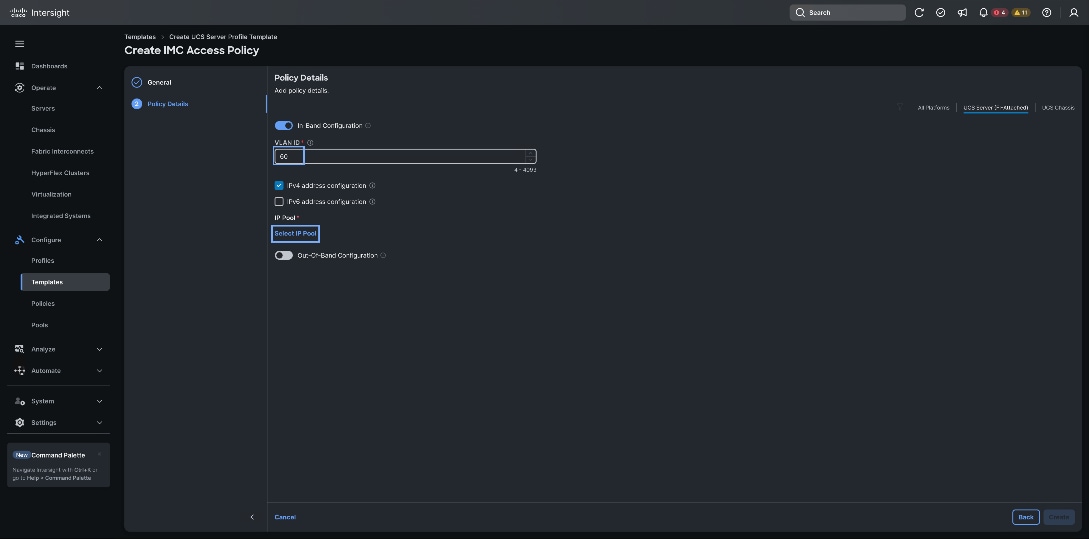
Step 8. Select Create Pool.
Step 9. Verify the correct organization is selected from the drop-down list (for example, X-Series) and provide a name for the policy (for example, FlexPod-VDI-IMC-IB-IPPool). Click Next.
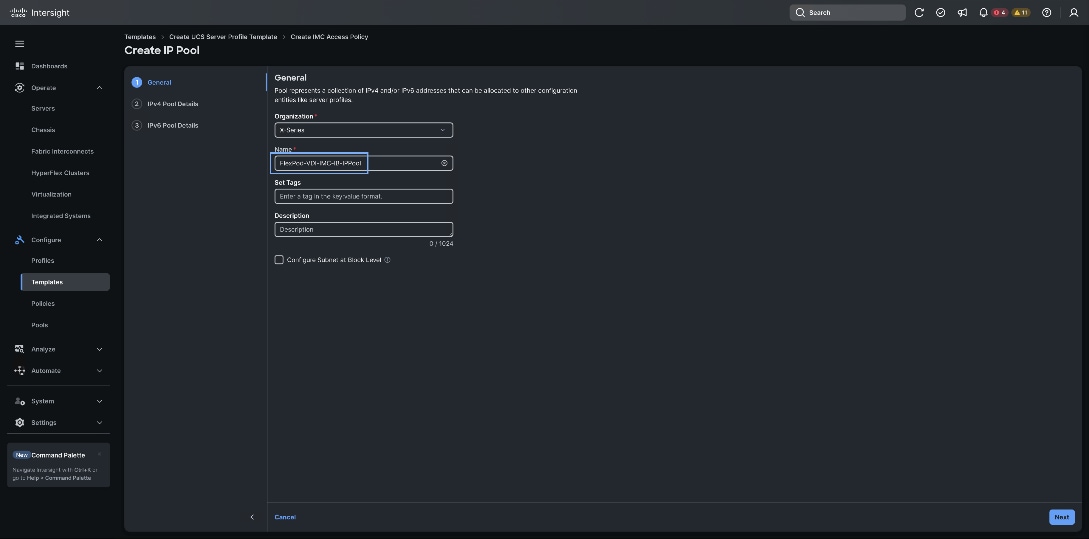
Step 10. Select Configure IPv4 Pool and provide the information to define a pool for KVM IP address assignment including an IP Block.
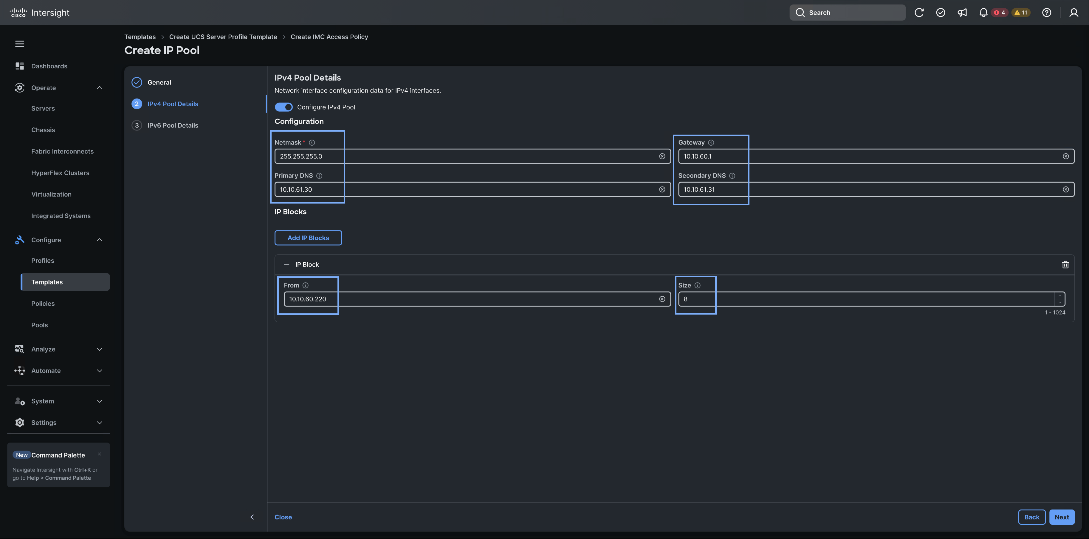
Note: The management IP pool subnet should be accessible from the host that is trying to open the KVM connection. In the example shown here, the hosts trying to open a KVM connection would need to be able to route to 10.81.72.0/24 subnet.
Step 11. Click Next.
Step 12. Deselect Configure IPv6 Pool.
Step 13. Click Create to finish configuring the IP address pool.
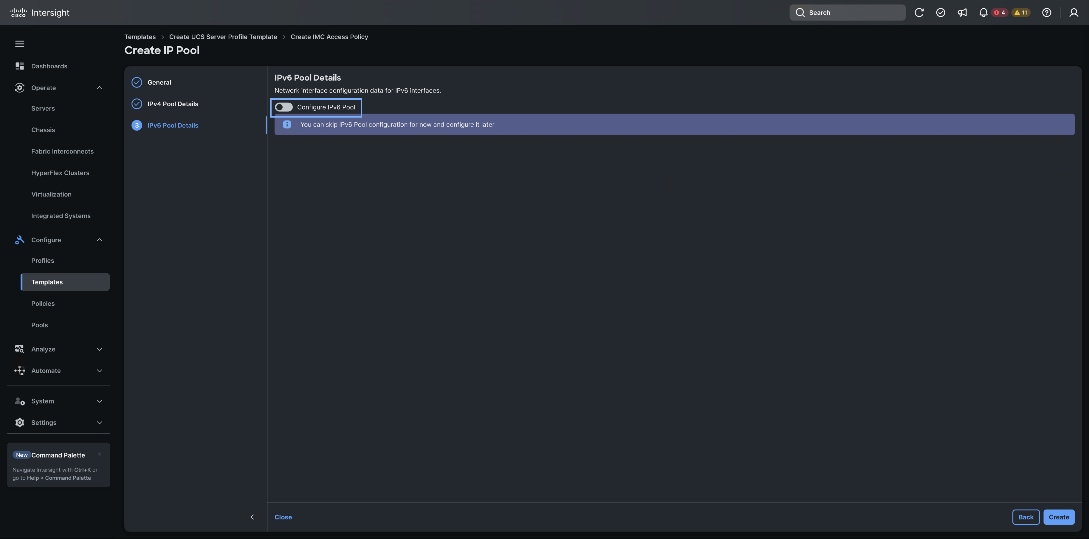
Step 14. Click Create to finish configuring the IMC access policy.
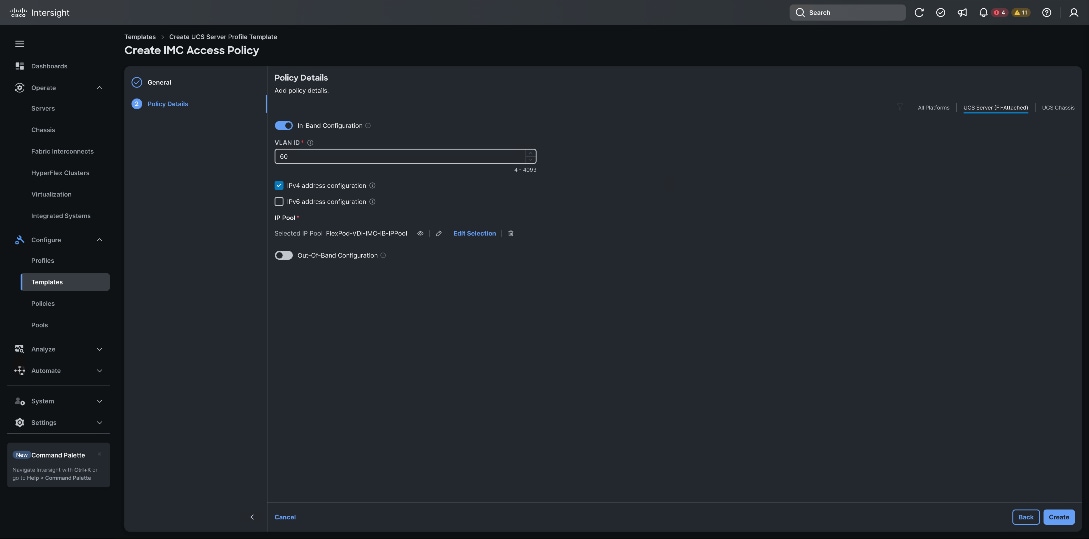
Procedure 2. Configure IPMI Over LAN Policy
Step 1. Click Select Policy and then click Create New.

Step 2. Create New.
Step 3. Verify correct organization is selected from the drop-down list (for example, X-Series) and provide a name for the policy (for example, FlexPod-IPMIoLAN). Click Next.
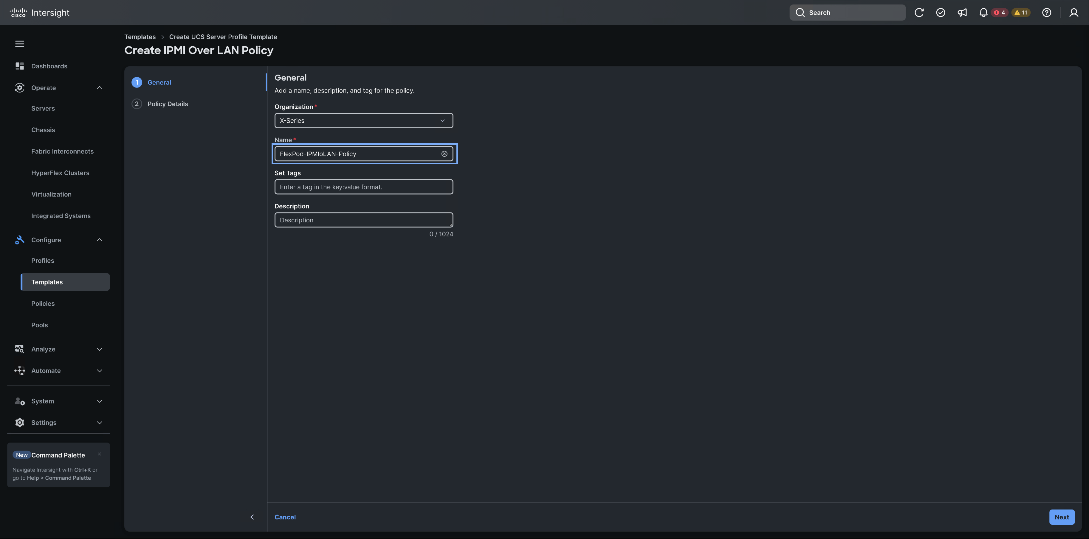
Step 4. Turn on Enable IPMI Over LAN.
Step 5. Click Create.
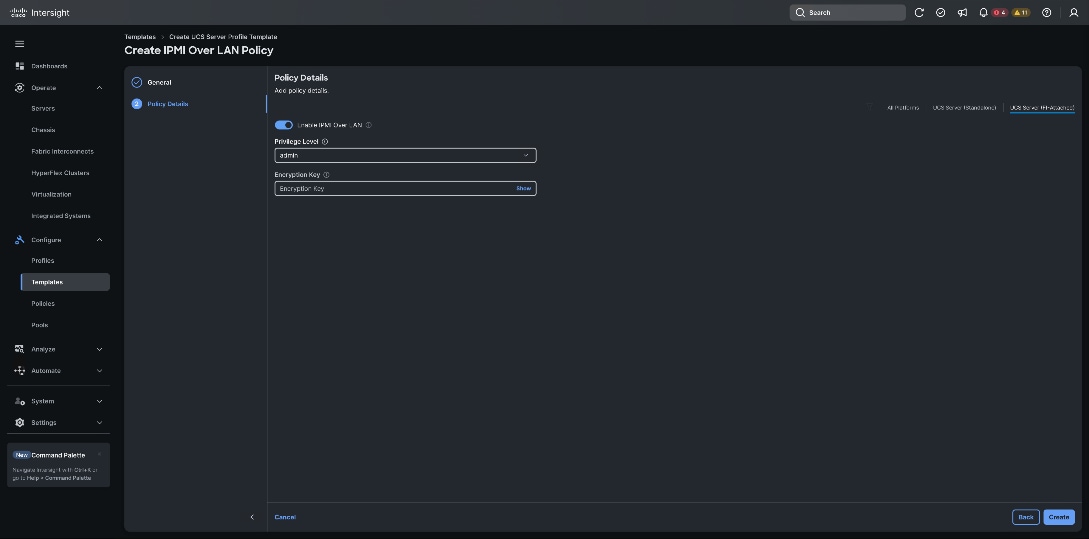
Procedure 3. Configure Local User Policy
Step 1. Click Select Policy.
Step 2. Click Create Policy.
Step 3. Verify correct organization is selected from the drop-down list (for example, X-Series) and provide a name for the policy (for example, FlexPod-VDI-LocalUser-Policy). Click Next.
Step 4. Verify that UCS Server (FI-Attached) is selected.
Step 5. Verify that Enforce Strong Password is selected.
Step 6. Click Add New User and then click + next to the New User.
Step 7. Provide the username (for example, fpadmin), choose a role for example, admin), and provide a password.
Note: The username and password combination defined here will be used to log into KVMs. The typical Cisco UCS admin username and password combination cannot be used for KVM access.
Step 8. Click Create to finish configuring local user policy.
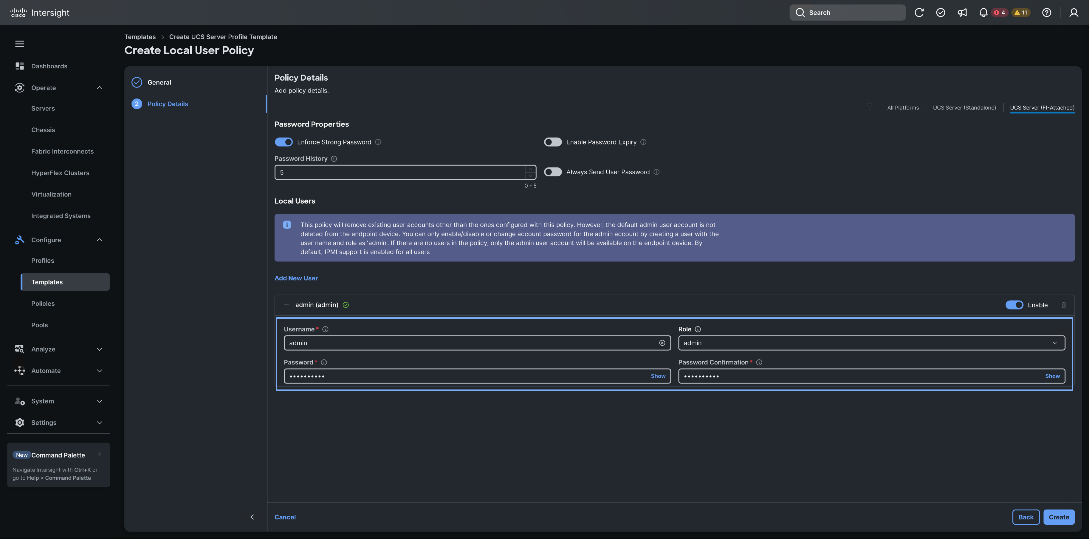
Step 9. Click Next to go to Storage Configuration.
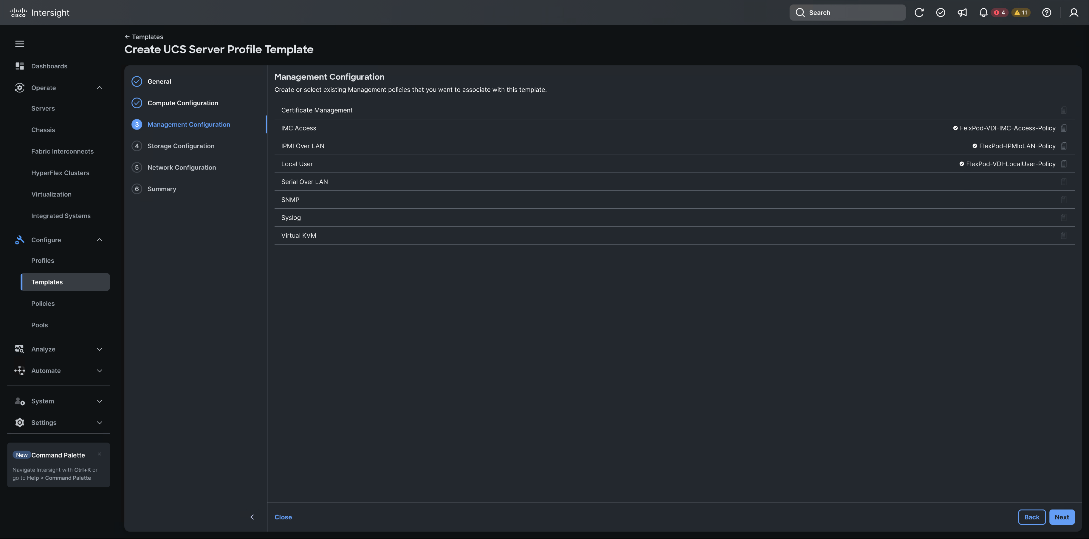
Procedure 4. Storage Configuration
Step 1. From the Storage Configuration screen, click Next. No configuration is needed in the local storage system.
Procedure 5. Network Configuration
Step 1. Go to Network Configuration > LAN Connectivity.
The LAN connectivity policy defines the connections and network communication resources between the server and the LAN. This policy uses pools to assign MAC addresses to servers and to identify the vNICs that the servers use to communicate with the network. For iSCSI hosts, this policy also defined an IQN address pool.
For consistent vNIC placement, manual vNIC placement is utilized.
The FC boot from SAN hosts uses 4 vNICs configured as listed in Table 15.
Table 15. vNICs for LAN Connectivity
| vNIC |
Slot ID |
Switch ID |
PCI Order |
VLANs |
| vSwitch0-A |
MLOM |
A |
2 |
60 |
| vSwitch0-B |
MLOM |
B |
3 |
60 |
| VDS0-A |
MLOM |
A |
4 |
61-64 |
| VDS0-B |
MLOM |
B |
5 |
61-64 |
Note: The PCI order 0 and 1 will be used in the SAN Connectivity policy to create vHBA-A and vHBA-B.
Step 2. Click Select Policy and then click Create New.
Step 3. Click Create Policy.
Step 4. Verify correct organization is selected from the drop-down list and provide a name for the policy (for example, FlexPod-VDI-LanConn). Click Next.
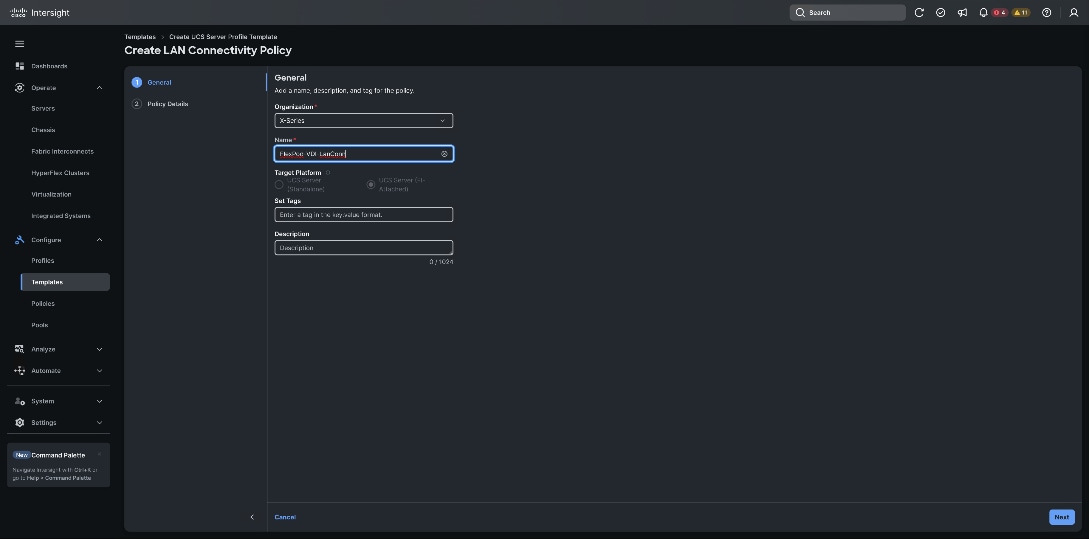
Step 5. Under vNIC Configuration, select Manual vNICs Placement.
Step 6. From the Add drop-down list click vNIC.
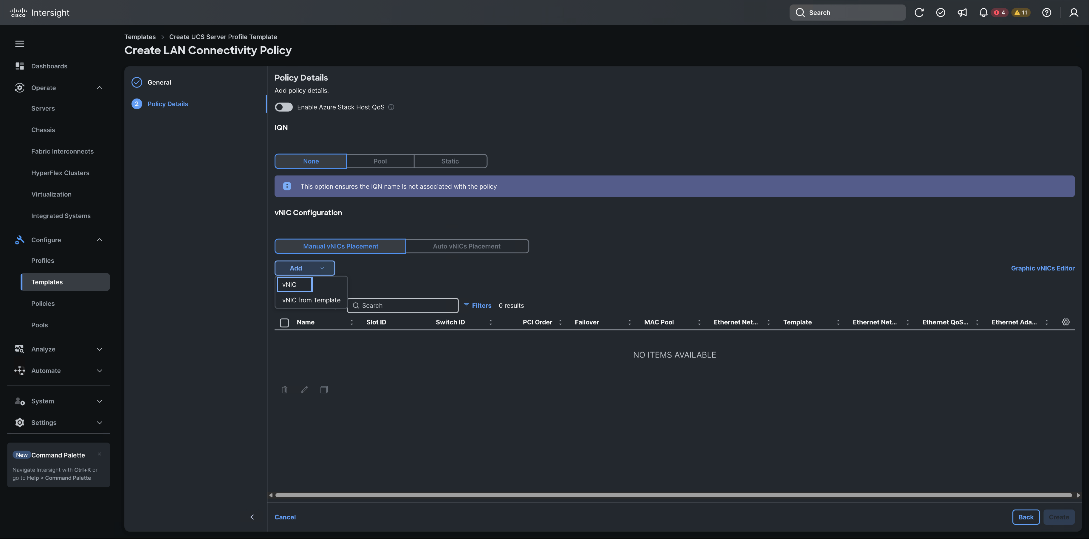
Step 7. Provide vNIC name.

Procedure 6. Create MAC Address Pool for Fabric A and B
When creating the first vNIC, the MAC address pool has not been defined yet, therefore a new MAC address pool will need to be created. Two separate MAC address pools are configured for each Fabric. FP-MAC-A will be reused for all Fabric-A vNICs, and FP-MAC-B will be reused for all Fabric-B vNICs.
Table 16. MAC Address Pools
| Pool Name |
Starting MAC Address |
Size |
vNICs |
| FlexPod-MAC-Pool-A |
00:25:B5:04:0A:00 |
16* |
eth0-eth2 |
| FlexPod-MAC-Pool-B |
00:25:B5:04:0B:00 |
16* |
eth1, eth3 |
Note: Each server requires 2 MAC addresses from the pool. Adjust the size of the pool according to your requirements.
Step 1. Click Select Pool.
Step 2. Click Create New.
Step 3. Verify correct organization is selected from the drop-down list (for example, X-Series) and provide a name for the pool from Table 16 depending on the vNIC being created (for example, FlexPod-MAC-Pool-A for Fabric A).
Step 4. Click Next.
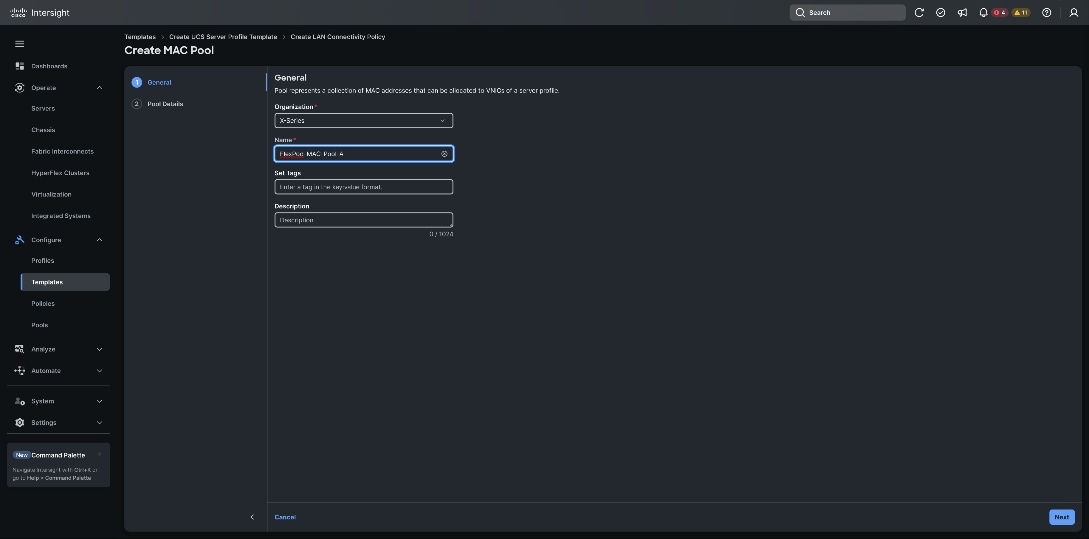
Step 5. Provide the starting MAC address from Table 16 (for example, 00:25:B5:04:0A:00).
Note: For troubleshooting FlexPod, some additional information is always coded into the MAC address pool. For example, in the starting address 00:25:B5:04:0A:00, 04 is the rack ID and 0A indicates Fabric A.
Step 6. Provide the size of the MAC address pool from Table 16 (for example, 16).
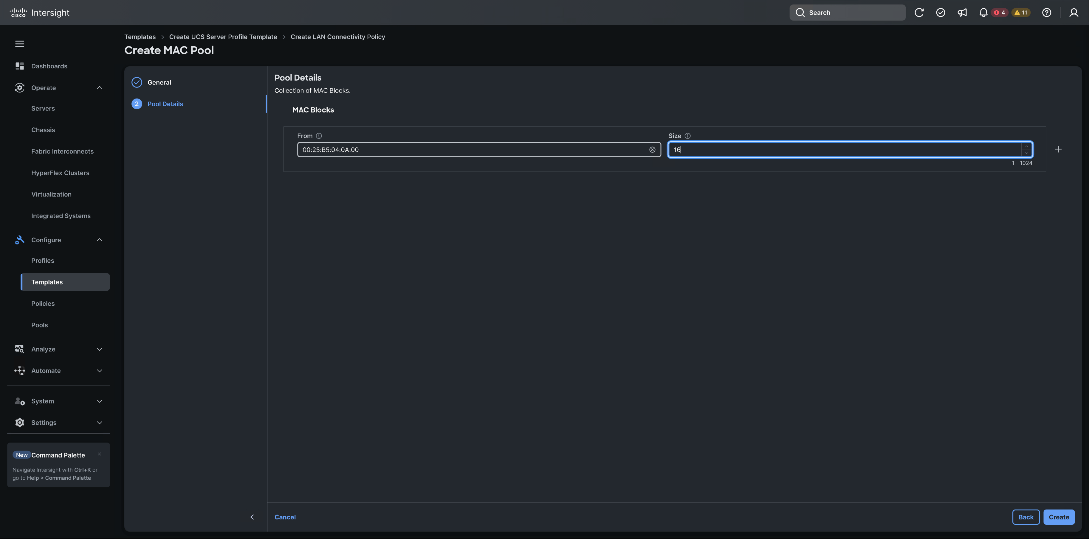
Step 7. Click Create to finish creating the MAC address pool.
Step 8. Select Advanced placement and provide Slot ID, Switch ID, and PCI Order information from Table 15.
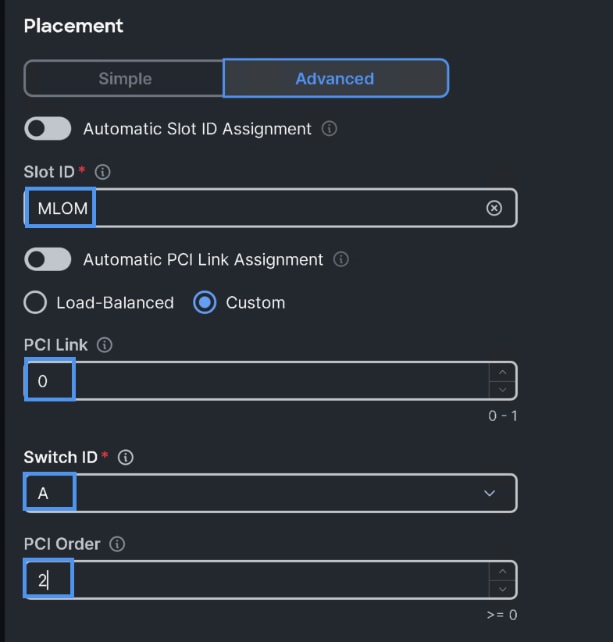
Step 9. For Consistent Device Naming (CDN), from the drop-down list select vNIC Name.
Step 10. Verify that Failover is disabled because the failover will be provided by attaching multiple NICs to the VMware vSwitch and VDS.
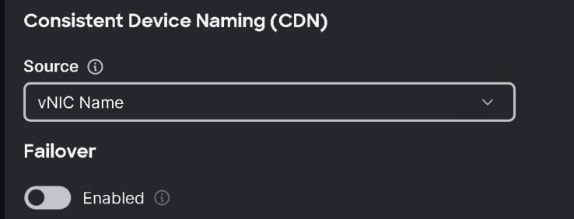
Procedure 7. Create Ethernet Network Group Policy for a vNIC
The Ethernet Network Group policies will be created and reused on applicable vNICs as explained below. The Ethernet Network Group policy defines the VLANs allowed for a particular vNIC, therefore multiple network group policies will be defined for this deployment as described in this procedure.
Table 17. Ethernet Group Policy Values
| Group Policy Name |
Native VLAN |
Apply to vNICs |
VLANs |
| VDI-vSwitch0-NetGrp-Policy |
Native-VLAN (1) |
vSwitch0-A, vSwitch0-B |
60 |
| VDI-VDS0-NetGrp-Policy |
Native-VLAN (1) |
03-VDS0-A, 04-VDS0-B |
61-64 |
Step 1. Click Select Policy under Ethernet Network Group Policy.
Step 2. Click Create New.
Step 3. Verify correct organization is selected from the drop-down list (for example, X-Series) and provide a name for the policy from Table 17 (for example, VDI-vSwitch0-NetGrp).
Step 4. Click Next.
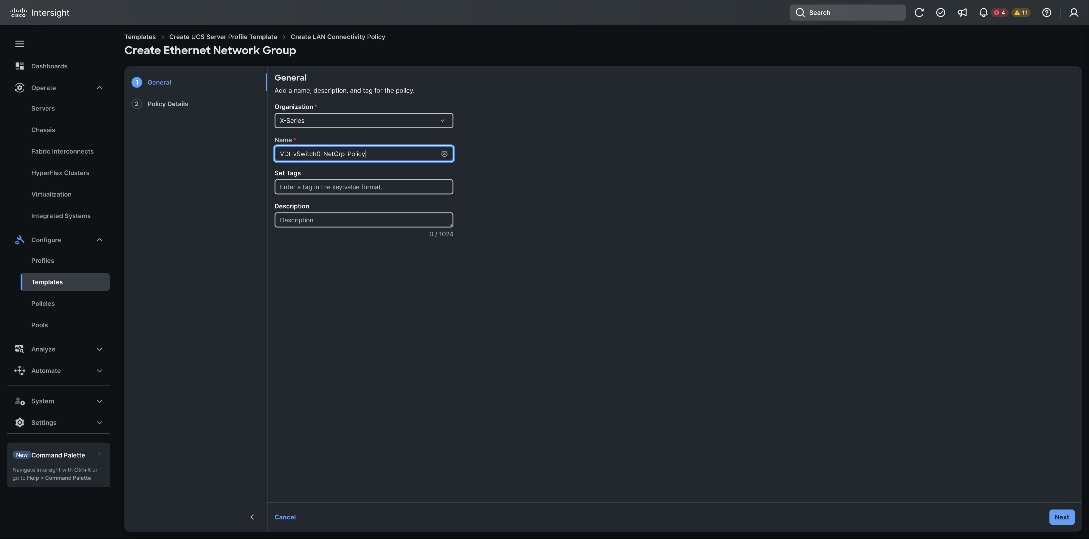
Step 5. Enter the allowed VLANs from Table 6 (for example, 30-36) and the native VLAN ID from Table 6 (for example, 2).
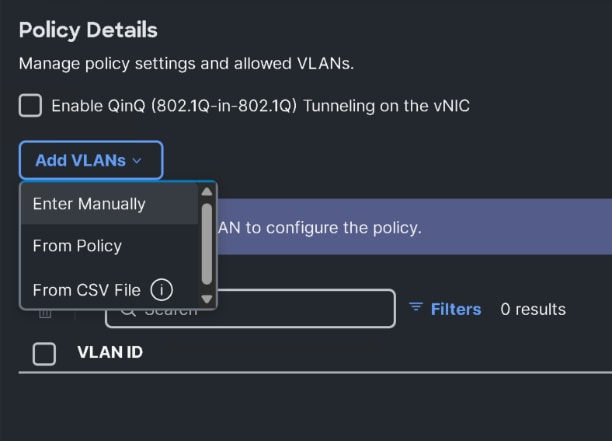
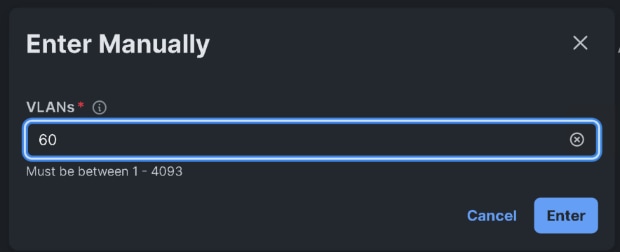
Step 6. Click Create to finish configuring the Ethernet network group policy.
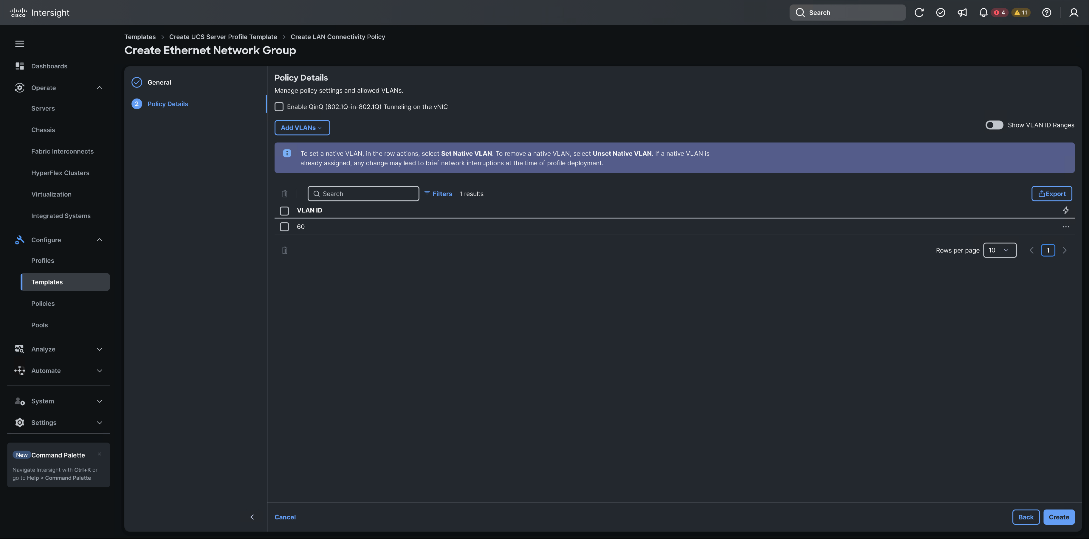
Note: When ethernet group policies are shared between two vNICs, the ethernet group policy only needs to be defined for the first vNIC. For subsequent vNIC policy mapping, click Select Policy and select the previously defined ethernet group policy from the list.
Procedure 8. Create Ethernet Network Control Policy
The Ethernet Network Control Policy is used to enable Cisco Discovery Protocol (CDP) and Link Layer Discovery Protocol (LLDP) for the vNICs. A single policy will be created and reused for all the vNICs.
Step 1. Click Select Policy under Ethernet Network Control Policy.
Step 2. Click Create New.
Step 3. Verify correct organization is selected from the drop-down list (for example, X-Series) and provide a name for the policy (for example, VDI-Enable-CDP-LLDP).
Step 4. Click Next.
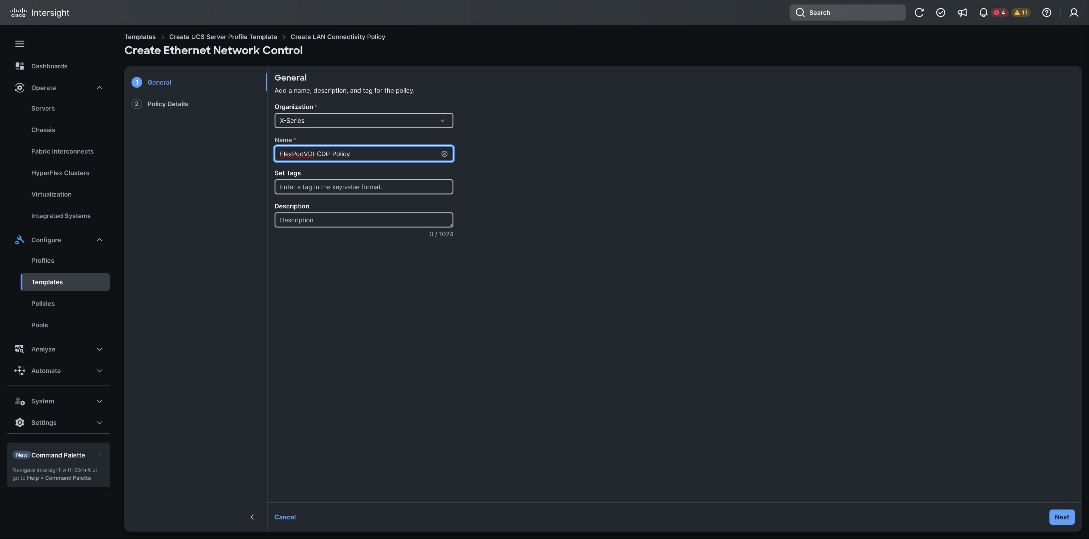
Step 5. Enable Cisco Discovery Protocol and Enable Transmit and Enable Receive under LLDP.
Step 6. Click Create to finish creating Ethernet network control policy.
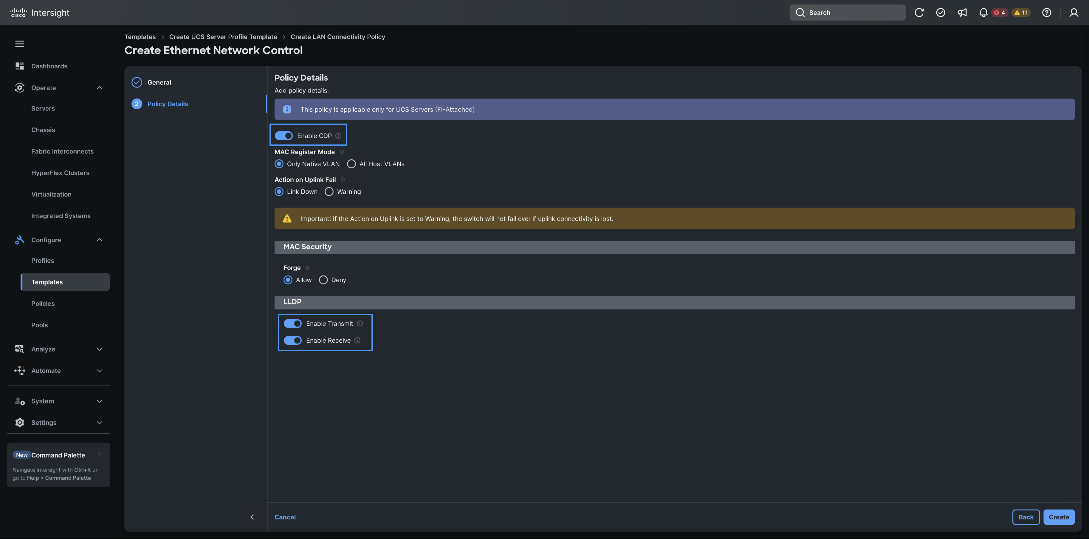
Procedure 9. Create Ethernet QoS Policy
Ethernet QoS policy is used to enable jumbo maximum transmission units (MTUs) for all the vNICs. A single policy will be created and reused for all the vNICs.
Step 1. Click Select Policy under Ethernet QoS.
Step 2. Click Create New.
Step 3. Verify correct organization is selected from the drop-down list (for example, X-Series) and provide a name for the policy (for example, FlexPod-VDI-EthQoS-Policy).
Step 4. Click Next.
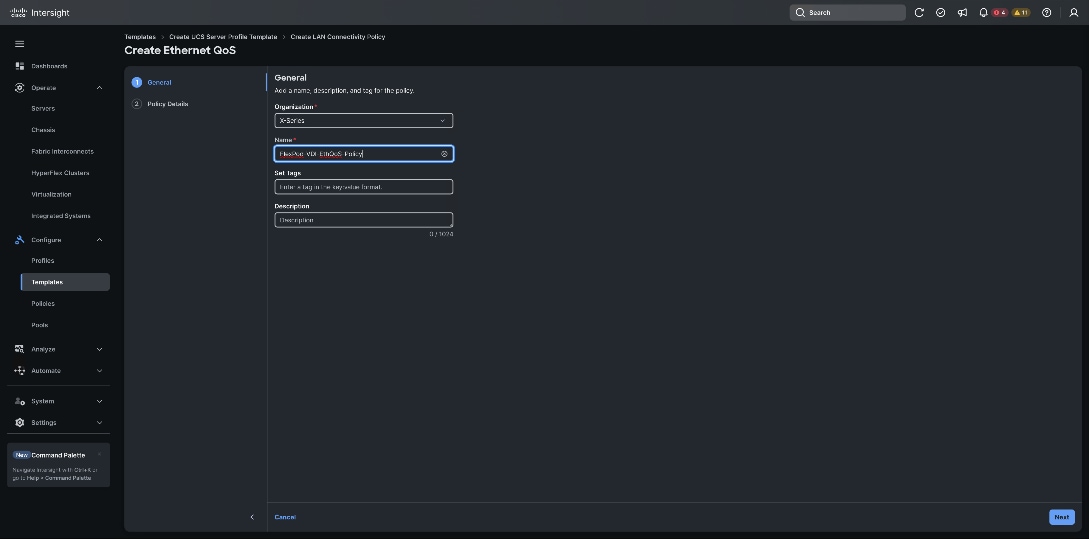
Step 5. Change the MTU, Bytes value to 9000.
Step 6. Click Create to finish setting up the Ethernet QoS policy.
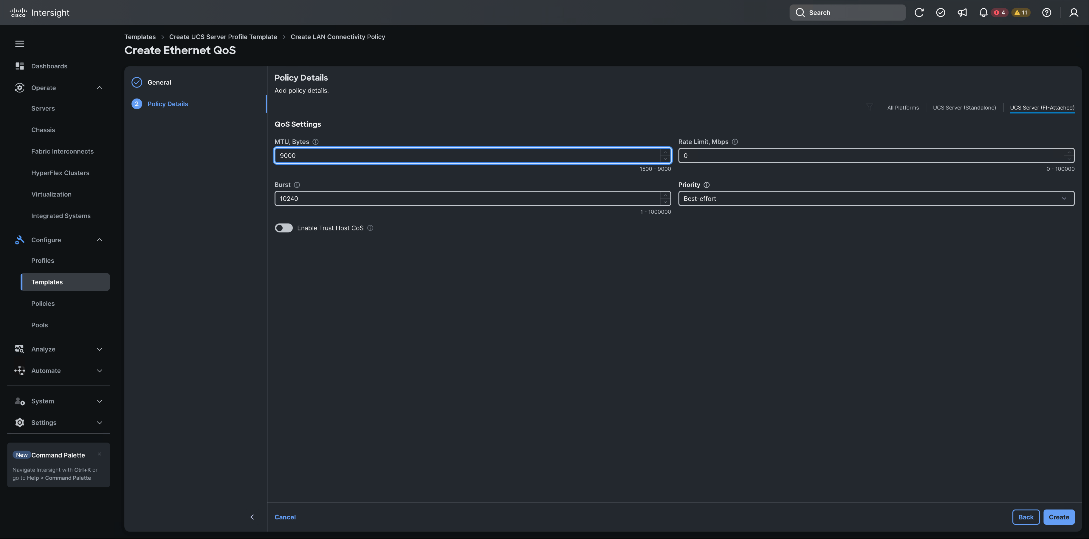
Procedure 10. Create Ethernet Adapter Policy
Ethernet adapter policy is used to set the interrupts and the send and receive queues. The values are set according to the best-practices guidance for the operating system in use. Cisco Intersight provides default VMware Ethernet Adapter policy for typical VMware deployments.
Optionally, you can configure a tweaked ethernet adapter policy for additional hardware receive queues handled by multiple CPUs in scenarios where there is a lot of vMotion traffic and multiple flows. In this deployment, a modified ethernet adapter policy, VDI-VMware-High-Traffic, is created and attached to the 01-VDS0-A and 02-VDS0-B interfaces which handle vMotion.
Table 18. Ethernet Adapter Policy association to vNICs
| Policy Name |
vNICs |
| FlexPod-VDI-EthAdapter-VMware |
01-vSwitch0-A, 02-vSwitch0-B |
| Flex-Pod-VDI-VMware-High-Traffic |
01-VDS0-A, 02-VDS0-B |
Step 1. Click Select Policy under Ethernet Adapter.
Step 2. Click Create New.
Step 3. Verify correct organization is selected from the drop-down list (for example, X-Series) and provide a name for the policy (for example, VDI-EthAdapter-VMware). Click Next.
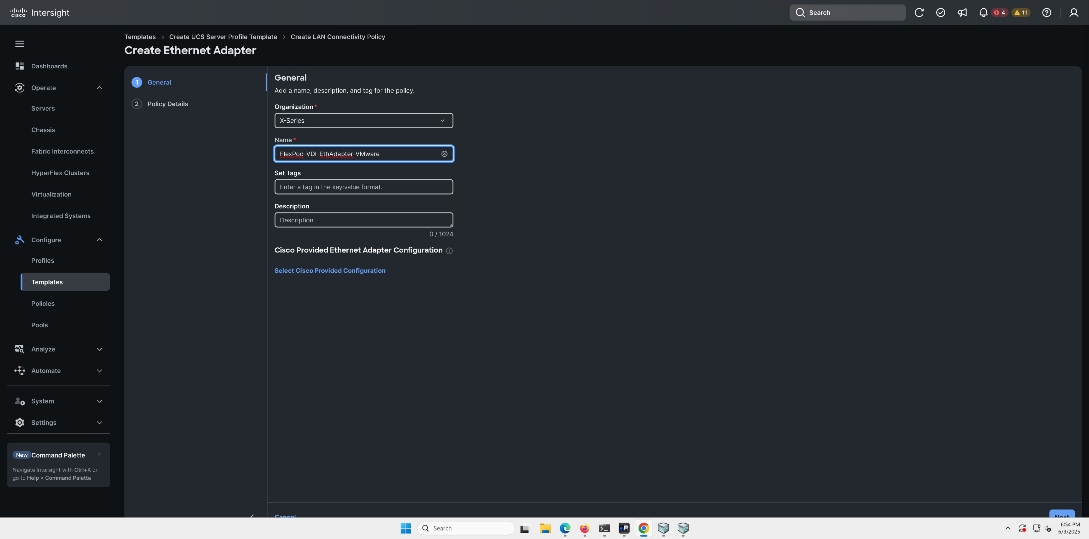
Step 4. Click Select Default Configuration under Ethernet Adapter Default Configuration.
Step 5. From the list, select VMware. Click Select.
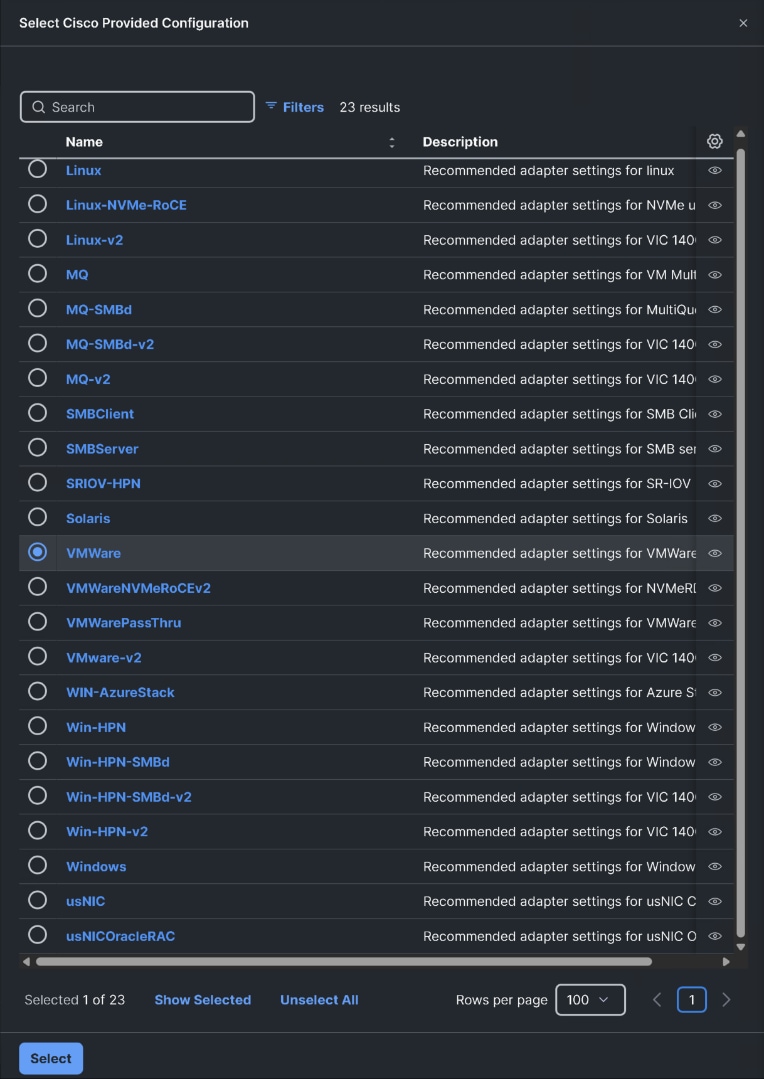
Step 6. Click Next.
Step 7. For the VDI-EthAdapter-VMware policy, click Create and skip the rest of the steps in this section.
Step 8. For the optional VDI-VMware-High-Traffic policy (for VDS interfaces), make the following modifications to the policy:
- Increase Interrupts to 11
- Increase Receive Queue Count to 8
- Increase Completion Queue Count to 9
- Enable Receive Side Scaling
Step 9. Click Create.
Step 10. Click Add to finish creating the vNIC.
Step 11. Go back to Step 1 and repeat vNIC creation for all four vNICs.
Step 12. Verify all four vNICs were successfully created.
Step 13. Click Create to finish creating the LAN Connectivity policy for hosts.
Procedure 11. Create SAN Connectivity Policy
Step 1. Click Select Policy next to SAN Connectivity.

Step 2. Click Create New.
Note: A SAN connectivity policy determines the network storage resources and the connections between the server and the storage device on the network. This policy enables you to configure the vHBAs that the servers use to communicate with the SAN.
Table 19. vHBA for boot from FC SAN
| vNIC/vHBA Name |
Slot |
Switch ID |
PCI Order |
| vHBA-A |
MLOM |
A |
0 |
| vHBA-B |
MLOM |
B |
1 |
Step 3. Verify the correct organization is selected from the drop-down list and provide a name for the policy (for example, L151-DMZ-GEN5-SAN-CONN_Pol).
Step 4. Select Manual vHBAs Placement.
Step 5. Select Pool under WWNN.
Note: The WWNN address pools have not been defined yet therefore a new WWNN address pool has to be defined.
Step 6. Click Select Pool under WWNN Pool.
Step 7. Click Create New.
Step 8. Verify the correct organization is selected from the drop-down list and provide a name for the policy (for example, L151-DMZ-K8-GEN5-WWN-Pool).
Step 9. Click Next.
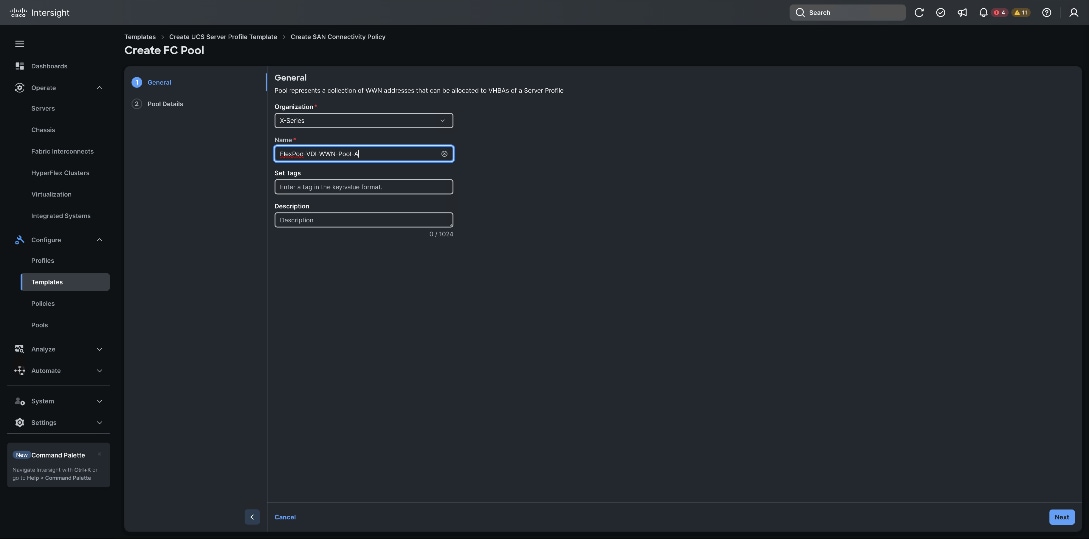
Step 10. Provide the starting WWNN block address and the size of the pool. Click Create.
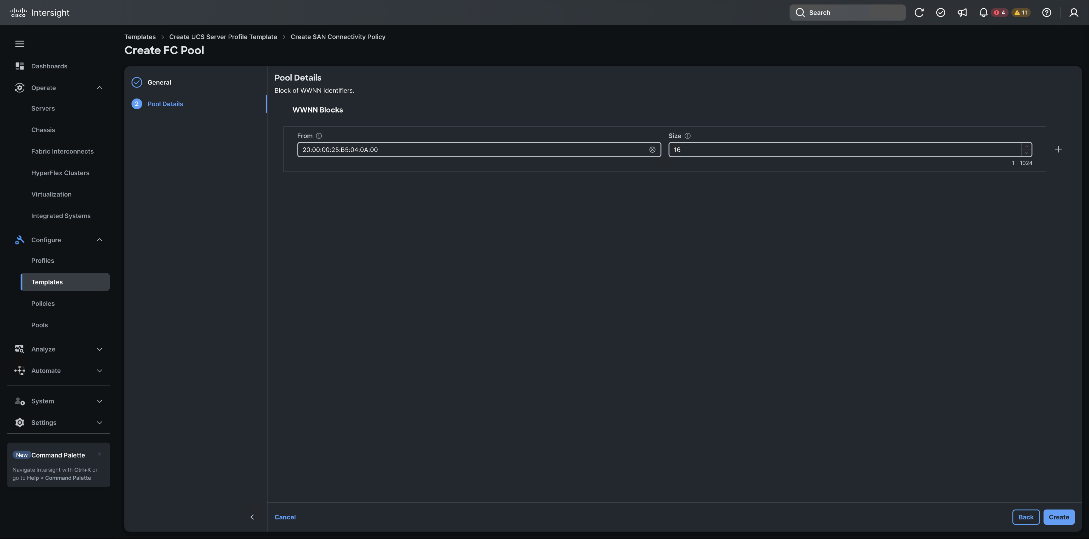
Note: As a best practice, additional information should always be coded into the WWNN address pool for troubleshooting. For example, in the address 20:00:00:25:B5:23:00:00, 23 is the rack ID.
Step 11. Click Add vHBA.
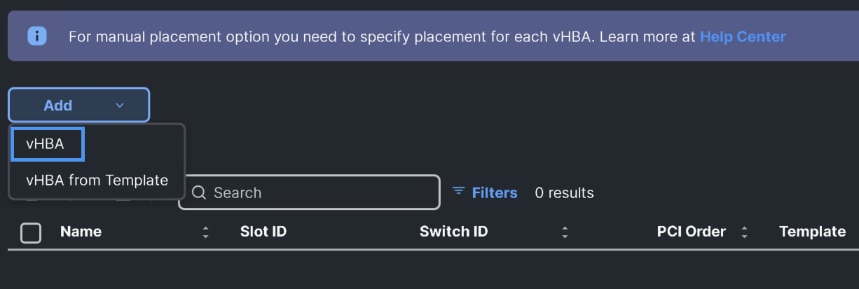
Step 12. Enter vHBA-A for the Name and select fc-initiator from the drop-down list.

Note: The WWPN address pool has not been defined yet therefore a WWPN address pool for Fabric A will be defined.
Step 13. Click Select Pool under WWPN Address Pool and then click Create New.
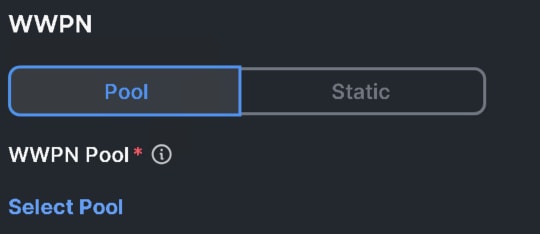
Step 14. Verify the correct organization is selected from the drop-down list and provide a name for the policy (for example, FlexPod-VDI-WWPN-Pool-A).
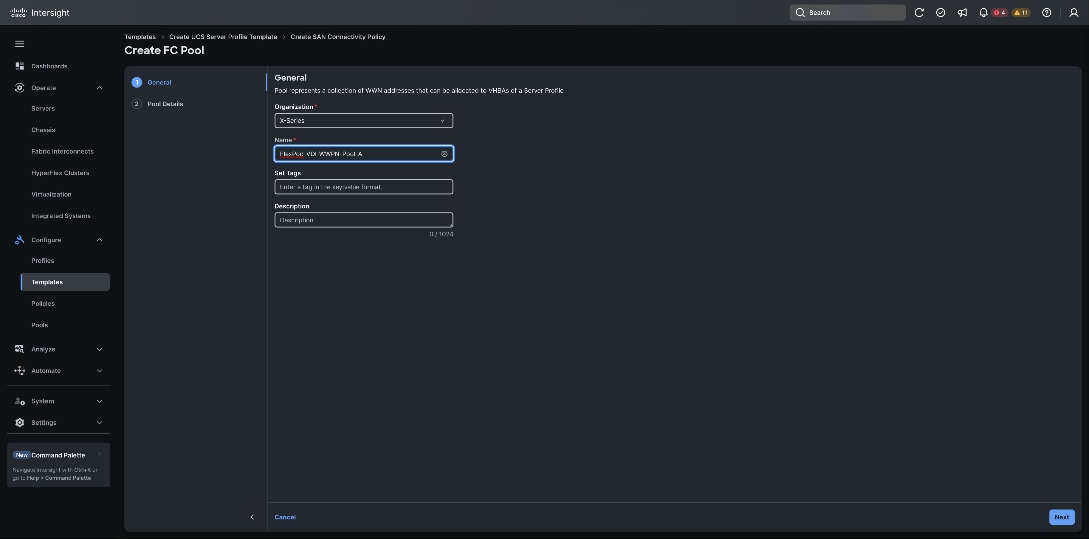
Step 15. Provide the starting WWPN block address for SAN A and the size. Click Create.
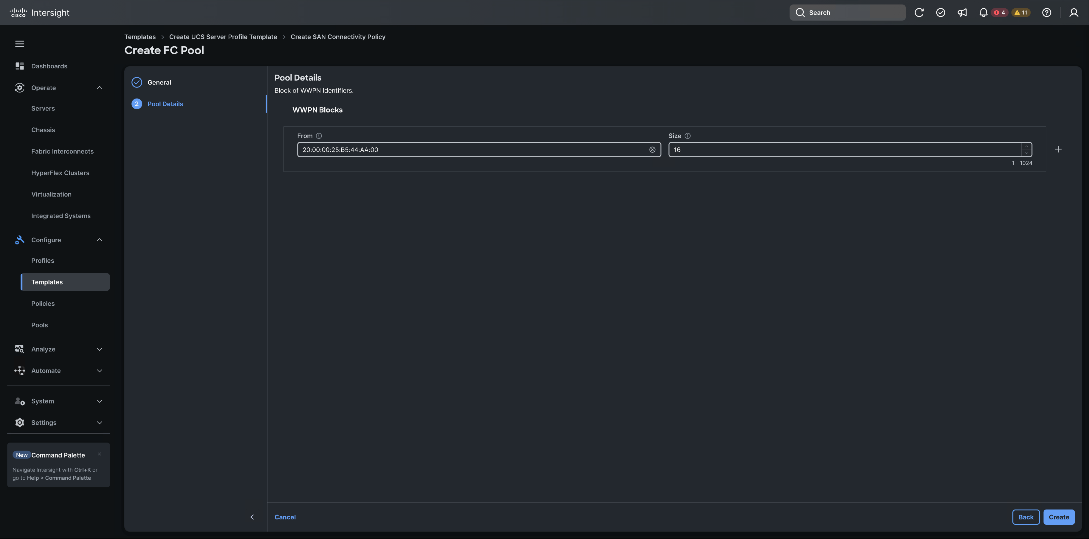
Step 16. Provide the Switch ID (for example, A) and PCI Order (for example, 0) from Table 11.
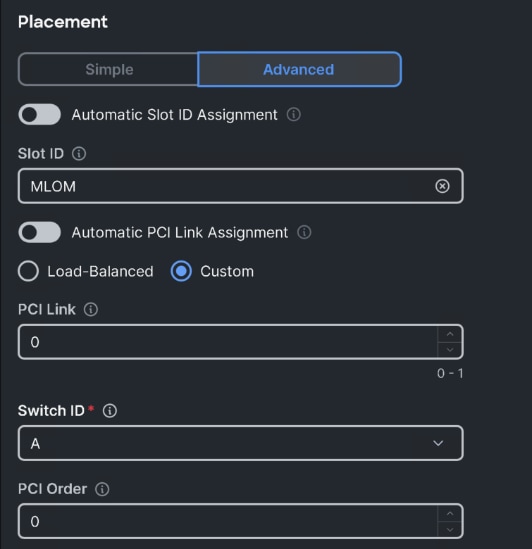
Step 17. Click Select Policy under Fibre Channel Network and then click Create Policy.
Note: A Fibre Channel network policy governs the VSAN configuration for the virtual interfaces. In this deployment, VSAN 100 will be used for vHBA-A and VSAN 101 will be used for vHBA-B.
Step 18. Verify the correct organization is selected from the drop-down list and provide a name for the policy (for example, FlexPod-VDI-FCN-A-Pol). Click Next.
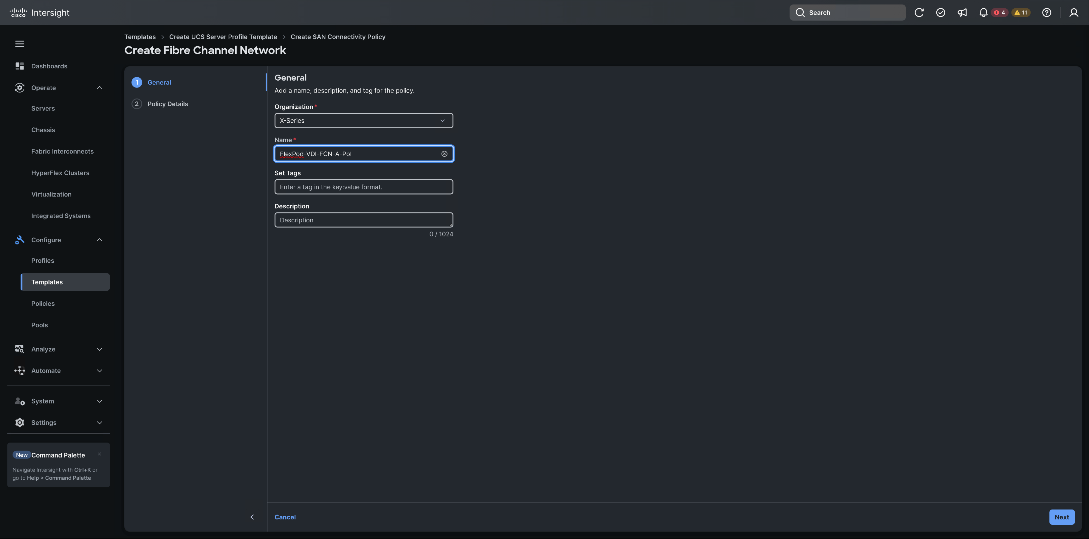
Step 19. For the scope, select UCS Server (FI-Attached).
Step 20. Under VSAN ID, provide the VSAN information (for example, 100).
Step 21. Click Create.
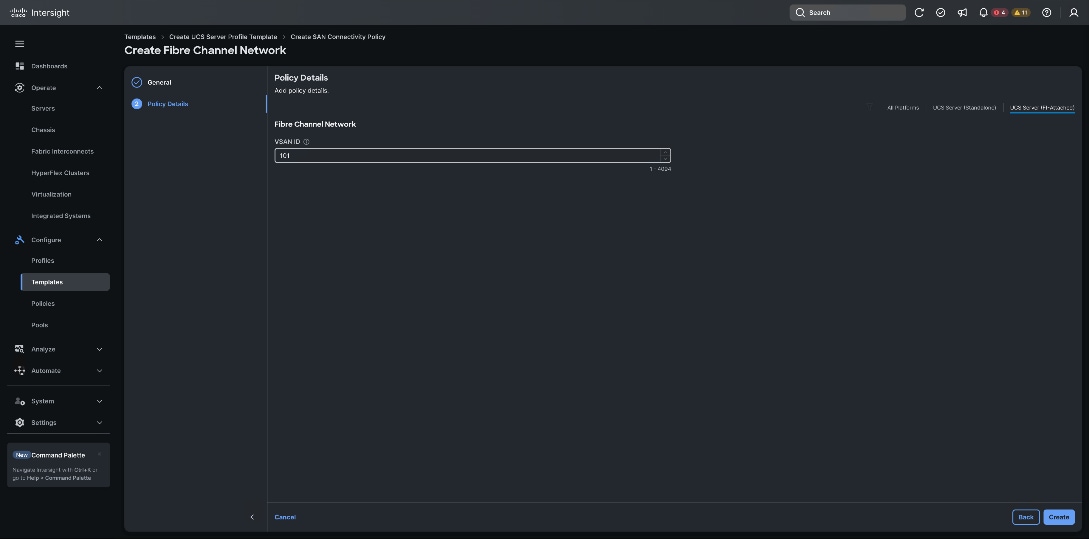
Step 22. Click Select Policy under Fibre Channel QoS and then click Create New.
Note: The Fibre Channel QoS policy assigns a system class to the outgoing traffic for a vHBA. This system class determines the quality of service for the outgoing traffic. The Fibre Channel QoS policy used in this deployment uses default values and will be shared by all vHBAs.
Step 23. Verify the correct organization is selected from the drop-down list and provide a name for the policy (for example, FlexPod-VDI-FC-QOS-Pol). Click Next.
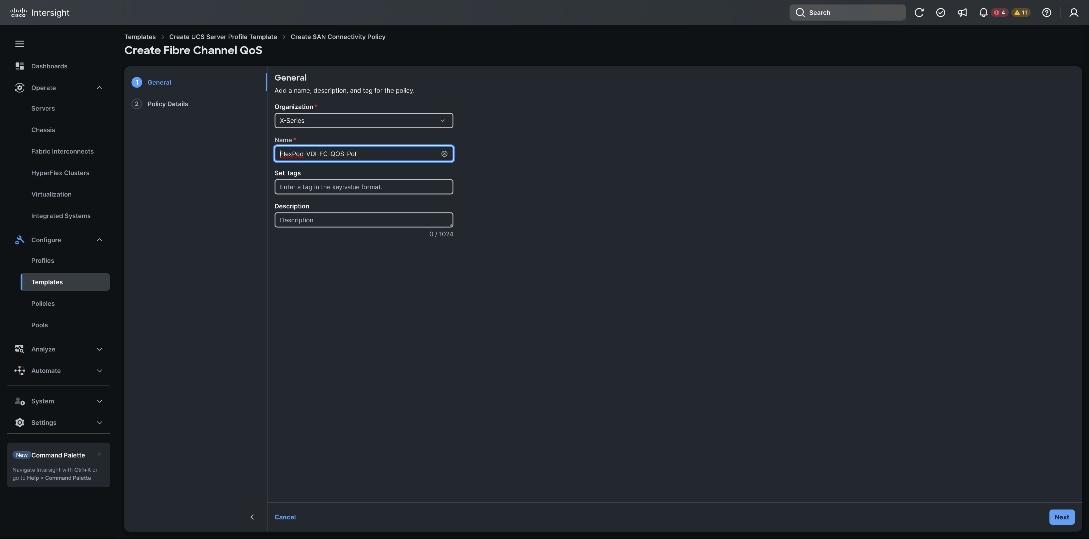
Step 24. For the scope, select UCS Server (FI-Attached).
Note: Do not change the default values on the Policy Details screen.
Step 25. Click Create.
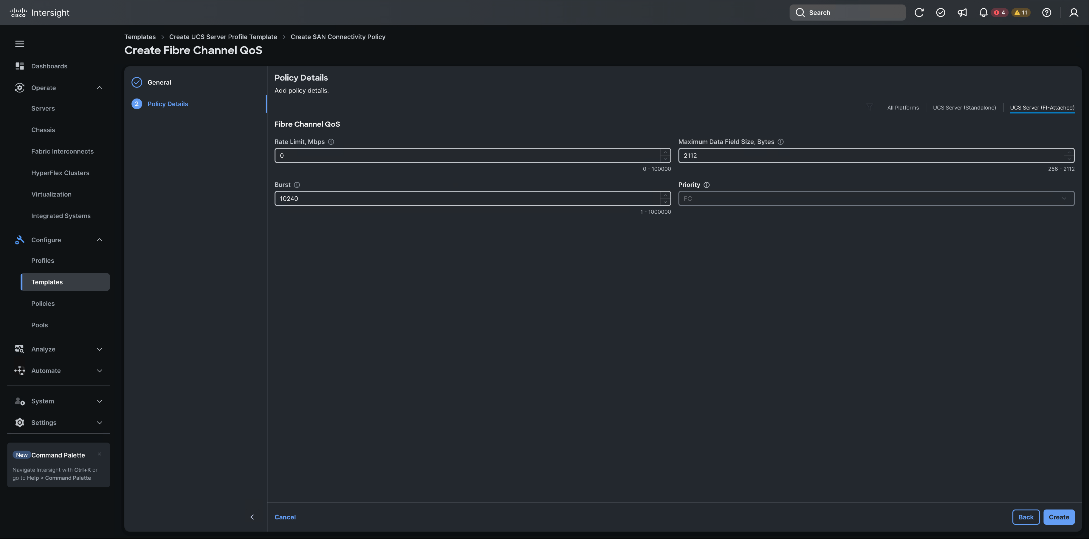
Step 26. Click Select Policy under Fibre Channel Adapter.
Step 27. Click Create Policy.
Note: A Fibre Channel adapter policy governs the host-side behavior of the adapter, including the way that the adapter handles traffic. This validation uses the default values for the adapter policy, and the policy will be shared by all the vHBAs.
Step 28. Verify the correct organization is selected from the drop-down list and provide a name for the policy (for example, FlexPod-VDI-FC-Adapter-Pol).
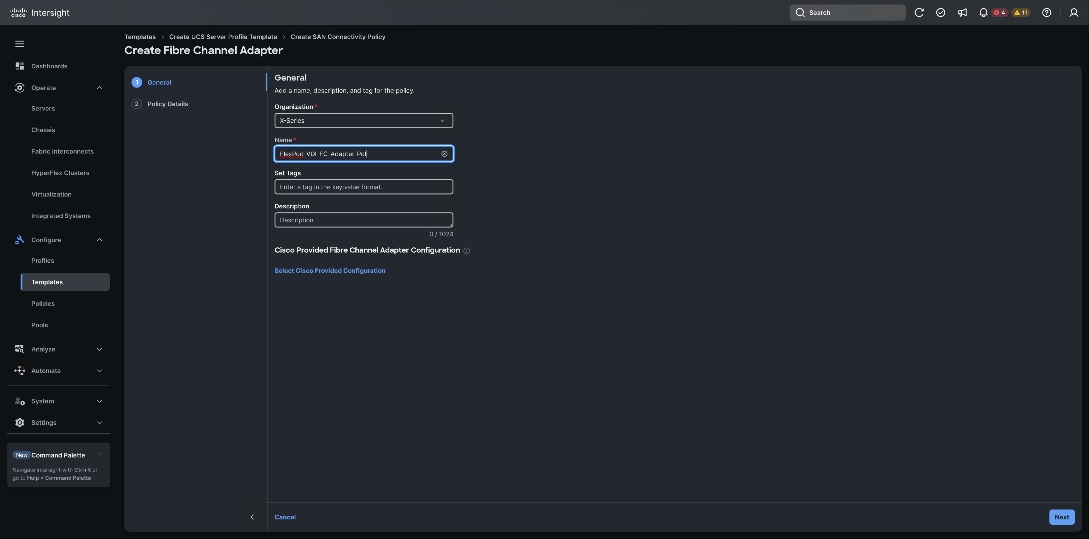
Step 29. For the scope, select UCS Server (FI-Attached).
Note: Do not change the default values on the Policy Details screen.
Step 30. Click Create.
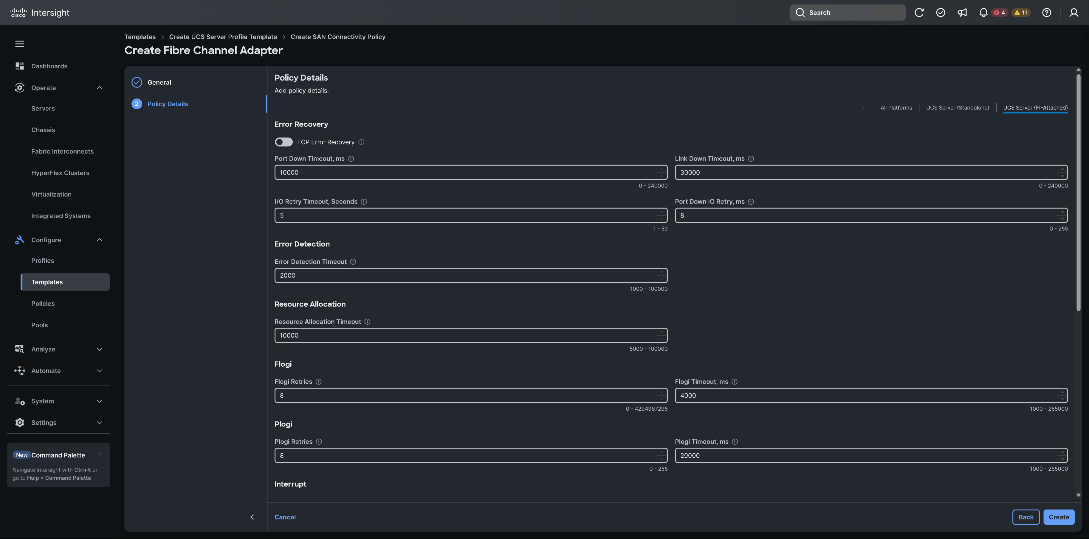
Step 31. Click Add to create vHBA-A.
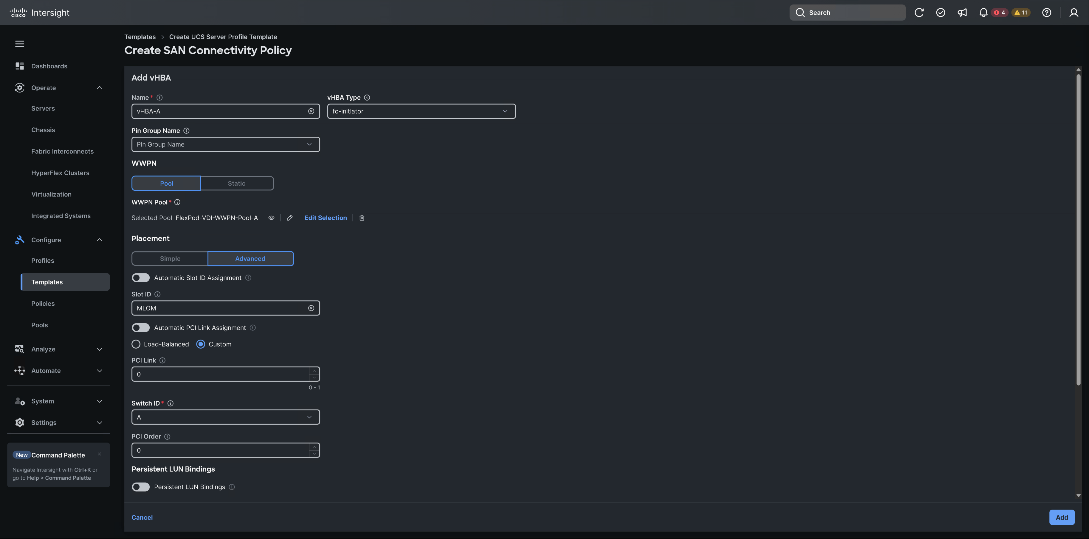
Step 32. Repeat steps 1 – 31 to create the vHBA-B using the same steps from above using pools and Fibre Channel Network policy for SAN-B.
Step 33. Verify both vHBAs are added to the SAN connectivity policy.
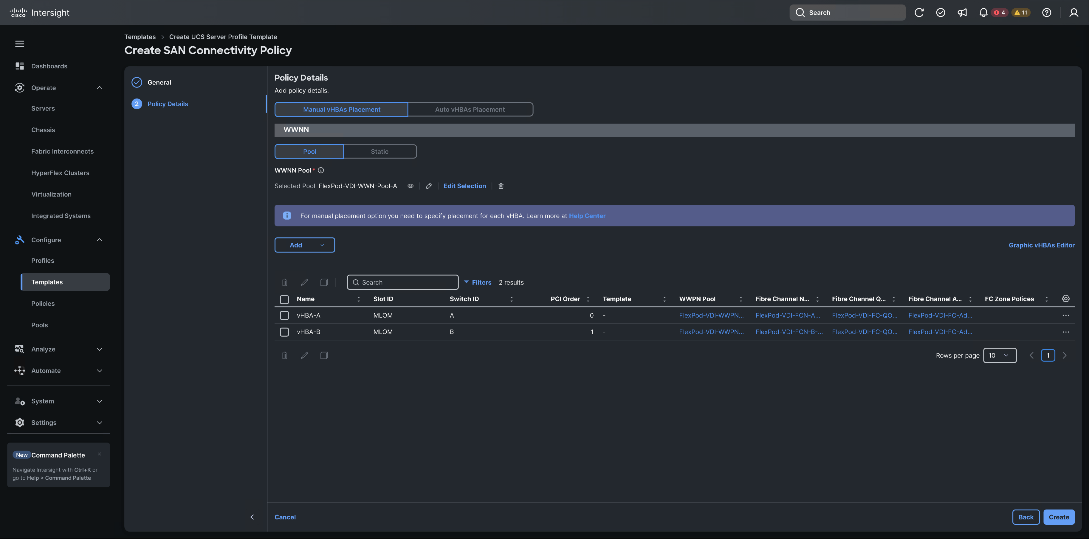
Step 34. When the LAN connectivity policy and SAN connectivity policy are created and assigned, click Next to move to the Summary screen.
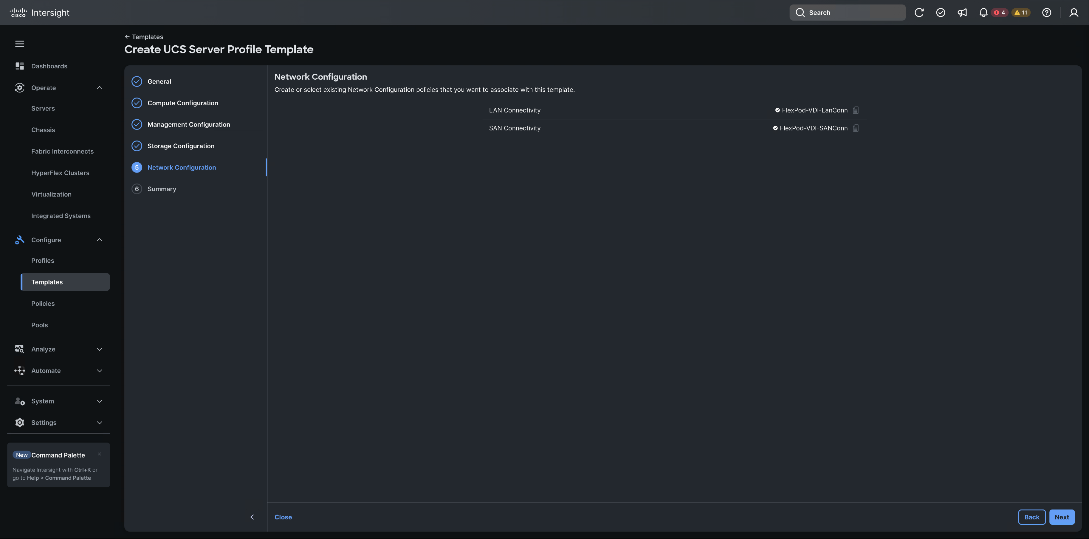
Step 1. When the LAN connectivity policy is created, click Next to the Summary screen.
Step 2. On the summary screen, verify policies mapped to various settings (Compute, Management, Storage, Network).
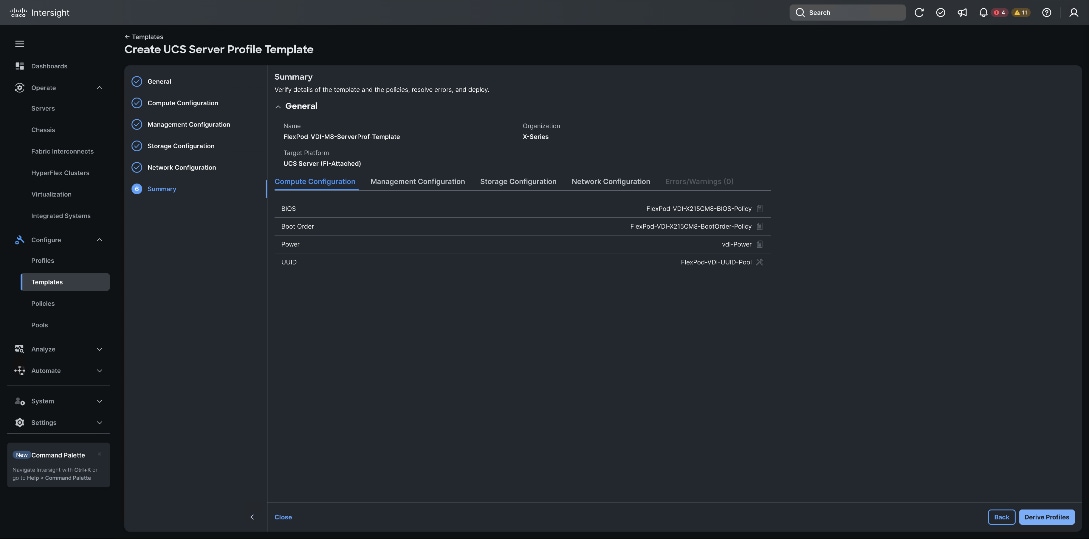
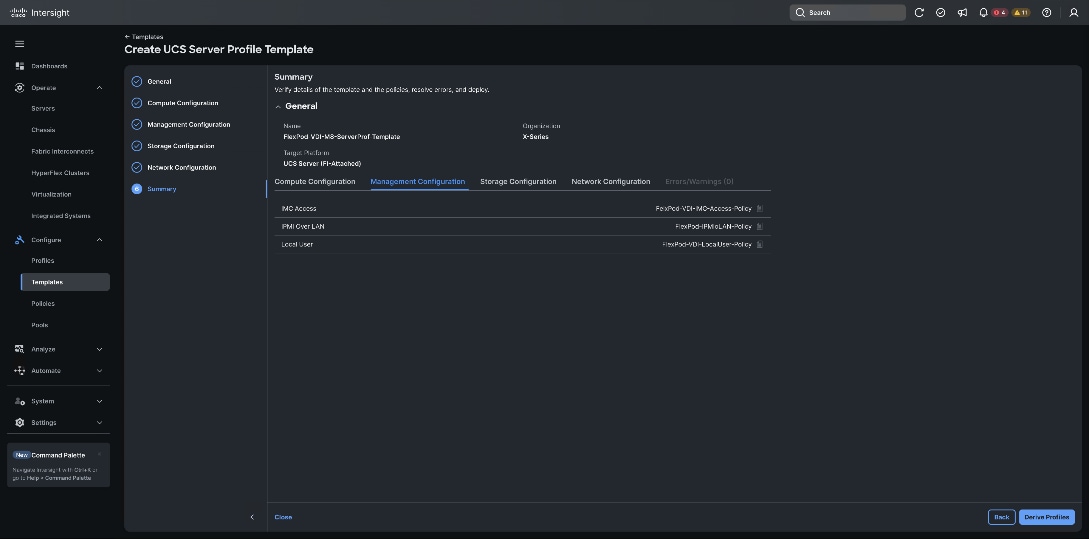
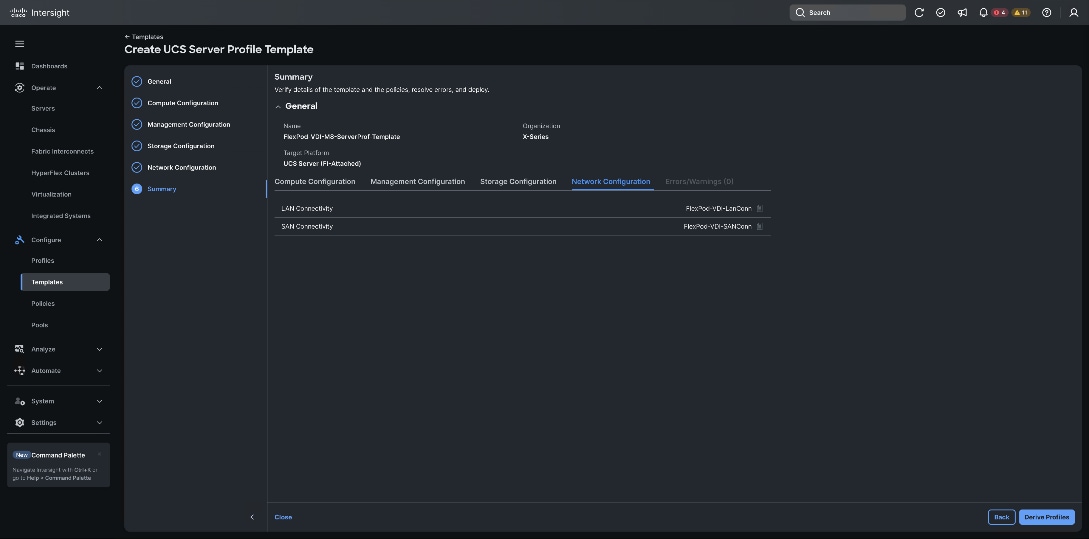
Procedure 13. Derive Server Profile
Step 1. From the Server profile template Summary screen, click Derive Profiles.
Note: This action can also be performed later by navigating to Templates, clicking “…” next to the template name and selecting Derive Profiles.
Step 2. Under the Server Assignment, select Assign Now. You can select one or more servers depending on the number of profiles to be deployed.
Step 3. Click Next.
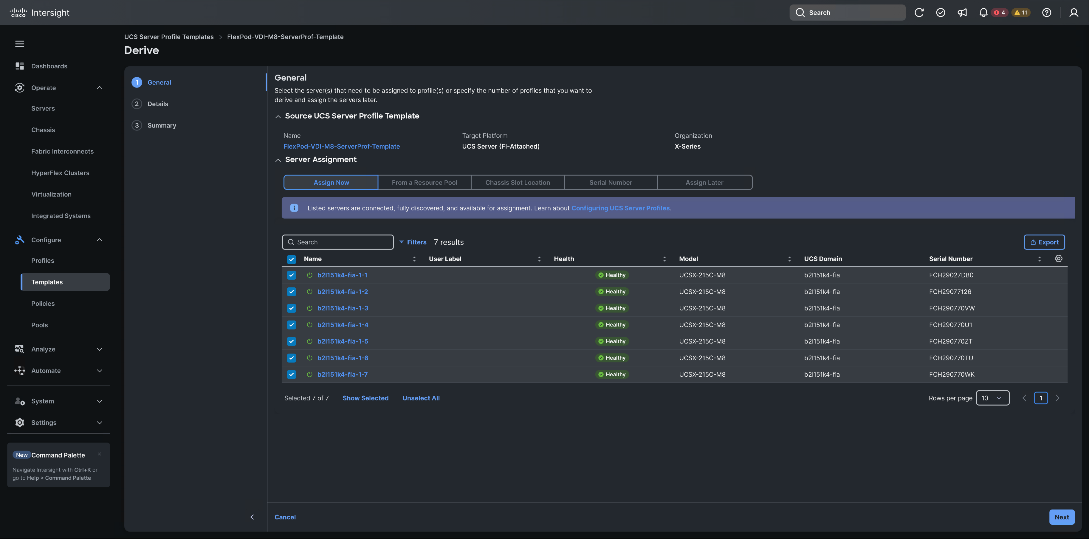
Note: Cisco Intersight will fill the default information for the number of servers selected.
Step 4. Adjust the Prefix and number if needed.
Step 5. Click Next.
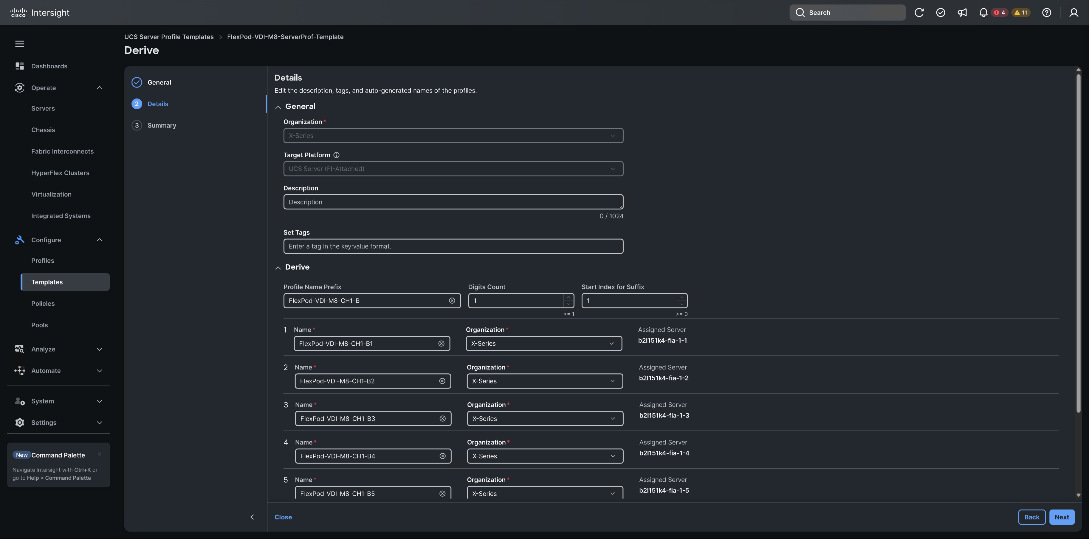
Step 6. Verify the information and click Derive to create the Server Profiles.
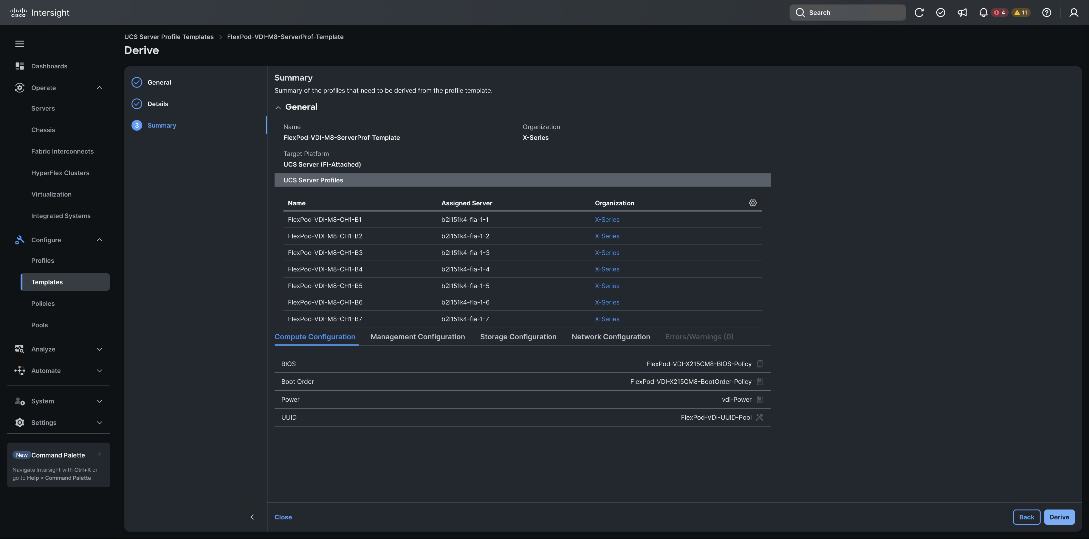
Step 7. Cisco Intersight will start configuring the server profiles and will take some time to apply all the policies. Use the Requests tab to see the progress.

When the Server Profiles are deployed successfully, they will appear under the Server Profiles with the status of OK.
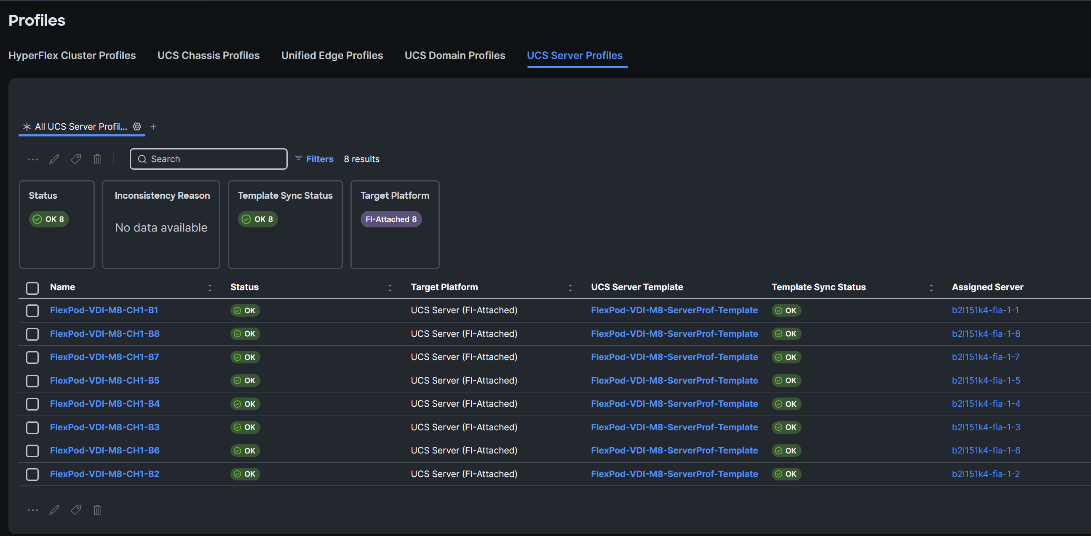
This section describes the ONTAP boot storage setup process.
Procedure 1. Create Boot LUNs
Step 1. Run the following commands to create three boot LUNs:
lun create -vserver VDI-SVM -path /vol/Boot_CH1B1/Boot_CH1B1 -size 32GB -ostype vmware -space-reserve disabled
lun create -vserver VDI-SVM -path /vol/Boot_CH1B2/Boot_CH1B2 -size 32GB -ostype vmware -space-reserve disabled
lun create -vserver VDI-SVM -path /vol/Boot_CH1B3/Boot_CH1B3 -size 32GB -ostype vmware -space-reserve disabled
lun create -vserver VDI-SVM -path /vol/Boot_CH1B4/Boot_CH1B4 -size 32GB -ostype vmware -space-reserve disabled
lun create -vserver VDI-SVM -path /vol/Boot_CH1B5/Boot_CH1B5 -size 32GB -ostype vmware -space-reserve disabled
lun create -vserver VDI-SVM -path /vol/Boot_CH1B6/Boot_CH1B6 -size 32GB -ostype vmware -space-reserve disabled
lun create -vserver VDI-SVM -path /vol/Boot_CH1B7/Boot_CH1B7 -size 32GB -ostype vmware -space-reserve disabled
lun create -vserver VDI-SVM -path /vol/Boot_CH1B8/Boot_CH1B8 -size 32GB -ostype vmware -space-reserve disabled
Procedure 2. Create igroups
Step 1. Create initiator groups (igroups) by entering the following commands from the storage cluster management node Secure Shell (SSH) connection:
lun igroup create –vserver VDI-SVM –igroup ESXCH1B1-FC –protocol fcp –ostype vmware –initiator <vm-host-01-wwpna>, <vm-host-01-wwpnb>
lun igroup create –vserver VDI-SVM –igroup ESXCH1B2-FC –protocol fcp –ostype vmware –initiator <vm-host-01-wwpna>, <vm-host-01-wwpnb>
lun igroup create –vserver VDI-SVM –igroup ESXCH1B3-FC –protocol fcp –ostype vmware –initiator <vm-host-01-wwpna>, <vm-host-01-wwpnb>
lun igroup create –vserver VDI-SVM –igroup ESXCH1B4-FC –protocol fcp –ostype vmware –initiator <vm-host-01-wwpna>, <vm-host-01-wwpnb>
lun igroup create –vserver VDI-SVM –igroup ESXCH1B5-FC –protocol fcp –ostype vmware –initiator <vm-host-01-wwpna>, <vm-host-01-wwpnb>
lun igroup create –vserver VDI-SVM –igroup ESXCH1B6-FC –protocol fcp –ostype vmware –initiator <vm-host-01-wwpna>, <vm-host-01-wwpnb>
lun igroup create –vserver VDI-SVM –igroup ESXCH1B7-FC –protocol fcp –ostype vmware –initiator <vm-host-01-wwpna>, <vm-host-01-wwpnb>
lun igroup create –vserver VDI-SVM –igroup ESXCH1B8-FC –protocol fcp –ostype vmware –initiator <vm-host-01-wwpna>, <vm-host-01-wwpnb>
Step 2. To view the three igroups just created, use the command lun igroup show:
lun igroup show -protocol fcp
Procedure 3. Map Boot LUNs to igroup
Step 1. From the storage cluster management SSH connection, enter the following commands:
lun mapping create –vserver VDI-SVM –path /vol/Boot_CH1B1/Boot_CH1B1 –igroup ESXCH1B1-FC –lun-id 0
lun mapping create –vserver VDI-SVM –path /vol/Boot_CH1B2/Boot_CH1B2 –igroup ESXCH1B2-FC –lun-id 0
lun mapping create –vserver VDI-SVM –path /vol/Boot_CH1B3/Boot_CH1B3 –igroup ESXCH1B3-FC –lun-id 0
lun mapping create –vserver VDI-SVM –path/vol/Boot_CH1B4/Boot_CH1B4 –igroup ESXCH1B4-FC –lun-id 0
lun mapping create –vserver VDI-SVM –path /vol/Boot_CH1B5/Boot_CH1B5 –igroup ESXCH1B5-FC –lun-id 0
lun mapping create –vserver VDI-SVM –path /vol/Boot_CH1B6/Boot_CH1B6 –igroup ESXCH1B6-FC –lun-id 0
lun mapping create –vserver VDI-SVM –path /vol/Boot_CH1B7/Boot_CH1B7 –igroup ESXCH1B7-FC –lun-id 0
lun mapping create –vserver VDI-SVM –path /vol/Boot_CH1B8/Boot_CH1B8 –igroup ESXCH1B8-FC –lun-id 0
Step 2. In the Cisco Intersight navigation pane, click the Equipment tab.
Step 3. Go to Servers > Service Profiles> Host1.
Step 4. Right-click Host1 and select KVM Console.
Step 5. Click Boot Device and then select CD/DVD.
Step 6. Click Virtual Media and Mount the ESXi ISO image.
Step 7. Boot into ESXi installer and follow the prompts to complete installing VMware vSphere ESXi hypervisor.
Step 8. When selecting a storage device to install ESXi, select Remote LUN provisioned through NetApp Storage Administrative console and access through FC connection.
Note: Adding a management network for each VMware host is necessary for managing the host and connection to vCenter Server. Please select the IP address that can communicate with an existing or a new vCenter Server.
Step 9. After the server has finished rebooting, press F2 to enter into configuration wizard for ESXi Hypervisor.
Step 10. Log in as root and enter the corresponding password.
Step 11. Select the Configure the Management Network option and press Enter.
Step 12. Select the VLAN (Optional) option and press Enter. Enter the VLAN In-Band management ID and press Enter.
Step 13. From the Configure Management Network menu, select IP Configuration and press Enter.
Step 14. Select Set Static IP Address and Network Configuration option by using the space bar. Enter the IP address to manage the first ESXi host. Enter the subnet mask for the first ESXi host. Enter the default gateway for the first ESXi host. Press Enter to accept the changes to the IP configuration.
Step 15. IPv6 Configuration is set to automatic.
Step 16. Select the DNS Configuration option and press Enter.
Step 17. Enter the IP address of the primary and secondary DNS server. Enter Hostname.
Step 18. Enter DNS Suffixes.
Step 19. Since the IP address is assigned manually, the DNS information must also be entered manually.
Note: The steps provided vary based on the configuration. Please make the necessary changes according to your configuration
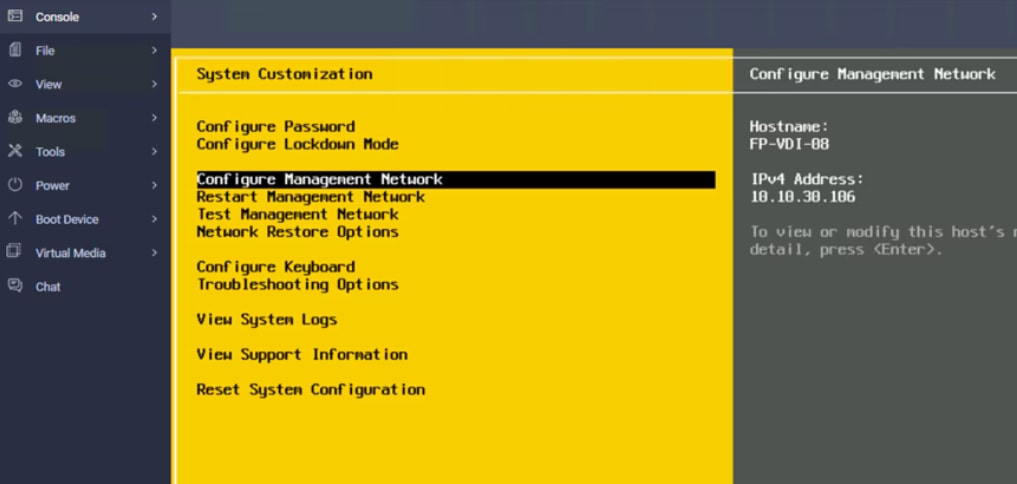
Install VMware vSphere 8.0 U3
This chapter contains the following:
Install VMware ESXi 8.0 U3
This section provides detailed instructions for installing VMware ESXi 8.0 U3 in a FlexPod environment. After the procedures are completed, three booted ESXi hosts will be provisioned.
Several methods exist for installing ESXi in a VMware environment. These procedures focus on how to use the built-in keyboard, video, mouse (KVM) console and virtual media features in Cisco Intersight to map remote installation media to individual servers and connect to their boot logical unit numbers (LUNs).
Procedure 1. Download ESXi 8.0 U3 from Broadcom
Step 1. Go to: Cisco Custom Image for ESXi 8.0U3 Install CD. You will need a user id and password on broadcom.com to download this software.
Step 2. Download the .iso file.
Procedure 2. Install ESXi 8.0 U3
Step 1. Log into Cisco Intersight.
Step 2. From the menu go to Operate > Servers.
Step 3. Click the … icon for the server being access and select Launch vKVM. Accept Certificate.
Step 4. Click Boot Device and then select vKVM Mapped vDVD.
Step 5. Click Virtual Media and select vKVM Mapped vDVD. Browse to the ESXi iso image file. Click Map Drive to mount the ESXi ISO image.
Step 6. Boot into ESXi installer and follow the prompts to complete installing VMware vSphere ESXi hypervisor.
Step 7. When selecting a storage device to install ESXi, select Remote LUN provisioned through ONTAP System Manager on NetApp AFF A50 and accessed through FC connection.
Step 8. Unmount the vKVM Mapped vDVD. Reboot the server.
Procedure 3. Set Up Management Networking for ESXi Hosts
Note: Adding a management network for each VMware host is necessary for managing the host.
Step 1. After the server has finished rebooting, in the UCS KVM console, press F2 to customize VMware ESXi.
Step 2. Log in as root, enter the corresponding password, and press Enter to log in.
Step 3. Use the down arrow key to select Troubleshooting Options and press Enter.
Step 4. Select Enable ESXi Shell and press Enter.
Step 5. Select Enable SSH and press Enter.
Step 6. Press Esc to exit the Troubleshooting Options menu.
Step 7. Select the Configure Management Network option and press Enter.
Step 8. Select Network Adapters and press Enter.
Step 9. Verify that the numbers in the Hardware Label field match the numbers in the Device Name field. If the numbers do not match, note the mapping of vmnic ports to vNIC ports for later use.
Step 10. Using the spacebar, select vmnic1.
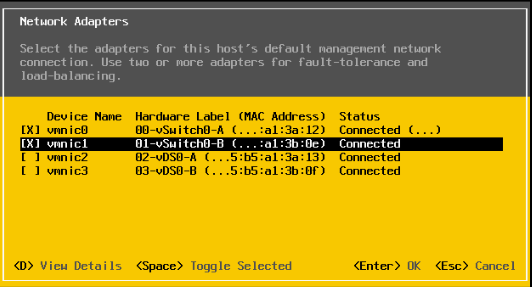
Note: In lab testing, examples were seen where the vmnic and device ordering do not match. In this case, use the Consistent Device Naming (CDN) to note which vmnics are mapped to which vNICs and adjust the upcoming procedure accordingly.
Step 11. Press Enter.
Step 12. Select the VLAN option and press Enter.
Step 13. Enter the <ib-mgmt-vlan-id> and press Enter.
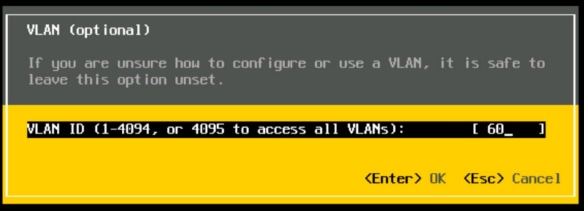
Step 14. Select IPv4 Configuration and press Enter.
Step 15. Select the Set static IPv4 address and network configuration option by using the arrow keys and space bar.
Step 16. Move to the IPv4 Address field and enter the IP address for managing the ESXi host.
Step 17. Move to the Subnet Mask field and enter the subnet mask for the ESXi host.
Step 18. Move to the Default Gateway field and enter the default gateway for the ESXi host.
Step 19. Press Enter to accept the changes to the IP configuration.
Step 20. Select the IPv6 Configuration option and press Enter.
Step 21. Using the spacebar, select Disable IPv6 (restart required) and press Enter.
Step 22. Select the DNS Configuration option and press Enter.
Note: Since the IP address is assigned manually, the DNS information must also be entered manually.
Step 23. Using the spacebar, select Use the following DNS server addresses and hostname.
Step 24. Move to the Primary DNS Server field and enter the IP address of the primary DNS server.
Step 25. Optional: Move to the Alternate DNS Server field and enter the IP address of the secondary DNS server.
Step 26. Move to the Hostname field and enter the fully qualified domain name (FQDN) for the ESXi host.
Step 27. Press Enter to accept the changes to the DNS configuration.
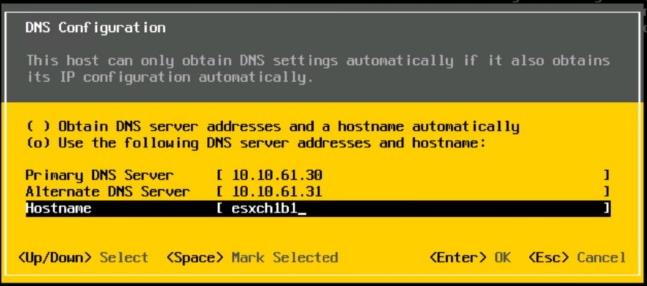
Step 28. Press Esc to exit the Configure Management Network submenu.
Step 29. Press Y to confirm the changes and reboot the ESXi host.
Note: This ESXi deployment used the Cisco VIC nenic (2.0.17.0-1OEM.800.1.0.20613240) and nfnic (5.0.0.46-1OEM.803.0.0.24022510) driver versions included in the Custom Cisco VMware ESXi 8.0 U3.24022510 image (VMware-ESXi-8.0.U3-24022510-Custom-Cisco-4.3.5-a.iso), designed for Cisco Intersight Managed Mode Server Firmware version 6.0(1.250122), along with NetApp NFS VAAI Tools version 2.0.1-16. These versions were validated and supported at the time this document was published. For the most current supported firmware and software combinations, please consult the Cisco UCS Hardware Compatibility List and the NetApp Interoperability Matrix Tool.
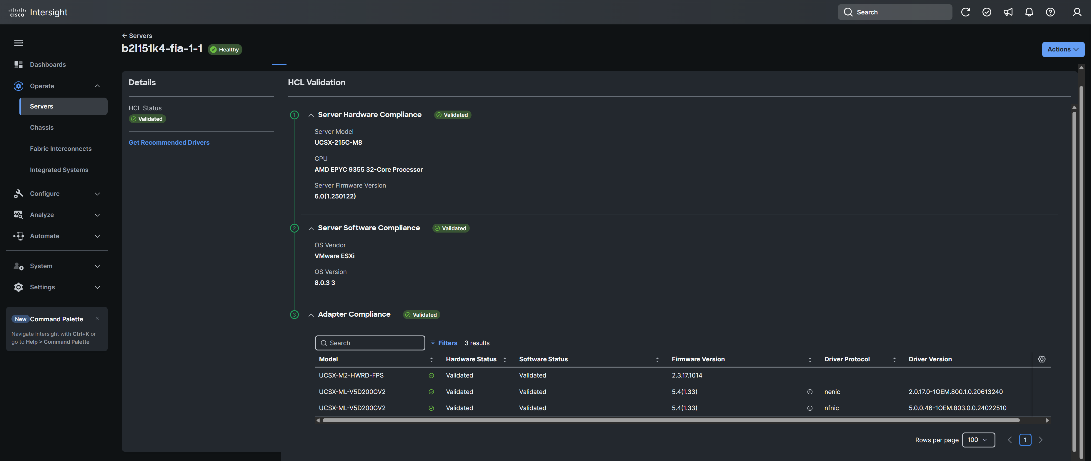
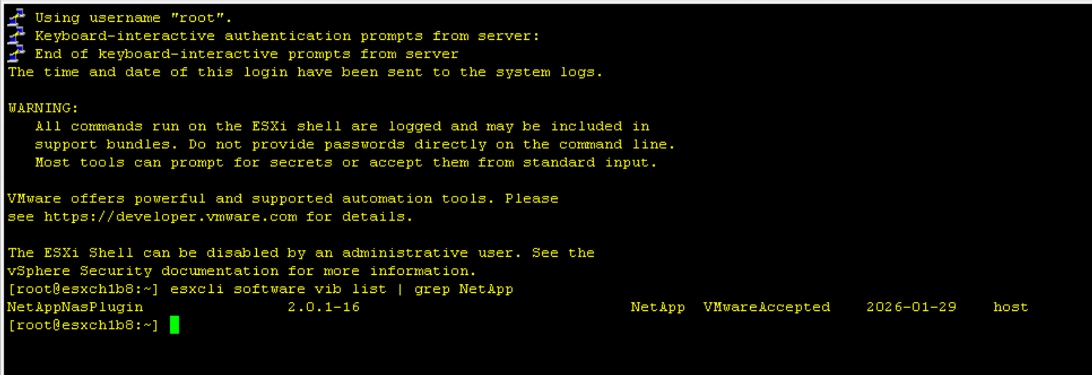
VMware vCenter 8.0 U3
This section describes how to configure Vmware vCenter 8.0 U3.
Procedure 1. Build the VMware vCenter Server Appliance
Note: The VCSA deployment consists of 2 stages: install and configuration.
Step 1. Locate and copy the VMware-VCSA-all-8.0.3-24022515 file to the desktop of the management workstation. This ISO is for the VMware vSphere 8.0 U3 vCenter Server Appliance.
Note: It is important to use at a minimum VMware vCenter release 8.0 U3 to ensure access to all needed features.
Step 2. Using ISO mounting software, mount the ISO image as a disk on the management workstation.
Step 3. In the mounted disk directory, navigate to the vcsa-ui-installer > win32 directory and double-click installer.exe. The vCenter Server Appliance Installer wizard appears.
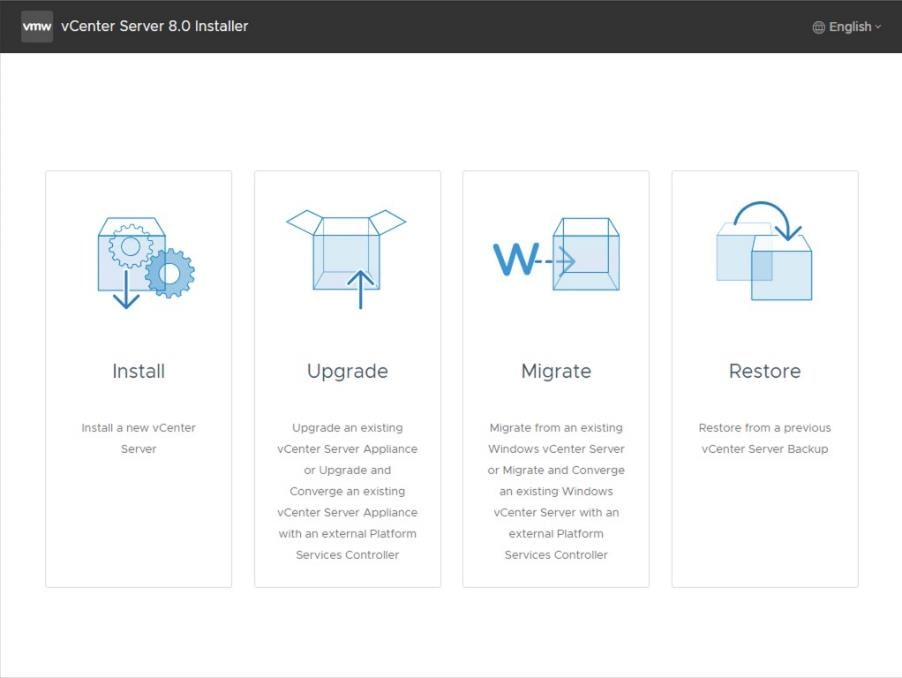
Step 4. Click Install to start the vCenter Server Appliance deployment wizard.
Step 5. Click NEXT in the Introduction section.
Step 6. Read and accept the license agreement and click NEXT.
Step 7. In the vCenter Server deployment target window, enter the host name or IP address of the first ESXi host, Username (root) and Password. Click NEXT.
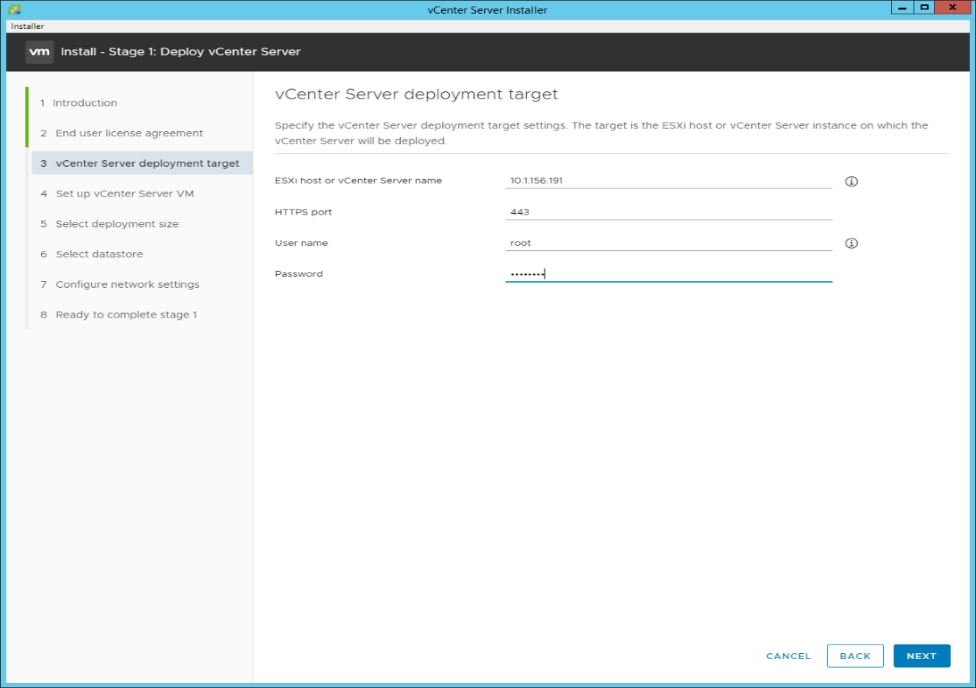
Step 8. Click YES to accept the certificate.
Step 9. Enter the Appliance VM name and password details in the Set up vCenter Server VM section. Click NEXT.
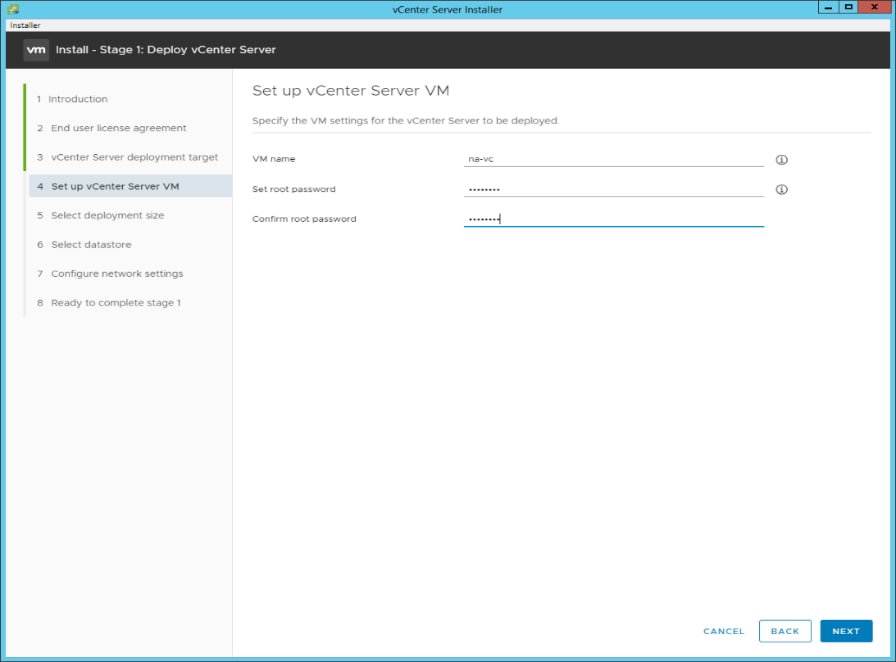
Step 10. In the Select deployment size section, click the Deployment size and Storage size. For example, click Small and Default. Click NEXT.
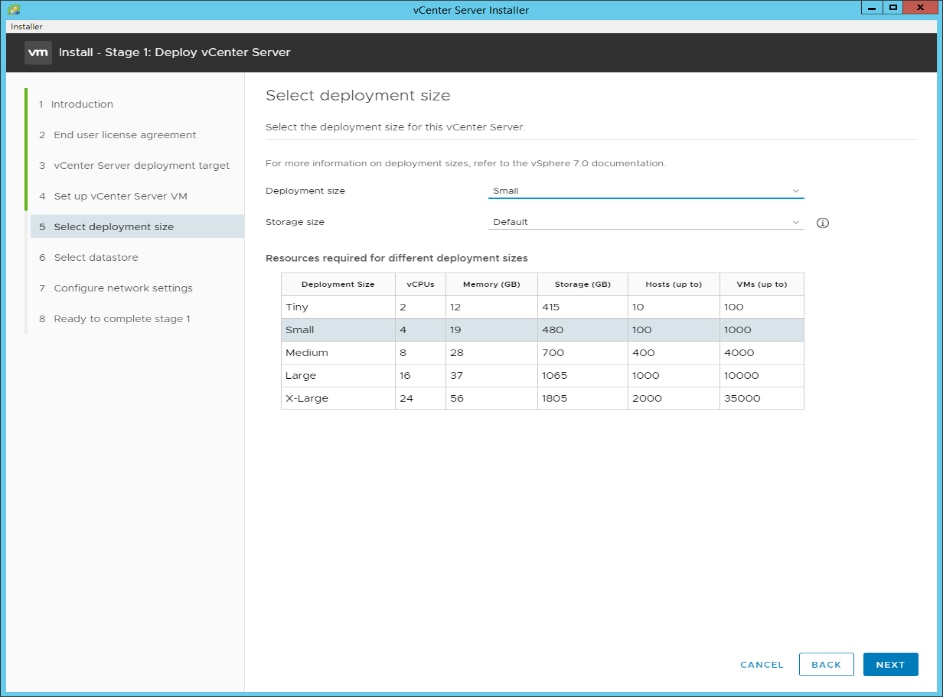
Step 11. Click infra_datastore for storage. Click NEXT.
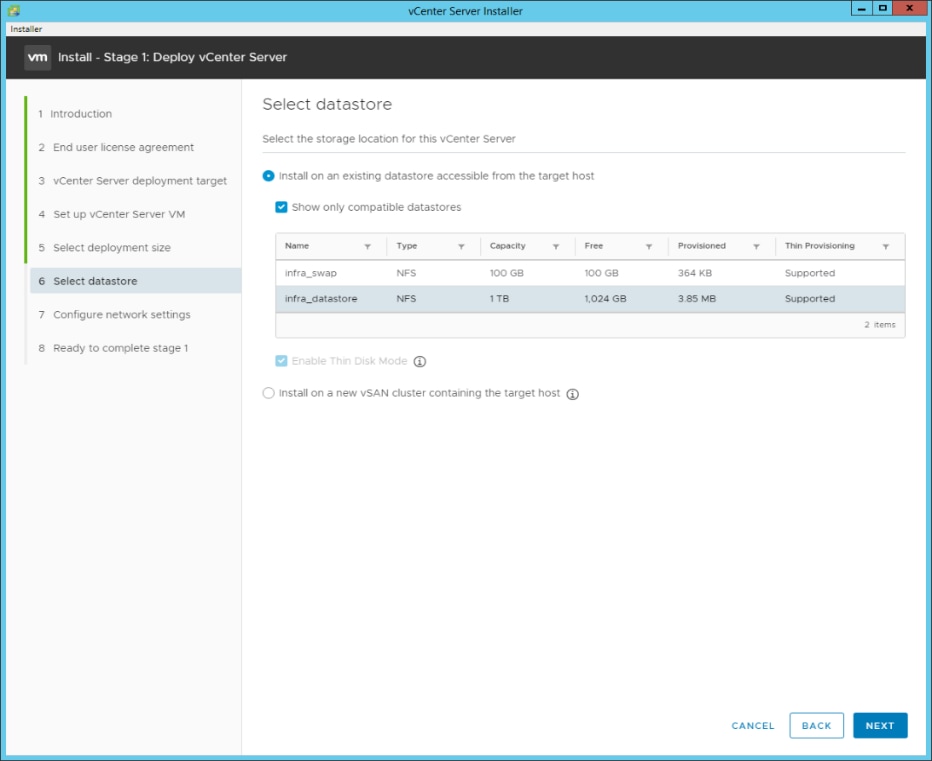
Step 12. In the Network Settings section, configure the following settings:
a. Click a Network: IB-MGMT Network.
Note: It is important that the vCenter VM stay on the IB-MGMT Network on vSwitch0 and that it not get moved to a vDS. If vCenter is moved to a vDS and the virtual environment is completely shut down and then brought back up, and it is attempted to bring up vCenter on a different host than the one it was running on before the shutdown, vCenter will not have a functional network connection. With the vDS, for a virtual machine to move from one host to another, vCenter must be up and running to coordinate the move of the virtual ports on the vDS. If vCenter is down, the port move on the vDS cannot occur correctly. Moving vCenter to a different host on vSwitch0 to be brought up always occurs correctly without requiring vCenter to already be up and running.
b. IP version: IPV4
c. IP assignment: static
d. FQDN: <vcenter-fqdn>
e. IP address: <vcenter-ip>
f. Subnet mask or prefix length: <vcenter-subnet-mask>
g. Default gateway: <vcenter-gateway>
h. DNS Servers: <dns-server1>,<dns-server2>
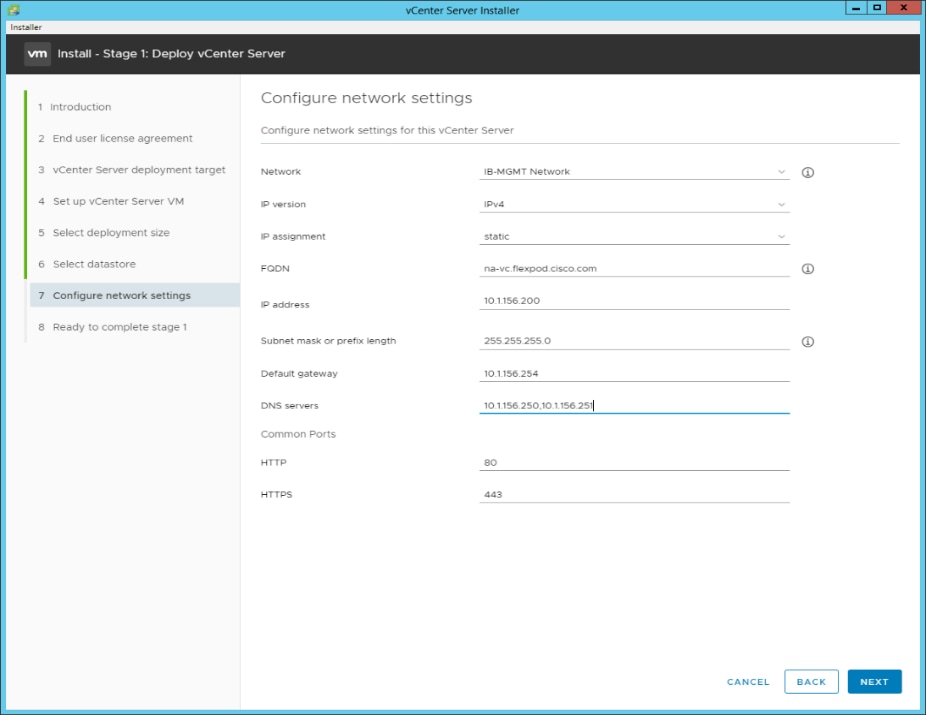
Step 13. Click NEXT.
Step 14. Review all values and click FINISH to complete the installation.
Note: The vCenter Server appliance installation will take a few minutes to complete.
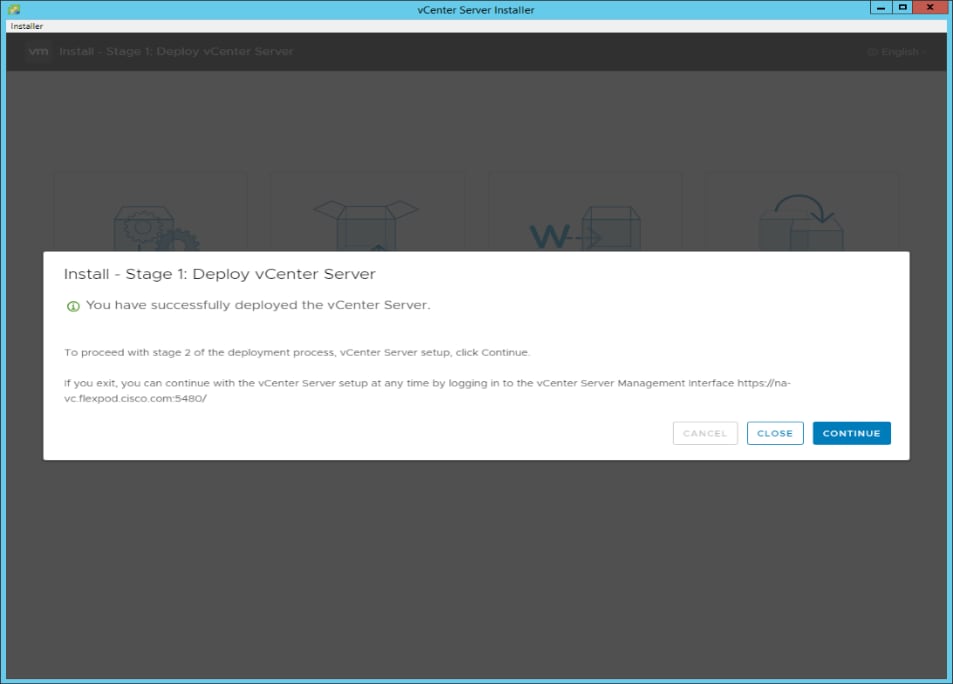
Step 15. Click CONTINUE to proceed with stage 2 configuration.
Step 16. Click NEXT.
Step 17. In the vCenter Server configuration window, configure these settings:
- Time Synchronization Mode: Synchronize time with NTP servers.
- NTP Servers: <nexus-a-ntp-ip>,<nexus-b-ntp-ip>
- SSH access: Enabled
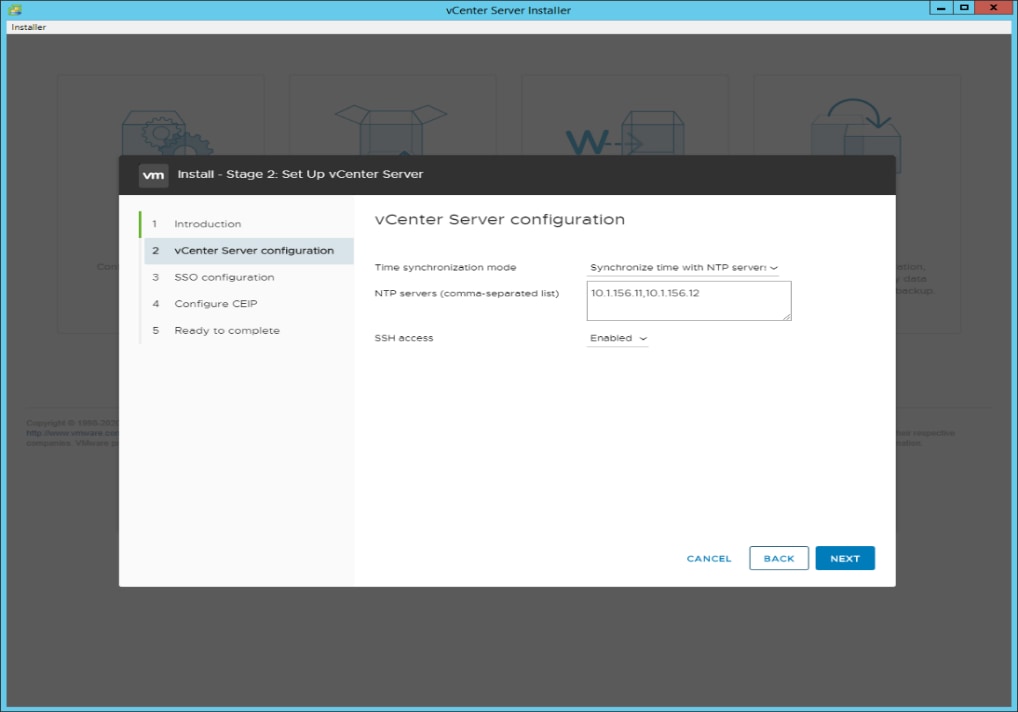
Step 18. Click NEXT.
Step 19. Complete the SSO configuration as shown below or according to your organization’s security policies:
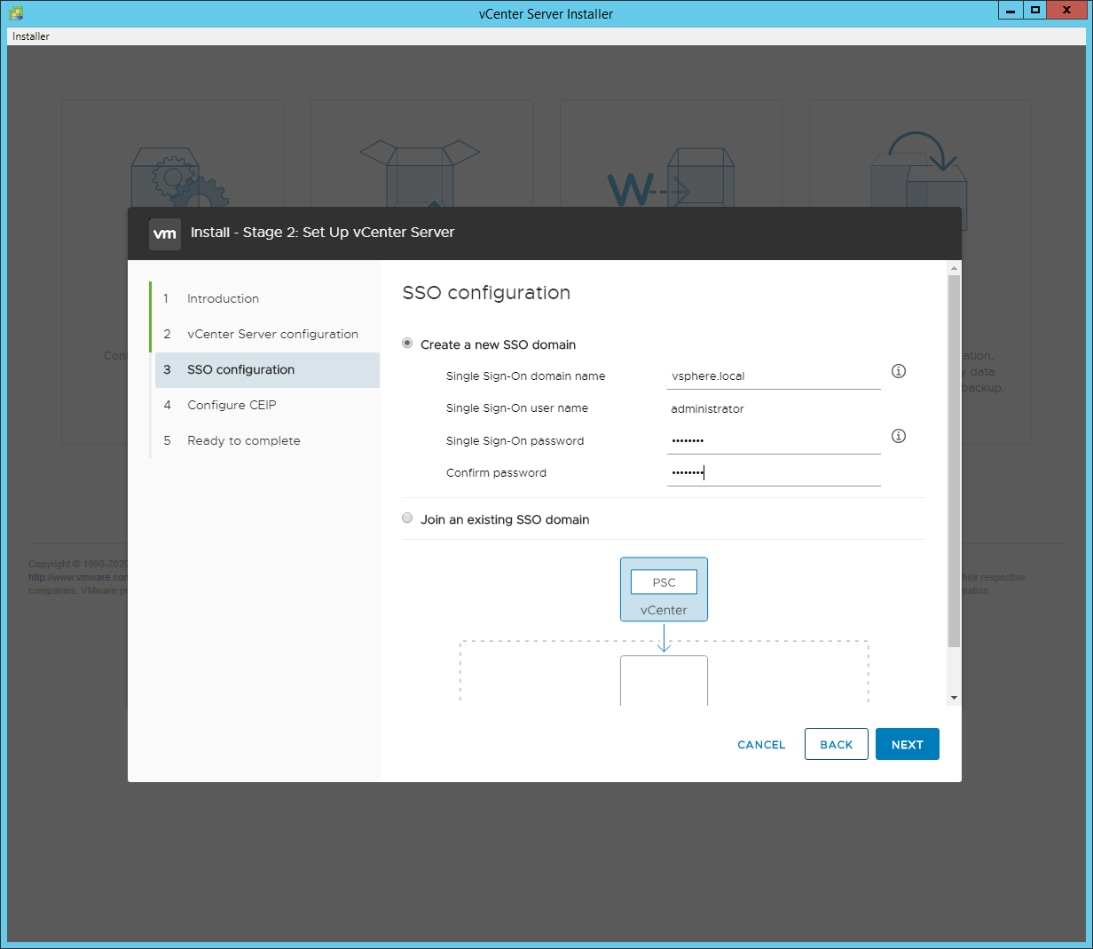
Step 20. Click NEXT.
Step 21. Decide whether to join VMware’s Customer Experience Improvement Program (CEIP).
Step 22. Click NEXT.
Step 23. Review the configuration and click FINISH.
Step 24. Click OK.
Note: The Server setup will take a few minutes to complete.
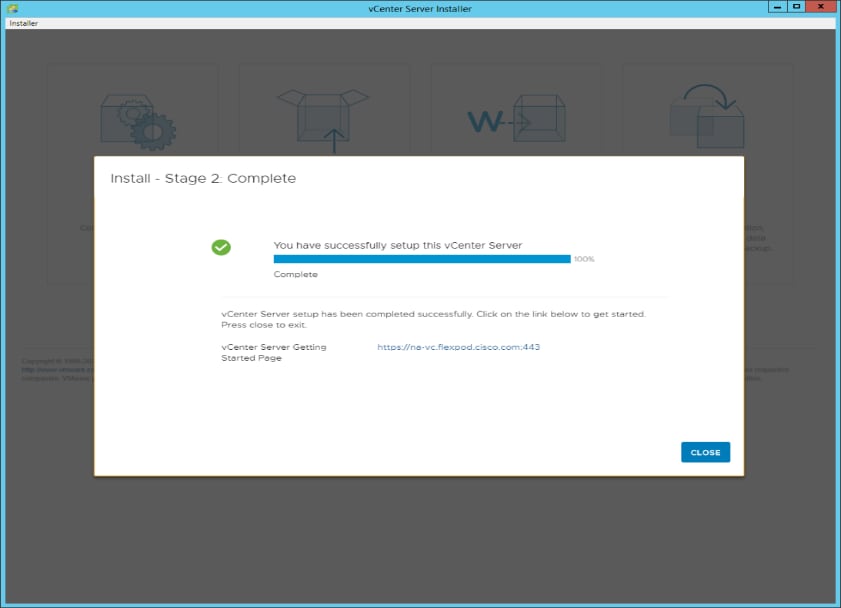
Two VMware Clusters in two vCenter data center were used to support the FlexPod for VDI solution.
This procedure covers creation of the VDI Workload Cluster dedicated to hosting VDI user workloads
Note: The Infrastructure Cluster, if not already existing in the customer environment, can be created using these procedures.
Procedure 1. Create and Prepare vSphere Cluster for VDI Workload
Step 1. Using a web browser, navigate to https://<vcenter-ip-address>:5480.
Step 2. Log into the VMware vCenter Server Management interface as root with the root password set in the vCenter installation.
Step 3. Click Time.
Step 4. Click EDIT.
Step 5. Select the appropriate Time zone and click SAVE.
Step 6. Click Administration.
Step 7. According to your Security Policy, adjust the settings for the root user and password.
Step 8. Click Update.
Step 9. Go to root > Logout to logout of the Appliance Management interface.
Step 10. Using a web browser, navigate to https://<vcenter-fqdn>.
Note: With VMware vCenter 8.0 U3 the use of the vCenter FQDN is required.
Step 11. Log in using the Single Sign-On username (administrator@vsphere.local) and password created during the vCenter installation.
Step 12. Click ACTIONS > New Datacenter.
Step 13. Type FlexPod-DC in the Datacenter name field.
Step 14. Click OK.
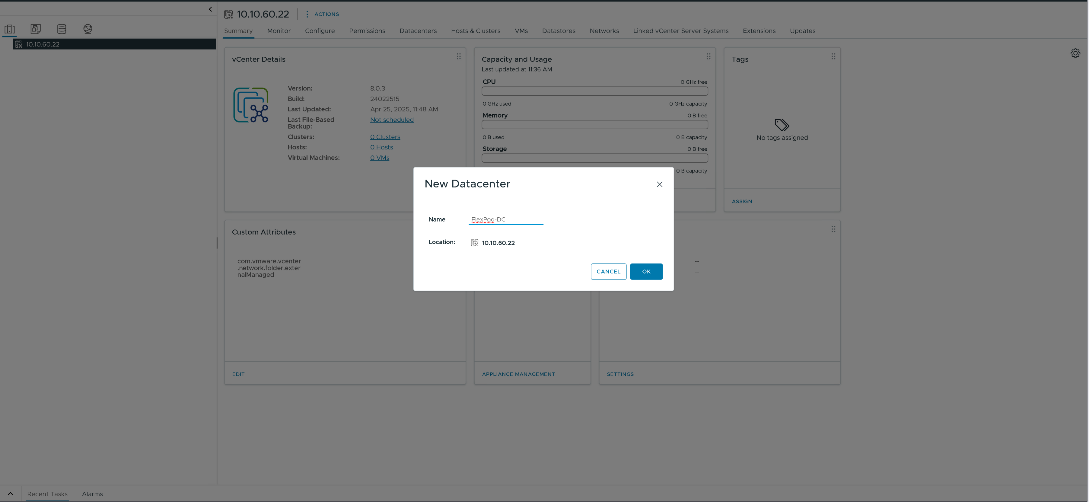
Step 15. Expand the vCenter.
Step 16. Right-click the datacenter FlexPod-DC in the list in the left pane. Click New Cluster.
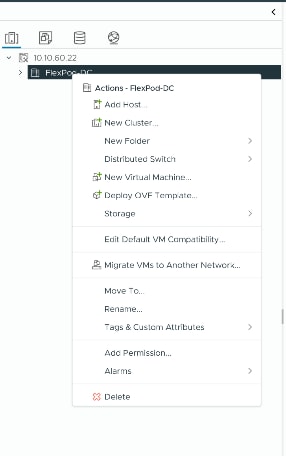
Step 17. Name the cluster FlexPod-VDI.
Step 18. Turn on DRS and click Next.
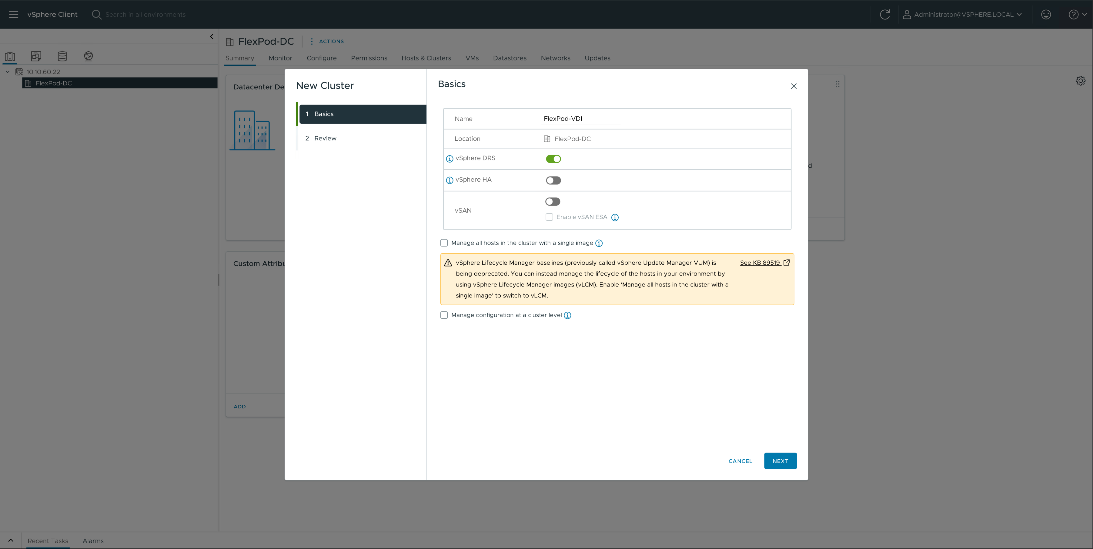
Step 19. Click OK to create the new cluster.
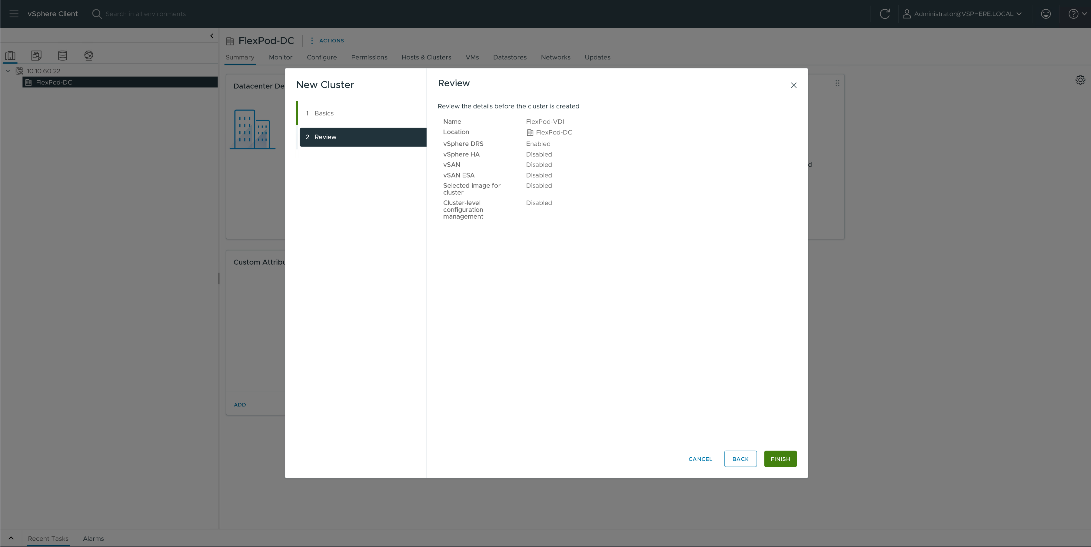
Step 20. Right-click FlexPod-VDI and click Settings.
Step 21. Click Configuration > Quickstart.
Step 22. In Add hosts field click Add.
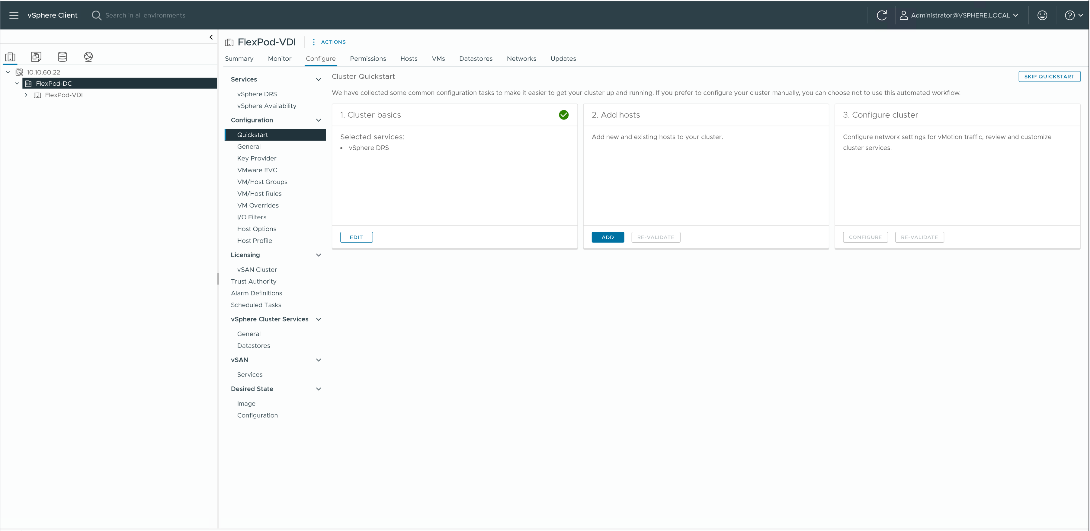
Step 23. In the IP address or FQDN field, enter either the IP address or the FQDN of the first VMware ESXi host. Enter root for the Username and the root password. Click NEXT.
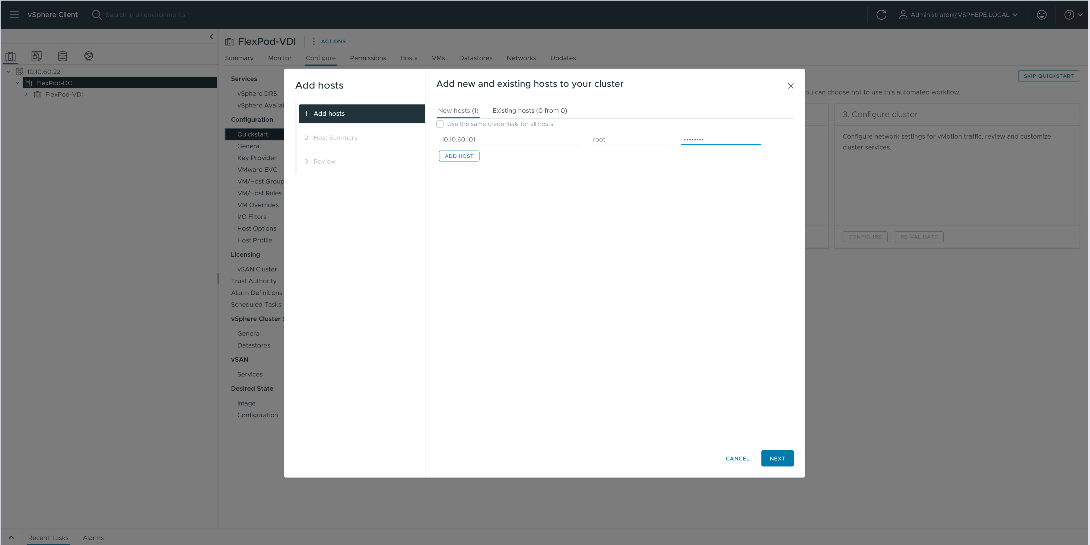
Step 24. In the Security Alert window, click the host and click OK.
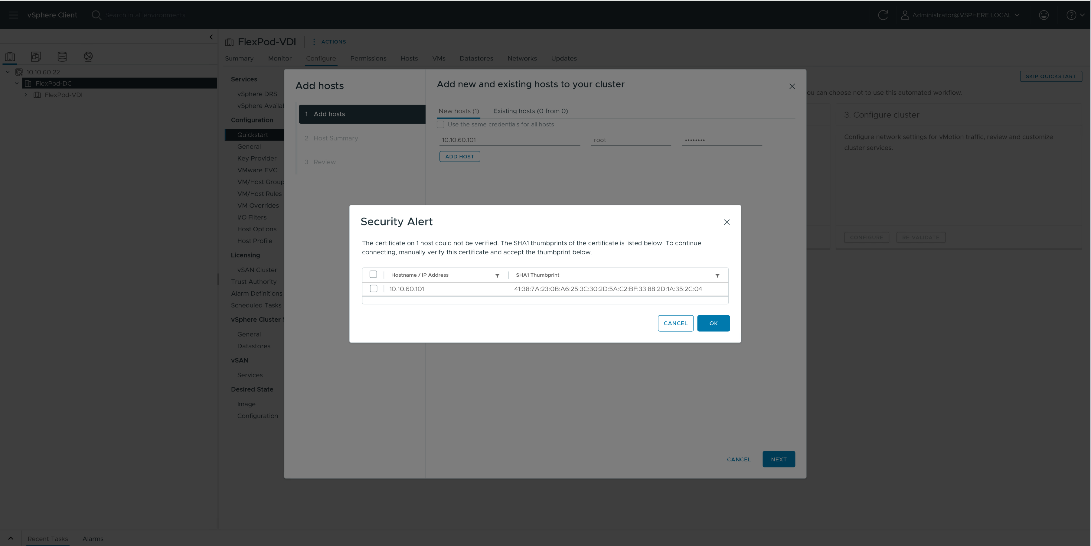
Step 25. Verify the Host summary information and click NEXT.
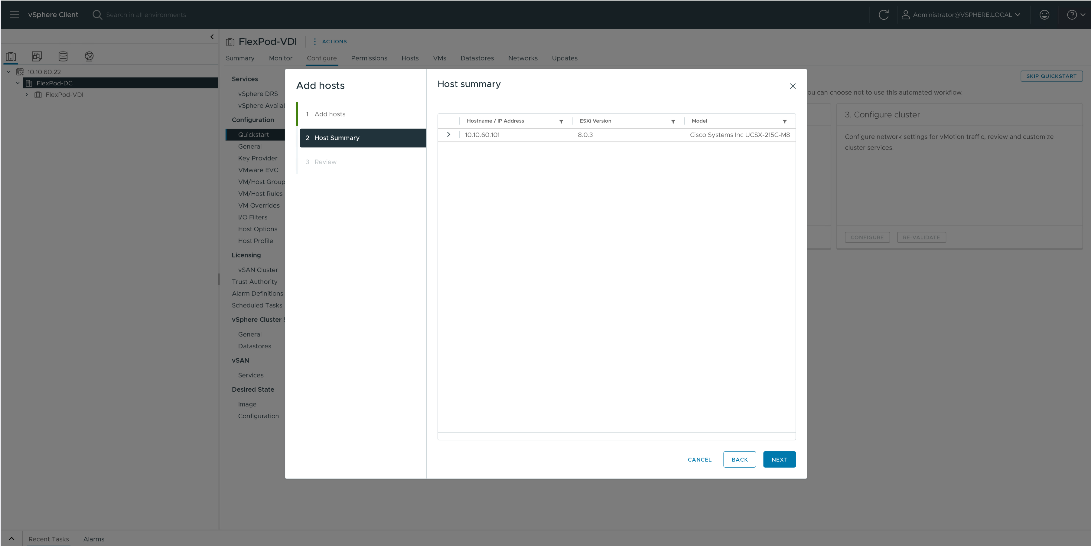
Step 26. Click Finish.
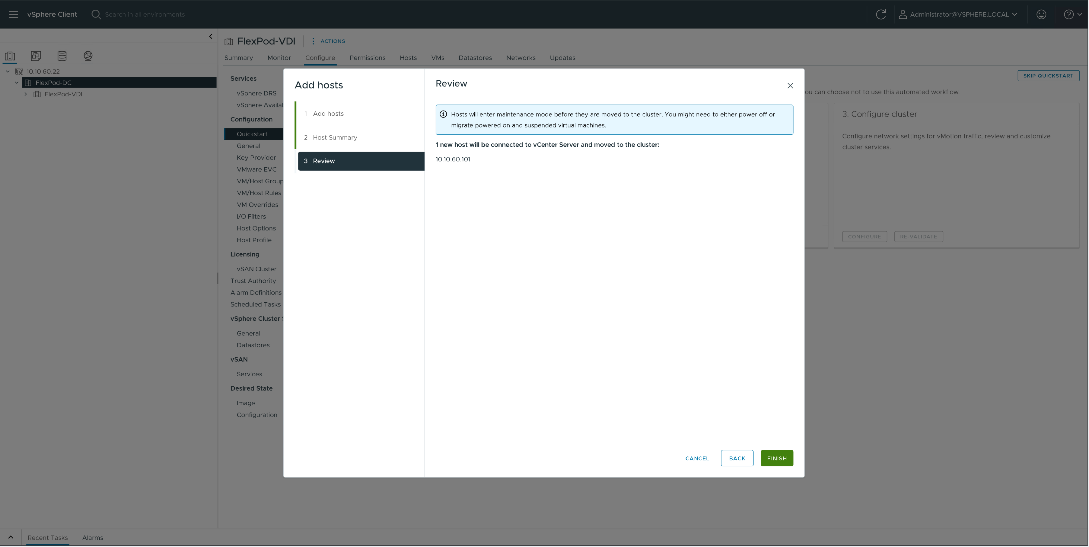
Note: The added ESXi host will have warnings that the ESXi Shell and SSH have been enabled. These warnings can be suppressed.
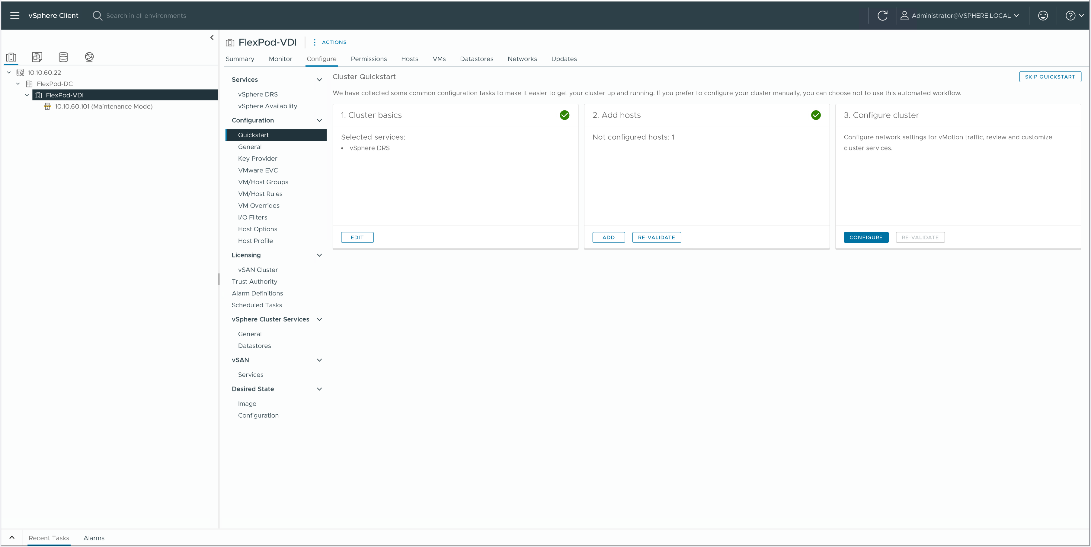
Step 27. Right-click Host object and click Settings
Step 28. Under Hardware, click Overview. Scroll down and ensure the Power Management Active policy is High Performance. If the Power Management Active policy is not High Performance, to the right of Power Management, click EDIT POWER POLICY.
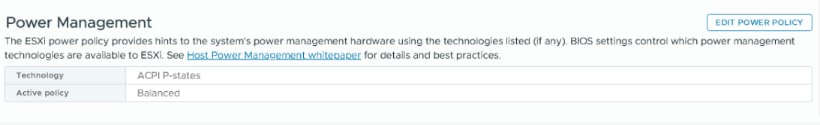
Step 29. Click High performance and click OK.
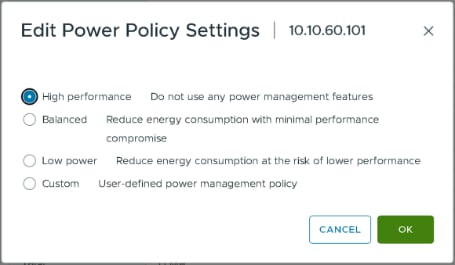
Step 30. Configure NTP for all hosts in your vSphere cluster.
Step 1. On the vSphere Web Client home screen, select the Host object from the list on the left. From the Configure tab System area click Time Configuration.
Step 2. From Add Service drop-down list select Network Time protocol option.
Step 3. Provide the IP addresses for the NTP servers in your environment. Click OK.
Step 4. Test the service configuration.
Step 1. In the vSphere Web Client home screen, select the vCenter object from the list on the left. From the Inventory Lists area click Datacenter, then from the Actions list select Distributed Switch and click New Distributed Switch.
Step 2. Provide a name for the new distributed switch and select the location within the vCenter inventory where you would like to store the new vDS (a data center object or a folder). Click NEXT.
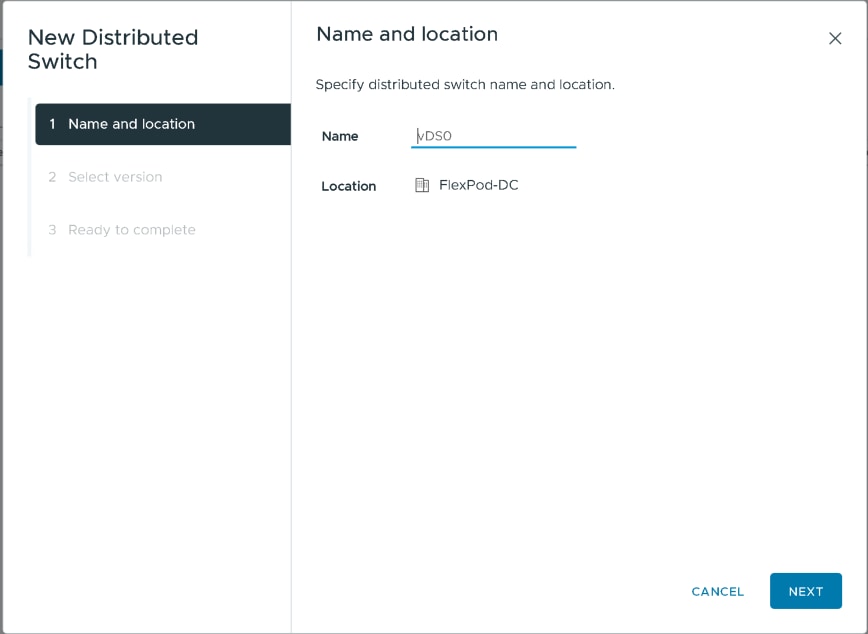
Step 3. Select the version of the vDS to create. Click NEXT.
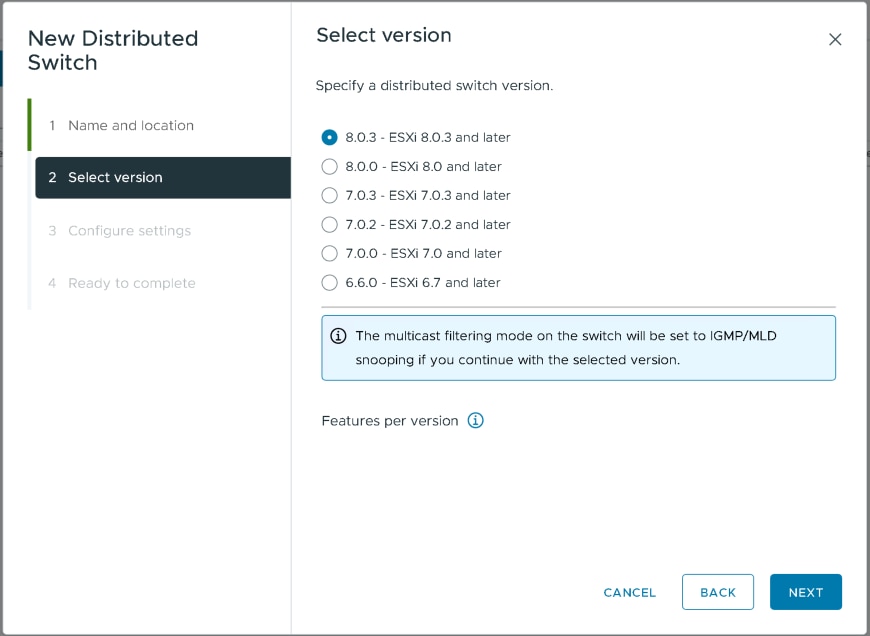
Step 4. Specify the Network Offloads compatibility as None and the number of uplink ports as 2. Uncheck the Create a default port group box. Click NEXT.
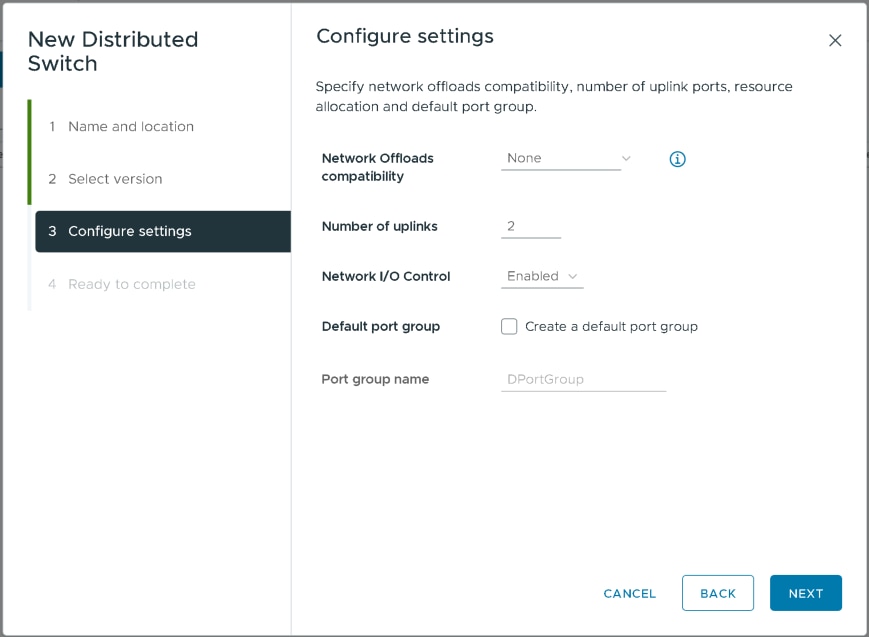
Step 5. Click Finish.
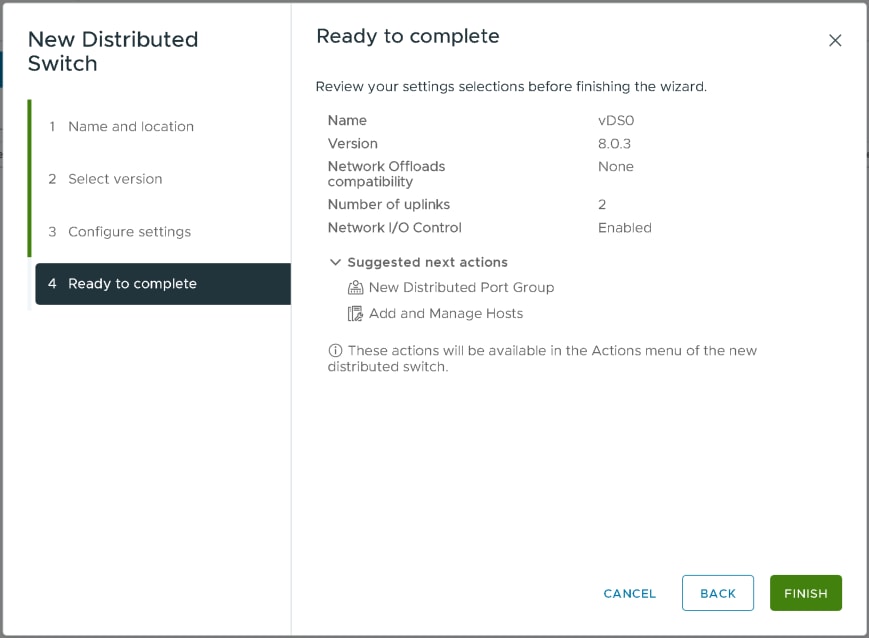
Step 6. Right-click the new distributed switch in the list of objects and select Settings > Edit Settings....
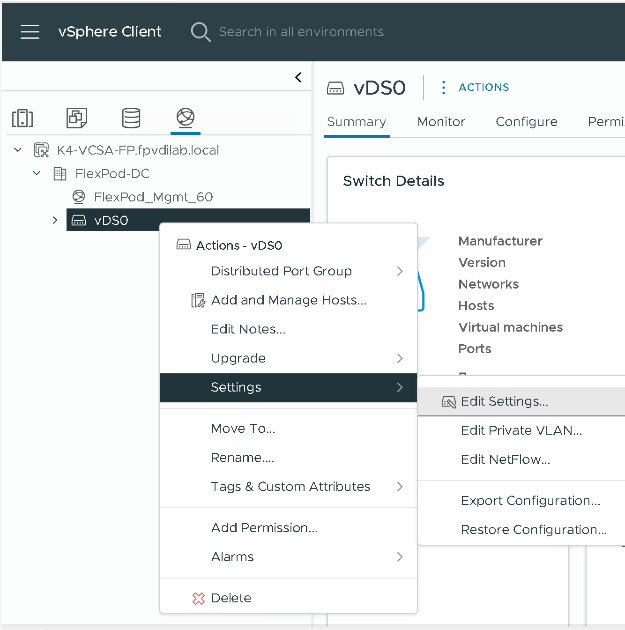
Step 7. In the Distributed Switch-Edit Settings dialog box Advanced tab, set the MTU to 9000, Discovery protocol to Link Layer Discovery Protocol and Operation to Both. Click OK.
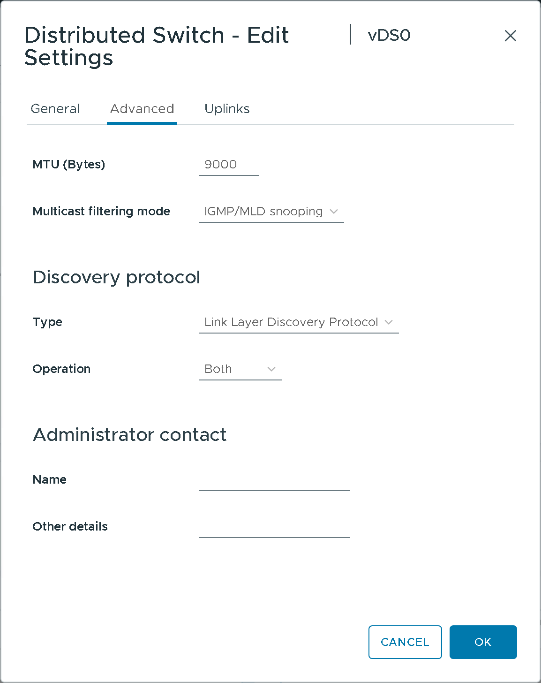
Note: In server profiles vmnic2 and vmnic3 are created for the use as vDS uplinks.
Step 8. Right-click the new distributed switch in the list of objects and select Add and Manage Hosts from the Actions menu.
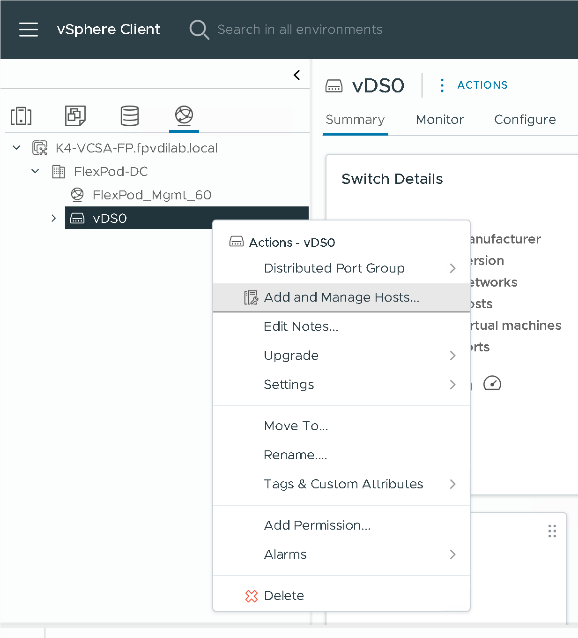
Step 9. Select the Add hosts button and click NEXT.
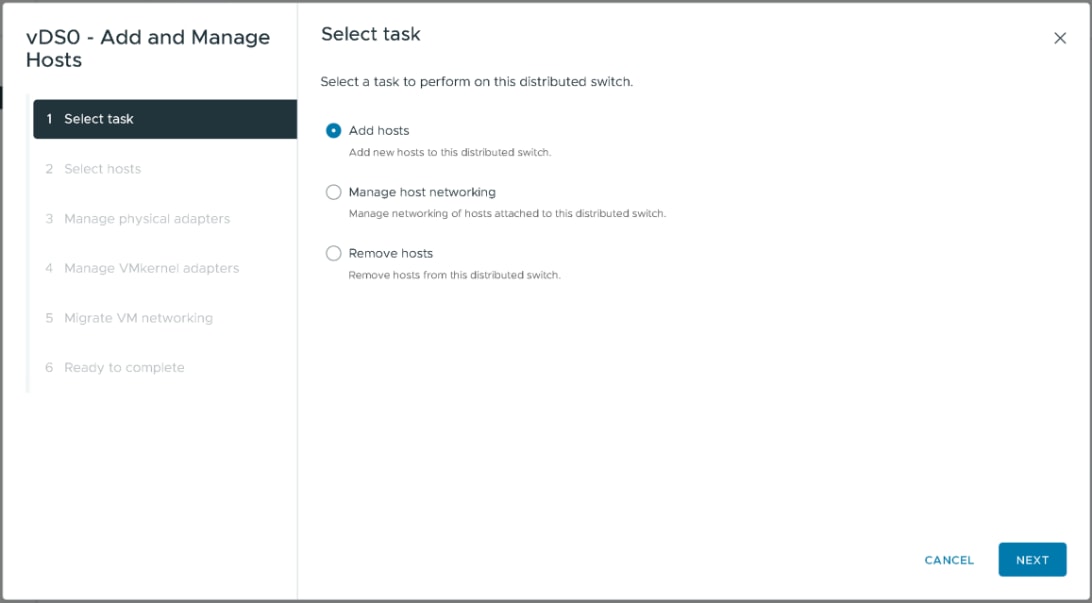
Step 10. From the list of the new hosts, check the boxes with the names of each ESXi host you would like to add to the VDS. Click NEXT.
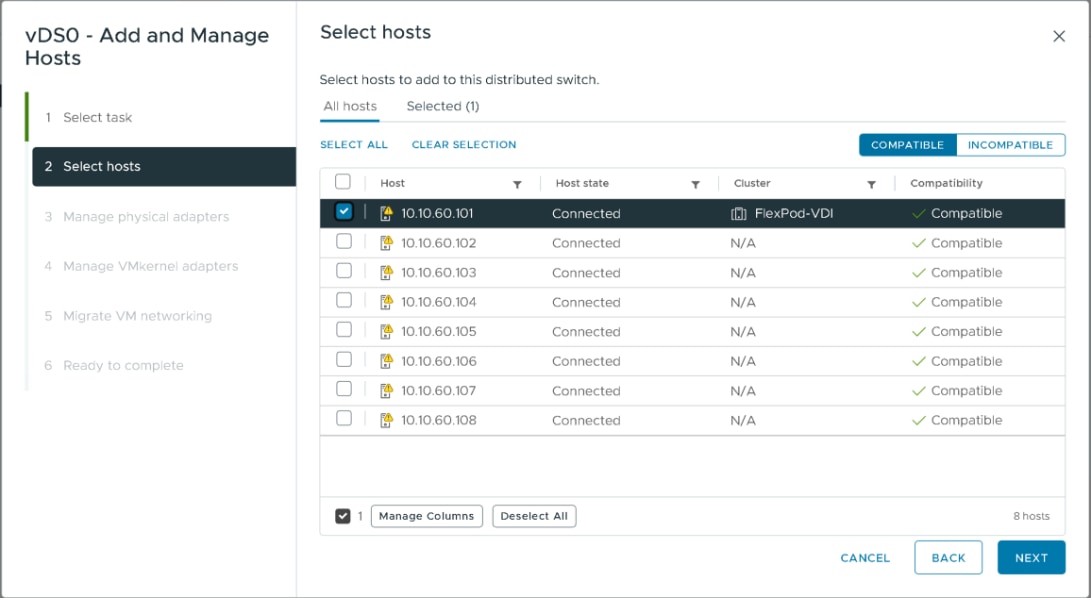
Step 11. In the Manage physical adapters menu, click Adapters on all hosts and configure the adapters (in this case - vmnic2 and vmnic3) in an ESXi host as Uplink 1 and Uplink 2 for the vDS.
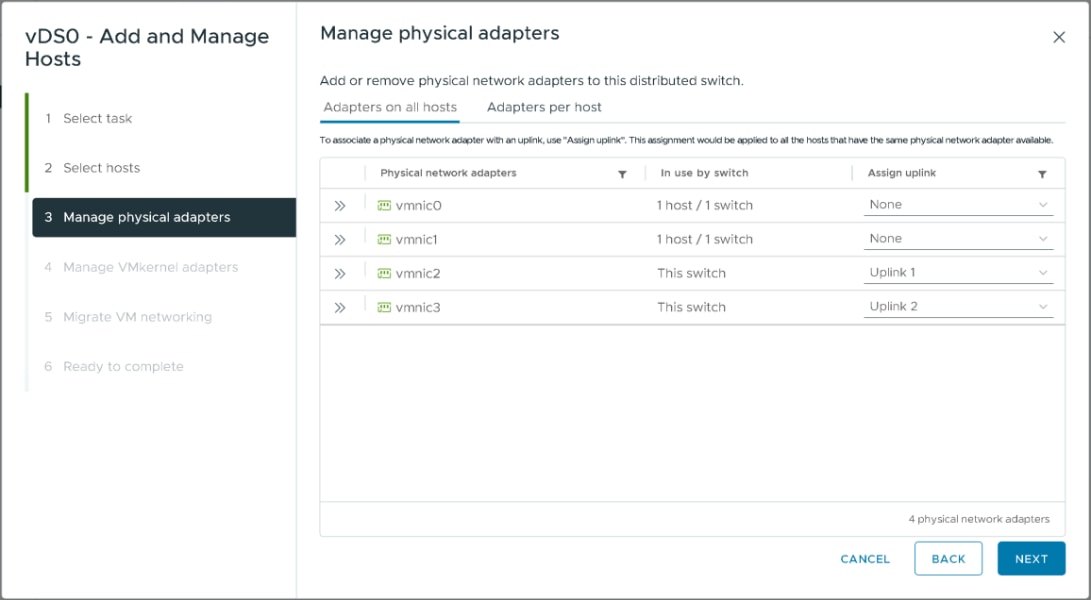
Step 12. In the Manage VMkernel, click NEXT to continue.
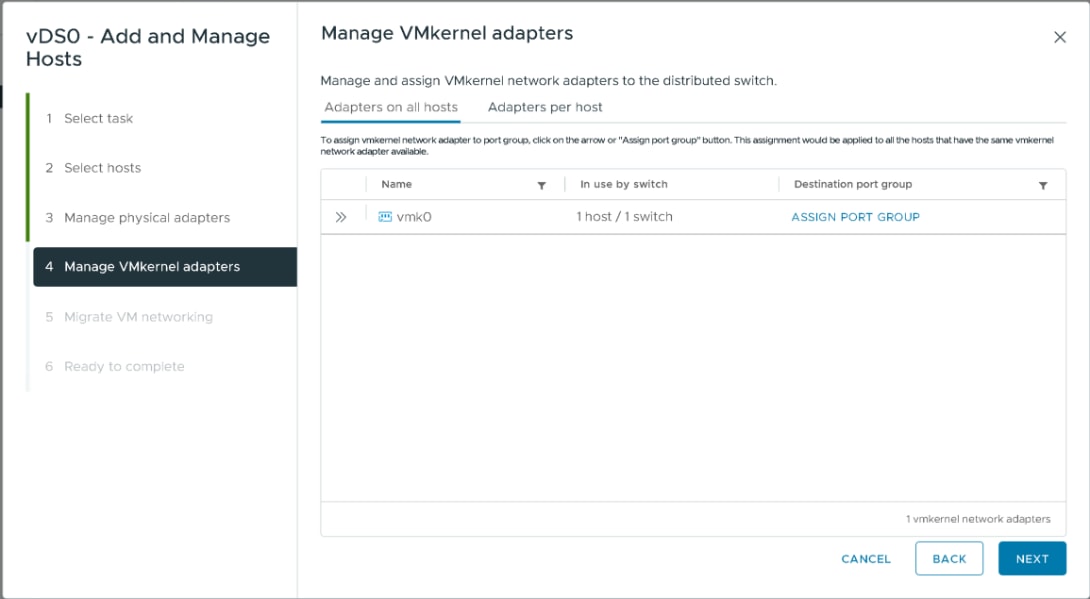
Step 13. In the Migrate VM networking, click NEXT to continue.
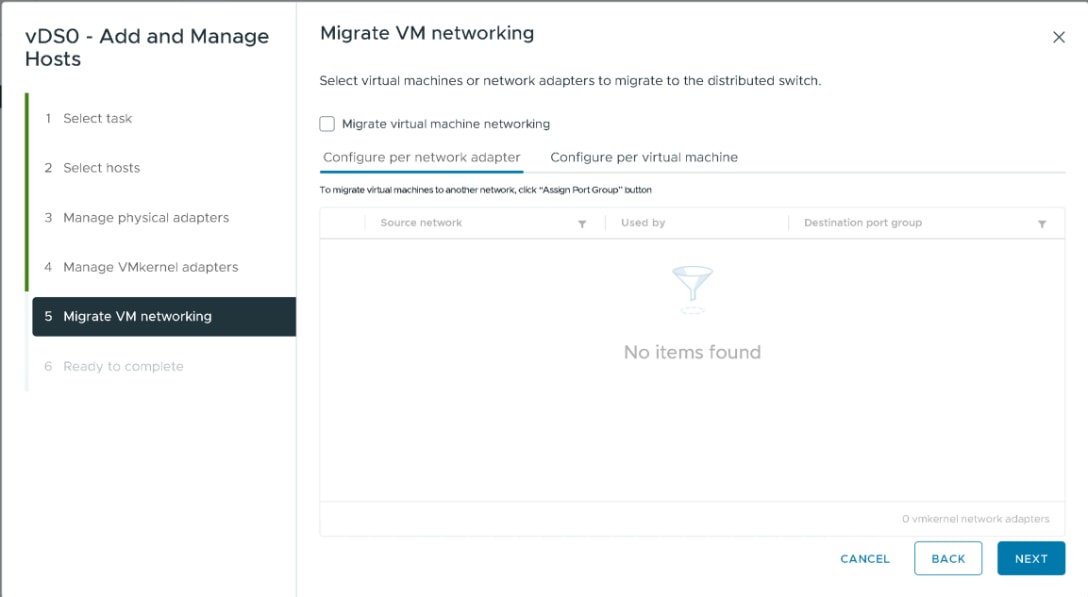
Step 14. Click FINISH.
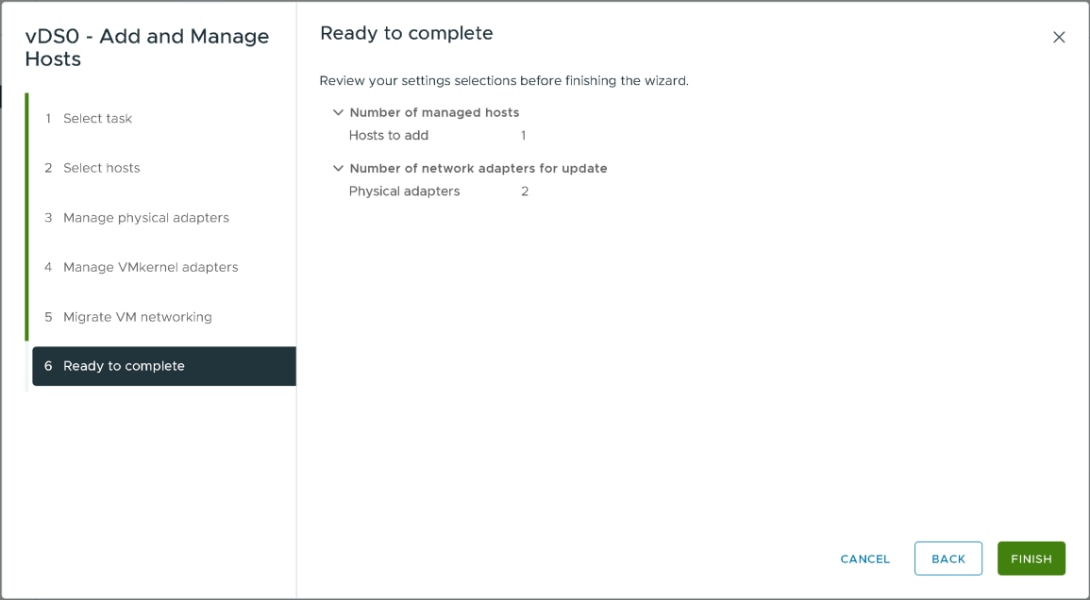
Procedure 4. Create a Distributed Port Group for vMotion traffic
Step 1. Right-click Distributed switch and select Distributed Port Group then click New Distributed Port Group.
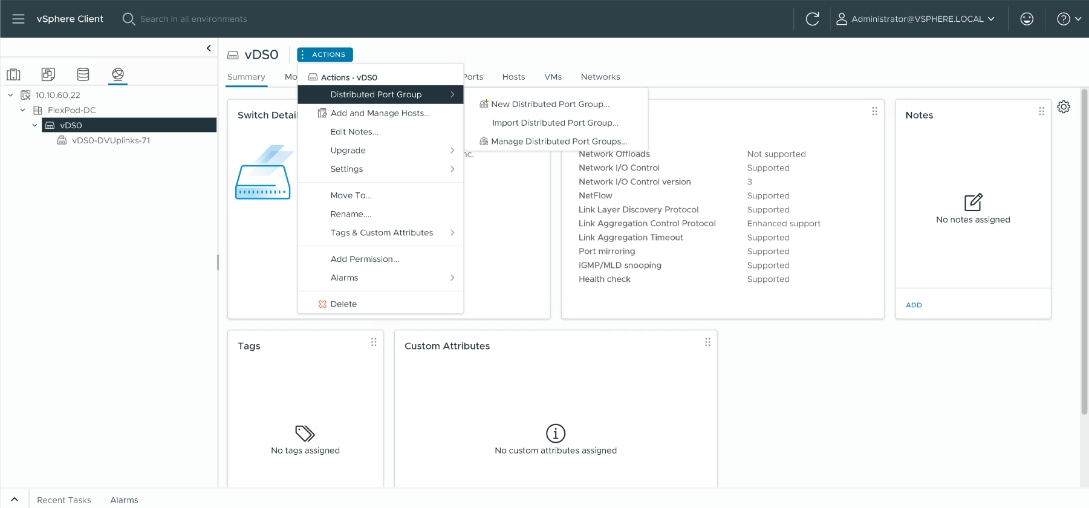
Step 2. On the New Distributed Port Group dialog box, enter a Name (for example vMotion), and click NEXT.
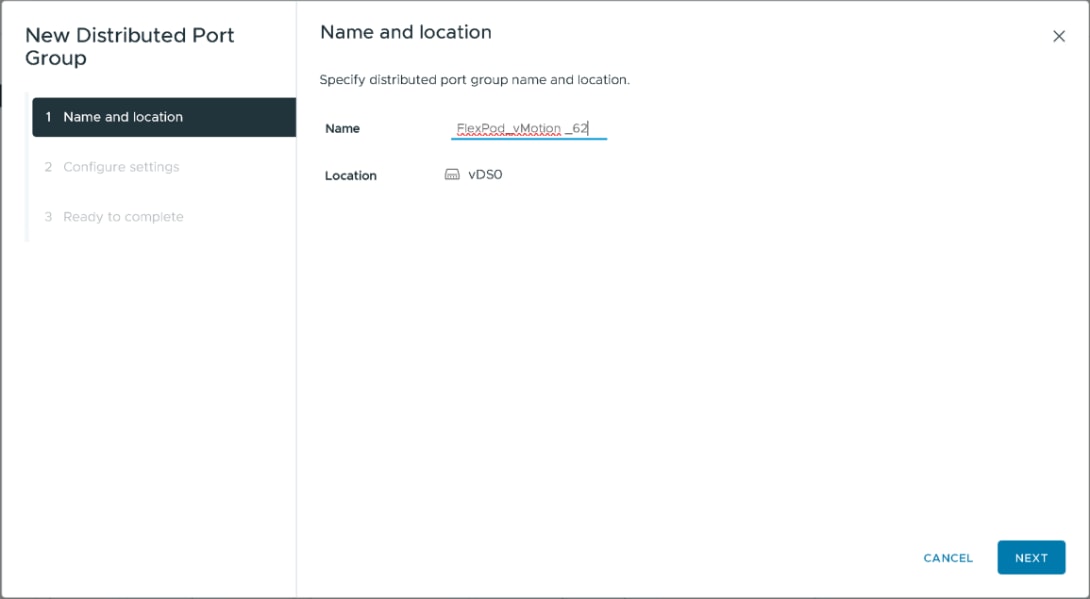
Step 3. In the VLAN type field, select VLAN, and set the VLAN ID to your VLAN (–for example 62). Check the Customize default policies configuration checkbox and click NEXT.
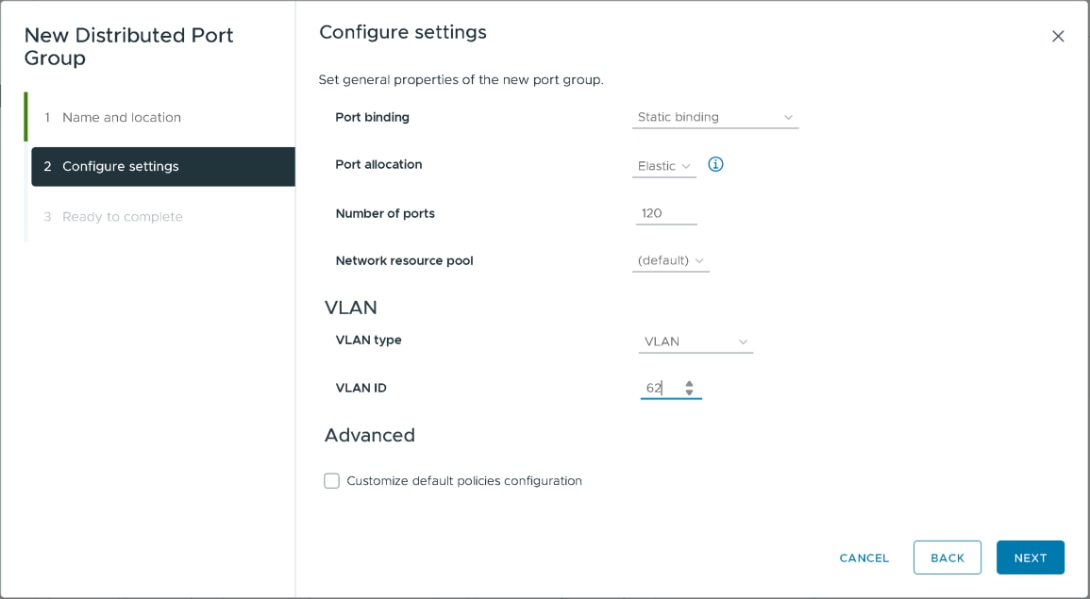
Step 4. In the Ready to complete dialog box, review all the changes, and click FINISH.
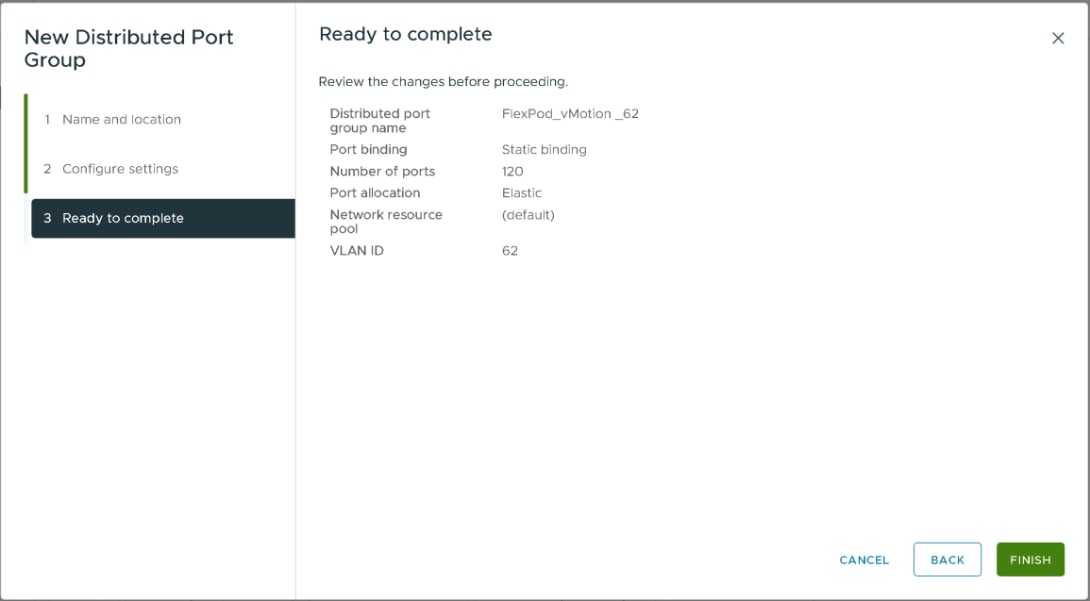
Procedure 5. Create a Distributed Port Groups for VDI and Storage traffic
Step 1. Right-click the Distributed switch and select Distributed Port Group then click New Distributed Port Group.
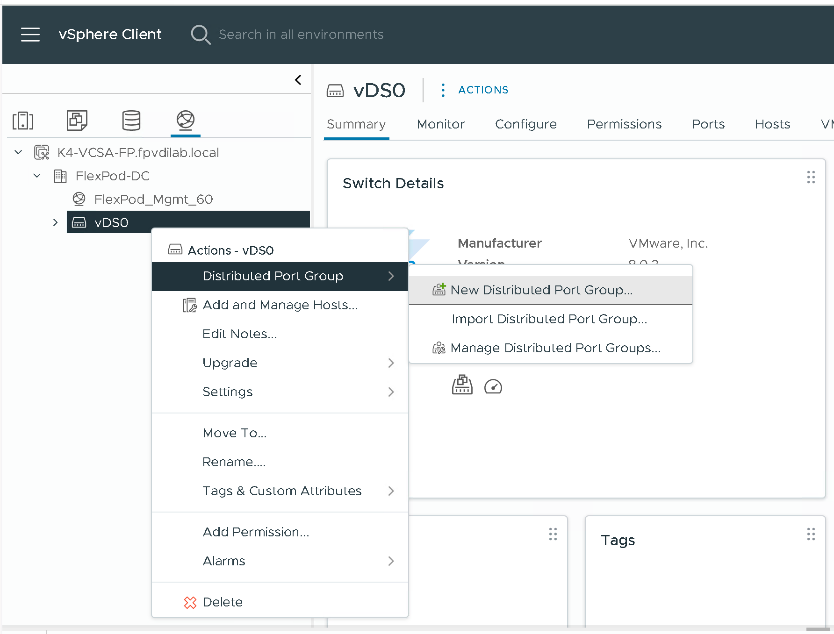
Step 2. On the New Distributed Port Group dialog box, enter a Name, and click NEXT.
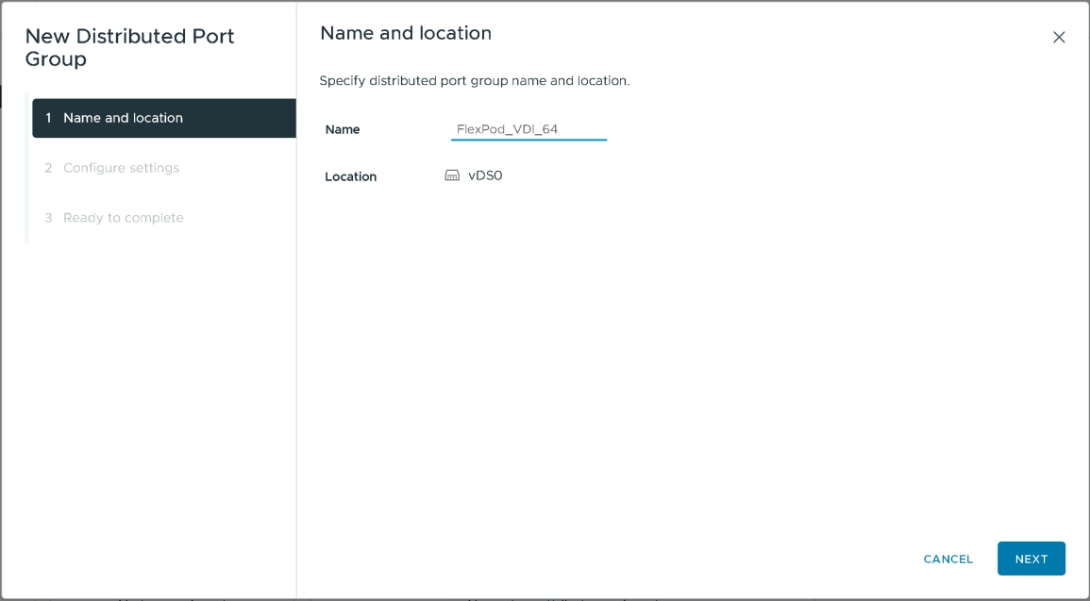
Step 3. In the VLAN type field, select VLAN, and set the VLAN ID to your VLAN (–for example 64). Check the Customize default policies configuration checkbox and click NEXT.
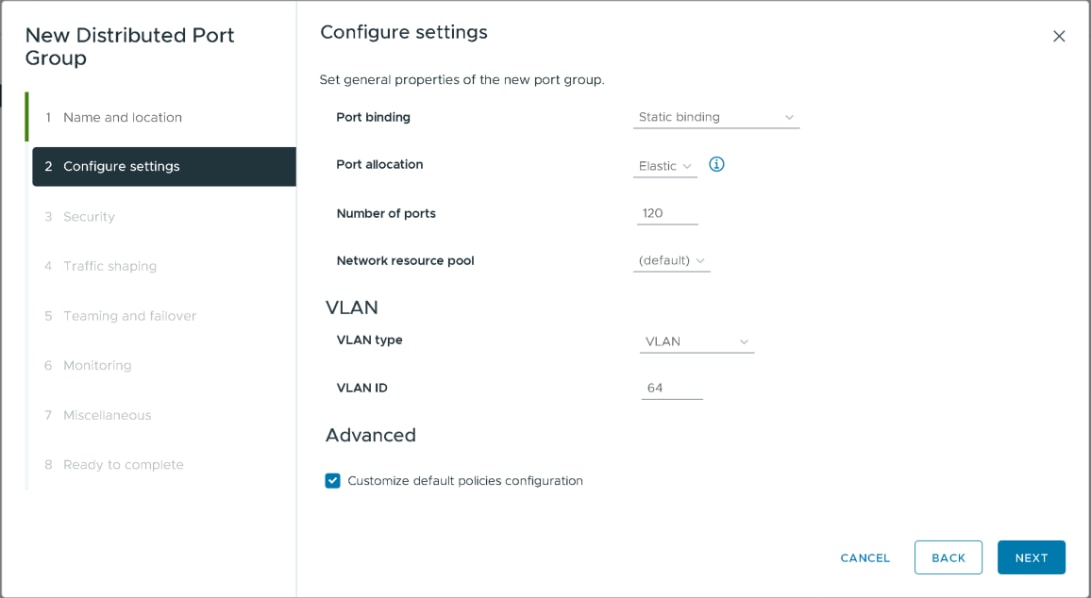
Step 4. On the Security dialog box, click NEXT.
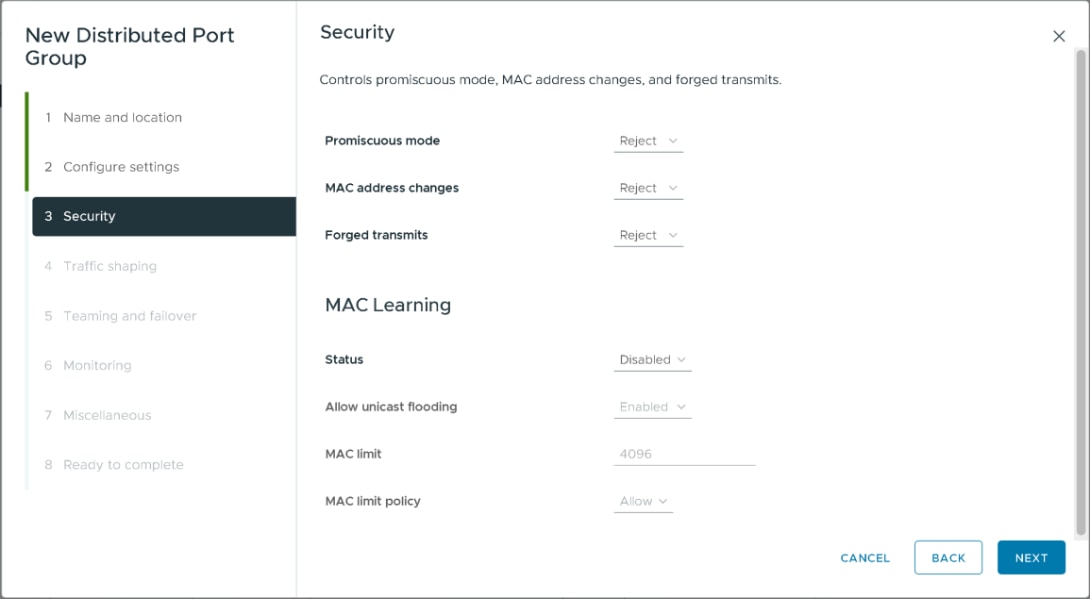
Step 5. On the Traffic shaping dialog box, click NEXT.
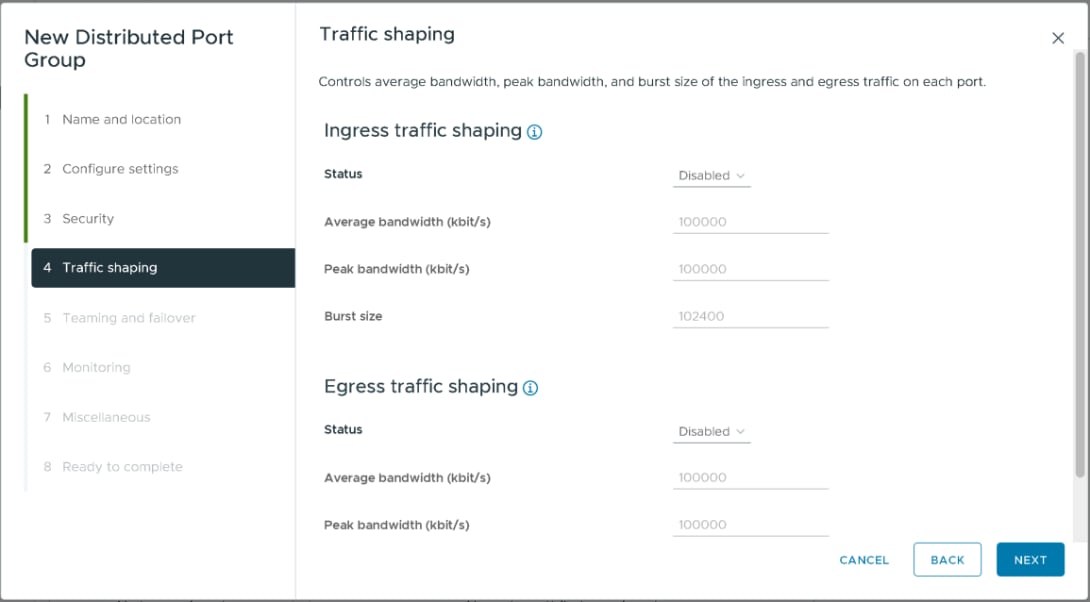
Step 6. In the Teaming and failover dialog box, for Active uplinks set Uplink 1 and Uplink 2. Click NEXT.
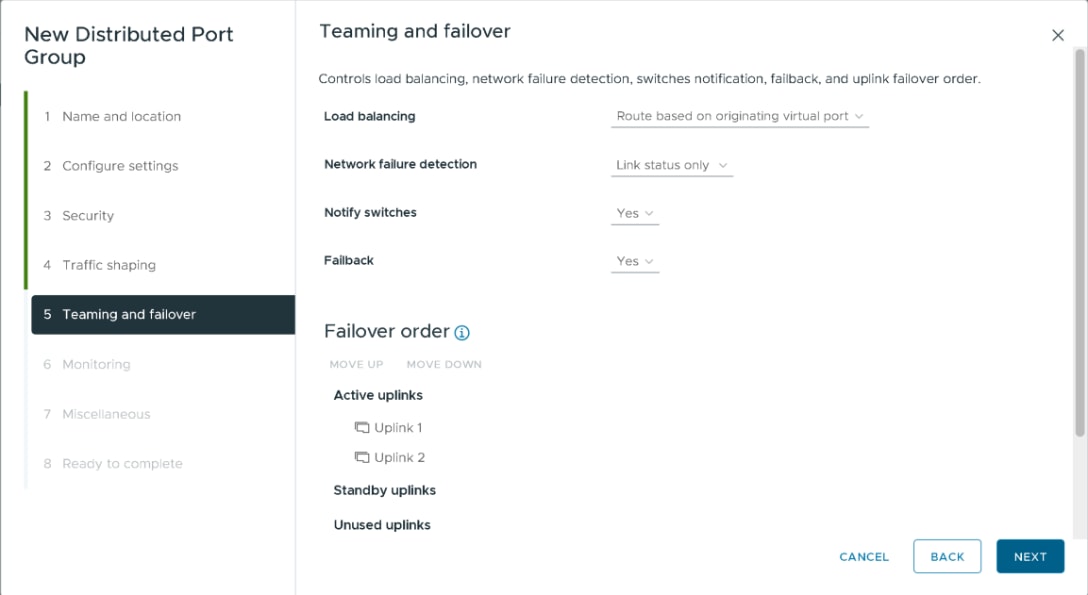
Step 7. In the Monitoring dialog box, set NetFlow to Disabled, and click NEXT.
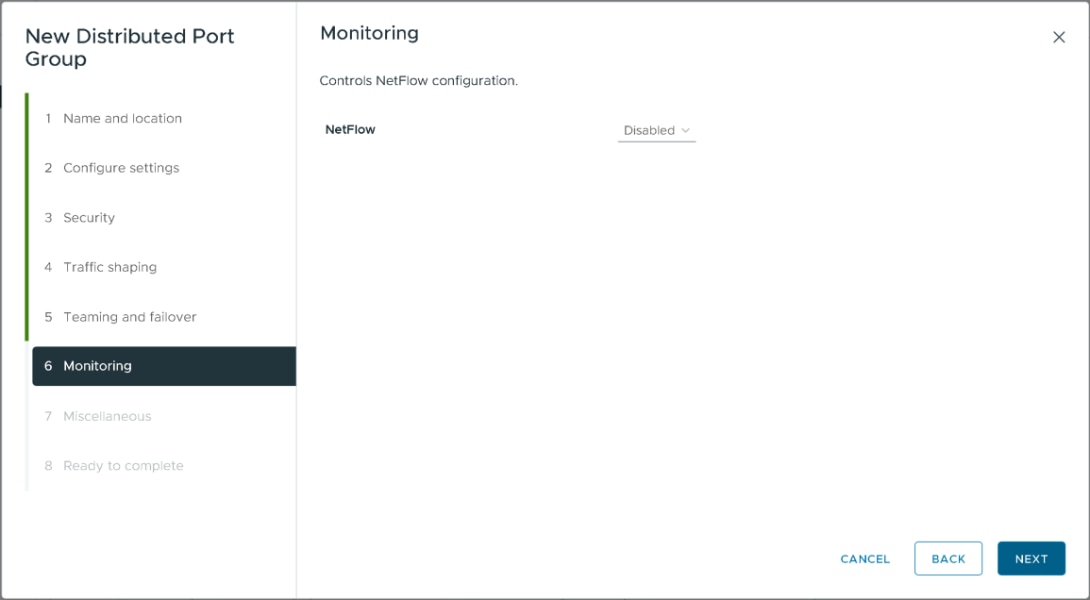
Step 8. In the Miscellaneous dialog box, set Block All Ports to No, and click NEXT.
Step 9. In the Ready to complete dialog box, review all the changes, and click FINISH.
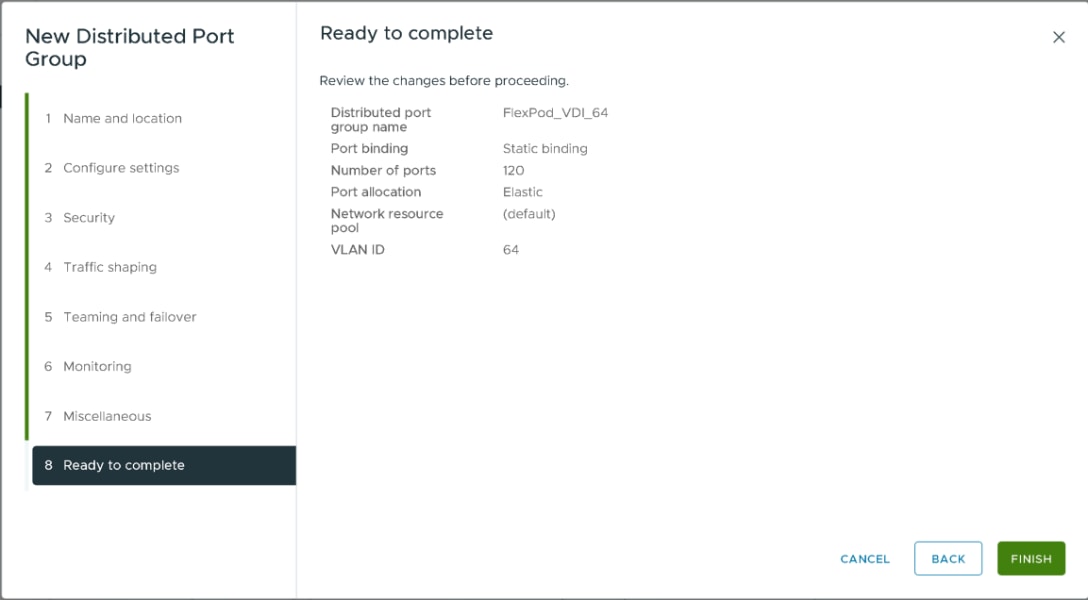
Step 10. Repeat this procedure to create Distributed Port Group for Storage traffic.
Procedure 6. Add a VMkernel Adapters to distributed port groups
Step 1. Right-click the distributed port group and select Add VMkernel Adapters….
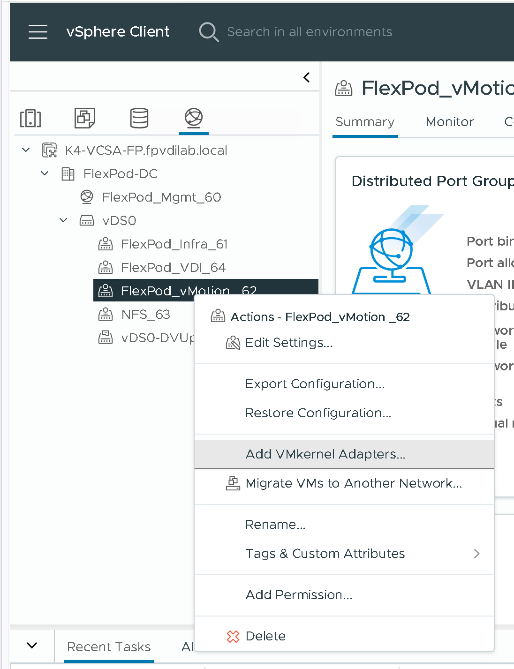
Step 2. Select Attached Hosts and click NEXT.
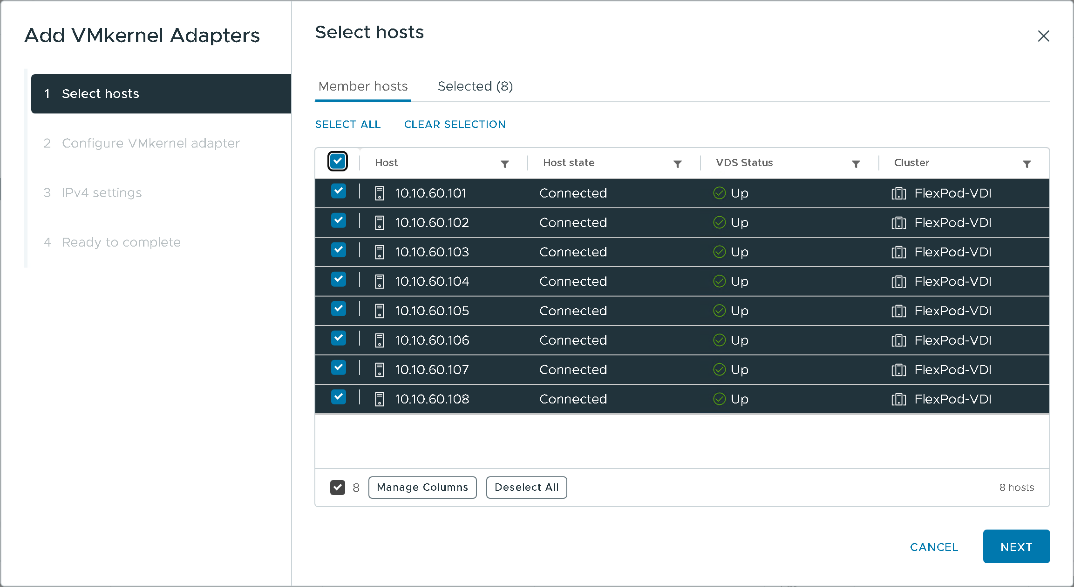
Step 3. Select service (for example vMotion) in Available services and click NEXT.
Note: NFS VMkernel adapters does not require any services.
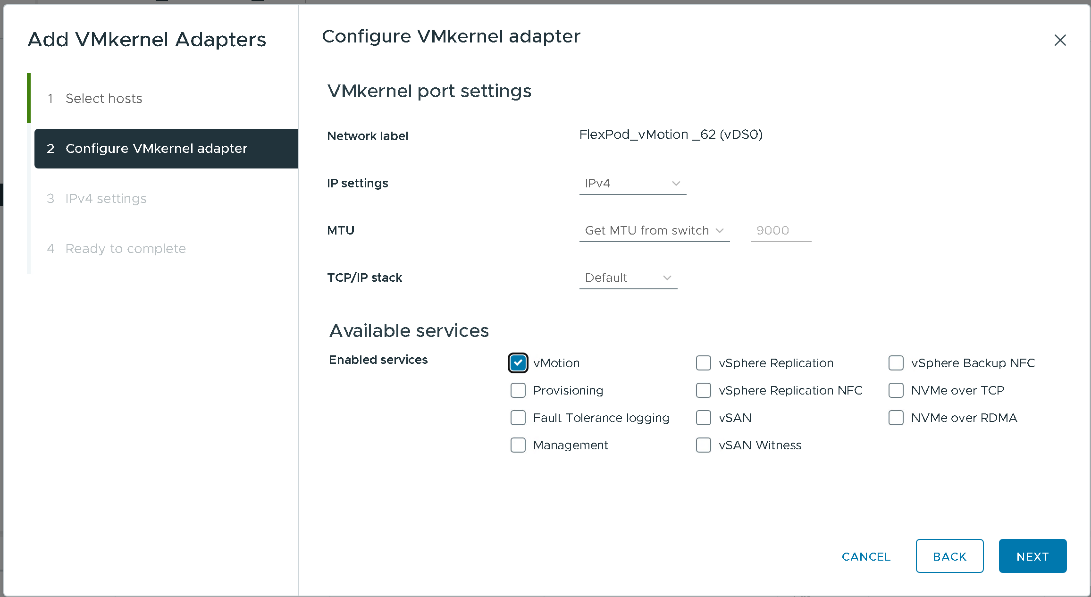
Step 4. Enter the Network Settings and Gateway details and click NEXT.
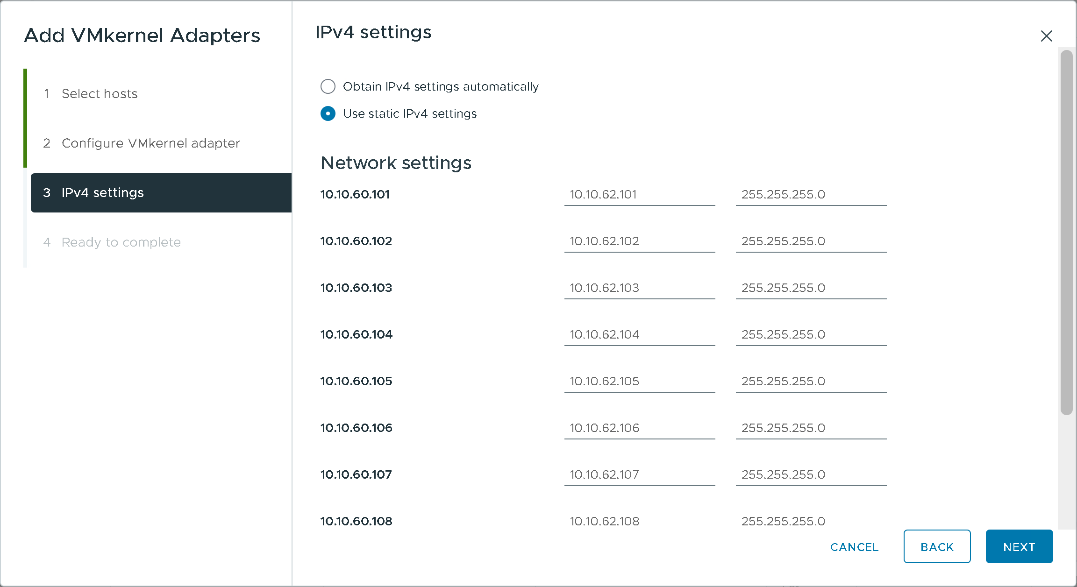
Step 5. Click FINISH.
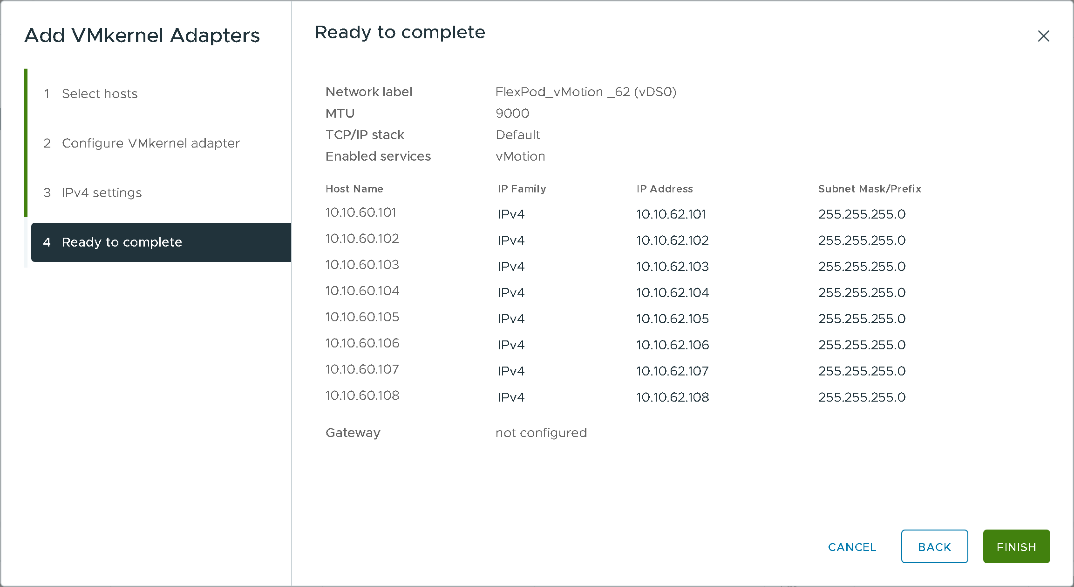
Step 6. Repeat the Add VMkernel Adapters… steps for the NFS traffic, and any other required port groups.
Note: Completed configuration can be verified under the Distributed Switch Topology tab.
Procedure 7. Create FC datastores
Step 1. Right-click the Cluster or Host in the inventory.
Step 2. Go to Storage > New Datastore.
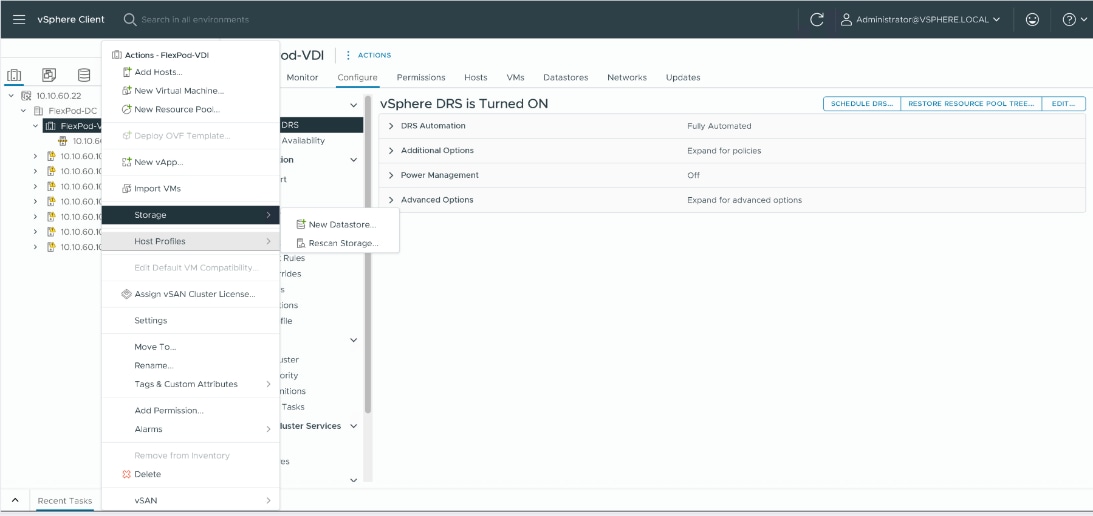
Step 3. Select VMFS as the datastore type and click Next.
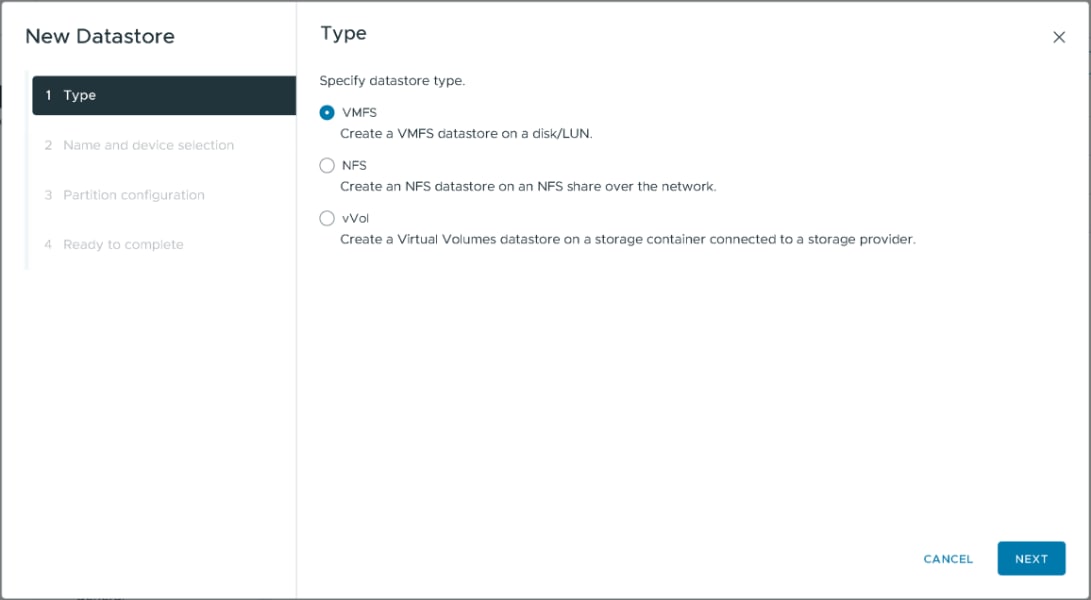
Step 4. Provide a Datastore Name.
Step 5. Select the newly discovered LUN from the list of available devices.
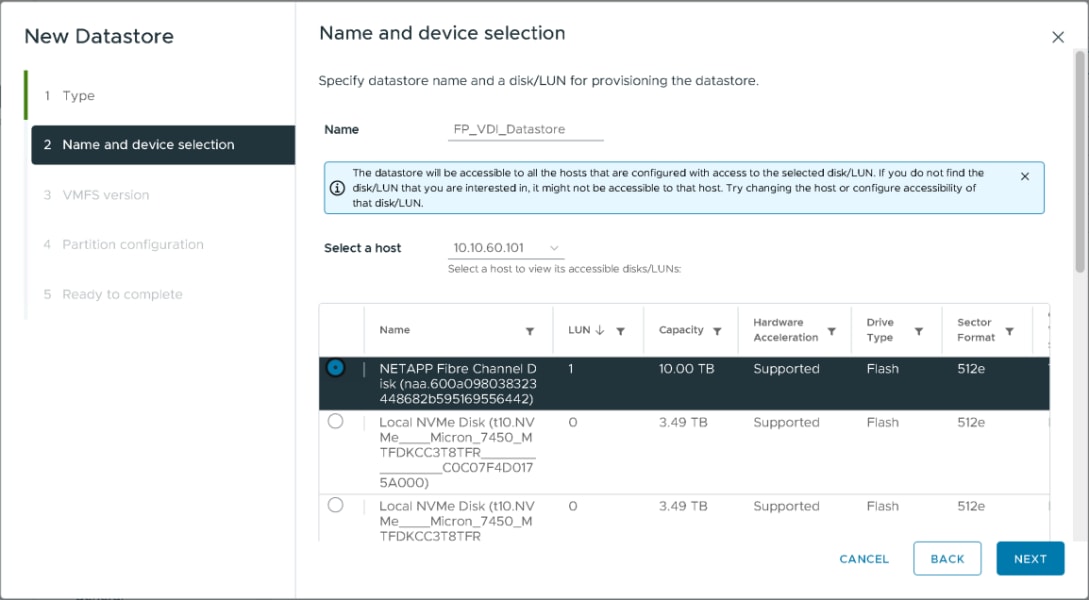
Step 6. Select the VMFS version VMFS 6.
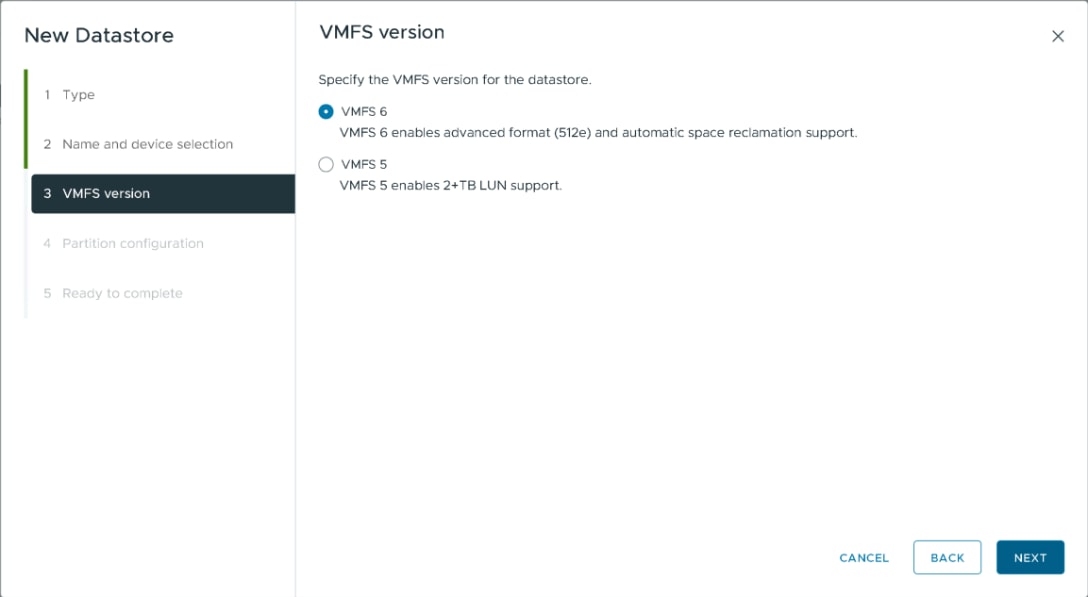
Step 7. Review the partition configuration (default is usually to use the entire disk).
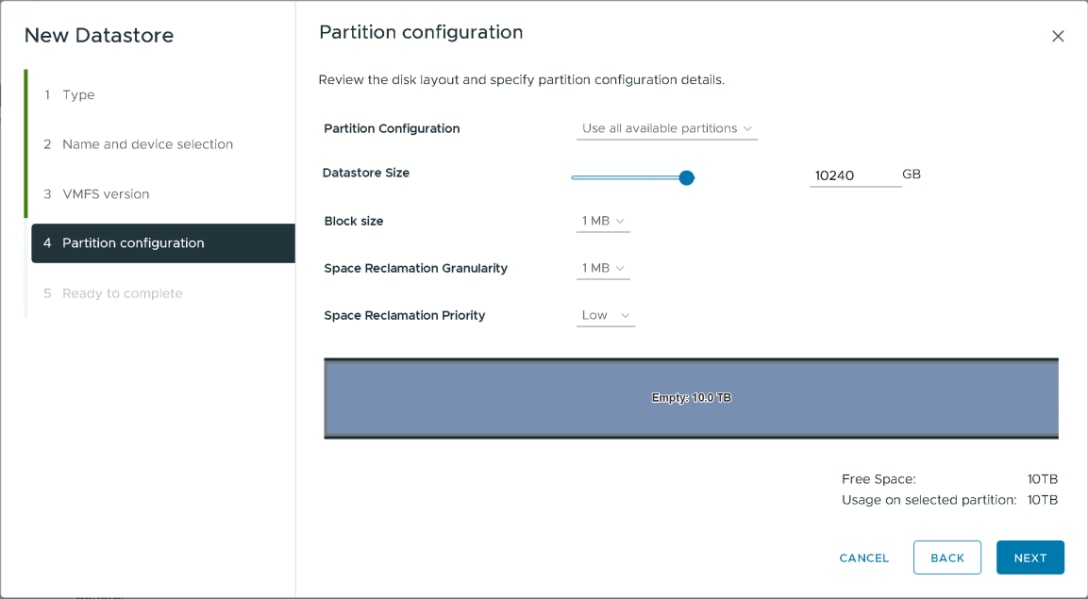
Step 8. Click Finish.
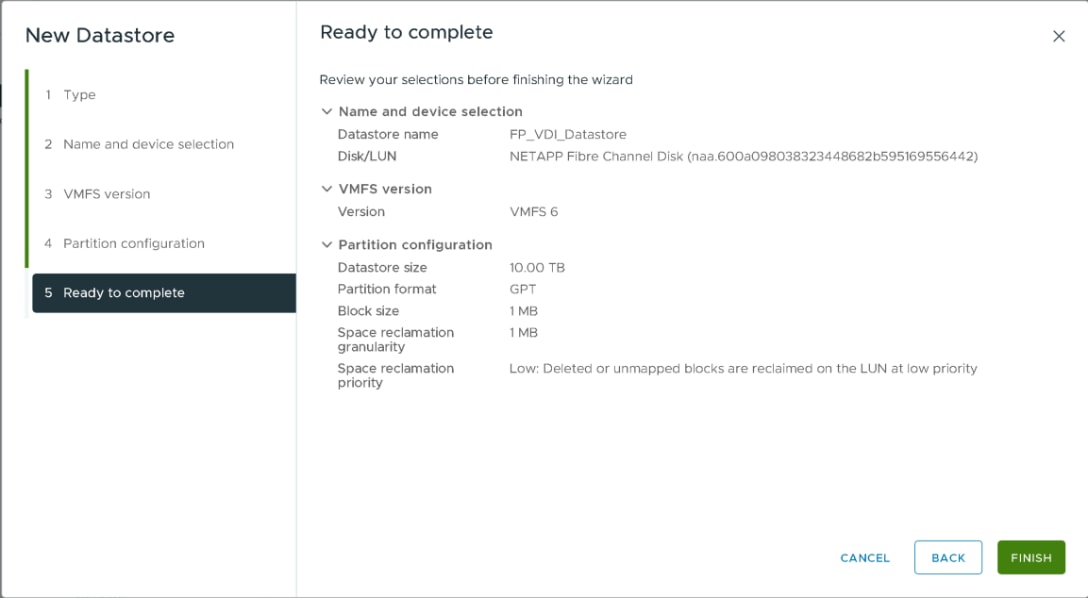
Procedure 8. Create NFS datastores
Step 1. Right-click the Cluster or Host in the inventory.
Step 2. Go to Storage > New Datastore.
Step 3. Select NFS as the datastore type and click Next.
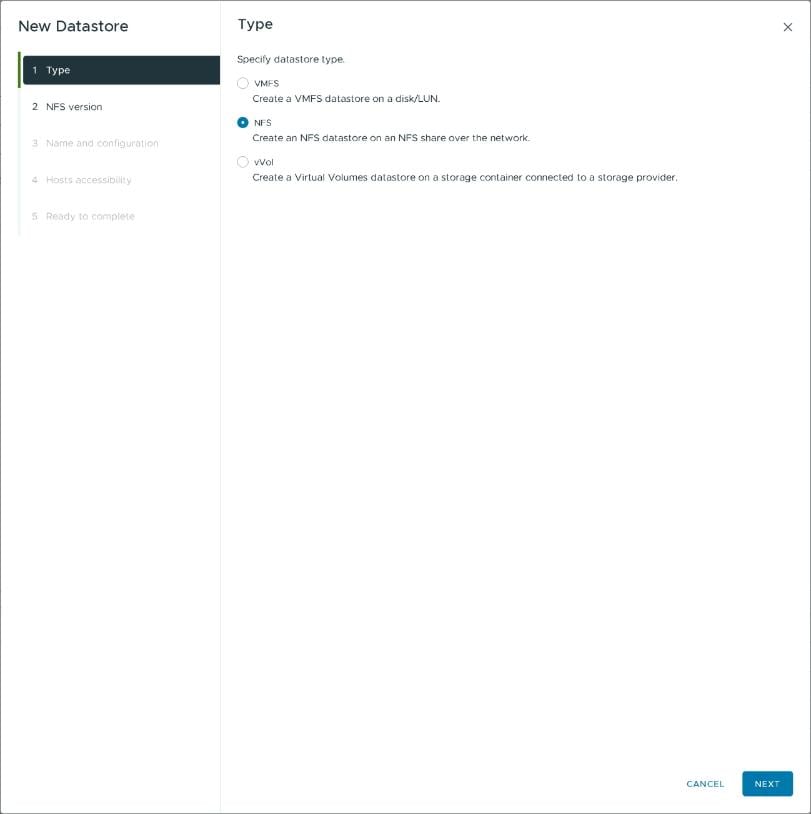
Step 4. Select the NFS version NFS 4.1. Click Next.
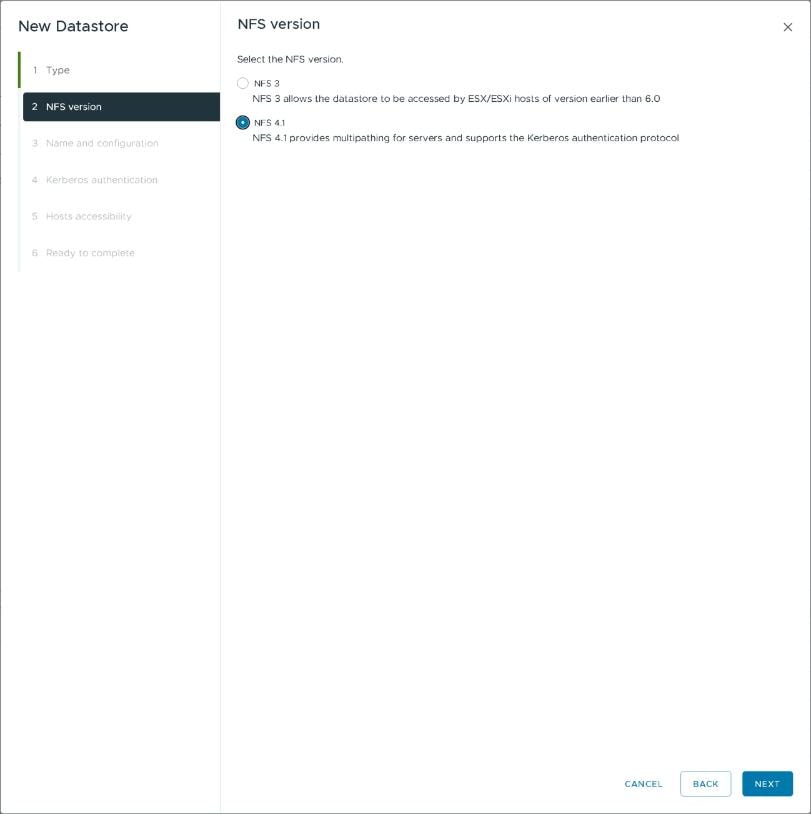
Step 5. Click Next after entering the following details:
- Name: A descriptive name for the datastore.
- Folder: The mount path exported by the storage array (for example, /vol/nfs_datastore).
- Server: The IP address or FQDN of the storage array’s NFS interface.
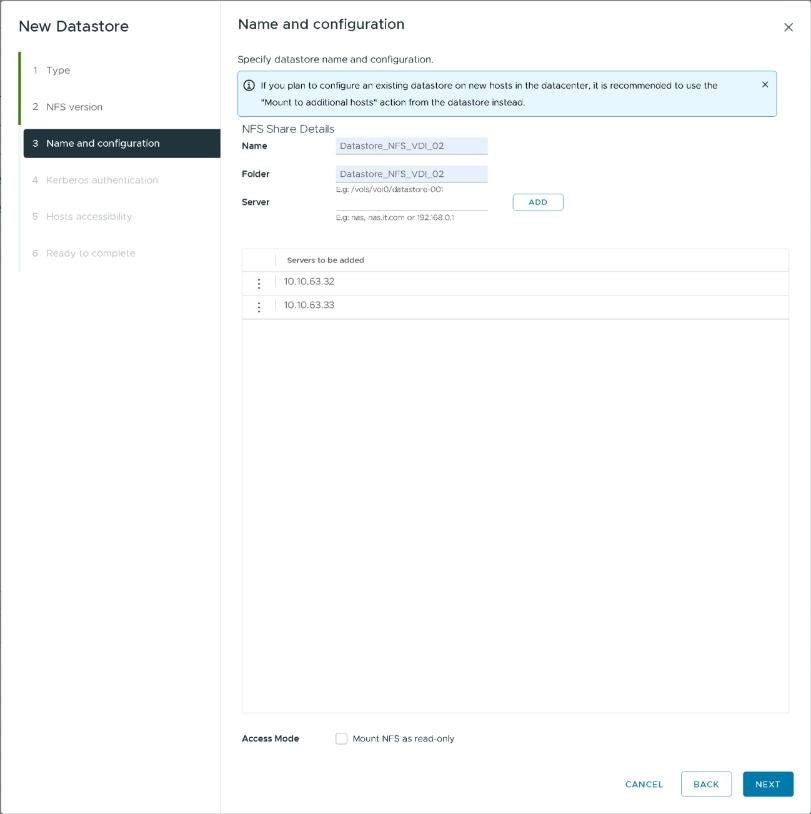
Step 6. Select the Hosts in the cluster that should mount this datastore. Click Next.
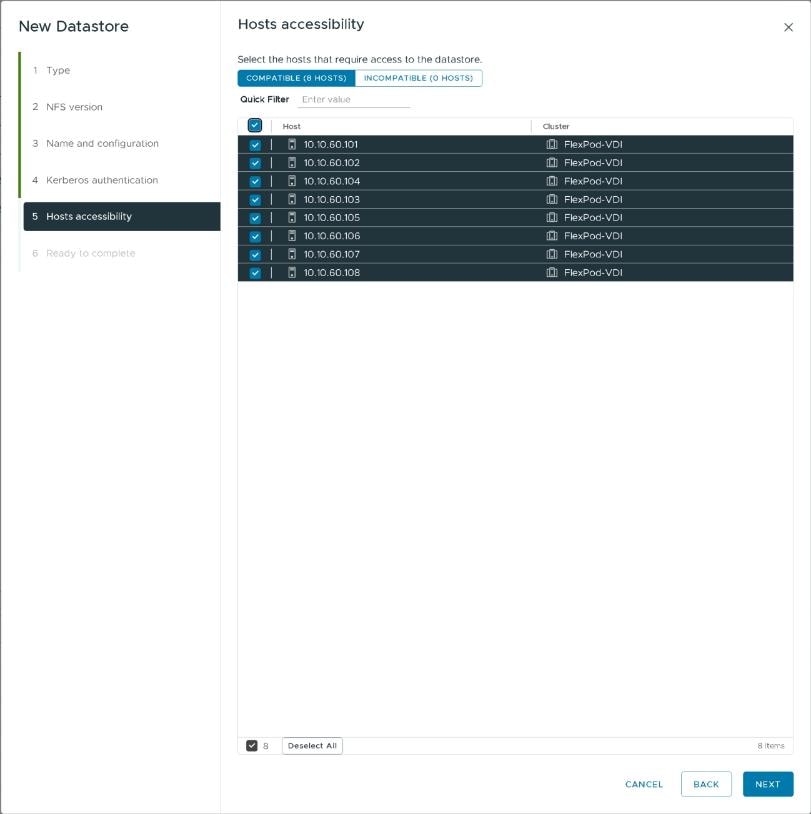
Step 7. Review the settings and click Finish.
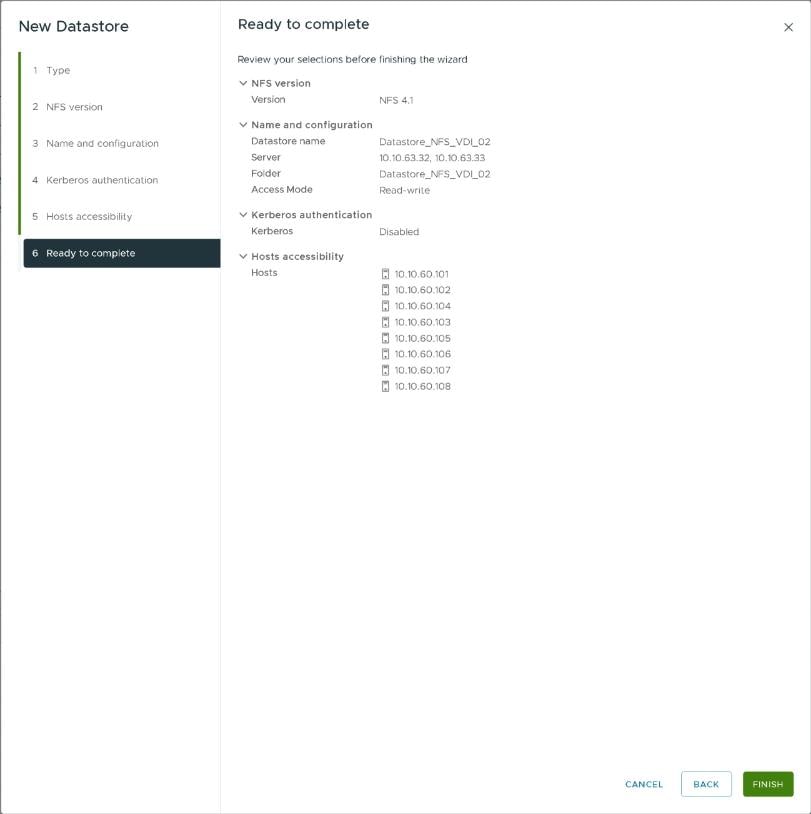
Finalize the NetApp ONTAP Storage Configuration
This chapter contains the following:
● Configure DNS for infrastructure SVM
● Create and enable auditing configuration for the SVM
● Delete the residual default broadcast domains with ifgroups (Applicable for 2-node cluster only)
● Configure and Test AutoSupport
This chapter contains the procedures to finalize the NetApp controller configuration.
Procedure 1. Configure DNS for infrastructure SVM
Step 1. To configure DNS for the VDI-SVM, run the following command:
dns create -vserver <vserver-name> -domains <dns-domain> -nameserve <dns-servers>
Example:
VDI Workload Cluster
Procedure 2. Create and enable auditing configuration for the SVM
Step 1. To create auditing configuration for the SVM, run the following command:
vserver audit create -vserver VDI-SVM -destination /audit_log
Step 2. Run the following command to enable audit logging for the SVM:
vserver audit enable -vserver VDI-SVM
Note: It is recommended that you enable audit logging so you can capture and manage important support and availability information. Before you can enable auditing on the SVM, the SVM’s auditing configuration must already exist.
Note: If you do not perform the configuration steps for the SVM, you will see a warning in AIQUM stating “Audit Log is disabled.”
Step 1. To delete the residual default broadcast domains that are not in use, run the following commands:
broadcast-domain delete -broadcast-domain <broadcast-domain-name>
broadcast-domain delete -broadcast-domain Default-1
broadcast-domain delete -broadcast-domain Default-2
Note: NetApp AutoSupport sends support summary information to NetApp through HTTPS.
Step 1. Test the AutoSupport configuration by sending a message from all nodes of the cluster:
autosupport invoke -node * -type all -message “FlexPod storage configuration completed”
This chapter contains the following:
● FlexPod Automated Deployment with Ansible
FlexPod Automated Deployment with Ansible
If using the published Ansible playbooks to configure the FlexPod infrastructure, follow the procedures detailed in this section.
Ansible Automation Workflow and Solution Deployment
The Ansible automated FlexPod solution uses a management workstation (control machine) to run Ansible playbooks to configure Cisco Nexus, NetApp ONTAP Storage, Cisco UCS, Cisco MDS, and VMware ESXi.
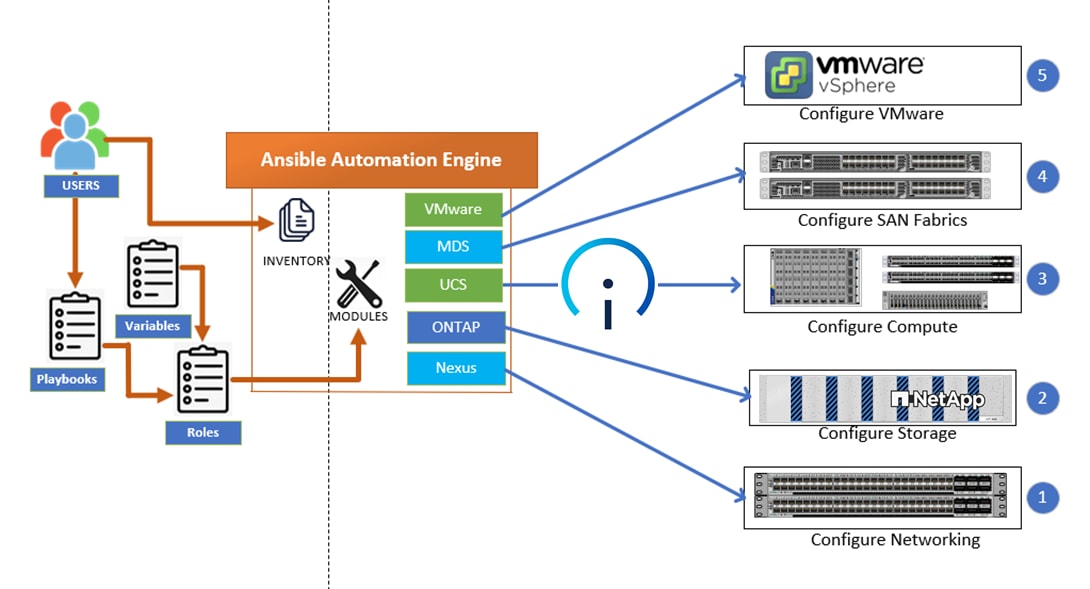
To use the Ansible playbooks demonstrated in this document (Getting Started with Red Hat Ansible), the management workstation must also have a working installation of Git and access to the Cisco DevNet public GitHub repository. The Ansible playbooks used in this document are cloned from the public repositories, located at the following links:
● Cisco DevNet: https://developer.cisco.com/codeexchange/github/repo/ucs-compute-solutions/FlexPod-IMM-VMware/
● GitHub repository for FlexPod infrastructure setup: https://github.com/ucs-compute-solutions/FlexPod-IMM-VMware
● For more information on FlexPod setup using Ansible, go to https://www.cisco.com/c/en/us/td/docs/unified_computing/ucs/UCS_CVDs/flexpod_iac_e2d_deploy.html.
Build the Virtual Machines and Environment for Workload Testing
This chapter contains the following:
● Software Infrastructure Configuration
● Install and Configure Citrix Virtual Apps and Desktops
● Install Citrix Virtual Apps and Desktops Delivery Controller, Citrix Licensing, and StoreFront
● Install and Configure Citrix Provisioning Server 2402
● Install the Citrix Provisioning Server Target Device Software
● Provision Virtual Desktop Machines
● Citrix Virtual Apps and Desktops Policies and Profile Management
● FSLogix for Citrix Virtual Apps and Desktops Profile Management
Create all necessary DHCP scopes for the environment and set the Scope Options.
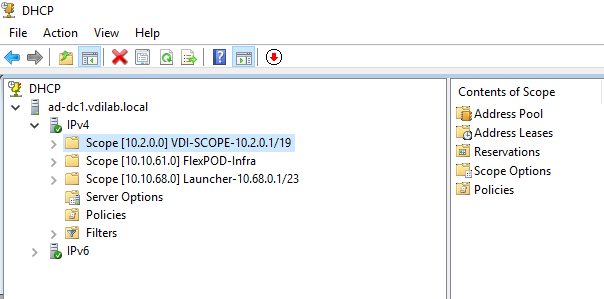
Software Infrastructure Configuration
This section explains how to configure the software infrastructure components that comprise this solution.
Install and configure the infrastructure virtual machines by following the process listed in Table 20.
Table 20. Test Infrastructure Virtual Machine Configuration
| Configuration |
Citrix Virtual Apps and Desktops Controllers Virtual Machines |
Citrix Provisioning Servers Virtual Machines |
| Operating system |
Microsoft Windows Server 2022 |
Microsoft Windows Server 2022 |
| Virtual CPU amount |
6 |
6 |
| Memory amount |
24 GB |
24 GB |
| Network |
VMXNET3 Infra-Mgmt-31 |
VMXNET3 Infra-Mgmt-31 |
| Disk-1 (OS) size |
40 GB |
40 GB |
| Disk-2 size |
- |
200 GB Disk Store |
| Configuration |
Microsoft Active Directory DCs Virtual Machines |
vCenter Server Appliance Virtual Machine |
| Operating system |
Microsoft Windows Server 2022 |
VCSA – SUSE Linux |
| Virtual CPU amount |
4 |
8 |
| Memory amount |
8 GB |
32 GB |
| Network |
VMXNET3 Infra-Mgmt-31 |
VMXNET3 k23-InBand-Mgmt-31 |
| Disk size |
40 GB |
698.84 GB (across 13 VMDKs) |
| Configuration |
Microsoft SQL Server Virtual Machine |
Citrix StoreFront Controller Virtual Machine |
| Operating system |
Microsoft Windows Server 2022 Microsoft SQL Server 2022 |
Microsoft Windows Server 2022 |
| Virtual CPU amount |
8 |
4 |
| Memory amount |
24GB |
8 GB |
| Network |
VMXNET3 Infra-Mgmt-31 |
VMXNET3 Infra-Mgmt-31 |
| Disk-1 (OS) size |
40 GB |
40 GB |
| Disk-2 size |
100 GB SQL Databases\Logs |
- |
This section provides guidance regarding creating the golden (or master) images for the environment. Virtual machines for the master targets must first be installed with the software components needed to build the golden images. Additionally, all available security patches as of October 2021 for the Microsoft operating systems, SQL server and Microsoft Office 2021 were installed.
To prepare Single-session OS or Multi-session OS master virtual machine, there are three major steps: installing the PVS Target Device x64 software (if delivered with Citrix Provisioning Services), installing the Virtual Delivery Agents (VDAs), and installing application software.
Note: For this CVD, the images contain the basics needed to run the Login VSI workload.
The final step is to optimize the Windows OS. The Citrix Optimizer Tool includes customizable templates to enable or disable Windows system services and features using Citrix recommendations and best practices across multiple systems. Because most Windows system services are enabled by default, the optimization tool can easily disable unnecessary services and features to improve performance.
Note: In this CVD, the Citrix Optimizer Tool - v3.5.0.1 was used. Base images were optimized with the Default template for Windows 11 version 21H2, 22H2, 23H2, 24H2 (2009), or Windows Server 2022 version 21H2 (2009) from Citrix. Additionally, all Windows built-in apps except Windows Store were removed from all images and Windows Defender was disabled on the Windows 11 PVS golden image.
The Single-session OS and Multi-session OS master target virtual machines were configured as detailed in Table 21.
Table 21. Single-session OS and Multi-session OS Virtual Machines Configurations
| Configuration |
Single-session OS Virtual Machines |
Multi-session OS Virtual Machines |
| Operating system |
Microsoft Windows 11 64-bit |
Microsoft Windows Server 2022 |
| Virtual CPU amount |
2 |
4 |
| Memory amount |
4 GB |
24 GB |
| Network |
VMXNET3 FlexPod_VDI_64 |
VMXNET3 FlexPod_VDI_64 |
| SCSI Controller |
LSI Logic SAS |
LSI Logic SAS |
| Citrix PVS vDisk size Citrix MCS Disk Size |
64 GB (dynamic) 64 GB |
90 GB (dynamic) 90 GB |
| PVS write cache Disk size |
24 GB |
|
| Citrix PVS write cache RAM cache size |
256 MB |
|
| Additional software used for testing |
Microsoft Office 2021 LTSC Std Office Update applied |
Microsoft Office 2021 LTSC Std Office Update applied FSLogix 25.09 |
| Additional Configuration |
Configure DHCP Add to domain Install VMWare tool Install .Net 3.x, 4.x Activate Office Install VDA Agent Run PVS Imaging Wizard (For non-persistent Desktops only) |
Configure DHCP Add to domain Install VMWare tool Install .Net 3.x, 4.x Activate Office Install VDA Agent
|
Install and Configure Citrix Virtual Apps and Desktops
This section explains the installation of the core components of the Citrix Virtual Apps and Desktops system. This CVD installs two Citrix Virtual Apps and Desktops Delivery Controllers to support both hosted shared desktops (HSD), non-persistent hosted virtual desktops (HVD), and persistent hosted virtual desktops (HVD).
Citrix recommends that you use Secure HTTP (HTTPS) and a digital certificate to protect vSphere communications. Citrix recommends that you use a digital certificate issued by a certificate authority (CA) according to your organization's security policy. Otherwise, if the security policy allows, use the VMware-installed self-signed certificate.
Procedure 1. Install vCenter Server Self-Signed Certificate
Step 1. Add the FQDN of the computer running vCenter Server to the hosts file on that server, located at SystemRoot/
WINDOWS/system32/Drivers/etc/. This step is required only if the FQDN of the computer running vCenter Server is not already present in DNS.
Step 2. Open Internet Explorer and enter the address of the computer running vCenter Server (for example, https://FQDN as the URL).
Step 3. Accept the security warnings.
Step 4. Click the Certificate Error in the Security Status bar and select View certificates.
Step 5. Click Install certificate, select Local Machine, and then click Next.
Step 6. Select Place all certificates in the following store and then click Browse.
Step 7. Click Show physical stores.
Step 8. Click Trusted People.
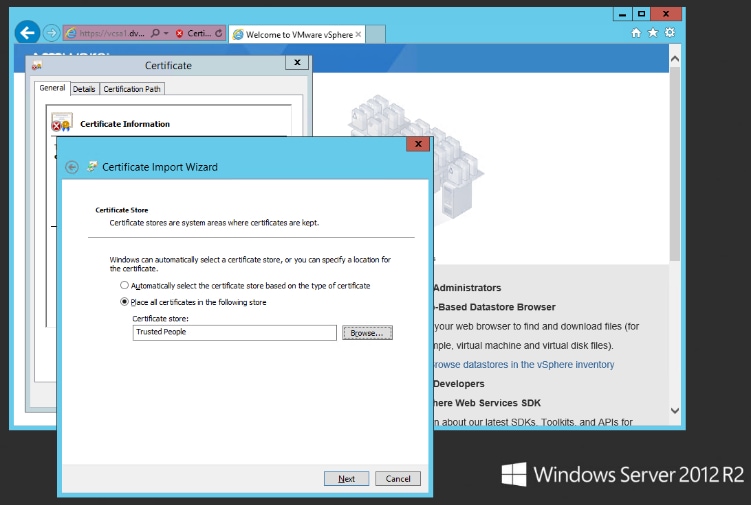
Step 9. Click Next and then click Finish.
Step 10. Repeat steps 1-9 on all Delivery Controllers and Provisioning Servers.
Install Citrix Virtual Apps and Desktops Delivery Controller, Citrix Licensing, and StoreFront
The process of installing the Citrix Virtual Apps and Desktops Delivery Controller also installs other key Citrix Virtual Apps and Desktops software components, including Studio, which is used to create and manage infrastructure components, and Director, which is used to monitor performance and troubleshoot problems.
Note: Dedicated StoreFront and License servers should be implemented for large scale deployments.
Procedure 1. Install Citrix License Server
Step 1. To begin the installation, connect to the first Citrix License server and launch the installer from the 2402Citrix_Virtual_Apps_and_Desktops_7_2402_LTSR_CU3_3100.
Step 2. Click Start.
Step 3. Click Extend Deployment – Citrix License Server.
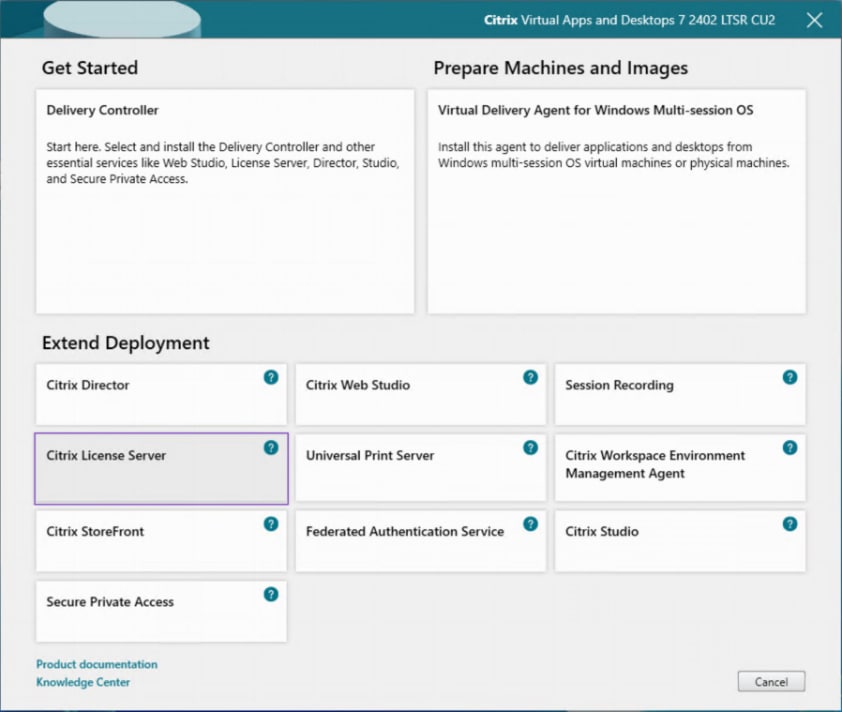
Step 4. Read the Citrix License Agreement. If acceptable, indicate your acceptance of the license by selecting the radio button for I have read, understand, and accept the terms of the license agreement.
Step 5. Click Next.
Step 6. Click Next.
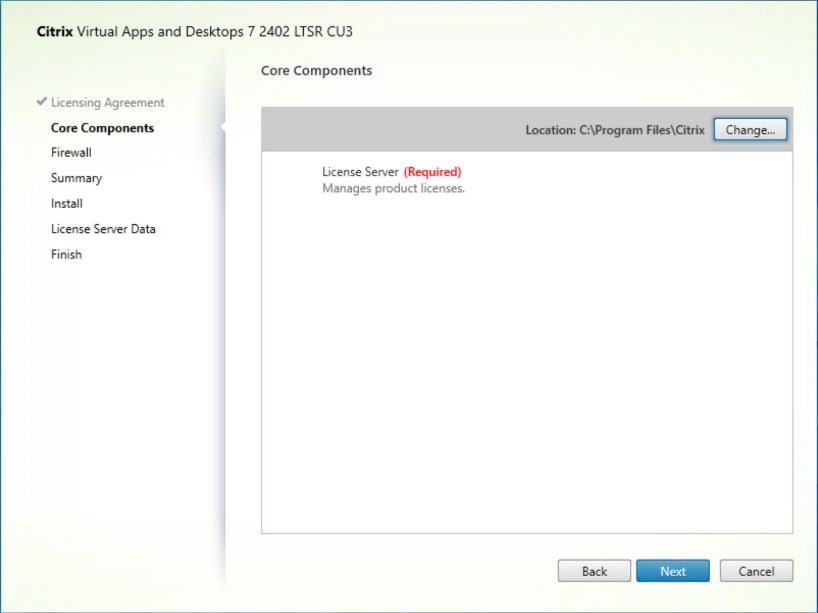
Step 7. Select the default ports and automatically configured firewall rules.
Step 8. Click Next.
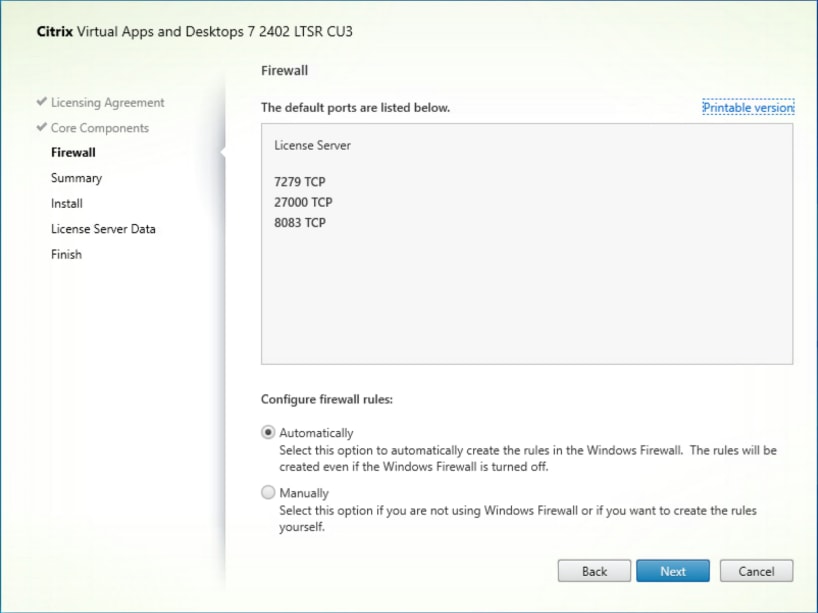
Step 9. Click Install.
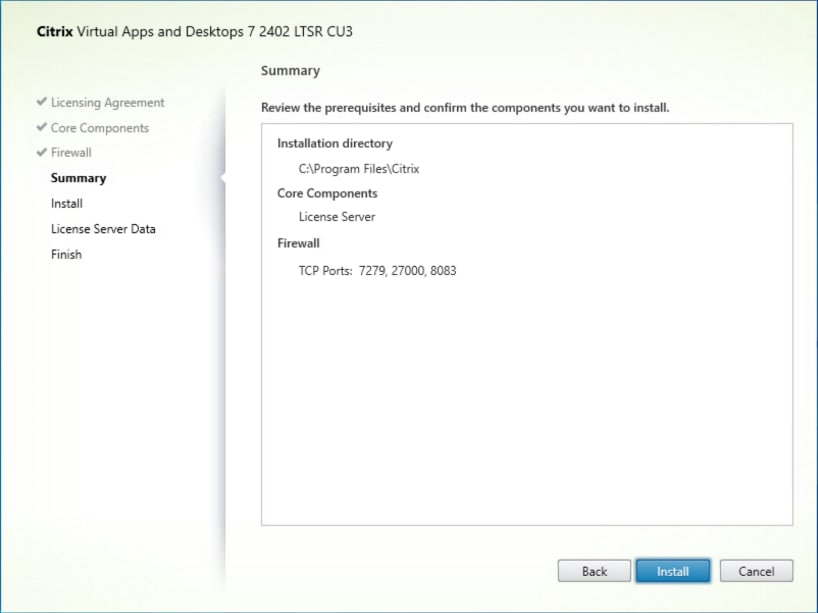
Step 10. Select appropriate Licensing Telemetry setting (such as None of the above). Click Next.
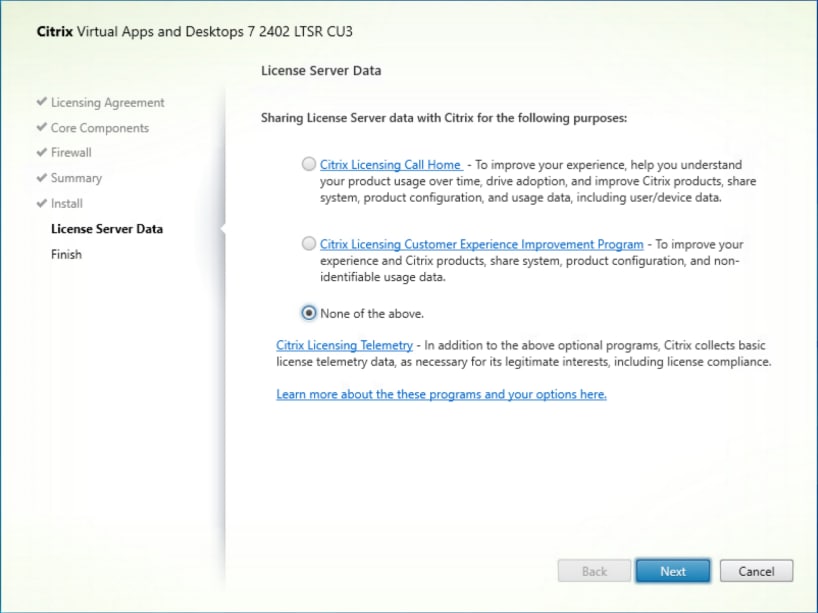
Step 11. Click Finish to complete the installation.
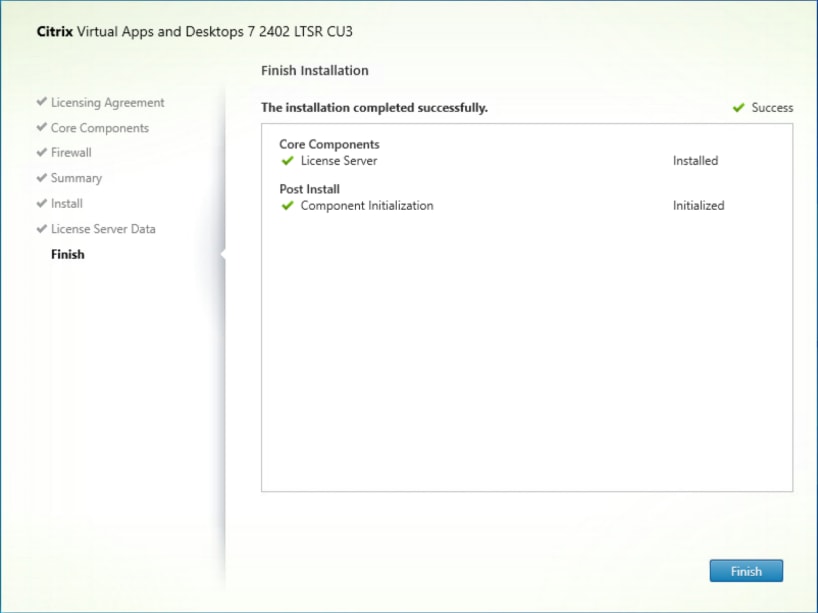
Procedure 2. Install Citrix Licenses
Note: This CVAD environment used the License Activation Service (LAS), cloud-based licensing solution for on-premises Citrix License Servers. The more details on the LAS can be found here.
Step 1. Log in to the Citrix Licensing Manager on the license server virtual machine. On the Dashboard click Go to Registration.
Step 2. Click Register.
Step 3. Copy the displayed 8-character code.
Step 4. On Citrix Cloud portal go to Licensing > Licensed deployment > License Servers. Click Add License Server. Paste the copied code and click Next.
Step 5. Review registration details and click Register.
Step 6. Confirm the current registration state with Citrix Cloud in Citrix Licensing Manager.
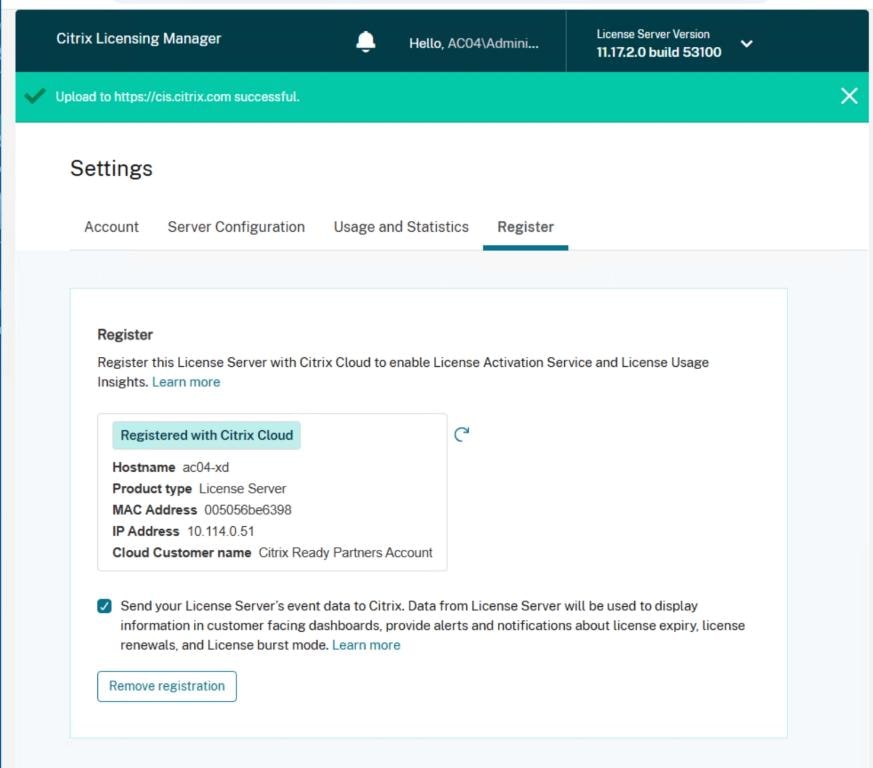
Step 7. Confirm that the license files have been read and enabled correctly.
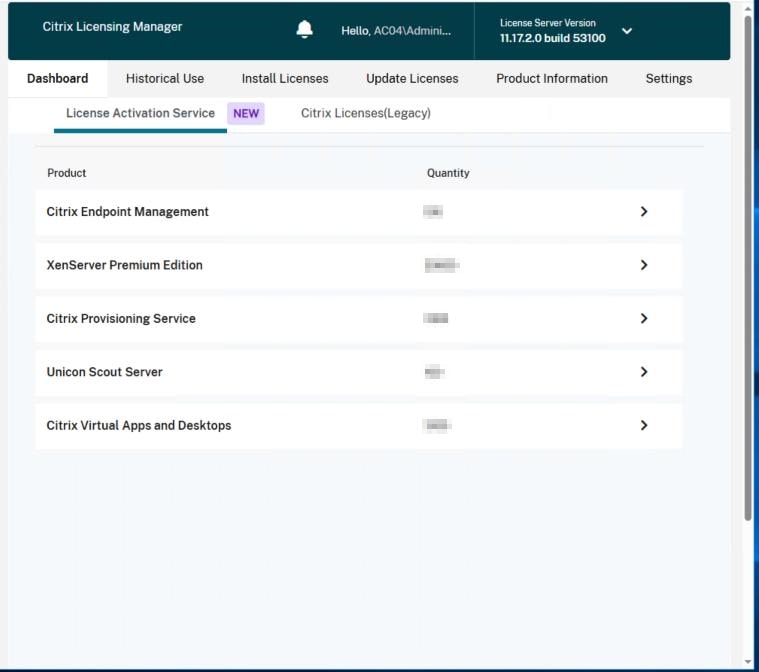
Procedure 3. Install the Citrix Virtual Apps and Desktops
Step 1. To begin the installation, connect to the first Delivery Controller server and launch the installer from the Citrix_Virtual_Apps_and_Desktops_7_2402_LTSR_CU3_3100.
Step 2. Click Start.
Step 3. The installation wizard presents a menu with three subsections. Click Get Started - Delivery Controller.
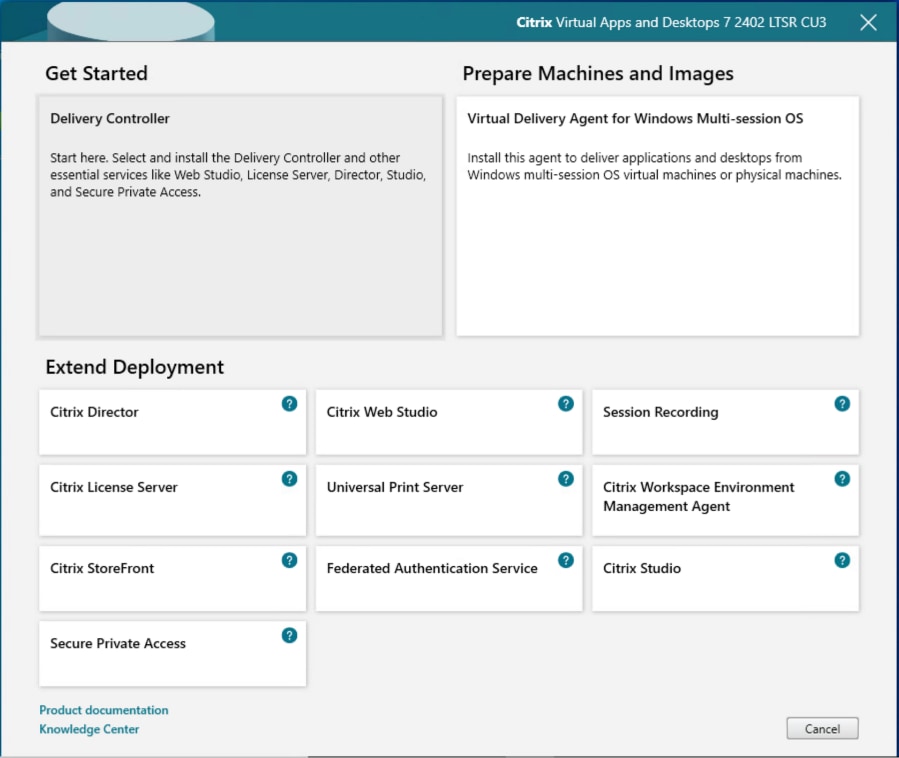
Step 4. Read the Citrix License Agreement. If acceptable, indicate your acceptance of the license by selecting the radio button for I have read, understand, and accept the terms of the license agreement.
Step 5. Click Next.
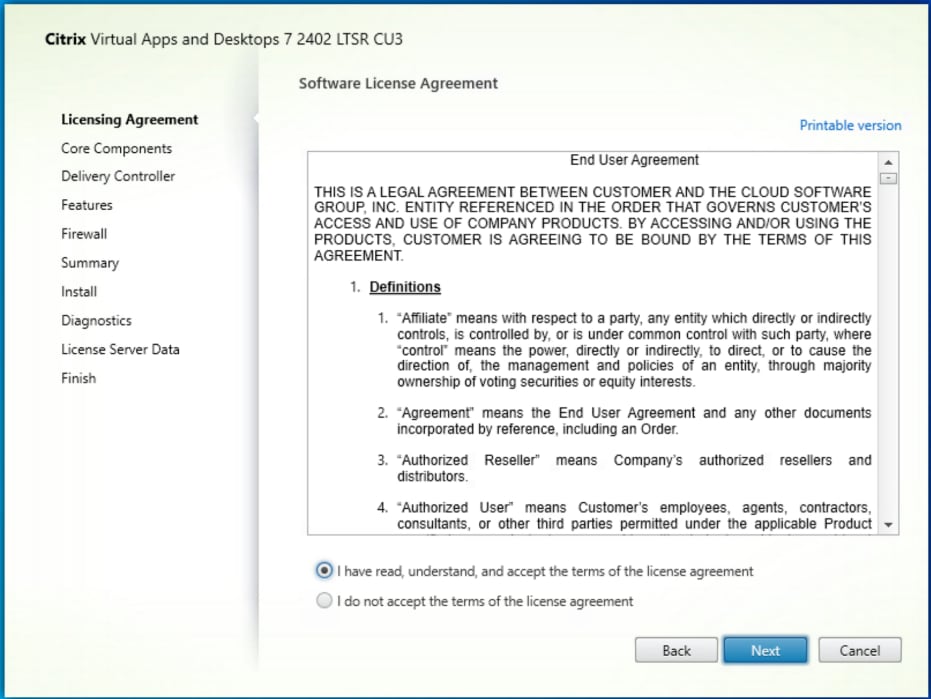
Step 6. Select the components to be installed on the first Delivery Controller Server:
- Delivery Controller
- Studio
- Director
Step 7. Click Next.
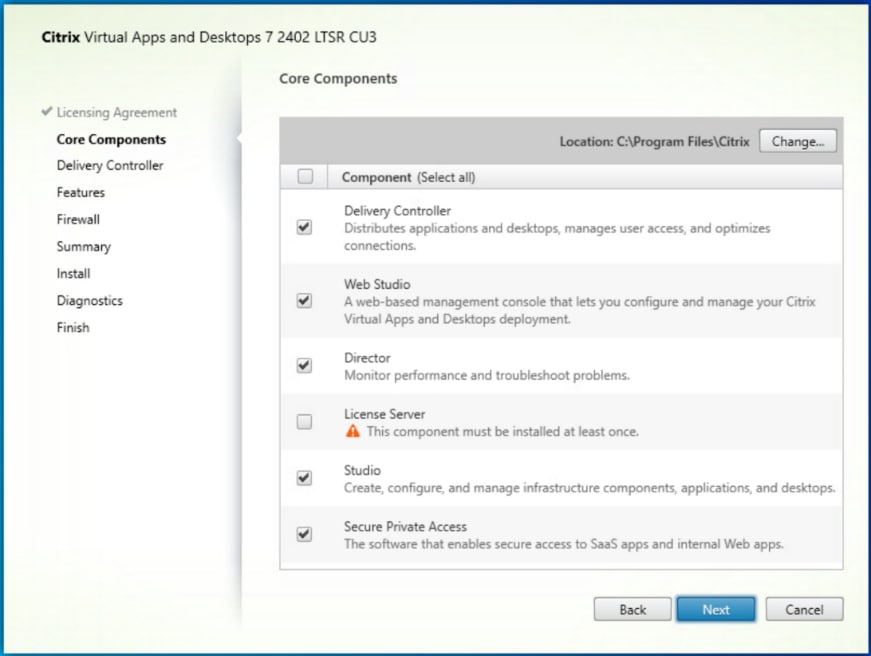
Step 8. Enter FQDN for the delivery controller. Click Add.
Step 9. Click Next.
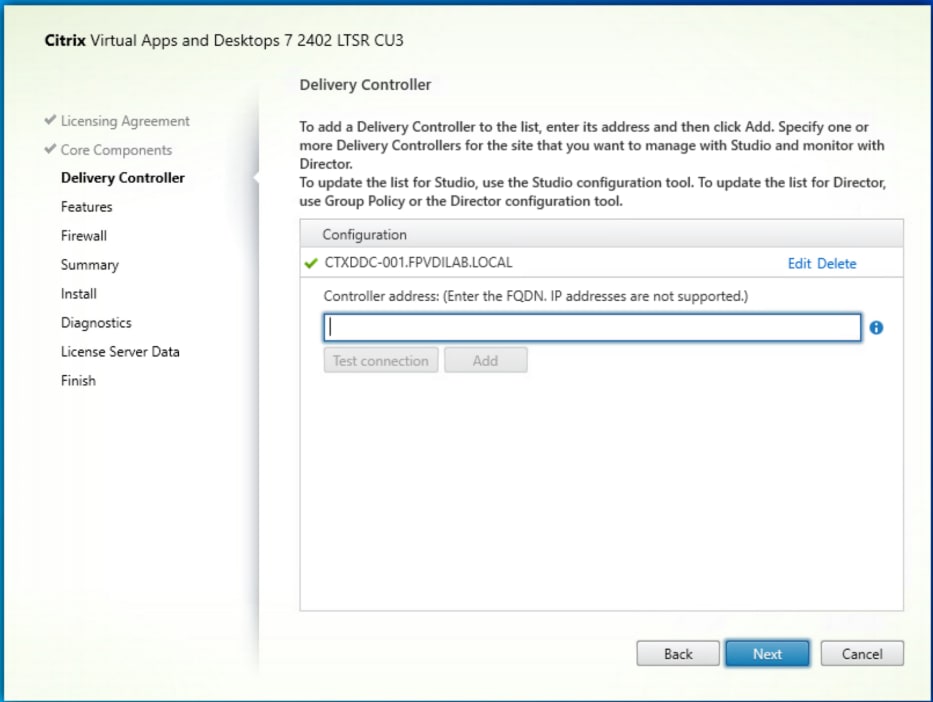
Step 10. Since a dedicated SQL Server will be used to Store the Database, leave Install Microsoft SQL Server 2014 SP2 Express unchecked.
Step 11. Click Next.
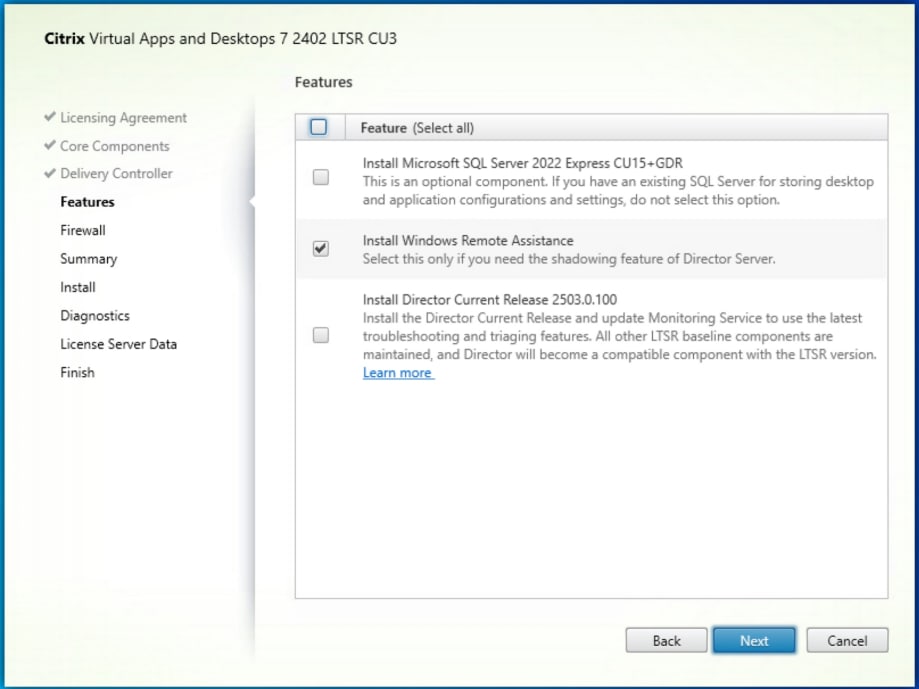
Step 12. Select the default ports and automatically configured firewall rules.
Step 13. Click Next.
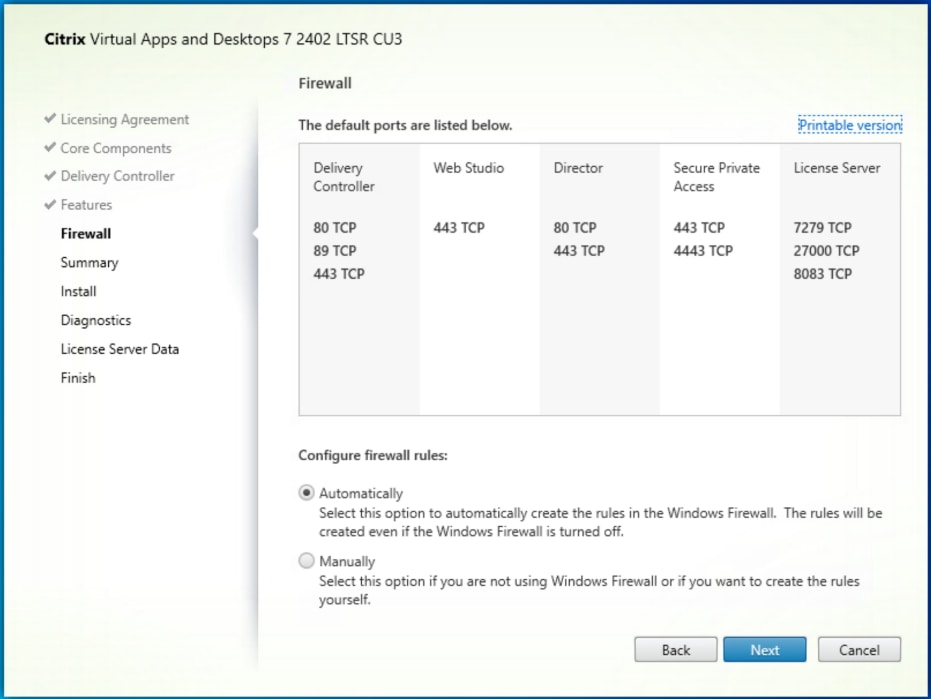
Step 14. Click Install to begin the installation.
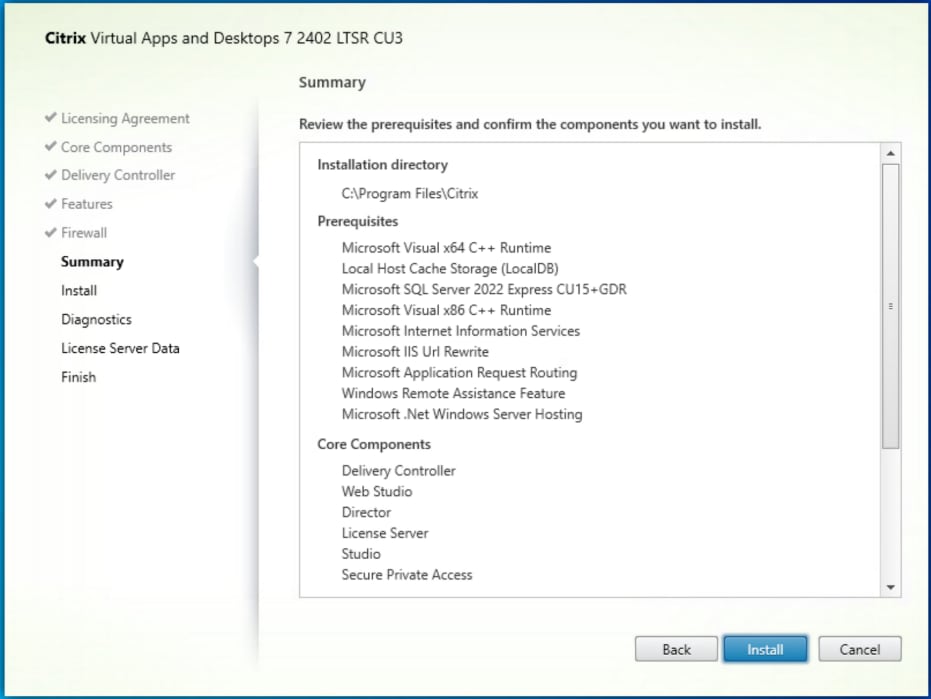
Note: Multiple reboots may be required to finish installation.
Step 15. (Optional) Collect diagnostic information/Call Home participation.
Step 16. Click Next.
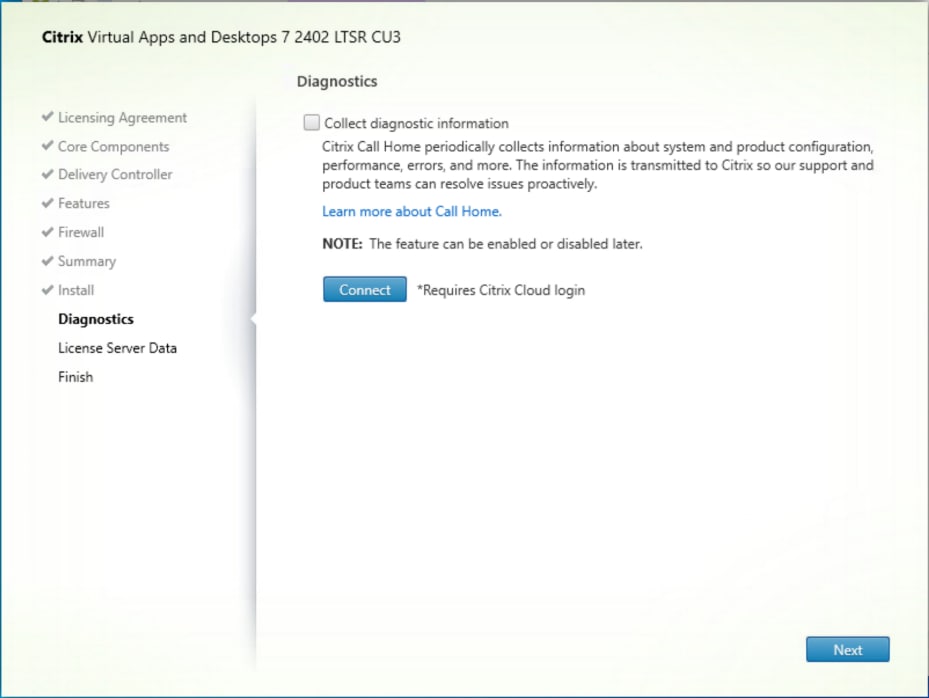
Step 17. Click Next.
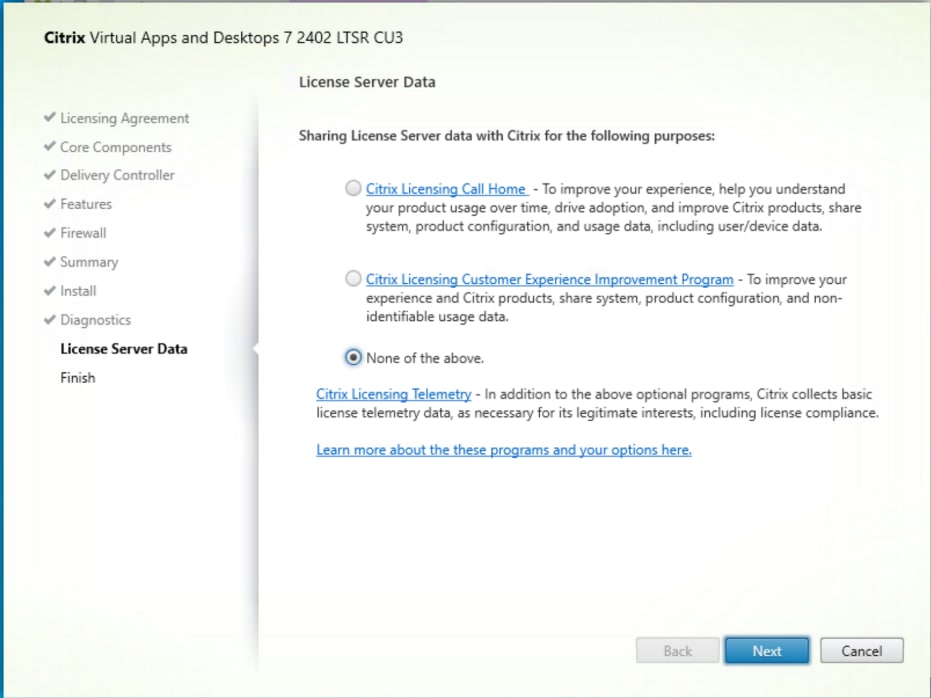
Step 18. Click Finish to completed the installation. (Optional) Check Launch Studio to launch Citrix Studio Console.
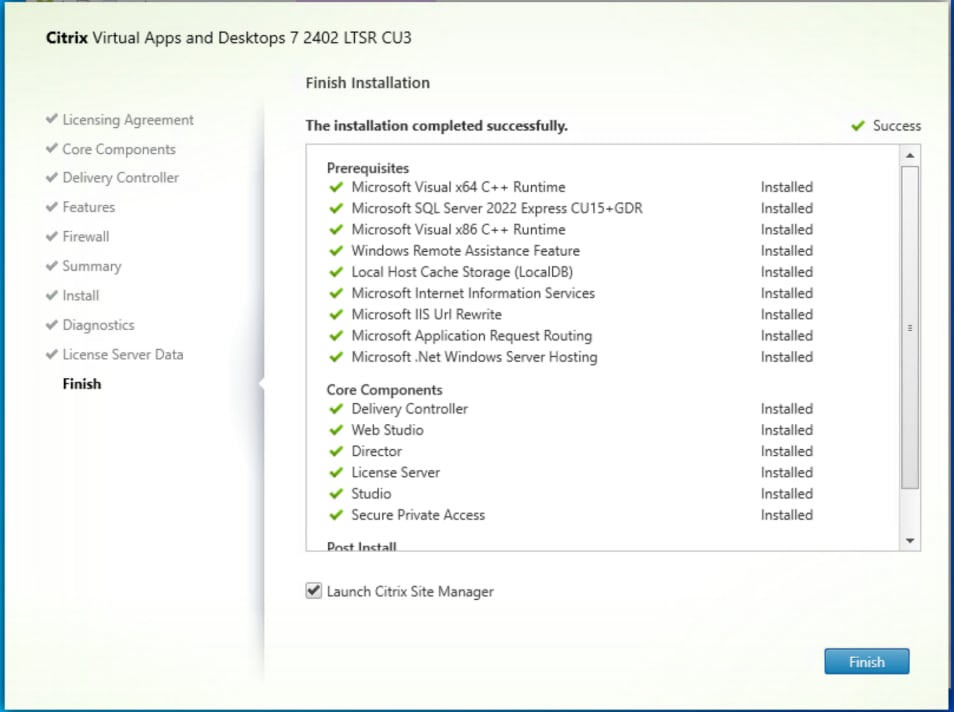
Procedure 4. Additional Delivery Controller Configuration
Note: After the first controller is completely configured and the Site is operational, you can add additional controllers. In this CVD, we created two Delivery Controllers.
To configure additional Delivery Controllers, repeat the steps in section Install the Citrix Virtual Apps and Desktops.
Step 1. To begin the installation of the second Delivery Controller, connect to the second Delivery Controller server and launch the installer from the Citrix_Virtual_Apps_and_Desktops_7_2402_LTSR_CU3_3100.
Step 2. Click Start.
Step 3. Click Delivery Controller.
Step 4. Repeat the steps used to install the first Delivery Controller; Install the Citrix Virtual Apps and Desktops, including the step of importing an SSL certificate for HTTPS between the controller and vSphere.
Step 5. Review the Summary configuration. Click Finish.
Step 6. (Optional) Configure Collect diagnostic information /Call Home participation. Click Next.
Step 7. Verify the components installed successfully. Click Finish.
Citrix Studio is a management console that allows you to create and manage infrastructure and resources to deliver desktops and applications. Replacing Desktop Studio from earlier releases, it provides wizards to set up your environment, create workloads to host applications and desktops, and assign applications and desktops to users.
Citrix Studio launches automatically after the Delivery Controller installation, or if necessary, it can be launched manually. Studio is used to create a Site, which is the core of the Citrix Virtual Apps and Desktops environment consisting of the Delivery Controller and the Database.
Step 1. From Citrix Studio, click Deliver applications and desktops to your users.
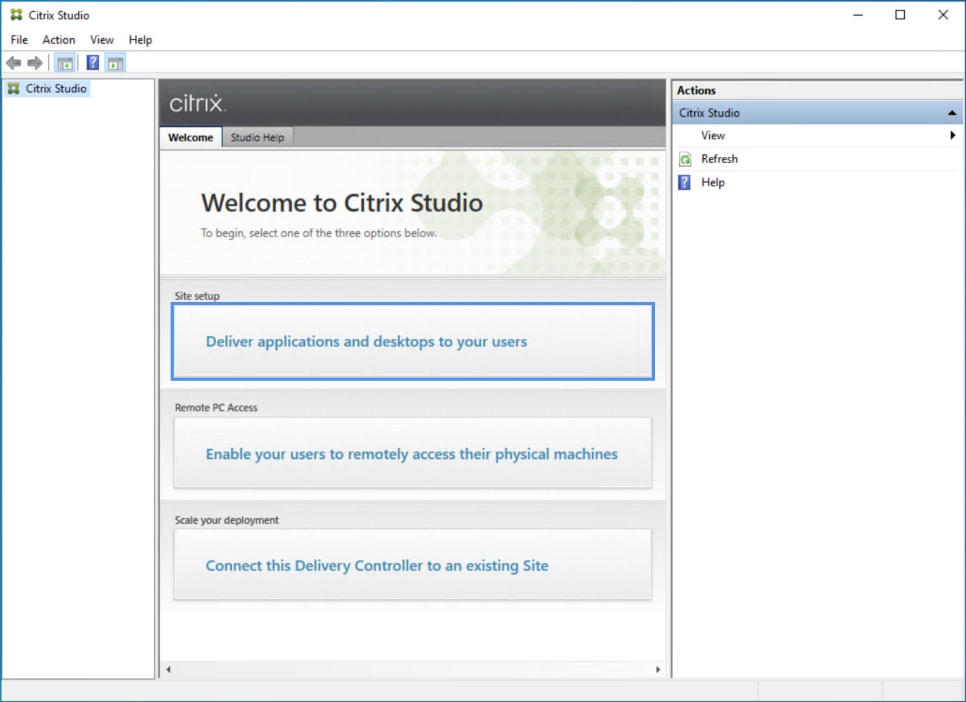
Step 2. Select the radio button for An empty, unconfigured Site.
Step 3. Enter a site name.
Step 4. Click Next.
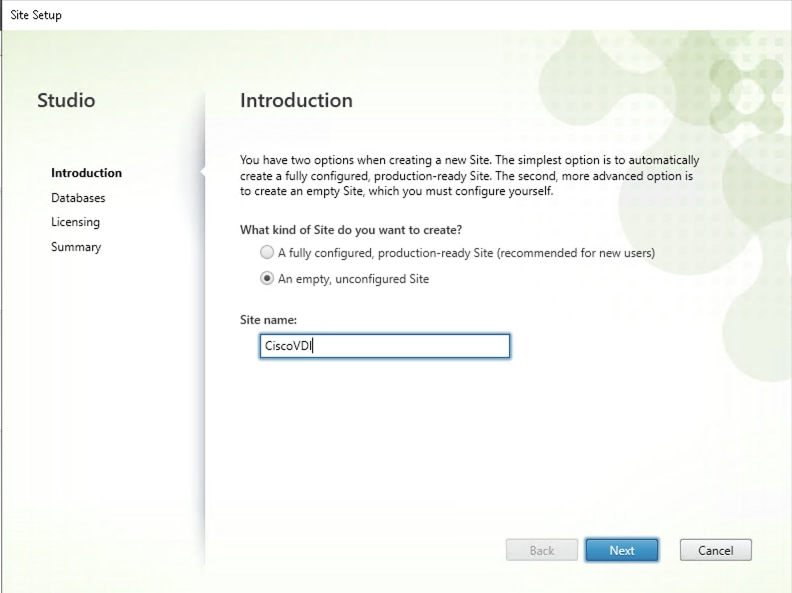
Step 5. Provide the Database Server Locations for each data type.
Note: For an SQL AlwaysOn Availability Group, use the group’s listener DNS name.
Step 6. Click Select to specify additional controllers (Optional at this time. Additional controllers can be added later).
Step 7. Click Next.
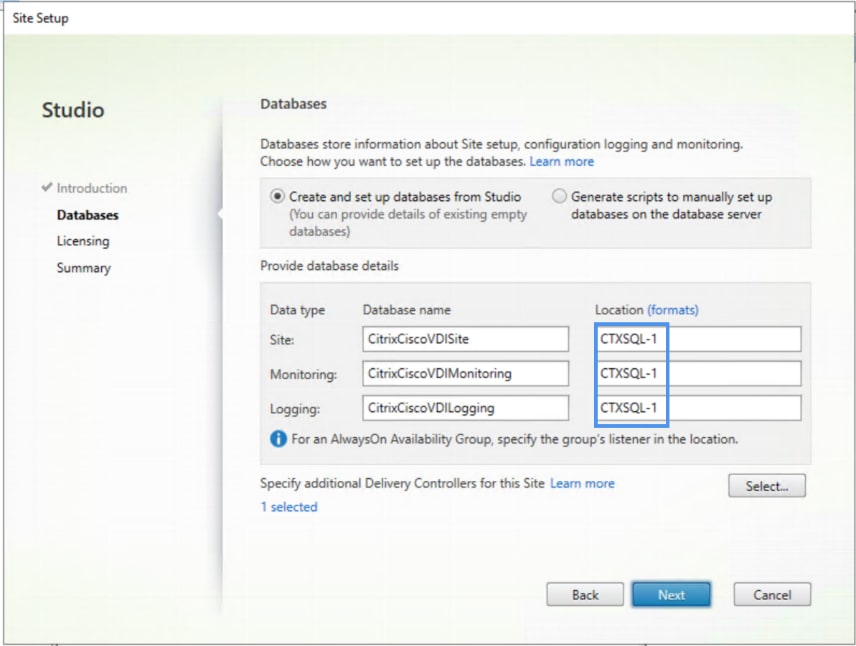
Step 8. Provide the FQDN of the license server.
Step 9. Click Connect to validate and retrieve any licenses from the server.
Note: If no licenses are available, you can use the 30-day free trial or activate a license file.
Step 10. Confirm Certificate, if required.
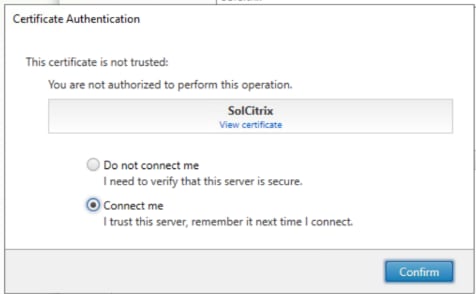
Step 11. Select the appropriate product edition using the license radio button.
Step 12. Click Next.
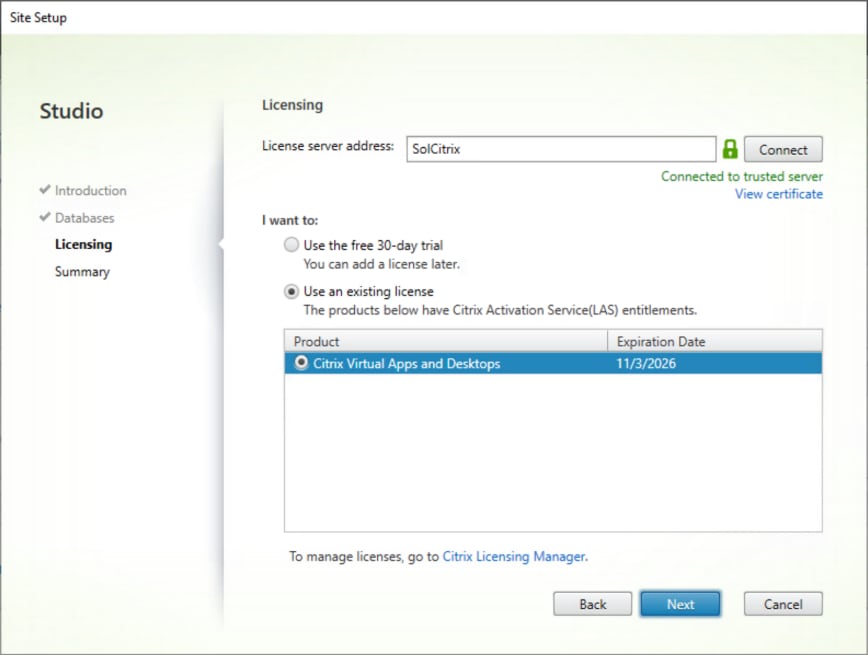
Step 13. Verify information on the Summary page.
Step 14. Click Finish.
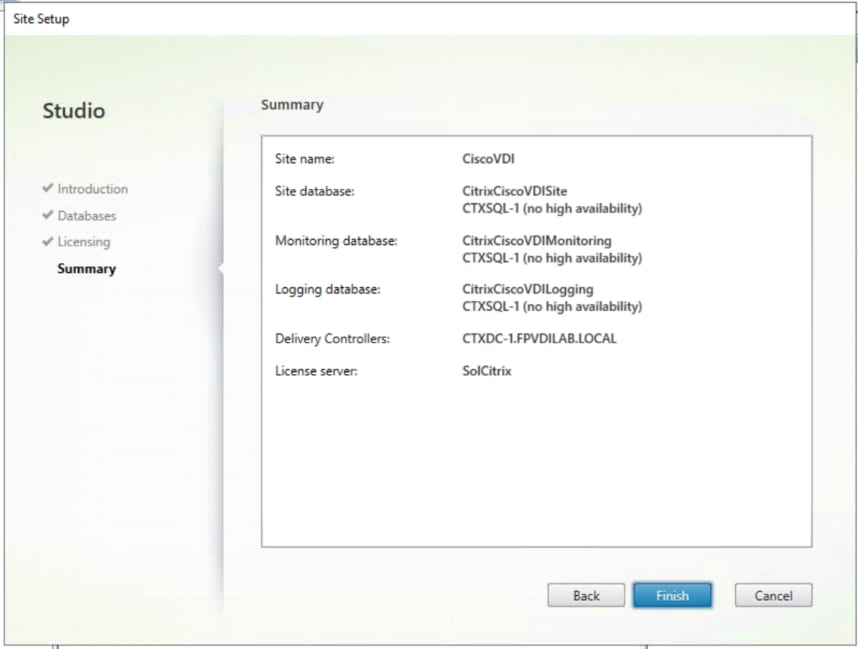
Procedure 6. Configure the Citrix Virtual Apps and Desktops Site Hosting Connection
Step 1. Go to Configuration > Hosting in Studio, click Add Connection and Resources.
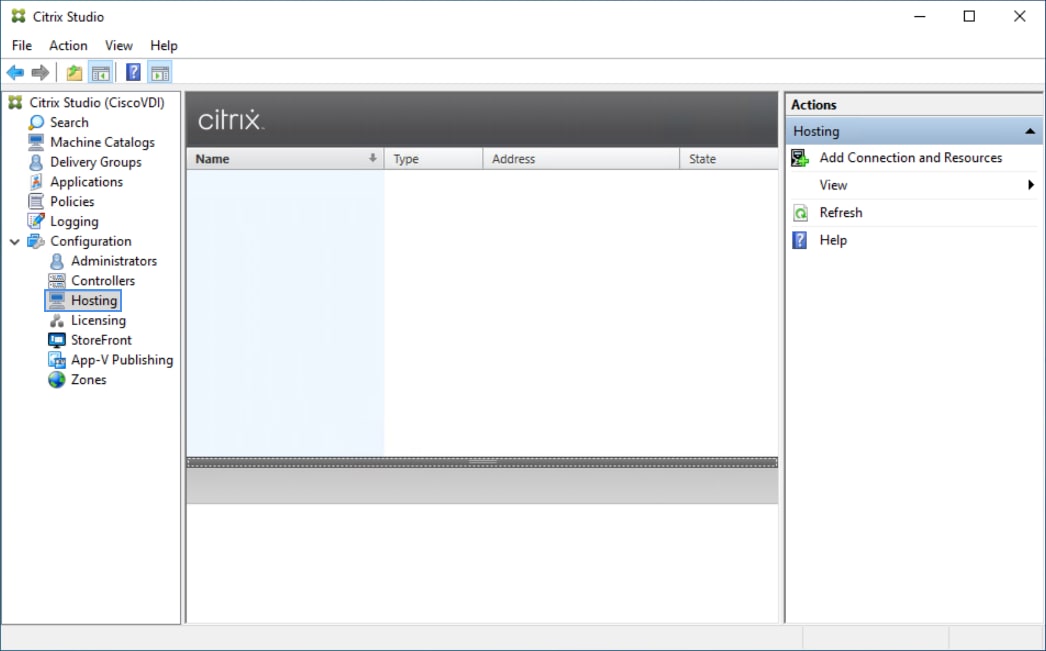
Step 2. On the Connection page:
a. Select the Connection type of VMware vSphere.
b. Enter the FQDN of the vCenter server (in Server_FQDN/sdk format).
c. Enter the username (in domain\username format) for the vSphere account.
d. Provide the password for the vSphere account.
e. Provide a connection name.
f. Select the tool to create virtual machines: Machine Creation Services or Citrix Provisioning.
Step 3. Click Next.
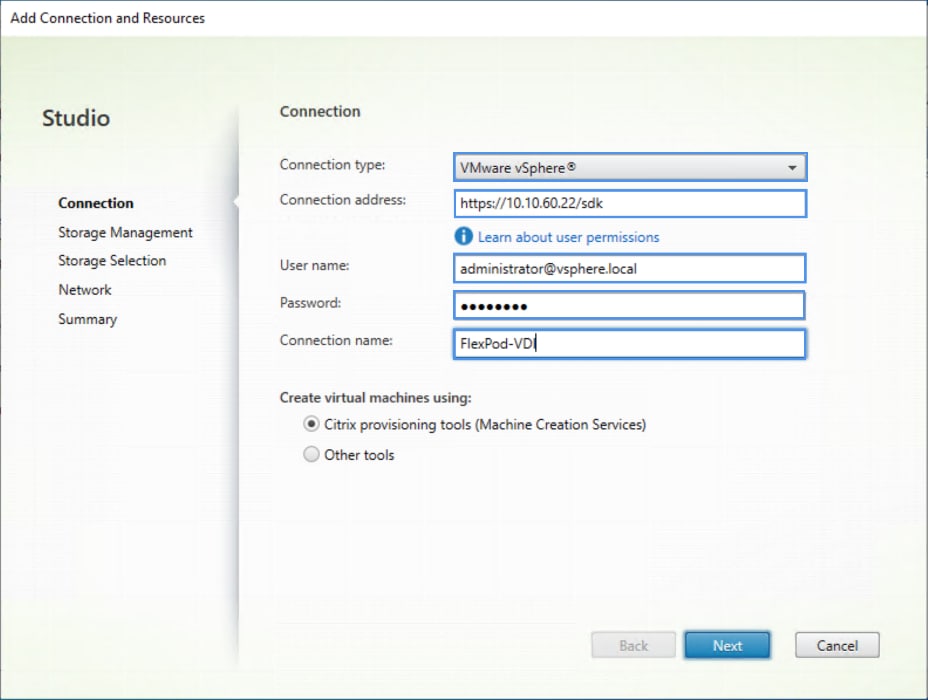
Step 4. Accept the certificate and click OK to trust the hypervisor connection.
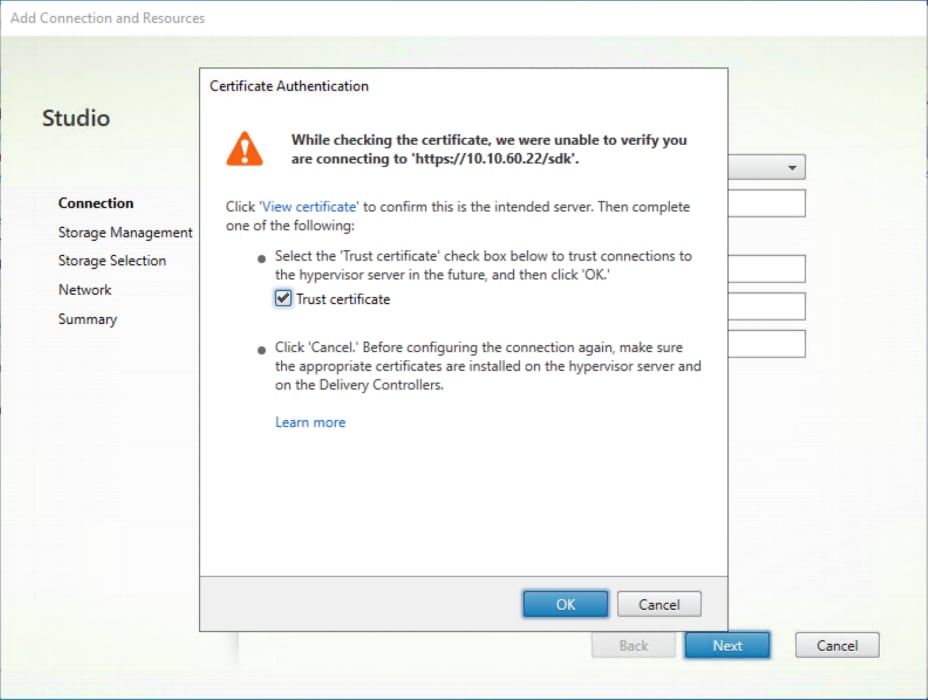
Step 5. Select a storage management method:
a. Select a cluster that will be used by this connection.
b. Check Use storage shared by hypervisors radio button.
Step 6. Click Next.
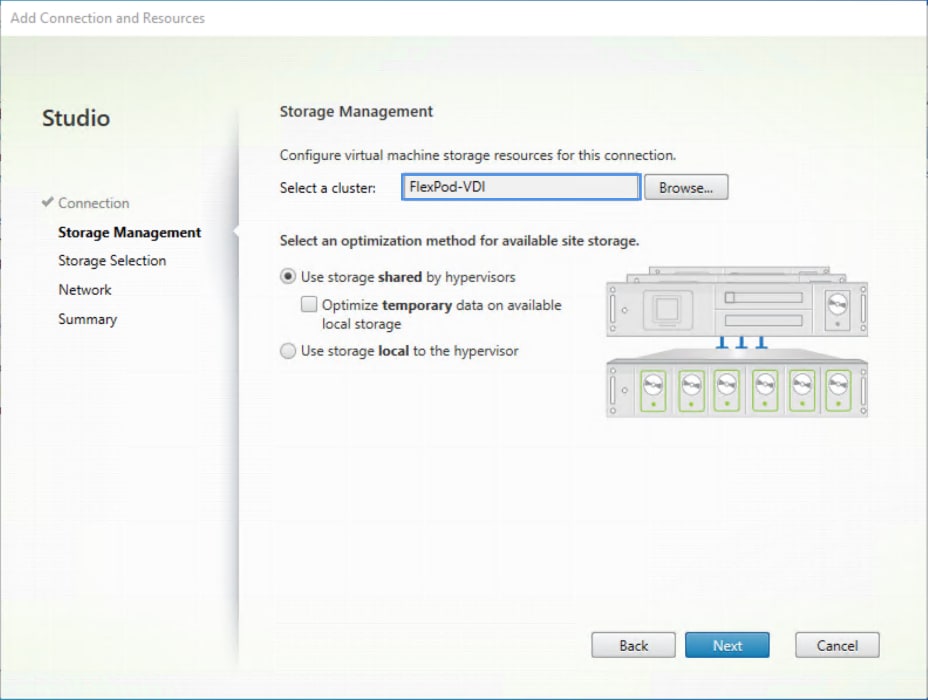
Step 7. Select the Storage to be used by this connection, use all provisioned for desktops datastores.
Step 8. Click Next.
Note: The following datastores were enabled during the testing:
4 Fibre Channel datastores for block storage access
4 NFS datastores for IP-based storage access
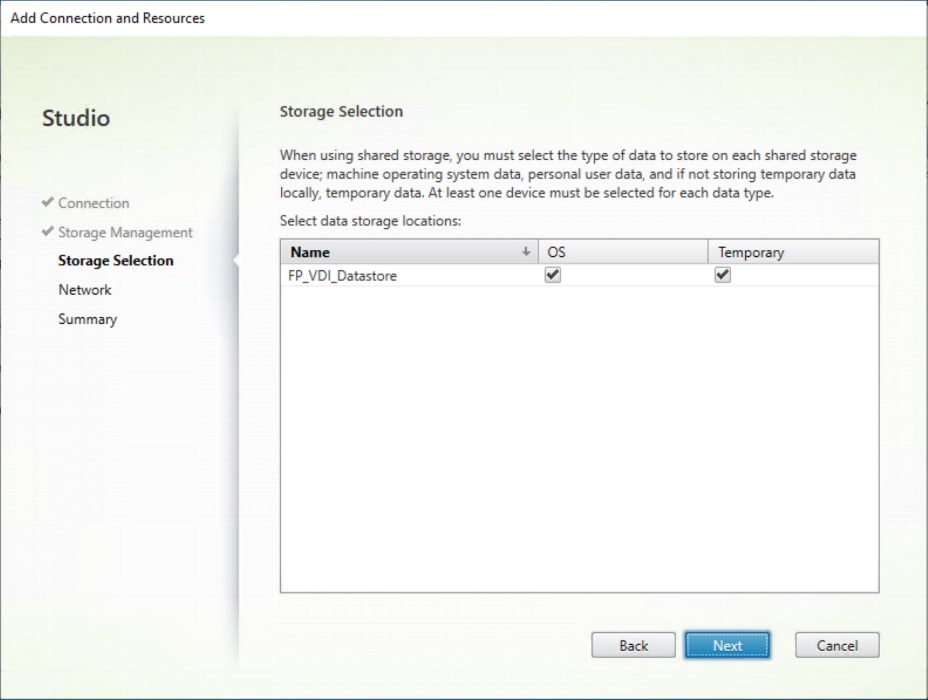
Step 9. Select the Network to be used by this connection.
Step 10. Click Next.
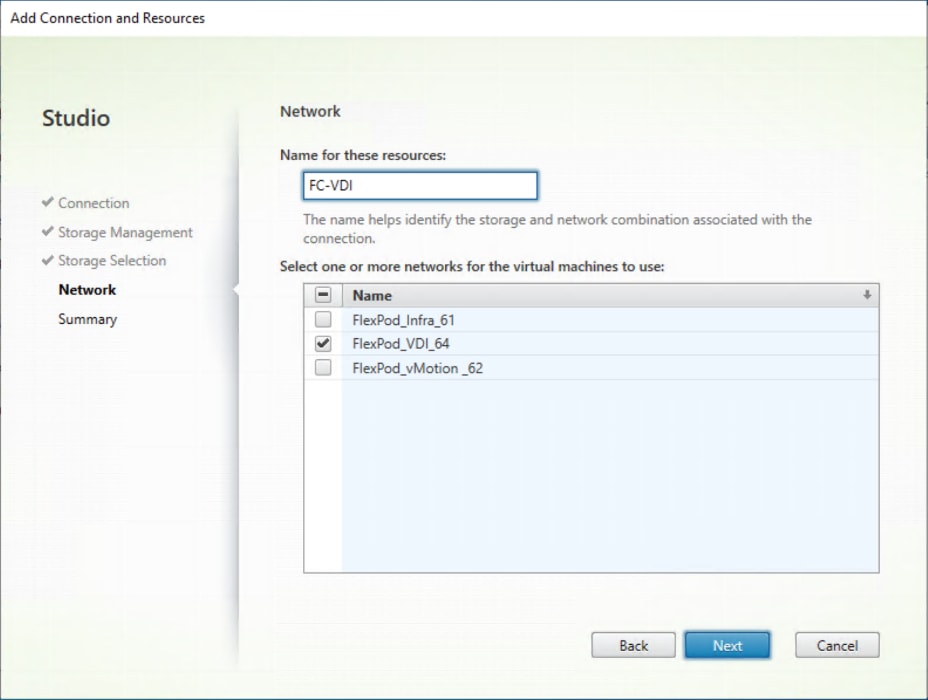
Step 11. Review Add Connection and Recourses Summary.
Step 12. Click Finish.
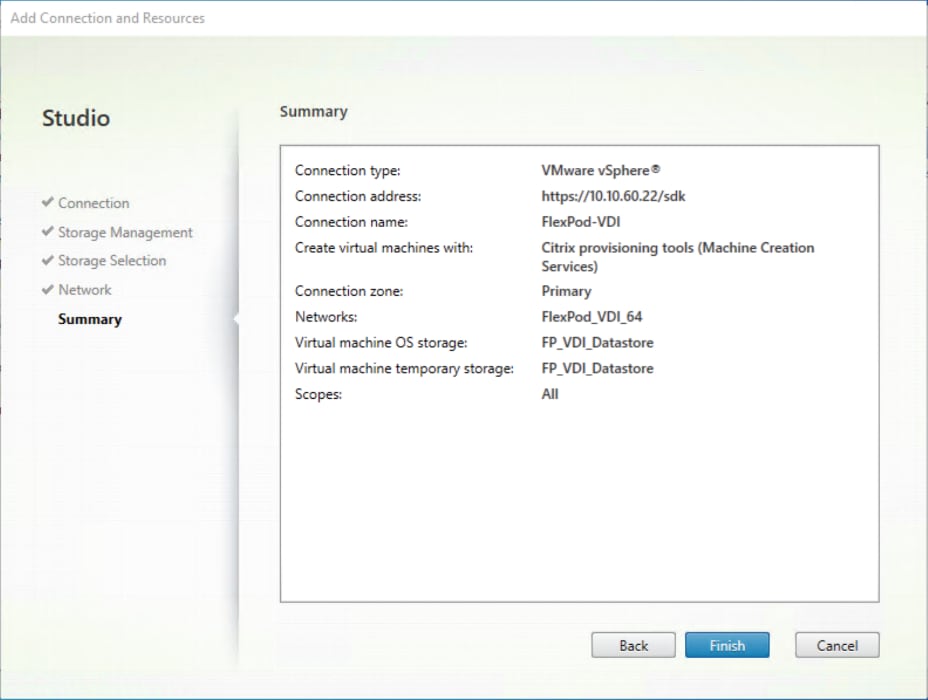
Procedure 7. Configure the Citrix Virtual Apps and Desktops Site Administrators
Step 1. Connect to the Citrix Virtual Apps and Desktops server and open Citrix Studio Management console.
Step 2. From the Configuration menu, select Administrator and select Create Administrator.
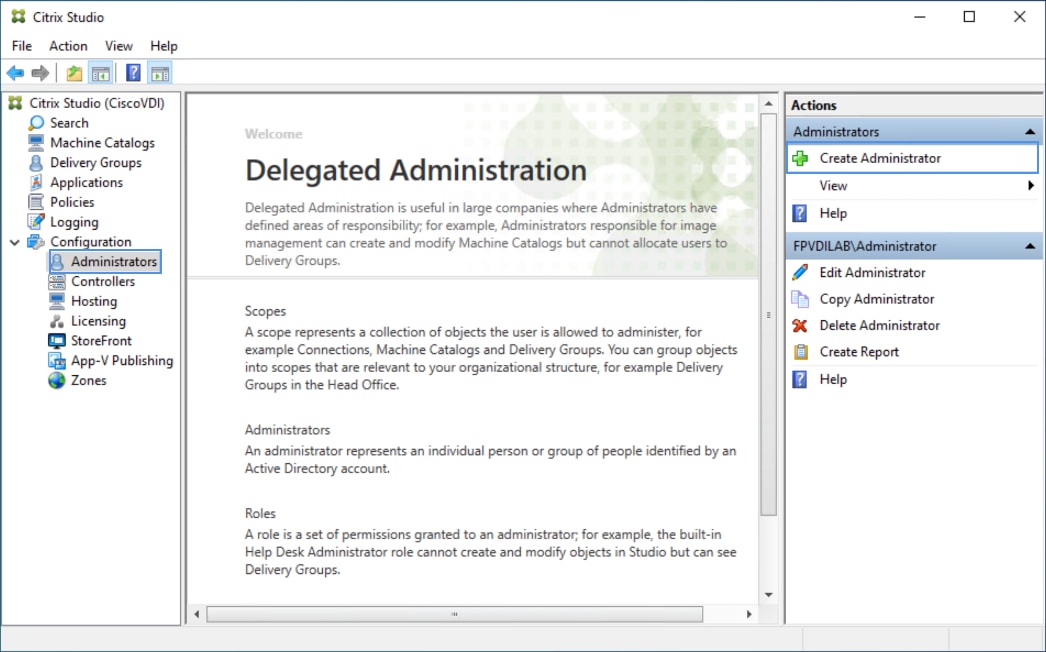
Step 3. Select or Create appropriate scope and click Next.
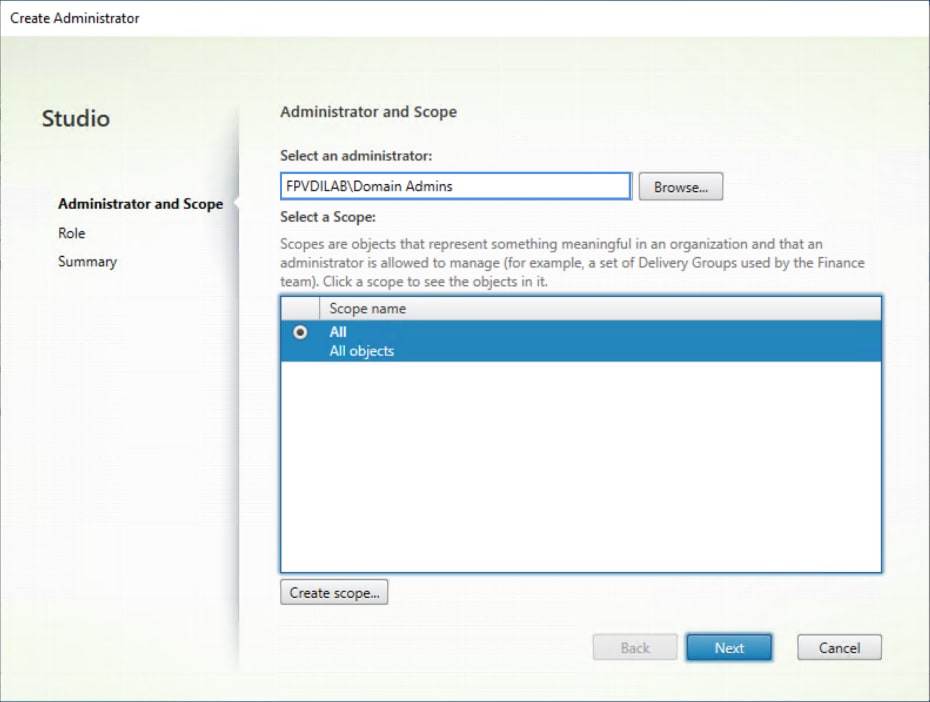
Step 4. Select an appropriate Role.
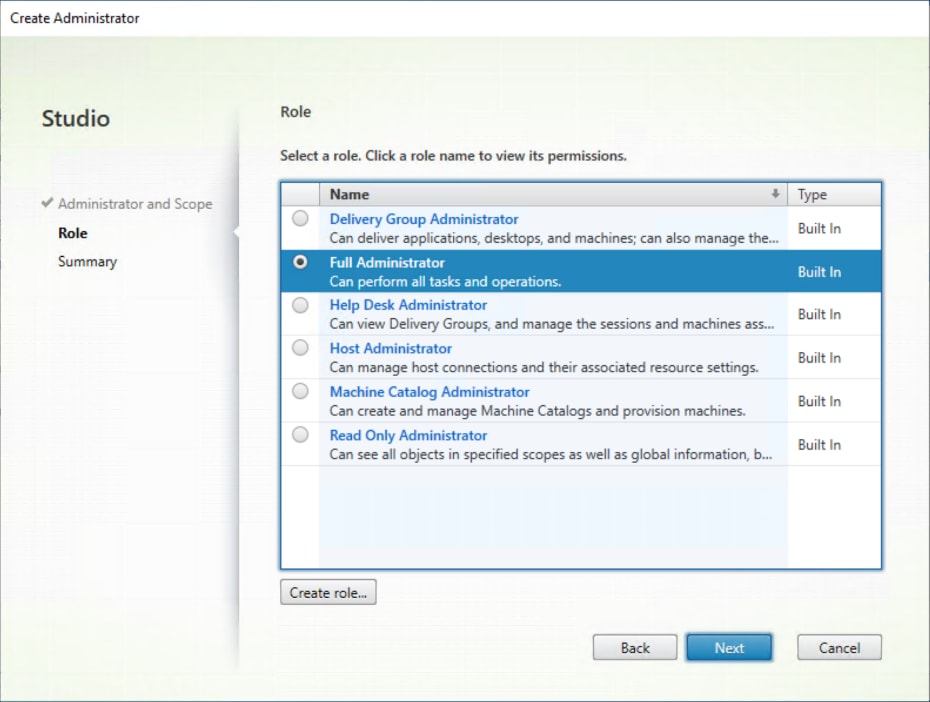
Step 5. Review the Summary, check Enable administrator and click Finish.
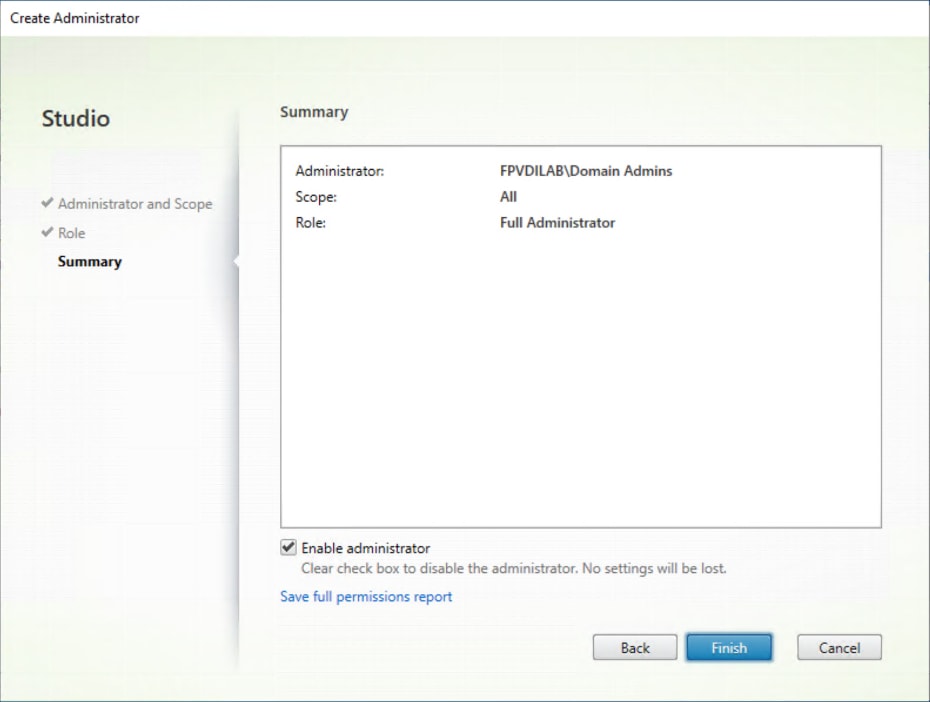
Procedure 8. Install and Configure StoreFront
Note: Citrix StoreFront stores aggregate desktops and applications from Citrix Virtual Apps and Desktops sites, making resources readily available. In this CVD, we created two StoreFront servers on dedicated virtual machines.
Step 1. To begin the installation of the StoreFront, connect to the first StoreFront server and launch the installer from the Citrix_Virtual_Apps_and_Desktops_7_2402_LTSR_CU3_3100.
Step 2. Click Start.
Step 3. Click Extend Deployment Citrix StoreFront.
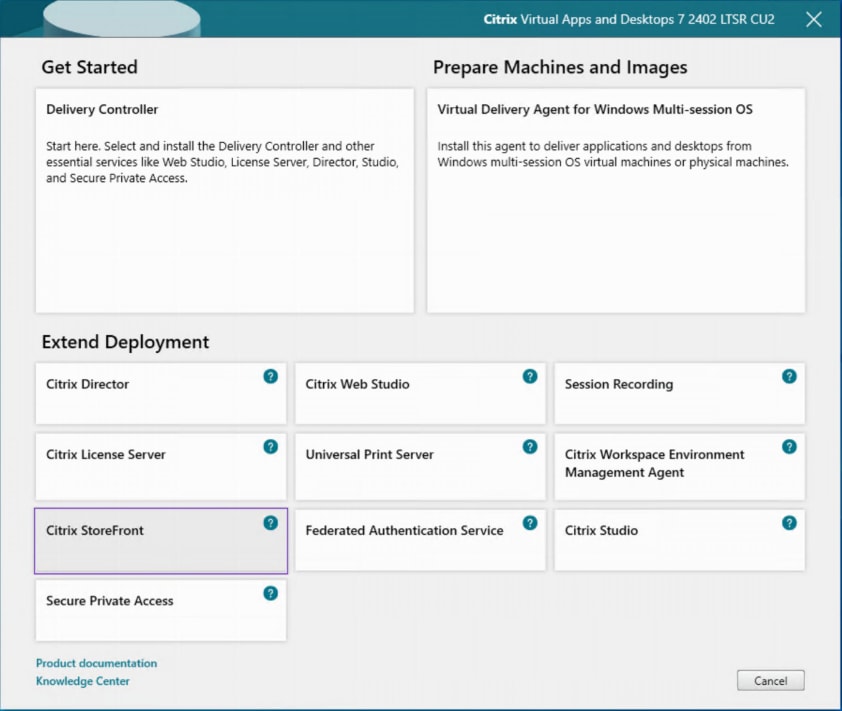
Step 4. Indicate your acceptance of the license by selecting I have read, understand, and accept the terms of the license agreement.
Step 5. Click Next.
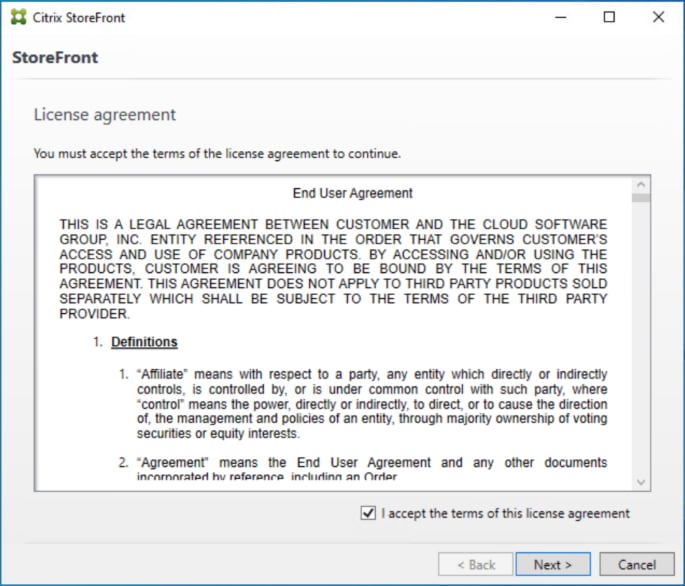
Step 6. Review the prerequisites and click Next.
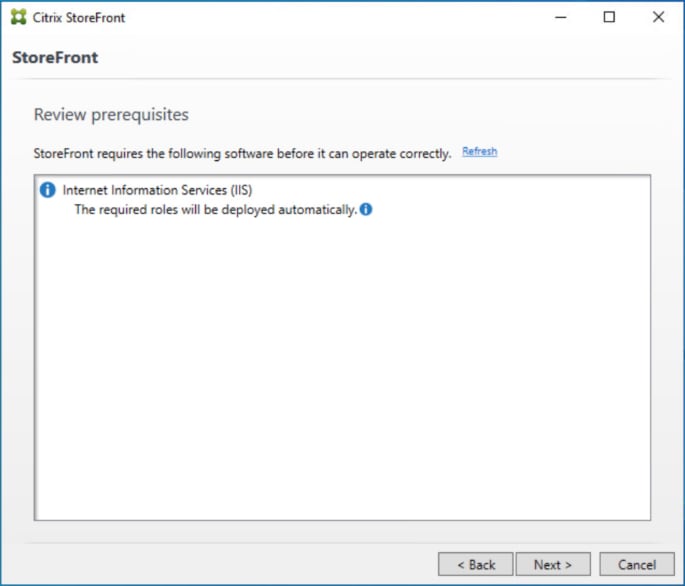
Step 7. Click Install.
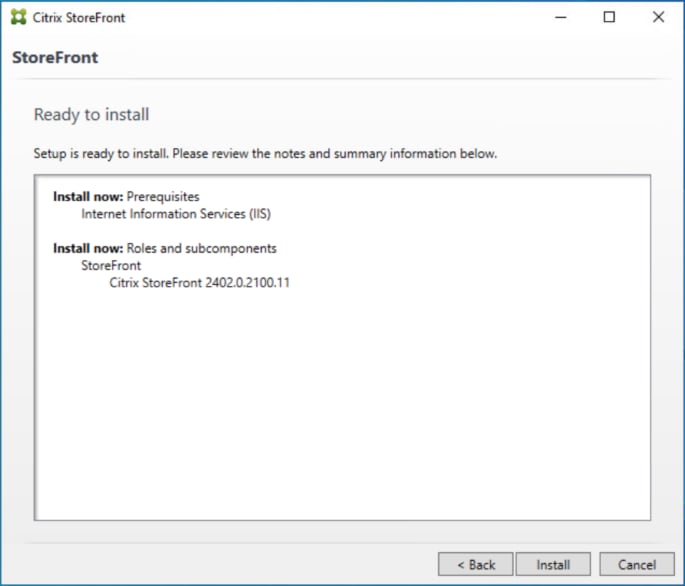
Step 8. Click Finish.
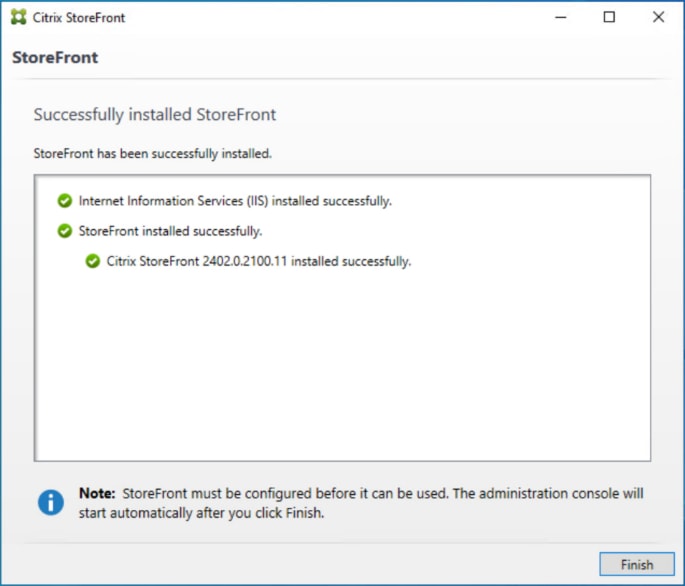
Step 9. Click Yes to reboot the server.
Step 10. Open the StoreFront Management Console.
Step 11. Click Create a new deployment.
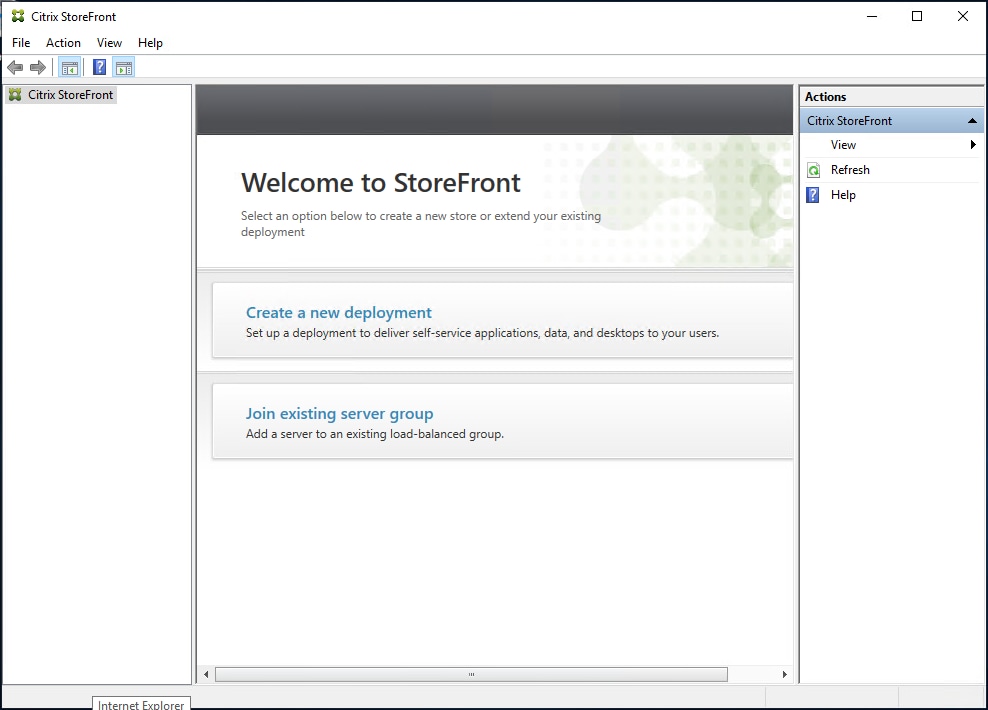
Step 12. Specify a name for your Base URL.
Step 13. Click Next.
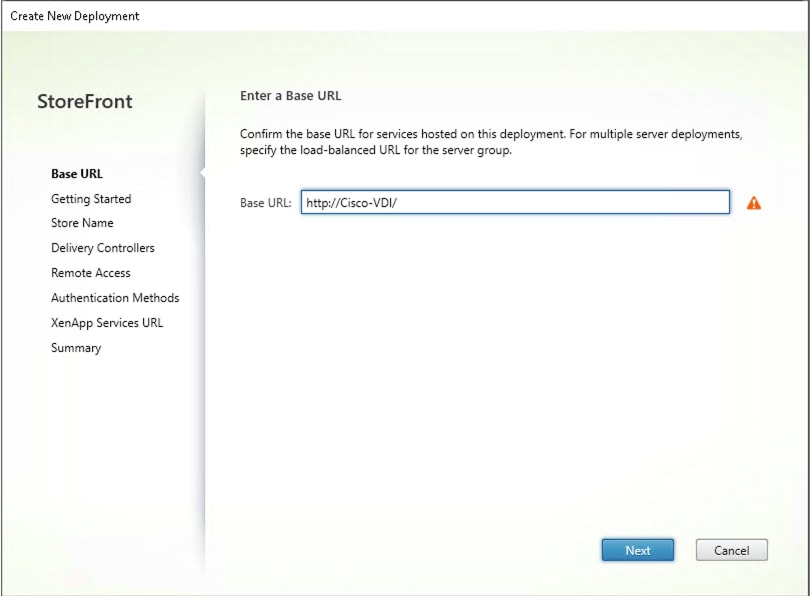
Note: For a multiple server deployment use the load balancing environment in the Base URL box.
Step 14. Click Next.
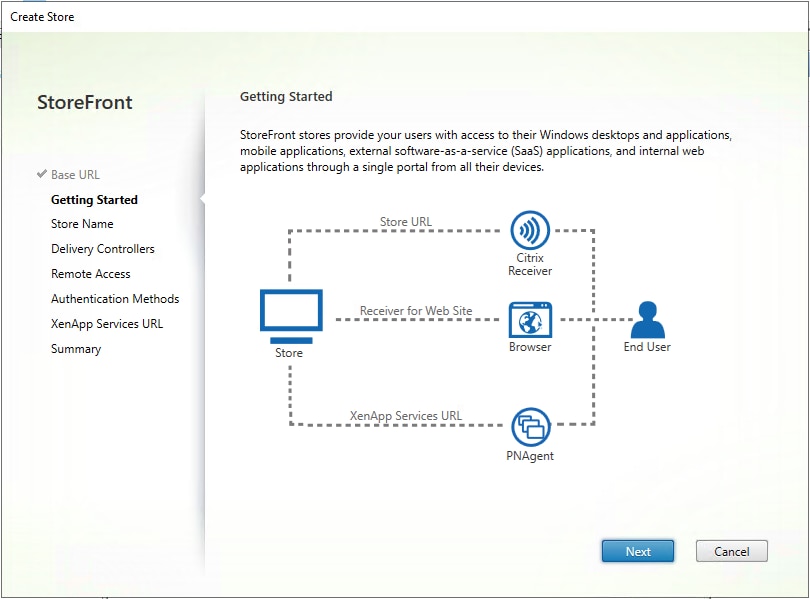
Step 15. Specify a name for your store and click Next.
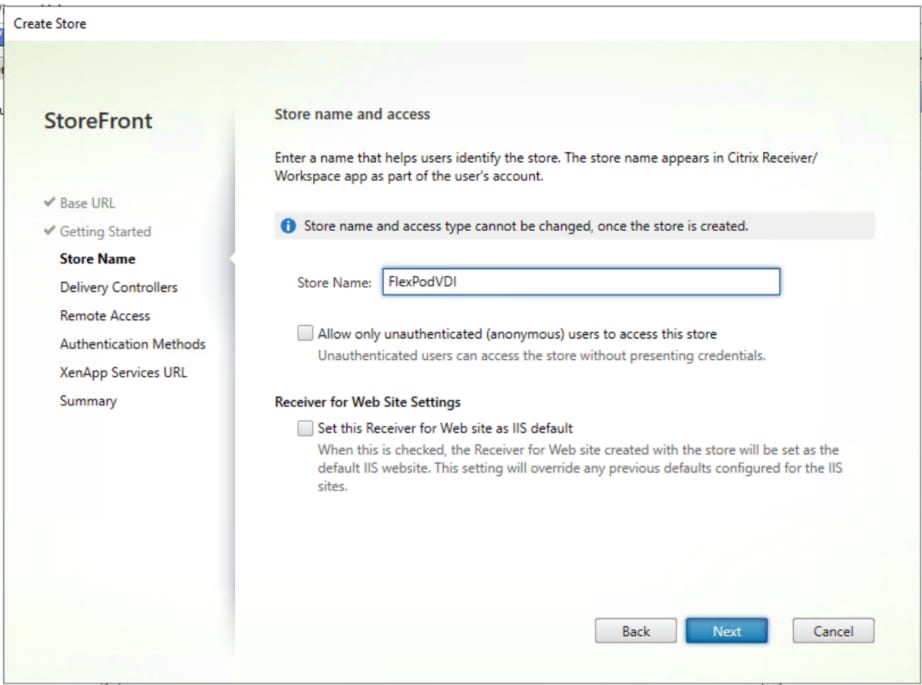
Step 16. Click Add to specify the Delivery controllers for your new Store.
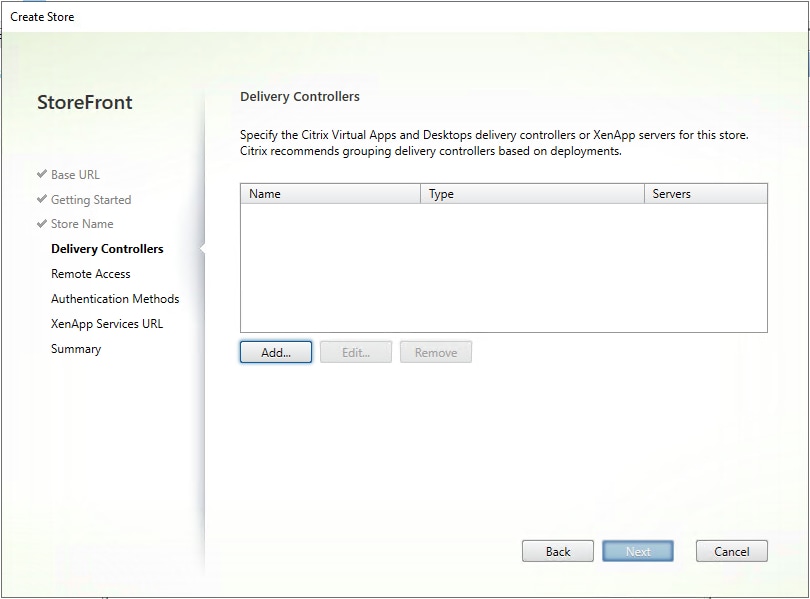
Step 17. Add the required Delivery Controllers to the store.
Step 18. Click OK.
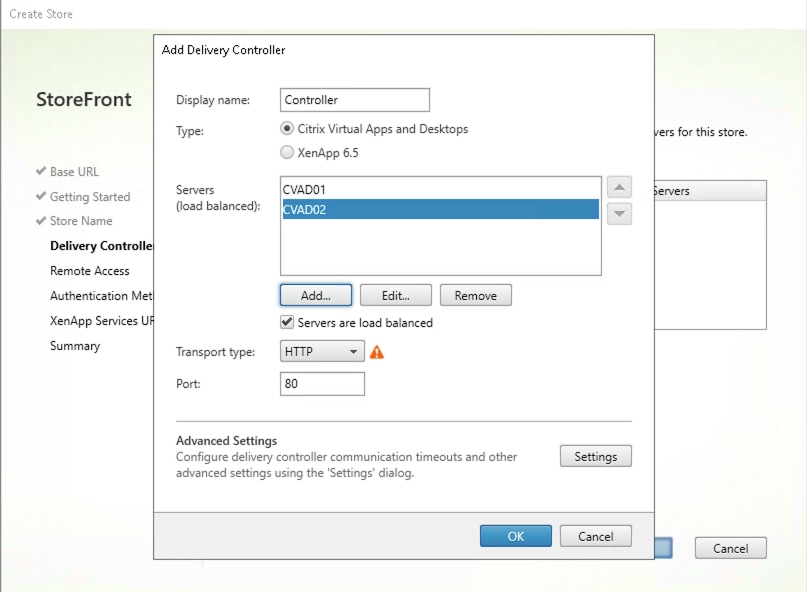
Step 19. Click Next.
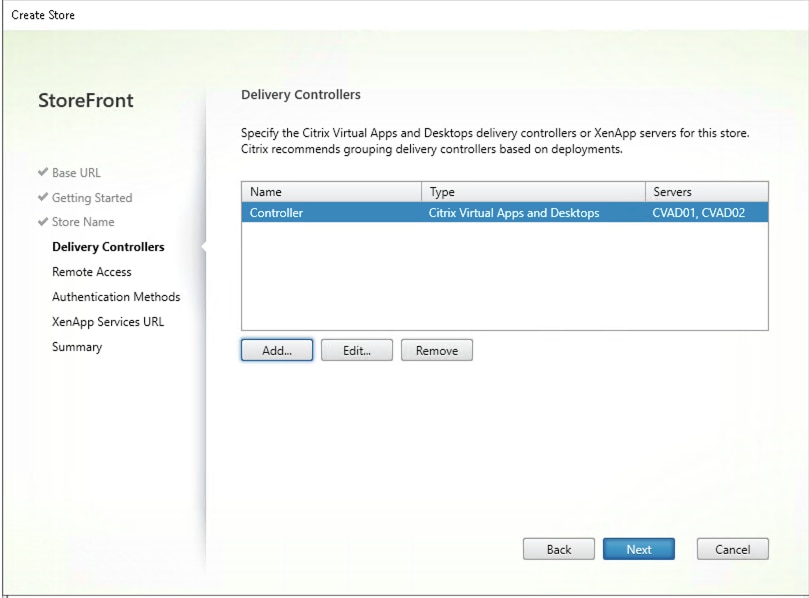
Step 20. Specify how connecting users can access the resources, in this environment only local users on the internal network are able to access the store.
Step 21. Click Next.
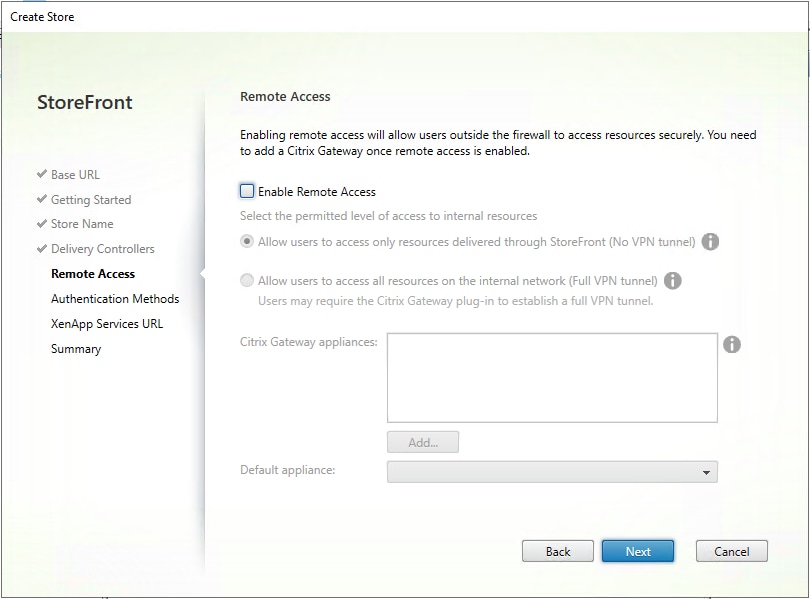
Step 22. On the Authentication Methods page, select the methods your users will use to authenticate to the store. The following methods were configured in this deployment:
● Username and password: Users enter their credentials and are authenticated when they access their stores.
● Domain passthrough: Users authenticate to their domain-joined Windows computers, and their credentials are used to log them in automatically when they access their stores.
Step 23. Click Next.
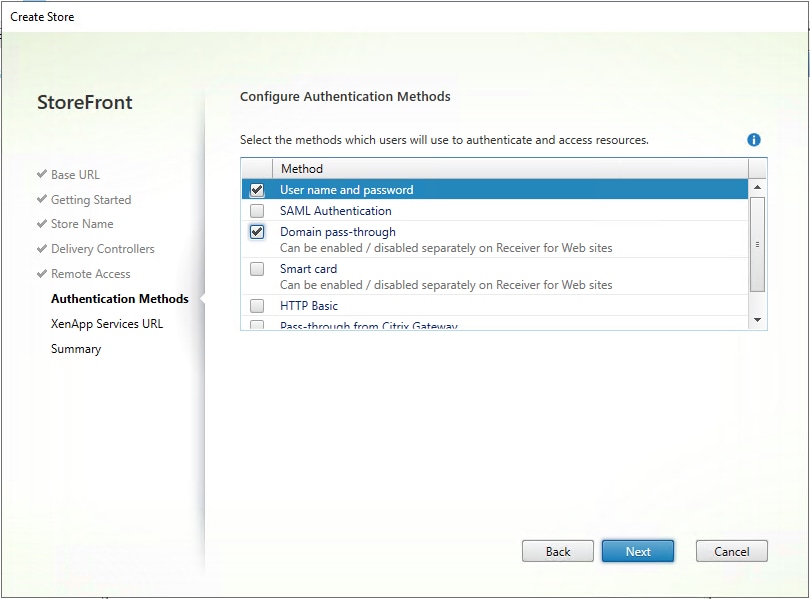
Step 24. Configure the XenApp Service URL for users who use PNAgent to access the applications and desktops.
Step 25. Click Create.
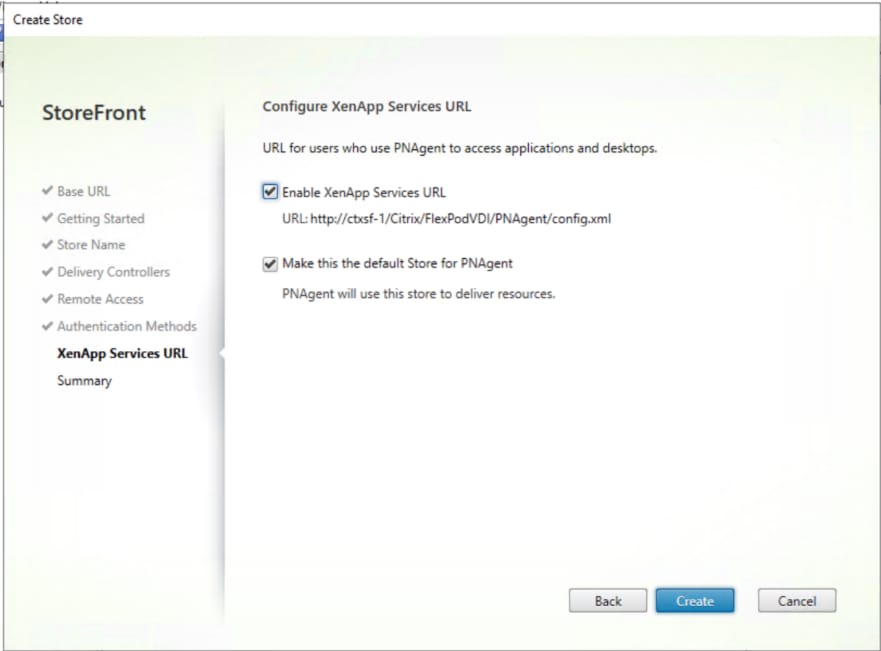
Step 26. After creating the store click Finish.
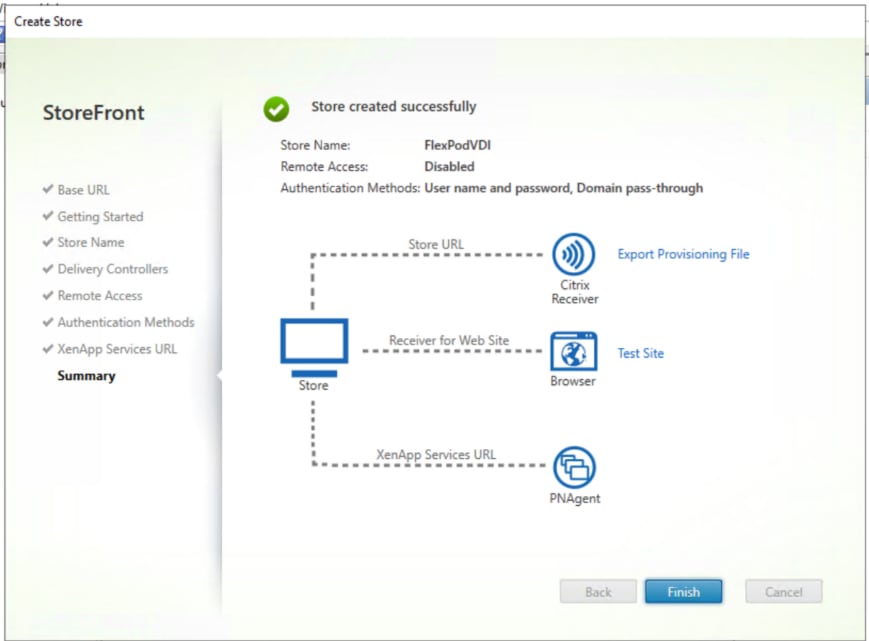
Procedure 9. Additional StoreFront Configuration
Note: After the first StoreFront server is completely configured and the Store is operational, you can add additional servers.
Step 1. Install the second StoreFront using the installation steps detailed in Procedure 8.
Step 2. Connect to the first StoreFront server.
Step 3. To add the second server and generate the authorization information that allows the additional StoreFront server to join the server group, select Add Server from Actions pane in the Server Group.
Step 4. Copy the authorization code.
Step 5. From the StoreFront Console on the second server select Join existing server group.
Step 6. In the Join Server Group dialog, enter the name of the first Storefront server and paste the Authorization code into the Join Server Group dialog.
Step 7. Click Join.
A message appears when the second server has joined successfully.
Step 8. Click OK.
The second StoreFront is now in the Server Group.
Install and Configure Citrix Provisioning Server 2402
In most implementations, there is a single vDisk providing the standard image for multiple target devices. Thousands of target devices can use a single vDisk shared across multiple Provisioning Services (PVS) servers in the same farm, simplifying virtual desktop management. This section describes the installation and configuration tasks required to create a PVS implementation.
The PVS server can have many stored vDisks, and each vDisk can be several gigabytes in size. Your streaming performance and manageability can be improved using a RAID array, SAN, or NAS. PVS software and hardware requirements are available in the Provisioning Services 2402 document.
Procedure 1. Configure Prerequisites
Step 1. Set the following Scope Options on the DHCP server hosting the PVS target machines:
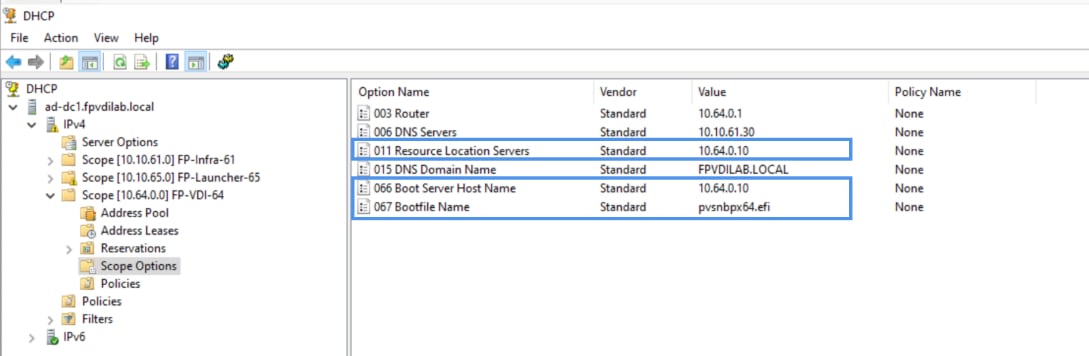
Step 2. Create a DNS host records with multiple PVS Servers IP for TFTP Load Balancing:
Note: Only one MS SQL database is associated with a farm. You can choose to install the Provisioning Services database software on an existing SQL database, if that machine can communicate with all Provisioning Servers within the farm, or with a new SQL Express database machine, created using the SQL Express software that is free from Microsoft.
The following databases are supported: Microsoft SQL Server 2022, 2019,2017, 2016 SP2 (Express, Standard, and Enterprise Editions). Please review the Citrix documentation for further reference.
Note: Microsoft SQL 2022 was installed separately for this CVD.
Procedure 2. Install and Configure Citrix Provisioning Service 2402
Step 1. Connect to Citrix Provisioning server and launch Citrix Provisioning Services 2402 LTSR CU3_1 ISO and let AutoRun launch the installer.
Step 2. Click Console Installation.
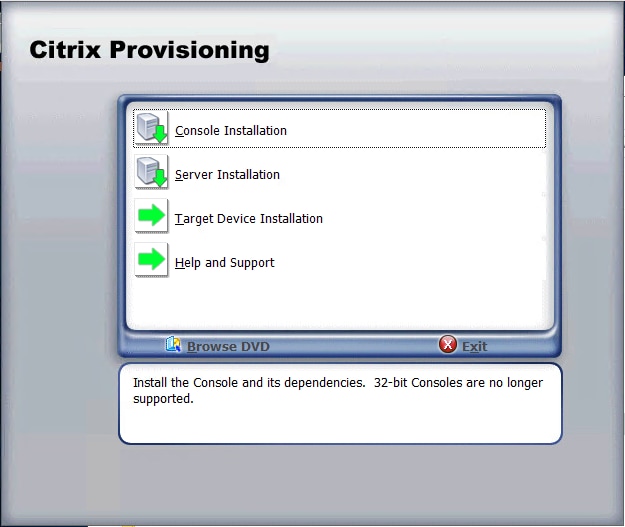
Step 3. Click Install to start the console installation.
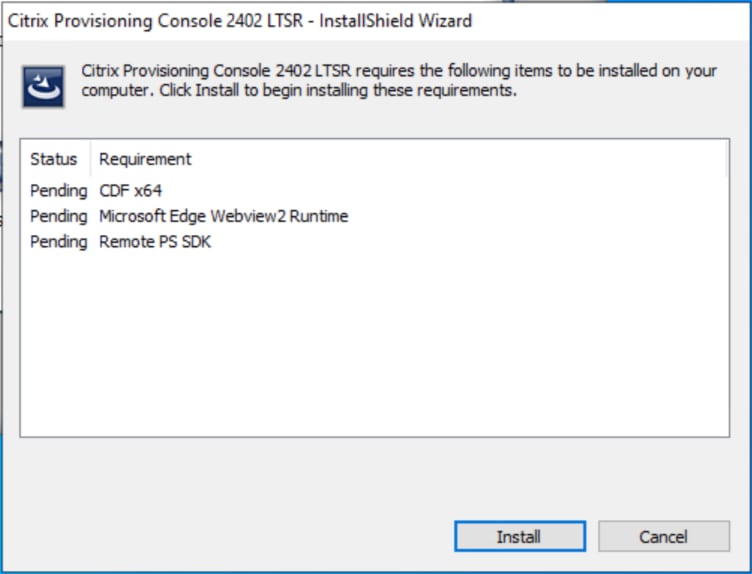
Step 4. Click Next.
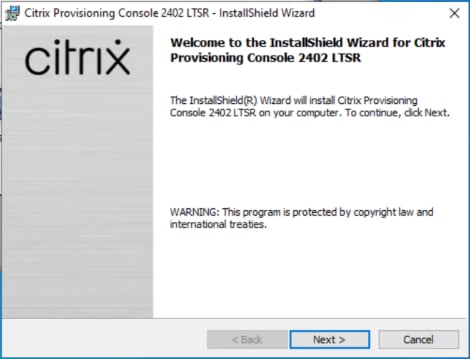
Step 5. Read the Citrix License Agreement. If acceptable, select the radio button I accept the terms in the license agreement.
Step 6. Click Next.
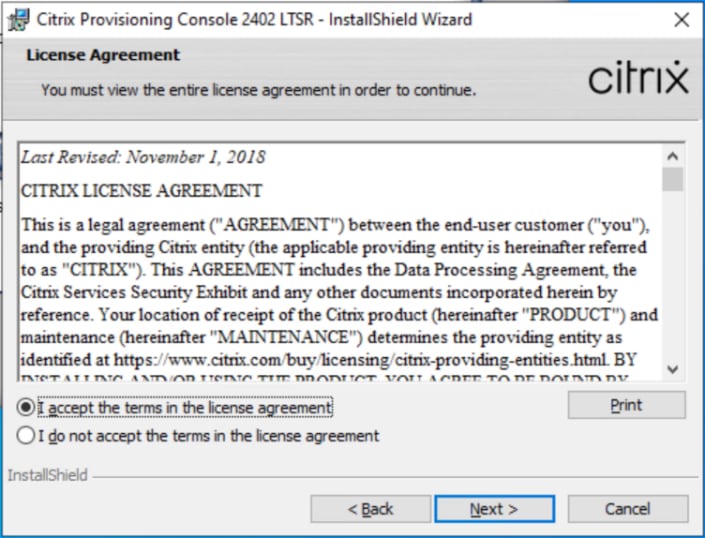
Step 7. Optionally, provide User Name and Organization.
Step 8. Click Next.
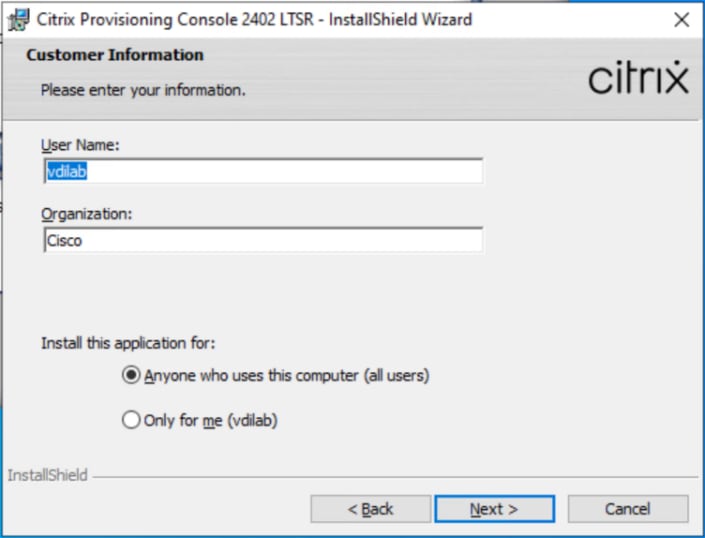
Step 9. Accept the default path.
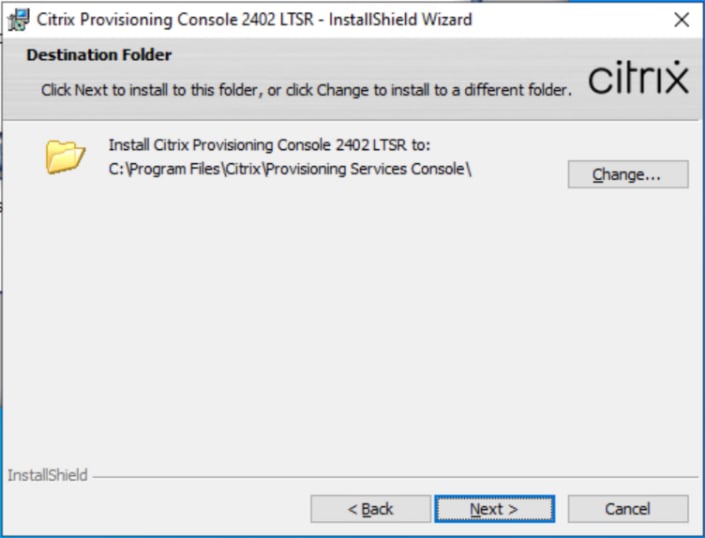
Step 10. Click Install.
Step 11. Click Finish after successful installation.
Step 12. From the main installation screen, select Server Installation.
Step 13. Click Install on the prerequisites dialog.
Step 14. Click Next when the Installation wizard starts.
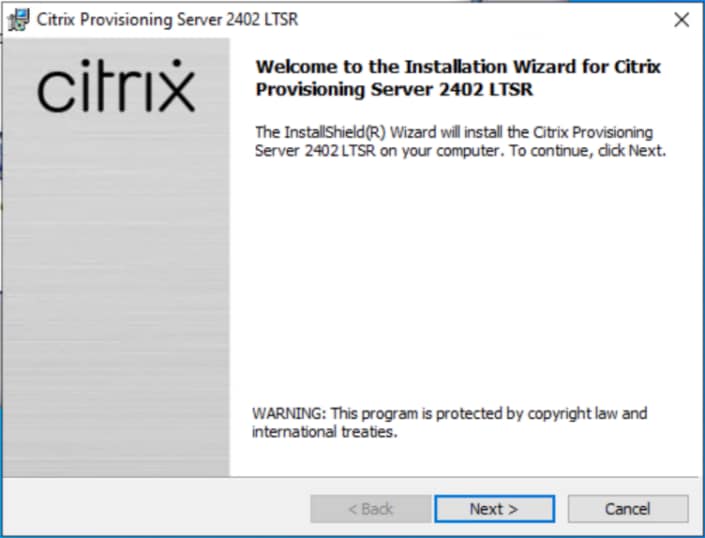
Step 15. Review the license agreement terms. If acceptable, select the radio button I accept the terms in the license agreement.
Step 16. Click Next.
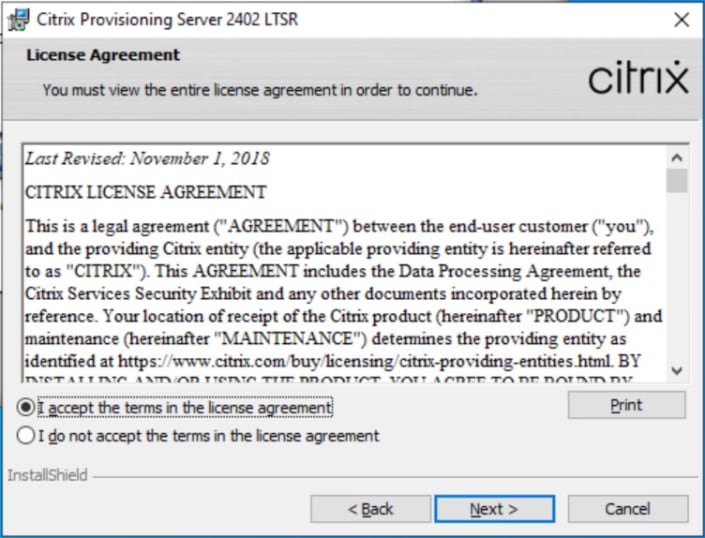
Step 17. Select Automatically open all Citrix Provisioning ports. Click Next.
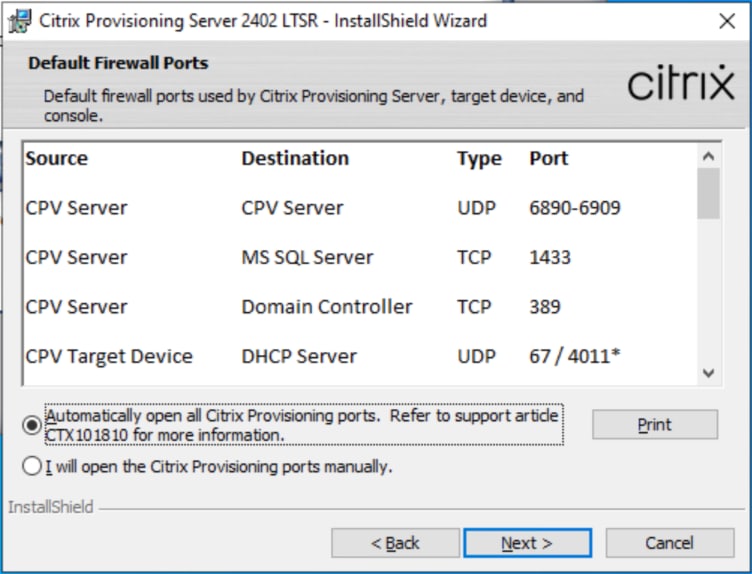
Step 18. Provide User Name and Organization information. Select who will see the application.
Step 19. Click Next.
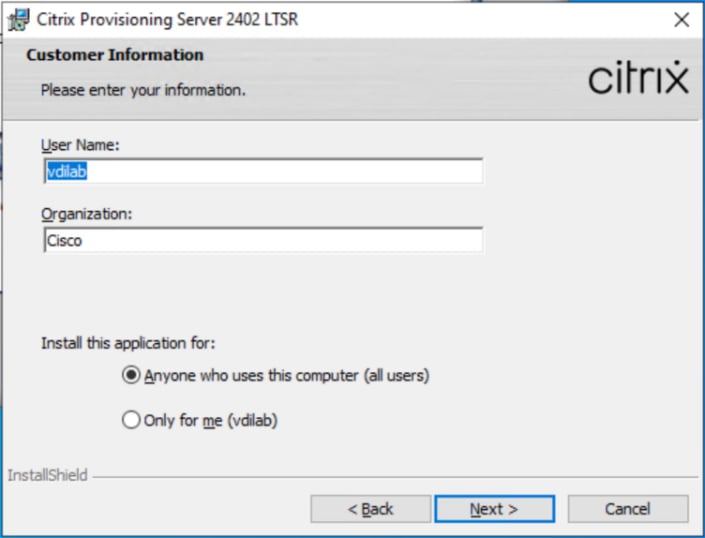
Step 20. Accept the default installation location.
Step 21. Click Next.
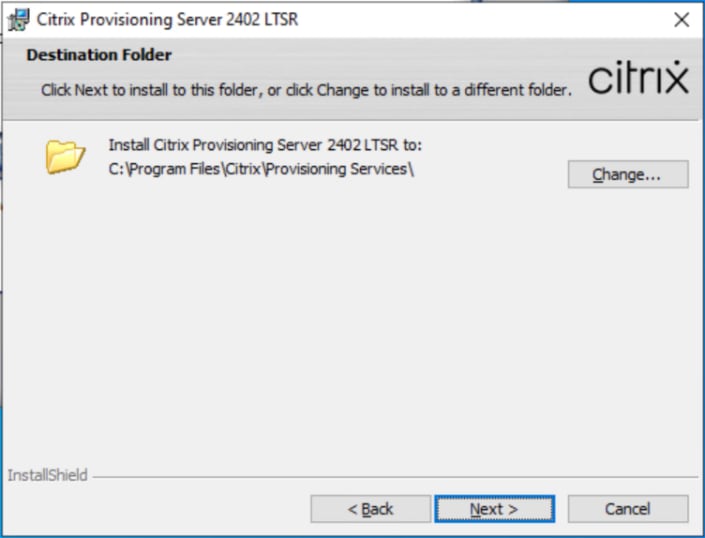
Step 22. Click Install to begin the installation.
Step 23. Click Finish when the install is complete.
Procedure 3. Configure Citrix Provisioning Services
Step 1. Start the Citrix Provisioning Configuration wizard.
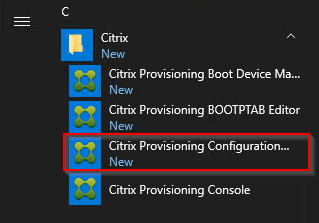
Step 2. Click Next.
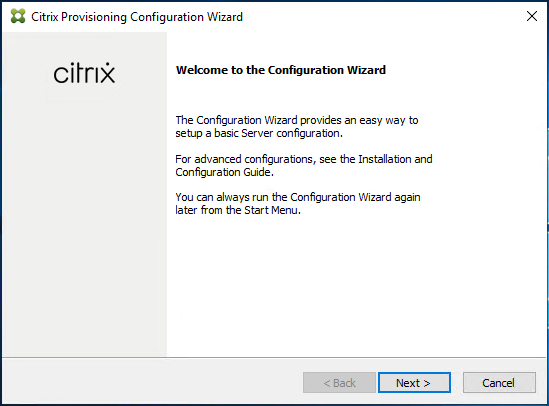
Step 3. Since the PVS server is not the DHCP server for the environment, select the radio button The service that runs on another computer.
Step 4. Click Next.
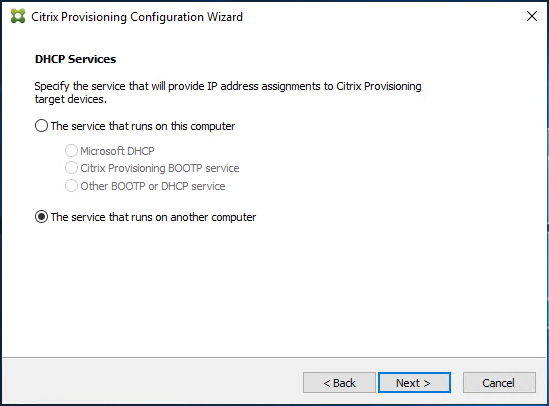
Step 5. Since DHCP boot options are used for TFTP services, select the radio button labeled The service that runs on another computer.
Step 6. Click Next.
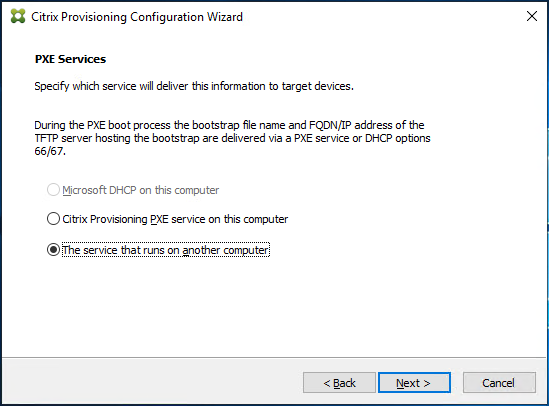
Step 7. Since this is the first server in the farm, select the radio button Create farm.
Step 8. Click Next.
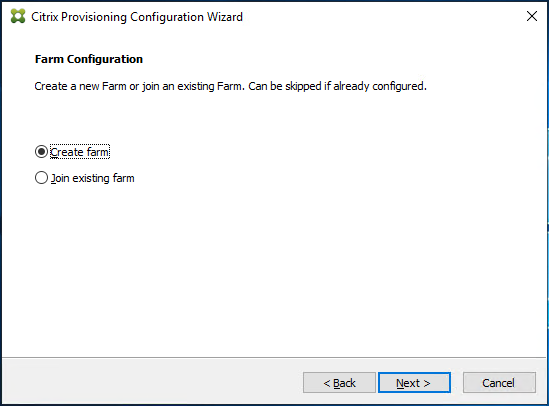
Step 9. Enter the FQDN of the SQL server.
Step 10. Click Next.
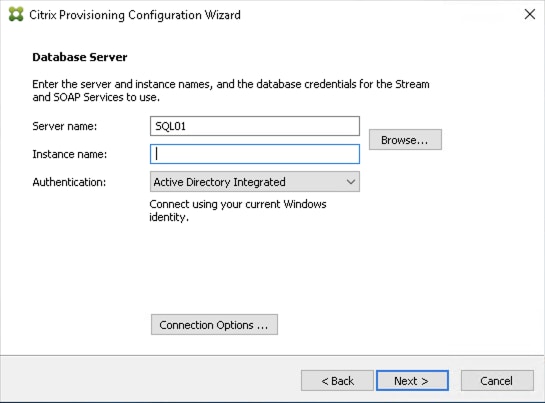
Step 11. Provide the Database, Farm, Site, and Collection name.
Step 12. Click Next.
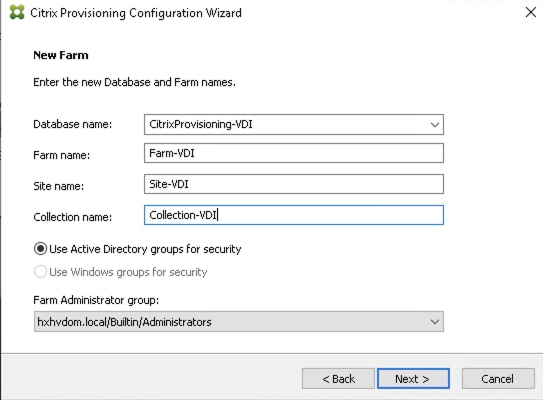
Step 13. Provide the vDisk Store details.
Step 14. Click Next.
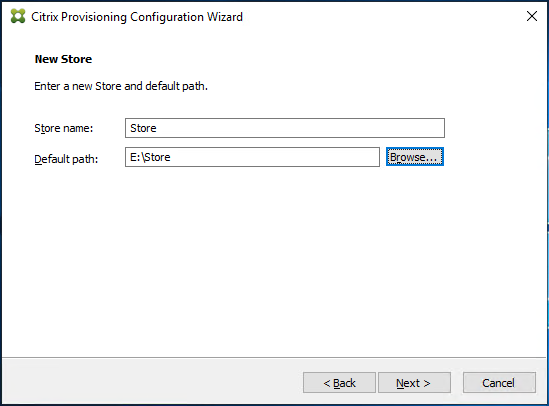
Note: For large scale PVS environment, it is recommended to create the share using support for CIFS/SMB3 on an enterprise ready File Server.
Step 15. Provide the FQDN of the license server.
Step 16. Optionally, provide a port number if changed on the license server.
Step 17. Click Next.
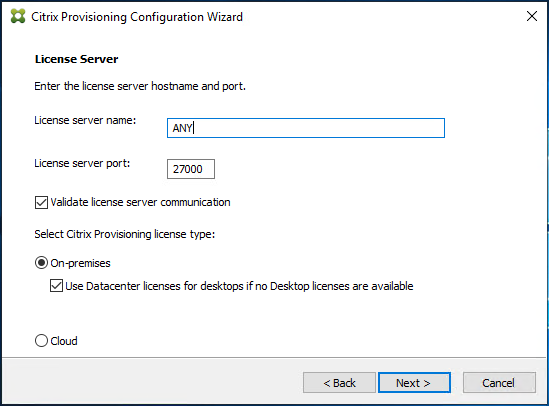
Step 18. If an Active Directory service account is not already setup for the PVS servers, create that account prior to clicking Next in this dialog.
Step 19. Select the Specified user account radio button.
Step 20. Complete the User name, Domain, Password, and Confirm password fields, using the PVS account information created earlier.
Step 21. Click Next.
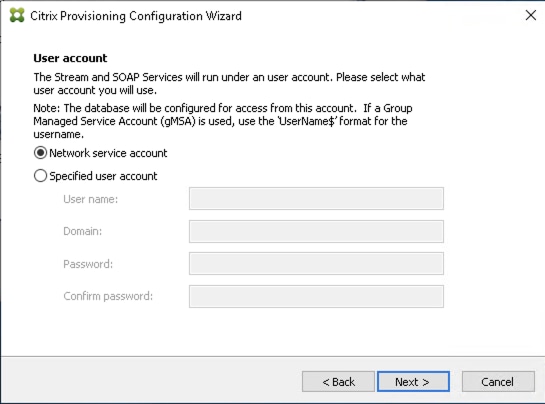
Step 22. Set the Days between password updates to 7.
Note: This will vary per environment. 7 days for the configuration was appropriate for testing purposes.
Step 23. Click Next.
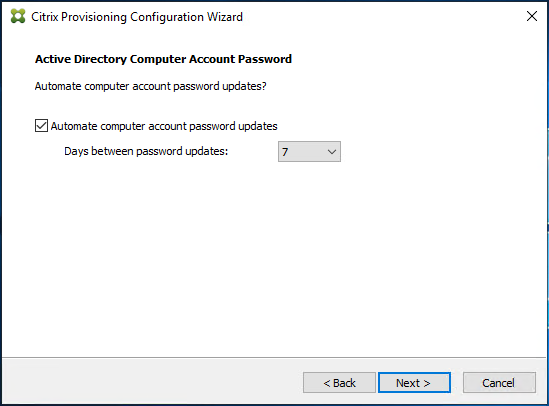
Step 24. Keep the defaults for the network cards.
Step 25. Click Next.
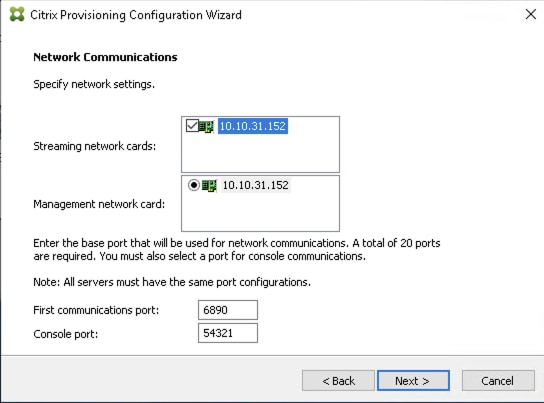
Step 26. Select Use the Citrix Provisioning Services TFTP service checkbox.
Step 27. Click Next.
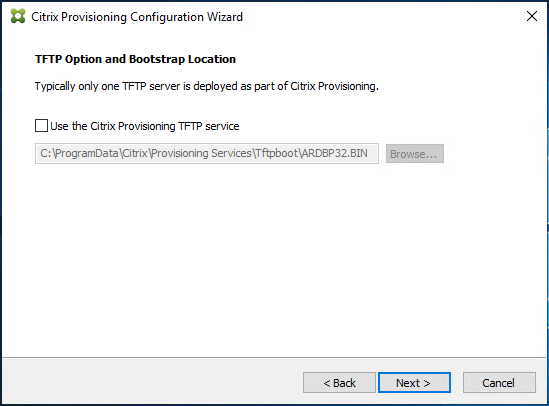
Step 28. If Soap Server is used, provide details.
Step 29. Click Next.
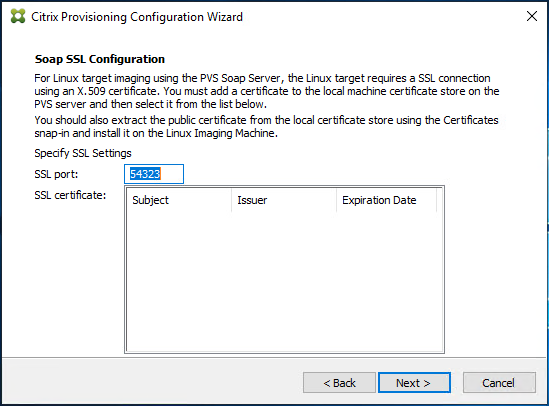
Step 30. If desired, fill in Problem Report Configuration.
Step 31. Click Next.
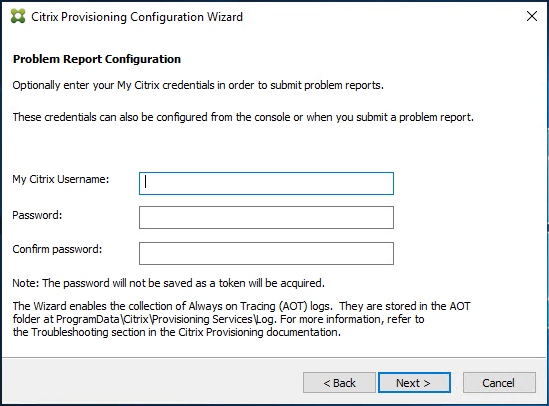
Step 32. Click Finish to start the installation.
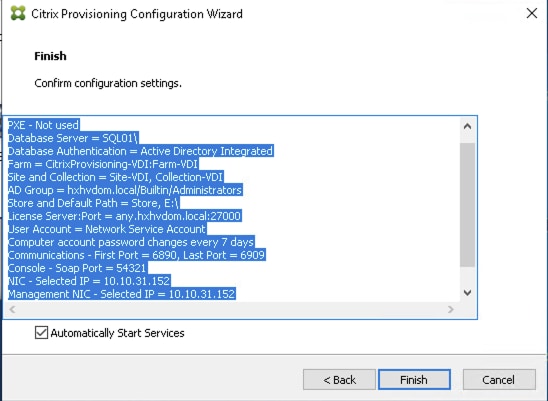
Step 33. When the installation is completed, click Done.
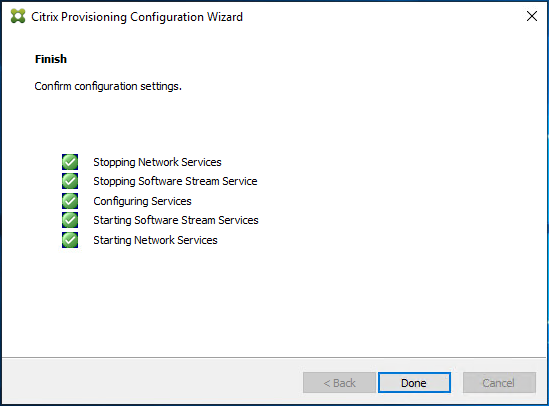
Procedure 4. Install Additional PVS Servers
Note: Complete the installation steps on the additional PVS servers up to the configuration step where it asks to Create or Join a farm. In this CVD, we repeated the procedure to add a total of three PVS servers.
This procedure details how to join additional Provisioning servers to the farm already configured in the previous steps.
Step 1. On the Farm Configuration dialog, select Join existing farm.
Step 2. Click Next.
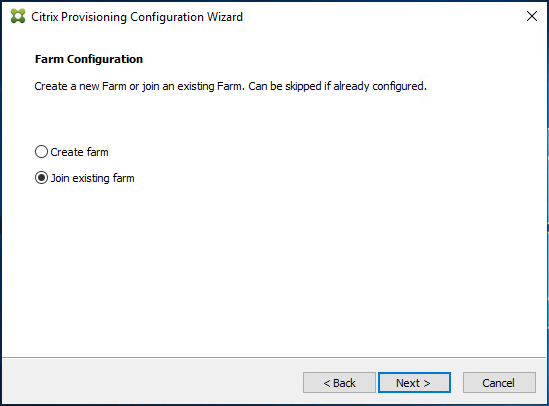
Step 3. Provide the FQDN of the SQL Server.
Step 4. Click Next.
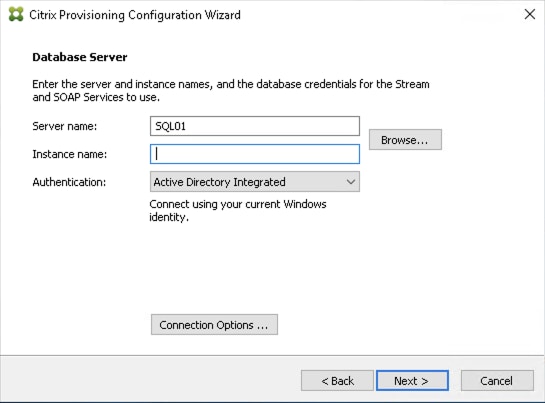
Step 5. Accept the Farm Name.
Step 6. Click Next.
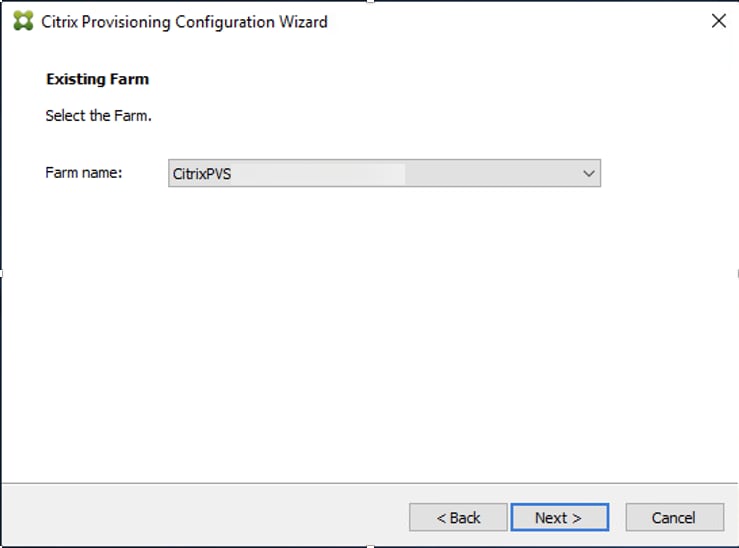
Step 7. Accept the Existing Site.
Step 8. Click Next.
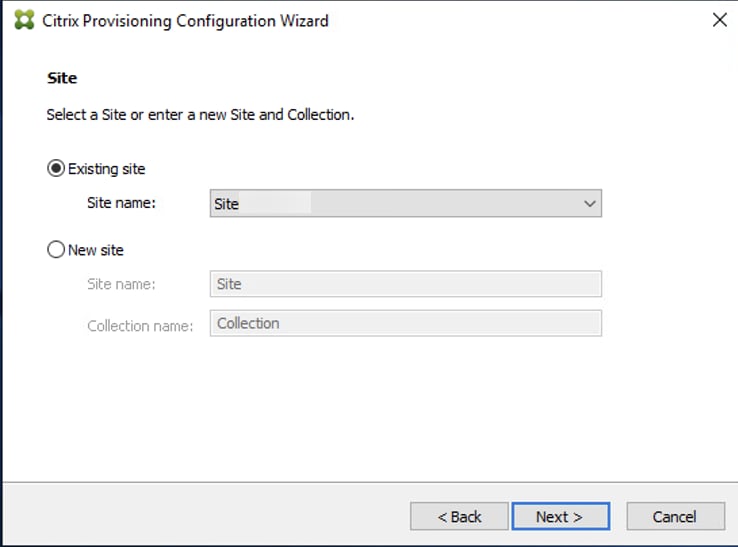
Step 9. Accept the existing vDisk store.
Step 10. Click Next.
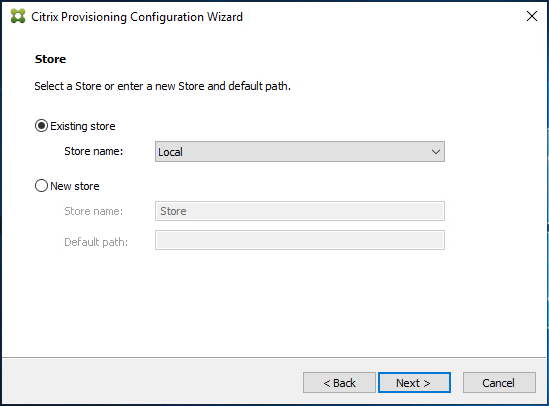
Step 11. Provide the FQDN of the license server.
Step 12. Optionally, provide a port number if changed on the license server.
Step 13. Click Next.
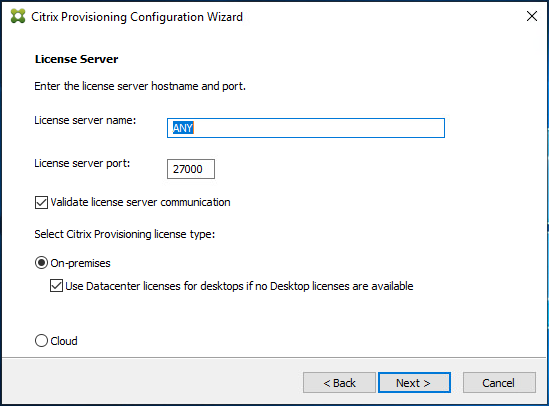
Step 14. Provide the PVS service account information.
Step 15. Click Next.
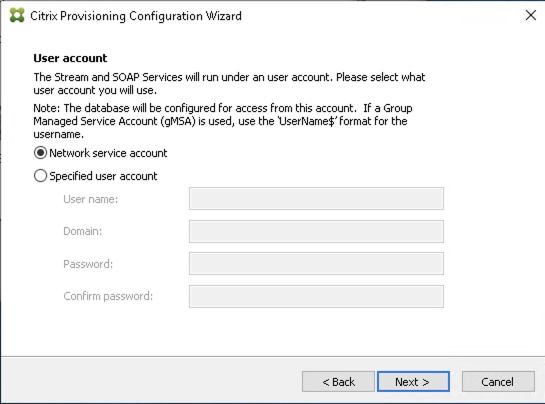
Step 16. Set the Days between password updates to 7.
Step 17. Click Next.
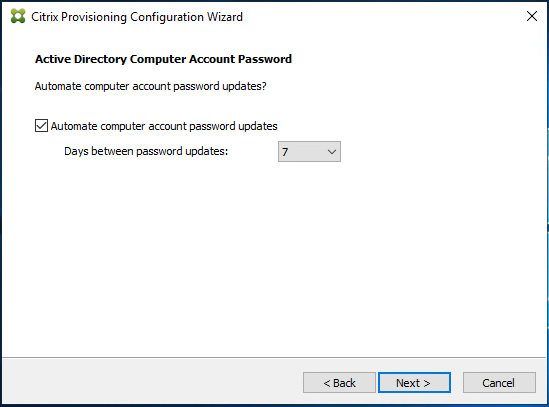
Step 18. Accept the network card settings.
Step 19. Click Next.
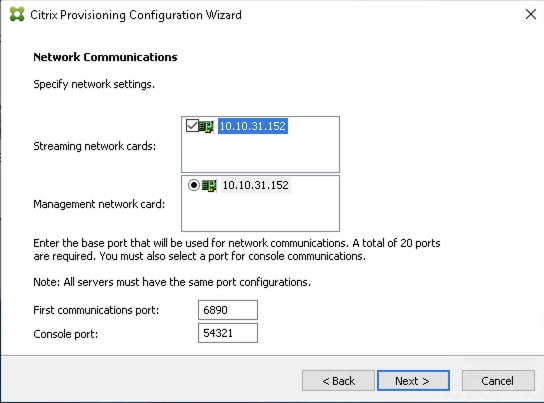
Step 20. Check the box for Use the Citrix Provisioning Services TFTP service.
Step 21. Click Next.
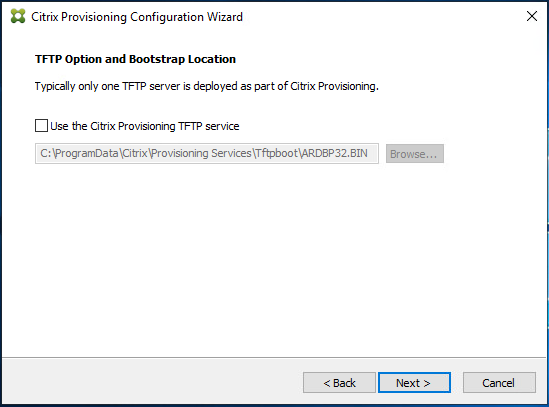
Step 22. If Soap Server is used, provide details.
Step 23. Click Next.
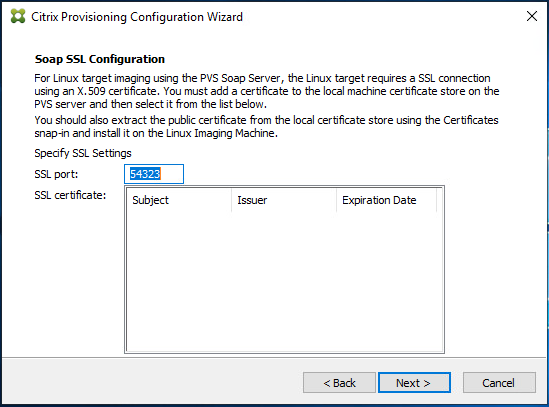
Step 24. If desired, fill in the Problem Report Configuration.
Step 25. Click Next.
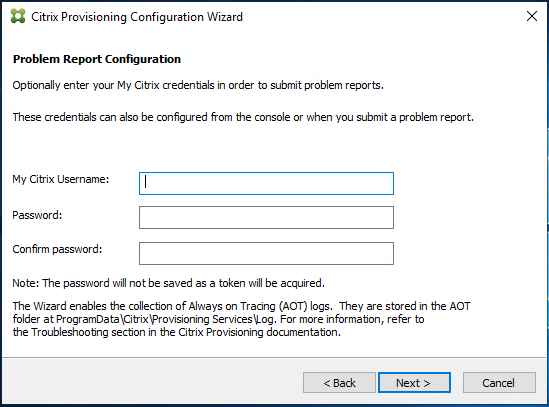
Step 26. Click Finish to start the installation process.
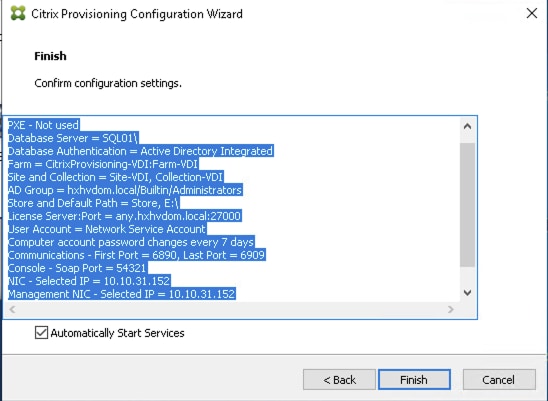
Step 27. Click Done when the installation finishes.
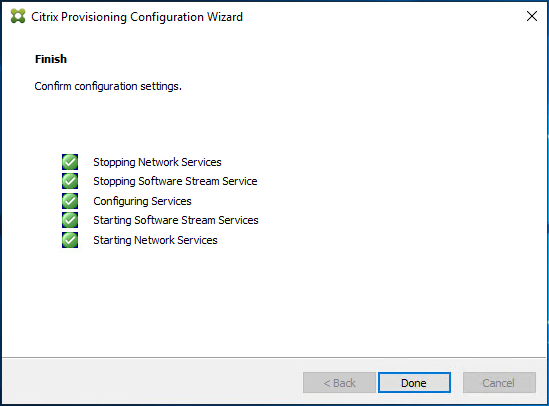
Note: Optionally, you can install the Provisioning Services console on the second PVS server following the procedure in the section Install the Citrix Provisioning Server Target Device Software.
Step 28. After completing the steps to install the three additional PVS servers, launch the Provisioning Services Console to verify that the PVS Servers and Stores are configured and that DHCP boot options are defined.
Step 29. Launch Provisioning Services Console and select Connect to Farm.
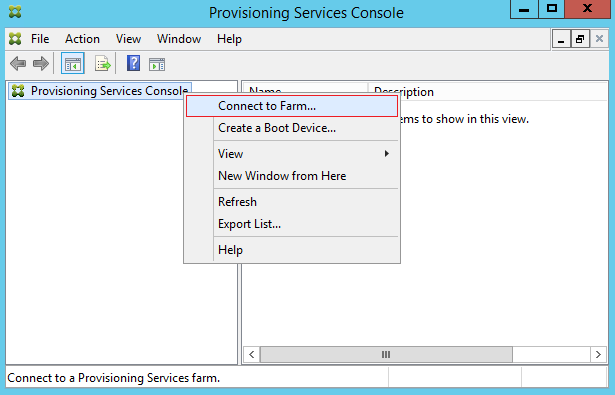
Step 30. Enter Localhost for the PVS1 server.
Step 31. Click Connect.
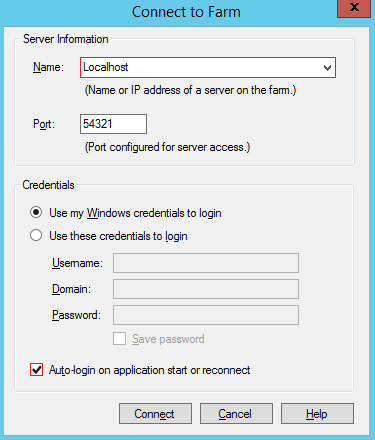
Step 32. Right-click Store and select Properties from the drop-down list.
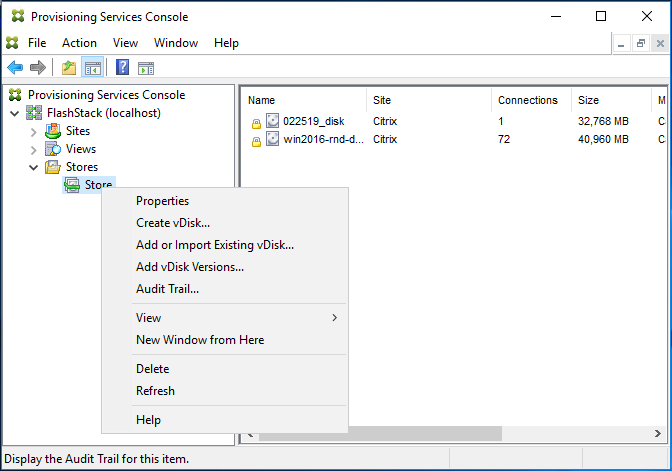
Step 33. In the Store Properties dialog, add the Default store path to the list of Default write cache paths.
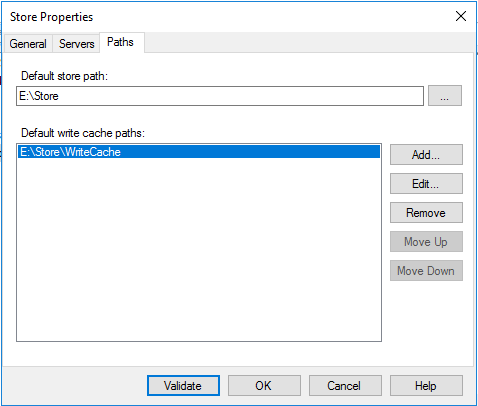
Step 34. Click Validate. If the validation is successful, click Close and then click OK to continue.
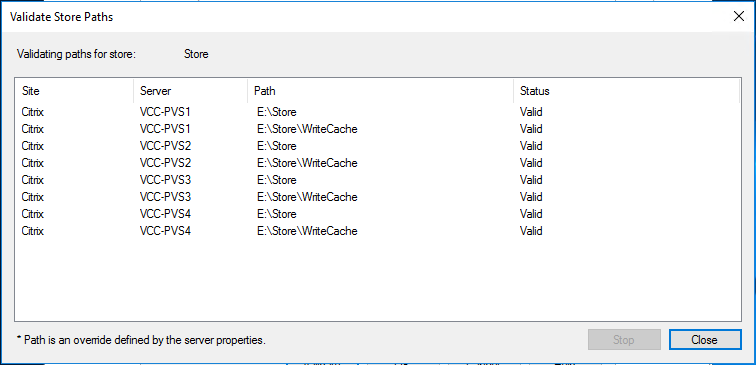
Procedure 5. Install Citrix Virtual Apps and Desktops Virtual Desktop Agents
Virtual Delivery Agents (VDAs) are installed on the server and workstation operating systems and enable connections for desktops and apps. The following procedure was used to install VDAs for both Single-session OS and Multi-session OS.
By default, when you install the Virtual Delivery Agent, Citrix User Profile Management is installed silently on master images. (Using profile management as a profile solution is optional, but FSLogix was used for this CVD and is described in a later section.)
Step 1. Launch the Citrix Virtual Apps and Desktops installer from Citrix_Virtual_Apps_and_Desktops_7_2402_ LTSR_CU3_3100.
Step 2. Click Start on the Welcome Screen.
Step 3. To install the VDA for the Hosted Virtual Desktops (VDI), select Virtual Delivery Agent for Windows Single-session OS.
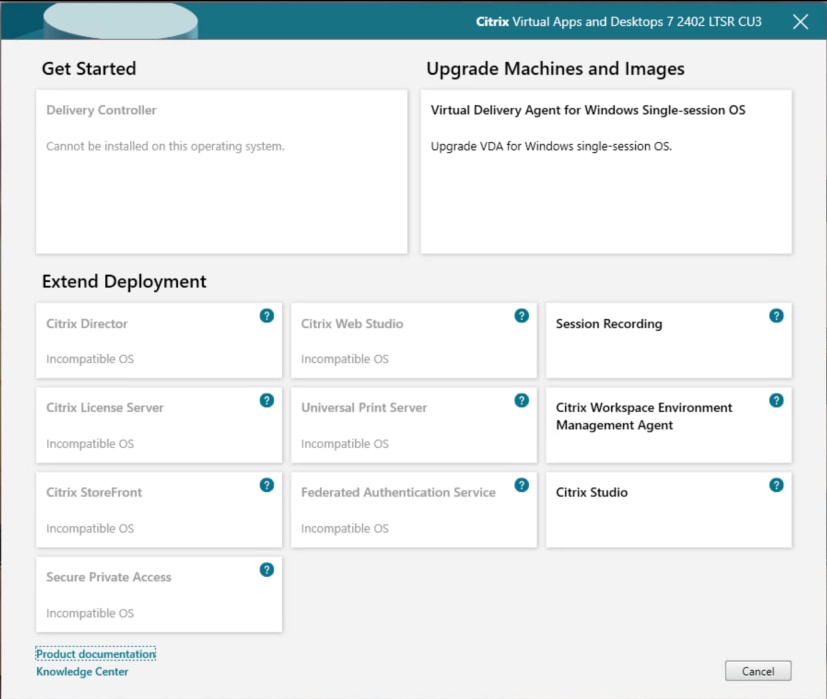
Step 4. Complete the steps found in the Virtual Delivery Agent installation.
Step 5. Select Create a master MCS image.
Step 6. Click Next.
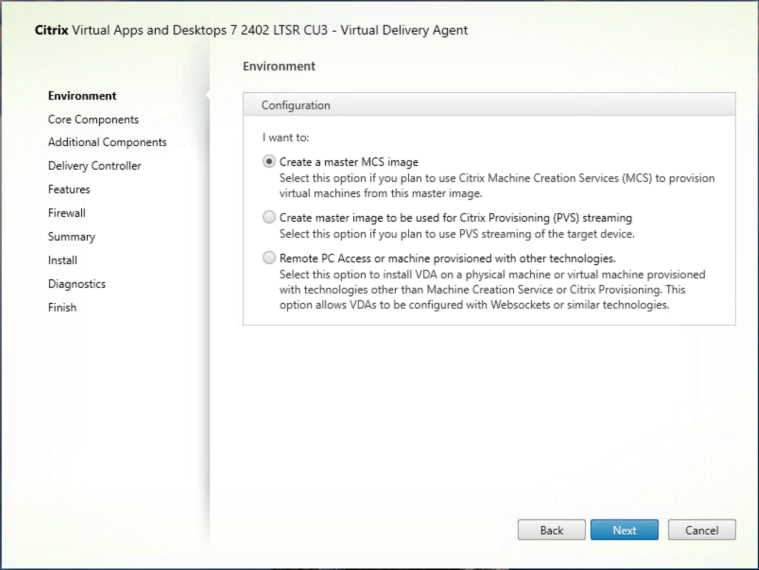
Step 7. Select Create a master image to be used for Citrix Provisioning streaming or third-party provisioning tools when building image to be delivered with Citrix Provisioning tools.
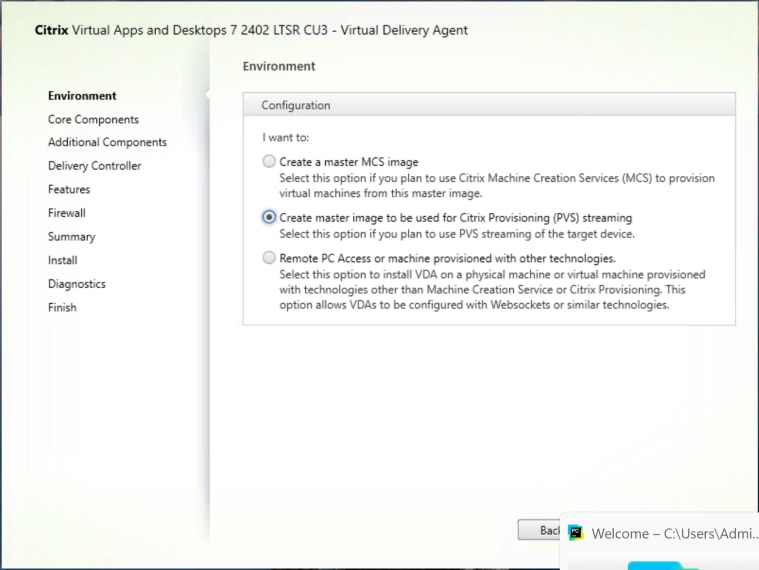
Step 8. Optional; do not select the Citrix Workspace App.
Step 9. Click Next.
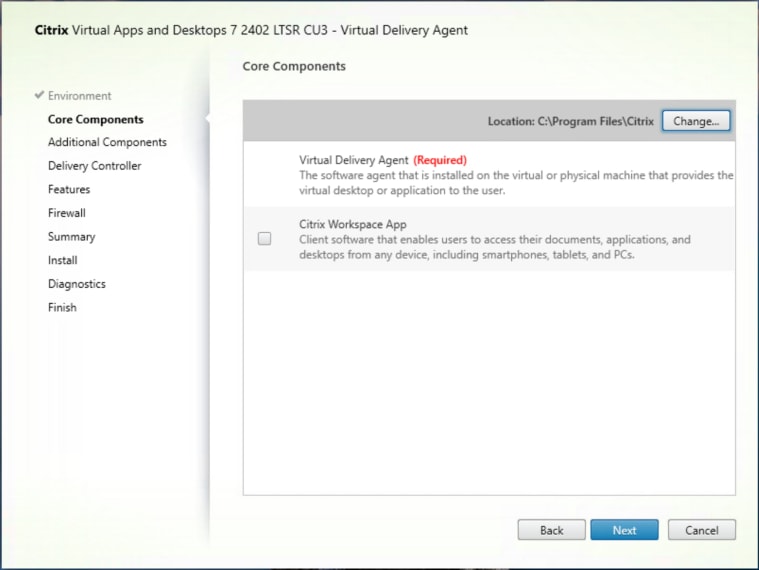
Step 10. Select the additional components required for your image.
Note: In this design, only the default components were installed on the image.
Step 11. Click Next.
Step 12. Configure the Delivery Controllers.
Step 13. Click Next.
Step 14. Click Yes
Step 15. Optional; select additional features.
Step 16. Click Next.
Step 17. For firewall rules, select Automatically.
Step 18. Click Next.
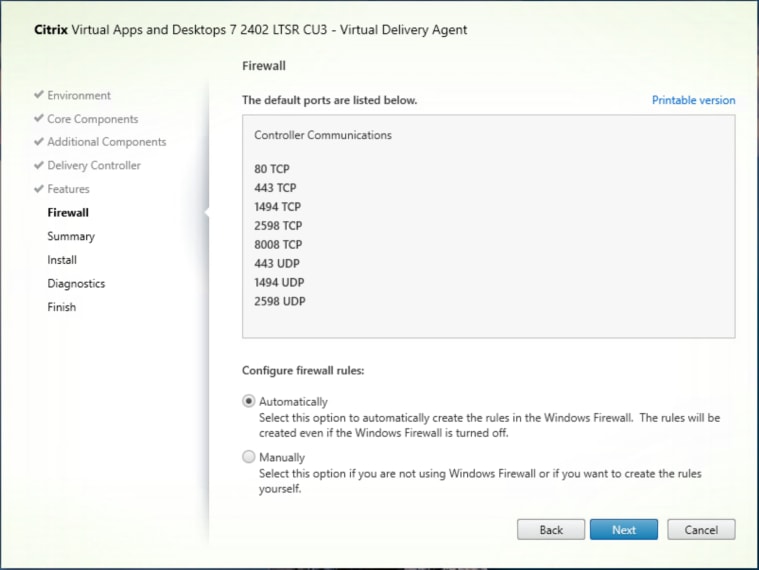
Step 19. Verify the Summary and click Install.
Note: The installation requires a reboot.
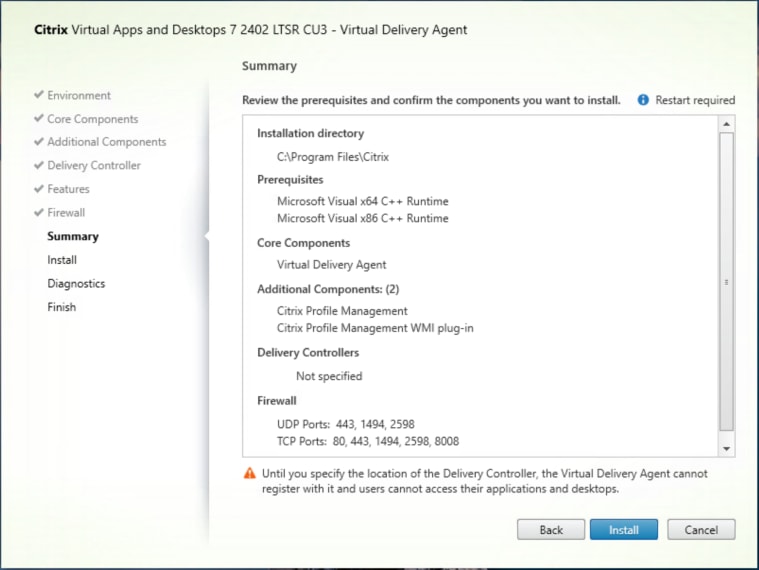
Step 20. Optional; configure Citrix Call Home participation.
Step 21. Click Next.
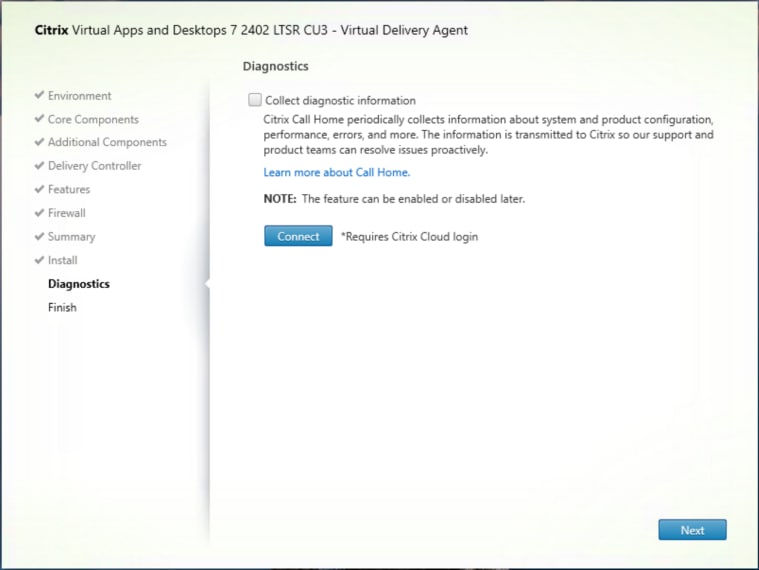
Step 22. Check Restart Machine.
Step 23. Click Finish and the machine will reboot automatically.
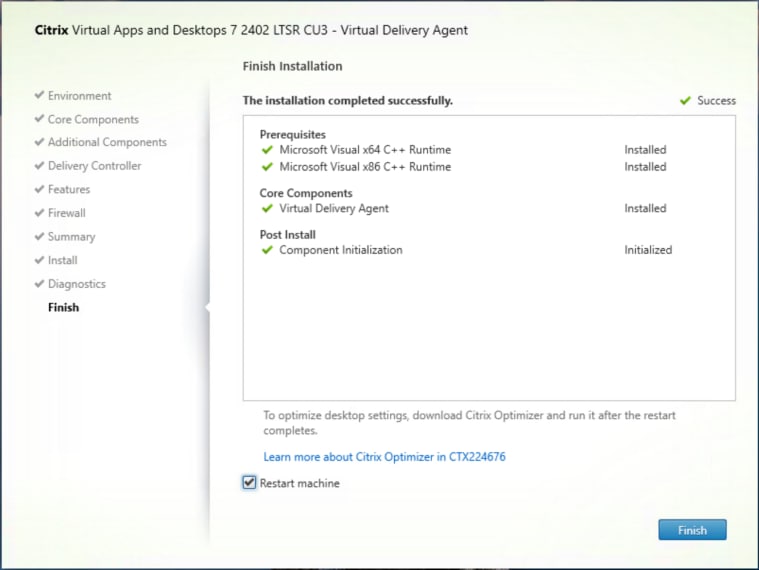
Install the Citrix Provisioning Server Target Device Software
The Master Target Device refers to the target device from which a hard disk image is built and stored on a vDisk. Provisioning Services then streams the contents of the vDisk created to other target devices. This procedure installs the PVS Target Device software that is used to build the RDS and VDI golden images.
Procedure 1. Install the Citrix Provisioning Server Target Device software
Step 1. Launch the PVS installer from the Citrix_Provisioning_2402_LTSR ISO.
Step 2. Click Target Device Installation.
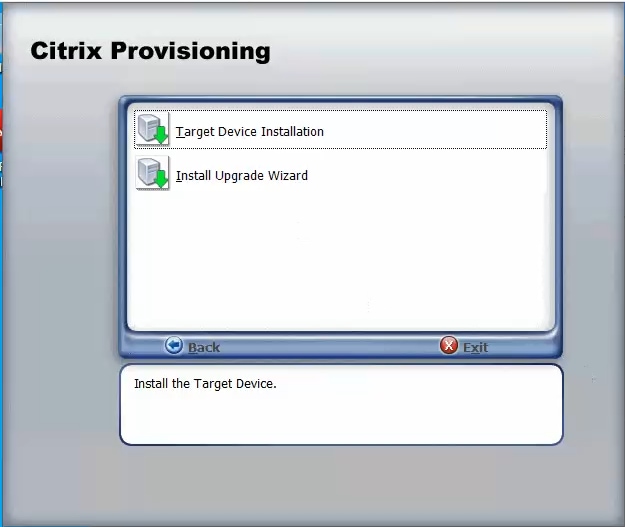
Note: The installation wizard will check to resolve dependencies and then begin the PVS target device installation process.
Step 3. Click Next.
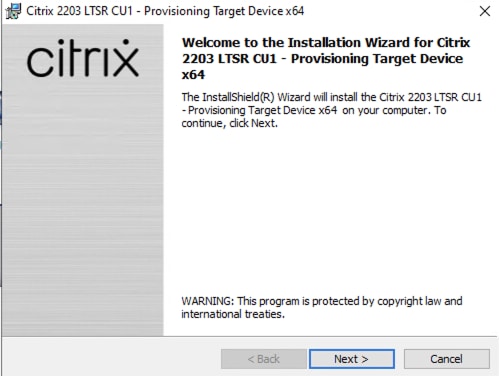
Step 4. Indicate your acceptance of the license by selecting I have read, understand, and accept the terms of the license agreement.
Step 5. Click Next.
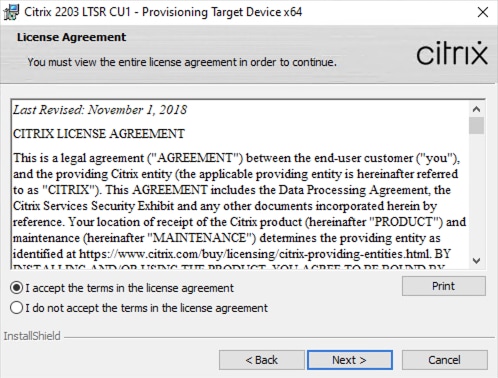
Step 6. Optional; provide the Customer information.
Step 7. Click Next.
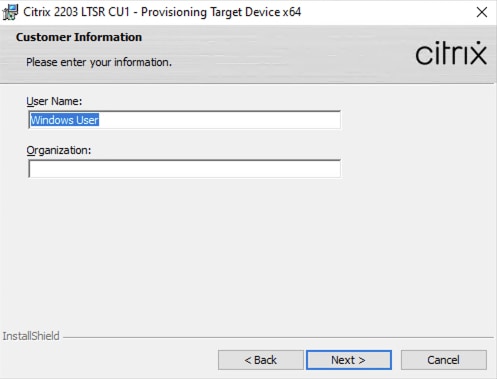
Step 8. Accept the default installation path.
Step 9. Click Next.
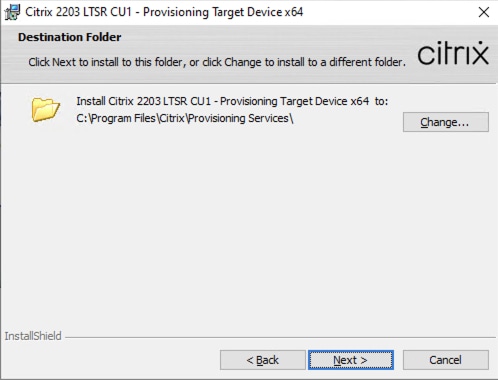
Step 10. Click Install.
Step 11. Deselect the checkbox to launch the Imaging Wizard and click Finish.
Step 12. Click Yes to reboot the machine.
Procedure 2. Create Citrix Provisioning Server vDisks
The PVS Imaging Wizard automatically creates a base vDisk image from the master target device.
The PVS Imaging Wizard's Welcome page appears.
Step 1. Click Next.
Step 2. The Connect to Farm page appears. Enter the name or IP address of a Provisioning Server within the farm to connect to and the port to use to make that connection.
Step 3. Use the Windows credentials (default) or enter different credentials.
Step 4. Click Next.
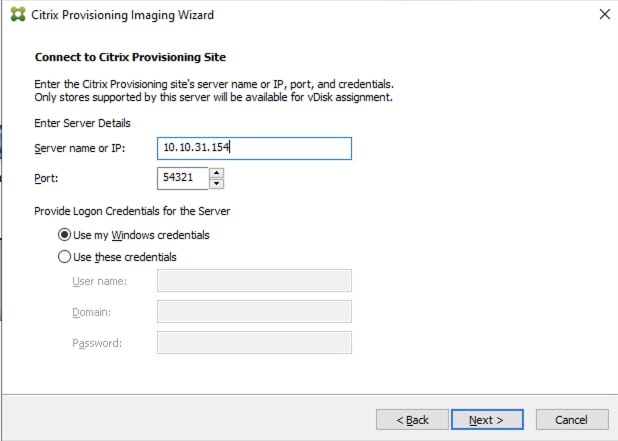
Step 5. Select Create a vDisk.
Step 6. Click Next.
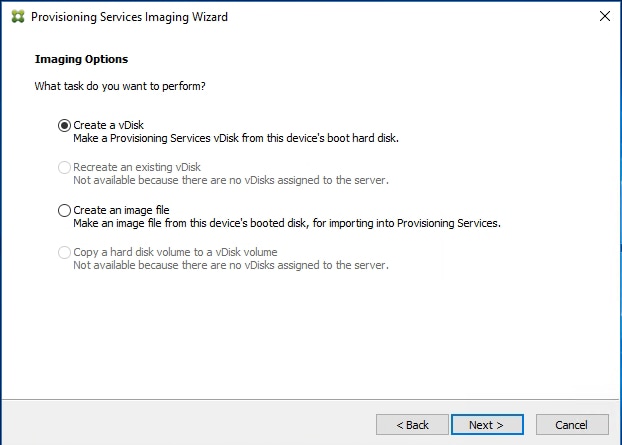
The Add Target Device page appears.
Step 7. Select the Target Device Name, the MAC address associated with one of the NICs that was selected when the target device software was installed on the master target device, and the Collection to which you are adding the device.
Step 8. Click Next.
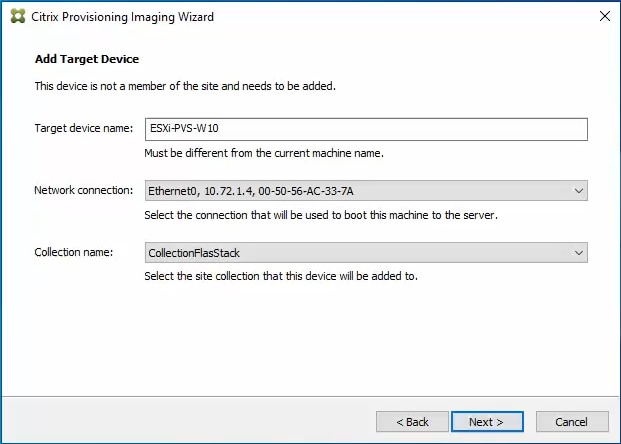
Step 9. The New vDisk dialog displays. Enter the vDisk name.
Step 10. Select the Store where the vDisk will reside. Select the vDisk type, either Fixed or Dynamic, from the drop-down list.
Note: This CVD used Dynamic rather than Fixed vDisks.
Step 11. Click Next.
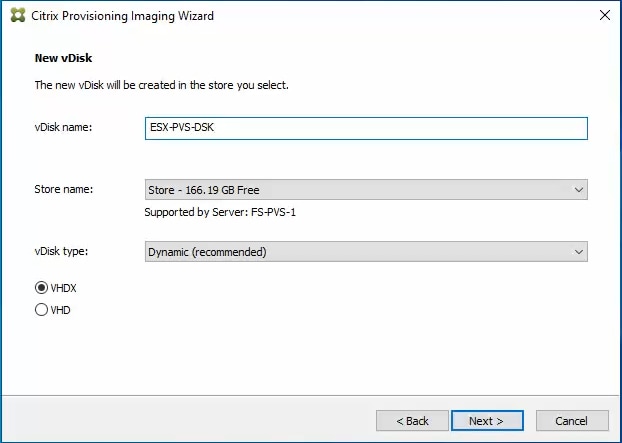
Step 12. On the Microsoft Volume Licensing page, select the volume license option to use for target devices. For this CVD, volume licensing is not used, so the None button is selected.
Step 13. Click Next.
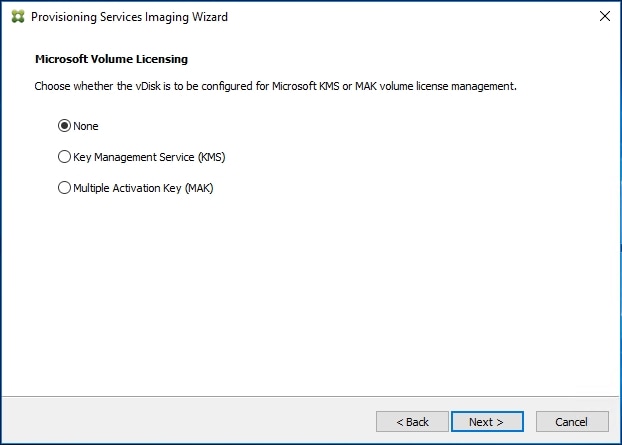
Step 14. Select Image entire boot disk on the Configure Image Volumes page.
Step 15. Click Next.
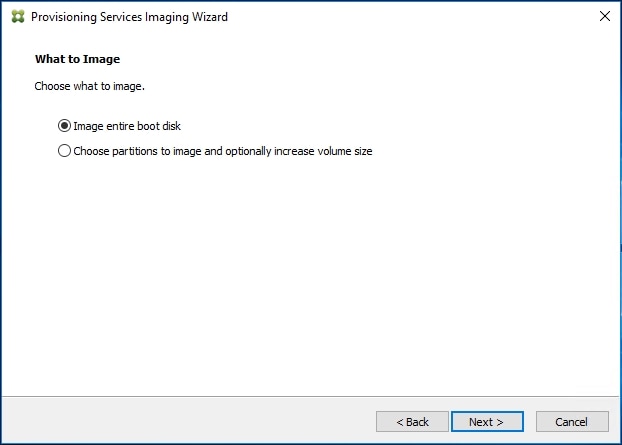
Step 16. Select Optimize for hard disk again for Provisioning Services before imaging on the Optimize Hard Disk for Provisioning Services.
Step 17. Click Next.
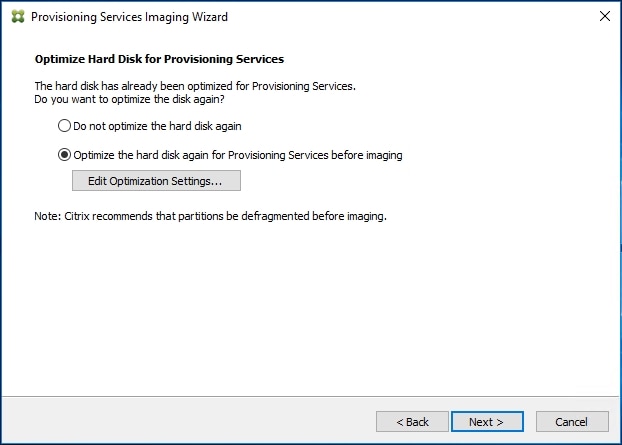
Step 18. Click Create on the Summary page.
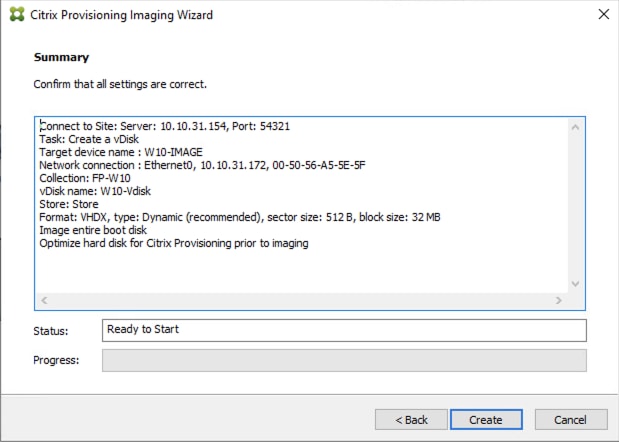
Step 19. Review the configuration and click Continue.
Step 20. When prompted, click No to shut down the machine.
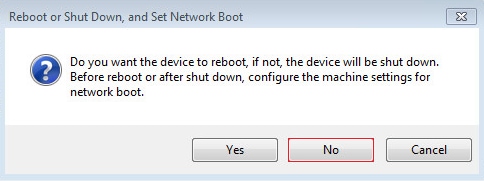
Step 21. Edit the VM options and under Boot Options, check the box for During the next boot, force entry into the EFI setup.
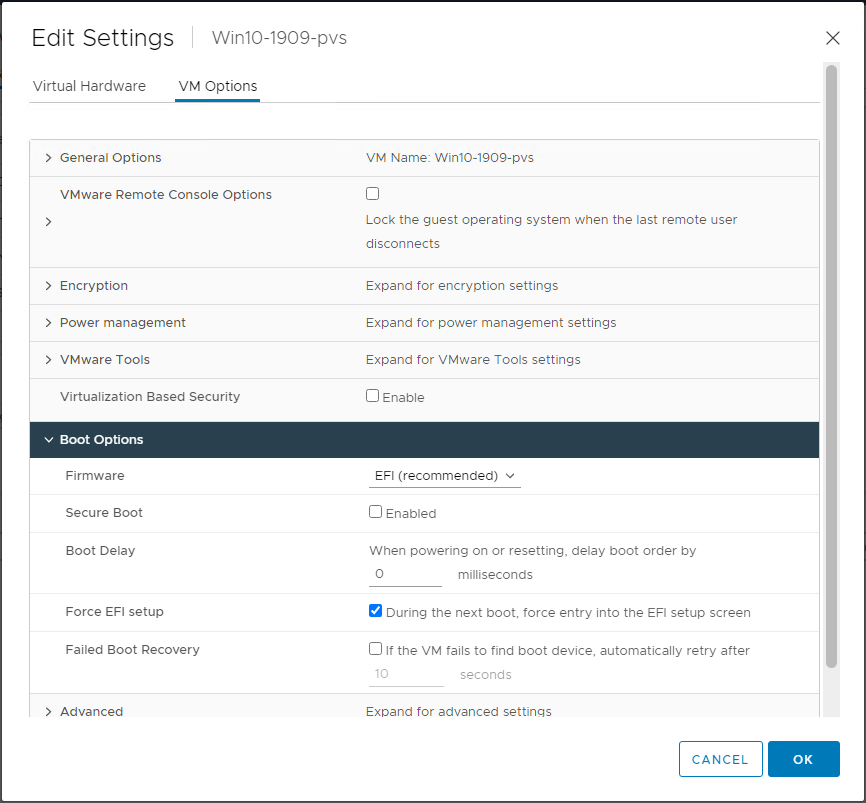
Step 22. Configure the VM settings for EFI network boot.
Step 23. Click Commit changes and exit.
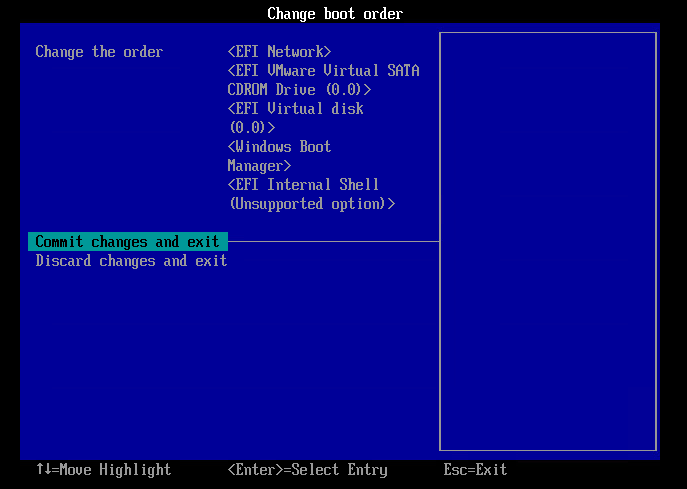
Step 24. After restarting the virtual machine, log into the master target. The PVS imaging process begins, copying the contents of the C: drive to the PVS vDisk located on the server.
Note: If prompted to Format disk, disregard the message, and allow Provisioning Imaging Wizard to finish.
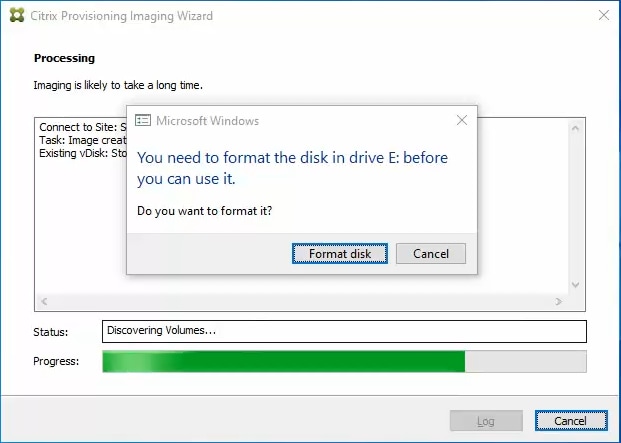
Step 25. A message is displayed when the conversion is complete, click Done.
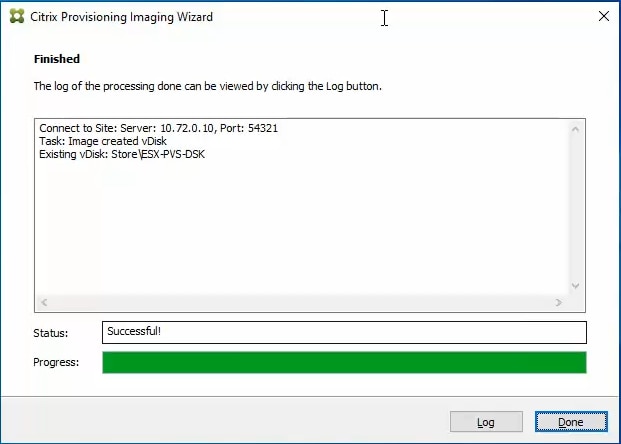
Step 26. Shutdown the virtual machine used as the VDI or RDS master target.
Step 27. Connect to the PVS server and validate that the vDisk image is available in the Store.
Step 28. Right-click the newly created vDisk and select Properties.
Step 29. On the vDisk Properties dialog, change Access mode to Standard Image (multi-device, read-only access).
Step 30. Set the Cache Type to Cache in device RAM with overflow on hard disk.
Step 31. Set Maximum RAM size (MBs): 256.
Step 32. Click OK.
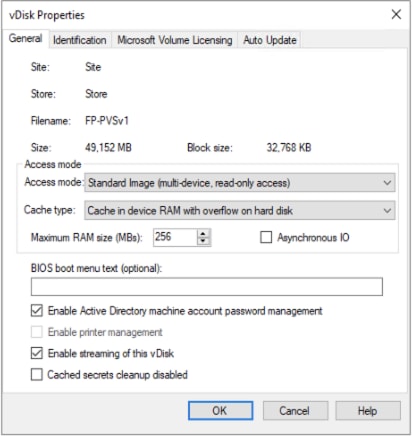
Provision Virtual Desktop Machines
Citrix Provisioning Services Citrix Virtual Desktop Setup Wizard
Procedure 1. Create PVS Streamed Virtual Desktop Machines
Step 1. Create a Master Target Virtual Machine.
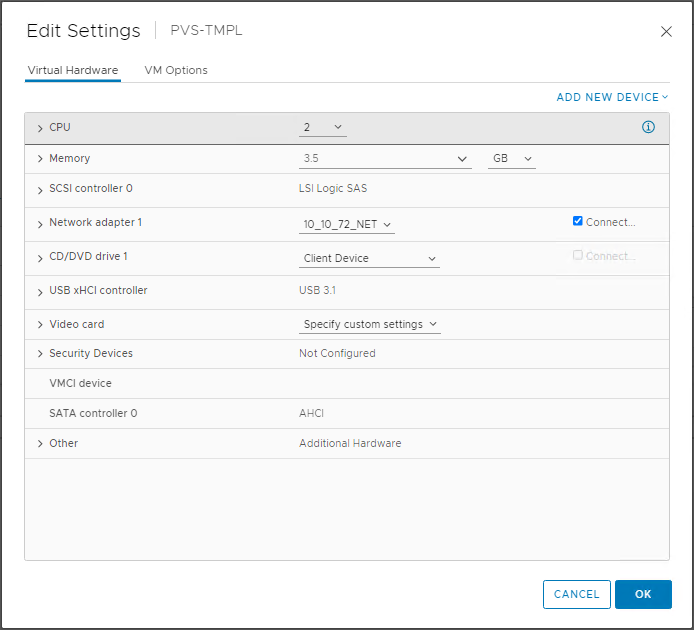
Step 2. Right-click and select Clone then select Clone to Template.
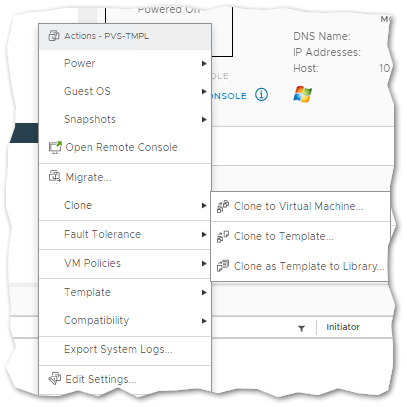
Step 3. Start the Citrix Virtual Apps and Desktops Setup Wizard from the Provisioning Services Console.
Step 4. Click Sites.
Step 5. Right-click the site.
Step 6. Select Citrix Virtual Desktop Setup Wizard… .
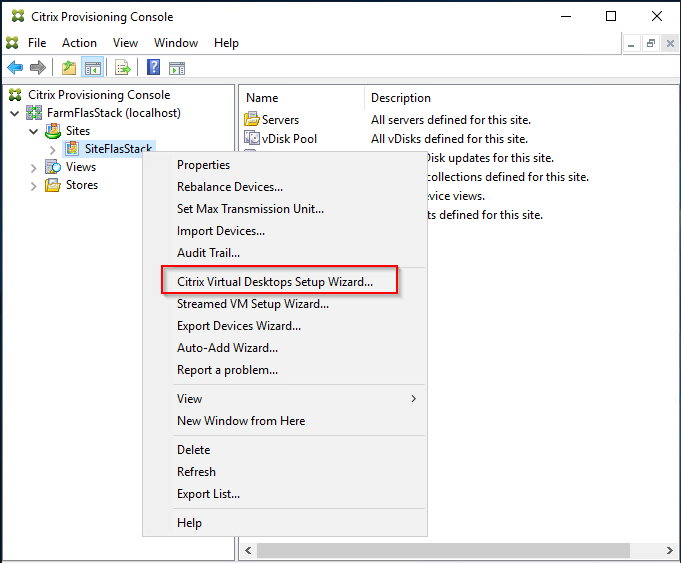
Step 7. Click Next.
Step 8. Enter the address of the Citrix Virtual Desktop Controller that will be used for the wizard operations.
Step 9. Click Next.
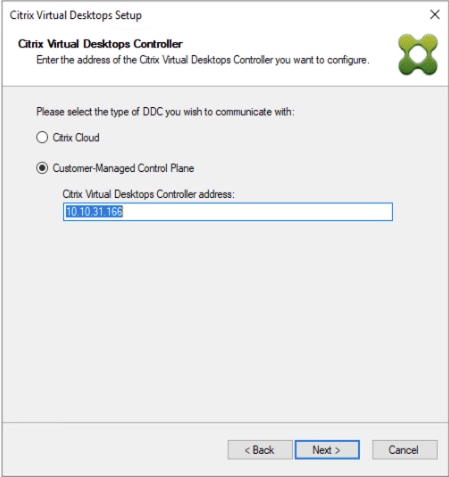
Step 10. Select the Host Resources that will be used for the wizard operations.
Step 11. Click Next.
Step 12. Provide Citrix Virtual Desktop Controller credentials.
Step 13. Click OK.
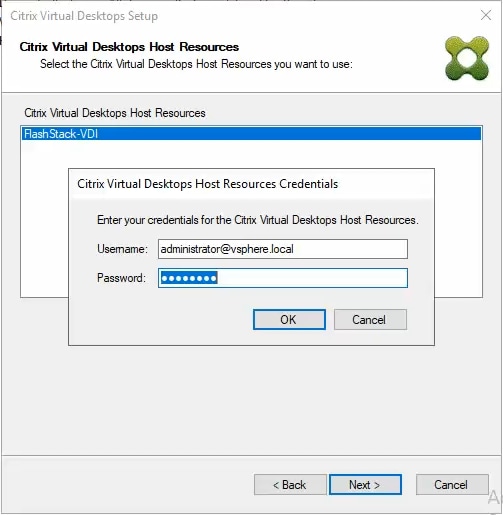
Step 14. Select the template previously created.
Step 15. Click Next.
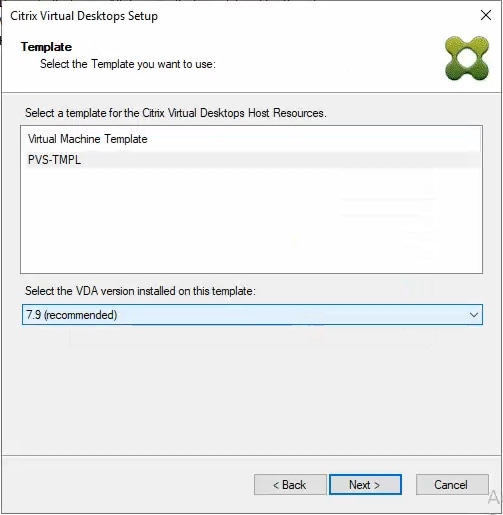
Step 16. Select the virtual disk (vDisk) that will be used to stream the provisioned virtual machines.
Step 17. Click Next.
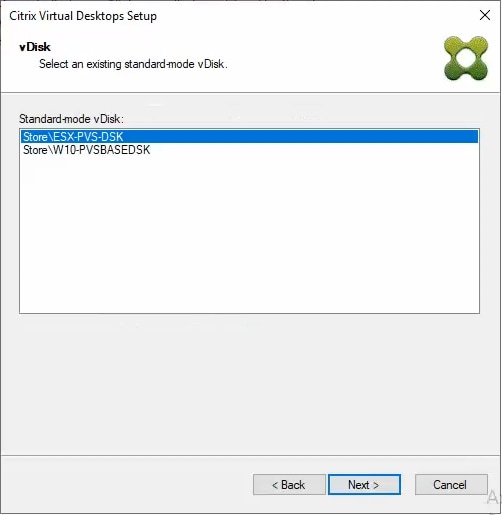
Step 18. Select Create new catalog.
Step 19. Provide a Catalog name.
Step 20. Click Next.
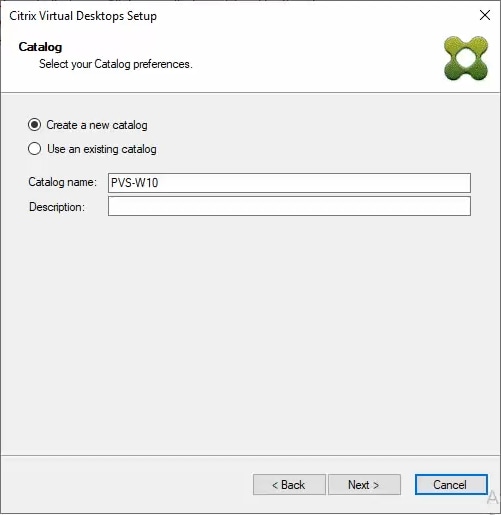
Step 21. Select Single-session OS for Machine catalog Operating System.
Step 22. Click Next.
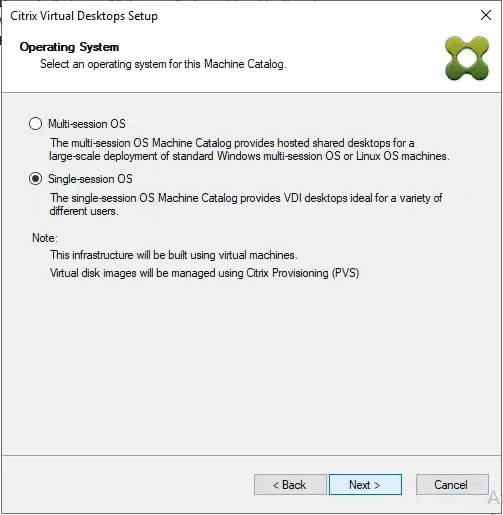
Step 23. Select A random, pooled virtual desktop each time.
Step 24. Click Next.
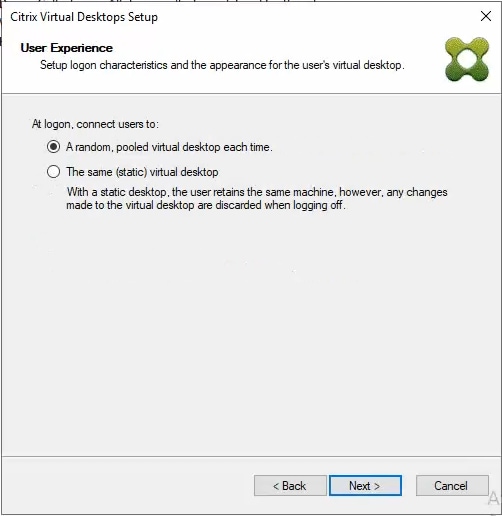
Step 25. On the Virtual machines dialog, specify the following:
● The number of virtual machines to create.
Note: It is recommended to create 200 or less per provisioning run. Create a single virtual machine at first to verify the procedure.
● 2 for Number of vCPUs for the virtual machine
● 3584 MB for the amount of memory for the virtual machine
● 6GB for the Local write cache disk.
Step 26. Click Next.
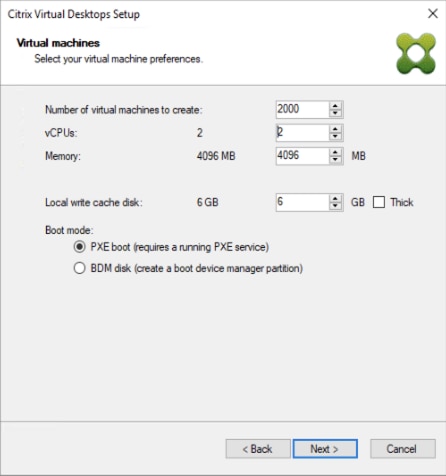
Step 27. Select the Create new accounts.
Step 28. Click Next.
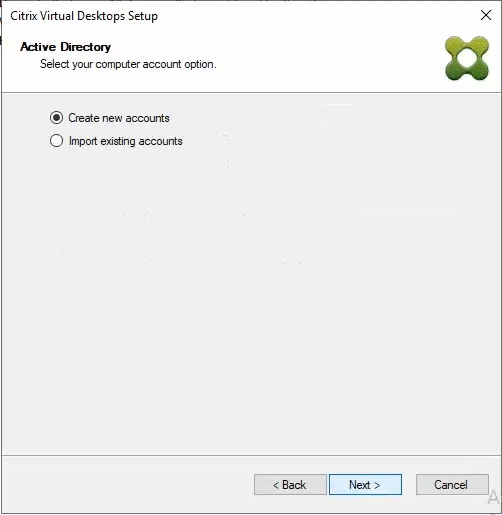
Step 29. Specify the Active Directory Accounts and Location. This is where the wizard should create computer accounts.
Step 30. Provide the Account naming scheme. An example name is shown in the text box below the naming scheme selection location.
Step 31. Click Next.
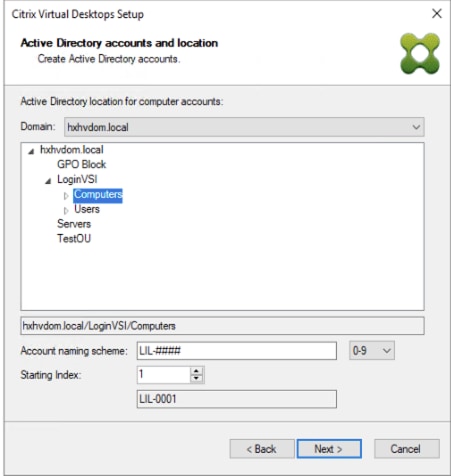
Step 32. Verify the information on the Summary screen.
Step 33. Click Finish to begin the virtual machine creation.
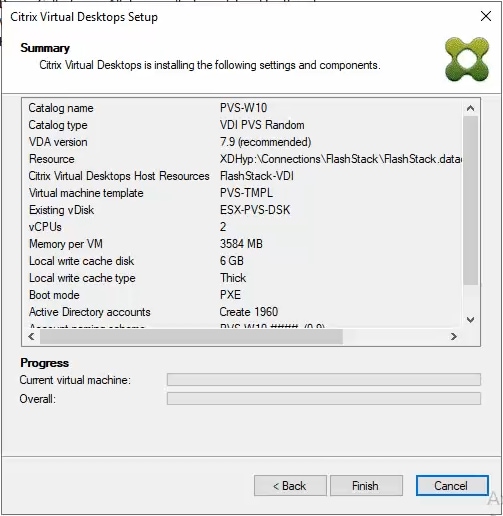
Step 34. When the wizard is done provisioning the virtual machines, click Done.
Step 35. When the wizard is done provisioning the virtual machines, verify the Machine Catalog on the Citrix Virtual Apps and Desktops Controller:
● Connect to a Citrix Virtual Apps and Desktops server and launch Citrix Studio.
● Select Machine Catalogs in the Studio navigation pane.
● Select a machine catalog.
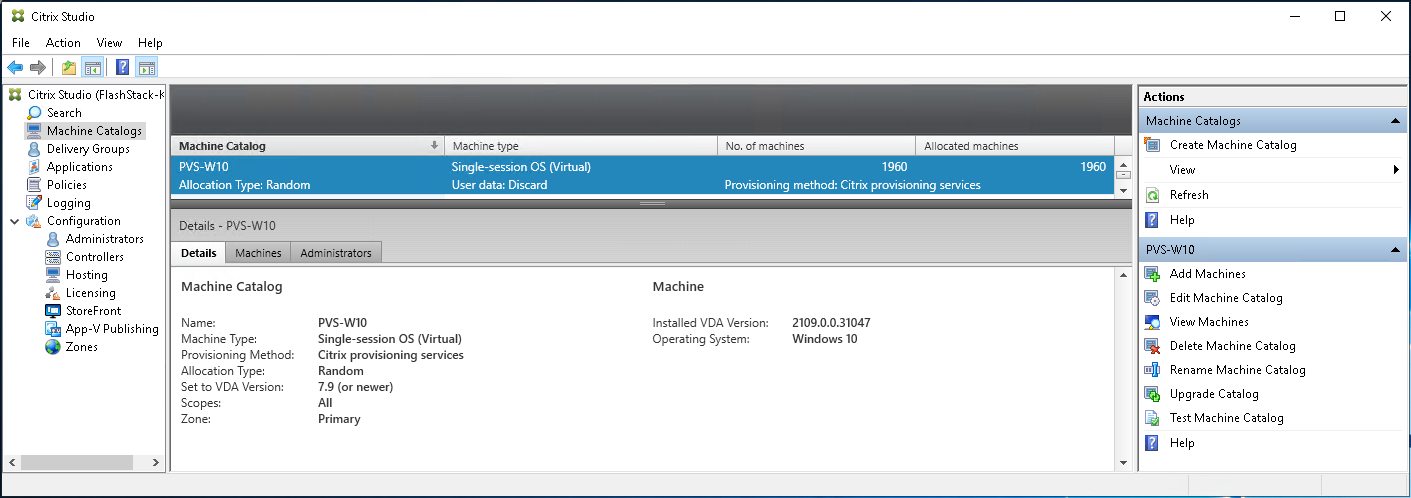
Citrix Virtual Desktop Setup using Machine Creation Services (MCS)
Procedure 1. Citrix Machine Creation Services
Step 1. Connect to a Citrix Virtual Apps and Desktops server and launch Citrix Studio.
Step 2. Select Create Machine Catalog from the Actions pane.
Step 3. Click Next.
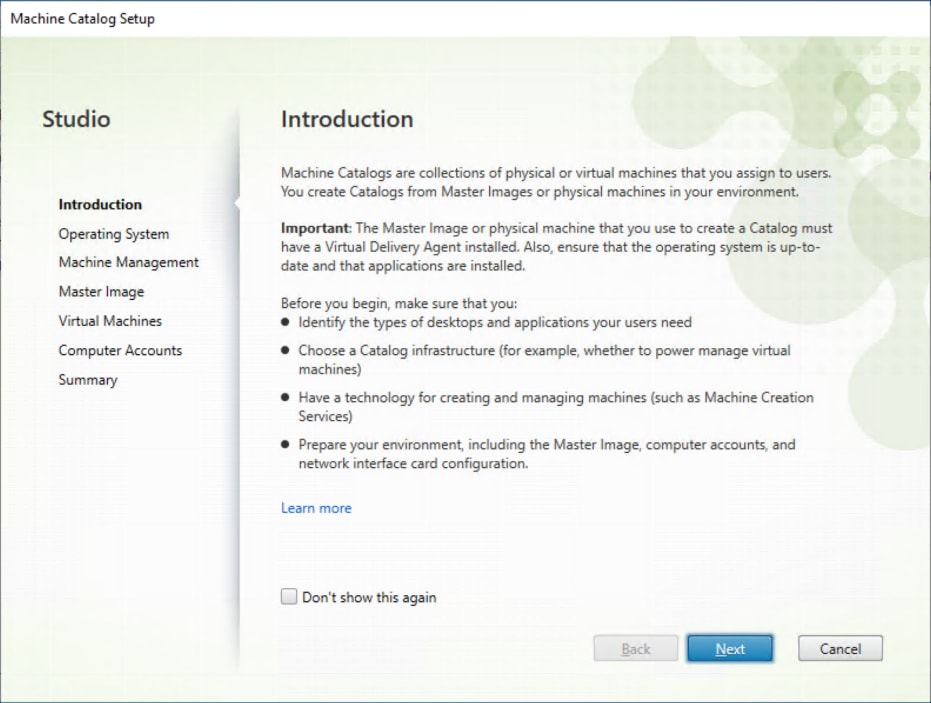
Step 4. Select Single-session OS.
Step 5. Click Next.
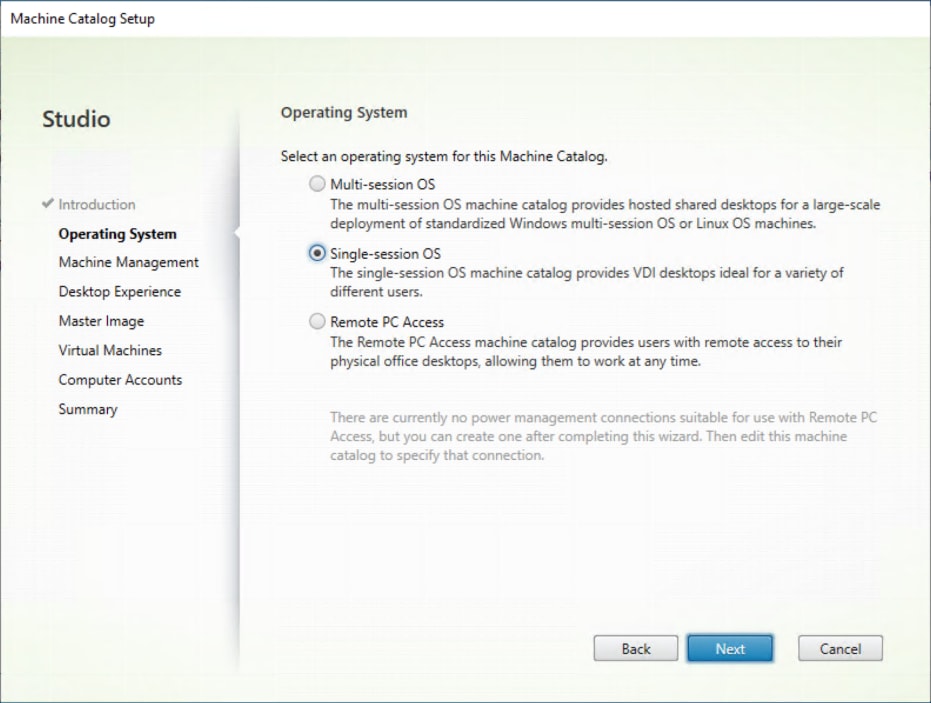
Step 6. Select Multi-session OS when using Windows Server 2022 desktops.
Step 7. Select the appropriate machine management.
Step 8. Click Next.
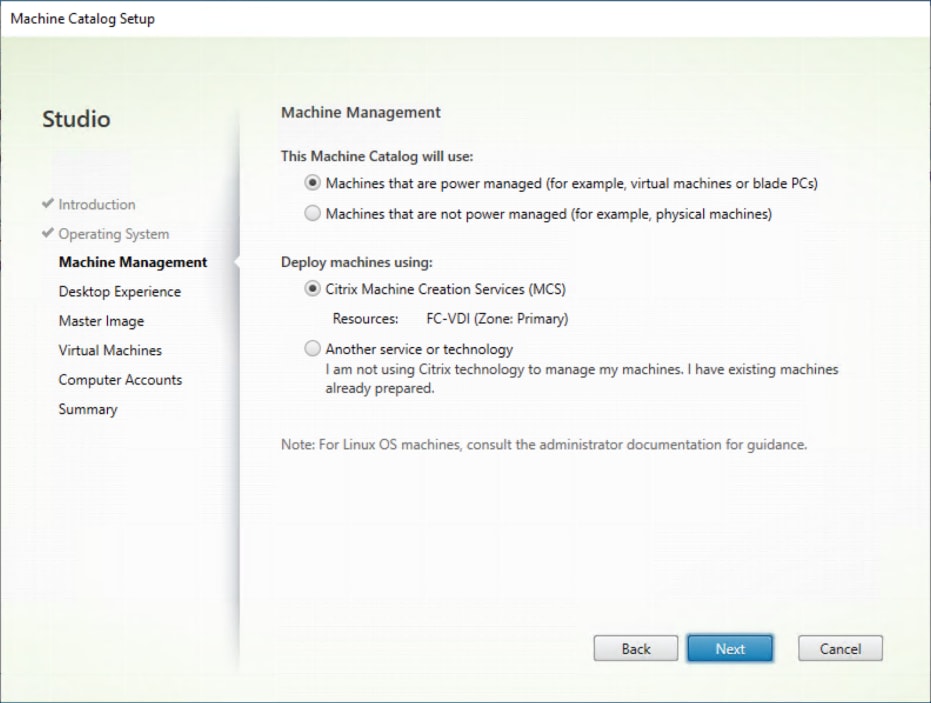
Step 9. For Desktop Experience, select I want users to connect to a new (random) desktop each time they log on.
Step 10. Click Next.
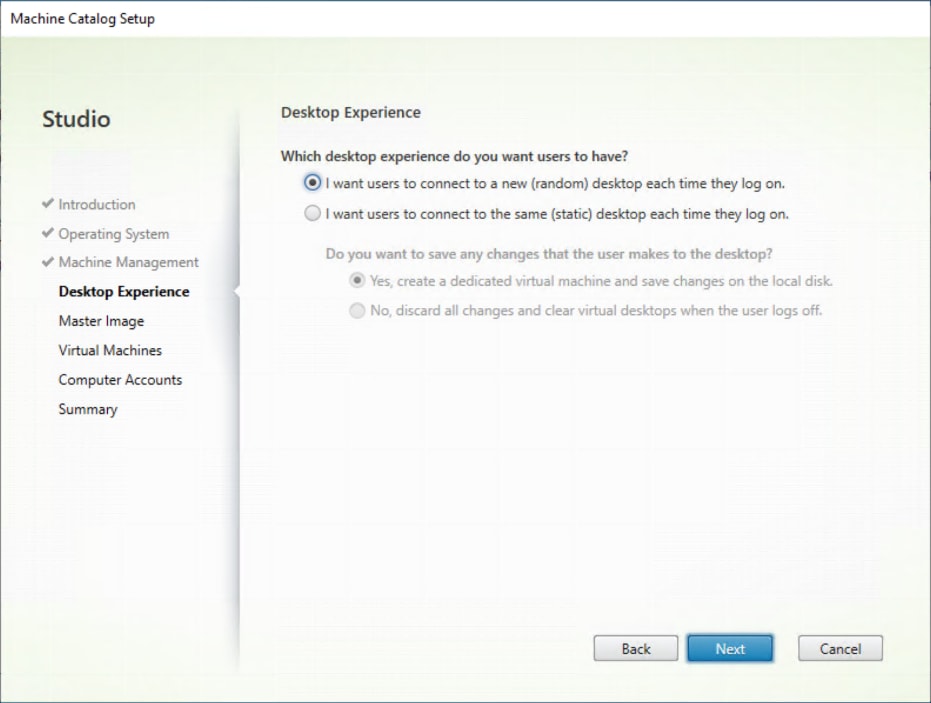
Step 11. Select a Virtual Machine to be used for Catalog Master Image.
Step 12. Click Next.
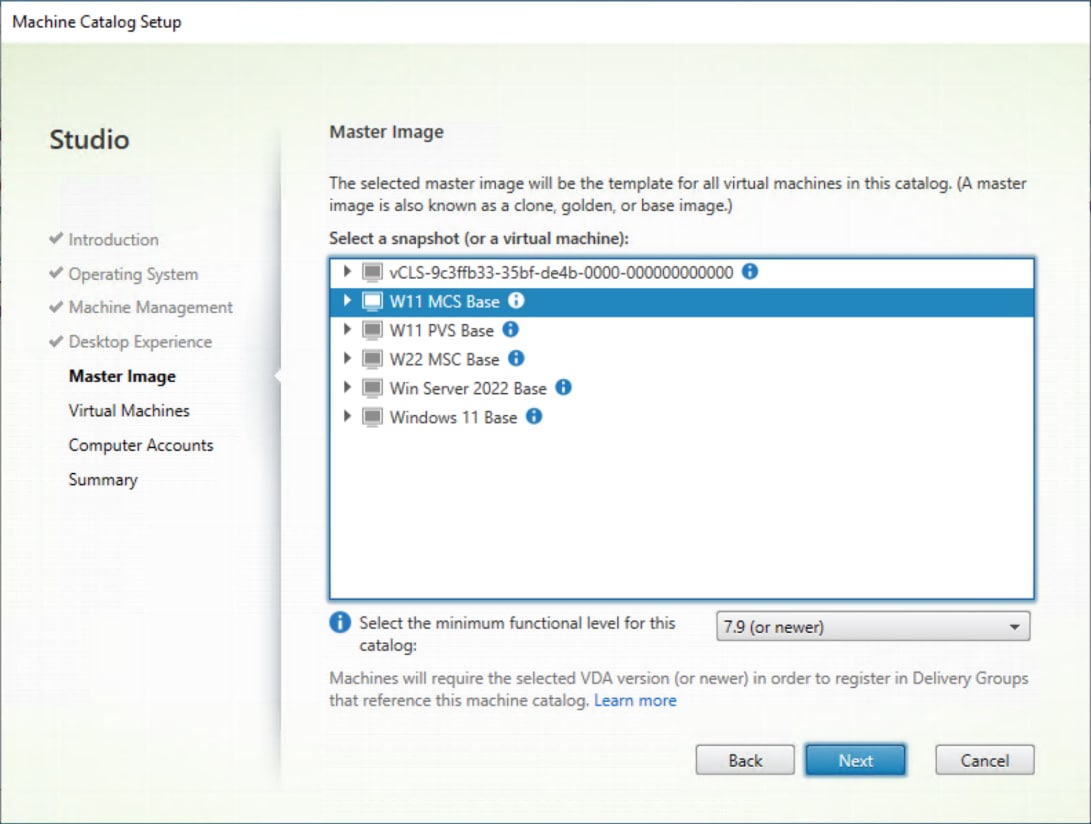
Step 13. Specify the number of desktops to create and machine configuration.
Step 14. Set amount of memory (MB) to be used by virtual desktops.
Step 15. Select Full Copy for machine copy mode.
Step 16. Click Next.
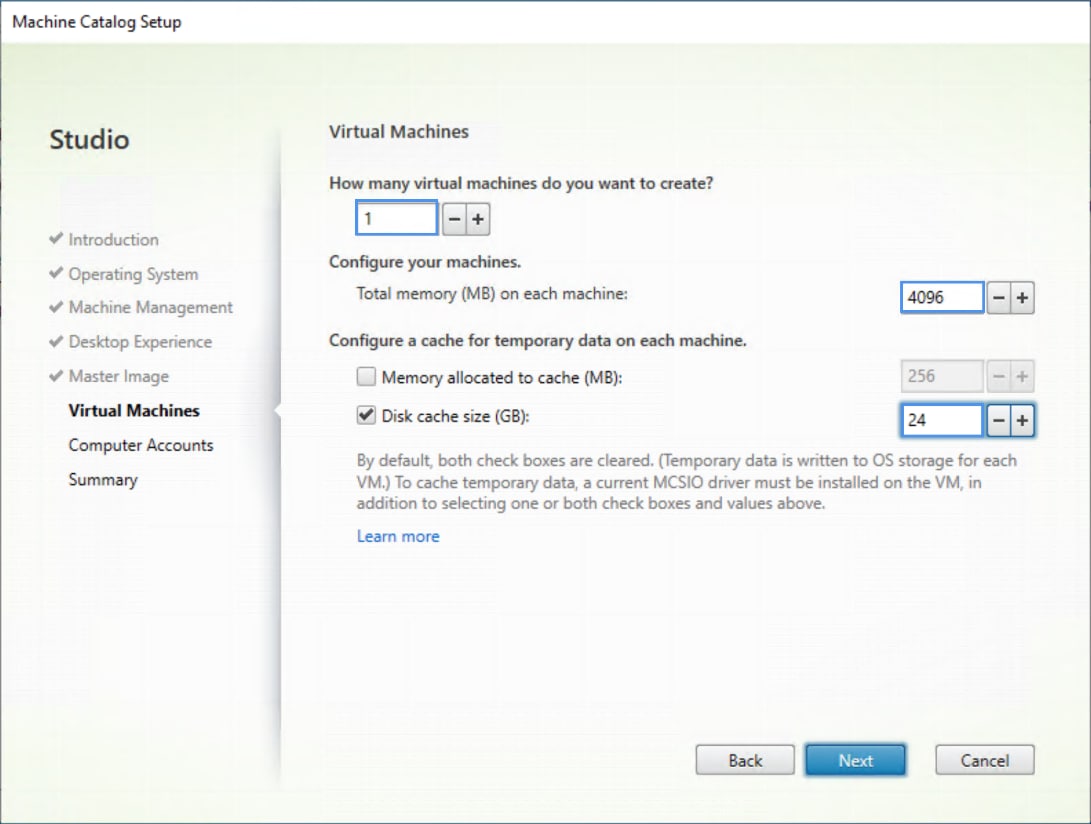
Step 17. Specify the AD account naming scheme and OU where accounts will be created.
Step 18. Click Next.
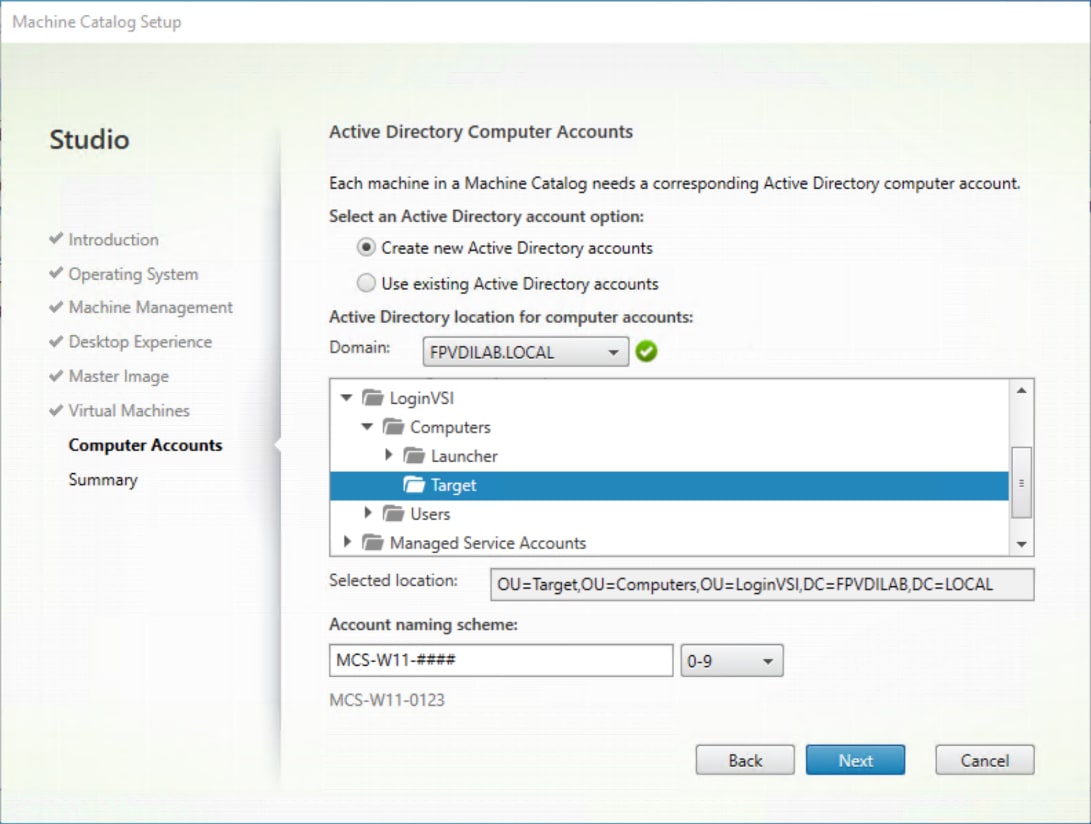
Step 19. On the Summary page specify Catalog name and click Finish to start the deployment.
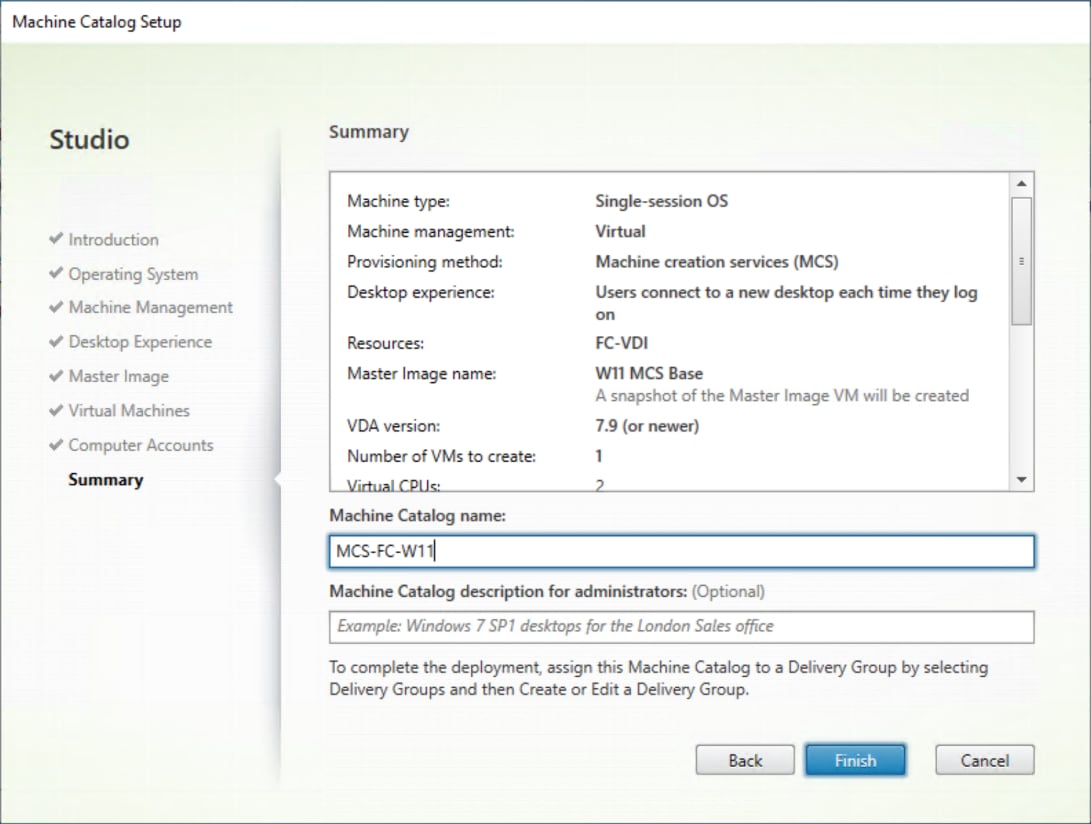
Procedure 2. Create Delivery Groups
Delivery Groups are collections of machines that control access to desktops and applications. With Delivery Groups, you can specify which users and groups can access which desktops and applications.
Note: The following steps describe the procedure to create a Delivery Group for persistent VDI desktops. When you have completed these steps, repeat the procedure to a Delivery Group for RDS desktops.
Step 1. Connect to a Citrix Virtual Apps and Desktops server and launch Citrix Studio.
Step 2. Right-click Deliver Group and select Create Delivery Group from the Actions pane.
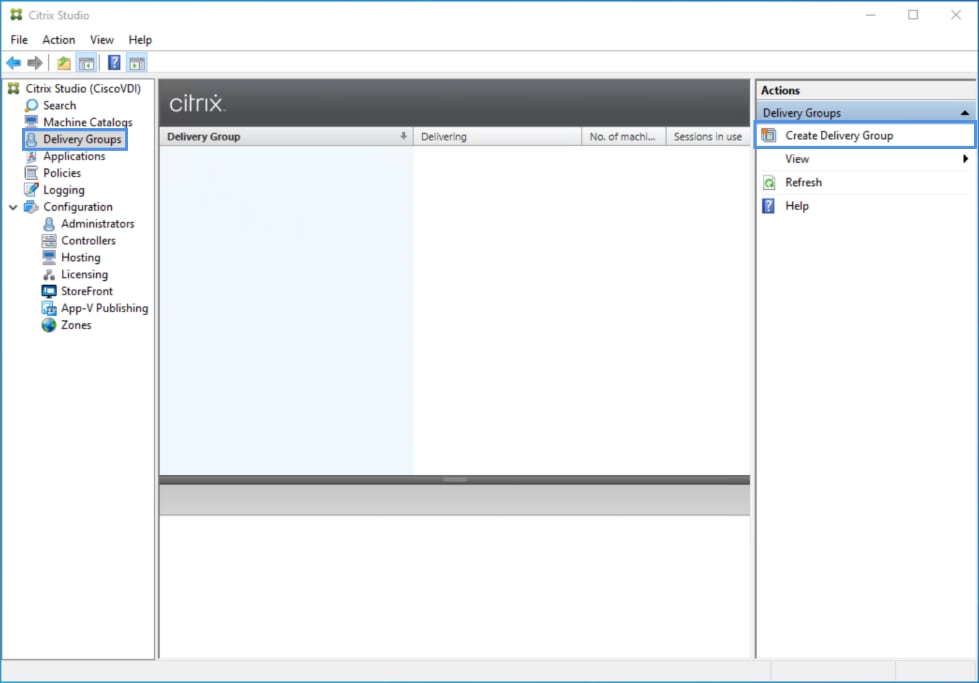
Step 3. Click Next.
Step 4. Specify the Machine Catalog and increment the number of machines to add.
Step 5. Click Next.
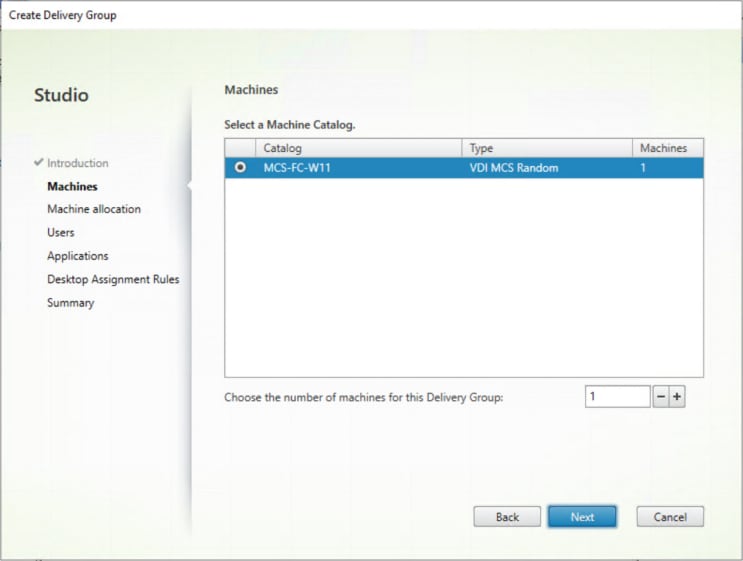
Step 6. To make the Delivery Group accessible, you must add users. Select Allow any authenticated users to use this Delivery Group.
Note: User assignment can be updated any time after Delivery group creation by accessing Delivery group properties in Desktop Studio.
Step 7. Click Next.
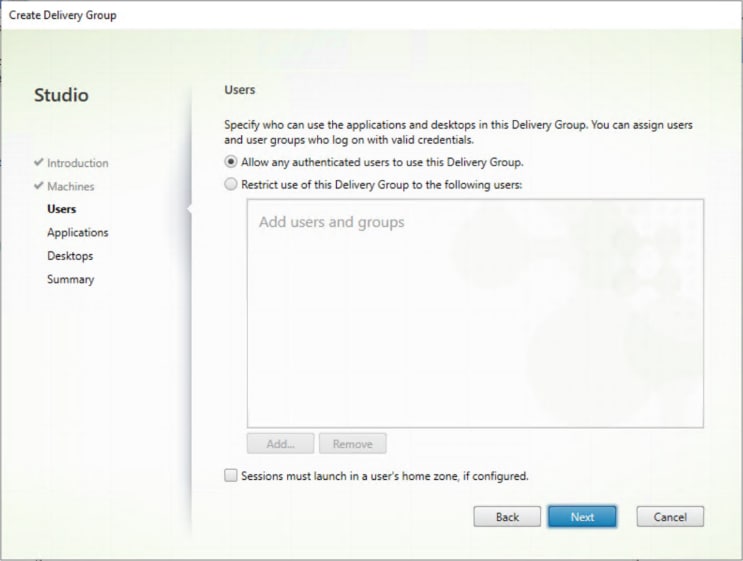
Step 8. Click Next (no applications are used in this design).
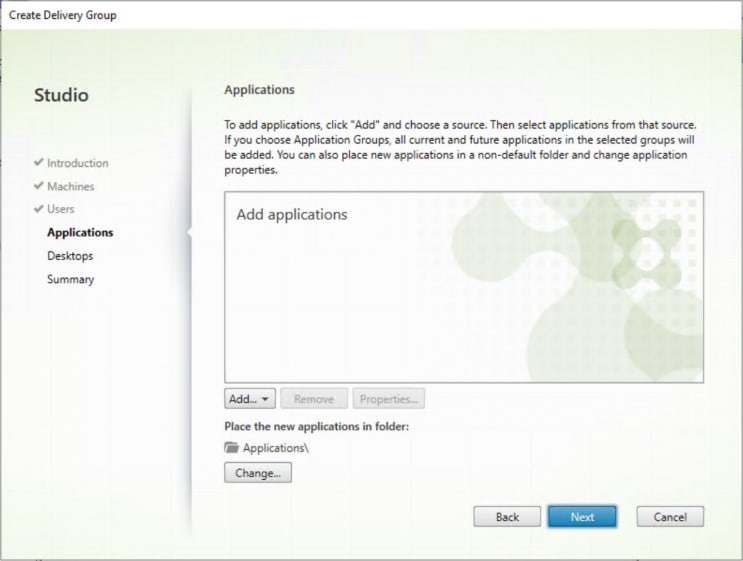
Step 9. Select Add….
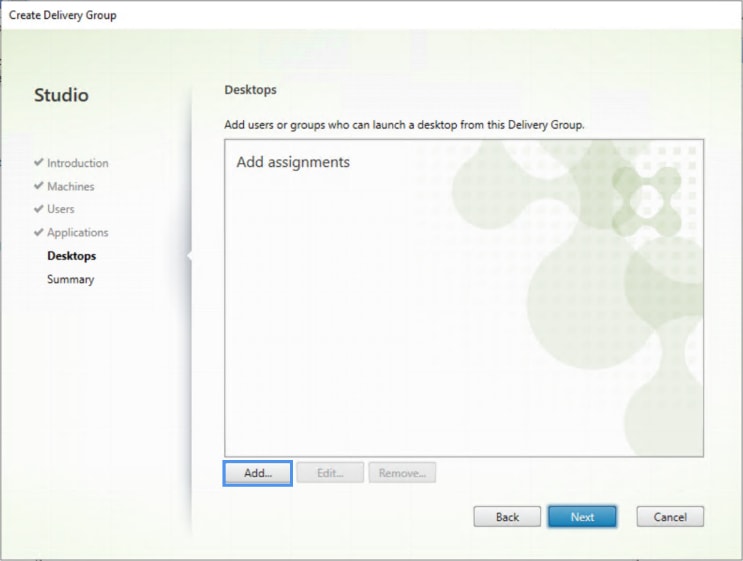
Step 10. Select Allow everyone with access to this Delivery Group to have a desktop assigned. Click Next.
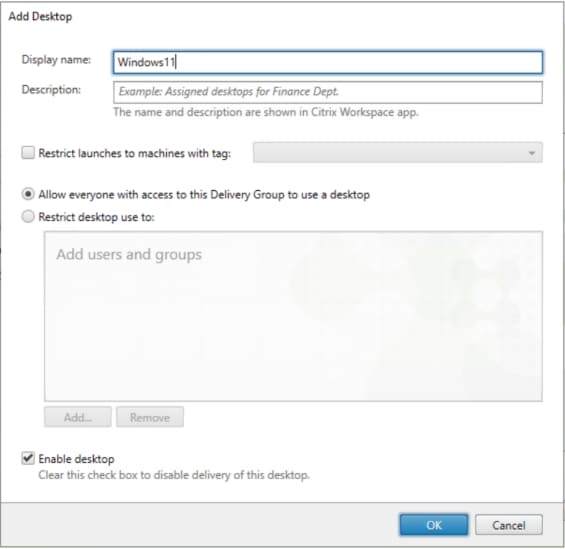
Step 11. Click Next.
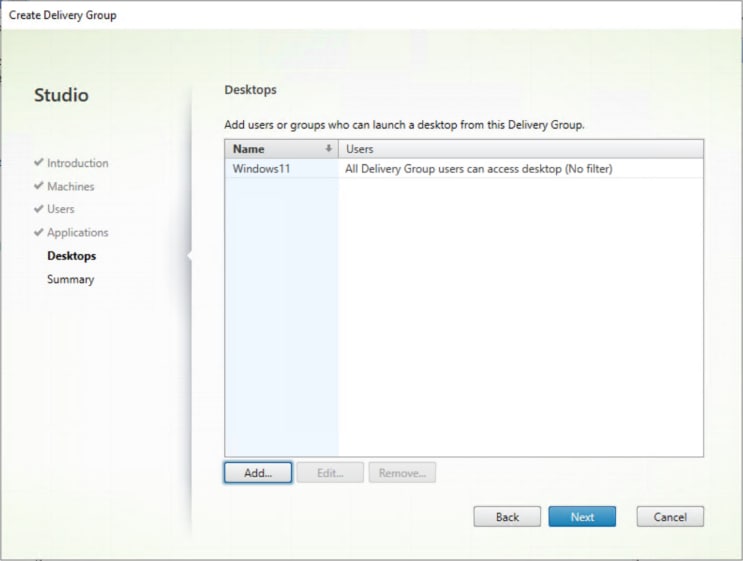
Step 12. On the Summary dialog, review the configuration. Enter a Delivery Group name and a Description (Optional).
Step 13. Click Finish.
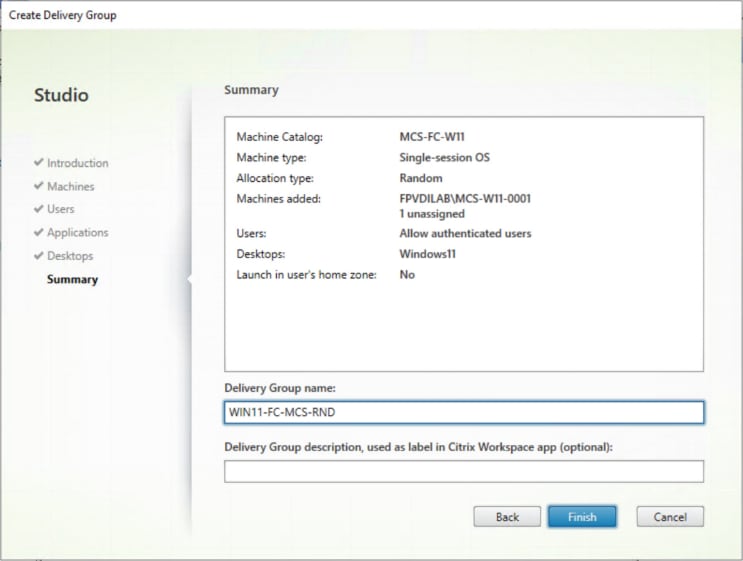
Citrix Studio lists the created Delivery Groups as well as the type, number of machines created, sessions, and applications for each group in the Delivery Groups tab.
Step 14. From the drop-down list, select Turn on Maintenance Mode.
Citrix Virtual Apps and Desktops Policies and Profile Management
Policies and profiles allow the Citrix Virtual Apps and Desktops environment to be easily and efficiently customized.
Configure Citrix Virtual Apps and Desktops Policies
Citrix Virtual Apps and Desktops policies control user access and session environments, and are the most efficient method of controlling connection, security, and bandwidth settings. You can create policies for specific groups of users, devices, or connection types with each policy. Policies can contain multiple settings and are typically defined through Citrix Studio.
Note: The Windows Group Policy Management Console can also be used if the network environment includes Microsoft Active Directory and permissions are set for managing Group Policy Objects).
Figure 33 and Figure 34 shows the policies for Login VSI testing in this CVD. This policy was created from the Citrix provided High Server Scalability Policy template.
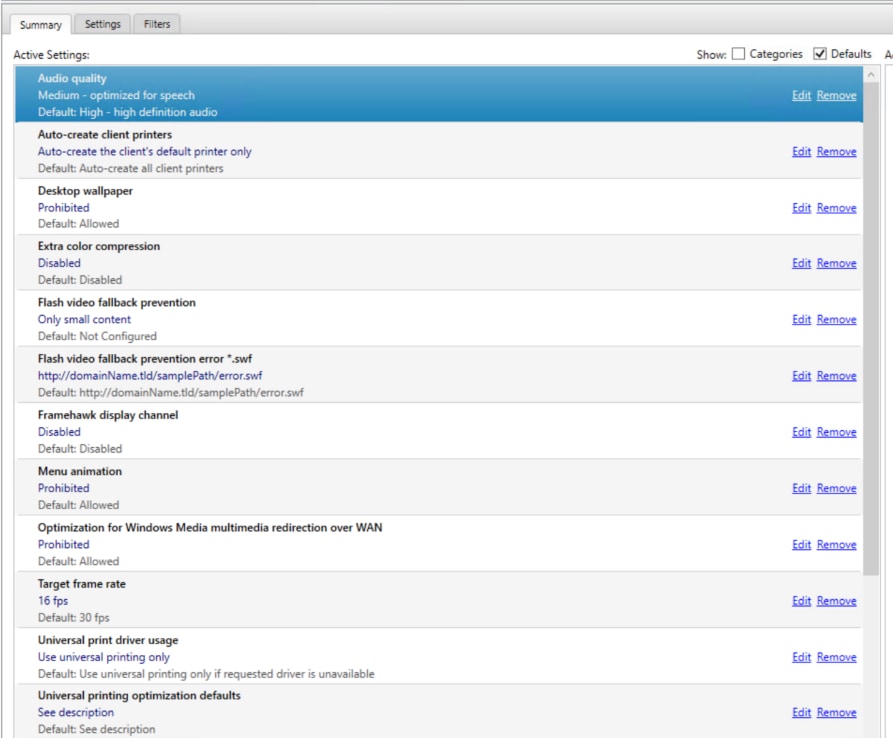
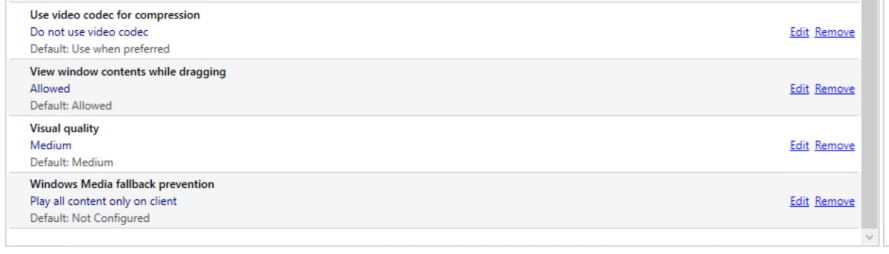
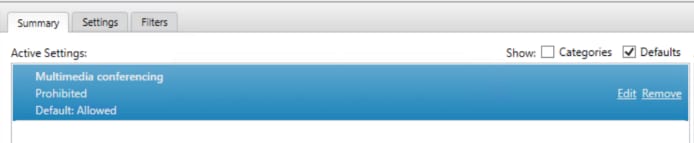
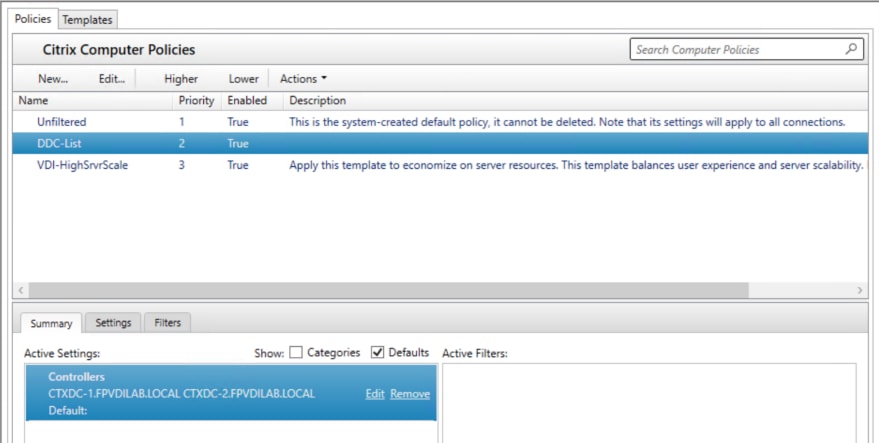
FSLogix for Citrix Virtual Apps and Desktops Profile Management
FSLogix for user profiles allows the Citrix Virtual Apps and Desktops environment to be easily and efficiently customized. Two CIFS Logical Interfaces (LIFs) were created on separate storage processor nodes and ports on the NetApp A50, each assigned a unique IP address. Correspondingly, two distinct CIFS shares were configured, each hosted on different volumes distributed across the separate storage processors. To achieve load balancing, DNS round-robin was implemented by creating two DNS A records with the same CIFS server name pointing to the IP addresses of both LIFs. Additionally, two FSLogix Group Policy Objects (GPOs) were deployed, each specifying the UNC path to one of the CIFS shares, effectively splitting user access evenly between the two shares at a 50/50 ratio.
This configuration ensures balanced SMB client connections across the storage processors and separates user profiles between the two shares for optimized performance and management in the FlexPod environment.
Procedure 1. Configure FSLogix for Citrix Virtual Apps and Desktops Profiles Profile Container
Profile Container is a full remote profile solution for non-persistent environments. Profile Container redirects the entire user profile to a remote location. Profile Container configuration defines how and where the profile is redirected.
Note: Profile Container is inclusive of the benefits found in Office Container.
Step 1. Verify that you meet all entitlement and configuration requirements.
Step 2. Download and install FSLogix Software
Step 3. Consider the storage and network requirements for your users' profiles (in this CVD, we used the Netapp A50 to store the FSLogix Profile disks).
Step 4. Verify that your users have appropriate storage permissions where profiles will be placed.
Step 5. Profile Container is installed and configured after stopping use of other solutions used to manage remote profiles.
Step 6. Exclude the VHD(X) files for Profile Containers from Anti-Virus (AV) scanning.
Procedure 2. Configure FSLogix Profile Management
Step 1. When the FSLogix software is downloaded, copy the fslogix.admx and fslogix.adml to the PolicyDefinitions folder in your domain to manage the settings with Group Policy.
Step 2. On your VDI master image, install the FSLogix agent FSLogixAppsSetup and accept all the defaults.
Step 3. Create a Group Policy object and link it to the Organizational Unit the VDI computer accounts.
Step 4. Right-click the FSLogix GPO policy.
Step 5. Enable FSLogix Profile Management.
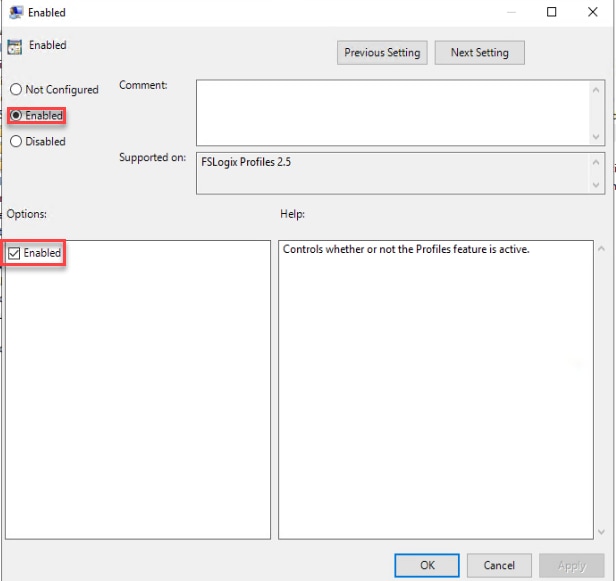
Step 6. Select Profile Type.
Note: In this solution, we used Read-Write profiles.
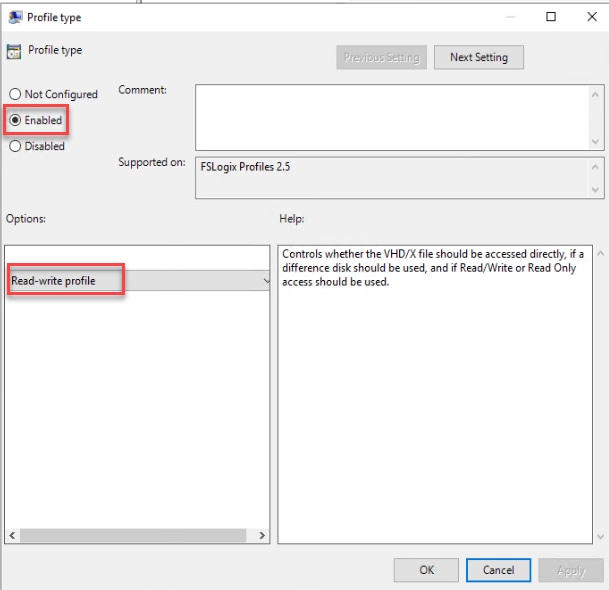
Step 7. Enter the location of the Profile location (our solution used a CIFS share on the NetApp Array).
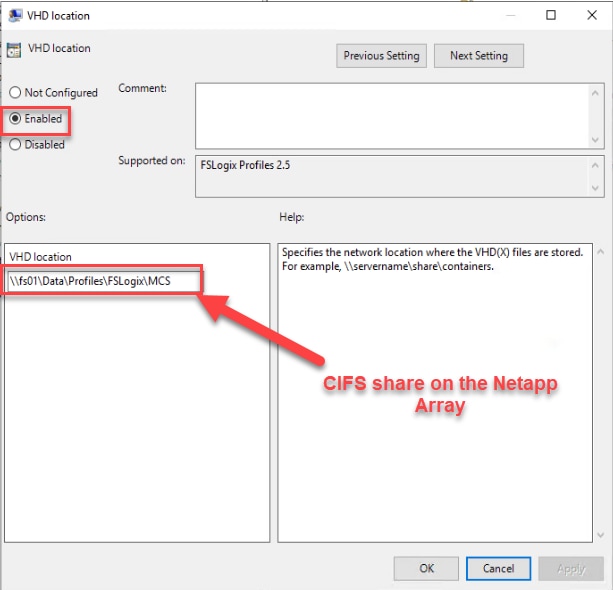
Note: We recommend using the Dynamic VHDX setting.
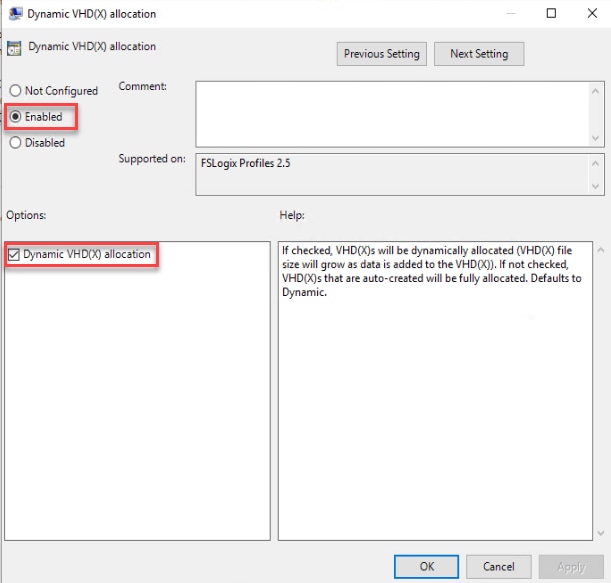
Note: VHDX is recommended over VHD.
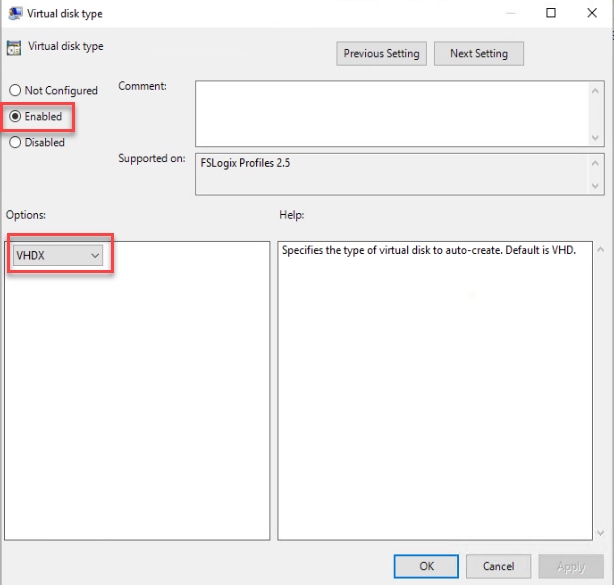
Note: We enabled the Swap directory name components setting for an easier administration, but it is not necessary for improved performance.
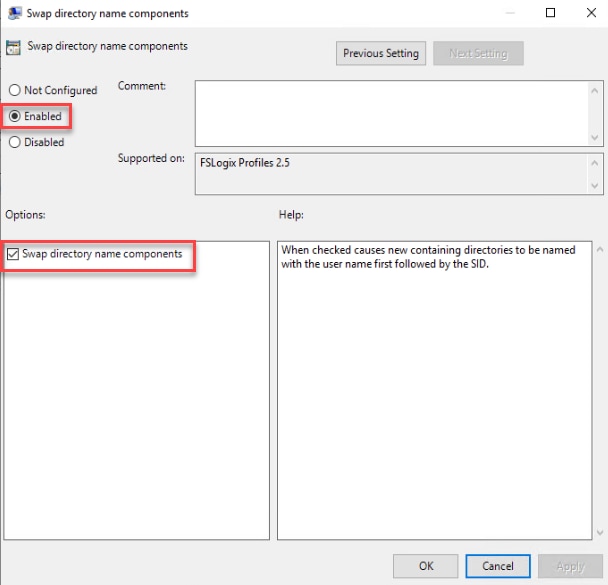
Tech tip: FSLogix is an outstanding method of controlling the user experience and profile data in a VDI environment. There are many helpful settings and configurations for VDI with FSLogix that were not used in this solution.
This chapter contains the following:
● Cisco UCS Test Configuration for Single Compute Node Scalability
● Testing Methodology and Success Criteria
● Single-Server Recommended Maximum Workload
The test configuration includes a single Cisco UCS X9508 chassis housing up to eight Cisco UCS X215c M8 compute nodes, Cisco UCS 6536 Fabric Interconnects, Cisco Nexus 93180YC-FX3 switches, Cisco MDS 9132T switches for SAN connectivity, and NetApp AFF A50 all-flash storage arrays configured as single chassis HA pair. The configuration validates desktop user workloads using Citrix Virtual Apps and Desktops 7 LTSR.
This single chassis FlexPod configuration with NetApp AFF series provides a high-performance, resilient, and scalable platform suitable for enterprise workloads, combining Cisco UCS compute, Nexus and MDS networking, and NetApp all-flash storage in a converged infrastructure stack and ensures predictable performance and scalability for enterprise VDI deployments.
Note: In this solution, we tested a single Cisco UCS X215c M8 Compute Node Server to validate against the performance of one Compute Node and eight Cisco UCS X215c M8 Compute Node Servers in a single chassis to illustrate linear scalability for each workload use case studied.
Cisco UCS Test Configuration for Single Compute Node Scalability
This test case validates Recommended Maximum Workload per host server using Citrix Virtual Apps and Desktops 7 LTSR with 384 RDS sessions, 230 VDI Non-Persistent sessions, and 230 VDI Persistent sessions.
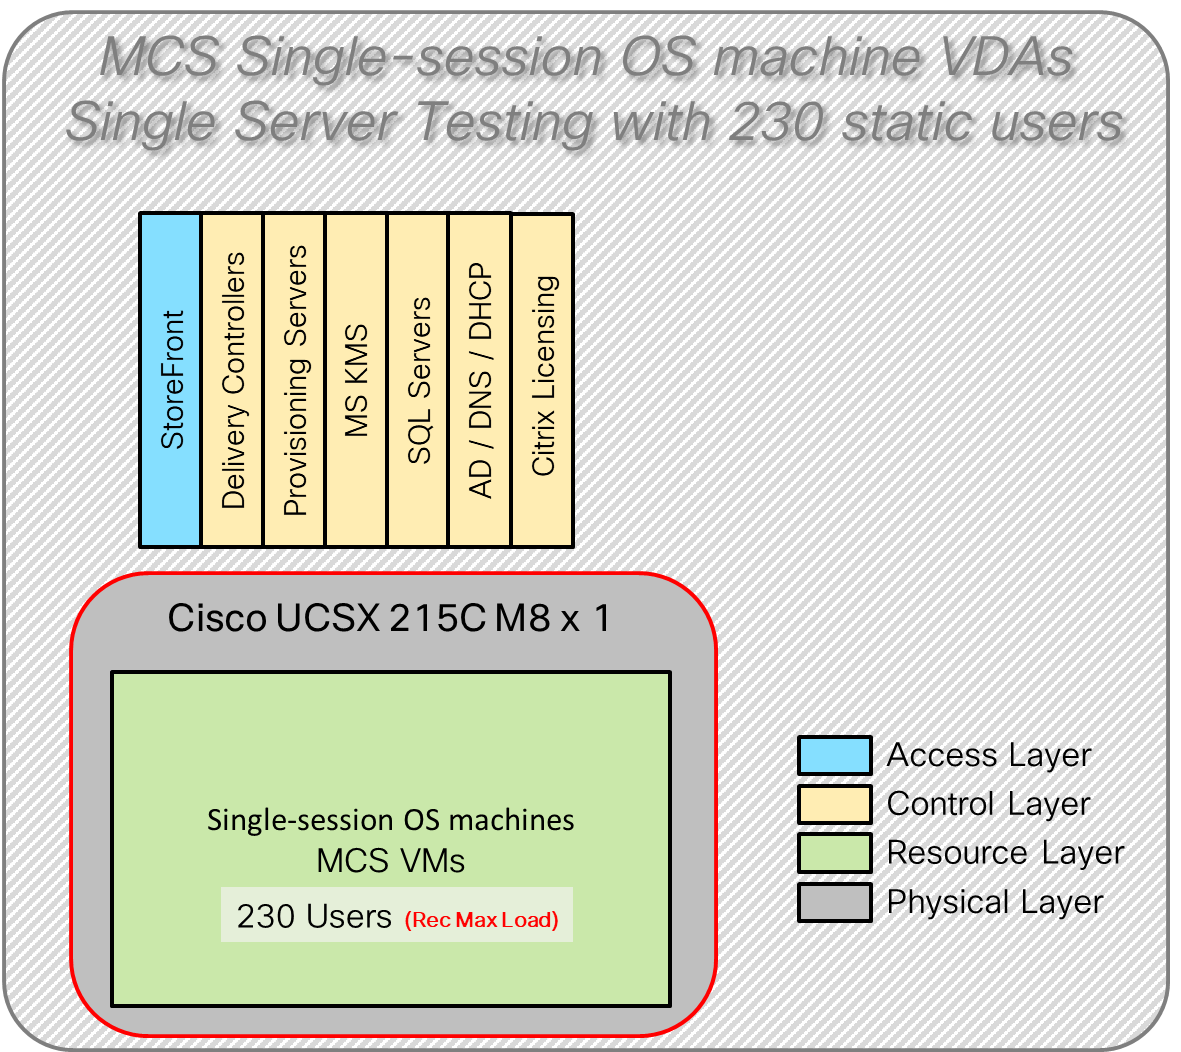
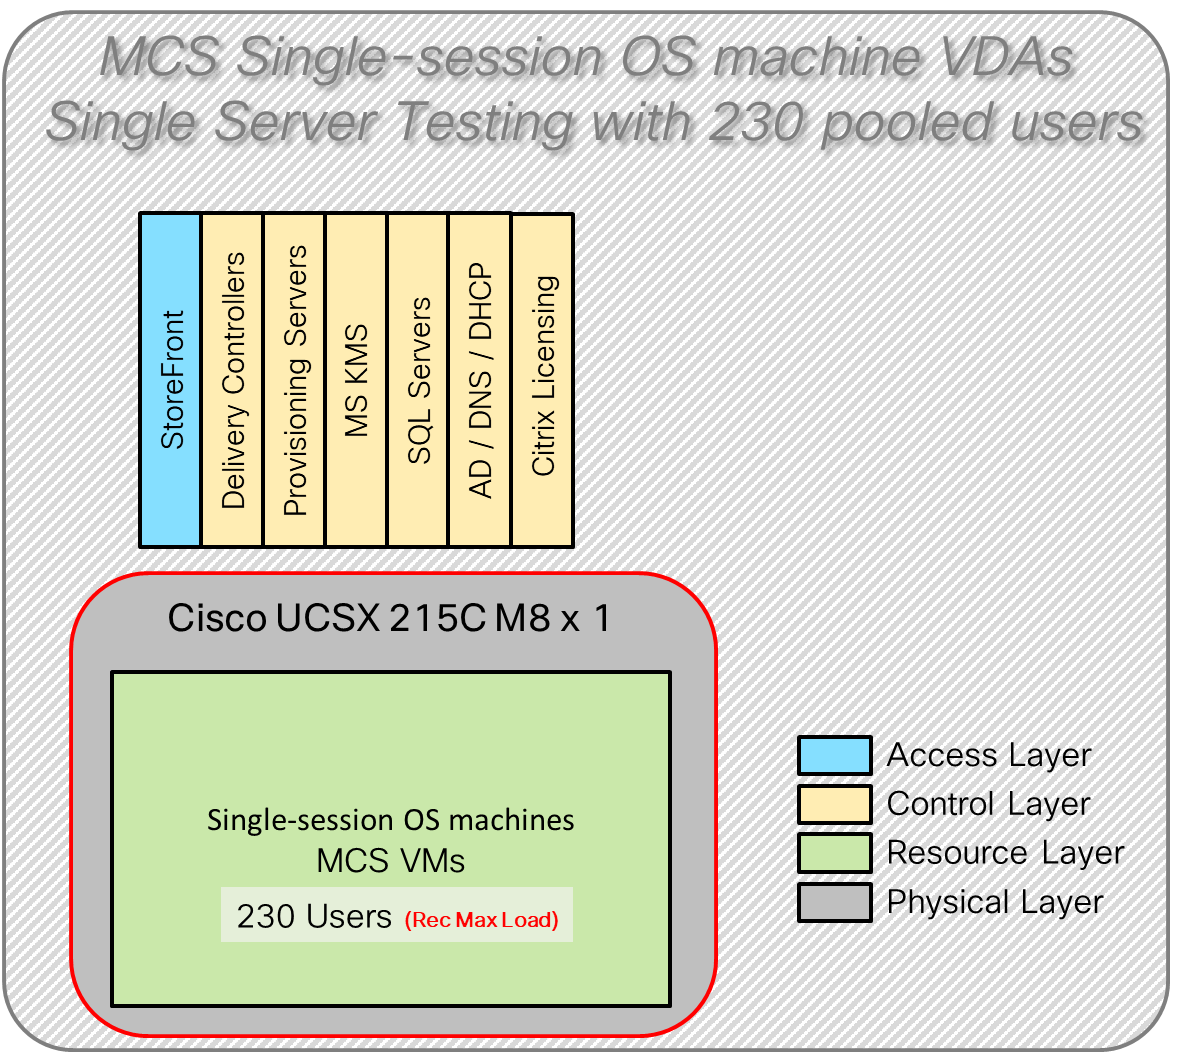
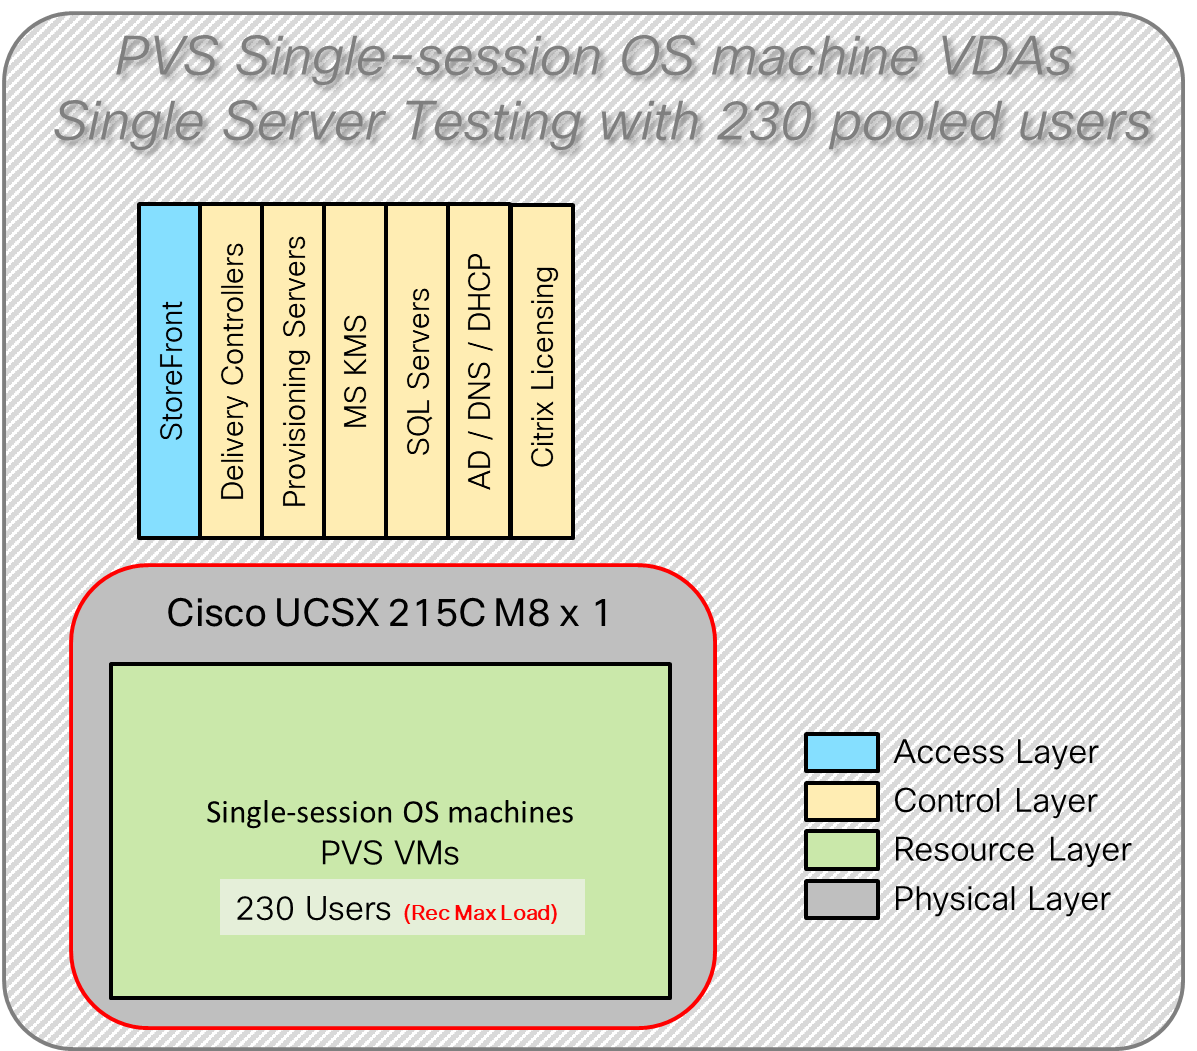
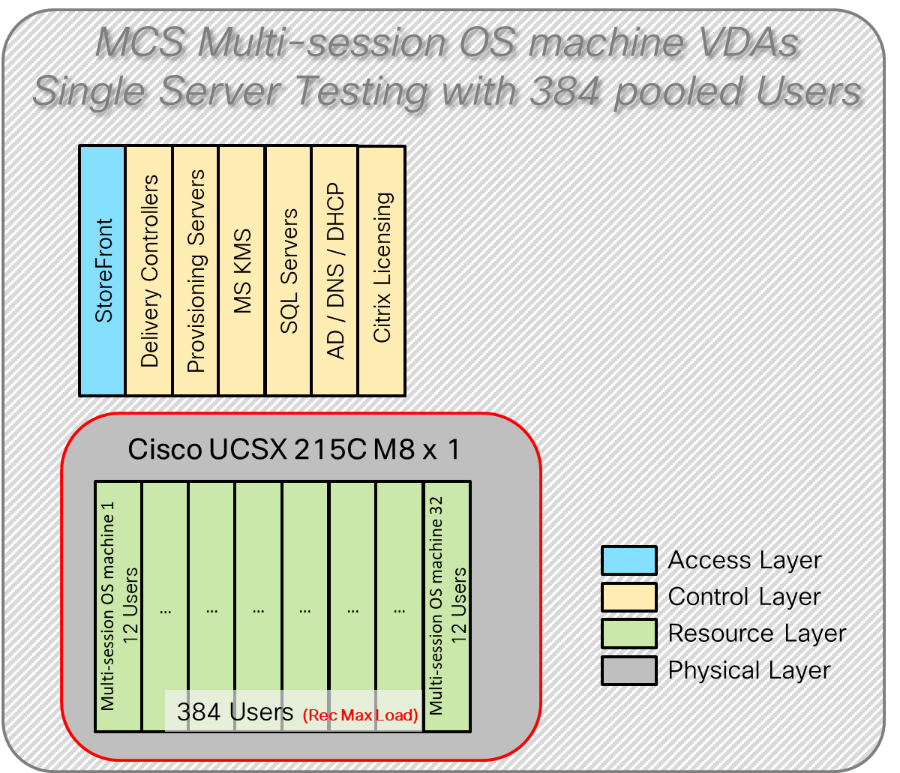
Hardware components:
● 2 Cisco UCS 6536 5th Generation Fabric Interconnects
● 1 (RDS/VDI Host) Cisco UCS X215c -M8 Compute Nodes with AMD EPYC 9355 3.55 GHz 32-Core processors, 1TB 6400MHz RAM for all host Compute Nodes
● Cisco UCS VIC 15231 CNA (1 per Compute Node)
● 2 Cisco Nexus N9K-C93180YC-FX Access Switches
● NetApp AFF A50
Software components:
● Cisco UCS firmware 6.0(1.250122)
● NetApp ONTAP 9.17.1P4
● VMware ESXi 8.0 U3 for host Compute Nodes
● Citrix Virtual Apps and Desktops 7 2402 LTSR U3 VDI Desktops and RDS Desktops
● FSLogix 25.09 for User Profile management
● Microsoft SQL Server 2022
● Microsoft Windows 11 64 bit, 2vCPU, 4 GB RAM, 40 GB HDD (master)
● Microsoft Windows Server 2022, 8vCPU, 32GB RAM, 60 GB vDisk (master)
● Microsoft Office 2021
● Login Enterprise 5.14.7 Knowledge Worker Workload (Benchmark Mode)
● NAbox 3.3
Cisco UCS Configuration for Full Scale Testing
This test case validates 8 Compute Node workloads using Citrix Virtual Apps and Desktops 7 LTSR with 2688 RDS sessions, 1610 VDI Non-Persistent sessions, and 1610 VDI Persistent sessions. Server N+1 fault tolerance is factored into this solution for each workload and infrastructure cluster.
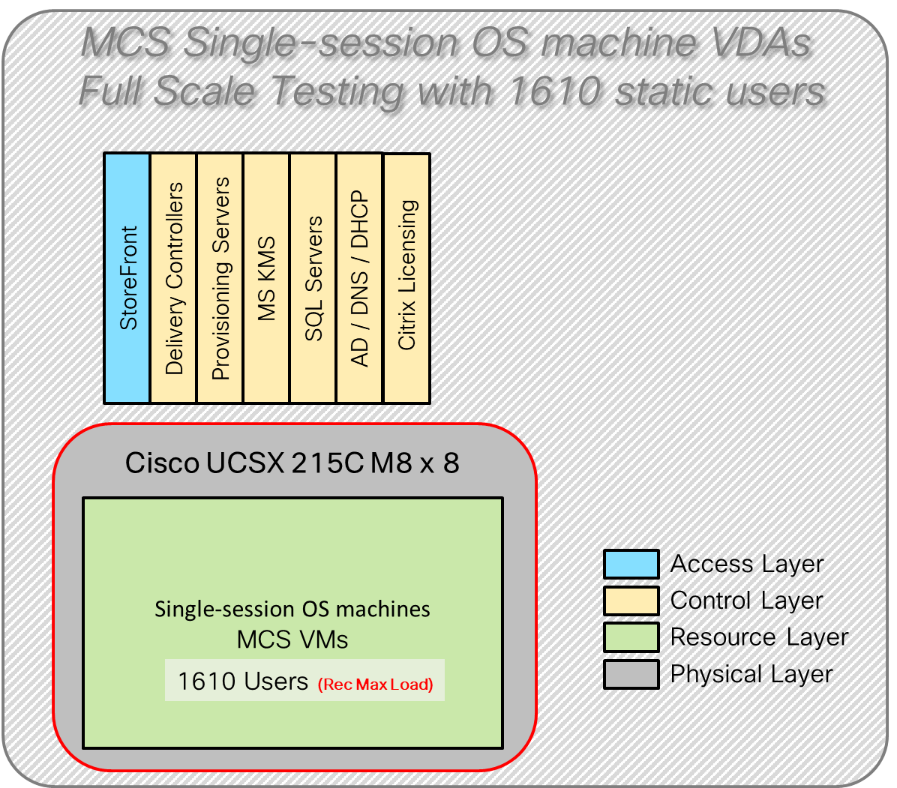
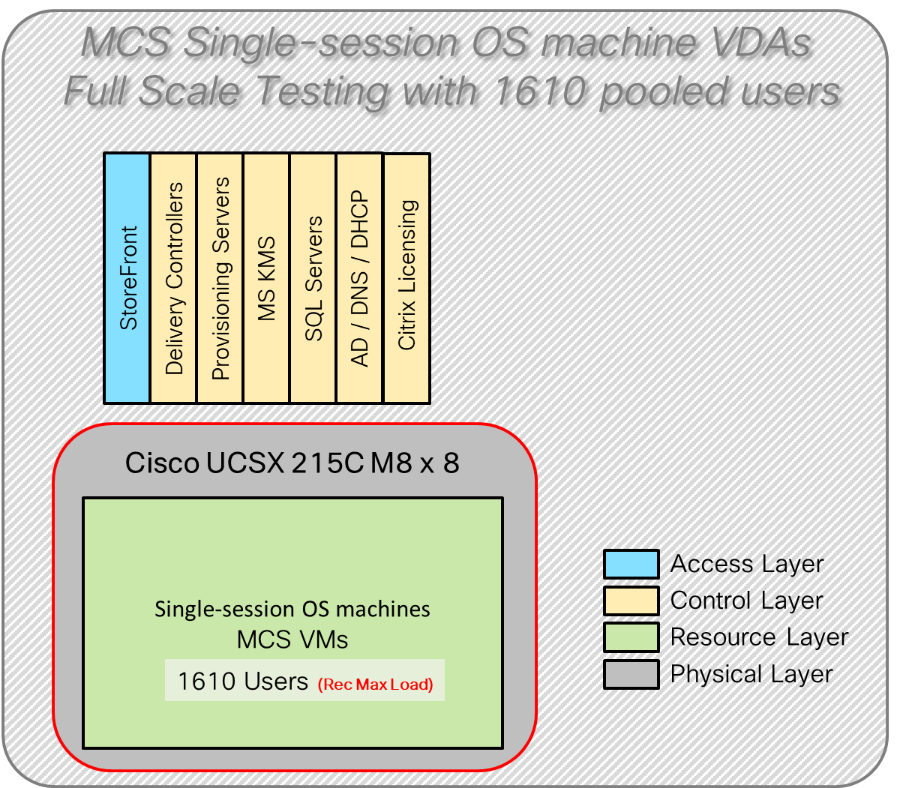
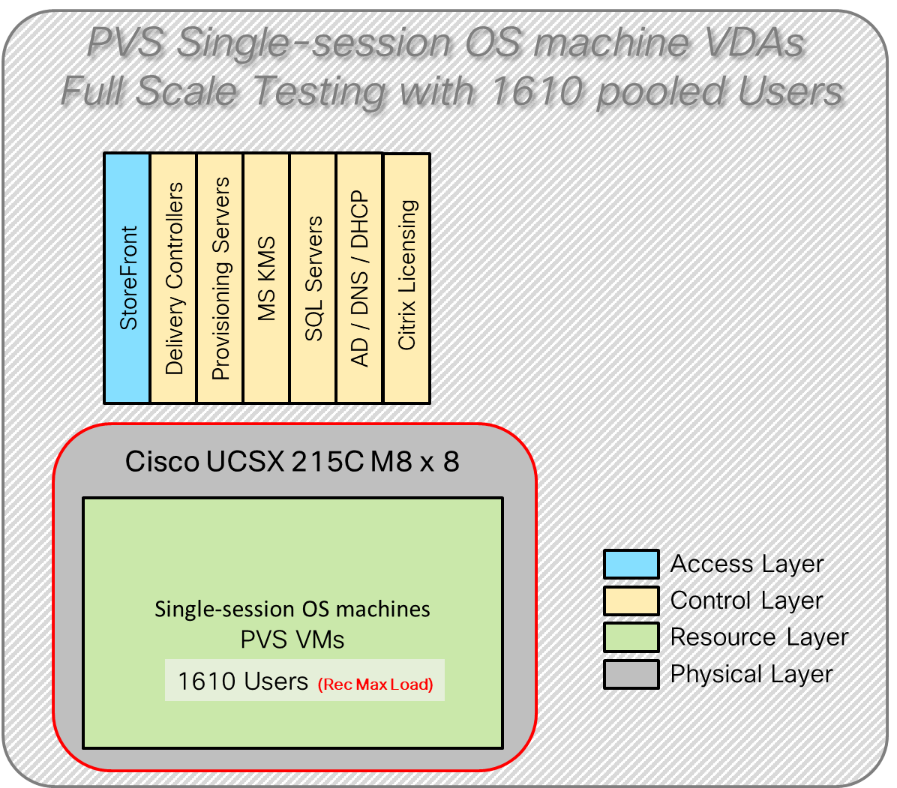
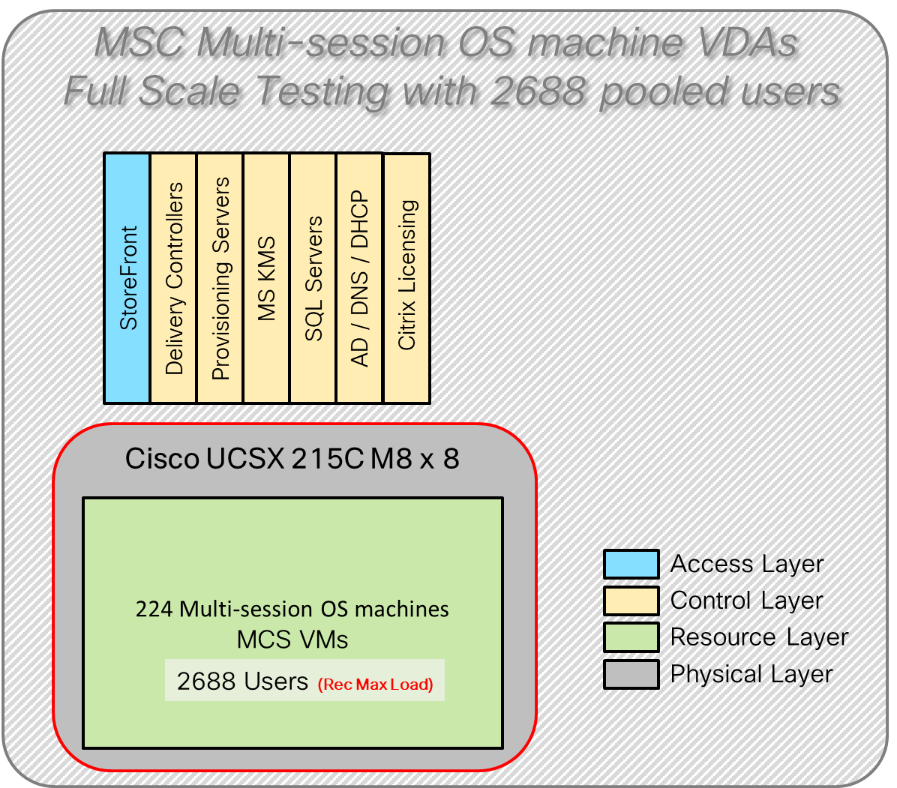
Hardware components:
● 2 Cisco UCS 6536 5th Generation Fabric Interconnects
● 4 (Infrastructure Hosts) Cisco UCS C220 M5 Rack Servers
● 8 (RDS/VDI Host) Cisco UCS X215c -M8 Compute Nodes with AMD EPYC 9355 3.55 GHz 32-Core processors, 1TB 6400MHz RAM for all host Compute Nodes
● Cisco UCS VIC 15231 CNA (1 per Compute Node)
● 2 Cisco Nexus N9K-C93180YC-FX Access Switches
● 1 NetApp AFF A50 storage system (2x storage controllers- Active/Active High Availability pair) with 8x 1.92TB NVMe SSD- 9 TB usable / 36TB effective (4:1 efficiency)
Software components:
● Cisco UCS firmware 6.0(1.250122)
● VMware ESXi 8.0 U3 for host Compute Nodes
● Citrix Virtual Apps and Desktops 7 2402 LTSR U3 VDI Hosted Virtual Desktops and RDS Hosted Shared Desktops
● Citrix Provisioning Server 7 2402 LTSR U3 VDI Desktops
● FSLogix 25.09 for User Profile management
● Microsoft SQL Server 2022
● Microsoft Windows 11 64 bit, 2vCPU, 4 GB RAM, 40 GB vDisk (master)
● Microsoft Windows Server 2022, 8vCPU, 32GB RAM, 60 GB vDisk (master)
● Microsoft Office 2021
● Login Enterprise 5.14.7 Knowledge Worker Workload (Benchmark Mode)
● NAbox 3.3
Testing Methodology and Success Criteria
All validation testing was conducted on-site within the Cisco labs in San Jose, California.
The testing results focused on the entire process of the virtual desktop lifecycle by capturing metrics during the desktop boot-up, user logon and virtual desktop acquisition (also referred to as ramp-up,) user workload execution (also referred to as steady state), and user logoff for the Citrix Virtual Apps and Desktops Hosted Virtual Desktop and RDS Hosted Shared models under test.
Test metrics were gathered from the hypervisor, virtual desktop, storage, and load generation software to assess the overall success of an individual test cycle. Each test cycle was not considered passing unless all of the planned test users completed the ramp-up and steady state phases (described below) and unless all metrics were within the permissible thresholds as noted as success criteria.
Three successfully completed test cycles were conducted for each hardware configuration, and results were found to be relatively consistent from one test to the next.
In this deployment guide, End User Experience testing introduced by the Login Enterprise testing platform from Login VSI was used quantify how a user perceives system responsiveness. This solution validation provides better insights into both the scalability and the performance quality of the FlexPod architecture.
About Login VSI
Login VSI helps organizations proactively manage the performance, cost, and capacity of their virtual desktops and applications wherever they reside – traditional, hybrid, or in the cloud. The Login Enterprise platform is 100% agentless and can be used in all major VDI and DaaS environments, including Citrix, VMware, and Microsoft. With 360° proactive visibility, IT teams can plan and maintain successful digital workplaces with less cost, fewer disruptions, and lower risk. Founded in 2012, Login VSI is headquartered in Boston, Massachusetts, and Amsterdam, Netherlands. Visit www.loginvsi.com.
Login Enterprise
Login Enterprise, by Login VSI, is the industry-standard software used to simulate a human-centric workload used for the purpose of benchmarking the capacity and performance of a VDI solutions. The performance testing documented in this Reference Architecture utilized the Login Enterprise benchmarking tool (https://www.loginvsi.com/platform/). The virtual user technology of Login Enterprise simulates real-world users performing real-world tasks while measuring the time required for each interaction. Login Enterprise assesses desktop performance, application performance, and user experience to determine the overall responsiveness of the VDI solution. Using Login Enterprise for VDI capacity planning helps to determine the optimal hardware configuration to support the desired number of users and applications.
About the EUX Score
The Login Enterprise End-User Experience (EUX) Score is a unique measurement that provides an accurate and realistic evaluation of user experience in virtualized or physical desktop environments. The score is based on metrics that represent system resource utilization and application responsiveness. The results are then combined to produce an overall score between 1 and 10 that closely correlates with the real user experience. See the table below for general performance guidelines with respect to the EUX Score.
| Score |
Assessment |
| Greater than 8.5 |
Excellent |
| 7.5-8.5 |
Very Good |
| 6.5 – 7.5 |
Good |
| 5.5 – 6.5 |
Fair |
| Less than 5.5 |
Poor |
See the following article for more information: https://support.loginvsi.com/hc/en-us/articles/4408717958162-Login-Enterprise-EUX-Score-
About VSImax
The Login Enterprise VSImax is a performance metric used to measure the maximum user capacity or scalability of a virtualized desktop infrastructure (VDI) environment. The EUX Score is used to determine the VSImax, and it represents the maximum number of virtual users that can be supported by the infrastructure while still maintaining acceptable performance levels.
Login Enterprise Workloads
Login Enterprise Workloads are human-centric workloads designed to simulate a user interacting with predetermined applications in a human-paced way. The industry-standard workloads that come with Login Enterprise are Knowledge Worker and Task Worker. These workloads are based on the Microsoft Office suite and popular browsers used in the enterprise. Other workloads are available from Login VSI.
Knowledge worker
An enterprise knowledge worker is a medium to heavy duty productivity user that regularly uses a web browser, an email client, and specializes in a wide range of software to create spreadsheets, documents, and presentations. It is common for knowledge workers to have multiple applications and browsers open at once, regularly switching between these applications. The knowledge worker expects a responsive user experience and has little tolerance for variation in performance.
Task worker
An enterprise task worker is a light duty productivity user that regularly uses a static web browser to access internal sites, an email client and an application that is the basis for their task. Task workers stay focused on the task at hand and switch between apps on occasion. The task worker is tolerant of some workspace lag. Task workers often take the form of data processing workers, call center agents, tellers, and receptionists.
Single-Server Recommended Maximum Workload
For both the Citrix Virtual Apps and Desktops Hosted Virtual Desktop and Citrix Hosted Shared Desktop use cases, a recommended maximum workload was determined by the Login Enterprise Load Test based on the Knowledge Worker Application group end user experience measurements and Compute Node server operating parameters.
This recommended maximum workload approach allows you to determine the server N+1 fault tolerance load the Compute Node can successfully support in the event of a server outage for maintenance or upgrade.
Our recommendation is that the Login VSI EUX score does not go below 6.5 (Good) to insure that end user experience is outstanding. Additionally, during steady state, the average processor core utilization should average no more than 90 percent.
Note: Memory should never be oversubscribed for Desktop Virtualization workloads.
| Test Phase |
Description |
| Boot |
Start all RDS and VDI virtual machines at the same time |
| Idle |
The rest time after the last desktop is registered on the XD Studio. (typically, a 30-45 minute, <60 min) |
| Logon |
The logon phase of the test is where sessions are launched and start executing the workload over a 48 minutes duration |
| Steady state |
The steady state phase is where all users are logged in and performing various workload tasks such as using Microsoft Office, Web browsing, playing videos. |
| Logoff |
Sessions finish executing the workload and logoff |
The following protocol was used for each test cycle in this study to ensure consistent results.
Pre-Test Setup for Single and Multi-Compute Node Testing
All virtual machines were shut down utilizing the Citrix Virtual Apps and Desktops Studio and vCenter.
All Launchers for the test were shut down. They were then restarted in groups of 10 each minute until the required number of launchers was running with the Login VSI Agent at a “waiting for test to start” state.
Procedure 1. Test Run Protocol
To simulate severe, real-world environments, Cisco requires the log-on and start-work sequence, known as Ramp Up, to complete in 48 minutes. Additionally, it’s required to start all sessions, whether single server users or full scale test users to become active within two minutes after the last session is launched.
In addition, Cisco performs three consecutive load tests with workload generated by Knowledge Worker Application group for all single server and scale testing. This assures that our tests represent real-world scenarios. For each of the three consecutive runs on single server tests, the same process was followed.
1. Time 0:00:00 Start esxtop logging on the VDI Host Compute Nodes used in the test run
2. Time 0:00:10 Start Storage Partner Performance logging on Storage System
3. Time 0:05: Boot Virtual Desktops/RDS Virtual Machines using Citrix Virtual Apps and Desktops Studio
Note: The boot rate should be around 10-12 VMs per minute per server.
4. Time 0:06 First machines boot
5. Time 0:30 Single Server or Scale target number of desktop VMs booted on 1 or more Compute Nodes
Note: No more than 30 minutes for boot up of all virtual desktops is allowed.
6. Time 0:35 Single Server or Scale target number of desktop VMs desktops registered on Citrix Virtual Apps and Desktops Studio
7. Virtual machine settling time.
Note: No more than 60 Minutes of rest time is allowed after the last desktop is registered on the Citrix Virtual Apps and Desktops Studio for idle time before start of the test. Typically, a 30-45 minute rest period is sufficient.
8. Time 1:35 Start Login Enterprise Load Test based on the Knowledge Worker Application group, setting login of all test users within 48 minutes and the test duration at 15 minutes, with Single Server or Scale target number of desktop VMs utilizing sufficient number of Launchers (at 20-25 sessions/Launcher)
9. Time 2:23 Single Server or Scale target number of desktop VMs desktops launched (48 minute benchmark launch rate)
10. Time 2:25 All launched sessions must become active
Note: All sessions launched must become active for a valid test run within this window.
11. Time 2:40 Login VSI Test Ends (based on test duration period designated above.)
12. Time 2:55 All active sessions logged off
13. Time 2:57 All logging terminated; Test complete
14. Time 3:15 Copy all log files off to archive; Set virtual desktops to maintenance mode through broker; Shutdown all Windows machines
15. Time 3:45 Ready for the new test sequence.
The objective of this testing was to generate the performance and scalability data required to validate multiple Citrix deployment models running on FlexPod architecture. Specifically, the test program evaluated the following architectures:
● Citrix RDS Hosted Shared Desktop (RDS) provisioned with Citrix Machine Creation Services (MCS)
● Citrix Virtual Apps and Desktops Hosted Virtual Desktop (VDI), randomly assigned and non-persistent, provisioned with Citrix Provisioning Services, and Citrix Machine Creation Services (MCS)
● Citrix Virtual Apps and Desktops Hosted Virtual Desktop (VDI), statically assigned and persistent, based on full-clone desktops
These workloads were hosted on VMware ESXi 8.0 U3 with Microsoft Windows 11 virtual desktops and Microsoft Windows Server 2022 session hosts running on X-Series M8 Compute Node servers with AMD Gen 5 EPYC processors. Shared storage, fibre channel and NFS, were provided by a NetApp AFF A50 storage system.
Our pass criteria for this testing:
● Cisco will run tests at a session count level that effectively utilizes the Compute Node capacity measured by CPU utilization, memory utilization, storage utilization, and network utilization. We will use Login Enterprise to launch Knowledge Worker 2022 application group to simulate user workloads. The number of launched sessions must equal active sessions within two minutes of the last session launched in a test as observed on the Login Enterprise console.
● The Citrix Virtual Apps and Desktops Studio should be monitored throughout the steady state to make sure of the following:
◦ All running sessions report In Use throughout the steady state
◦ No sessions move to unregistered, unavailable, or available state at any time during steady state
Within 20 minutes of the test, all sessions on all launchers must have logged out automatically. Stuck sessions define a test failure condition.
● Cisco requires three consecutive runs with EUX results within +/-1% variability to pass the Cisco Validated Design performance criteria. For white papers written by partners, two consecutive runs within +/-1% variability are accepted. (All test data from partner run testing must be supplied along with the proposed white paper.)
● We will publish Cisco Validated Designs with our recommended workload following the process above and will note that we did not reach a VSImax dynamic in our testing.
Test Results
This chapter contains the following:
● Single-Server Recommended Maximum Workload Testing
● Fibre channel datastore: Single-Server Recommended Maximum Workload for RDS with 384 Users
● NFS datastore: Single-Server Recommended Maximum Workload for RDS with 384 Users
● Fibre channel datastore: Full-Scale PVS Non-Persistent Workload Testing with 1600 Users
● NFS datastore: Full-Scale RDS Workload Testing with 2600 Users
● NetApp AFF A50 Storage Detailed Test Results for Cluster Scalability Test
● 2600 Users Citrix HSD (RDS) Windows 2022 Sessions
● 1600 Users Persistent Desktops Cluster Test
● 1600 Users PVS Non-Persistent Desktops Cluster Test
● Scalability Considerations and Guidelines
● Scalability of Citrix Virtual Apps and Desktops 7 LTSR Configuration
● Microsoft Azure and Citrix Cloud
The data presented in this section is intended to provide representative reference points for customers and partners designing similar environments. The validation results reflect the performance observed under the specific hardware, software, and configuration conditions documented in this solution. As such, these results should be viewed as illustrative of achievable outcomes within this validated design and not as a comprehensive characterization of performance across all Citrix Virtual Apps and Desktops deployments.
Single-Server Recommended Workload Testing
This section details the key performance metrics captured on Cisco UCS compute nodes during single-server testing to verify the Recommended Maximum Workload per host. The testing consisted of three scenarios: 384 RDS sessions, 230 VDI non-persistent sessions, and 230 VDI persistent sessions. These desktops were deployed using various Citrix CVAD methods across both Fibre Channel and NFS datastores.
Fibre channel datastore: Single-Server Recommended Maximum Workload for RDS with 384 Users
The recommended maximum workload for a Cisco UCS X215c M8 Compute Node with dual AMD EPYC 9355 processors, 1TB 6400MHz RAM is 384 Server 2022 Hosted Shared Desktop sessions. The dedicated Compute Node server ran 32 Server 2022 Virtual Machines. Each virtual server was configured with 4 vCPUs and 24GB RAM.
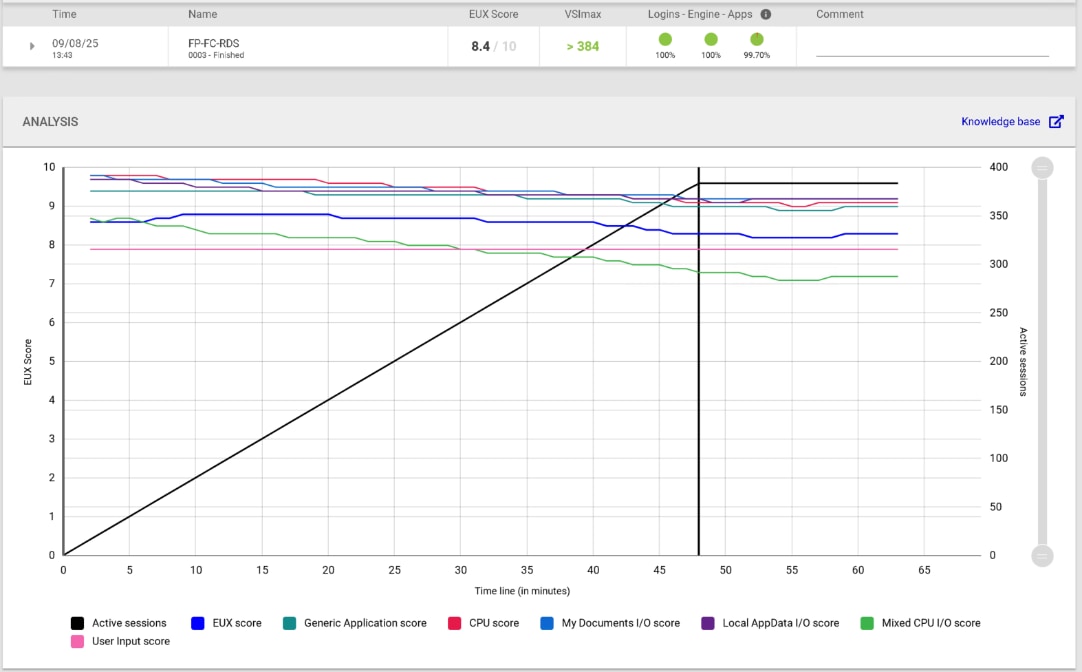
Performance data for the server running the workload as follows:
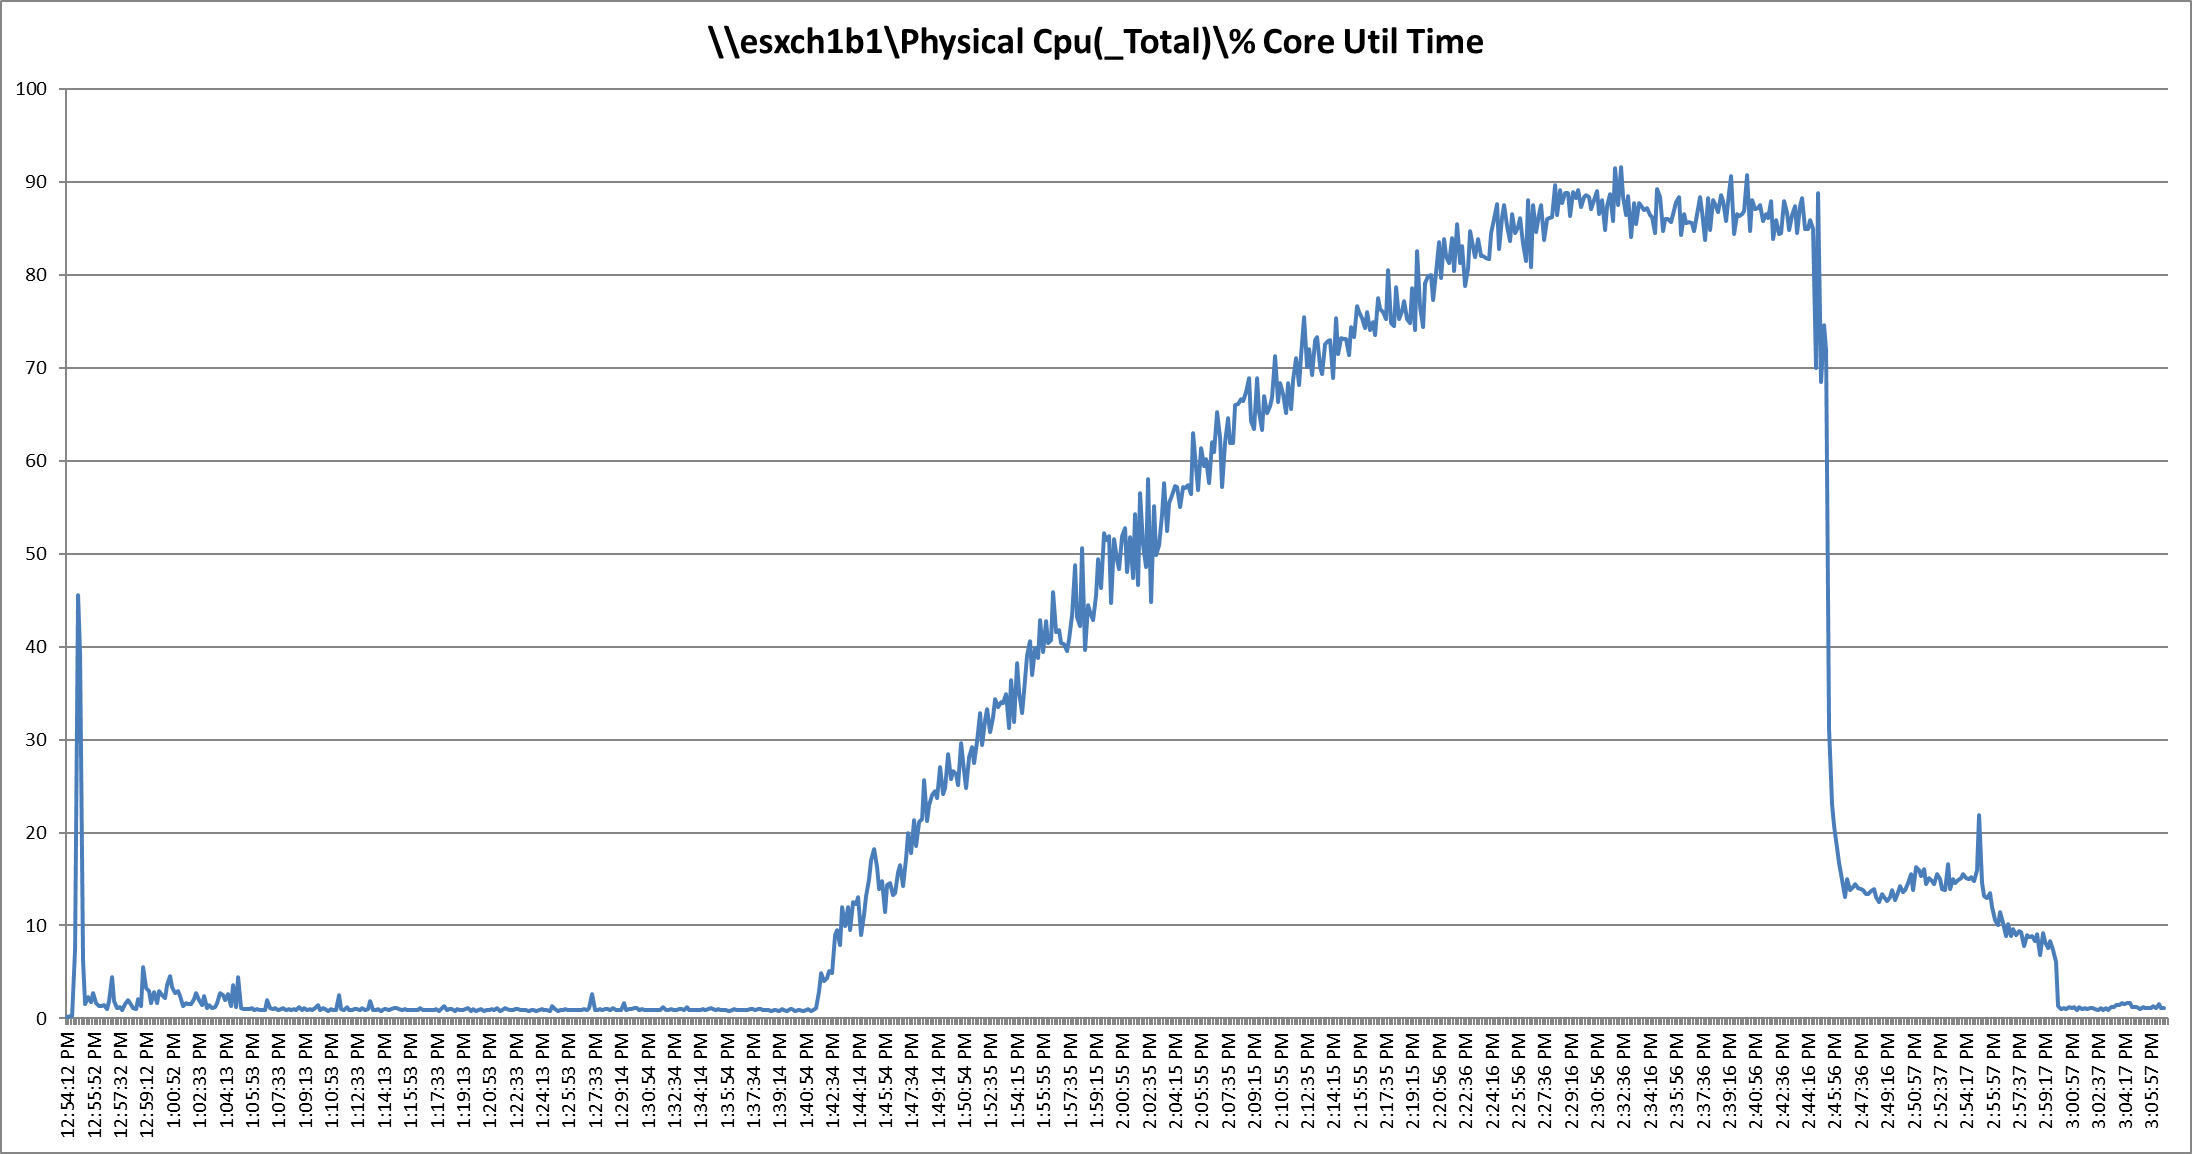
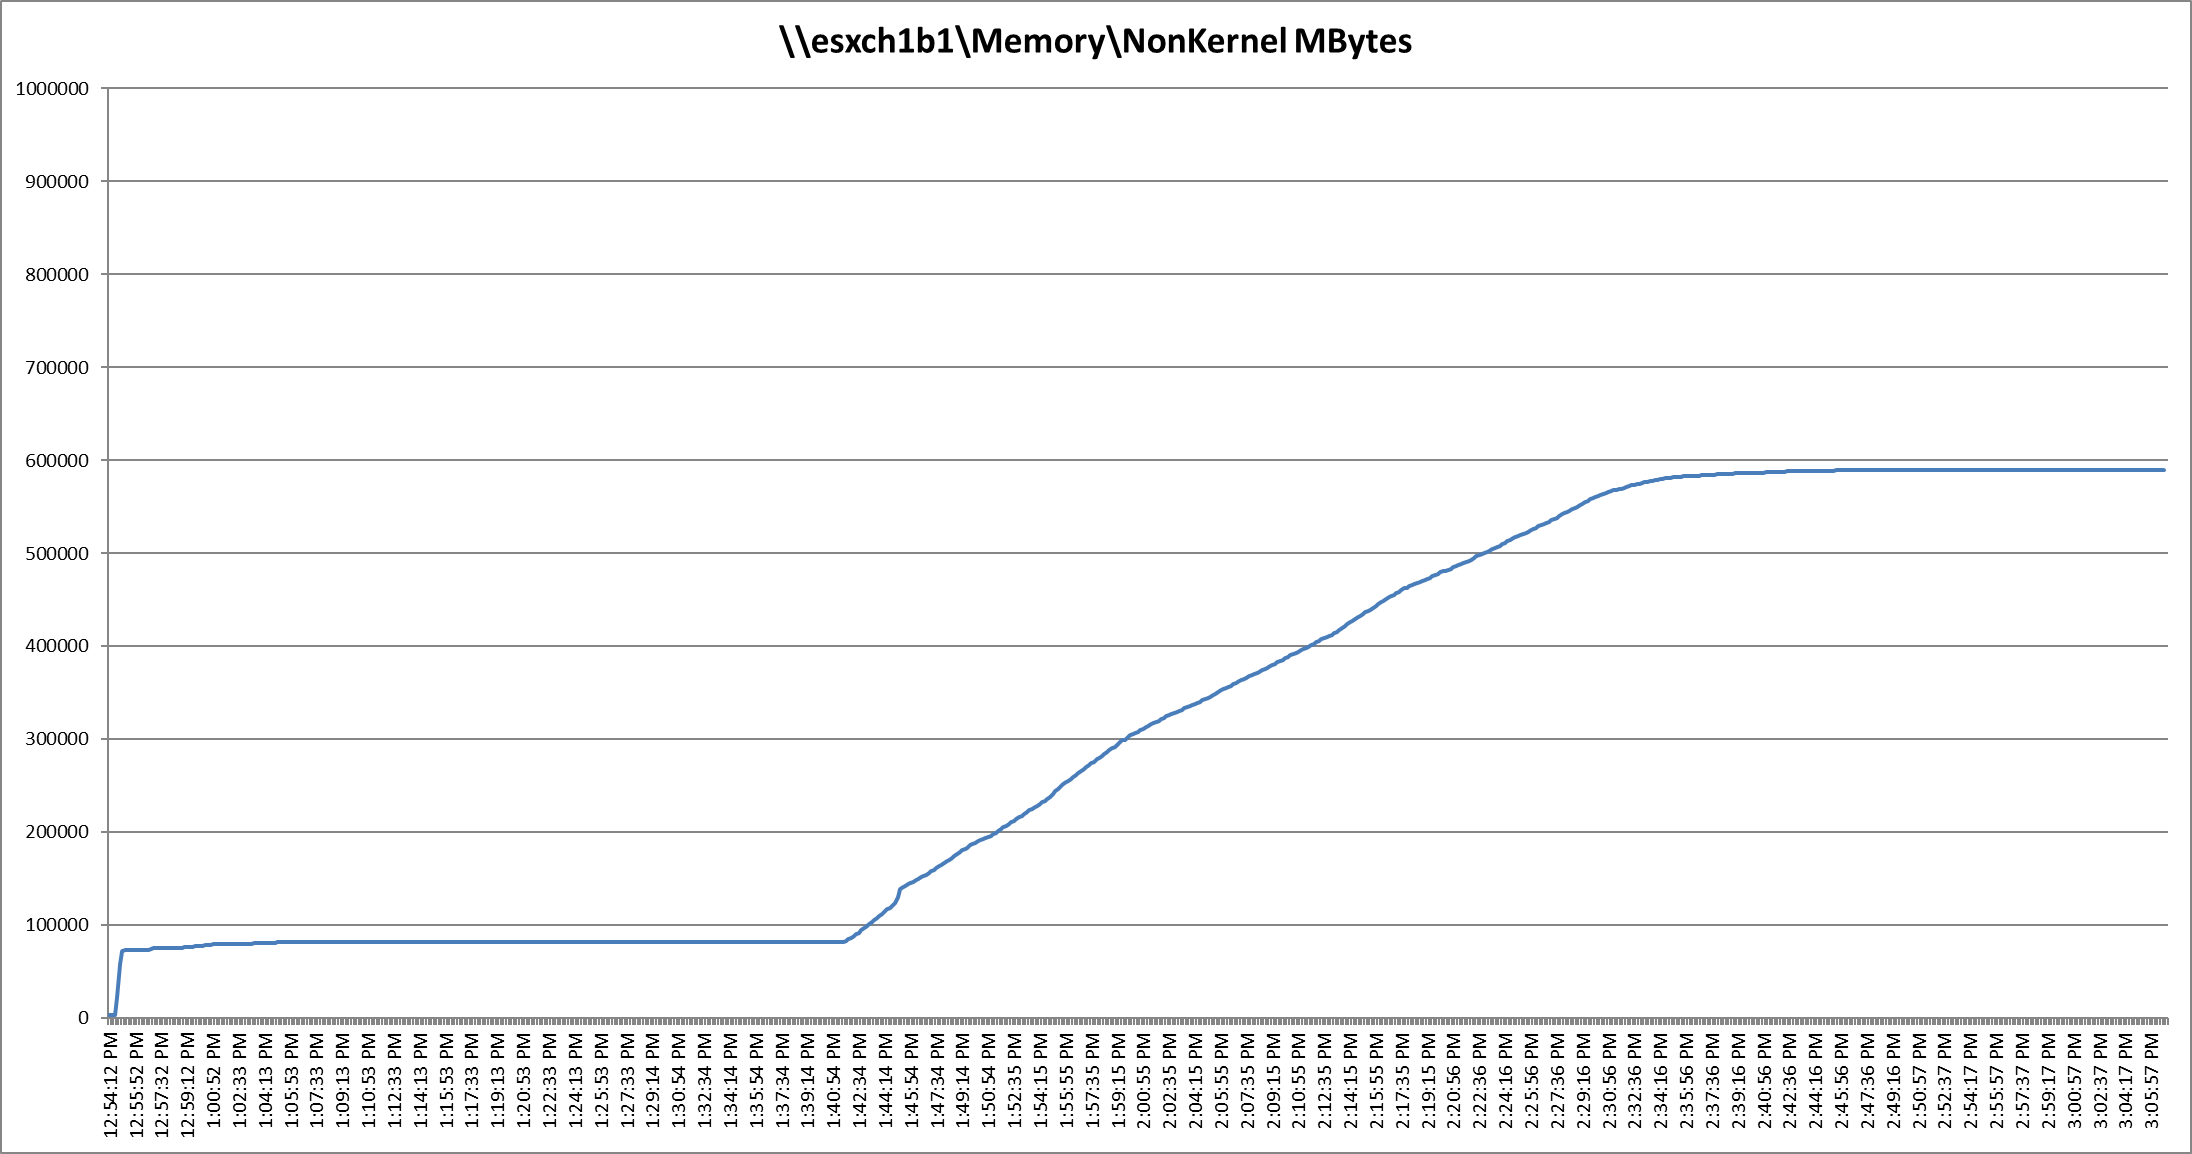
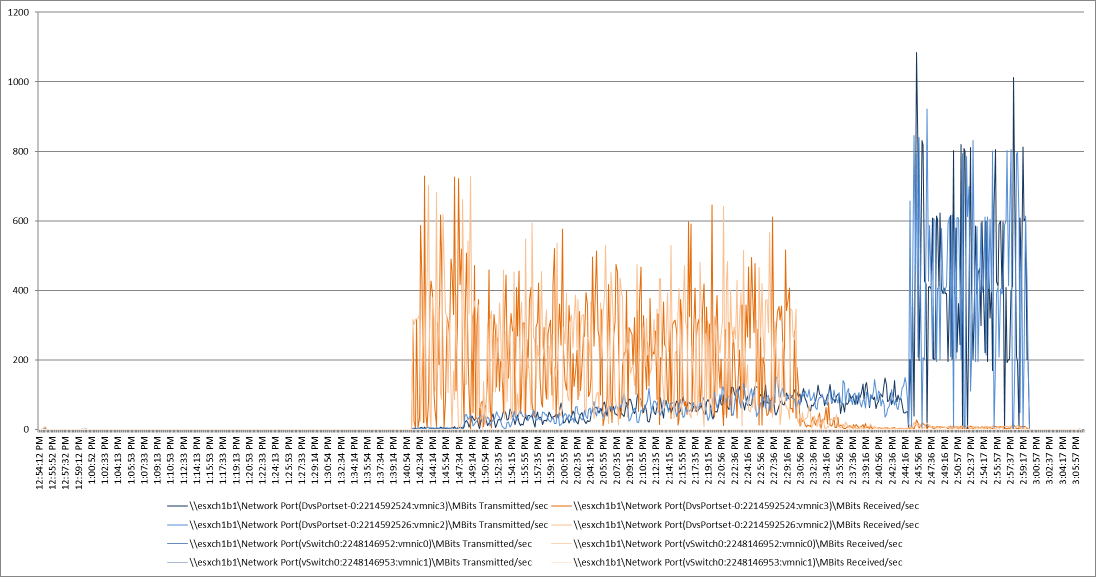
Fibre channel datastore: Single-Server Recommended Maximum Workload for MCS VDI Non-Persistent with 230 Users
The recommended maximum workload for a Cisco UCS X215c M8 Compute Node with dual AMD EPYC 9355 processors, 1TB 6400MHz RAM is 230 Windows 11 64-bit virtual machines with 2 vCPU and 4GB RAM. Login VSI and node performance data as follows:
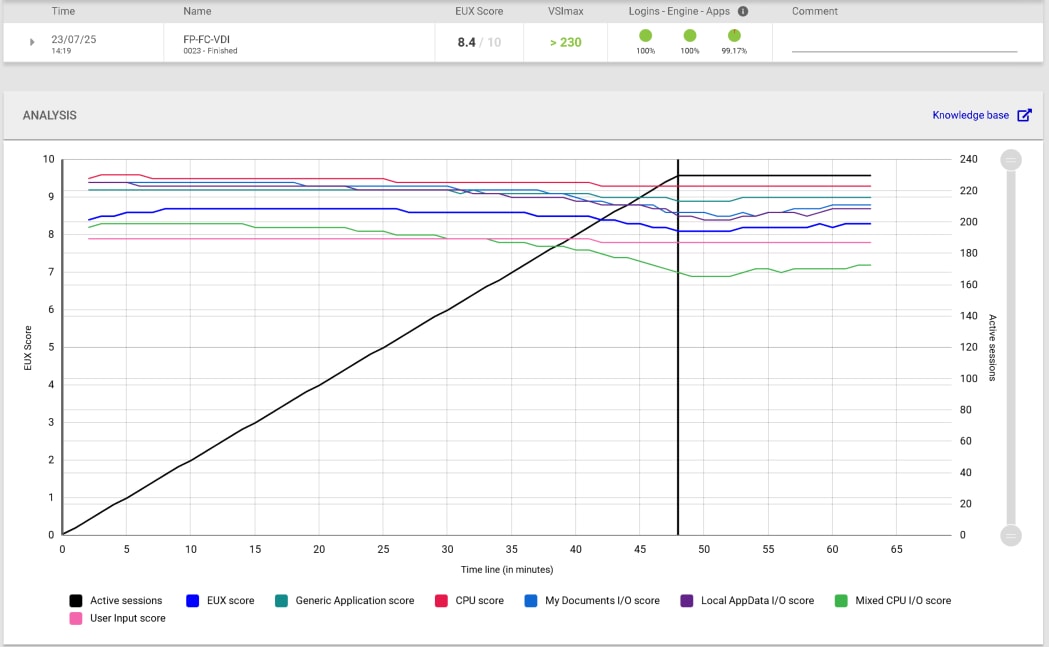
Performance data for the server running the workload as follows:
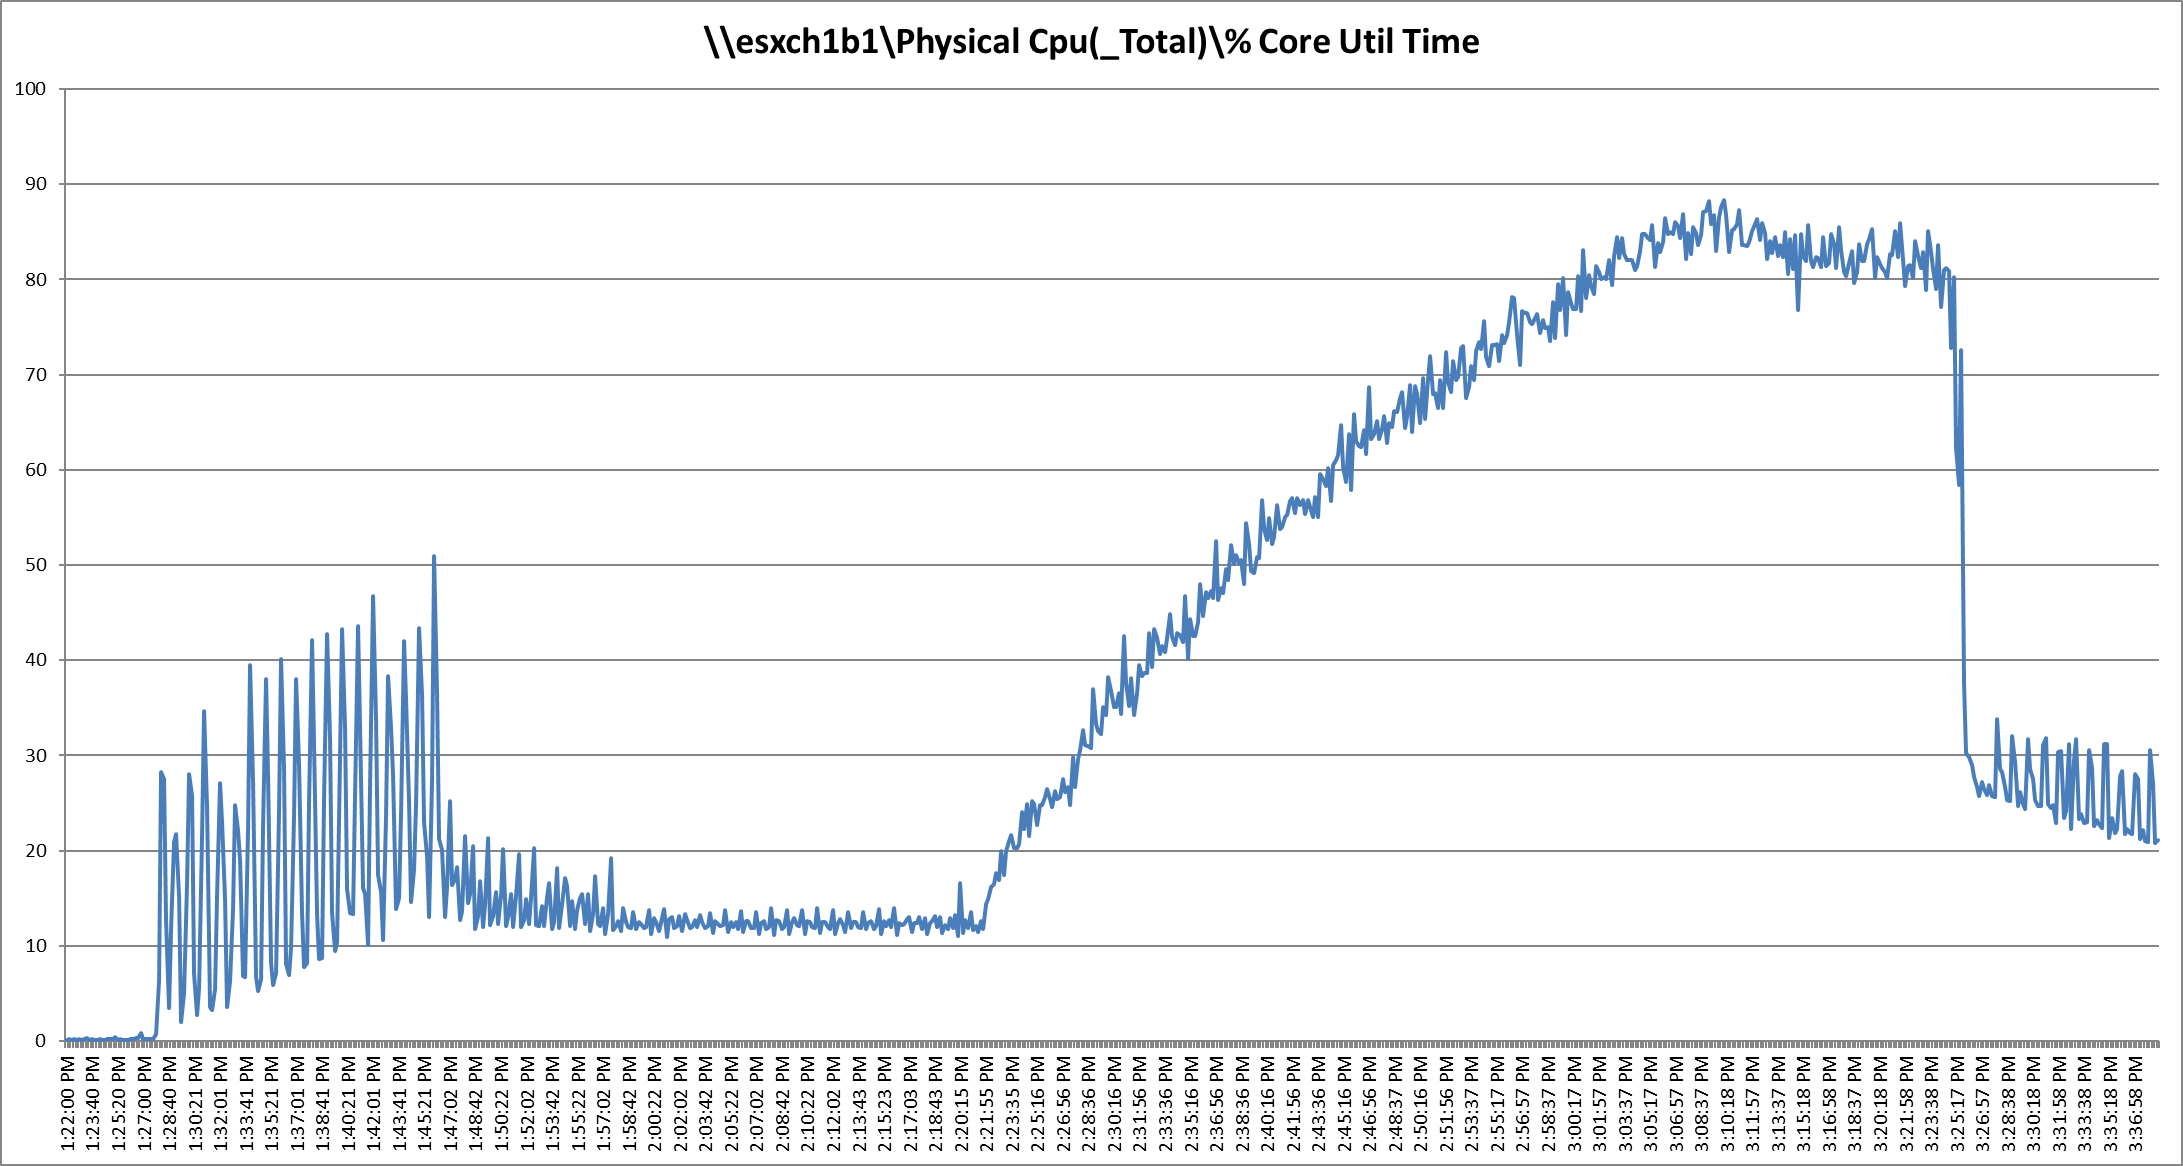
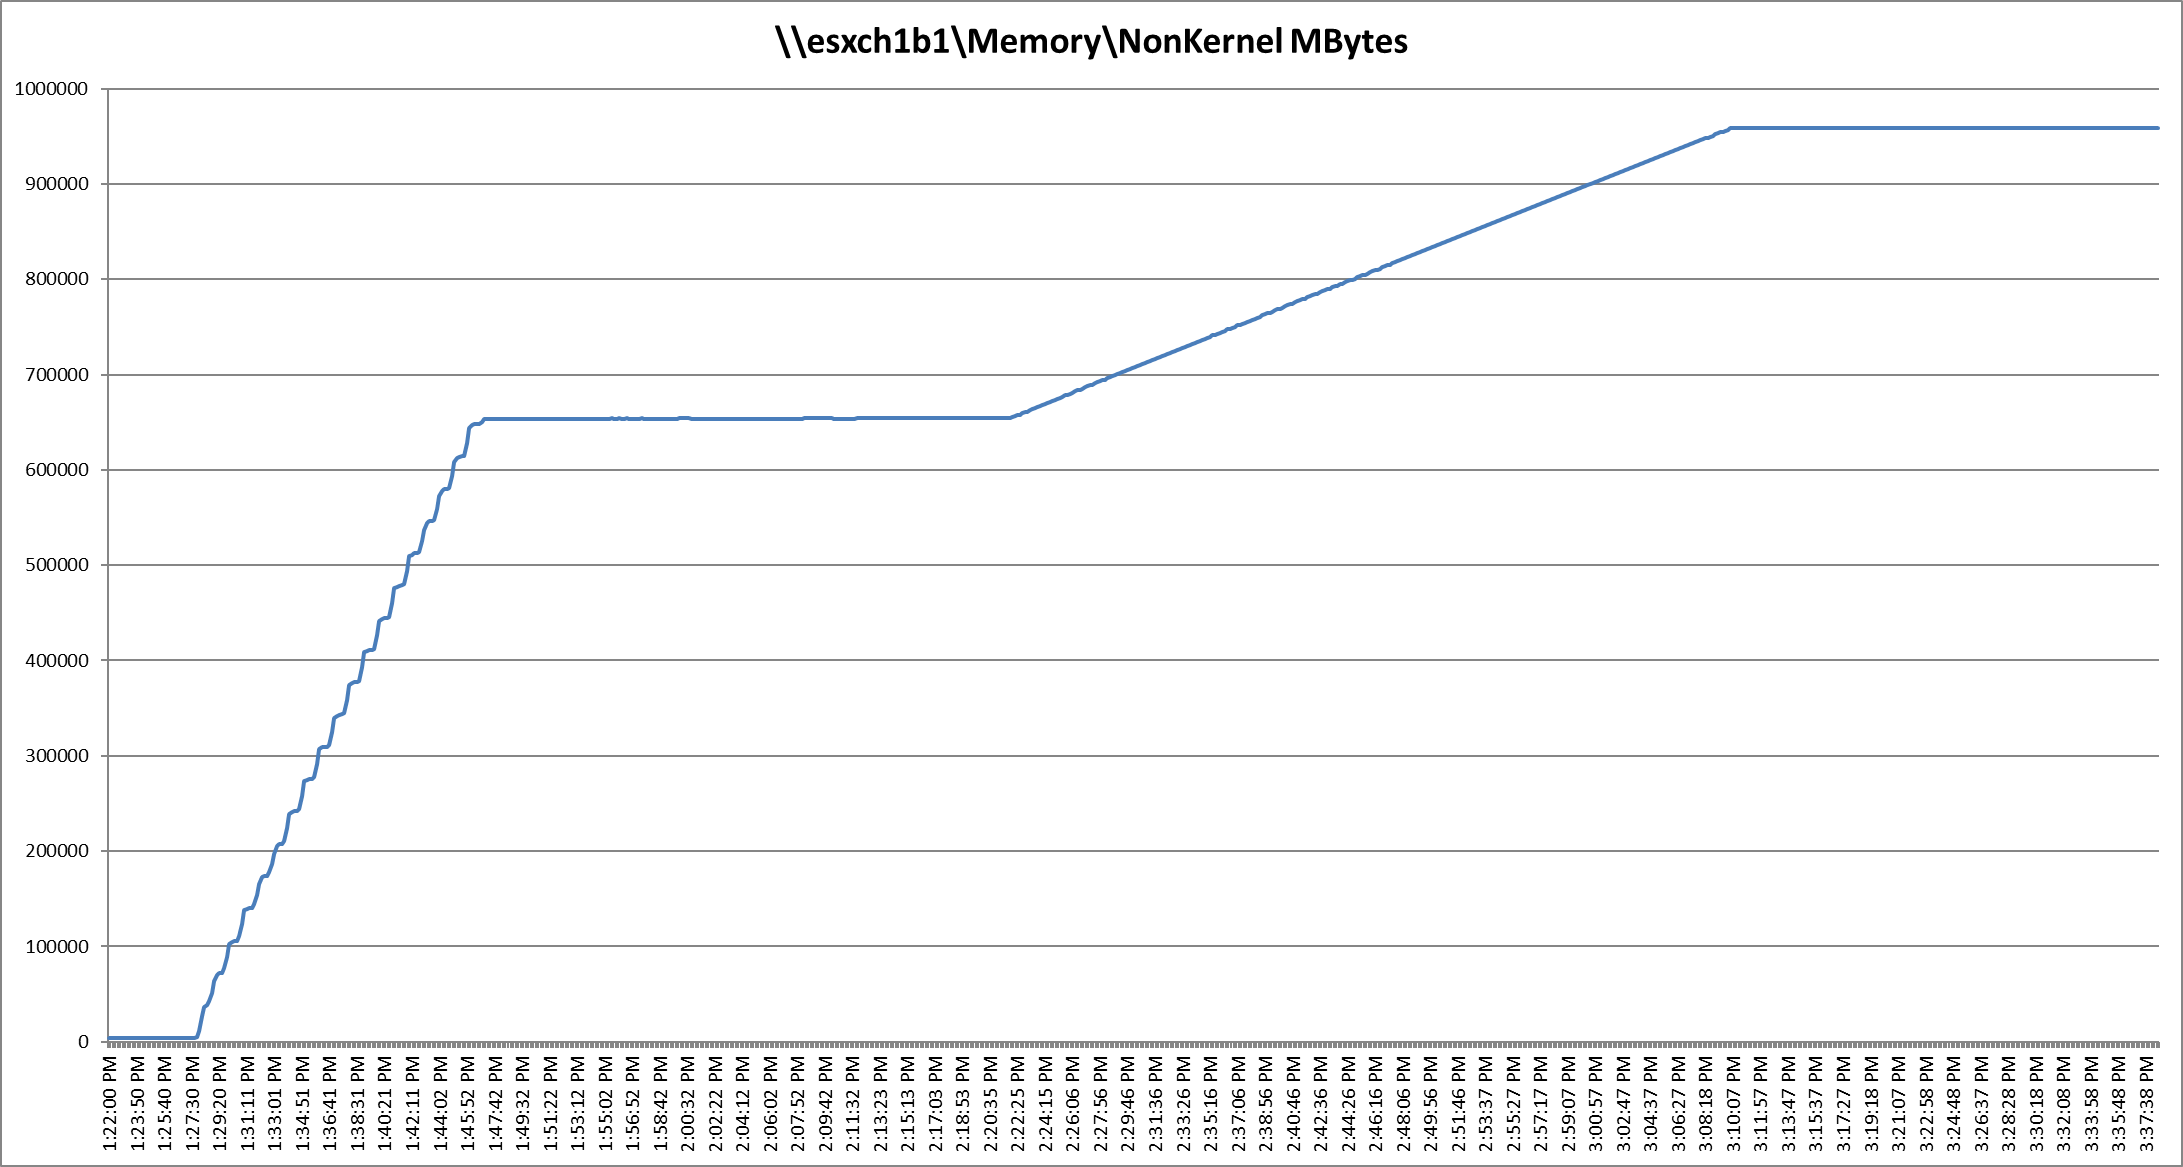
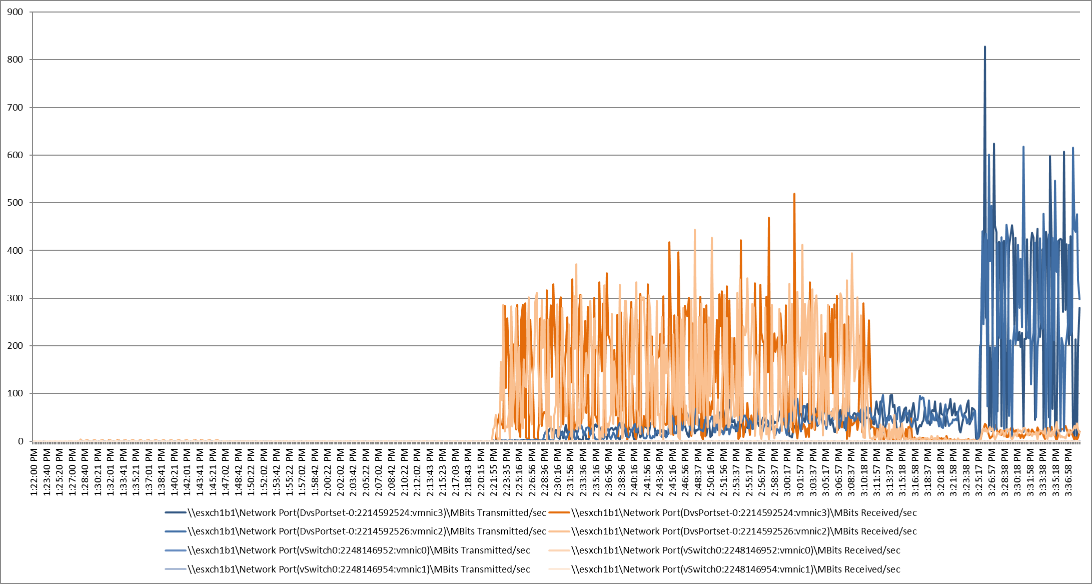
Fibre channel datastore: Single-Server Recommended Maximum Workload for PVS VDI Non-Persistent with 230 Users
The recommended maximum workload for a Cisco UCS X215c M8 Compute Node with dual AMD EPYC 9355 processors, 1TB 6400MHz RAM is 230 Windows 11 64-bit virtual machines with 2 vCPU and 4GB RAM.
Login VSI and node performance data as follows:
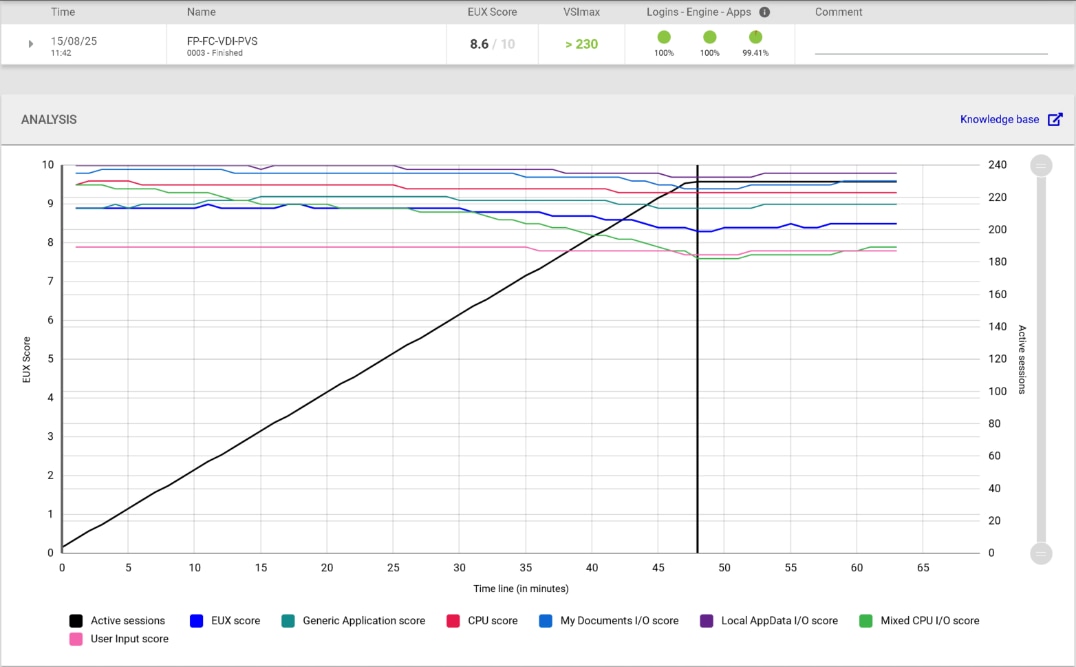
Performance data for the server running the workload as follows:
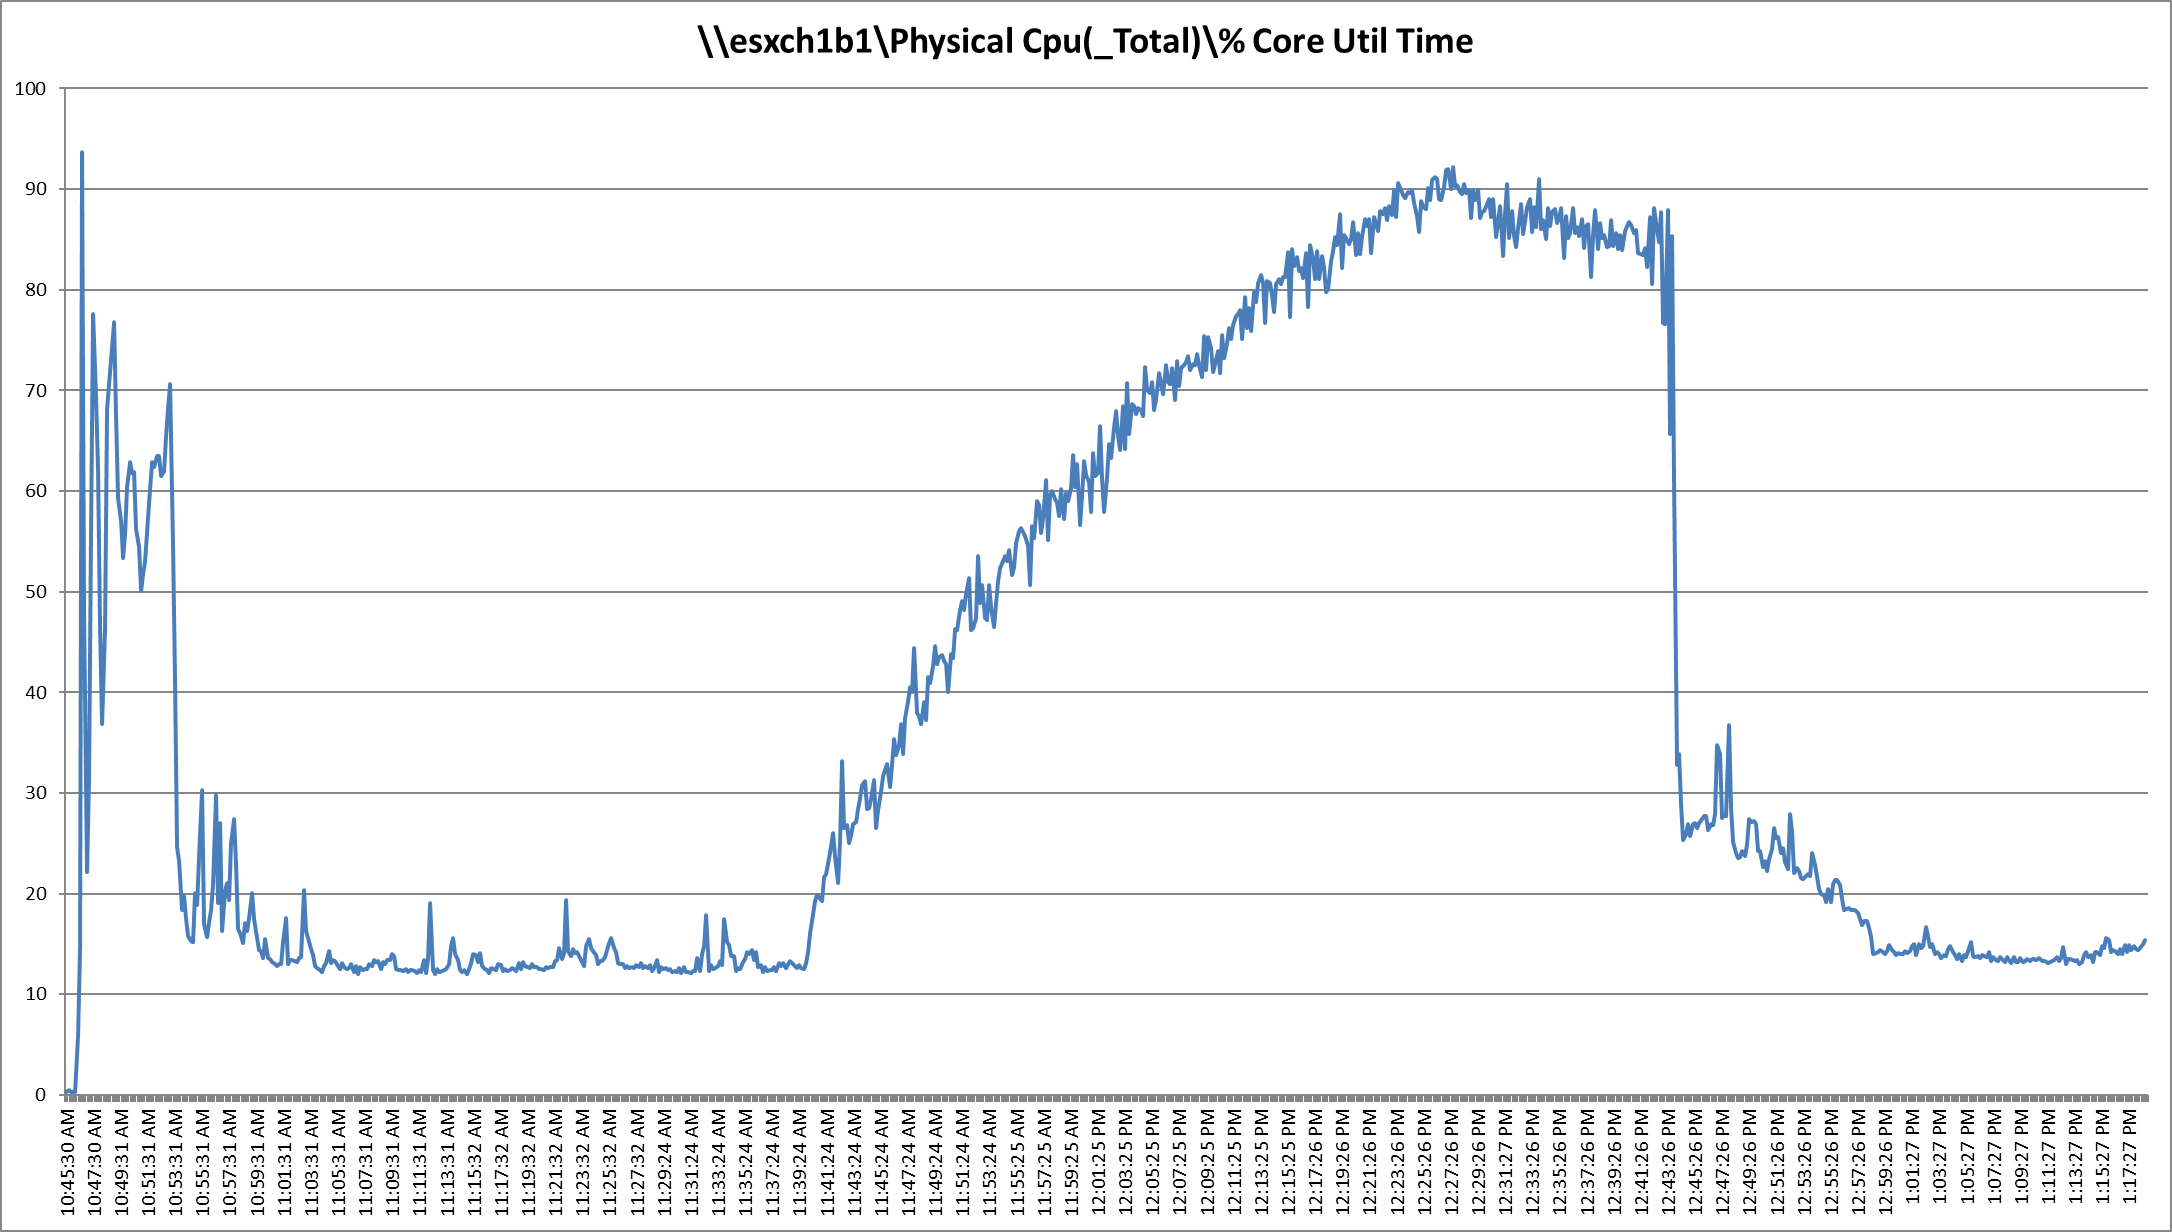
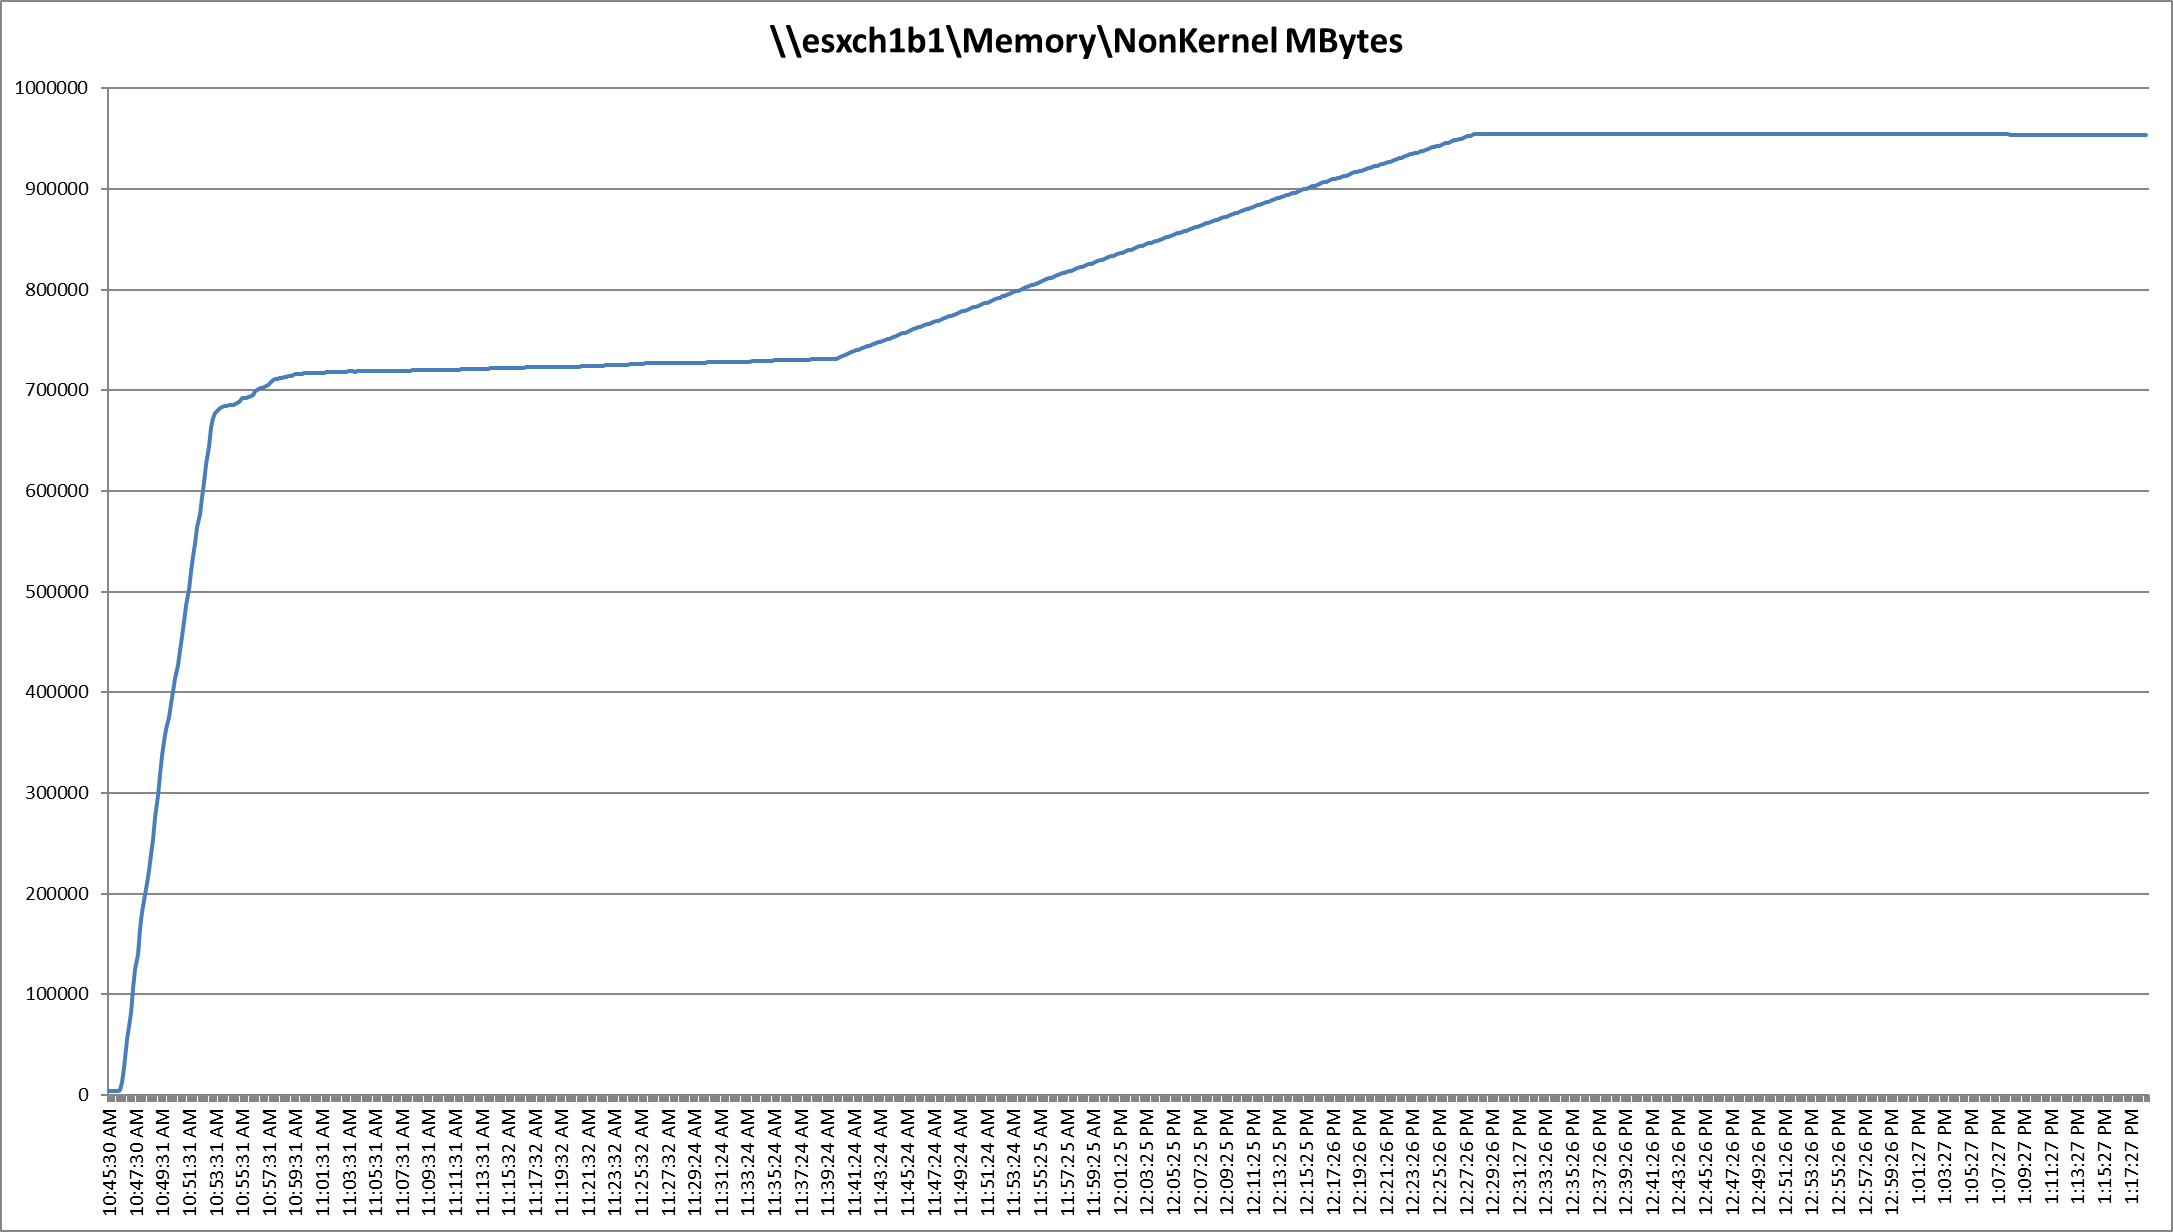
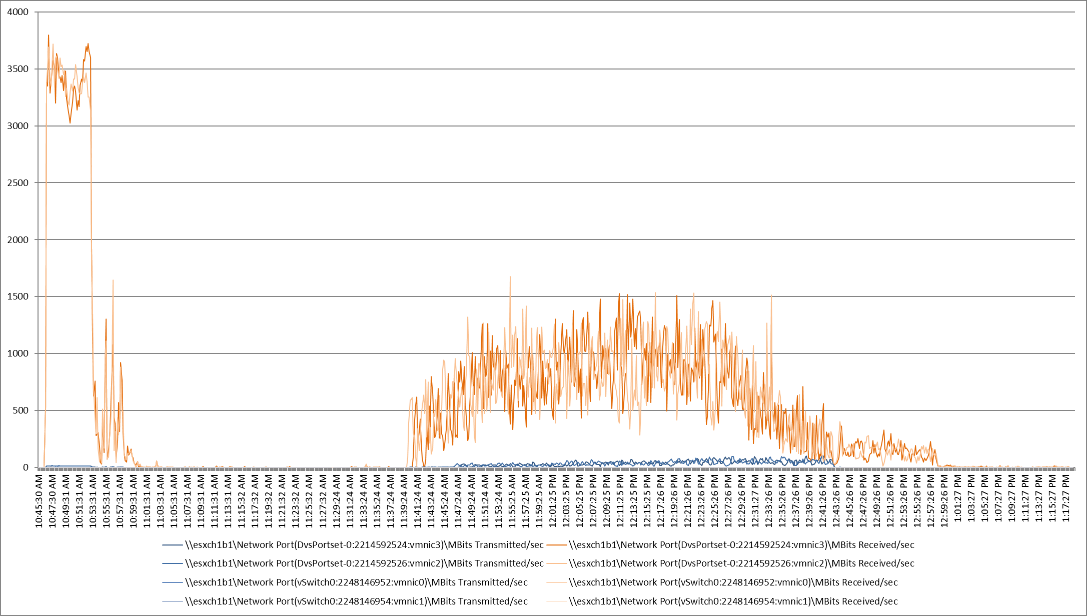
Fibre channel datastore: Single-Server Recommended Maximum Workload for VDI Persistent with 230 Users
The recommended maximum workload for a Cisco UCS X215c M8 Compute Node with dual AMD EPYC 9355 processors, 1TB 6400MHz RAM is 230 Windows 11 64-bit virtual machines with 2 vCPU and 4GB RAM. Login VSI and Compute Node performance data as follows:
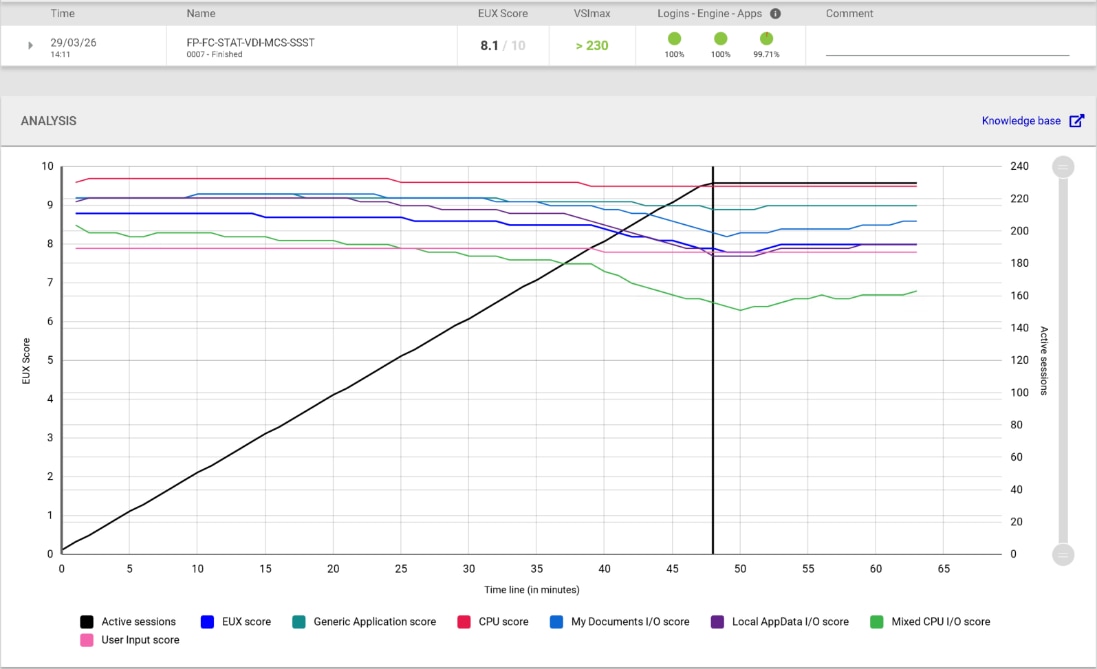
Performance data for the server running the workload as follows:
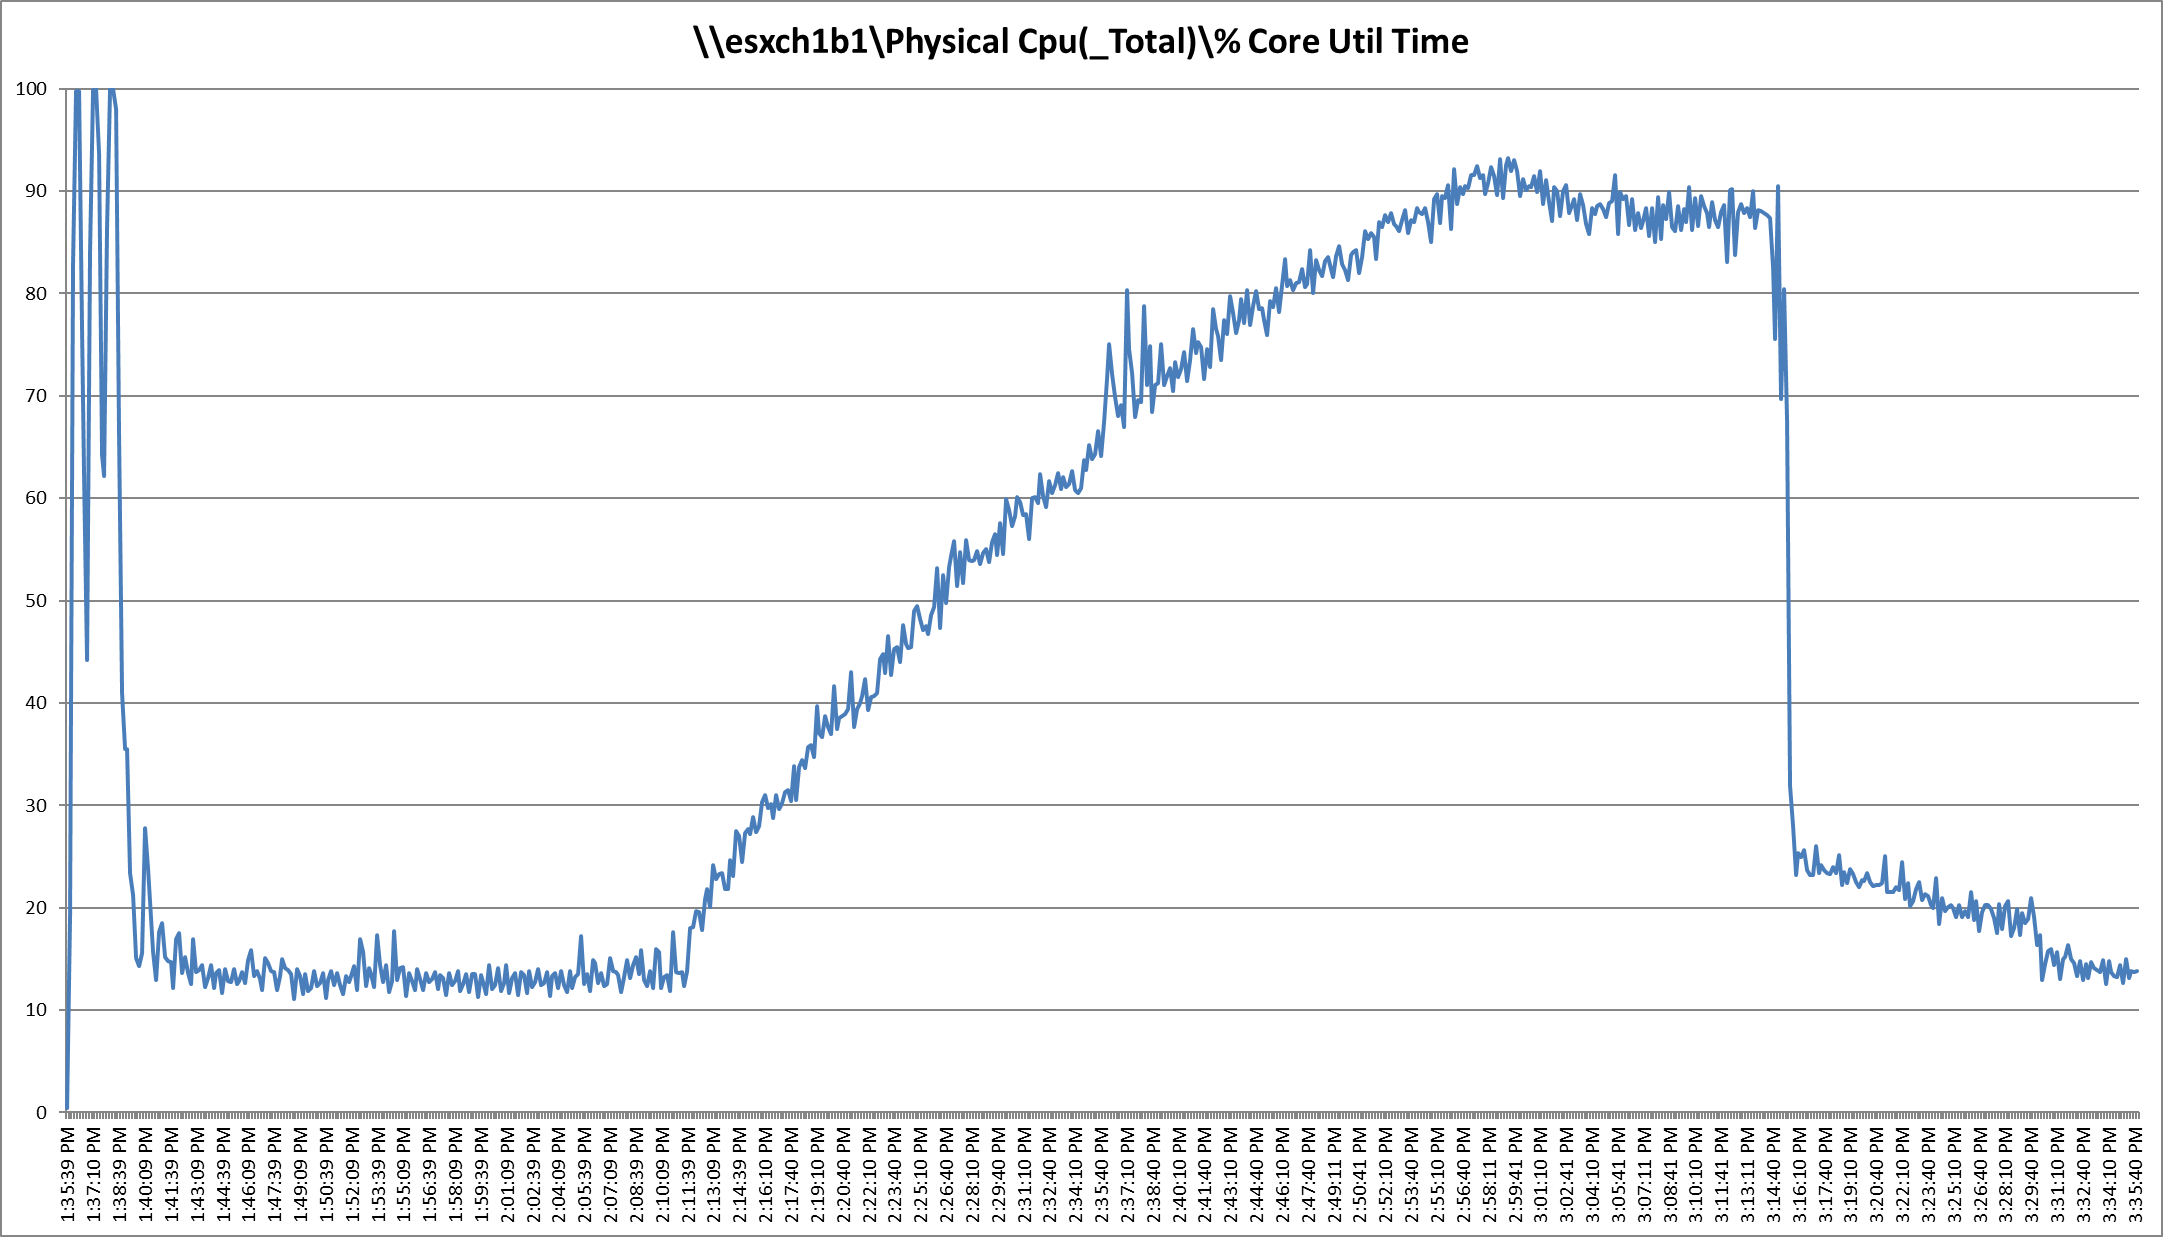
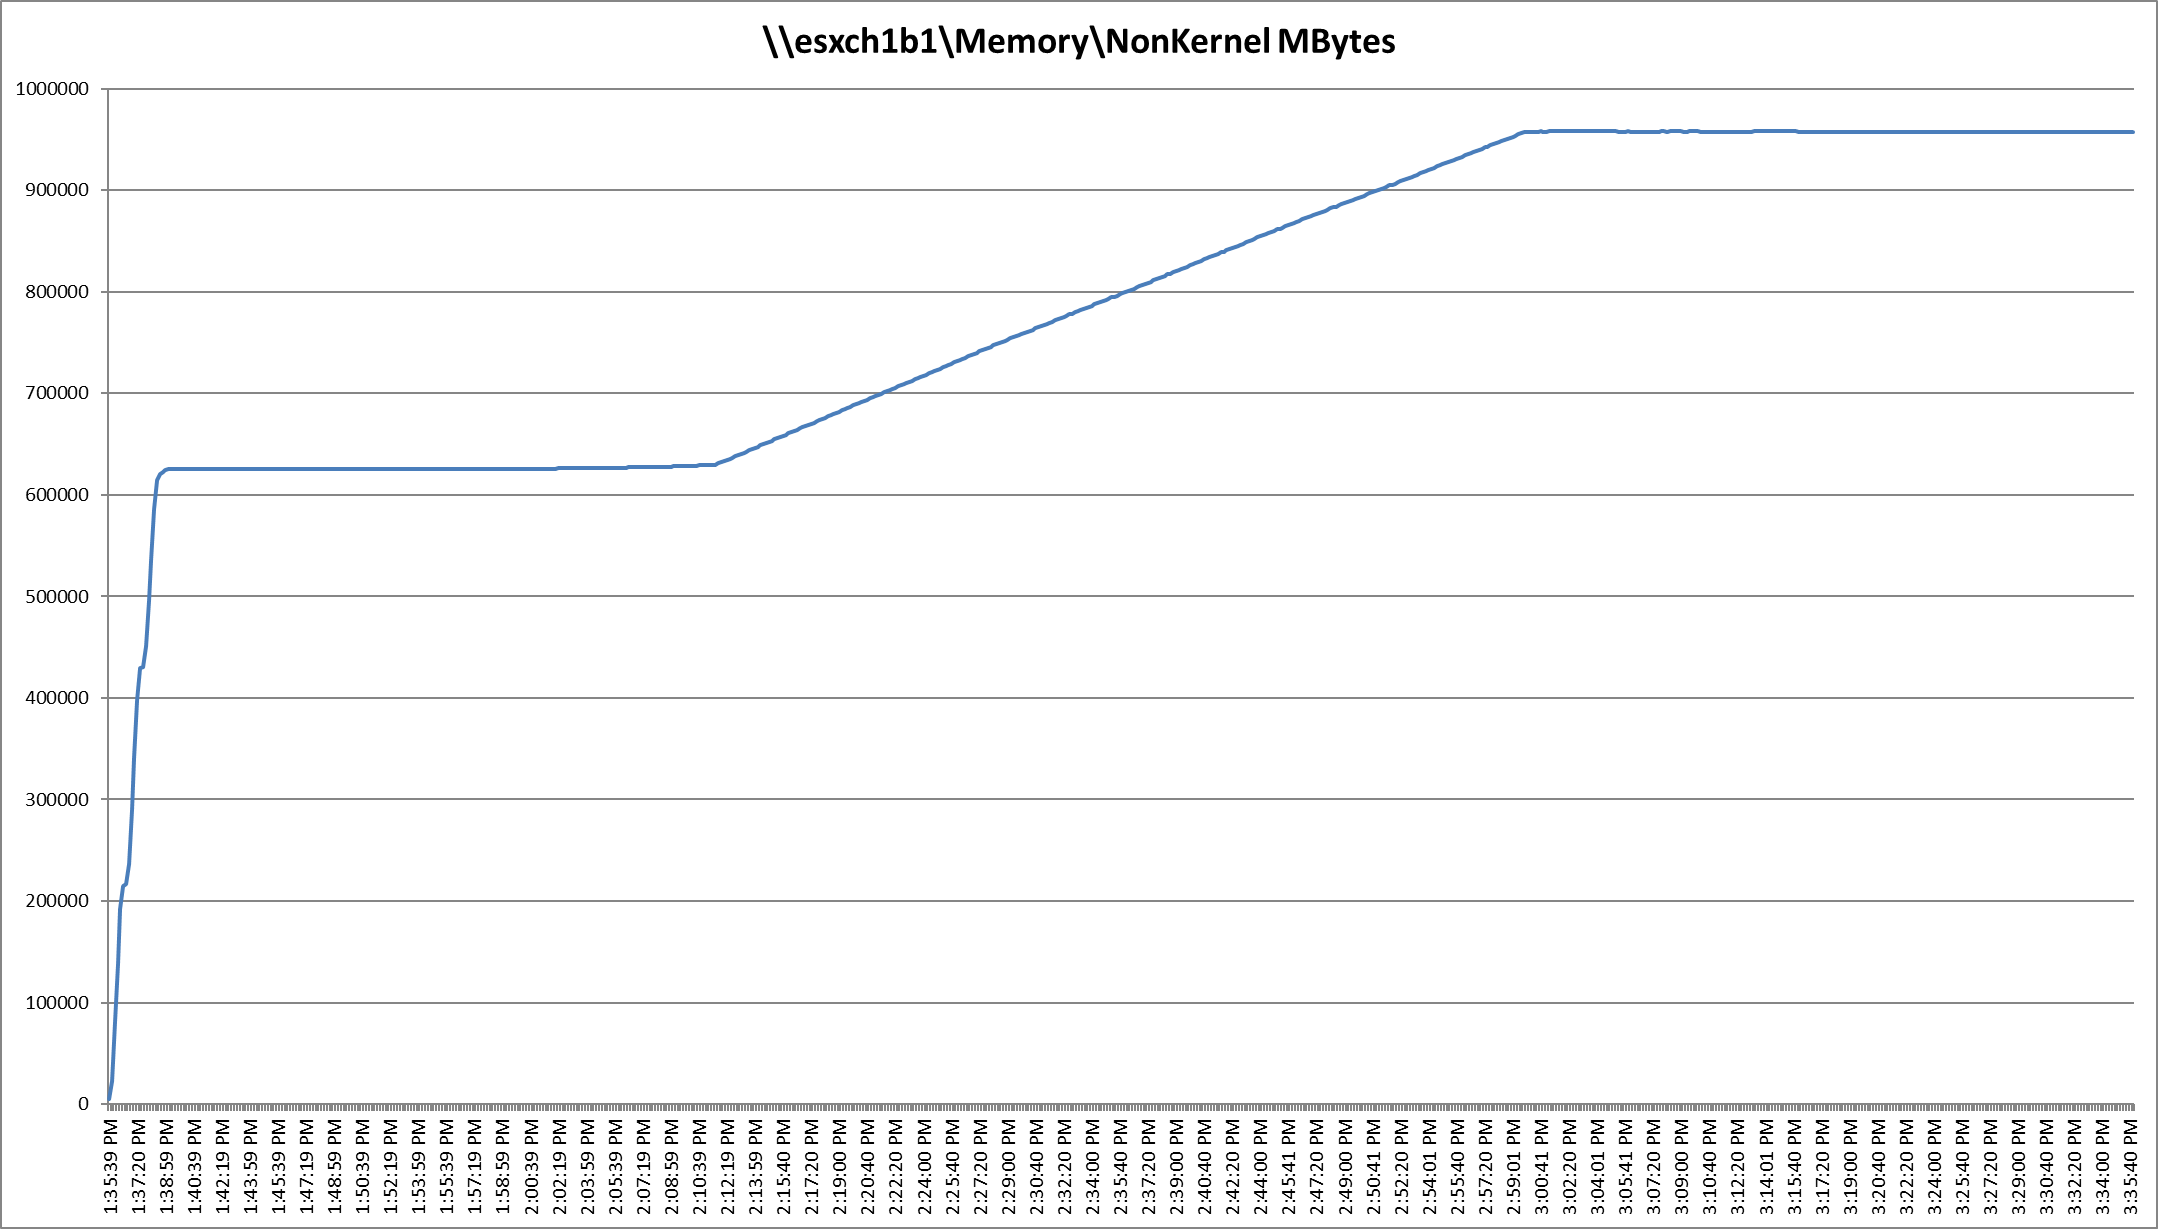
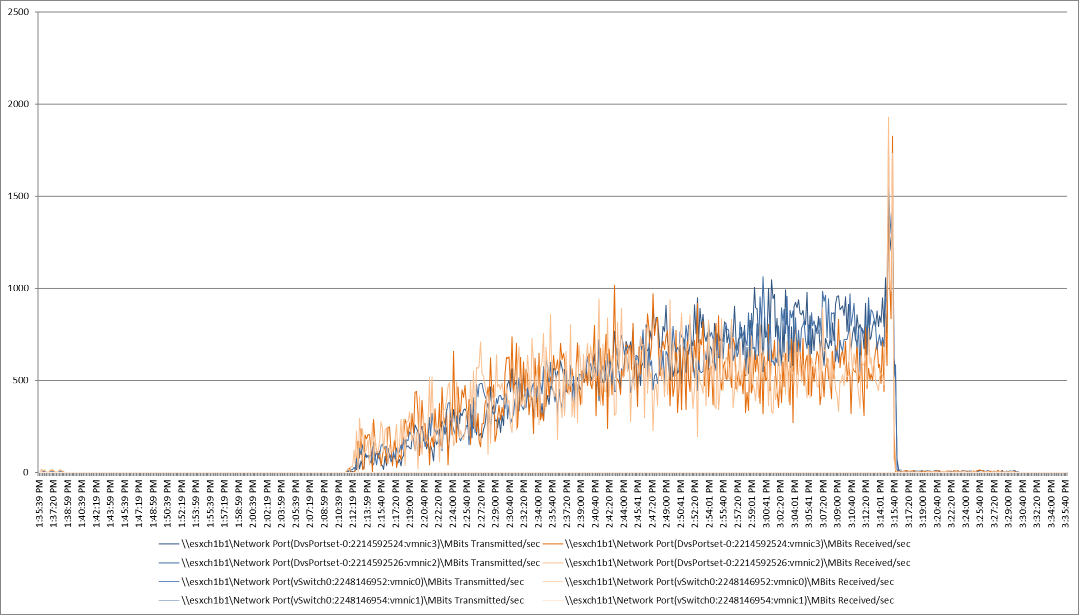
NFS datastore: Single-Server Recommended Maximum Workload for RDS with 384 Users
The recommended maximum workload for a Cisco UCS X215c M8 Compute Node with dual AMD EPYC 9355 processors, 1TB 6400MHz RAM is 384 Server 2022 Hosted Shared Desktop sessions. Each dedicated Compute Node server ran 10 Server 2022 Virtual Machines. Each virtual server was configured with 4 vCPUs and 24GB RAM.
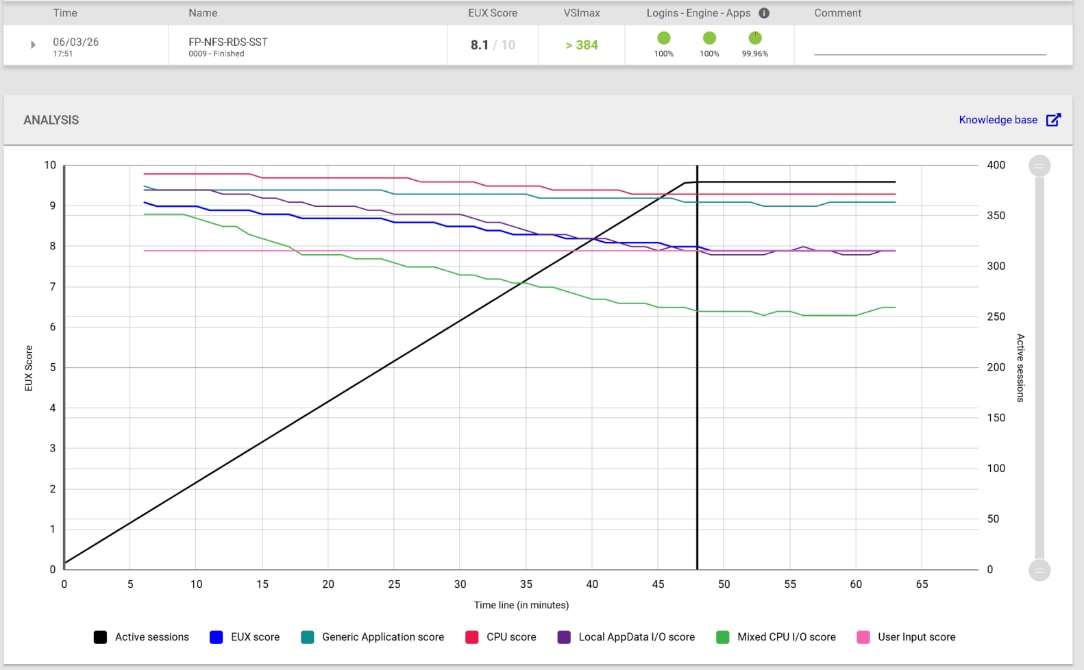
Performance data for the server running the workload as follows:
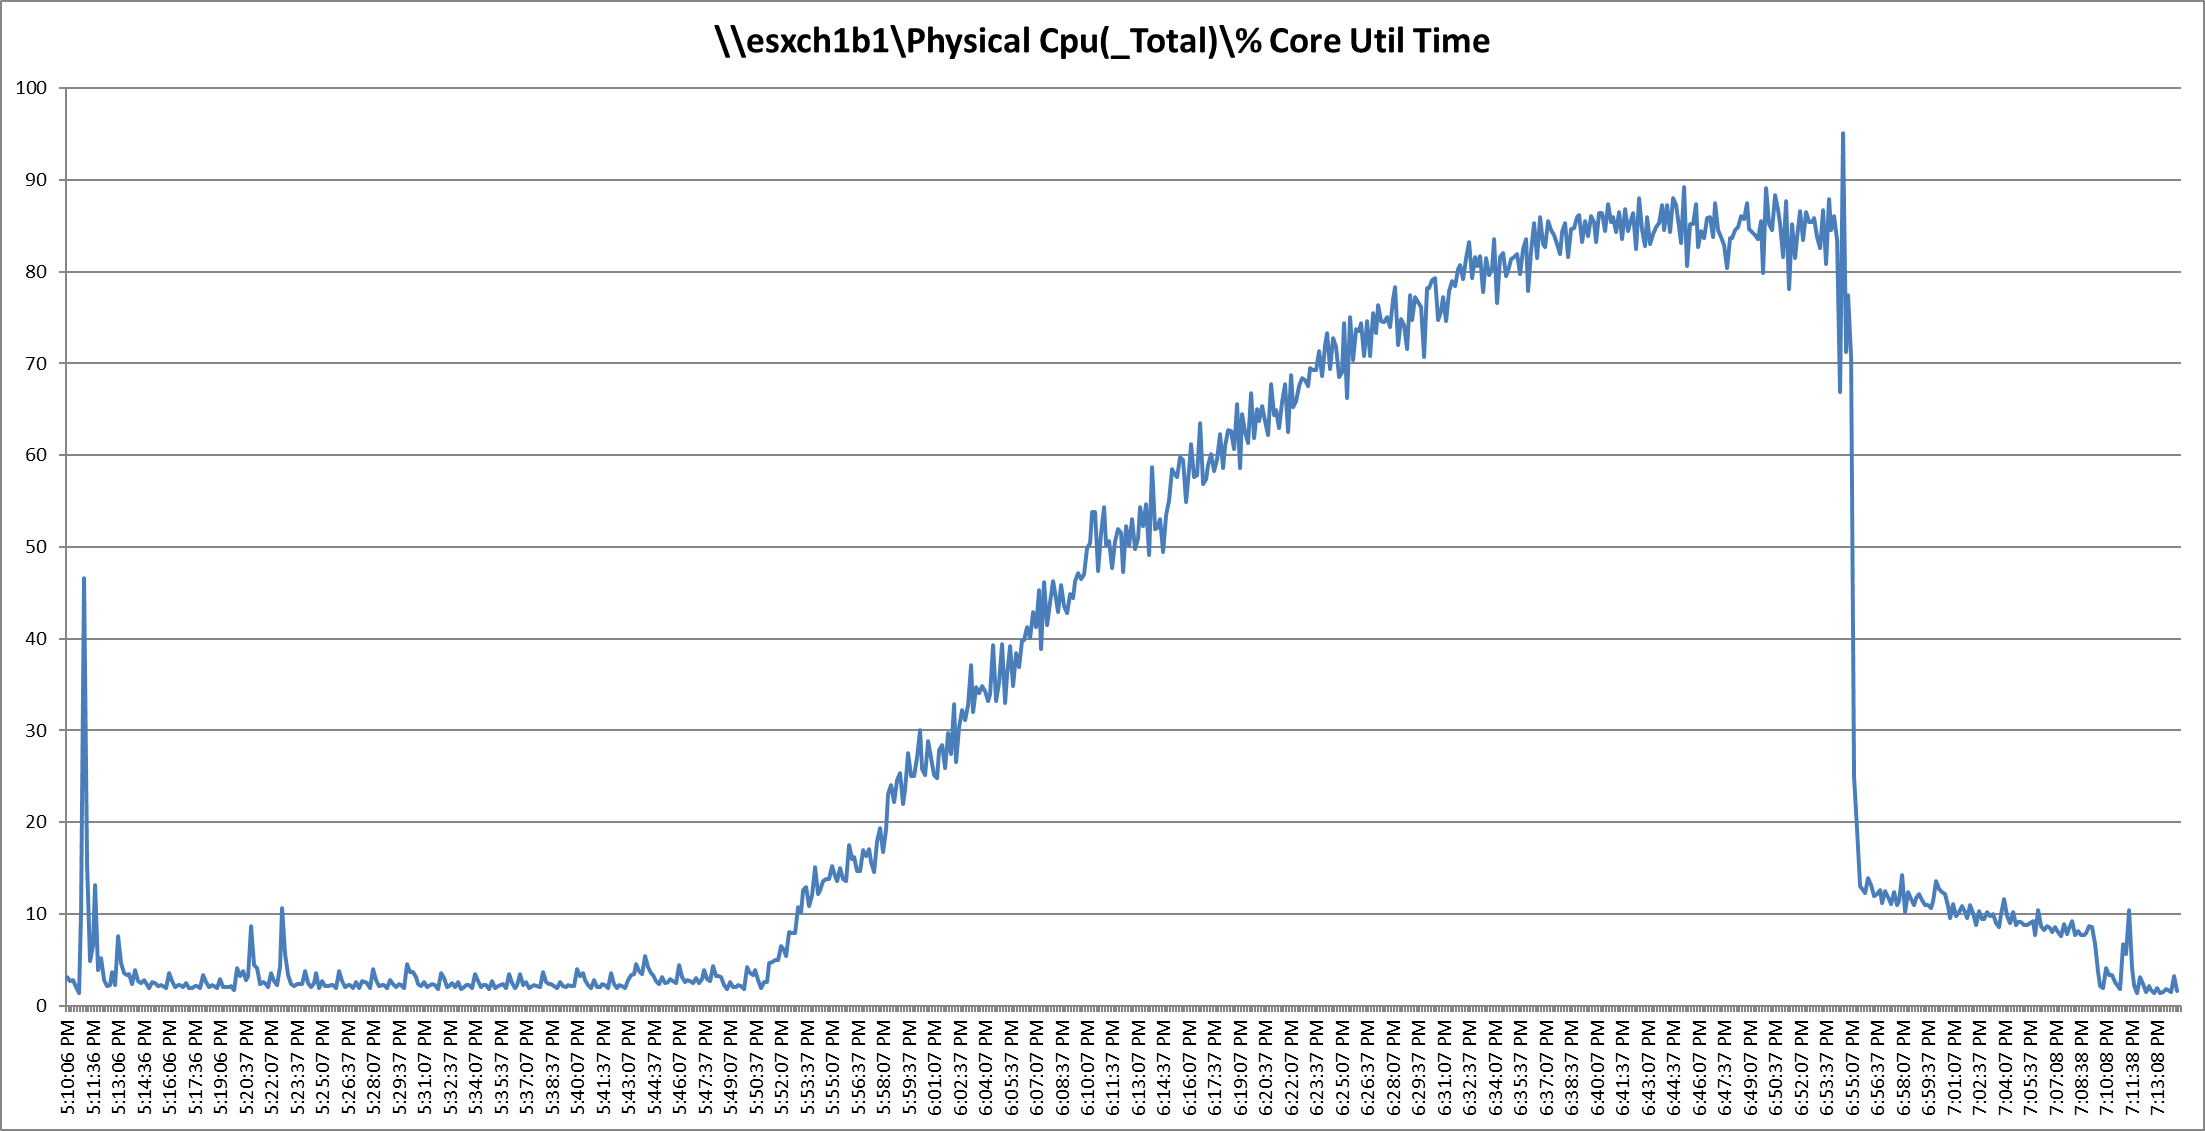
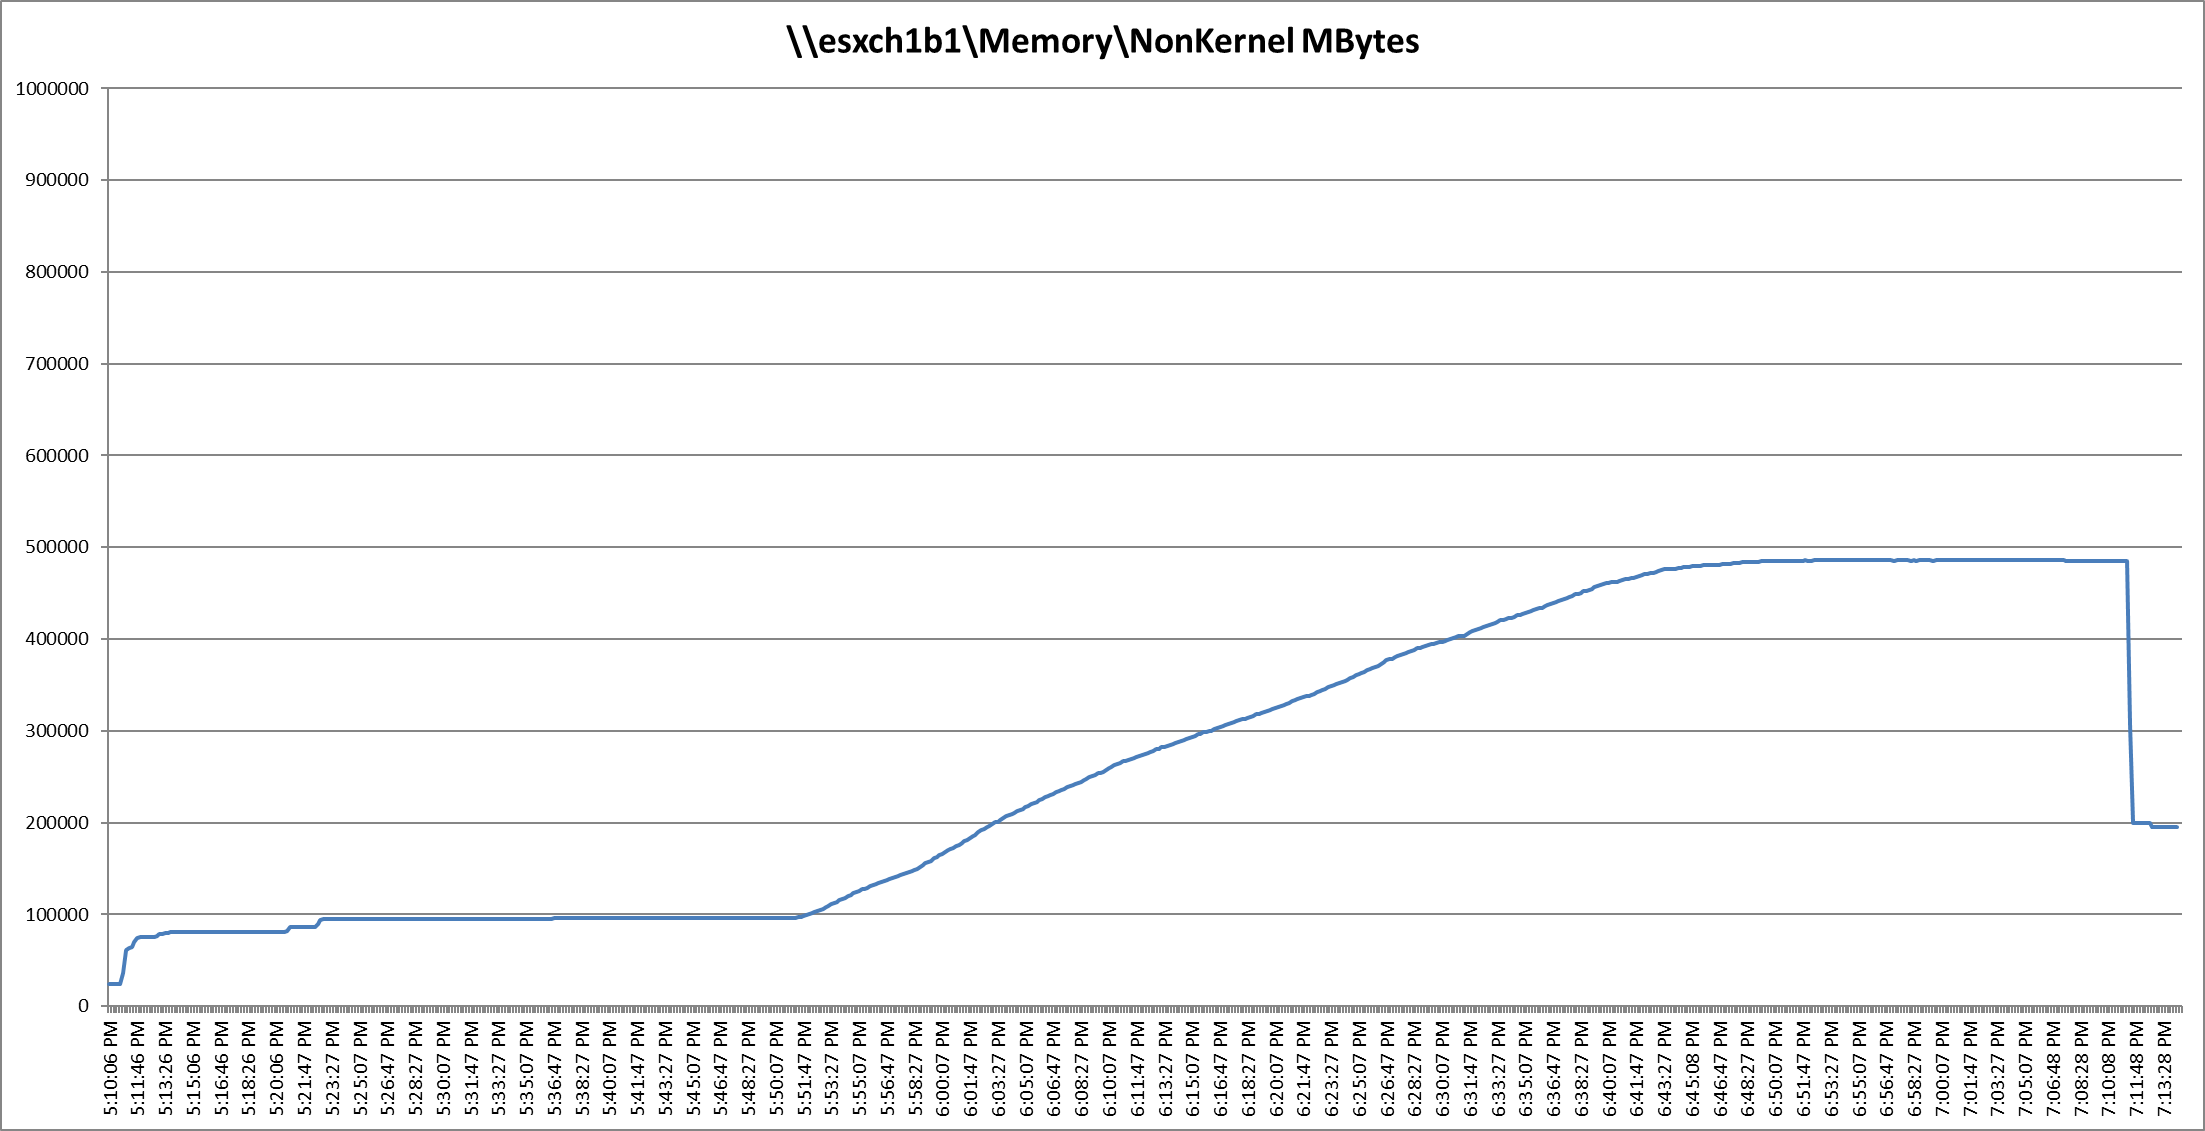
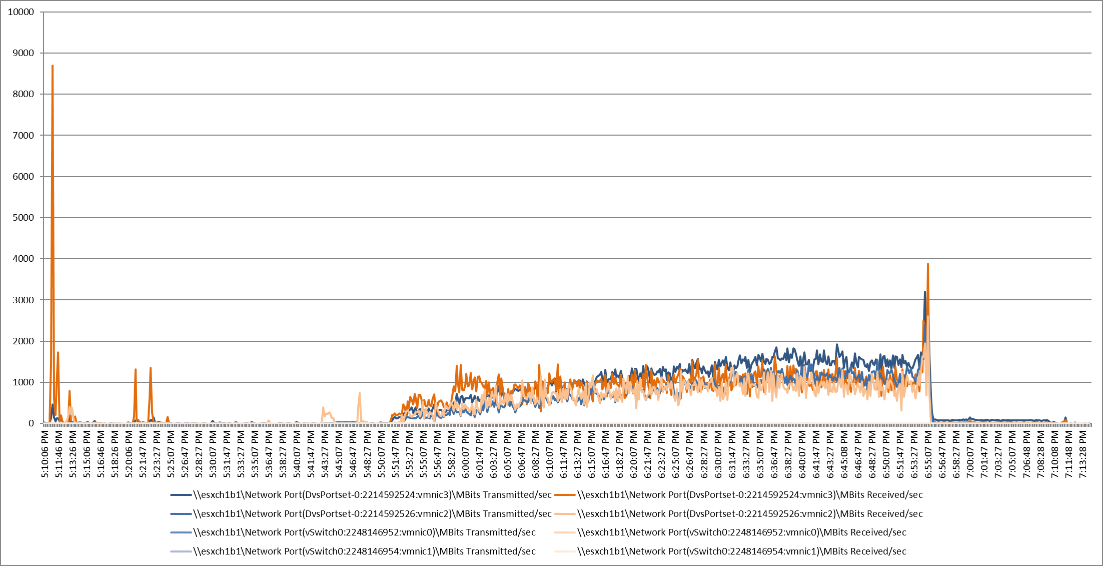
NFS datastore: Single-Server Recommended Maximum Workload for MCS VDI Non-Persistent with 230 Users
The recommended maximum workload for a Cisco UCS X215c M8 Compute Node with dual AMD EPYC 9355 processors, 1TB 6400MHz RAM is 230 Windows 11 64-bit virtual machines with 2 vCPU and 4GB RAM. Login VSI and node performance data as follows:
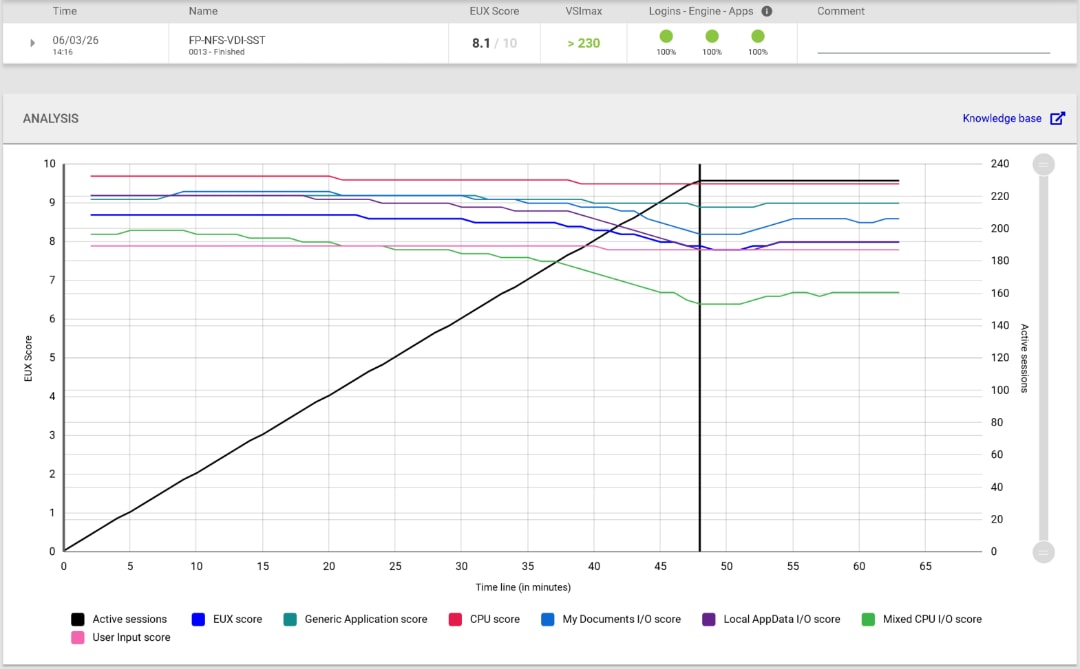
Performance data for the server running the workload as follows:
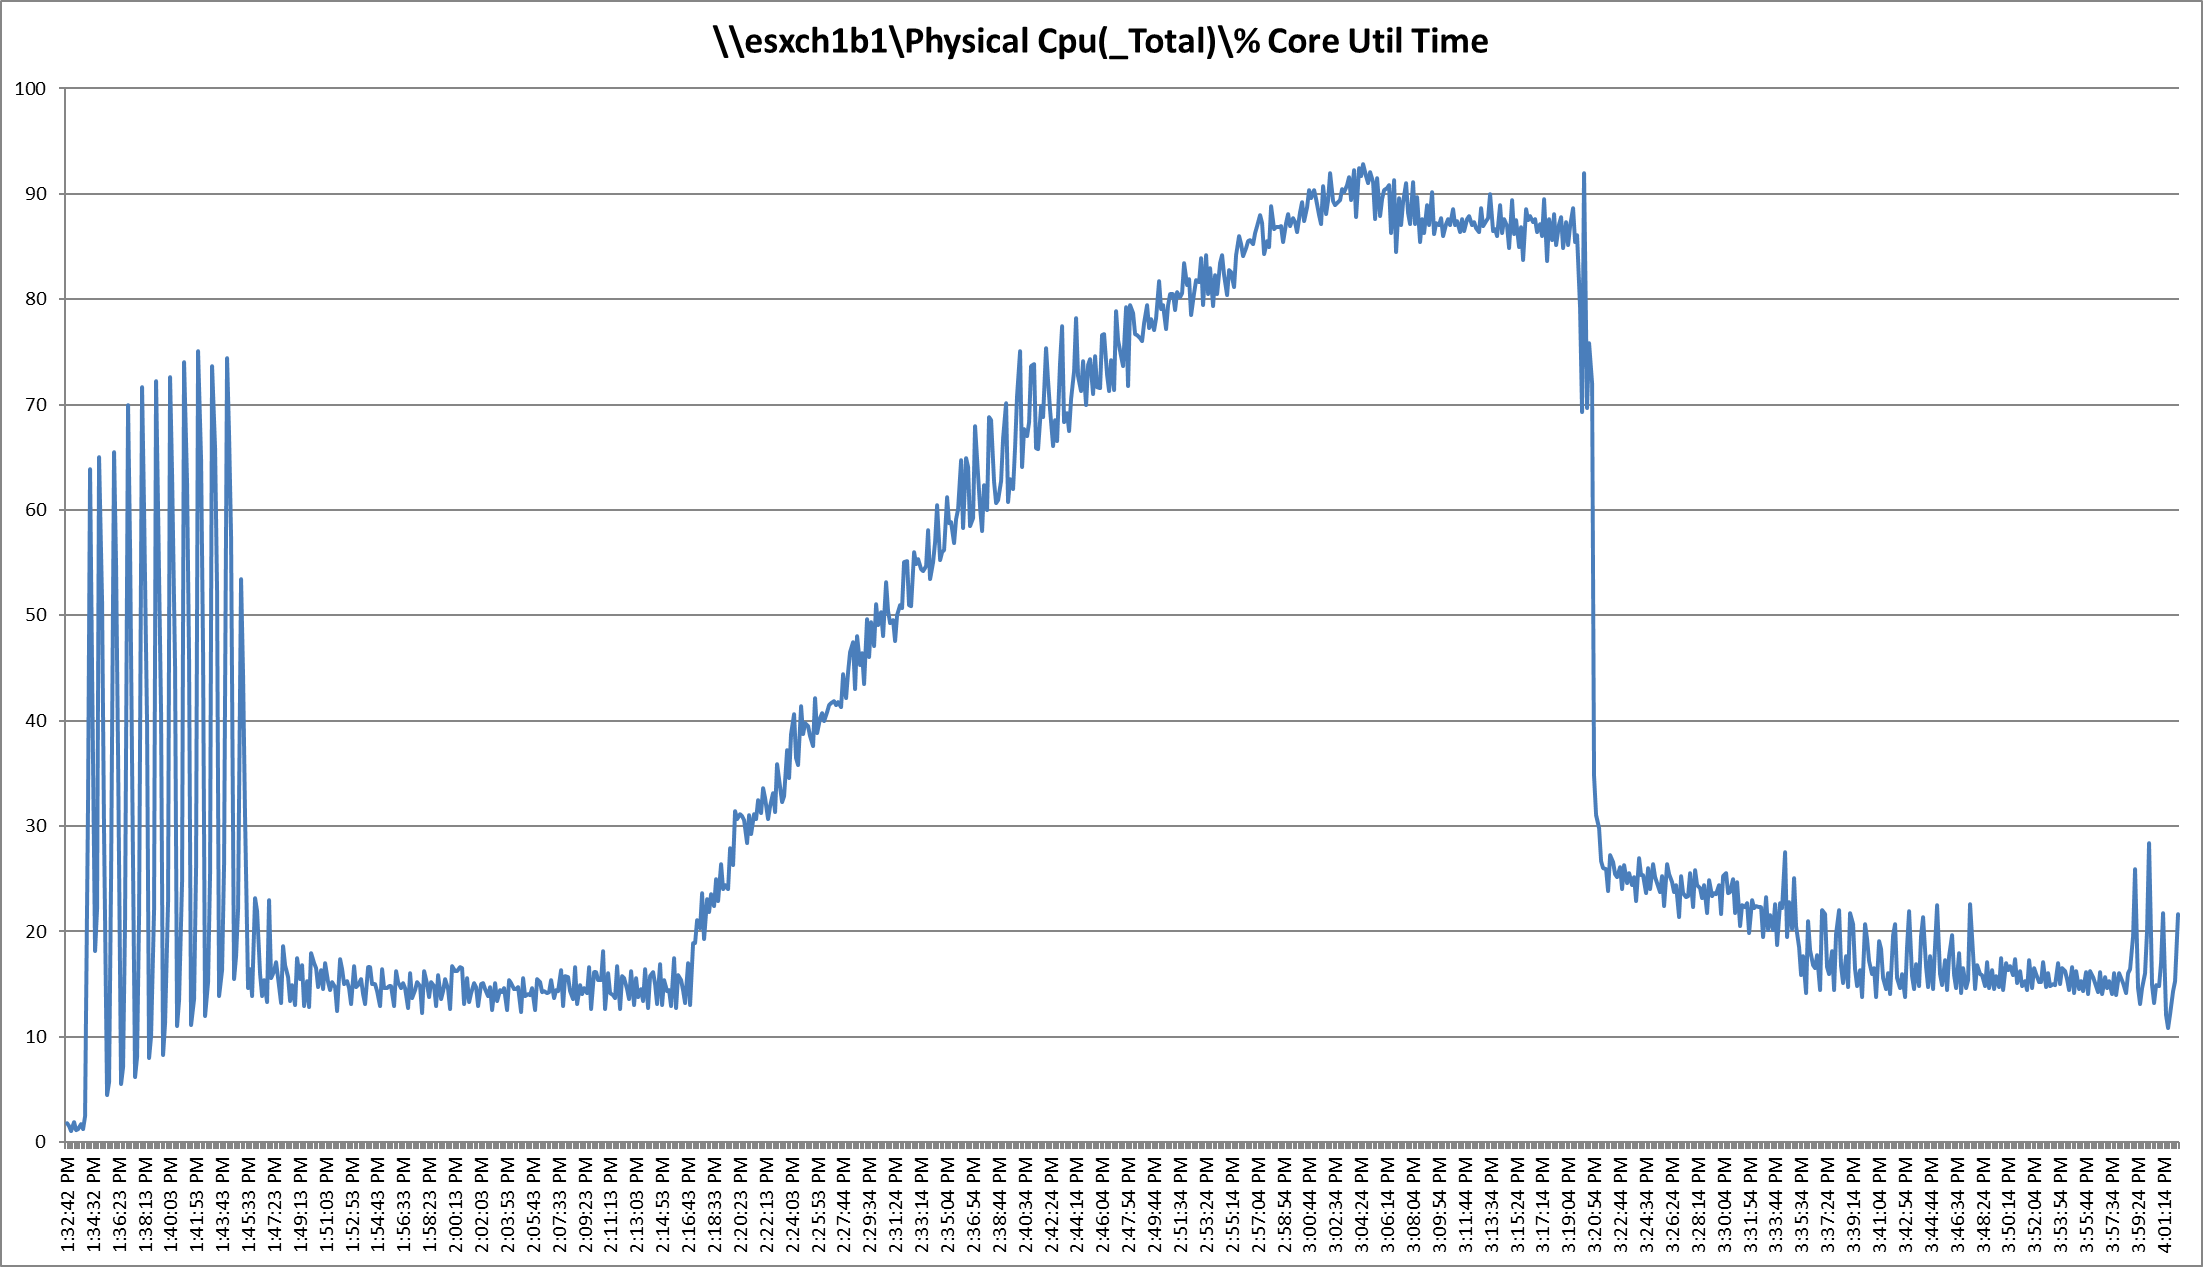
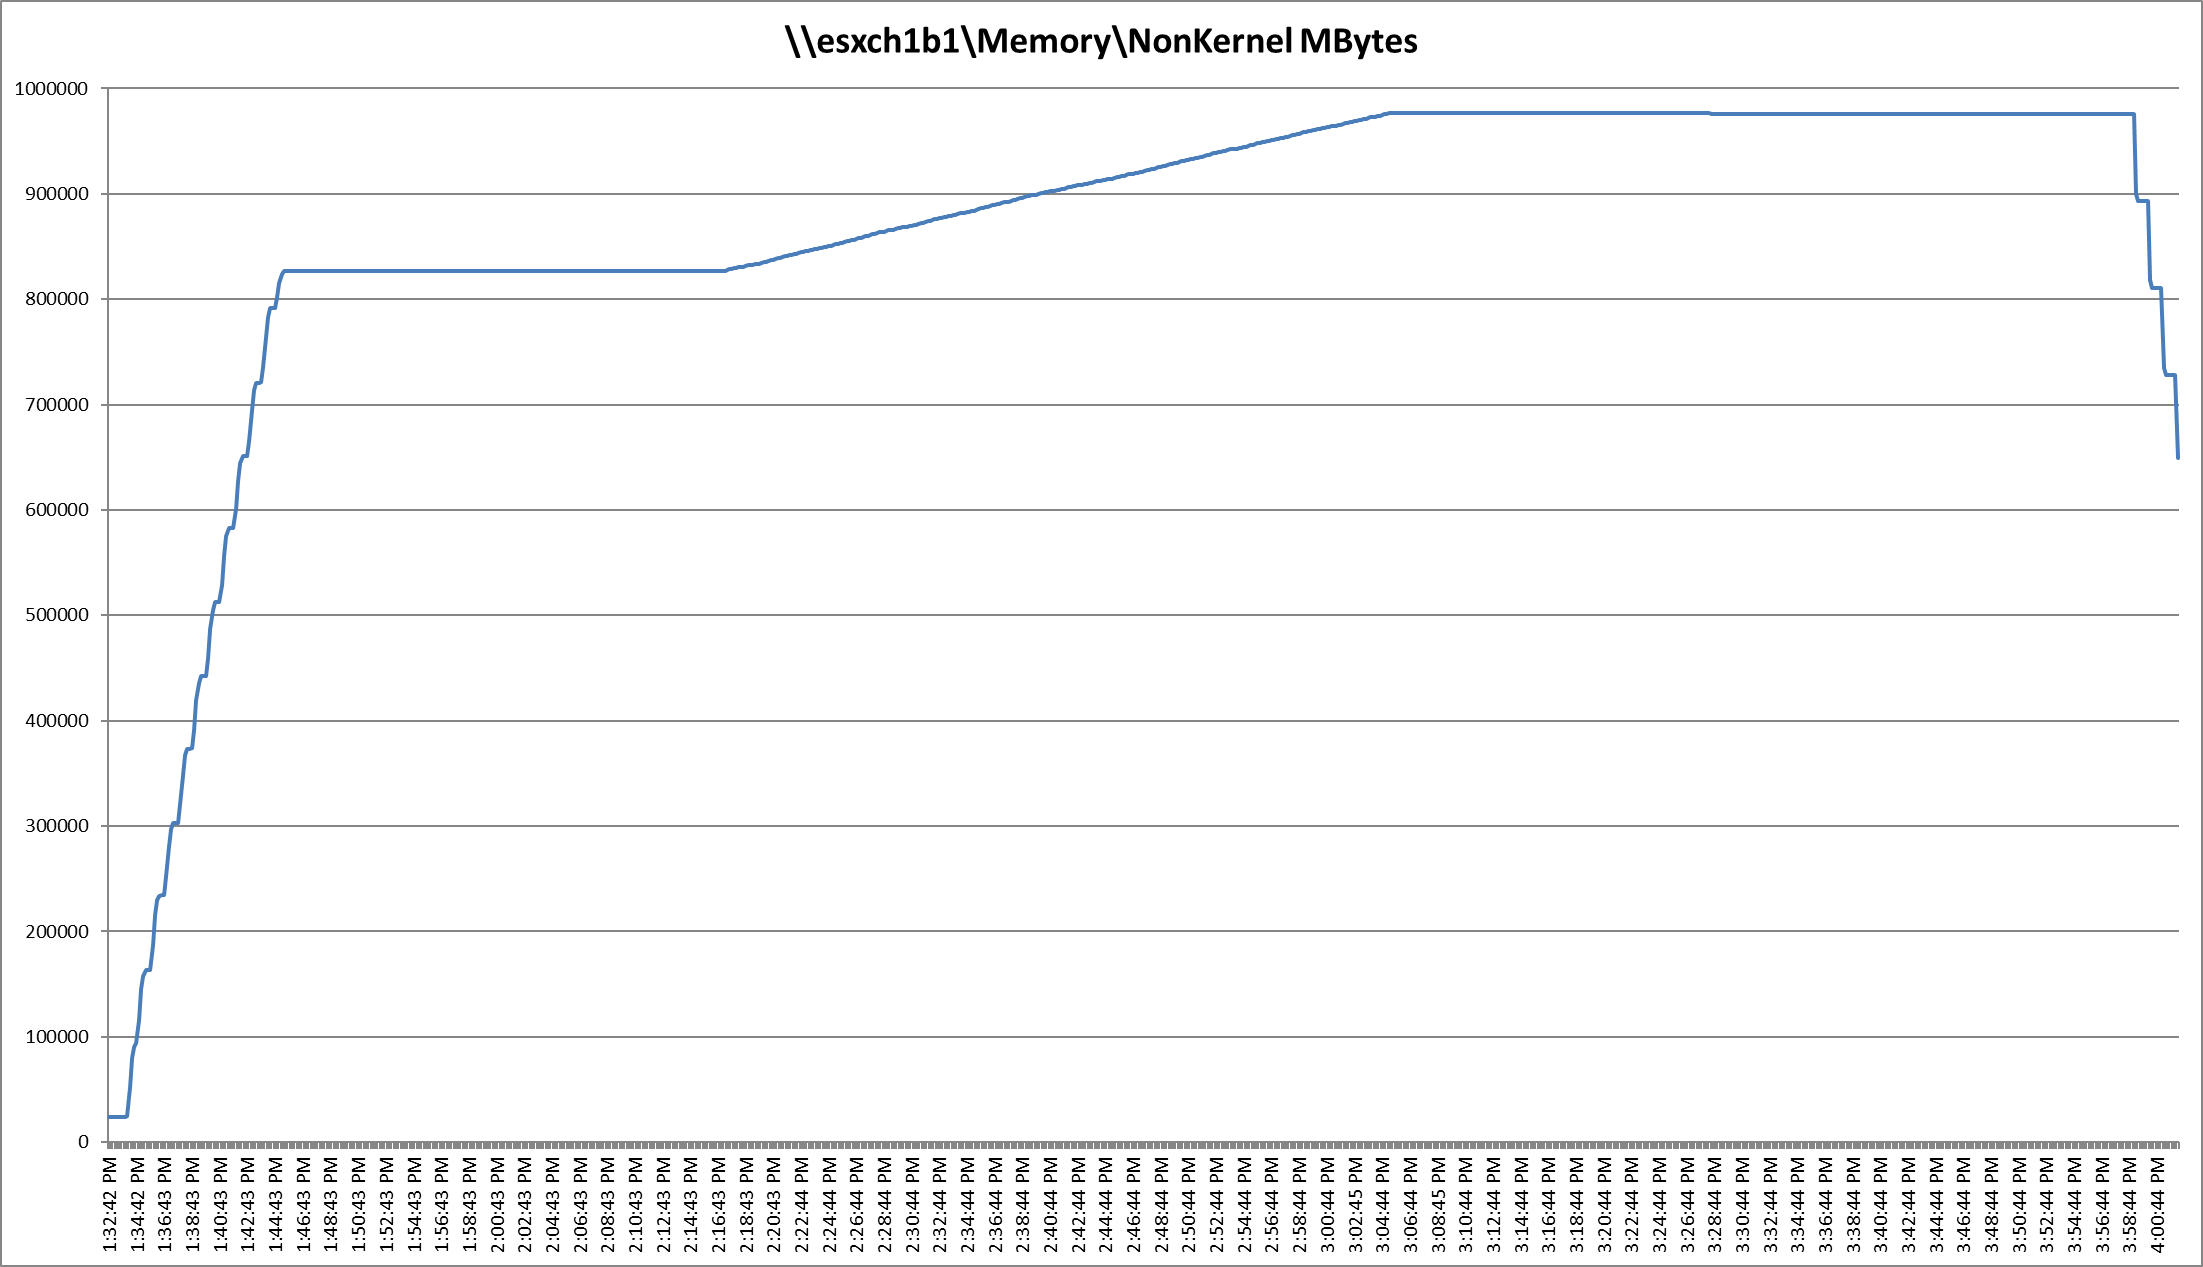
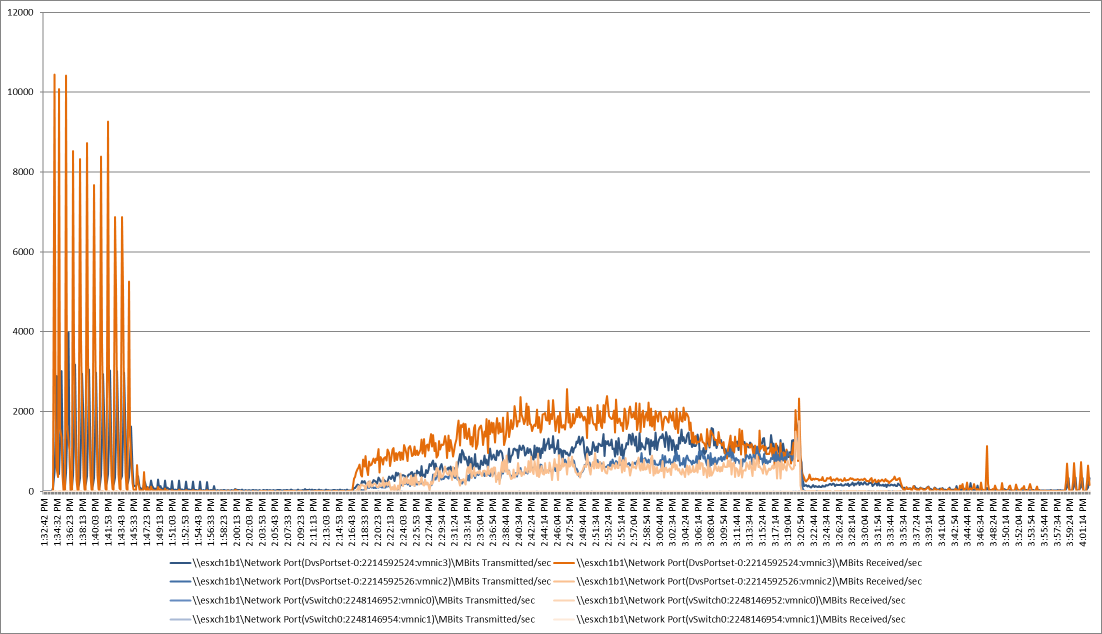
NFS datastore: Single-Server Recommended Maximum Workload for PVS VDI Non-Persistent with 230 Users
The recommended maximum workload for a Cisco UCS X215c M8 Compute Node with dual AMD EPYC 9355 processors, 1TB 6400MHz RAM is 230 Windows 11 64-bit virtual machines with 2 vCPU and 4GB RAM. Login VSI and node performance data as follows:
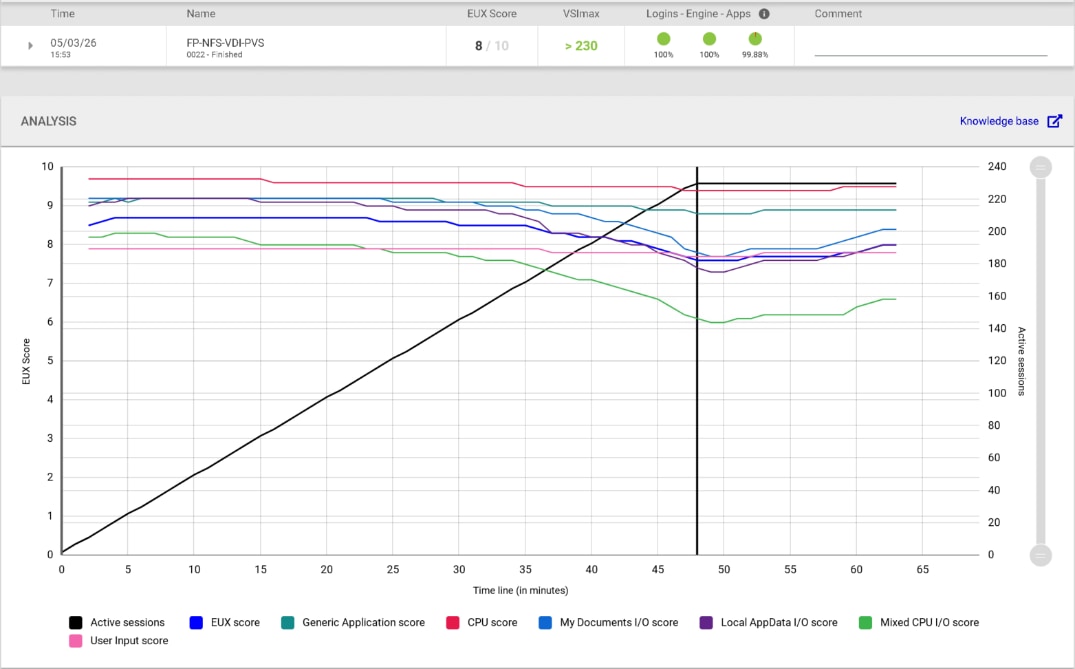
Performance data for the server running the workload as follows:
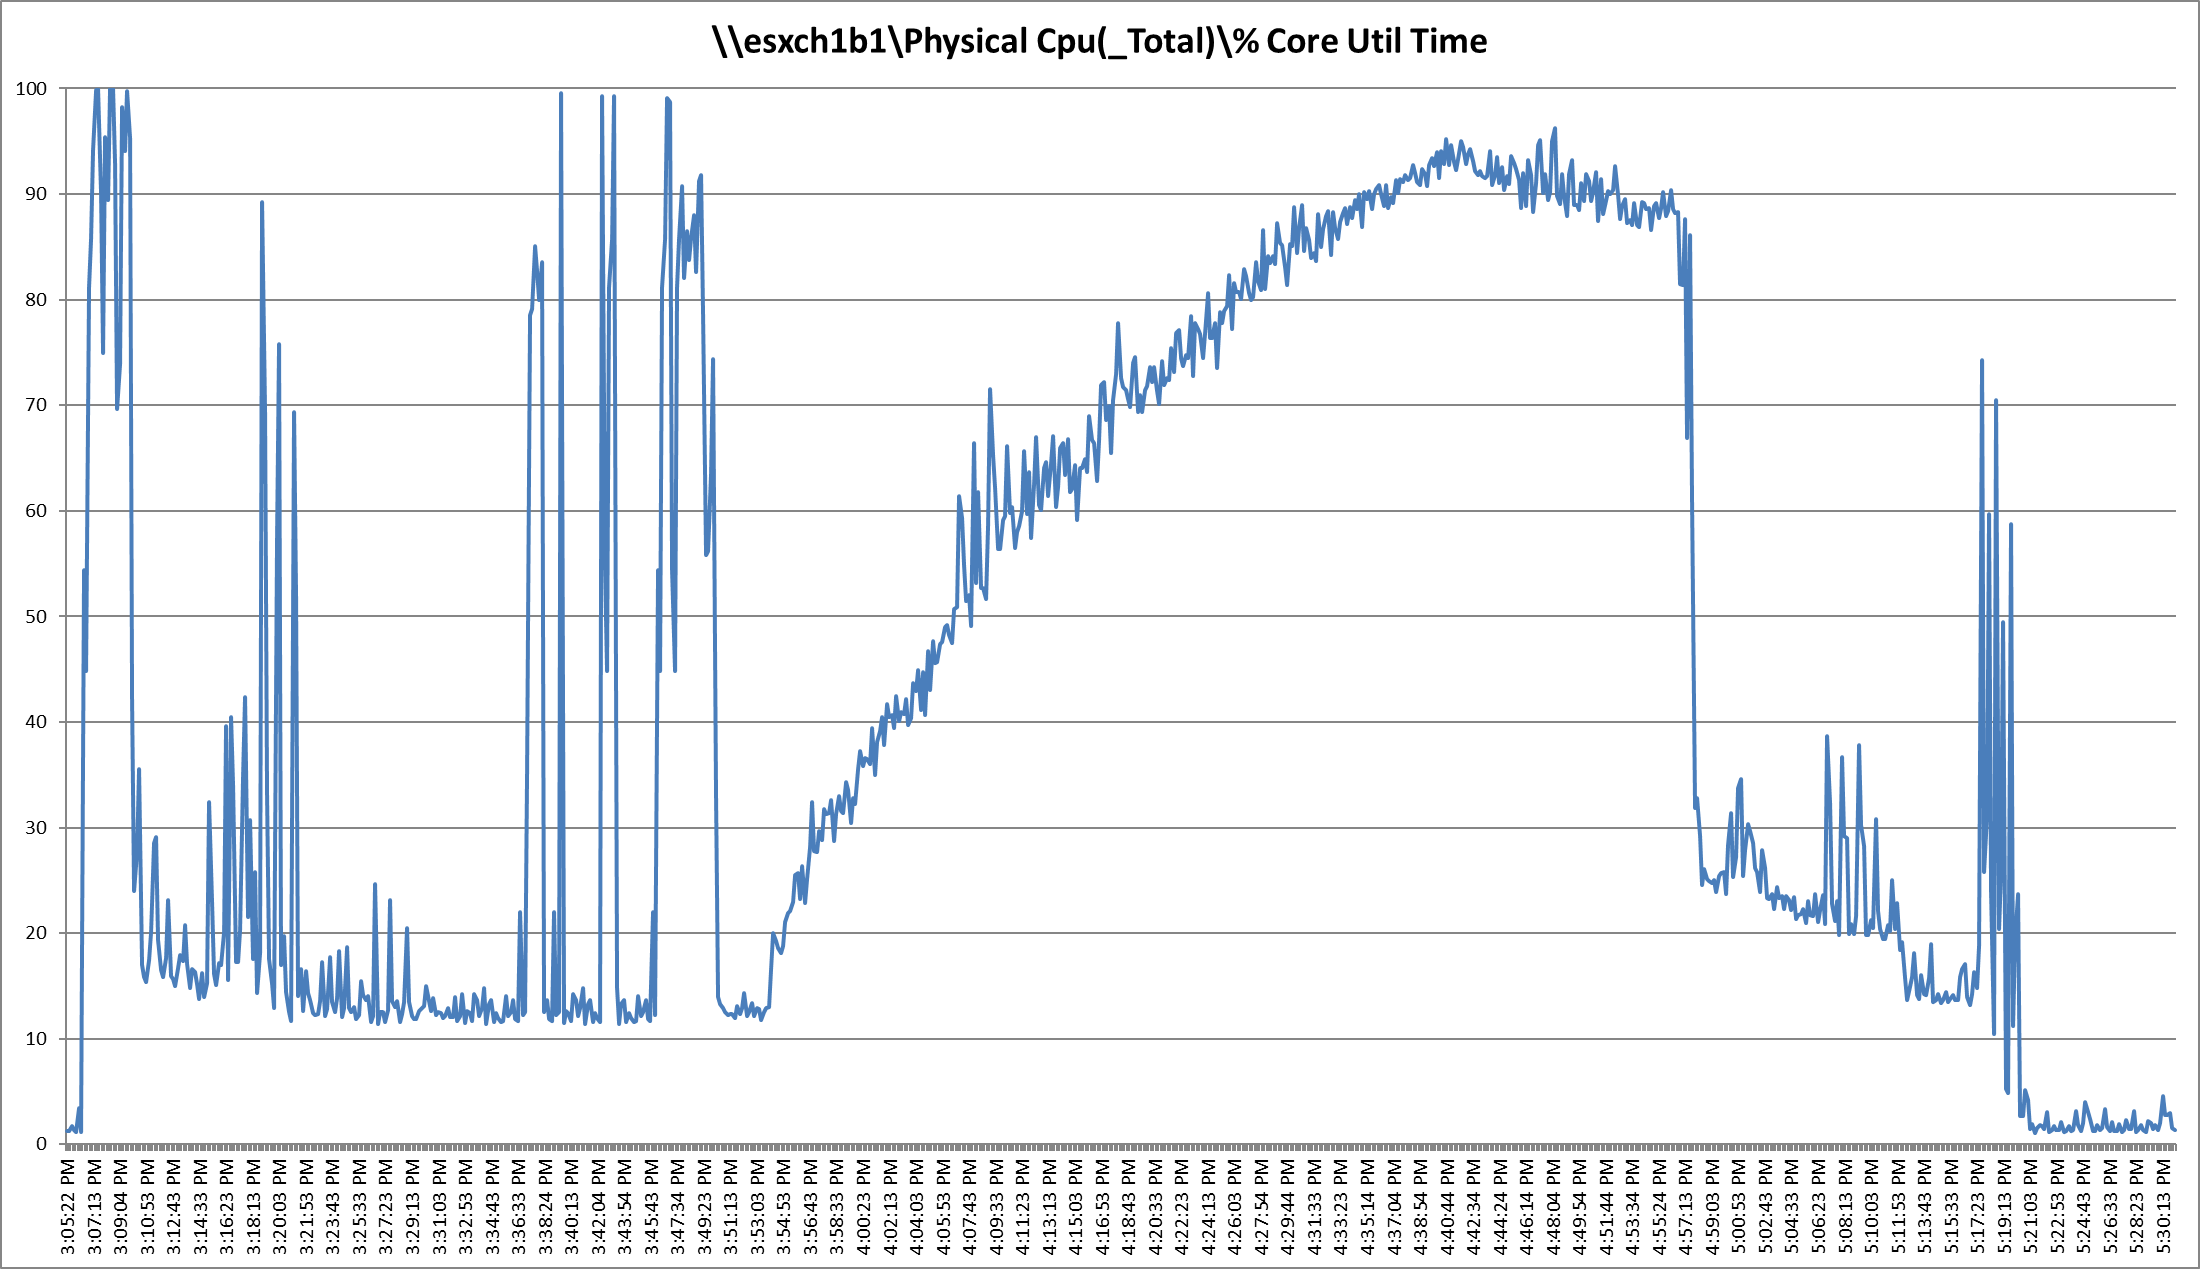
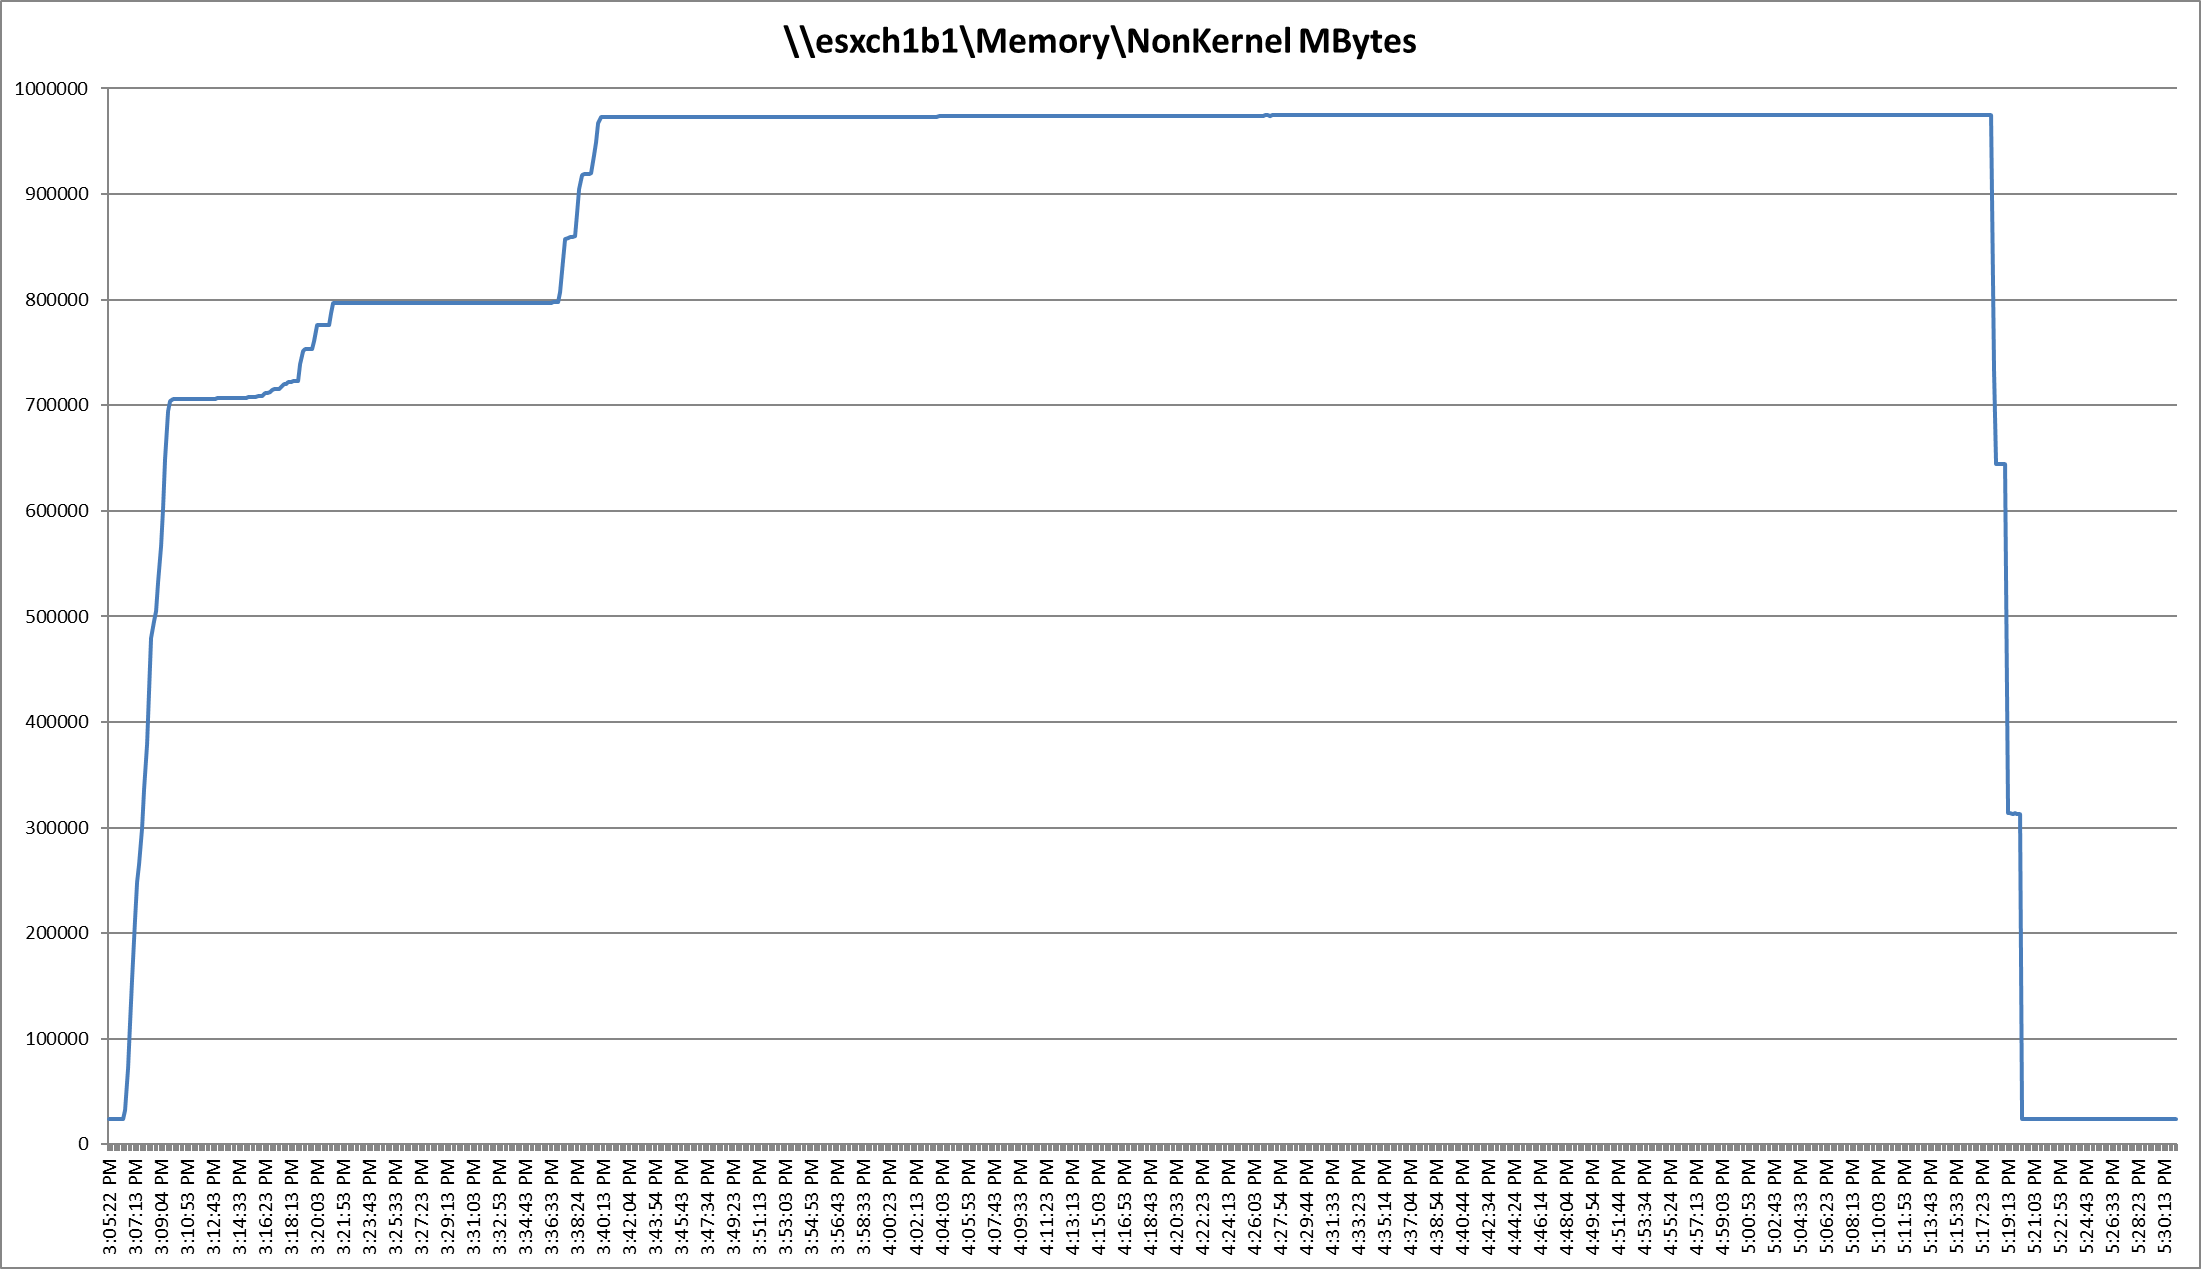
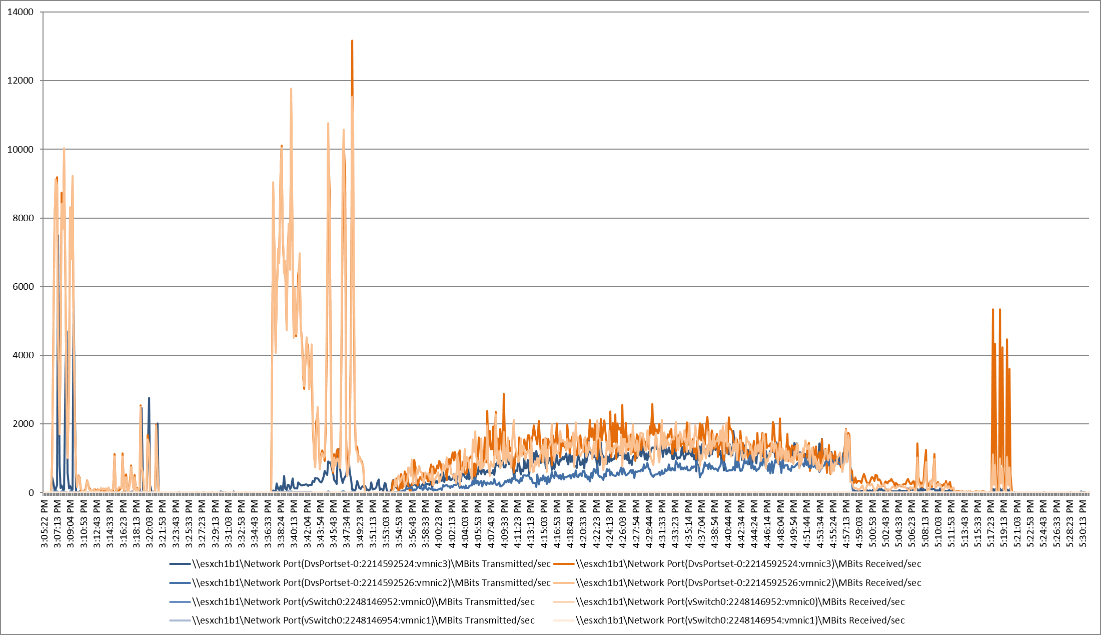
NFS datastore: Single-Server Recommended Maximum Workload for VDI Persistent with 230 Users
The recommended maximum workload for a Cisco UCS X215c M8 Compute Node with dual AMD EPYC 9355 processors, 1TB 6400MHz RAM is 230 Windows 11 64-bit virtual machines with 2 vCPU and 4GB RAM. Login VSI and Compute Node performance data as follows:
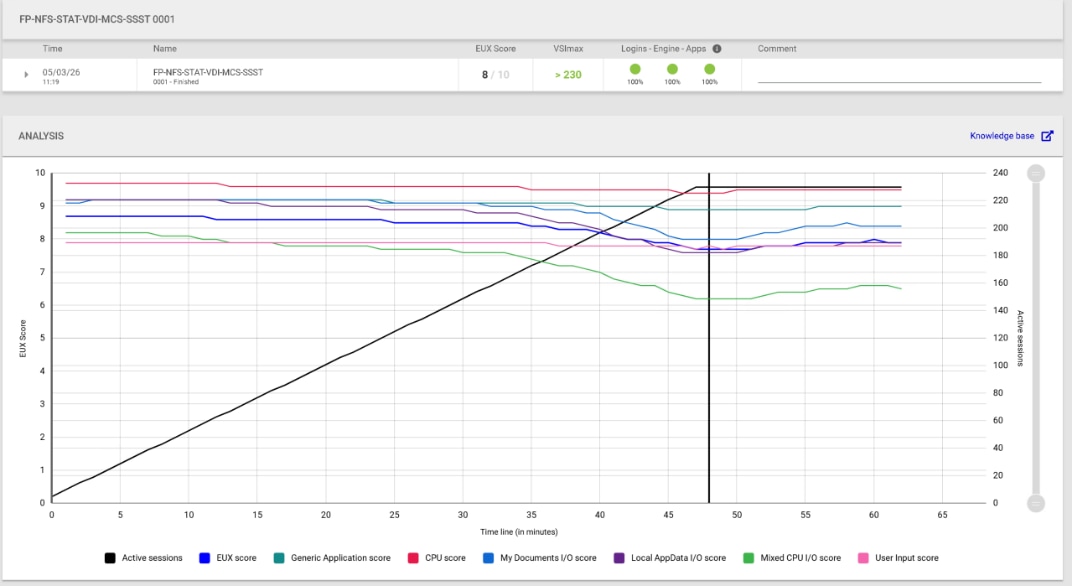
Performance data for the server running the workload as follows:
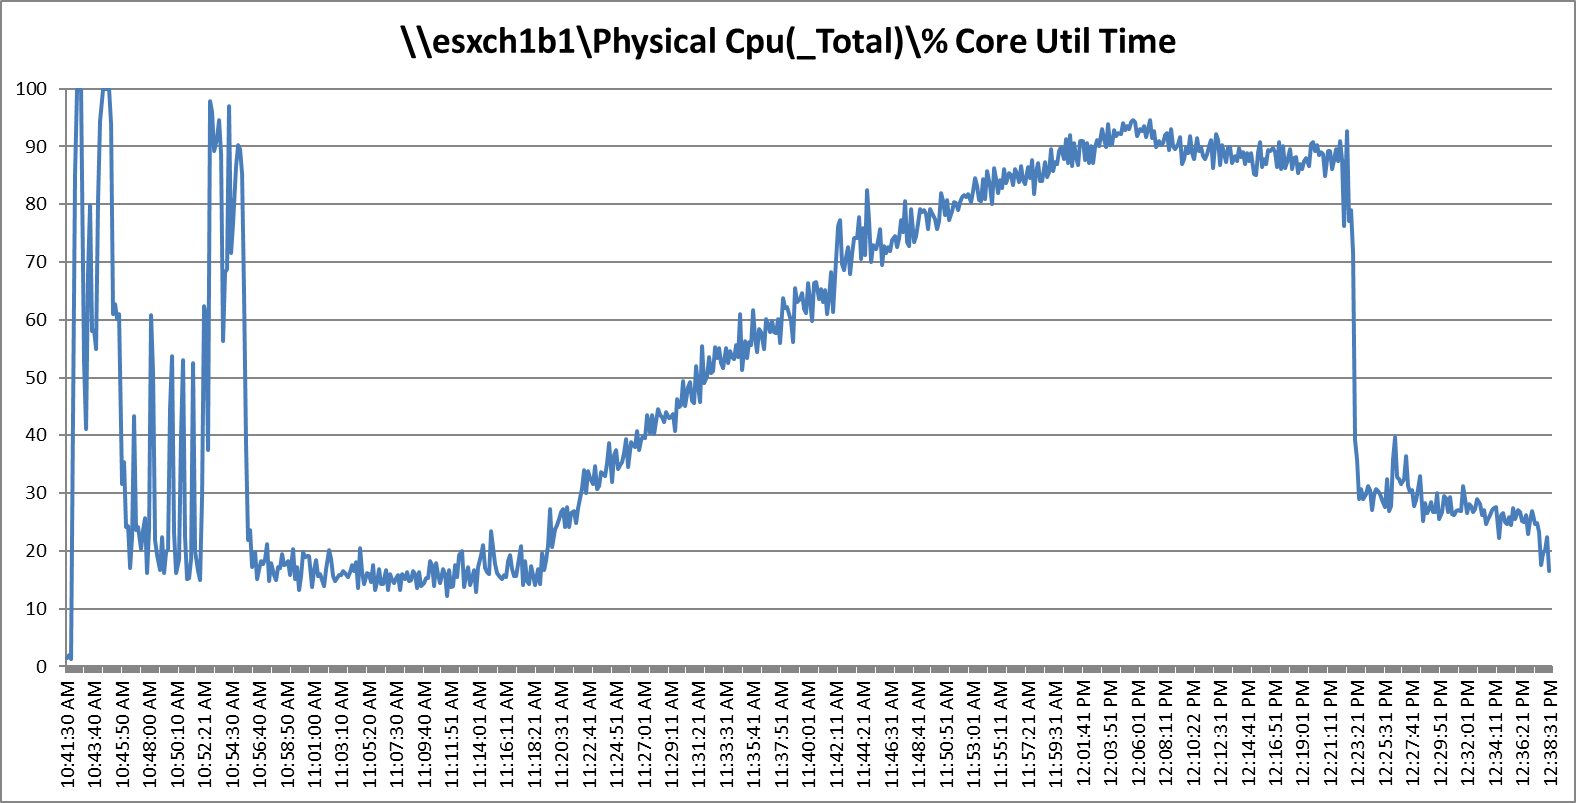
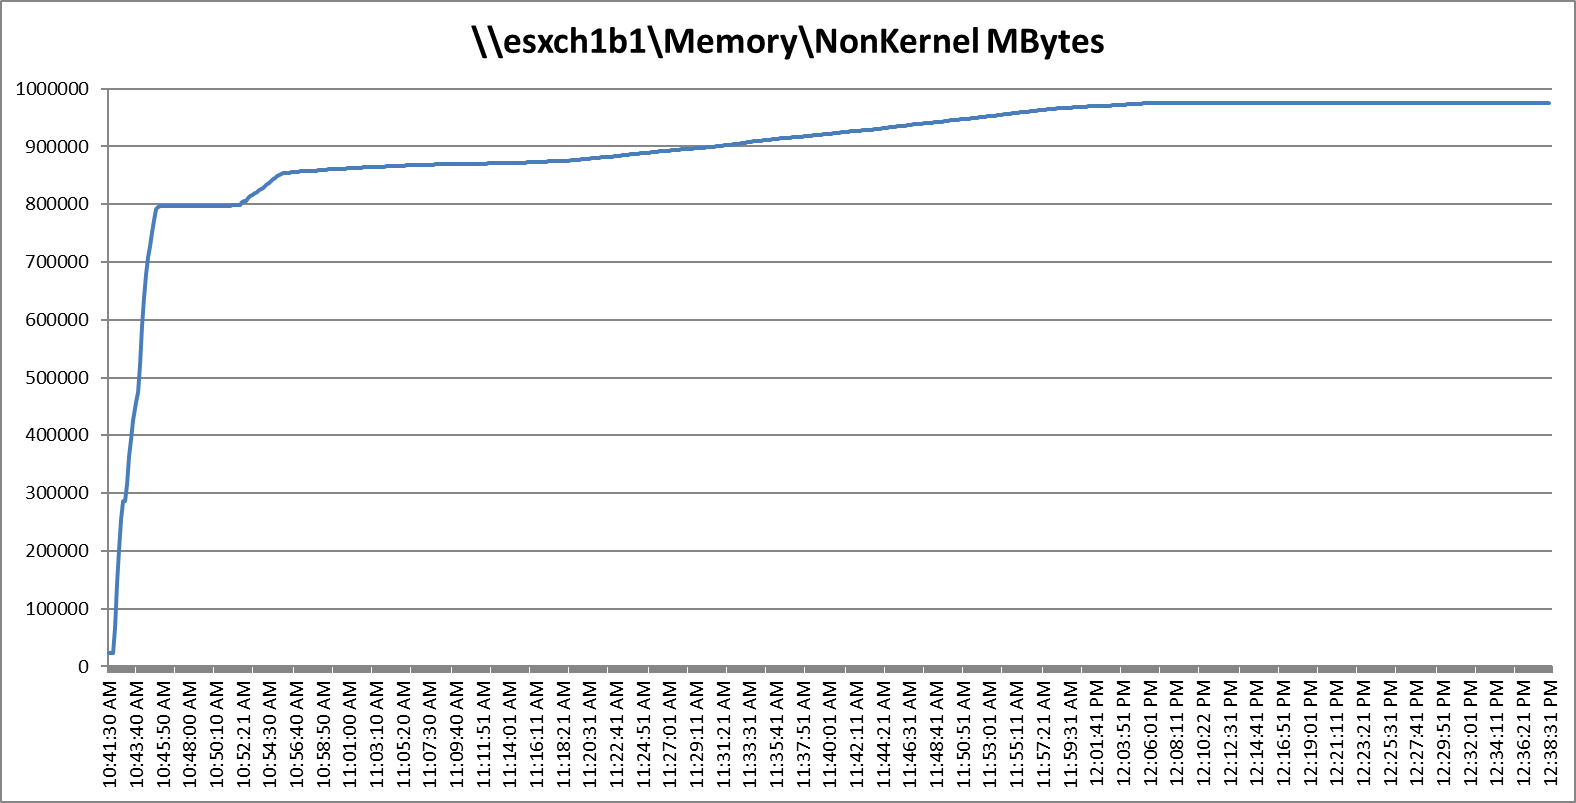
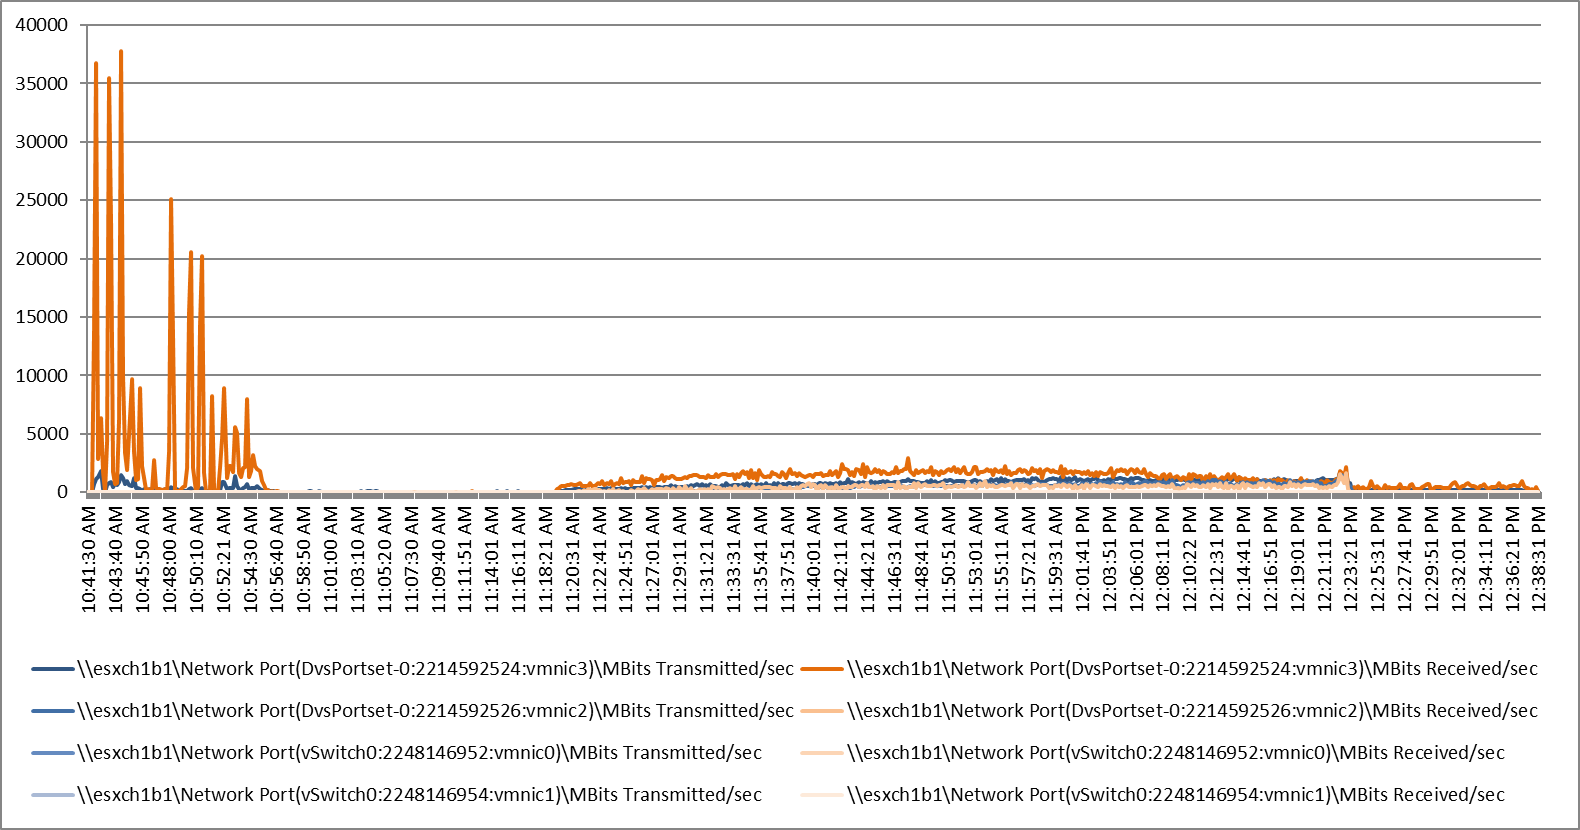
Full-Scale Workload Testing
This section details the key performance metrics captured on the Cisco UCS platform during full-scale testing. The testing used an 8-compute-node cluster configured for N+1 redundancy, leveraging either four Fibre Channel or four NFS datastores to validate this Citrix CVAD solution.
Fibre channel datastore: Full-Scale RDS Workload Testing with 2600 Users
This section shows the key performance metrics that were captured on the Cisco UCS, during the full-scale testing. The full-scale testing with 2688 users comprised of: 2688 Hosted Shared Desktop Sessions using eight compute nodes deployed with MCS on four NFS datastores.
The combined mixed workload for the solution is 2688 users. To achieve the target, sessions were launched against all workload clusters concurrently. As per the Cisco Test Protocol for VDI solutions, all sessions were launched within 48 minutes (using the official Knowledge Worker Workload in VSI Benchmark Mode) and all launched sessions became active within two minutes subsequent to the last logged in session
The configured system efficiently and effectively delivered the following results.
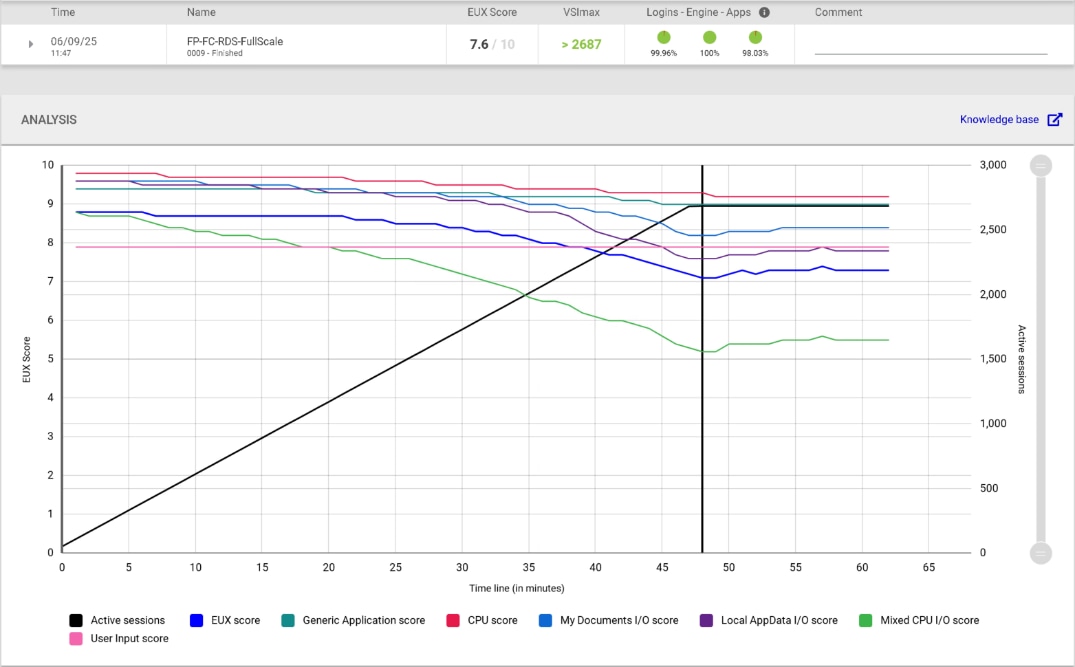
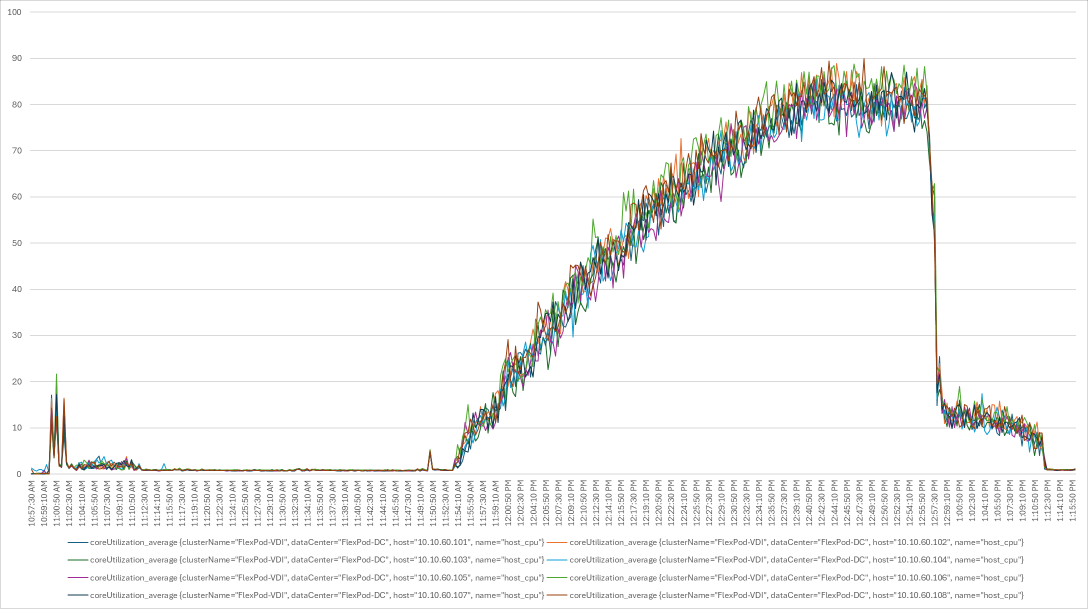
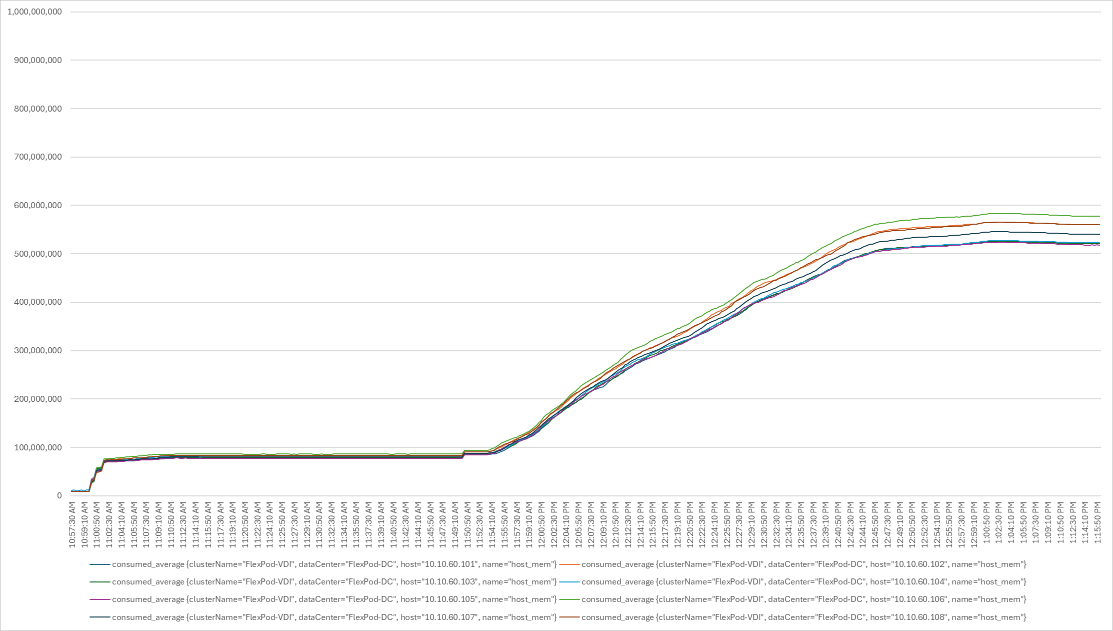
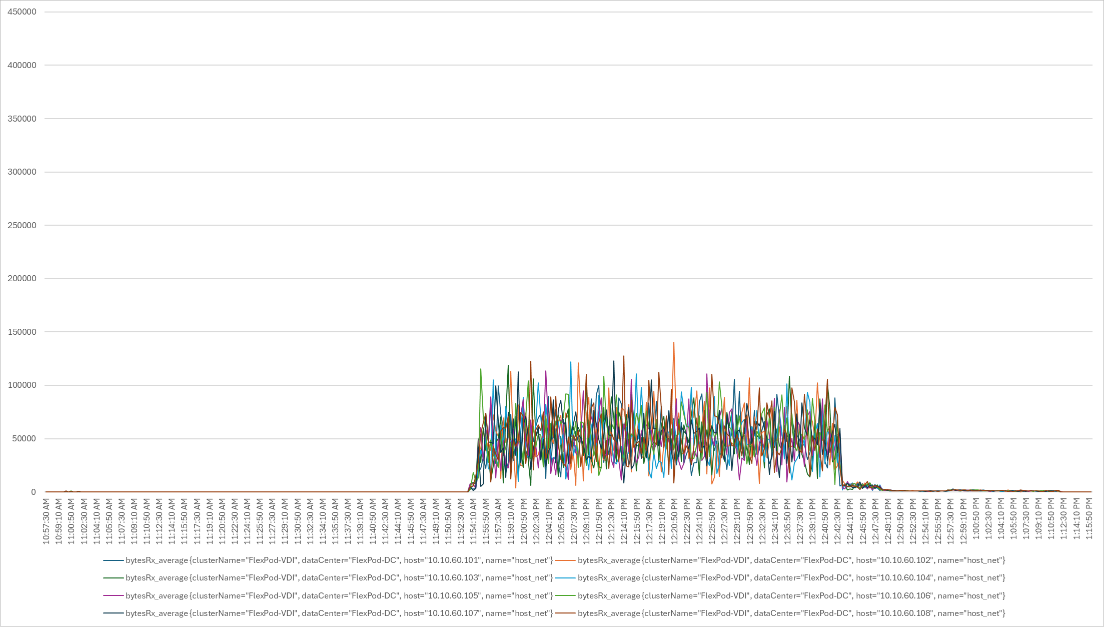
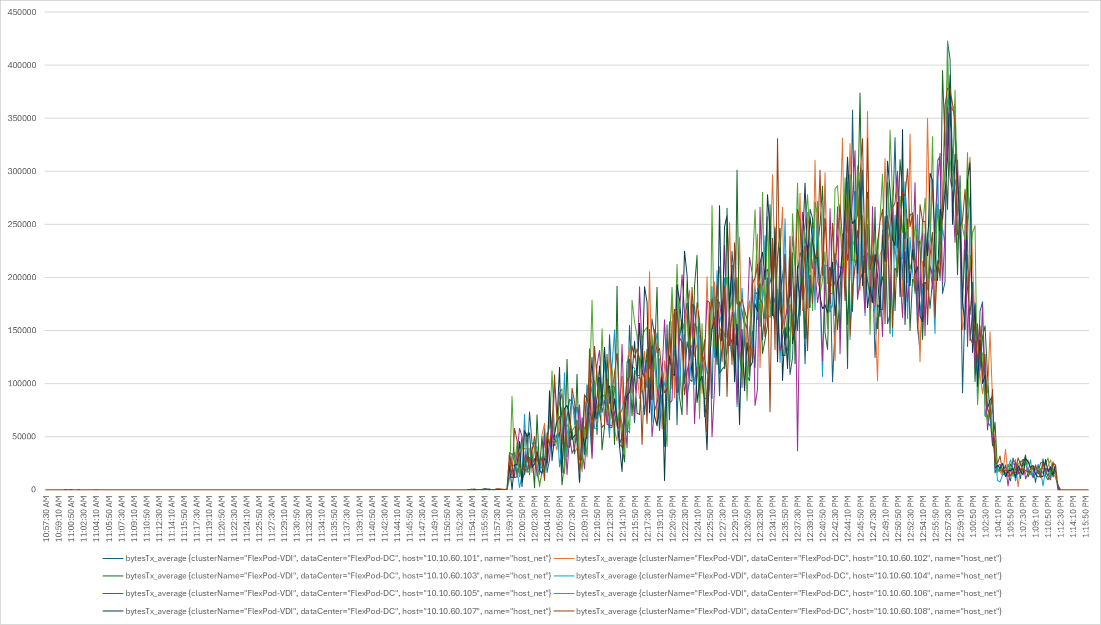
Fibre channel datastore: Full-Scale MCS Non-Persistent Workload Testing with 1600 Users
This section shows the key performance metrics that were captured on the Cisco UCS, during the full-scale testing. The full-scale testing with 1610 users comprised of: 1610 Hosted Virtual Desktops using 8 compute nodes.
The combined mixed workload for the solution is 1610 users. To achieve the target, sessions were launched against all workload clusters concurrently. As per the Cisco Test Protocol for VDI solutions, all sessions were launched within 48 minutes (using the official Knowledge Worker Workload in VSI Benchmark Mode) and all launched sessions became active within two minutes subsequent to the last logged in session.
The configured system efficiently and effectively delivered the following results.
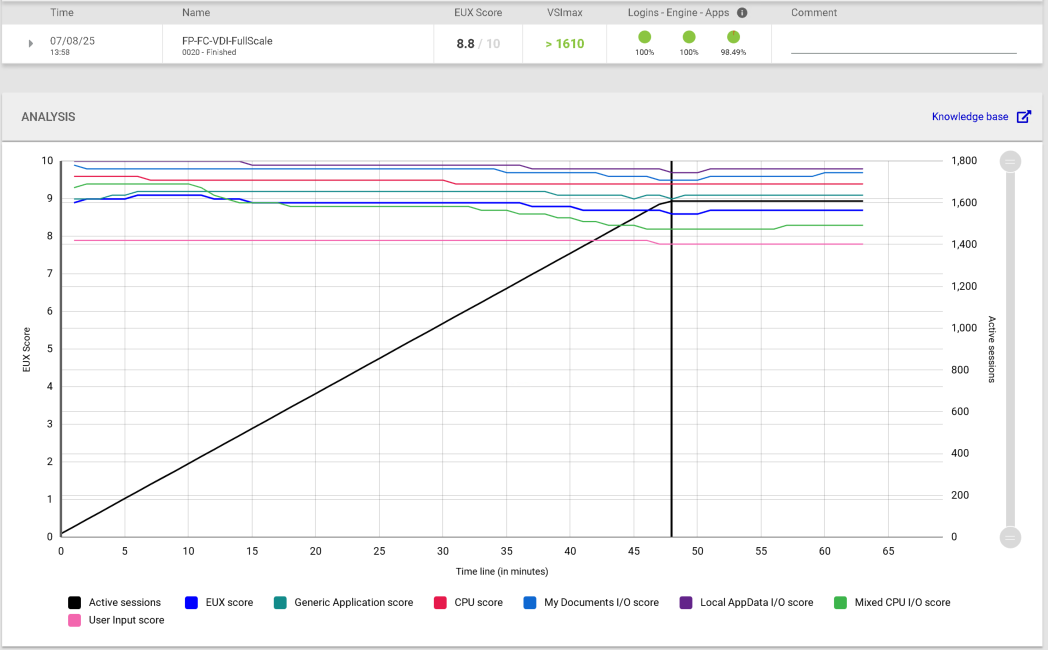
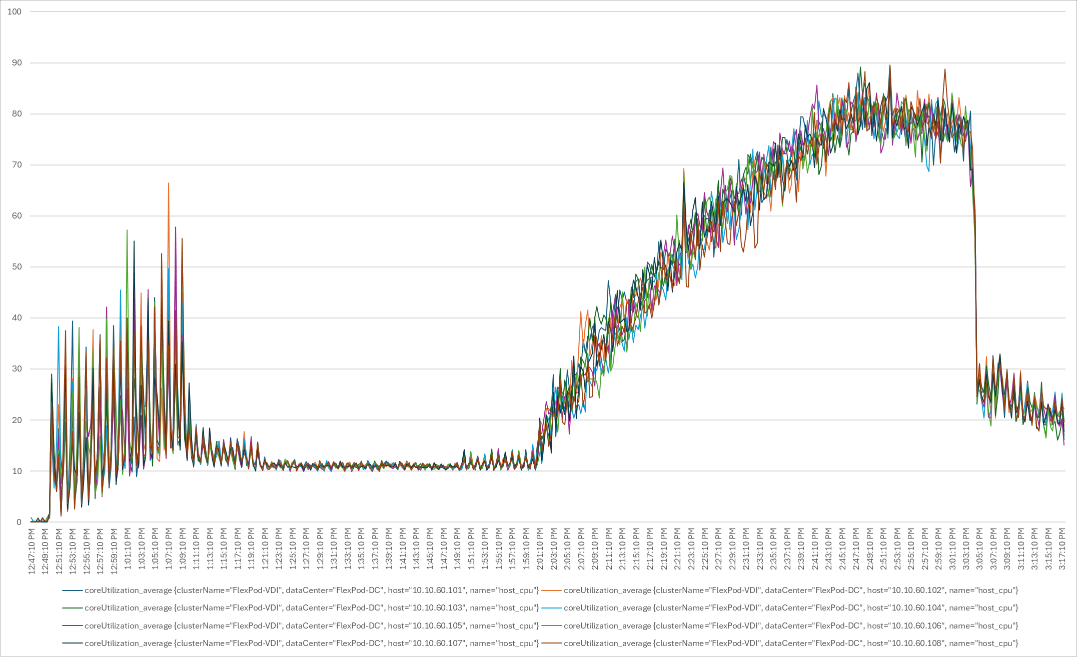
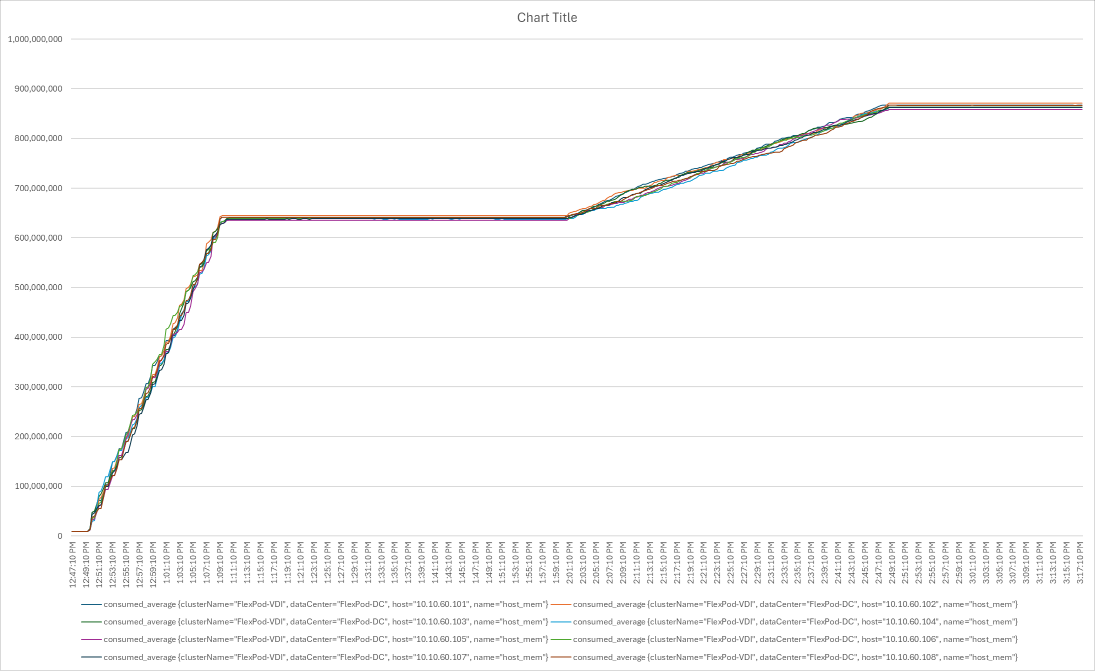
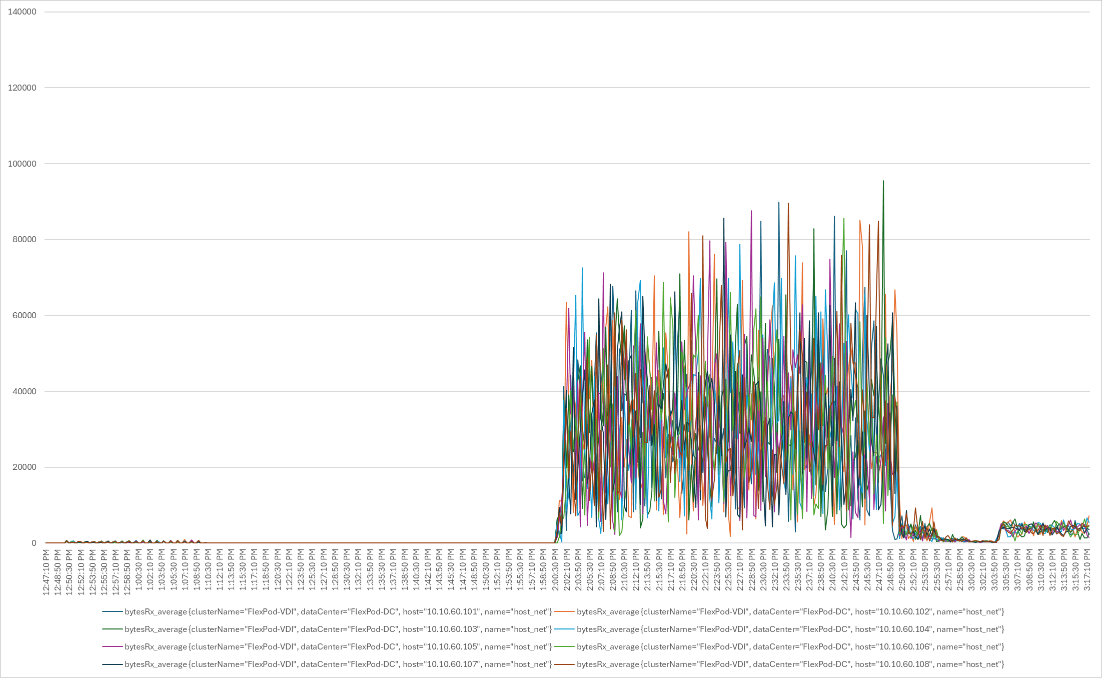
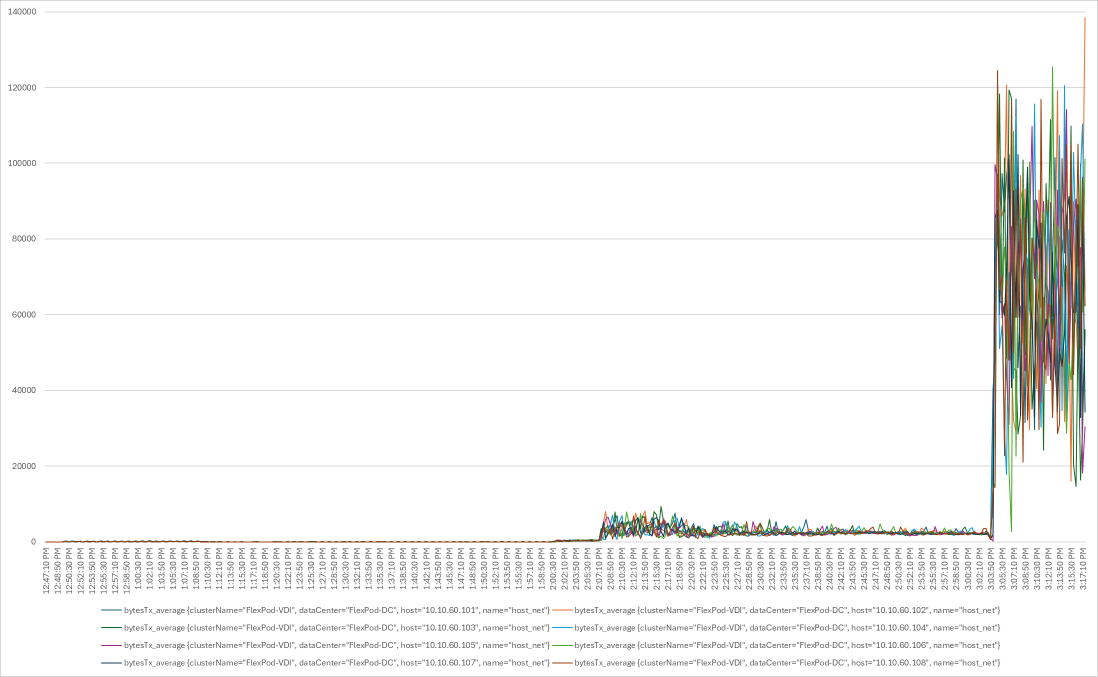
Fibre channel datastore: Full-Scale PVS Non-Persistent Workload Testing with 1600 Users
This section shows the key performance metrics that were captured on the Cisco UCS, during the full-scale testing. The full-scale testing with 1610 users comprised of: 1610 Hosted Virtual Desktops using 8 compute nodes.
The combined mixed workload for the solution is 1610 users. To achieve the target, sessions were launched against all workload clusters concurrently. As per the Cisco Test Protocol for VDI solutions, all sessions were launched within 48 minutes (using the official Knowledge Worker Workload in VSI Benchmark Mode) and all launched sessions became active within two minutes subsequent to the last logged in session.
The configured system efficiently and effectively delivered the following results.
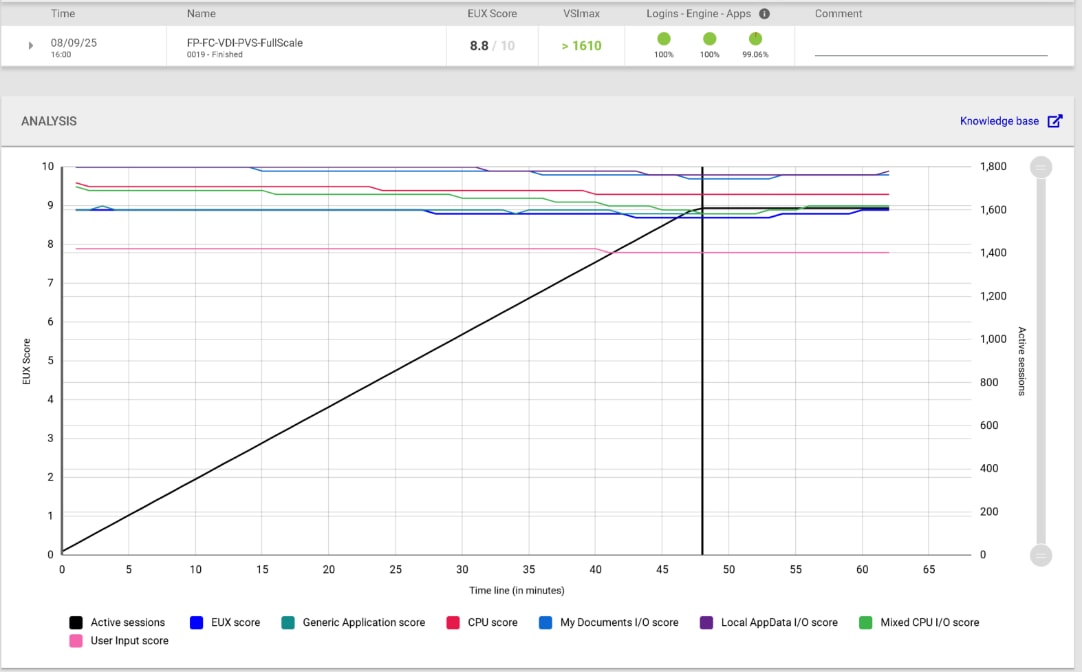
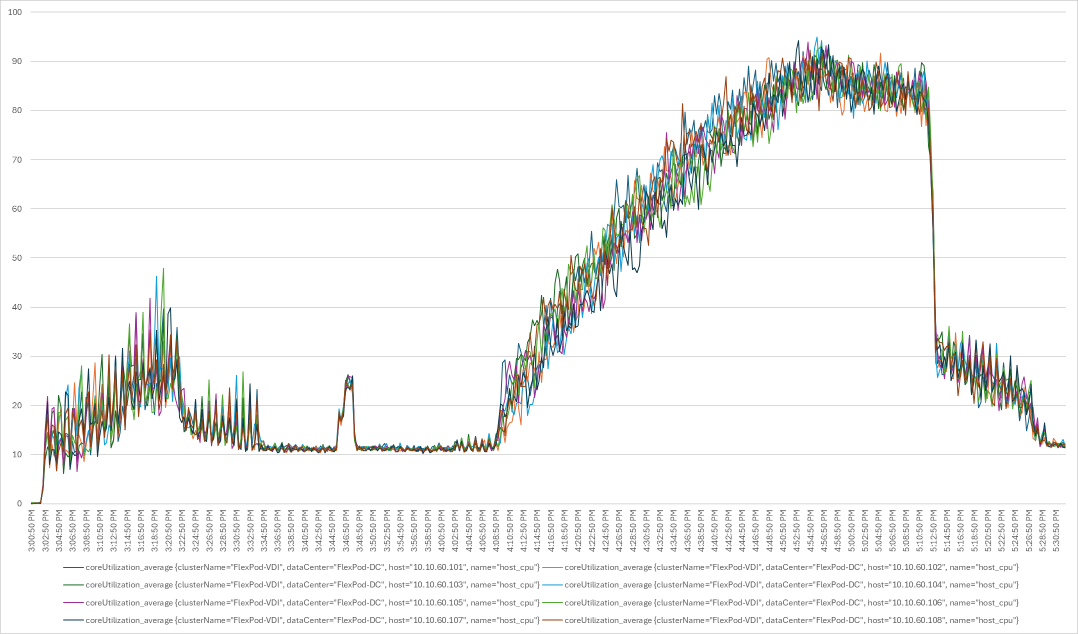
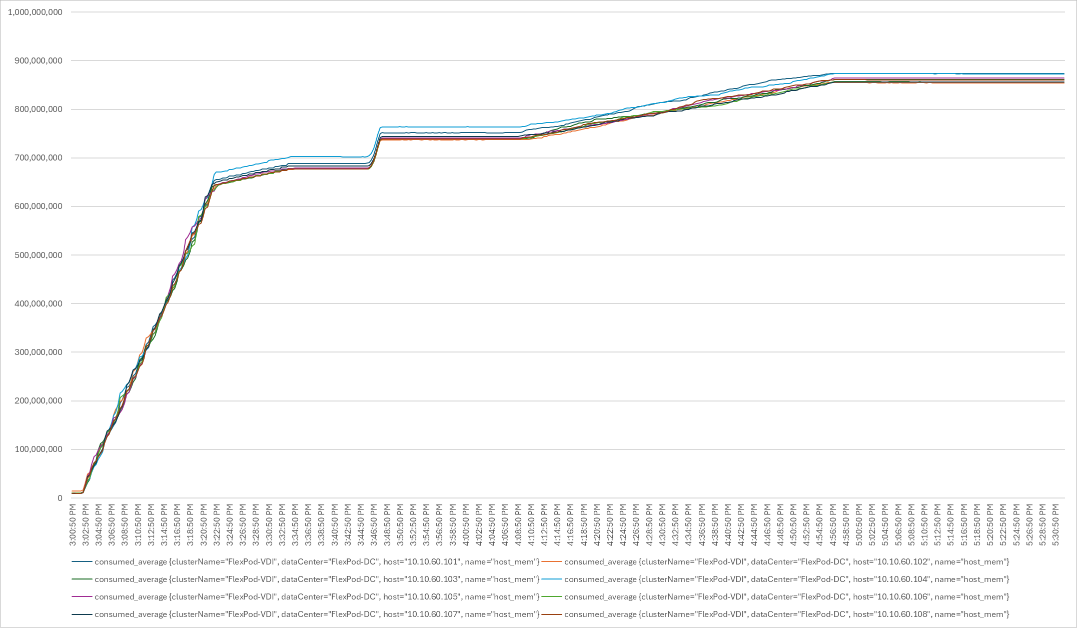
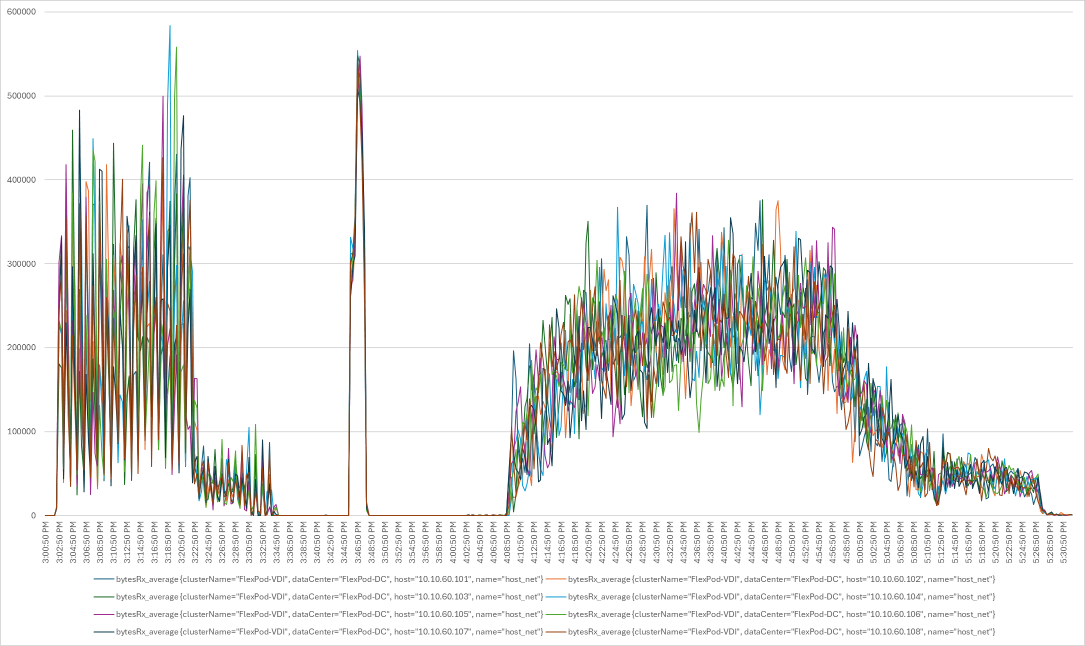
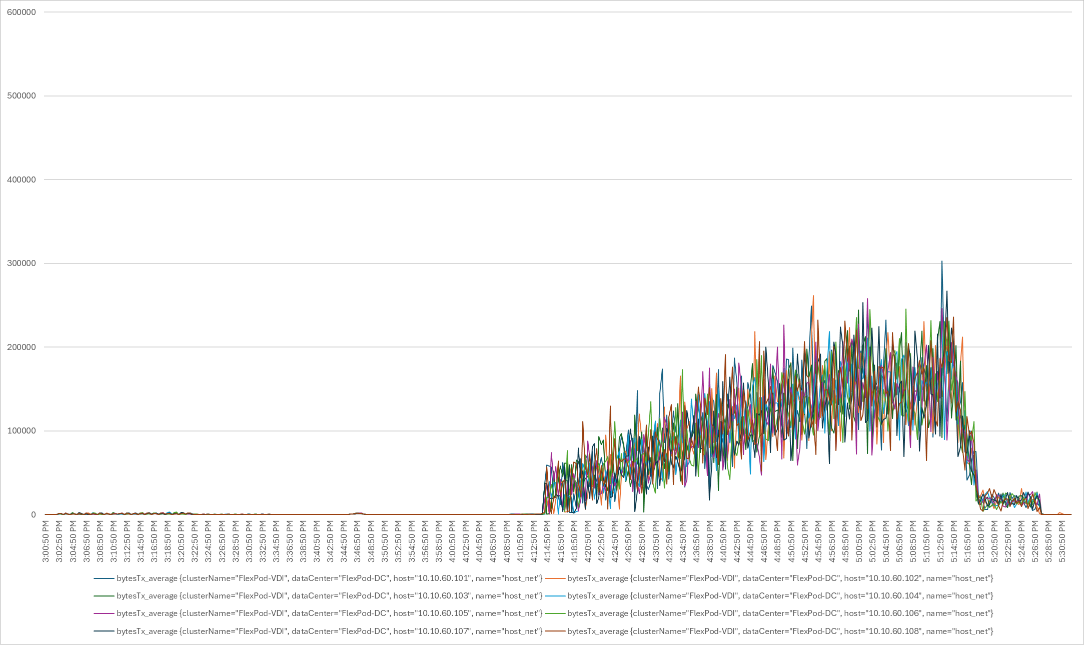
Fibre channel datastore: Full-Scale Persistent Workload Testing with 1600 Users
This section shows the key performance metrics that were captured on the Cisco UCS, during the full-scale testing. The full-scale testing with 1610 users comprised of: 1610 Persistent Hosted Virtual Desktop using 8 compute nodes.
The combined mixed workload for the solution is 1610 users. To achieve the target, sessions were launched against all workload clusters concurrently. As per the Cisco Test Protocol for VDI solutions, all sessions were launched within 48 minutes (using the official Knowledge Worker Workload in VSI Benchmark Mode) and all launched sessions became active within two minutes after the last logged in session.
The configured system efficiently and effectively delivered the following results:
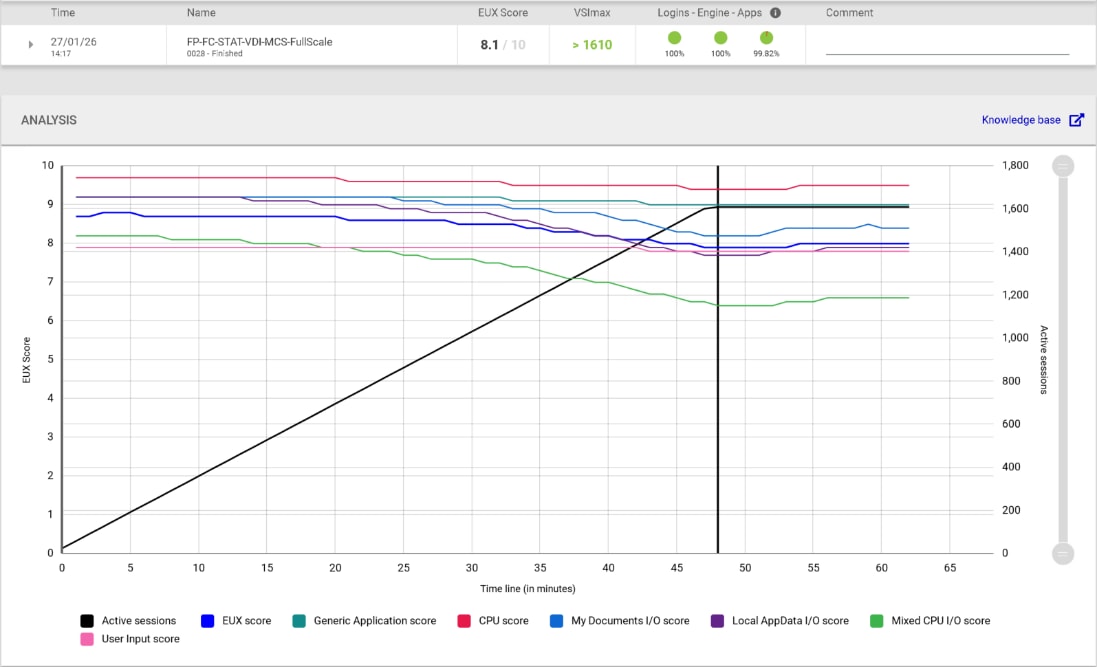
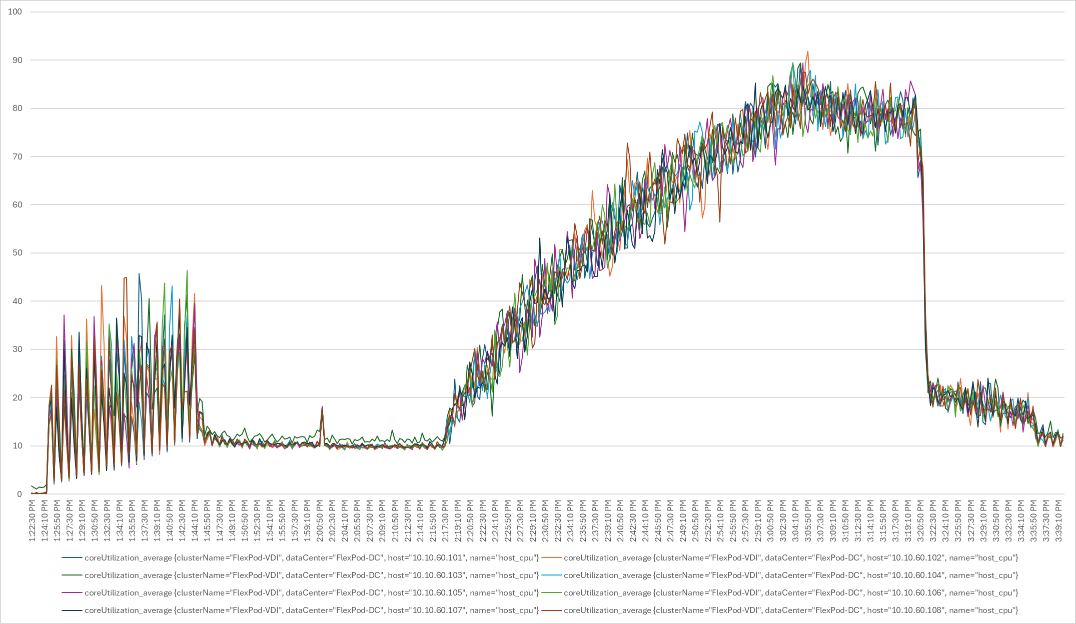
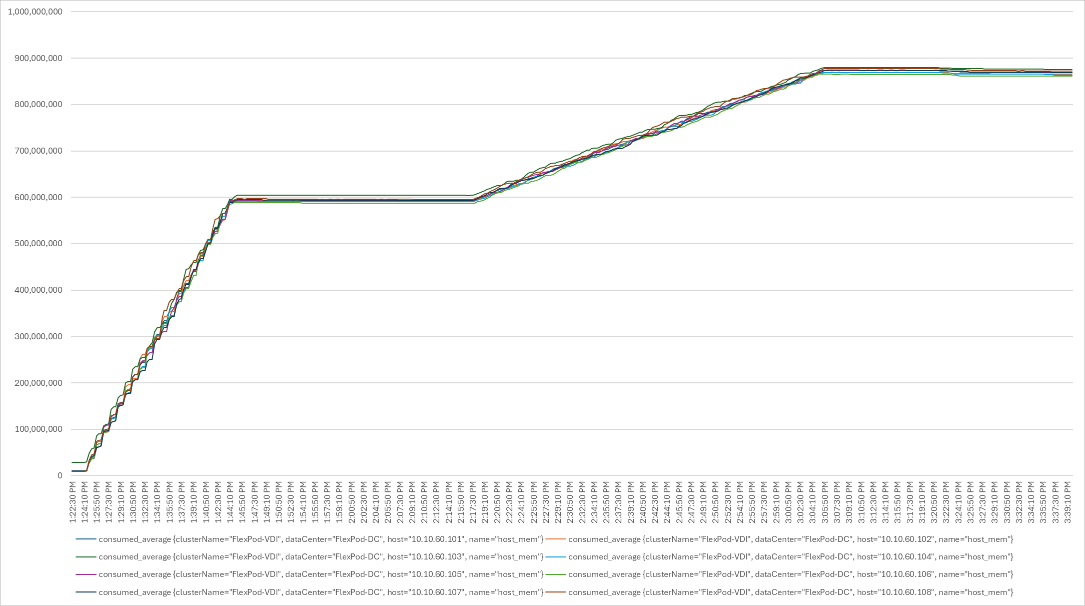
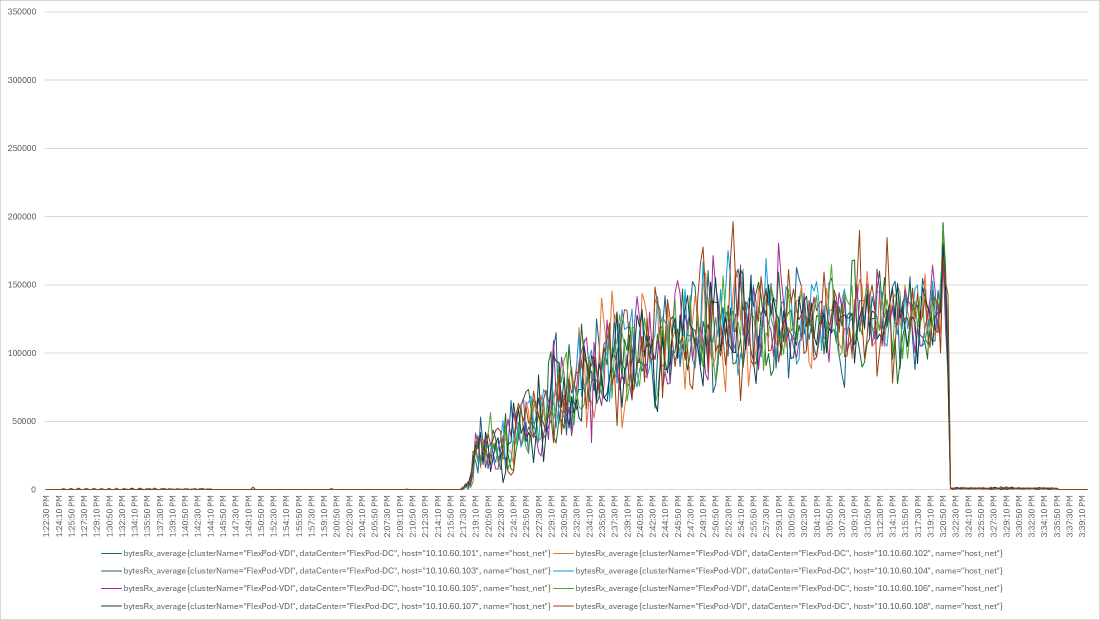
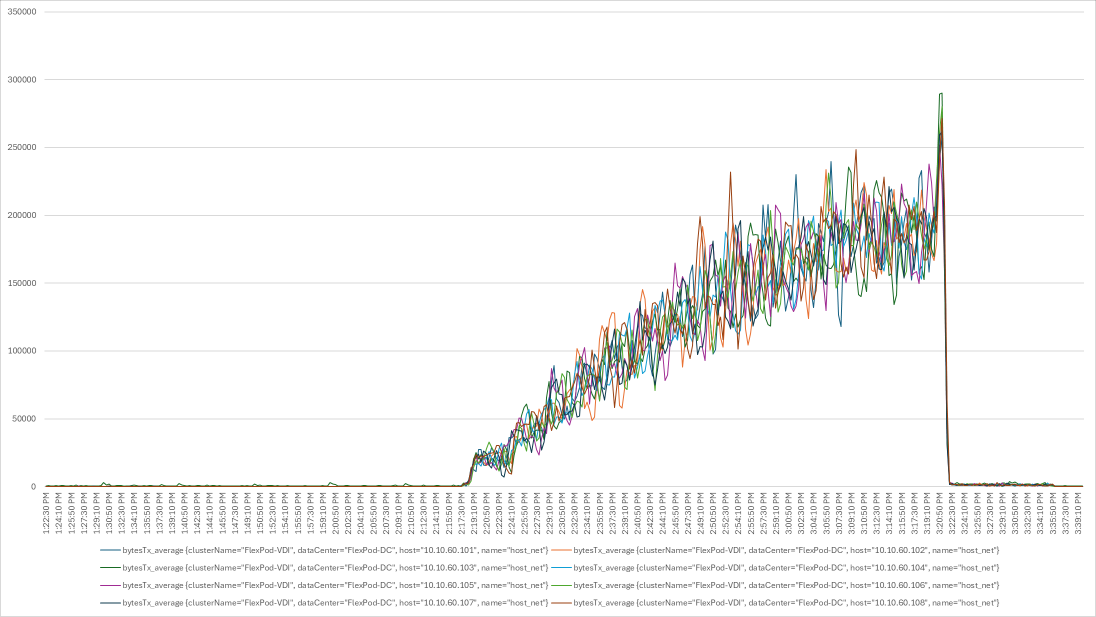
NFS datastore: Full-Scale RDS Workload Testing with 2600 Users
This section shows the key performance metrics that were captured on the Cisco UCS, during the full-scale testing. The full-scale testing with 2688 users comprised of: 2688 Hosted Shared Desktops sessions using eight compute nodes deployed with MCS on four NFS datastores.
The combined mixed workload for the solution is 2688 users. To achieve the target, sessions were launched against all workload clusters concurrently. As per the Cisco Test Protocol for VDI solutions, all sessions were launched within 48 minutes (using the official Knowledge Worker Workload in VSI Benchmark Mode) and all launched sessions became active within two minutes subsequent to the last logged in session
The configured system efficiently and effectively delivered the following results:
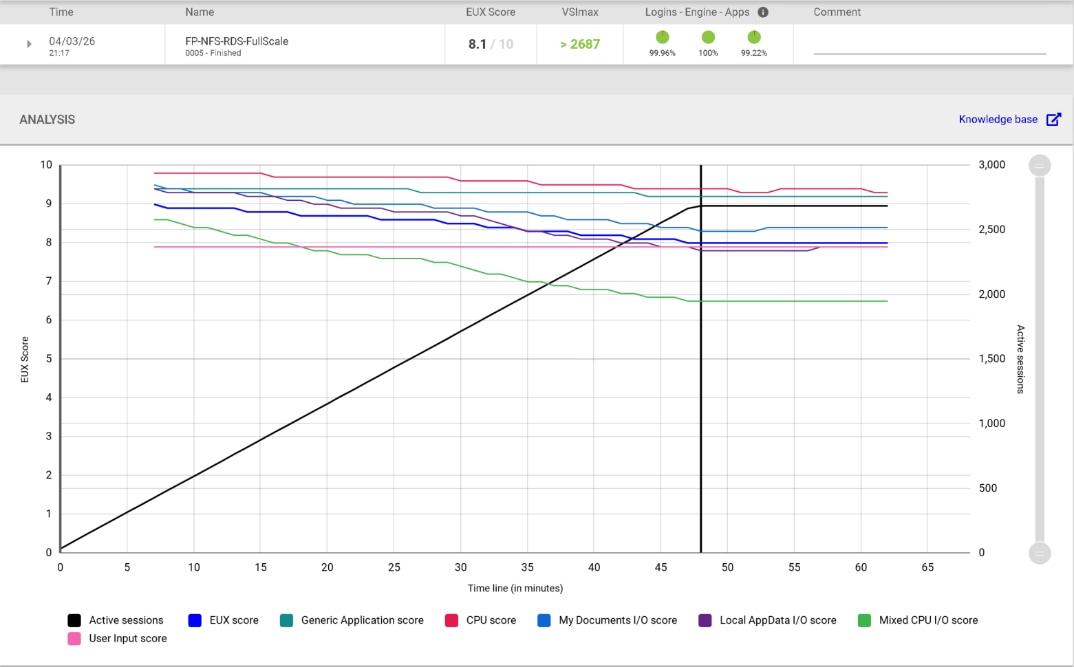
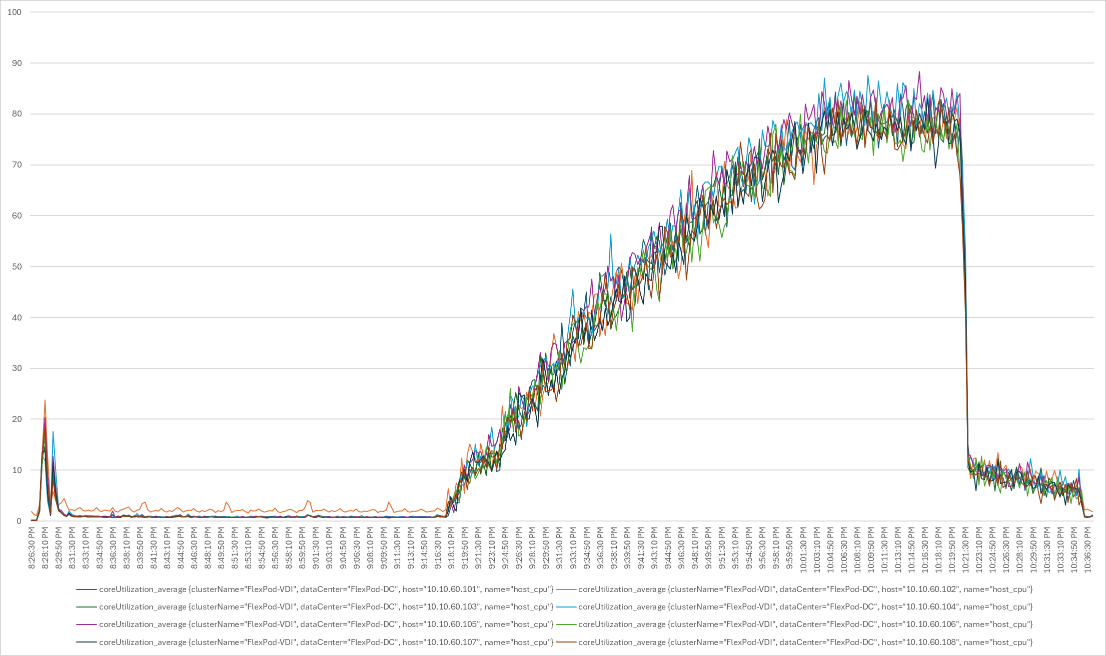
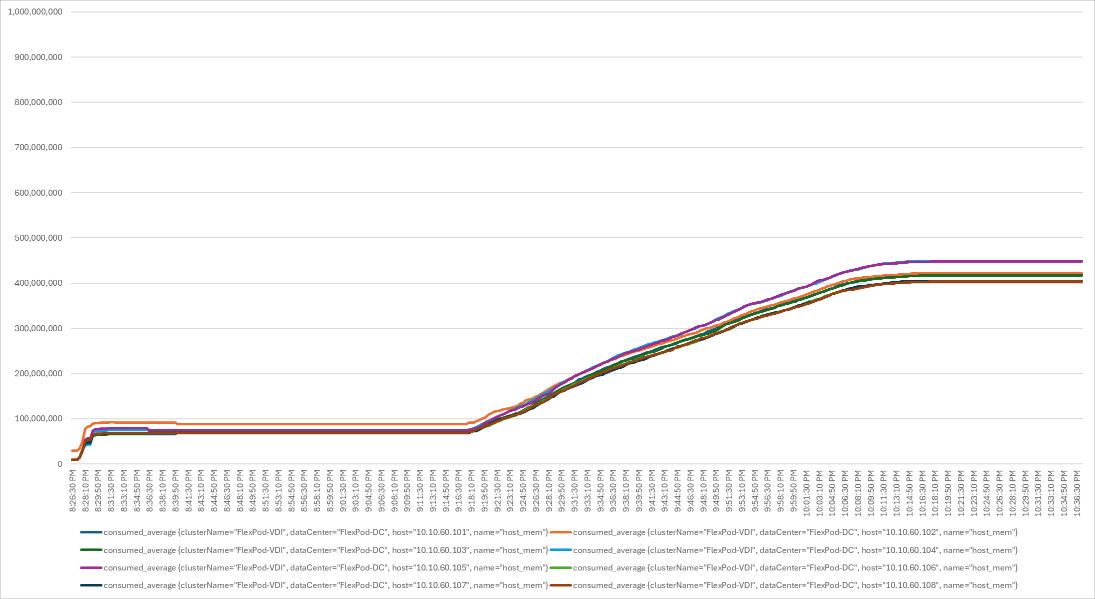
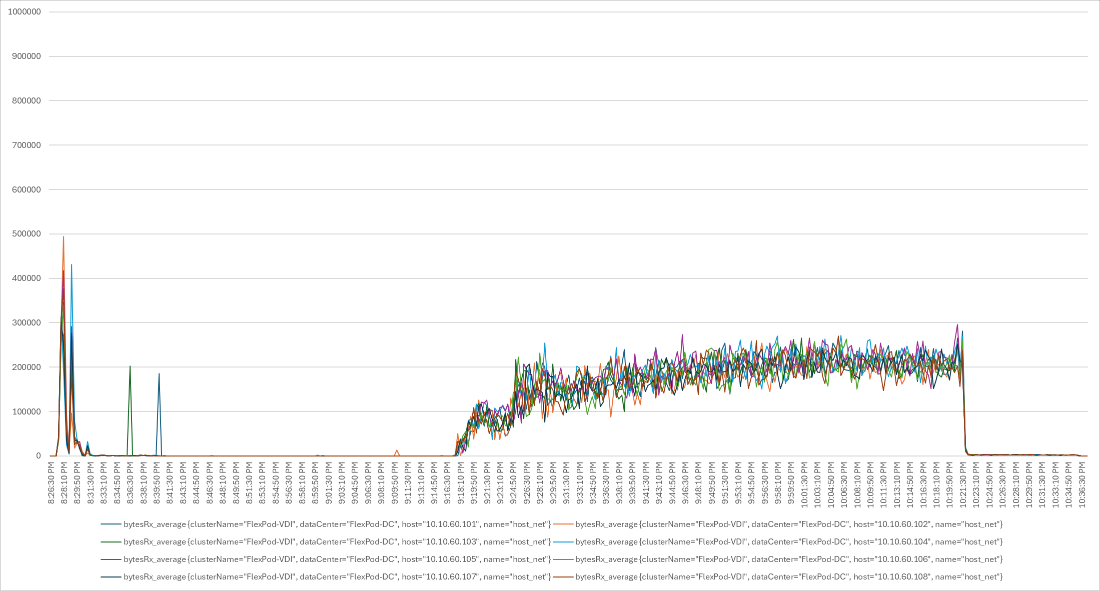
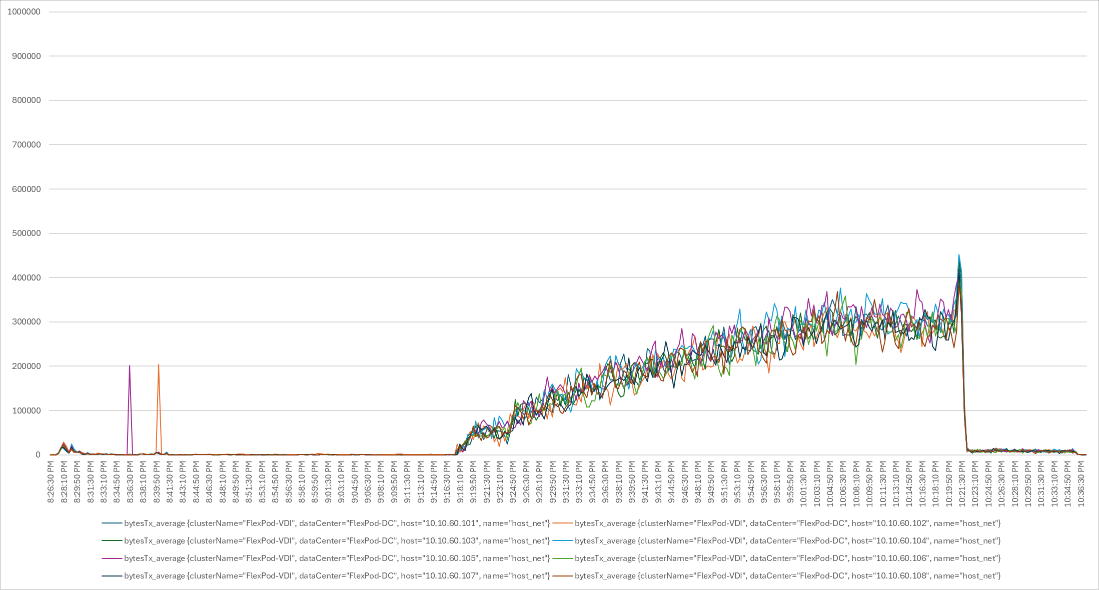
NFS datastore: Full-Scale MCS Non-Persistent Workload Testing with 1600 Users
This section shows the key performance metrics that were captured on the Cisco UCS, during the full-scale testing. The full-scale testing with 1610 users comprised of: 1600 Hosted Virtual Desktops using eight compute nodes deployed with MCS on four NFS datastores.
The combined mixed workload for the solution is 1610 users. To achieve the target, sessions were launched against all workload clusters concurrently. As per the Cisco Test Protocol for VDI solutions, all sessions were launched within 48 minutes (using the official Knowledge Worker Workload in VSI Benchmark Mode) and all launched sessions became active within two minutes subsequent to the last logged in session.
The configured system efficiently and effectively delivered the following results:
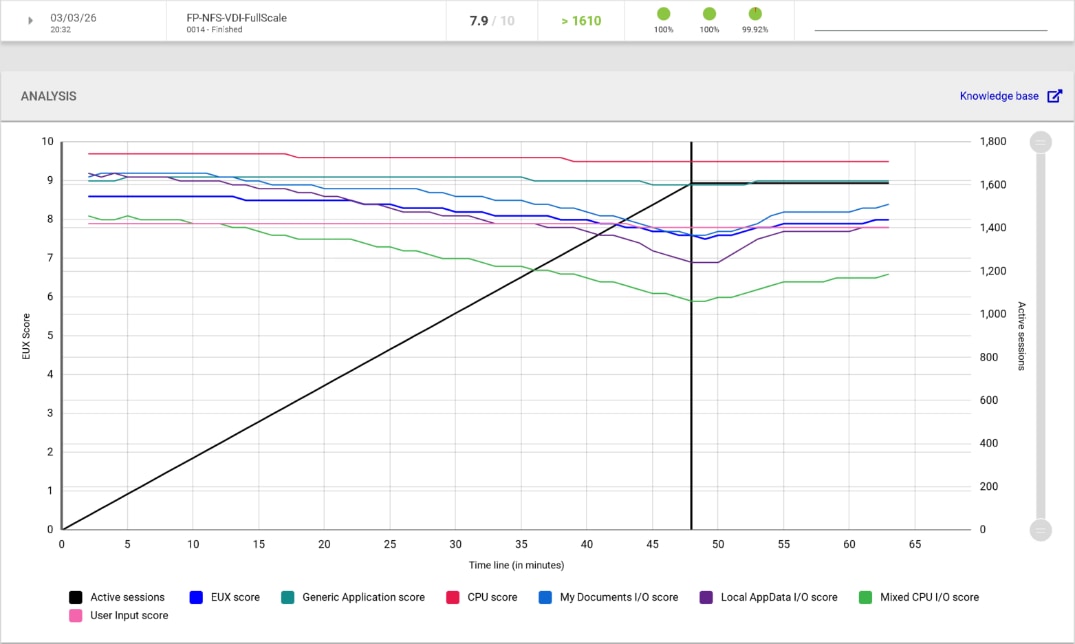
Performance data for the servers running the workload as follows:
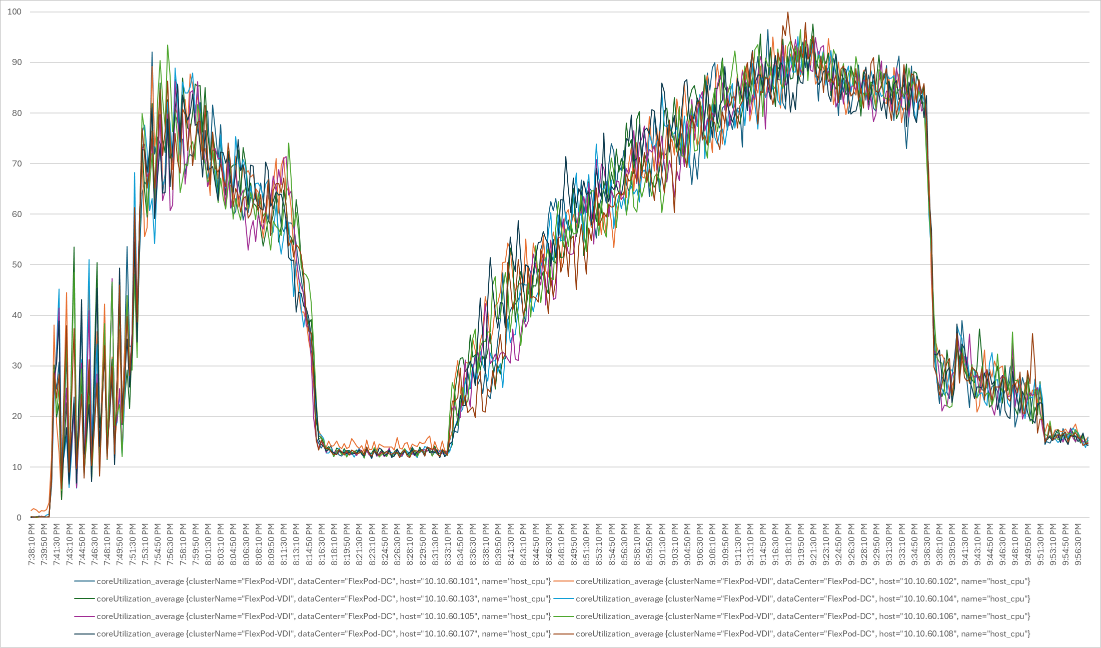
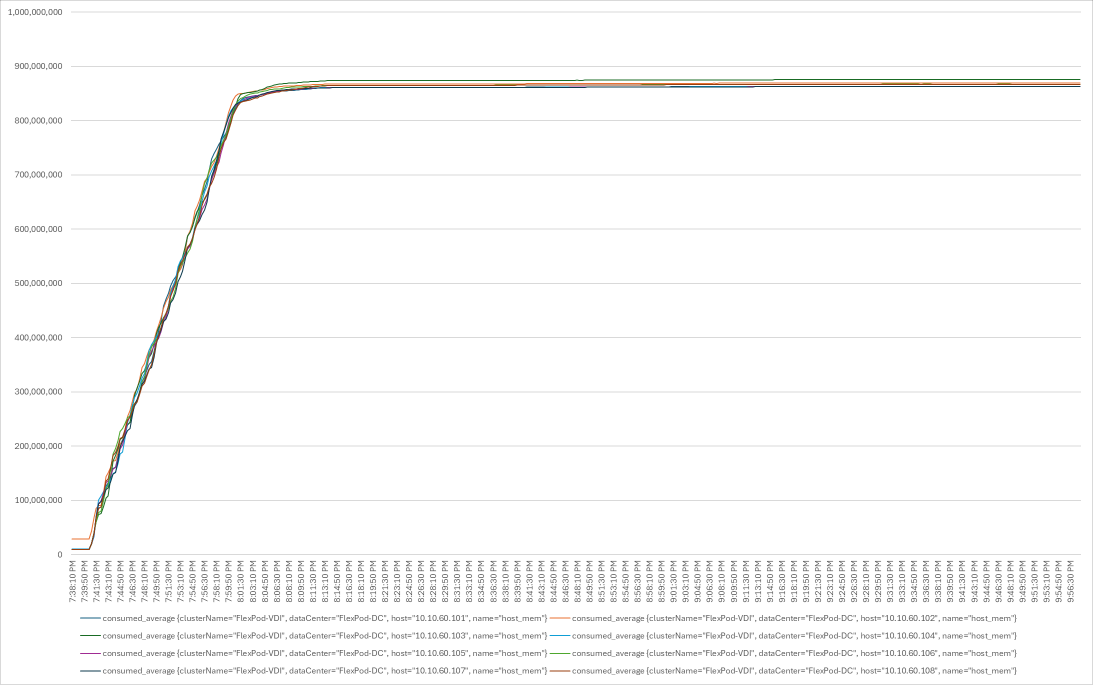
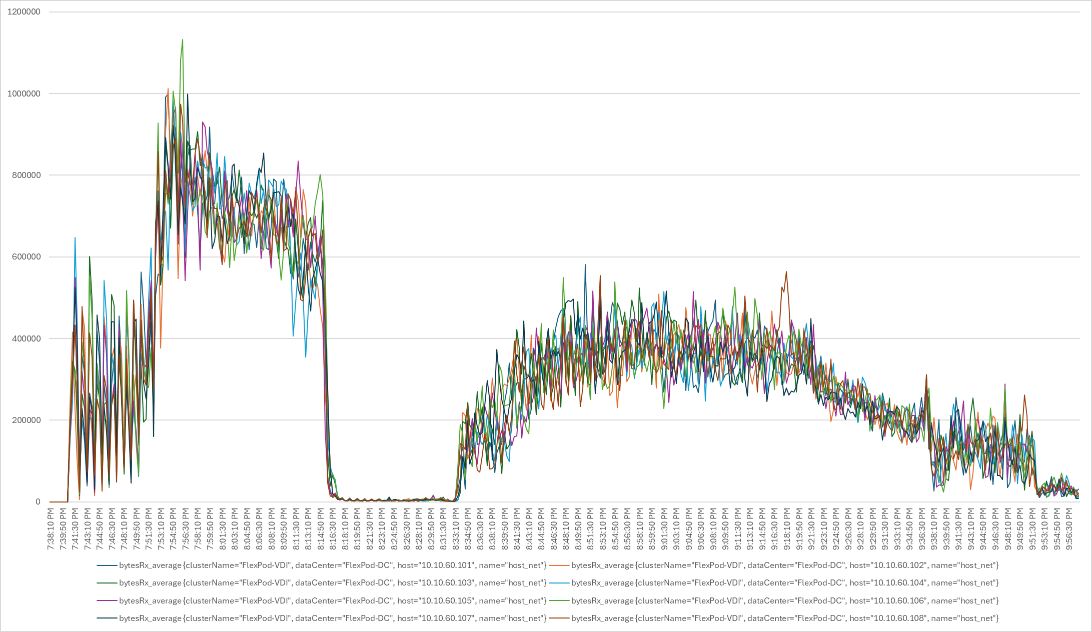
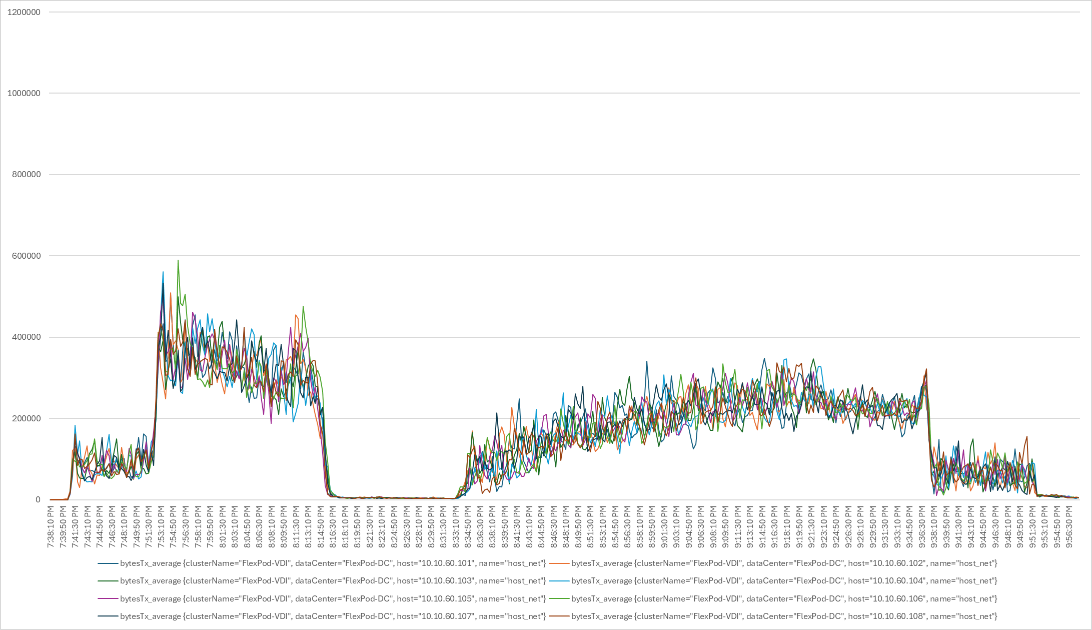
NFS datastore: Full-Scale PVS Non-Persistent Workload Testing with 1600 Users
This section shows the key performance metrics that were captured on the Cisco UCS, during the full-scale testing. The full-scale testing with 1610 users comprised of: 1610 Hosted Virtual Desktops using eight compute nodes deployed with PVS on four NFS datastores.
The combined mixed workload for the solution is 1610 users. To achieve the target, sessions were launched against all workload clusters concurrently. As per the Cisco Test Protocol for VDI solutions, all sessions were launched within 48 minutes (using the official Knowledge Worker Workload in VSI Benchmark Mode) and all launched sessions became active within two minutes after the last logged in session, followed by the 15 minutes steady state.
The configured system efficiently and effectively delivered the following results:
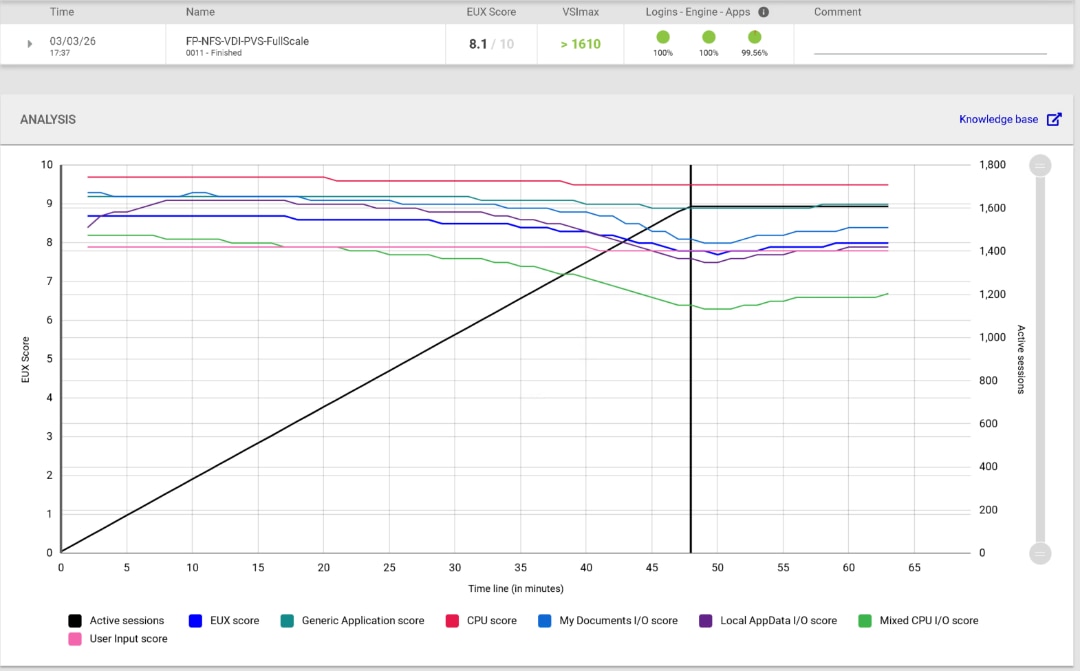
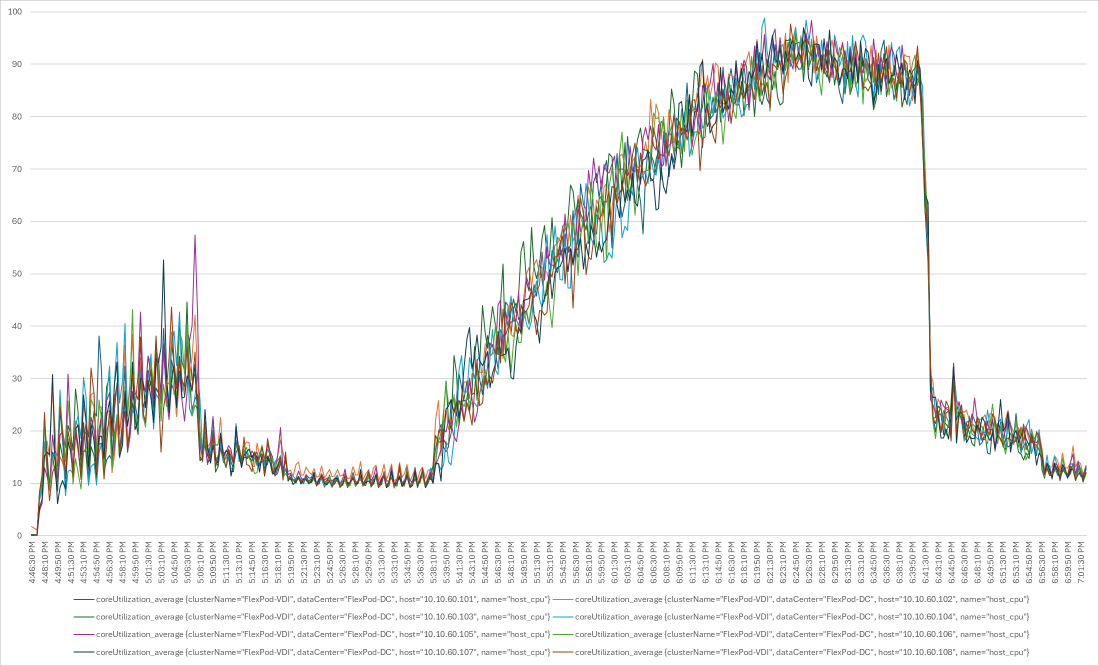
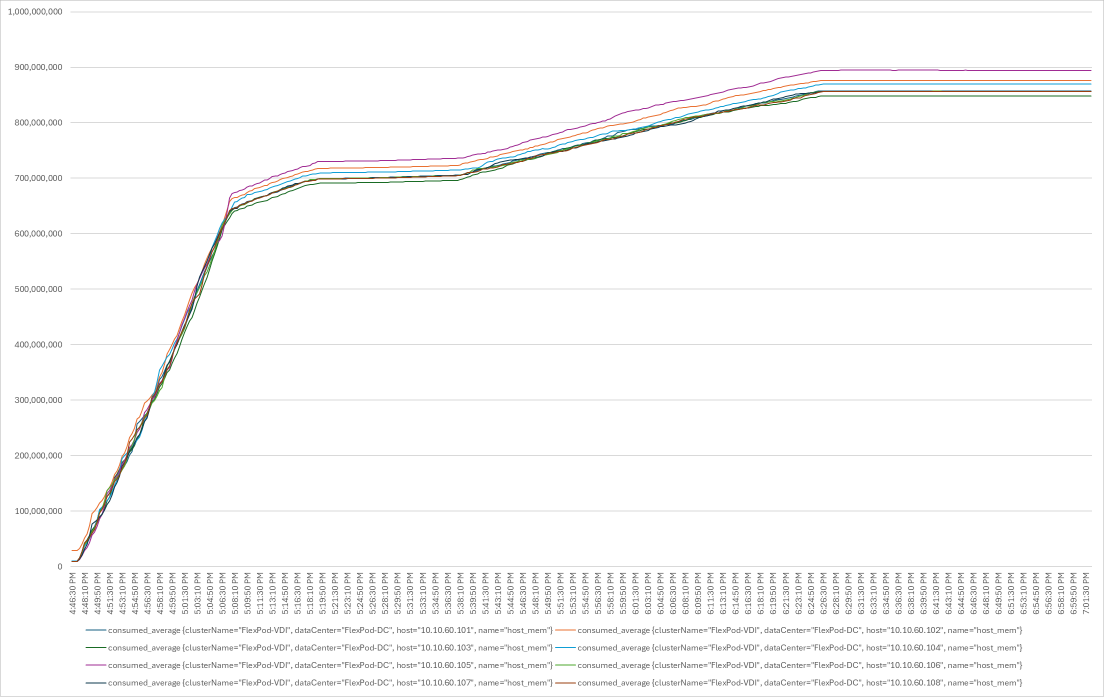
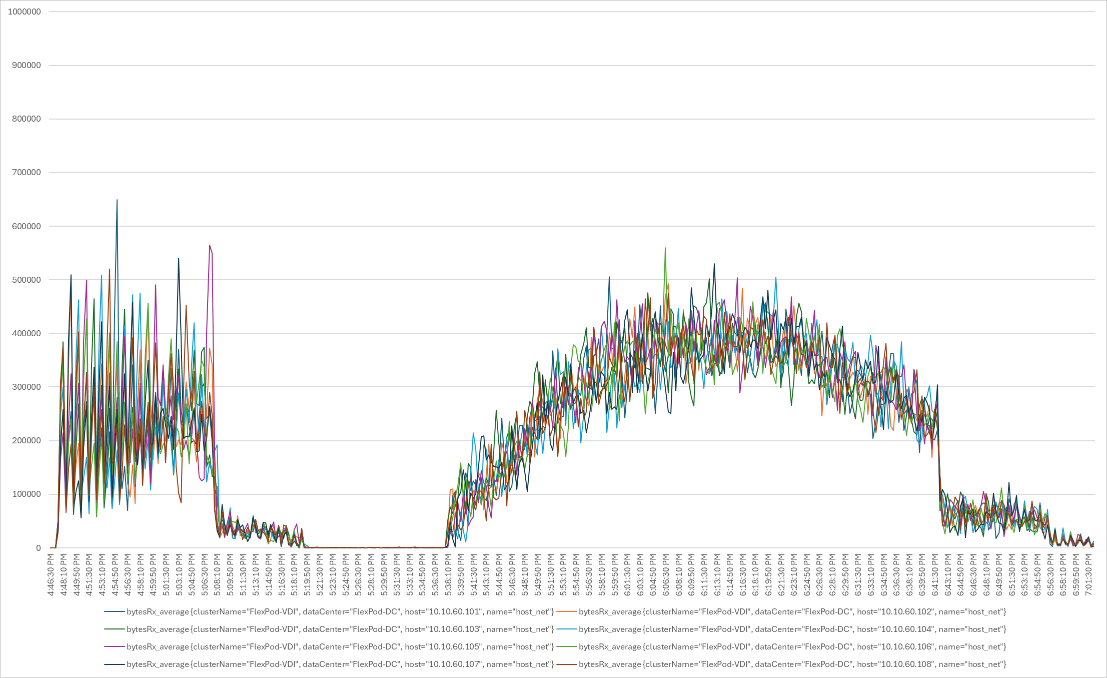
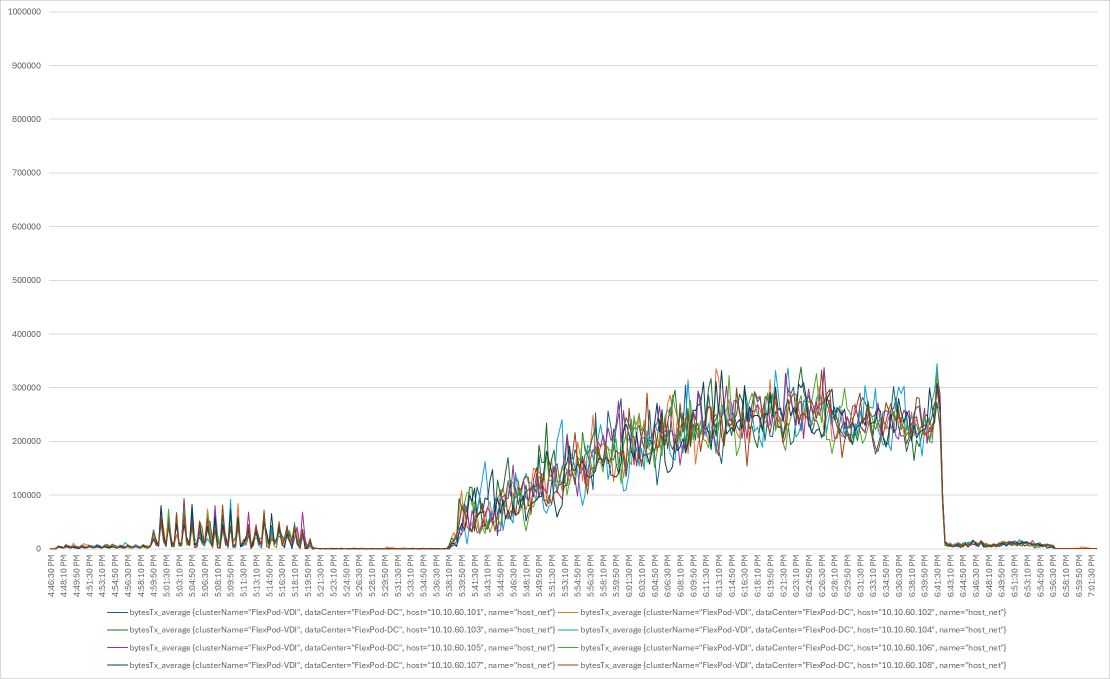
NFS datastore: Full-Scale Persistent Workload Testing with 1600 Users
This section shows the key performance metrics that were captured on the Cisco UCS, during the full-scale testing. The full-scale testing with 1610 users comprised of: 1610 Persistent Hosted Virtual Desktop using eight compute nodes deployed with MCS on four NFS datastores.
The combined mixed workload for the solution is 1610 users. To achieve the target, sessions were launched against all workload clusters concurrently. As per the Cisco Test Protocol for VDI solutions, all sessions were launched within 48 minutes (using the official Knowledge Worker Workload in VSI Benchmark Mode) and all launched sessions became active within two minutes subsequent to the last logged in session.
The configured system efficiently and effectively delivered the following results:
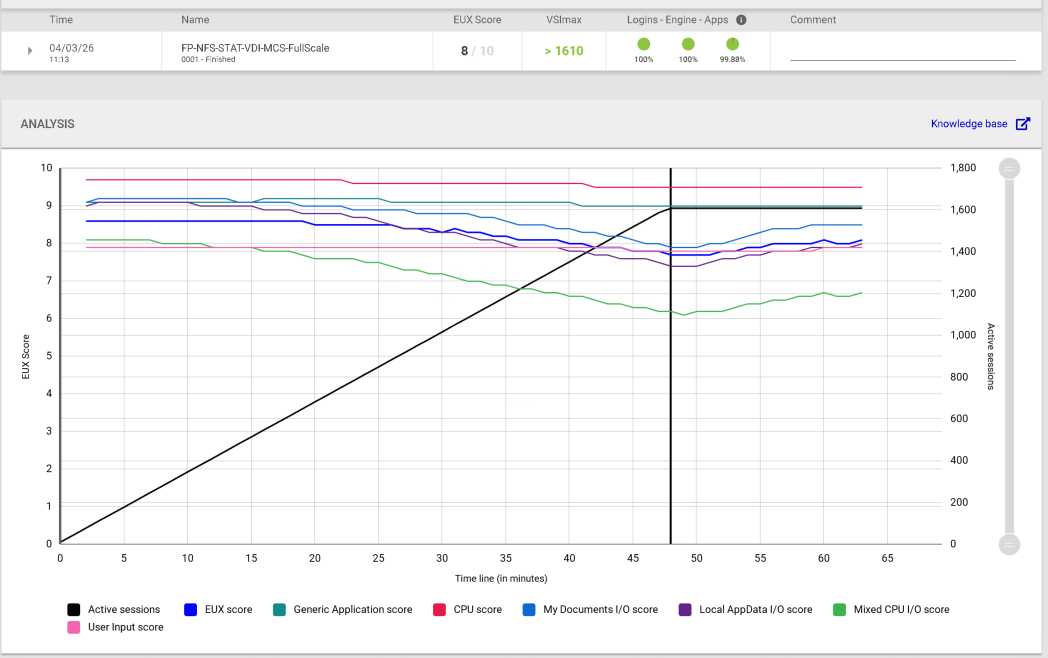
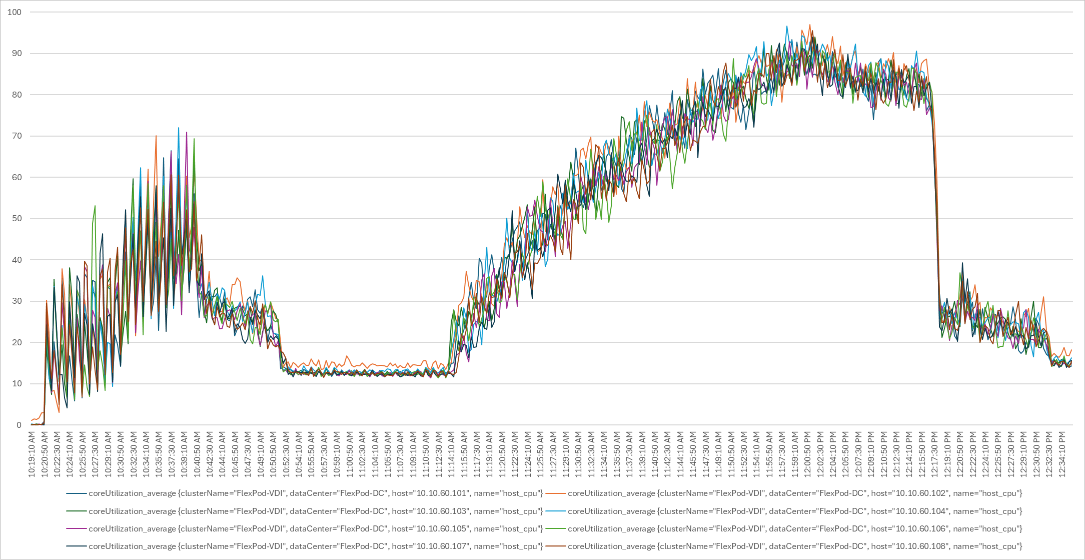
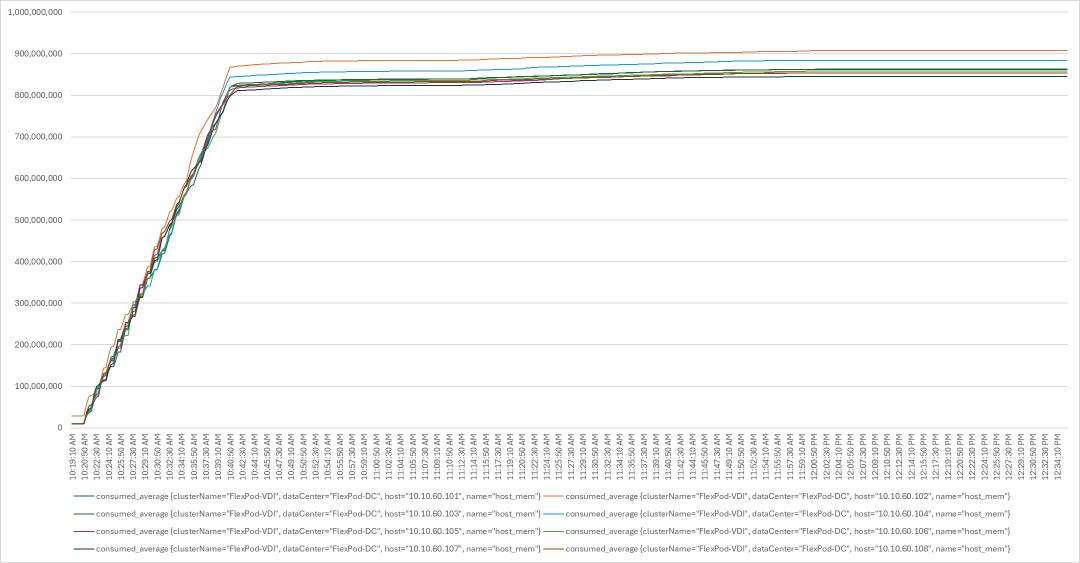
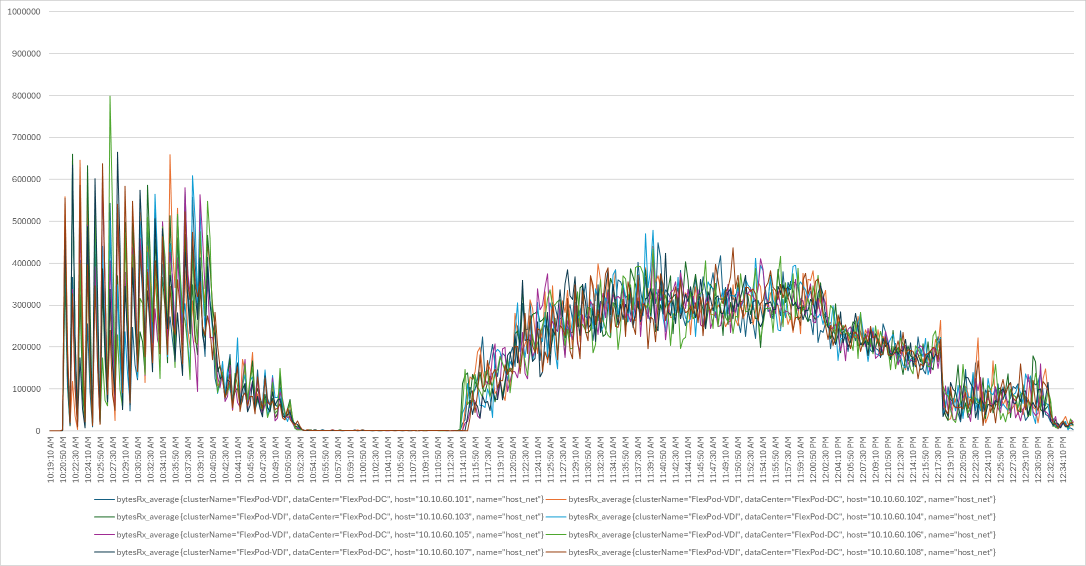
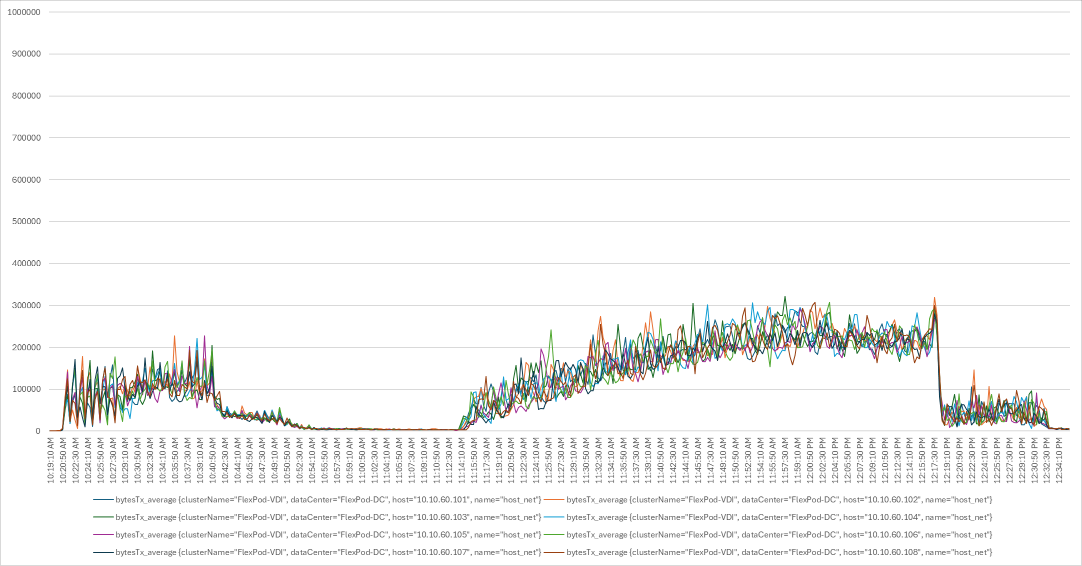
NVIDIA GPU Workloads
This solution does not include testing workloads utilizing NVIDIA GPUs. However, the Cisco UCS X-Series supports a wide range of NVIDIA GPU cards that can be highly beneficial for VDI environments.
For guidance on installing and configuring NVIDIA GPUs in Cisco UCS X-Series servers, please refer to the latest hardware installation guides in the Cisco Documentation portal.
For Cisco VDI best practices regarding GPU acceleration, refer to the latest Cisco Validated Designs and white papers produced by our technical solutions team."
NetApp AFF A50 Storage Detailed Test Results for Cluster Scalability Test
This section provides analysis of the NetApp AFF A50 system performance results for each of the Citrix software module testing (HSD, PVS, Persistent), which we call cluster testing, and they are identified previously in this document. Specifically, it depicts and discusses the results for the following test case scenarios:
● 2600 Windows Server 2022 Citrix Hosted Shared desktops (RDS)
● 1600 Windows 11 x64 Citrix PVS Non-Persistent desktops
● 1600 Windows 11 x64 Citrix MCS Non-Persistent desktops
● 1600 Windows 11 x64 Citrix Persistent Full-Clone desktops
From a storage perspective, it is critical to maintain a latency of less than a millisecond for an optimal end-user experience no matter the IOPS and bandwidth being driven. The test results indicate that the AFF A50 system delivers that essential minimum level of latency despite thousands of desktops hosted on the AFF A50 system.
The sections that follow show screenshots of storage performance of all three use case scenarios with information about IOPS, bandwidth, and latency at the peak of each use case test. In all three use cases (cluster level testing with HSD PVS VDI, full clone persistent desktops and full-scale mixed workload sessions, the criteria followed prior to launching Login VSI workload test are the same
2600 Users Citrix HSD (RDS) Windows 2022 Sessions
This test uses Login VSI for the workload generator in Benchmark mode with the Knowledge Worker user type and with Citrix Remote Desktop Service Hosted (RDSH) sessions for the VDI delivery mechanism. For this test, we used 4 volumes. This test uses Citrix Cache on RAM feature which takes a lot of stress off of the storage, so you can see low IOPS for all the volumes in the following figures.
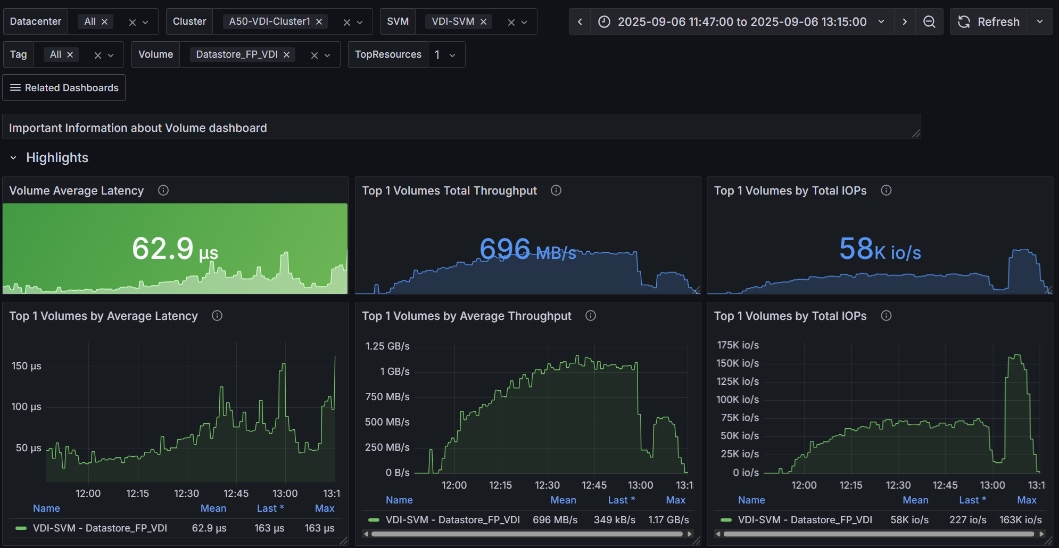
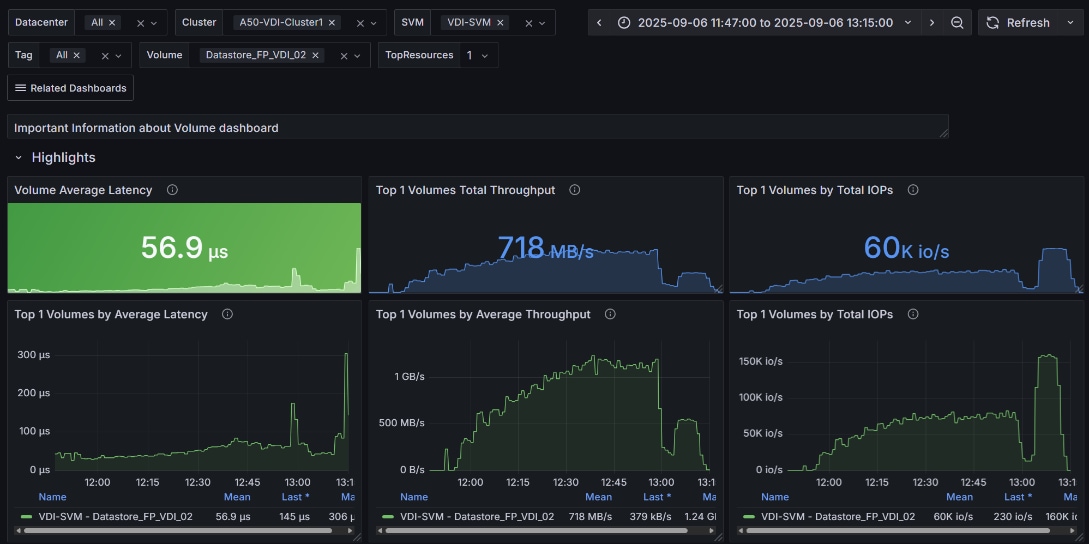
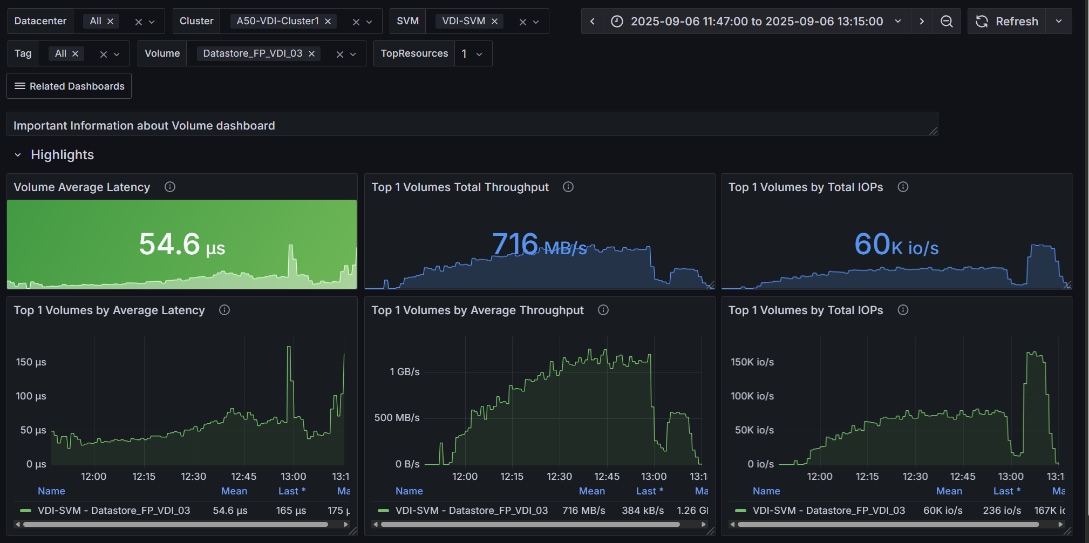
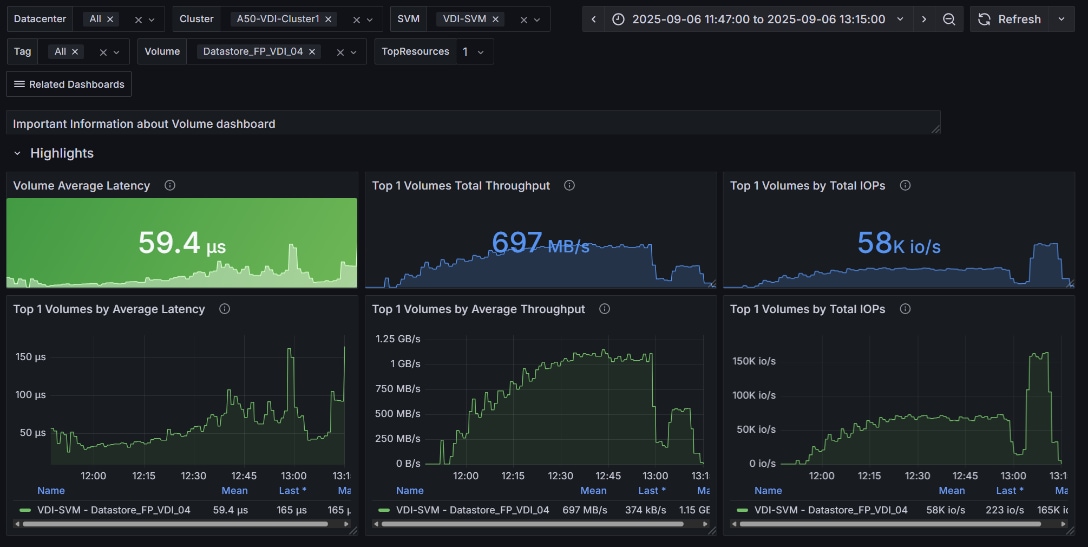
1600 Users Persistent Desktops Cluster Test
NetApp AFF A50 Test Results for 1600 Persistent Windows 11 x64 Citrix MCS Desktops
This section describes the key performance metrics that were captured on the NetApp Storage AFF A50 array during the testing with 1600 persistent desktops. For this test 4 volumes were used, and the average latency is below 1ms for all the volumes.
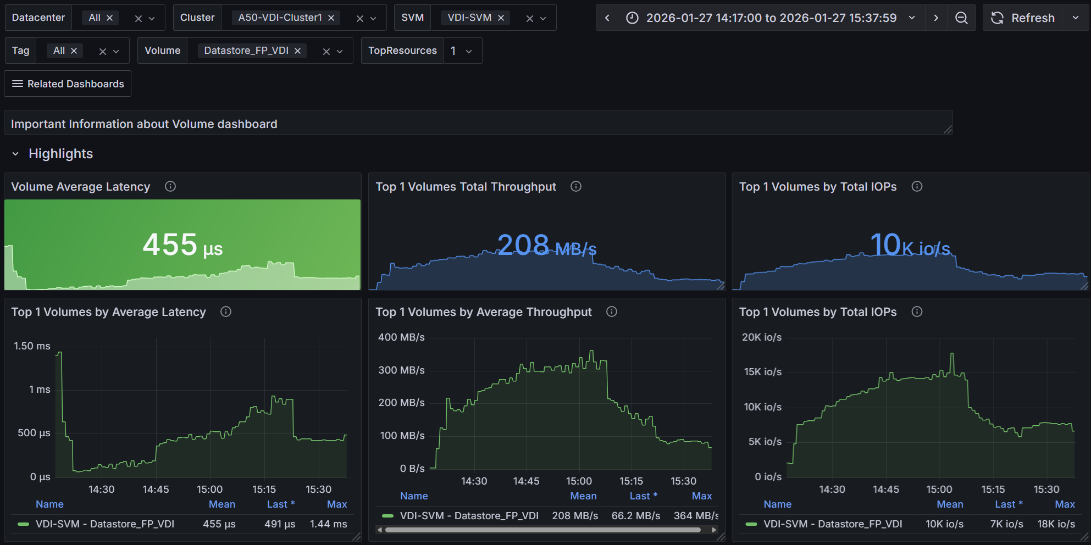
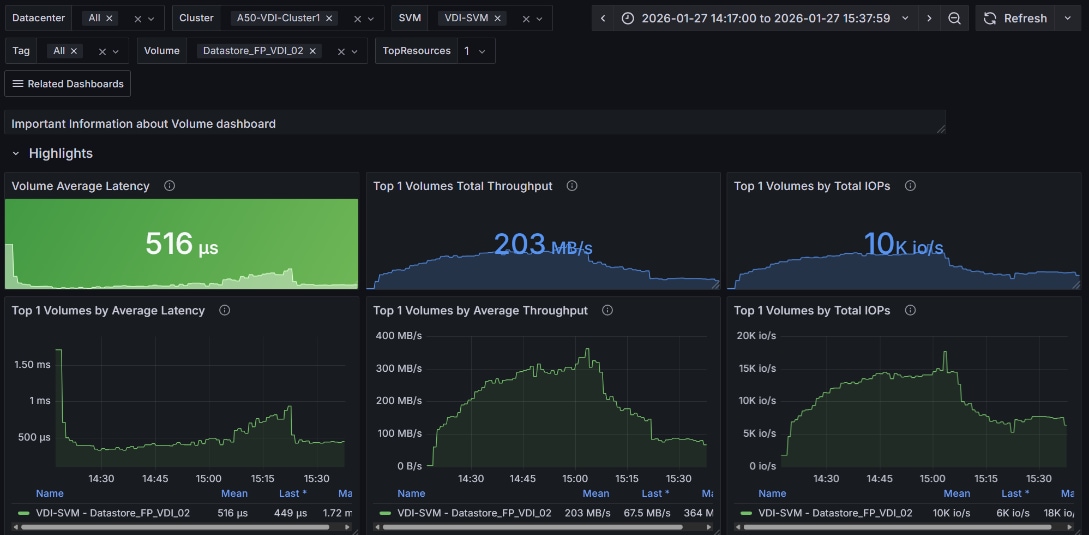
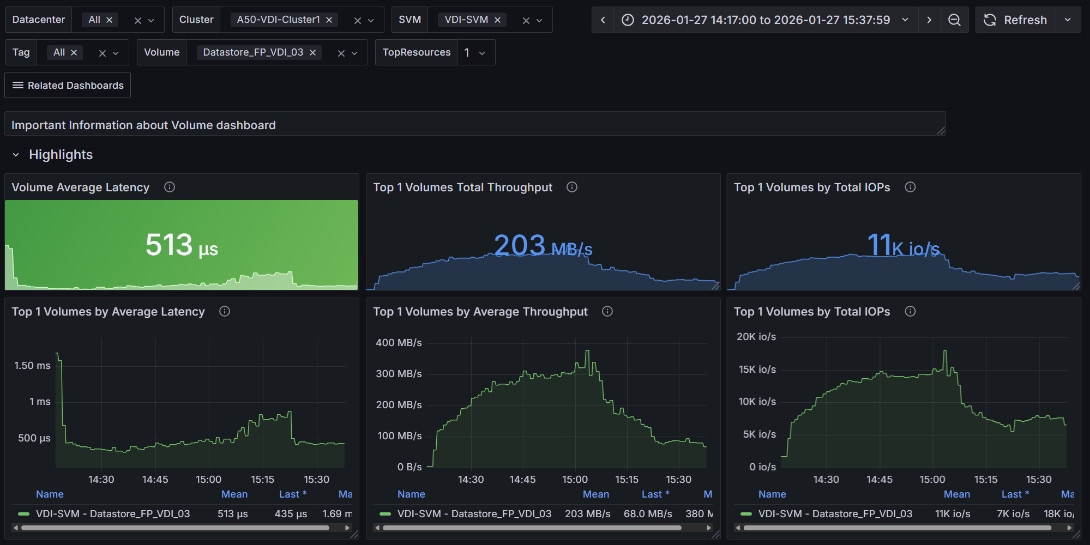
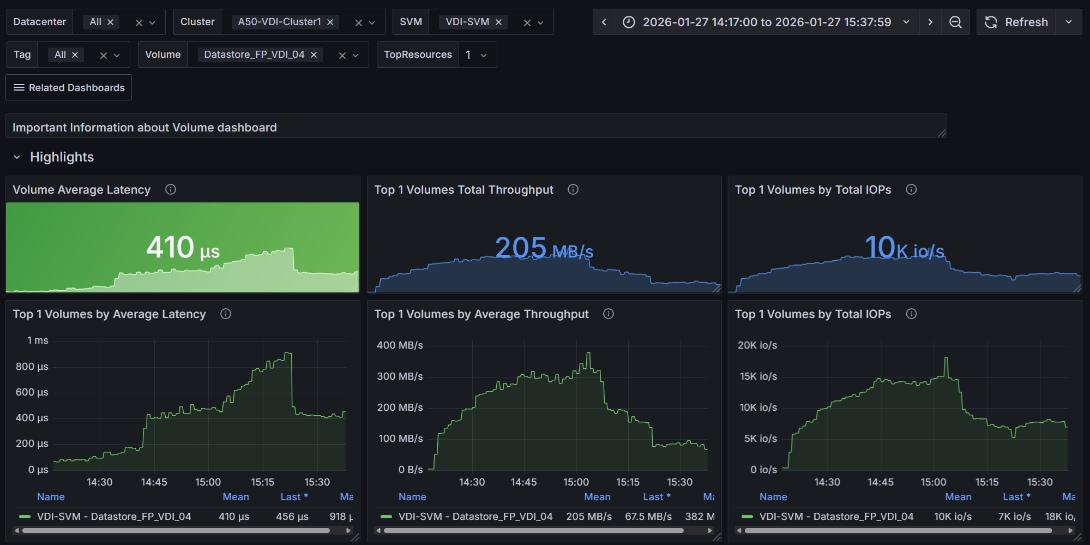
1600 Users PVS Non-Persistent Desktops Cluster Test
NetApp AFF A50 Test Results for 1600 Non-Persistent Windows 11 x64 Citrix PVS Desktops
For this test, 4 volumes were used, and the average latency is way below 1ms for all the volumes and the latency was not higher than 1ms at any time.
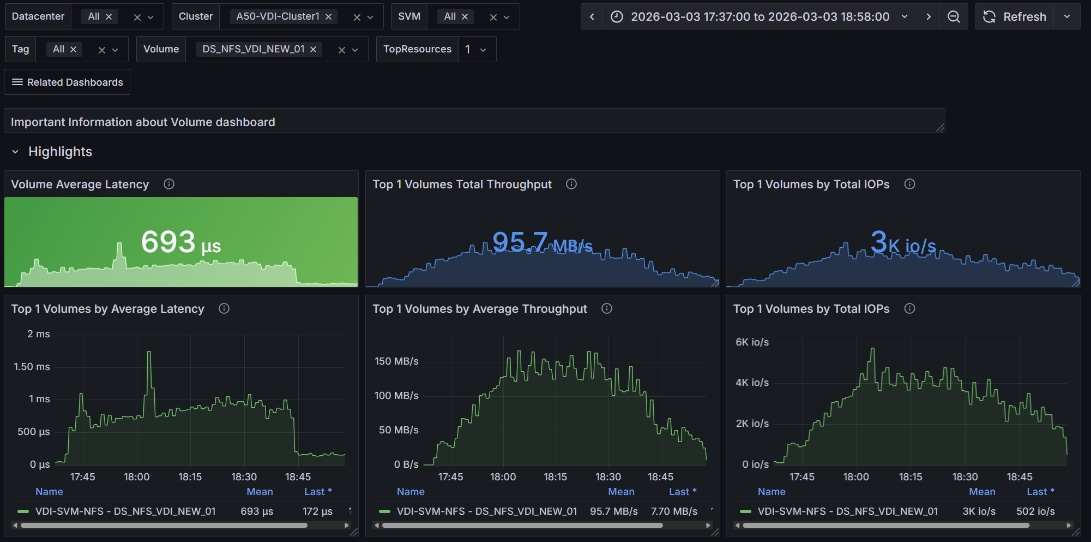
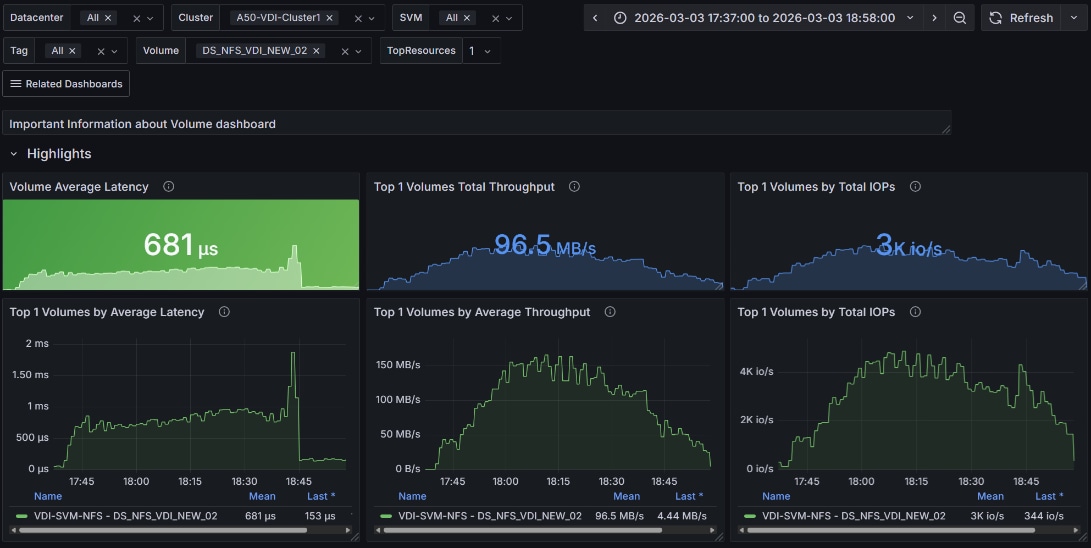
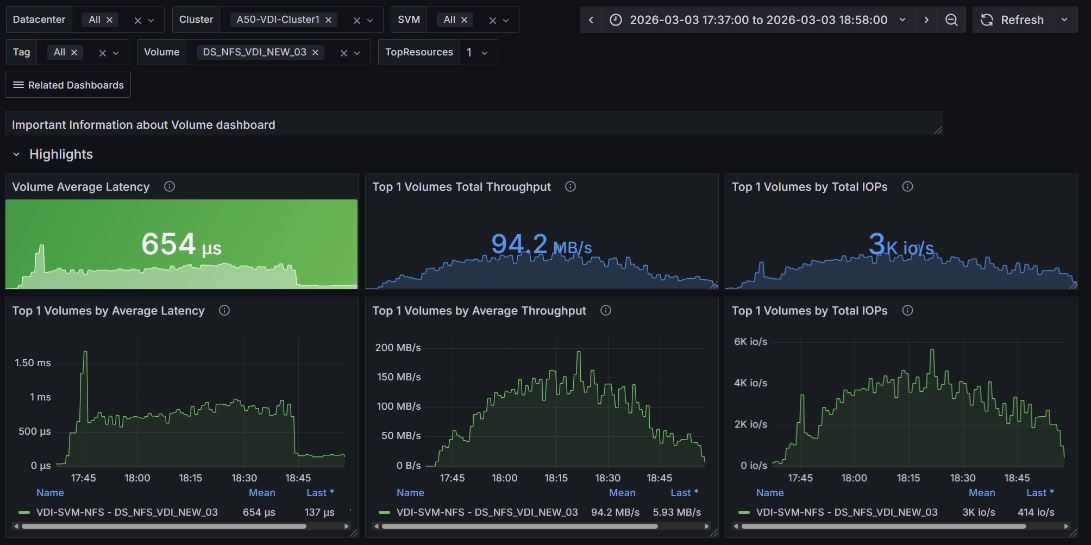
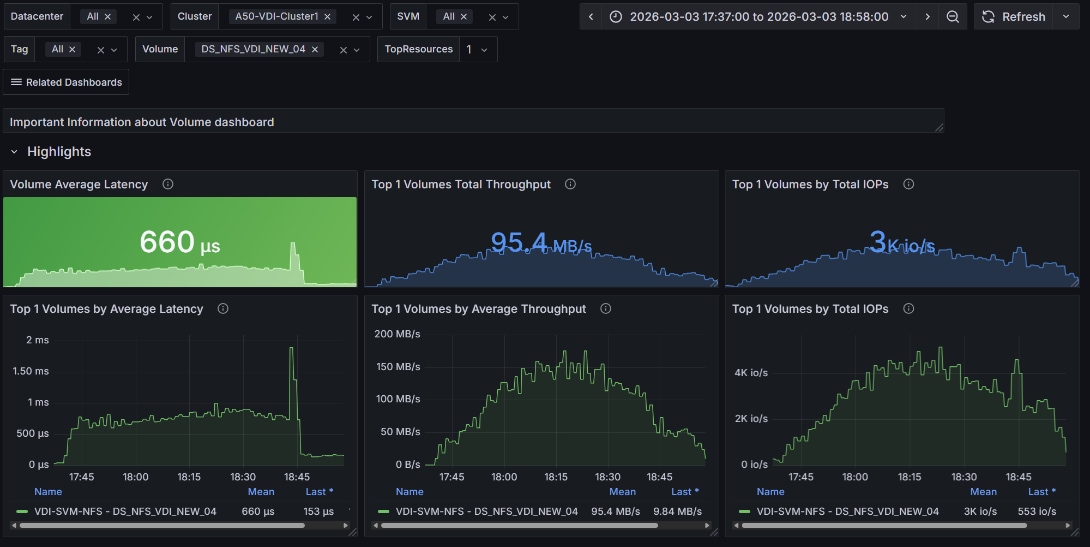
1600 Users MCS Non-Persistent Desktops Cluster Test
NetApp AFF A50 Test Results for 1600 Non-Persistent Windows 11 x64 Citrix MCS Desktops
For this test, 4 volumes were used, and the average latency is way below 1ms for all the volumes and the latency was not higher than 1ms at any time.
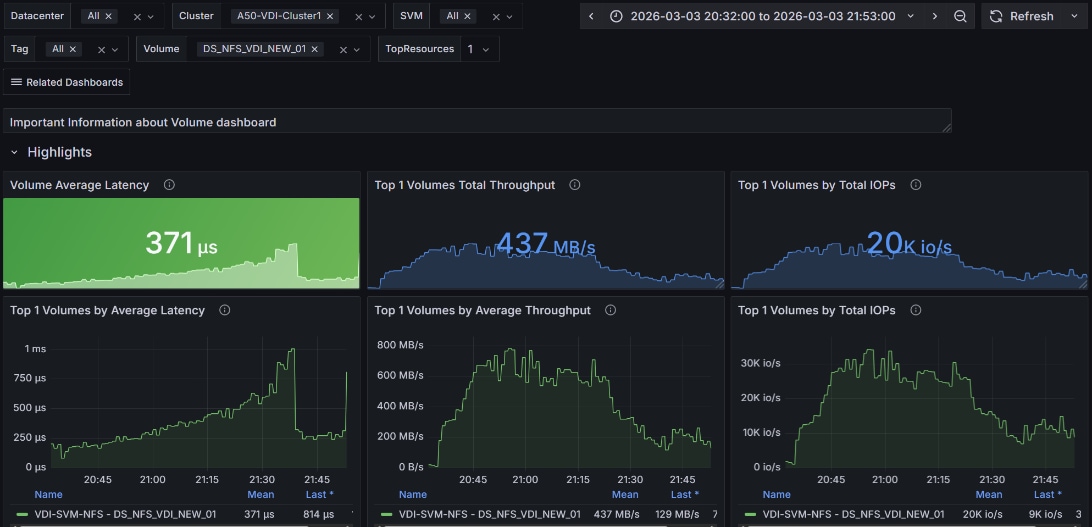
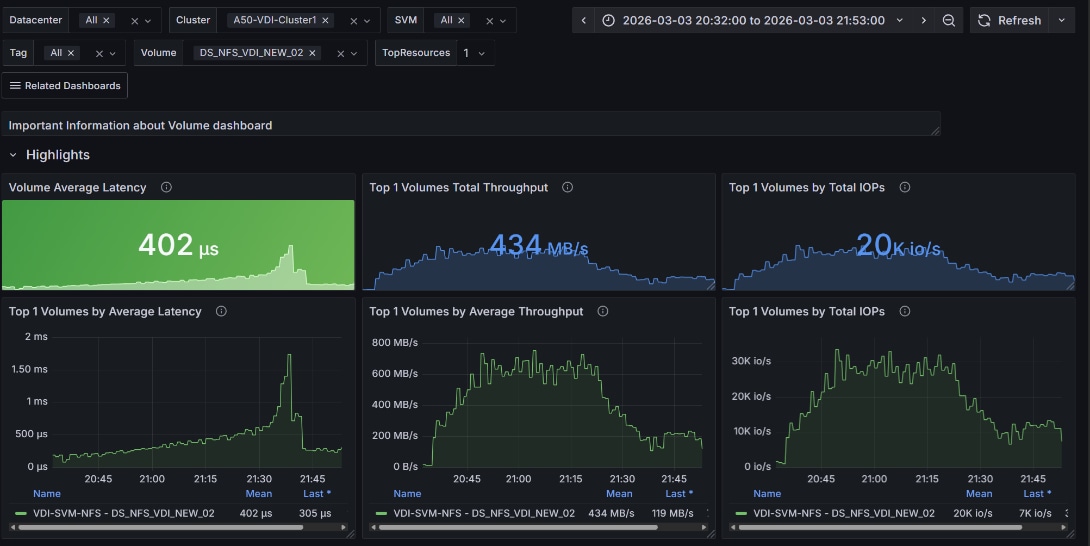
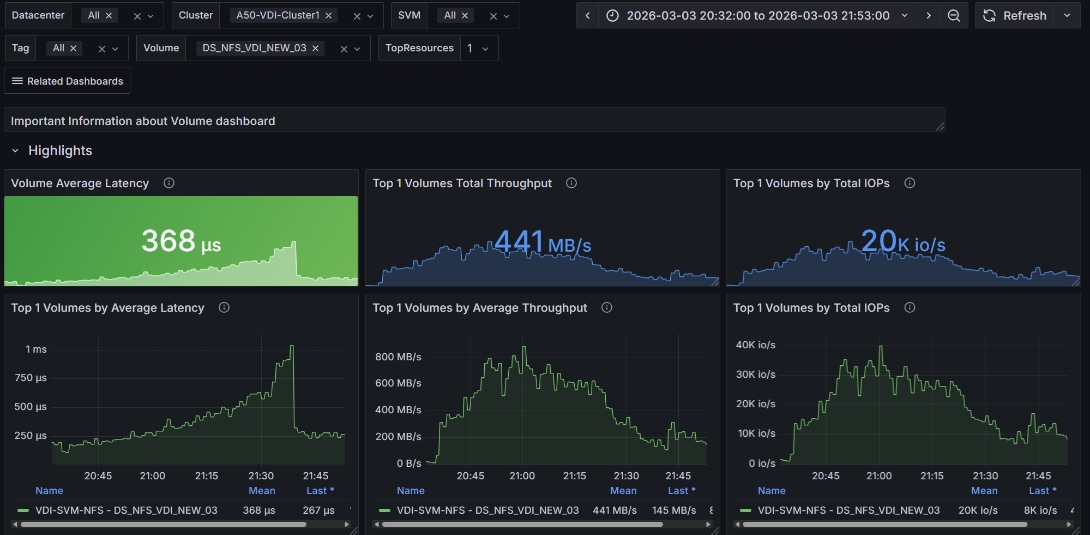
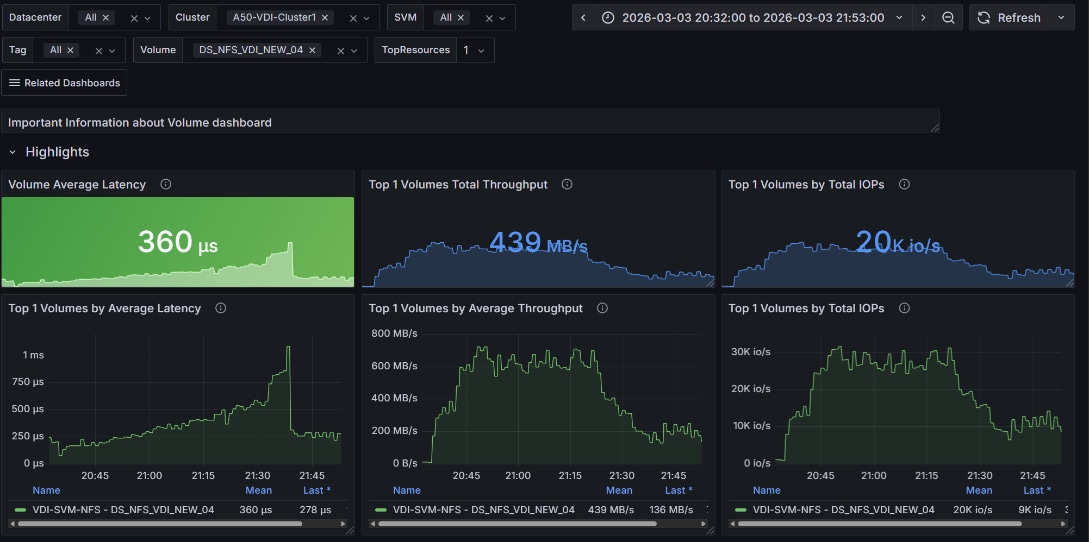
Scalability Considerations and Guidelines
There are many factors to consider when you begin to scale beyond 2600 Users, which this reference architecture has successfully tested. This 2600-seat solution provides a large-scale building block that can be replicated to confidently scale-out to tens of thousands of users.
As our results indicate, we have proven linear scalability in the Cisco UCS Reference Architecture as tested:
● Cisco UCS domains consist of a pair of Fabric Interconnects and a pair of chassis that can easily be scaled out with VDI growth.
● With Intersight, you get all of the benefits of SaaS delivery and full lifecycle management of distributed Intersight-connected servers and third-party storage across data centers, remote sites, branch offices, and edge environments. This empowers you to analyze, update, fix, and automate your environment in ways that were not possible with prior generations' tools. As a result, your organization can achieve significant TCO savings and deliver applications faster in support of new business initiatives.
● As scale grows, the value of the combined Cisco UCS fabric and Cisco Nexus physical switches increases dramatically to define the Quality of Services required to deliver excellent end user experience 100 percent of the time.
● To accommodate the Cisco Nexus 9000 upstream connectivity in the way we describe in the network configuration section, two Ethernet uplinks are needed to be configured on the Cisco UCS 6536 Fabric Interconnect.
The backend storage has to be scaled accordingly, based on the IOPS considerations described in the NetApp scaling section. Please refer the NetApp section that follows this one for scalability guidelines.
NetApp AFF Storage Guidelines for Scale Desktop Virtualization Workloads
Storage sizing has three steps:
1. Gathering solution requirements.
2. Estimating storage capacity and performance.
3. Obtaining recommendations for the storage configuration.
Solution Assessment
Assessment is an important first step. Lakeside VDI Assessment is recommended to collect network, server, and storage requirements.
Virtual desktop sizing depends on the following:
● The number of the seats
● The VM workload (applications, VM size, and VM OS)
● The connection broker (Citrix Virtual Apps and Desktops)
● The hypervisor type (vSphere, Citrix Hypervisor, or Hyper-V)
● The provisioning method (NetApp clone, Linked clone, PVS, and MCS)
● Future storage growth
● Disaster recovery requirements
● User home directories
NetApp has developed a sizing tool called the System Performance Modeler (SPM) that simplifies the process of performance sizing for NetApp systems. It has a step-by-step wizard to support varied workload requirements and provides recommendations for meeting your performance needs.
Storage sizing has two factors: capacity and performance. NetApp recommends using the NetApp SPM tool to size the virtual desktop solution. To use this tool, contact NetApp partners and NetApp sales engineers who have the access to SPM. When using the NetApp SPM to size a solution, NetApp recommends separately sizing the VDI workload (including the write cache and personal vDisk if used), and the CIFS profile and home directory workload. When sizing CIFS, NetApp recommends sizing with a heavy user workload. Eighty percent concurrency was assumed in this solution.
Capacity Considerations
Deploying Citrix Virtual Apps and Desktops with PVS imposes the following capacity considerations:
● vDisk. The size of the vDisk depends on the OS and the number of applications installed. It is a best practice to create vDisks larger than necessary in order to leave room for any additional application installations or patches. Each organization should determine the space requirements for its vDisk images. For example, a 20GB vDisk with a Windows 7 image is used. NetApp deduplication can be used for space savings.
● Write cache file. NetApp recommends a size range of 4 to 18GB for each user. Write cache size is based on what type of workload and how often the VM is rebooted. In this example, 4GB is used for the write-back cache. Since NFS is thin provisioned by default, only the space currently used by the VM will be consumed on the NetApp storage. If iSCSI or FCP is used, N x 4GB would be consumed as soon as a new virtual machine is created.
● PvDisk. Normally, 5 to 10GB is allocated, depending on the application and the size of the profile. Use 20 percent of the master image as a starting point. NetApp recommends running deduplication.
● CIFS home directory. Various factors must be considered for each home directory deployment. The key considerations for architecting and sizing a CIFS home directory solution include the number of users, the number of concurrent users, the space requirement for each user, and the network load. Run deduplication to obtain space savings.
● Infrastructure. Host Citrix Virtual Apps and Desktops, PVS, SQL Server, DNS, and DHCP.
The space calculation formula for a 2000-seat deployment is as follows: Number of vDisk x 20GB + 2000 x 4GB write cache + 2000 x 10GB PvDisk + 2000 x 5GB user home directory x 70% + 500 x 1GB vSwap + 500GB infrastructure.
Performance Considerations
Defining your performance requirements is essential. To ensure an optimal setup, contact your NetApp account team to obtain the latest information about the tools you can use and the recommended software and hardware configurations.
Size, the read/write ratio, and random or sequential reads comprise the I/O considerations. We use 90 percent write and 10 percent read for PVS workload. Storage CPU utilization must also be considered. Table 23 can be used as guidance for your sizing calculations for a PVS workload when using a LoginVSI heavy workload.
Table 23. Typical IOPS without RAM Cache plus Overflow Feature
|
|
Boot IOPS |
Login IOPS |
Steady IOPS |
| Write Cache (NFS) |
8-10 |
9 |
7.5 |
| vDisk (CIFS SMB 3) |
0.5 |
0 |
0 |
| Infrastructure (NFS) |
2 |
1.5 |
0 |
Scalability of Citrix Virtual Apps and Desktops 7 LTSR Configuration
Citrix Virtual Apps and Desktops environments can scale to large numbers. When implementing Citrix Virtual Apps and Desktops, consider the following in scaling the number of hosted shared and hosted virtual desktops:
● Types of storage in your environment
● Types of desktops that will be deployed
● Data protection requirements
● For Citrix Provisioning Server pooled desktops, the write cache sizing and placement
When designing and deploying this CVD environment Cisco and Citrix recommends using N+1 schema for virtualization host servers to accommodate resiliency. In all Reference Architectures (such as this CVD), this recommendation is applied to all host servers.
The entire Cisco solution for VDI on FlexPod was deployed and managed on Cisco Intersight. All policies and profiles were deployed using tried and true best practices for VDI on Cisco UCS systems.
Citrix Cloud is a platform that hosts and administers Citrix cloud services. It connects to your resources through connectors on any cloud or infrastructure you choose (on-premises, public cloud, private cloud, or hybrid cloud). It allows you to create, manage, and deploy workspaces with apps and data to your end-users from a single console.
To learn more about key service components in Citrix Cloud, see the following resources:
● Citrix Workspace conceptual diagram: Provides an overview of key areas such as identity, workspace intelligence, and single sign-on.
● Reference Architectures: Provides comprehensive guides for planning your Citrix Workspace implementation, including use cases, recommendations, and related resources.
● Citrix DaaS reference architectures: Provides in-depth guidance for deploying Citrix DaaS (formerly Virtual Apps and Desktops service) with related services.
With this test, the Citrix Cloud was configured to run on-premise virtual desktops for user access. For more information, see https://docs.citrix.com/en-us/tech-zone/learn/poc-guides/cvads.html
For the users to have desktops available in the event of an on-premise failure, the Citrix desktops were configured in the Microsoft Azure tenant, to copy the user data and virtual machines using ONTAP. For more information, see https://docs.citrix.com/en-us/citrix-daas-azure.html
Microsoft Azure and Citrix Cloud
Procedure 1. Solution Steps
Step 1. Configure Azure Active Directory to enable directory services are consistent.
Step 2. Create Public IP for the CSR/VPN gateway.
Step 3. Configure on-prem subnets in the Azure Local Network Gateway.
Step 4. Configure subnets for Azure resource use to create the Virtual Network Gateway and creating Azure based subnets.
Step 5. Create a site to site VPN with Cisco CSR to connect the on-premise resources with Azure resources.
Step 6. Test two way connectivity between on-prem subnets and Azure subnets.
Step 7. Build virtual machines in Azure with software and Citrix image.
Step 8. In Citrix Cloud create hosting connection and catalog to Microsoft Azure.
Step 9. Add on-prem and cloud VMs to a single desktop delivery group
For more information, see https://docs.citrix.com/en-us/citrix-daas-azure/catalogs-create.html#creating-catalogs-of-azure-ad-domain-joined-machines
When the on-premise desktops are no longer available, the Microsoft Azure-based desktops will power on and register with the delivery group. You will be able to access their corporate desktops while their data and files are being replicated using NetApp’s Cloud technology previously described.
FlexPod delivers a platform for enterprise end user computing deployments and cloud data centers using Cisco UCS Compute Node and Rack Servers, Cisco fabric interconnects, Cisco Nexus 9000 switches, Cisco MDS 9100 fibre channel switches and NetApp Storage AFF A50 Storage Array. FlexPod is designed and validated using compute, network and storage best practices and high availability to reduce deployment time, project risk and IT costs while maintaining scalability and flexibility for addressing a multitude of IT initiatives. This CVD validates the design, performance, management, scalability, and resilience that FlexPod provides to customers wanting to deploy enterprise-class VDI.
Vadim Lebedev—Leader, Technical Marketing, CSPG UCS Solutions – US, Cisco Systems, Inc.
Vadim Lebedev has been a part of Cisco's Computing Systems Product Group team for the last ten years, where he focuses on designing, testing validating solutions, creating technical content, and conducting performance testing and benchmarking. He has extensive experience in server and desktop virtualization and is considered an expert in desktop/server virtualization, Cisco Unified Computing System, Cisco Nexus Switching, and NVIDIA Graphics.
Sweksha Chaubey—Technical Marketing Engineer, NetApp
Sweksha Chaubey is a Technical Marketing Engineer at NetApp. She joined NetApp in 2025 having joined the organization as a college fresher. She has built a strong foundational understanding of NetApp ONTAP and related storage technologies through hands-on learning and practical exposure.
For their support and contribution to the design, validation, and creation of this Cisco Validated Design, the authors would like to thank:
● Bobby Oommen - Sr. Manager, Technical Marketing, NetApp
● Abhinav Singh - Sr. Technical Marketing Engr, NetApp
● Kamini Singh - Technical Marketing Engineer, NetApp
This section provides links to additional information for each partner’s solution component of this document.
Cisco Intersight Configuration Guides
● https://intersight.com/help/saas/supported_systems#supported_hardware_for_intersight_managed_mode
Cisco Nexus Switching References
● https://www.cisco.com/c/en/us/support/switches/nexus-9000-series-switches/series.html
● http://www.cisco.com/c/en/us/products/switches/nexus-N9K-C93180YC-FX -switch/index.html
Cisco MDS 9000 Service Switch References
● http://www.cisco.com/c/en/us/products/storage-networking/product-listing.html
● https://docs.citrix.com/en-us/citrix-virtual-apps-desktops/2402-ltsr
● https://docs.citrix.com/en-us/provisioning/2402-ltsr/
● Citrix VDI Handbook 2402 LTSR
VMware References
● https://techdocs.broadcom.com/us/en/vmware-cis/vsphere/vsphere/8-0.html
● https://technet.microsoft.com/en-us/library/hh831620(v=ws.11).aspx
● https://technet.microsoft.com/en-us/library/dn281793(v=ws.11).aspx
● https://support.microsoft.com/en-us/kb/2833839
● https://technet.microsoft.com/en-us/library/hh831447(v=ws.11).aspx
● Login Enterprise knowledge base
● NetApp AFF A-series: http://www.netapp.com/us/products/storage-systems/all-flash-array/aff-a-series.aspx
● ONTAP 9: http://www.netapp.com/us/products/data-management-software/ontap.aspx
● NetApp Support Site: https://mysupport.netapp.com/documentation/docweb/index.html?productID=62379⟨uage=en-US
● NetApp Products: http://www.netapp.com/us/products/management-software/
● Hardware Universe: NetApp Hardware Universe
● ONTAP Tools: https://mysupport.netapp.com/site/products/all/details/otv10/downloads-tab
● IMT: Interoperability Matrix Tool
Appendix A: Build of Materials for Cisco Components
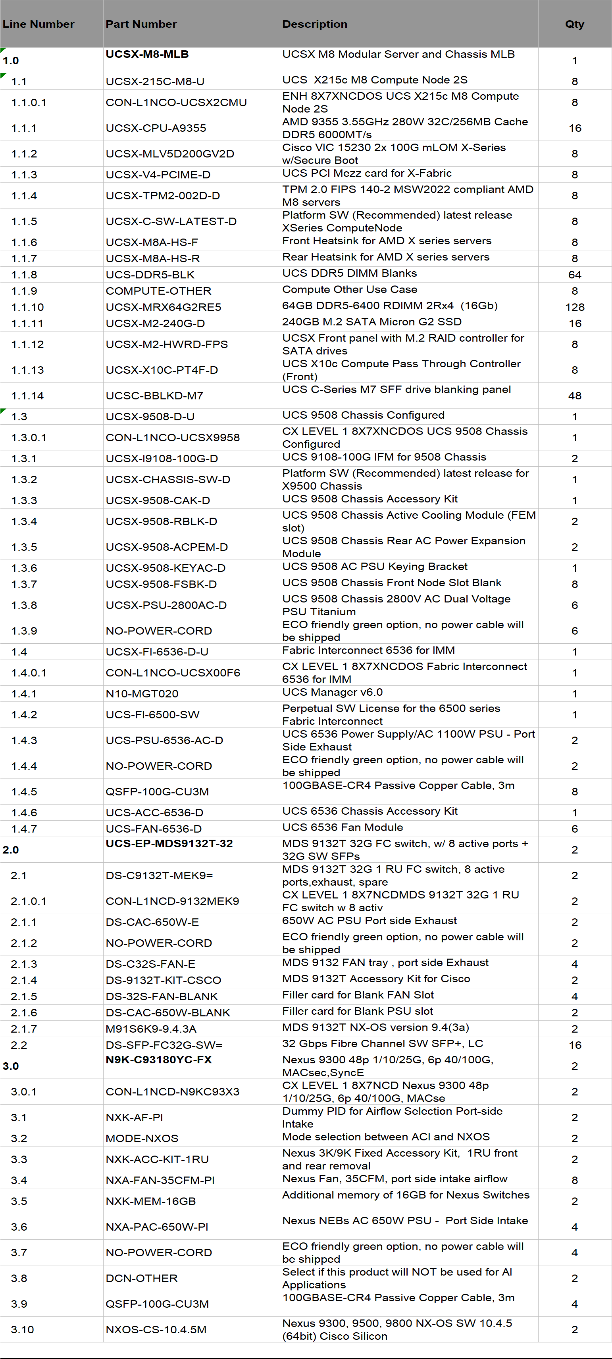
| 20273793 |
AFF-A50 |
|
1 |
| 20273793 |
AFF-A50-001 |
AFF A50 HA System |
2 |
| 20273793 |
AFF-A50A-HA-SSA |
AFF A50 System Serial Attached |
2 |
| 20273793 |
SW-ONTAP-ONE-E-C |
SW,ONTAP One Package, Encryption,-C |
2 |
| 20273793 |
AFF-A50A-100-C |
AFF A50,HA,CTL,Encl,-C |
1 |
| 20273793 |
SW-ONTAP9.16.1-NVE |
SW,ONTAP9.16.1,Data at Rest Encrypt Capable |
2 |
| 20273793 |
SW-ONTAPO-FLASH-A50-C |
SW,ONTAP One Package, Per TB,Flash,A50,-C |
15 |
| 20273793 |
SW-ONTP-FLASH-A50-PR |
SW,ONTAP, Per TB,Flash,Cap Pricing,A50 |
15 |
| 20273793 |
SW-OTHR-OO-FLASH-A50-PR |
SW,OTHER,OO,Per TB,Flash,Cap Pricing,A50 |
15 |
| 20273793 |
X60132A-C |
IO Module,4PT,10/25GbE,-C |
2 |
| 20273793 |
X60130A-C |
IO Module,2PT,100GbE,-C |
4 |
| 20273793 |
X66240A-2-N-C |
Cable,25GbE,SFP28-SFP28,Cu,2m,-C |
8 |
| 20273793 |
X66200-2-N-C |
Cable,Cntlr-Switch OM4,MPO/MPO,2m,-C |
6 |
| 20273793 |
X65405-N-C |
QSFP28,100GbE,SR,-C |
4 |
| 20273793 |
X65402-N-C |
QSFP,Opt,40Gb,Shortwave,-C |
4 |
| 20273793 |
X-02659-00-N-C |
Rail Kit,4-Post,Rnd/Sq-Hole,Adj,24-32,-C |
1 |
| 20273793 |
X800-42U-R6-C |
Jumper Crd,In-Cab,C13-C14,-C |
2 |
| 20273793 |
X60300A-C |
Blanking Panel,IO Module |
2 |
| 20273793 |
X97602A-C |
Power Supply,1600W,Titanium,-C |
2 |
| 20273793 |
SWITCHLESS |
2-Node Switchless Cluster |
1 |
| 20273793 |
PERSONALITY-DNA |
Platform Personality DNA |
16 |
| 20273793 |
CLUSTER-HA-IO-40G-100G |
Card for HA and can also include Cluster |
2 |
| 20273793 |
DATA-AT-REST-ENCRYPTION |
Data at Rest Encryption Capable Operating Sys |
2 |
| 20273793 |
MULTIPATH-C |
Multipath configuration |
1 |
| 20273793 |
CS-4HR-REPLACEMENT-A |
4hr Parts Replacement |
1 |
| 20273793 |
SSP-G1A-ADVISOR |
Advisor,SW Support |
1 |
| 20273793 |
SVC-G1A-ADVISOR |
Advisor,HW Support |
1 |
| 20273793 |
X4024A-2-A-C |
Drive Pack 2X1.92TB,NVMe4,SED,-C |
4 |
| 20273793 |
X93108A-C |
BLANK,DSK DRV FILLER,NS224,-C |
16 |
| 20273793 |
PS-DEPLOY-STAND-AFF-M |
PS Deployment,Standard,AFF,Med |
1 |
| 20273793 |
CS-4HR-REPLACEMENT-A |
4hr Parts Replacement |
0 |
| 20273793 |
CS-G1A-SE-ADVISOR |
SupportEdge Advisor |
0 |
| 20273793 |
SW-SMIRROR-CLD-ONTAP-ONE |
|
1 |
| 20273793 |
SW-SMIRROR-CLD |
Snapmirror Cloud SW |
1000000 |
| 20273793 |
SW-S3-SM-ONTAP-ONE |
|
1 |
| 20273793 |
SW-S3-SMIRROR |
S3 SnapMirror SW |
1000000 |
CVD Program
ALL DESIGNS, SPECIFICATIONS, STATEMENTS, INFORMATION, AND RECOMMENDATIONS (COLLECTIVELY, "DESIGNS") IN THIS MANUAL ARE PRESENTED "AS IS," WITH ALL FAULTS. CISCO AND ITS SUPPLIERS DISCLAIM ALL WARRANTIES, INCLUDING, WITHOUT LIMITATION, THE WARRANTY OF MERCHANTABILITY, FITNESS FOR A PARTICULAR PURPOSE AND NONINFRINGEMENT OR ARISING FROM A COURSE OF DEALING, USAGE, OR TRADE PRACTICE. IN NO EVENT SHALL CISCO OR ITS SUPPLIERS BE LIABLE FOR ANY INDIRECT, SPECIAL, CONSEQUENTIAL, OR INCIDENTAL DAMAGES, INCLUDING, WITHOUT LIMITATION, LOST PROFITS OR LOSS OR DAMAGE TO DATA ARISING OUT OF THE USE OR INABILITY TO USE THE DESIGNS, EVEN IF CISCO OR ITS SUPPLIERS HAVE BEEN ADVISED OF THE POSSIBILITY OF SUCH DAMAGES.
THE DESIGNS ARE SUBJECT TO CHANGE WITHOUT NOTICE. USERS ARE SOLELY RESPONSIBLE FOR THEIR APPLICATION OF THE DESIGNS. THE DESIGNS DO NOT CONSTITUTE THE TECHNICAL OR OTHER PROFESSIONAL ADVICE OF CISCO, ITS SUPPLIERS OR PARTNERS. USERS SHOULD CONSULT THEIR OWN TECHNICAL ADVISORS BEFORE IMPLEMENTING THE DESIGNS. RESULTS MAY VARY DEPENDING ON FACTORS NOT TESTED BY CISCO.
CCDE, CCENT, Cisco Eos, Cisco Lumin, Cisco Nexus, Cisco StadiumVision, Cisco TelePresence, Cisco WebEx, the Cisco logo, DCE, and Welcome to the Human Network are trademarks; Changing the Way We Work, Live, Play, and Learn and Cisco Store are service marks; and Access Registrar, Aironet, AsyncOS, Bringing the Meeting To You, Catalyst, CCDA, CCDP, CCIE, CCIP, CCNA, CCNP, CCSP, CCVP, Cisco, the Cisco Certified Internetwork Expert logo, Cisco IOS, Cisco Press, Cisco Systems, Cisco Systems Capital, the Cisco Systems logo, Cisco Unified Computing System (Cisco UCS), Cisco UCS B-Series Compute Node Servers, Cisco UCS C-Series Rack Servers, Cisco UCS S-Series Storage Servers, Cisco UCS X-Series, Cisco Intersight, Cisco UCS Management Software, Cisco Unified Fabric, Cisco Application Centric Infrastructure, Cisco Nexus 9000 Series, Cisco Nexus 7000 Series. Cisco Prime Data Center Network Manager, Cisco NX-OS Software, Cisco MDS Series, Cisco Unity, Collaboration Without Limitation, EtherFast, EtherSwitch, Event Center, Fast Step, Follow Me Browsing, FormShare, GigaDrive, HomeLink, Internet Quotient, IOS, iPhone, iQuick Study, LightStream, Linksys, MediaTone, MeetingPlace, MeetingPlace Chime Sound, MGX, Networkers, Networking Academy, Network Registrar, PCNow, PIX, PowerPanels, ProConnect, ScriptShare, SenderBase, SMARTnet, Spectrum Expert, StackWise, The Fastest Way to Increase Your Internet Quotient, TransPath, WebEx, and the WebEx logo are registered trade-marks of Cisco Systems, Inc. and/or its affiliates in the United States and certain other countries. (LDW_P7)
All other trademarks mentioned in this document or website are the property of their respective owners. The use of the word partner does not imply a partnership relationship between Cisco and any other company. (0809R)