Describes Snort 2 to Snort 3 migration scenarios and examples.
Migrate from Snort 2 to Snort 3
Migrating from Snort 2 to Snort 3
-
involves converting and adapting the Snort 2 rules to the Snort 3 rule syntax,
-
optimizes the rules for improved detection and performance, and
-
allows organizations to leverage the enhanced features and capabilities of Snort 3.
Organizations with Threat Defense devices managed by the Secure Firewall Management Center can opt for a hybrid deployment approach during the migration from Snort 2 to Snort 3. This approach allows for a gradual transition and minimizes potential disruptions, if any.
Benefits of migrating to snort 3
Snort 3 provides
-
Enhanced protocol support: Snort 3 provides improved protocol support, allowing you to detect and monitor threats across a wide range of modern protocols, including encrypted traffic.
-
Streamlined rule management: Snort 3 offers a more user-friendly rule language and rule management system, making it easier to create, modify, and manage rules effectively.
-
Improved performance: Snort 3 has been optimized to handle higher traffic volumes more efficiently, ensuring timely threat detection and reducing the risk of performance bottlenecks.
Sample business scenario
This sample business scenario is an illustrative situation that
-
demonstrates how organizations evaluate network security inspection engine migrations,
-
shows the roles and motivations of security analysts and network administrators in technology decisions, and
-
highlights the benefits of upgrading from legacy to modern security monitoring solutions.
Organizational migration scenario
Alice works as a security analyst in a large organization that heavily relies on the Snort inspection engine to monitor and protect their network infrastructure. The organization has been using Snort Version 2 for several years, but they have encountered some limitations and challenges.
Bob, the network administrator, is looking to migrate from Snort 2 to Snort 3 to overcome these issues and enhance his organization's network security capabilities.
This migration will also improve network security monitoring, enhance performance, and streamline rule management.
Best practices for migrating from Snort 2 to Snort 3
Follow these best practices when migrating from Snort 2 to Snort 3 to ensure data integrity and maintain security coverage.
-
Back up your intrusion policy before performing the migration. See the Export Configurations task in the Cisco Secure Firewall Management Center Administration Guide.
-
Before upgrading a device to Snort 3, if changes are made in Snort 2, use the synchronize utility to include the latest synchronization from Snort 2 to Snort 3 so that you can start with a similar coverage. See Synchronize Snort 2 rules with Snort 3.
-
Snort 2 custom rules are not automatically converted to Snort 3 and must be manually migrated. See Convert Snort 2 Custom IPS Rules to Snort 3.
-
Synchronization does not migrate Snort 2 rules with thresholds or suppressions. These rules must be created again in Snort 3.
Prerequisites for migration
Complete these prerequisites before starting the migration process to ensure system readiness and data protection.
-
Have a working knowledge of Snort. To learn about the Snort 3 architecture, see Snort 3 Adoption.
-
Back up your management center. See Backup the Management Center.
-
Back up your intrusion policy. See Exporting Configurations.
End-to-end migration workflow
Summary
Depending on your requirements, go through the stages listed in the workflow to complete the migration of your device from Snort 2 to Snort 3.
Workflow

These are the stages of migrating Snort 2 to Snort 3:
- Enable Snort 3 on the device. See Enable Snort 3 on Threat Defense device.
- Convert Snort 2 rules to Snort 3. See Convert Snort 2 rules of a single intrusion policy to Snort 3.
- Deploy configuration. See Deploy configuration changes.
Enable Snort 3 on Threat Defense device
Enable Snort 3 on your Threat Defense device for enhanced security capabilities.
Use this procedure to upgrade from Snort 2 to Snort 3 on your Threat Defense device.
During the deployment process, there could be a momentary traffic loss because the current inspection engine needs to be shut down.
Procedure
| 1. | Choose . |
|
| 2. | Click the corresponding device to go to the device home page. |
|
| 3. | Click the Device tab. |
|
| 4. | In the Inspection Engine section, click Upgrade. 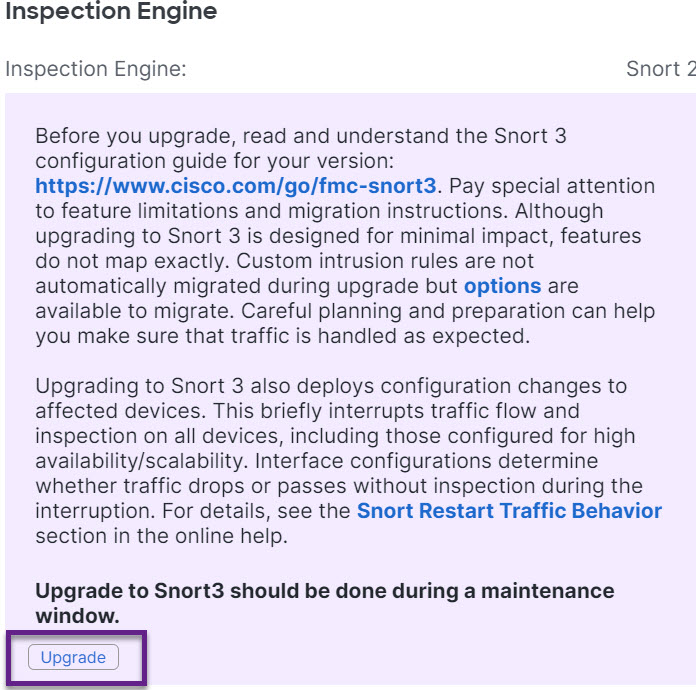
|
|
| 5. | Click Yes. |
What to do next
Deploy the changes on the device. See Deploy configuration changes.
The system converts your policy configurations during the deployment process to make them compatible with the selected Snort version.
Convert Snort 2 rules of a single intrusion policy to Snort 3
This task synchronizes and converts Snort 2 intrusion policy rules to Snort 3 format, ensuring that custom rules, thresholds, and suppressions are properly migrated to maintain security policy effectiveness when using Snort 3 engines.
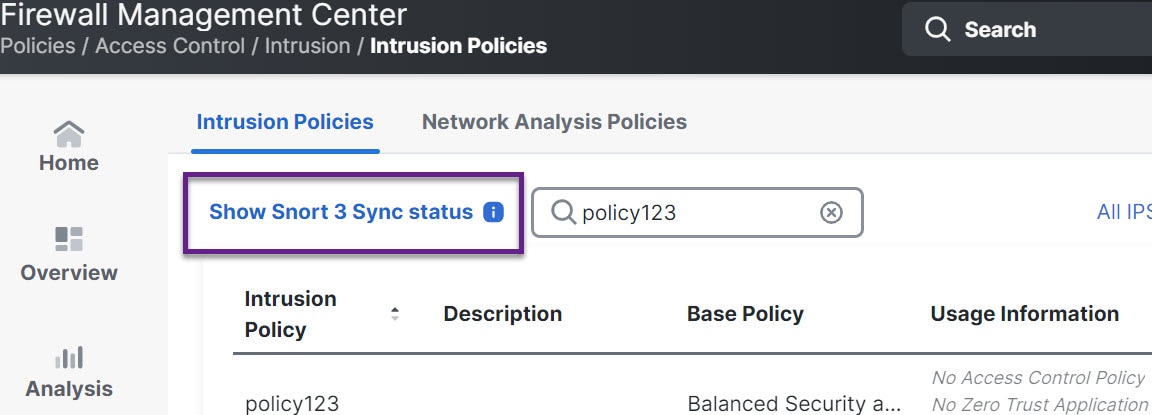
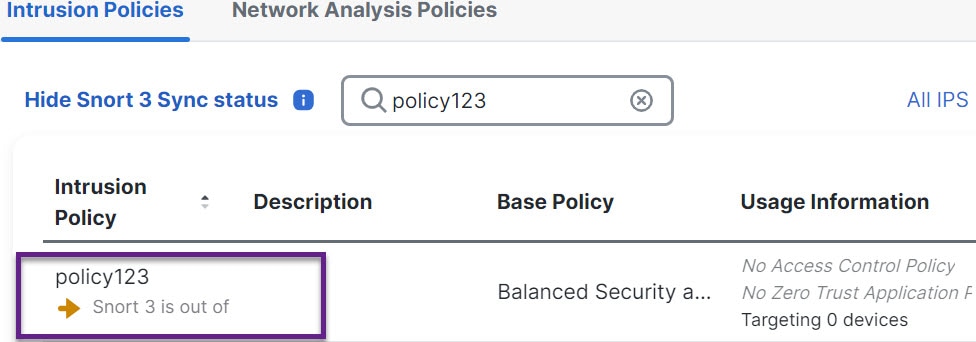
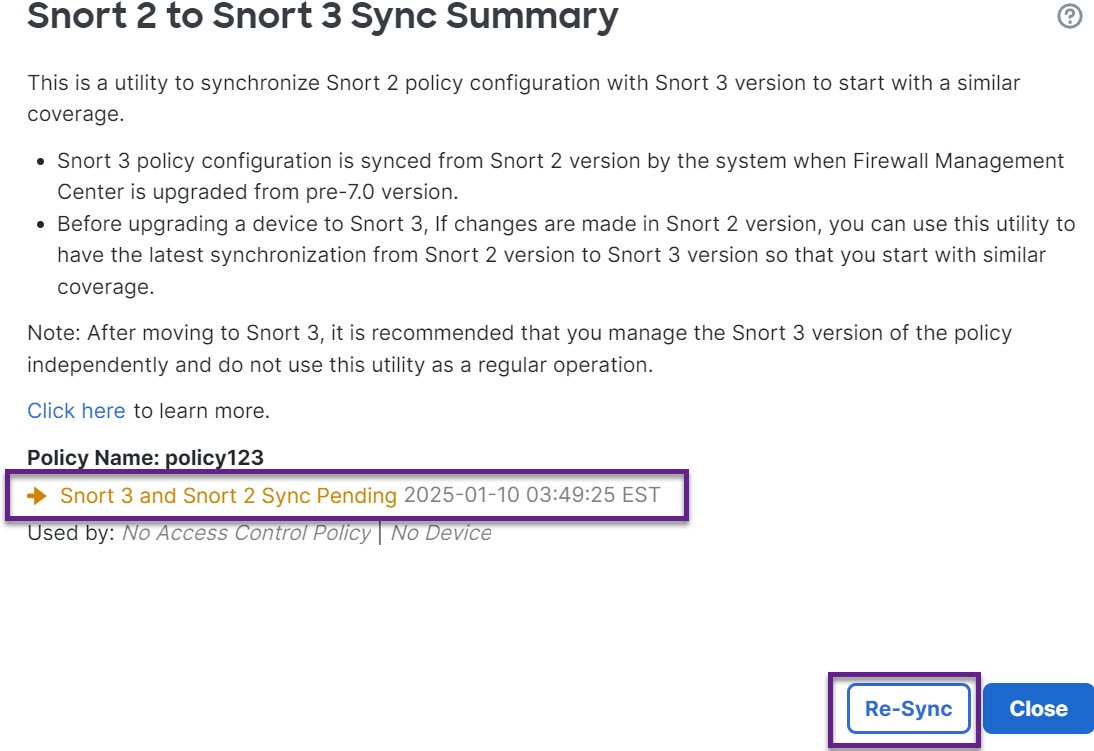
When intrusion policies display an orange arrow indicator, the Snort 2 and Snort 3 versions are not synchronized. The synchronization process uses the snort2Lua tool to convert rules and may require manual intervention for custom rules, thresholds, and suppressions that cannot be automatically migrated.
Before you begin
Follow these steps to convert Snort 2 rules of a single intrusion policy to Snort 3:
Procedure
| 1. | Choose .
|
|
| 2. | To migrate the 76 custom rules, perform either one of these steps:
|
|
| 3. | Click the Download Summary Details link to download the rules in .txt format. This is a sample of the summary that is displayed. Example: |
|
| 4. | Click Close to close the Sync Summary dialog box. |
|
| 5. | To check the rules with status: ERROR, choose and click the Snort 2 version of the intrusion policy. |
|
| 6. | Under Policy Information, click Rules and filter for the rule. For example, enter PSNG_TCP_PORTSCAN in the Filterfield to find the rule. |
|
| 7. | Click Show Details to view the detailed version of the rule. |
|
| 8. | Create the rule again in Snort 3 using Snort 3 rule guidelines and save the file as a .txt or .rules file. For more information, see www.snort3.org. |
|
| 9. | Upload the custom rule that you just created locally to the list of all the Snort 3 rules. See Add Custom Rules to Rule Groups. |


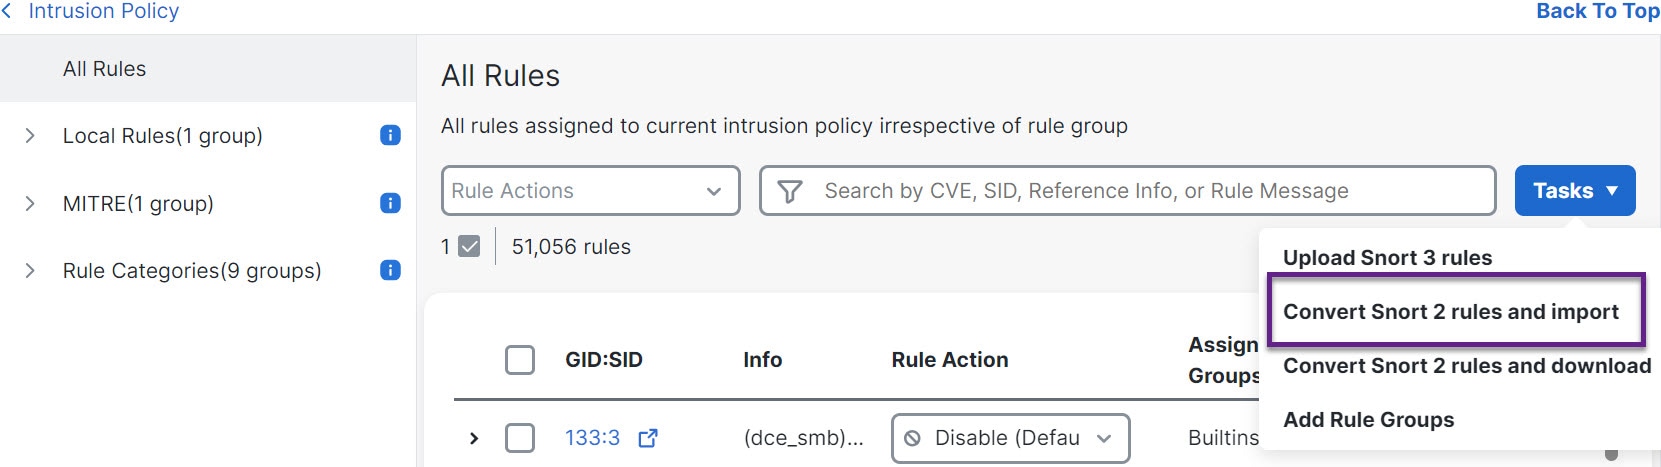


What to do next
Deploy configuration changes. See Deploy configuration changes.