Describes how to generate Snort 3 recommendations for optimizing intrusion detection and prevention based on network traffic analysis and security requirements.
Snort 3 rule recommendations
Snort 3 rule recommendations are a security tuning feature that
-
automatically tune your intrusion policy with rules specific to the host environment,
-
enable additional rules or tune the current rule set by disabling rules for vulnerabilities not present in your network, and
-
use the host database to determine rules that apply to your environment.
How rule recommendations work
The management center builds a database of hosts on your network with details such as the IP address, hostname, operating system, services, users, and client applications through passive discovery. Based on this information, the system maps vulnerabilities to each discovered host. The recommendations feature uses this host database to determine the rules that apply to your environment.
In Snort 3, there are four security levels, each corresponding to a specific Talos policy:
-
Level 1–Connectivity Over Security
-
Level 2–Balanced Security and Connectivity
-
Level 3–Security Over Connectivity
-
Level 4–Maximum Detection
Check the Accept Recommendations to Disable Rules check box to disable rules for vulnerabilities not found on the hosts in your network. Check this option only if you have to trim your rule set because of a high number of alerts, or to improve inspection performance.
For more information, see Secure Firewall recommended rules.
Benefits
-
By configuring recommendations, you can tailor your intrusion policy to detect specific types of threats more effectively using rules that are specific to the host environment.
-
Recommendations contribute to a more efficient and effective incident response process by reducing false positives and false negatives.
Sample business scenario
A sample business scenario is a network security implementation that demonstrates how a large corporate network uses Snort 3 as its primary intrusion detection and prevention system to enhance incident response capabilities through vulnerability-based rule generation and intrusion policy optimization.
Business scenario details
In this scenario, a large corporate network adopts robust network security measures in a rapidly evolving threat landscape. The security team wants to enhance their incident response capabilities by generating recommendations or rule sets based on the vulnerabilities detected in the host network. This helps to optimize their intrusion policies, thereby safeguarding the network more effectively.
Best practices
-
You must have high-quality, accurate host data.
Because of the passive nature of network discovery, your threat defense devices must be positioned as close as possible to your protected hosts. This allows the threat defense devices to watch network traffic to and from these hosts, giving you accurate data about applications, services, and vulnerabilities on your network.
-
Devices should have visibility to east–west traffic flows as well as north–south traffic flows to build an accurate host profile.
-
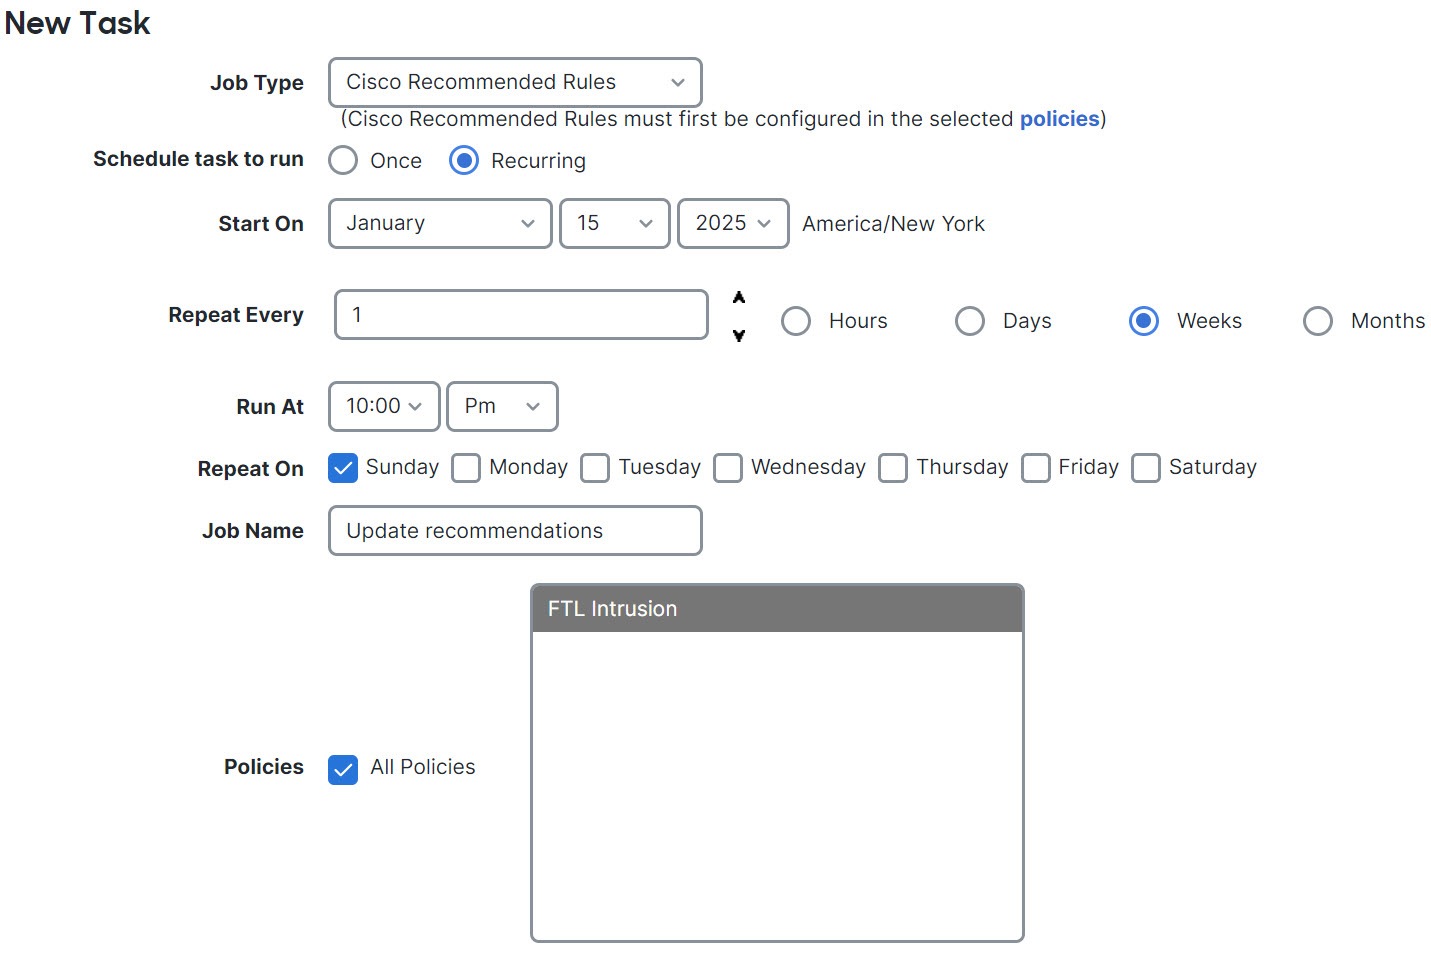
You can create a scheduled task to update recommendations automatically.
Prerequisites for generating recommendations
-
Ensure that hosts are present in the system to generate recommendations.
-
Protected networks configured for recommendations should map to the hosts present in the system.
Generate Snort 3 recommendations
Generate and apply Snort 3 rule recommendations to optimize your intrusion policy based on your network configuration and security requirements.
Snort 3 recommendations help you configure intrusion policies with rules that are tailored to your network environment. The system analyzes your protected networks and suggests appropriate security levels and rule configurations.
Procedure
| 1. | Choose . |
|
| 2. | Click the Snort 3 Version button of the corresponding intrusion policy. |
|
| 3. | Click the Recommendations (Not in Use) layer to configure the rule recommendations. 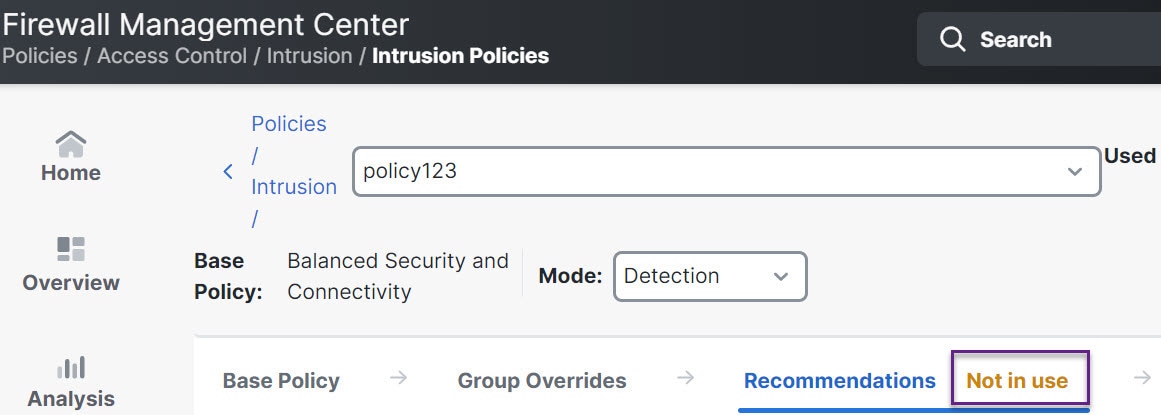
In the Cisco Recommended Rules window, you can set the security level. 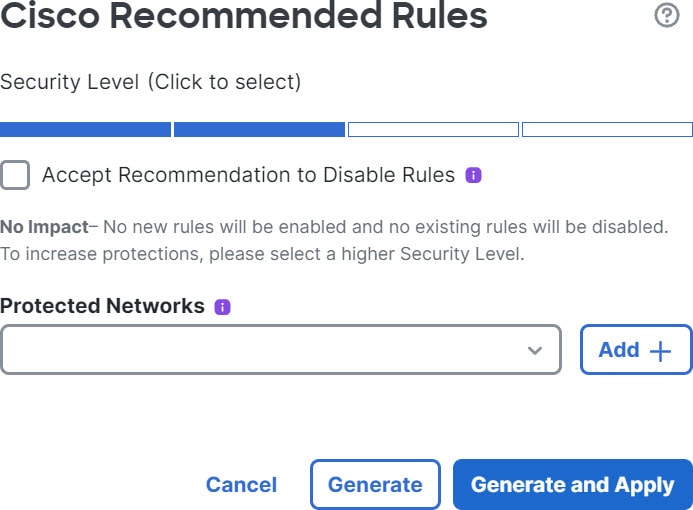
|
|
| 4. | Click to select the security level. |
|
| 5. | (Optional) Check the Accept Recommendation to Disable Rules check box to disable the rules written for vulnerabilities not found on the hosts in your network. Use this option, only if you have to trim your rule set because of a high number of alerts or to improve inspection performance. |
|
| 6. | From the Protected Networks drop-down list, choose the network objects that must be examined by the recommendations. By default, any IPv4 or IPv6 networks are selected if you do not make a selection. Click Add + to create a new network object of type Host or Network and click Save. |
|
| 7. | Generate and apply recommendations:
Recommendations are generated successfully. A new recommendation tab appears with all the recommended rules and their corresponding recommended actions. Rule action preset filters are also available for this tab, in addition to new recommendations. |
|
| 8. | Verify the recommendations and then apply them accordingly:
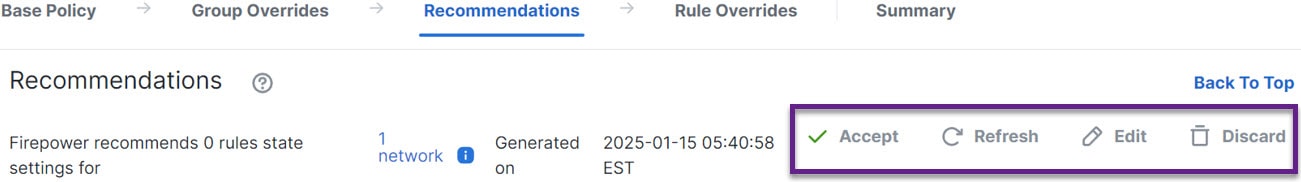
Under All Rules, the Recommended Rules section displays the recommended rules. 
|
|
| 9. | To effectively use recommendations, they must be updated periodically. Follow these steps:
|

What to do next
Deploy configuration changes. Refer to Deploy configuration changes.