Migrate from the Cisco ACI Endpoint Update App to the Cisco APIC Integration with the Secure Firewall Management Center

The following topics discuss the Cisco ACI Endpoint Update App to the Cisco APIC integration with the Secure Firewall Management Center.

About the migration

This chapter discusses how to migrate your configuration and objects from the Cisco ACI Endpoint Update App to the Cisco APIC integration with Secure Firewall Management Center. Among the reasons to migrate:

  • The Cisco APIC integration uses the dynamic attributes connector, which retrieves dynamic objects (that is, network object groups, EPGs, and ESGs) from Cisco APIC and sends them to the Secure Firewall Management Center.


Note


As an alternative to this migration, you can use the Standalone ACI-Endpoint-Update-App.


To migrate, perform the following tasks:

  1. On Cisco APIC, get the site prefix and update interval from the Cisco ACI Endpoint Update App, disable learning, and choose a user with the appropriate privilege level.

    See Migration step 1: Prepare Cisco APIC

  2. On the dynamic attributes connector, create a Cisco APIC connector.

    See Migration step 2: Configure the dynamic attributes connector

  3. As a final verification step, make sure you see objects on the Secure Firewall Management Center.

    See Migration final step: View dynamic objects in the Secure Firewall Management Center.

Migration step 1: Prepare Cisco APIC

Get required information

To migrate to the Cisco APIC integration with Secure Firewall Management Center, you must get all of the following information:

  • Cisco ACI Endpoint Update App site prefix and update interval

  • Cisco APIC tenant name

  • Cisco APIC application profile name

  • EPG name

  • User with at least the read-all role with readPriv access and the tenant-admin role with writePriv access for the security domain that contains the network object groups to send to ASA.

For more information, see Get required information for the integration.

Disable learning for the Cisco ACI Endpoint Update App

To prevent the Cisco ACI Endpoint Update App from communicating with Secure Firewall Management Center, you must disable learning.

  1. Log in to Cisco APIC as a user with the tenant-admin role with writePriv access.

  2. Click Apps.

  3. Under ACI Endpoint Update app, click Open.

  4. Select the check box next to one or more tenants you're integrating with Secure Firewall Management Center.

  5. On the right side of the page, click .

  6. From the list, click Disable Learning.

  7. Select the checkbox to optionally erase all existing learning objects on the Cisco APIC device with which the Cisco ACI Endpoint Update App was previously associated.

  8. Click Submit.

Migration final step: View dynamic objects in the Secure Firewall Management Center

(Optional.) The following task enables you to confirm the integration was successful by viewing dynamic objects in the Secure Firewall Management Center.

Before you begin

Create the Cisco APIC connector as discussed in Create a Cisco APIC connector.

Procedure


Step 1

Log in to the Secure Firewall Management Center

Step 2

Expand Objects > Object Management > External Attributes > Dynamic Object.

Dynamic objects have their own naming conventions; for example, AWS dynamic objects have names like aws_AMAZON.

Dynamic objects created by the integration with Cisco APIC have names matching the pattern:

APIC-site-name_tenant-name_application-profile-name_EPG-or-ESG-name

Example.

Step 3

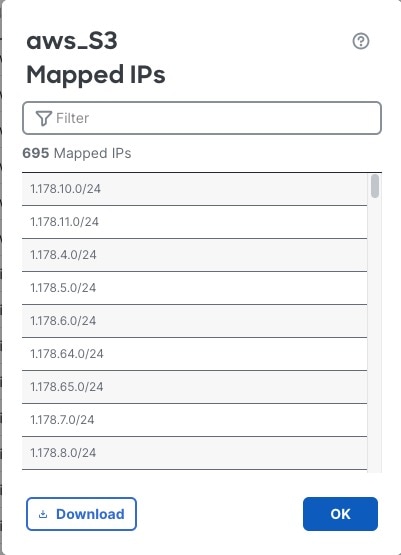
To view IP addresses associated with each dynamic object, click (IPs) at the end of the row.

Example:

Find and optionally download IP addresses associated with a dynamic object