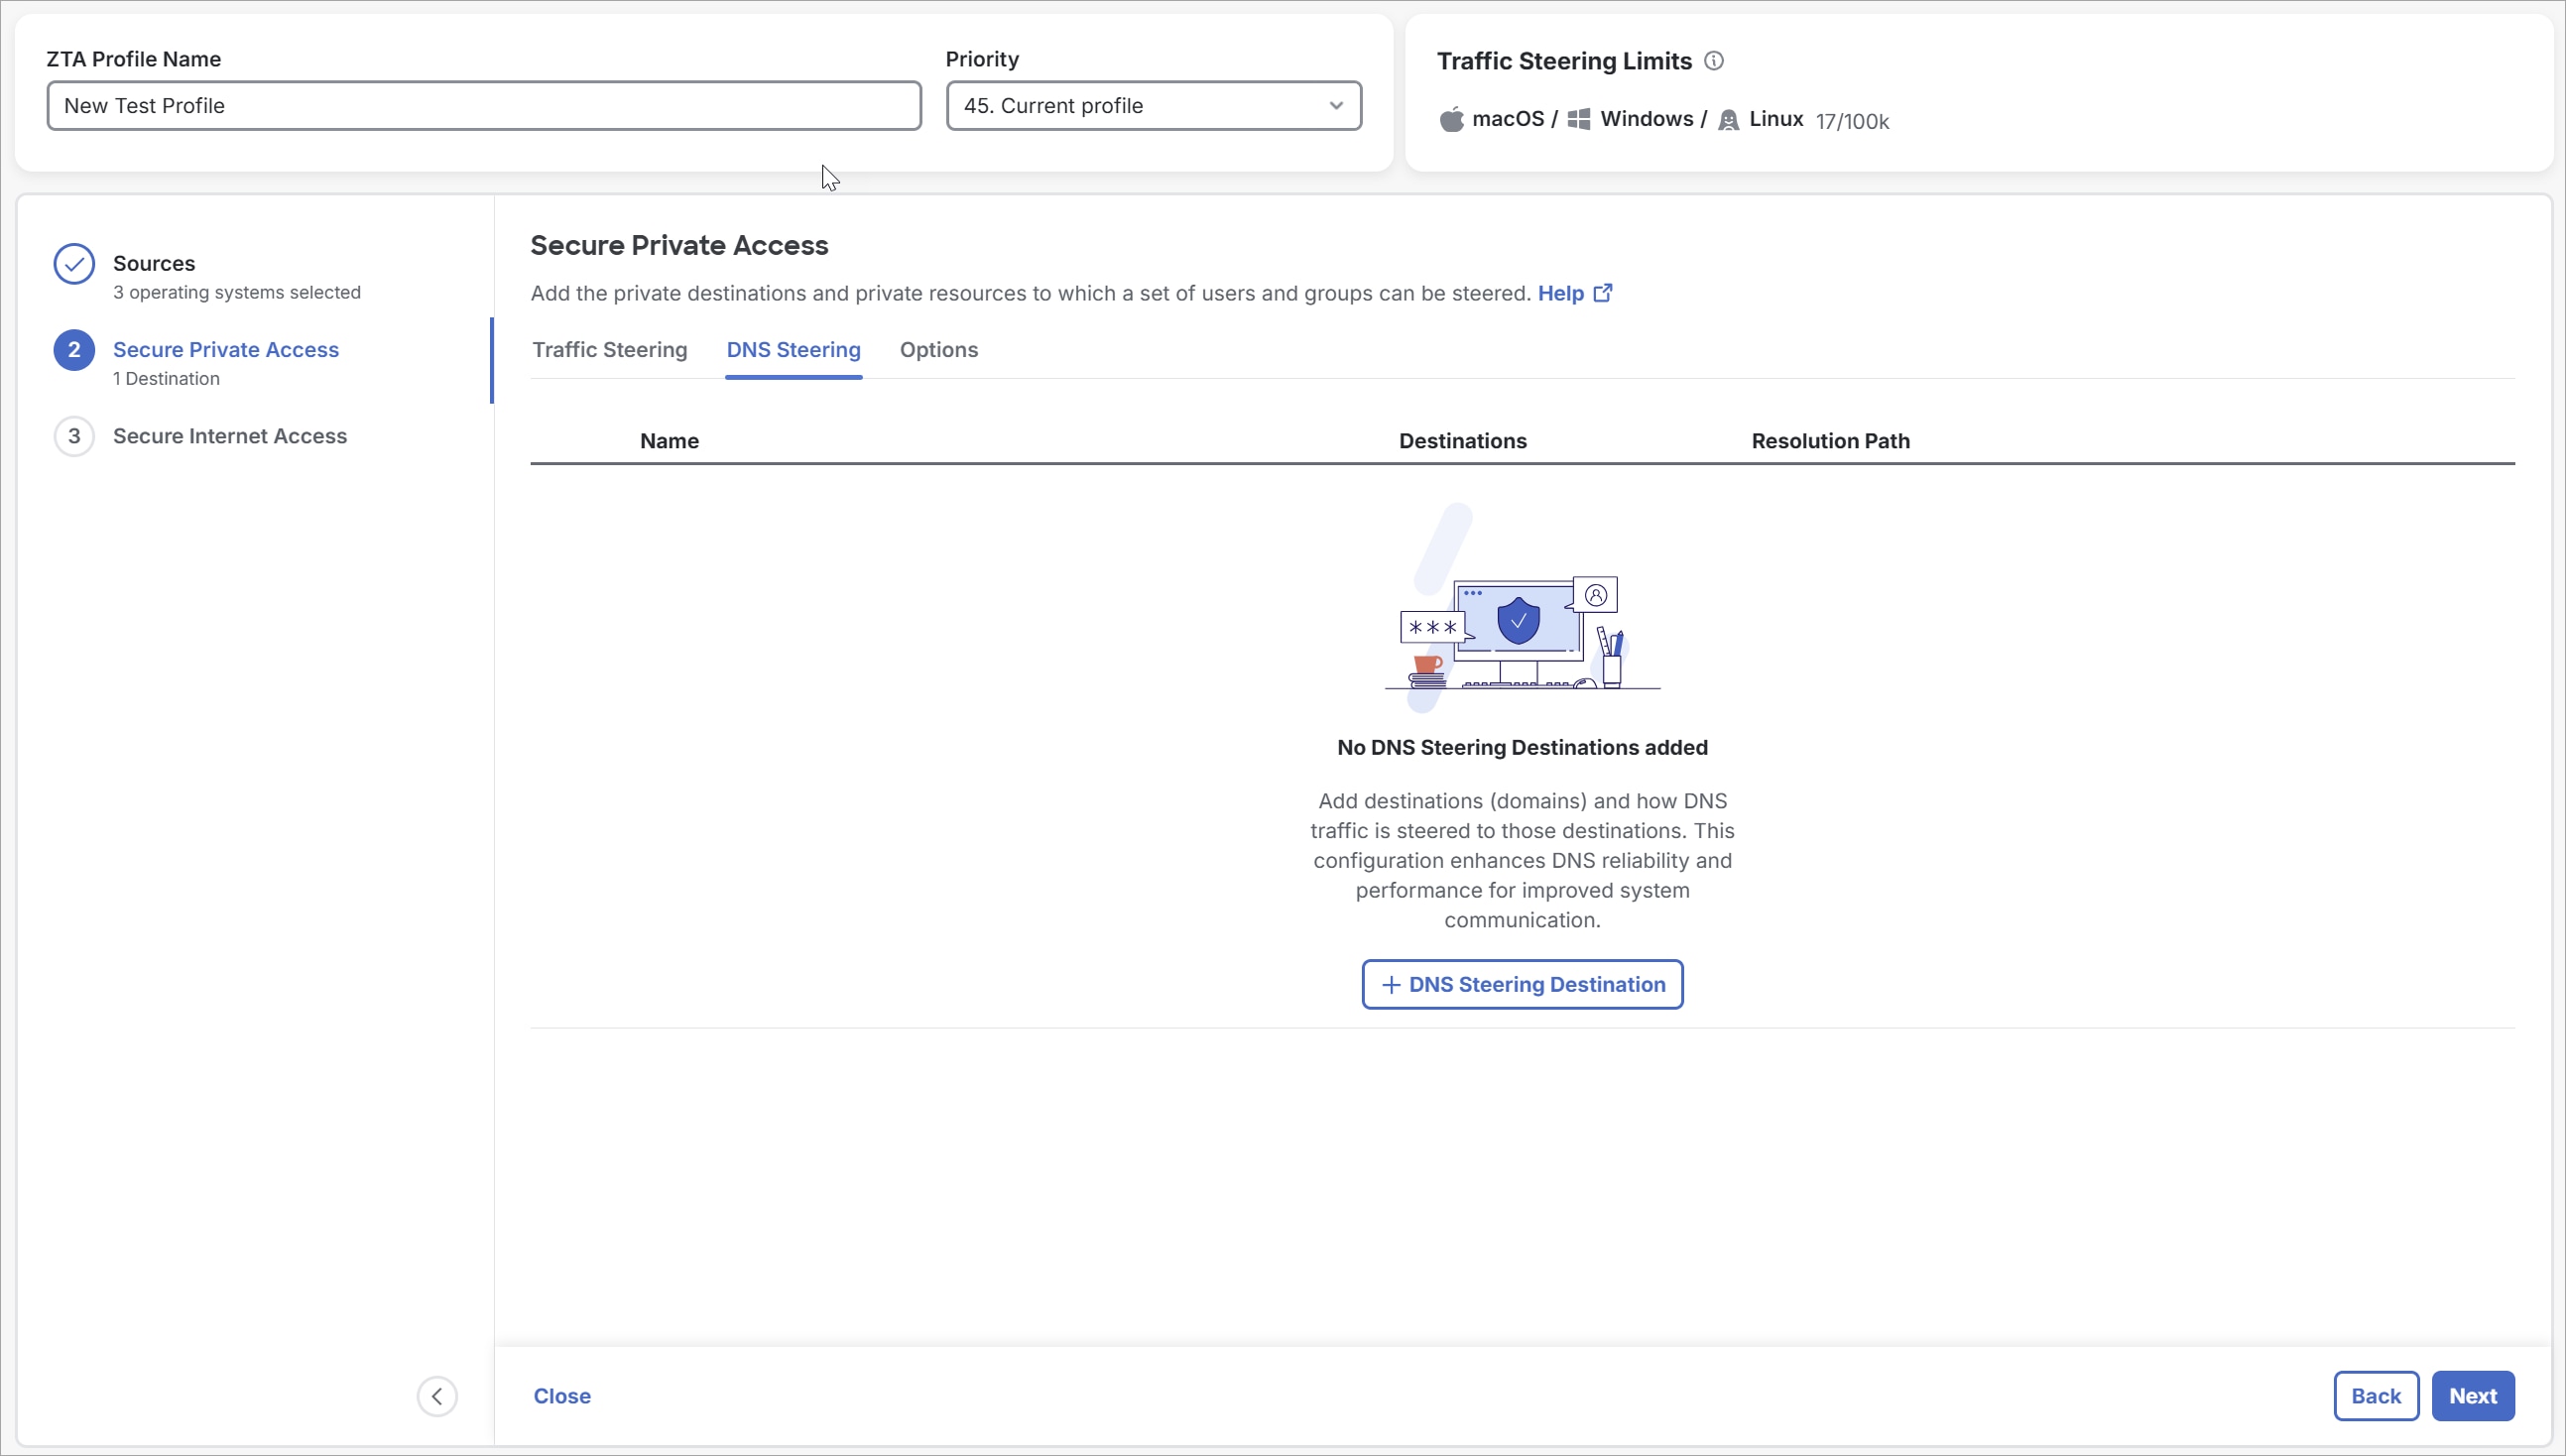
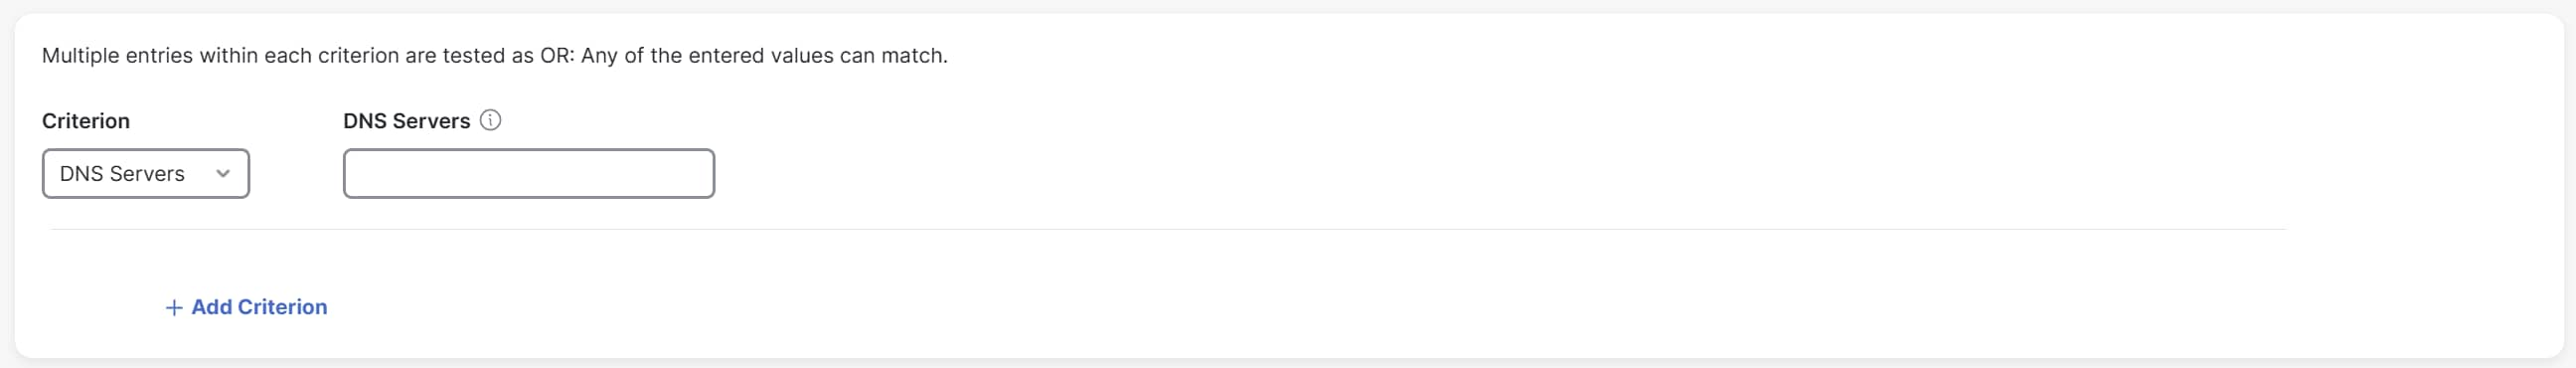
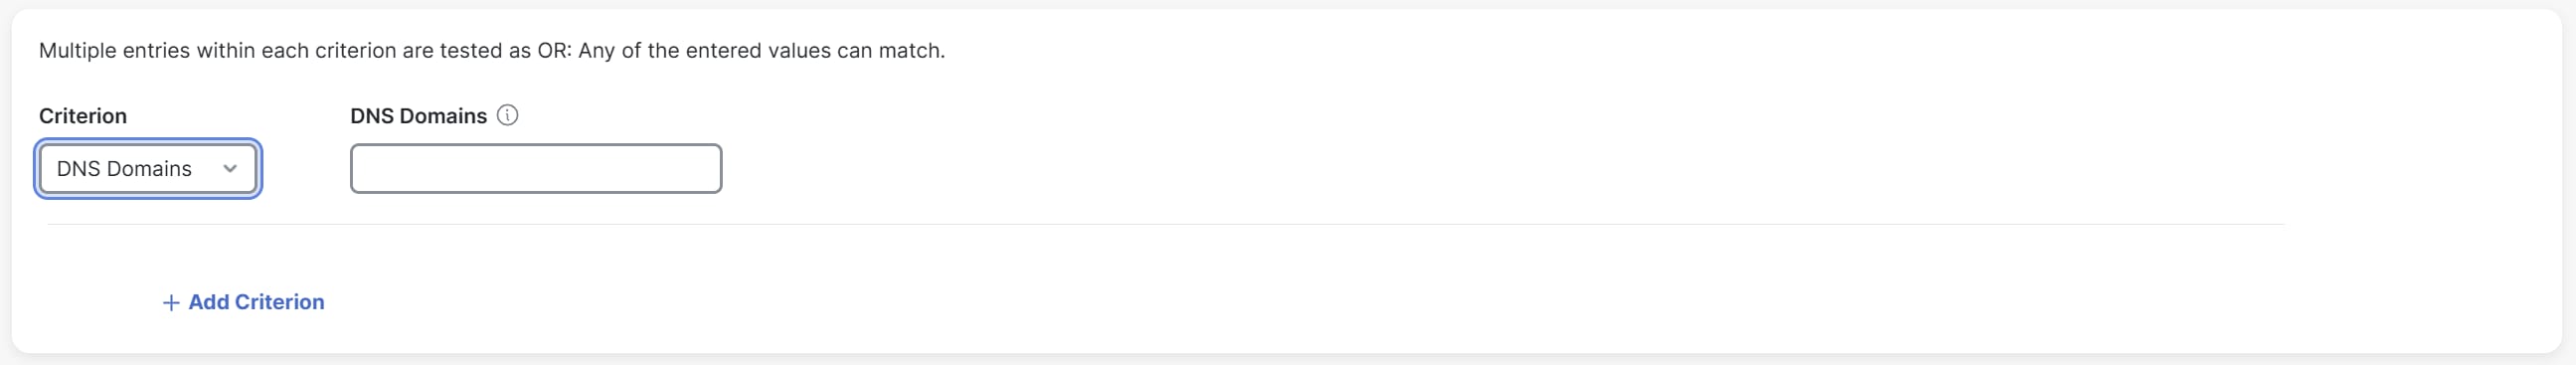
Describes Traffic Steering for Zero Trust Access Client-Based Connections in Cisco Secure Access. DNS Steering selectively directs matching DNS requests based on configured domains to a customer-defined private resolution path where you can resolve matching queries by using one or more specified internal DNS servers.
DNS Steering selectively directs matching DNS requests based on configured domains to a customer-defined private resolution path where you can resolve matching queries by using one or more specified internal DNS servers.
Successful application connectivity still depends on follow-up hostname resolution, policy coverage, and reachability of the returned endpoints through the intended ZTA path. DNS Steering affects how queries are routed, not the DNS records themselves or their authoritative source.
We strongly encourage you to utilize DNS Steering when an applications depends on DNS records to resolve interal services like the following:
-
When the client must discover a service endpoint before connecting.
-
When the service records exist only in internal DNS.
-
When DNS responses return target hostnames that require additional A, AAAA, or CNAME lookups and subsequent connections.
-
When the same user population is already using ZTA and you want to reduce VPN dependence for discovery-based workflows.
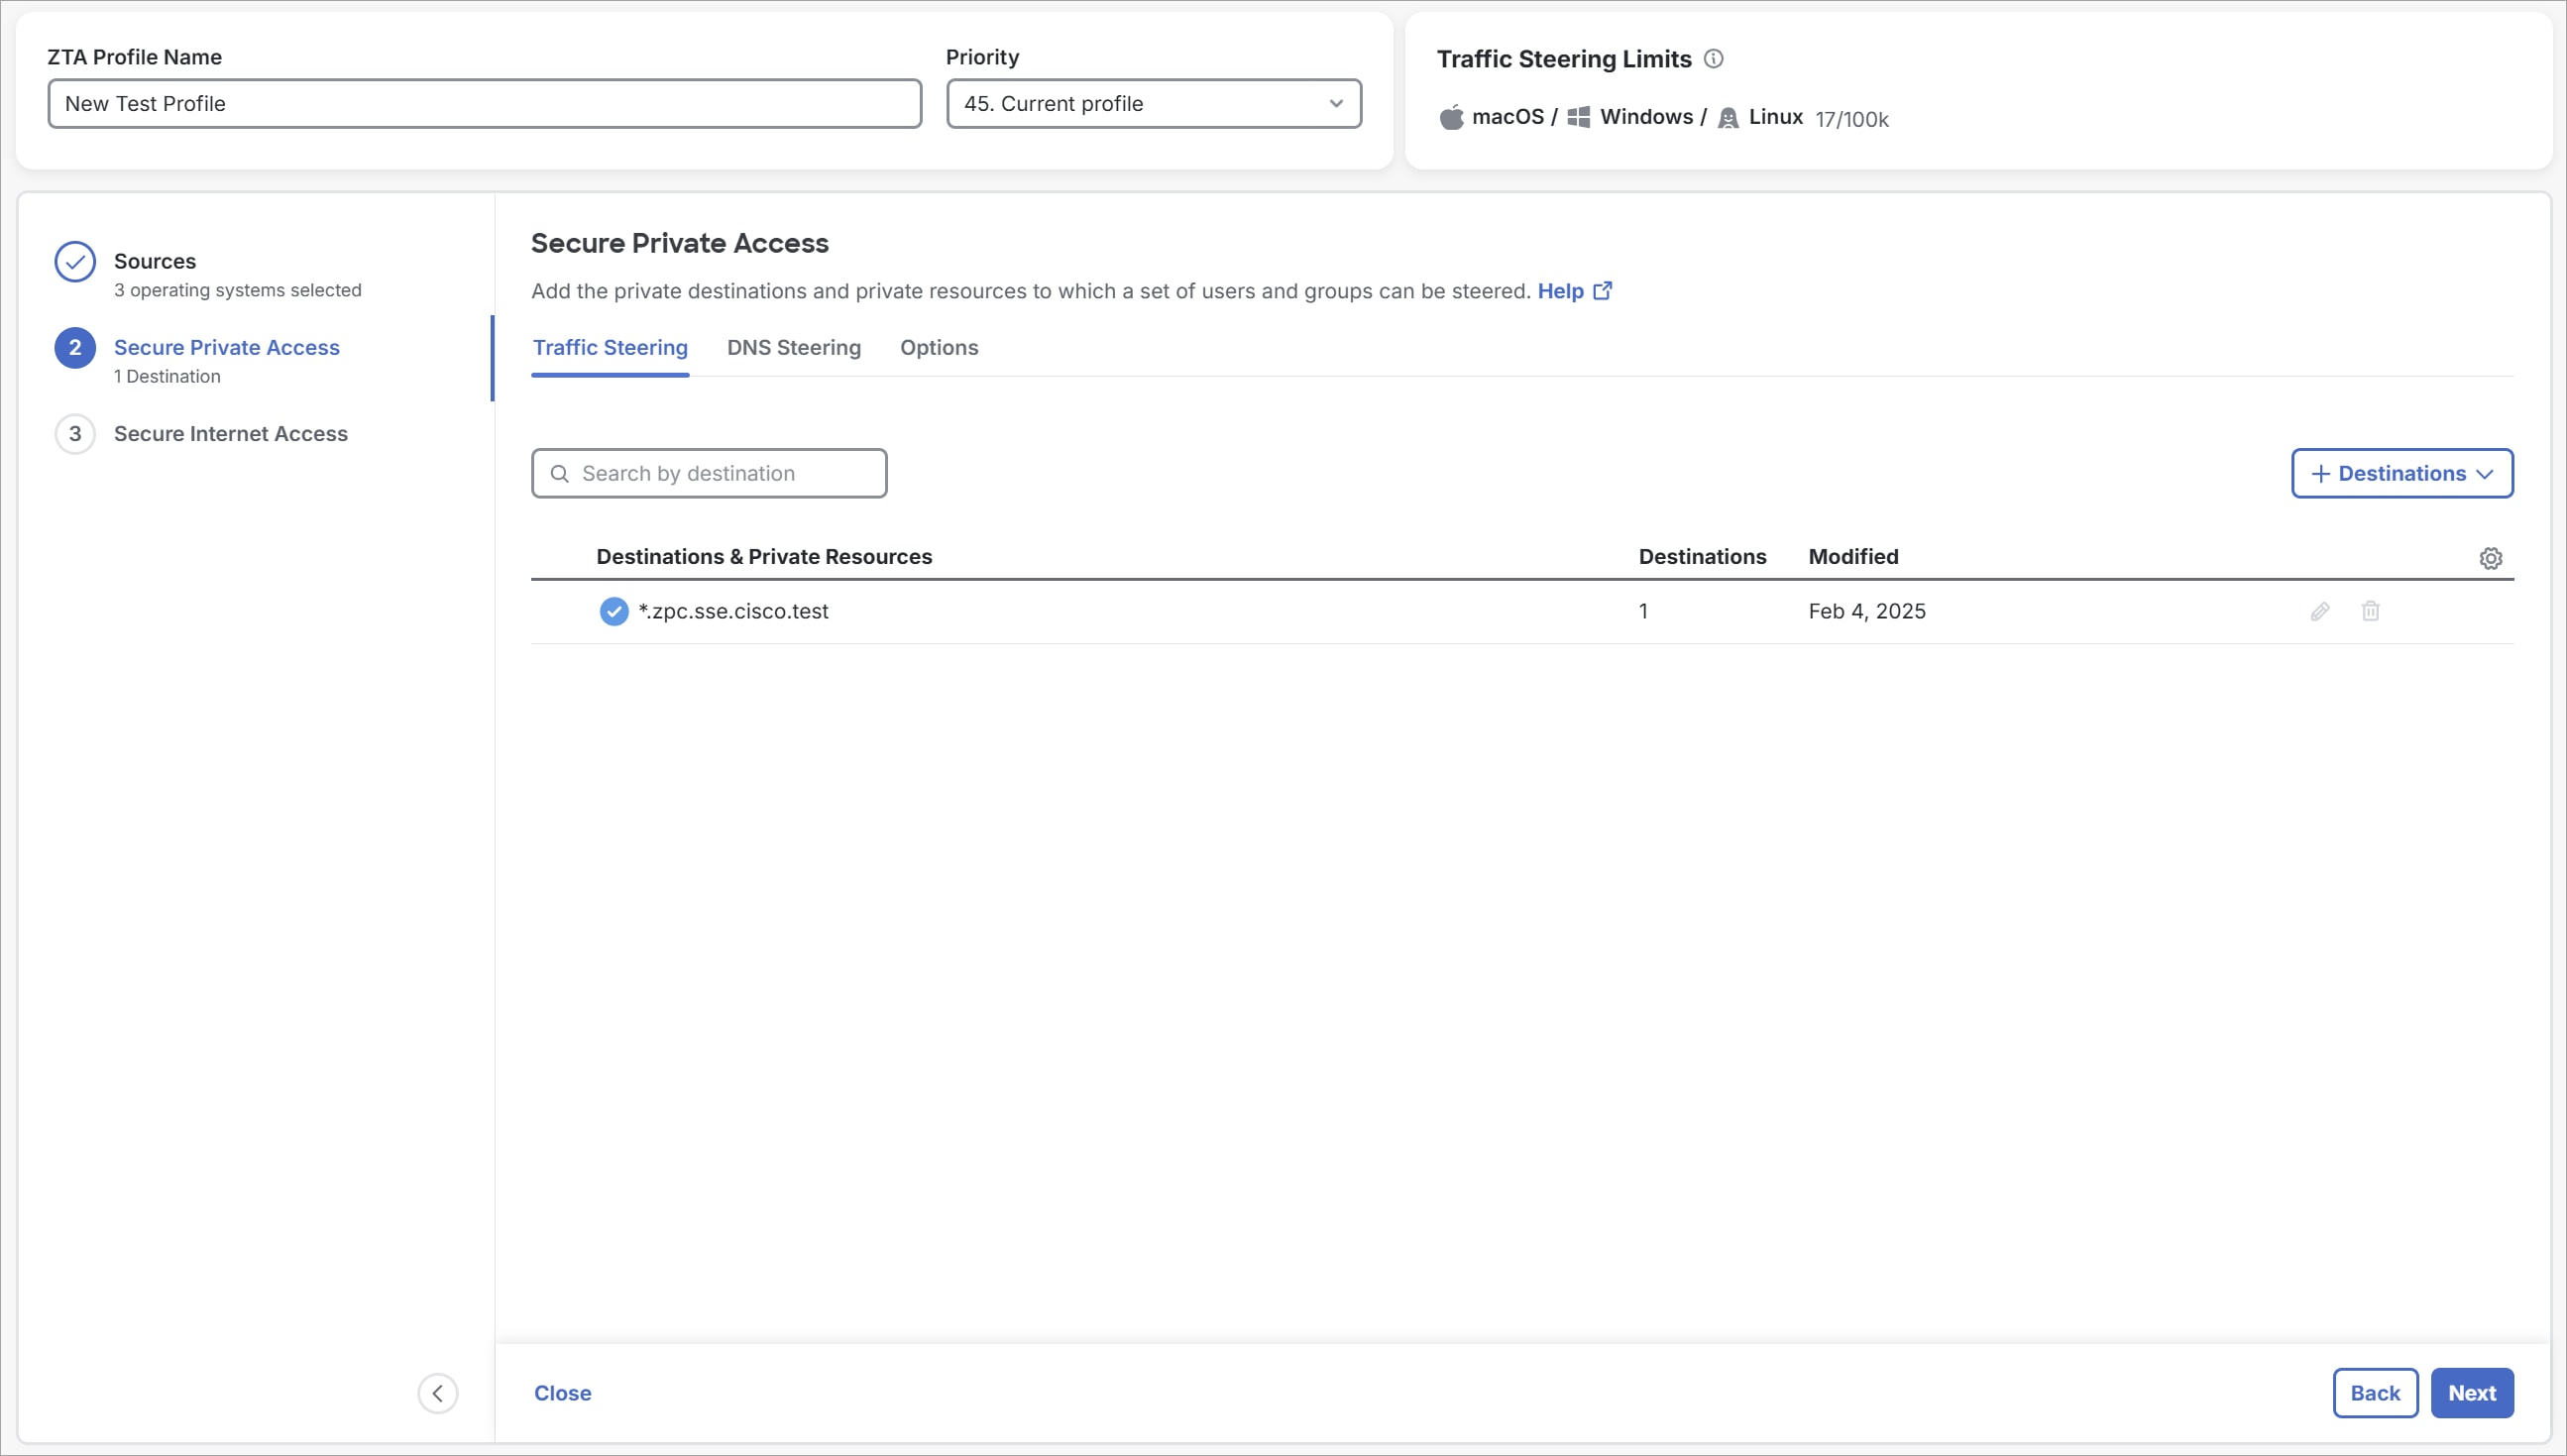
In Cisco Secure Access, Zero Trust traffic steering rules apply only for Client-based Zero Trust Access (ZTA) connections to internal destinations that are configured as private resources. When you configure a Private Resource, Secure Access automatically adds an entry for each configured resource address for Client-based ZTA to the Zero Trust Traffic Steering page, in order to direct end-user traffic to the resource.
View the traffic steering rules, but in most cases you should not edit the rules on the page. For more information, see Best Practices.
Use Cases for DNS Steering
If you edit entries that were automatically added to this page when you configured a Private Resource, the traffic steering rules for the resource are not updated when you make future edits to the Private Resource configuration page.
If you change the destination address on the Zero Trust Traffic Steering page, the original Private Resource will not have a traffic steering rule and Client-based ZTA connections to that resource will not occur even if configured in the resource.
AD Controller Discovery
Discover an appropriate domain controller over ZTA without requiring a full VPN connection solely for private DNS resolution. The client sends the service discovery request to the private resolution path, receives domain controller hostnames from internal DNS, and then proceeds with normal identity traffic to the returned hosts.
There may be other enterprise applications that rely on internal discovery records can find the correct service endpoint without requiring users to know the final hostname in advance. Internal discovery records are resolved through the intended private DNS path, allowing the application to continue with its normal connection logic after discovery completes.
Kerberos Dependent Authentication
dentity workflows that depend on Kerberos service discovery while working remotely through ZTA after sign-in. DNS steering preserves that discovery path for supported post-login workflows prior to authentication.
LDAP Directory Lookups
Enterprise applications that use LDAP often rely on DNS service records to locate directory services without hardcoding individual server names. By locating the internal DNS and then connecting to the returned directory server, you can steer the relevant discovery namespace allows this pattern to work over ZTA.