Describes Manage Zero Trust Access Posture Profiles in Cisco Secure Access. These profiles specify end-user device requirements when connecting to private and internet resources using Zero Trust Access.
These profiles specify end-user device requirements when connecting to private and internet resources using Zero Trust Access.
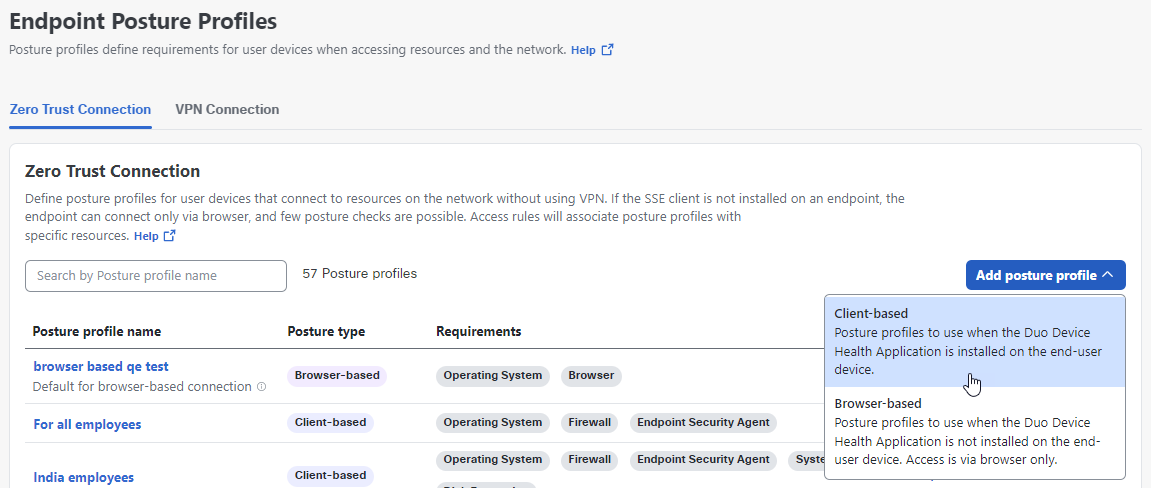
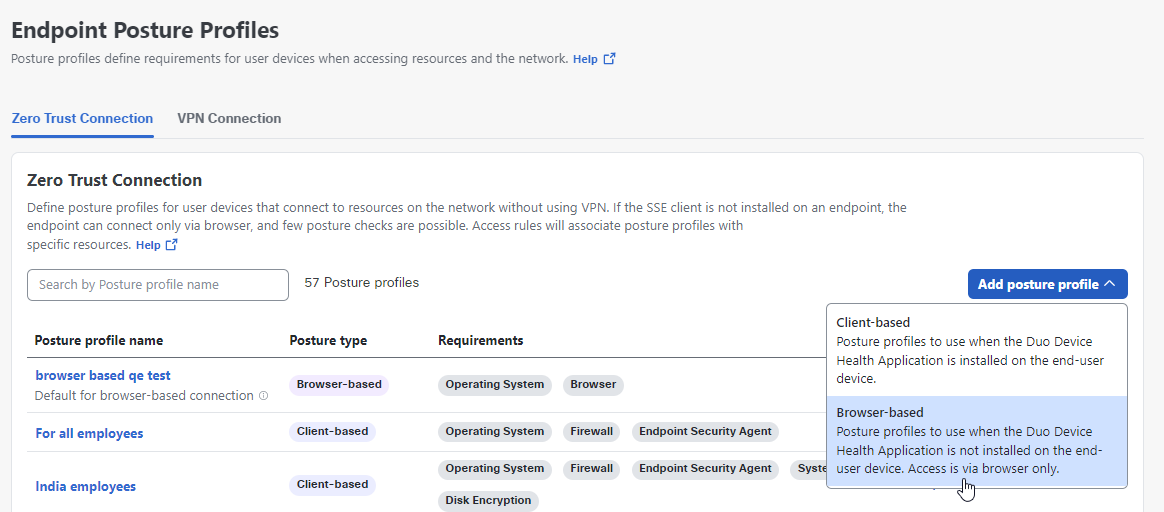
There are two types of profiles to choose from:
-
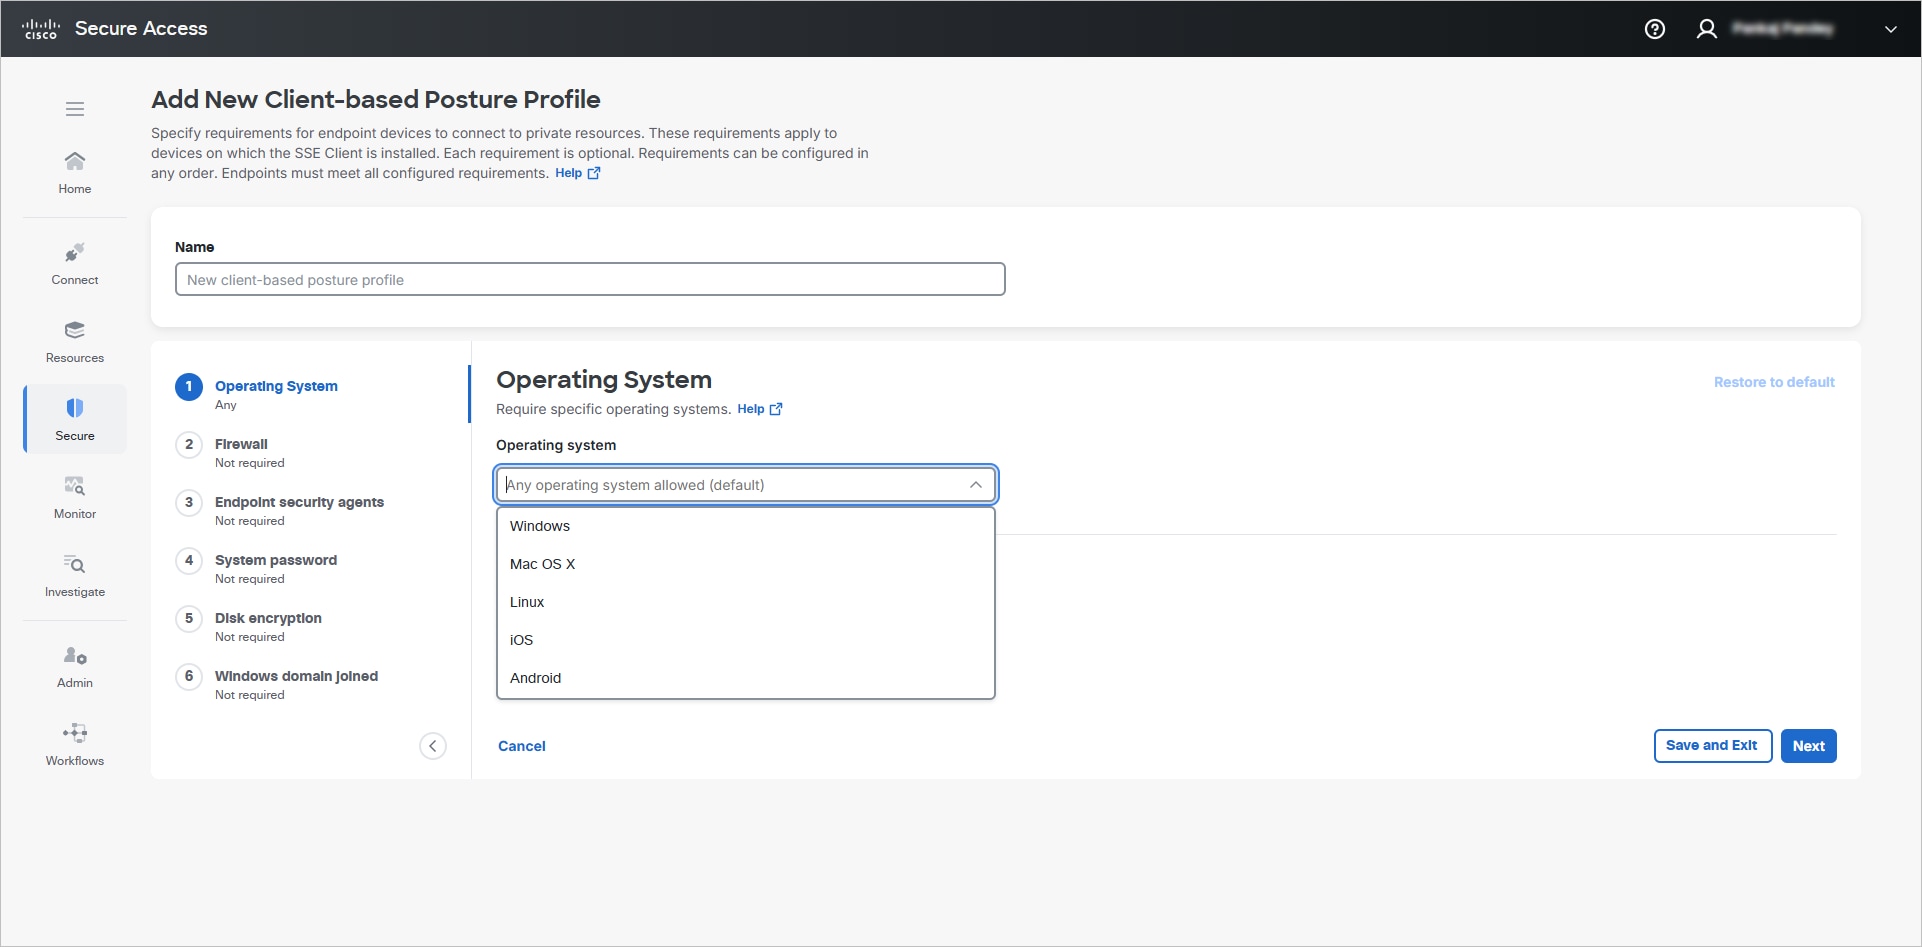
Client-based - Choose this as the default profile for devices on which the Cisco Secure Client is installed. Client-based profiles can also be used for internet access. See Add a Client-Based Zero Trust Access Posture Profile
-
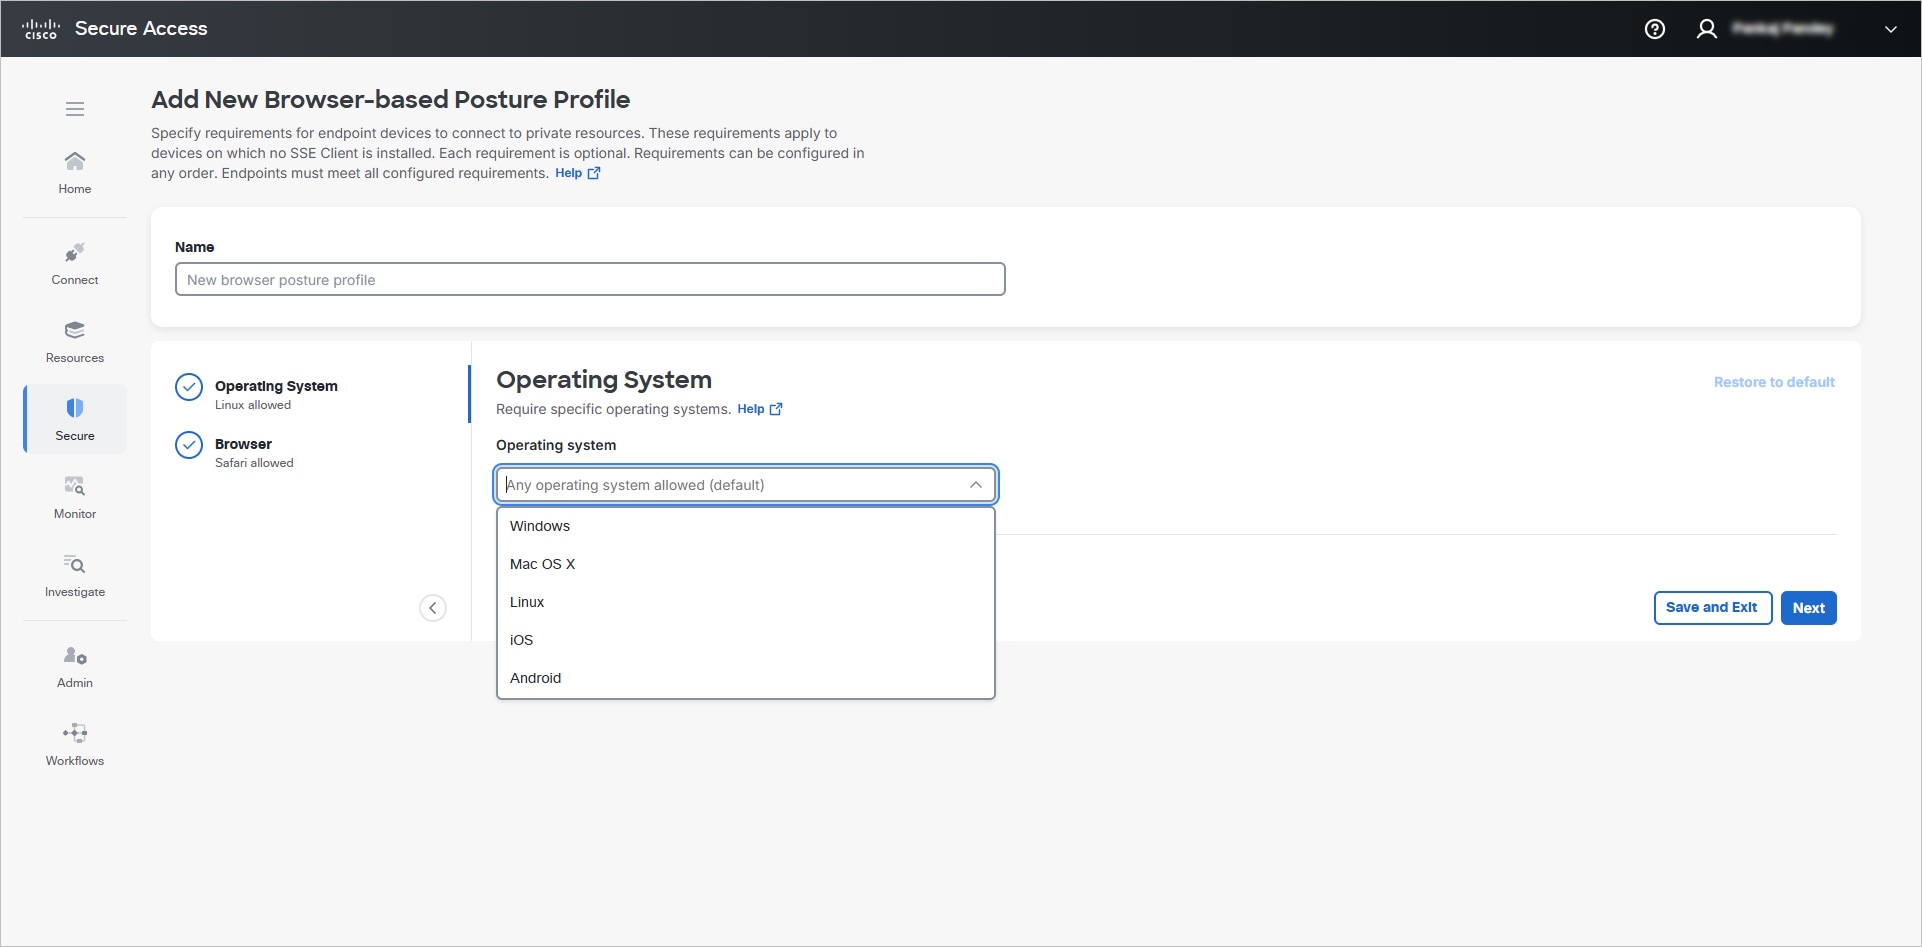
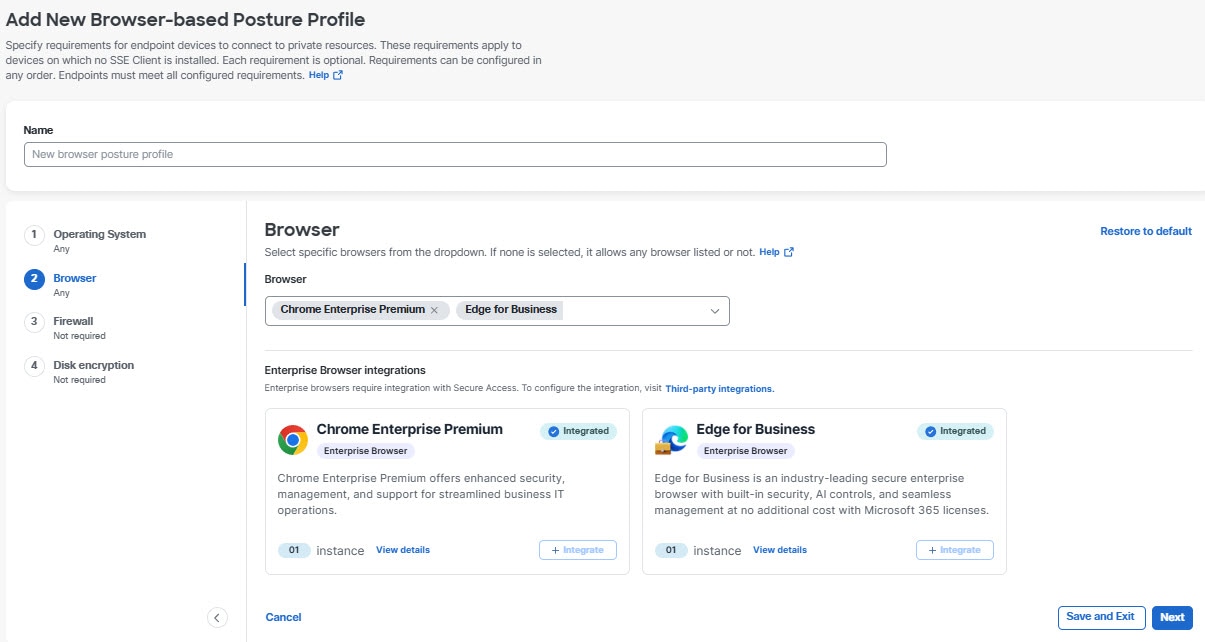
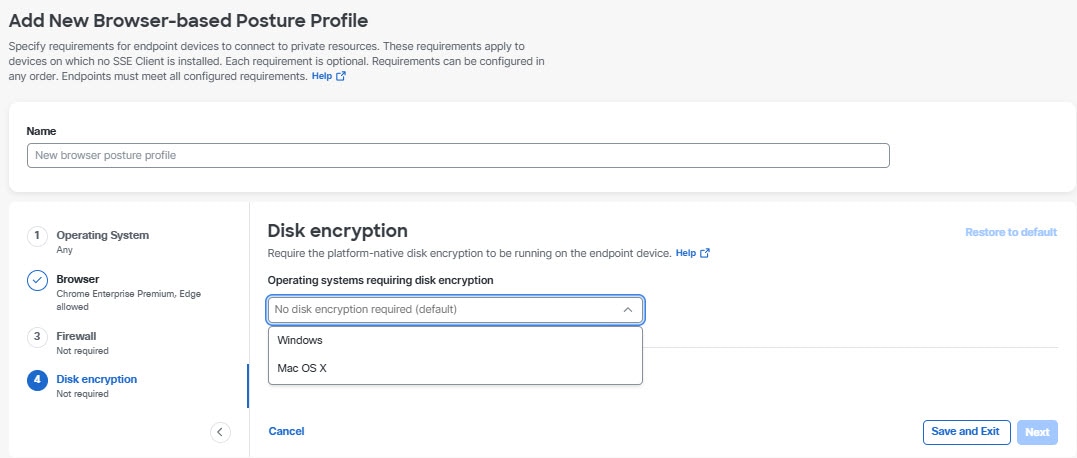
Browser-based - Choose this as the default profile for devices on which the Cisco Secure Client is not installed. See Add a Browser-Based Zero Trust Access Posture Profile
Enterprise browsers do not currently support proactive analysis functionality.
Client-based access permits more posture requirements than clientless access, so you should tailor profiles to the type of access.
ZTA Posture Timeouts
Timeouts are built into ZTA posture profiles and are expected in a healthy environment. Note that these are not applicable for mobile ZTA
Posture Refresh rate - 5 minutes.
A posture refresh rate is the status of the posture fetched by the client-based access policy. It is cached in a cookie and the cookie itself is what expires at five minutes.
Stale Posture Status - 15 minutes.
This is max amount of time before a posture is considered stale and outdated. The posture status is fetched from Duo cloud is timestamped from the end device. If that timestamp is 15 minutes or greater when it is fetched, then the posture is considered stale and is rejected.
Zero Trust Access Posture Attributes
The following
-
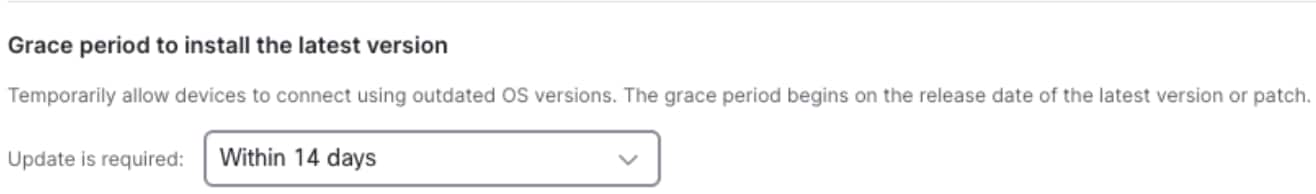
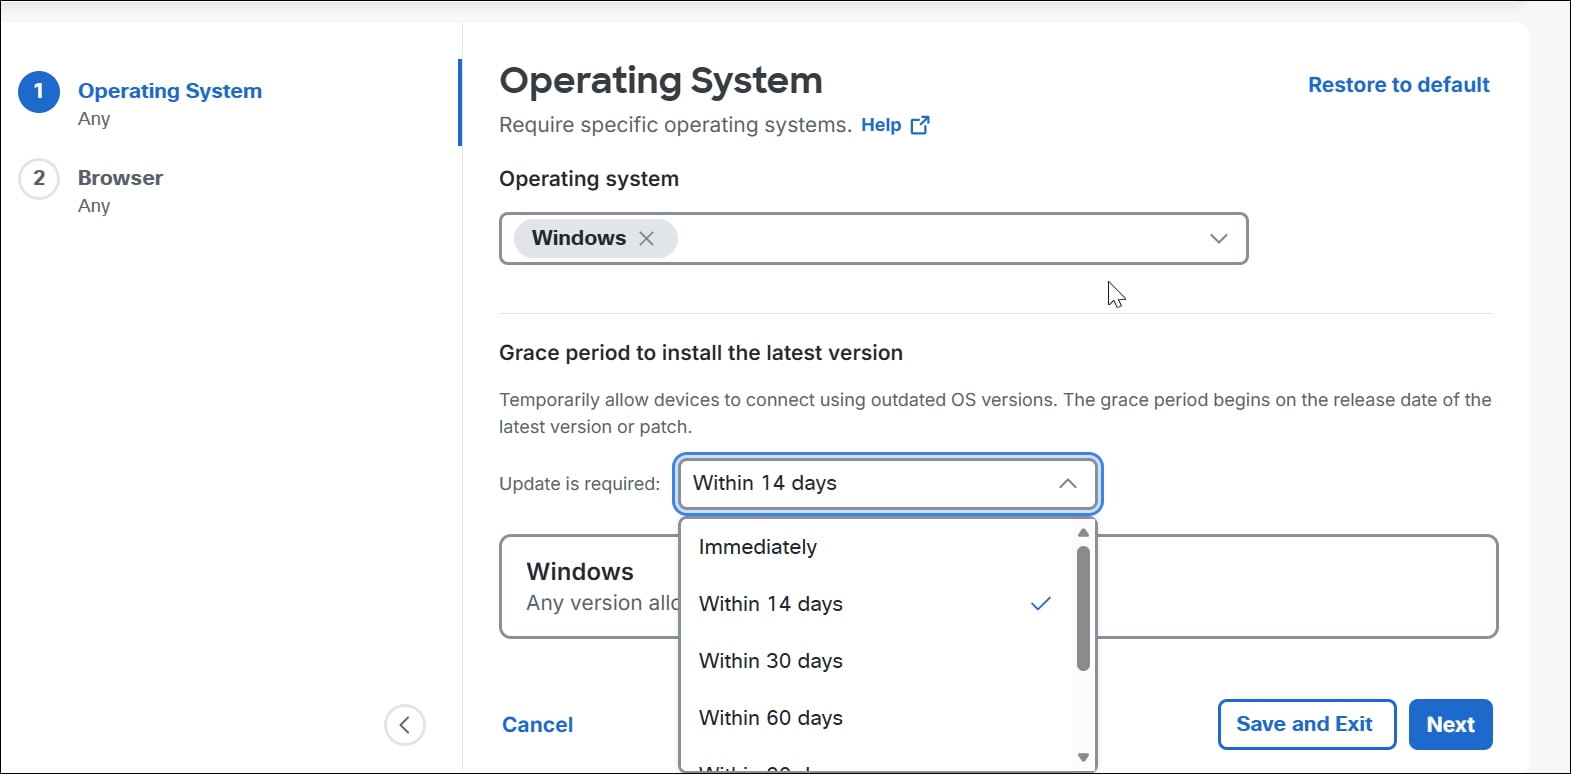
Supported operating systems
-
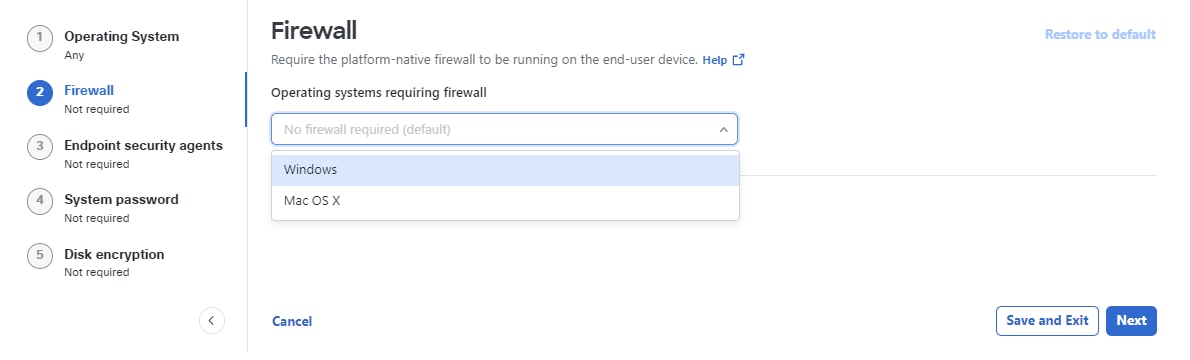
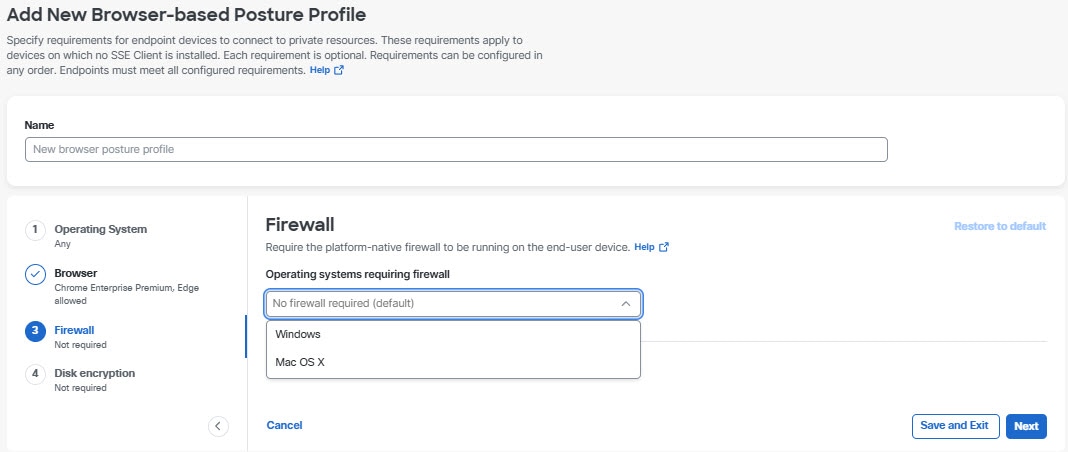
Firewall
-
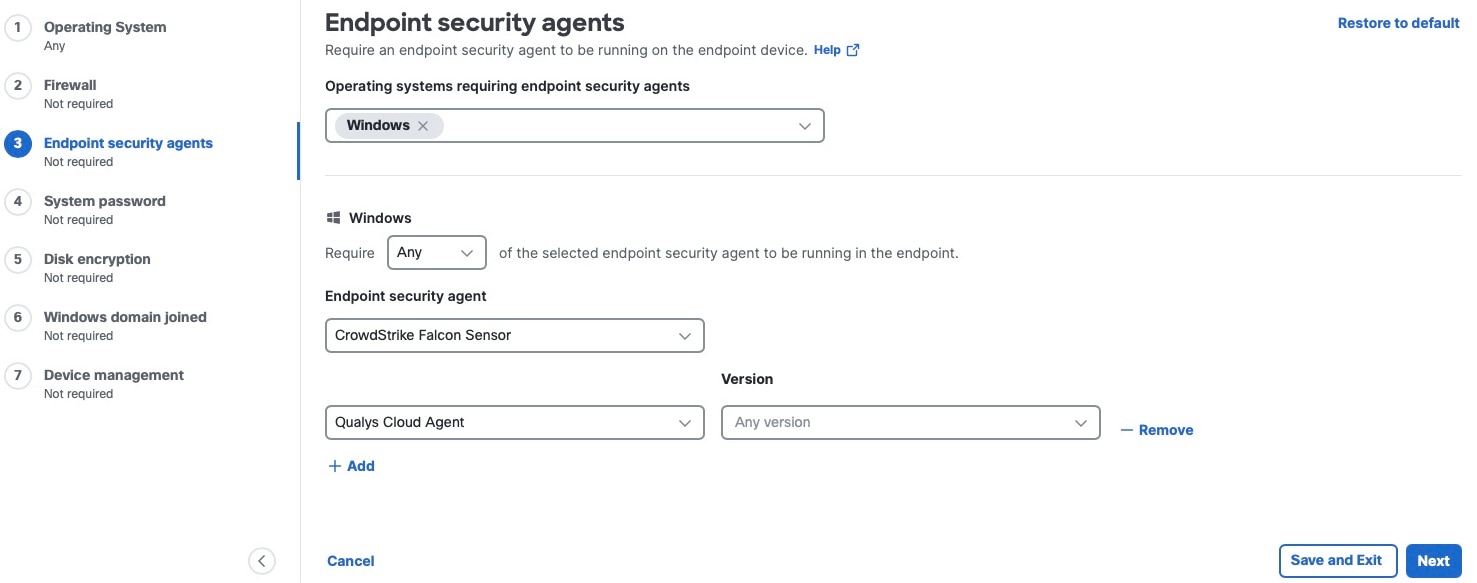
Endpoint security agents
-
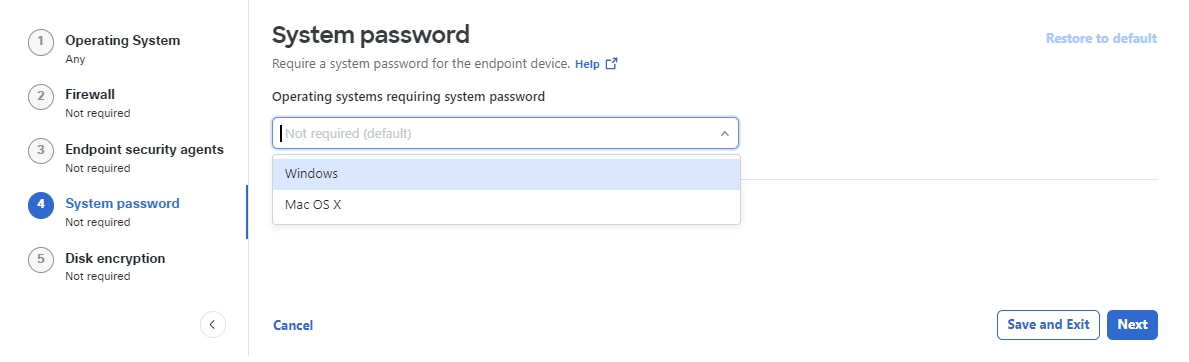
System password
-
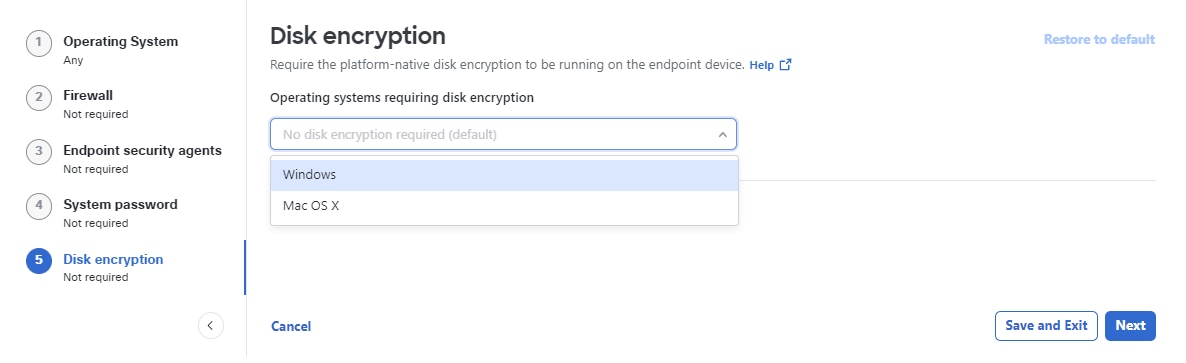
Disk encryption
-
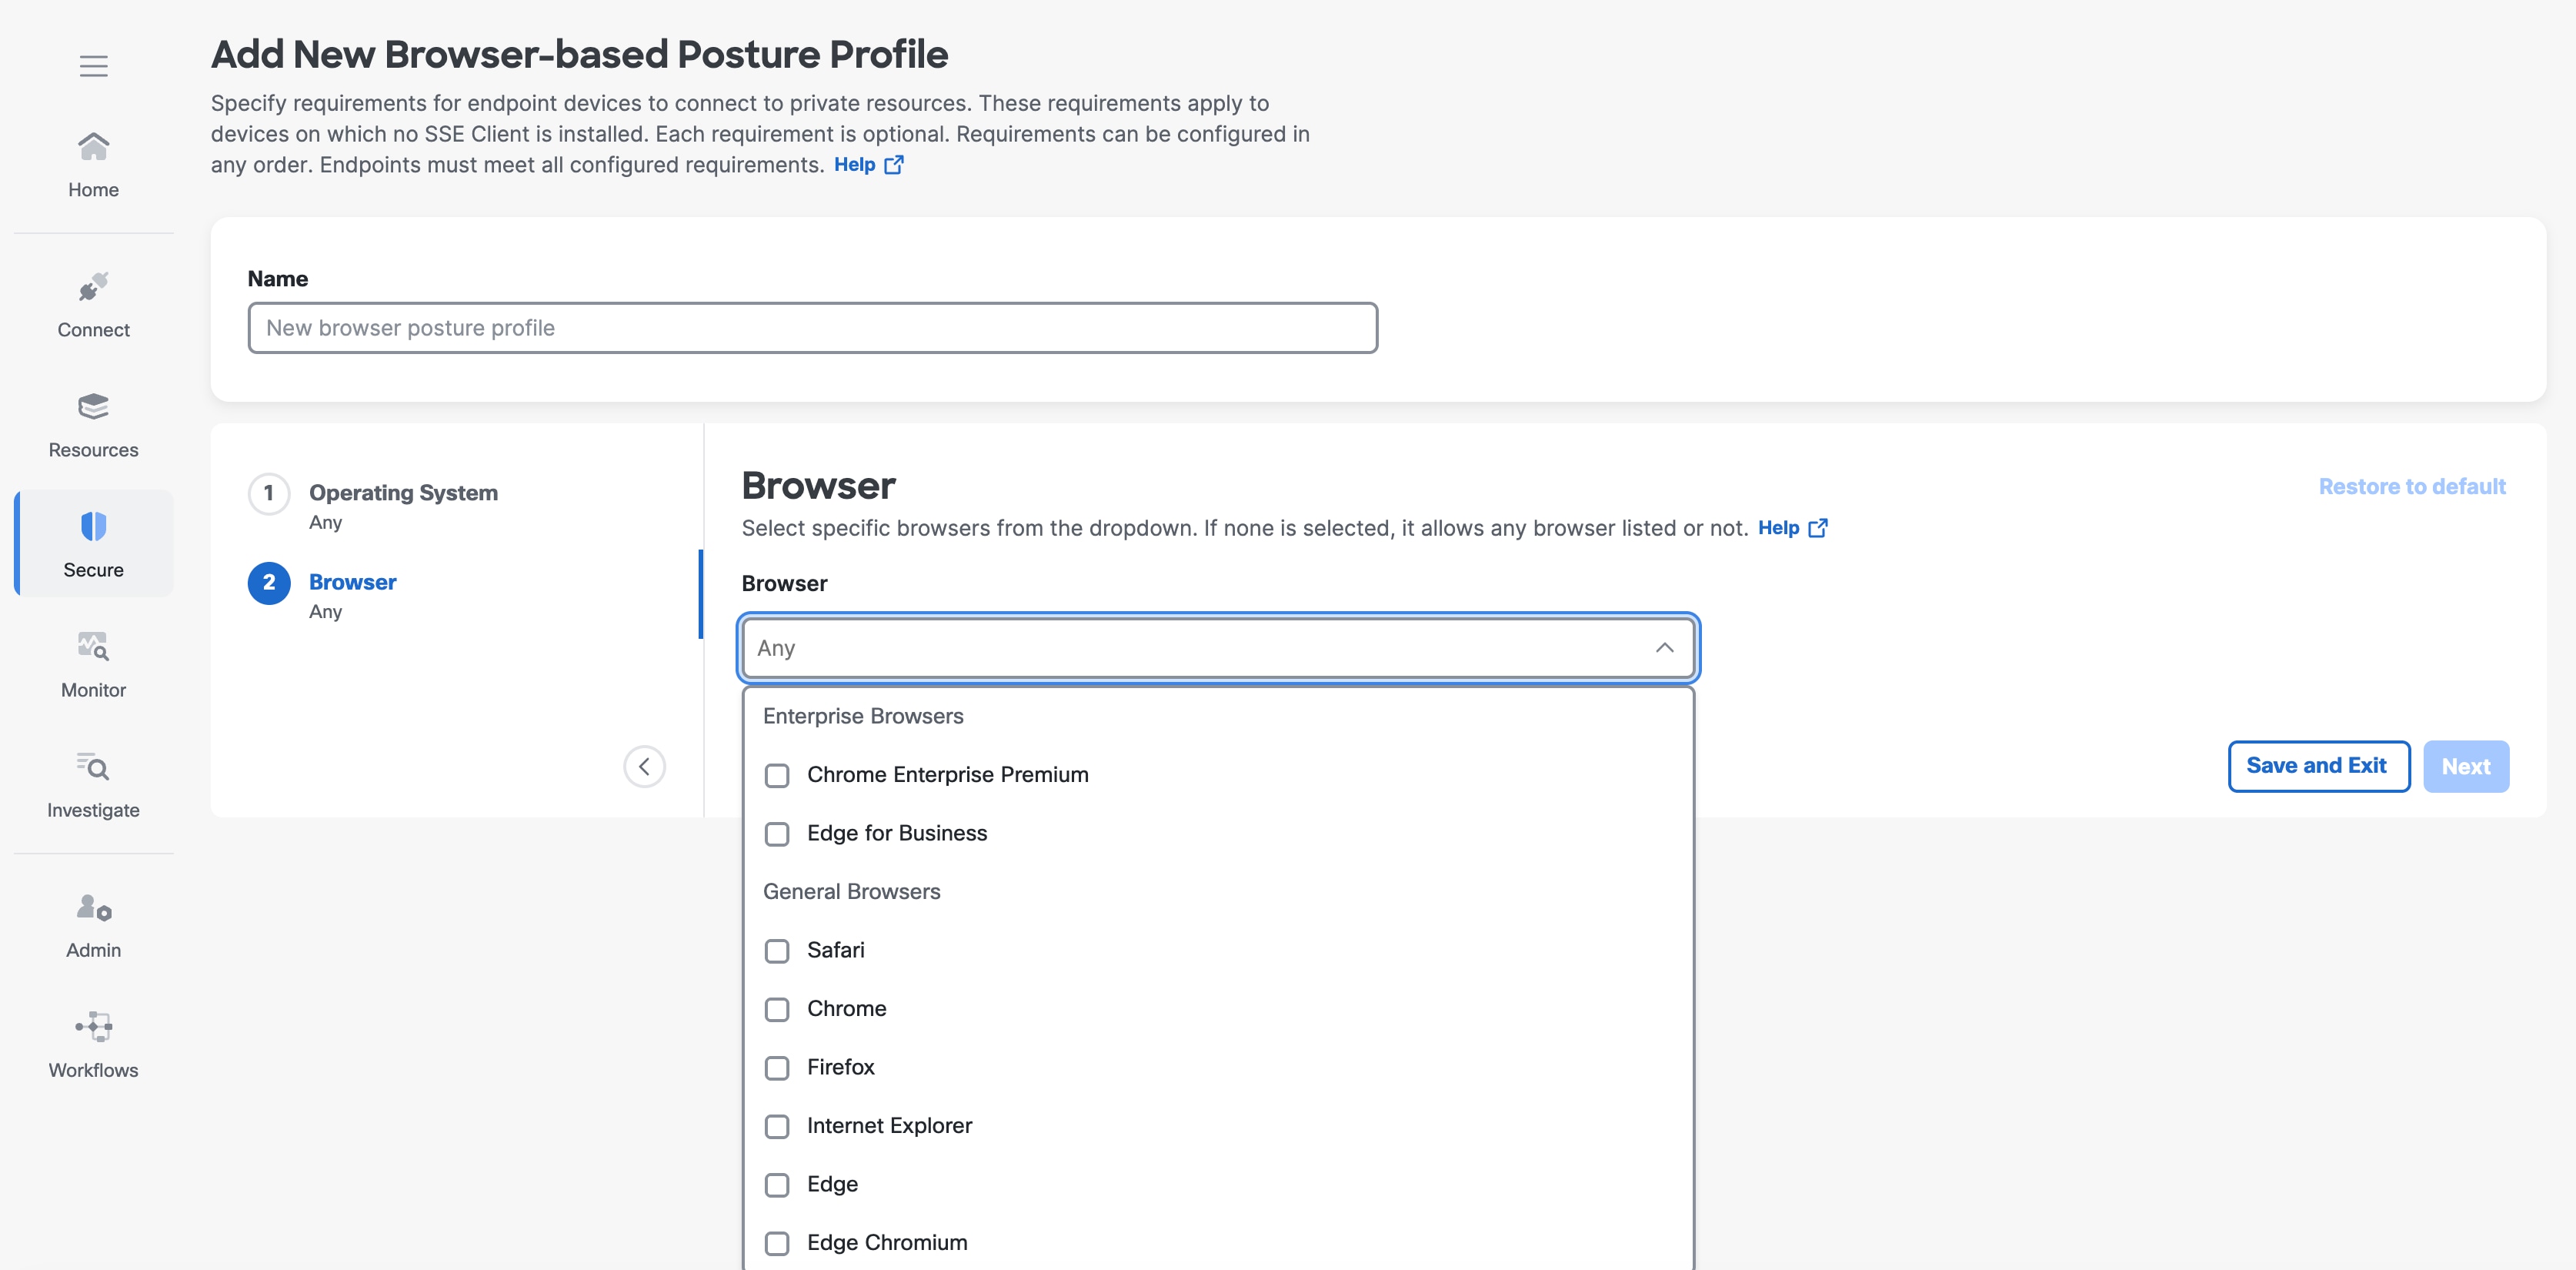
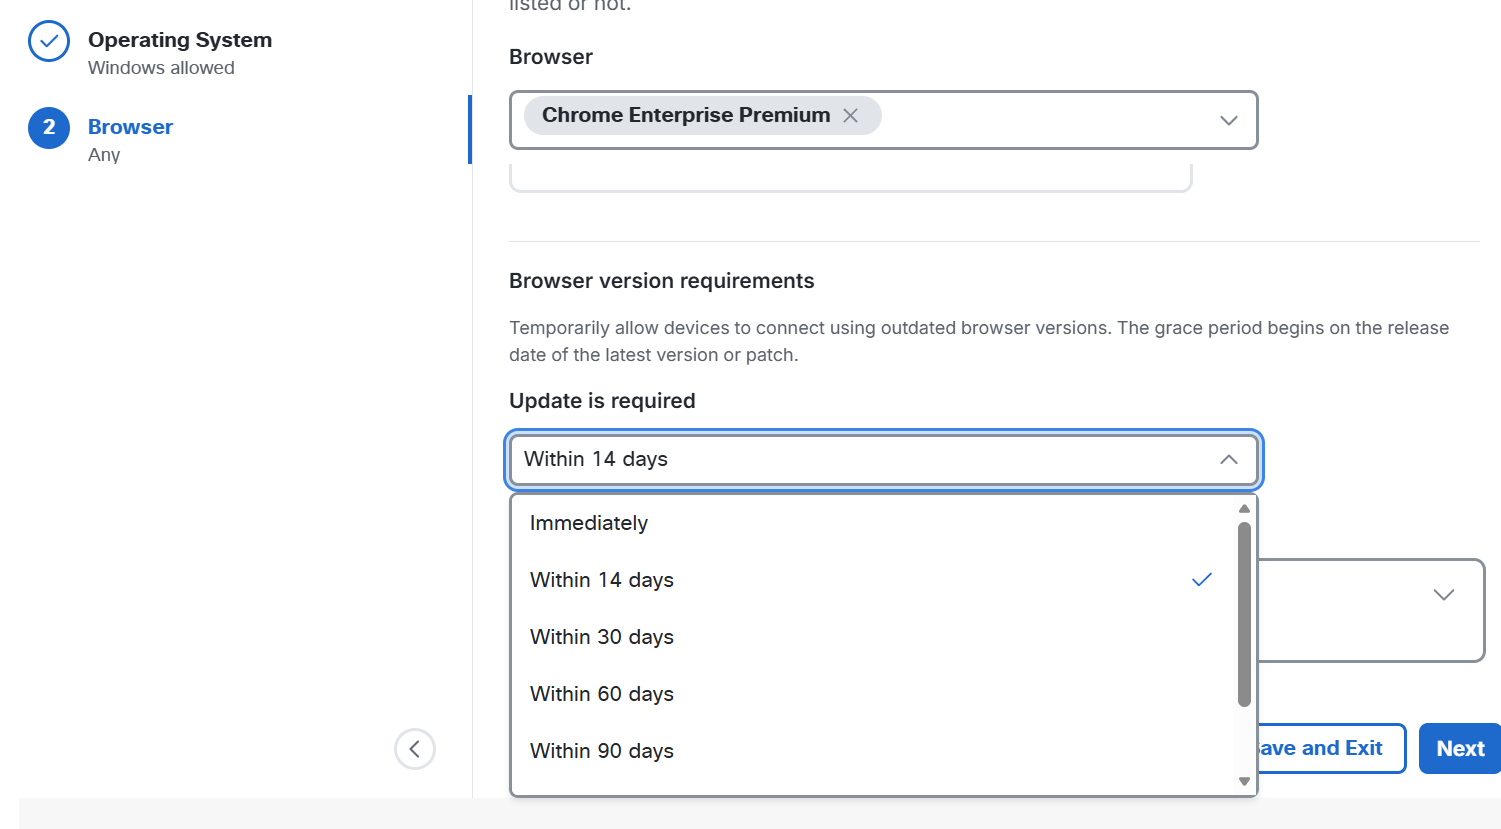
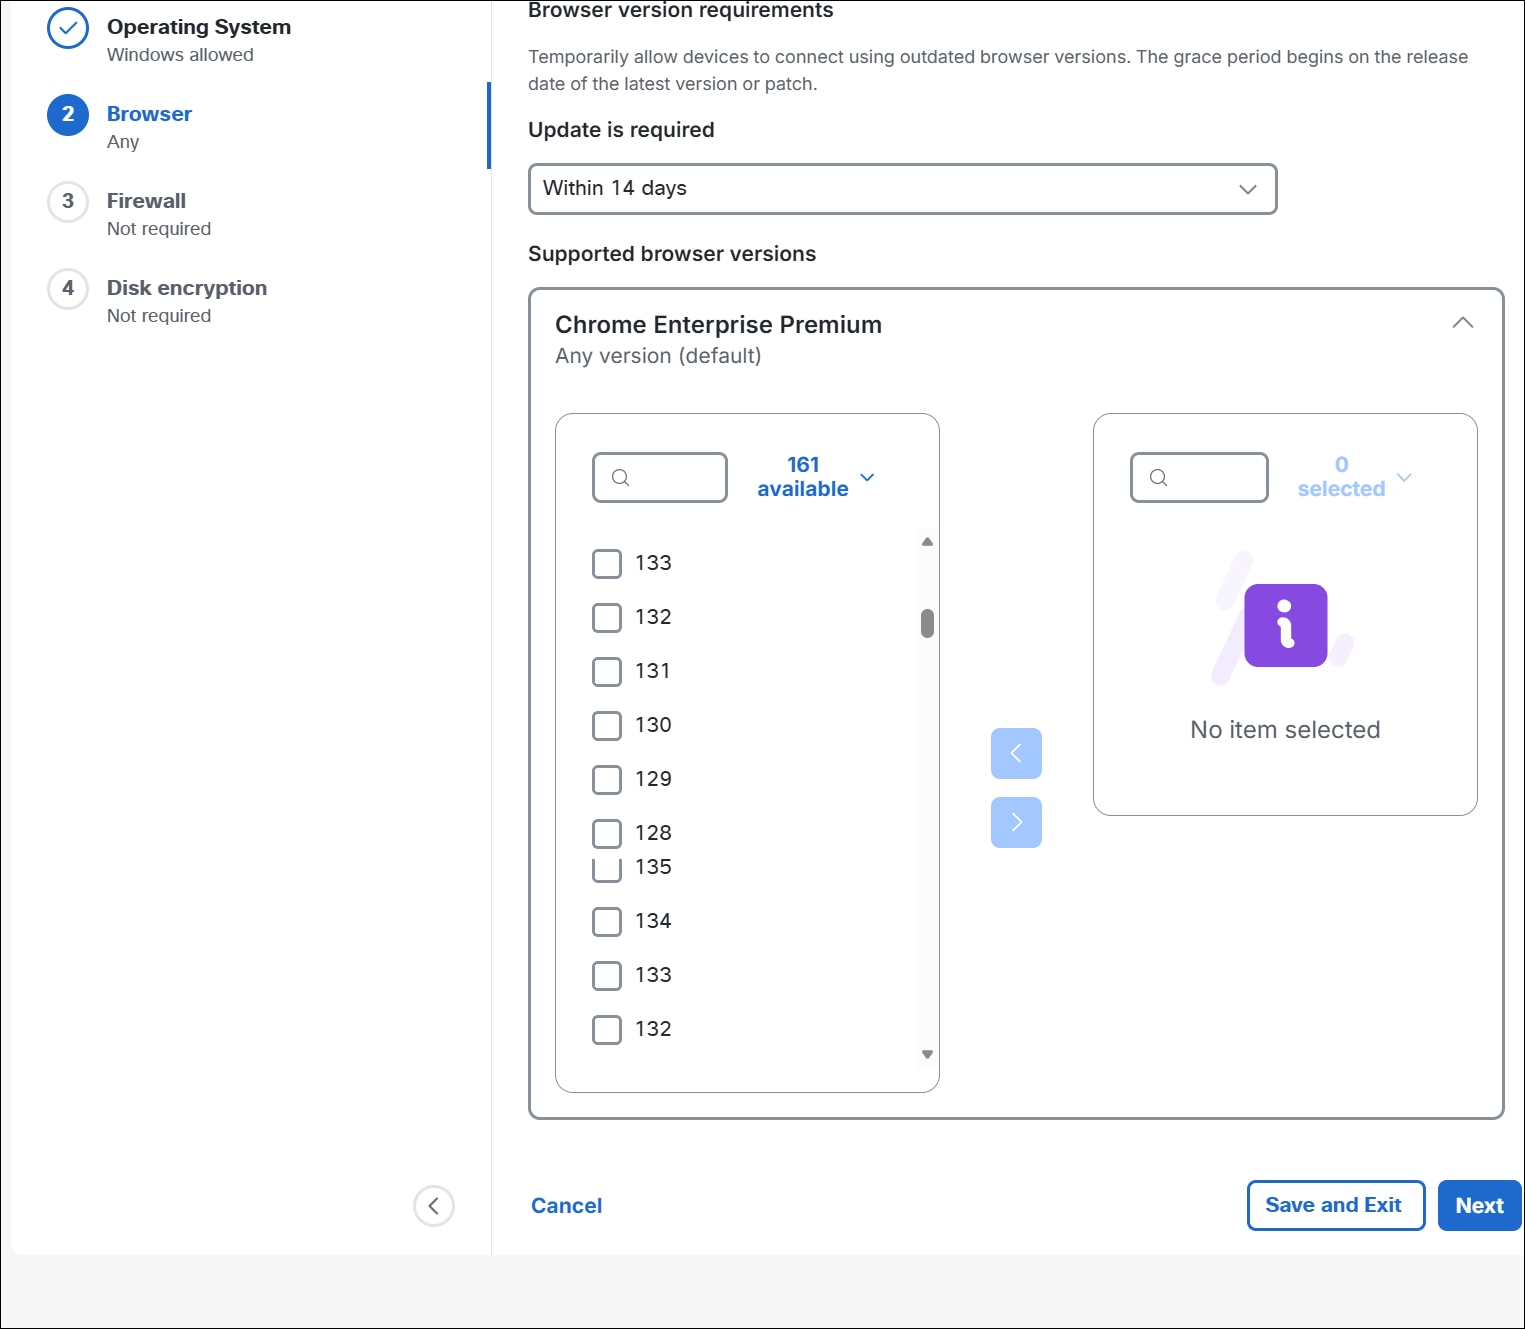
Browser